Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
The Sorry State Of SSL by Hynek Schlawack
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
PyCon 2014
April 12, 2014
Technology
580
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
The Sorry State Of SSL by Hynek Schlawack
PyCon 2014
April 12, 2014
More Decks by PyCon 2014
See All by PyCon 2014
Postgres Performance for Humans by Craig Kerstiens
pycon2014
28
3.7k
Technical Onboarding, Training, and Mentoring by Kate Heddleston and Nicole Zuckerman
pycon2014
1
2.4k
"My big gay adventure. Making, releasing and selling an indie game made in python." by Luke Miller
pycon2014
2
1.7k
Farewell and Welcome Home, Python in Two Genders by Naomi_Ceder
pycon2014
1
820
Deliver Your Software in an Envelope by Augie Fackler and Nathaniel Manista
pycon2014
1
620
Hitchhikers Guide to Free and Open Source Participation by Elena Williams
pycon2014
6
1.3k
Localization Revisted (aka. Translations Evolved) by Ruchi Varshney
pycon2014
0
740
Smart Dumpster by Bradley E. Angell
pycon2014
0
600
Software Engineering for Hackers: Bridging the Two Solitudes by Tavish Armstrong
pycon2014
0
790
Other Decks in Technology
See All in Technology
購入ドメインでの課題と取り組み
ykagano
0
140
AI時代のAPI開発を加速する品質ガードレール / API Quality Guardrails in the AI Era
yokawasa
0
150
Snapshot Testing in Practice: Predictable and Reliable SwiftUI Views
fespinoza
0
120
AI時代だからこそ推したい!Gitコマンド再入門
munakata
0
150
Oracle Base Database Service 技術詳細
oracle4engineer
PRO
17
120k
AI Made Us Faster at Solving the Wrong Problems
marceloancelmo
0
160
AI 時代の Azure エンジニアリング ~ 私たちは何を磨き、何を任せるのか ~
chack411
1
470
[2026 Oracle Technical Deep Dive] オンプレミスDBのCloud移行アプローチ:移行計画に基づくメソッドとツールの選択 (2026年9月17日開催)
oracle4engineer
PRO
0
150
SDDの運用にめげずに向き合った話
sansantech
PRO
1
130
オブザーバビリティを高める AI エージェント体験を考える / Designing AI Agent Experiences That Enhance Observability
aoto
PRO
2
310
生成AIを使って「人が」考える技術 ― AI時代の人機共想と実践ノウハウ|UNITT AC2026
ishiirikie
0
550
カンファレンスに参加した後の浮遊感とセルフケア
pauli
0
310
Featured
See All Featured
Deep Space Network (abreviated)
tonyrice
0
350
Self-Hosted WebAssembly Runtime for Runtime-Neutral Checkpoint/Restore in Edge–Cloud Continuum
chikuwait
0
860
SEOcharity - Dark patterns in SEO and UX: How to avoid them and build a more ethical web
sarafernandez
0
300
BBQ
matthewcrist
89
10k
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
Reality Check: Gamification 10 Years Later
codingconduct
0
2.3k
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
340
Getting science done with accelerated Python computing platforms
jacobtomlinson
2
520
10 Git Anti Patterns You Should be Aware of
lemiorhan
PRO
659
62k
DevOps and Value Stream Thinking: Enabling flow, efficiency and business value
helenjbeal
1
400
Mobile First: as difficult as doing things right
swwweet
225
10k
Leadership Guide Workshop - DevTernity 2021
reverentgeek
1
380
Transcript
THE SORRY STATE OF SSL Hynek Schlawack
@hynek https://hynek.me https://github.com/hynek https://www.variomedia.de Hi!
None
None
None
ONLY LINK ox.cx/t
WTF
WTF SSL
WTF SSL & TLS
TIMELINE
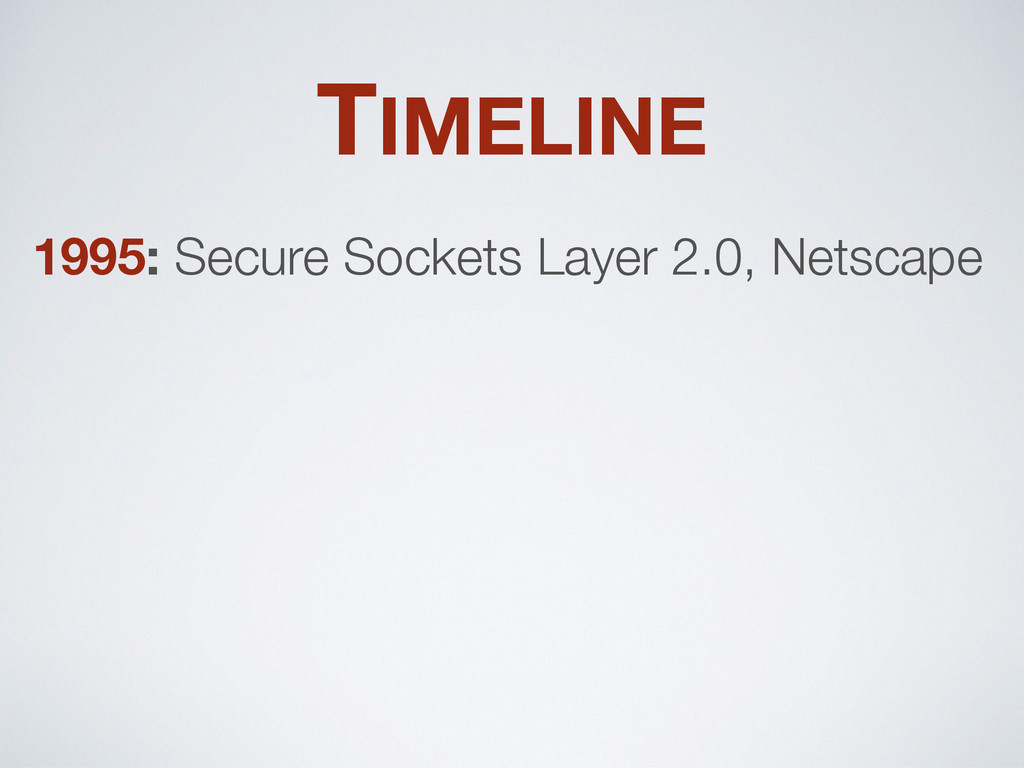
TIMELINE 1995: Secure Sockets Layer 2.0, Netscape
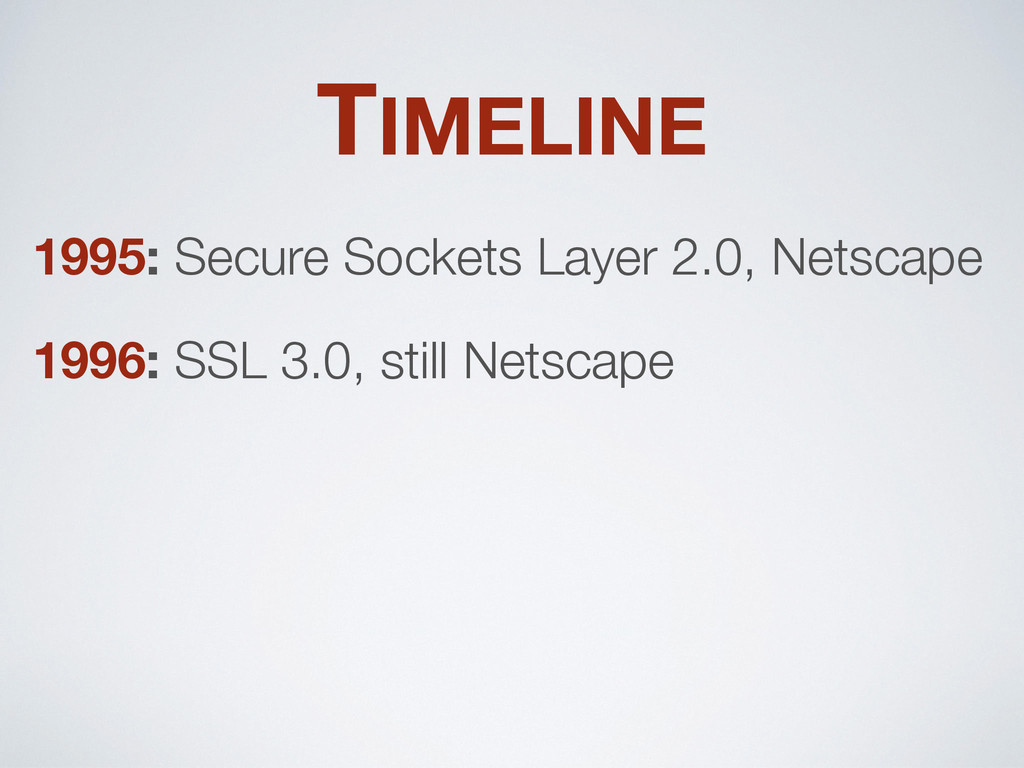
TIMELINE 1995: Secure Sockets Layer 2.0, Netscape 1996: SSL 3.0,
still Netscape
TIMELINE 1995: Secure Sockets Layer 2.0, Netscape 1996: SSL 3.0,
still Netscape 1999: Transport Layer Security 1.0, IETF
TIMELINE 1995: Secure Sockets Layer 2.0, Netscape 1996: SSL 3.0,
still Netscape 1999: Transport Layer Security 1.0, IETF 2006: TLS 1.1
TIMELINE 1995: Secure Sockets Layer 2.0, Netscape 1996: SSL 3.0,
still Netscape 1999: Transport Layer Security 1.0, IETF 2006: TLS 1.1 2008: TLS 1.2
2013
2013 • newfound scrutiny
2013 • newfound scrutiny • browsers add TLS 1.2
2013 • newfound scrutiny • browsers add TLS 1.2 •
just using TLS not enough
TLS
TLS • identity
TLS • identity • confidentiality
TLS • identity • confidentiality • integrity
TLS HYGIENE
SERVERS
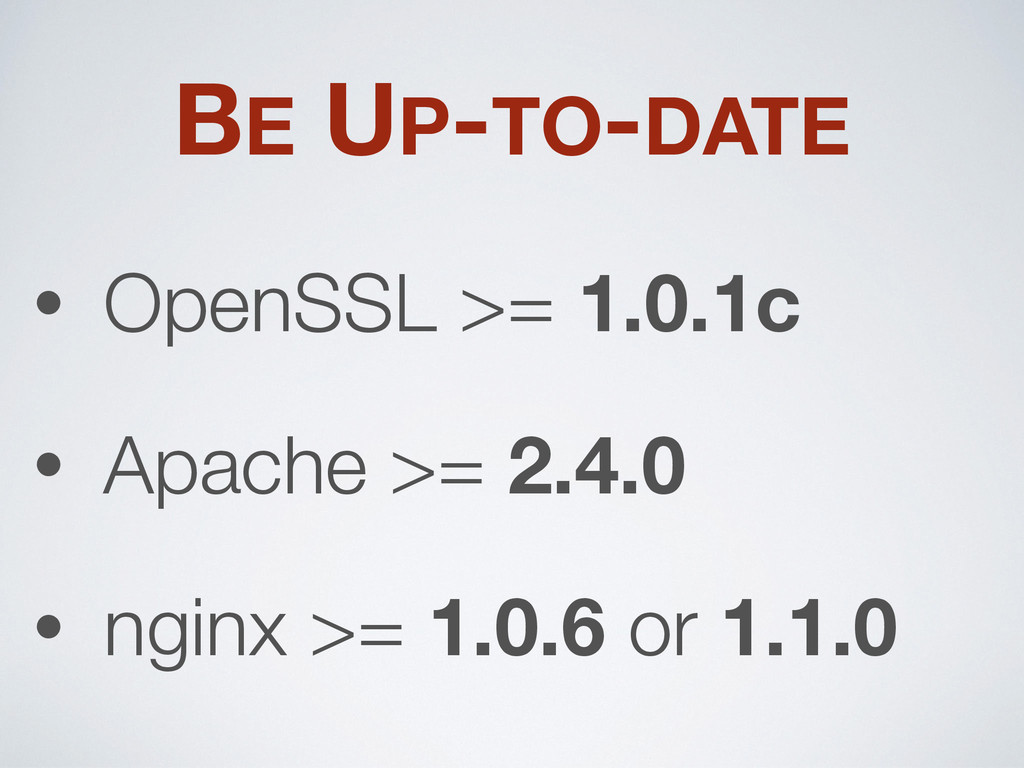
BE UP-TO-DATE • OpenSSL >= 1.0.1c • Apache >= 2.4.0
• nginx >= 1.0.6 or 1.1.0
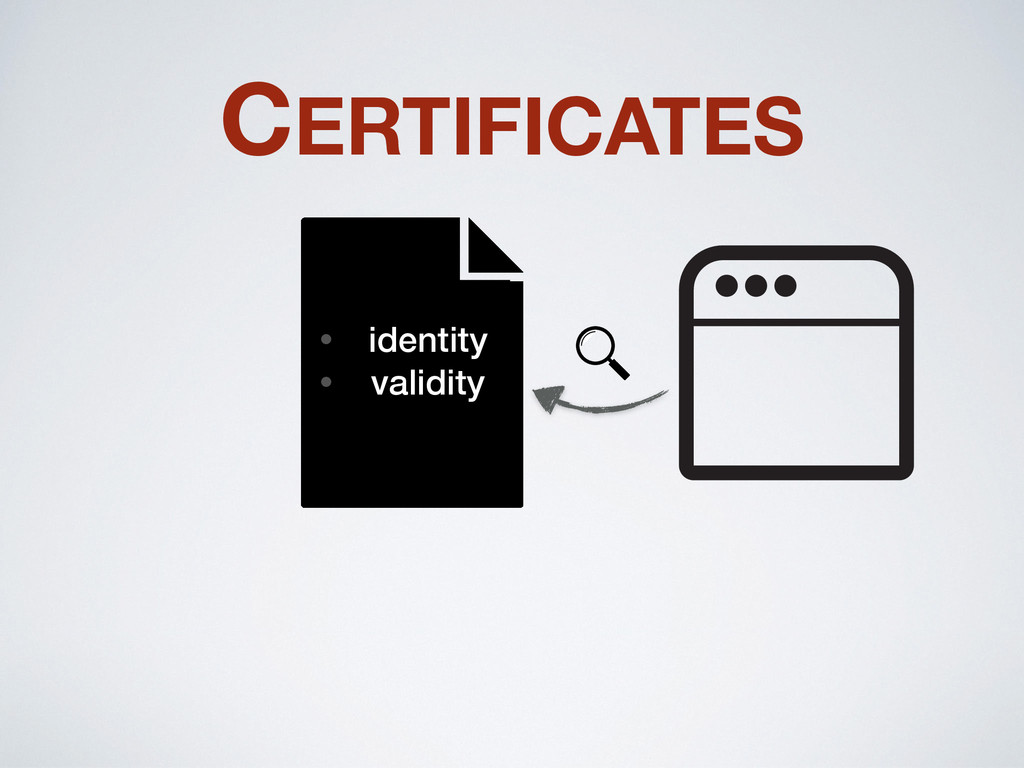
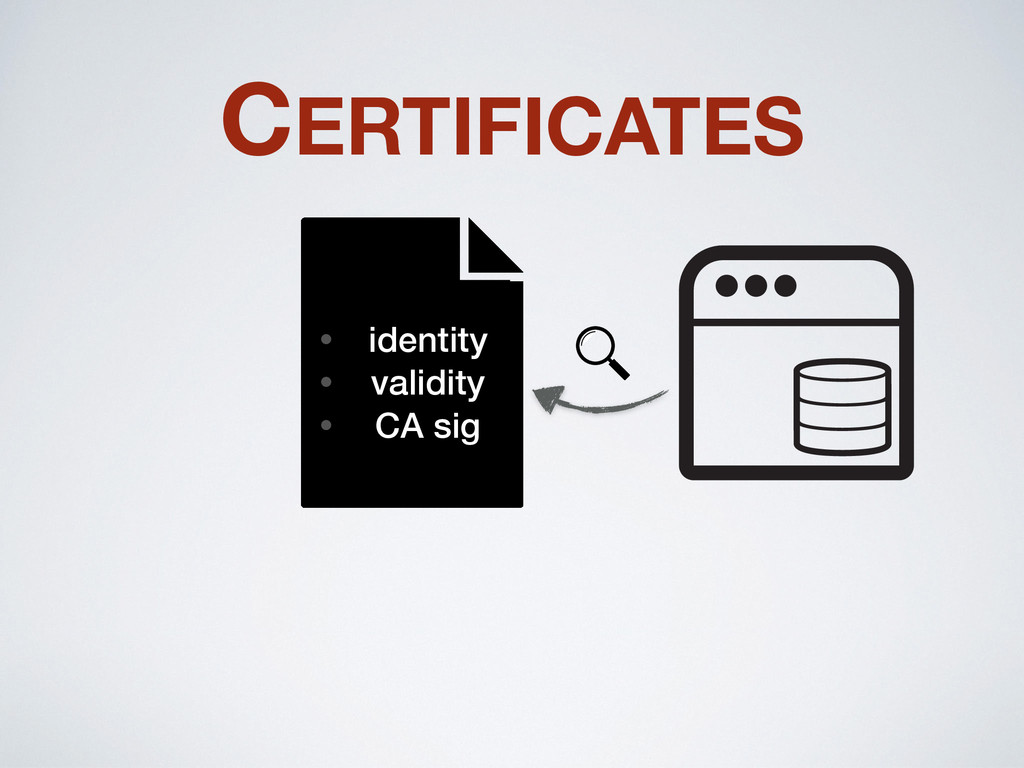
CERTIFICATES • identity • validity
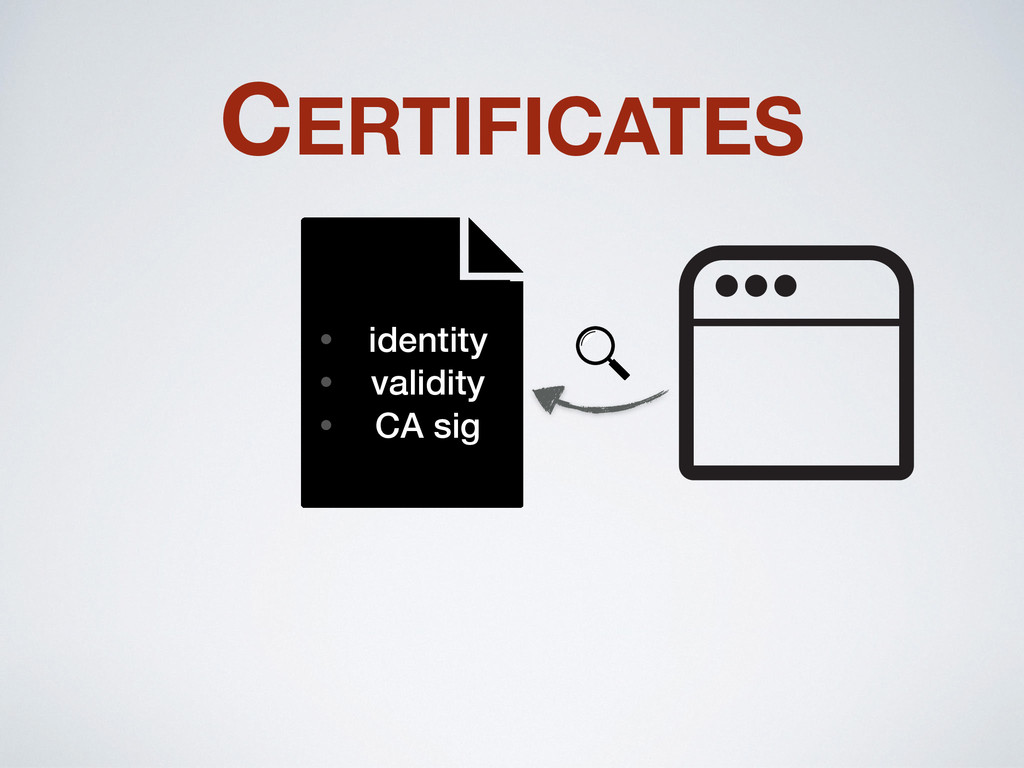
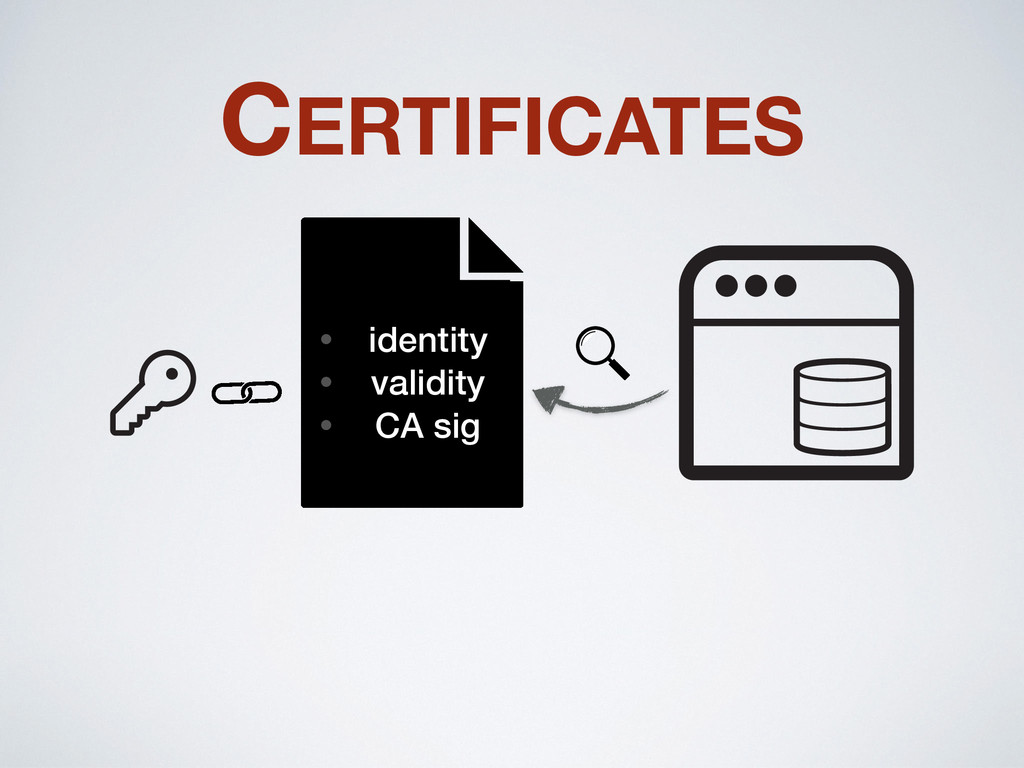
CERTIFICATES • identity • validity • CA sig
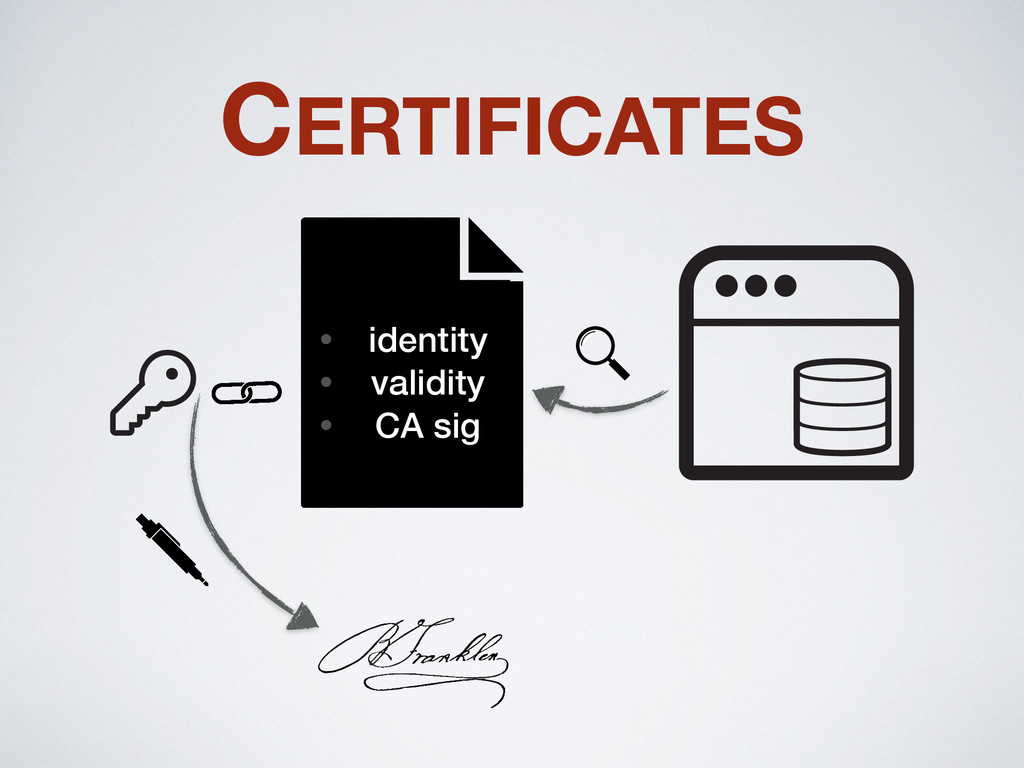
CERTIFICATES • identity • validity • CA sig
CERTIFICATES • identity • validity • CA sig
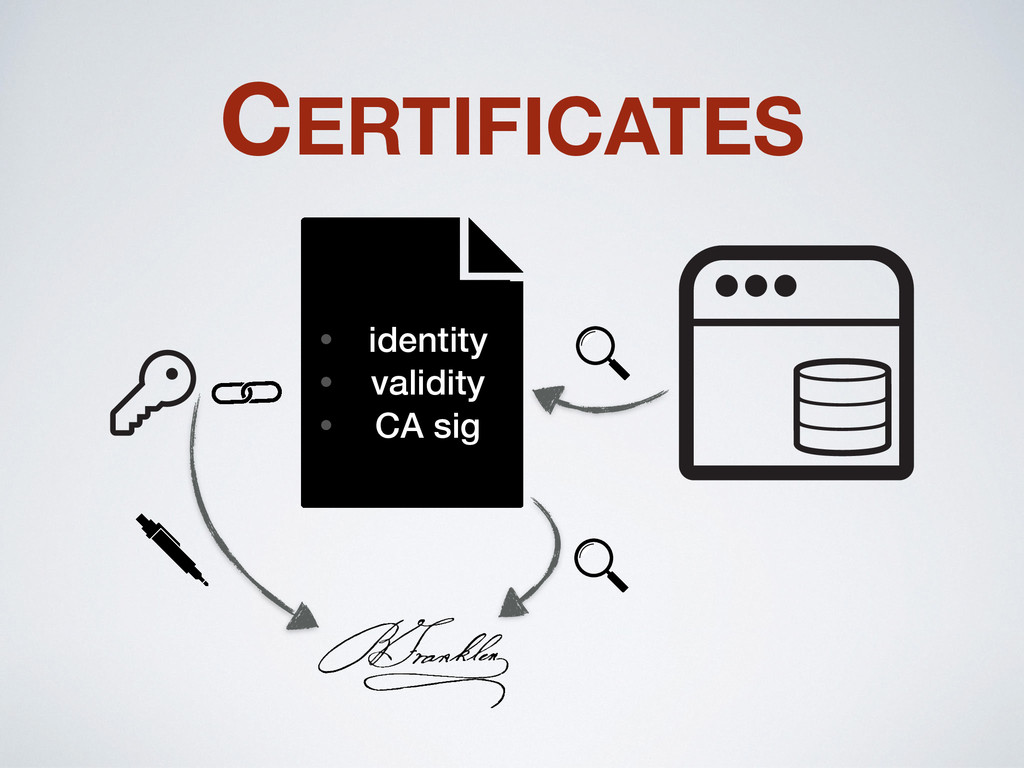
CERTIFICATES • identity • validity • CA sig
CERTIFICATES • identity • validity • CA sig
EXTENDED VALIDATION CERTIFICATES
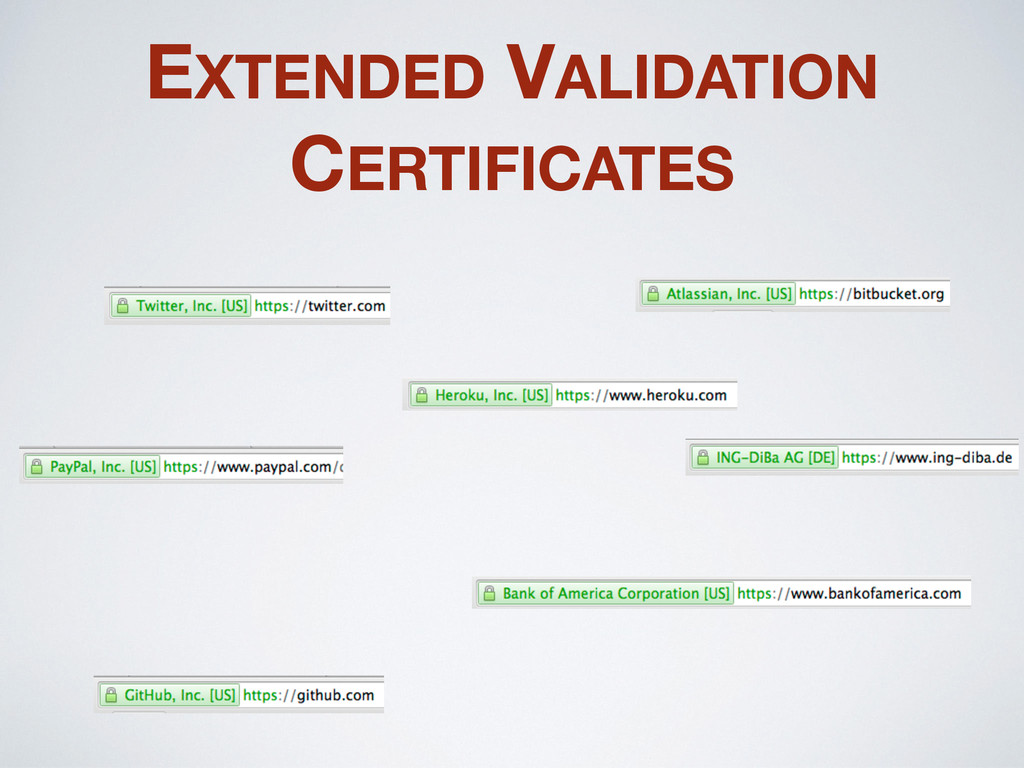
EXTENDED VALIDATION CERTIFICATES
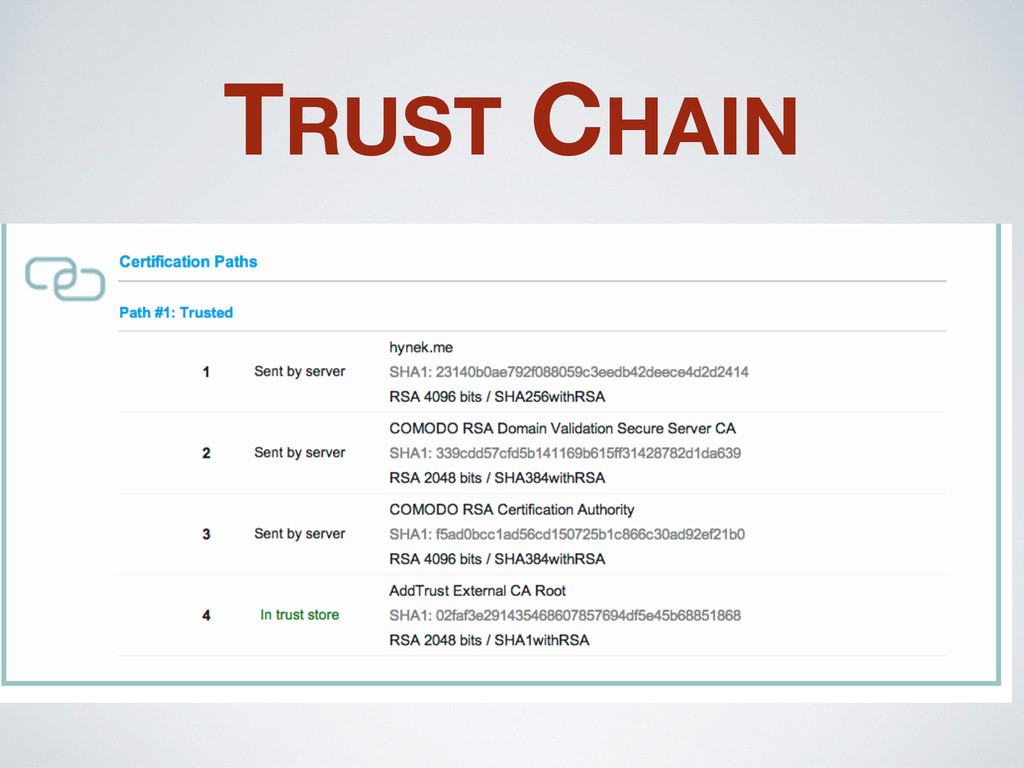
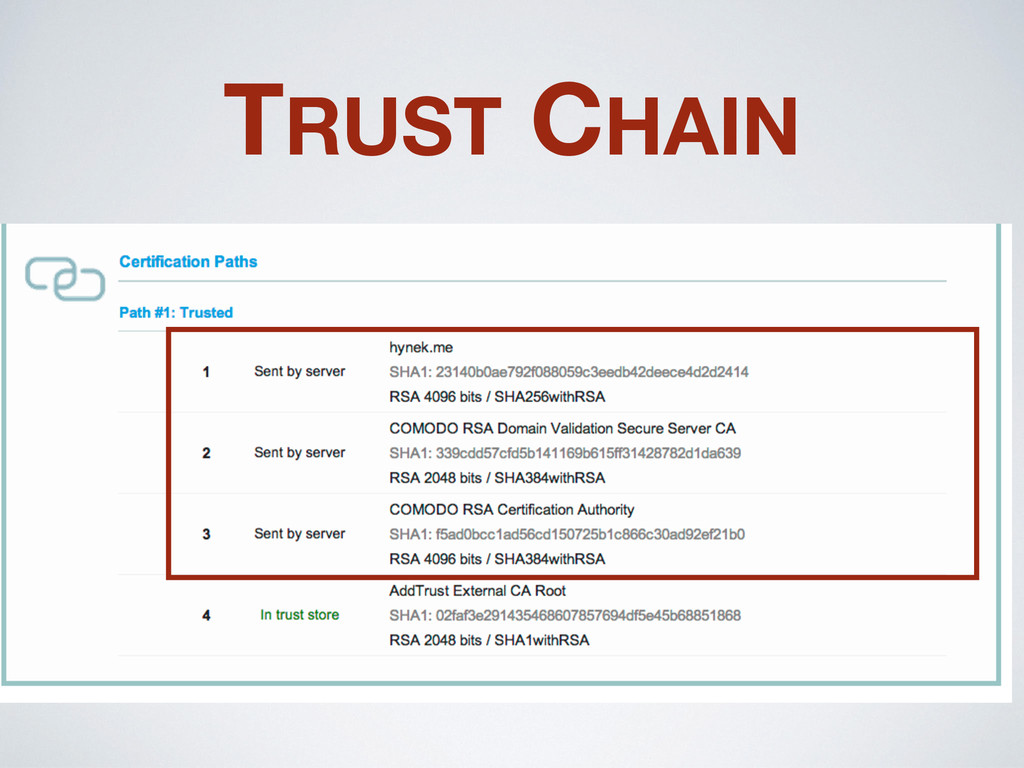
TRUST CHAIN
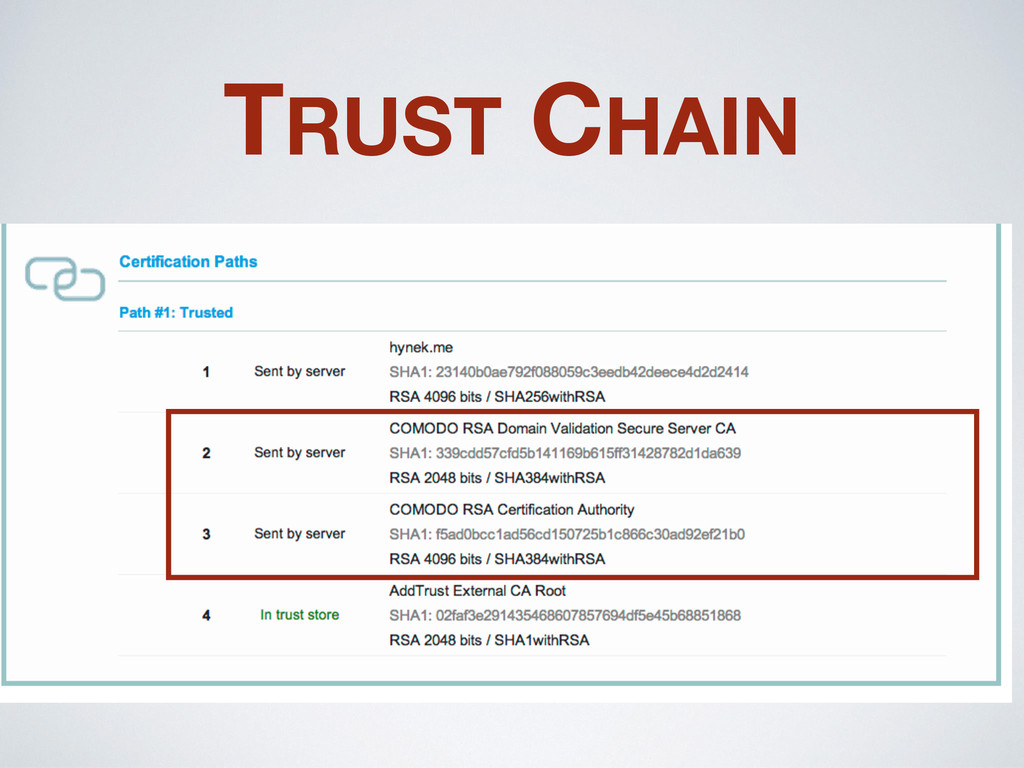
TRUST CHAIN
TRUST CHAIN
CERTIFICATES • trust chain
CERTIFICATES • trust chain • host name/service
CERTIFICATES • trust chain • host name/service • already/still valid?
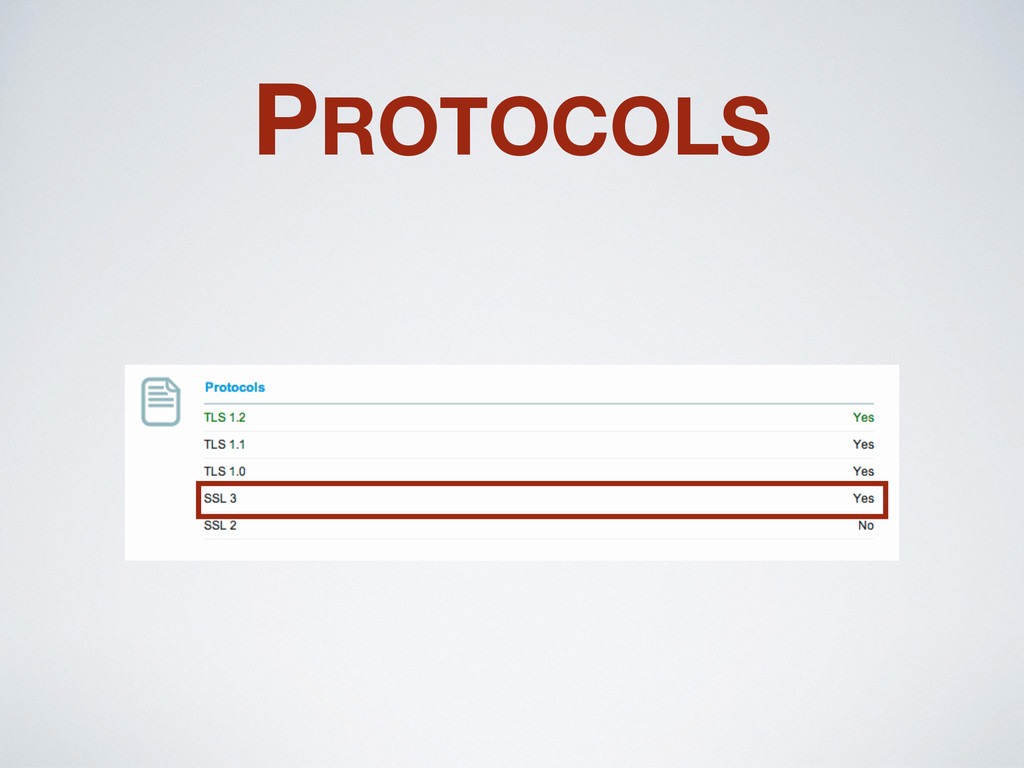
DISABLE • SSL 2.0
DISABLE • SSL 2.0 • SSL 3.0 (if you can)
DISABLE • SSL 2.0 • SSL 3.0 (if you can)
• TLS compression
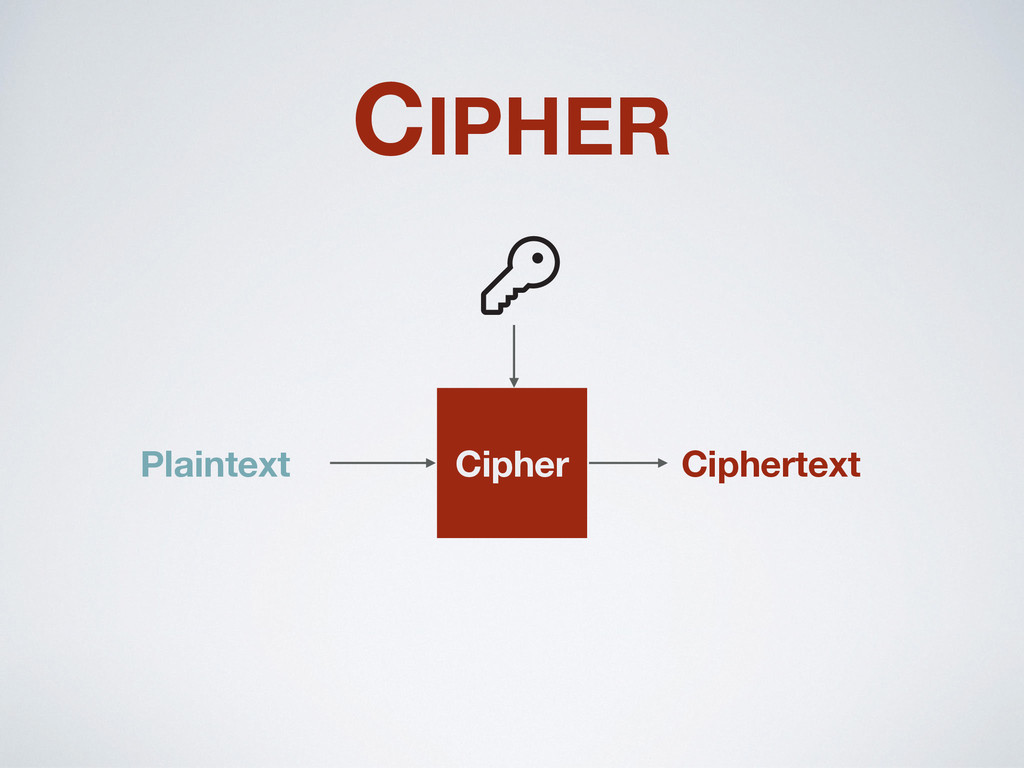
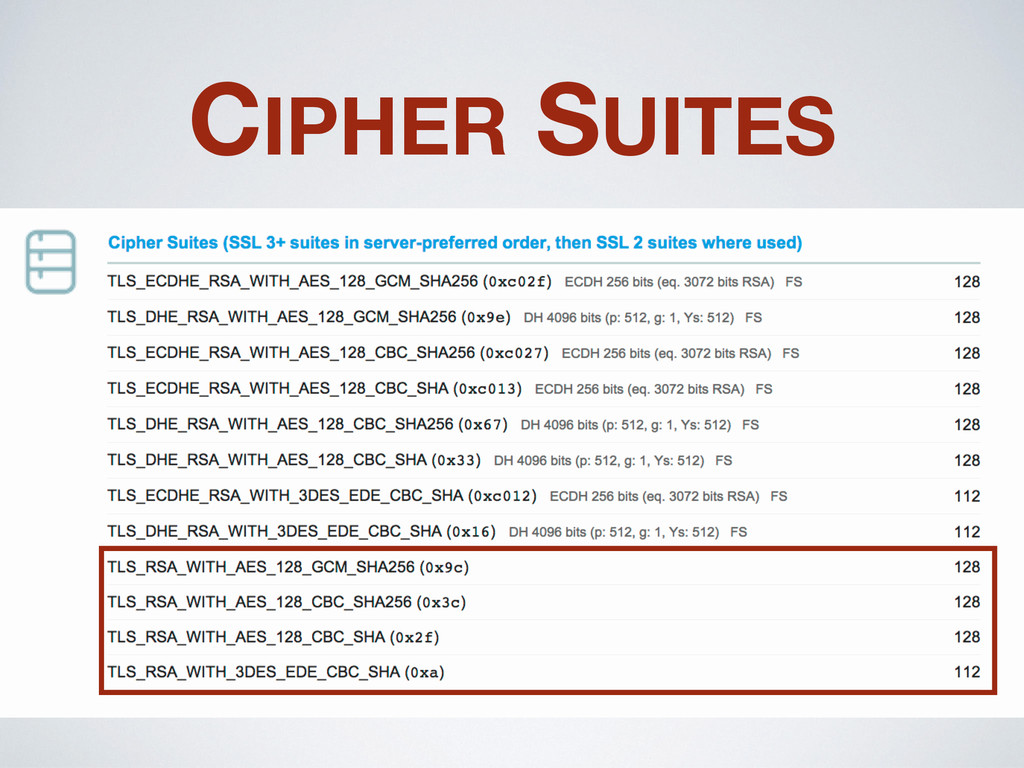
CIPHER SUITES
CIPHER
CIPHER Cipher
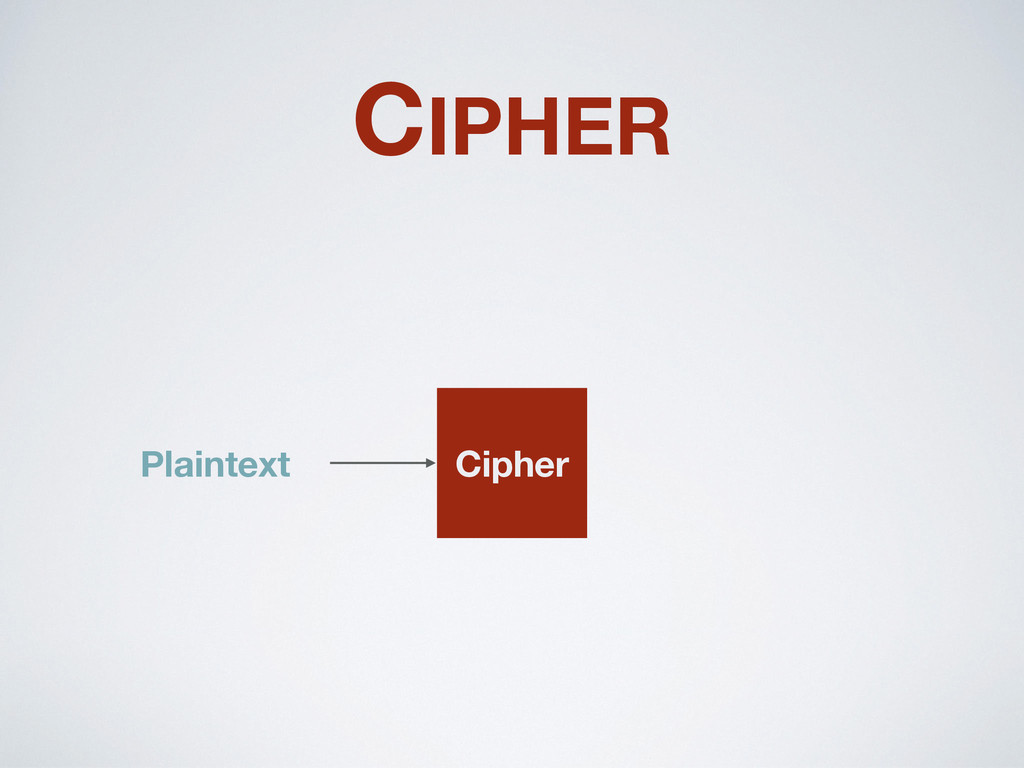
CIPHER Cipher Plaintext
CIPHER Cipher Plaintext
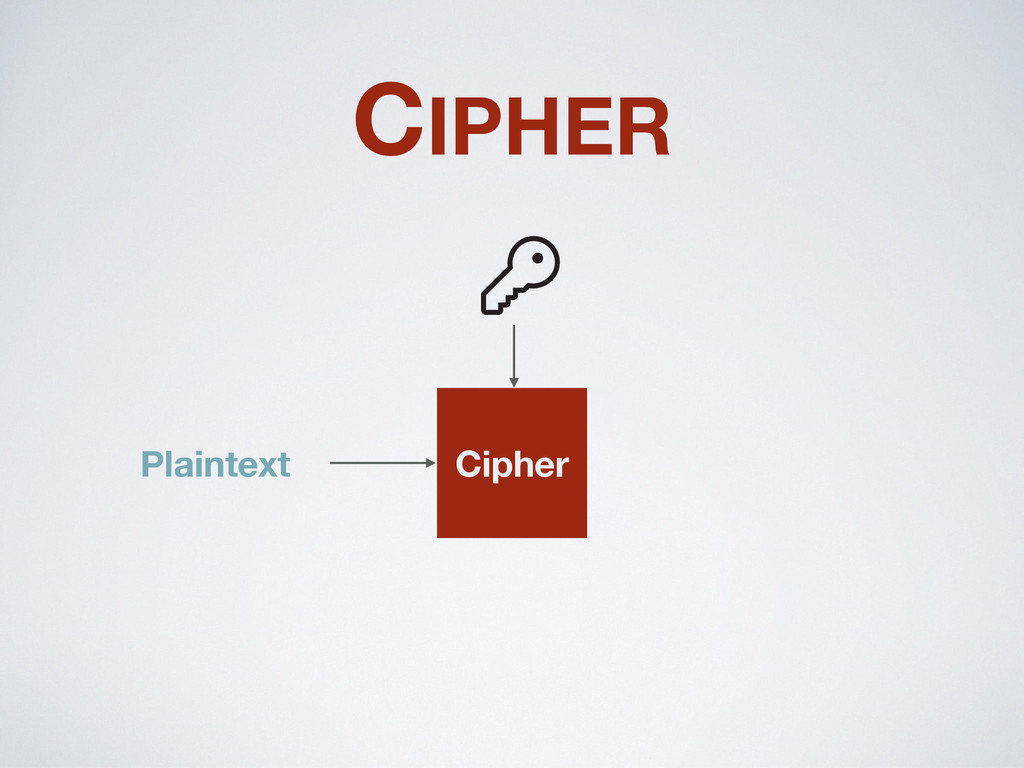
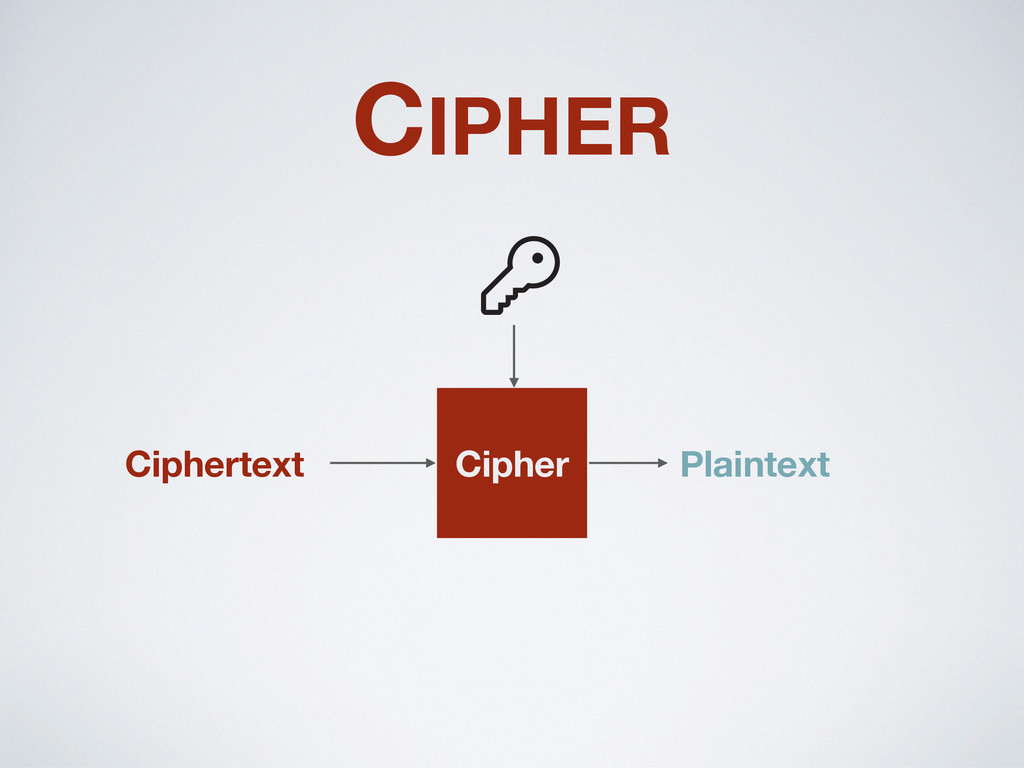
CIPHER Cipher Ciphertext Plaintext
Ciphertext CIPHER Cipher Plaintext
CIPHER: MODE
CIPHER: MODE • CBC
CIPHER: MODE • CBC • stream ciphers
CIPHER: MODE • CBC • stream ciphers • GCM
ENCRYPTION: PREFER THIS
ENCRYPTION: PREFER THIS AES128-GCM &
ENCRYPTION: PREFER THIS AES128-GCM & ChaCha20
ENCRYPTION: FALL BACK TO AES128-CBC
ENCRYPTION: IF LIFE IS CRUEL TO YOU 3DES-CBC
ENCRYPTION: EOL
ENCRYPTION: DANGEROUS • EXP-*
ENCRYPTION: DANGEROUS • EXP-* • DES
ENCRYPTION: DANGEROUS • EXP-* • DES • RC4
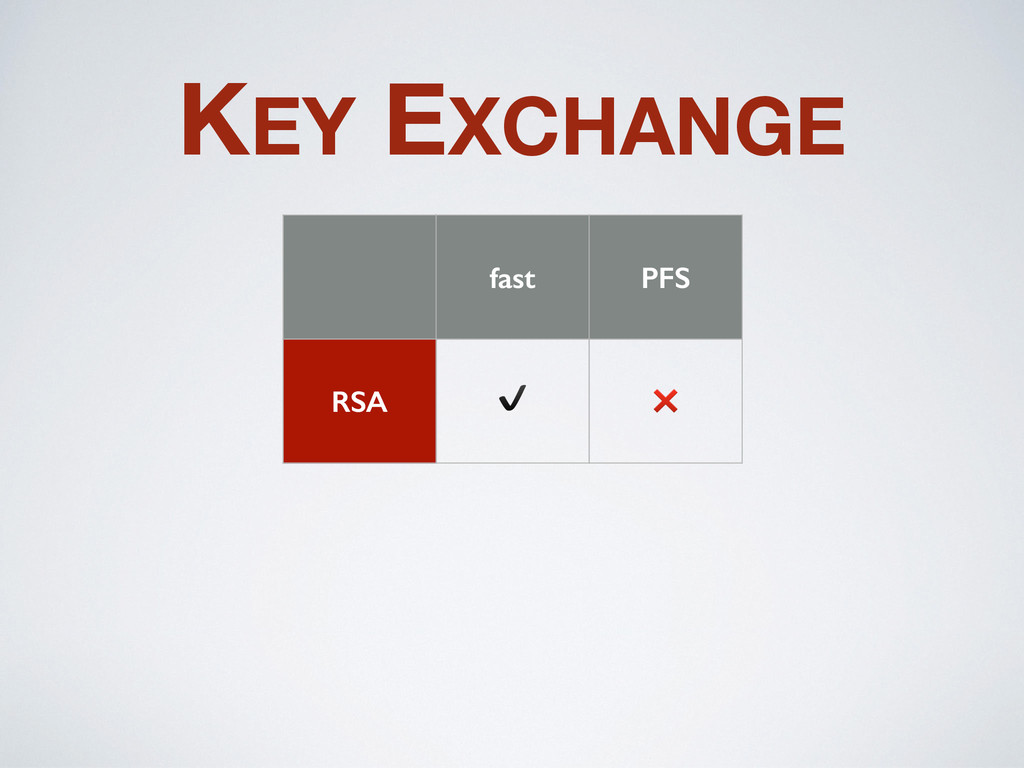
KEY EXCHANGE
KEY EXCHANGE fast PFS RSA ✔️ ❌
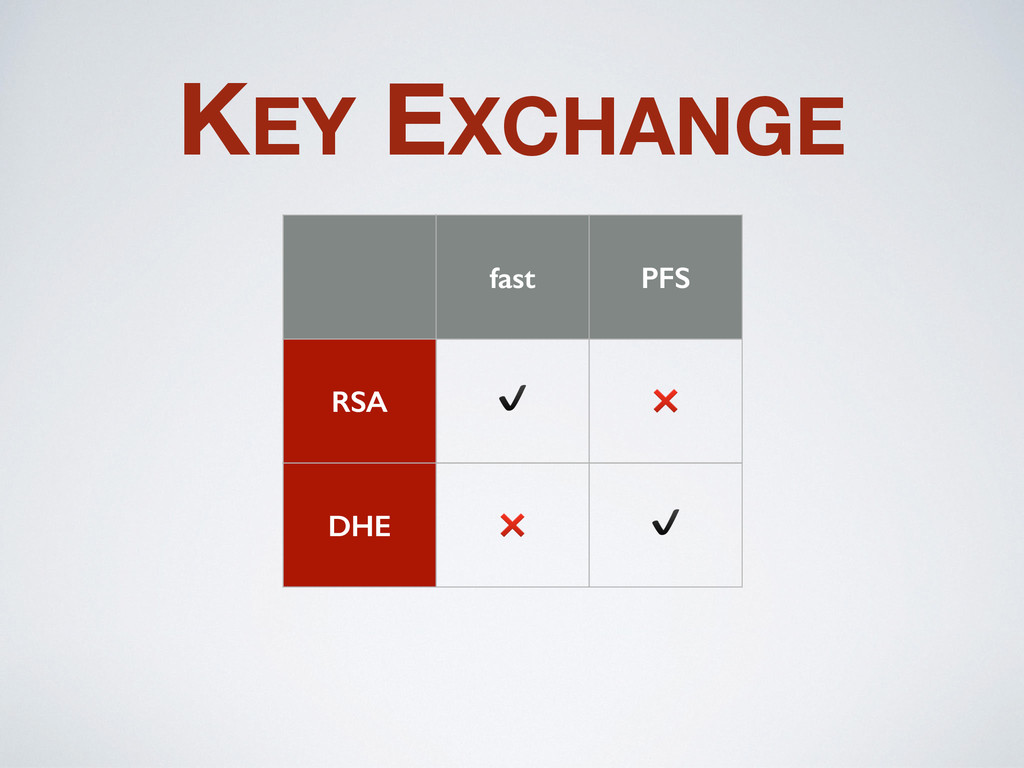
KEY EXCHANGE fast PFS RSA ✔️ ❌ DHE ❌ ✔️
KEY EXCHANGE fast PFS RSA ✔️ ❌ DHE ❌ ✔️
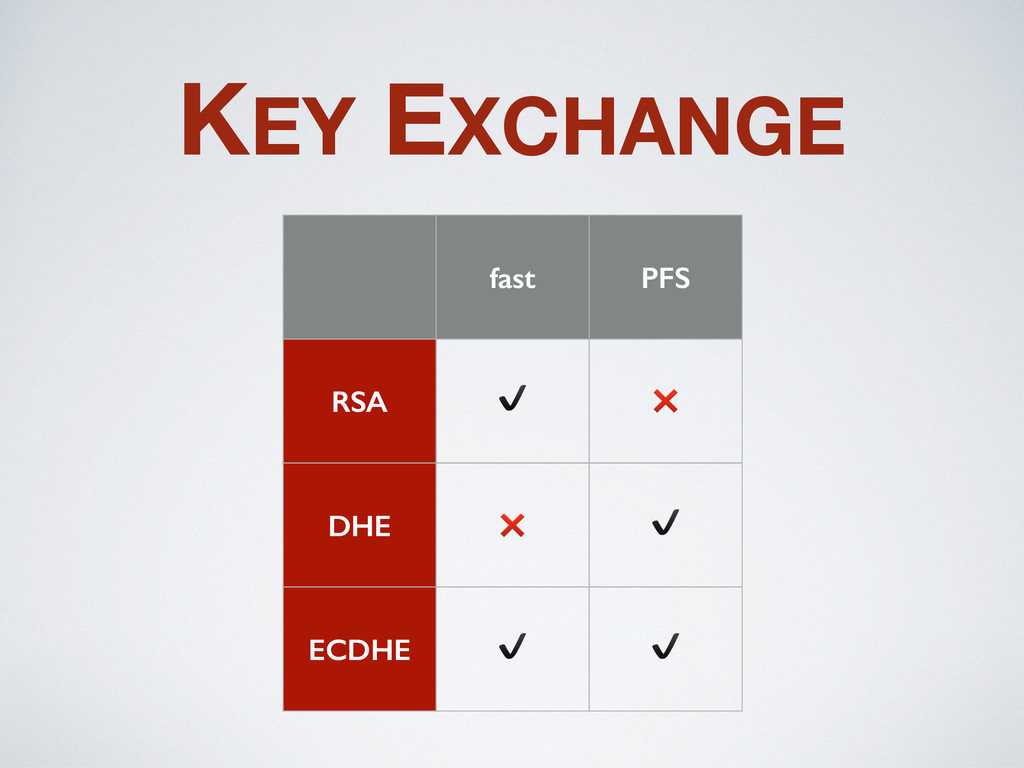
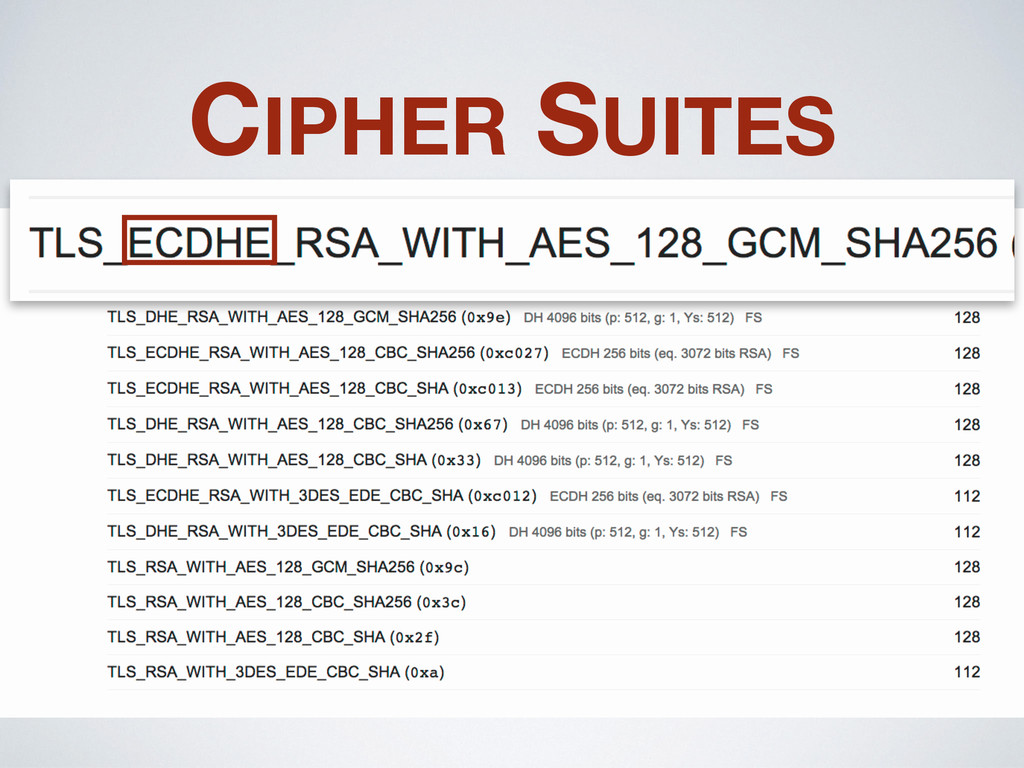
ECDHE ✔️ ✔️
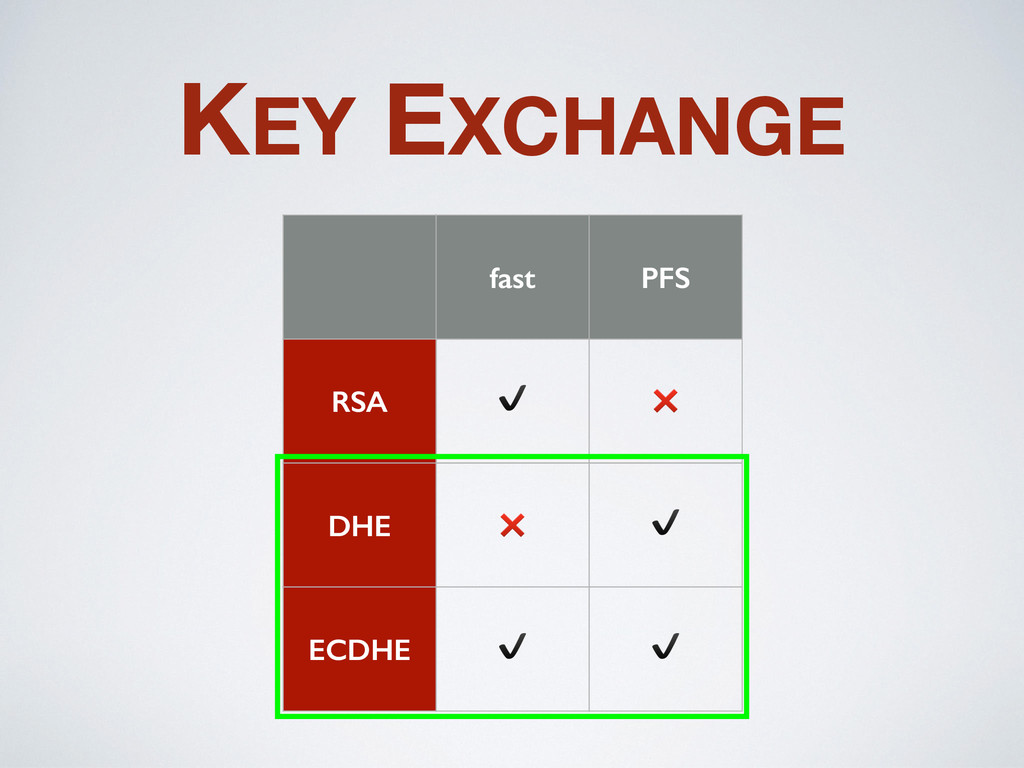
KEY EXCHANGE fast PFS RSA ✔️ ❌ DHE ❌ ✔️
ECDHE ✔️ ✔️
INTEGRITY: MACS • Message Authentication Code
INTEGRITY: MACS • Message Authentication Code • HMAC
INTEGRITY: MACS • Message Authentication Code • HMAC • GCM
HAVE THE LAST WORD
YOU’RE DONE!
YOU’RE DONE! (but test your results!)
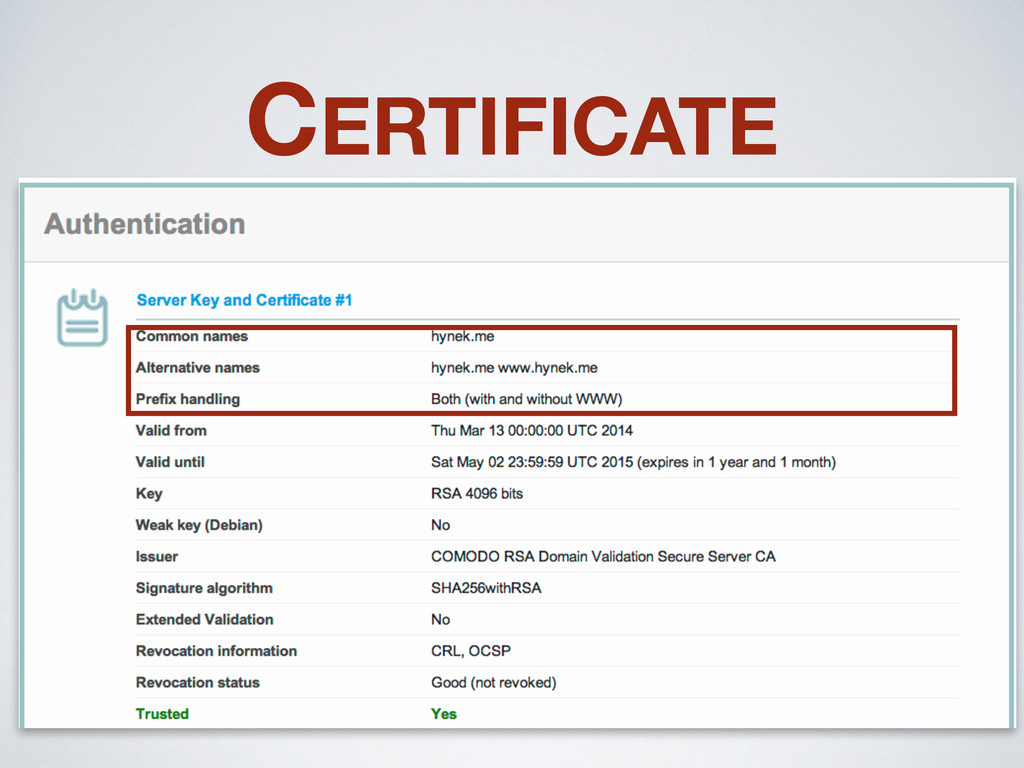
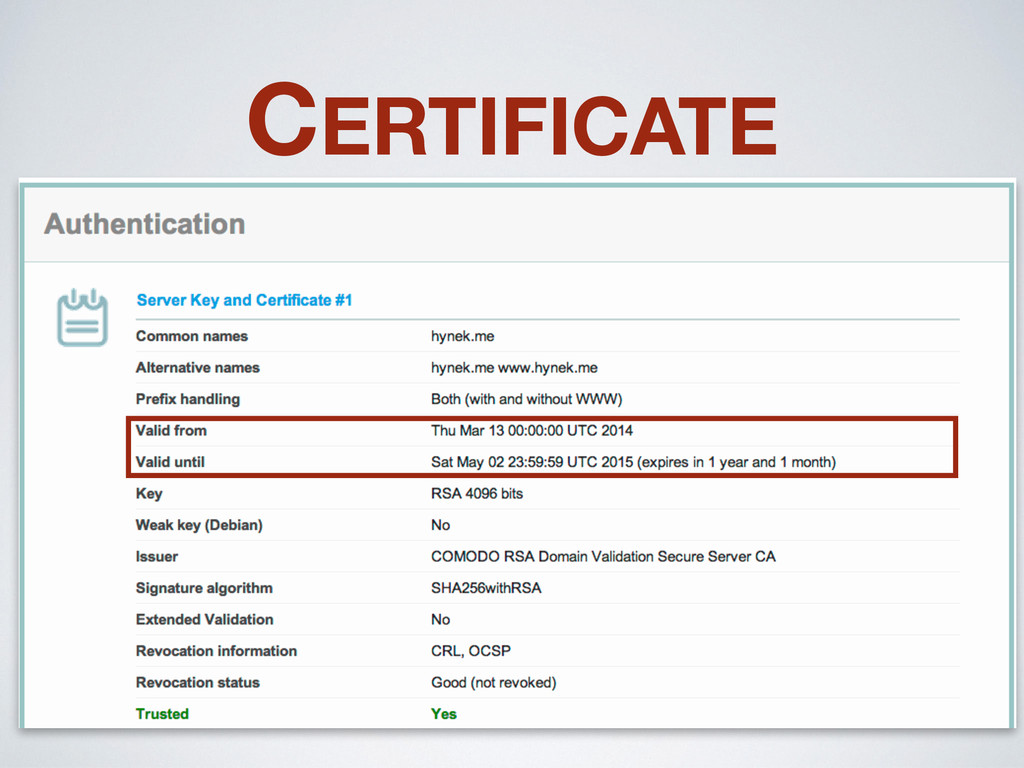
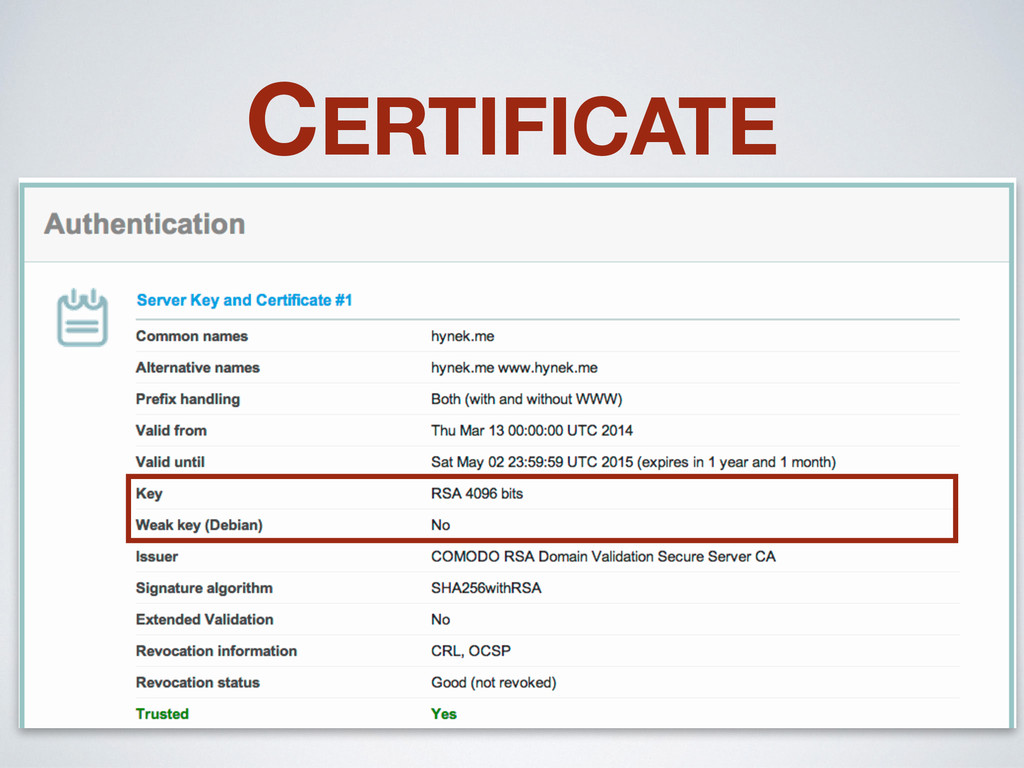
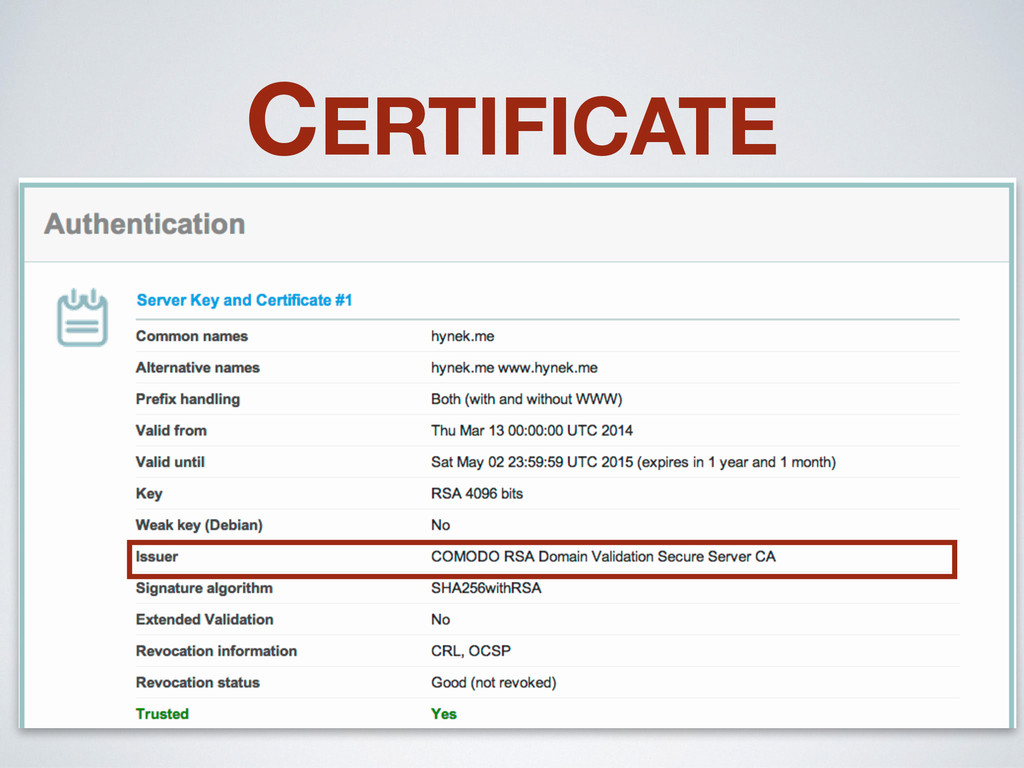
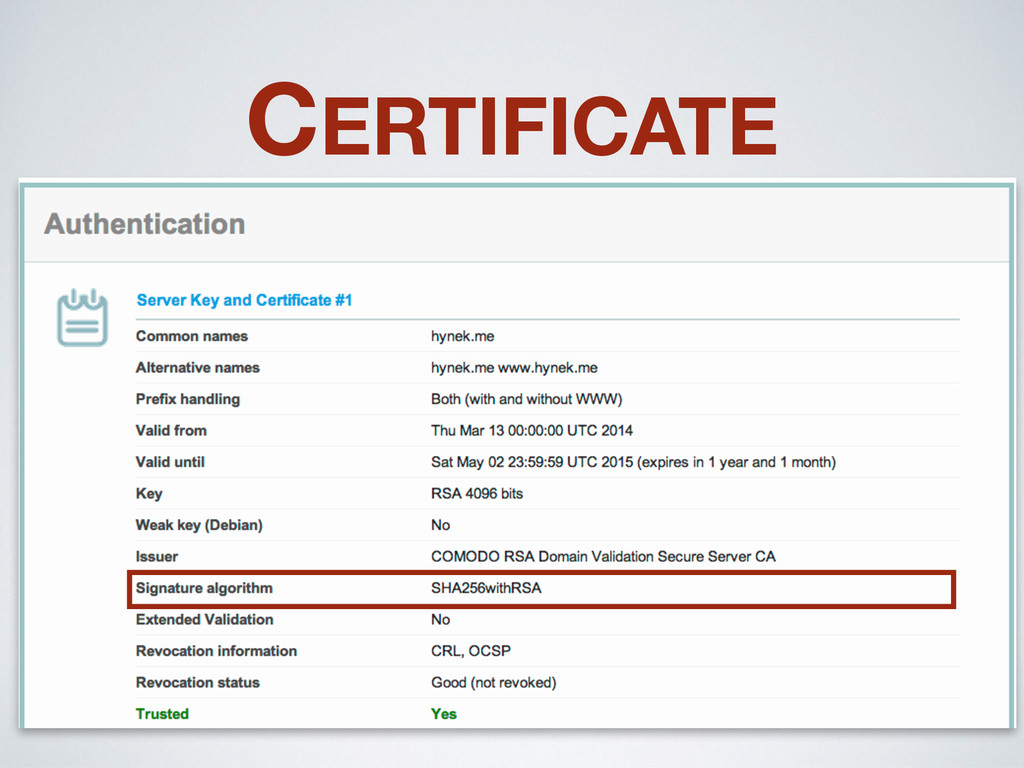
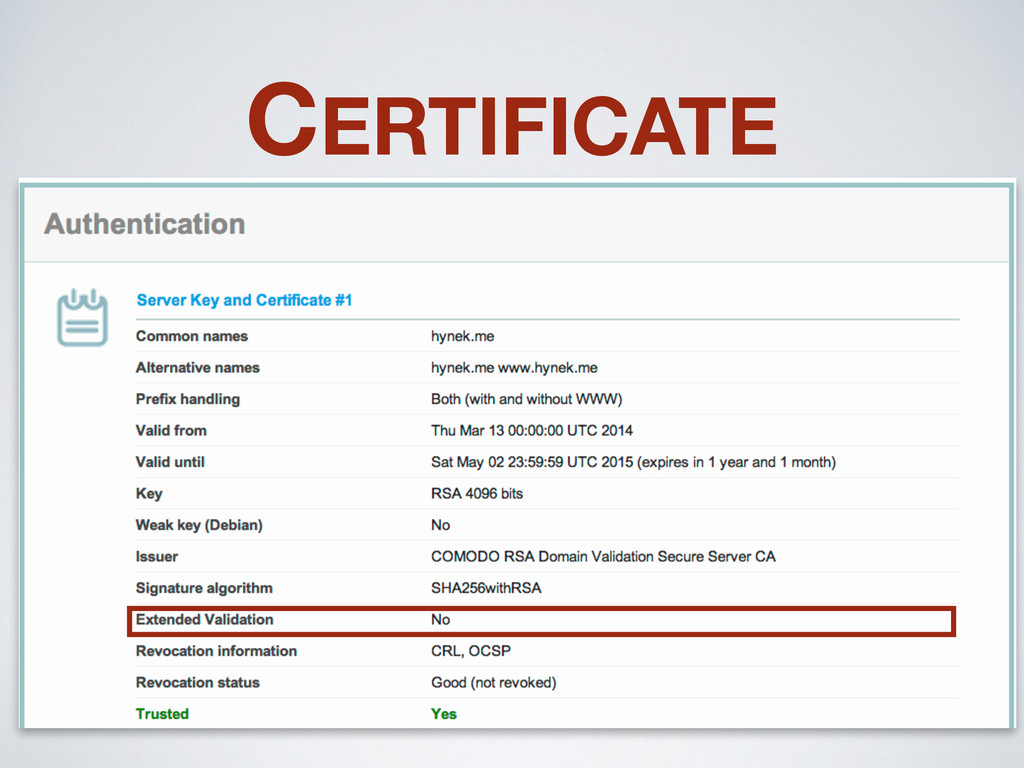
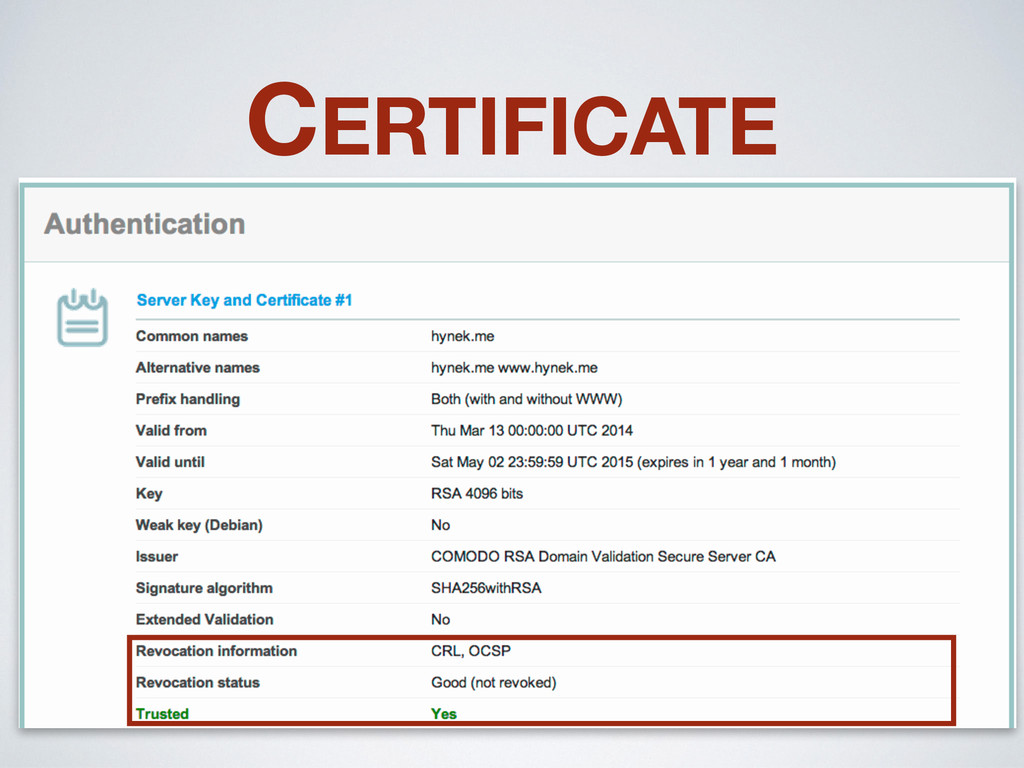
CERTIFICATE
CERTIFICATE
CERTIFICATE
CERTIFICATE
CERTIFICATE
CERTIFICATE
CERTIFICATE
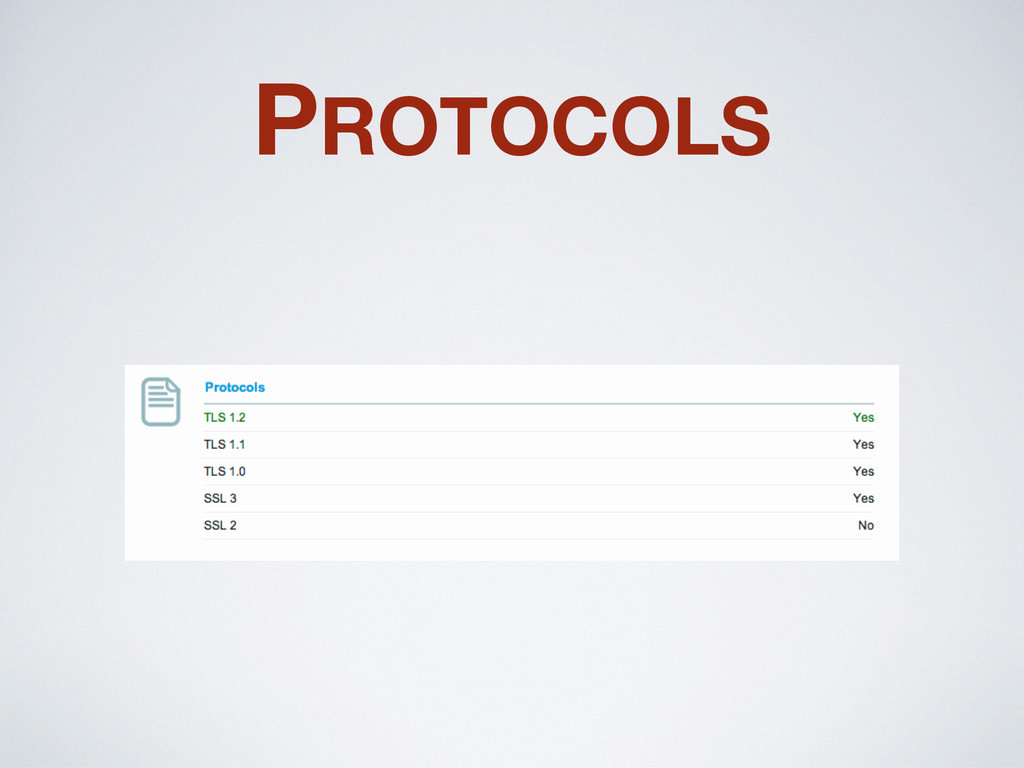
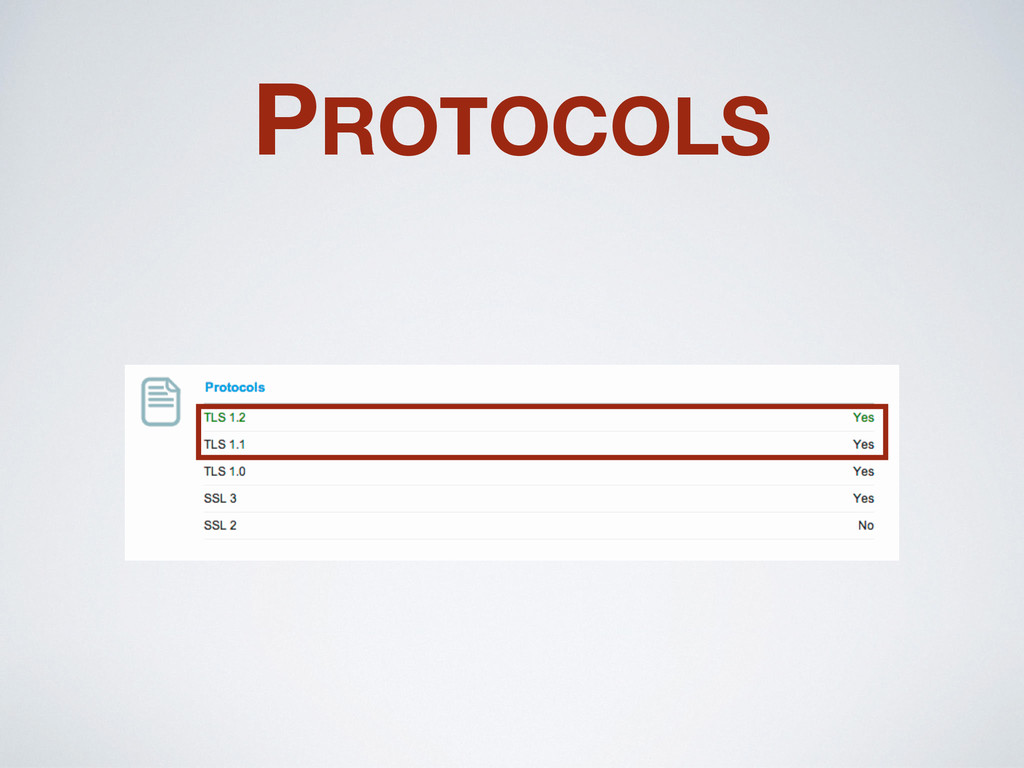
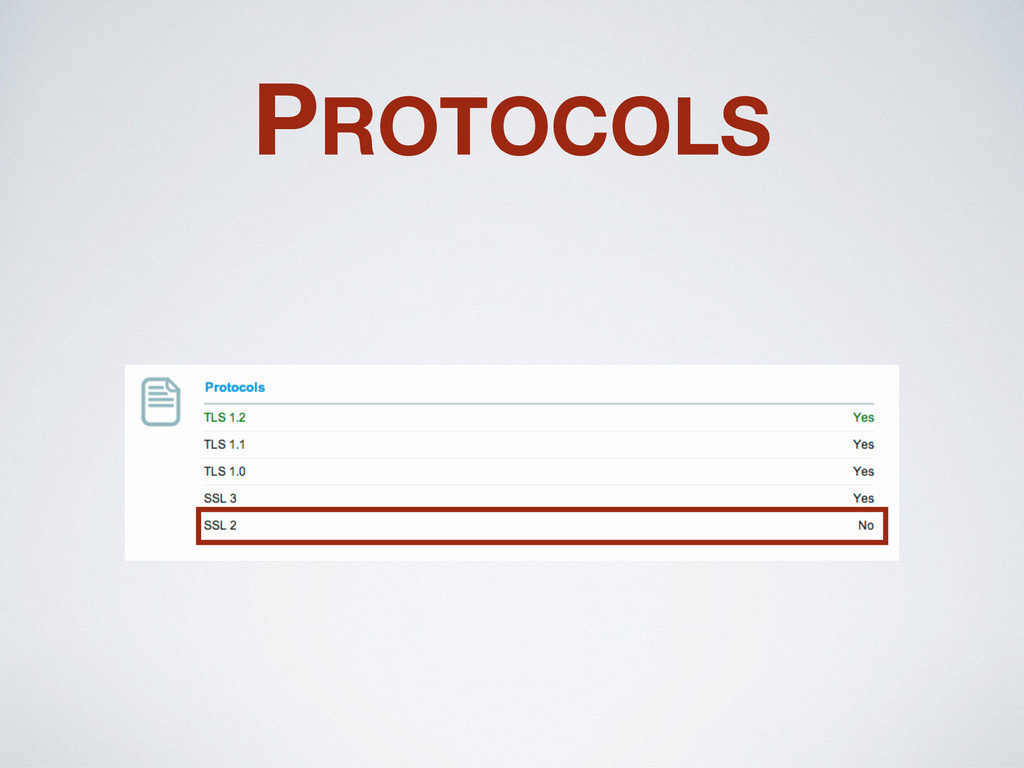
PROTOCOLS
PROTOCOLS
PROTOCOLS
PROTOCOLS
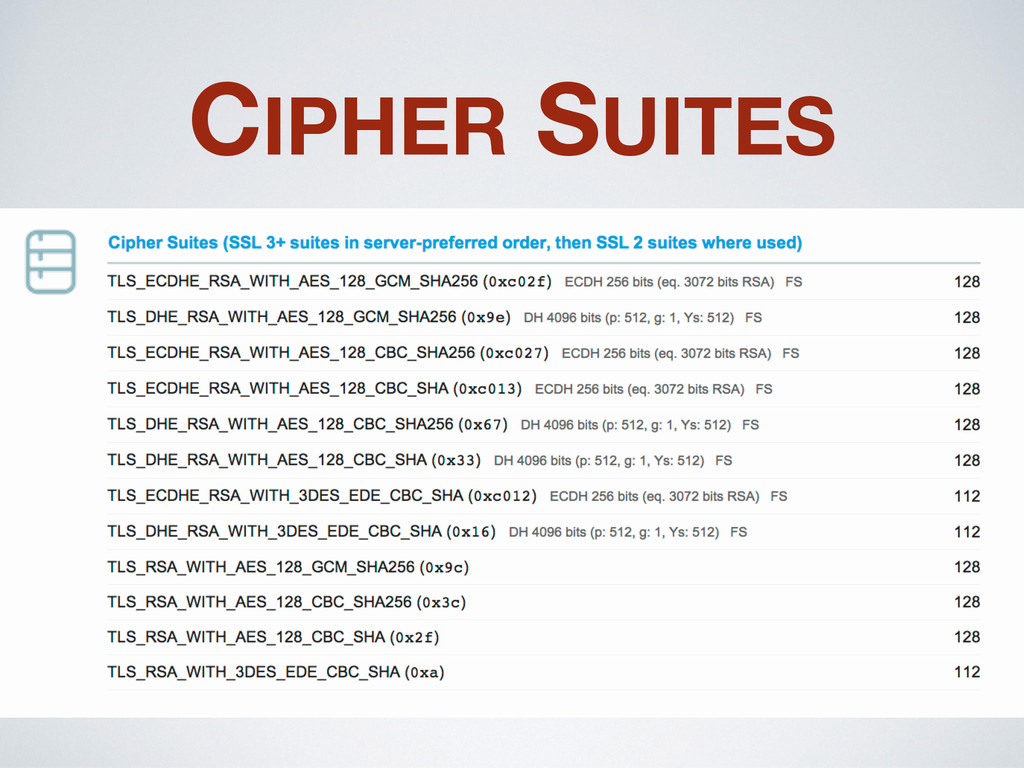
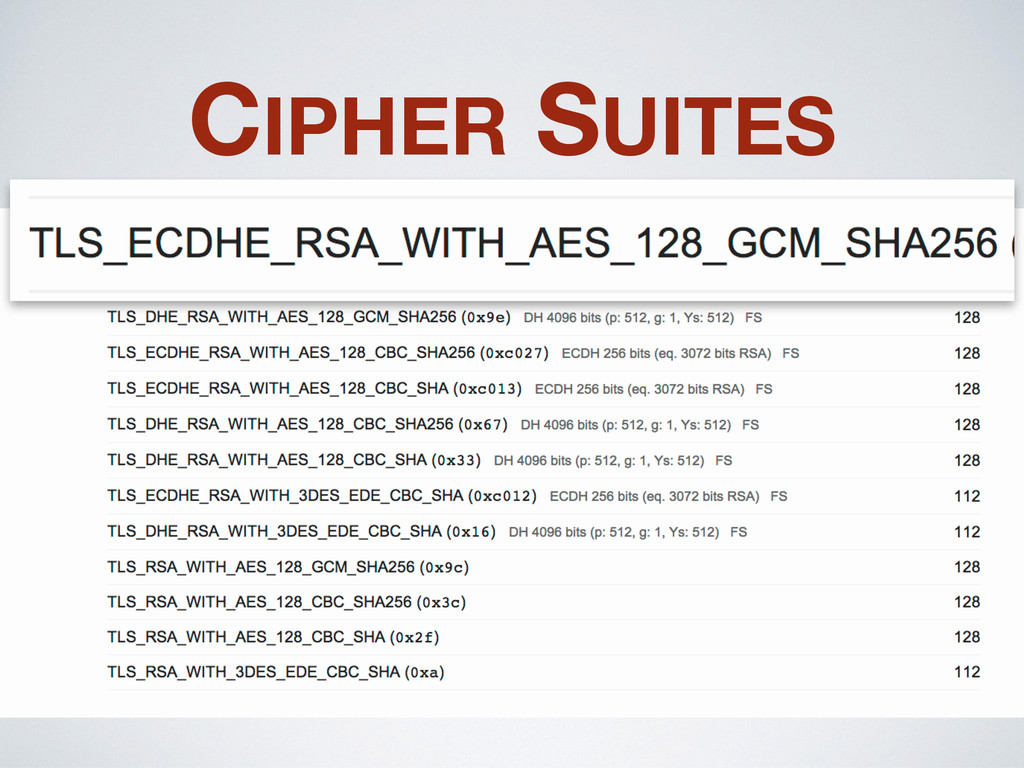
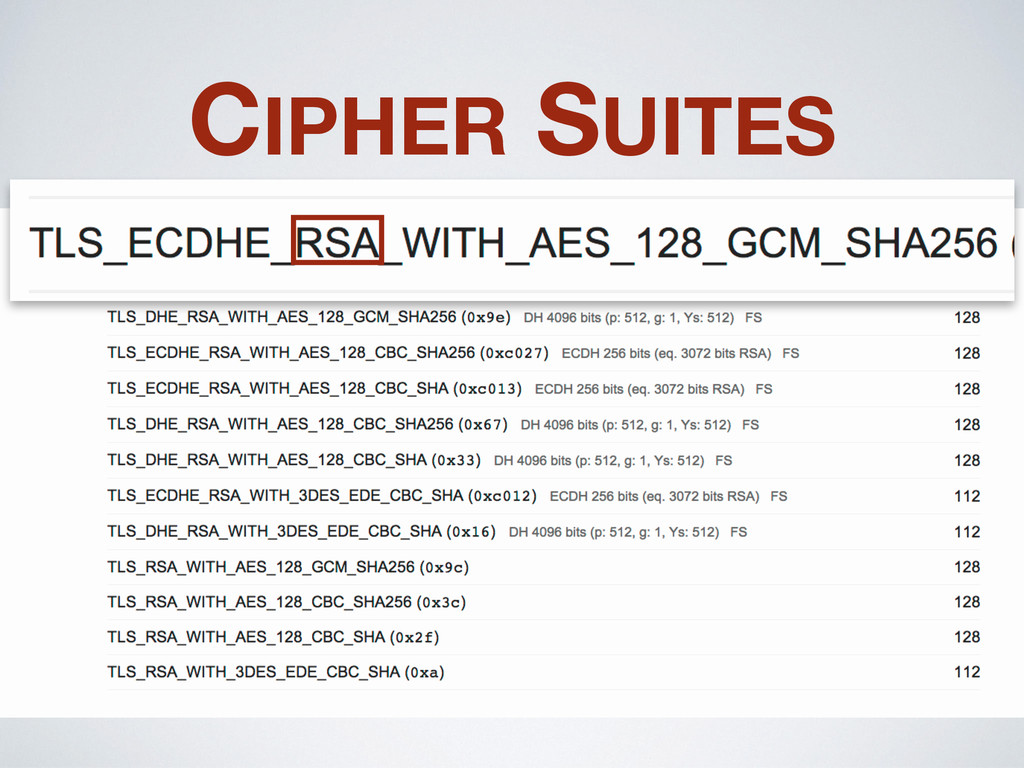
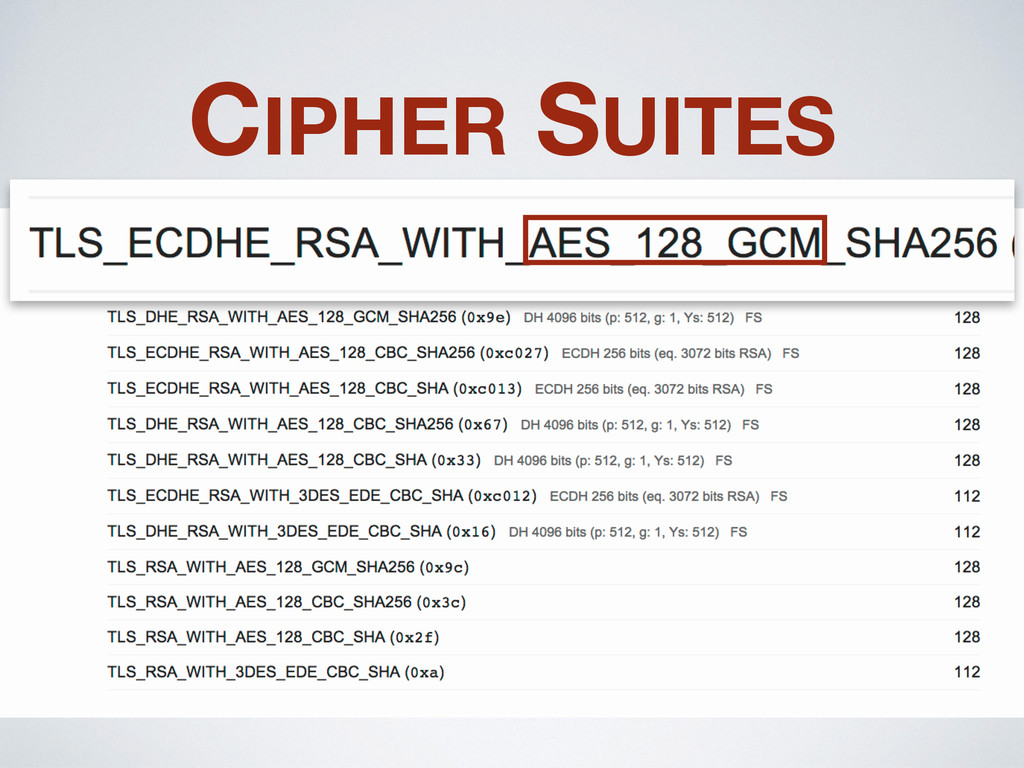
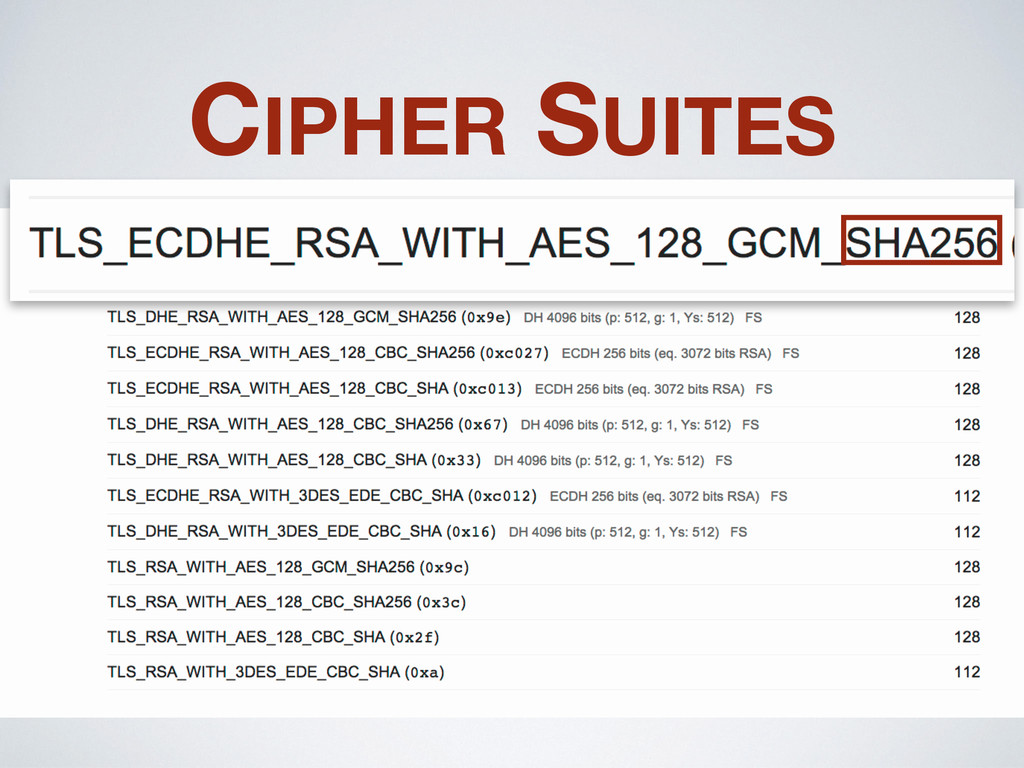
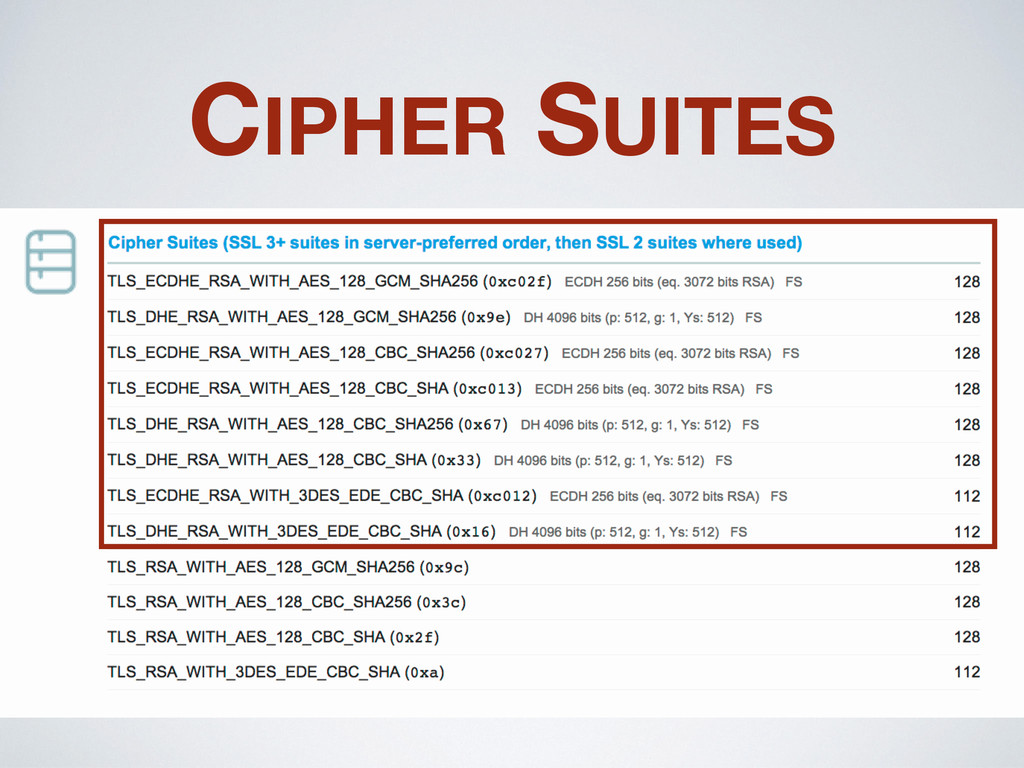
CIPHER SUITES
CIPHER SUITES
CIPHER SUITES
CIPHER SUITES
CIPHER SUITES
CIPHER SUITES
CIPHER SUITES
CIPHER SUITES
CLIENTS
YOU HAD ONE JOB!
YOU HAD ONE JOB! VERIFY!
VERIFY THE CERTIFICATE! • valid?
VERIFY THE CERTIFICATE! • valid? • trustworthy chain?
VERIFY THE CERTIFICATE! • valid? • trustworthy chain? • correct
hostname/service?
TRUST CHAIN
TRUST CHAIN • VERIFY_PEER
TRUST CHAIN • VERIFY_PEER • trust stores OS dependent
TRUST CHAIN • VERIFY_PEER • trust stores OS dependent •
SSL_CTX_set_default_ verify_paths
SYSTEM CA • FreeBSD: ca_root_nss
SYSTEM CA • FreeBSD: ca_root_nss • debian/Red Hat: ca-certificates
SYSTEM CA • FreeBSD: ca_root_nss • debian/Red Hat: ca-certificates •
OS X: TEA or homebrew
SYSTEM CA • FreeBSD: ca_root_nss • debian/Red Hat: ca-certificates •
OS X: TEA or homebrew • Windows: wincertstore
SYSTEM CA • FreeBSD: ca_root_nss • debian/Red Hat: ca-certificates •
OS X: TEA or homebrew • Windows: wincertstore • or: Mozilla/certifi
HOSTNAME VERIFICATION OpenSSL to developers:
HOSTNAME VERIFICATION OpenSSL to developers: LOL
DON’T VERIFY TRUST CHAIN I can pretend to be Google
with any self-signed certificate.
DON’T VERIFY HOSTNAME I can pretend to be Google with
any valid certificate.
None
SET SOME OPTIONS • acceptable ciphers • disable SSL 2.0
THAT’S ALL!
USERS
FUNDAMENTAL MISCONCEPTIONS
FUNDAMENTAL MISCONCEPTIONS • no end-to-end security
FUNDAMENTAL MISCONCEPTIONS • no end-to-end security • metadata
VPN?
VPN? • sees all your traffic
VPN? • sees all your traffic • same for CDN
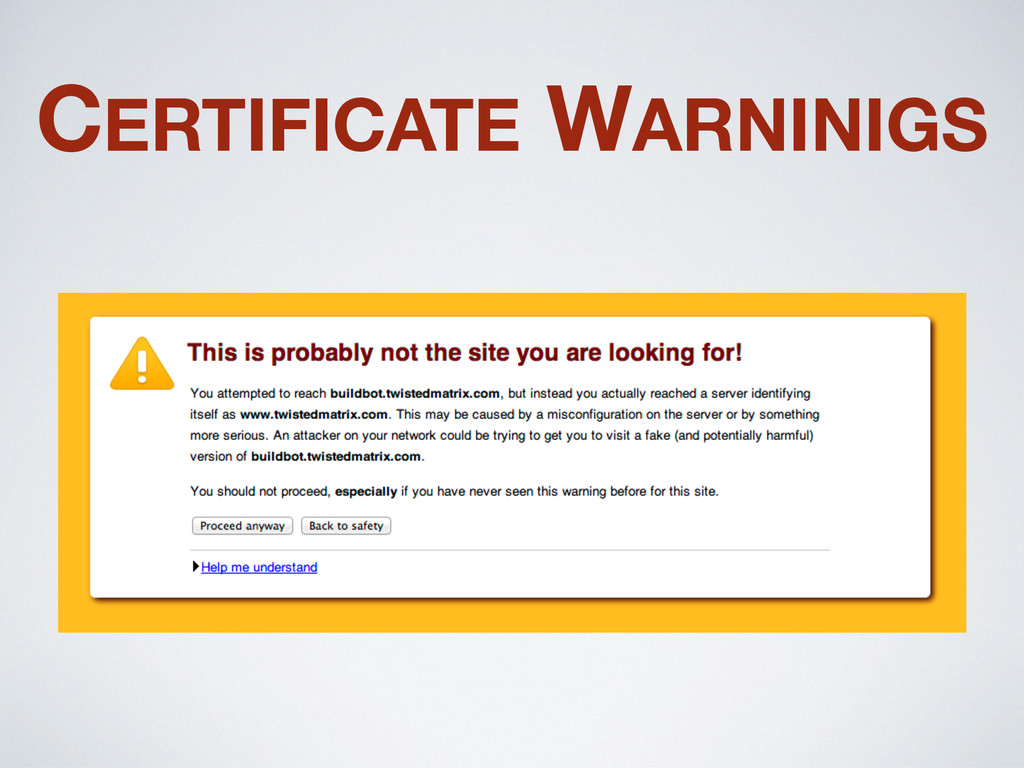
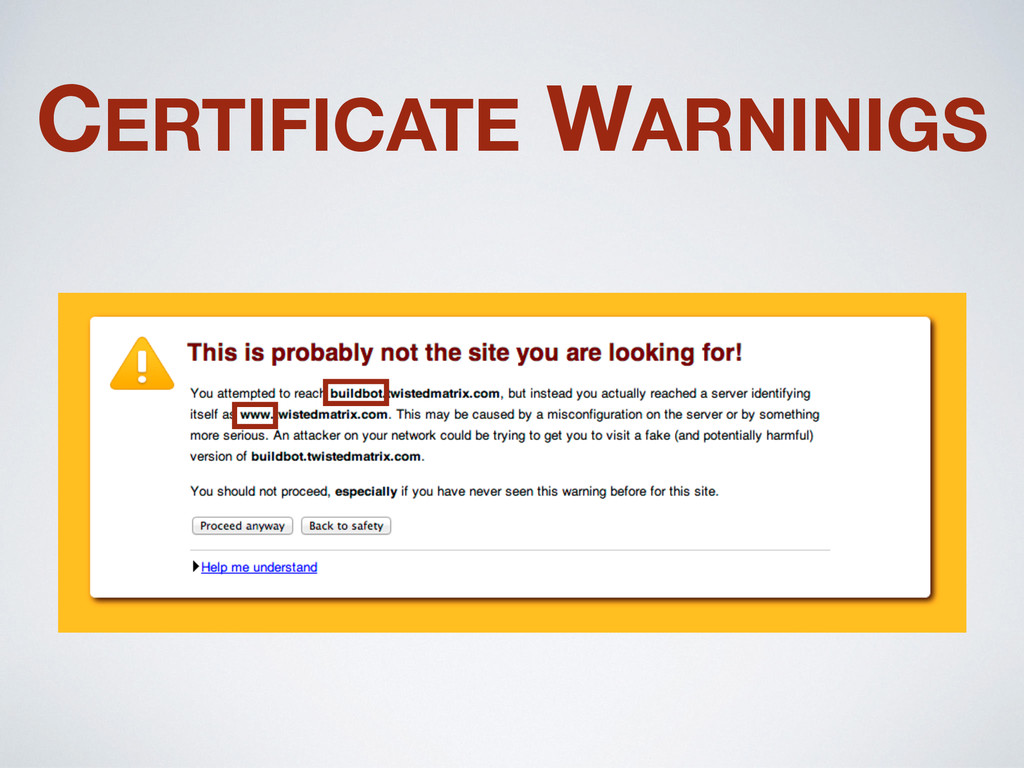
CERTIFICATE WARNINIGS
CERTIFICATE WARNINIGS
ROOT CERTIFICATE POISONING
TRUST ISSUES
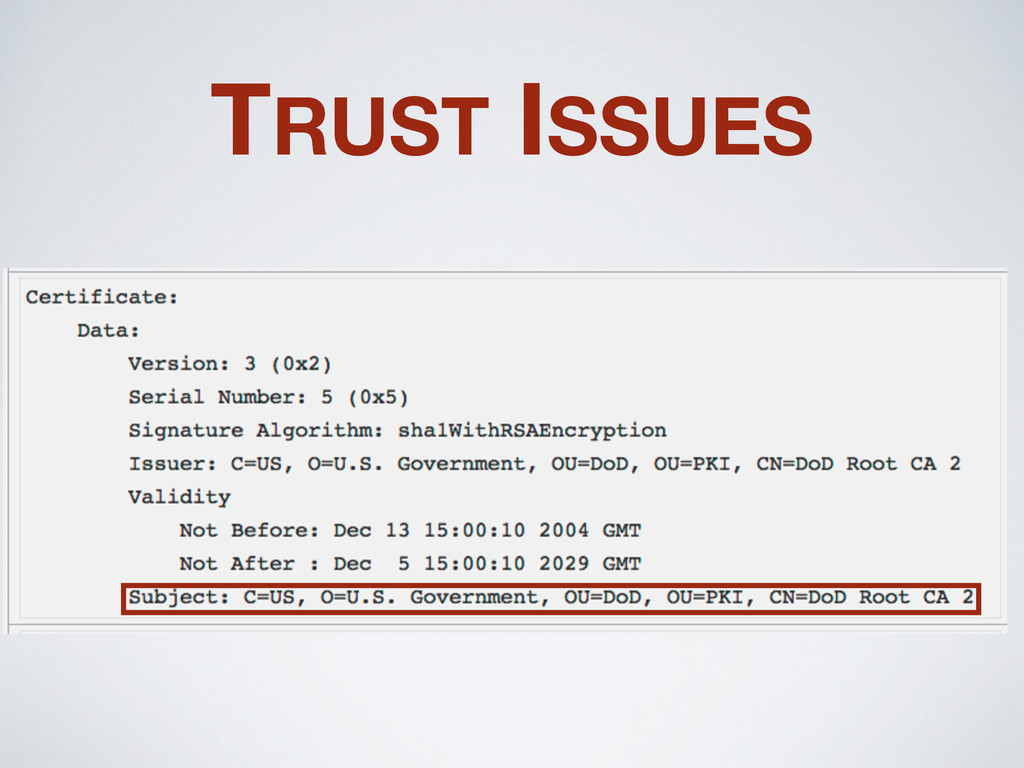
TRUST ISSUES
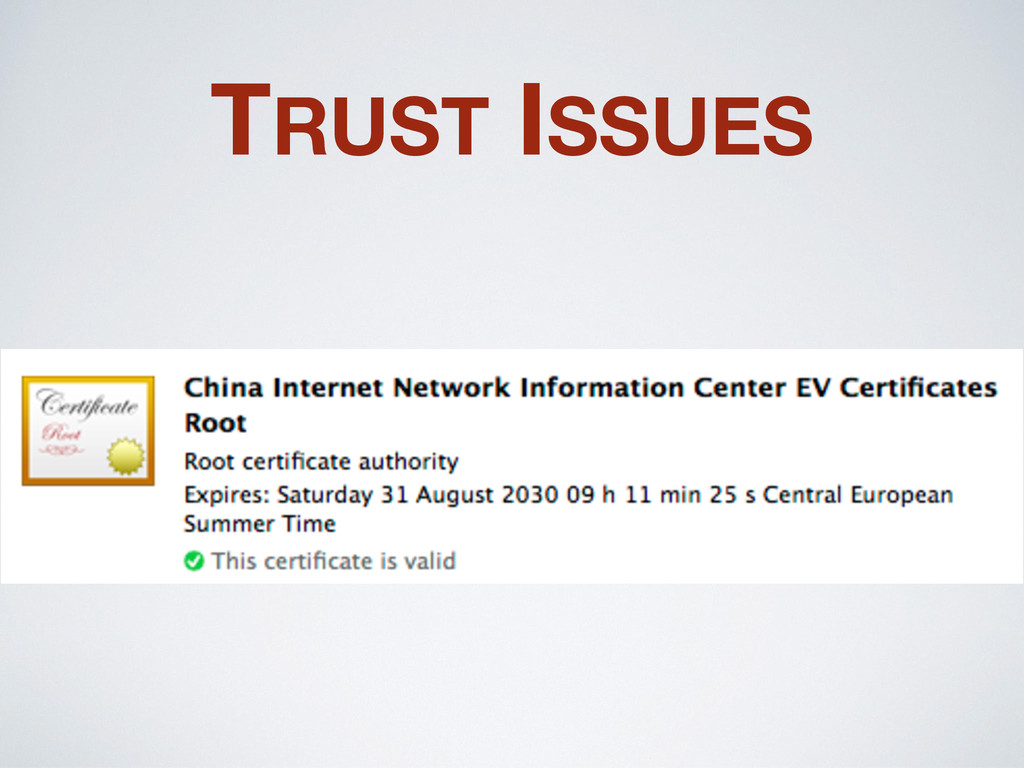
TRUST ISSUES
TRUST ISSUES
TRUST ISSUES • hacked
TRUST ISSUES • hacked • screw up
TRUST ISSUES • hacked • screw up • court orders
TRUST ISSUES • hacked • screw up • court orders
• big corp
None
DON’T DO IT YOURSELF IF YOU CAN HELP IT. Rule
of Thumb
STANDARD LIBRARY VS. PYOPENSSL
STANDARD LIBRARY
STANDARD LIBRARY • terrible pre-3.3
STANDARD LIBRARY • terrible pre-3.3 • very incomplete in 2.7
STANDARD LIBRARY • terrible pre-3.3 • very incomplete in 2.7
• PFS impossible
STANDARD LIBRARY • terrible pre-3.3 • very incomplete in 2.7
• PFS impossible • missing options
STANDARD LIBRARY • terrible pre-3.3 • very incomplete in 2.7
• PFS impossible • missing options • bound to Python’s OpenSSL
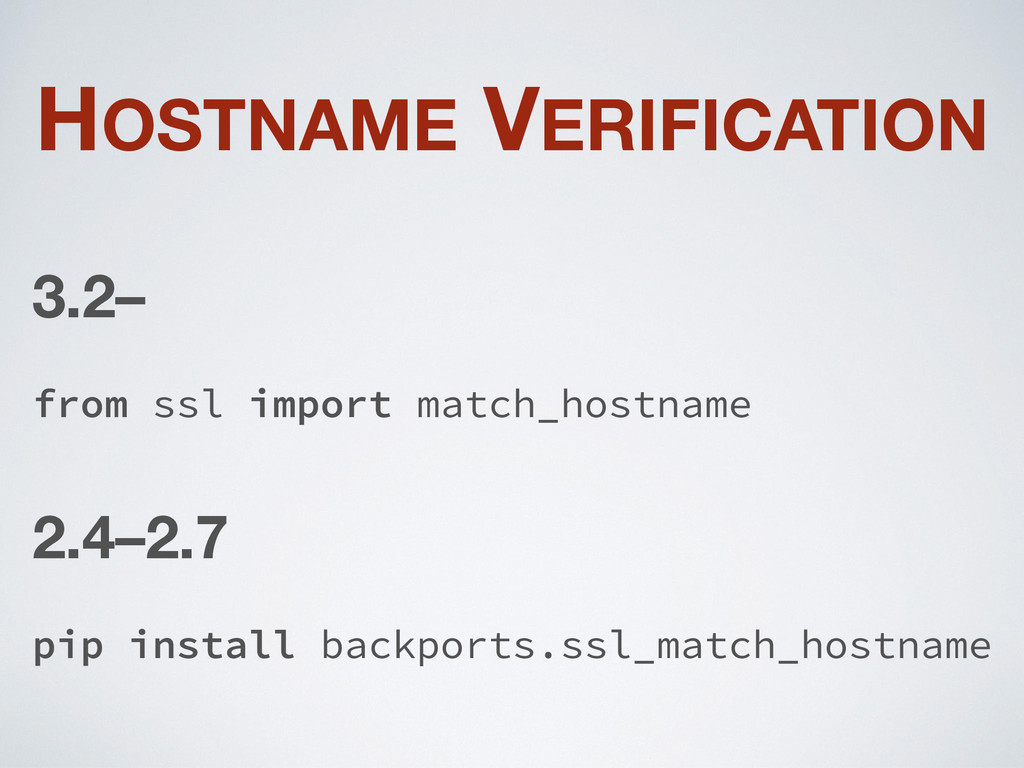
HOSTNAME VERIFICATION 3.2– from ssl import match_hostname 2.4–2.7 pip install
backports.ssl_match_hostname
PYOPENSSL
PYOPENSSL • Python 2.6+, 3.2+, and PyPy
PYOPENSSL • Python 2.6+, 3.2+, and PyPy • more complete
API coverage
PYOPENSSL • Python 2.6+, 3.2+, and PyPy • more complete
API coverage • no server ECDHE (yet)
PYOPENSSL • Python 2.6+, 3.2+, and PyPy • more complete
API coverage • no server ECDHE (yet) • cryptography!
CRYPTOGRAPHY.IO
CRYPTOGRAPHY.IO • Python crypto w/o footguns
CRYPTOGRAPHY.IO • Python crypto w/o footguns • PyPy ♥ cffi
CRYPTOGRAPHY.IO • Python crypto w/o footguns • PyPy ♥ cffi
• SecureTransport is coming!
CRYPTOGRAPHY.IO • Python crypto w/o footguns • PyPy ♥ cffi
• SecureTransport is coming! • gives pyOpenSSL momentum
HOSTNAME VERIFICATION service_identity
LIBRARIES & FRAMEWORKS
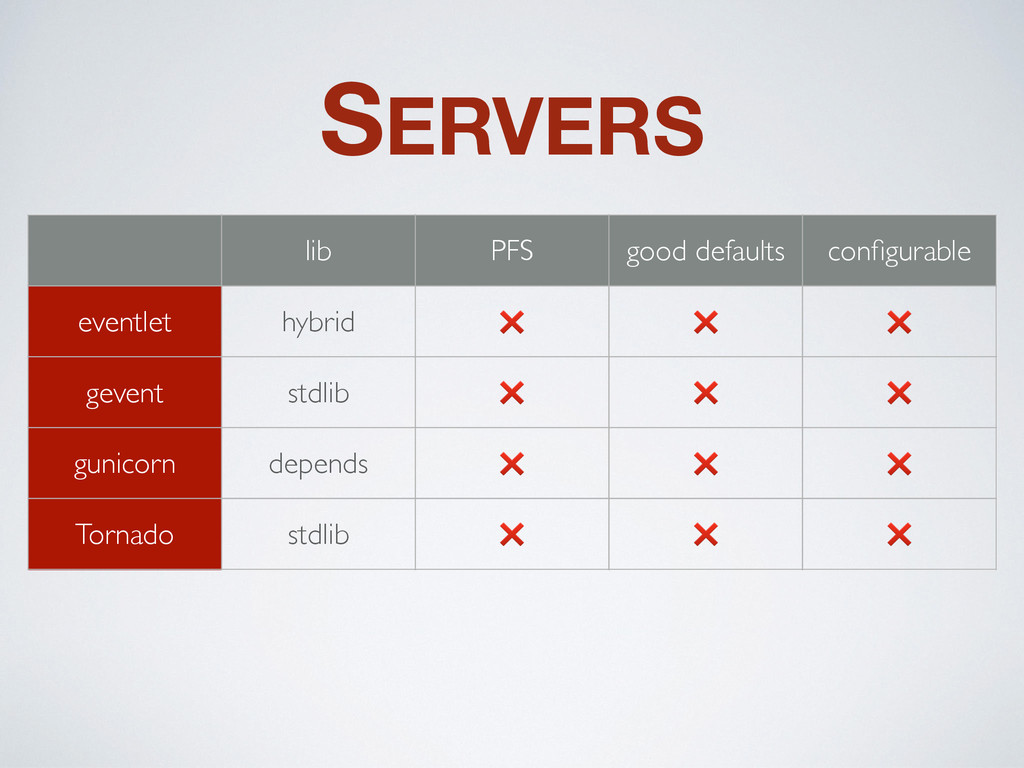
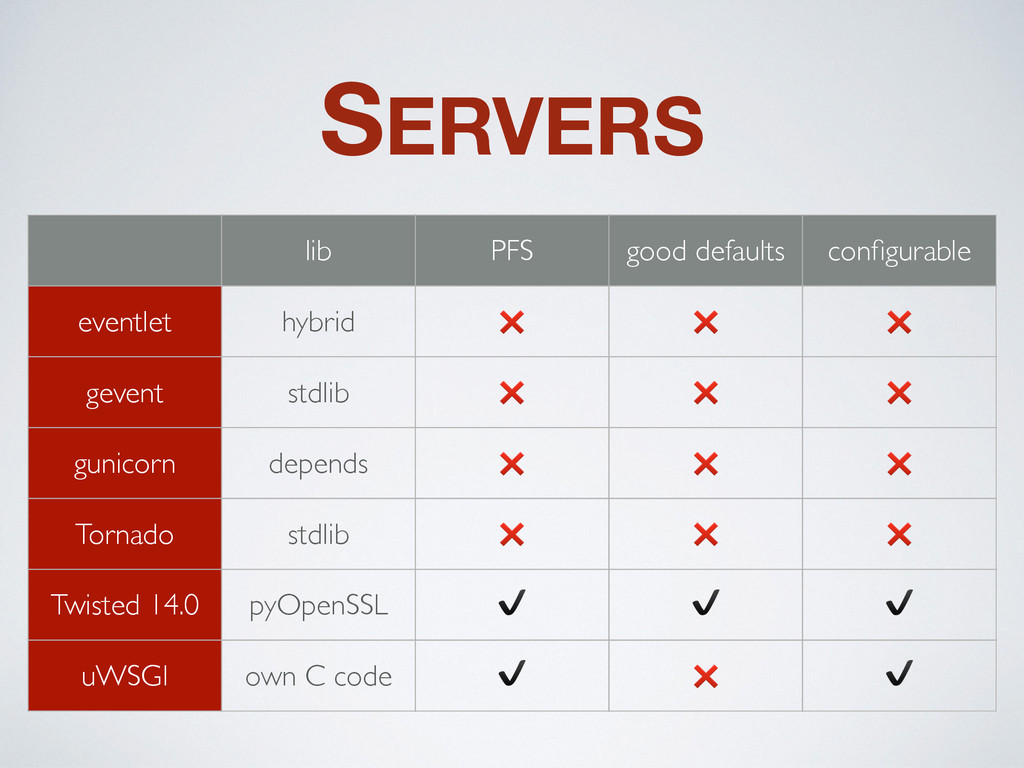
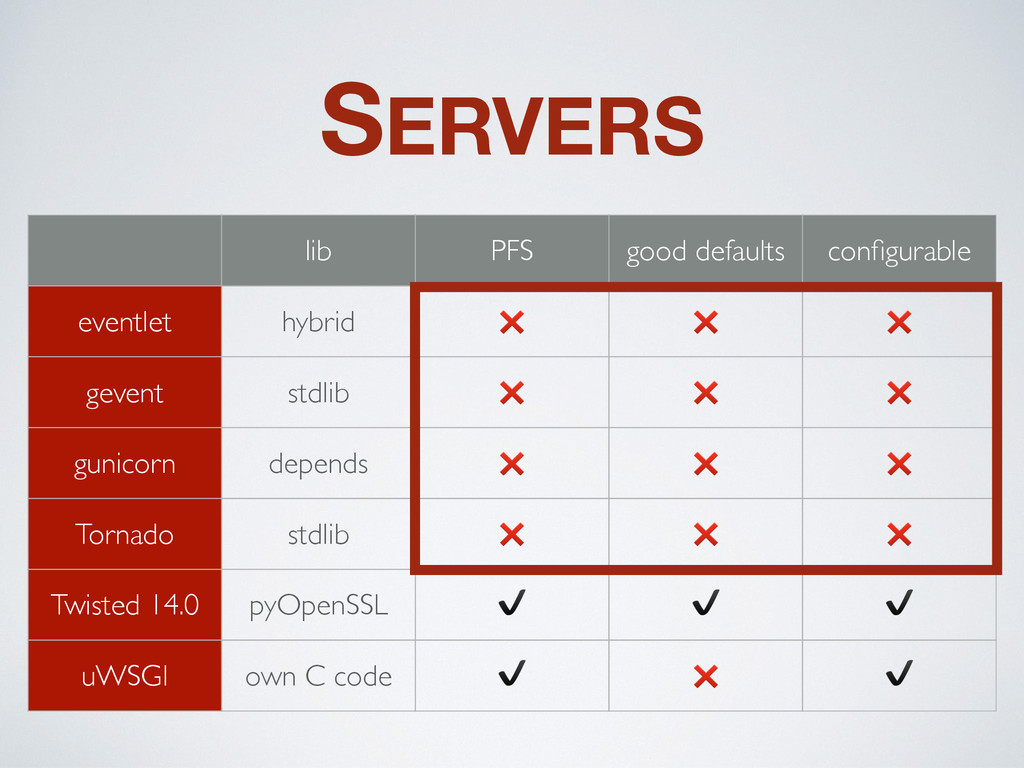
SERVERS lib PFS good defaults configurable eventlet hybrid ❌ ❌
❌ gevent stdlib ❌ ❌ ❌ gunicorn depends ❌ ❌ ❌ Tornado stdlib ❌ ❌ ❌
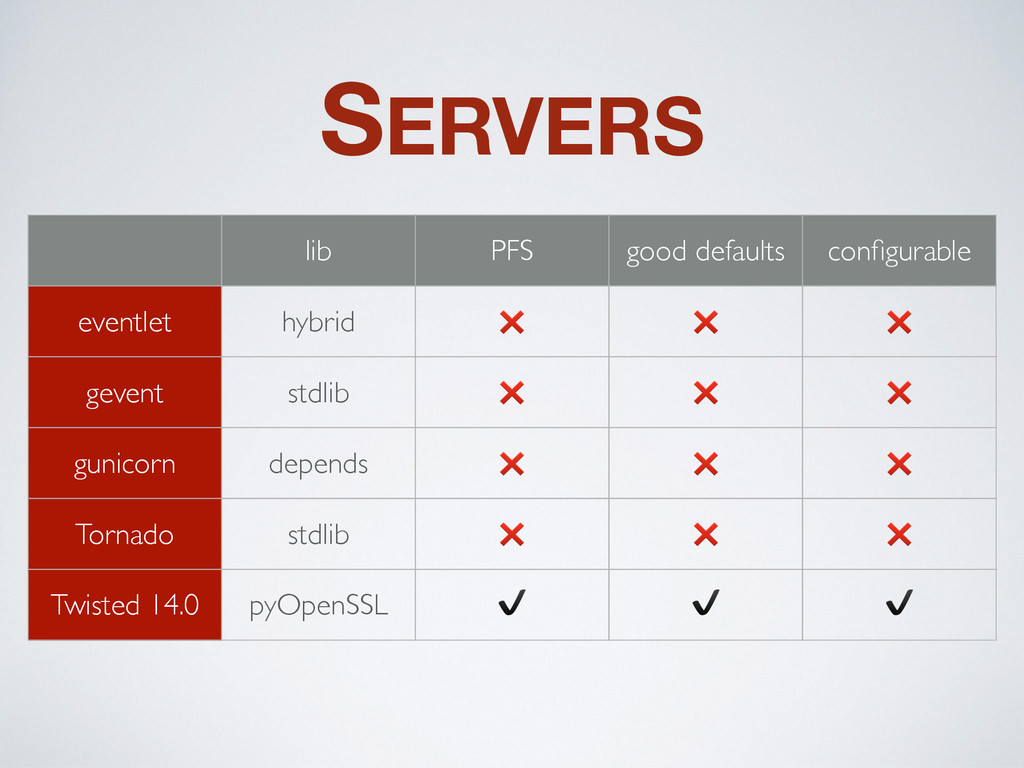
SERVERS lib PFS good defaults configurable eventlet hybrid ❌ ❌
❌ gevent stdlib ❌ ❌ ❌ gunicorn depends ❌ ❌ ❌ Tornado stdlib ❌ ❌ ❌ Twisted 14.0 pyOpenSSL ✔️ ✔️ ✔️
SERVERS lib PFS good defaults configurable eventlet hybrid ❌ ❌
❌ gevent stdlib ❌ ❌ ❌ gunicorn depends ❌ ❌ ❌ Tornado stdlib ❌ ❌ ❌ Twisted 14.0 pyOpenSSL ✔️ ✔️ ✔️ uWSGI own C code ✔️ ❌ ✔️
SERVERS lib PFS good defaults configurable eventlet hybrid ❌ ❌
❌ gevent stdlib ❌ ❌ ❌ gunicorn depends ❌ ❌ ❌ Tornado stdlib ❌ ❌ ❌ Twisted 14.0 pyOpenSSL ✔️ ✔️ ✔️ uWSGI own C code ✔️ ❌ ✔️
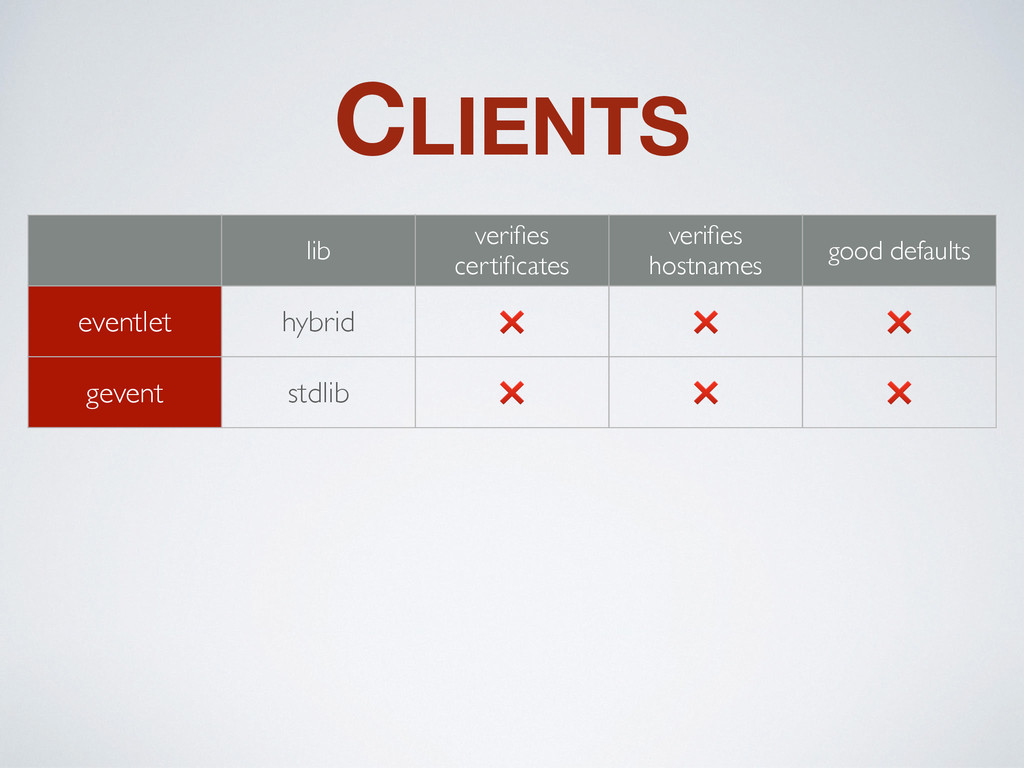
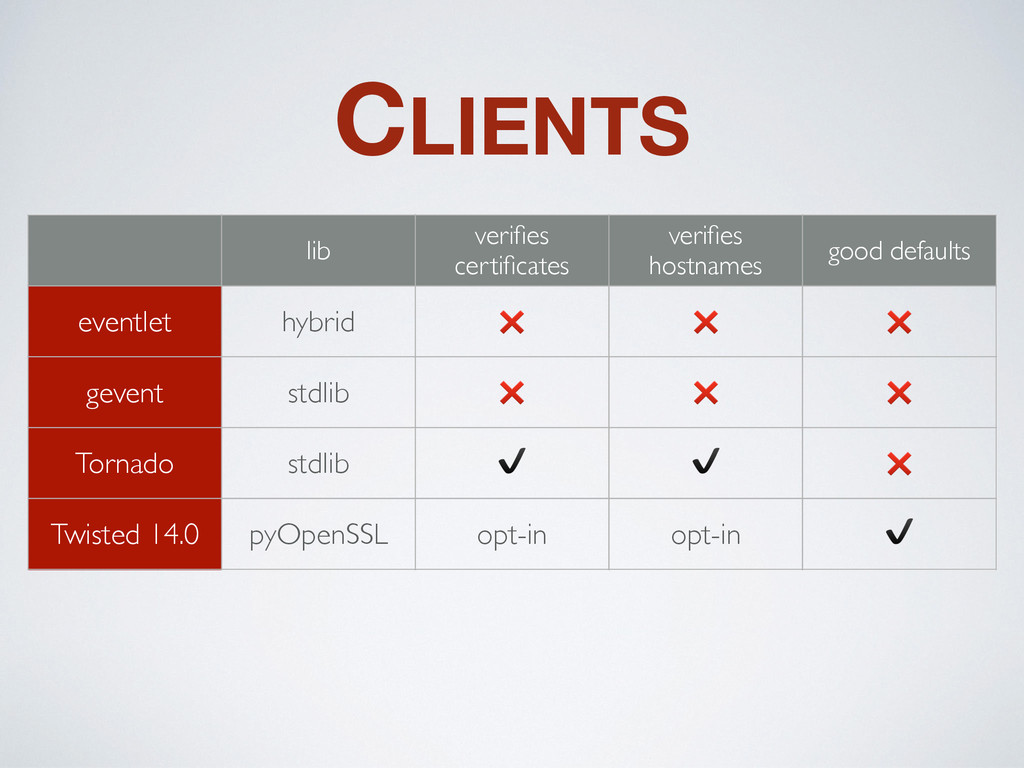
CLIENTS lib verifies certificates verifies hostnames good defaults eventlet hybrid
❌ ❌ ❌ gevent stdlib ❌ ❌ ❌
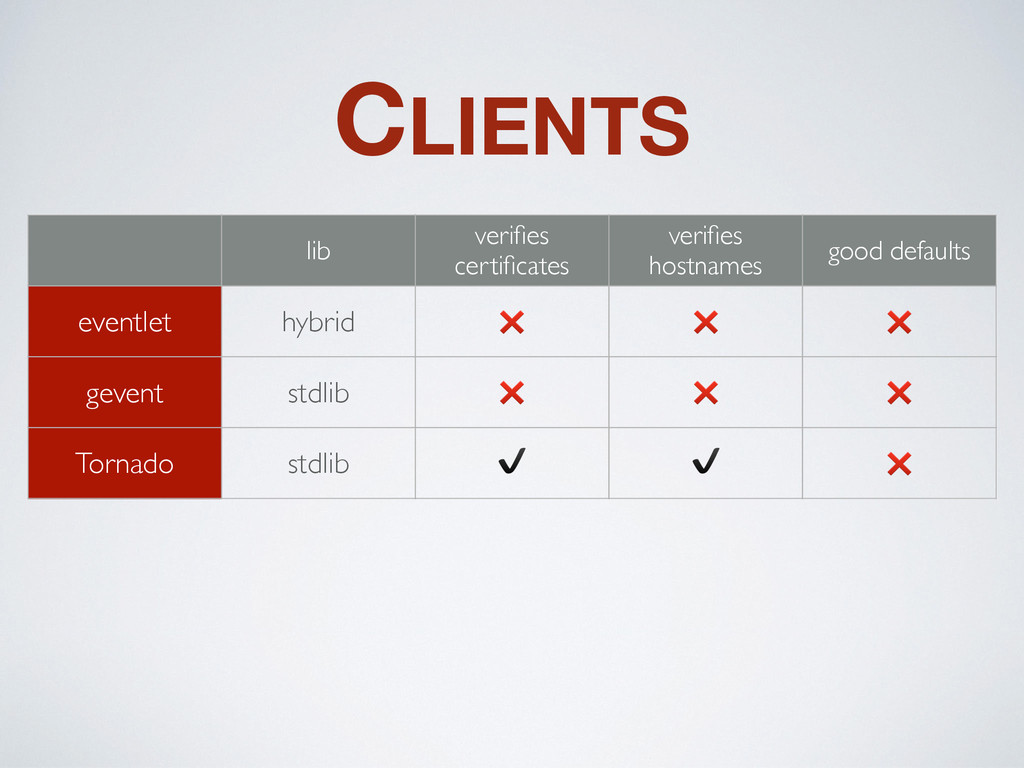
CLIENTS lib verifies certificates verifies hostnames good defaults eventlet hybrid
❌ ❌ ❌ gevent stdlib ❌ ❌ ❌ Tornado stdlib ✔️ ✔️ ❌
CLIENTS lib verifies certificates verifies hostnames good defaults eventlet hybrid
❌ ❌ ❌ gevent stdlib ❌ ❌ ❌ Tornado stdlib ✔️ ✔️ ❌ Twisted 14.0 pyOpenSSL opt-in opt-in ✔️
CLIENTS lib verifies certificates verifies hostnames good defaults eventlet hybrid
❌ ❌ ❌ gevent stdlib ❌ ❌ ❌ Tornado stdlib ✔️ ✔️ ❌ Twisted 14.0 pyOpenSSL opt-in opt-in ✔️ urllib2 stdlib ❌ ❌ ❌
CLIENTS lib verifies certificates verifies hostnames good defaults eventlet hybrid
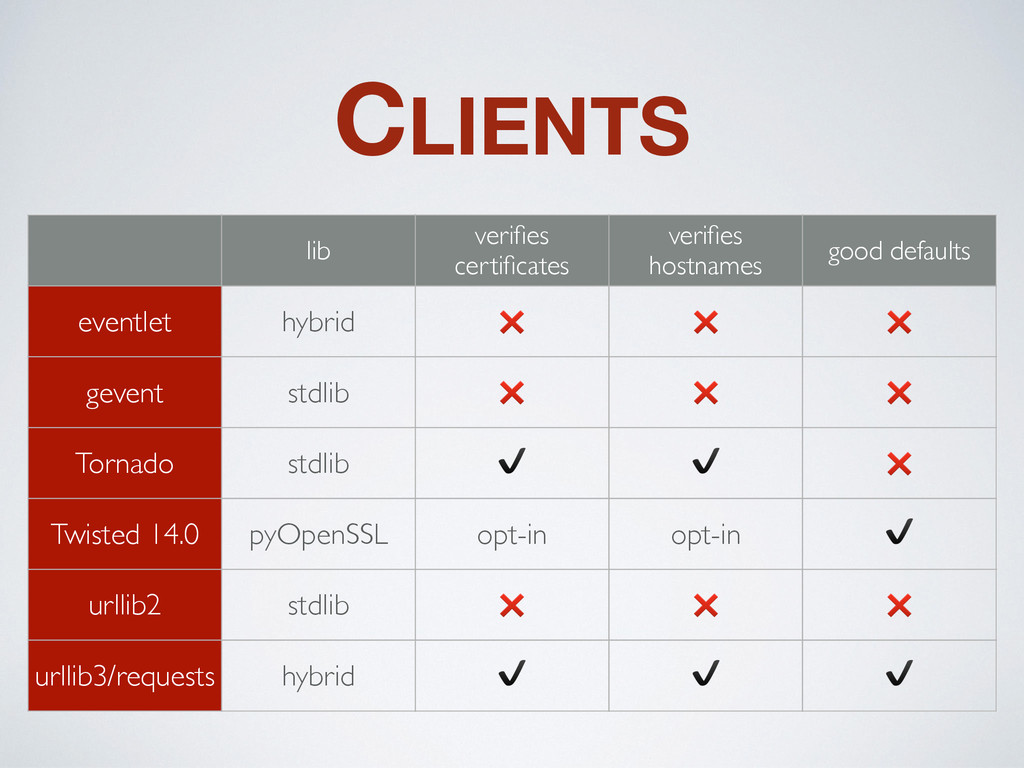
❌ ❌ ❌ gevent stdlib ❌ ❌ ❌ Tornado stdlib ✔️ ✔️ ❌ Twisted 14.0 pyOpenSSL opt-in opt-in ✔️ urllib2 stdlib ❌ ❌ ❌ urllib3/requests hybrid ✔️ ✔️ ✔️
SUMMARY
SUMMARY • keep TLS out of Python if you can
SUMMARY • keep TLS out of Python if you can
• use pyOpenSSL-powered requests for HTTPS
SUMMARY • keep TLS out of Python if you can
• use pyOpenSSL-powered requests for HTTPS • write servers in Twisted
SUMMARY • keep TLS out of Python if you can
• use pyOpenSSL-powered requests for HTTPS • write servers in Twisted • use pyOpenSSL
SUMMARY • keep TLS out of Python if you can
• use pyOpenSSL-powered requests for HTTPS • write servers in Twisted • use pyOpenSSL • use Python 2 stdlib only for clients
WHY SORRY?
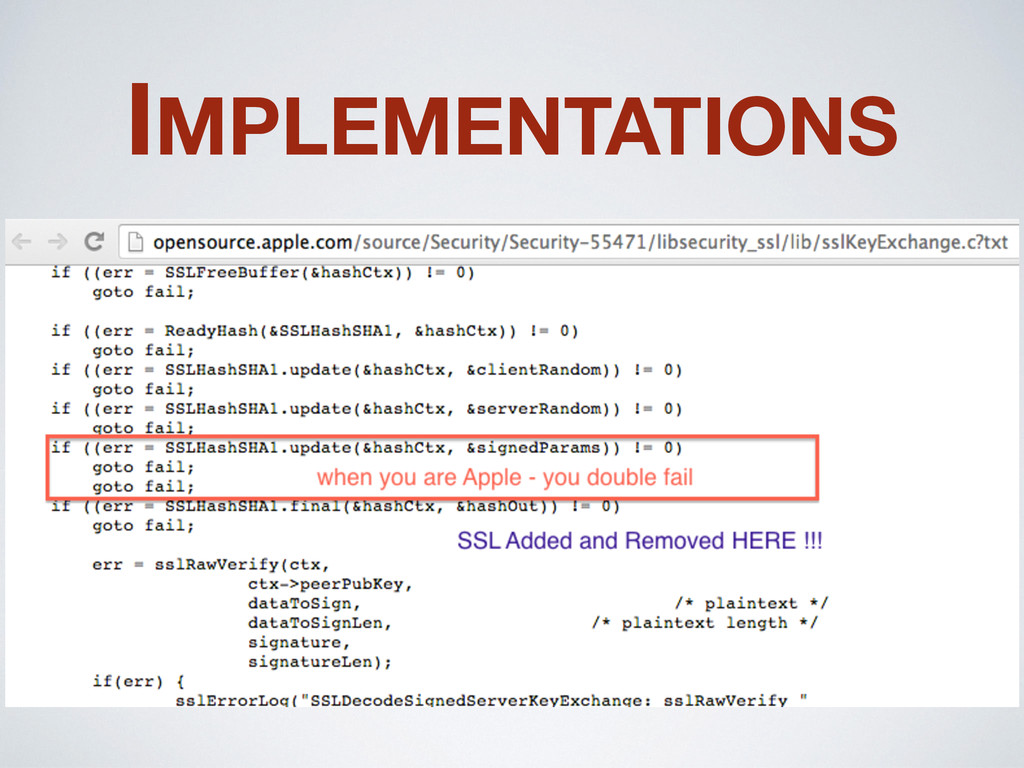
IMPLEMENTATIONS
IMPLEMENTATIONS
USERS
USERS • run outdated software
USERS • run outdated software • click certificate warnings away
USERS • run outdated software • click certificate warnings away
• are at the mercy of 3rd parties
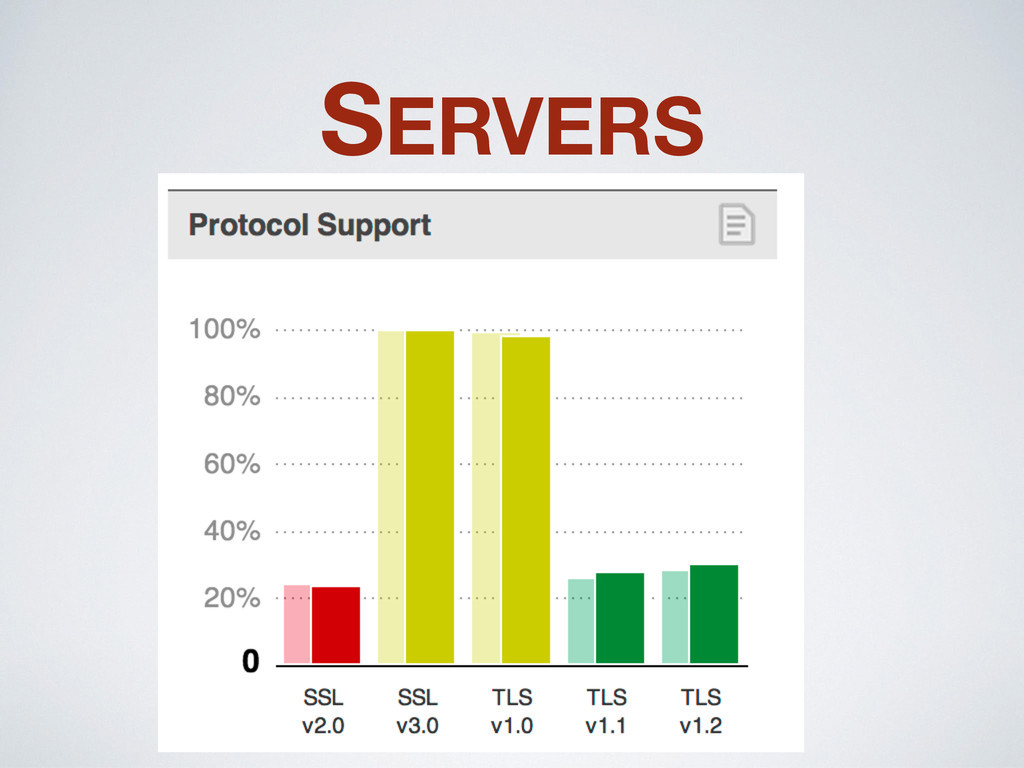
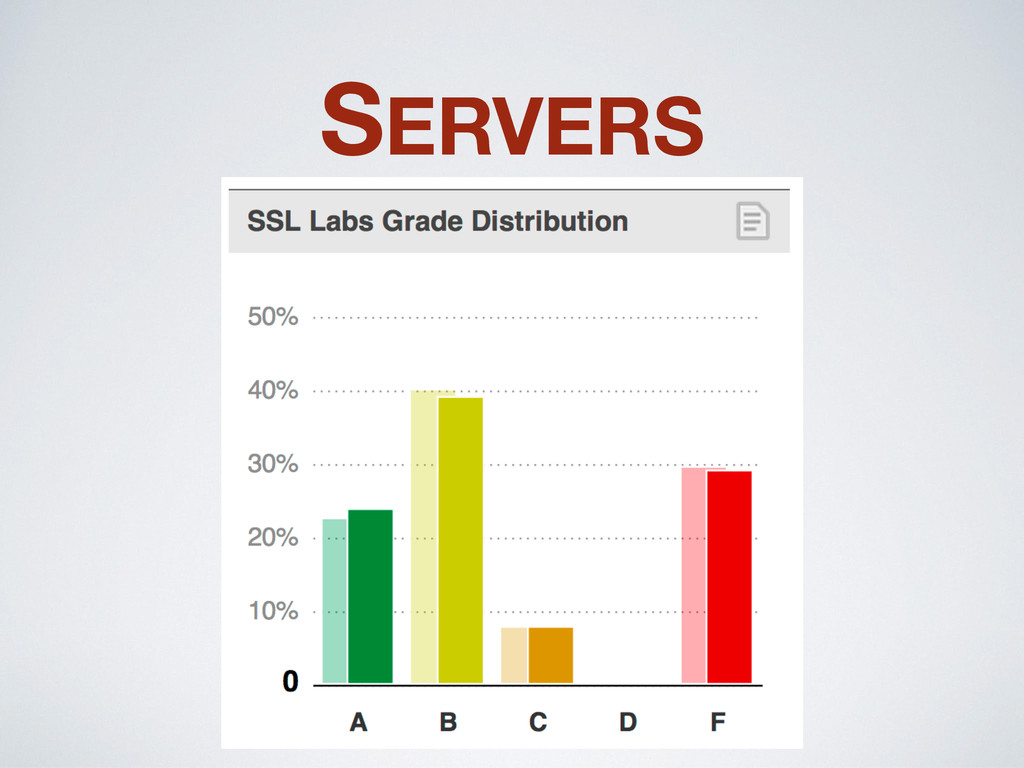
SERVERS
SERVERS
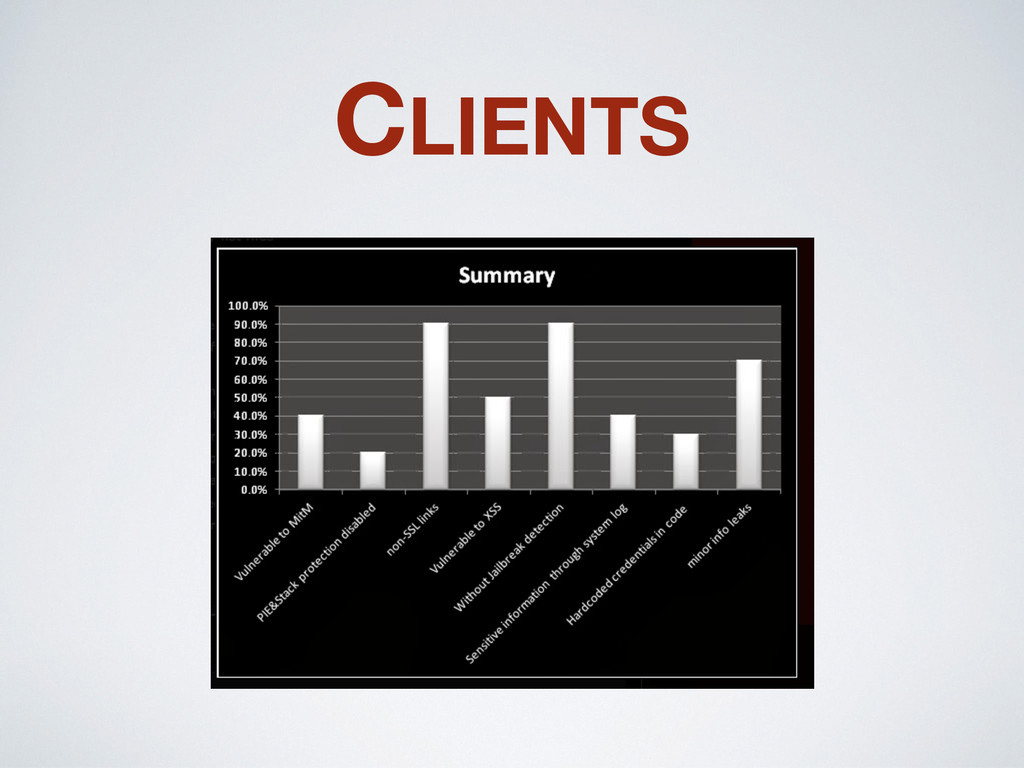
CLIENTS
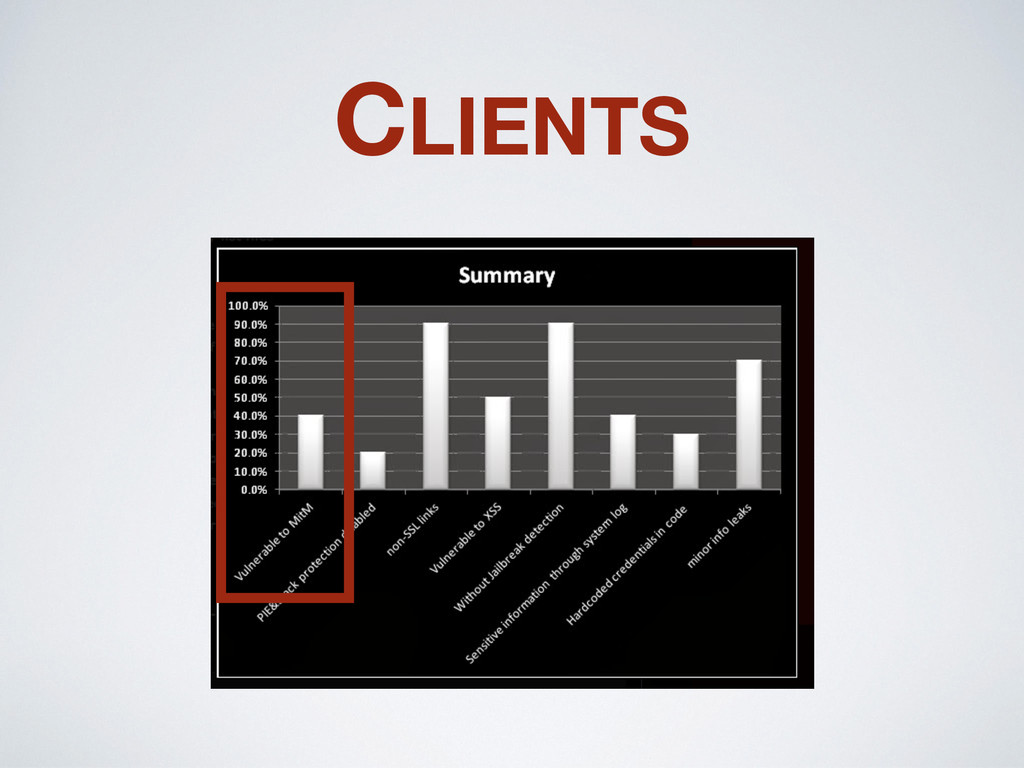
CLIENTS
PYTHON Is at the forefront of terrible.
HOPE
HOPE • people care again
HOPE • people care again • stdlib
HOPE • people care again • stdlib • PyCA
CALLS TO ACTION
CALLS TO ACTION
CALLS TO ACTION
CALLS TO ACTION
CALLS TO ACTION
ox.cx/t @hynek Crypto Open Space!


 pycon2014
 ykagano
 yokawasa
 fespinoza
 munakata
 oracle4engineer
 marceloancelmo
 chack411
 sansantech
 aoto
 ishiirikie
 pauli
 tonyrice
 chikuwait
 sarafernandez
 matthewcrist
 panda_program
 codingconduct
 baasie
 jacobtomlinson
 lemiorhan
 helenjbeal
 swwweet
 reverentgeek