Upgrade to Pro — share decks privately, control downloads, hide ads and more …

AirBox

Avatar for Aruj Parajuli Aruj Parajuli
November 28, 2014

 AirBox

Cloud Based Hosting Platform

Avatar for Aruj Parajuli

Aruj Parajuli

November 28, 2014

More Decks by Aruj Parajuli

Other Decks in Technology

Transcript

  1. AirBox Vaishali Srivastav - 20114047 Apoorv Vikram Singh - 20114104

    Nikhil Kumar Bharti - 20112005 Aruj Parajuli - 20114145
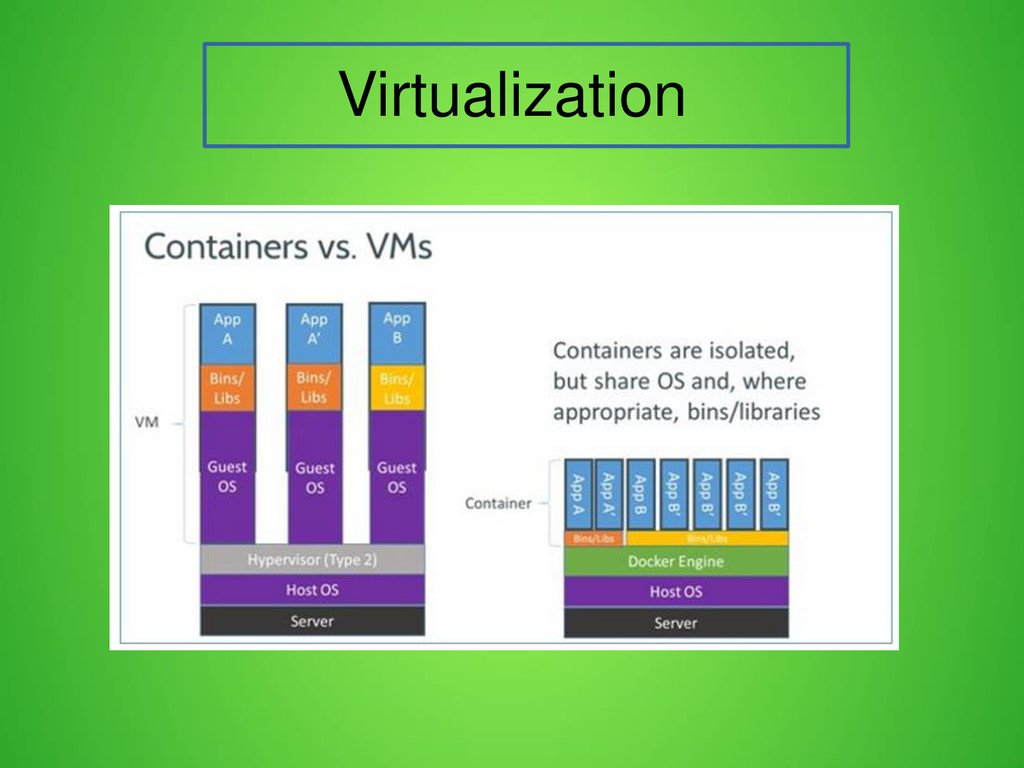
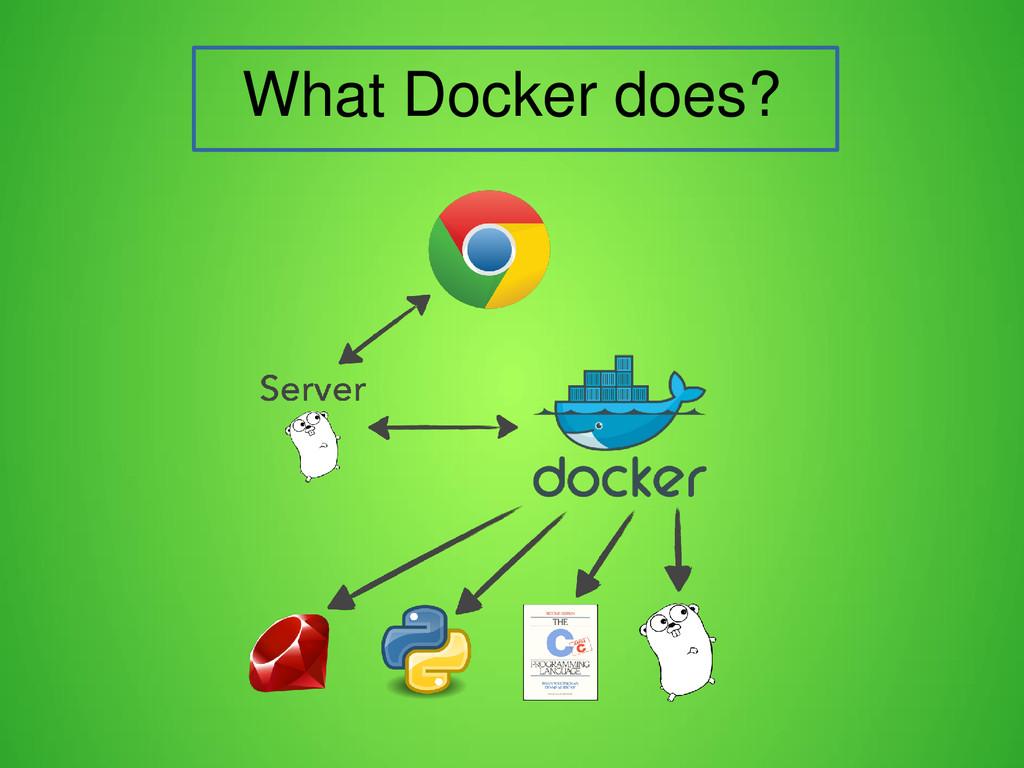
  2. Indroduction Cloud Based Hosting Platform Encryption(AES-128 Bit) & Security Virtualization

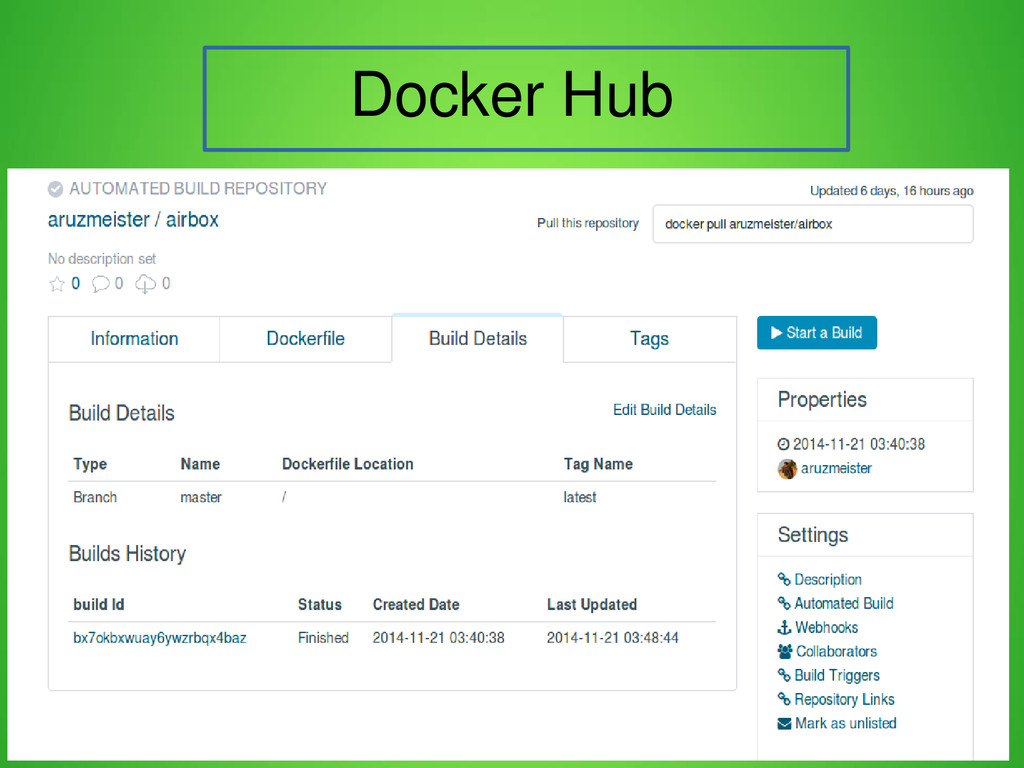
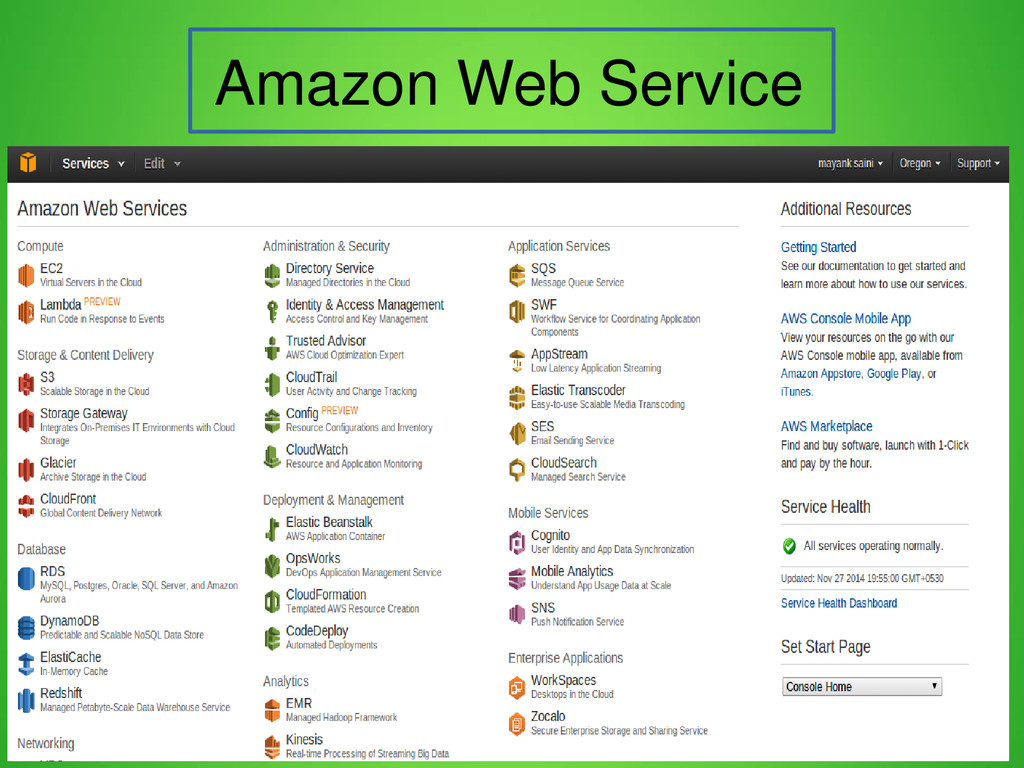
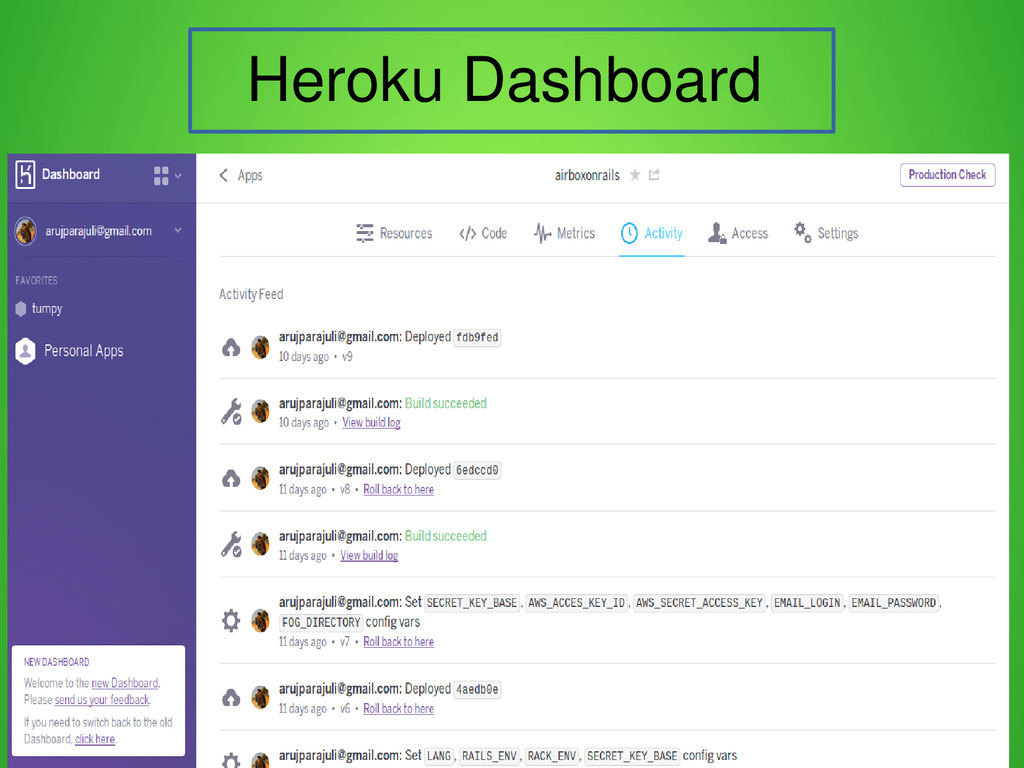
    :- Docker Cloud Platform :- AWS, Heroku & DigitalOcean Version Control System :- GIT
  3. Technology Stack Web Framework:- Ruby on Rails Programming Language:- Ruby

    Database:- Postgres & Sqlite Web Development :- HTML, CSS, JS
  4. What is Ruby on Rails? Web application development framework RubyGems

    MVC ORM(ActiveRecord) DRY(Don't Repeat Yourself) Convention over Configuration API, Routes & Portability Ruby
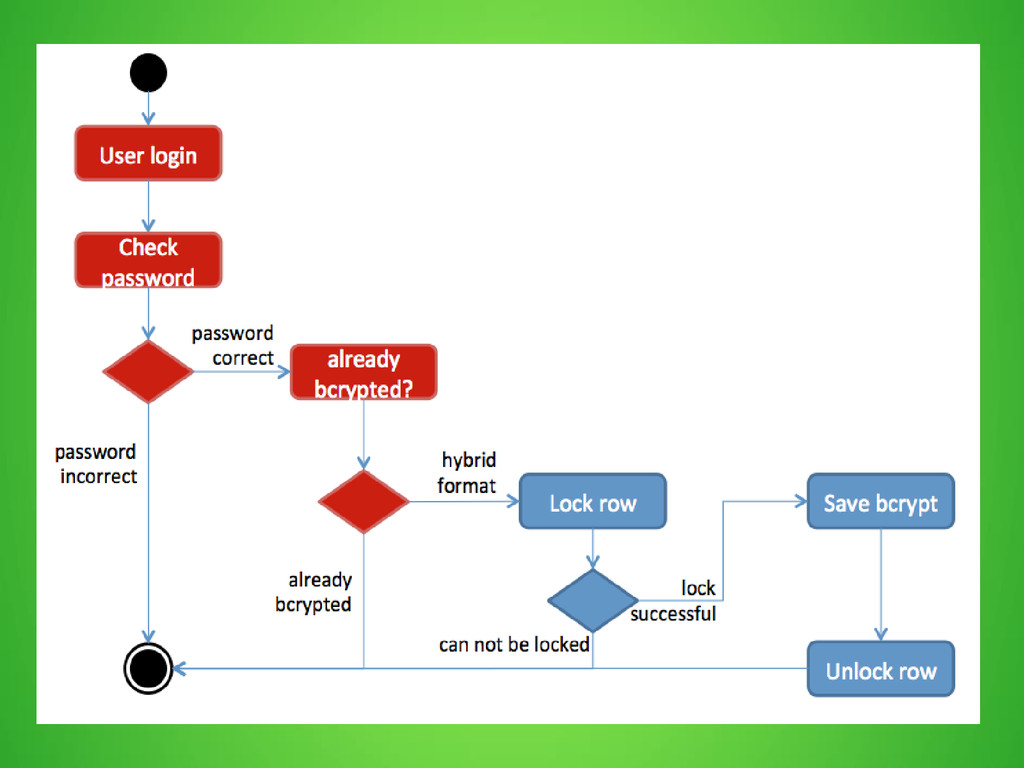
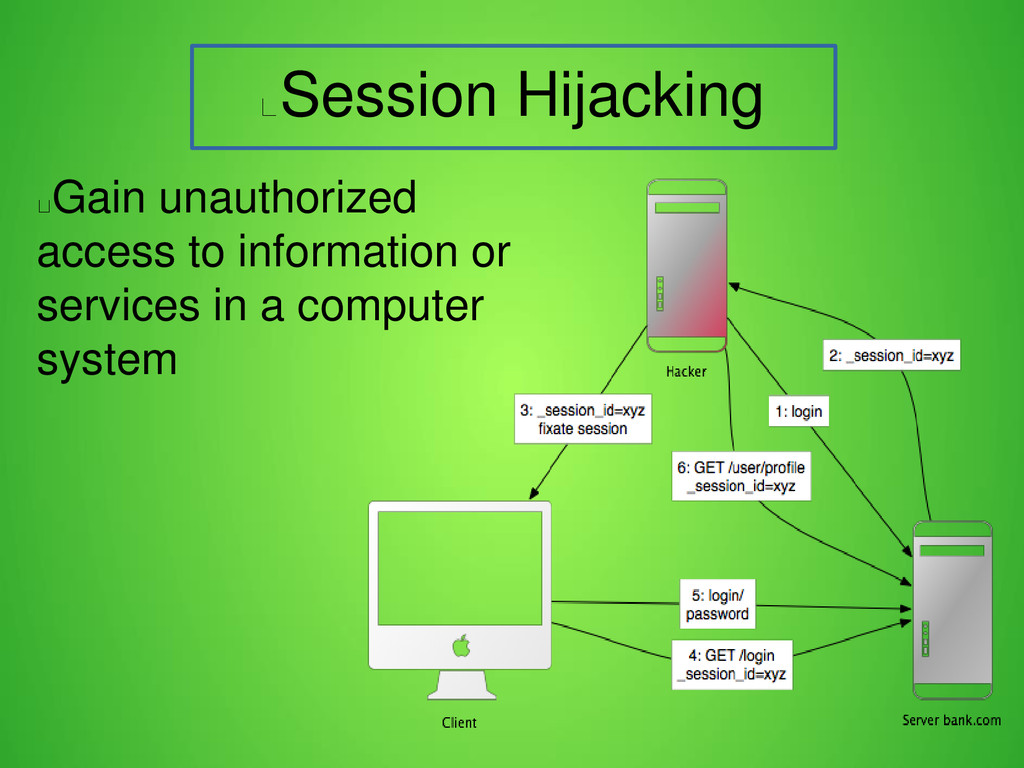
  5. Security Prevent SQL Injection Cross-Site Request Forgery and XSS Prevent

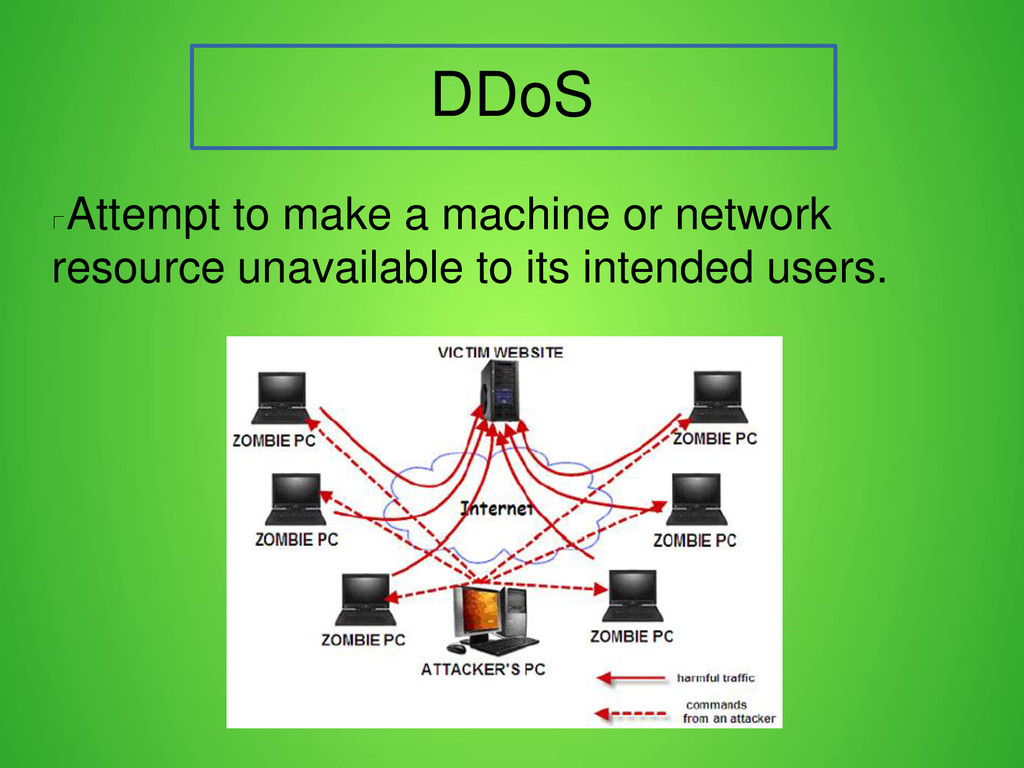
    Brute Forcing Prevent Privilege Escalation Reduce DDOS attack Prevent Clickjacking Prevent Session Hijacking and Session fixation Encryption in user fields Prevent Heartbleed
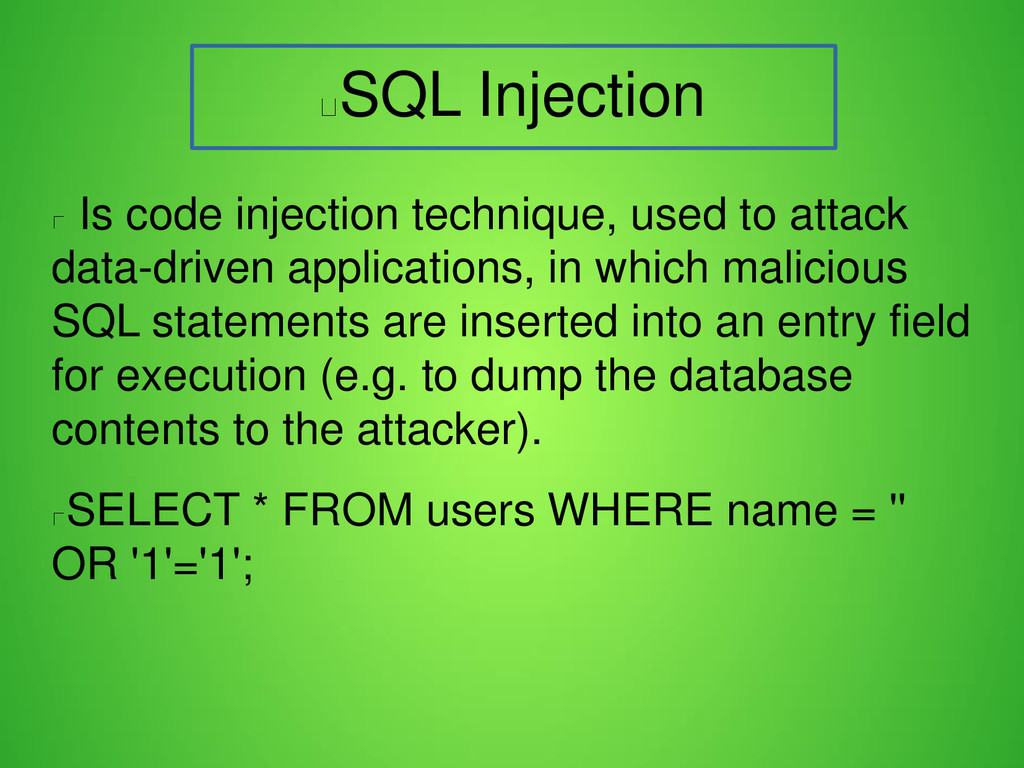
  6. SQL Injection Is code injection technique, used to attack data-driven

    applications, in which malicious SQL statements are inserted into an entry field for execution (e.g. to dump the database contents to the attacker). SELECT * FROM users WHERE name = '' OR '1'='1';
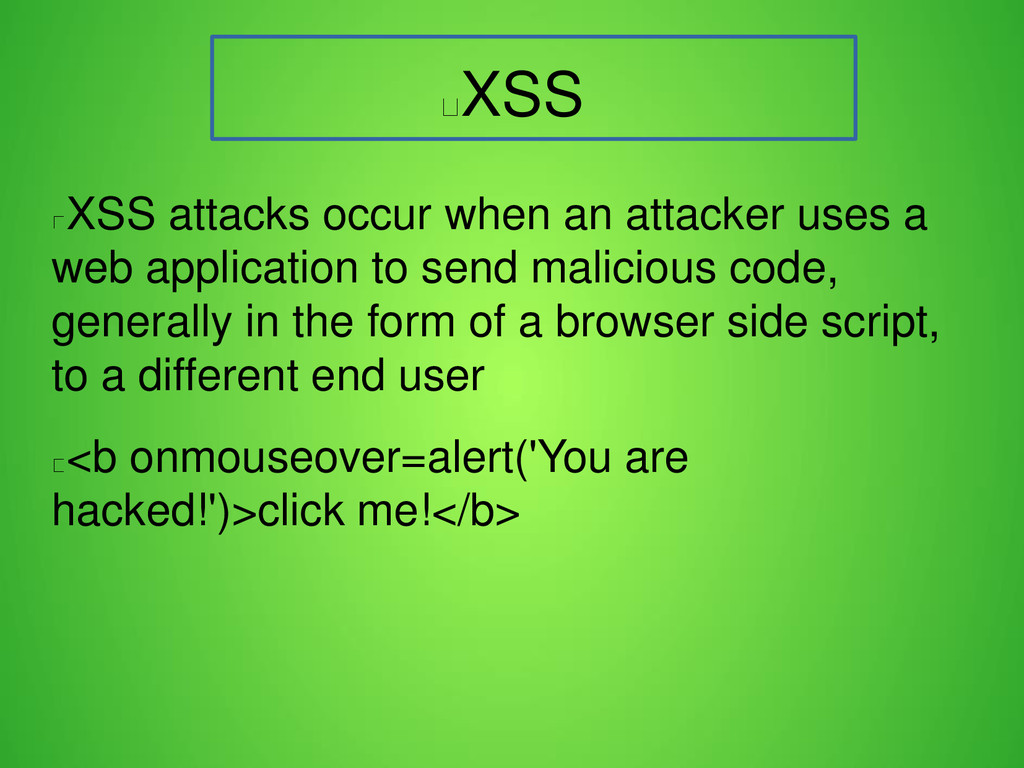
  7. XSS XSS attacks occur when an attacker uses a web

    application to send malicious code, generally in the form of a browser side script, to a different end user <b onmouseover=alert('You are hacked!')>click me!</b>
  8. Brute-Force Brute-force attacks on accounts are trial and error attacks

    on the login credentials When password guessing, this method is very fast when used to check all short passwords, but for longer passwords other methods such as the dictionary attack are used
  9. Privilege Escalation Act of exploiting a bug or design flaw

    on software application to gain elevated access to resources that are normally protected from an application or user. @project = Project.find(params[:id])
  10. Clickjacking Malicious technique of tricking a Web user into clicking

    on something different from what the user perceives, thus potentially revealing confidential information or taking control of their computer while clicking on seemingly innocuous web pages
  11. Heartbleed Vulnerability is classified as a buffer over- read, a

    situation where more data can be read than should be allowed Weakness allows stealing the information protected, under normal conditions, by the SSL/TLS encryption used to secure the Internet
  12. Bootstrap Save lots of time Responsive features Consistent design Easy

    to to use & Integration Compatible with browsers & smatphone Open Source Less & Sass Support