Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Securing the Things: APIs in the IoT Era

Securing the Things: APIs in the IoT Era

The explosion of IoT has brought numerous changes to the way we use technology. From massive enterprises to the individual consumer, improvements in convenience and automation of most aspects of our lives has seen dramatic progress – yet security continues to be an ongoing concern in the software and devices we've all grown to depend on. The talk will focus on examining the protocols used in popular IoT devices, including how each operates in the wild, the inherent security concerns during design, as well as real world examples of practical attacks against them.

Avatar for Randy Westergren

Randy Westergren

November 03, 2016

Other Decks in Technology

Transcript

  1. Overview • What is IoT, really? • Communication Protocols ◦

    MQTT ◦ Custom TCP • Implementation Concerns • Real-World Attack Examples • Future Outlook
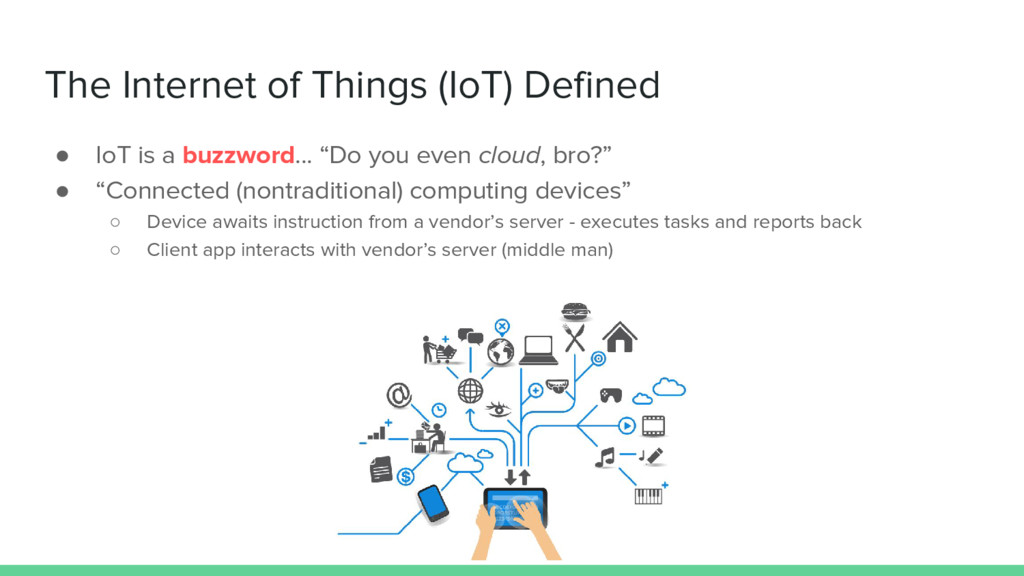
  2. The Internet of Things (IoT) Defined • IoT is a

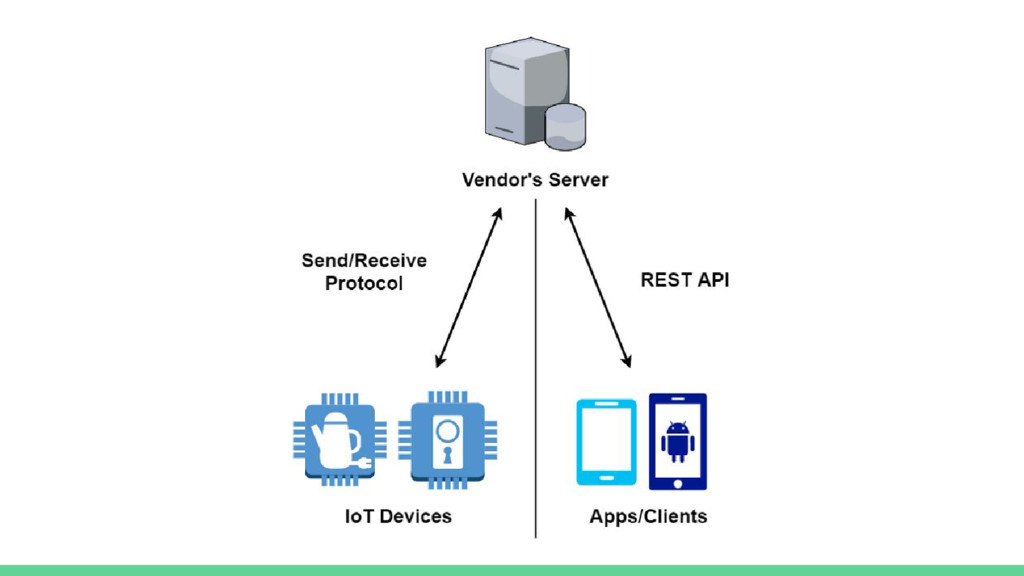
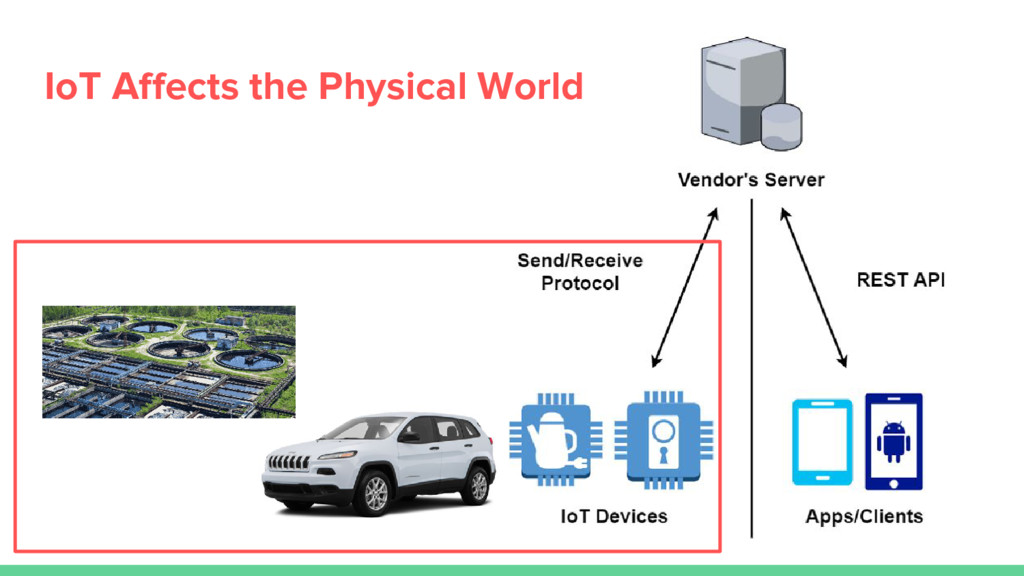
    buzzword... “Do you even cloud, bro?” • “Connected (nontraditional) computing devices” ◦ Device awaits instruction from a vendor’s server - executes tasks and reports back ◦ Client app interacts with vendor’s server (middle man)
  3. Examples of IoT in Action • Brew that coffee! •

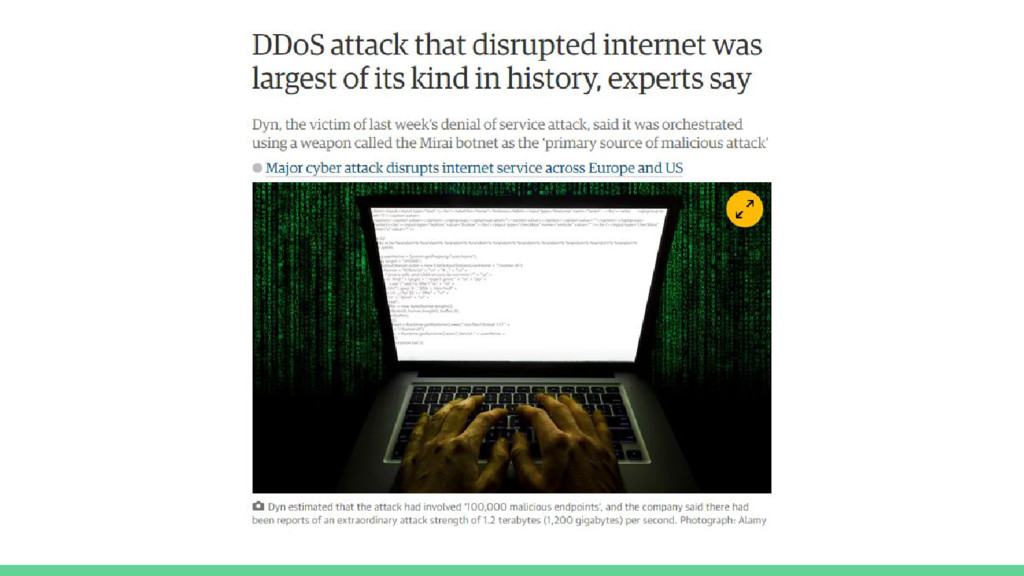
    Adjust the refrigerator’s temperature • Open the garage door • Start the car • Change the chemical mix at the water treatment plant • DDoS <this> target
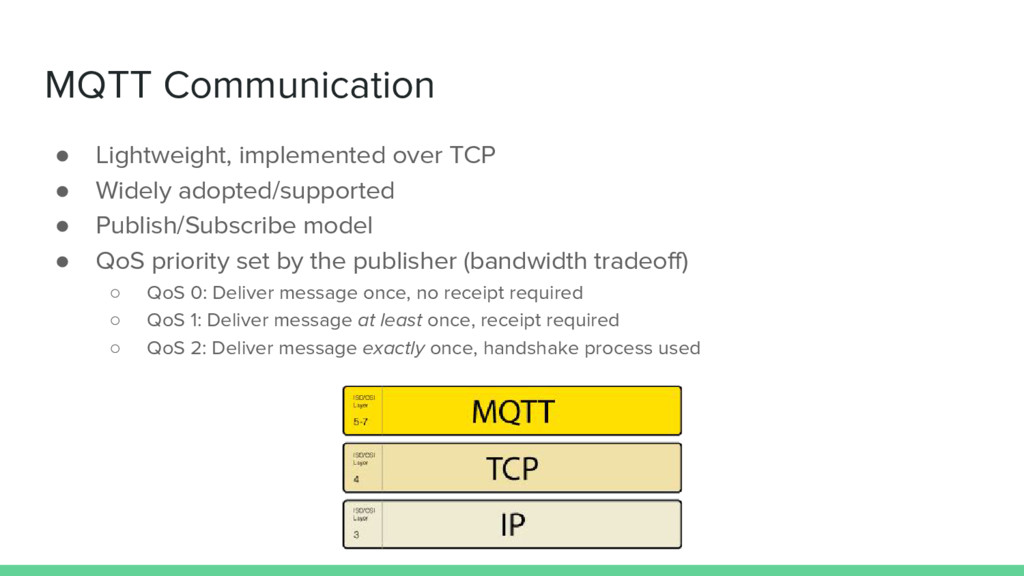
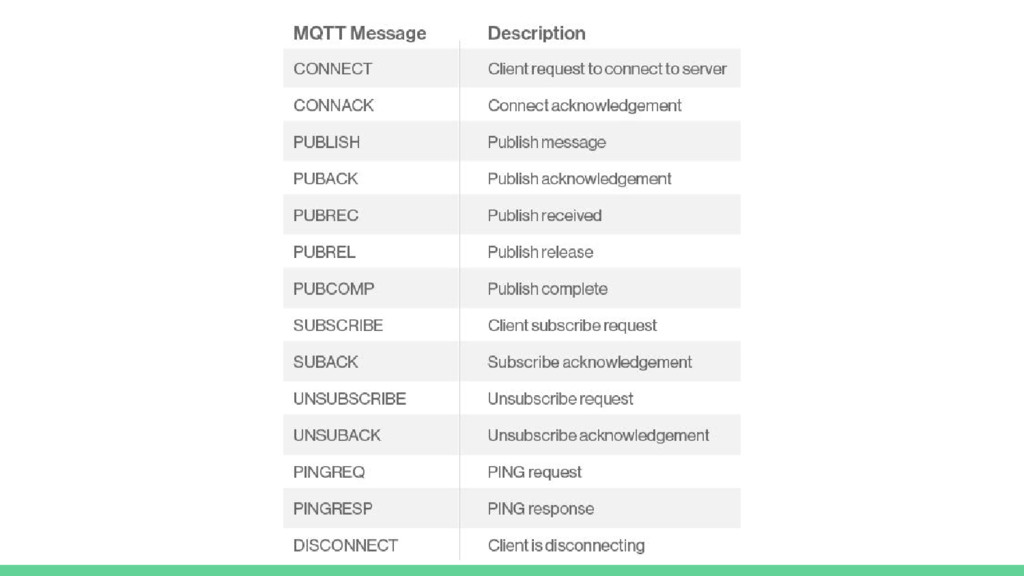
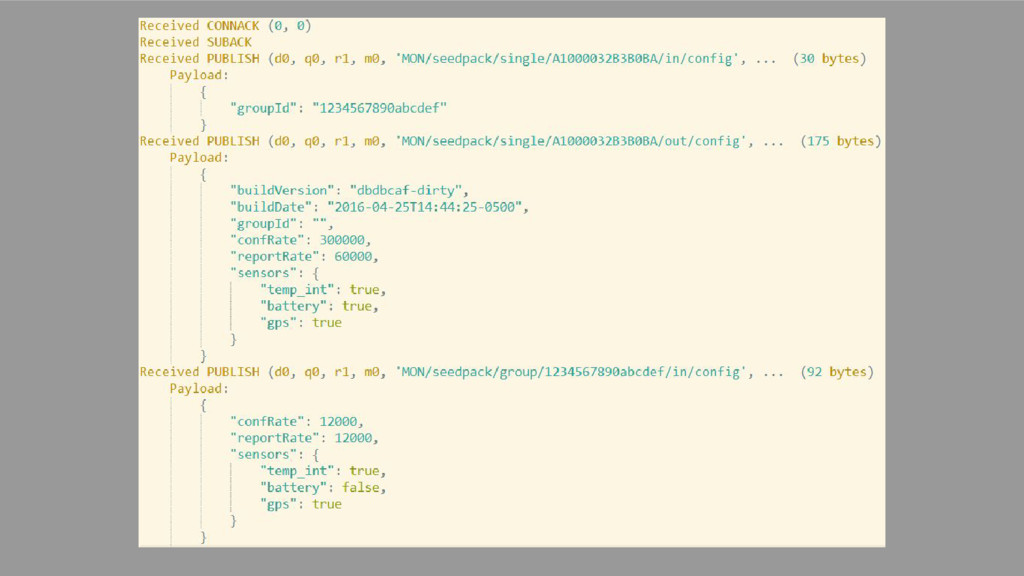
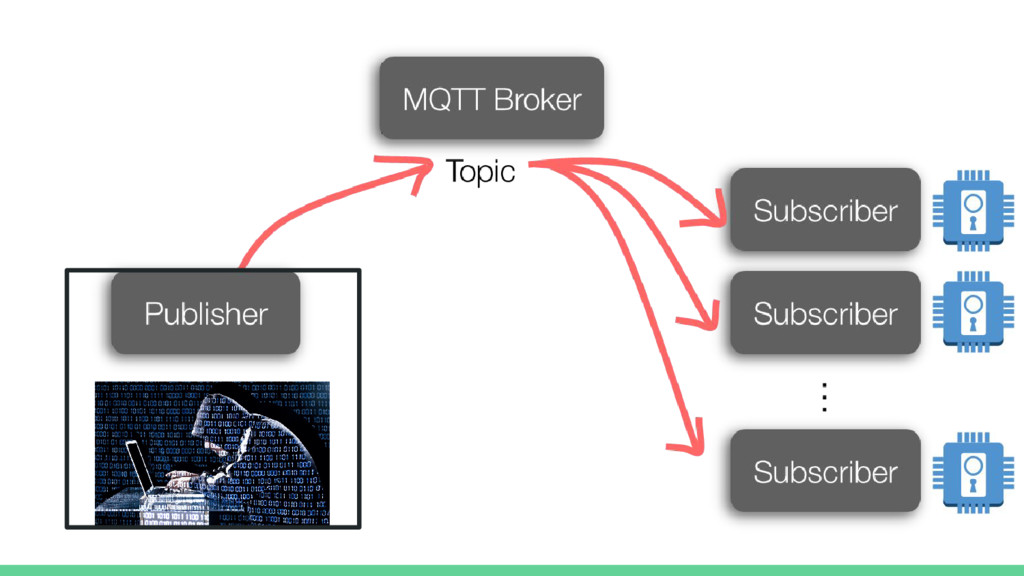
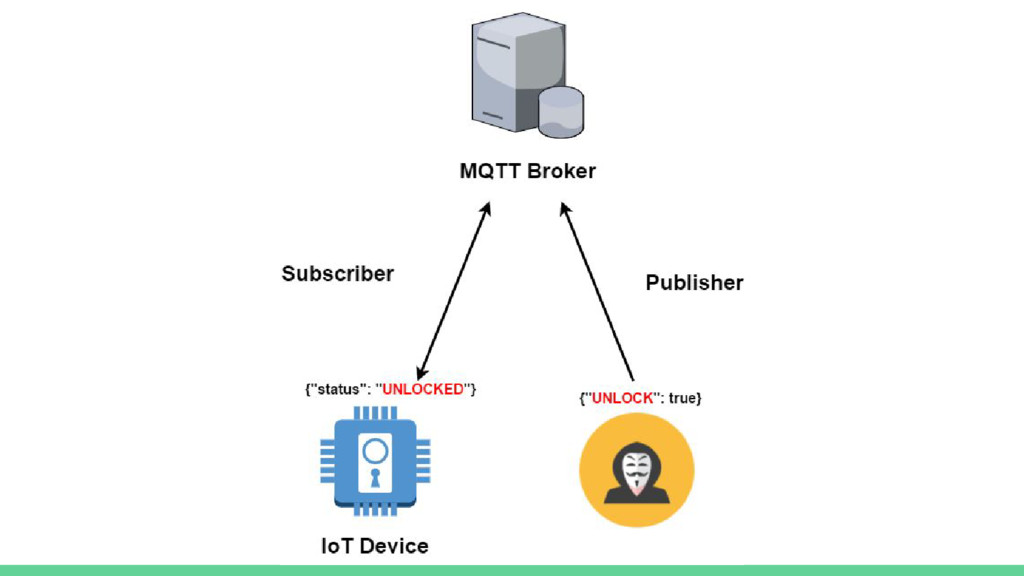
  4. MQTT Communication • Lightweight, implemented over TCP • Widely adopted/supported

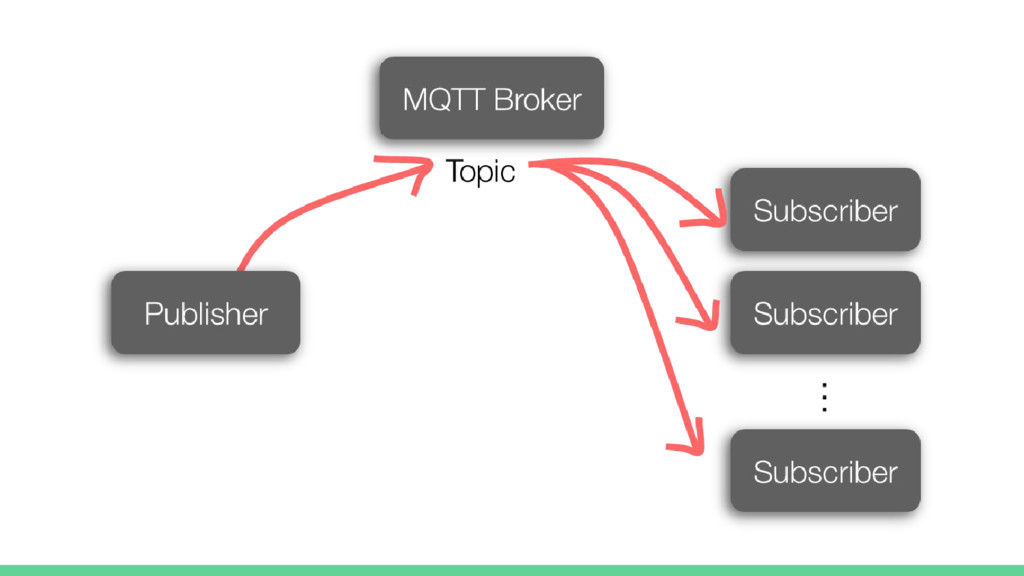
    • Publish/Subscribe model • QoS priority set by the publisher (bandwidth tradeoff) ◦ QoS 0: Deliver message once, no receipt required ◦ QoS 1: Deliver message at least once, receipt required ◦ QoS 2: Deliver message exactly once, handshake process used
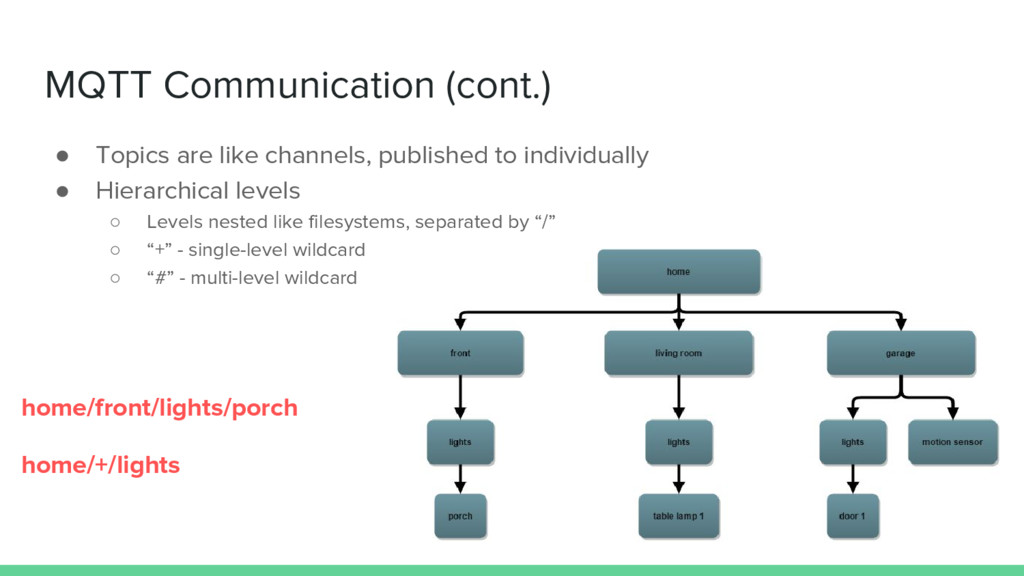
  5. MQTT Communication (cont.) • Topics are like channels, published to

    individually • Hierarchical levels ◦ Levels nested like filesystems, separated by “/” ◦ “+” - single-level wildcard ◦ “#” - multi-level wildcard home/front/lights/porch home/+/lights
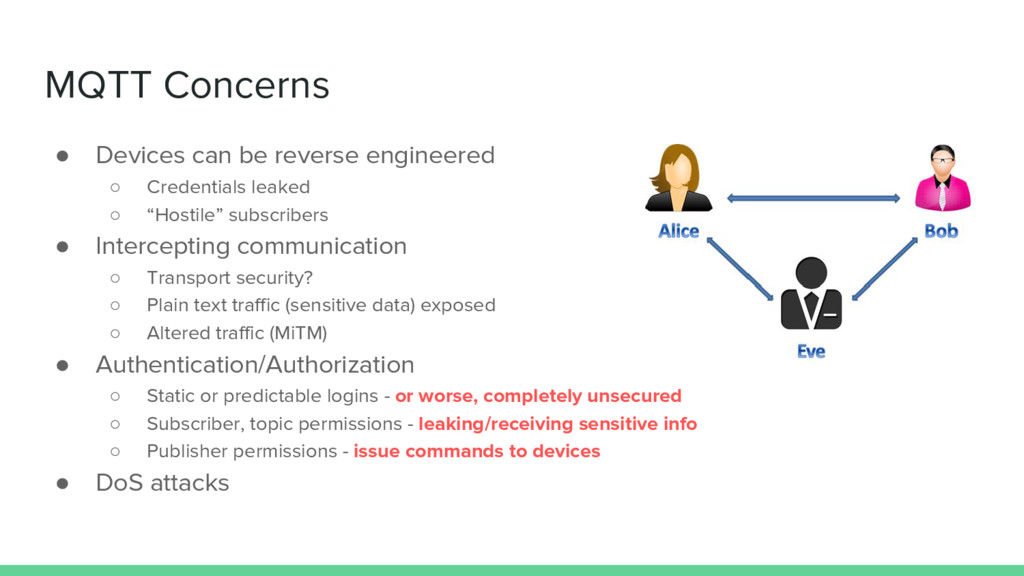
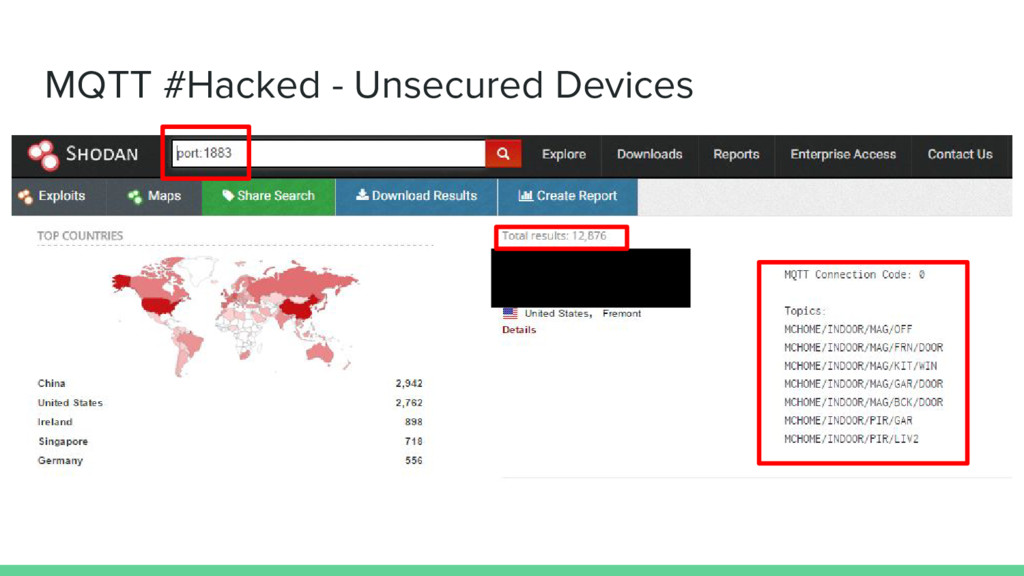
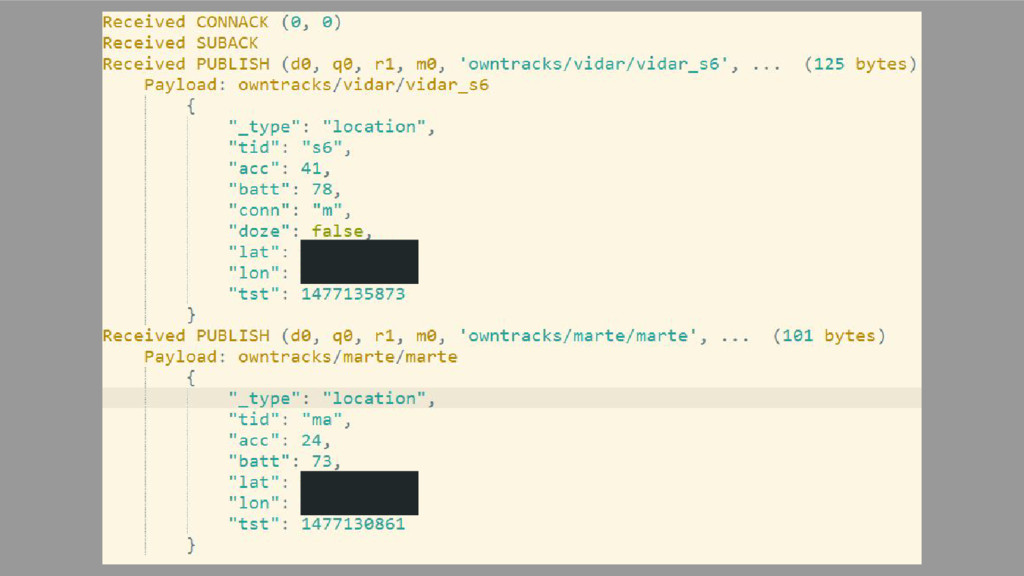
  6. MQTT Concerns • Devices can be reverse engineered ◦ Credentials

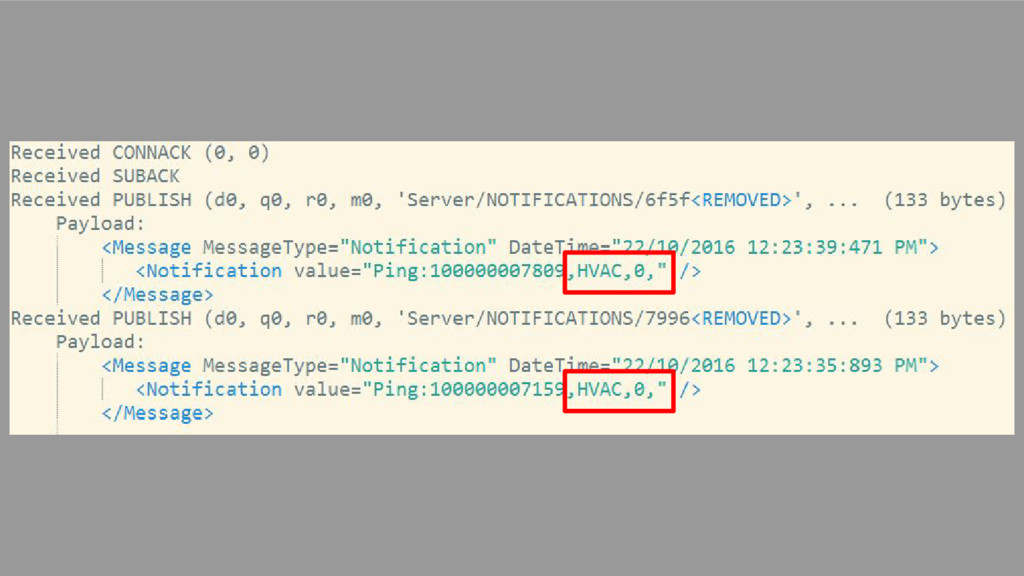
    leaked ◦ “Hostile” subscribers • Intercepting communication ◦ Transport security? ◦ Plain text traffic (sensitive data) exposed ◦ Altered traffic (MiTM) • Authentication/Authorization ◦ Static or predictable logins - or worse, completely unsecured ◦ Subscriber, topic permissions - leaking/receiving sensitive info ◦ Publisher permissions - issue commands to devices • DoS attacks
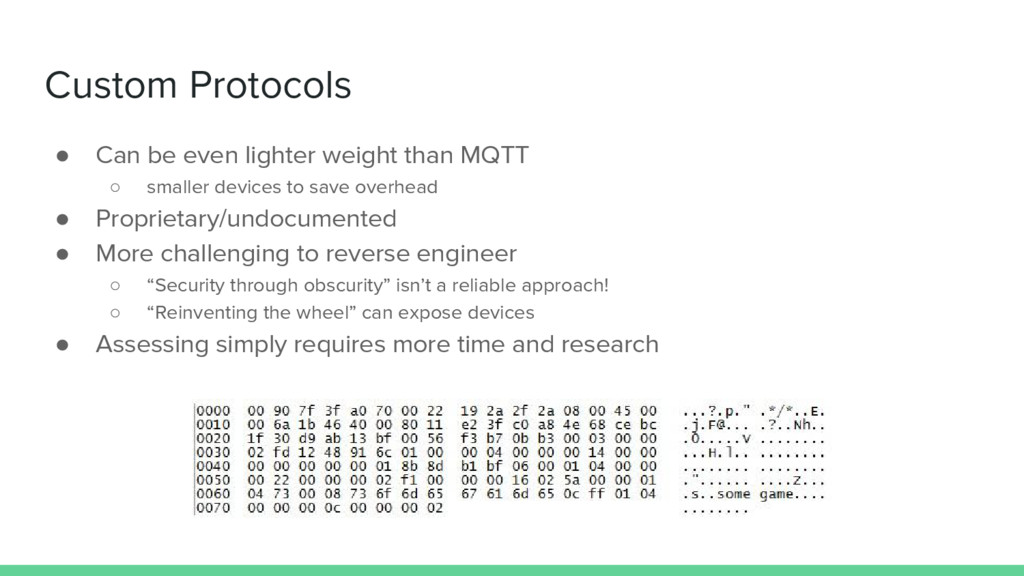
  7. Custom Protocols • Can be even lighter weight than MQTT

    ◦ smaller devices to save overhead • Proprietary/undocumented • More challenging to reverse engineer ◦ “Security through obscurity” isn’t a reliable approach! ◦ “Reinventing the wheel” can expose devices • Assessing simply requires more time and research
  8. Custom Protocol Concerns • No higher-level tools (proxies) to work

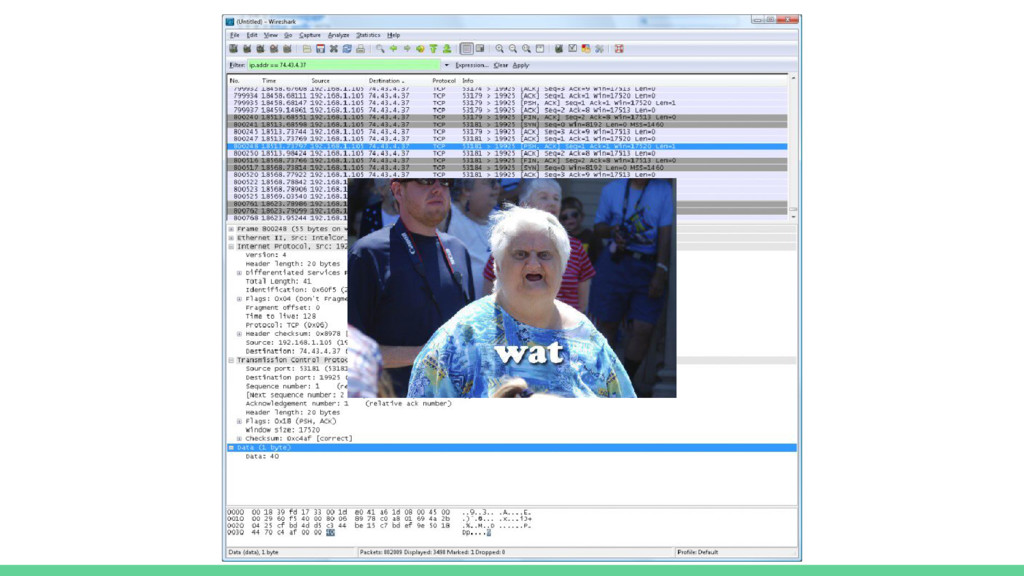
    with • Packet sniffers (Wireshark, tcpdump) are typically used to collect and inspect protocol communication • Reversing depends on the device, protocol, and results of the packet captures • Example client apps can help in reverse engineering
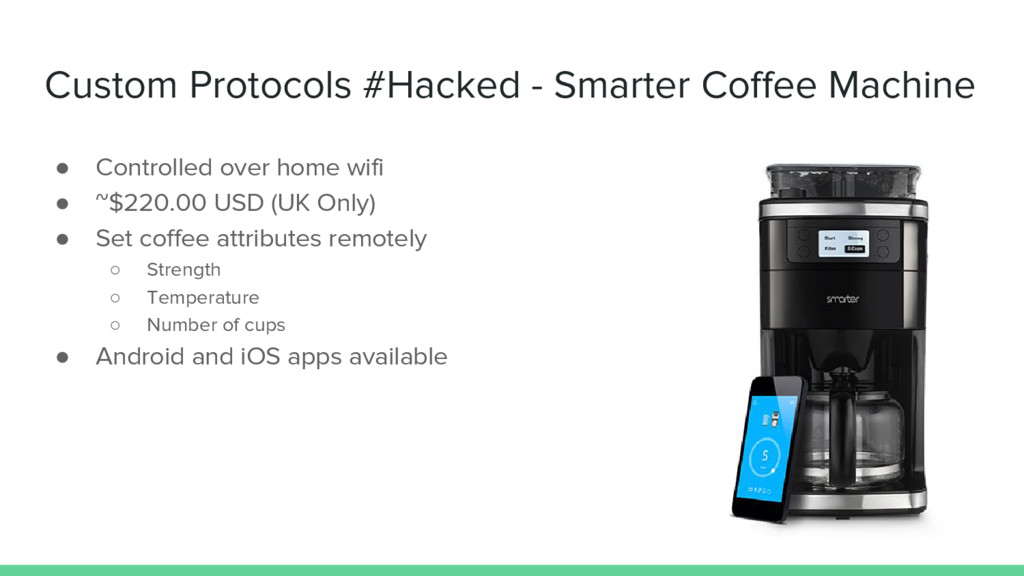
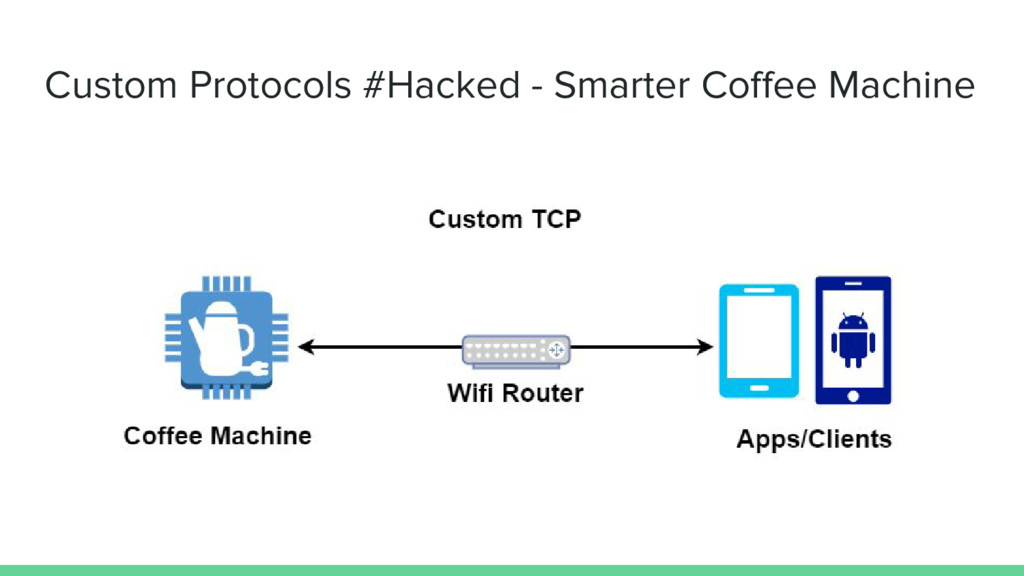
  9. Custom Protocols #Hacked - Smarter Coffee Machine • Controlled over

    home wifi • ~$220.00 USD (UK Only) • Set coffee attributes remotely ◦ Strength ◦ Temperature ◦ Number of cups • Android and iOS apps available
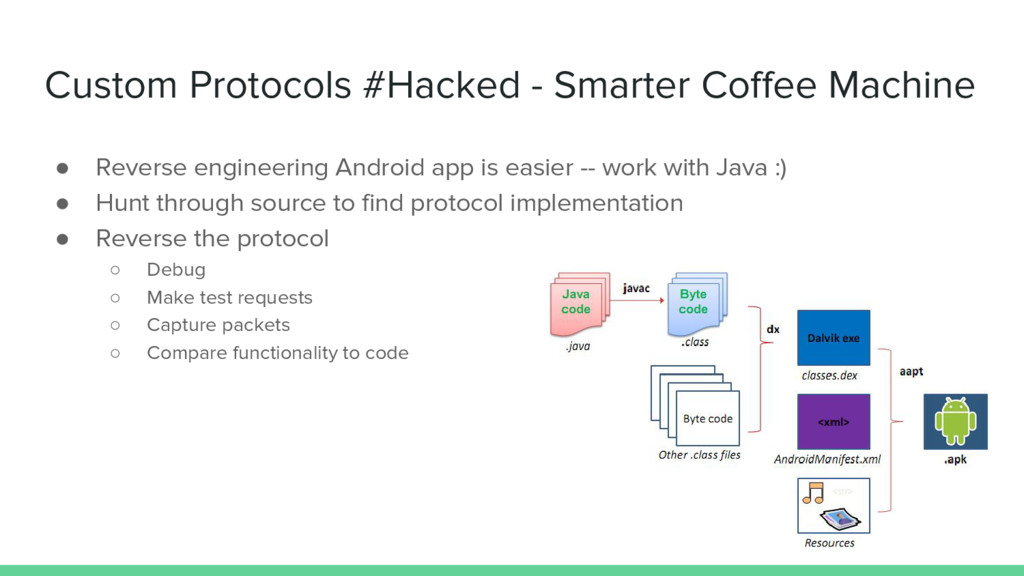
  10. Custom Protocols #Hacked - Smarter Coffee Machine • Reverse engineering

    Android app is easier -- work with Java :) • Hunt through source to find protocol implementation • Reverse the protocol ◦ Debug ◦ Make test requests ◦ Capture packets ◦ Compare functionality to code
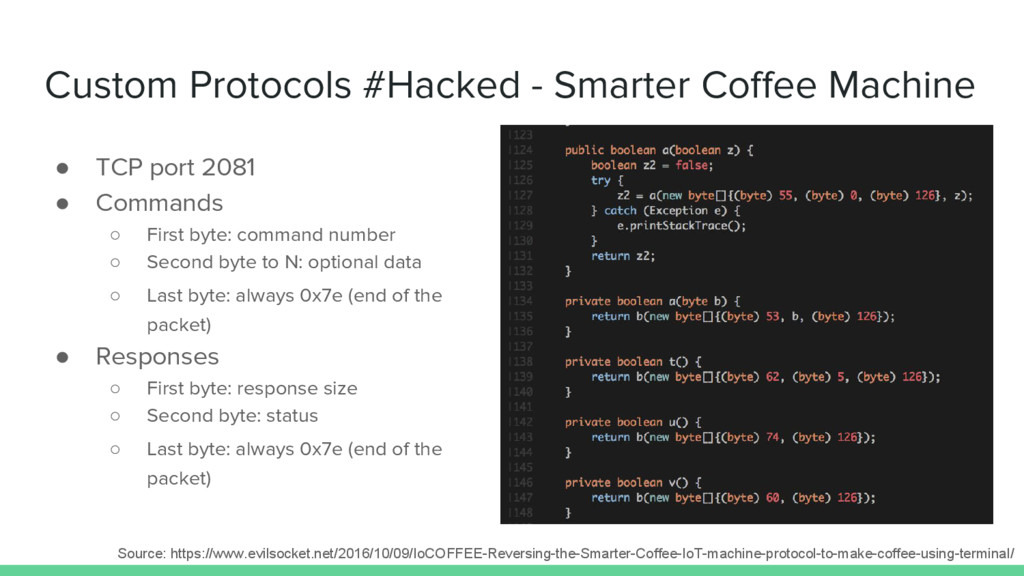
  11. Custom Protocols #Hacked - Smarter Coffee Machine • TCP port

    2081 • Commands ◦ First byte: command number ◦ Second byte to N: optional data ◦ Last byte: always 0x7e (end of the packet) • Responses ◦ First byte: response size ◦ Second byte: status ◦ Last byte: always 0x7e (end of the packet) Source: https://www.evilsocket.net/2016/10/09/IoCOFFEE-Reversing-the-Smarter-Coffee-IoT-machine-protocol-to-make-coffee-using-terminal/
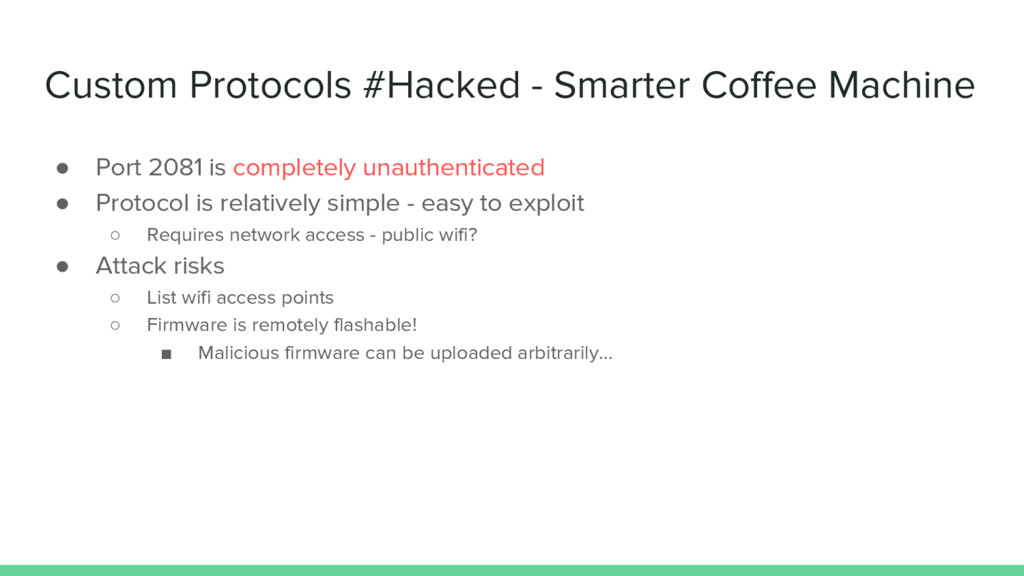
  12. Custom Protocols #Hacked - Smarter Coffee Machine • Port 2081

    is completely unauthenticated • Protocol is relatively simple - easy to exploit ◦ Requires network access - public wifi? • Attack risks ◦ List wifi access points ◦ Firmware is remotely flashable! ▪ Malicious firmware can be uploaded arbitrarily...