Share
Embed
Securing containers
Containers are slowly becoming the standardized units of deployment. As containers become more popular, they also become the focus targets for attacking the system. I talk about the ways in which containers can be attacked and how these attacks can be mitigated
Sathya
June 09, 2018
Transcript
27 slides
-
© 2018 Adobe Systems Incorporated. All Rights Reserved. Securing Containers
Sathyajith Bhat | Senior DevOps Engineer – Adobe I/O -
© 2018 Adobe Systems Incorporated. All Rights Reserved. 2 $whoami
§ Sathyajith Bhat § Senior DevOps Engineer - Adobe I/O § Organizer, Bangalore AWS Users’ Group § Author - Practical Docker with Python -
© 2018 Adobe Systems Incorporated. All Rights Reserved. 3 Run
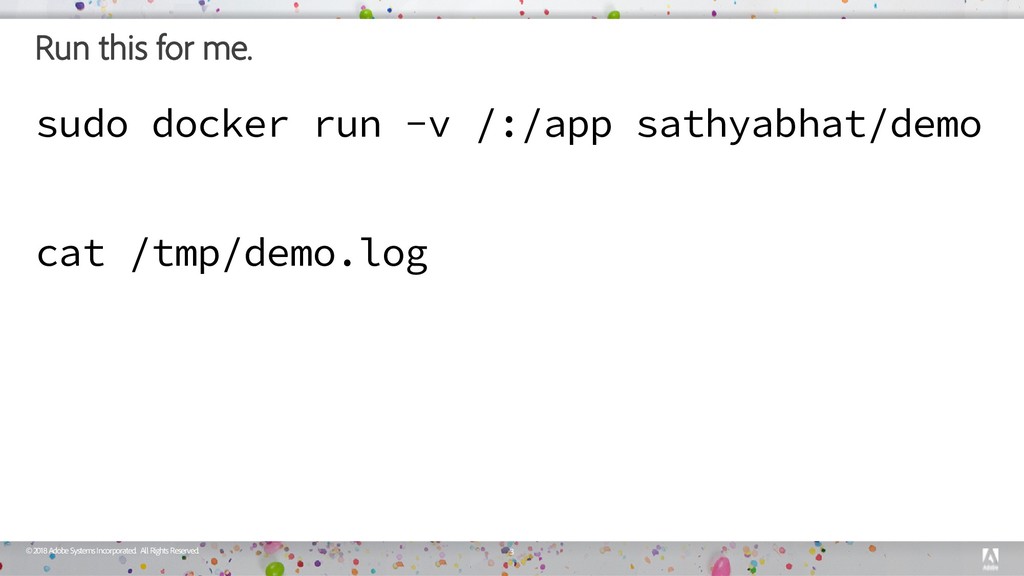
this for me. sudo docker run -v /:/app sathyabhat/demo cat /tmp/demo.log -
© 2018 Adobe Systems Incorporated. All Rights Reserved. 4 Adobe
I/O § Adobe I/O is the place for developers looking to integrate, extend, or create apps and experiences based on Adobe's products and technologies. § Adobe I/O API Gateway § A performant API Gateway based on Nginx and Openresty § 1.5 billion+ API calls per day § Adobe I/O Events § An event notification service to inform subscribing systems of near real-time events happening in Adobe services. § Adobe I/O Runtime § A serverless platform(currently in private beta) based on Apache OpenWhisk which allows a developer to execute code on Adobe's infrastructure. -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Containers -
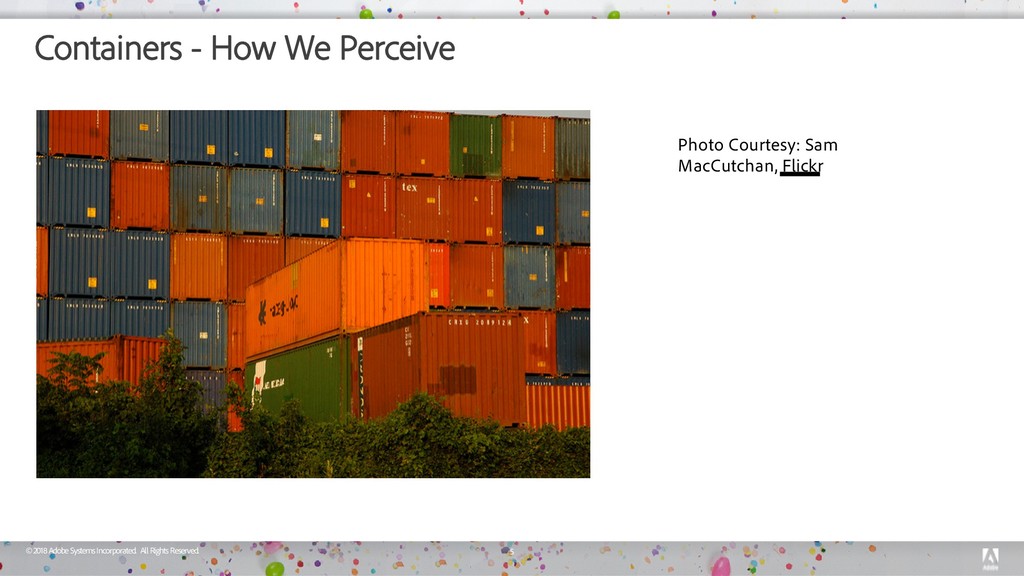
How We Perceive 5 Photo Courtesy: Sam MacCutchan, Flickr -
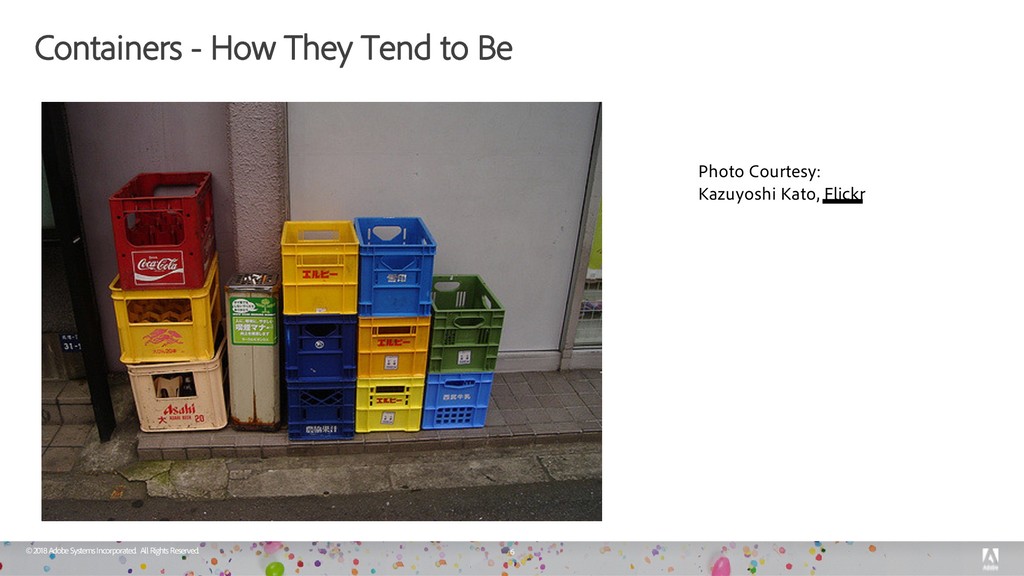
© 2018 Adobe Systems Incorporated. All Rights Reserved. Containers -
How They Tend to Be 6 Photo Courtesy: Kazuyoshi Kato, Flickr -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Threats to
Containers § From Docker Hosts § From noisy neighbours § From within containers § From external world § From within the application 7 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Different mechanisms
§ Control Groups (cgroups) § Namespaces § Kernel Capabilities § Seccomp § Image Security § Vulnerability Scanning 8 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. cgroups §
Group, Limit & isolate resource utilization § Resources that can be controlled: CPU, Memory, Disk, Network § cgroups Docker uses: § Memory § HugeTBL § CPU § CPUSet § BlkIO § Devices § /sys/fs/cgroups 9 -
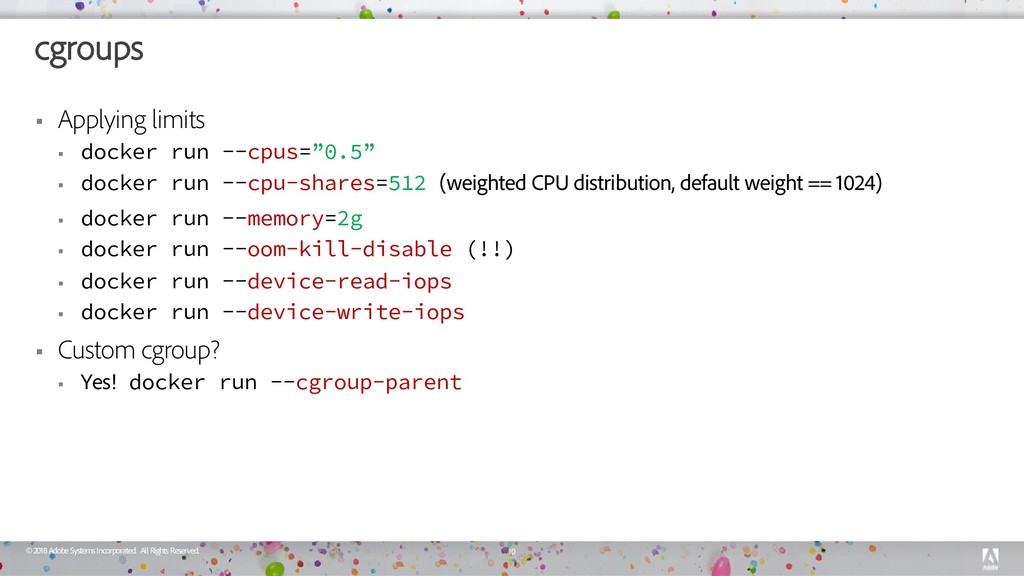
© 2018 Adobe Systems Incorporated. All Rights Reserved. cgroups §
Applying limits § docker run --cpus=”0.5” § docker run --cpu-shares=512 (weighted CPU distribution, default weight == 1024) § docker run --memory=2g § docker run --oom-kill-disable (!!) § docker run --device-read-iops § docker run --device-write-iops § Custom cgroup? § Yes! docker run --cgroup-parent 10 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Namespaces §
Abstraction which makes a process appear they are isolated § Controls what processes can see § Different types of namespaces: § Mount § PID § UTS § IPC § Network § User 11 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Namespaces -
User Namespace Remapping § Remap a user with a container to another user on the Host § Remap privileged user within container to non-privileged one outside host § Enabling remapping: § dockerd --userns-remap=”remap-user:remap-group” § Or, edit daemon.json { userns-remap: “remap-user” } 12 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Namespaces -
User Namespace Remapping Caveats § Ensure the users/groups are created & associated with your user § Enable/Disable it on a new Docker install than existing one § Can no longer user --pid=host or --network=host 13 -
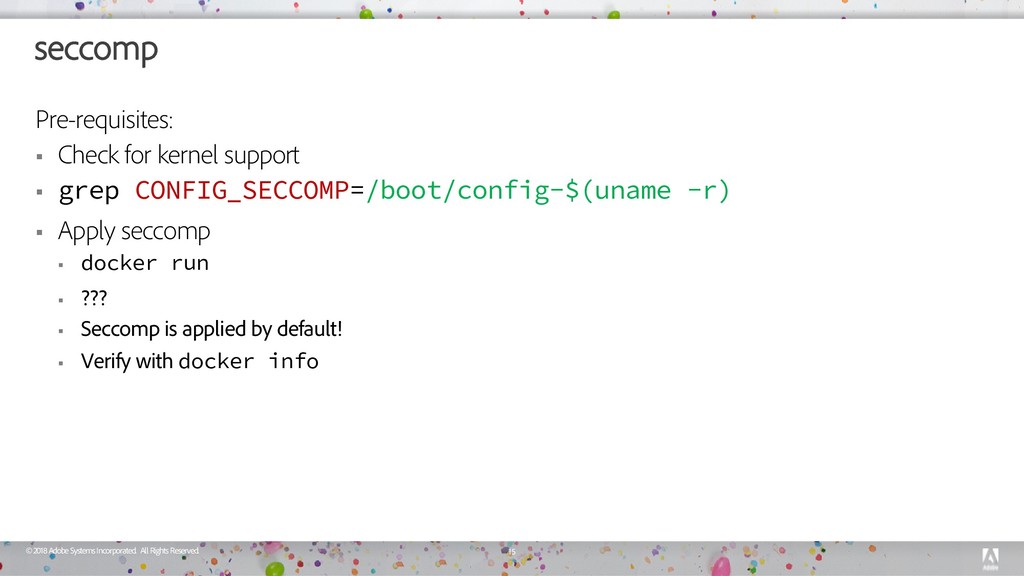
© 2018 Adobe Systems Incorporated. All Rights Reserved. seccomp §
Secure Mode Computing § Kernel feature, restricts syscalls that a process can do § Create custom profiles, pass a different profile for each container § Default seccomp policy for Docker § Disables 44 system calls of 300+ system calls 14 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. seccomp Pre-requisites:
§ Check for kernel support § grep CONFIG_SECCOMP=/boot/config-$(uname -r) § Apply seccomp § docker run § ??? § Seccomp is applied by default! § Verify with docker info 15 -
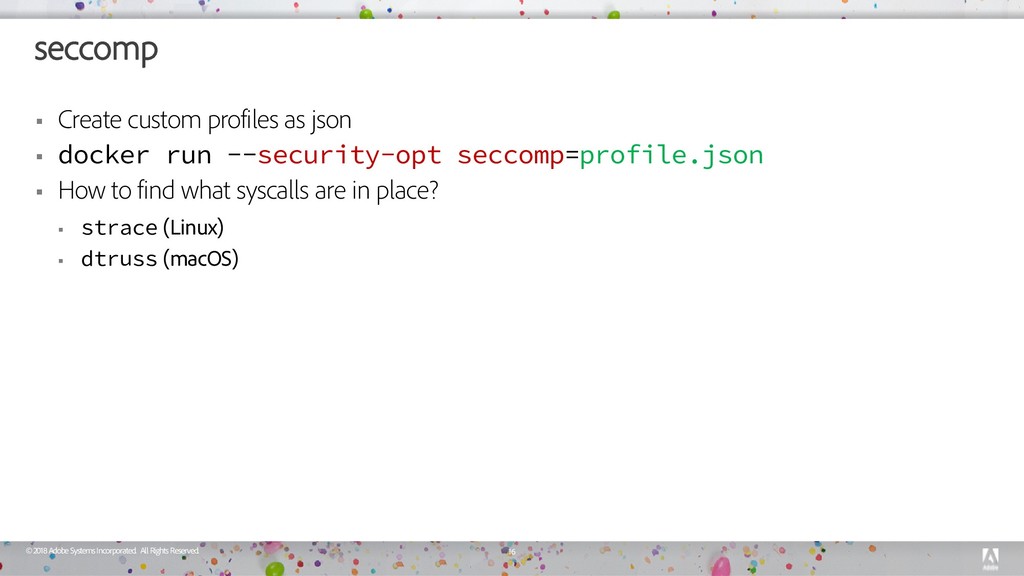
© 2018 Adobe Systems Incorporated. All Rights Reserved. seccomp §
Create custom profiles as json § docker run --security-opt seccomp=profile.json § How to find what syscalls are in place? § strace (Linux) § dtruss (macOS) 16 -
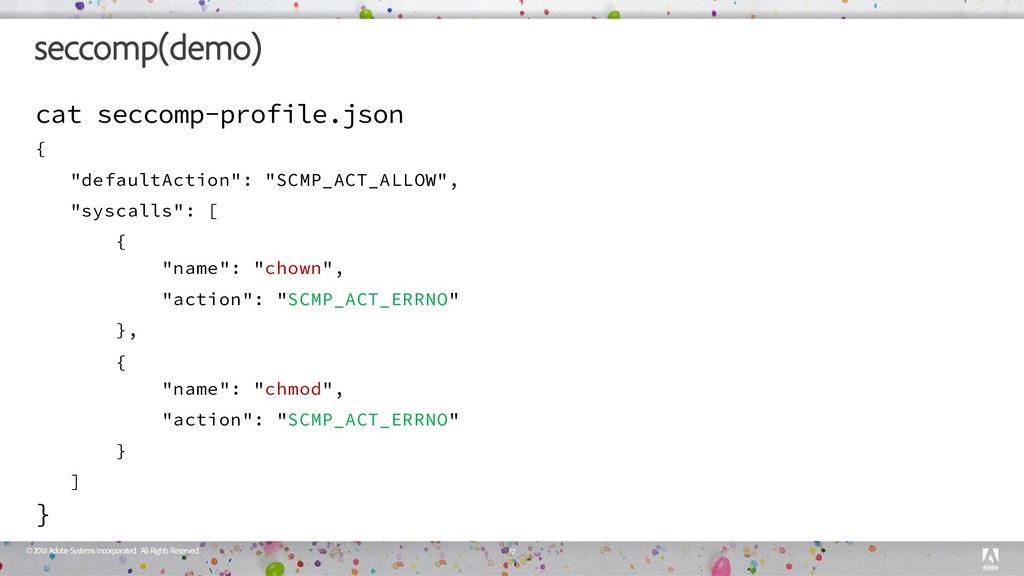
© 2018 Adobe Systems Incorporated. All Rights Reserved. seccomp(demo) cat
seccomp-profile.json { "defaultAction": "SCMP_ACT_ALLOW", "syscalls": [ { "name": "chown", "action": "SCMP_ACT_ERRNO" }, { "name": "chmod", "action": "SCMP_ACT_ERRNO" } ] } 17 -
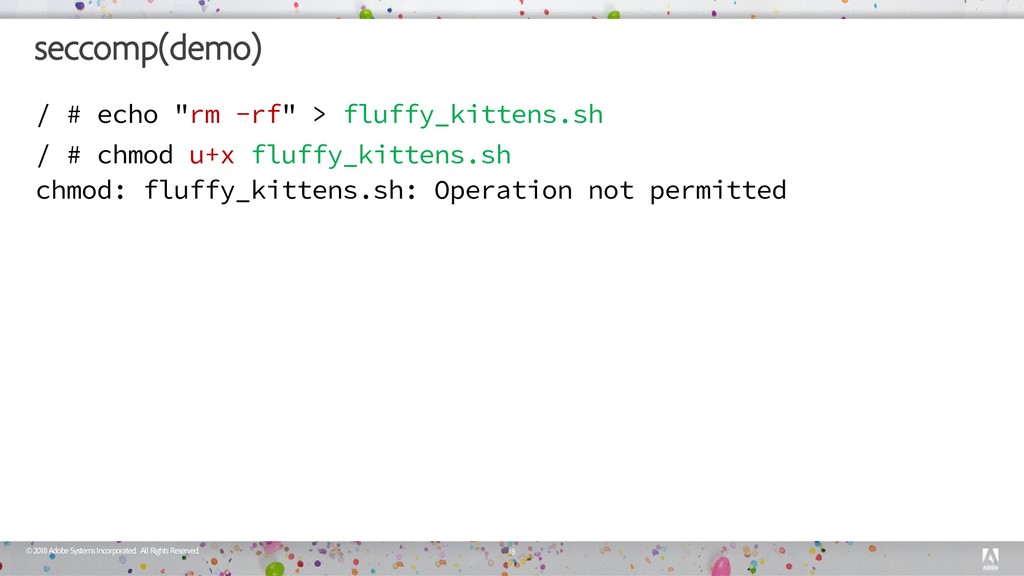
© 2018 Adobe Systems Incorporated. All Rights Reserved. seccomp(demo) /
# echo "rm -rf" > fluffy_kittens.sh / # chmod u+x fluffy_kittens.sh chmod: fluffy_kittens.sh: Operation not permitted 18 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Kernel Capabilities
§ Drop unnecessary capabilities from the container § Alternatively, provide necessary ones § Don’t need chown capability? Drop it § docker run --cap-drop=chown 19 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. AppArmor §
Mandatory Access Control § Why? § Unix permissions allow for R/W/X § No fine grained permissions § Why should your application look at other logs? § Docker expects AppArmor policies to be loaded on Docker host 20 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Managing Vulnerabilities
§ Images are still software - and old, if not rebuilt § Heartbleed § Vulnerability in openSSL § Ghost § Vulnerability in glibc 21 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Managing Vulnerabilities
Vulnerability Scanners § Clair (CoreOS) § Twistlock § Aqua Container Security § Sysdig Falco 22 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Trusted Images
§ Don’t use images blindly § Host the images in private/self-hosted registry § Publishing to Docker Hub? Enable Docker Content Trust 23 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Docker Content
Trust § Enable content trust § export DOCKER_CONTENT_TRUST=1 § Images must have content signatures § Trust is managed by use of signing keys § Offline key: Root of content trust § Repository key for signing tags § Server managed Timestamp key 24 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. References §
Kernel Capabilities § Tutorial on Creating AppArmor Profiles § Docker Security Docs § Sysadmin Casts - Linux Control Groups § Searchable Syscall Table § Google Chrome Seccomp Sandbox Implementation Doc § User Namespaces in Docker Engine 25 -
© 2018 Adobe Systems Incorporated. All Rights Reserved. Thanks! §
Twitter - sathyabhat § Email: [email protected] § https://www.adobe.io | @adobeio 26