Upgrade to Pro — share decks privately, control downloads, hide ads and more …

[AWS Expert Online for JAWS-UG 39] Amazon Guard...

Avatar for Hibiki Sato Hibiki Sato
September 16, 2026

[AWS Expert Online for JAWS-UG 39] Amazon GuardDuty 検出結果の読み方 - いつもの操作がなぜ検出された? 確認観点の勘所

GuardDuty の検出結果で、特に末尾がAnomalousBehavior の検出結果タイプについて、確認すべき観点を実際の検出結果 JSON を参考に紹介します。

Avatar for Hibiki Sato

Hibiki Sato

September 16, 2026

Other Decks in Technology

Transcript

  1. 2026/09 AWS EXPERT ONLINE FOR JAWS-UG Amazon GuardDuty 検出結果の読み方 いつもの操作がなぜ検出された?

    確認観点の勘所 佐藤 響貴 Cloud Support Engineer / AWS Japan © 2026, Amazon Services, Inc. its affiliates. All rights reserved. © 2026,Web Amazon Web Services, Inc. or or its affiliates. All rights reserved. 1
  2. 自己紹介 佐藤 響貴 アマゾン ウェブ サービス ジャパン合同会社 PHOTO 技術支援本部 クラウドサポートエンジニア

    主な担当サービス Amazon GuardDuty Amazon Inspector © 2026, Amazon Services, Inc. its affiliates. All rights reserved. © 2026,Web Amazon Web Services, Inc. or or its affiliates. All rights reserved. AWS Security Hub 2
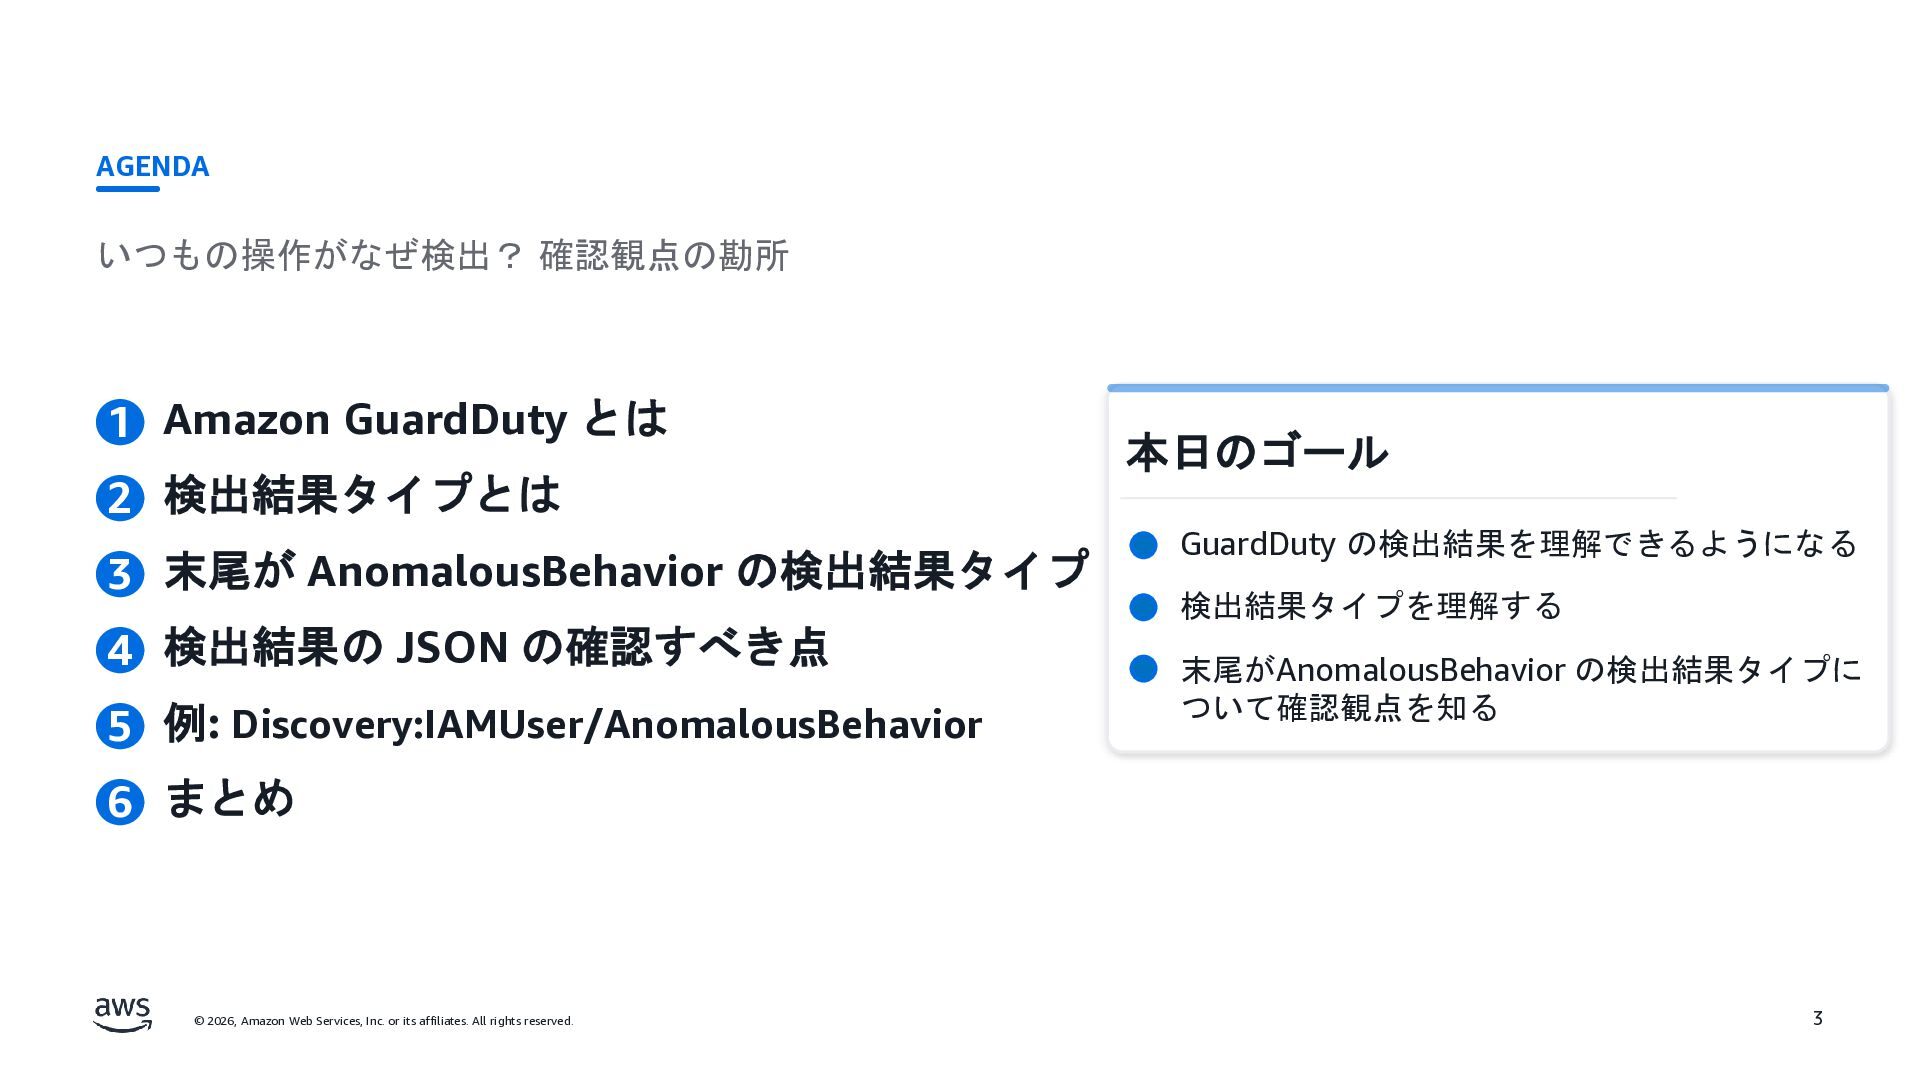
  3. AGENDA いつもの操作がなぜ検出? 確認観点の勘所 1 Amazon GuardDuty とは 2 検出結果タイプとは 3

    末尾が AnomalousBehavior の検出結果タイプ 4 検出結果の JSON の確認すべき点 5 例: Discovery:IAMUser/AnomalousBehavior 本日のゴール GuardDuty の検出結果を理解できるようになる 検出結果タイプを理解する 末尾がAnomalousBehavior の検出結果タイプに ついて確認観点を知る 6 まとめ © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 3
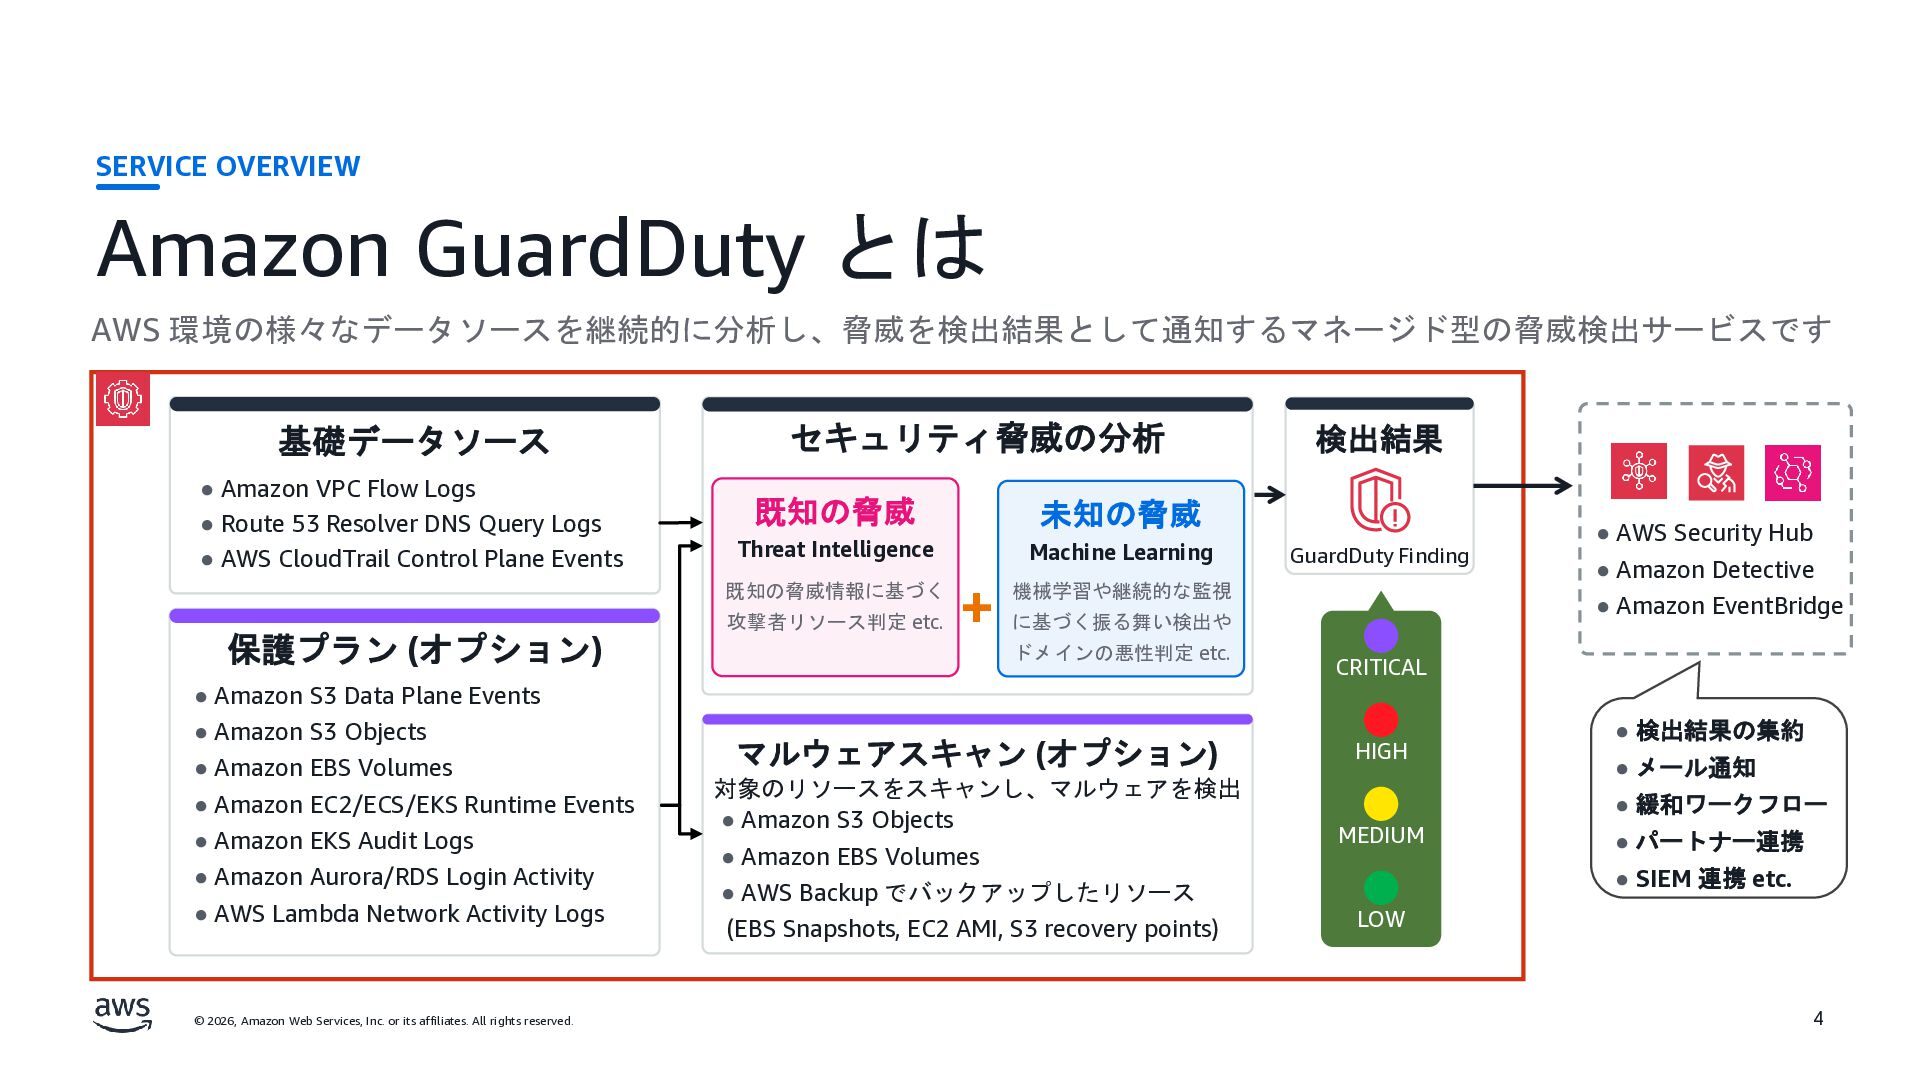
  4. SERVICE OVERVIEW Amazon GuardDuty とは AWS 環境の様々なデータソースを継続的に分析し、脅威を検出結果として通知するマネージド型の脅威検出サービスです 基礎データソース • Amazon

    VPC Flow Logs • Route 53 Resolver DNS Query Logs • AWS CloudTrail Control Plane Events セキュリティ脅威の分析 既知の脅威 未知の脅威 Threat Intelligence Machine Learning 既知の脅威情報に基づく 保護プラン (オプション) 攻撃者リソース判定 etc. + 検出結果 GuardDuty Finding 機械学習や継続的な監視 • Amazon Detective • Amazon EventBridge に基づく振る舞い検出や ドメインの悪性判定 etc. • AWS Security Hub CRITICAL • Amazon S3 Data Plane Events • Amazon S3 Objects • Amazon EBS Volumes • Amazon EC2/ECS/EKS Runtime Events • Amazon EKS Audit Logs • Amazon Aurora/RDS Login Activity • AWS Lambda Network Activity Logs © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. マルウェアスキャン (オプション) 対象のリソースをスキャンし、マルウェアを検出 • Amazon S3 Objects • Amazon EBS Volumes • AWS Backup でバックアップしたリソース (EBS Snapshots, EC2 AMI, S3 recovery points) HIGH • 検出結果の集約 • メール通知 • 緩和ワークフロー MEDIUM • パートナー連携 • SIEM 連携 etc. LOW 4
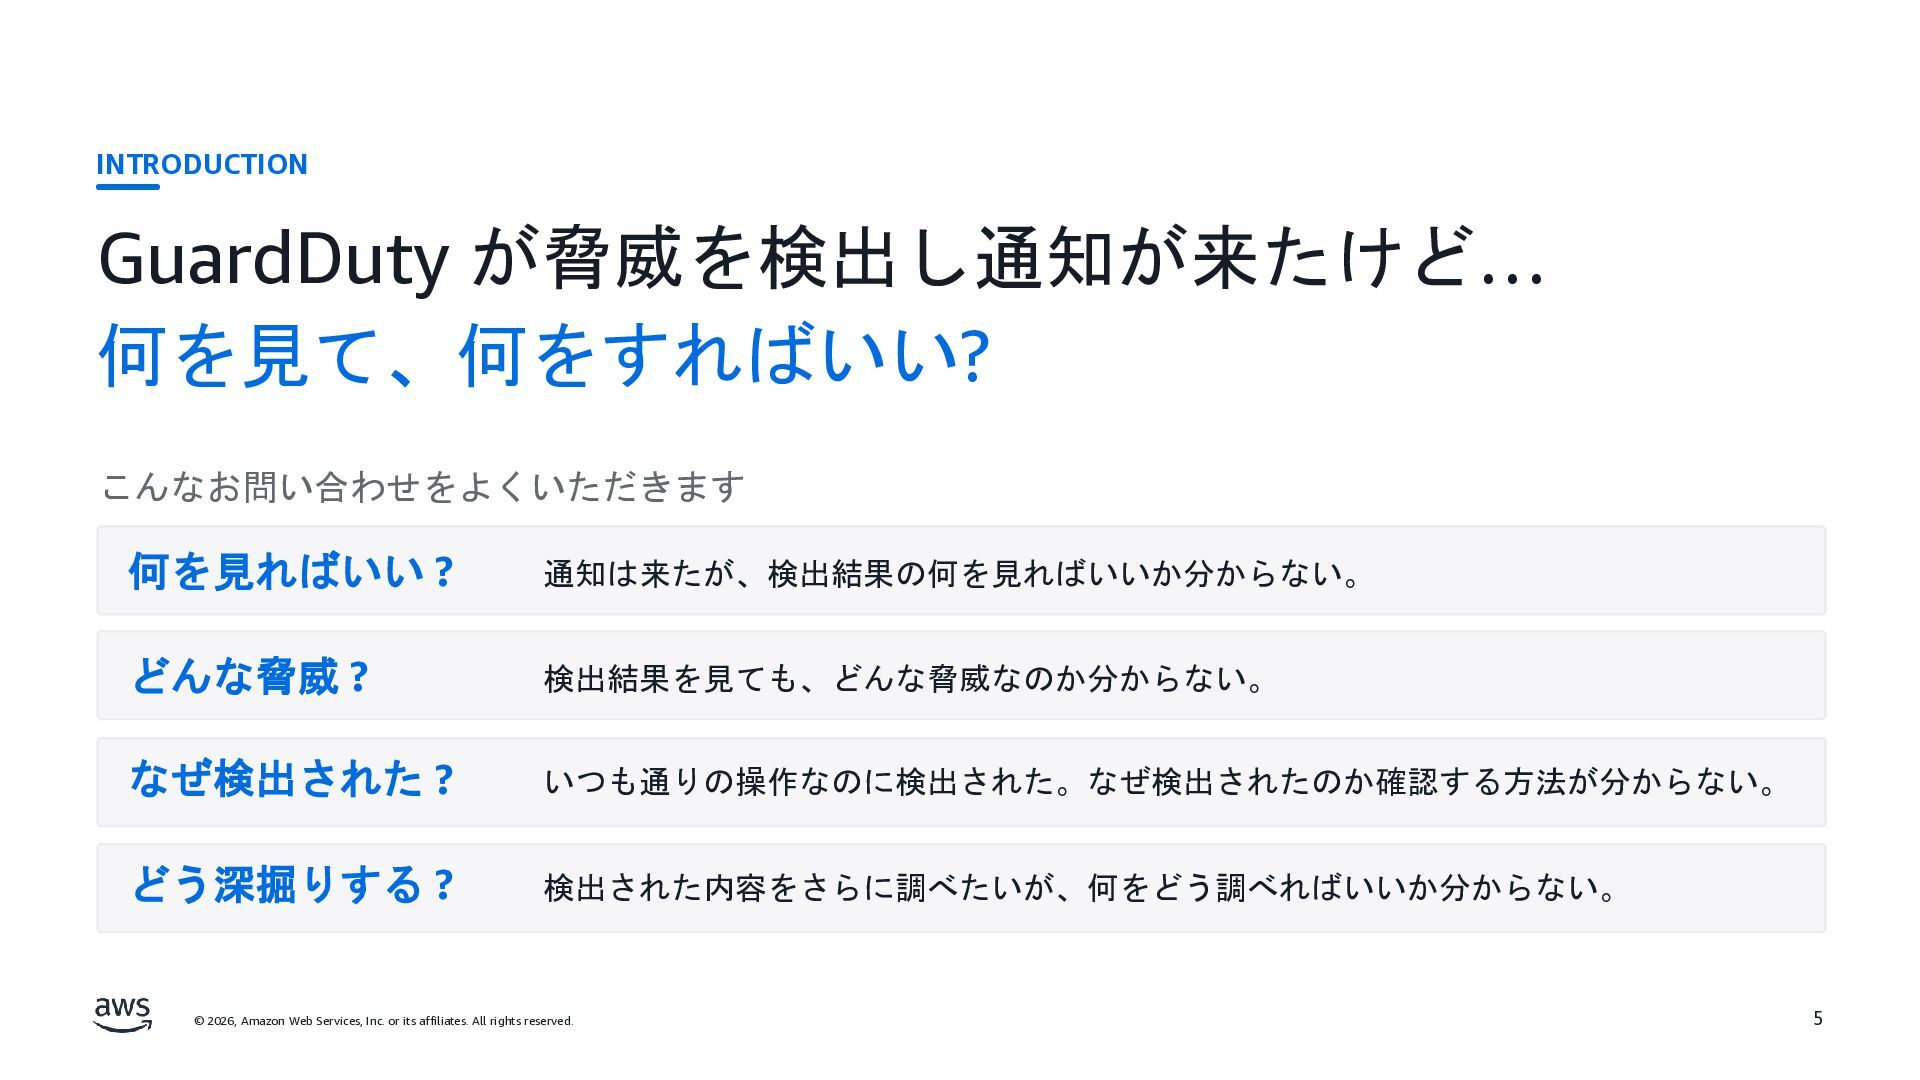
  5. INTRODUCTION GuardDuty が脅威を検出し通知が来たけど… 何を見て、何をすればいい? こんなお問い合わせをよくいただきます 何を見ればいい ? 通知は来たが、検出結果の何を見ればいいか分からない。 どんな脅威 ?

    検出結果を見ても、どんな脅威なのか分からない。 なぜ検出された ? いつも通りの操作なのに検出された。なぜ検出されたのか確認する方法が分からない。 どう深掘りする ? 検出された内容をさらに調べたいが、何をどう調べればいいか分からない。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 5
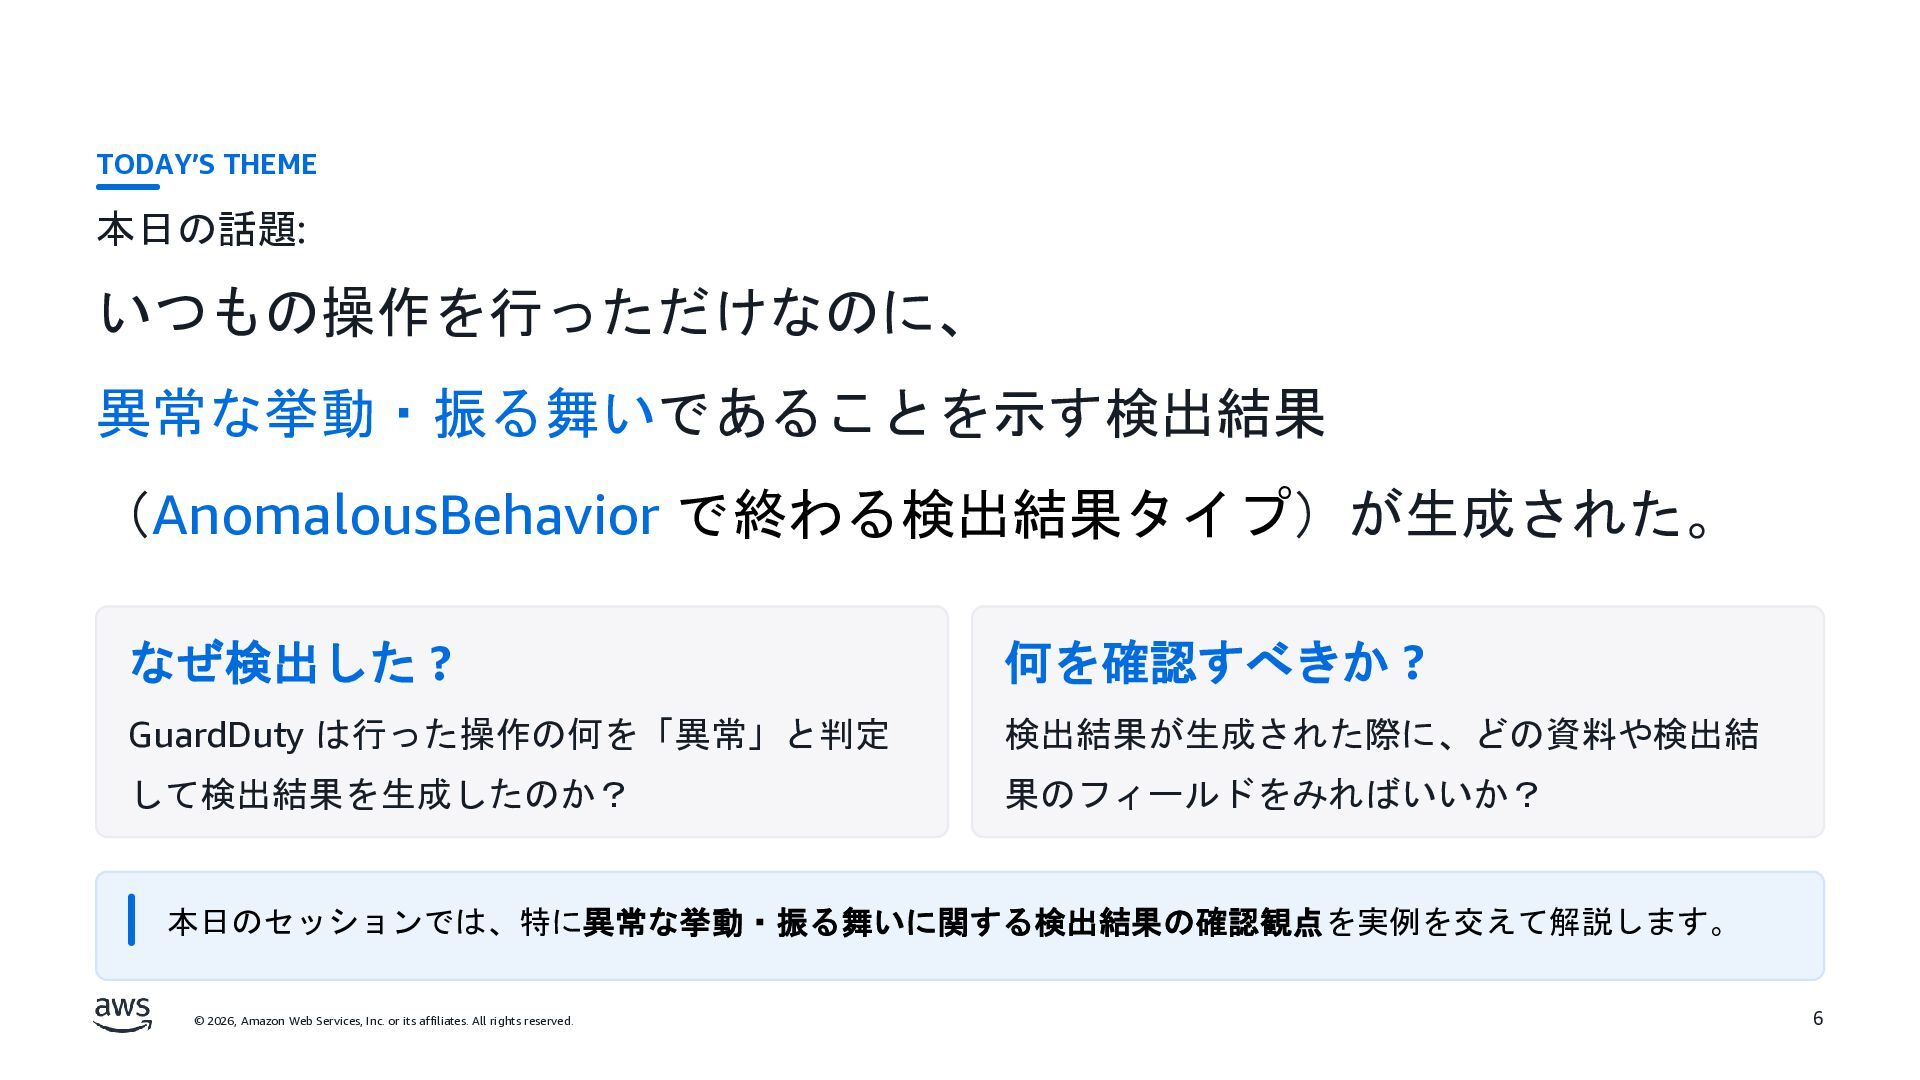
  6. TODAY’S THEME 本日の話題: いつもの操作を行っただけなのに、 異常な挙動・振る舞いであることを示す検出結果 (AnomalousBehavior で終わる検出結果タイプ)が生成された。 なぜ検出した ? 何を確認すべきか

    ? GuardDuty は行った操作の何を「異常」と判定 検出結果が生成された際に、どの資料や検出結 して検出結果を生成したのか? 果のフィールドをみればいいか? 本日のセッションでは、特に異常な挙動・振る舞いに関する検出結果の確認観点を実例を交えて解説します。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 6
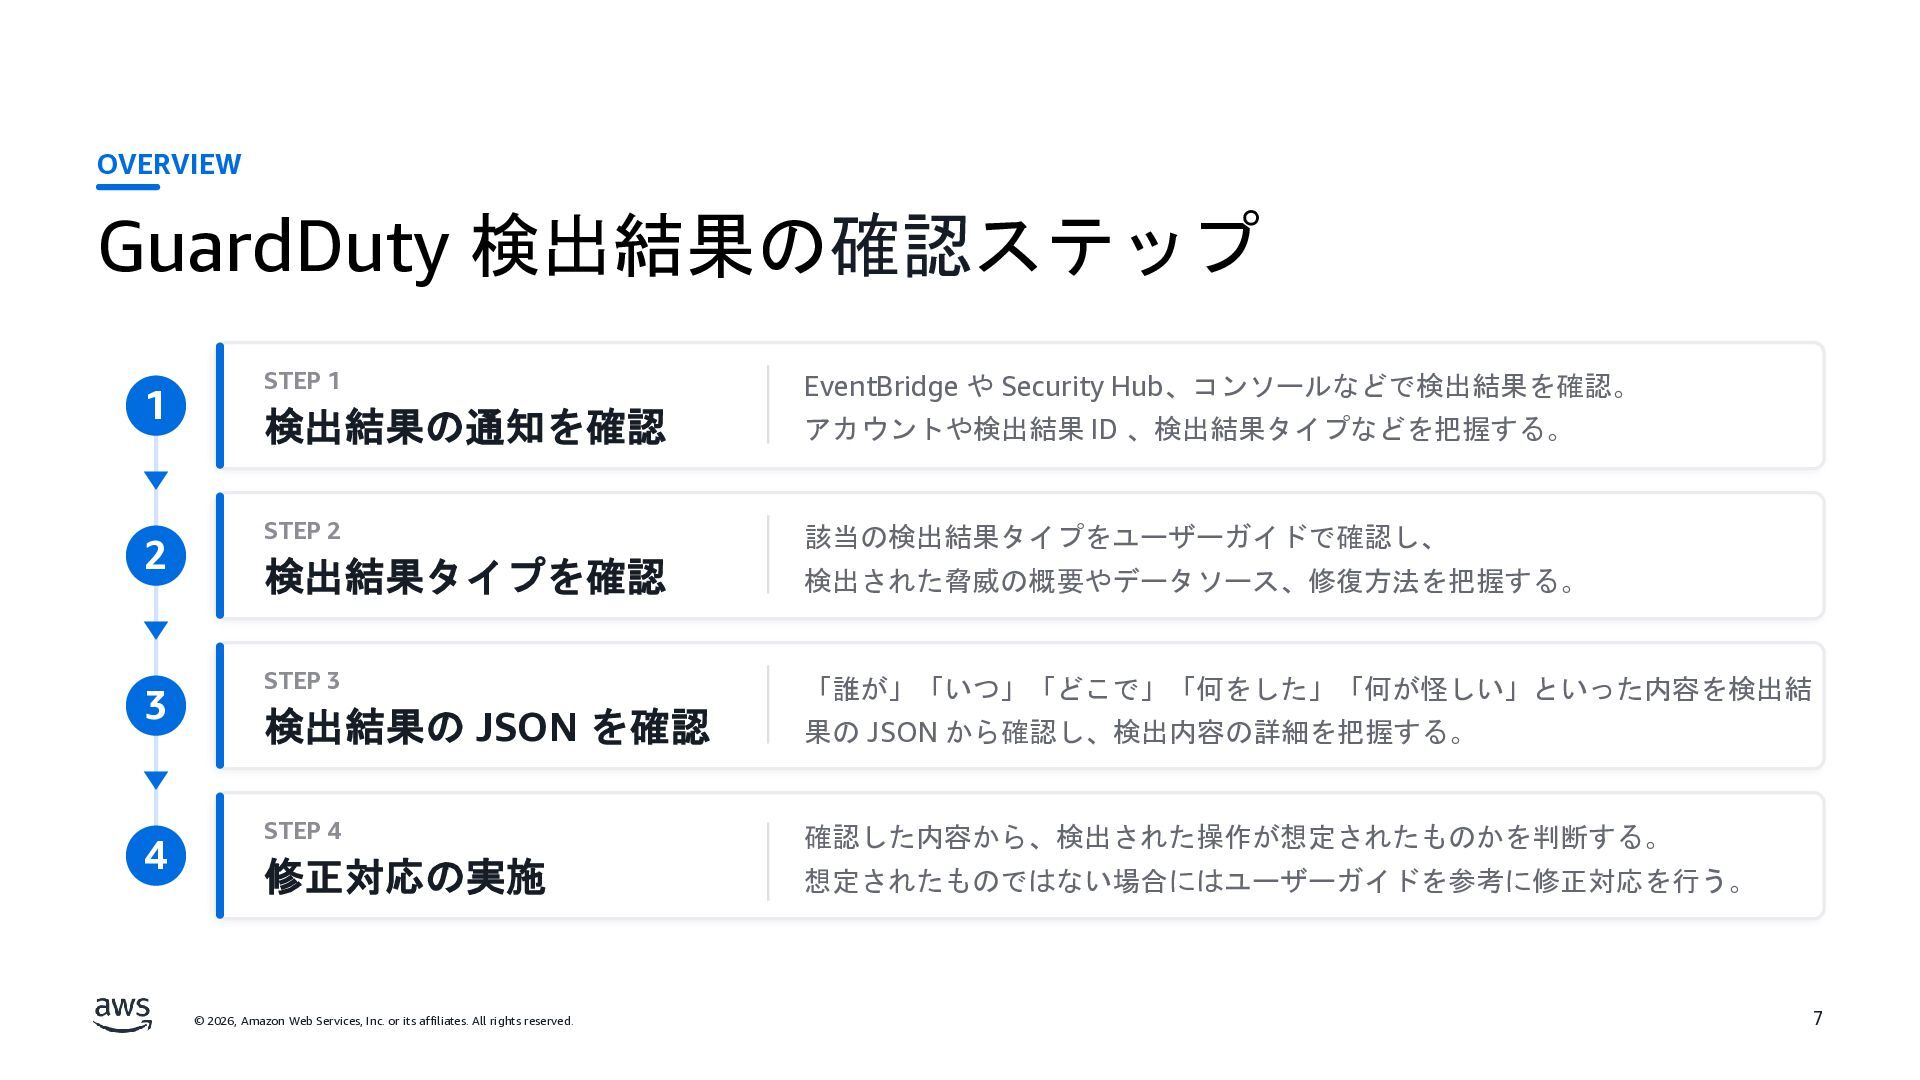
  7. OVERVIEW GuardDuty 検出結果の確認ステップ 1 2 3 4 STEP 1 EventBridge

    や Security Hub、コンソールなどで検出結果を確認。 検出結果の通知を確認 アカウントや検出結果 ID 、検出結果タイプなどを把握する。 STEP 2 該当の検出結果タイプをユーザーガイドで確認し、 検出結果タイプを確認 検出された脅威の概要やデータソース、修復方法を把握する。 STEP 3 「誰が」「いつ」「どこで」「何をした」「何が怪しい」といった内容を検出結 検出結果の JSON を確認 果の JSON から確認し、検出内容の詳細を把握する。 STEP 4 確認した内容から、検出された操作が想定されたものかを判断する。 修正対応の実施 想定されたものではない場合にはユーザーガイドを参考に修正対応を行う。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 7
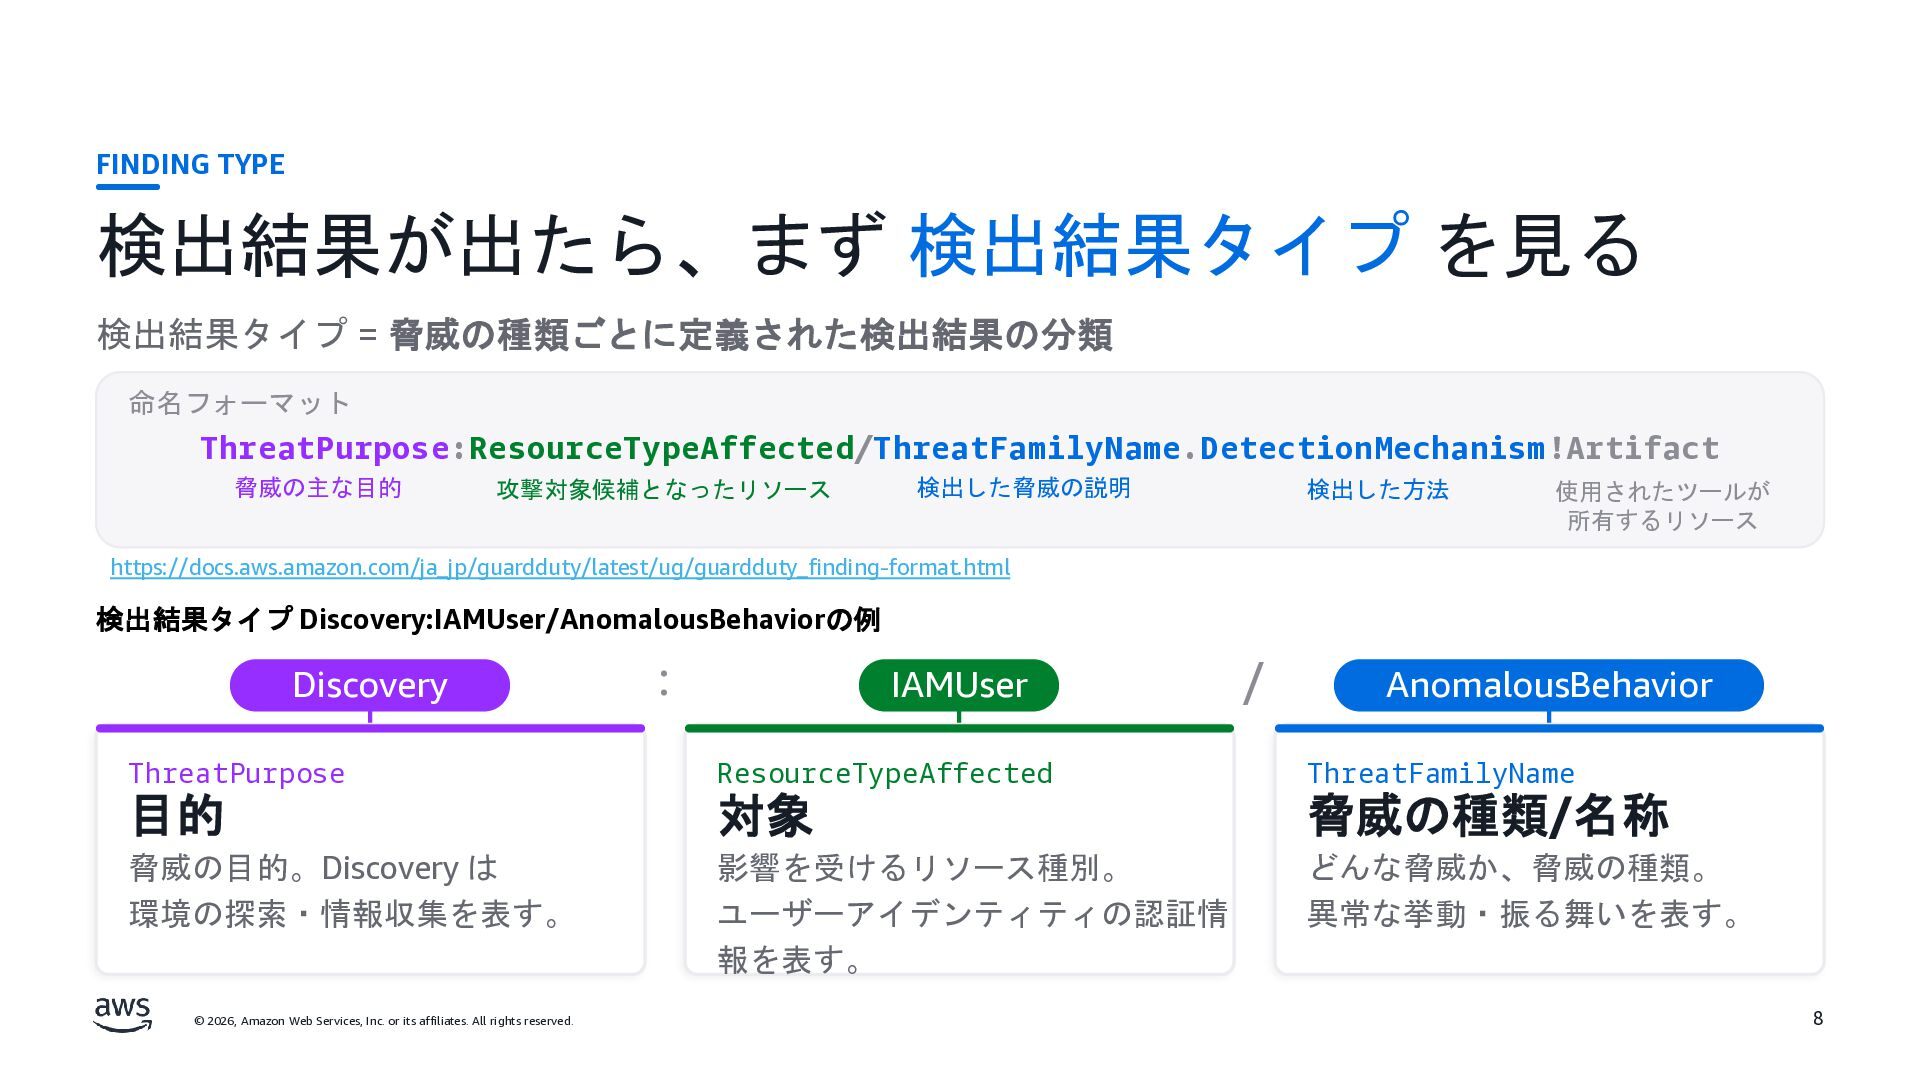
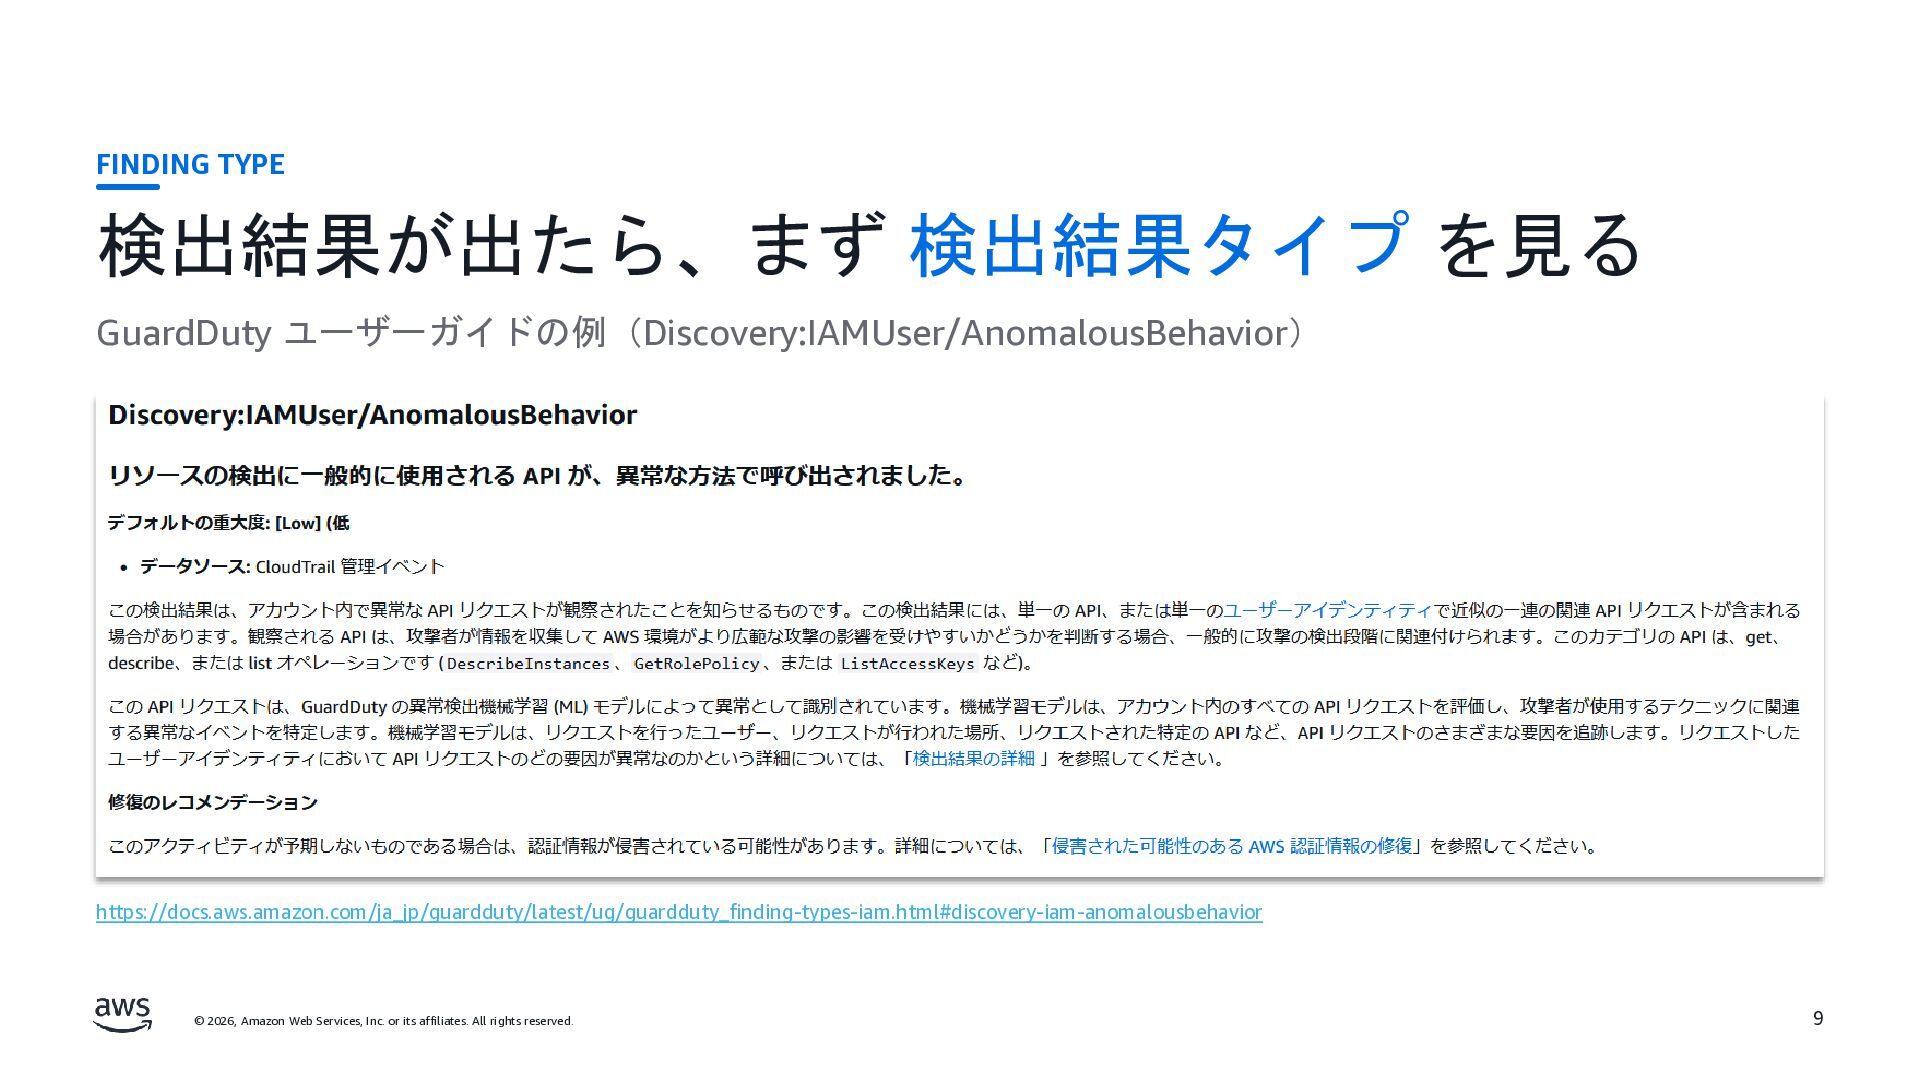
  8. FINDING TYPE 検出結果が出たら、まず 検出結果タイプ を見る 検出結果タイプ = 脅威の種類ごとに定義された検出結果の分類 命名フォーマット ThreatPurpose:ResourceTypeAffected/ThreatFamilyName.DetectionMechanism!Artifact

    脅威の主な目的 攻撃対象候補となったリソース 検出した脅威の説明 検出した方法 使用されたツールが 所有するリソース https://docs.aws.amazon.com/ja_jp/guardduty/latest/ug/guardduty_finding-format.html 検出結果タイプ Discovery:IAMUser/AnomalousBehaviorの例 Discovery : IAMUser / AnomalousBehavior ThreatPurpose ResourceTypeAffected ThreatFamilyName 目的 対象 脅威の種類/名称 脅威の目的。Discovery は 環境の探索・情報収集を表す。 影響を受けるリソース種別。 ユーザーアイデンティティの認証情 報を表す。 どんな脅威か、脅威の種類。 異常な挙動・振る舞いを表す。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 8
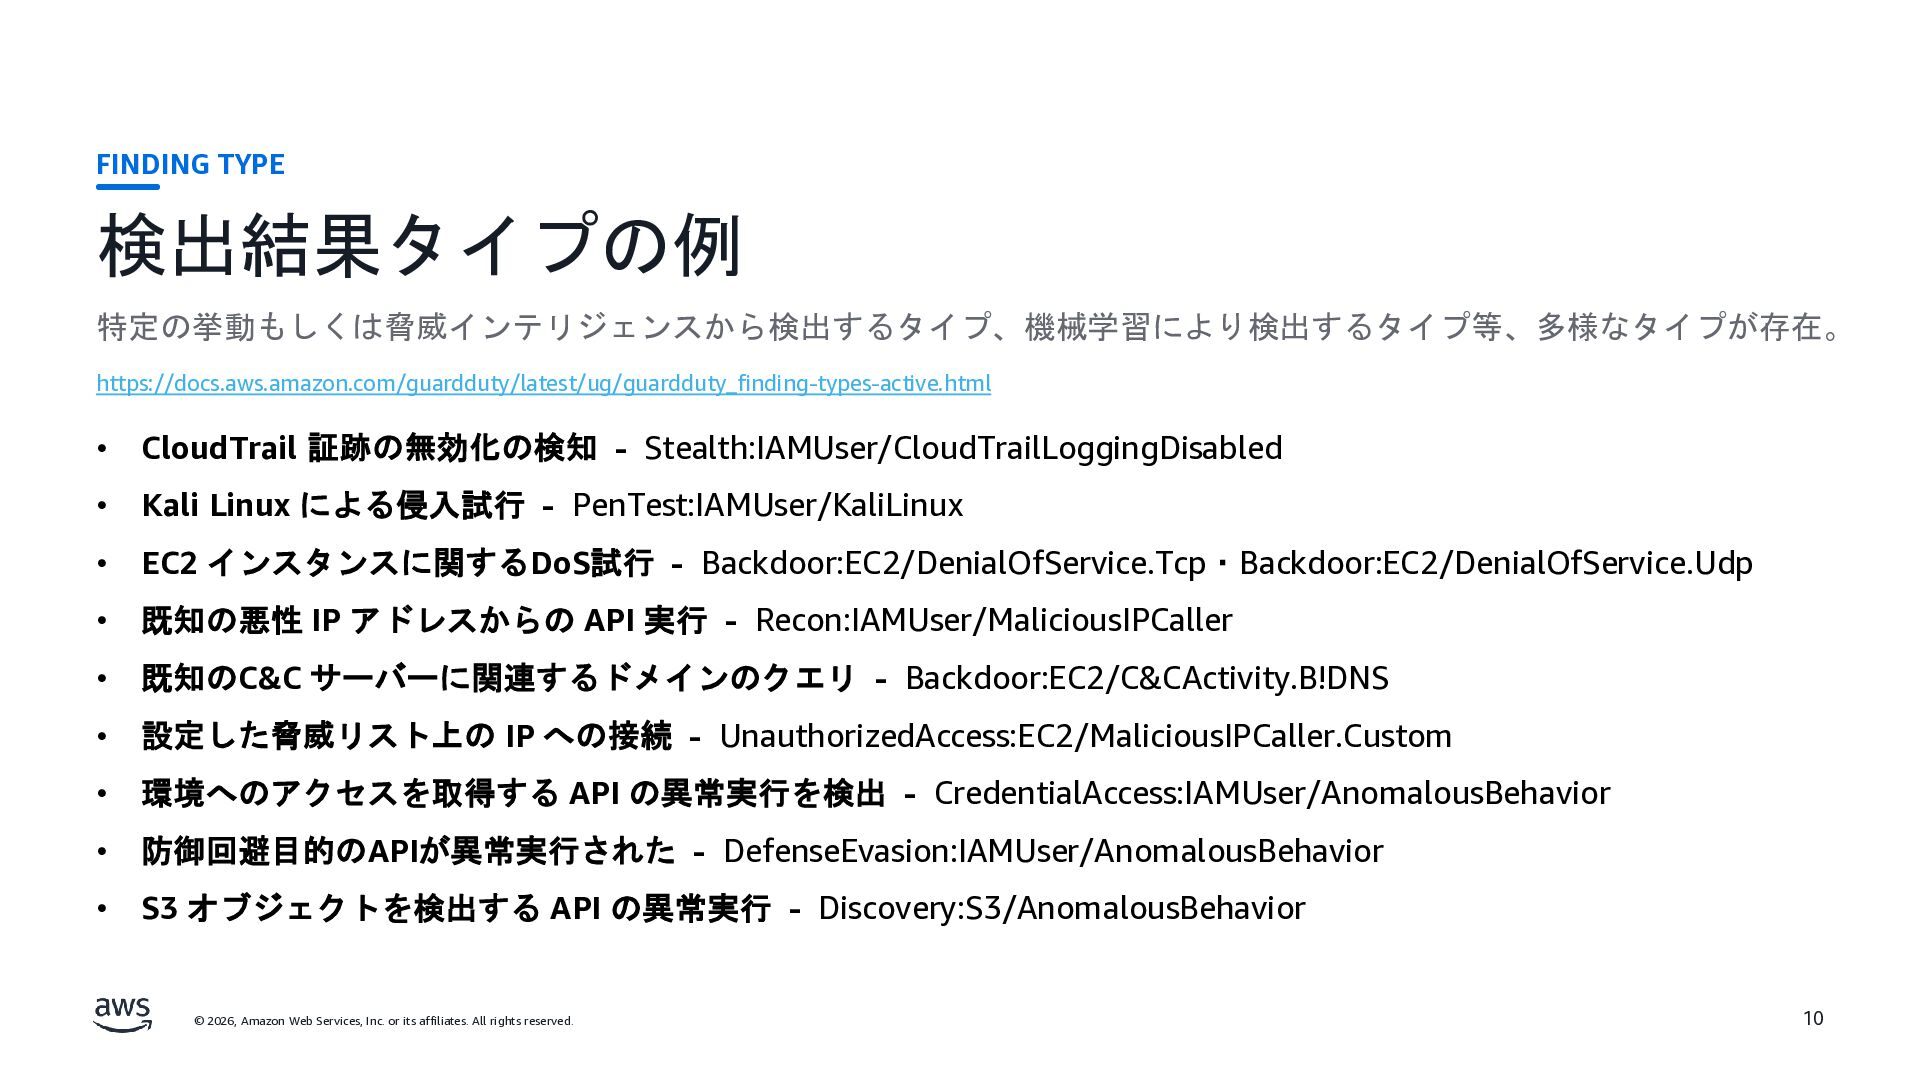
  9. FINDING TYPE 検出結果タイプの例 特定の挙動もしくは脅威インテリジェンスから検出するタイプ、機械学習により検出するタイプ等、多様なタイプが存在。 https://docs.aws.amazon.com/guardduty/latest/ug/guardduty_finding-types-active.html • CloudTrail 証跡の無効化の検知 - Stealth:IAMUser/CloudTrailLoggingDisabled

    • Kali Linux による侵入試行 - PenTest:IAMUser/KaliLinux • EC2 インスタンスに関するDoS試行 - Backdoor:EC2/DenialOfService.Tcp・Backdoor:EC2/DenialOfService.Udp • 既知の悪性 IP アドレスからの API 実行 - Recon:IAMUser/MaliciousIPCaller • 既知のC&C サーバーに関連するドメインのクエリ - Backdoor:EC2/C&CActivity.B!DNS • 設定した脅威リスト上の IP への接続 - UnauthorizedAccess:EC2/MaliciousIPCaller.Custom • 環境へのアクセスを取得する API の異常実行を検出 - CredentialAccess:IAMUser/AnomalousBehavior • 防御回避目的のAPIが異常実行された - DefenseEvasion:IAMUser/AnomalousBehavior • S3 オブジェクトを検出する API の異常実行 - Discovery:S3/AnomalousBehavior © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 10
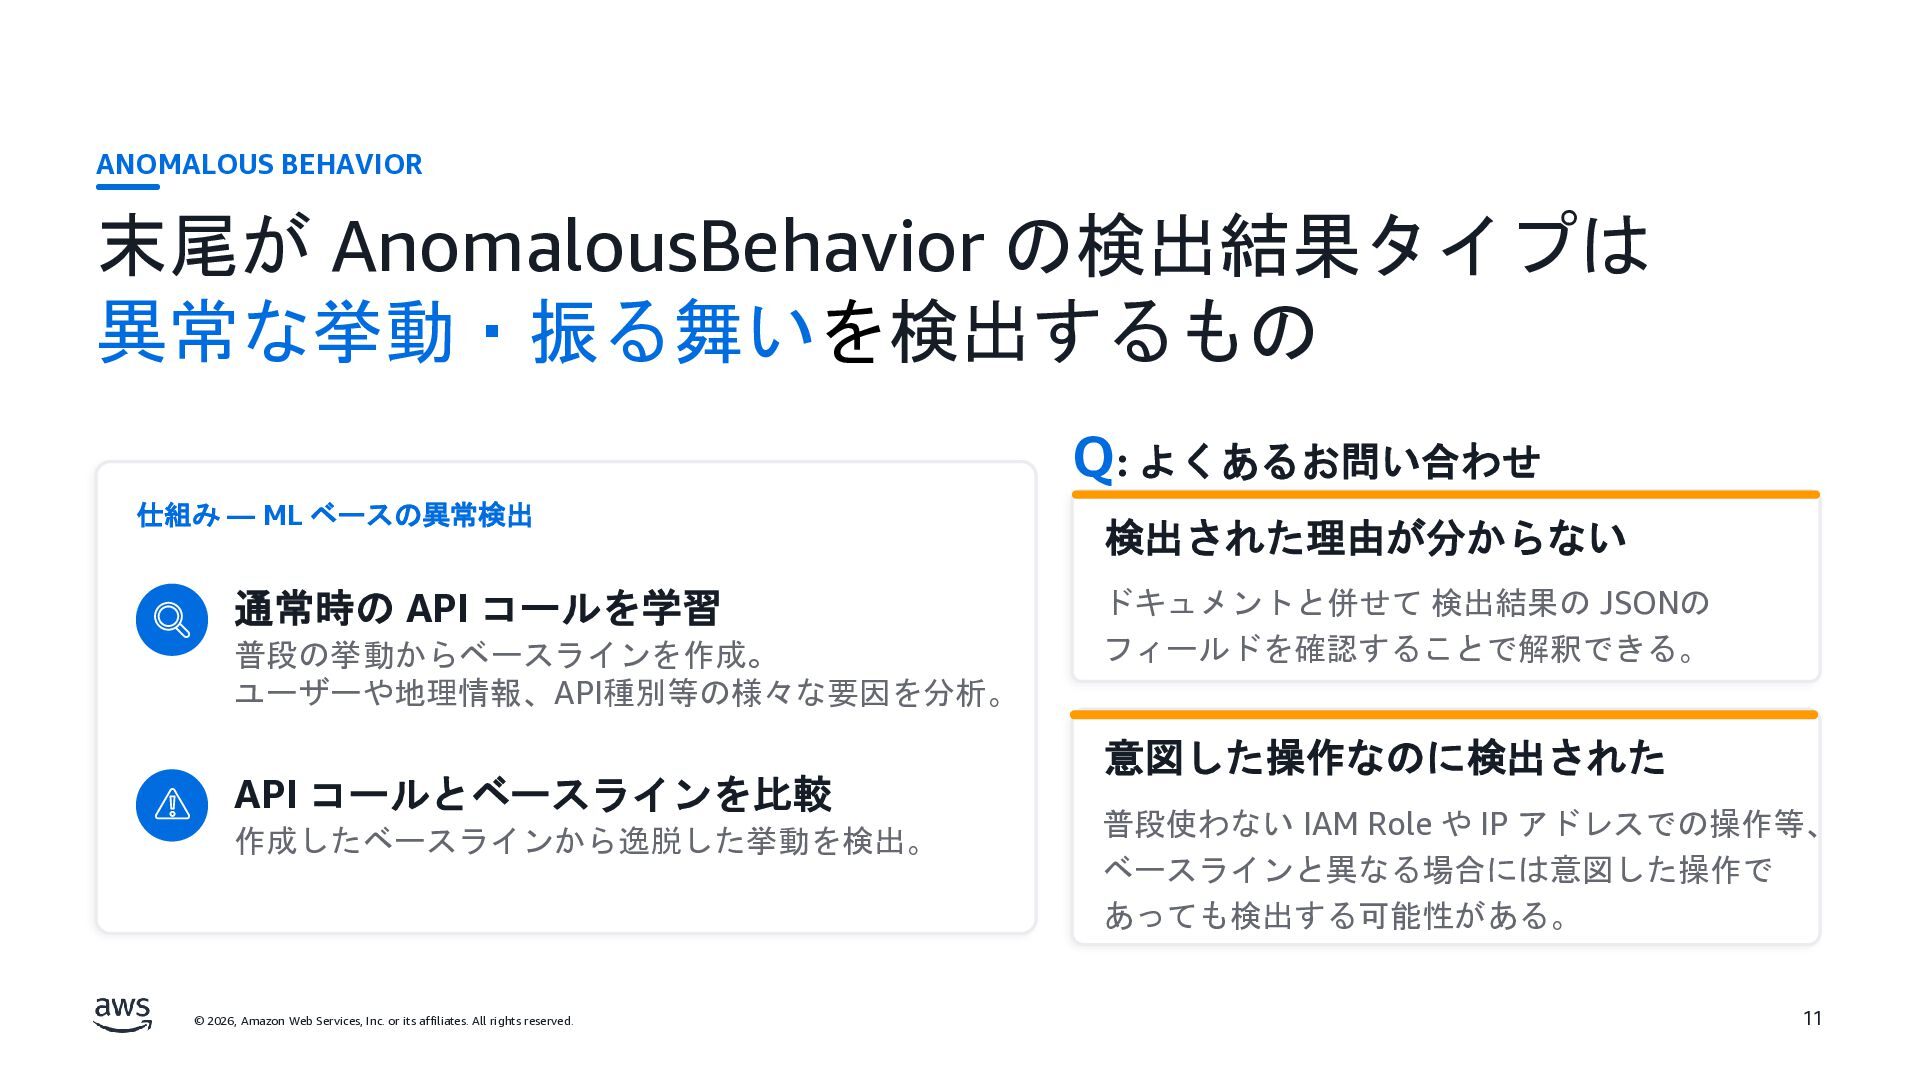
  10. ANOMALOUS BEHAVIOR 末尾が AnomalousBehavior の検出結果タイプは 異常な挙動・振る舞いを検出するもの Q: よくあるお問い合わせ 仕組み —

    ML ベースの異常検出 通常時の API コールを学習 普段の挙動からベースラインを作成。 ユーザーや地理情報、API種別等の様々な要因を分析。 API コールとベースラインを比較 作成したベースラインから逸脱した挙動を検出。 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 検出された理由が分からない ドキュメントと併せて 検出結果の JSONの フィールドを確認することで解釈できる。 意図した操作なのに検出された 普段使わない IAM Role や IP アドレスでの操作等、 ベースラインと異なる場合には意図した操作で あっても検出する可能性がある。 11
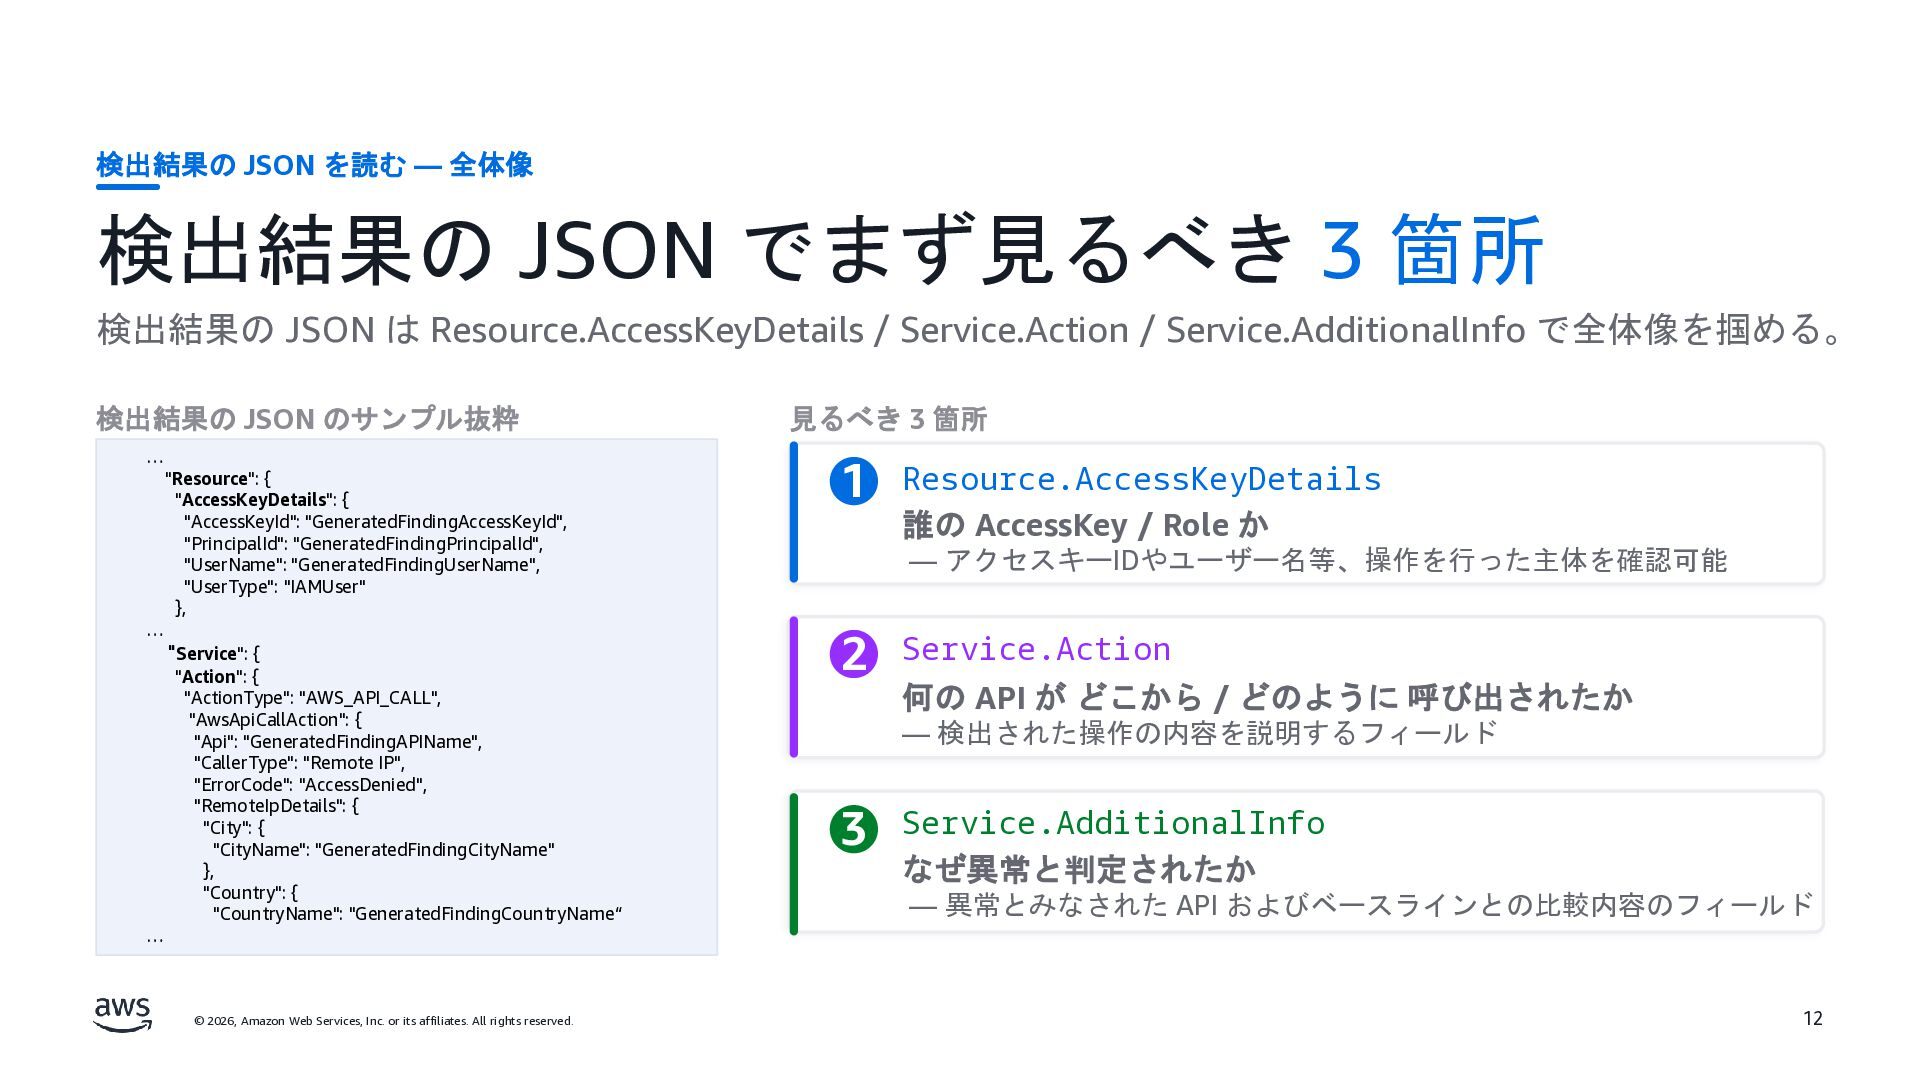
  11. 検出結果の JSON を読む — 全体像 検出結果の JSON でまず見るべき 3 箇所

    検出結果の JSON は Resource.AccessKeyDetails / Service.Action / Service.AdditionalInfo で全体像を掴める。 検出結果の JSON のサンプル抜粋 … "Resource": { "AccessKeyDetails": { "AccessKeyId": "GeneratedFindingAccessKeyId", "PrincipalId": "GeneratedFindingPrincipalId", "UserName": "GeneratedFindingUserName", "UserType": "IAMUser" }, … "Service": { "Action": { "ActionType": "AWS_API_CALL", "AwsApiCallAction": { "Api": "GeneratedFindingAPIName", "CallerType": "Remote IP", "ErrorCode": "AccessDenied", "RemoteIpDetails": { "City": { "CityName": "GeneratedFindingCityName" }, "Country": { "CountryName": "GeneratedFindingCountryName“ 見るべき 3 箇所 1 Resource.AccessKeyDetails 誰の AccessKey / Role か — アクセスキーIDやユーザー名等、操作を行った主体を確認可能 2 Service.Action 何の API が どこから / どのように 呼び出されたか — 検出された操作の内容を説明するフィールド 3 Service.AdditionalInfo なぜ異常と判定されたか — 異常とみなされた API およびベースラインとの比較内容のフィールド … © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 12
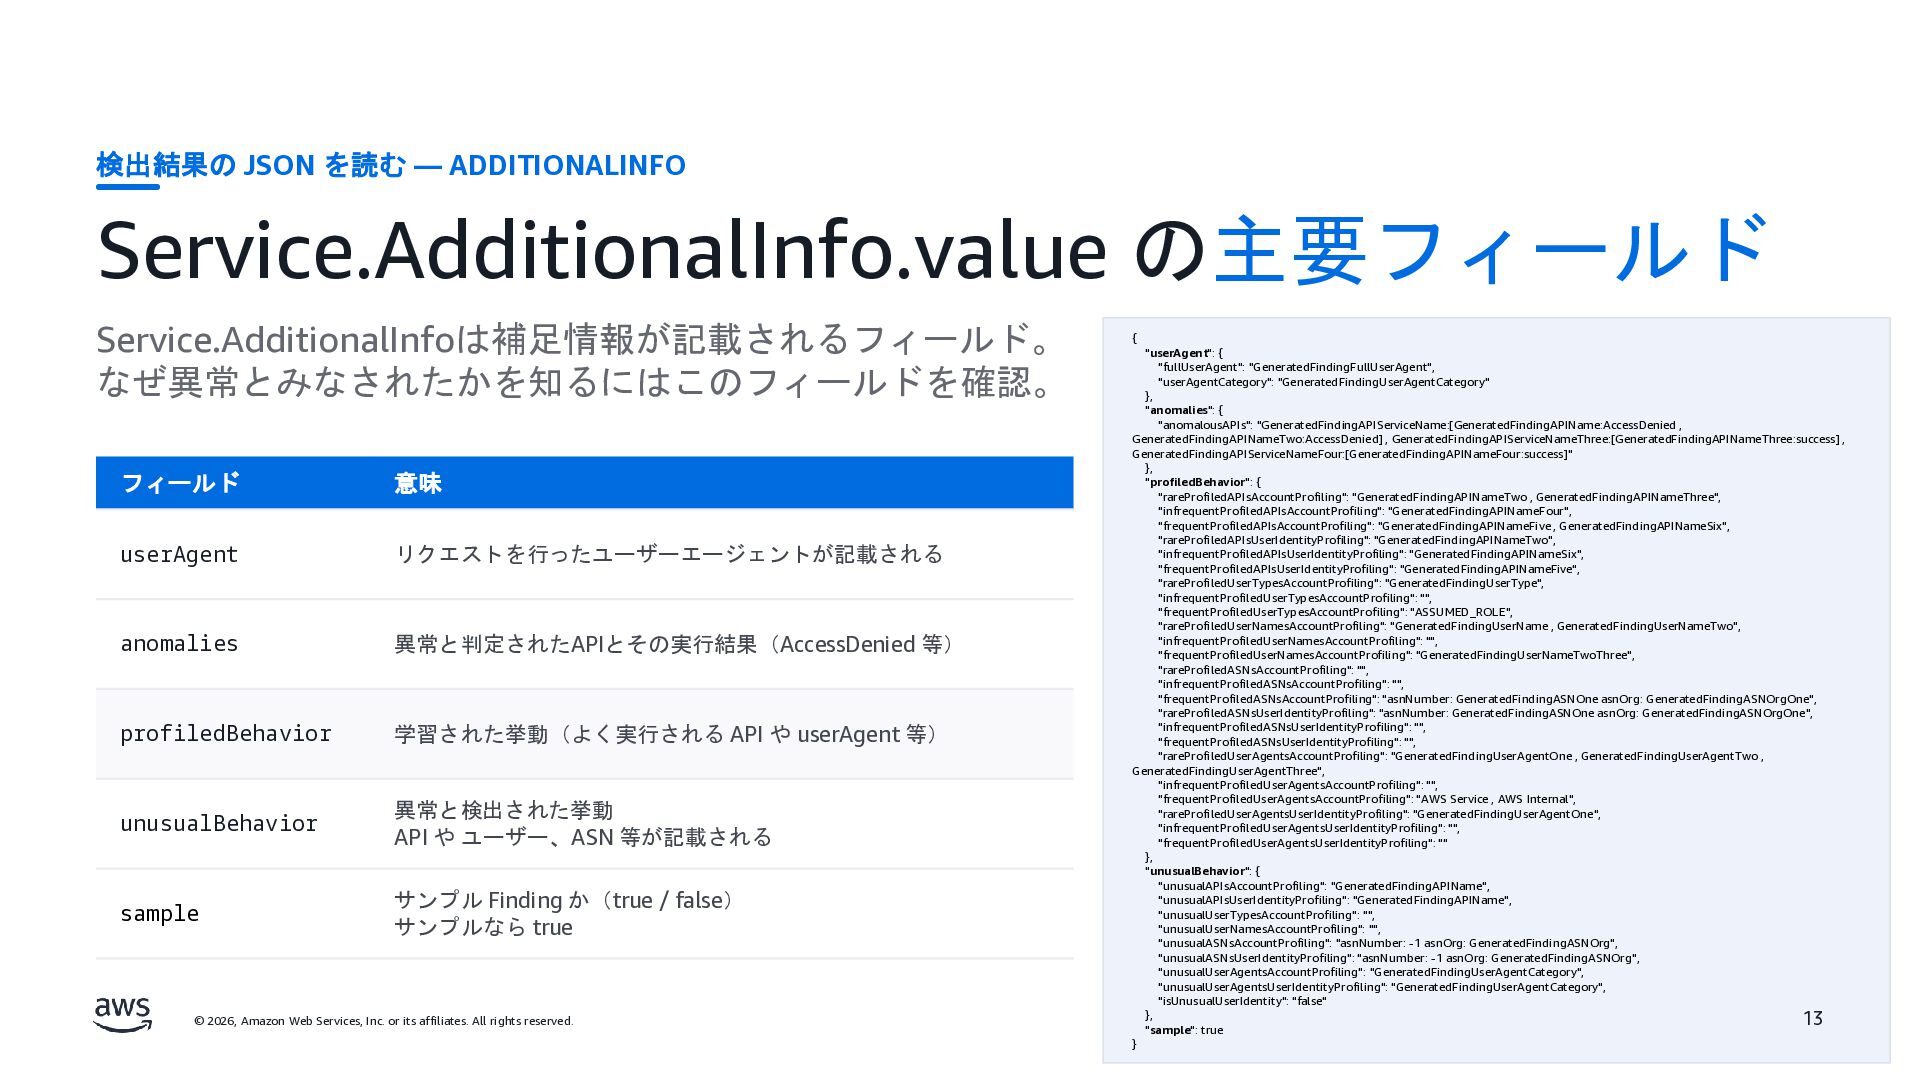
  12. 検出結果の JSON を読む — ADDITIONALINFO Service.AdditionalInfo.value の主要フィールド Service.AdditionalInfoは補足情報が記載されるフィールド。 なぜ異常とみなされたかを知るにはこのフィールドを確認。 フィールド

    意味 userAgent リクエストを行ったユーザーエージェントが記載される anomalies 異常と判定されたAPIとその実行結果(AccessDenied 等) profiledBehavior 学習された挙動(よく実行される API や userAgent 等) unusualBehavior 異常と検出された挙動 API や ユーザー、ASN 等が記載される sample サンプル Finding か(true / false) サンプルなら true © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. { "userAgent": { "fullUserAgent": "GeneratedFindingFullUserAgent", "userAgentCategory": "GeneratedFindingUserAgentCategory" }, "anomalies": { "anomalousAPIs": "GeneratedFindingAPIServiceName:[GeneratedFindingAPIName:AccessDenied , GeneratedFindingAPINameTwo:AccessDenied] , GeneratedFindingAPIServiceNameThree:[GeneratedFindingAPINameThree:success] , GeneratedFindingAPIServiceNameFour:[GeneratedFindingAPINameFour:success]" }, "profiledBehavior": { "rareProfiledAPIsAccountProfiling": "GeneratedFindingAPINameTwo , GeneratedFindingAPINameThree", "infrequentProfiledAPIsAccountProfiling": "GeneratedFindingAPINameFour", "frequentProfiledAPIsAccountProfiling": "GeneratedFindingAPINameFive , GeneratedFindingAPINameSix", "rareProfiledAPIsUserIdentityProfiling": "GeneratedFindingAPINameTwo", "infrequentProfiledAPIsUserIdentityProfiling": "GeneratedFindingAPINameSix", "frequentProfiledAPIsUserIdentityProfiling": "GeneratedFindingAPINameFive", "rareProfiledUserTypesAccountProfiling": "GeneratedFindingUserType", "infrequentProfiledUserTypesAccountProfiling": "", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", "rareProfiledUserNamesAccountProfiling": "GeneratedFindingUserName , GeneratedFindingUserNameTwo", "infrequentProfiledUserNamesAccountProfiling": "", "frequentProfiledUserNamesAccountProfiling": "GeneratedFindingUserNameTwoThree", "rareProfiledASNsAccountProfiling": "", "infrequentProfiledASNsAccountProfiling": "", "frequentProfiledASNsAccountProfiling": "asnNumber: GeneratedFindingASNOne asnOrg: GeneratedFindingASNOrgOne", "rareProfiledASNsUserIdentityProfiling": "asnNumber: GeneratedFindingASNOne asnOrg: GeneratedFindingASNOrgOne", "infrequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledASNsUserIdentityProfiling": "", "rareProfiledUserAgentsAccountProfiling": "GeneratedFindingUserAgentOne , GeneratedFindingUserAgentTwo , GeneratedFindingUserAgentThree", "infrequentProfiledUserAgentsAccountProfiling": "", "frequentProfiledUserAgentsAccountProfiling": "AWS Service , AWS Internal", "rareProfiledUserAgentsUserIdentityProfiling": "GeneratedFindingUserAgentOne", "infrequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserAgentsUserIdentityProfiling": "" }, "unusualBehavior": { "unusualAPIsAccountProfiling": "GeneratedFindingAPIName", "unusualAPIsUserIdentityProfiling": "GeneratedFindingAPIName", "unusualUserTypesAccountProfiling": "", "unusualUserNamesAccountProfiling": "", "unusualASNsAccountProfiling": "asnNumber: -1 asnOrg: GeneratedFindingASNOrg", "unusualASNsUserIdentityProfiling": "asnNumber: -1 asnOrg: GeneratedFindingASNOrg", "unusualUserAgentsAccountProfiling": "GeneratedFindingUserAgentCategory", "unusualUserAgentsUserIdentityProfiling": "GeneratedFindingUserAgentCategory", "isUnusualUserIdentity": "false" }, 13 "sample": true }
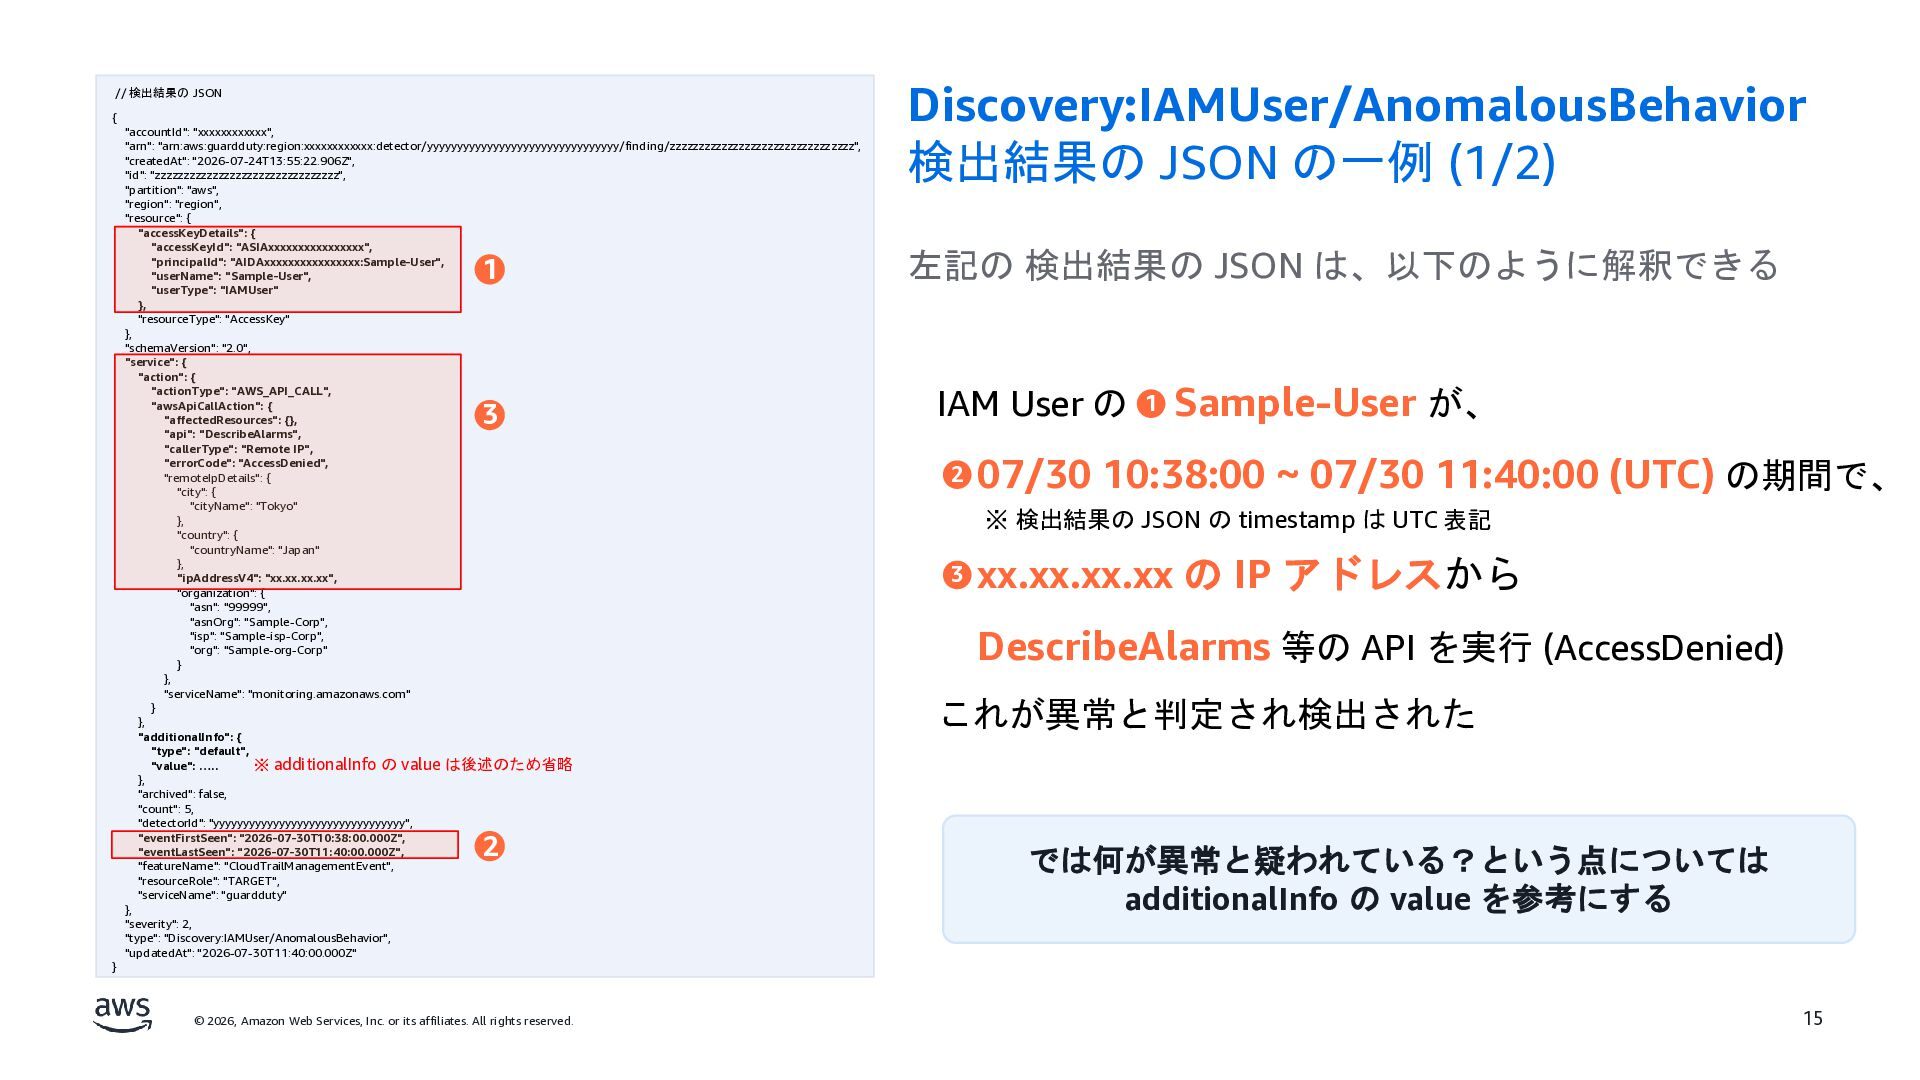
  13. // 検出結果の JSON { "accountId": "xxxxxxxxxxxx", "arn": "arn:aws:guardduty:region:xxxxxxxxxxxx:detector/yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy/finding/zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "createdAt": "2026-07-24T13:55:22.906Z",

    "id": "zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "partition": "aws", "region": "region", "resource": { "accessKeyDetails": { "accessKeyId": "ASIAxxxxxxxxxxxxxxxx", "principalId": "AIDAxxxxxxxxxxxxxxxx:Sample-User", "userName": "Sample-User", "userType": "IAMUser" }, "resourceType": "AccessKey" }, "schemaVersion": "2.0", "service": { "action": { "actionType": "AWS_API_CALL", "awsApiCallAction": { "affectedResources": {}, "api": "DescribeAlarms", "callerType": "Remote IP", "errorCode": "AccessDenied", "remoteIpDetails": { "city": { "cityName": "Tokyo" }, "country": { "countryName": "Japan" }, "ipAddressV4": "xx.xx.xx.xx", "organization": { "asn": "99999", "asnOrg": "Sample-Corp", "isp": "Sample-isp-Corp", "org": "Sample-org-Corp" } }, "serviceName": "monitoring.amazonaws.com" } }, "additionalInfo": { "type": "default", "value": ….. ※ additionalInfo の value は後述のため省略 }, "archived": false, "count": 5, "detectorId": "yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy", "eventFirstSeen": "2026-07-30T10:38:00.000Z", "eventLastSeen": "2026-07-30T11:40:00.000Z", "featureName": "CloudTrailManagementEvent", "resourceRole": "TARGET", "serviceName": "guardduty" }, "severity": 2, "type": "Discovery:IAMUser/AnomalousBehavior", "updatedAt": "2026-07-30T11:40:00.000Z" 1 3 2 Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (1/2) 左記の 検出結果の JSON は、以下のように解釈できる IAM User の 1 Sample-User が、 2 07/30 10:38:00 ~ 07/30 11:40:00 (UTC) の期間で、 ※ 検出結果の JSON の timestamp は UTC 表記 3 xx.xx.xx.xx の IP アドレスから DescribeAlarms 等の API を実行 (AccessDenied) これが異常と判定され検出された では何が異常と疑われている?という点については additionalInfo の value を参考にする } © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 15
  14. // 検出結果の JSON { "accountId": "xxxxxxxxxxxx", "arn": "arn:aws:guardduty:region:xxxxxxxxxxxx:detector/yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy/finding/zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "createdAt": "2026-07-24T13:55:22.906Z",

    "id": "zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "partition": "aws", "region": "region", "resource": { "accessKeyDetails": { "accessKeyId": "ASIAxxxxxxxxxxxxxxxx", "principalId": "AIDAxxxxxxxxxxxxxxxx:Sample-User", "userName": "Sample-User", "userType": "IAMUser" }, "resourceType": "AccessKey" }, "schemaVersion": "2.0", "service": { "action": { "actionType": "AWS_API_CALL", "awsApiCallAction": { "affectedResources": {}, "api": "DescribeAlarms", "callerType": "Remote IP", "errorCode": "AccessDenied", "remoteIpDetails": { "city": { "cityName": "Tokyo" }, "country": { "countryName": "Japan" }, "ipAddressV4": "xx.xx.xx.xx", "organization": { "asn": "99999", "asnOrg": "Sample-Corp", "isp": "Sample-isp-Corp", "org": "Sample-org-Corp" } }, "serviceName": "monitoring.amazonaws.com" } }, "additionalInfo": { "type": "default", "value": ….. }, "archived": false, "count": 5, "detectorId": "yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy", "eventFirstSeen": "2026-07-30T10:38:00.000Z", "eventLastSeen": "2026-07-30T11:40:00.000Z", "featureName": "CloudTrailManagementEvent", "resourceRole": "TARGET", "serviceName": "guardduty" }, "severity": 2, "type": "Discovery:IAMUser/AnomalousBehavior", "updatedAt": "2026-07-30T11:40:00.000Z" 1 "accessKeyDetails": { "accessKeyId": "ASIAxxxxxxxxxxxxxxxx", "principalId": "AIDAxxxxxxxxxxxxxxxx:Sample-User", "userName": "Sample-User", "userType": "IAMUser" }, Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (1/2) 左記の 検出結果の JSON は、以下のように解釈できる IAM User の 1 Sample-User が、 2 07/30 10:38:00 ~ 07/30 11:40:00 (UTC) の期間で、 ※ 検出結果の JSON の timestamp は UTC 表記 3 xx.xx.xx.xx の IP アドレスから DescribeAlarms 等の API を実行 (AccessDenied) これが異常と判定され検出された では何が異常と疑われている?という点については additionalInfo の value を参考にする } © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 16
  15. // 検出結果の JSON { "accountId": "xxxxxxxxxxxx", "arn": "arn:aws:guardduty:region:xxxxxxxxxxxx:detector/yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy/finding/zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "createdAt": "2026-07-24T13:55:22.906Z",

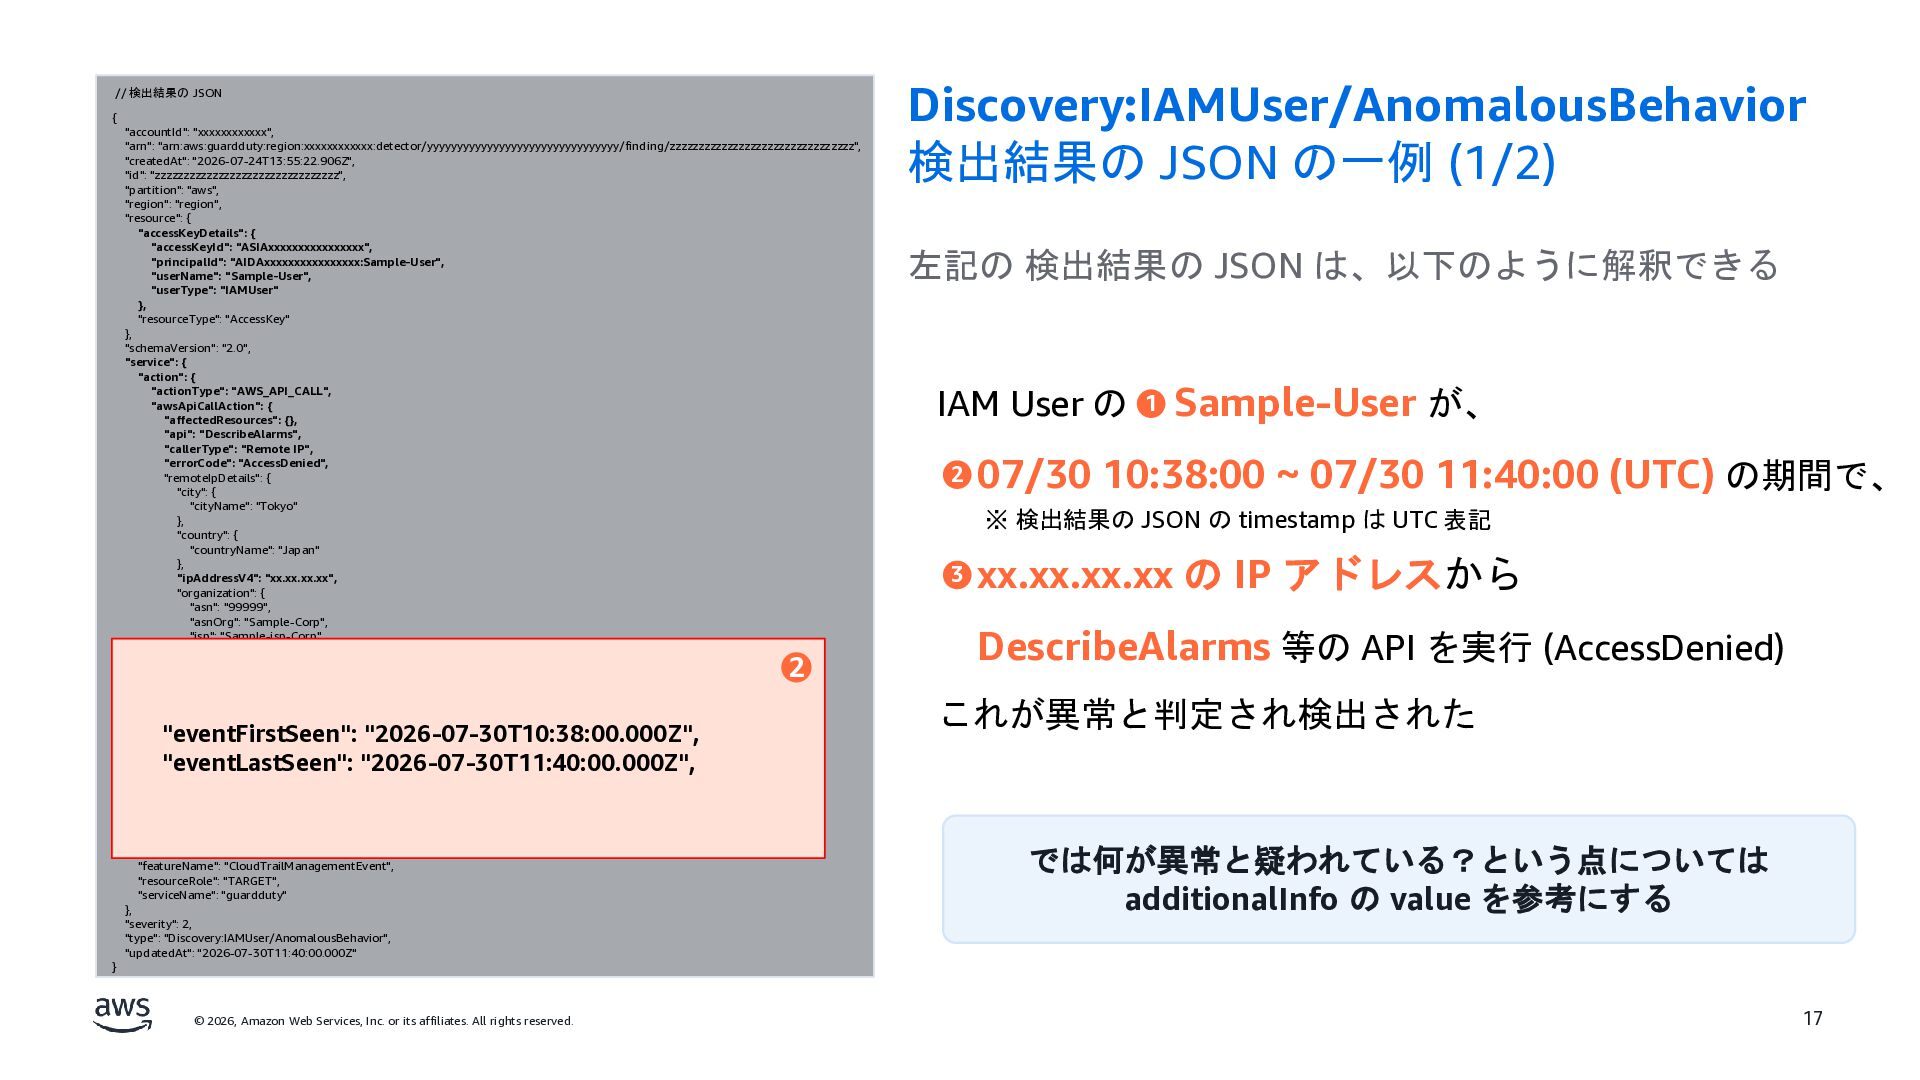
    "id": "zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "partition": "aws", "region": "region", "resource": { "accessKeyDetails": { "accessKeyId": "ASIAxxxxxxxxxxxxxxxx", "principalId": "AIDAxxxxxxxxxxxxxxxx:Sample-User", "userName": "Sample-User", "userType": "IAMUser" }, "resourceType": "AccessKey" }, "schemaVersion": "2.0", "service": { "action": { "actionType": "AWS_API_CALL", "awsApiCallAction": { "affectedResources": {}, "api": "DescribeAlarms", "callerType": "Remote IP", "errorCode": "AccessDenied", "remoteIpDetails": { "city": { "cityName": "Tokyo" }, "country": { "countryName": "Japan" }, "ipAddressV4": "xx.xx.xx.xx", "organization": { "asn": "99999", "asnOrg": "Sample-Corp", "isp": "Sample-isp-Corp", "org": "Sample-org-Corp" } }, "serviceName": "monitoring.amazonaws.com" } }, "additionalInfo": { "type": "default", "value": ….. ※ additionalInfo の value は後述のため省略 }, "archived": false, "count": 5, "detectorId": "yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy", "eventFirstSeen": "2026-07-30T10:38:00.000Z", "eventLastSeen": "2026-07-30T11:40:00.000Z", "featureName": "CloudTrailManagementEvent", "resourceRole": "TARGET", "serviceName": "guardduty" }, "severity": 2, "type": "Discovery:IAMUser/AnomalousBehavior", "updatedAt": "2026-07-30T11:40:00.000Z" 2 "eventFirstSeen": "2026-07-30T10:38:00.000Z", "eventLastSeen": "2026-07-30T11:40:00.000Z", Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (1/2) 左記の 検出結果の JSON は、以下のように解釈できる IAM User の 1 Sample-User が、 2 07/30 10:38:00 ~ 07/30 11:40:00 (UTC) の期間で、 ※ 検出結果の JSON の timestamp は UTC 表記 3 xx.xx.xx.xx の IP アドレスから DescribeAlarms 等の API を実行 (AccessDenied) これが異常と判定され検出された では何が異常と疑われている?という点については additionalInfo の value を参考にする } © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 17
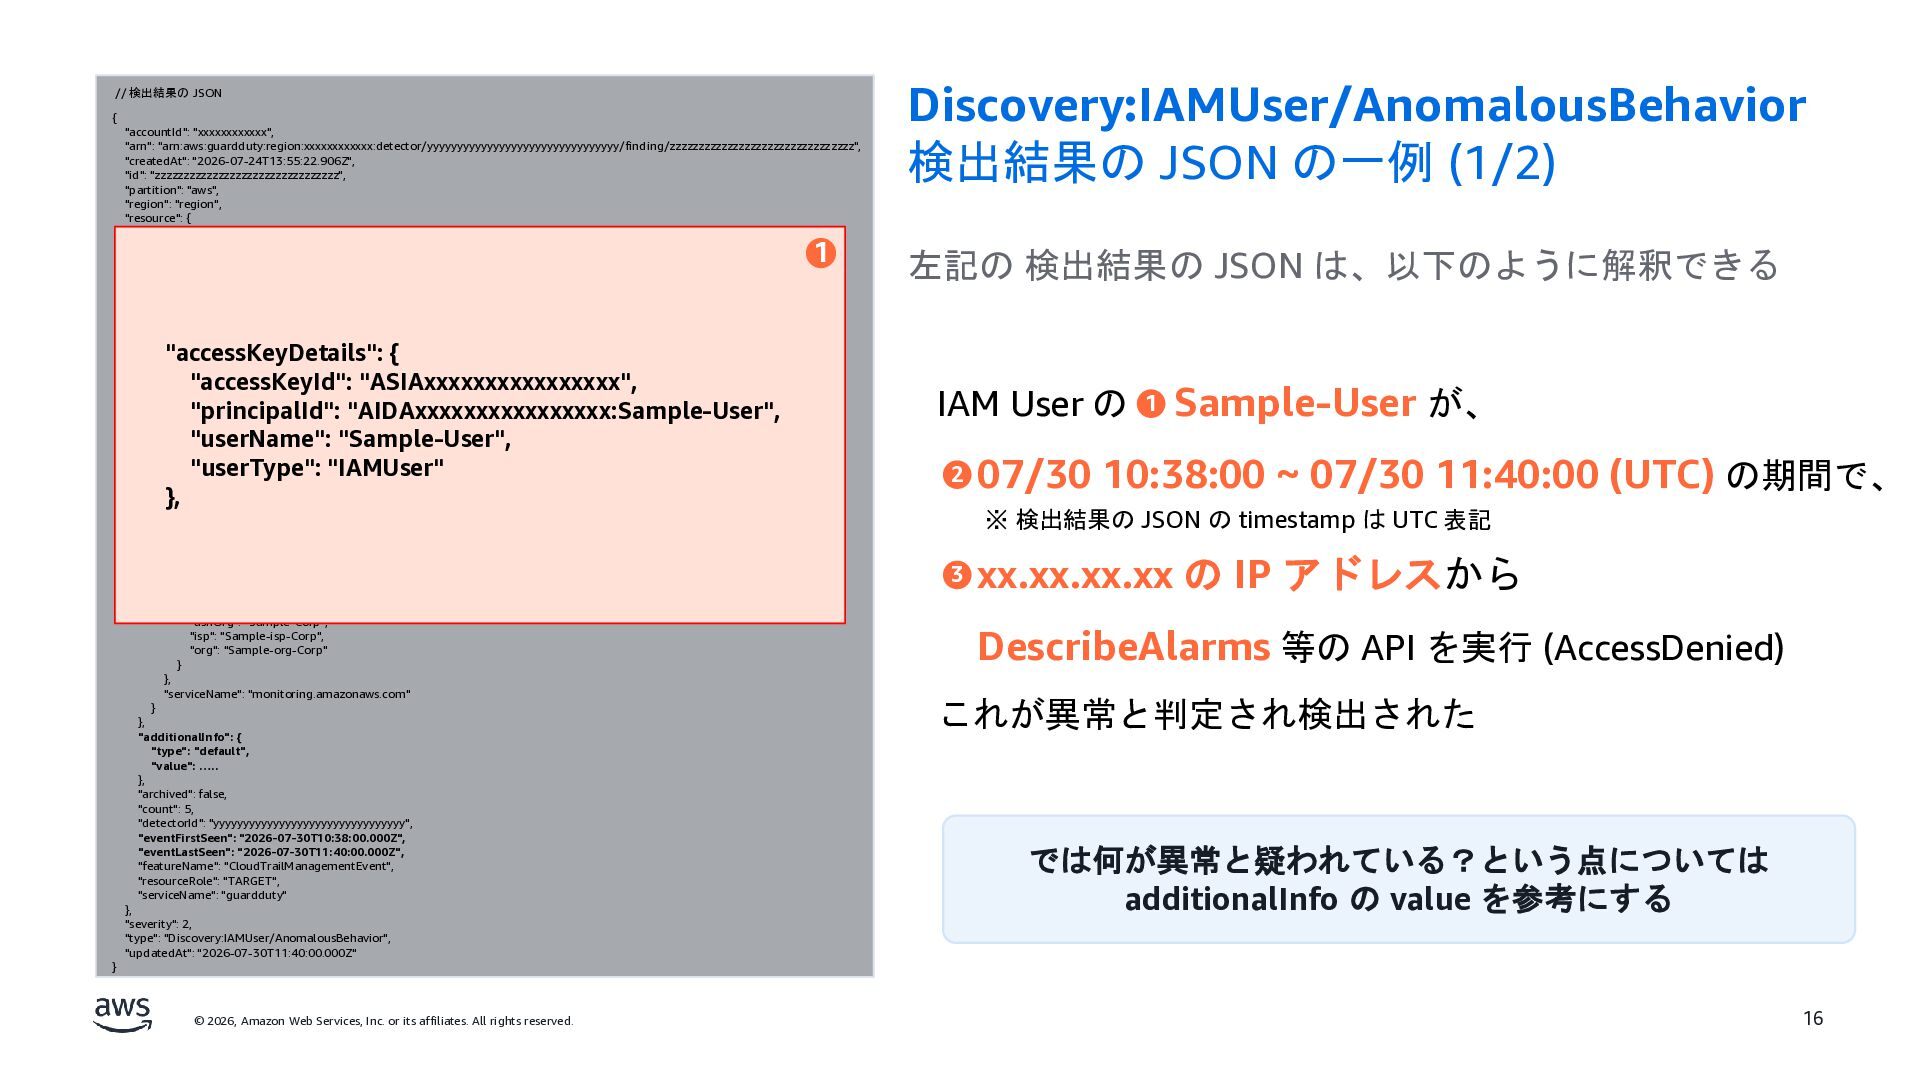
  16. // 検出結果の JSON { "accountId": "xxxxxxxxxxxx", "arn": "arn:aws:guardduty:region:xxxxxxxxxxxx:detector/yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy/finding/zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "createdAt": "2026-07-24T13:55:22.906Z",

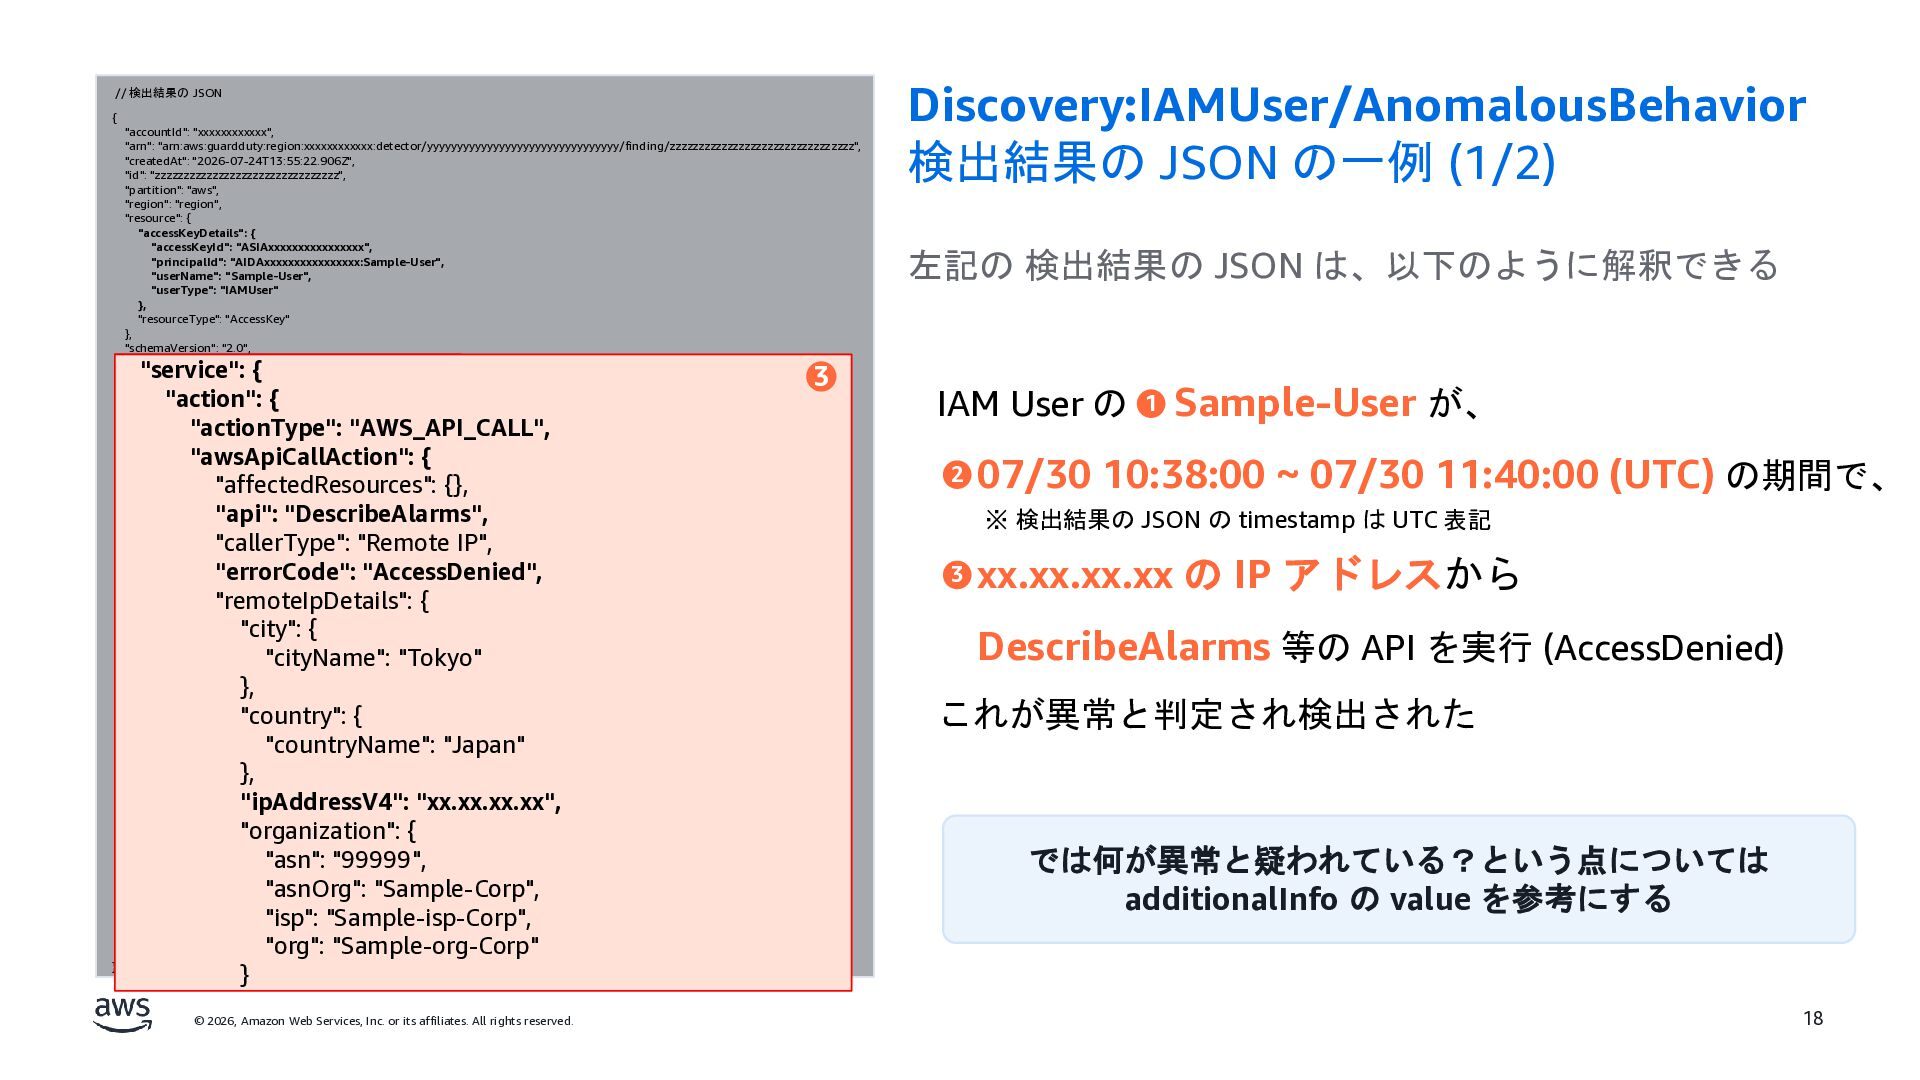
    "id": "zzzzzzzzzzzzzzzzzzzzzzzzzzzzzzzz", "partition": "aws", "region": "region", "resource": { "accessKeyDetails": { "accessKeyId": "ASIAxxxxxxxxxxxxxxxx", "principalId": "AIDAxxxxxxxxxxxxxxxx:Sample-User", "userName": "Sample-User", "userType": "IAMUser" }, "resourceType": "AccessKey" }, "schemaVersion": "2.0", "service": { "action": { "actionType": "AWS_API_CALL", "awsApiCallAction": { "affectedResources": {}, "api": "DescribeAlarms", "callerType": "Remote IP", "errorCode": "AccessDenied", "remoteIpDetails": { "city": { "cityName": "Tokyo" }, "country": { "countryName": "Japan" }, "ipAddressV4": "xx.xx.xx.xx", "organization": { "asn": "99999", "asnOrg": "Sample-Corp", "isp": "Sample-isp-Corp", "org": "Sample-org-Corp" } }, "serviceName": "monitoring.amazonaws.com" } }, "additionalInfo": { "type": "default", "value": ….. ※ additionalInfo の value は後述のため省略 }, "archived": false, "count": 5, "detectorId": "yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy", "eventFirstSeen": "2026-07-30T10:38:00.000Z", "eventLastSeen": "2026-07-30T11:40:00.000Z", "featureName": "CloudTrailManagementEvent", "resourceRole": "TARGET", "serviceName": "guardduty" }, "severity": 2, "type": "Discovery:IAMUser/AnomalousBehavior", "updatedAt": "2026-07-30T11:40:00.000Z" } "service": { "action": { 3 "actionType": "AWS_API_CALL", "awsApiCallAction": { "affectedResources": {}, "api": "DescribeAlarms", "callerType": "Remote IP", "errorCode": "AccessDenied", "remoteIpDetails": { "city": { "cityName": "Tokyo" }, "country": { "countryName": "Japan" }, "ipAddressV4": "xx.xx.xx.xx", "organization": { "asn": "99999", "asnOrg": "Sample-Corp", "isp": "Sample-isp-Corp", "org": "Sample-org-Corp" } © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 3 Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (1/2) 左記の 検出結果の JSON は、以下のように解釈できる IAM User の 1 Sample-User が、 2 07/30 10:38:00 ~ 07/30 11:40:00 (UTC) の期間で、 ※ 検出結果の JSON の timestamp は UTC 表記 3 xx.xx.xx.xx の IP アドレスから DescribeAlarms 等の API を実行 (AccessDenied) これが異常と判定され検出された では何が異常と疑われている?という点については additionalInfo の value を参考にする 18
  17. // 検出結果の JSON - Service.AdditionalInfo.value { "anomalies": { "anomalousAPIs": "monitoring.amazonaws.com:[DescribeAlarms:AccessDenied]

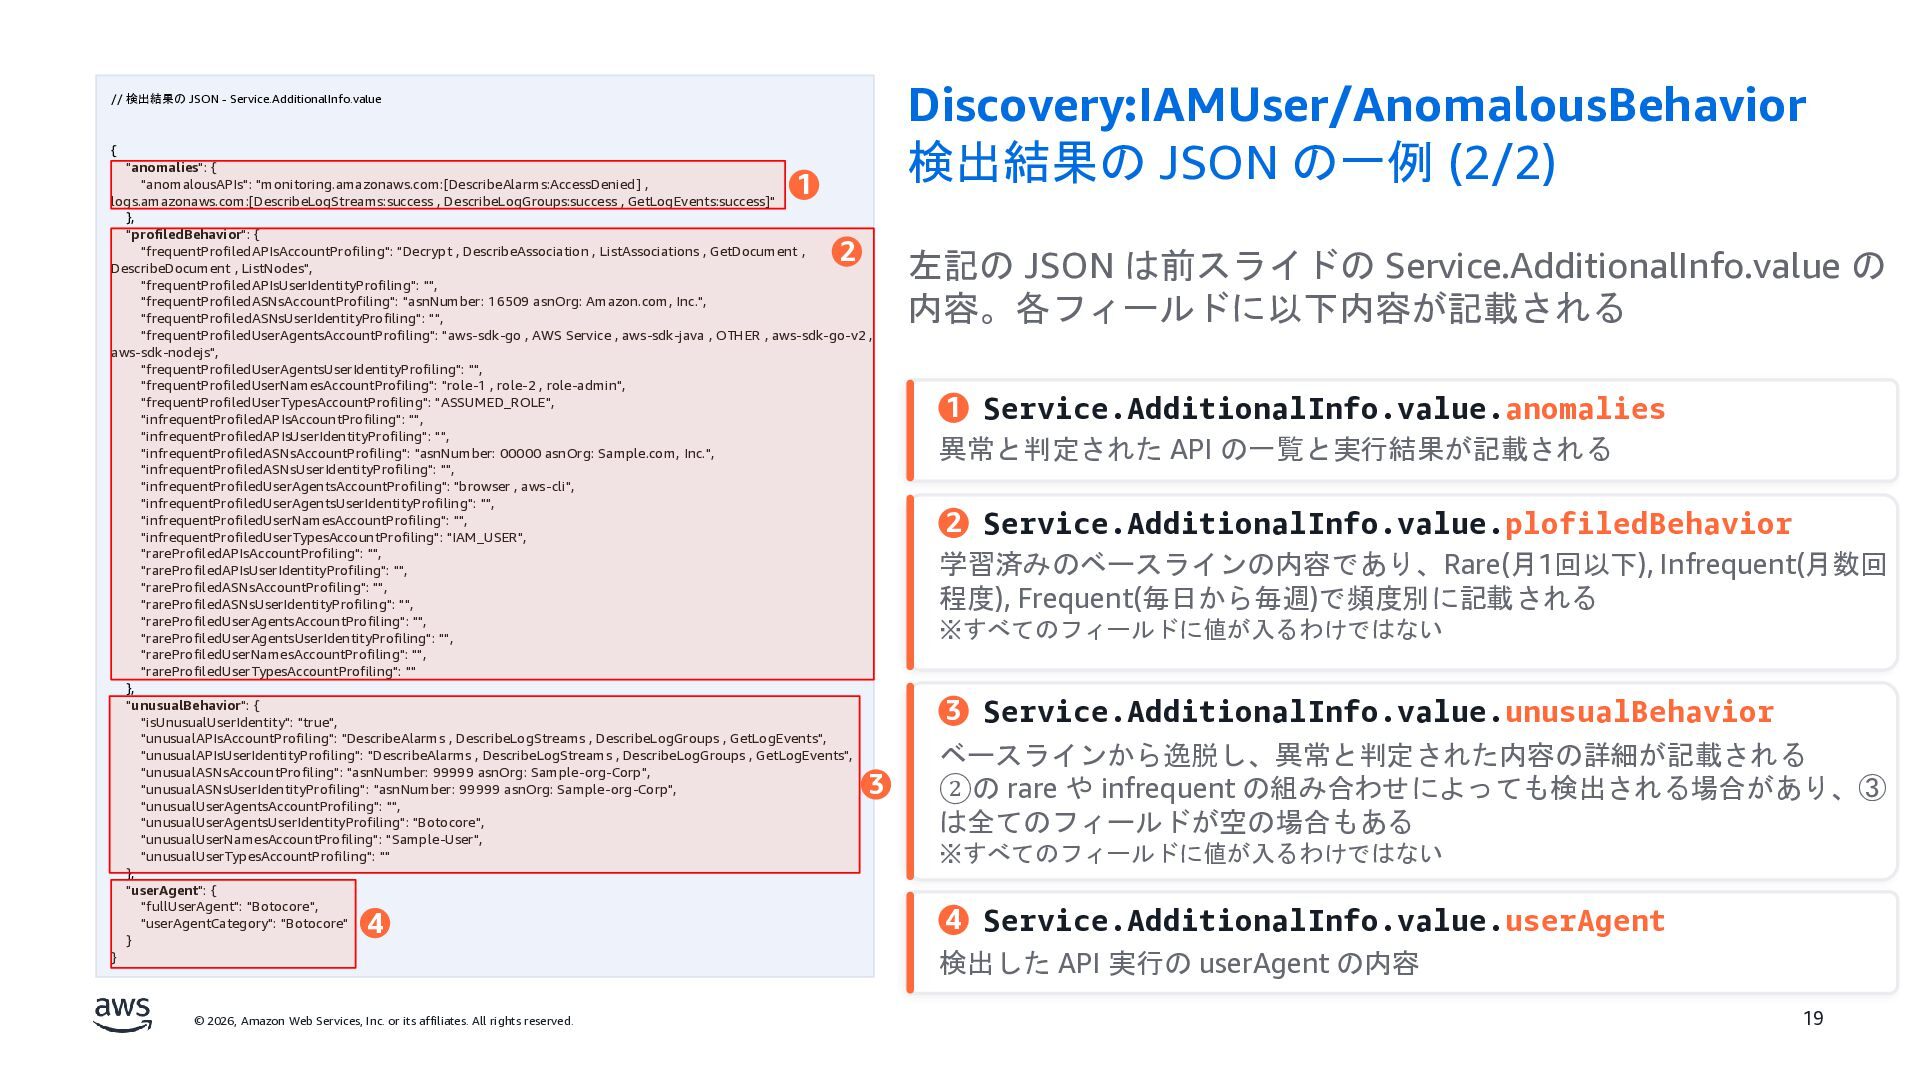
    , logs.amazonaws.com:[DescribeLogStreams:success , DescribeLogGroups:success , GetLogEvents:success]" }, "profiledBehavior": { "frequentProfiledAPIsAccountProfiling": "Decrypt , DescribeAssociation , ListAssociations , GetDocument , DescribeDocument , ListNodes", "frequentProfiledAPIsUserIdentityProfiling": "", "frequentProfiledASNsAccountProfiling": "asnNumber: 16509 asnOrg: Amazon.com, Inc.", "frequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledUserAgentsAccountProfiling": "aws-sdk-go , AWS Service , aws-sdk-java , OTHER , aws-sdk-go-v2 , aws-sdk-nodejs", "frequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserNamesAccountProfiling": "role-1 , role-2 , role-admin", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", "infrequentProfiledAPIsAccountProfiling": "", "infrequentProfiledAPIsUserIdentityProfiling": "", "infrequentProfiledASNsAccountProfiling": "asnNumber: 00000 asnOrg: Sample.com, Inc.", "infrequentProfiledASNsUserIdentityProfiling": "", "infrequentProfiledUserAgentsAccountProfiling": "browser , aws-cli", "infrequentProfiledUserAgentsUserIdentityProfiling": "", "infrequentProfiledUserNamesAccountProfiling": "", "infrequentProfiledUserTypesAccountProfiling": "IAM_USER", "rareProfiledAPIsAccountProfiling": "", "rareProfiledAPIsUserIdentityProfiling": "", "rareProfiledASNsAccountProfiling": "", "rareProfiledASNsUserIdentityProfiling": "", "rareProfiledUserAgentsAccountProfiling": "", "rareProfiledUserAgentsUserIdentityProfiling": "", "rareProfiledUserNamesAccountProfiling": "", "rareProfiledUserTypesAccountProfiling": "" }, "unusualBehavior": { "isUnusualUserIdentity": "true", "unusualAPIsAccountProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualAPIsUserIdentityProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualASNsAccountProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualASNsUserIdentityProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualUserAgentsAccountProfiling": "", "unusualUserAgentsUserIdentityProfiling": "Botocore", "unusualUserNamesAccountProfiling": "Sample-User", "unusualUserTypesAccountProfiling": "" }, "userAgent": { "fullUserAgent": "Botocore", "userAgentCategory": "Botocore" } } 1 2 3 4 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (2/2) 左記の JSON は前スライドの Service.AdditionalInfo.value の 内容。各フィールドに以下内容が記載される 1 Service.AdditionalInfo.value.anomalies 異常と判定された API の一覧と実行結果が記載される 2 Service.AdditionalInfo.value.plofiledBehavior 学習済みのベースラインの内容であり、Rare(月1回以下), Infrequent(月数回 程度), Frequent(毎日から毎週)で頻度別に記載される ※すべてのフィールドに値が入るわけではない 3 Service.AdditionalInfo.value.unusualBehavior ベースラインから逸脱し、異常と判定された内容の詳細が記載される ②の rare や infrequent の組み合わせによっても検出される場合があり、③ は全てのフィールドが空の場合もある ※すべてのフィールドに値が入るわけではない 4 Service.AdditionalInfo.value.userAgent 検出した API 実行の userAgent の内容 19
  18. // 検出結果の JSON - Service.AdditionalInfo.value { "anomalies": { "anomalousAPIs": "monitoring.amazonaws.com:[DescribeAlarms:AccessDenied]

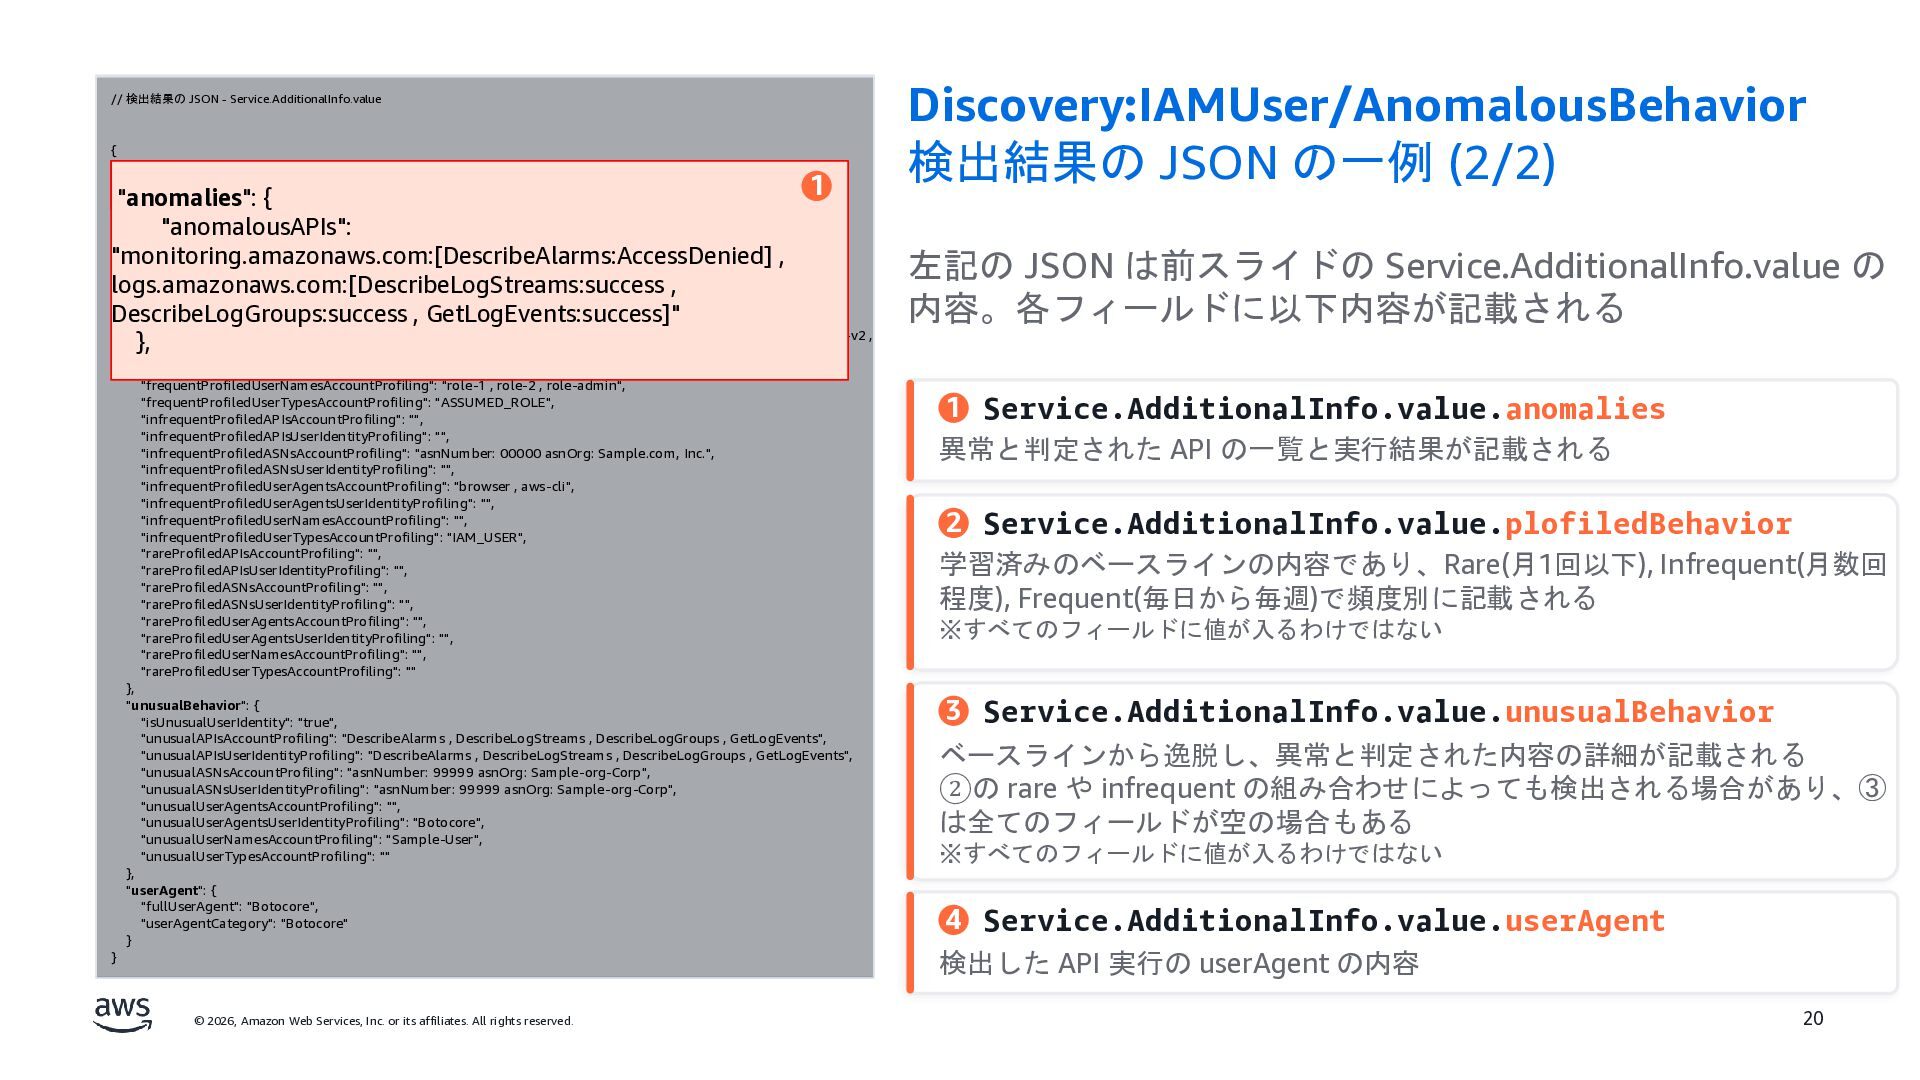
    , logs.amazonaws.com:[DescribeLogStreams:success , DescribeLogGroups:success , GetLogEvents:success]" }, "profiledBehavior": { "frequentProfiledAPIsAccountProfiling": "Decrypt , DescribeAssociation , ListAssociations , GetDocument , DescribeDocument , ListNodes", "frequentProfiledAPIsUserIdentityProfiling": "", "frequentProfiledASNsAccountProfiling": "asnNumber: 16509 asnOrg: Amazon.com, Inc.", "frequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledUserAgentsAccountProfiling": "aws-sdk-go , AWS Service , aws-sdk-java , OTHER , aws-sdk-go-v2 , aws-sdk-nodejs", "frequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserNamesAccountProfiling": "role-1 , role-2 , role-admin", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", "infrequentProfiledAPIsAccountProfiling": "", "infrequentProfiledAPIsUserIdentityProfiling": "", "infrequentProfiledASNsAccountProfiling": "asnNumber: 00000 asnOrg: Sample.com, Inc.", "infrequentProfiledASNsUserIdentityProfiling": "", "infrequentProfiledUserAgentsAccountProfiling": "browser , aws-cli", "infrequentProfiledUserAgentsUserIdentityProfiling": "", "infrequentProfiledUserNamesAccountProfiling": "", "infrequentProfiledUserTypesAccountProfiling": "IAM_USER", "rareProfiledAPIsAccountProfiling": "", "rareProfiledAPIsUserIdentityProfiling": "", "rareProfiledASNsAccountProfiling": "", "rareProfiledASNsUserIdentityProfiling": "", "rareProfiledUserAgentsAccountProfiling": "", "rareProfiledUserAgentsUserIdentityProfiling": "", "rareProfiledUserNamesAccountProfiling": "", "rareProfiledUserTypesAccountProfiling": "" }, "unusualBehavior": { "isUnusualUserIdentity": "true", "unusualAPIsAccountProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualAPIsUserIdentityProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualASNsAccountProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualASNsUserIdentityProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualUserAgentsAccountProfiling": "", "unusualUserAgentsUserIdentityProfiling": "Botocore", "unusualUserNamesAccountProfiling": "Sample-User", "unusualUserTypesAccountProfiling": "" }, "userAgent": { "fullUserAgent": "Botocore", "userAgentCategory": "Botocore" } } 1 "anomalies": { "anomalousAPIs": "monitoring.amazonaws.com:[DescribeAlarms:AccessDenied] , logs.amazonaws.com:[DescribeLogStreams:success , DescribeLogGroups:success , GetLogEvents:success]" }, © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (2/2) 左記の JSON は前スライドの Service.AdditionalInfo.value の 内容。各フィールドに以下内容が記載される 1 Service.AdditionalInfo.value.anomalies 異常と判定された API の一覧と実行結果が記載される 2 Service.AdditionalInfo.value.plofiledBehavior 学習済みのベースラインの内容であり、Rare(月1回以下), Infrequent(月数回 程度), Frequent(毎日から毎週)で頻度別に記載される ※すべてのフィールドに値が入るわけではない 3 Service.AdditionalInfo.value.unusualBehavior ベースラインから逸脱し、異常と判定された内容の詳細が記載される ②の rare や infrequent の組み合わせによっても検出される場合があり、③ は全てのフィールドが空の場合もある ※すべてのフィールドに値が入るわけではない 4 Service.AdditionalInfo.value.userAgent 検出した API 実行の userAgent の内容 20
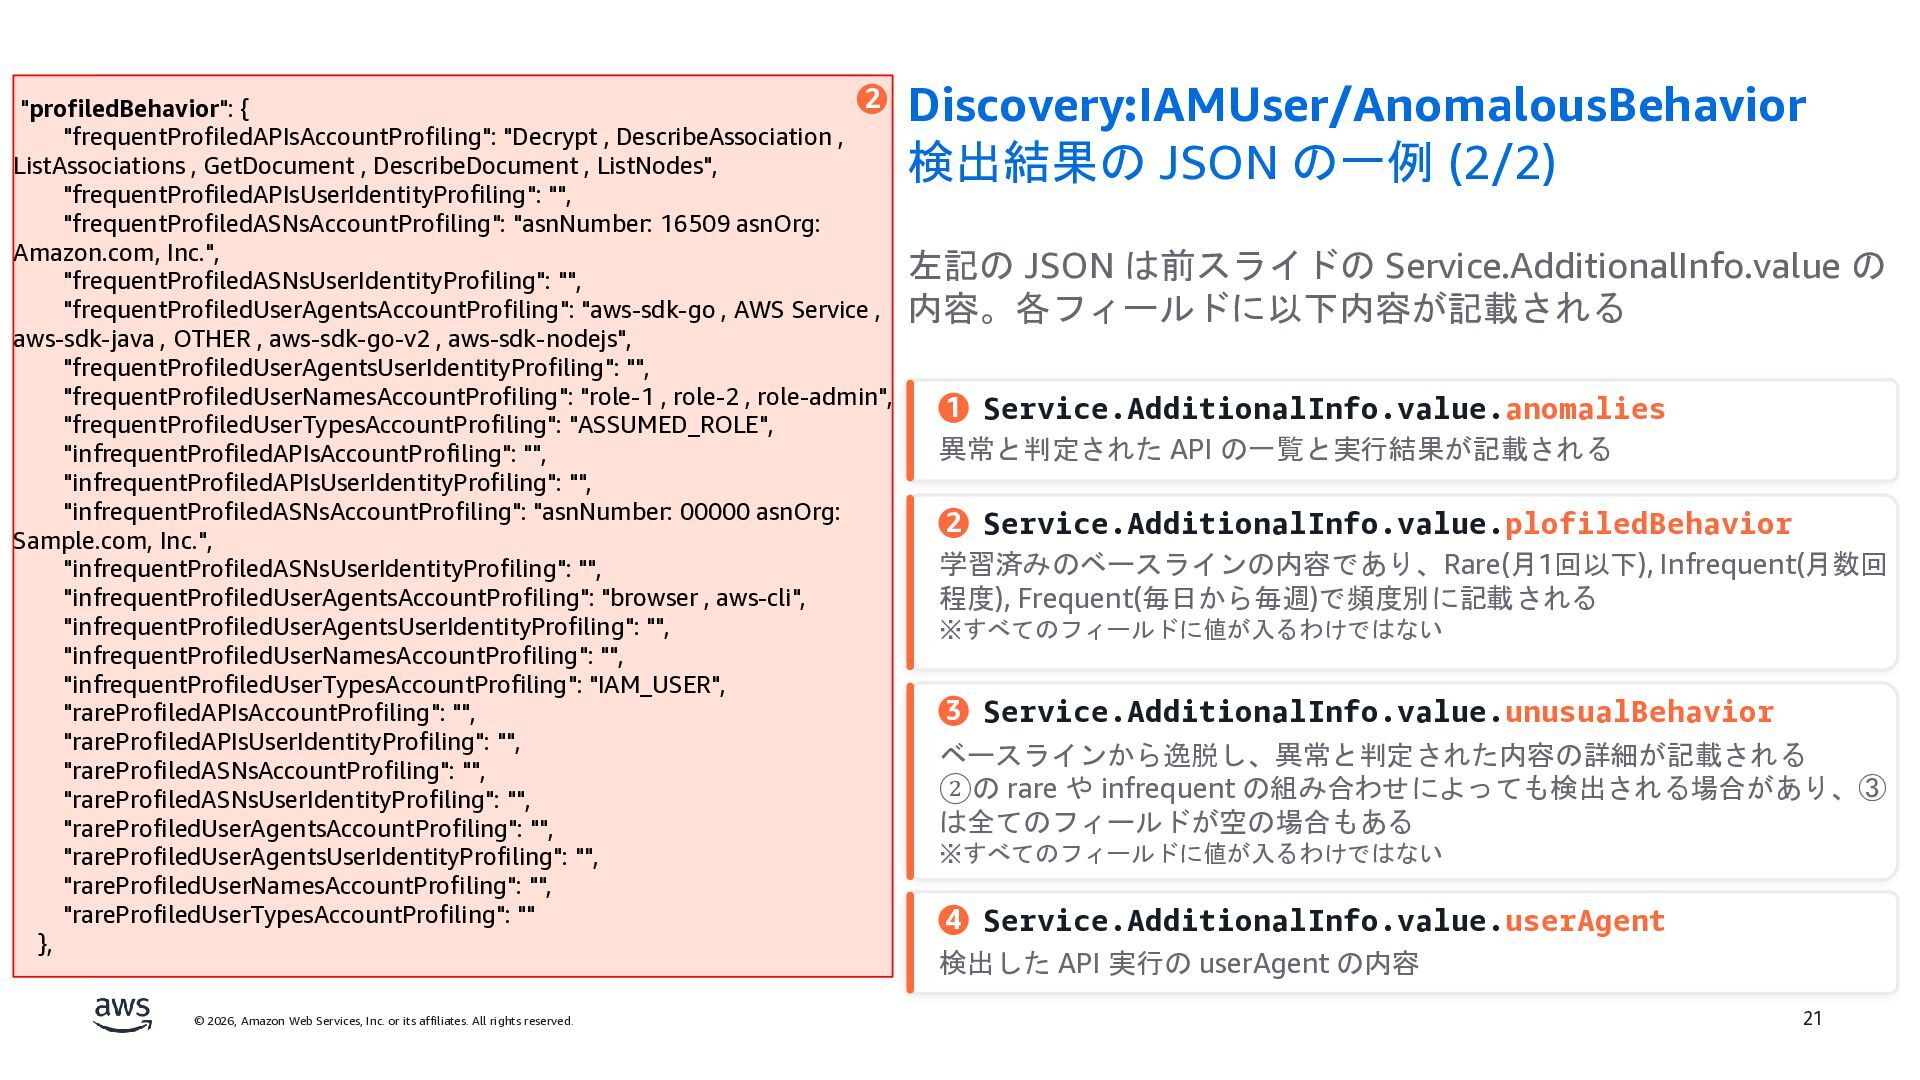
  19. Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (2/2) 2 "profiledBehavior": { "frequentProfiledAPIsAccountProfiling": "Decrypt

    , DescribeAssociation , { "anomalies": { ListAssociations , GetDocument , DescribeDocument , ListNodes", "anomalousAPIs": "monitoring.amazonaws.com:[DescribeAlarms:AccessDenied] , "frequentProfiledAPIsUserIdentityProfiling": "", logs.amazonaws.com:[DescribeLogStreams:success , DescribeLogGroups:success , GetLogEvents:success]" }, "frequentProfiledASNsAccountProfiling": "asnNumber: 16509 asnOrg: "profiledBehavior": { "frequentProfiledAPIsAccountProfiling": "Decrypt , DescribeAssociation , ListAssociations , GetDocument , Amazon.com, Inc.", 2 DescribeDocument , ListNodes", 左記の JSON は前スライドの Service.AdditionalInfo.value の "frequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledAPIsUserIdentityProfiling": "", "frequentProfiledASNsAccountProfiling": "asnNumber: 16509 asnOrg: Amazon.com, Inc.", "frequentProfiledUserAgentsAccountProfiling": "aws-sdk-go , AWS Service , 内容。各フィールドに以下内容が記載される "frequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledUserAgentsAccountProfiling": "aws-sdk-go , AWS Service , aws-sdk-java , OTHER , aws-sdk-go-v2 , aws-sdk-java , OTHER , aws-sdk-go-v2 , aws-sdk-nodejs", aws-sdk-nodejs", "frequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserNamesAccountProfiling": "role-1 , role-2 , role-admin", "frequentProfiledUserNamesAccountProfiling": "role-1 , role-2 , role-admin", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", 1 Service.AdditionalInfo.value.anomalies "infrequentProfiledAPIsAccountProfiling": "", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", "infrequentProfiledAPIsUserIdentityProfiling": "", "infrequentProfiledASNsAccountProfiling": "asnNumber: 00000 異常と判定された API の一覧と実行結果が記載される "infrequentProfiledAPIsAccountProfiling": "",asnOrg: Sample.com, Inc.", "infrequentProfiledASNsUserIdentityProfiling": "", "infrequentProfiledAPIsUserIdentityProfiling": "infrequentProfiledUserAgentsAccountProfiling": "browser , aws-cli","", "infrequentProfiledUserAgentsUserIdentityProfiling": "", "infrequentProfiledASNsAccountProfiling": "asnNumber: 00000 asnOrg: "infrequentProfiledUserNamesAccountProfiling": "", 2 Service.AdditionalInfo.value.plofiledBehavior "infrequentProfiledUserTypesAccountProfiling": "IAM_USER", Sample.com, Inc.", "rareProfiledAPIsAccountProfiling": "", 学習済みのベースラインの内容であり、Rare(月1回以下), Infrequent(月数回 "rareProfiledAPIsUserIdentityProfiling": "", "infrequentProfiledASNsUserIdentityProfiling": "", "rareProfiledASNsAccountProfiling": "", "infrequentProfiledUserAgentsAccountProfiling": "browser , aws-cli", 程度), Frequent(毎日から毎週)で頻度別に記載される "rareProfiledASNsUserIdentityProfiling": "", "rareProfiledUserAgentsAccountProfiling": "", "infrequentProfiledUserAgentsUserIdentityProfiling": "", ※すべてのフィールドに値が入るわけではない "rareProfiledUserAgentsUserIdentityProfiling": "", "rareProfiledUserNamesAccountProfiling": "", "infrequentProfiledUserNamesAccountProfiling": "", "rareProfiledUserTypesAccountProfiling": "" "infrequentProfiledUserTypesAccountProfiling": "IAM_USER", }, "unusualBehavior": { 3 Service.AdditionalInfo.value.unusualBehavior "rareProfiledAPIsAccountProfiling": "", "isUnusualUserIdentity": "true", "unusualAPIsAccountProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "rareProfiledAPIsUserIdentityProfiling": "", "unusualAPIsUserIdentityProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", ベースラインから逸脱し、異常と判定された内容の詳細が記載される "unusualASNsAccountProfiling": "asnNumber: 99999 "rareProfiledASNsAccountProfiling": "",asnOrg: Sample-org-Corp", "unusualASNsUserIdentityProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", ②の rare や infrequent の組み合わせによっても検出される場合があり、③ "rareProfiledASNsUserIdentityProfiling": "", "unusualUserAgentsAccountProfiling": "", "unusualUserAgentsUserIdentityProfiling": "Botocore", は全てのフィールドが空の場合もある "rareProfiledUserAgentsAccountProfiling": "", "unusualUserNamesAccountProfiling": "Sample-User", "unusualUserTypesAccountProfiling": "" ※すべてのフィールドに値が入るわけではない "rareProfiledUserAgentsUserIdentityProfiling": "", }, "rareProfiledUserNamesAccountProfiling": "", "userAgent": { "fullUserAgent": "Botocore", "rareProfiledUserTypesAccountProfiling": "" "userAgentCategory": "Botocore" 4 Service.AdditionalInfo.value.userAgent } }, } // 検出結果の JSON - Service.AdditionalInfo.value 検出した API 実行の userAgent の内容 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 21
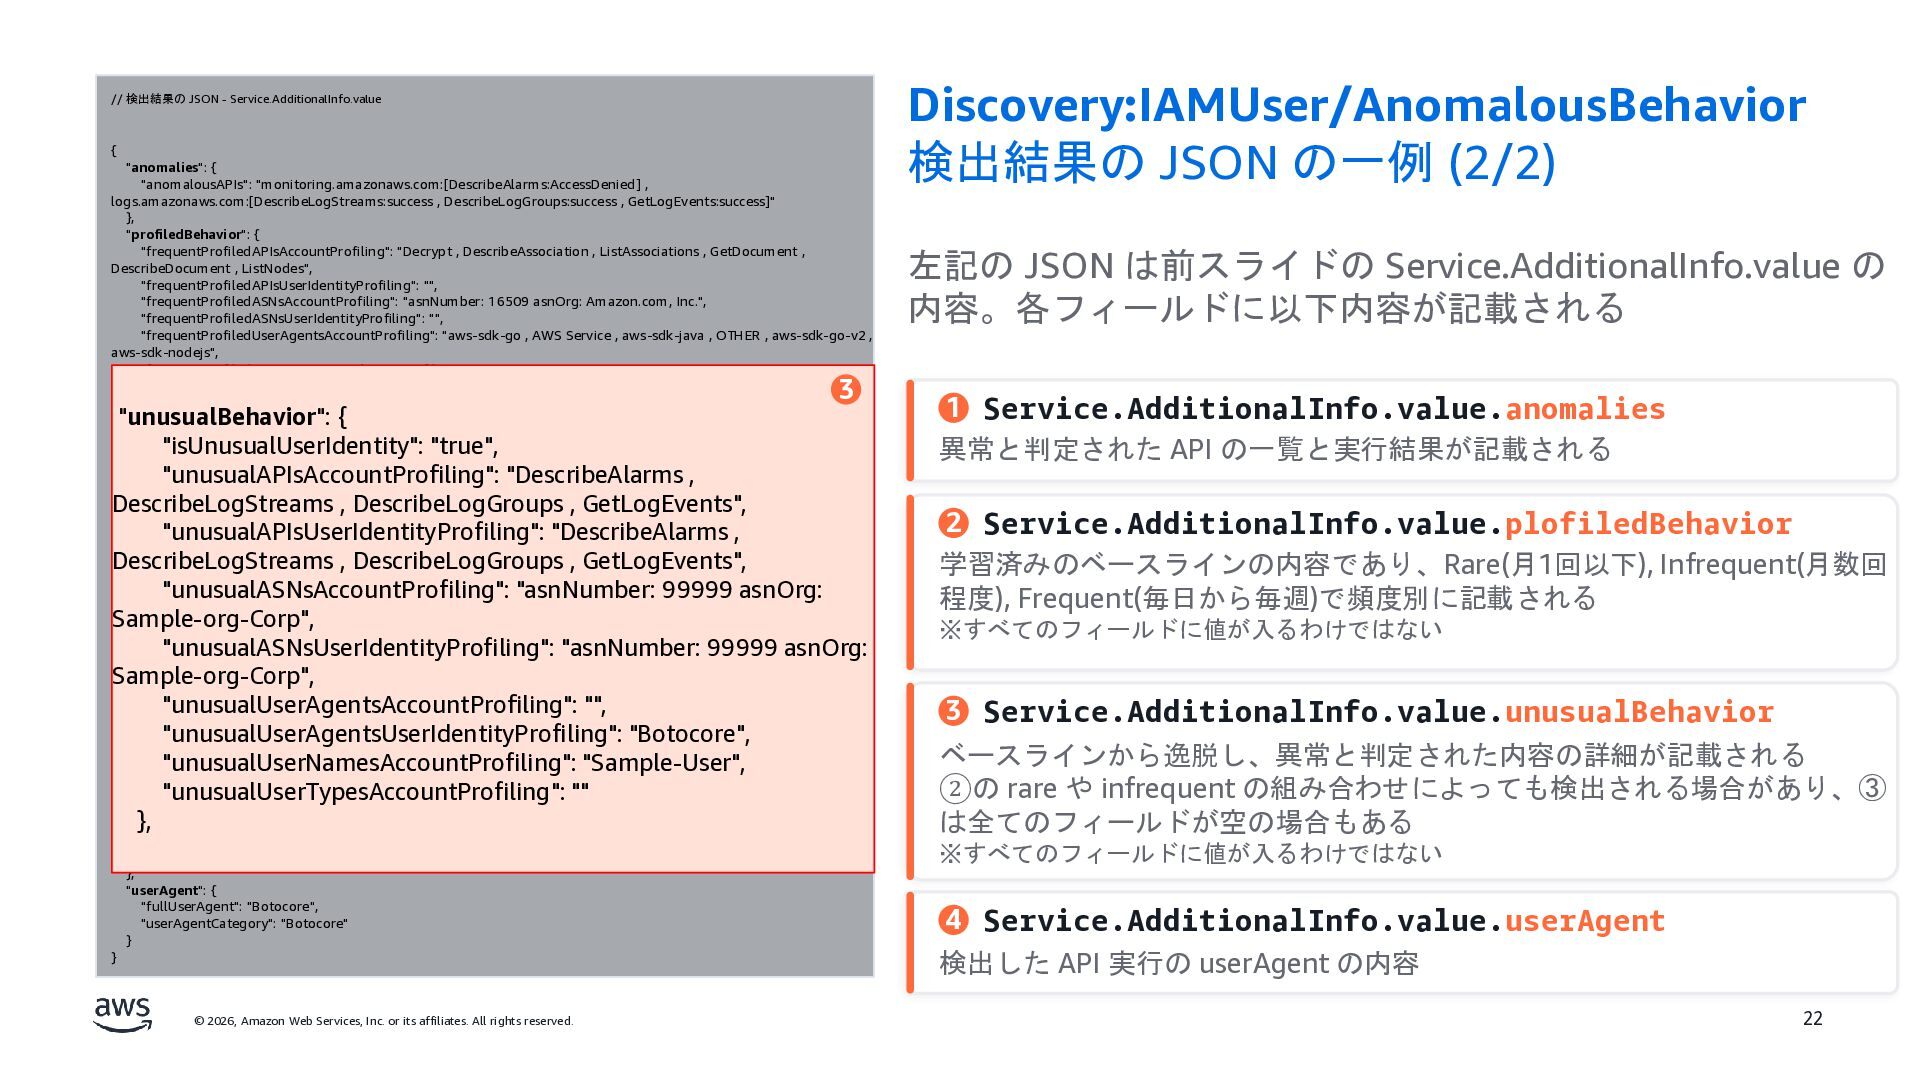
  20. // 検出結果の JSON - Service.AdditionalInfo.value { "anomalies": { "anomalousAPIs": "monitoring.amazonaws.com:[DescribeAlarms:AccessDenied]

    , logs.amazonaws.com:[DescribeLogStreams:success , DescribeLogGroups:success , GetLogEvents:success]" }, "profiledBehavior": { "frequentProfiledAPIsAccountProfiling": "Decrypt , DescribeAssociation , ListAssociations , GetDocument , DescribeDocument , ListNodes", "frequentProfiledAPIsUserIdentityProfiling": "", "frequentProfiledASNsAccountProfiling": "asnNumber: 16509 asnOrg: Amazon.com, Inc.", "frequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledUserAgentsAccountProfiling": "aws-sdk-go , AWS Service , aws-sdk-java , OTHER , aws-sdk-go-v2 , aws-sdk-nodejs", "frequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserNamesAccountProfiling": "role-1 , role-2 , role-admin", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", "infrequentProfiledAPIsAccountProfiling": "", "infrequentProfiledAPIsUserIdentityProfiling": "", "infrequentProfiledASNsAccountProfiling": "asnNumber: 00000 asnOrg: Sample.com, Inc.", "infrequentProfiledASNsUserIdentityProfiling": "", "infrequentProfiledUserAgentsAccountProfiling": "browser , aws-cli", "infrequentProfiledUserAgentsUserIdentityProfiling": "", "infrequentProfiledUserNamesAccountProfiling": "", "infrequentProfiledUserTypesAccountProfiling": "IAM_USER", "rareProfiledAPIsAccountProfiling": "", "rareProfiledAPIsUserIdentityProfiling": "", "rareProfiledASNsAccountProfiling": "", "rareProfiledASNsUserIdentityProfiling": "", "rareProfiledUserAgentsAccountProfiling": "", "rareProfiledUserAgentsUserIdentityProfiling": "", "rareProfiledUserNamesAccountProfiling": "", "rareProfiledUserTypesAccountProfiling": "" }, "unusualBehavior": { "isUnusualUserIdentity": "true", "unusualAPIsAccountProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualAPIsUserIdentityProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualASNsAccountProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualASNsUserIdentityProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualUserAgentsAccountProfiling": "", "unusualUserAgentsUserIdentityProfiling": "Botocore", "unusualUserNamesAccountProfiling": "Sample-User", "unusualUserTypesAccountProfiling": "" }, "userAgent": { "fullUserAgent": "Botocore", "userAgentCategory": "Botocore" } } 3 "unusualBehavior": { "isUnusualUserIdentity": "true", "unusualAPIsAccountProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualAPIsUserIdentityProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualASNsAccountProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualASNsUserIdentityProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualUserAgentsAccountProfiling": "", "unusualUserAgentsUserIdentityProfiling": "Botocore", "unusualUserNamesAccountProfiling": "Sample-User", "unusualUserTypesAccountProfiling": "" }, © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (2/2) 左記の JSON は前スライドの Service.AdditionalInfo.value の 内容。各フィールドに以下内容が記載される 1 Service.AdditionalInfo.value.anomalies 異常と判定された API の一覧と実行結果が記載される 2 Service.AdditionalInfo.value.plofiledBehavior 学習済みのベースラインの内容であり、Rare(月1回以下), Infrequent(月数回 程度), Frequent(毎日から毎週)で頻度別に記載される ※すべてのフィールドに値が入るわけではない 3 Service.AdditionalInfo.value.unusualBehavior ベースラインから逸脱し、異常と判定された内容の詳細が記載される ②の rare や infrequent の組み合わせによっても検出される場合があり、③ は全てのフィールドが空の場合もある ※すべてのフィールドに値が入るわけではない 4 Service.AdditionalInfo.value.userAgent 検出した API 実行の userAgent の内容 22
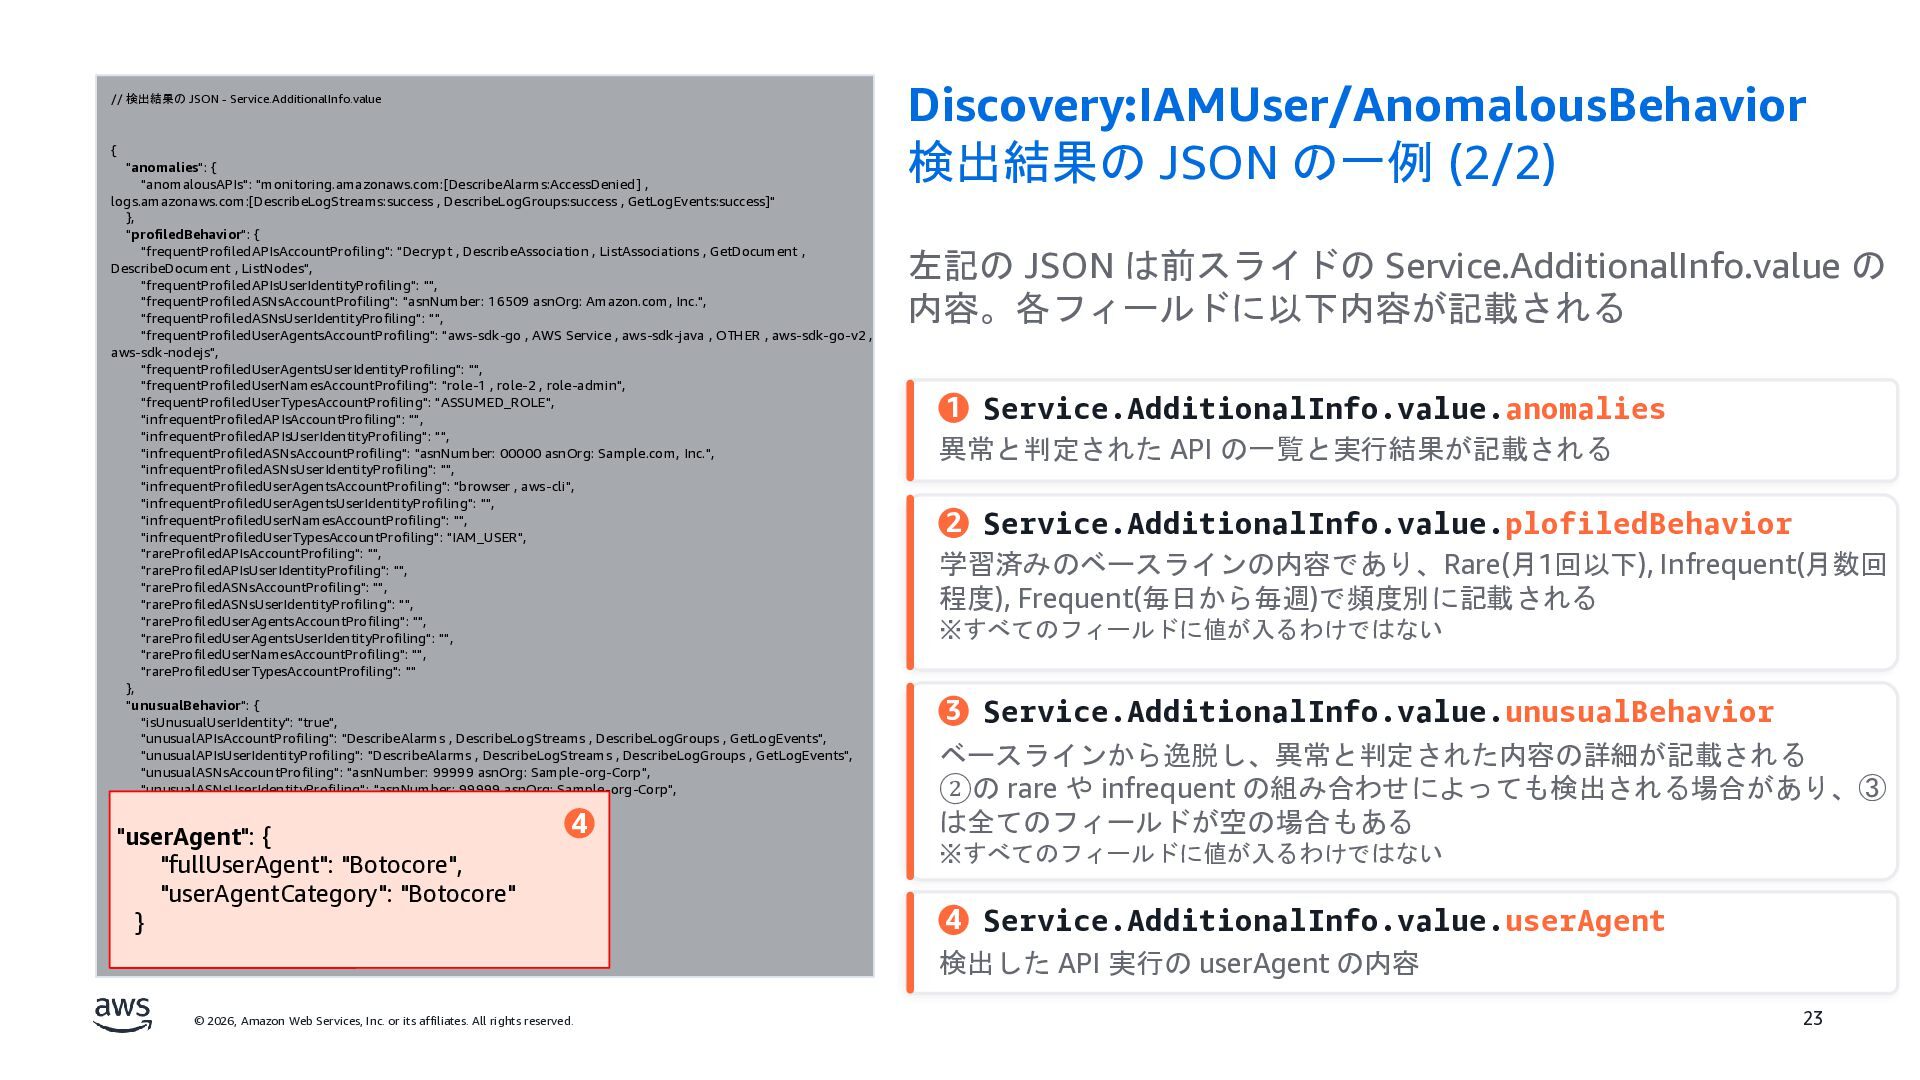
  21. // 検出結果の JSON - Service.AdditionalInfo.value { "anomalies": { "anomalousAPIs": "monitoring.amazonaws.com:[DescribeAlarms:AccessDenied]

    , logs.amazonaws.com:[DescribeLogStreams:success , DescribeLogGroups:success , GetLogEvents:success]" }, "profiledBehavior": { "frequentProfiledAPIsAccountProfiling": "Decrypt , DescribeAssociation , ListAssociations , GetDocument , DescribeDocument , ListNodes", "frequentProfiledAPIsUserIdentityProfiling": "", "frequentProfiledASNsAccountProfiling": "asnNumber: 16509 asnOrg: Amazon.com, Inc.", "frequentProfiledASNsUserIdentityProfiling": "", "frequentProfiledUserAgentsAccountProfiling": "aws-sdk-go , AWS Service , aws-sdk-java , OTHER , aws-sdk-go-v2 , aws-sdk-nodejs", "frequentProfiledUserAgentsUserIdentityProfiling": "", "frequentProfiledUserNamesAccountProfiling": "role-1 , role-2 , role-admin", "frequentProfiledUserTypesAccountProfiling": "ASSUMED_ROLE", "infrequentProfiledAPIsAccountProfiling": "", "infrequentProfiledAPIsUserIdentityProfiling": "", "infrequentProfiledASNsAccountProfiling": "asnNumber: 00000 asnOrg: Sample.com, Inc.", "infrequentProfiledASNsUserIdentityProfiling": "", "infrequentProfiledUserAgentsAccountProfiling": "browser , aws-cli", "infrequentProfiledUserAgentsUserIdentityProfiling": "", "infrequentProfiledUserNamesAccountProfiling": "", "infrequentProfiledUserTypesAccountProfiling": "IAM_USER", "rareProfiledAPIsAccountProfiling": "", "rareProfiledAPIsUserIdentityProfiling": "", "rareProfiledASNsAccountProfiling": "", "rareProfiledASNsUserIdentityProfiling": "", "rareProfiledUserAgentsAccountProfiling": "", "rareProfiledUserAgentsUserIdentityProfiling": "", "rareProfiledUserNamesAccountProfiling": "", "rareProfiledUserTypesAccountProfiling": "" }, "unusualBehavior": { "isUnusualUserIdentity": "true", "unusualAPIsAccountProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualAPIsUserIdentityProfiling": "DescribeAlarms , DescribeLogStreams , DescribeLogGroups , GetLogEvents", "unusualASNsAccountProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualASNsUserIdentityProfiling": "asnNumber: 99999 asnOrg: Sample-org-Corp", "unusualUserAgentsAccountProfiling": "", "unusualUserAgentsUserIdentityProfiling": "Botocore", "unusualUserNamesAccountProfiling": "Sample-User", "unusualUserTypesAccountProfiling": "" }, "userAgent": { "fullUserAgent": "Botocore", "userAgentCategory": "Botocore" } } "userAgent": { "fullUserAgent": "Botocore", "userAgentCategory": "Botocore" } 4 4 © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Discovery:IAMUser/AnomalousBehavior 検出結果の JSON の一例 (2/2) 左記の JSON は前スライドの Service.AdditionalInfo.value の 内容。各フィールドに以下内容が記載される 1 Service.AdditionalInfo.value.anomalies 異常と判定された API の一覧と実行結果が記載される 2 Service.AdditionalInfo.value.plofiledBehavior 学習済みのベースラインの内容であり、Rare(月1回以下), Infrequent(月数回 程度), Frequent(毎日から毎週)で頻度別に記載される ※すべてのフィールドに値が入るわけではない 3 Service.AdditionalInfo.value.unusualBehavior ベースラインから逸脱し、異常と判定された内容の詳細が記載される ②の rare や infrequent の組み合わせによっても検出される場合があり、③ は全てのフィールドが空の場合もある ※すべてのフィールドに値が入るわけではない 4 Service.AdditionalInfo.value.userAgent 検出した API 実行の userAgent の内容 23
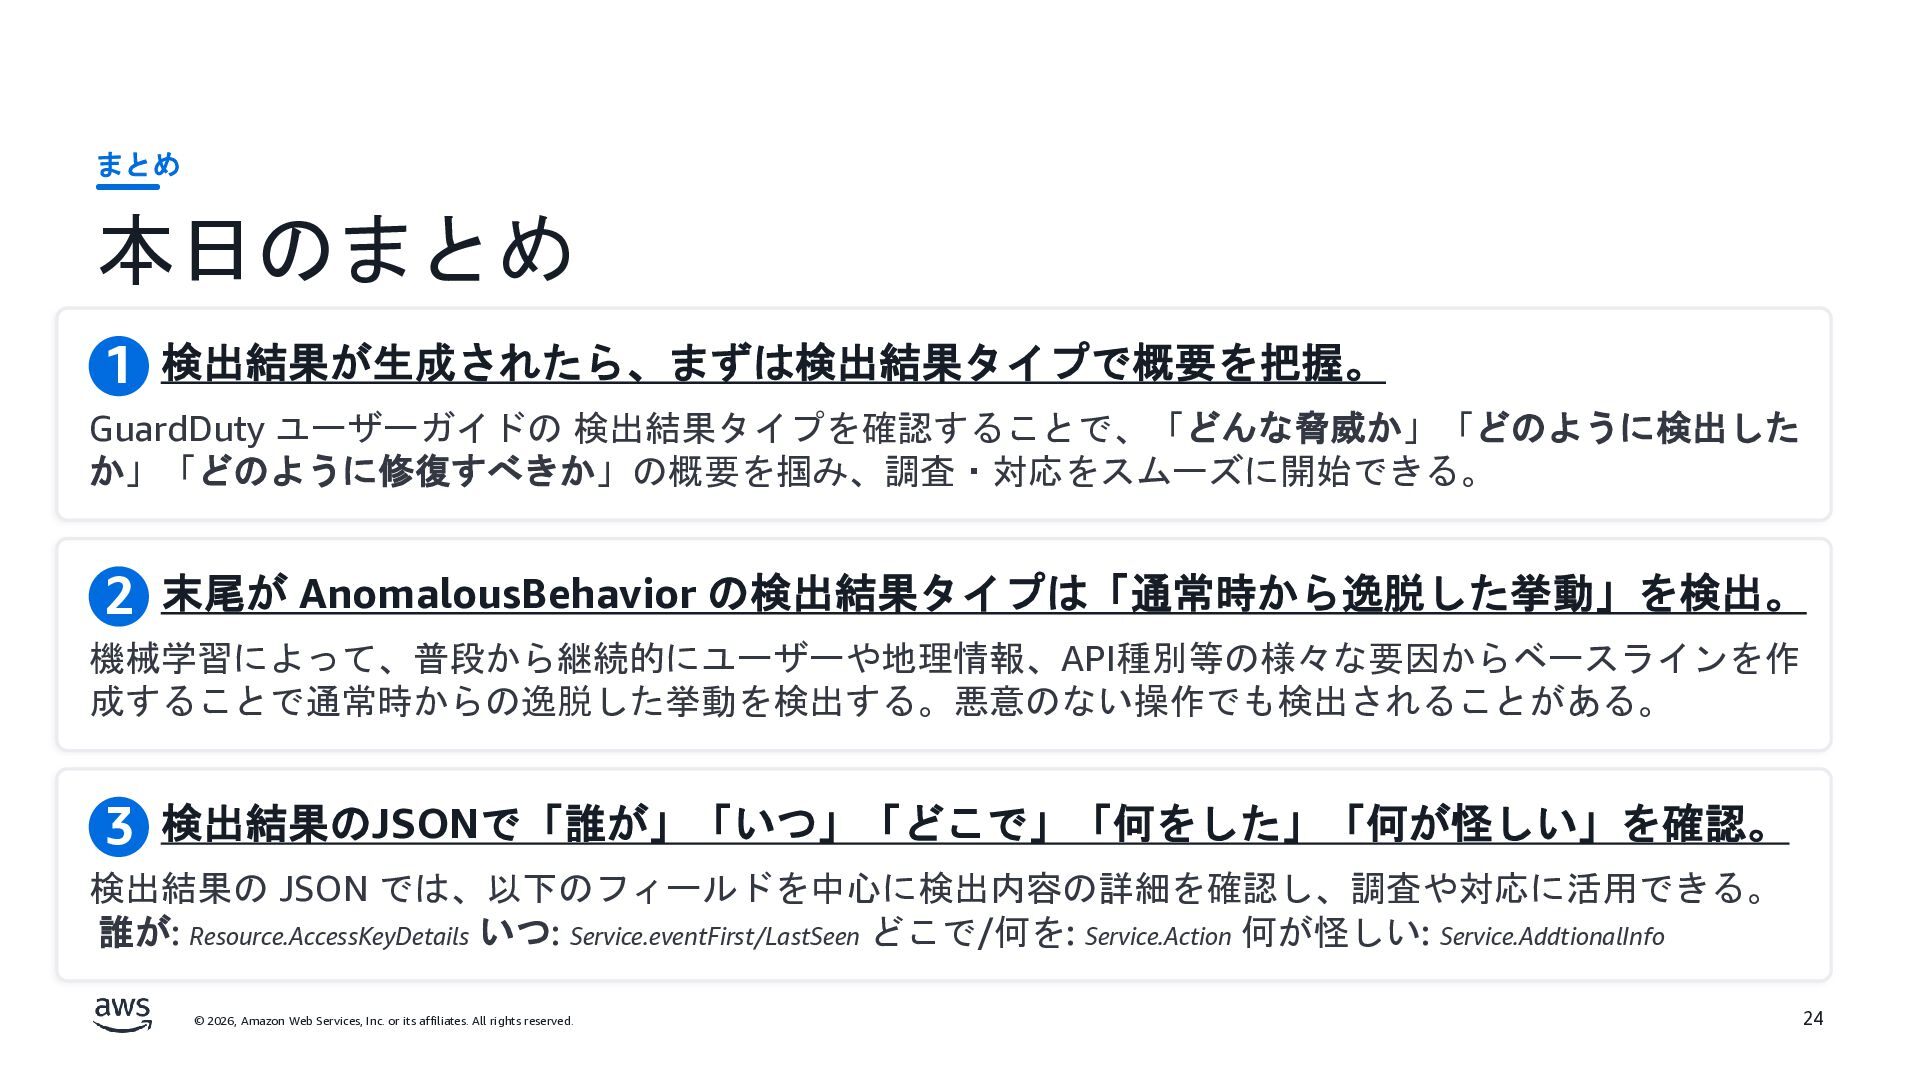
  22. まとめ 本日のまとめ 1 検出結果が生成されたら、まずは検出結果タイプで概要を把握。 GuardDuty ユーザーガイドの 検出結果タイプを確認することで、「どんな脅威か」「どのように検出した か」「どのように修復すべきか」の概要を掴み、調査・対応をスムーズに開始できる。 2 末尾が

    AnomalousBehavior の検出結果タイプは「通常時から逸脱した挙動」を検出。 機械学習によって、普段から継続的にユーザーや地理情報、API種別等の様々な要因からベースラインを作 成することで通常時からの逸脱した挙動を検出する。悪意のない操作でも検出されることがある。 3 検出結果のJSONで「誰が」「いつ」「どこで」「何をした」「何が怪しい」を確認。 検出結果の JSON では、以下のフィールドを中心に検出内容の詳細を確認し、調査や対応に活用できる。 誰が: Resource.AccessKeyDetails いつ: Service.eventFirst/LastSeen どこで/何を: Service.Action 何が怪しい: Service.AddtionalInfo © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. 24