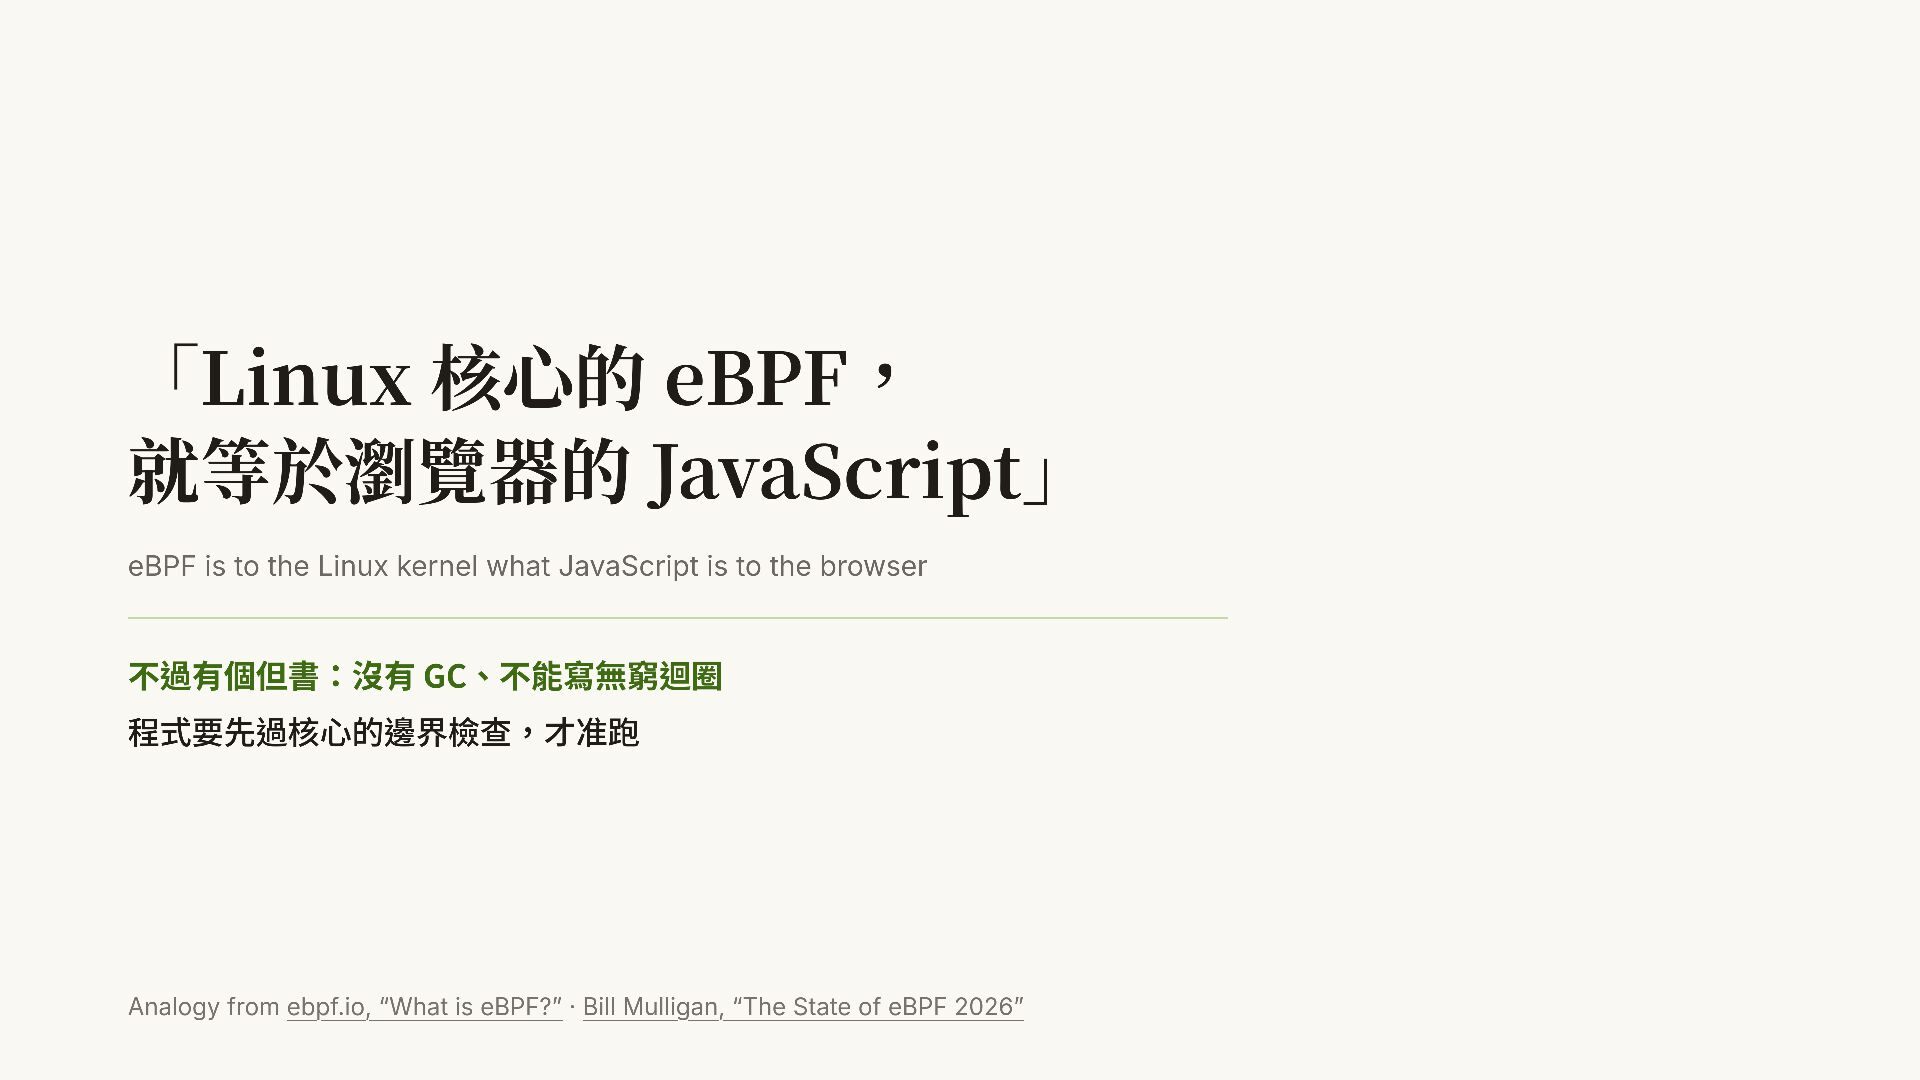
kernel what JavaScript is to the browser 不過有個但書:沒有 GC、不能寫無窮迴圈 程式要先過核心的邊界檢查,才准跑 Analogy from ebpf.io, “What is eBPF?” · Bill Mulligan, “The State of eBPF 2026”
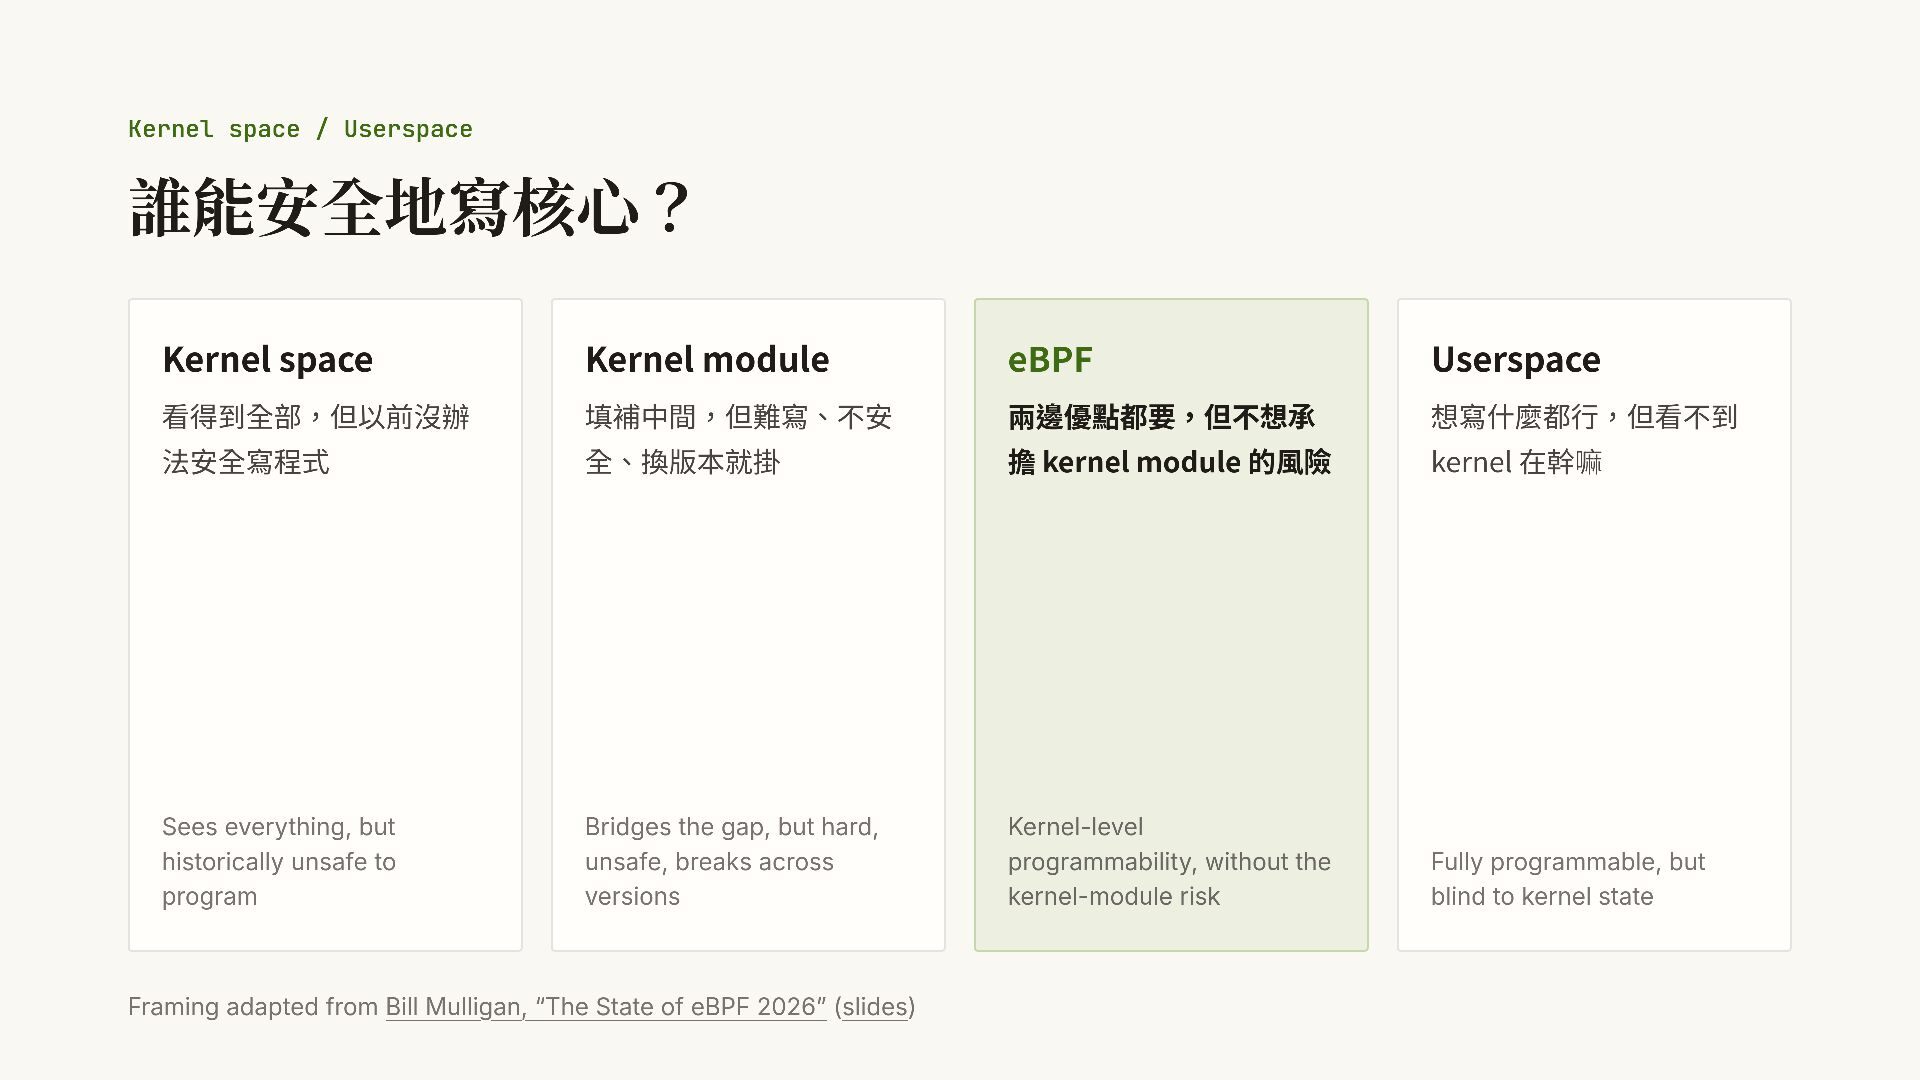
Userspace 看得到全部,但以前沒辦 填補中間,但難寫、不安 兩邊優點都要,但不想承 想寫什麼都行,但看不到 法安全寫程式 全、換版本就掛 擔 kernel module 的風險 kernel 在幹嘛 Sees everything, but historically unsafe to program Bridges the gap, but hard, unsafe, breaks across versions Kernel-level programmability, without the kernel-module risk Fully programmable, but blind to kernel state Framing adapted from Bill Mulligan, “The State of eBPF 2026” (slides)
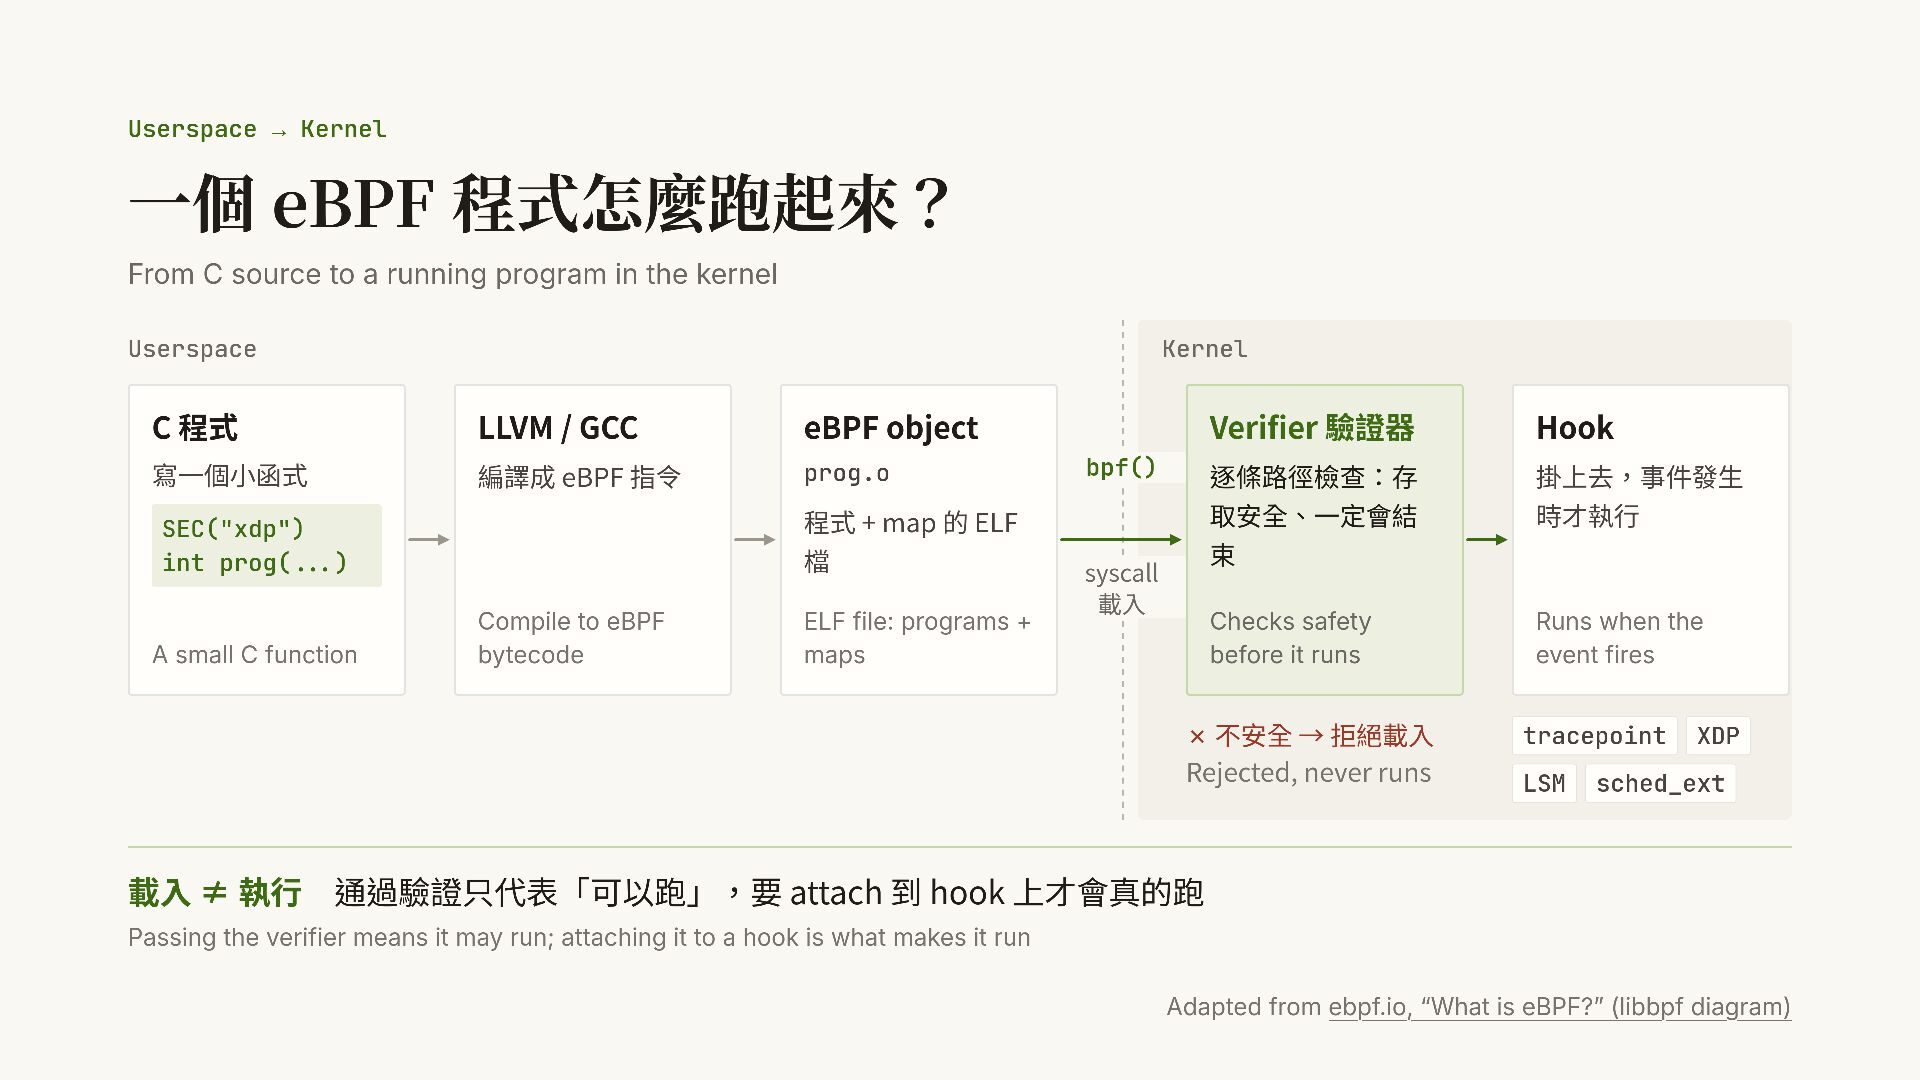
a running program in the kernel Userspace Kernel C 程式 LLVM / GCC eBPF object 寫一個小函式 編譯成 eBPF 指令 prog.o 程式 + map 的 ELF 檔 SEC("xdp") int prog(...) A small C function Compile to eBPF bytecode ELF file: programs + maps bpf() syscall 載入 Verifier 驗證器 Hook 逐條路徑檢查:存 取安全、一定會結 束 掛上去,事件發生 時才執行 Checks safety before it runs Runs when the event fires ✗ 不安全 → 拒絕載入 Rejected, never runs 載入 ≠ 執行 tracepoint LSM XDP sched_ext 通過驗證只代表「可以跑」,要 attach 到 hook 上才會真的跑 Passing the verifier means it may run; attaching it to a hook is what makes it run Adapted from ebpf.io, “What is eBPF?” (libbpf diagram)
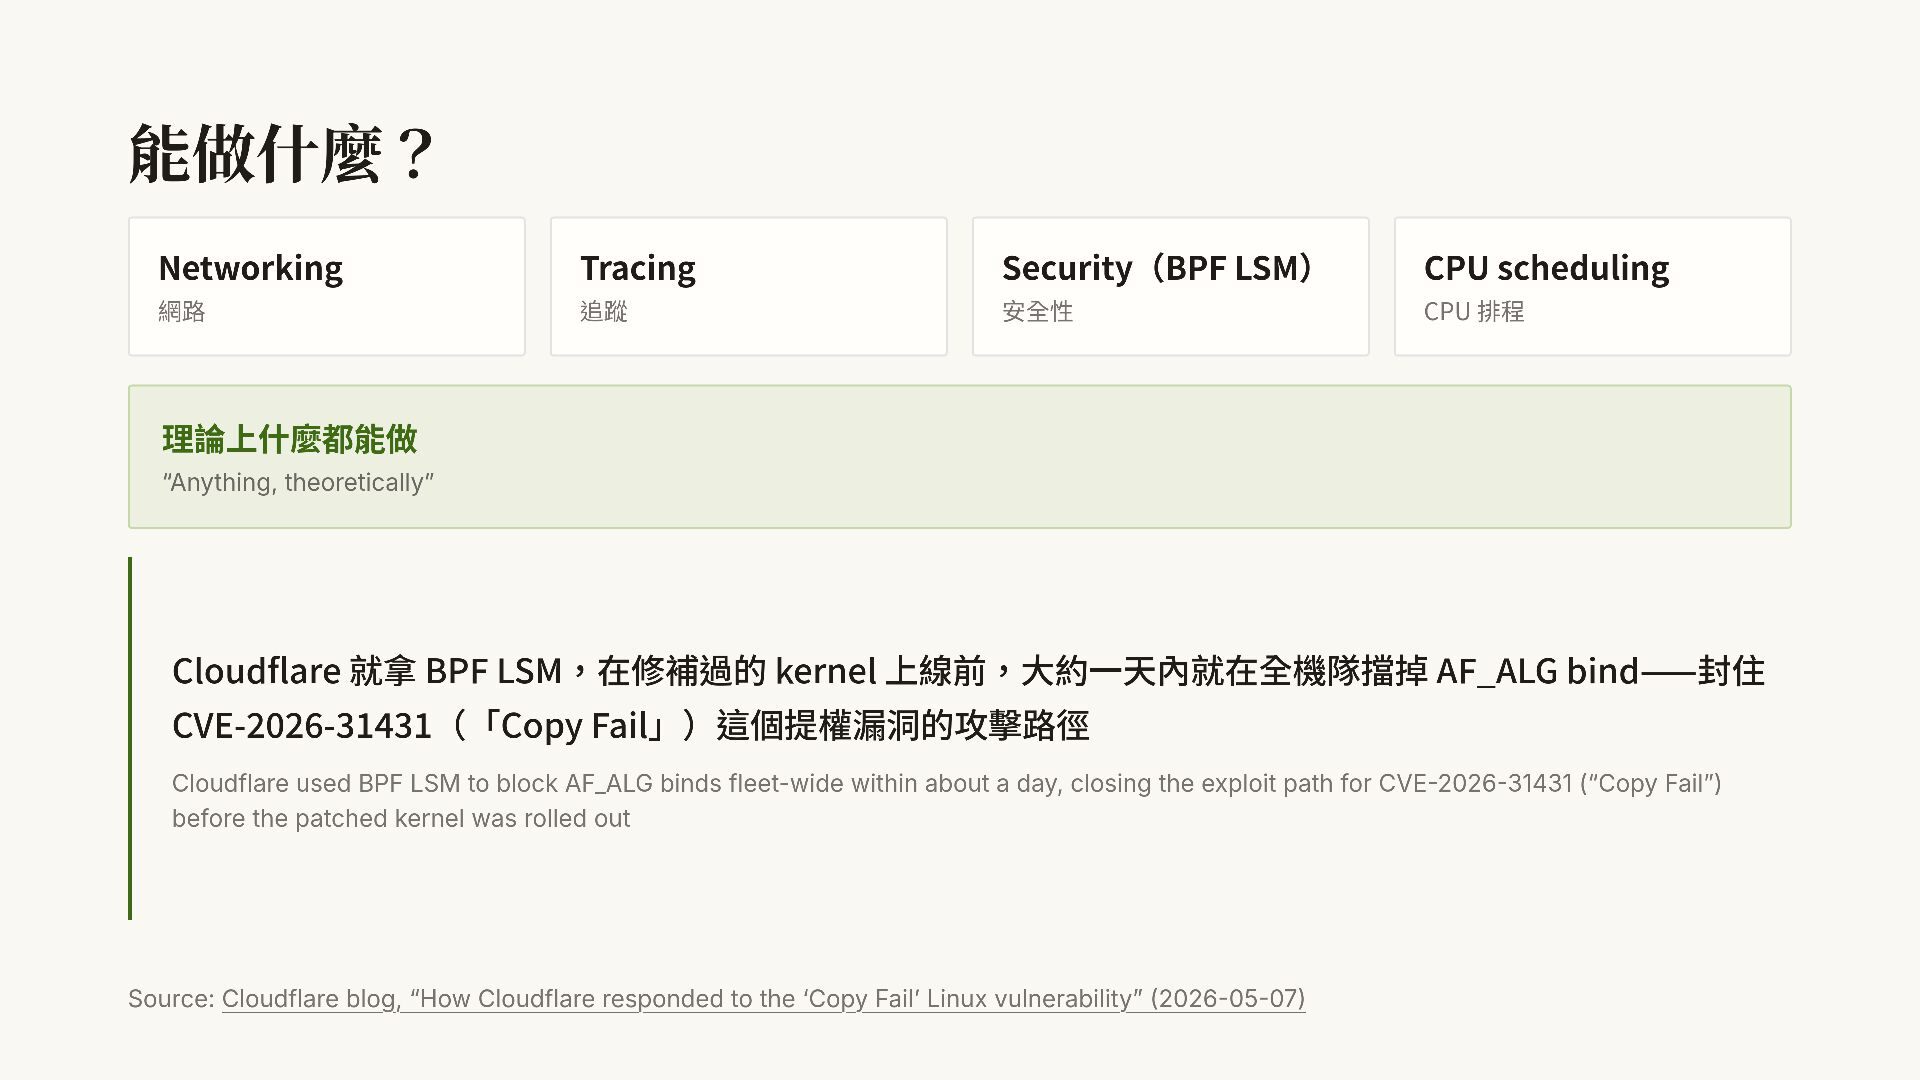
CPU 排程 理論上什麼都能做 “Anything, theoretically” Cloudflare 就拿 BPF LSM,在修補過的 kernel 上線前,大約一天內就在全機隊擋掉 AF_ALG bind——封住 CVE-2026-31431(「Copy Fail」)這個提權漏洞的攻擊路徑 Cloudflare used BPF LSM to block AF_ALG binds fleet-wide within about a day, closing the exploit path for CVE-2026-31431 (“Copy Fail”) before the patched kernel was rolled out Source: Cloudflare blog, “How Cloudflare responded to the ‘Copy Fail’ Linux vulnerability” (2026-05-07)
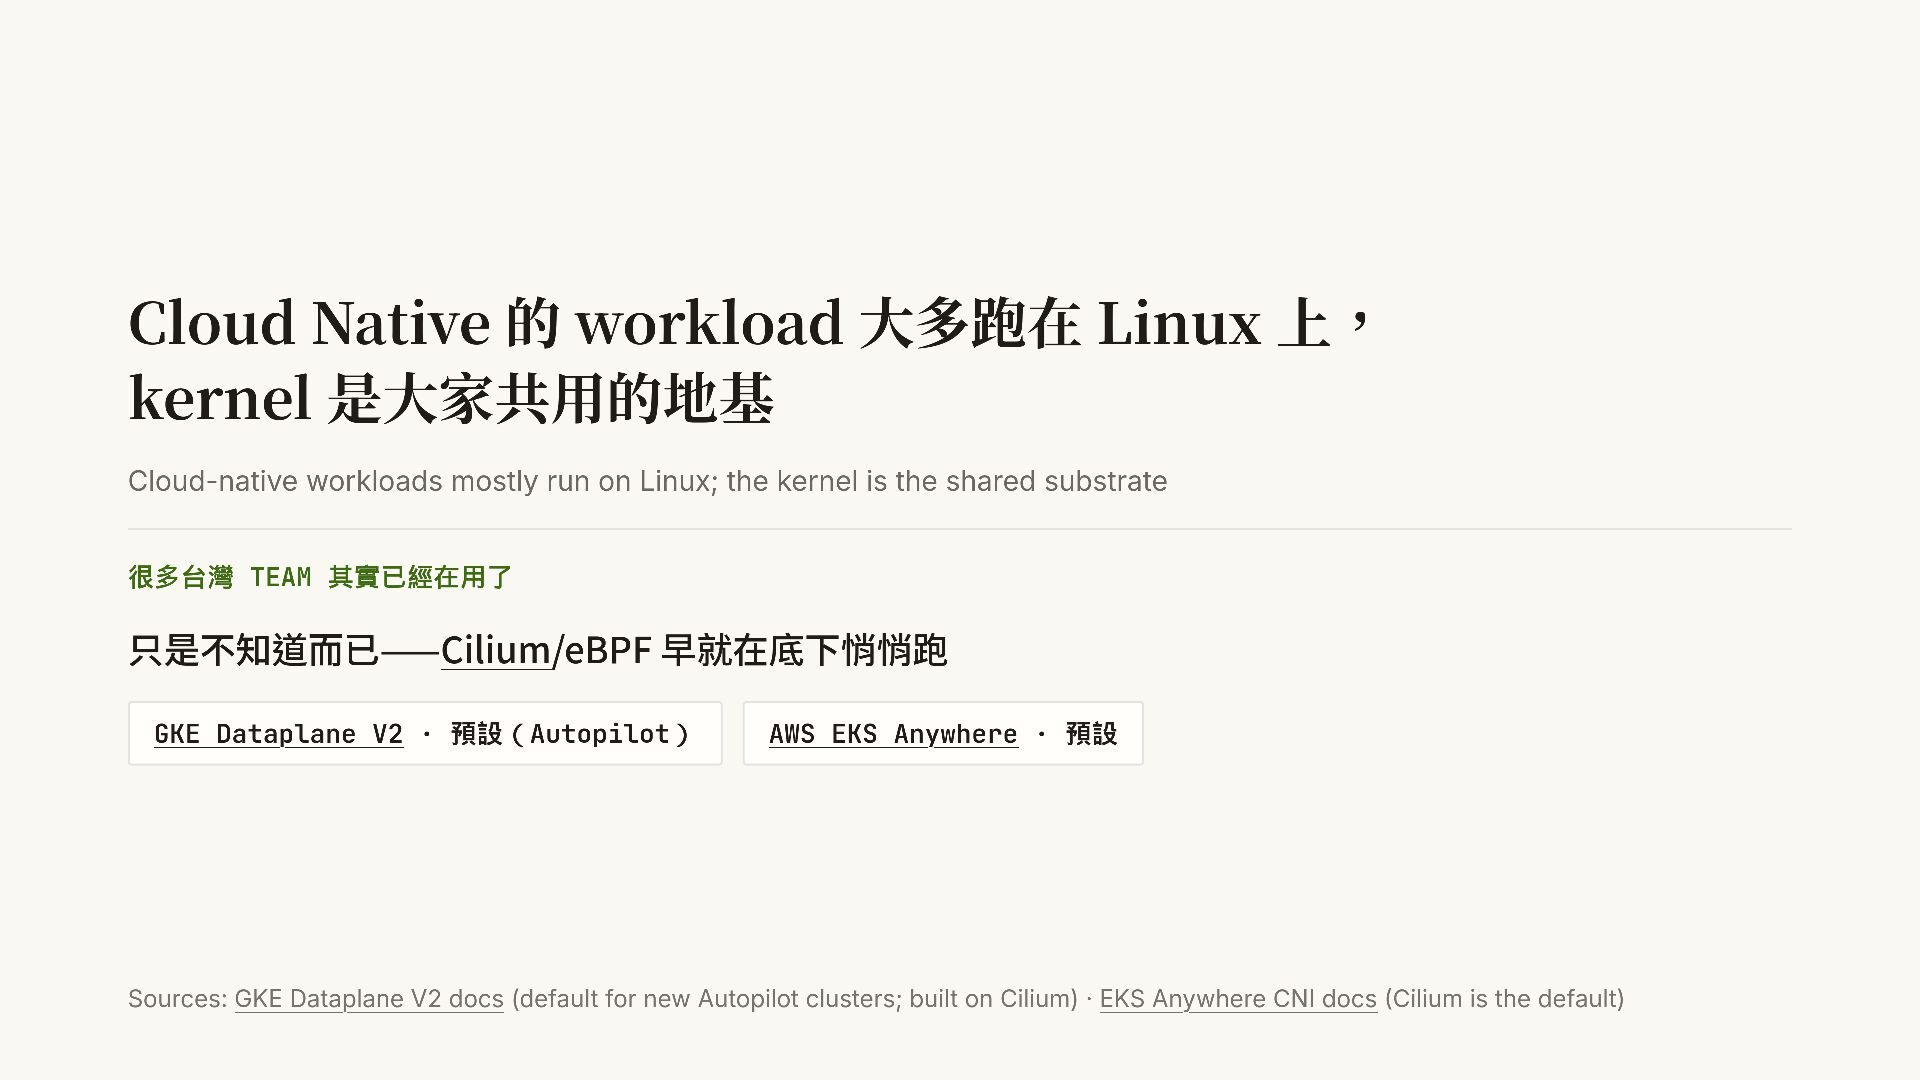
workloads mostly run on Linux; the kernel is the shared substrate 很多台灣 TEAM 其實已經在用了 只是不知道而已——Cilium/eBPF 早就在底下悄悄跑 GKE Dataplane V2 · 預設(Autopilot) AWS EKS Anywhere · 預設 Sources: GKE Dataplane V2 docs (default for new Autopilot clusters; built on Cilium) · EKS Anywhere CNI docs (Cilium is the default)
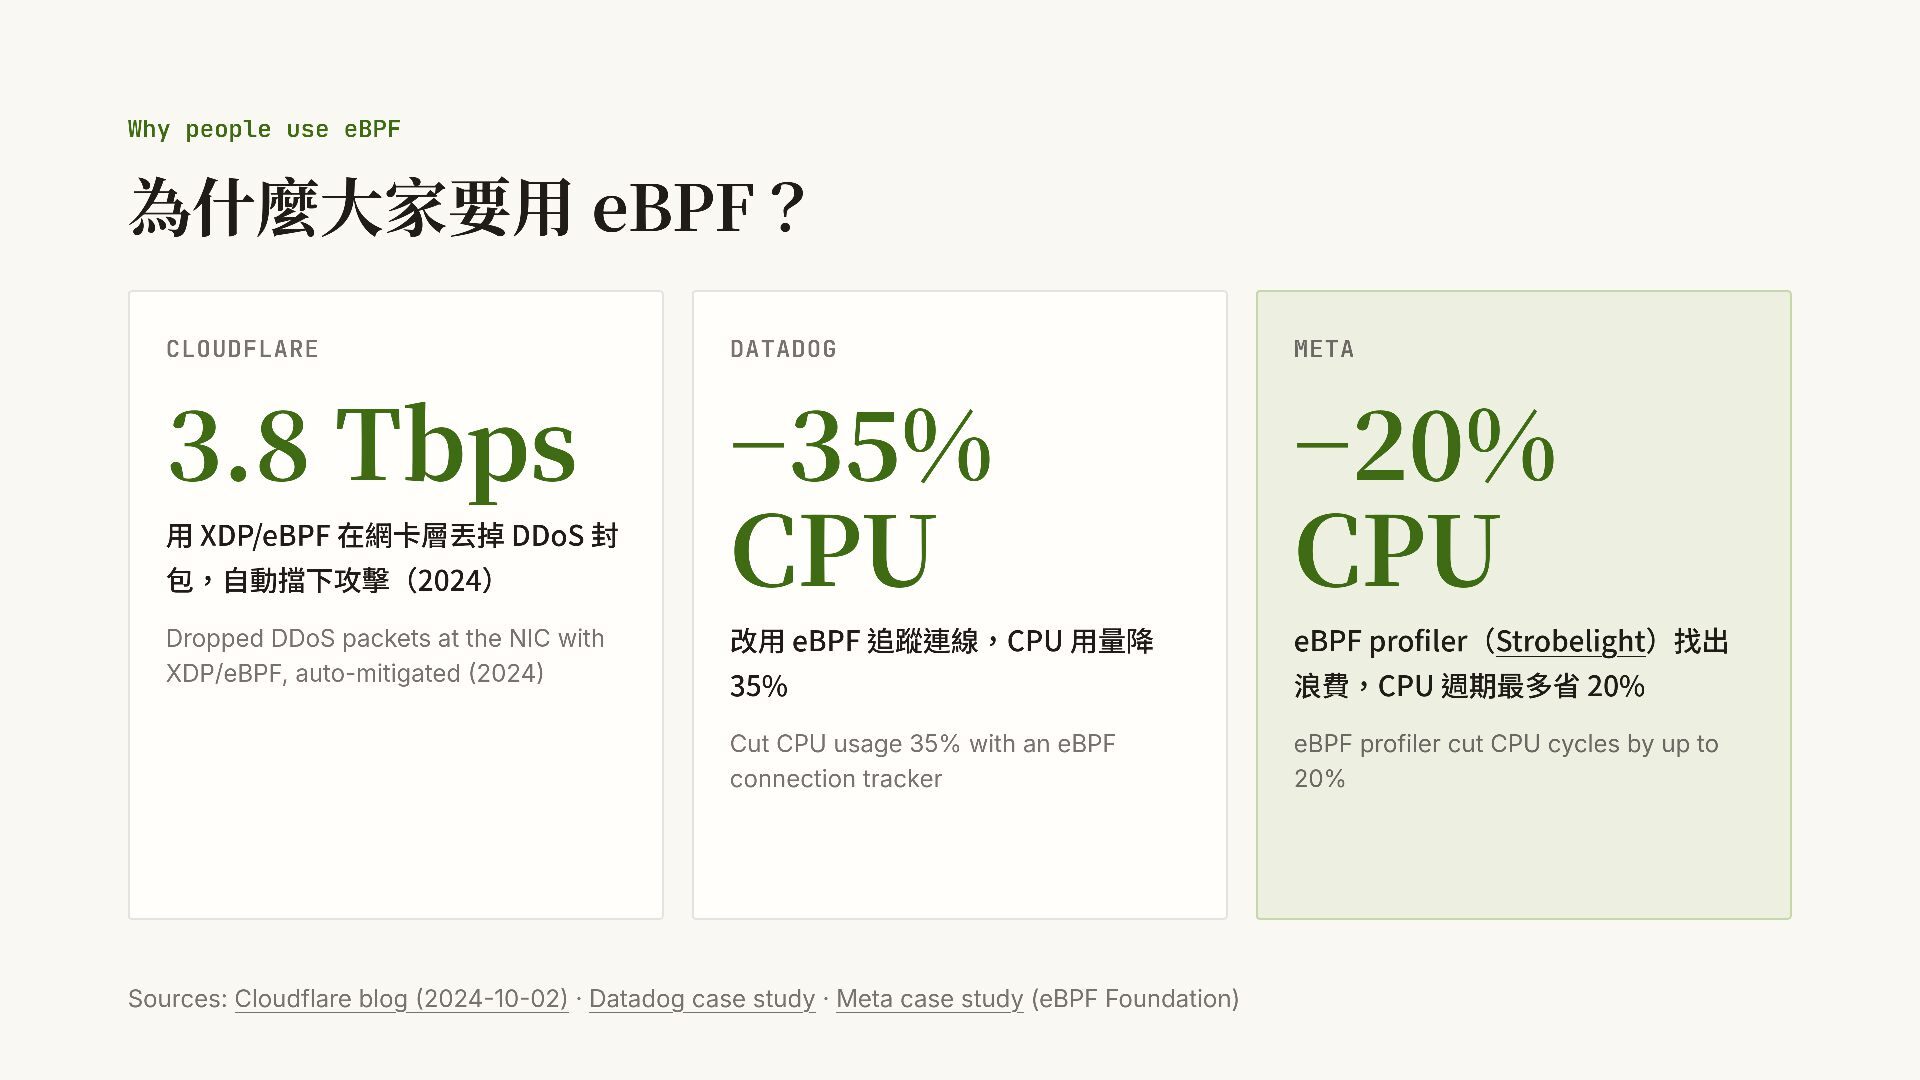
Tbps −35% CPU −20% CPU 改用 eBPF 追蹤連線,CPU 用量降 eBPF profiler(Strobelight)找出 35% 浪費,CPU 週期最多省 20% Cut CPU usage 35% with an eBPF connection tracker eBPF profiler cut CPU cycles by up to 20% 用 XDP/eBPF 在網卡層丟掉 DDoS 封 包,自動擋下攻擊(2024) Dropped DDoS packets at the NIC with XDP/eBPF, auto-mitigated (2024) Sources: Cloudflare blog (2024-10-02) · Datadog case study · Meta case study (eBPF Foundation)


 shunghsiyu
 eluwing
 mito201
 sato4mi
 kinunori
 tgidgd
 ryomaru0825
 oracle4engineer
 miu_crescent
 myohei
 happysamurai294
 kitazaki
 snoozer05
 ryanjones
 sferik
 reverentgeek
 sabderemane
 lara
 samlambert
 iamctodd
 carmenintech
 leimatthew05
 maggiecrowley
 takai
 sergeychernyshev