Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
The Most Dangerous Game
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
Scott J. Roberts
February 03, 2015
Technology
5.4k
5
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
The Most Dangerous Game
A presentation about merging Threat Intelligence and DFIR by the team behind YoloThre.at.
Scott J. Roberts
February 03, 2015
More Decks by Scott J. Roberts
See All by Scott J. Roberts
LLM SATs FTW
sroberts
0
1.8k
STRAT - A System-Centric Approach to Cyber Resilience
sroberts
0
130
Tortured Responders Dept - Scott & Rebekah's Edition
sroberts
0
200
Skynet the CTI Intern: Building Effective Machine Augmented Intelligence
sroberts
0
230
DRIVING INTELLIGENCE WITH MITRE ATT&CK: LEVERAGING LIMITED RESOURCES TO BUILD AN EVOLVING THREAT REPOSITORY
sroberts
0
170
Exploring Threat Intelligence: Insights and Tools from Vertex Synapse
sroberts
0
170
Homemade Ramen & Threat Intelligence
sroberts
2
670
Introduction to Open Source Security Tools
sroberts
3
5.1k
Building Effective Threat Intelligence Sharing
sroberts
1
170
Other Decks in Technology
See All in Technology
続・ソフトウェアアーキテクトのための意思決定術: Decision Readiness, Revisited — When AI Changes the Economics of Software Architecture
snoozer05
PRO
5
1.3k
(swiftc) NonCopyableとライフタイム修飾子
teamhimeh
0
170
You Have Agency(サンキュー、Ruby)
snoozer05
PRO
5
680
AI Agent 時代のデータ基盤: ClickHouse で実現する 超高速分析とコスト削減の両立
jozono
0
160
新米を「売り越さない」、Aurora DSQLで作る在庫ゼロ死守の限定ドロップEC
yama3133
0
170
AIに任せられるFlutterコードベースを作る 〜仕様をコードで表し、ハーネスで守る〜
myohei
1
630
視野はAIに、視座は人に / ai-for-breadth-humans-for-perspective
nkzn
6
3k
AIで選択肢が広がった組織設計の理想と現実
konifar
16
7.7k
【dbts2026】AIエージェントの 判断と探索を変える、 データベース エンジニアリング― 既存DBの処理と依存関係から作る、オペレーショナルオントロジー ―
shisyu_gaku
0
120
In-Context Learning再入門。ICLの勾配降下的解釈の研究動向を追ってみる。
dai08srhg
1
240
AX時代の自治体支援リソース再配分と役割分担の再構成:戦略とロードマップ(概要)
sishi2026
0
190
Software Engineering in an AI-Driven World
erikjhordan_rey
0
110
Featured
See All Featured
Put a Button on it: Removing Barriers to Going Fast.
kastner
60
4.6k
Code Review Best Practice
trishagee
74
20k
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
370
Building a A Zero-Code AI SEO Workflow
portentint
PRO
0
810
Dominate Local Search Results - an insider guide to GBP, reviews, and Local SEO
greggifford
PRO
0
400
[Rails World 2023 - Day 1 Closing Keynote] - The Magic of Rails
eileencodes
38
3.1k
DBのスキルで生き残る技術 - AI時代におけるテーブル設計の勘所
soudai
PRO
68
60k
The untapped power of vector embeddings
frankvandijk
2
2k
Ruling the World: When Life Gets Gamed
codingconduct
0
430
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
Gemini Prompt Engineering: Practical Techniques for Tangible AI Outcomes
mfonobong
2
620
Easily Structure & Communicate Ideas using Wireframe
afnizarnur
194
17k
Transcript
The Most Dangerous Game Hunting Adversaries Across the Internet
Kyle Maxwell Super Special Security Researcher @ iDefense
Scott J Roberts Advanced Persistent Incident Responder @ GitHub
How Kyle met Scott or How Scott met Kyle
If you are on the Twitter we’re @kylemaxwell & @sroberts
#YOLOTHREAT
Intelligence Concepts That everyone knows and already agrees on right…?
Data vs Intelligence Intelligence has gone through the intelligence process
Data is a raw piece of information without context
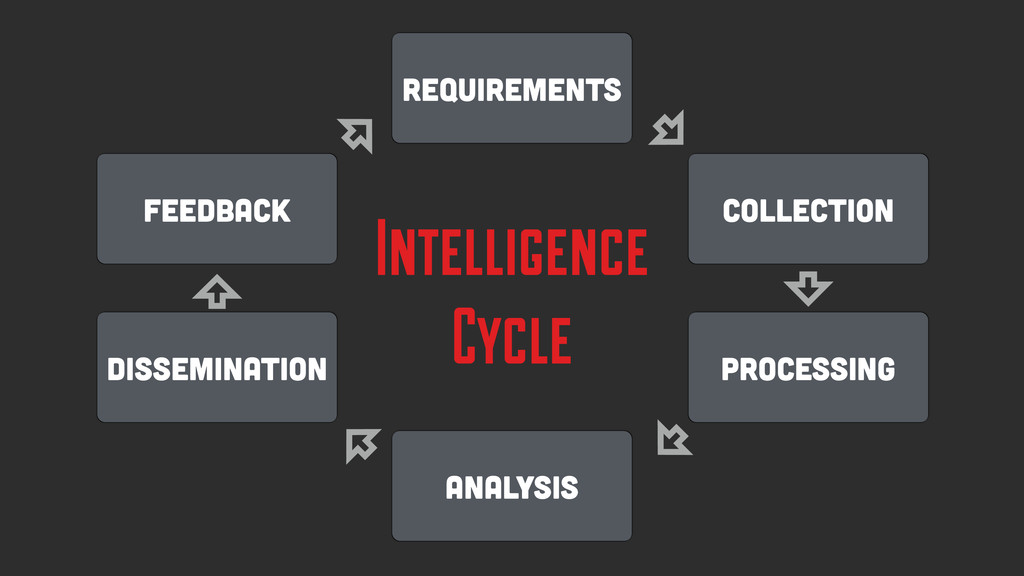
Feedback Analysis Processing Dissemination Collection Requirements Intelligence Cycle
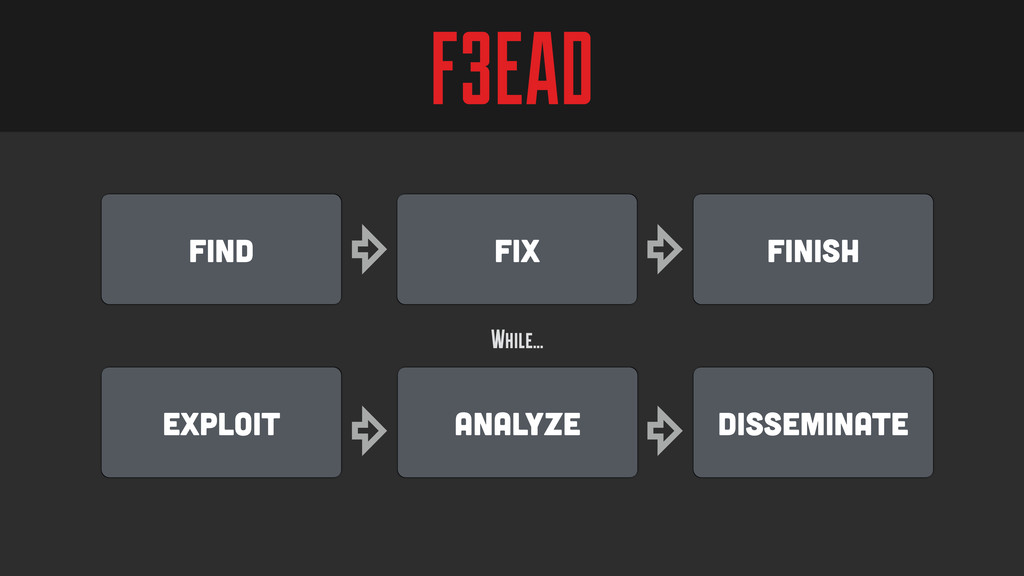
F3EAD While… Find Exploit Finish Disseminate Fix Analyze
The Target
What is Targeting? Making a plan for focusing threat research
& investigation
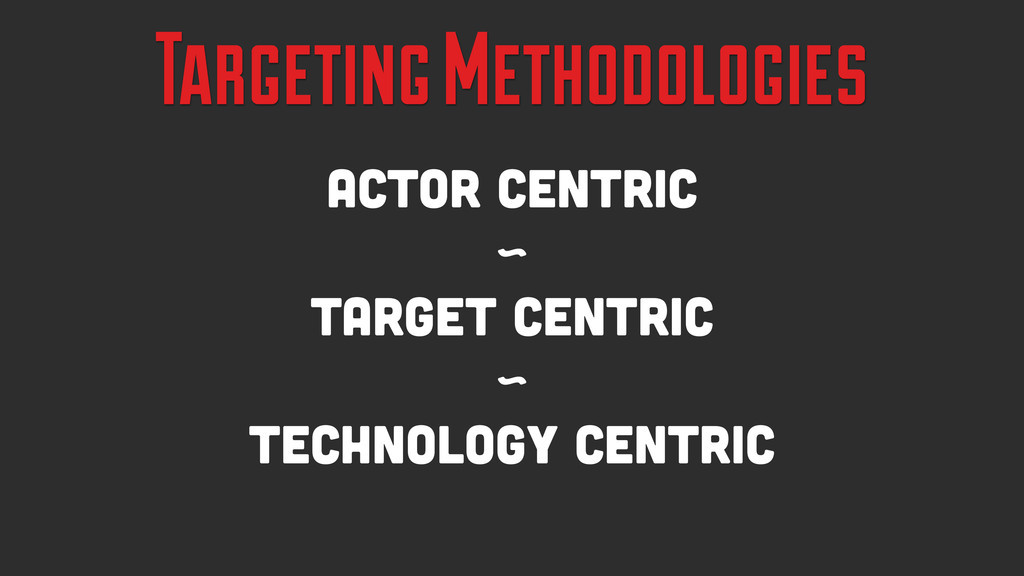
Targeting Methodologies Actor Centric ~ Target Centric ~ Technology centric
Feeds Needles in Haystacks
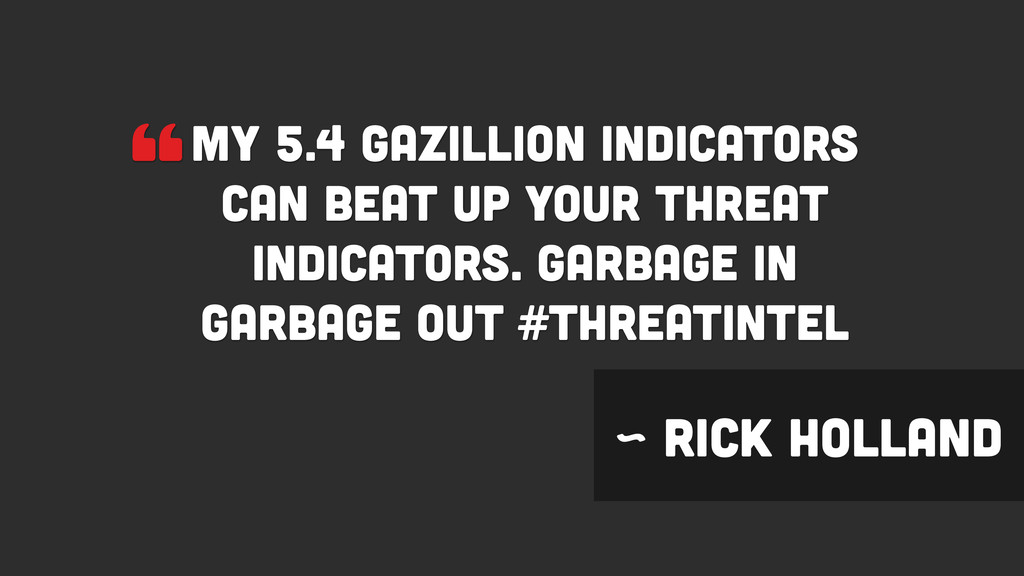
“My 5.4 gazillion indicators can beat up your threat indicators.
Garbage in garbage out #ThreatIntel ~ Rick Holland
Honeypots Bringing the Bad Guys to You
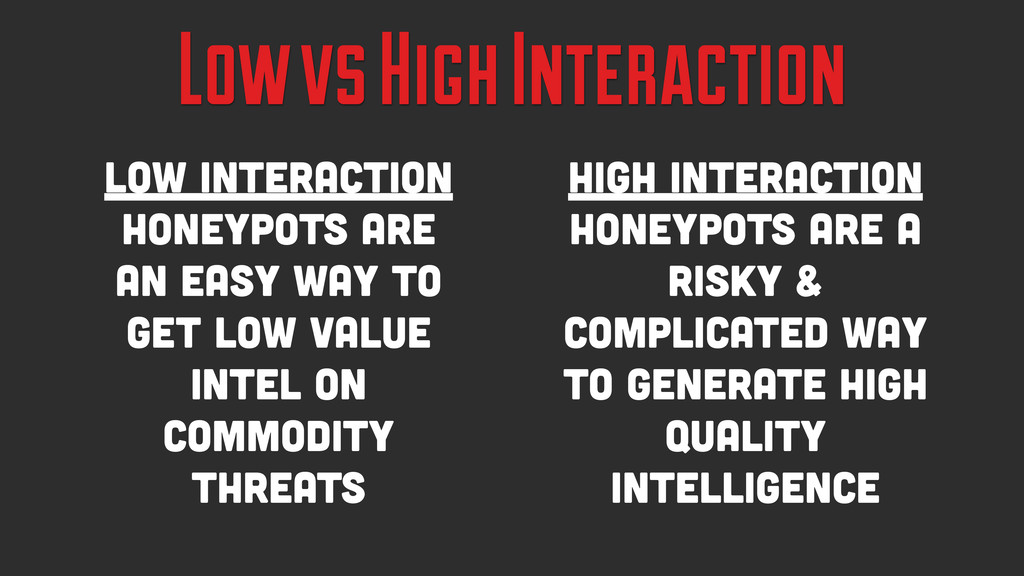
Low vs High Interaction High interaction honeypots are a risky
& complicated way to generate high quality intelligence Low interaction honeypots are an easy way to get low value intel on commodity threats
Software Old School: HoneyNet Project New Hotness: Modern Honey Network
by Threat Stream
Vulnerability Information Taking care of your Toys
“Structured vulnerability analysis is not threat intelligence it is requirements
gathering for threat intelligence. ~ @selil
Vendor Information Blogs ~ Reports ~ Services & APIs
Personal Aside to Vendors If you’re going to release a
report, blog post, etc: do not break the Cut and Copy Actions
None
Review Your Own Incidents Mine that fancy Incident Management System…
Review Your Others Incidents By sharing or News mining
The Hunt
What to Analyze Technical Sources
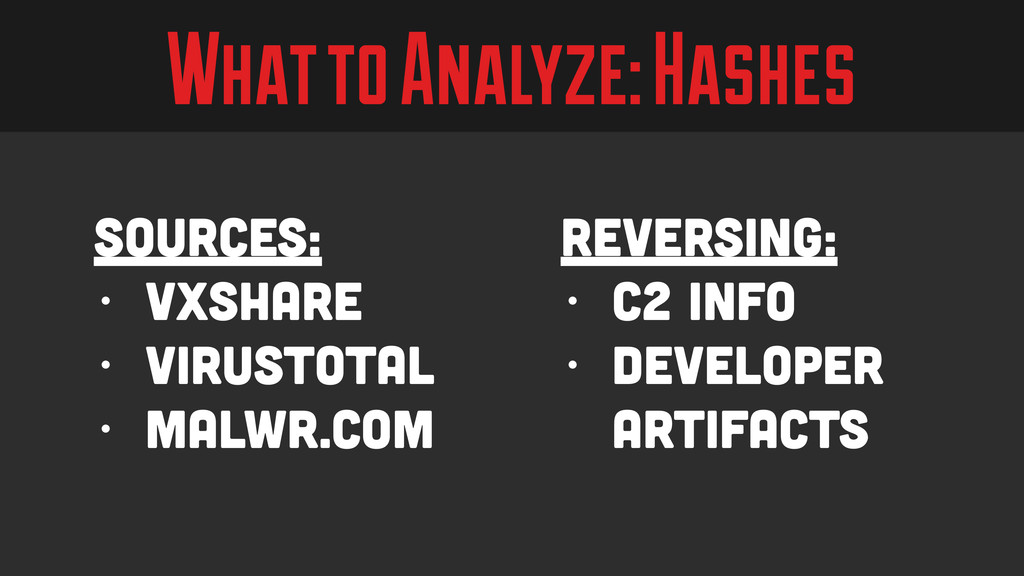
What to Analyze: Hashes Reversing: • C2 info • Developer
artifacts Sources: • VxShare • VirusTotal • malwr.com
What to Analyze: Passive DNS • Single most useful tool
for infrastructure research • What resolved to what, and when? • DNSDB (Farsight), PassiveTotal, VirusTotal
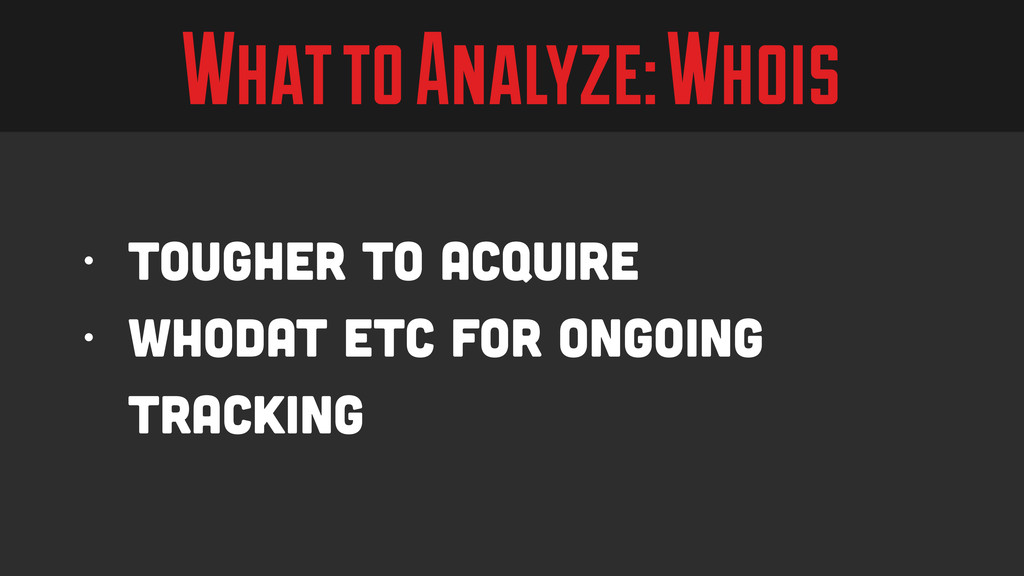
What to Analyze: Whois • Tougher to Acquire • WhoDat
etc for ongoing Tracking
What to Analyze Actors
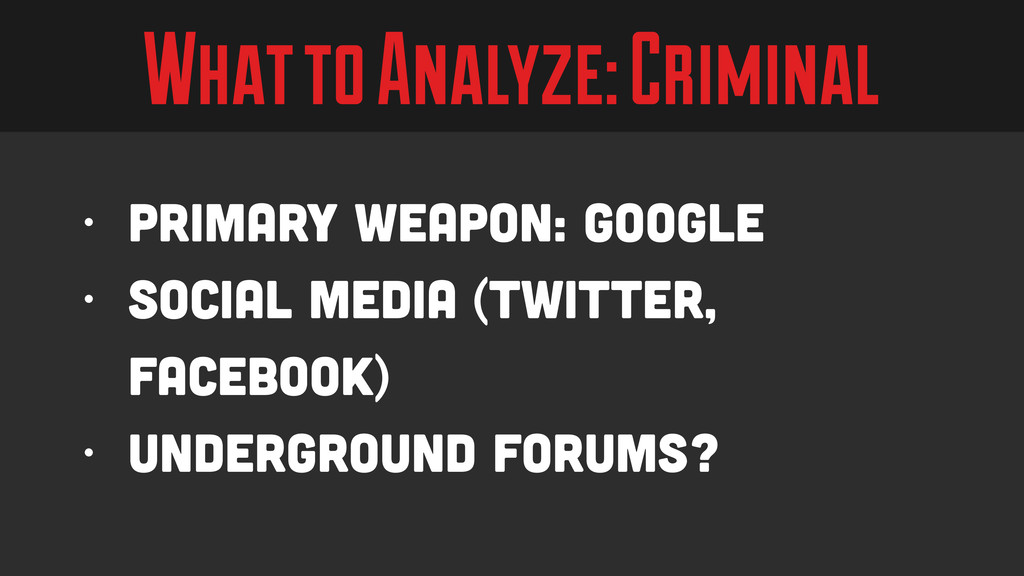
What to Analyze: Criminal • Primary Weapon: Google • Social
Media (Twitter, Facebook) • Underground forums?
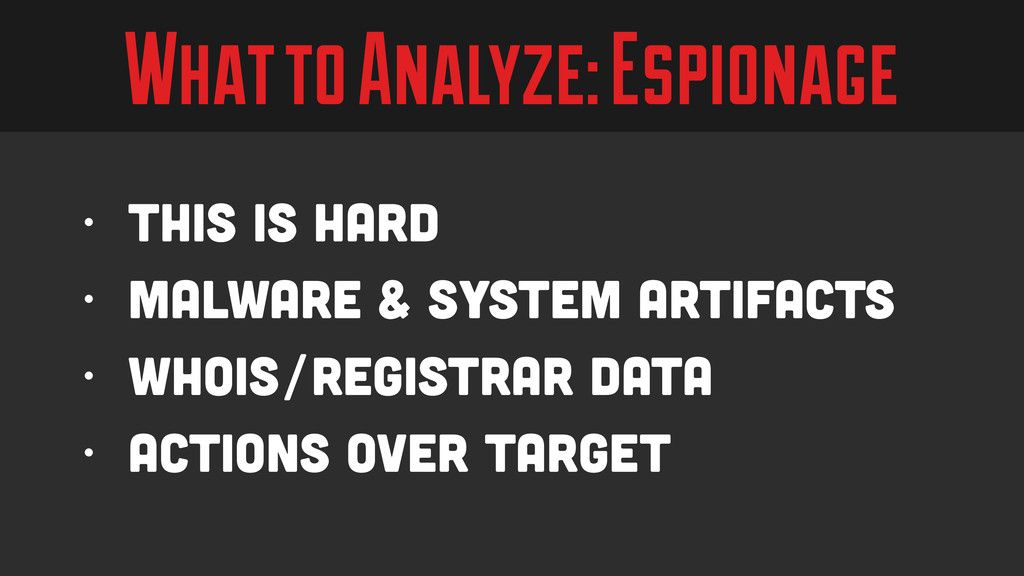
What to Analyze: Espionage • This is hard • Malware
& System artifacts • whois/registrar data • actions over target
How to Keep Tracking
Threat Library • CRITs is popular, MISP also • Lighter
solutions often work • Market hasn't fully addressed this
Web Monitoring Systems • Netflix Scumblr Meta SearcH (Works alongside
Sketchy) • Recorded Future • Lots of custom development
Malware Monitoring • VirusTotal is • Malware feeds with Lots
of custom internal solutions • Maltrieve, Viper, & Cuckoo
Internal Logging • Firewall, IDS, & Proxy • Web, mail,
& DNS • Authentication & Audit
The “Kill”
Incident Response The Entire Goal… Right?
The Imitation Game Don’t let them know that you know
that they know…
Attribution Probably doesn’t matter unless you can do this
Hand Cuffs or Cruise Missiles
KICK ‘EM OUT NOW! Sometimes it’s better to watch for
a while
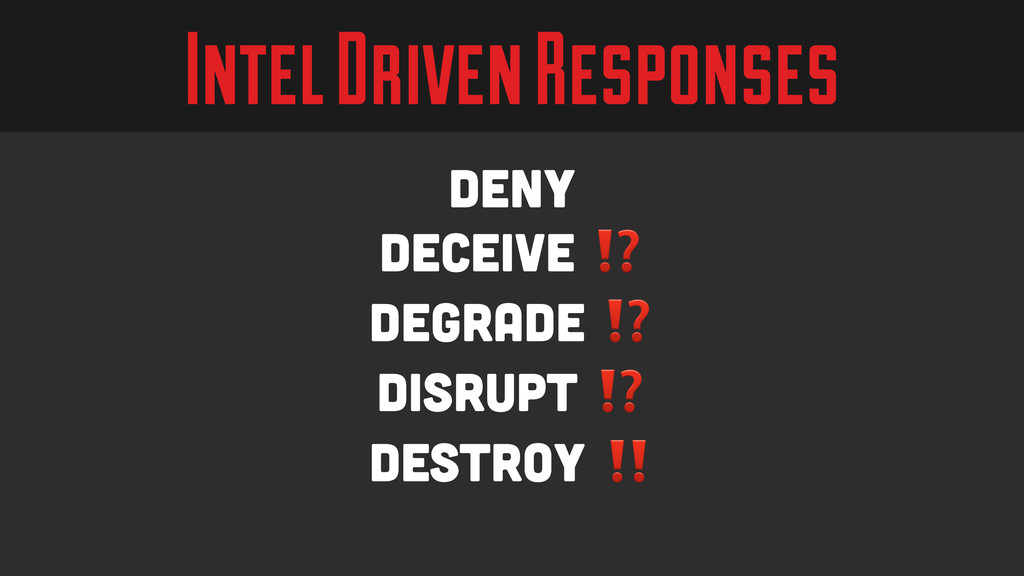
Intel Driven Responses deny Deceive ⁉️ degrade ⁉️ disrupt ⁉️
Destroy ‼️
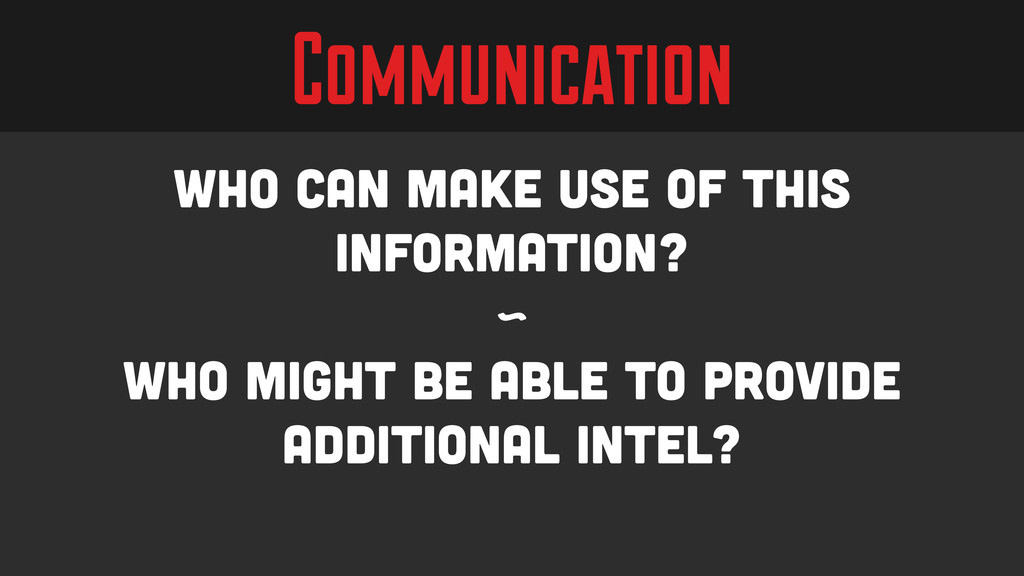
Communication Who can make use of this information? ~ Who
might be able to provide additional intel?
The Hunting Stories
Products IOCs & RFIs ~ Short Form Products ~ Long
Form Products
Audience Internal - Team Internal - Organization External - Peers
External - Wide
IOCs - Generalized Stix & OpenIOC
“you pretty much need a PHD in XML to understand
either STIX or TAXII ~ Jeff Bryner
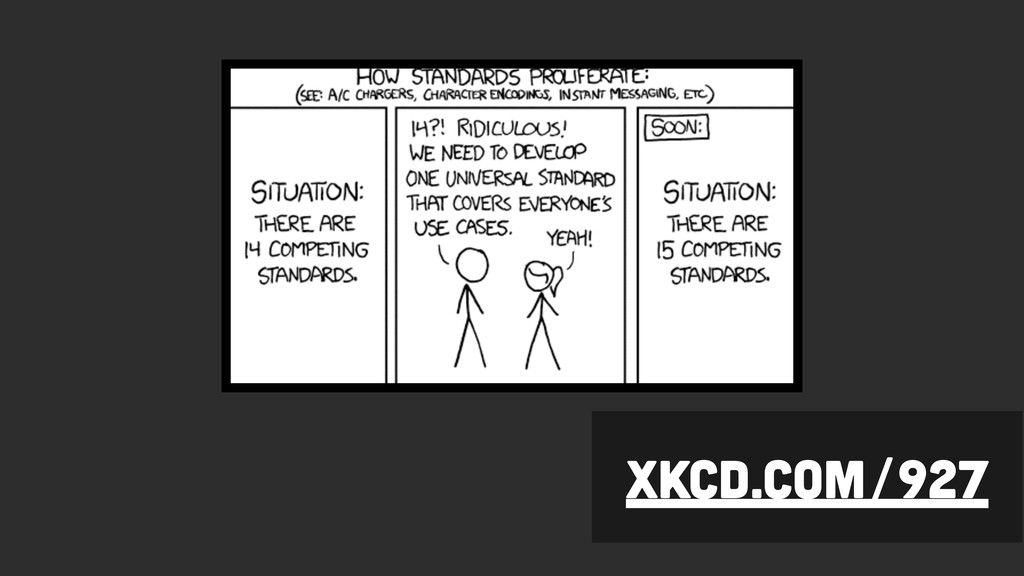
XKCD.com/927
IOCs - Specialized Yara: Malware centric av signature style IOCs,
getting more advanced Snort: Go to for network activity, Comprehensive and well supported
“OH: "Yara is an antivirus that you update using git
pull" ~ @tomchop_
Requests For Intelligence A Q/A requesting very specific Intelligence ~
Shortest form Possible ~ Fastest turn around
Short Form Products Intermediate products to support incident response ~
Focus on actionable Information
Long Form Products Comprehensive “All Source” intelligence products ~ Requires
considerable Time & a well rounded team
The Surprise…
You Can’t Download a Threat Intelligence Until now….
The Surprise Coming out of Stealth Today, our new Startup…
YOLOTHRE.At
Announcement yolothre.at has run out of runway (We used up
our whole Starbucks Gift Card) SO we’re open sourcing everything and going back to our old jobs...
YoloThre.at A collection of open source docker containers for Threat
Intel
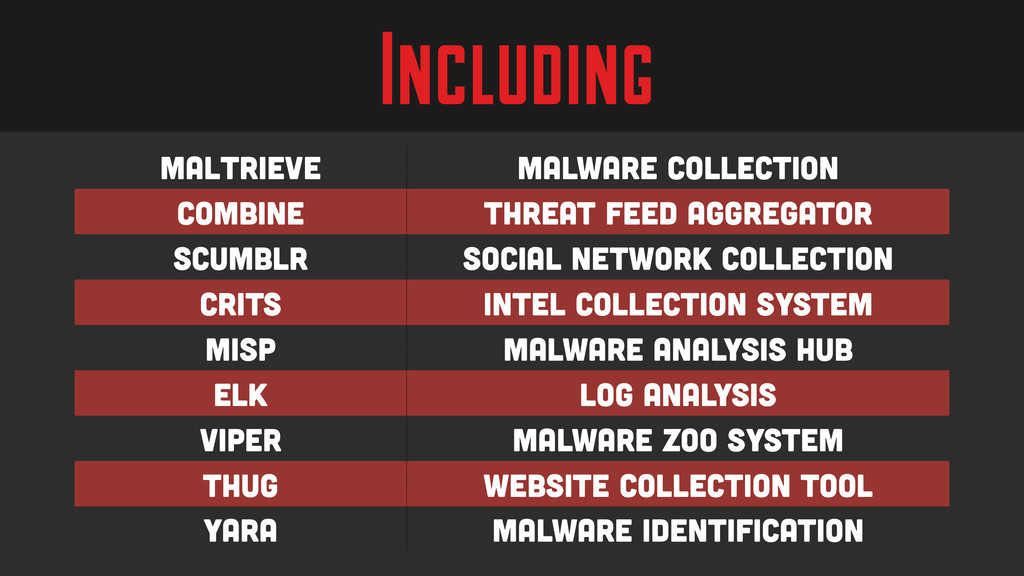
Including Maltrieve Malware Collection Combine Threat Feed Aggregator Scumblr Social
Network Collection CRITs Intel Collection System MISP Malware Analysis Hub ELK Log Analysis Viper Malware Zoo System Thug Website Collection Tool Yara Malware Identification
Review
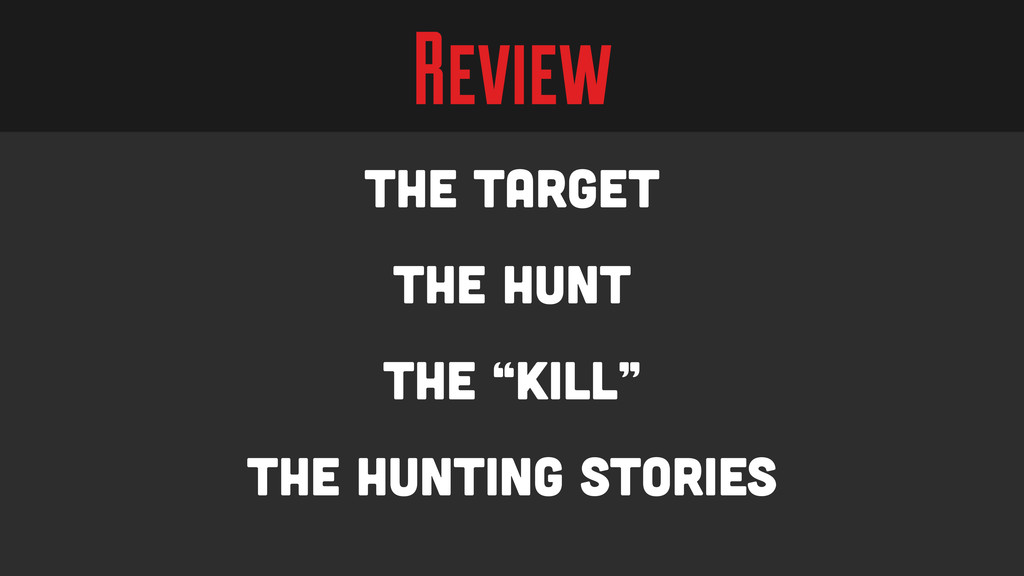
Review The Target The Hunt The “Kill” The Hunting Stories
Questions?
Thanks
None

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 sroberts
 snoozer05
 teamhimeh
 jozono
 yama3133
 myohei
 nkzn
 konifar
 shisyu_gaku
 dai08srhg
 sishi2026
 erikjhordan_rey
 kastner
 trishagee
 baasie
 portentint
 greggifford
 eileencodes
 soudai
 frankvandijk
 codingconduct
 cassininazir
 mfonobong
 afnizarnur