Share
Embed
DEVNATION LAB: From Zero to Hero: Securing your functions and services in the cloud
In this workshop, get hands on and learn how to secure a simple Java Script/HTML application using Single-Sign On (SSO). Build and deploy a microservice and secure it. And further connect it with social logins like Github. You will also have a chance to create your own authentication flows and play with OTP tokens etc. No IDE or installations required, only a working browser will do. Join to become and expert in securing your applications, functions and services with Red Hat SSO.
Shaaf Syed
June 29, 2023
Transcript
30 slides
-
dn.dev/kubemaster2 Technical Hands-On Lab sshaaf@redhat • Java developer, advocate, architect,
engineer… • Open source enthusiast, contributor • Technical evangelist, developer advocate, marketing • InfoQ Java Technical Editor • Volunteer, coach, trainer.. • Ask me about #Java, backends, architecture, containers.. fosstodon.org/@shaaf @syshaaf sshaaf https://www.linkedin.com/in/shaaf/ shaaf.dev -
dn.dev/kubemaster2 Technical Hands-On Lab masales@redhat • Java is my base
platform: developer, Certified Architect, evangelist… • But also: Net core, Golang, Python, C • Open source enthusiast and contributor • Master in cloud native applications and distributed systems • Focused on solution architecture • Always attentive to the topic of security in applications • Ask me about #Java, backends, cloud native, architecture, containers, application security.. @marcelodssales marcelomrwin marcelo-daniel-sales -
dn.dev/kubemaster2 Agenda: - Introduction - Technical Overview - Hands-on Labs
(Openshift/Keycloak/SSO) - Config - Securing apps - OpenID - Users and Groups - Identity providers and OAUTH - Advanced config (Themes, customization, OTP, encryption..) - Closing and next steps -
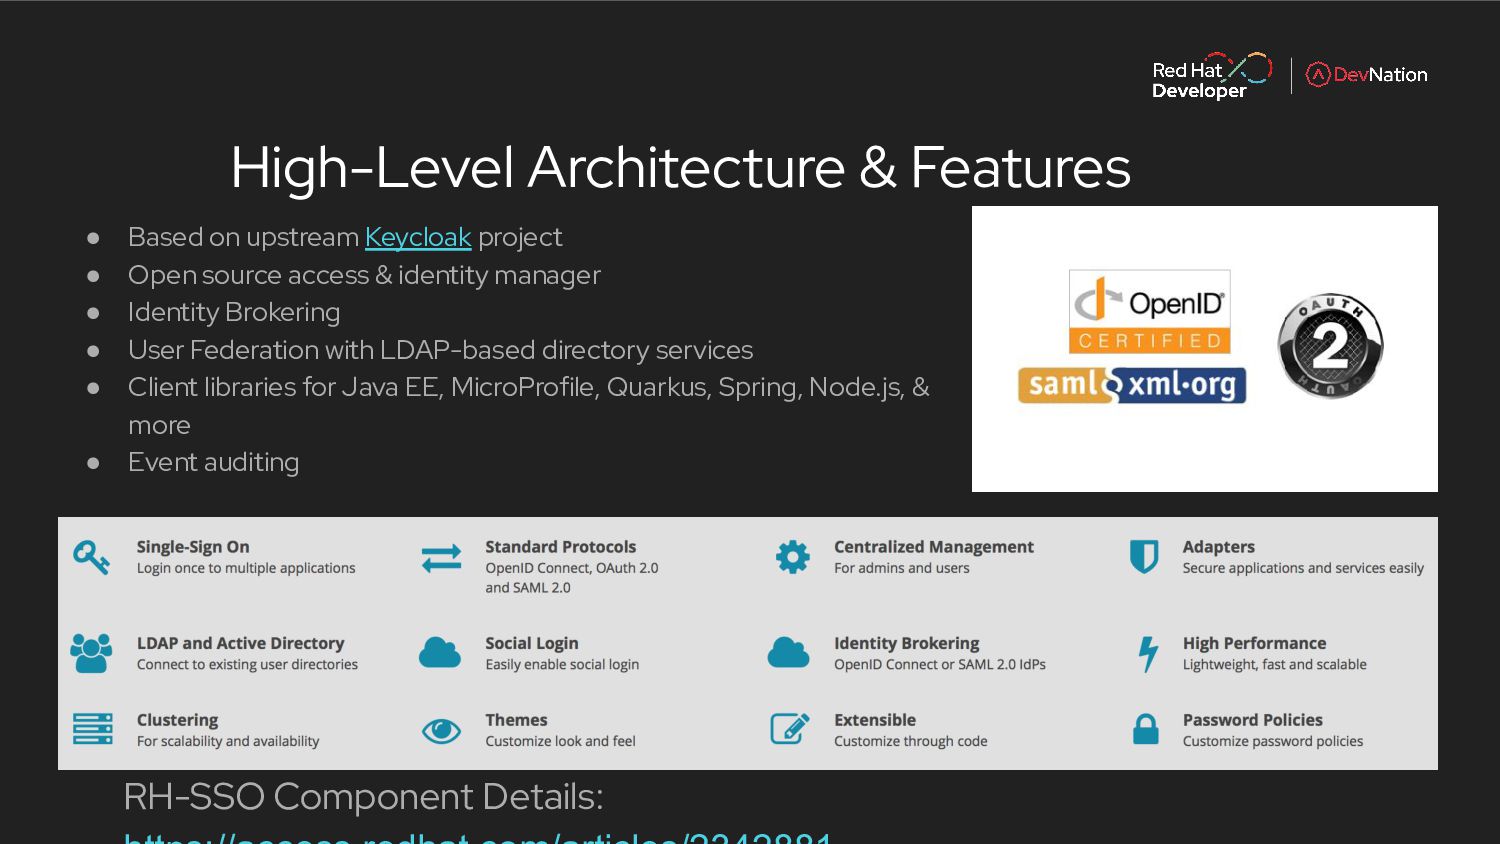
dn.dev/kubemaster2 High-Level Architecture & Features RH-SSO Component Details: • Based
on upstream Keycloak project • Open source access & identity manager • Identity Brokering • User Federation with LDAP-based directory services • Client libraries for Java EE, MicroProfile, Quarkus, Spring, Node.js, & more • Event auditing -
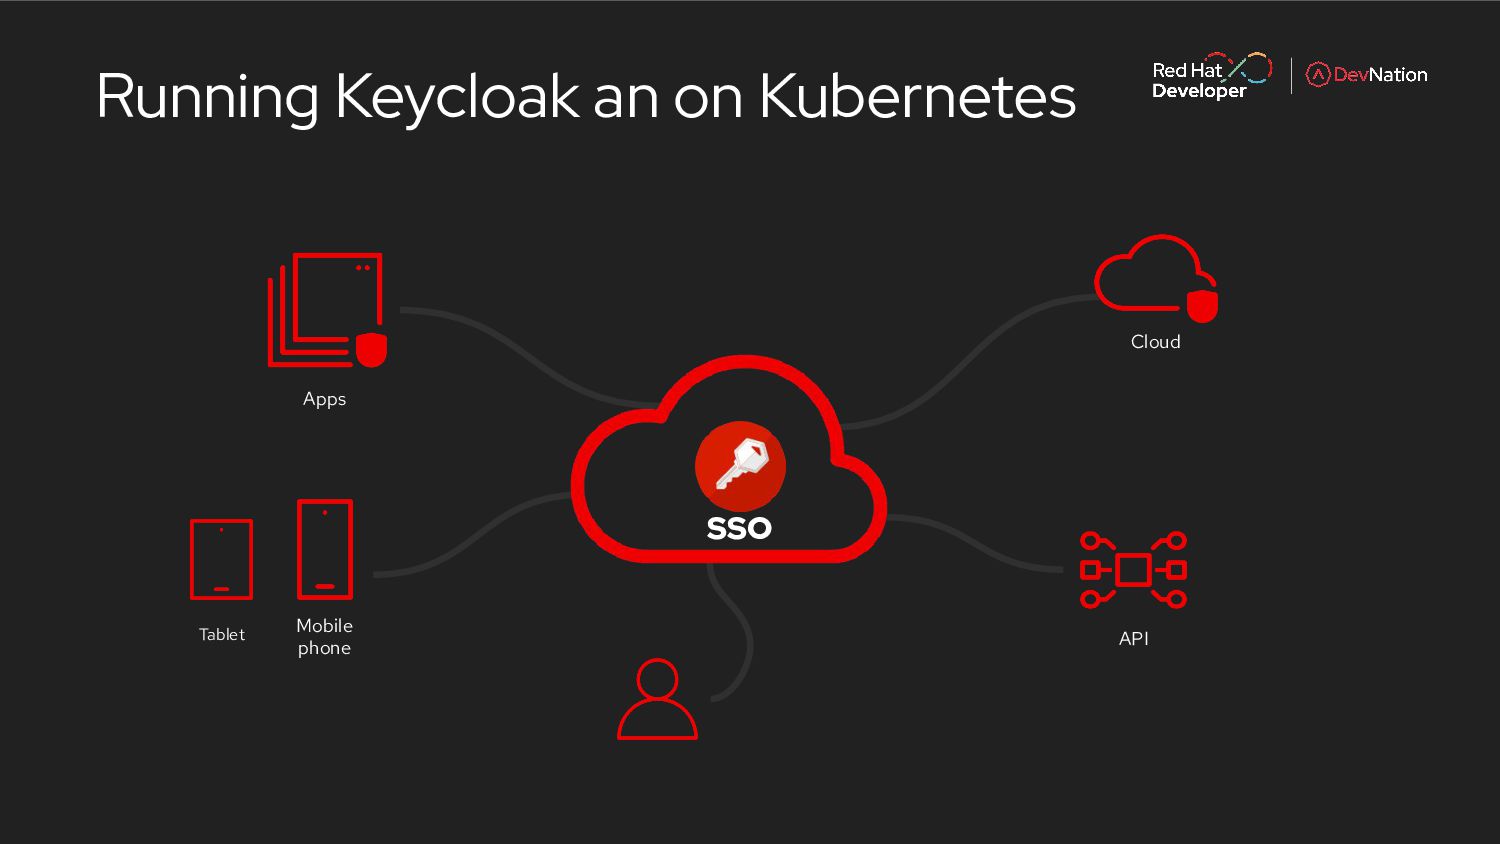
dn.dev/kubemaster2 Running Keycloak an on Kubernetes API Apps SSO Cloud
Mobile phone Tablet -
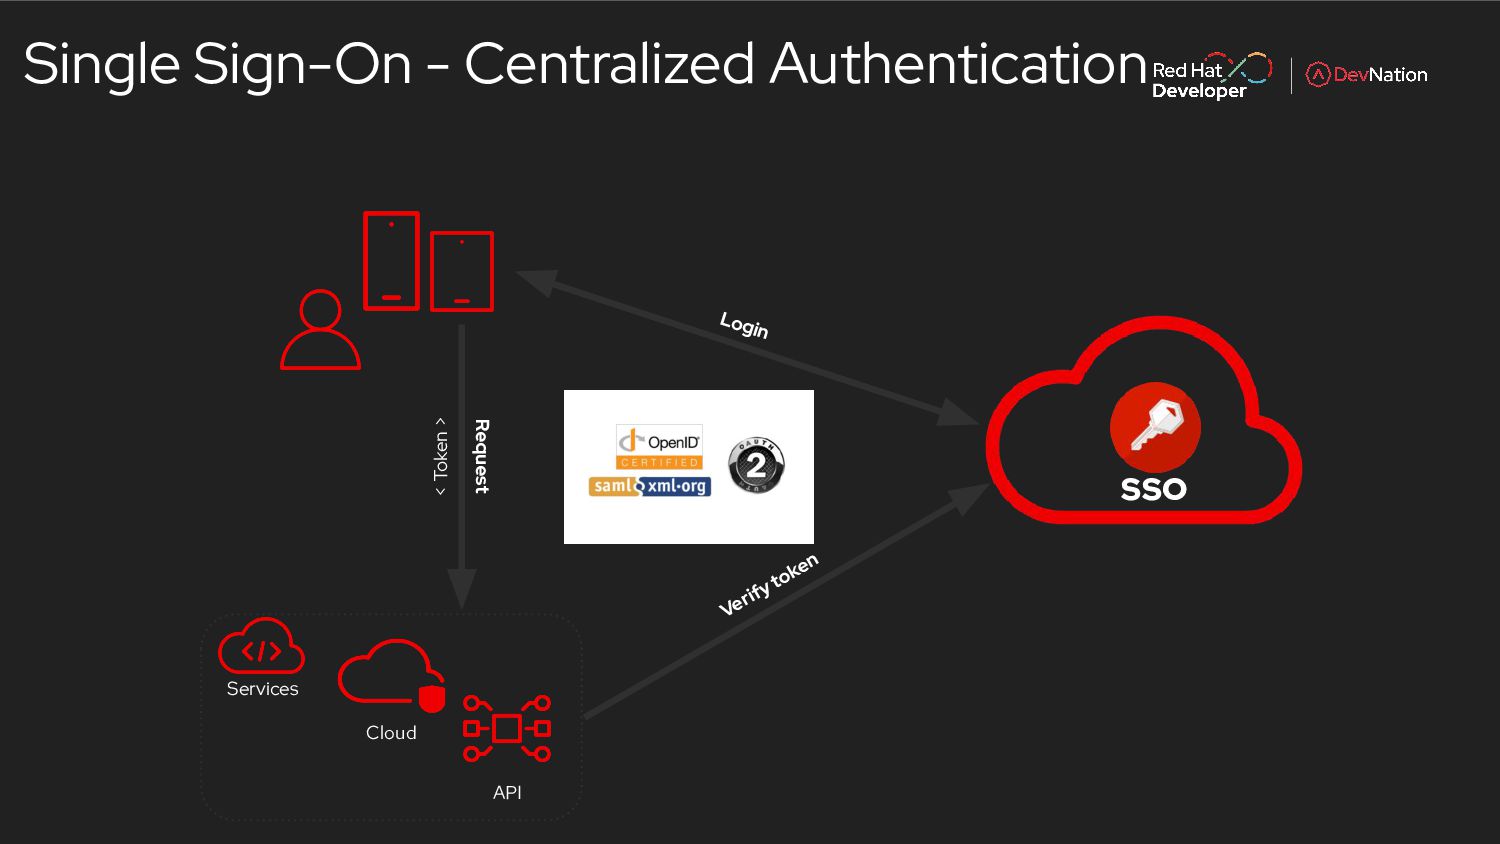
dn.dev/kubemaster2 Single Sign-On - Centralized Authentication SSO Login Request Verify
token < Token > API Cloud Services -
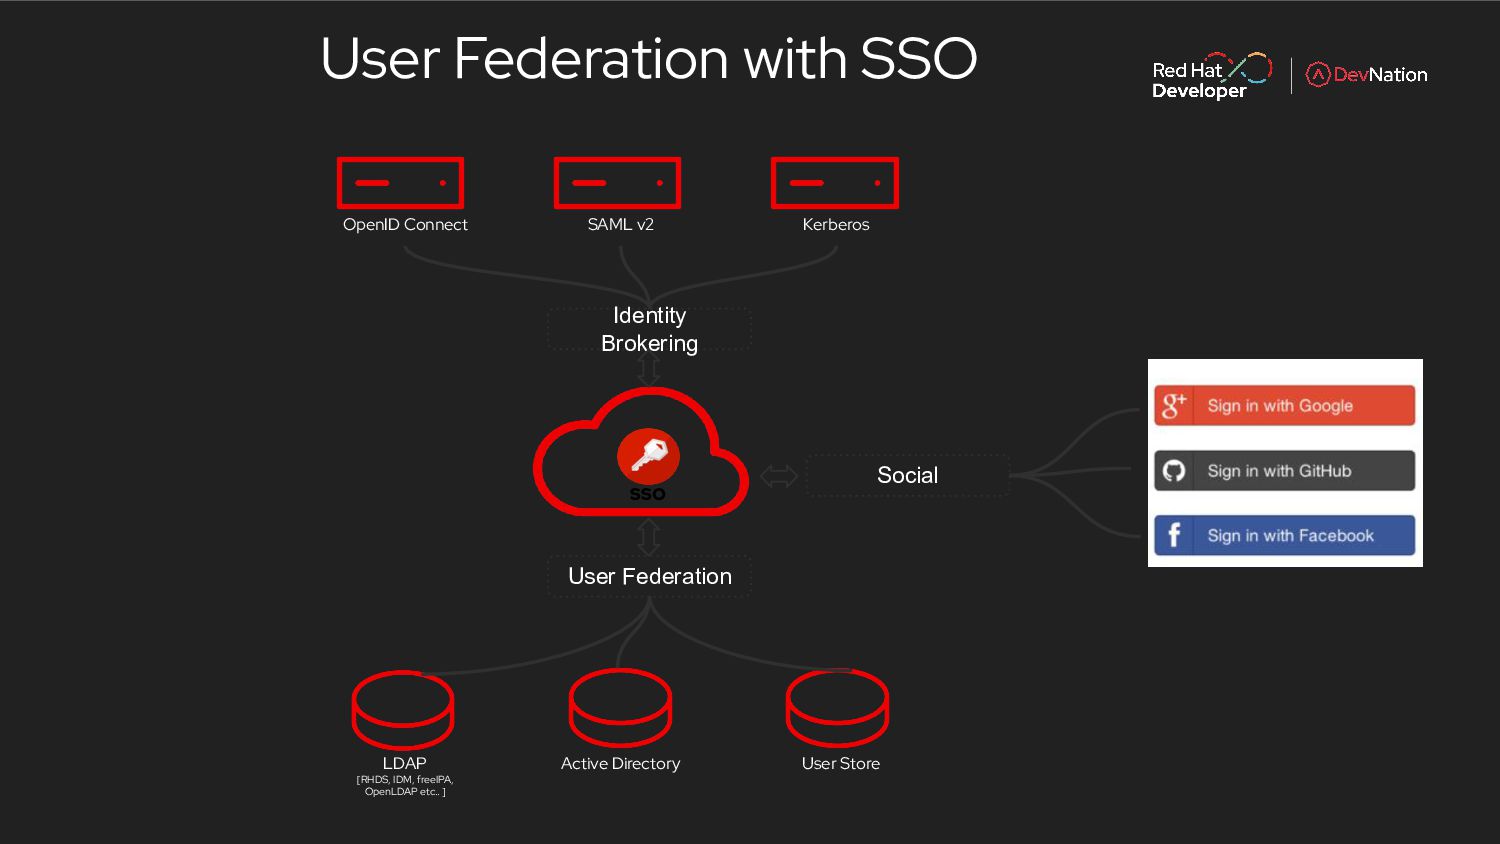
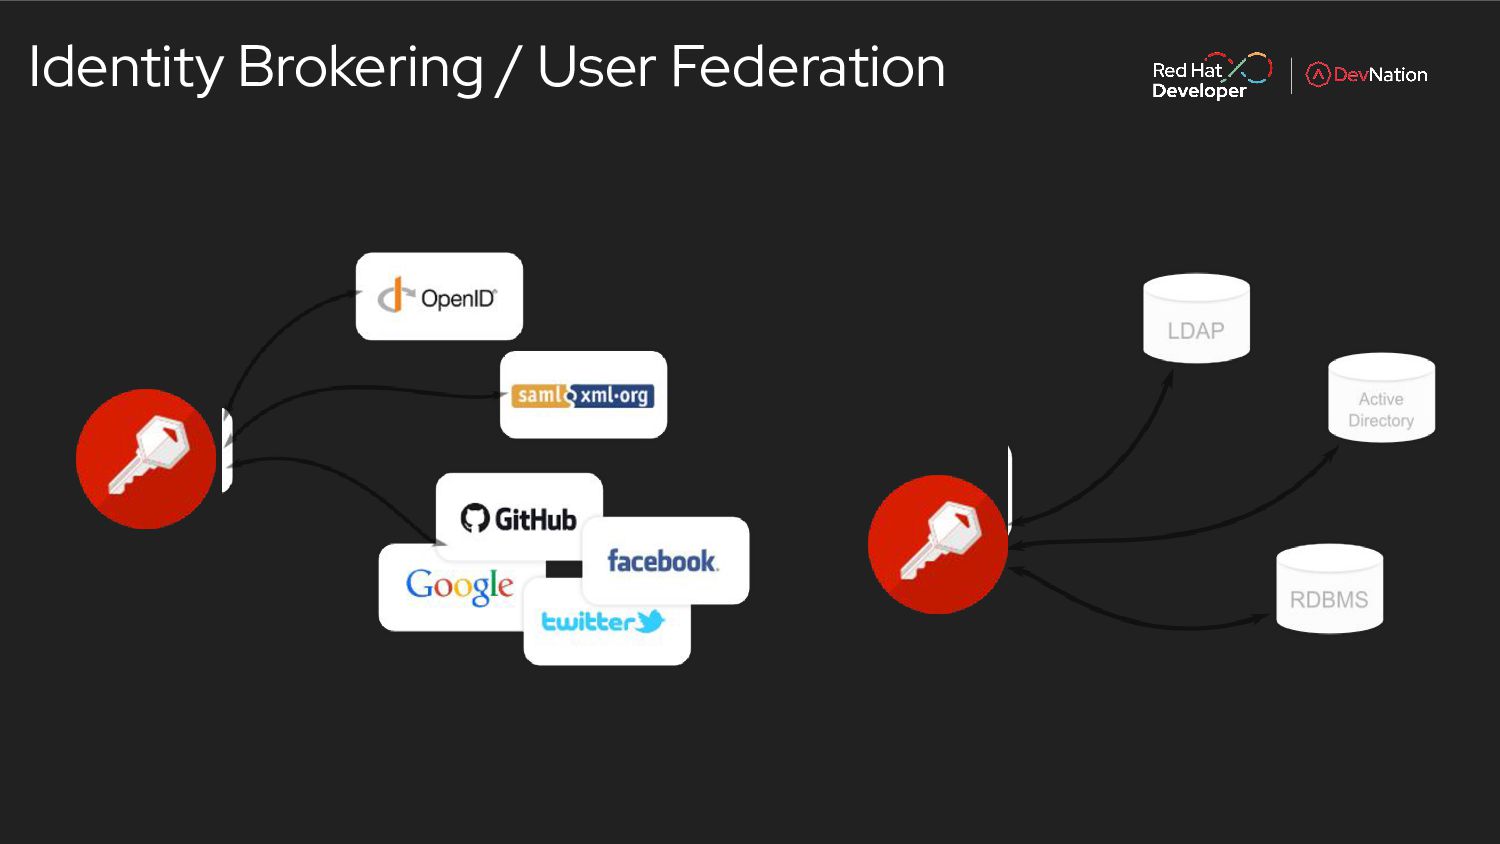
dn.dev/kubemaster2 User Federation with SSO SSO Identity Brokering OpenID Connect
SAML v2 Kerberos LDAP [RHDS, IDM, freeIPA, OpenLDAP etc.. ] Active Directory User Store User Federation Social -
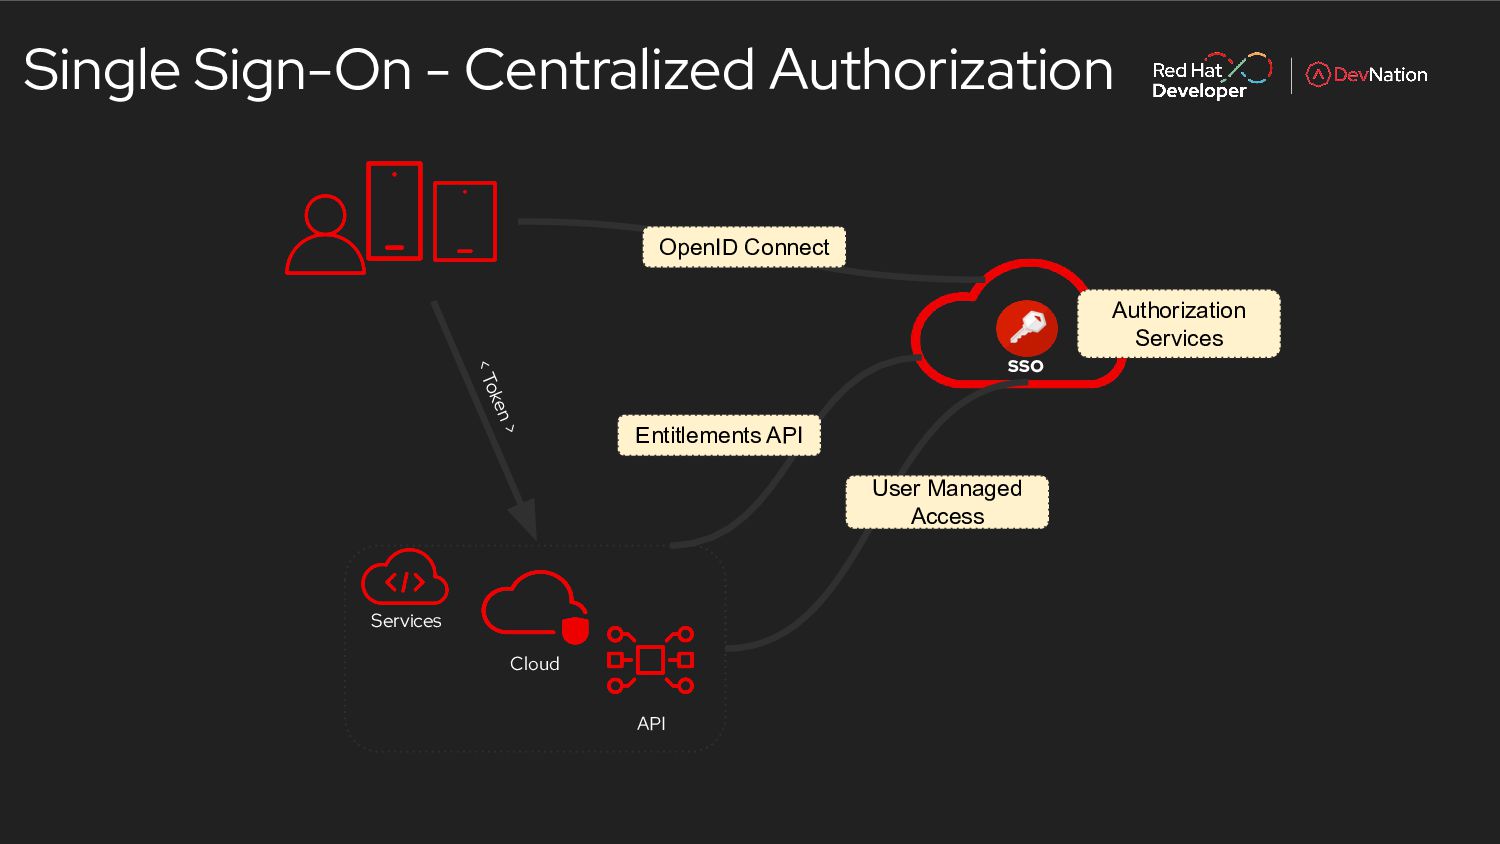
dn.dev/kubemaster2 Single Sign-On - Centralized Authorization SSO Authorization Services <
Token > User Managed Access API Cloud Services Entitlements API OpenID Connect -
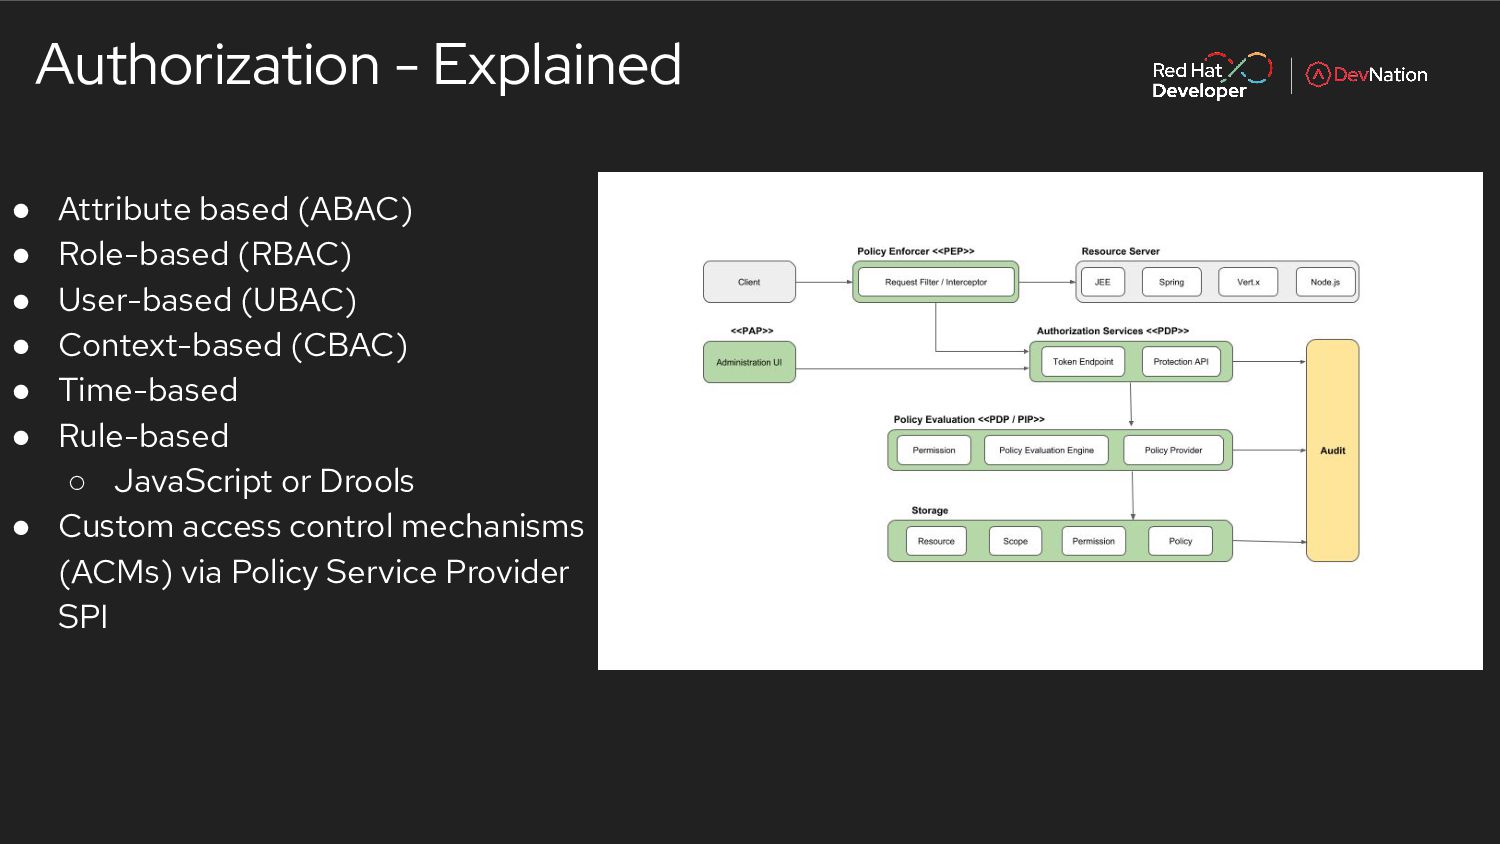
dn.dev/kubemaster2 Authorization - Explained • Attribute based (ABAC) • Role-based
(RBAC) • User-based (UBAC) • Context-based (CBAC) • Time-based • Rule-based ◦ JavaScript or Drools • Custom access control mechanisms (ACMs) via Policy Service Provider SPI -
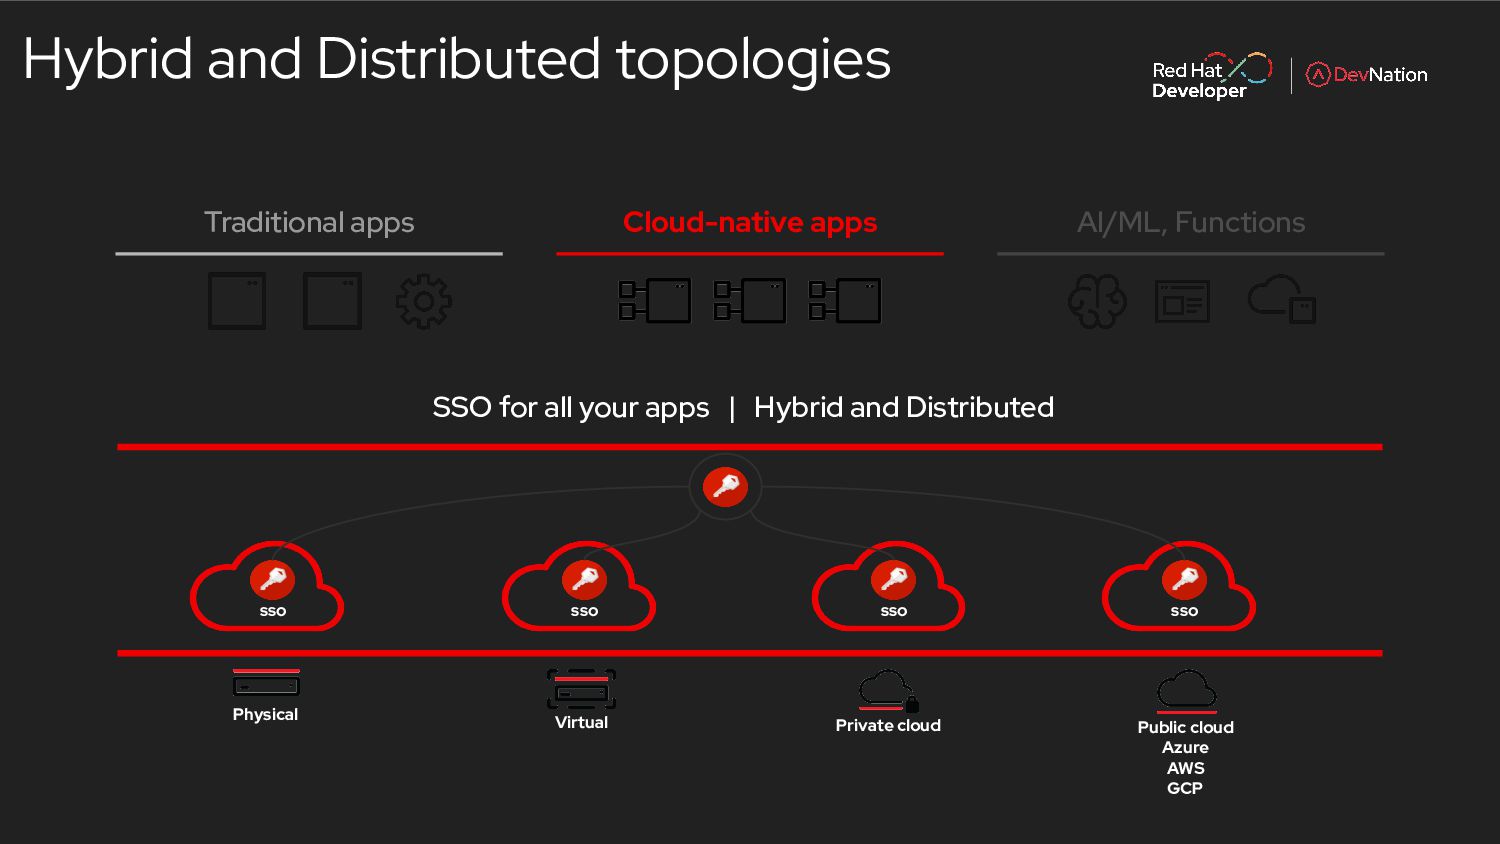
dn.dev/kubemaster2 Hybrid and Distributed topologies Cloud-native apps AI/ML, Functions SSO
for all your apps | Hybrid and Distributed Traditional apps Physical Virtual Private cloud Public cloud Azure AWS GCP SSO SSO SSO SSO -
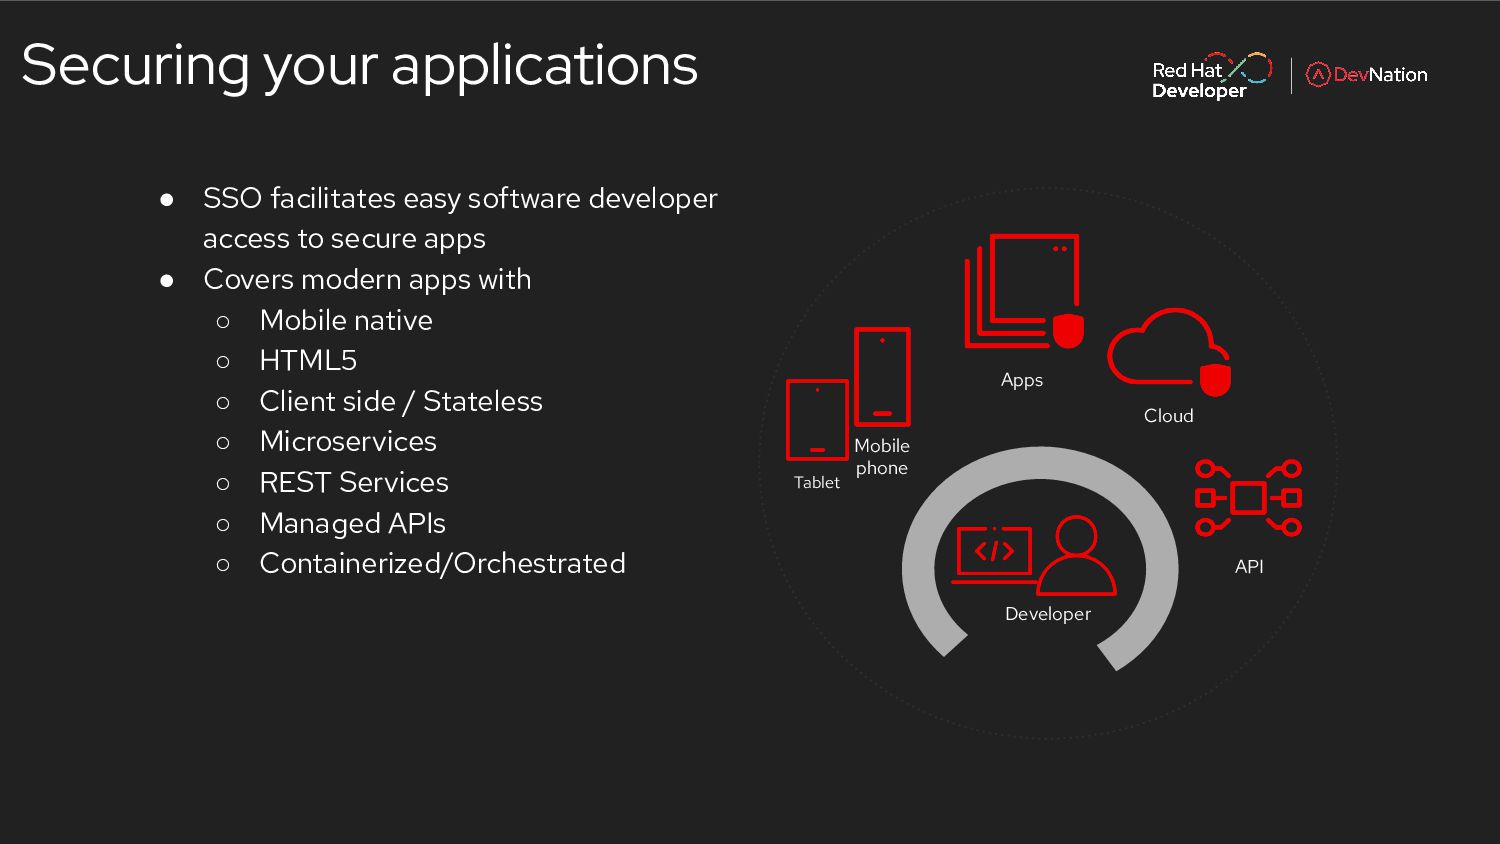
dn.dev/kubemaster2 Securing your applications • SSO facilitates easy software developer
access to secure apps • Covers modern apps with ◦ Mobile native ◦ HTML5 ◦ Client side / Stateless ◦ Microservices ◦ REST Services ◦ Managed APIs ◦ Containerized/Orchestrated API Apps Cloud Developer Mobile phone Tablet -
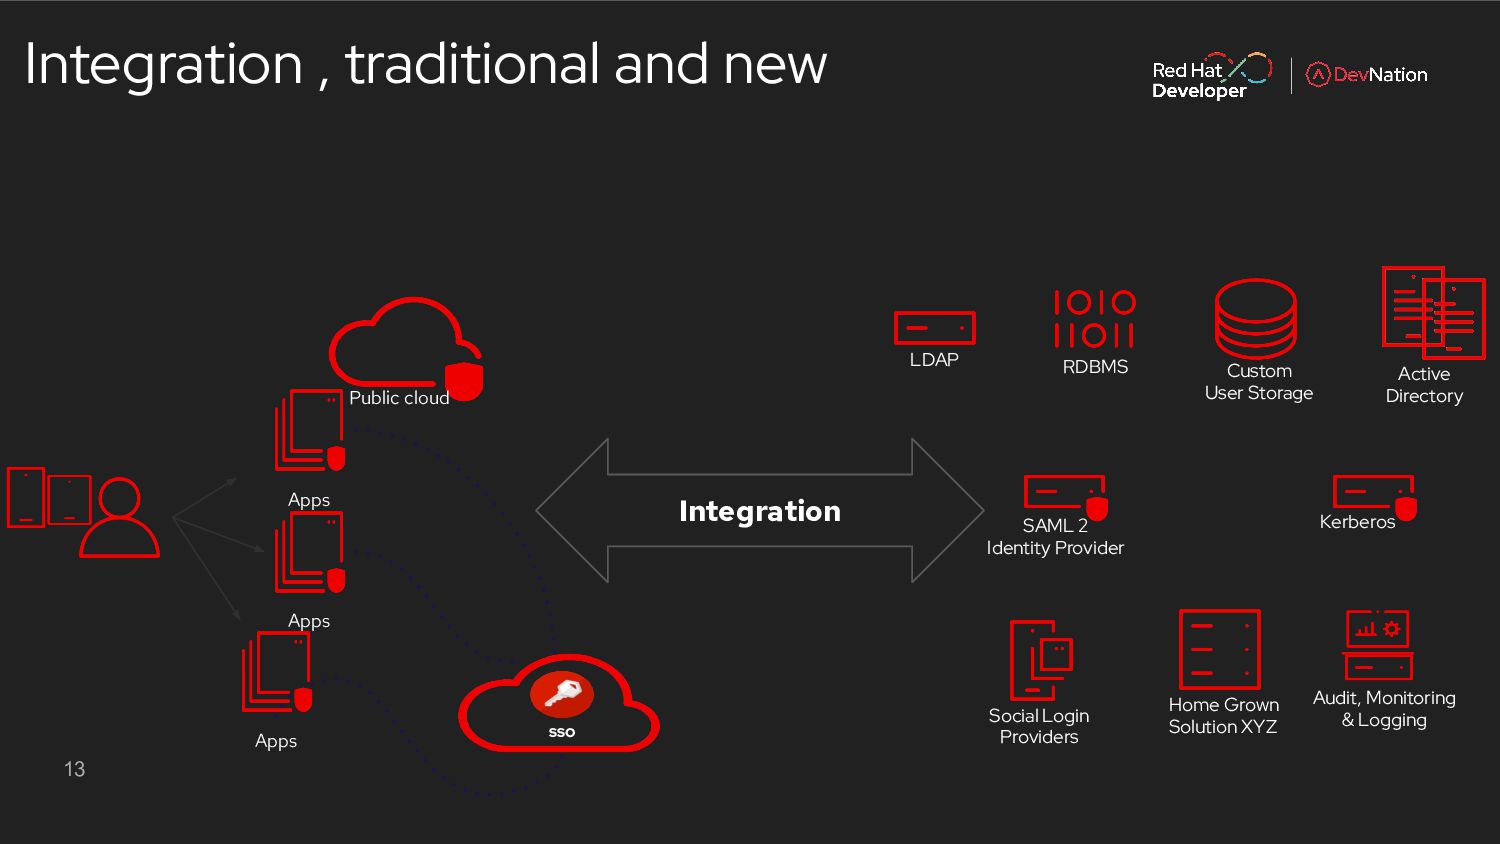
dn.dev/kubemaster2 13 Social Login Providers Integration Integration , traditional and
new LDAP Custom User Storage RDBMS Active Directory SAML 2 Identity Provider Kerberos Public cloud SSO Apps Apps Apps Home Grown Solution XYZ Audit, Monitoring & Logging -
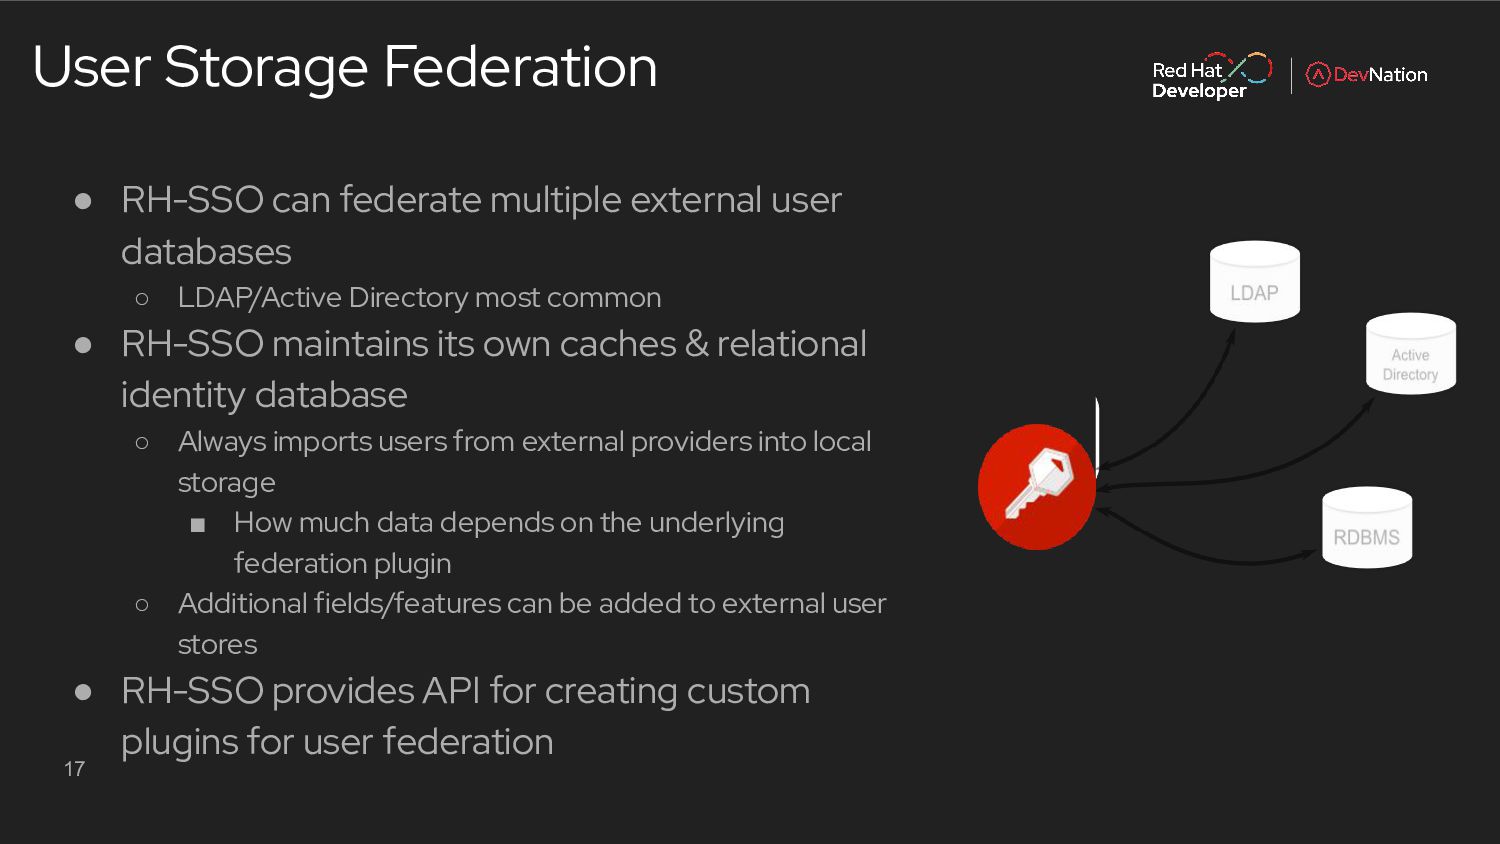
dn.dev/kubemaster2 User Storage Federation 17 • RH-SSO can federate multiple
external user databases ◦ LDAP/Active Directory most common • RH-SSO maintains its own caches & relational identity database ◦ Always imports users from external providers into local storage ▪ How much data depends on the underlying federation plugin ◦ Additional fields/features can be added to external user stores • RH-SSO provides API for creating custom plugins for user federation -
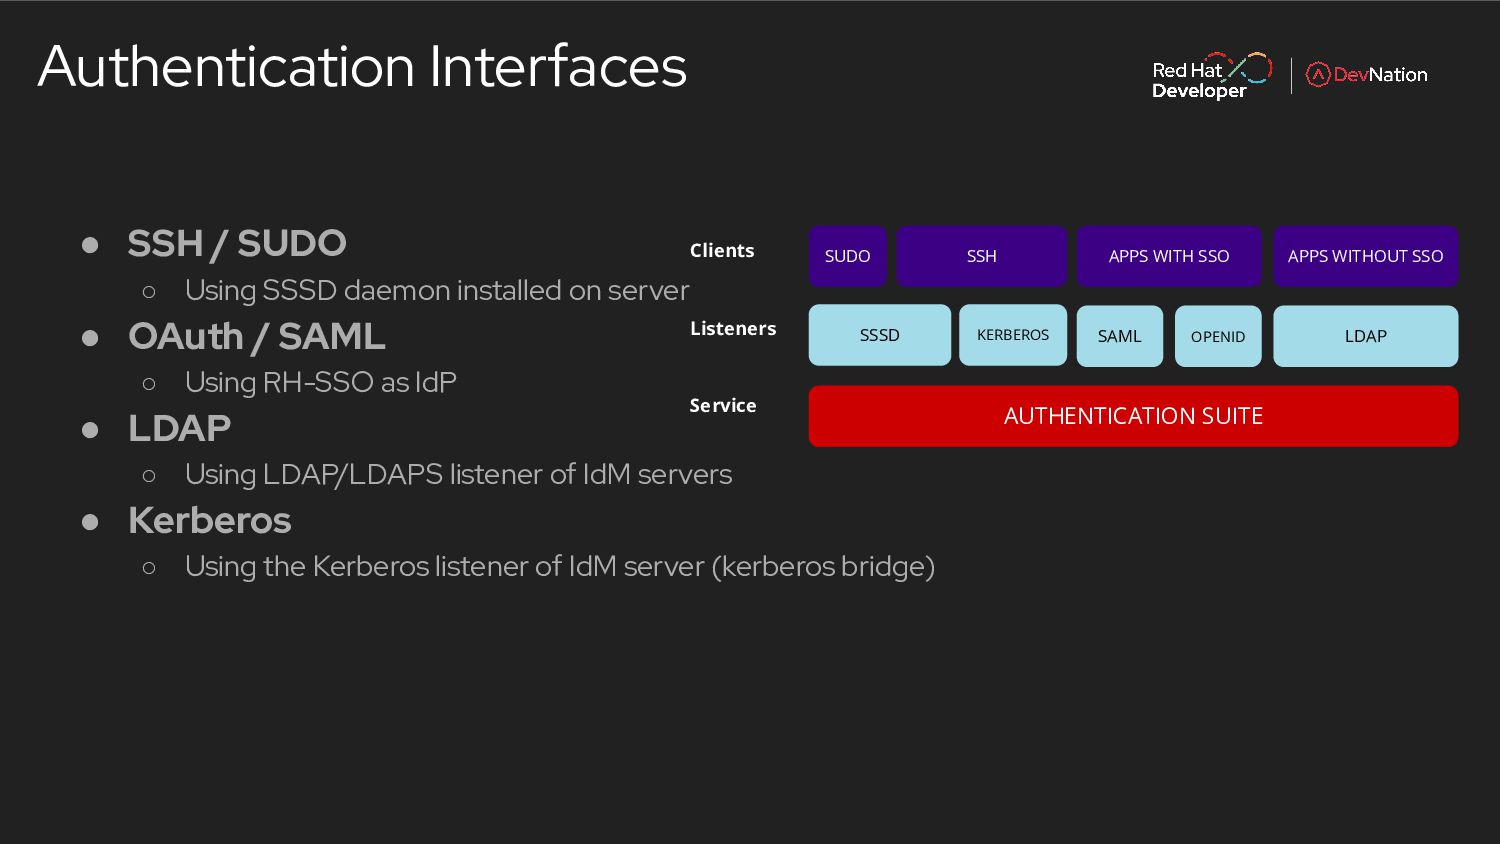
dn.dev/kubemaster2 Authentication Interfaces • SSH / SUDO ◦ Using SSSD
daemon installed on server • OAuth / SAML ◦ Using RH-SSO as IdP • LDAP ◦ Using LDAP/LDAPS listener of IdM servers • Kerberos ◦ Using the Kerberos listener of IdM server (kerberos bridge) AUTHENTICATION SUITE Service Listeners SSSD SAML OPENID LDAP SSH Clients SUDO APPS WITH SSO APPS WITHOUT SSO KERBEROS -
dn.dev/kubemaster2 SSO Concepts 21 • Users ◦ Entities that are
able to log into your system ◦ Can have attributes associated ▪ email, username, phone number, etc • Groups ◦ Users can be grouped together ◦ Users in a group inherit the attributes & roles of the group ◦ Typically used to manage users -
dn.dev/kubemaster2 SSO Concepts 22 • Credentials ◦ Pieces of data
that RH-SSO uses to verify the identity of a user ▪ Passwords, one-time passcodes, digital certificates, etc • Roles ◦ Type of category of a user ◦ Applications can assign permissions to roles rather than specific user ◦ Roles can be composed to contain other roles ◦ Typically used to manage applications & services -
dn.dev/kubemaster2 SSO Concepts 23 • Authentication ◦ Identifying & validating
a user • Authorization ◦ Granting access to a resource to a user • Clients ◦ Entities that can request authentication for a user ▪ Often is an application acting on behalf of a user but still needs to authenticate itself to a downstream service • Session ◦ Created upon login ◦ Contains information about the user ▪ When logged in, which applications participated in the authentication, etc ◦ Admins & users can view session information -
dn.dev/kubemaster2 SSO Concepts 24 • Identity Manager (IdM) / Identity
Access Manager (IAM) ◦ Controls information about users and services ◦ RH-SSO is an IAM, can be an IdM • Identity Provider (IdP) ◦ Service that can authenticate a user ◦ RH-SSO is an IdP • Service Provider (SP) ◦ System that receives & accepts authentications (SAML assertions, OIDC tokens, etc) -
dn.dev/kubemaster2 SSO Concepts 25 • Identity Provider Federation / Identity
Brokering ◦ Mechanism to delegate authentication to one of more IdPs ▪ Social login via Facebook, Google, GitHub, etc ◦ RH-SSO can delegate authentication to any other OpenID Connect or SAML 2.0 IdP • Identity Provider Mapper ◦ Ability to map incoming tokens/assertions to user & session attributes for propagating identity information -
dn.dev/kubemaster2 Keycloak / RH-SSO Concepts 26 [1] RH-SSO Supported Configurations:
https://access.redhat.com/articles/2342861 • Realm ◦ Manages a set of users, credentials, roles, & groups ◦ Users belong to realms ◦ Realms are isolated from each other ◦ Realms can only manage & authenticate users they control • Client Adapters ◦ Plugins installed to be able to communicate & be secured by RH-SSO [1] ▪ Java, JavaEE, Spring, Node.js, Javascript, etc • User Federation Provider ◦ Store & manage users ◦ Validate credentials from external stores & pull in identity information ▪ LDAP, Active Directory, Kerberos, custom, etc -
dn.dev/kubemaster2 Keycloak / RH-SSO Concepts 27 • Authentication Flows ◦
Workflows a user must perform when interacting with certain aspects of a system ▪ Registration flows, login flows, credential reset flows, etc • Registration Flow ◦ Workflow a user must perform when a realm allows self-registration ◦ Can define what profile information a user must enter ◦ Can require additional identity validation steps ▪ OTP, OOB, reCAPTCHA, etc • Login Flow ◦ Defines what types of credentials are required to perform a login ▪ Username/password, MFA, etc • Required Actions ◦ Actions a user must perform during the authentication process ▪ Interval-based and/or scheduled password reset, etc