Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
PHP 也有 Day #48:我是誰?我在哪?
Search
Star Rocket
October 01, 2019
Technology
100
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
PHP 也有 Day #48:我是誰?我在哪?
PHP 也有 Day #48:我是誰?我在哪?
Star Rocket
October 01, 2019
More Decks by Star Rocket
See All by Star Rocket
PHP 也有 Day #51:高效能框架的曙光 - 以 Laravel 經驗開發 Hyperf 應用
starrocket
1
370
PHP 也有 Day #50:處理前人的遺產—聊 legacy code
starrocket
0
100
PHP 也有 Day #49:邊緣人救星!用 Laravel 打造私人定製的聊天機器人
starrocket
0
460
PHP 也有 Day #48:我是誰?我在哪?
starrocket
0
100
API-整合測試
starrocket
0
160
How we talk about Engineering Culture at Phase
starrocket
0
62
PHP 也有 Day #47:打造好維護的 PHP 程式碼專案
starrocket
0
400
全端起手就用 Laravel+Vue.js 現場實作給你看
starrocket
0
240
PHP 也有 Day #45: VS Code 實戰料理 PHP 套件網站佐 Azure Pipelines
starrocket
0
160
Other Decks in Technology
See All in Technology
今話題のAI「Jev」って何? 宇宙最速で学ぶ会
minorun365
PRO
30
18k
その Lambda、8分で 管理者権限まで奪われます
k1nakayama
7
3.5k
バイブコーディング時代のWebアプリ開発入門~Cloud Runで学ぶセキュアなビルドとデプロイ
waiwai2111
1
140
2026-09-08 そのJavaモダナイゼーション、AIに丸投げで大丈夫?IBM Bobで変わる品質と効率
yutanonaka
1
130
開発投資の期待値を上げるプロダクトロードマップづくり ~プロダクトエンジニアが越境して事業を伸ばす~
kekekenta
1
240
アクセスキーこわい やめかたと漏らさない工夫
sassssan68
1
610
AgentCore Runtime上にAgentic Coding基盤を構築・展開する際の設計ポイントと限界点 / Design considerations and limitations when building an agentic coding platform on AgentCore Runtime
har1101
5
640
白金鉱業Meetup Vol.25 アウトカムが二値のデータに対するCausal Impact
brainpadpr
0
270
アプリログインとWeb認証基盤をつなぐ ASWebAuthenticationSession 作法
shimastripe
1
370
俺の仕事は AIに奪われないし、たぶんその BIも要らない
hikaruri
0
540
ソフトウェアDNAとクラウドエージェントのススメ
cloudace
0
120
アプリをもっと"iOSアプリっぽく"する小さな工夫 / Small Touches That Make Your App Feel More Like an iOS App
matsuji
2
1k
Featured
See All Featured
Bash Introduction
62gerente
615
220k
Optimising Largest Contentful Paint
csswizardry
37
4k
GraphQLとの向き合い方2022年版
quramy
50
15k
VelocityConf: Rendering Performance Case Studies
addyosmani
331
25k
Music & Morning Musume
bryan
48
7.4k
Leveraging Curiosity to Care for An Aging Population
cassininazir
1
500
AI: The stuff that nobody shows you
jnunemaker
PRO
10
1.1k
実際に使うSQLの書き方 徹底解説 / pgcon21j-tutorial
soudai
PRO
203
76k
Gemini Prompt Engineering: Practical Techniques for Tangible AI Outcomes
mfonobong
2
540
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
1
6.2k
The AI Revolution Will Not Be Monopolized: How open-source beats economies of scale, even for LLMs
inesmontani
PRO
3
3.7k
<Decoding/> the Language of Devs - We Love SEO 2024
nikkihalliwell
1
330
Transcript
我是誰︖我在哪︖ 聊聊 Web 的身分驗證
ABOUT MILES CURRENT Senior Developer @ 104 Corp. Volunteer @
DevOps Taiwan TAG PHP, Docker, DevOps
[email protected]
MilesChou
None
今天將會聊些什麼 Terminology Scenario Native App Security Topic
Terminology Authentication Entity Identifier
Server User
Server User Entity
Server User Identifier Entity
Server User Entity Identifier Miles Miles
Server User Entity Identifier Authentication Miles Miles
基本的安全問題 請求真的是該使⽤用者本身的意願所發出的請求嗎︖ 有沒有可能被竄改︖有沒有機會造假︖ 回應真的是伺服器的回應嗎︖ 有沒有可能被竄改︖有沒有機會造假︖
Scenario 從前從前,有個網站提供了很多服務
安安你好,第⼀一 一 次 來 來 嗎 ? 第⼀一 一 次
來 來 的 都 是 絕 緣 ⼈人 人 哦 ! 為了了讓你不再絕緣, 你先跟我講好,要怎麼驗證你是誰!
註冊的⽬目的 使⽤用者提供憑證資訊,如帳號、密碼、etc 伺服器提供 metadata
註冊的⽅方法 線上註冊 私訊註冊 線下註冊
User Login 身為⼀一個使⽤用者,我希望能使⽤用網站提供的服務
安安你好,第⼆二 二 次 來 來 嗎 ? 站著!⼝口 口 令
? 誰 ? 我知道你是麥爾斯了了,可是我⾦金金 金 金 ⿂魚 魚 腦 ! 24 分鐘內記得過來來刷新⼀一 一 下 !
User Login Challenge State Management Mechanism
實作 LaravelAuth Zend Authentication
Server-side Authentication 身為⼀一個伺服器,我希望能呼叫網站提供的 API
How about Authorization?
Server-side Authentication Trusted Server VPN、鎖 IP、發 token、etc. OAuth 2.0 Facebook、Google、GitHub、AWS、etc.
Terminology -OAuth2.0 Authorization Resource Owner Resource Server Client Authorization Server
Authorization Server Resource Owner Resource Server Client Authorization Request
Authorization Server Resource Owner Resource Server Client Authorization Grant
Authorization Server Resource Owner Resource Server Client Authorization Grant
Authorization Server Resource Owner Resource Server Client Access Token
Authorization Server Resource Owner Resource Server Client Access Token
Authorization Server Resource Owner Resource Server Client Protected Resource
微信偷連結 Facebook︖ 到底花⽣生省魔術︖請看 VCR!
微信偷連結 Facebook︖ Facebook 實作了 OAuth 2.0 微信 App 為 Client
授權範圍
Third-party Login 身為⼀一個外部網站,我希望能透過貴站做身分驗證
安安你好,你是麥爾斯的跟班嗎? 有刷過麥爾斯的臉就可以進場了了哦! 但過⼀一 一 回 兒 後 , 我還會再跟麥爾斯確認,你還是不是他的跟班
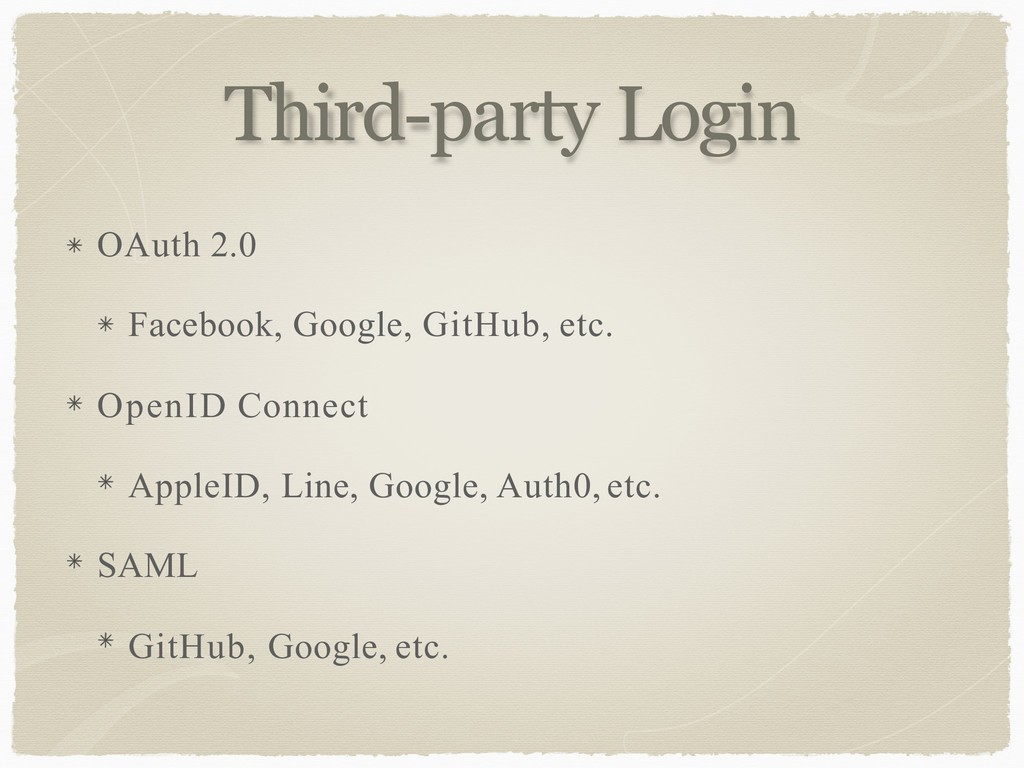
Third-party Login OAuth 2.0 Facebook, Google, GitHub, etc. OpenID Connect
AppleID, Line, Google, Auth0, etc. SAML GitHub, Google, etc.
Server User Provider Authentication Check
OpenID Connect
OpenID Connect Based-on OAuth 2.0 Use JWT on ID token
Discovery Dynamic Client Registration
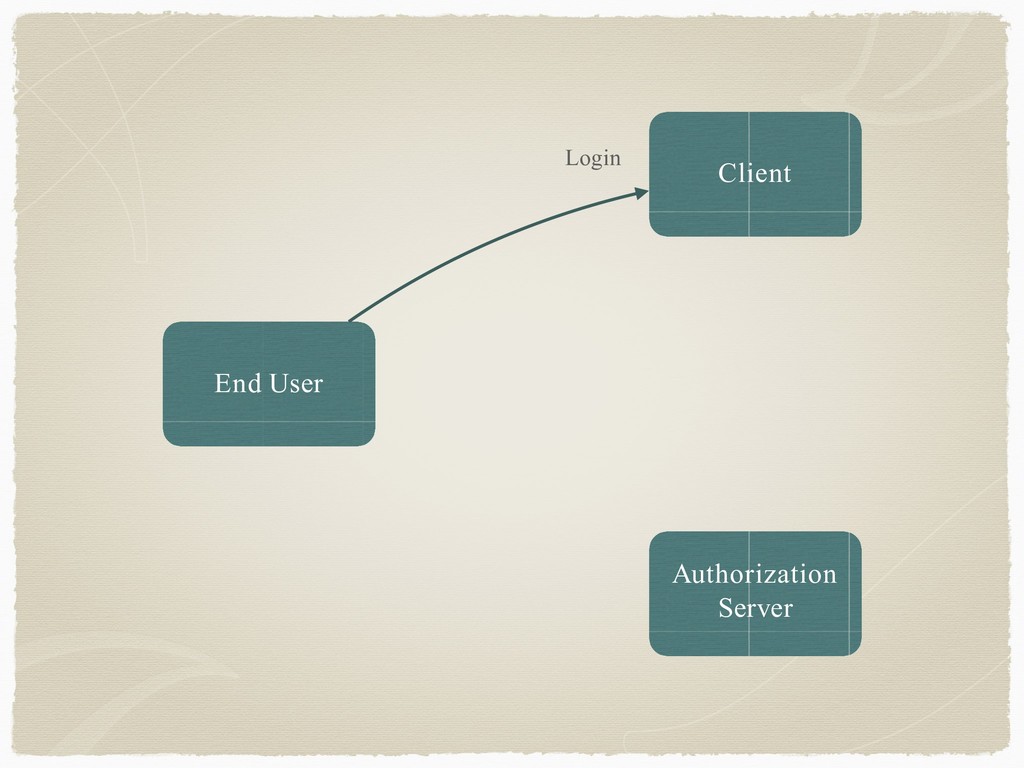
Authorization Server Client End User Login
Authorization Server Client End User Redirect to AuthorizationServer scope=openid
Authorization Server Client End User Authorization Request
GET / POST
Authorization Server Client End User Challenge
Client End User User Credentials Authorization Server
Authorization Server Client End User Authorization Request
Client End User Authorization Grant Authorization Server
Authorization Server Client End User Redirect to Client withCode
Authorization Server Client End User Use Code to get Access
Token ID Token
ID token
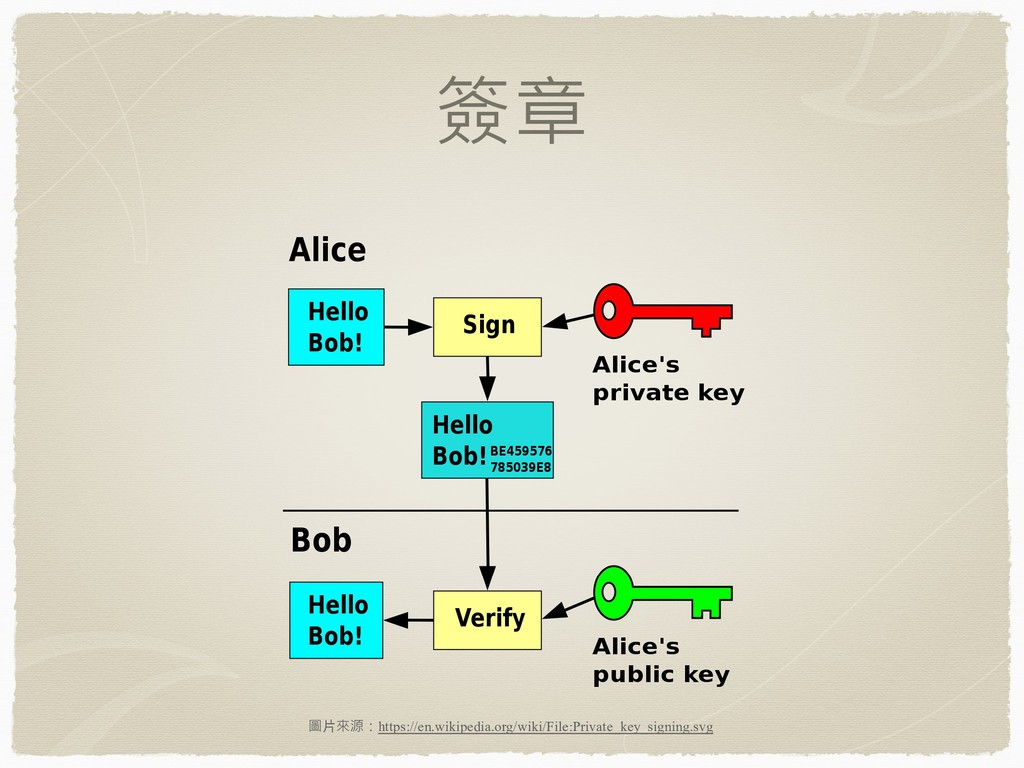
簽章 圖⽚來源:https://en.wikipedia.org/wiki/File:Private_key_signing.svg
簽章演算法 HS256 - HMVC using SHA-256 Line RS256 - RSASSA-PKCS1-v1_5
using SHA-256 AppleID, Google ES256 - ECDSA using P-256 and SHA-256 AppleID
Discovery AppleID Line Google
⽤用 用 講 的 不 就 很 會 ? 做⼀一
一 個 來 來 看 看 啊 !
Demo
Native App
先講結論 不要⽤用嵌入式 User Agent,即麻煩又危險 可使⽤用 PKCE 來解決這個問題
Chrome on Mobile 圖⽚來源:https://www.ory.sh/oauth2-for-mobile-app-spa-browser/
App on Mobile 圖⽚來源:https://www.ory.sh/oauth2-for-mobile-app-spa-browser/
Security Topic
基本 TLS CSRF XSS CSP Same-origin Policy
HTML 登入 無標準協定 網路釣⿂魚
Covert Redirect Redirect url 驗證
清除登入狀態 Token Revoke 的時機 OpenID Session Management Front-Channel Logout Back-Channel
Logout
Extra - Password 千萬不要存明碼 MD5 與 SHA1 已被認為是不安全的演算法 建議使⽤用 SHA256
Extra - Cookie 問題核⼼心在於過度依賴 Cookie 作為身分驗證的⼿手段 CSRF Session Hijacking Session
Fixation Weak Confidentiality Weak Integrity
Q & A


 starrocket
 minorun365
 k1nakayama
 waiwai2111
 yutanonaka
 kekekenta
 sassssan68
 har1101
 brainpadpr
 shimastripe
 hikaruri
 cloudace
 matsuji
 62gerente
 csswizardry
 quramy
 addyosmani
 bryan
 cassininazir
 jnunemaker
 soudai
 mfonobong
 aleyda
 inesmontani
 nikkihalliwell