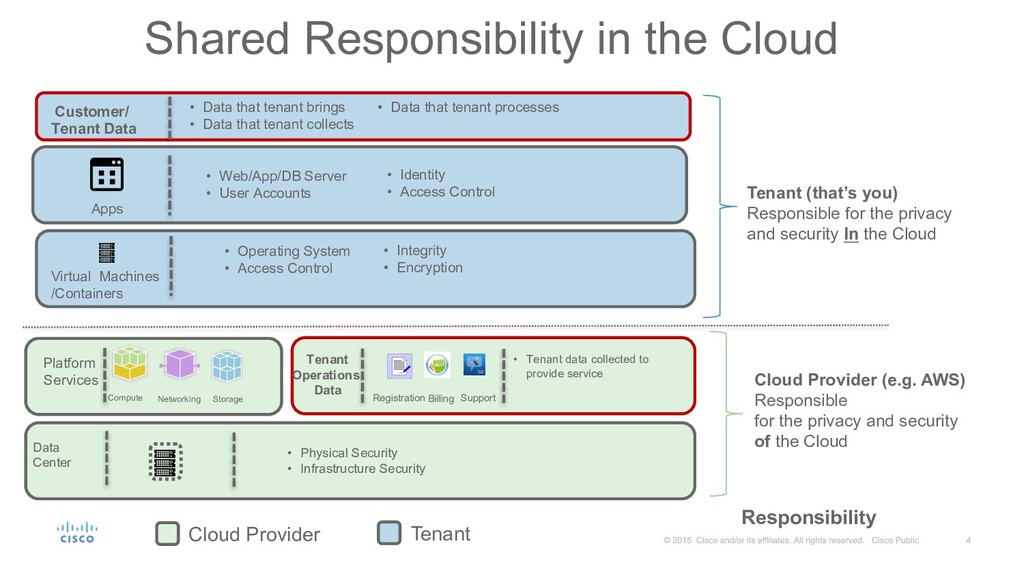
Storage Networking Virtual Machines /Containers Apps • Web/App/DB Server • User Accounts • Operating System • Access Control • Physical Security • Infrastructure Security • Identity • Access Control Cloud Provider Tenant Tenant Operations Data Registration Support Billing • Tenant data collected to provide service Customer/ Tenant Data • Integrity • Encryption • Data that tenant brings • Data that tenant collects • Data that tenant processes Cloud Provider (e.g. AWS) Responsible for the privacy and security of the Cloud Tenant (that’s you) Responsible for the privacy and security In the Cloud Responsibility
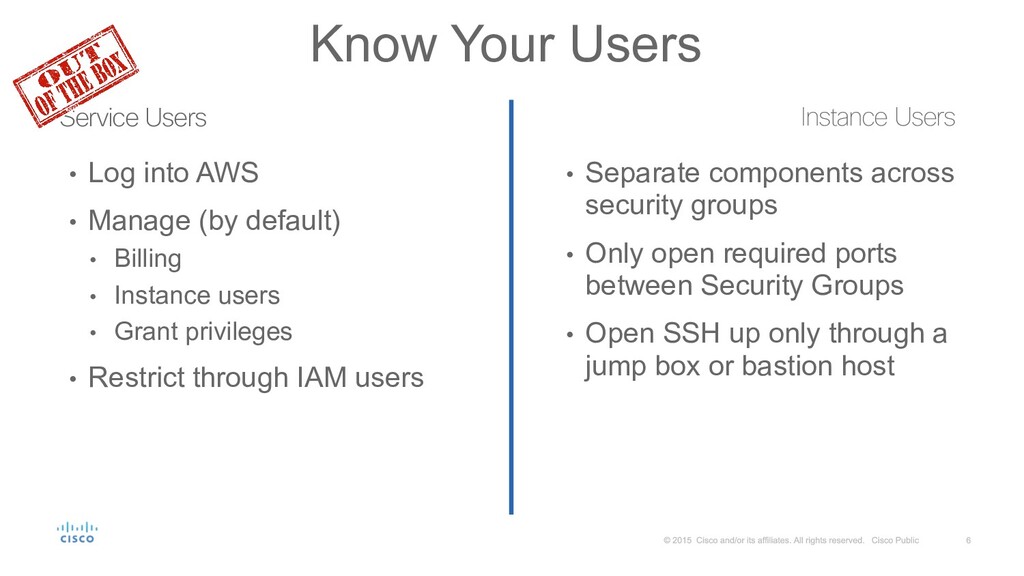
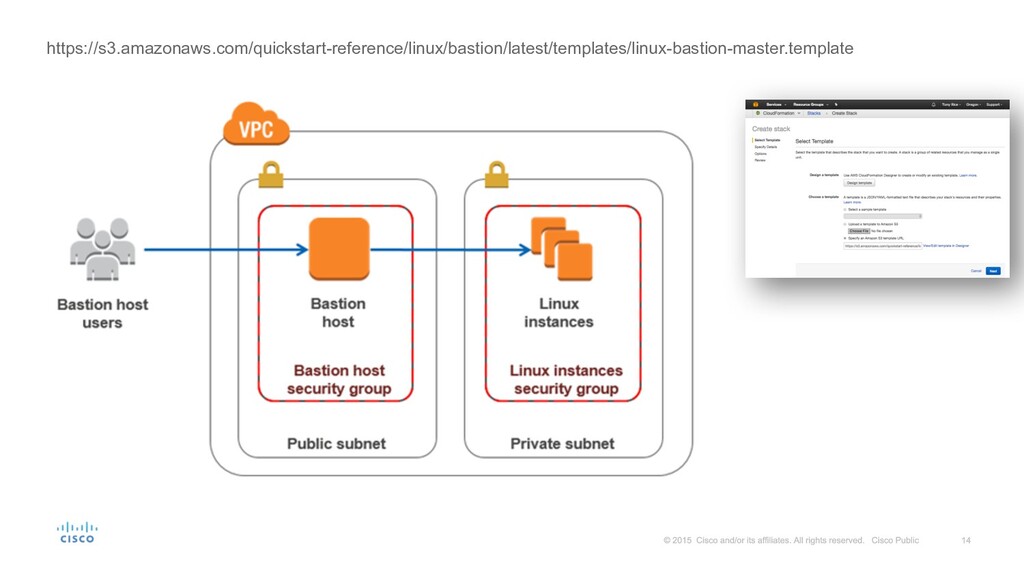
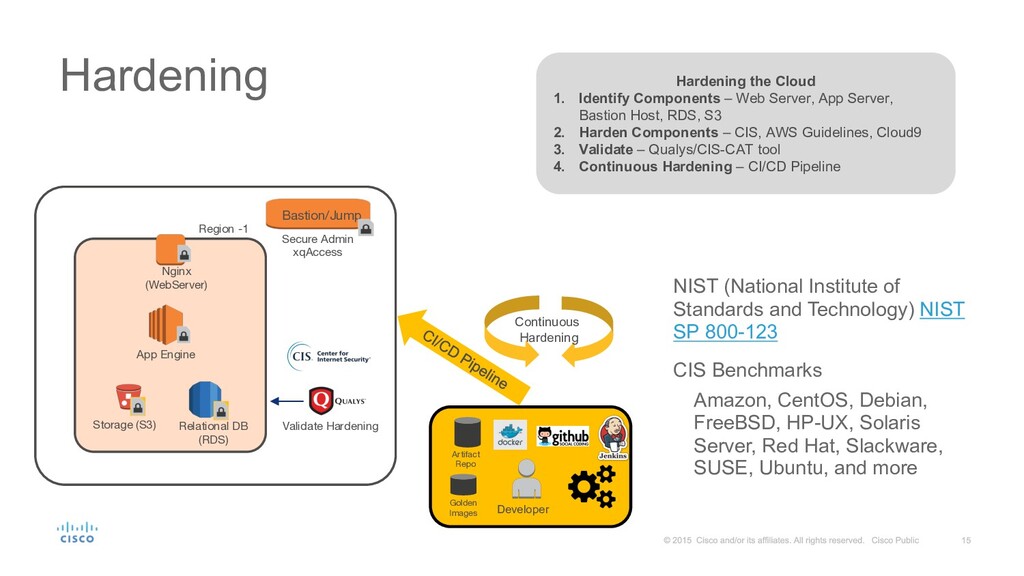
(by default) • Billing • Instance users • Grant privileges • Restrict through IAM users • Separate components across security groups • Only open required ports between Security Groups • Open SSH up only through a jump box or bastion host Know Your Users
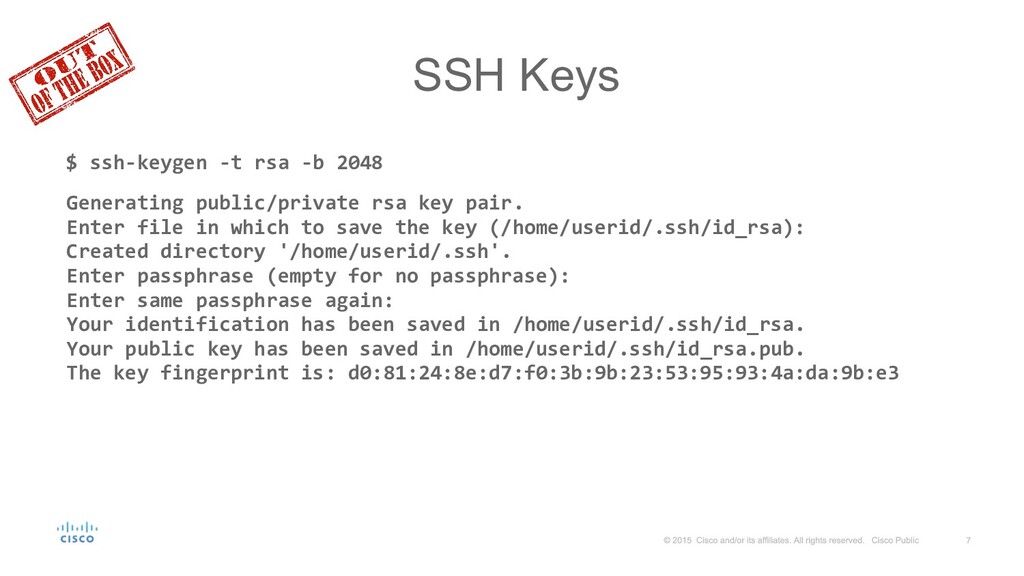
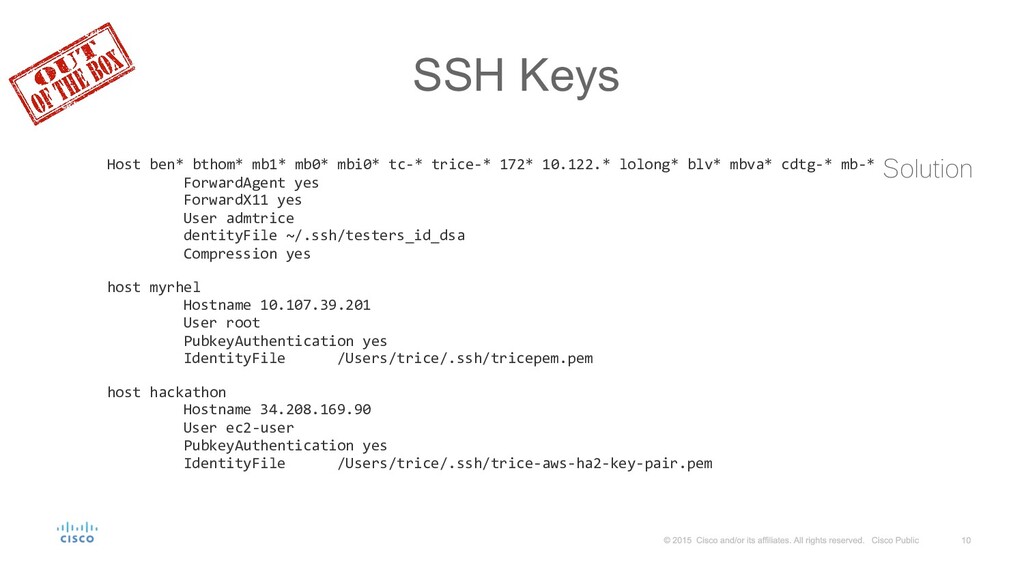
rsa key pair. Enter file in which to save the key (/home/userid/.ssh/id_rsa): Created directory '/home/userid/.ssh'. Enter passphrase (empty for no passphrase): Enter same passphrase again: Your identification has been saved in /home/userid/.ssh/id_rsa. Your public key has been saved in /home/userid/.ssh/id_rsa.pub. The key fingerprint is: d0:81:24:8e:d7:f0:3b:9b:23:53:95:93:4a:da:9b:e3
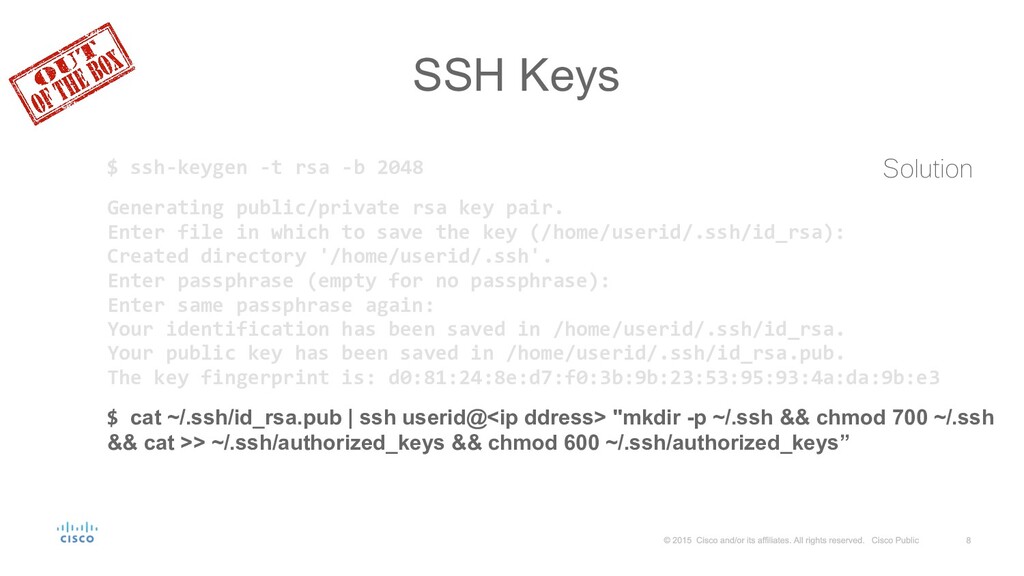
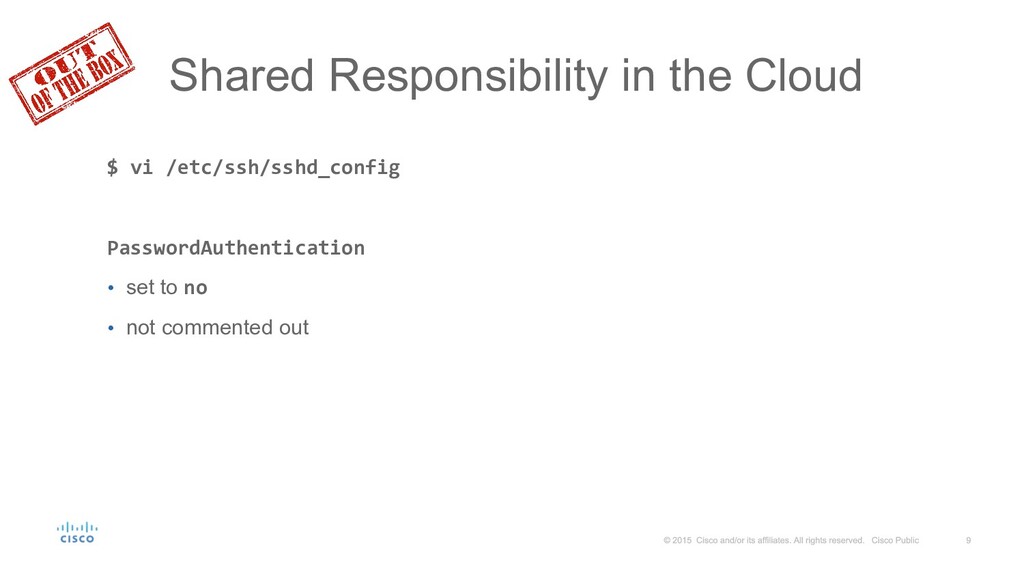
public/private rsa key pair. Enter file in which to save the key (/home/userid/.ssh/id_rsa): Created directory '/home/userid/.ssh'. Enter passphrase (empty for no passphrase): Enter same passphrase again: Your identification has been saved in /home/userid/.ssh/id_rsa. Your public key has been saved in /home/userid/.ssh/id_rsa.pub. The key fingerprint is: d0:81:24:8e:d7:f0:3b:9b:23:53:95:93:4a:da:9b:e3 $ cat ~/.ssh/id_rsa.pub | ssh userid@<ip ddress> "mkdir -p ~/.ssh && chmod 700 ~/.ssh && cat >> ~/.ssh/authorized_keys && chmod 600 ~/.ssh/authorized_keys”
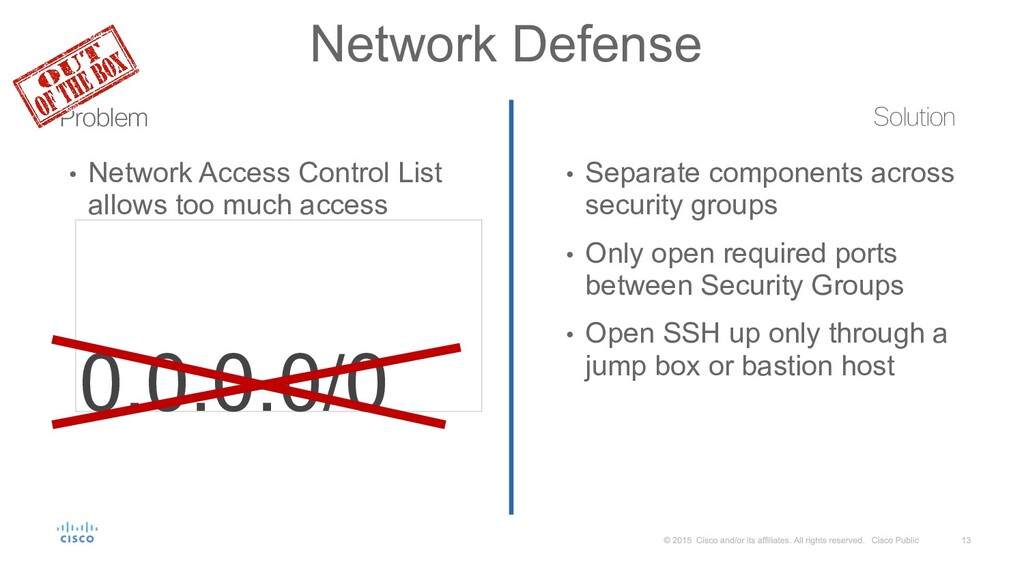
much access • Separate components across security groups • Only open required ports between Security Groups • Open SSH up only through a jump box or bastion host Network Defense
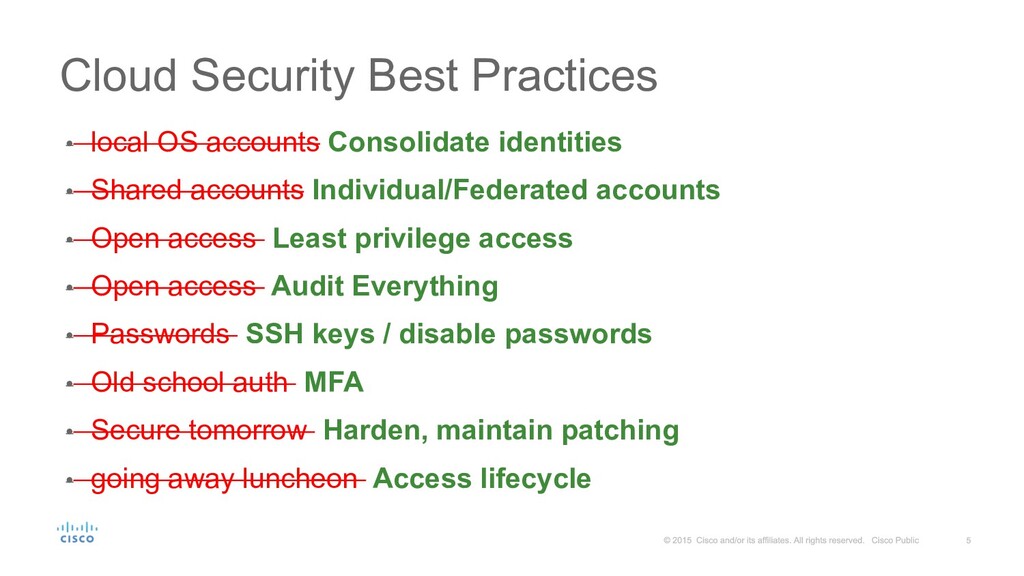
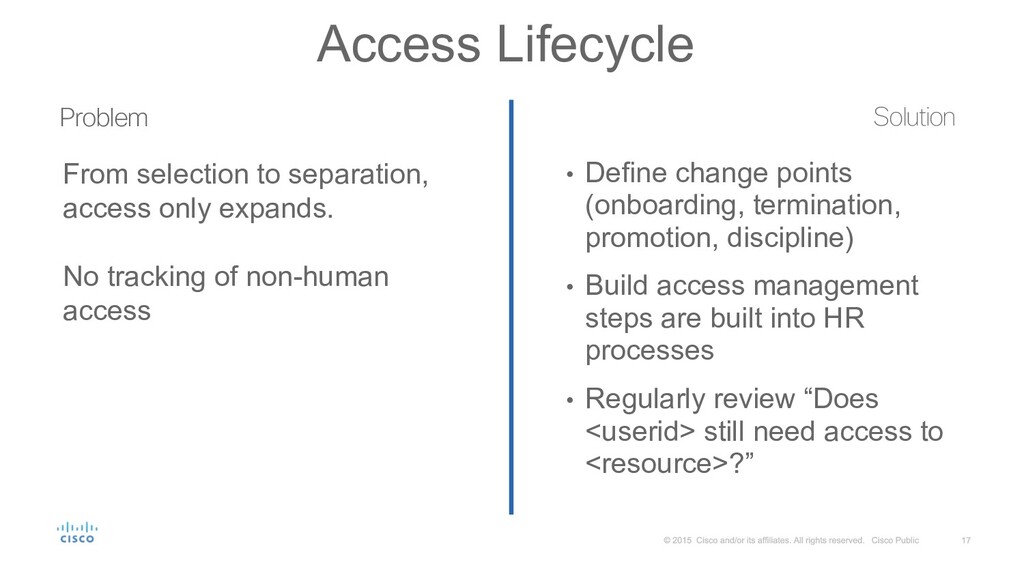
tracking of non-human access • Define change points (onboarding, termination, promotion, discipline) • Build access management steps are built into HR processes • Regularly review “Does <userid> still need access to <resource>?” Access Lifecycle
in your network? applications? • Cloudtrail and Cloudwatch provide easy solutions • Elk and Splunk for searching • Move logs off to cheap storage Audit Logging
ICMP DOS • Advertises your infrastructure, even known vulnerabilities • ICMP is disabled by default, leave it that way. • Disable again after any troubleshooting or auditing should ICMP
reserved. 20 • Amazon Web Services Security https://aws.amazon.com/security • Center for Internet Security http://cisecurity.org • Security of Cloud Computing: Seeing Through the Fog http://www.satnac.org.za/proceedings/2011/papers/Internet_Services_and_Applications/178.pdf • CSA Security Guidance Version 3 https://cloudsecurityalliance.org/download/security-guidance-for-critical-areas-of-focus-in-cloud-computing-v3/


 Your Podcast. Everywhere. Effortlessly.


 tonyrice
 lauravandoore
 soudai
 aleyda
 sergeychernyshev
 inesmontani
 hannesfritz
 baasie
 ks91
 ipullrank
 chriscoyier
 garrettdimon