Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
API authorization with OAuth
Search
Bastian Hofmann
October 17, 2012
Programming
1.2k
5
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
API authorization with OAuth
Bastian Hofmann
October 17, 2012
Transcript
110 slides
API authorization with OAuth @BastianHofmann
http://oauth.net/
API
None
None
None
ResearchGate gives science back to the people who make it
happen. We help researchers build reputation and accelerate scientific progress. On their terms. ‟
None
None
None
None
None
None
None
Questions? Ask!
http://speakerdeck.com/u/bastianhofmann
http://oauth.net/
http://tools.ietf.org/html/rfc5849
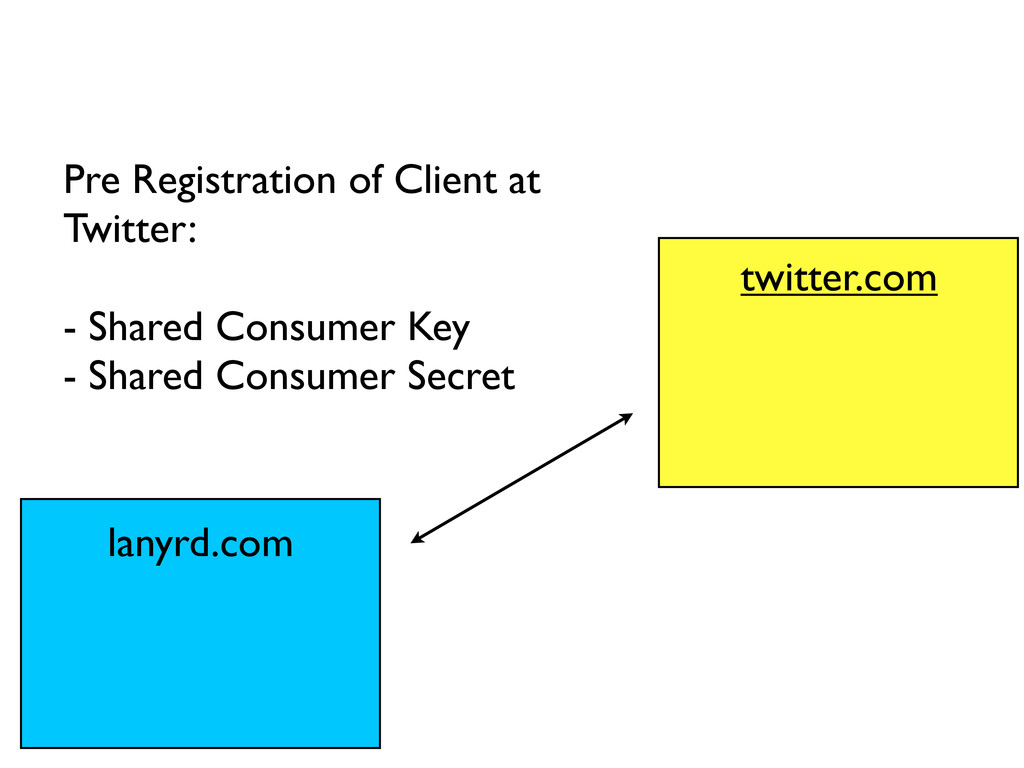
lanyrd.com twitter.com Pre Registration of Client at Twitter: - Shared
Consumer Key - Shared Consumer Secret
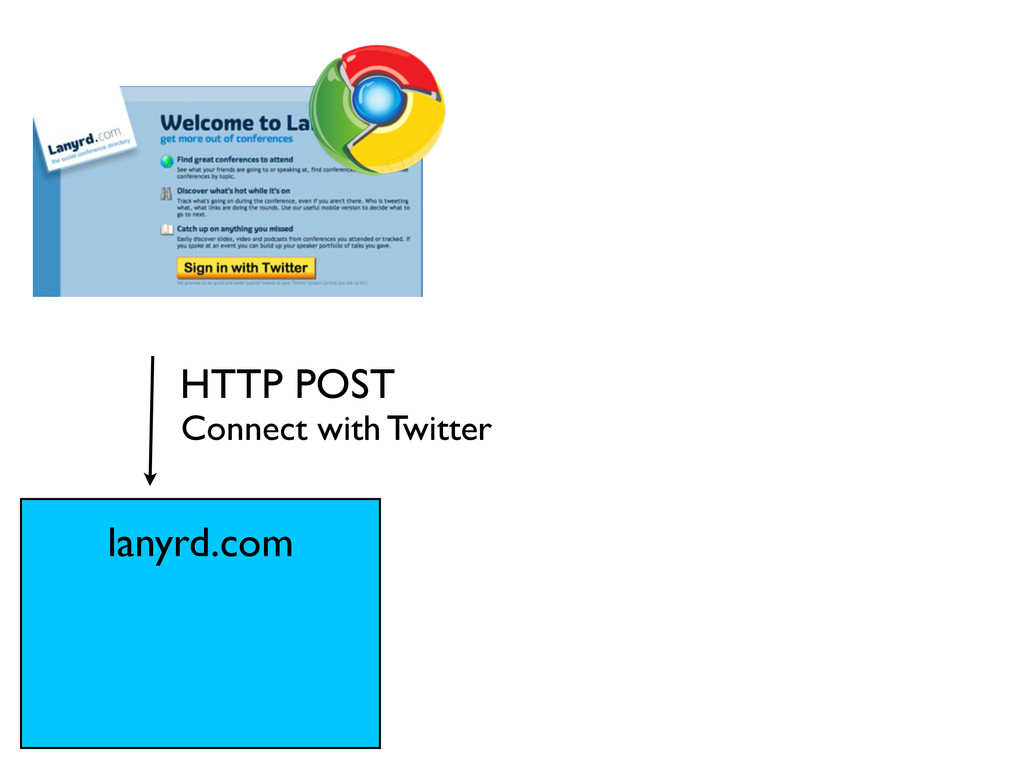
HTTP POST Connect with Twitter lanyrd.com
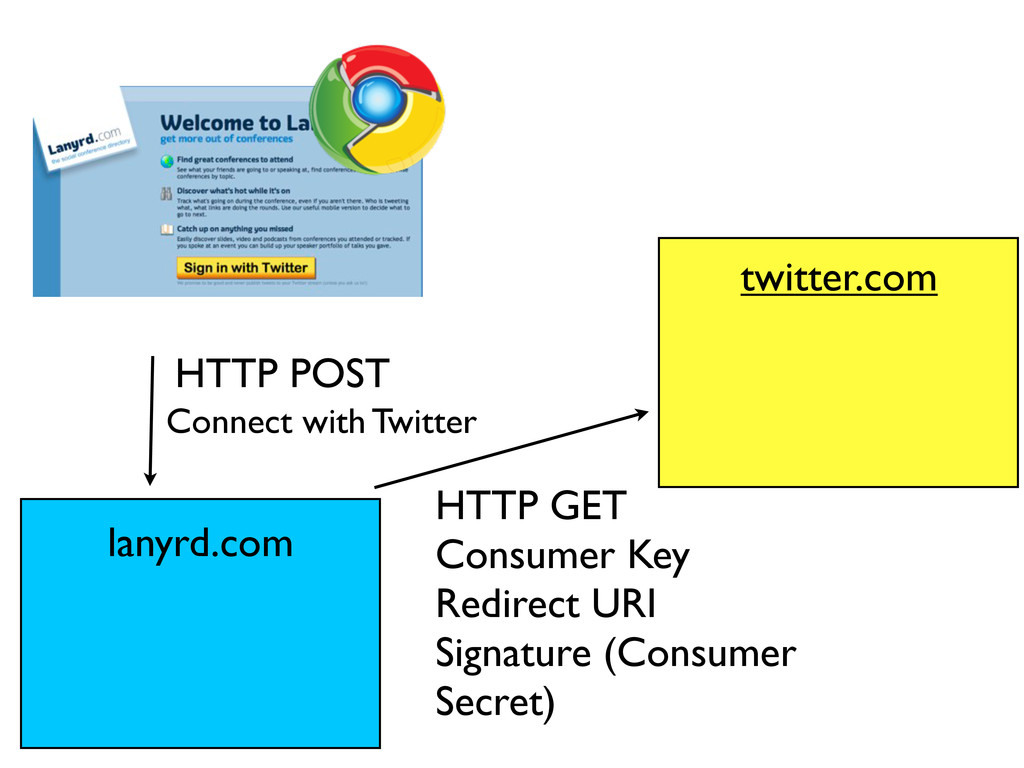
twitter.com HTTP POST Connect with Twitter HTTP GET Consumer Key
Redirect URI Signature (Consumer Secret) lanyrd.com
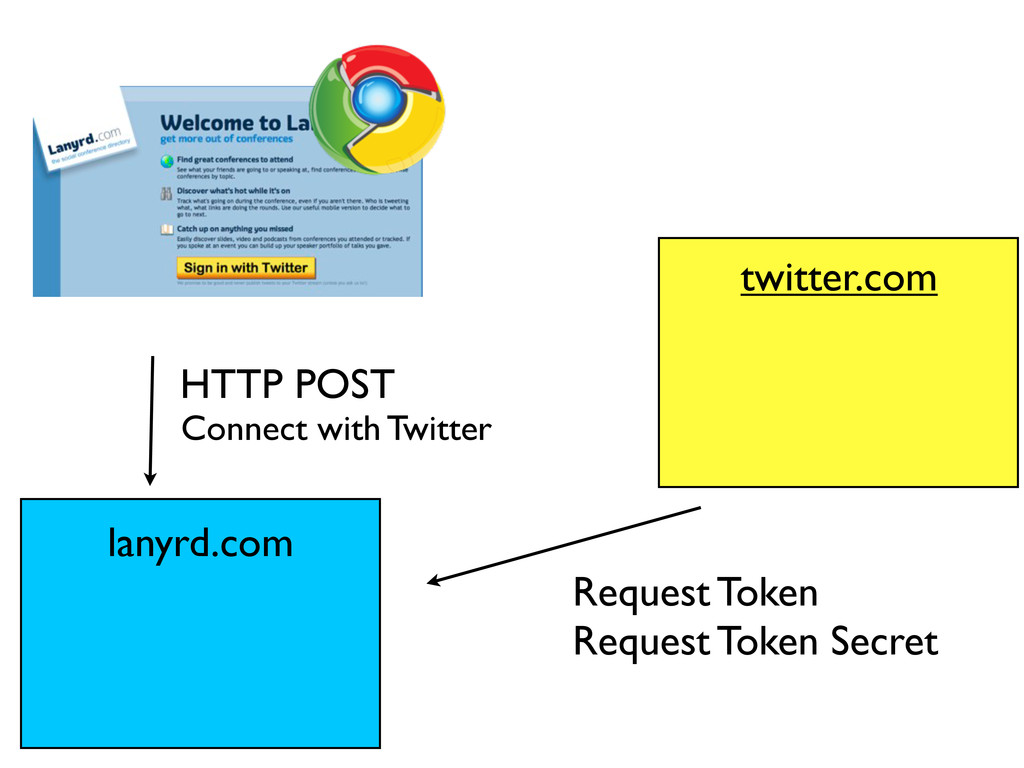
twitter.com HTTP POST Connect with Twitter Request Token Request Token
Secret lanyrd.com
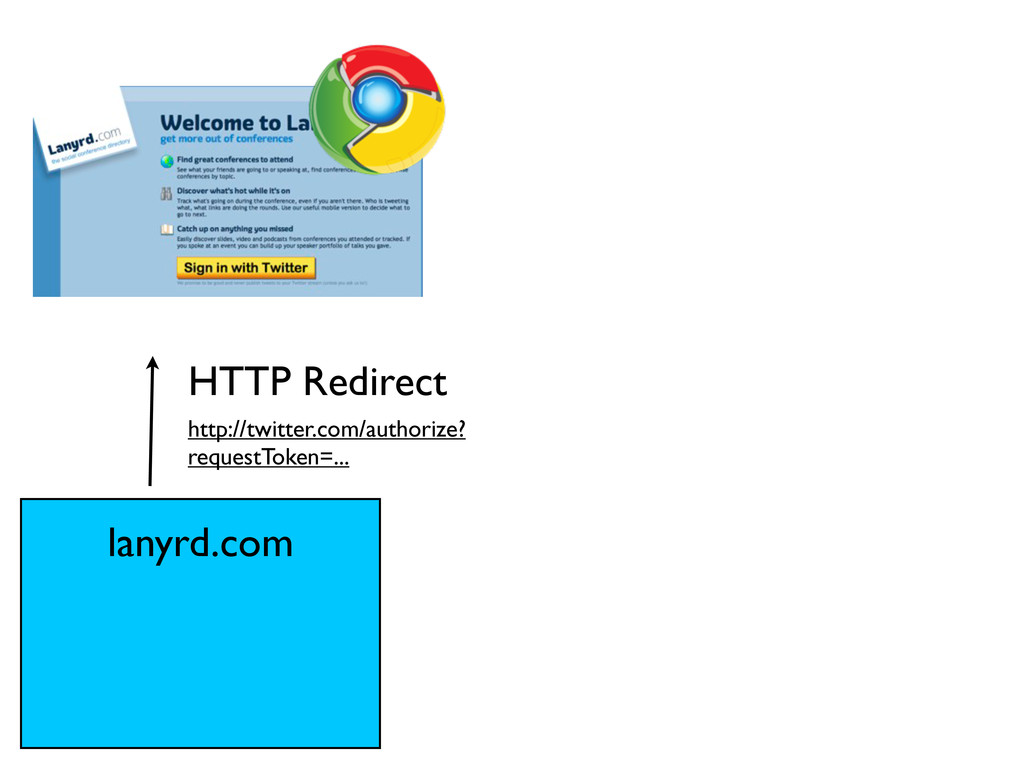
http://twitter.com/authorize? requestToken=... HTTP Redirect lanyrd.com
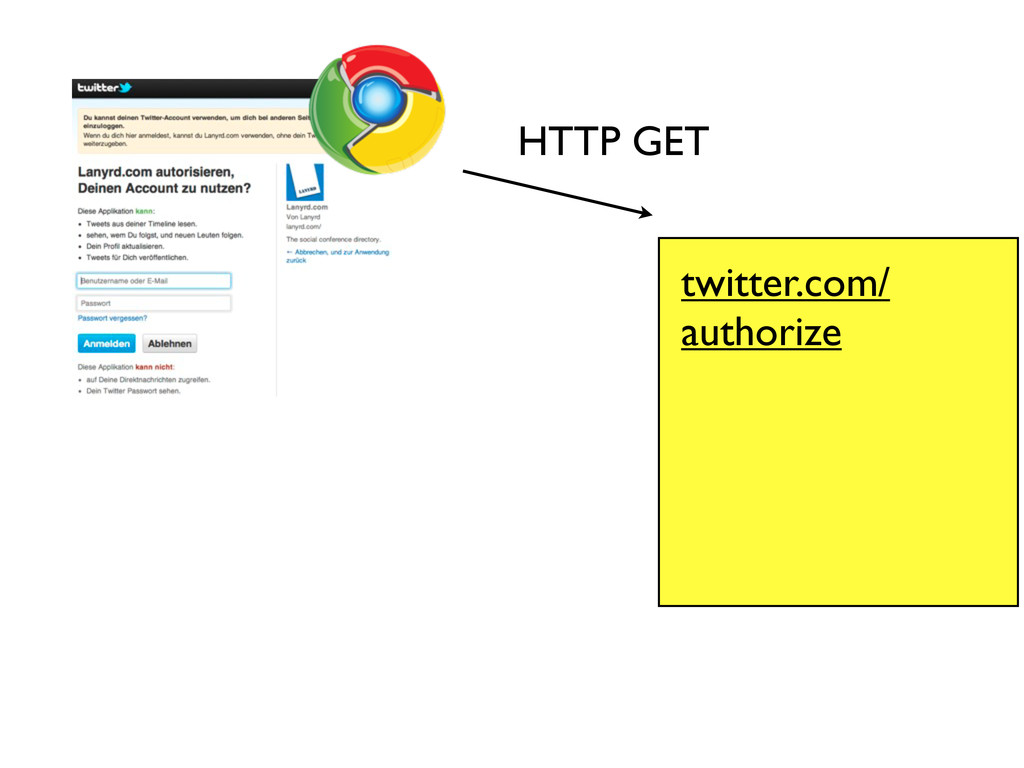
HTTP GET twitter.com/ authorize
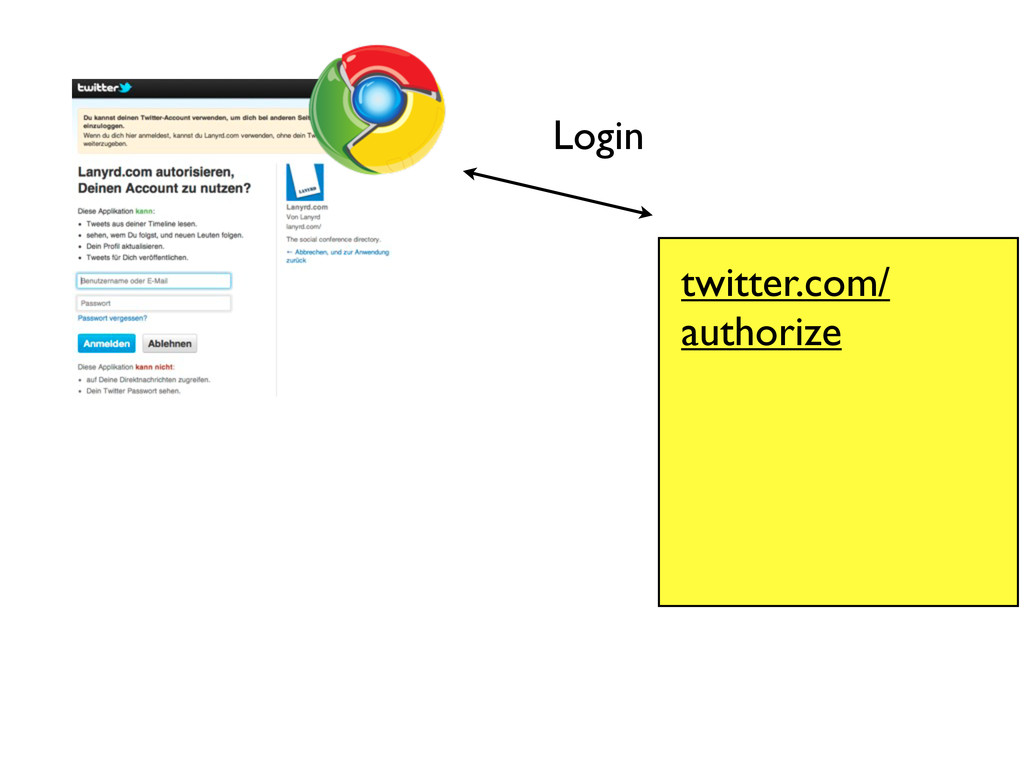
Login twitter.com/ authorize
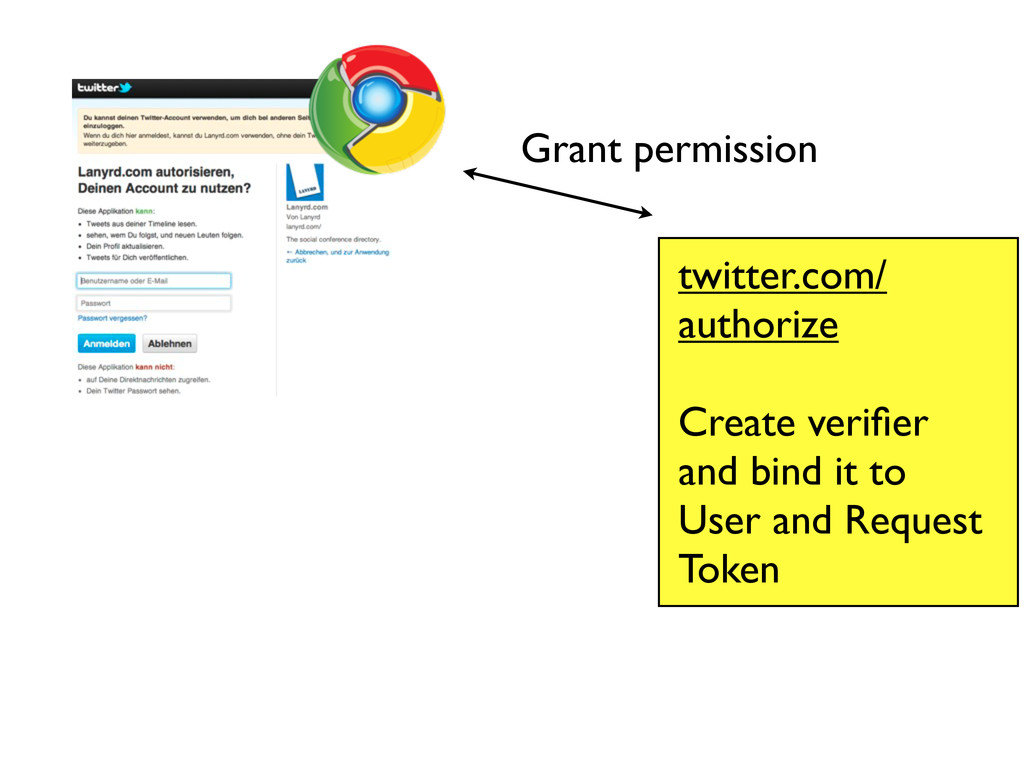
Grant permission twitter.com/ authorize Create verifier and bind it to
User and Request Token
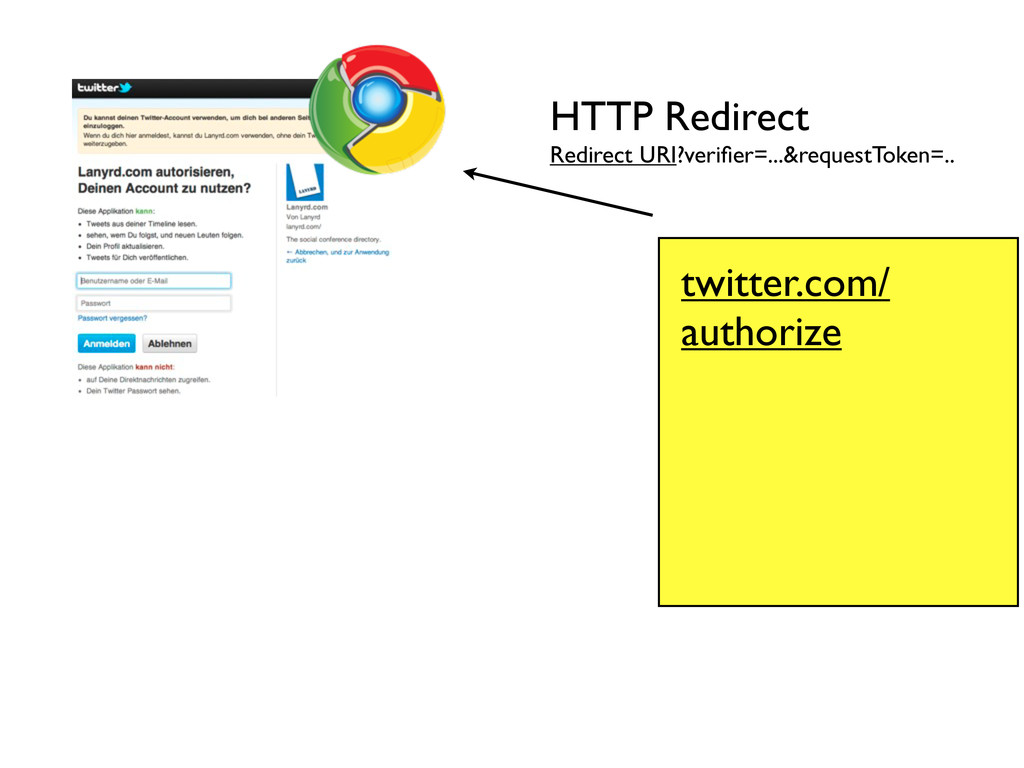
Redirect URI?verifier=...&requestToken=.. HTTP Redirect twitter.com/ authorize
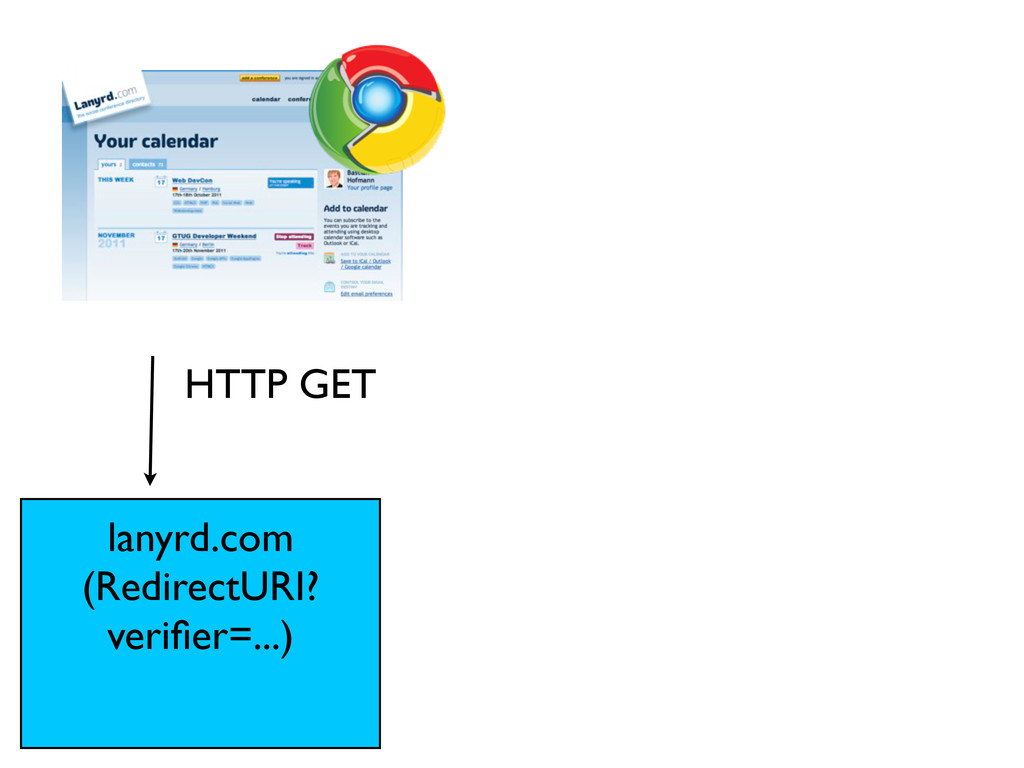
HTTP GET lanyrd.com (RedirectURI? verifier=...)
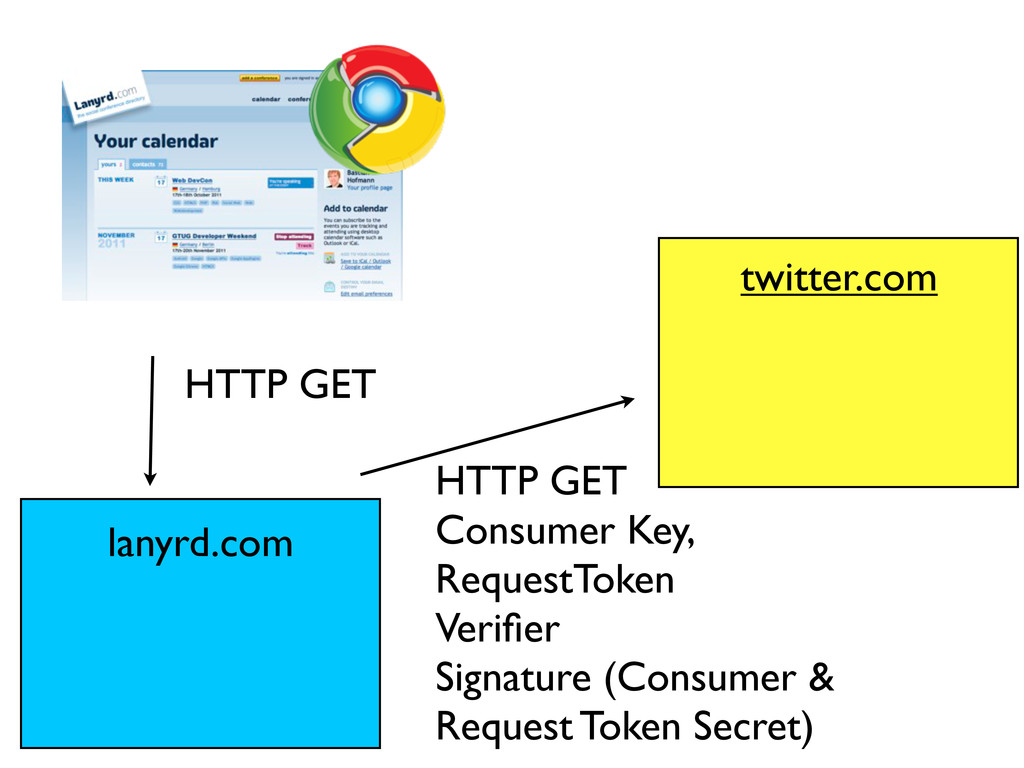
HTTP GET HTTP GET Consumer Key, RequestToken Verifier Signature (Consumer
& Request Token Secret) twitter.com lanyrd.com
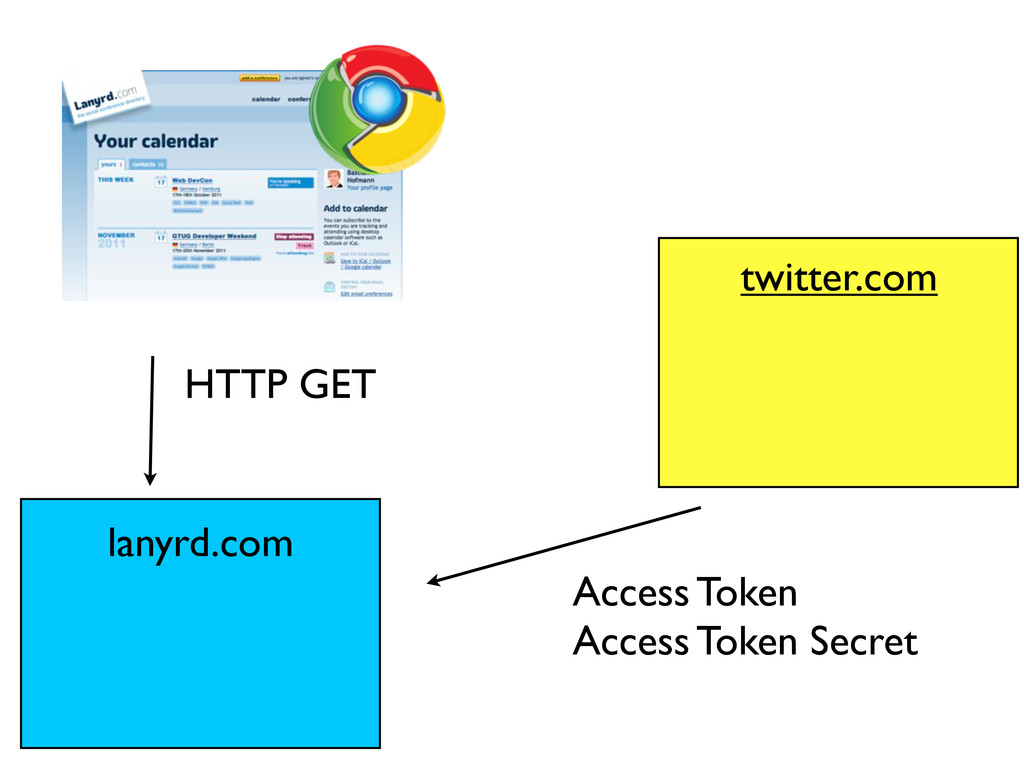
HTTP GET Access Token Access Token Secret twitter.com lanyrd.com
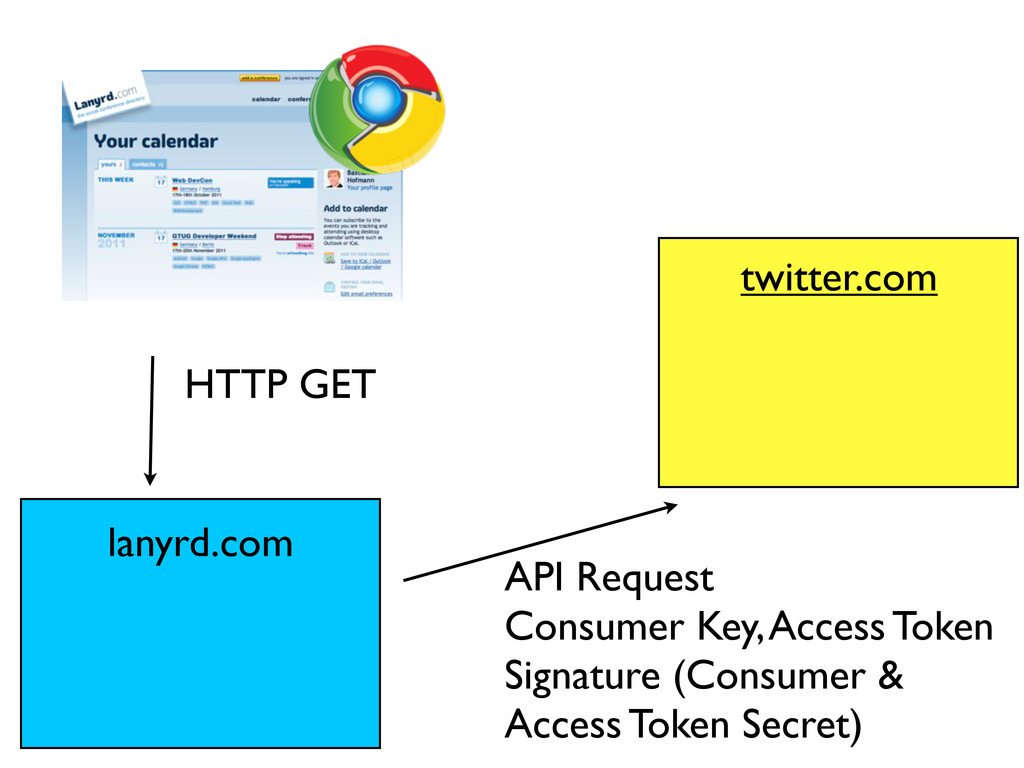
HTTP GET API Request Consumer Key, Access Token Signature (Consumer
& Access Token Secret) twitter.com lanyrd.com
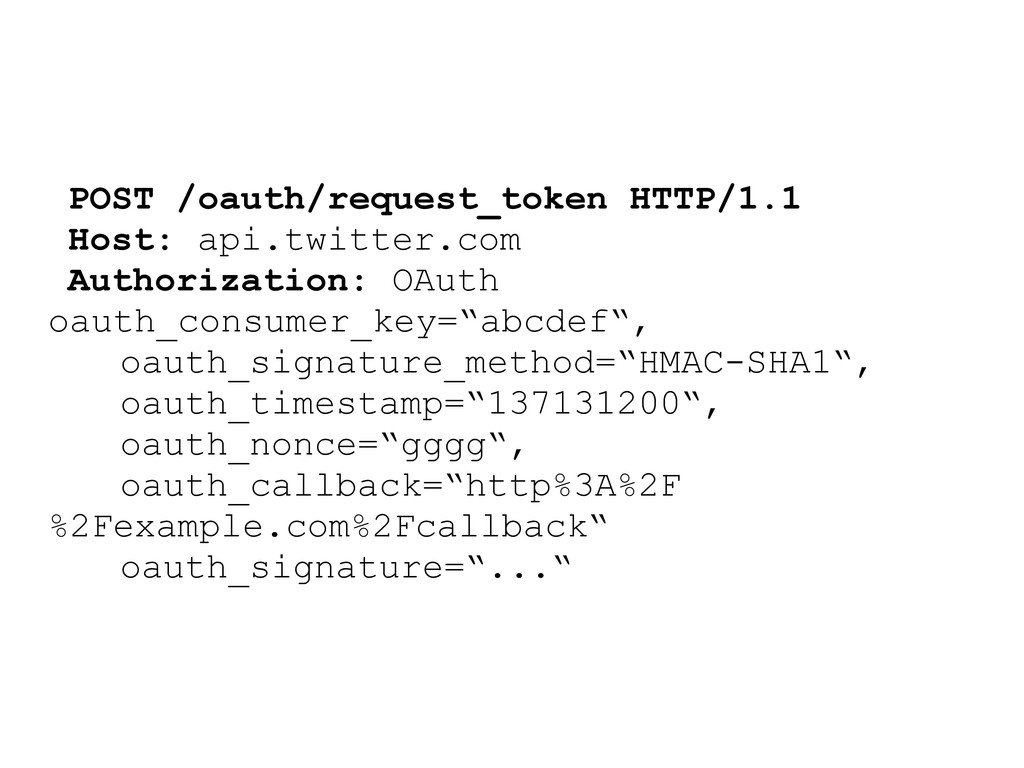
POST /oauth/request_token HTTP/1.1 Host: api.twitter.com Authorization: OAuth oauth_consumer_key=“abcdef“, oauth_signature_method=“HMAC-SHA1“, oauth_timestamp=“137131200“,
oauth_nonce=“gggg“, oauth_callback=“http%3A%2F %2Fexample.com%2Fcallback“ oauth_signature=“...“
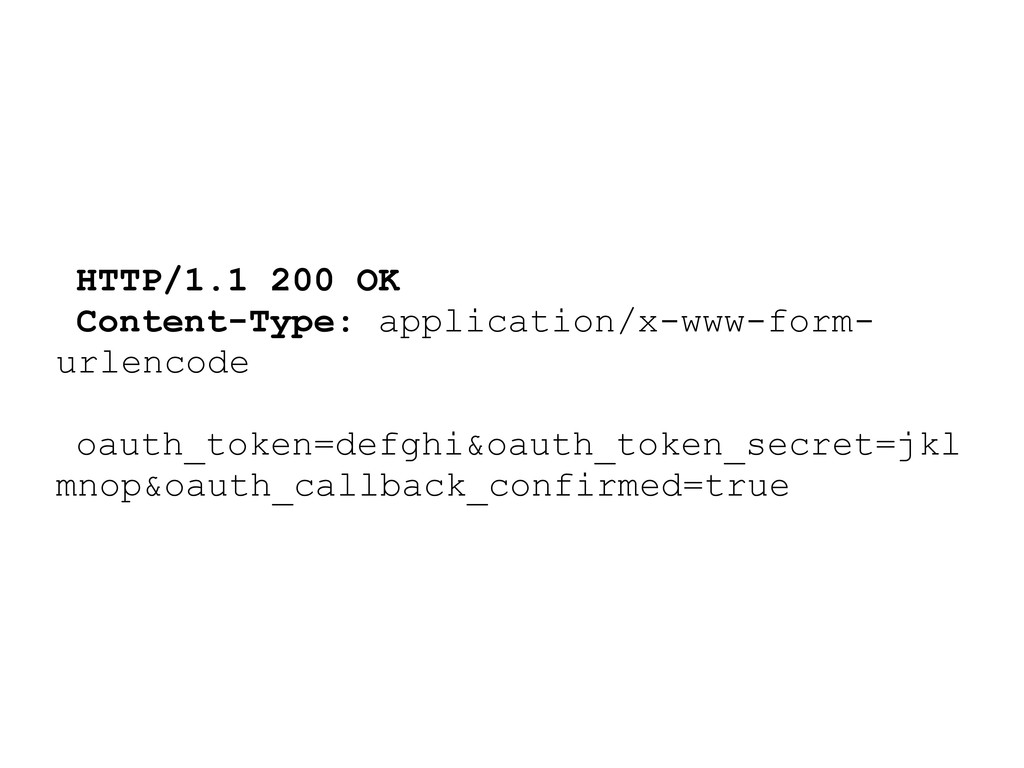
HTTP/1.1 200 OK Content-Type: application/x-www-form- urlencode oauth_token=defghi&oauth_token_secret=jkl mnop&oauth_callback_confirmed=true
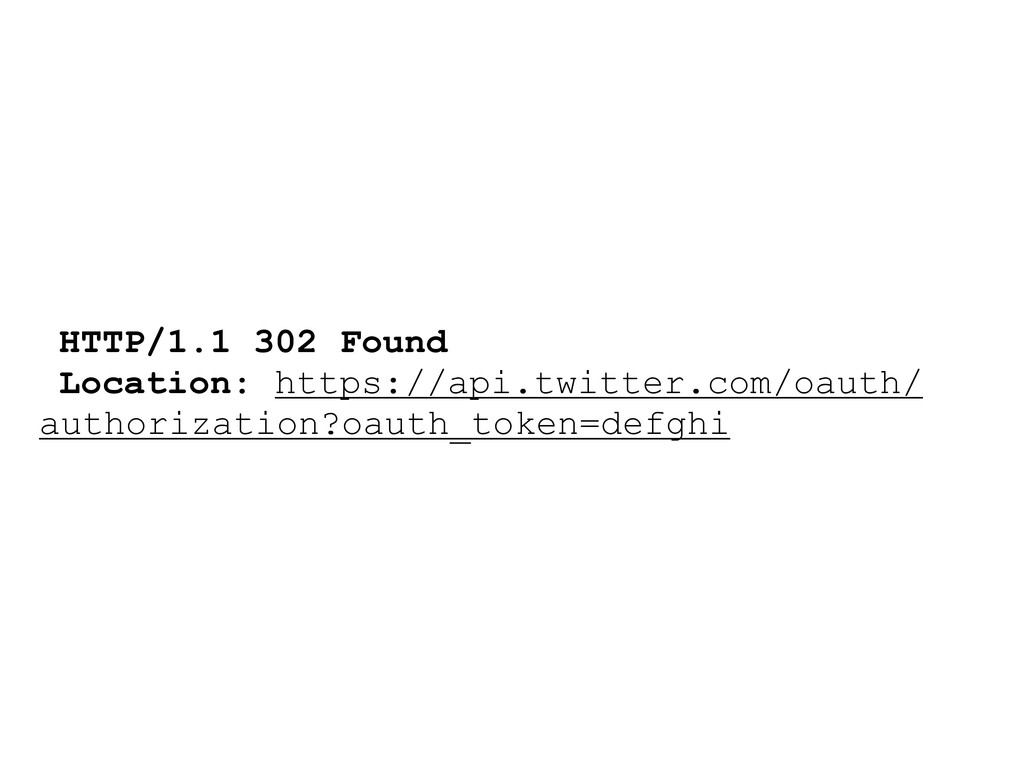
HTTP/1.1 302 Found Location: https://api.twitter.com/oauth/ authorization?oauth_token=defghi
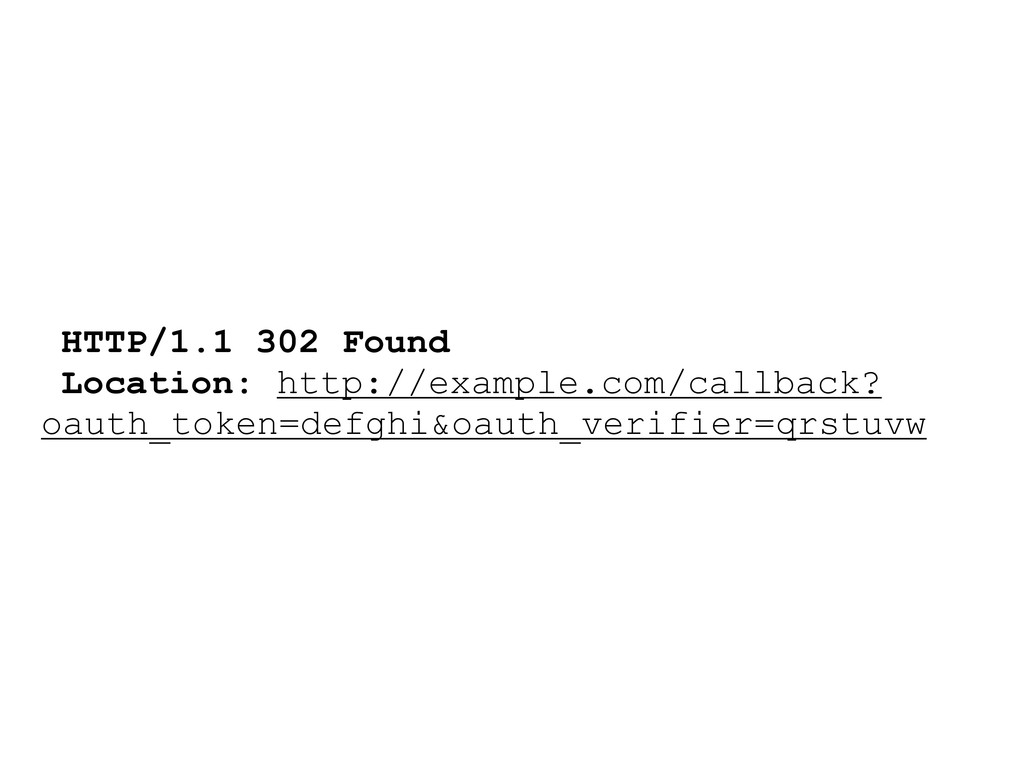
HTTP/1.1 302 Found Location: http://example.com/callback? oauth_token=defghi&oauth_verifier=qrstuvw
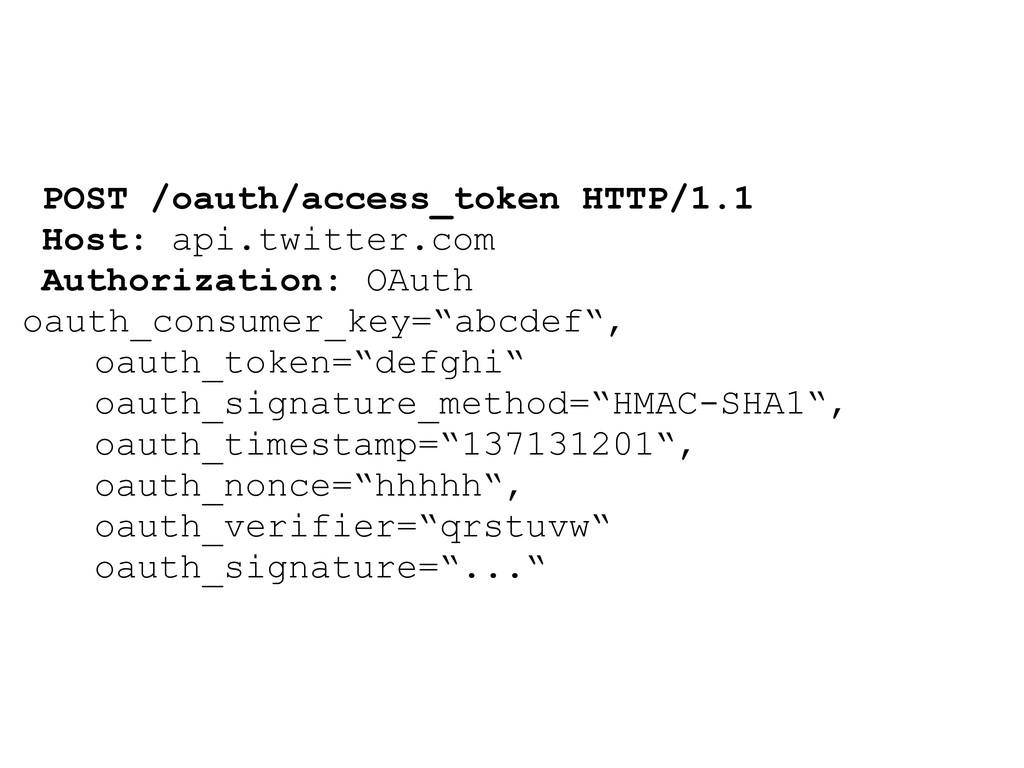
POST /oauth/access_token HTTP/1.1 Host: api.twitter.com Authorization: OAuth oauth_consumer_key=“abcdef“, oauth_token=“defghi“ oauth_signature_method=“HMAC-SHA1“,
oauth_timestamp=“137131201“, oauth_nonce=“hhhhh“, oauth_verifier=“qrstuvw“ oauth_signature=“...“
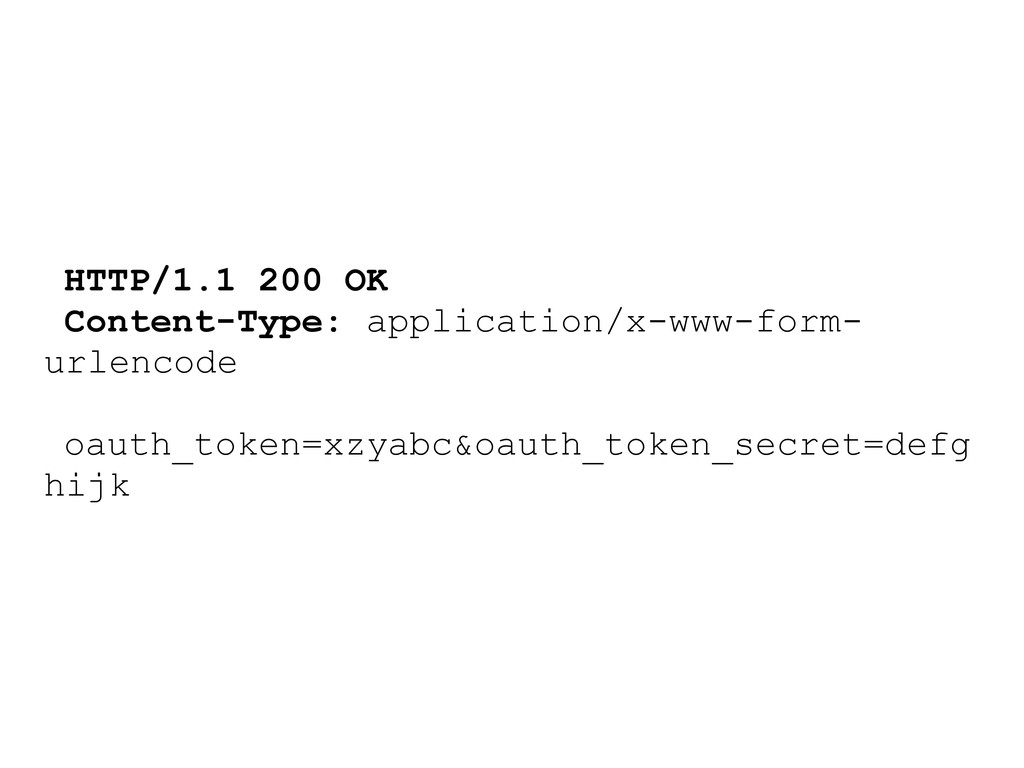
HTTP/1.1 200 OK Content-Type: application/x-www-form- urlencode oauth_token=xzyabc&oauth_token_secret=defg hijk
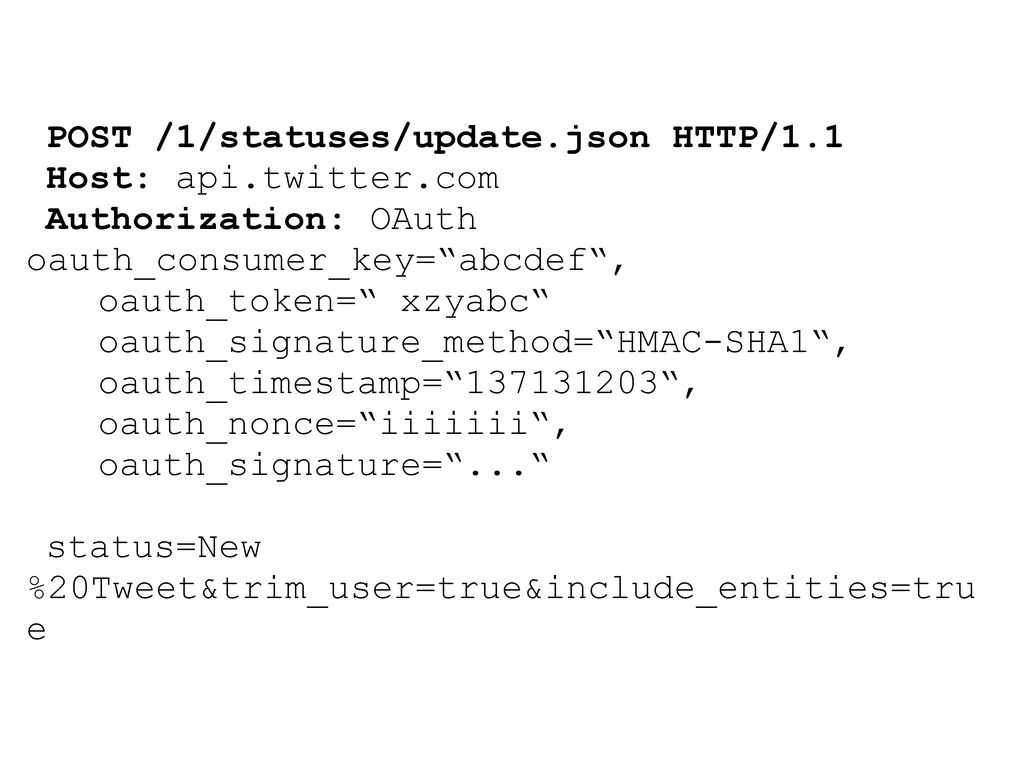
POST /1/statuses/update.json HTTP/1.1 Host: api.twitter.com Authorization: OAuth oauth_consumer_key=“abcdef“, oauth_token=“ xzyabc“
oauth_signature_method=“HMAC-SHA1“, oauth_timestamp=“137131203“, oauth_nonce=“iiiiiii“, oauth_signature=“...“ status=New %20Tweet&trim_user=true&include_entities=tru e
Signatures
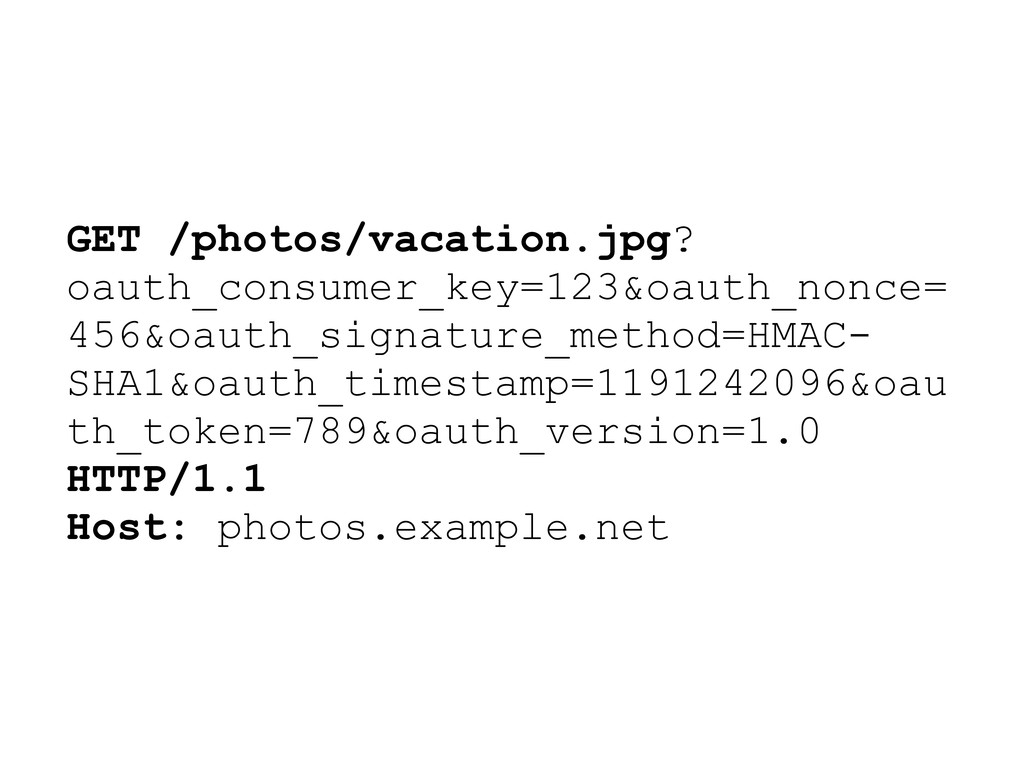
GET /photos/vacation.jpg? oauth_consumer_key=123&oauth_nonce= 456&oauth_signature_method=HMAC- SHA1&oauth_timestamp=1191242096&oau th_token=789&oauth_version=1.0 HTTP/1.1 Host: photos.example.net
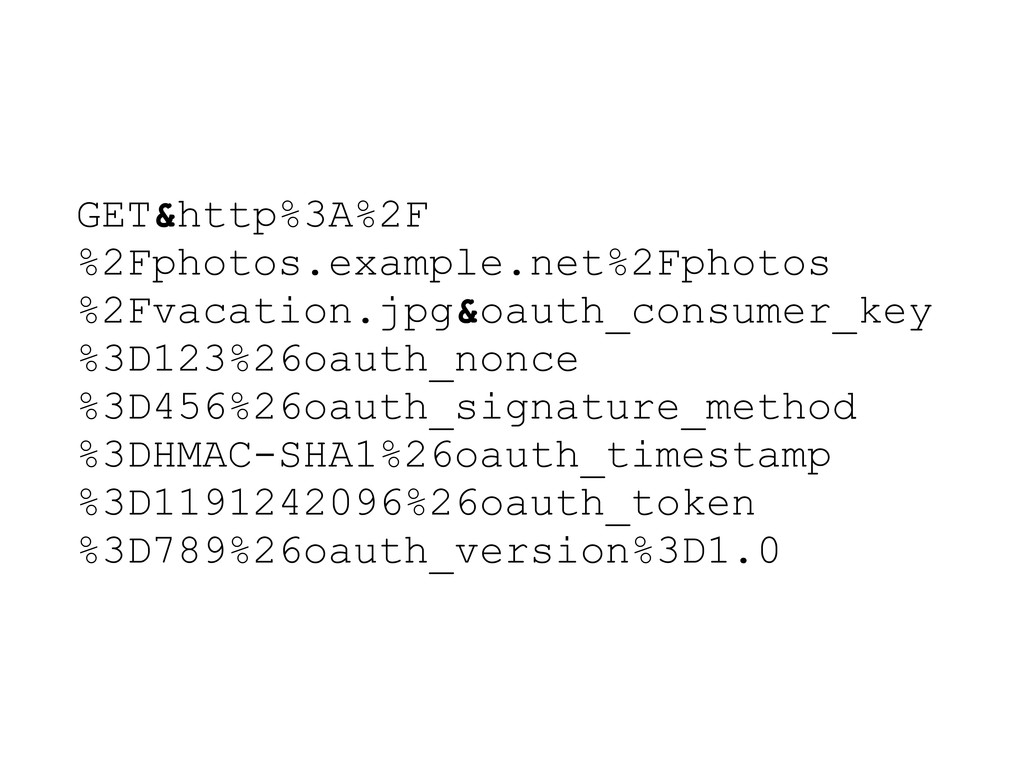
GET&http%3A%2F %2Fphotos.example.net%2Fphotos %2Fvacation.jpg&oauth_consumer_key %3D123%26oauth_nonce %3D456%26oauth_signature_method %3DHMAC-SHA1%26oauth_timestamp %3D1191242096%26oauth_token %3D789%26oauth_version%3D1.0
PLAINTEXT
HMAC-SHA1 Salt: consumerSecret(&tokenSecret)
RSA-SHA1 Public/Private Key
Problems Does not work well with non web or JavaScript
based clients The „Invalid Signature“ Problem Complicated Flow, many requests
How to fix it?
http://oauth.net/
31 drafts ...
...now final!
http://www.rfc-editor.org/rfc/rfc6749.txt
http://www.rfc-editor.org/rfc/rfc6750.txt
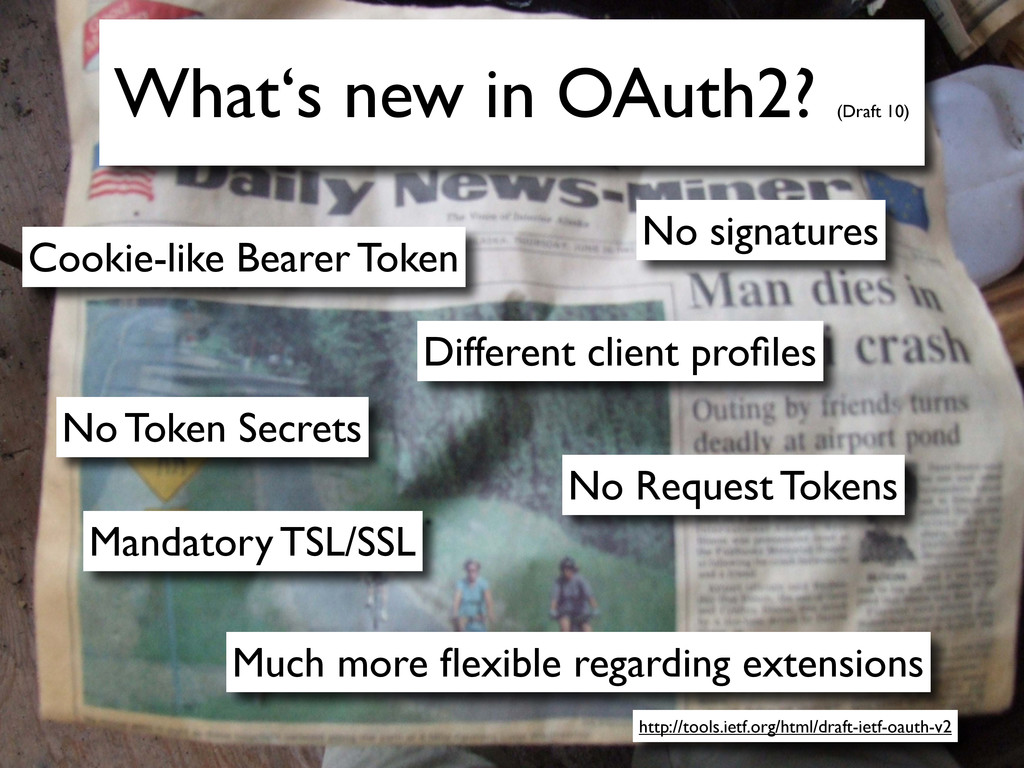
http://tools.ietf.org/html/draft-ietf-oauth-v2 What‘s new in OAuth2? (Draft 10) Different client profiles
No signatures No Token Secrets Cookie-like Bearer Token No Request Tokens Much more flexible regarding extensions Mandatory TSL/SSL
http://hueniverse.com/2012/07/oauth-2-0-and-the-road-to- hell/ ‟It is the biggest professional disappointment of my
career. Eran Hammer
http://www.tbray.org/ongoing/When/201x/2012/07/28/ Oauth2-dead OAuth 2 is useful today. ‟ Tim Bray
Web-Server Profile
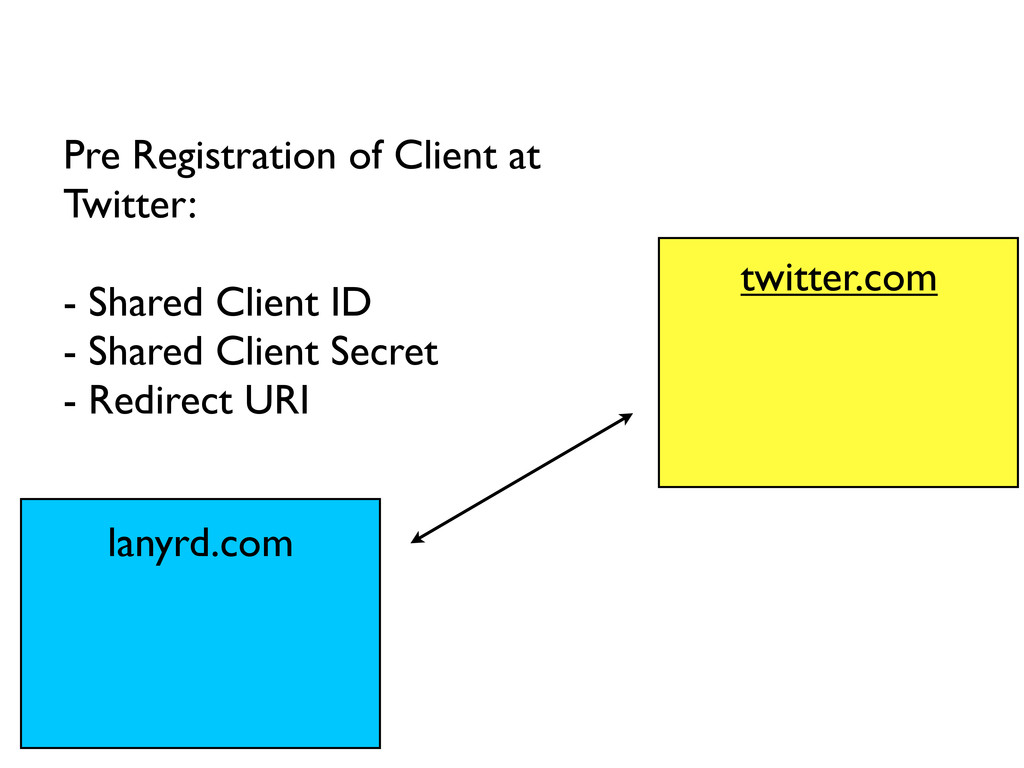
lanyrd.com twitter.com Pre Registration of Client at Twitter: - Shared
Client ID - Shared Client Secret - Redirect URI
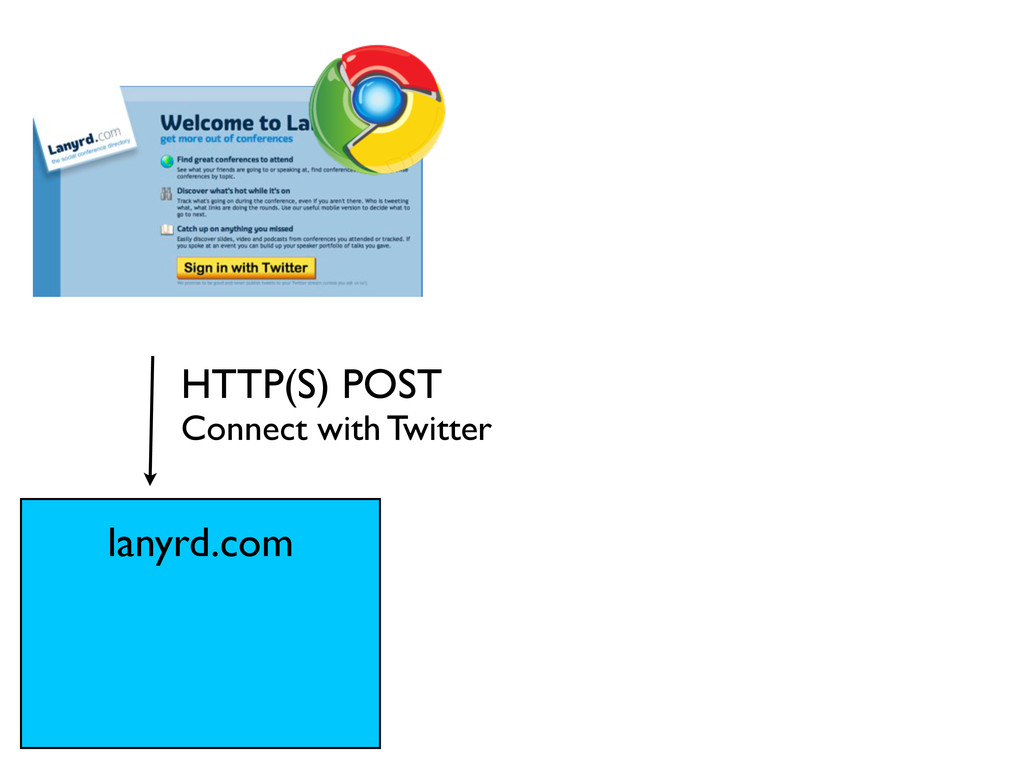
HTTP(S) POST Connect with Twitter lanyrd.com
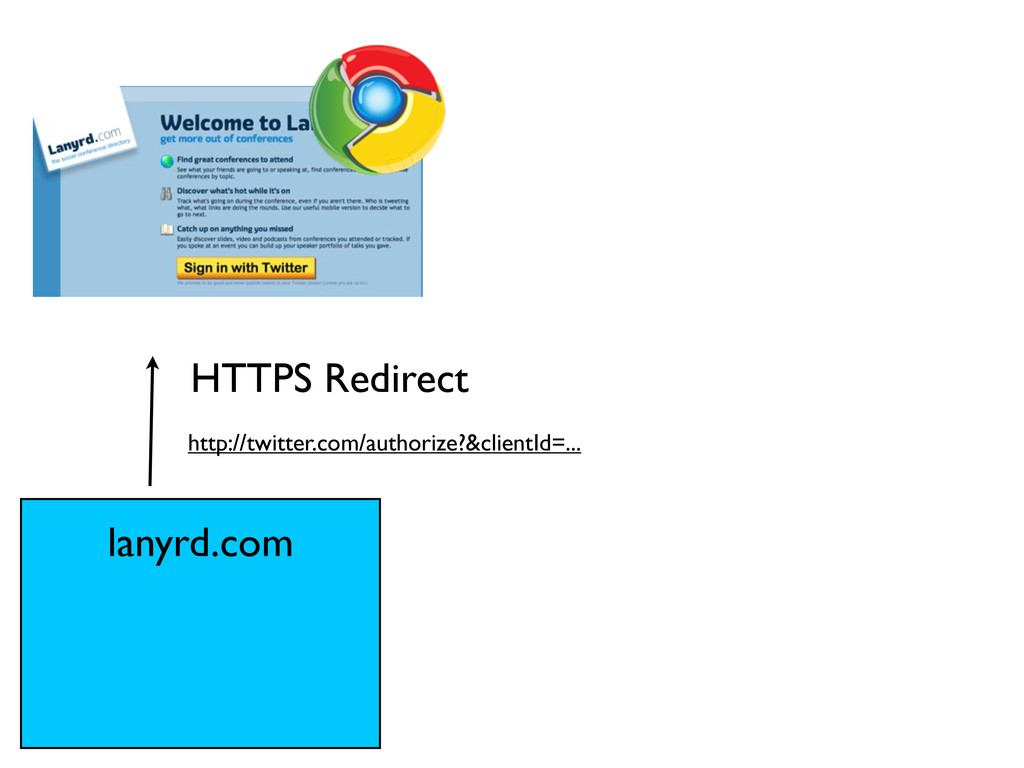
http://twitter.com/authorize?&clientId=... HTTPS Redirect lanyrd.com
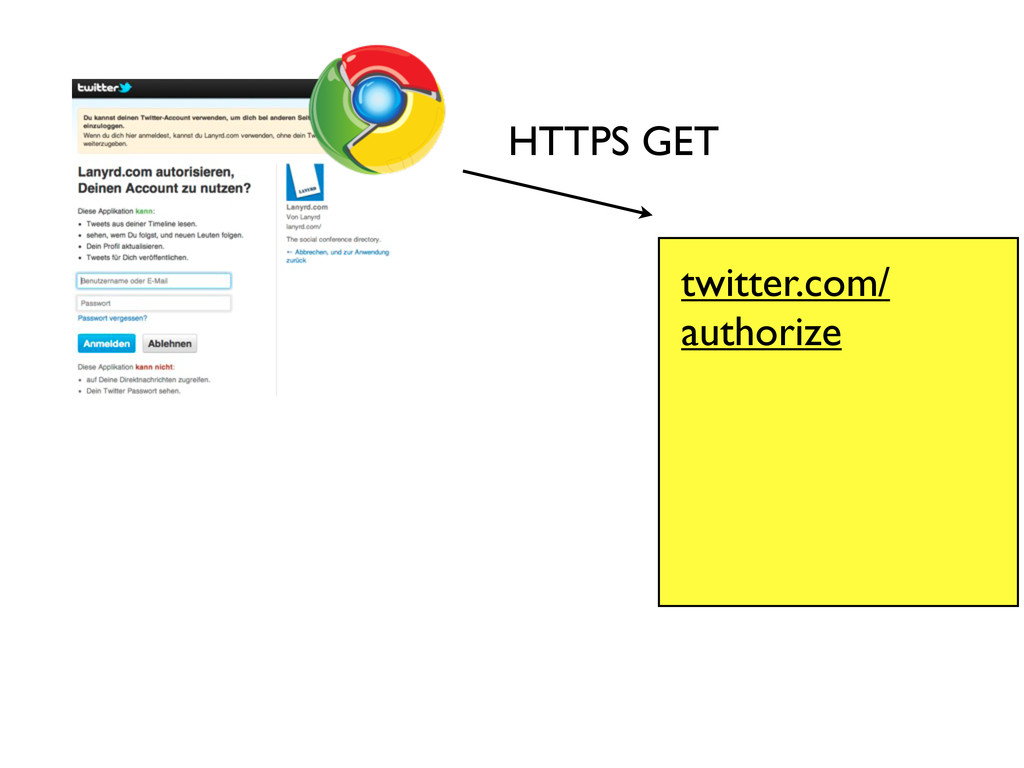
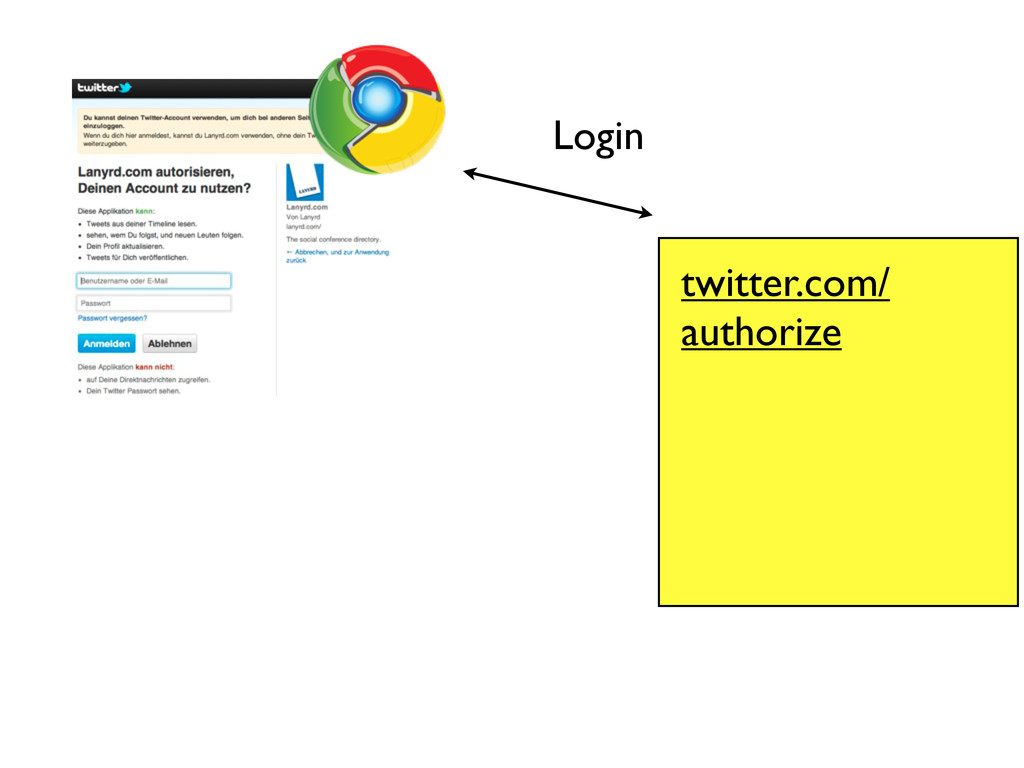
HTTPS GET twitter.com/ authorize
Login twitter.com/ authorize
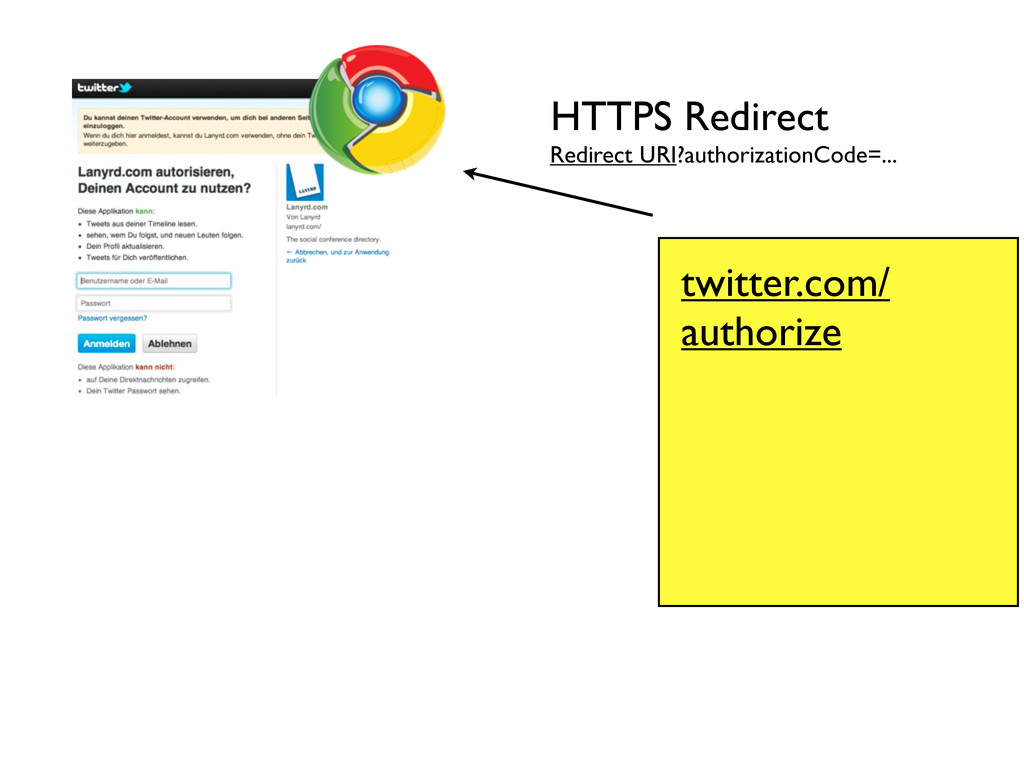
Grant permission twitter.com/ authorize Create authorization code and bind it
to User and ClientID
Redirect URI?authorizationCode=... HTTPS Redirect twitter.com/ authorize
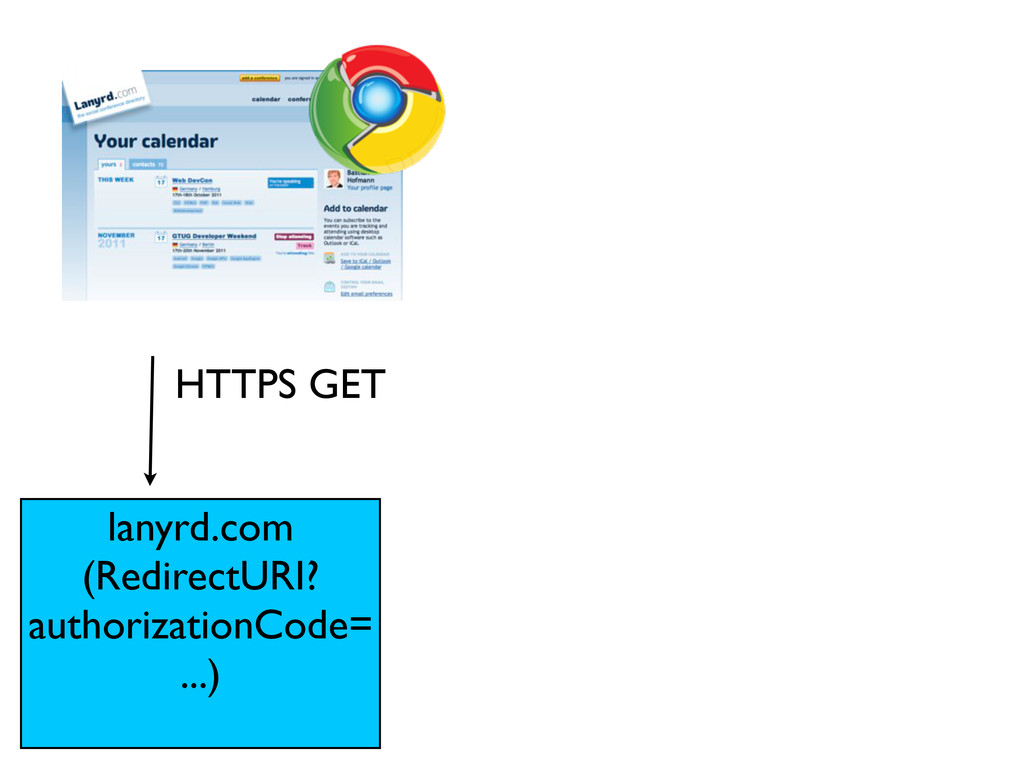
HTTPS GET lanyrd.com (RedirectURI? authorizationCode= ...)
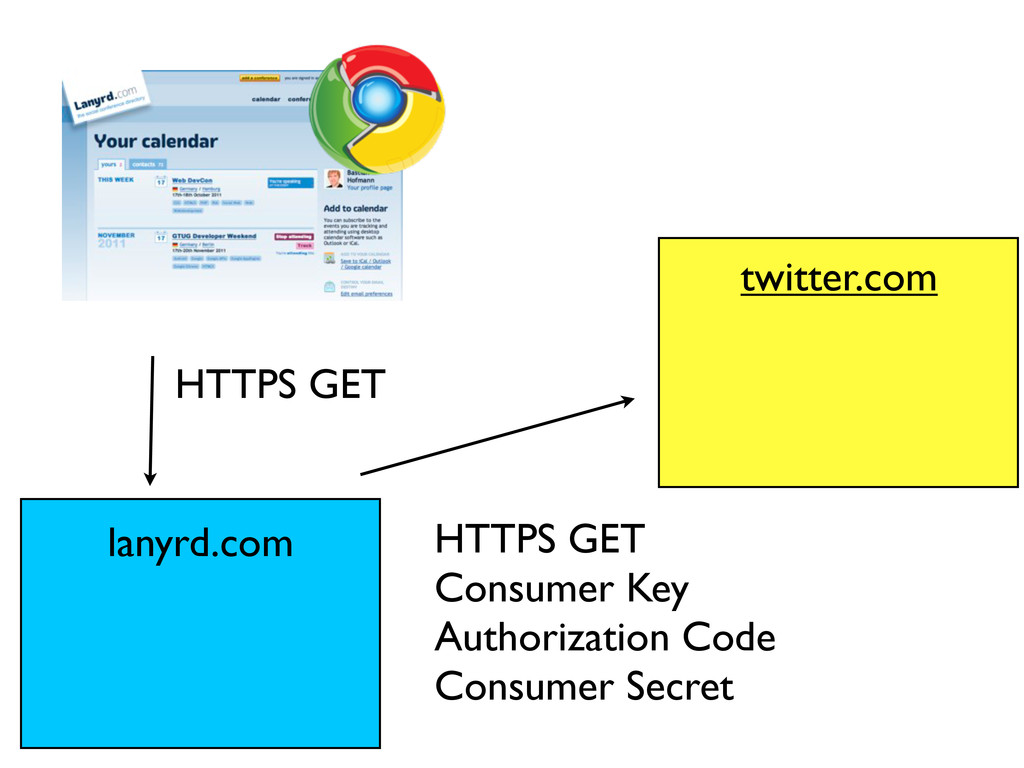
HTTPS GET HTTPS GET Consumer Key Authorization Code Consumer Secret
twitter.com lanyrd.com
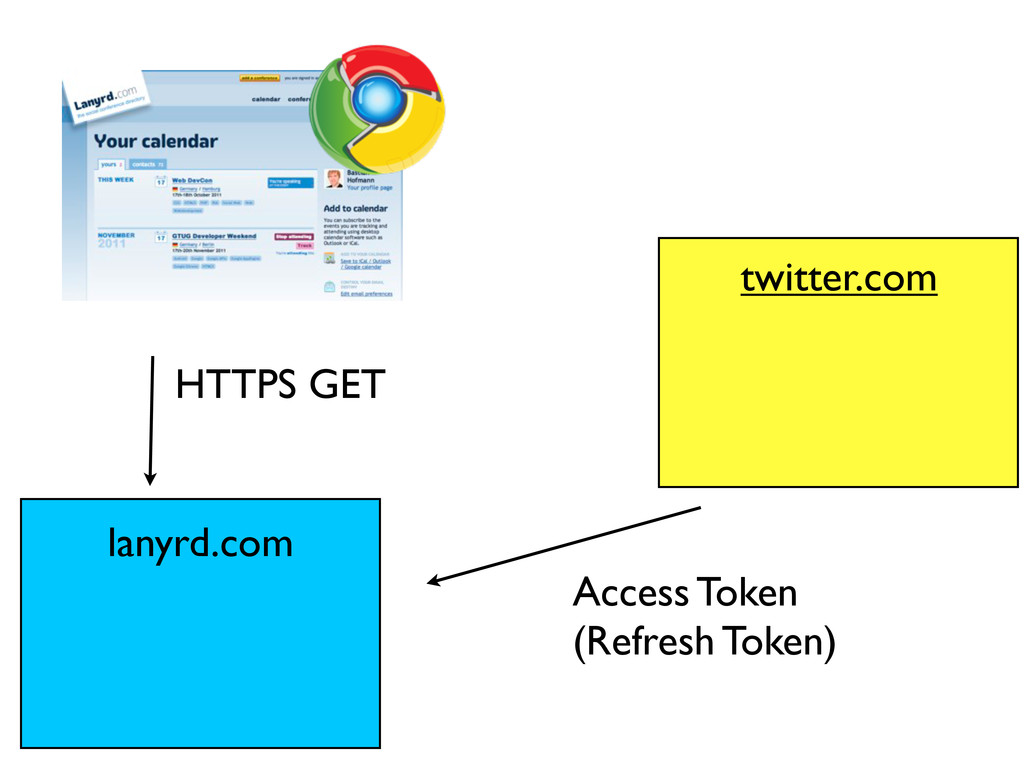
HTTPS GET Access Token (Refresh Token) twitter.com lanyrd.com
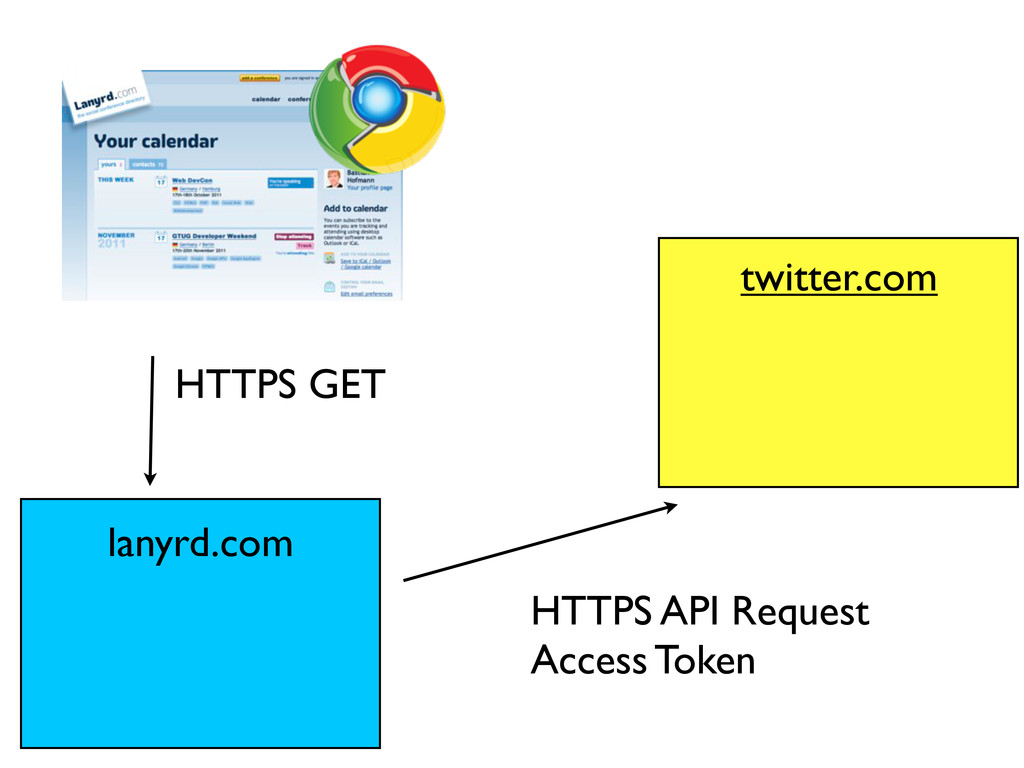
HTTPS GET HTTPS API Request Access Token twitter.com lanyrd.com
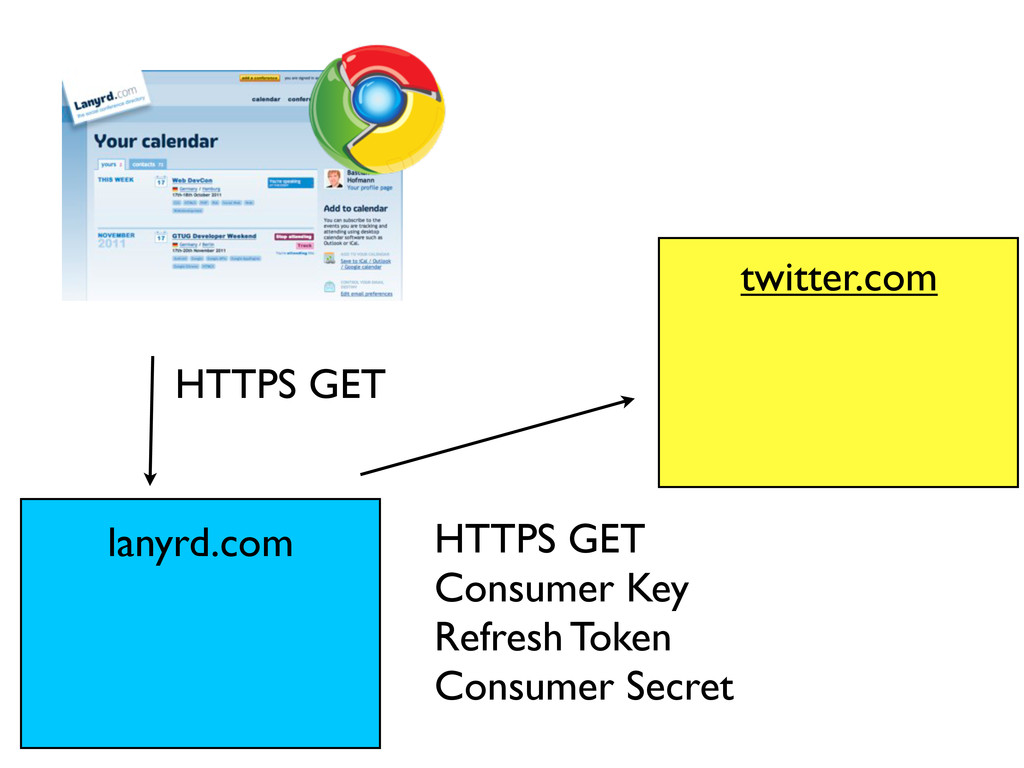
HTTPS GET HTTPS GET Consumer Key Refresh Token Consumer Secret
twitter.com lanyrd.com
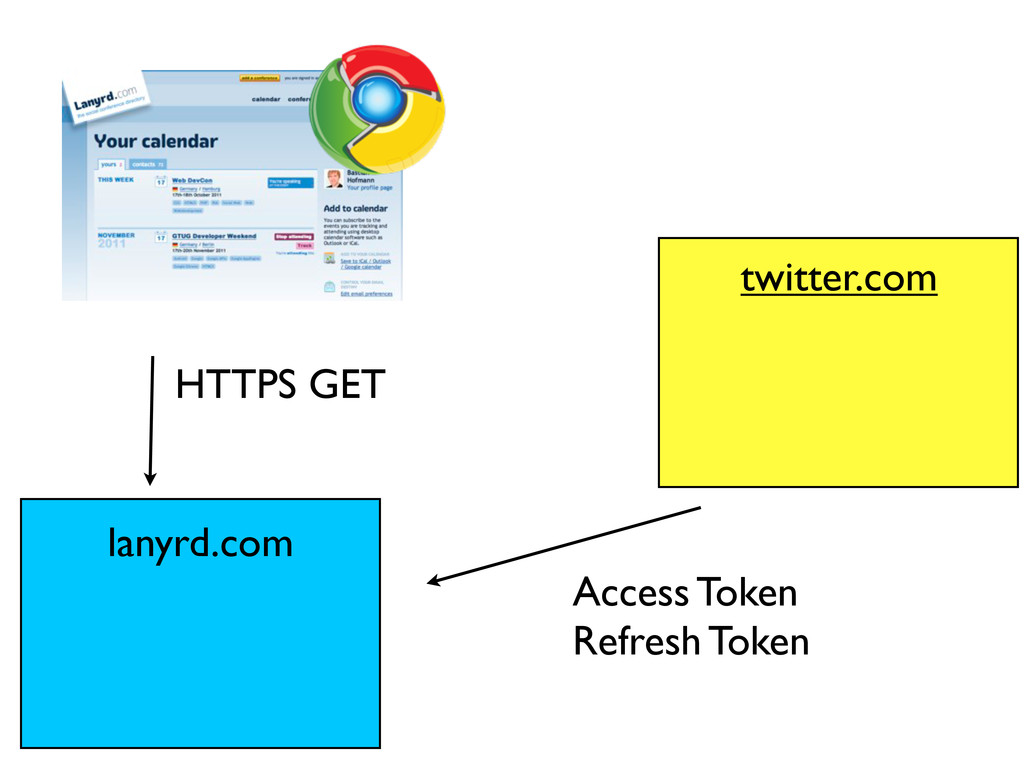
HTTPS GET Access Token Refresh Token twitter.com lanyrd.com
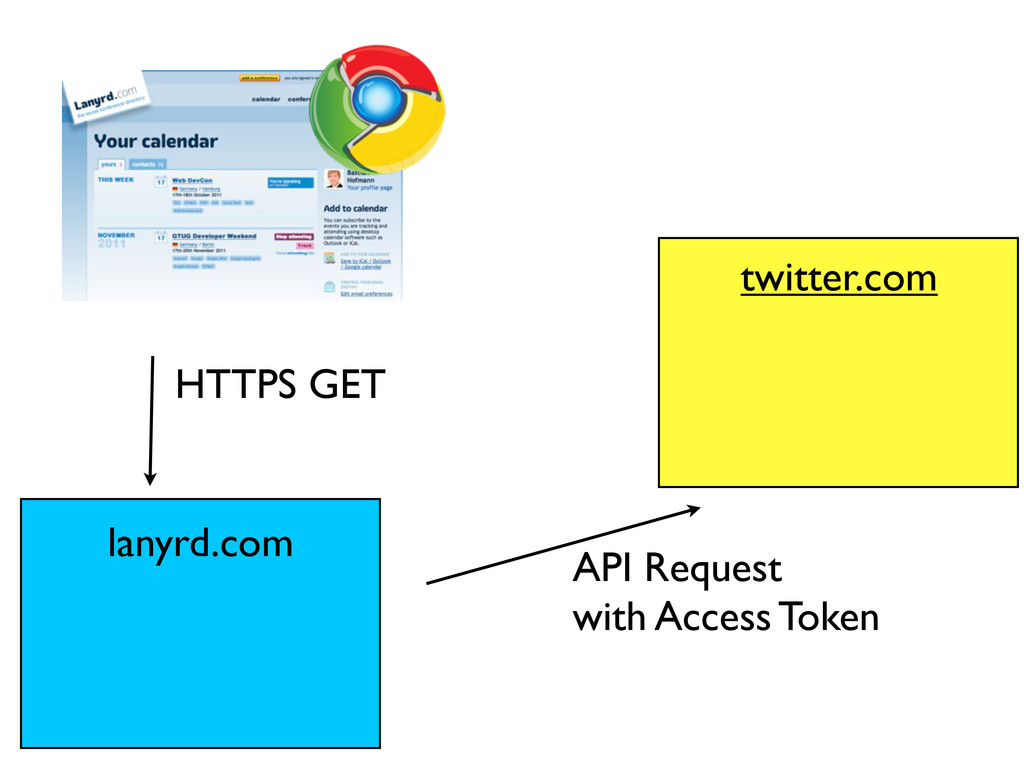
HTTPS GET API Request with Access Token twitter.com lanyrd.com
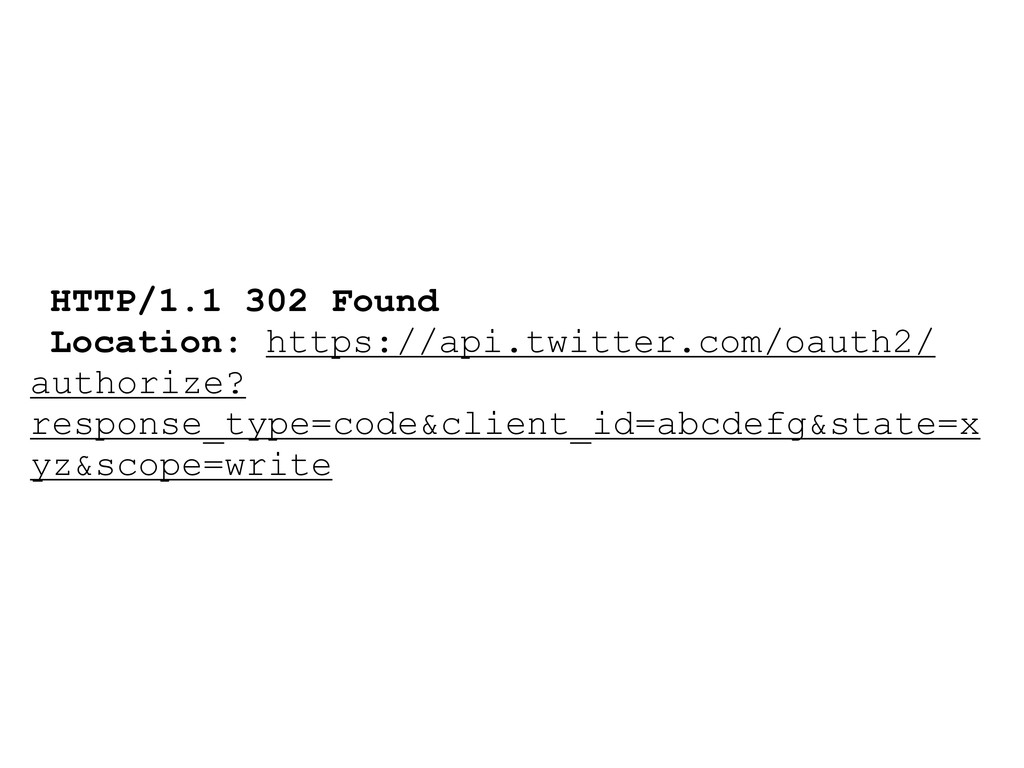
HTTP/1.1 302 Found Location: https://api.twitter.com/oauth2/ authorize? response_type=code&client_id=abcdefg&state=x yz&scope=write
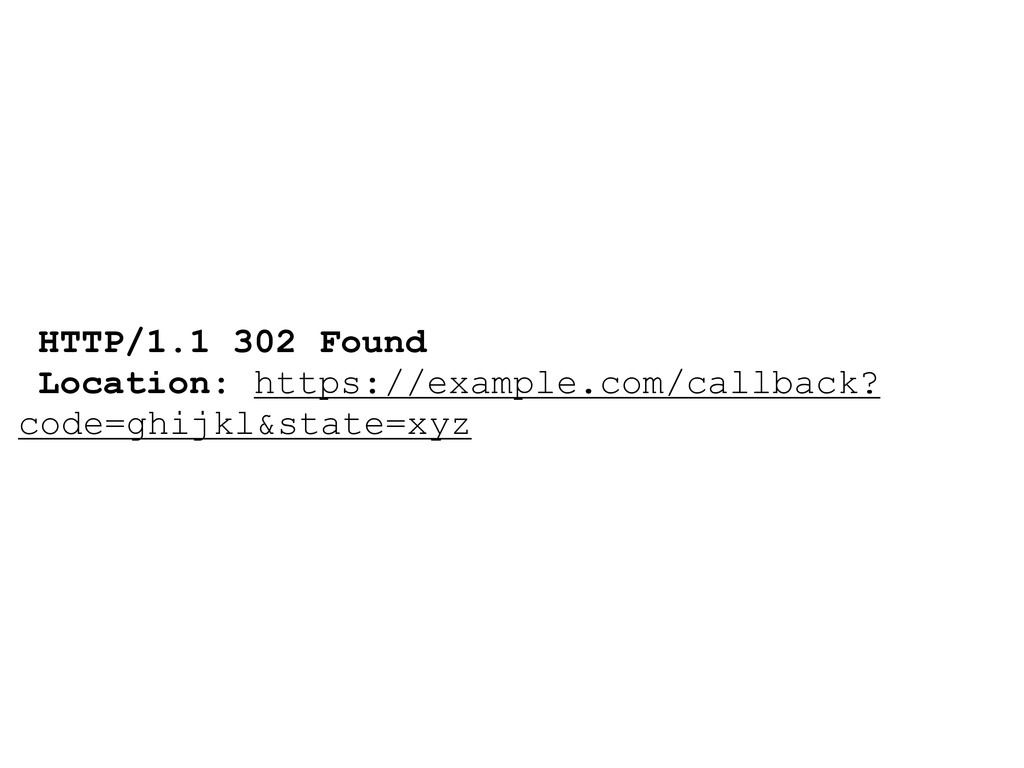
HTTP/1.1 302 Found Location: https://example.com/callback? code=ghijkl&state=xyz
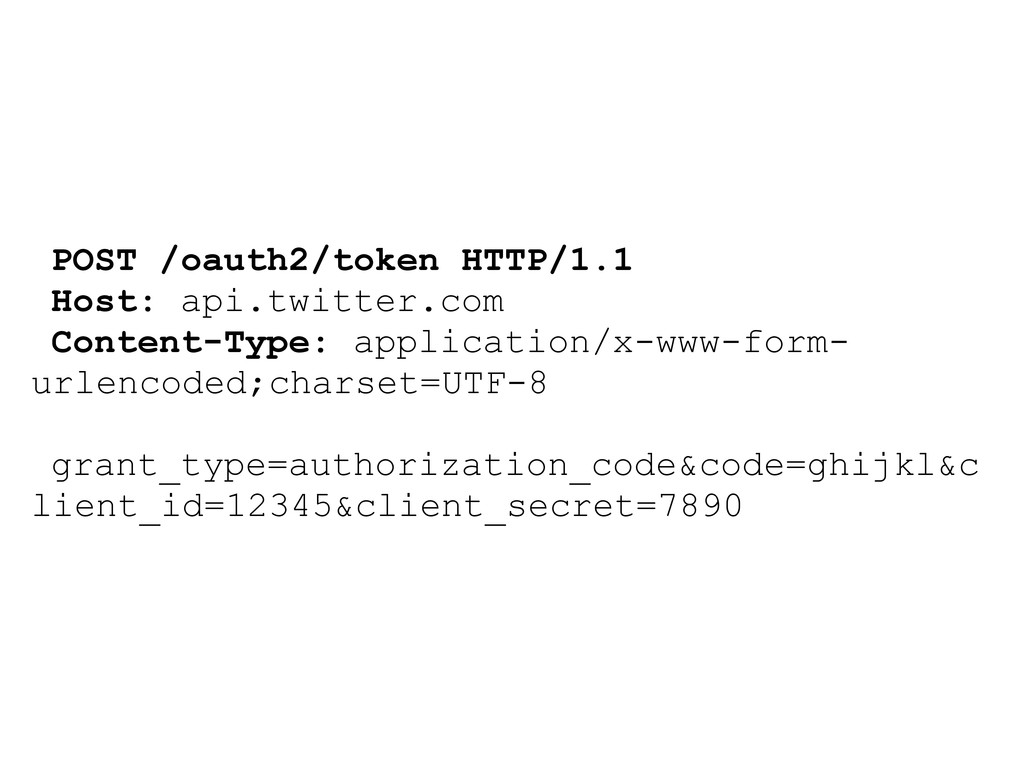
POST /oauth2/token HTTP/1.1 Host: api.twitter.com Content-Type: application/x-www-form- urlencoded;charset=UTF-8 grant_type=authorization_code&code=ghijkl&c lient_id=12345&client_secret=7890
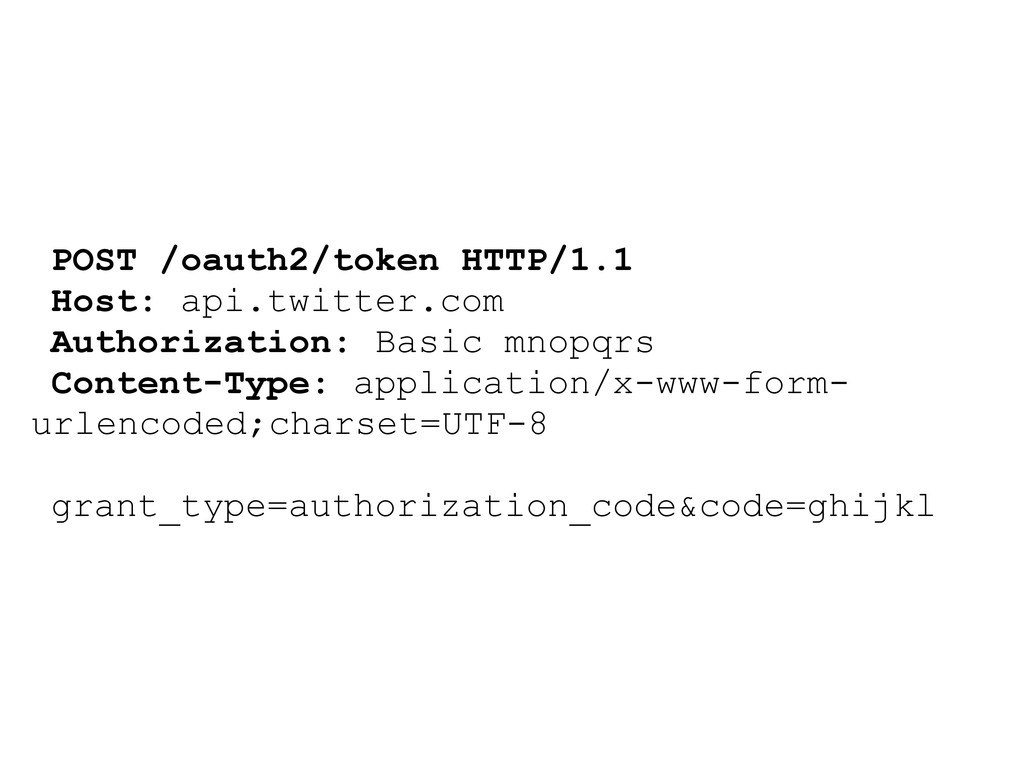
POST /oauth2/token HTTP/1.1 Host: api.twitter.com Authorization: Basic mnopqrs Content-Type: application/x-www-form-
urlencoded;charset=UTF-8 grant_type=authorization_code&code=ghijkl
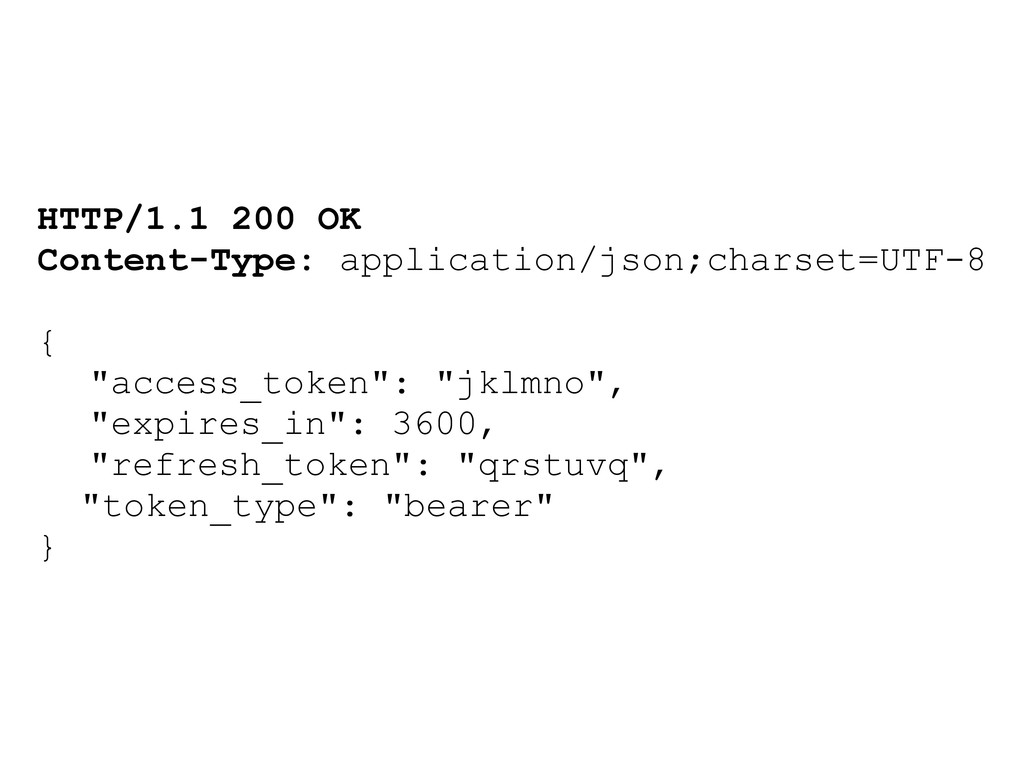
HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 { "access_token": "jklmno", "expires_in": 3600,
"refresh_token": "qrstuvq", "token_type": "bearer" }
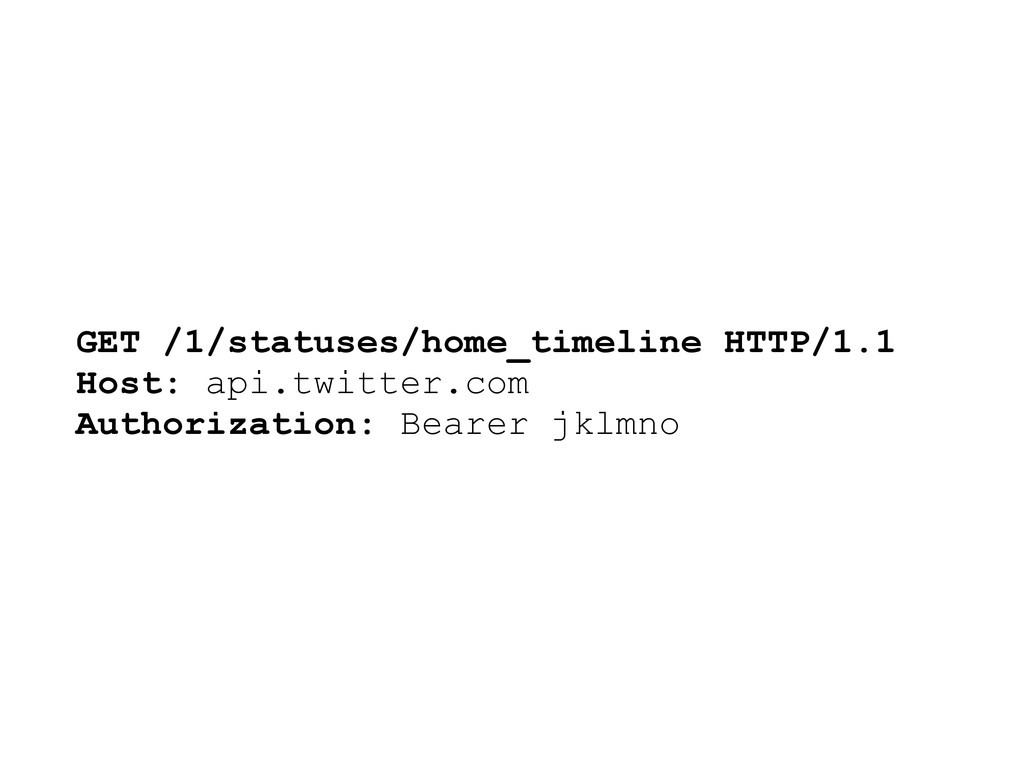
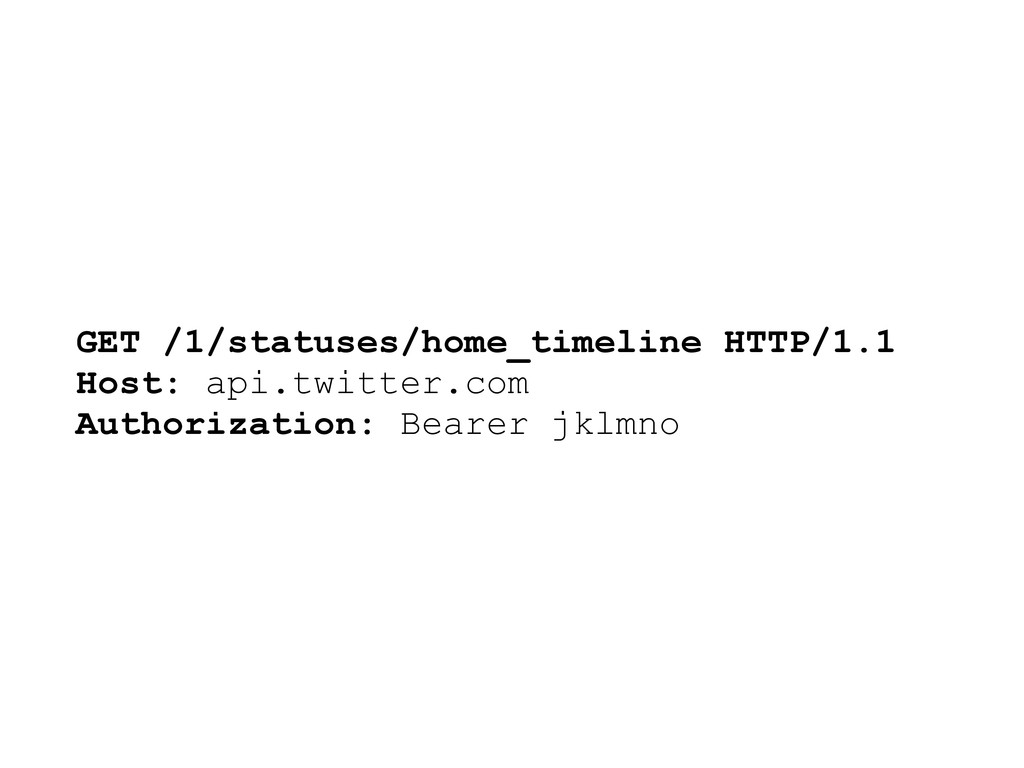
GET /1/statuses/home_timeline HTTP/1.1 Host: api.twitter.com Authorization: Bearer jklmno
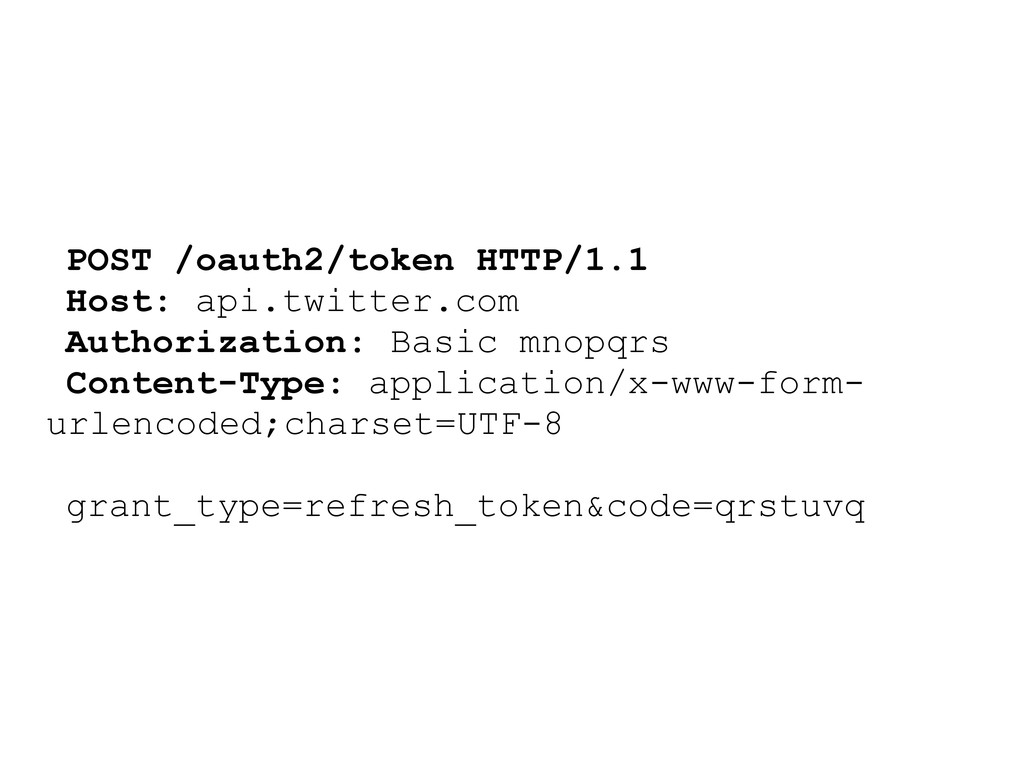
Refresh Token
POST /oauth2/token HTTP/1.1 Host: api.twitter.com Authorization: Basic mnopqrs Content-Type: application/x-www-form-
urlencoded;charset=UTF-8 grant_type=refresh_token&code=qrstuvq
Authorization Types
Bearer Tokens
http://www.rfc-editor.org/rfc/rfc6750.txt
GET /1/statuses/home_timeline HTTP/1.1 Host: api.twitter.com Authorization: Bearer jklmno
SSL not possible?
Signatures
http://tools.ietf.org/html/draft-ietf-oauth-v2-http-mac
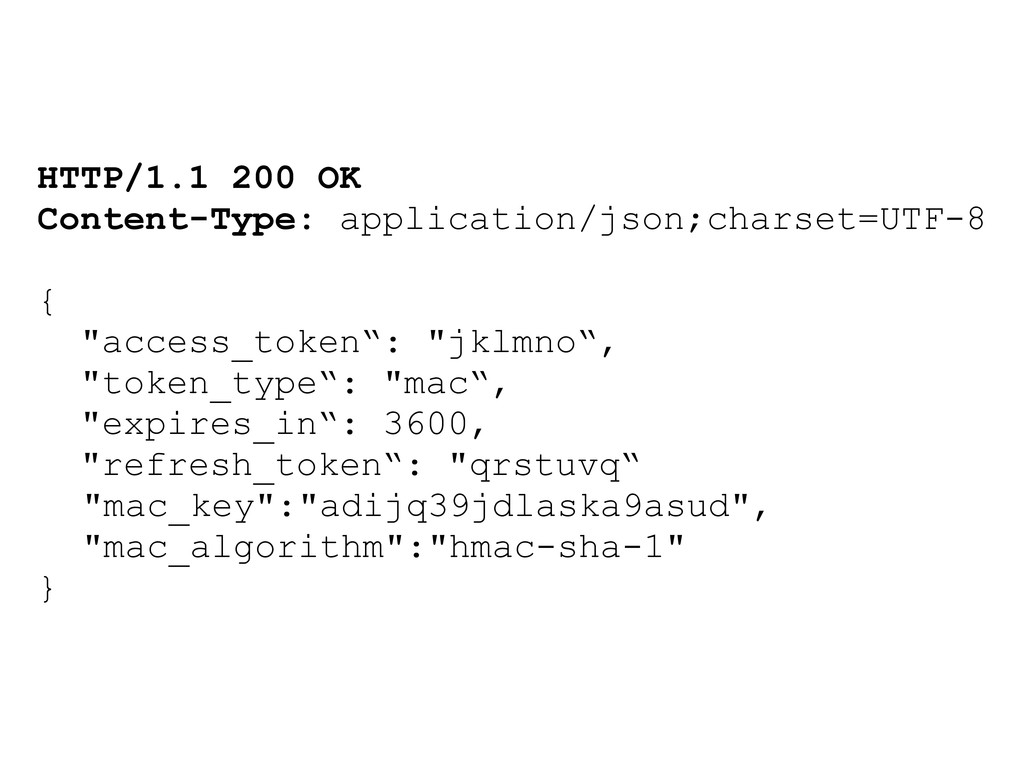
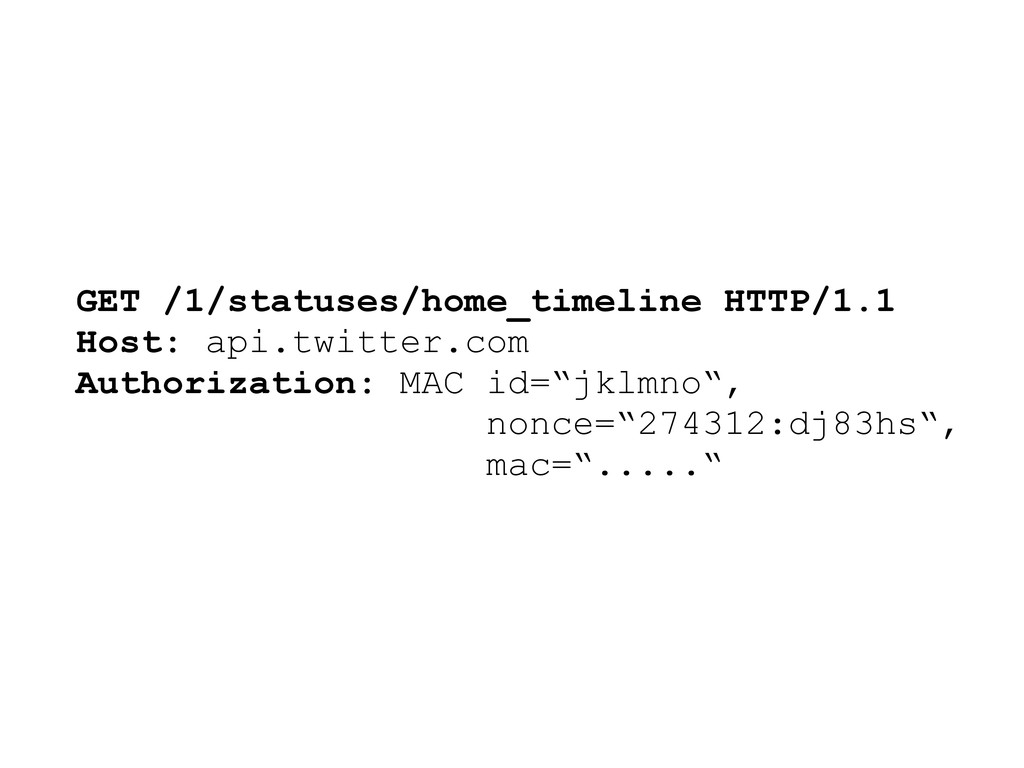
HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 { "access_token“: "jklmno“, "token_type“: "mac“,
"expires_in“: 3600, "refresh_token“: "qrstuvq“ "mac_key":"adijq39jdlaska9asud", "mac_algorithm":"hmac-sha-1" }
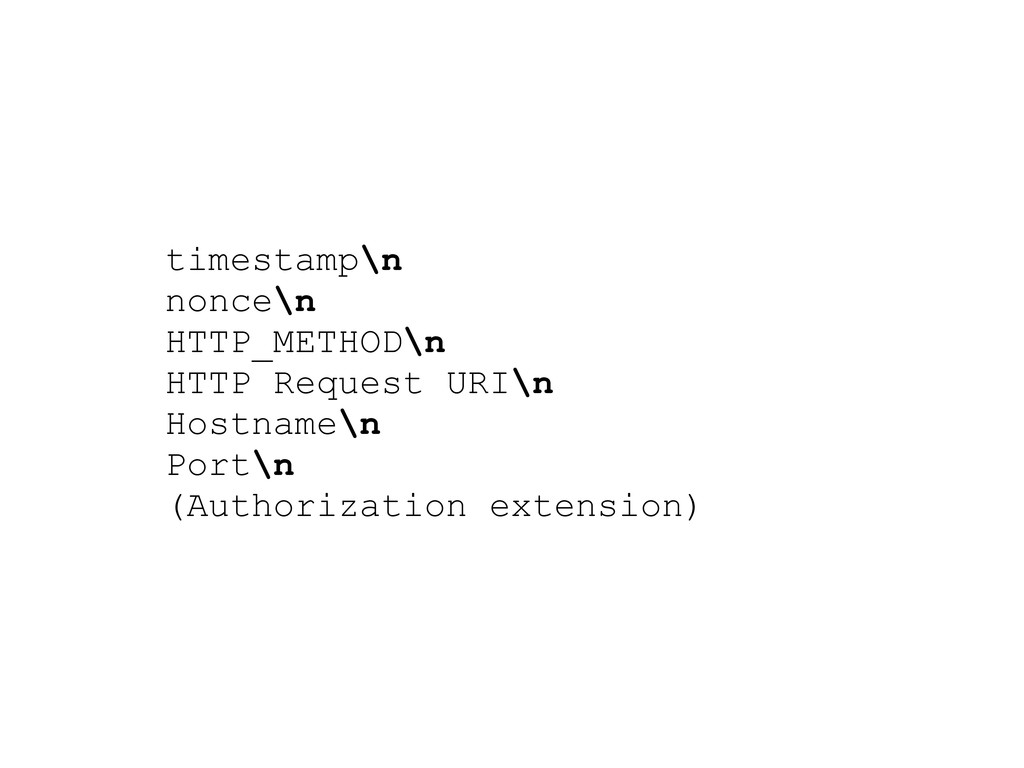
GET /1/statuses/home_timeline HTTP/1.1 Host: api.twitter.com Authorization: MAC id=“jklmno“, nonce=“274312:dj83hs“, mac=“.....“
timestamp\n nonce\n HTTP_METHOD\n HTTP Request URI\n Hostname\n Port\n (Authorization extension)
And JavaScript?
User-Agent Profile
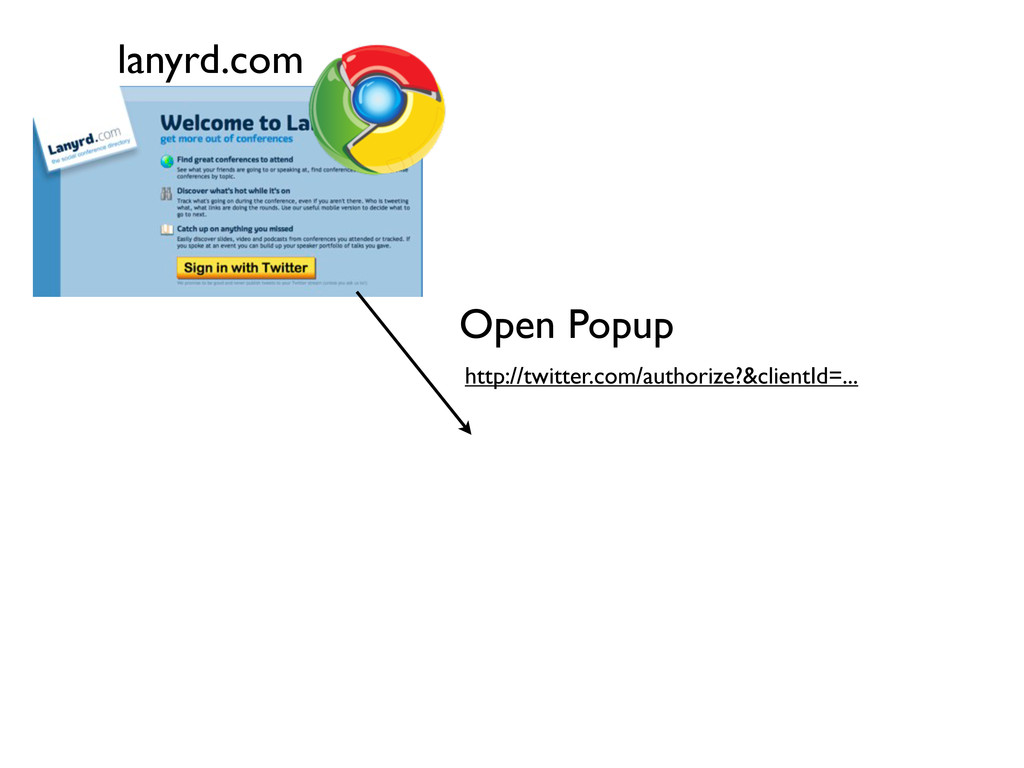
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com
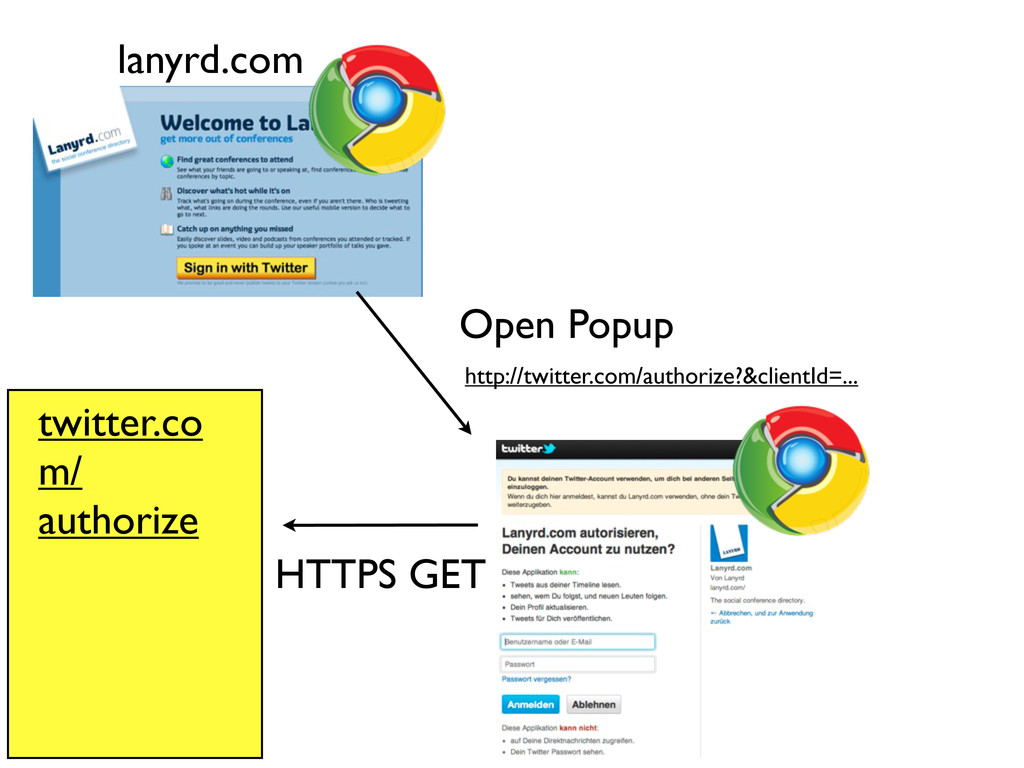
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com HTTPS GET twitter.co m/ authorize
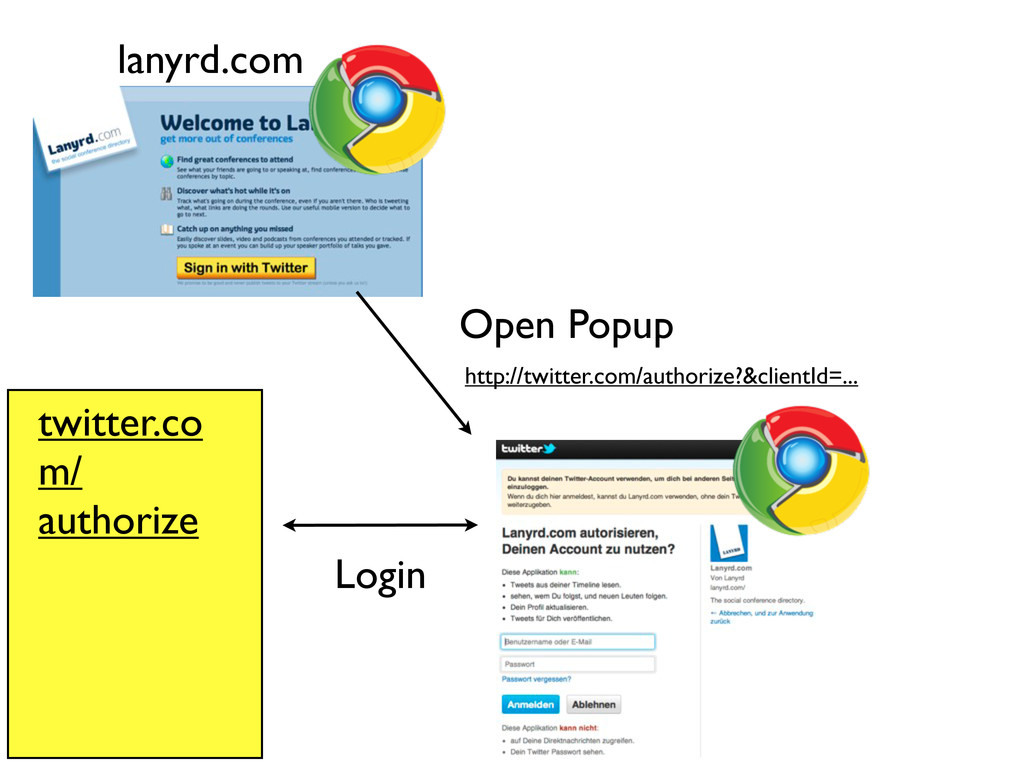
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com Login twitter.co m/ authorize
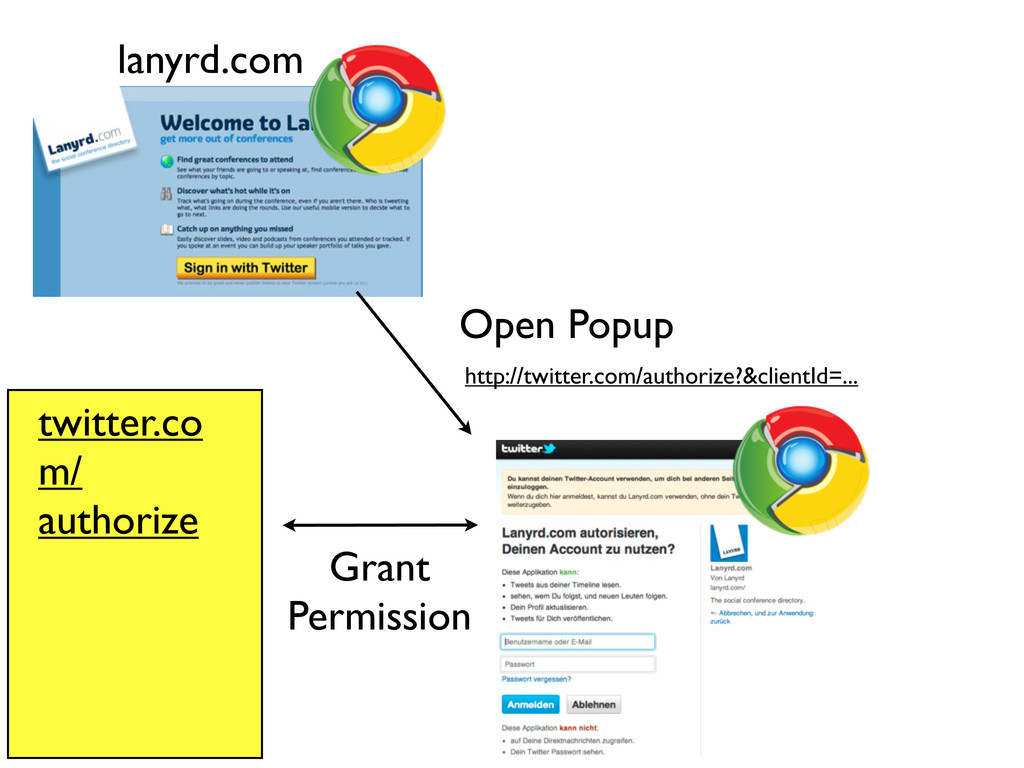
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com Grant Permission twitter.co m/ authorize
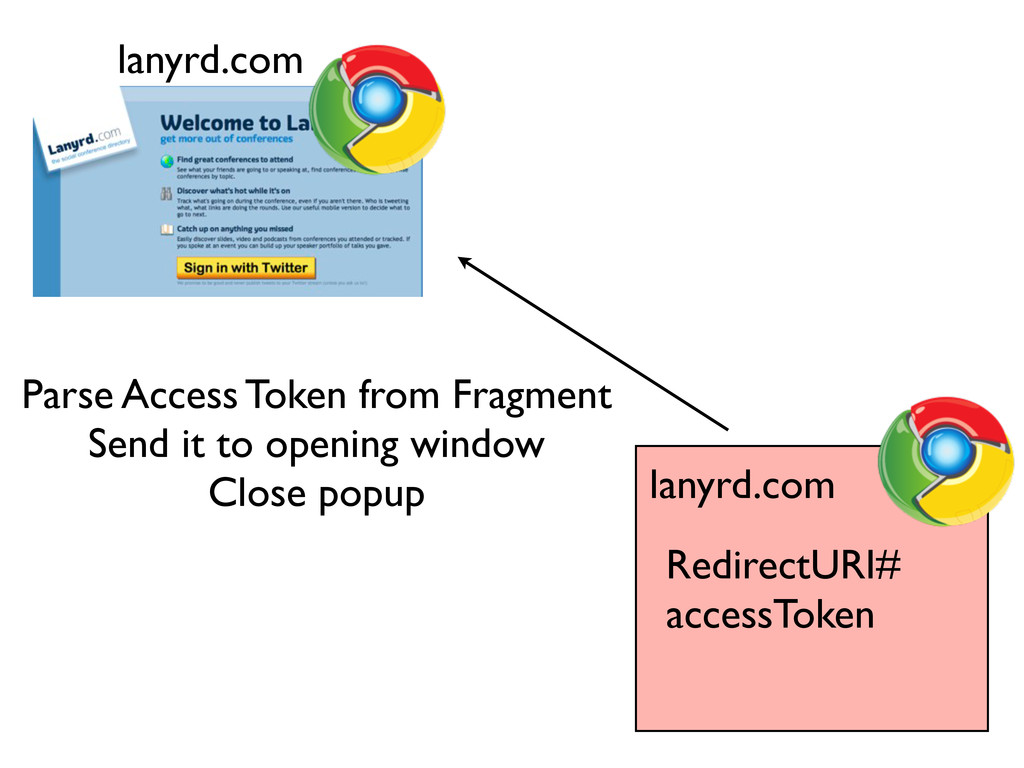
lanyrd.com HTTPS Redirect RedirectURI#acces sToken twitter.co m/ authorize RedirectURI# accessToken
lanyrd.com
lanyrd.com RedirectURI# accessToken Parse Access Token from Fragment Send it
to opening window Close popup lanyrd.com
Same Origin Policy
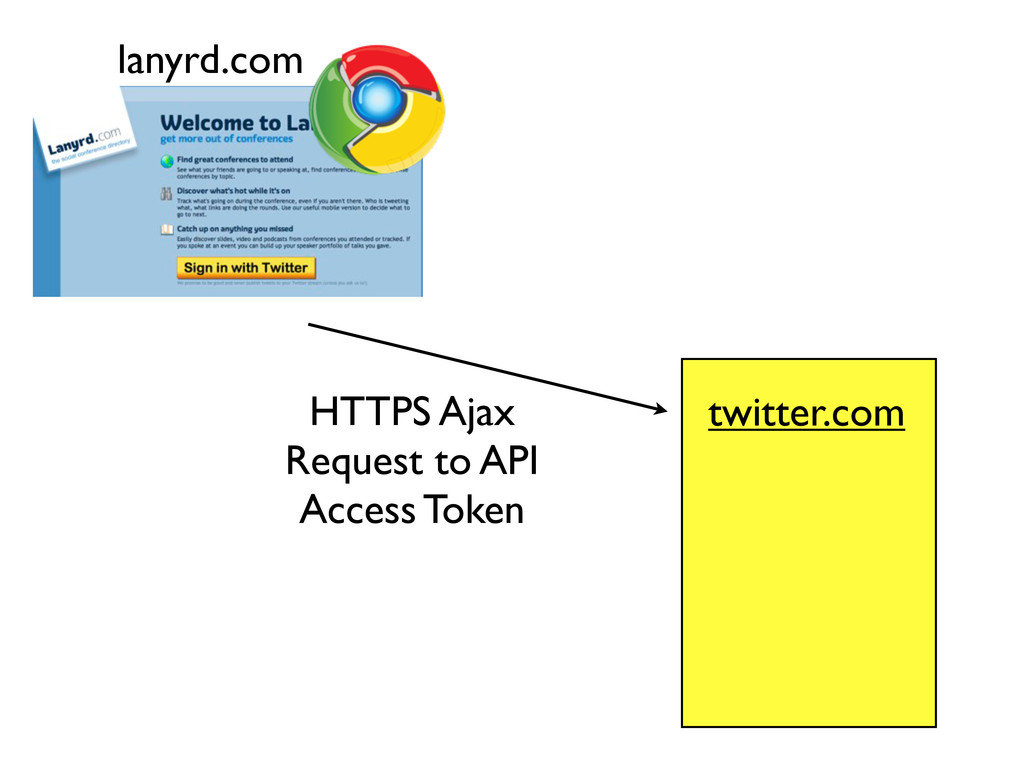
lanyrd.com HTTPS Ajax Request to API Access Token twitter.com
Same Origin Policy
None
JSONP
Cross Origin Request Sharing (CORS)
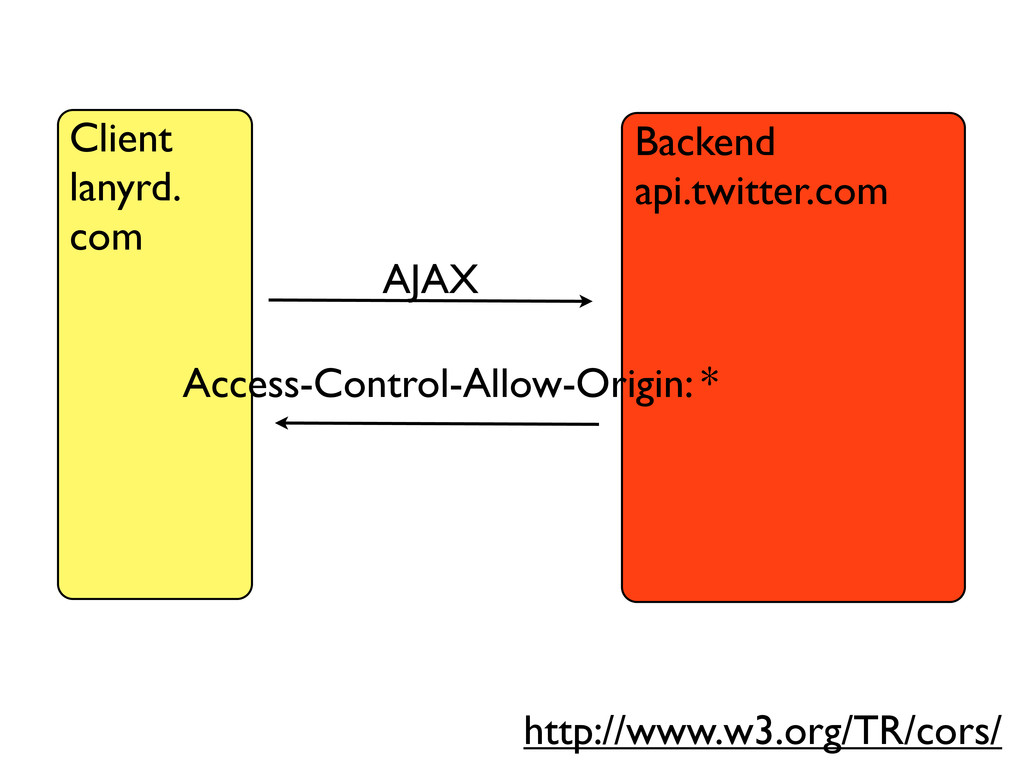
Backend api.twitter.com Client lanyrd. com AJAX Access-Control-Allow-Origin: * http://www.w3.org/TR/cors/
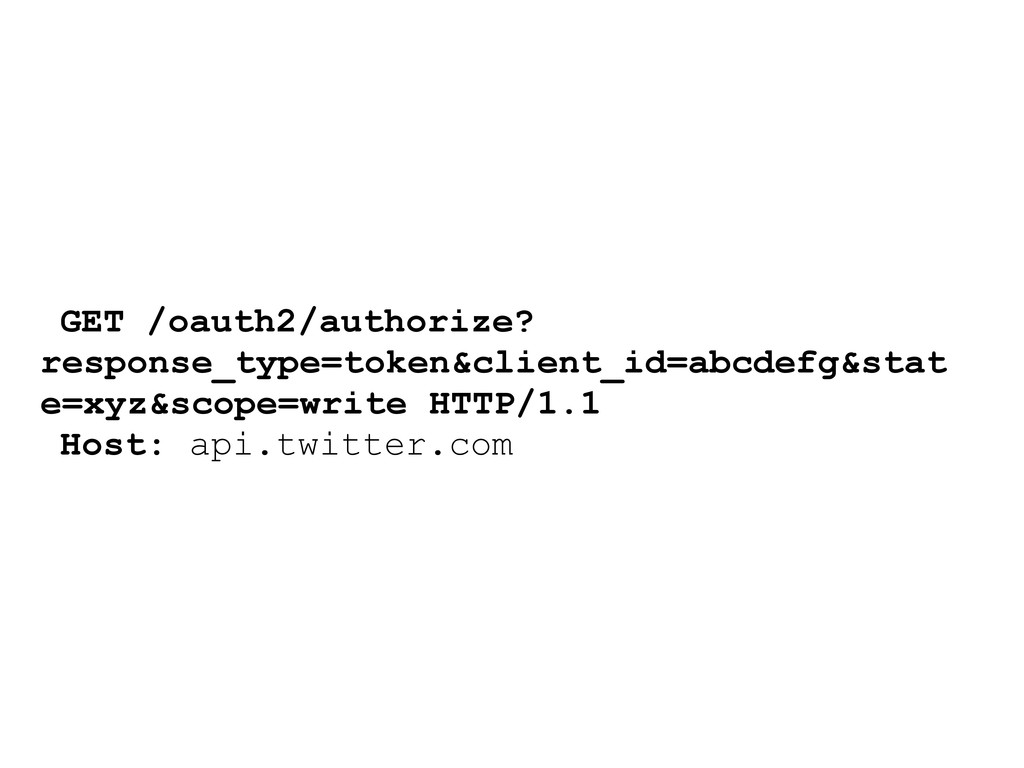
GET /oauth2/authorize? response_type=token&client_id=abcdefg&stat e=xyz&scope=write HTTP/1.1 Host: api.twitter.com
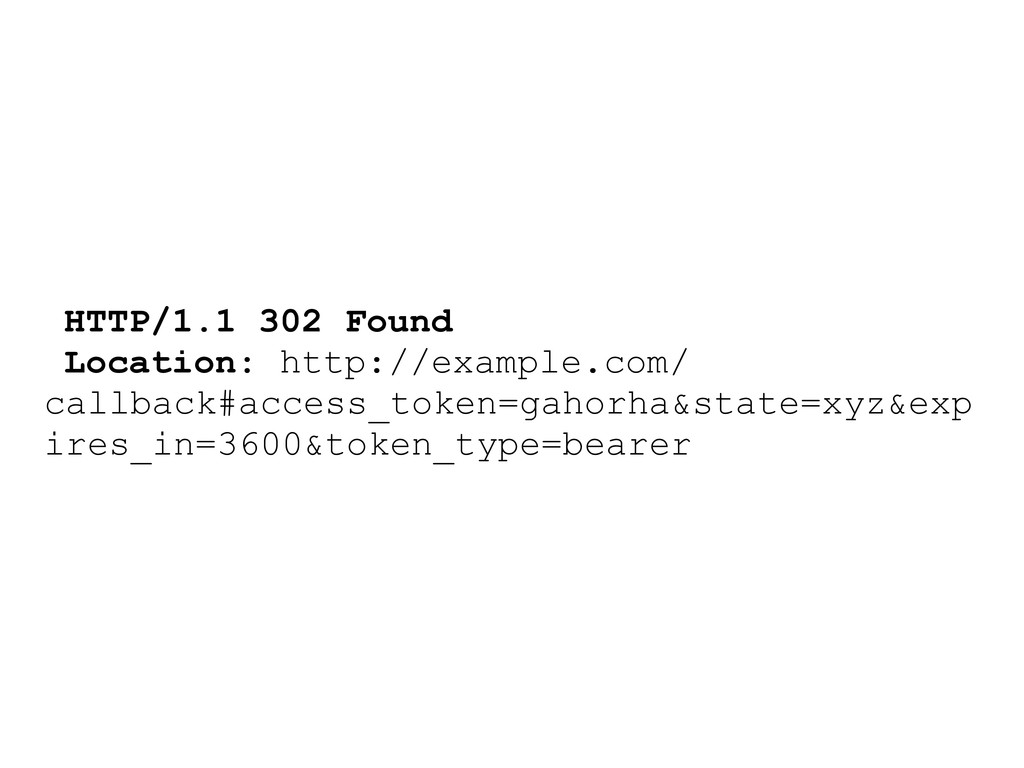
HTTP/1.1 302 Found Location: http://example.com/ callback#access_token=gahorha&state=xyz&exp ires_in=3600&token_type=bearer
1.<script> 2. var fragmentString = location.hash.substr(1); 3. var fragment =
{}; 4. var fragmentItemStrings = fragmentString.split('&'); 5. for (var i in fragmentItemStrings) { 6. var fragmentItem = fragmentItemStrings[i].split('='); 7. if (fragmentItem.length !== 2) { 8. continue; 9. } 10. fragment[fragmentItem[0]] = fragmentItem[1]; 11. } 12. opener.setAccessToken(fragment['access_token']); 13. window.close(); 14.</script>
State
Scopes Optional parameter for provider specific implementations Additional return values
Access Control
http://openidconnect.com/ Scope: „openid“ With access token additional values are returned
UserID: URL to Portable Contacts endpoint Timestamp Signature
Mobile/Desktop
h"p://twi"er.com/Bas2anHofmann h"ps://profiles.google.com/bashofmann h"p://lanyrd.com/people/Bas2anHofmann/ h"p://speakerdeck.com/u/bas2anhofmann
[email protected]
Did you like this talk?
https://joind.in/7360
More Decks by Bastian Hofmann
See All by Bastian Hofmann
Monitoring in Kubernetes with Prometheus and Grafana
bastianhofmann
0
390
Creating a fast Kubernetes Development Workflow
bastianhofmann
0
160
Highly available cross-region deployments with Kubernetes
bastianhofmann
1
190
From source to Kubernetes in 30 minutes
bastianhofmann
0
210
Introduction to Kubernetes
bastianhofmann
1
140
CI/CD with Kubernetes
bastianhofmann
0
260
Creating a fast Kubernetes Development Workflow
bastianhofmann
1
300
Deploying your first Micro-Service application to Kubernetes
bastianhofmann
2
220
Creating a fast Kubernetes Development Workflow
bastianhofmann
0
290
Other Decks in Programming
See All in Programming
例外からRich Errorsまで Kotlinエラーハンドリングの進化を読み解く
shiita0903
0
240
LLM 101
dalinaum
0
520
高橋メソッドでCVE解説シリーズ 〜CVE-2026-112816〜
hakkadaikon
0
270
仕様駆動開発入門 (何を作るかを先に決めて渡す) | 目指せ Kiro マスター 05
inariku
PRO
3
210
複数ドメインを一つのアプリに統合するFlutterの設計と運用_FlutterKaigi2026登壇資料(須永高弘)
takahirosunaga
0
200
疎結合とは何か?ソフトウェア設計における結合バランスについて考える #phpcon_niigata
kajitack
2
400
선언형 햅틱 라이브러리 진동을 소개합니다
l2hyunwoo
1
330
[DroidKnights 2026] Workflow AX: From Auto-Documented Policies to E2E Testing
raeminkang
0
610
小さなアプリを作って公開するまで
onozaty
0
220
protojson における文字化けの扱い
kazuki1023
0
460
Secure Your Coding Agent Like It’s Malware (v1.5) 🇬🇧 @Code.talks 2026
richargh
0
190
Enforcing Your Architecture with Unit Tests in the AI Era (Swift Connection X)
steliosf
PRO
1
190
Featured
See All Featured
A designer walks into a library…
pauljervisheath
211
25k
What does AI have to do with Human Rights?
axbom
PRO
1
2.5k
My Coaching Mixtape
mlcsv
0
390
Mozcon NYC 2025: Stop Losing SEO Traffic
samtorres
1
610
Information Architects: The Missing Link in Design Systems
soysaucechin
1
1.3k
AI Search: Implications for SEO and How to Move Forward - #ShenzhenSEOConference
aleyda
1
1.4k
Pawsitive SEO: Lessons from My Dog (and Many Mistakes) on Thriving as a Consultant in the Age of AI
davidcarrasco
1
310
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
680
HU Berlin: Industrial-Strength Natural Language Processing with spaCy and Prodigy
inesmontani
PRO
0
810
Deep Space Network (abreviated)
tonyrice
0
430
Stewardship and Sustainability of Urban and Community Forests
pwiseman
0
610


 bastianhofmann
 shiita0903
 dalinaum
 hakkadaikon
 inariku
 takahirosunaga
 kajitack
 l2hyunwoo
 raeminkang
 onozaty
 kazuki1023
 richargh
 steliosf
 pauljervisheath
 axbom
 mlcsv
 samtorres
 soysaucechin
 aleyda
 davidcarrasco
 reverentgeek
 inesmontani
 tonyrice
 pwiseman