Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
The face of X-Content-Type-Options which you ma...
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Yu Yagihashi
April 24, 2018
Programming
440
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
The face of X-Content-Type-Options which you may not know
LT向け資料。ざっっっっっっくりなのでまさかりはマジかんべん。 #roppongijs #2
Yu Yagihashi
April 24, 2018
More Decks by Yu Yagihashi
See All by Yu Yagihashi
A Security Engineer in the Web Re-architecture Project
yagihashoo
0
1.2k
A talk about XSS thousand knocks(Shibuya.XSS techtalk#10)
yagihashoo
5
3.2k
katagaitai勉強会#6 EasyなWeb編 / katagaitaiCTF#6 Web
yagihashoo
1
1.3k
Other Decks in Programming
See All in Programming
Secure Your Coding Agent Like It’s Malware (v1.5) 🇬🇧 @Code.talks 2026
richargh
0
110
[JA] Domain Modeling with Vanilla Rails: 「操作」から再考するRailsの設計論
yasaichi
4
1.9k
LLM 101
dalinaum
0
480
Rails初心者がパスキーを実装してみて大変だったこと
ktombow
0
160
Spec-Driven Development - Why Vaadin Is the Perfect Fit
simas
PRO
0
240
[DroidKnights 2026] Workflow AX: From Auto-Documented Policies to E2E Testing
raeminkang
0
560
DroidKnights 2026 Android A2UI Jetpack Compose 기반의 안전한 AI UI 렌더링 - 박제창
itsmedreamwalker
1
220
Optunaを作ったときにやりたかったこと、その後 (2026/10/16, Optuna Meetup #3)
iwiwi
4
1.5k
FactoryBotをやめればRSpecは速くなるのか?
yuta_onishi_97
0
1.7k
学びを記事・スライド・Xへ高速展開する― AI-assisted Learning Loopで回すコンテンツ生成術
ochtum
0
200
ActionController meets Protocol Buffers
sorah
1
800
Enforcing Your Architecture with Unit Tests in the AI Era (Swift Connection X)
steliosf
PRO
1
160
Featured
See All Featured
Product Roadmaps are Hard
iamctodd
55
13k
The Invisible Side of Design
smashingmag
301
52k
Into the Great Unknown - MozCon
thekraken
41
2.8k
Agile Actions for Facilitating Distributed Teams - ADO2019
mkilby
0
340
We Analyzed 250 Million AI Search Results: Here's What I Found
joshbly
2
2.1k
Unlocking the hidden potential of vector embeddings in international SEO
frankvandijk
0
1k
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
Done Done
chrislema
187
17k
Exploring the Power of Turbo Streams & Action Cable | RailsConf2023
kevinliebholz
37
6.7k
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.4k
Leadership Guide Workshop - DevTernity 2021
reverentgeek
1
430
How To Speak Unicorn (iThemes Webinar)
marktimemedia
1
630
Transcript
あなたの知らない(かもしれない) X-Content-Type-Options Yu YAGIHASHI(@yagihashoo) @Roppongi.js#2
None
None
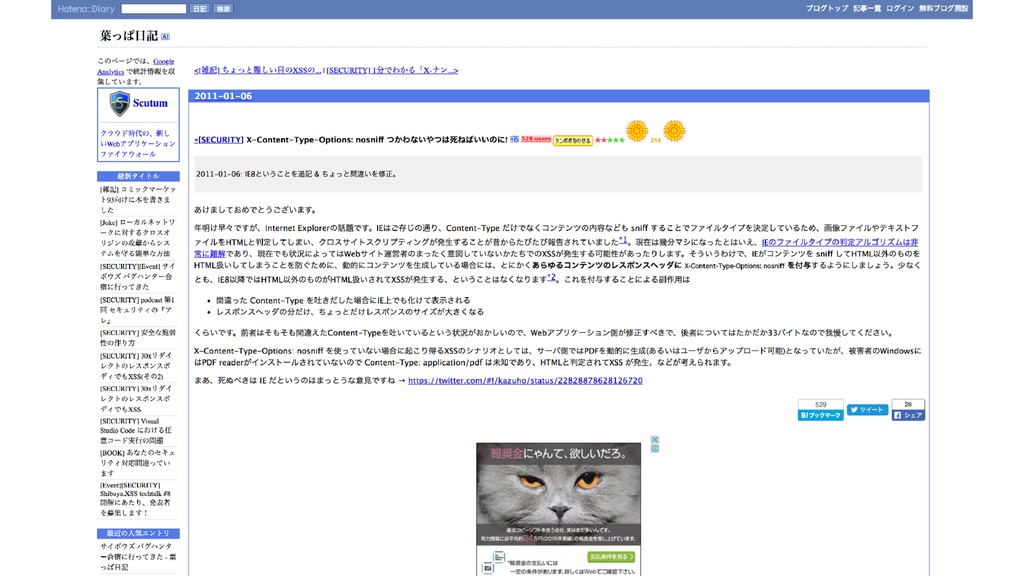
Content Sniffing • Content-Typeヘッダの内容に関係なく、レスポンスボディの内容に 応じてIEがContent-Typeを勝手に判断する機能 →と思っていませんか? • 正確なContent-Typeが設定されていても無視されるのが特に悪質で、 その解決策としてX-Content-Type-Optionsヘッダによるこの機能の 制御・無効化が一般的となった
• 具体的には、HTMLタグを含む画像ファイルを開くとHTMLとして 認識されてしまうことによるXSSなど
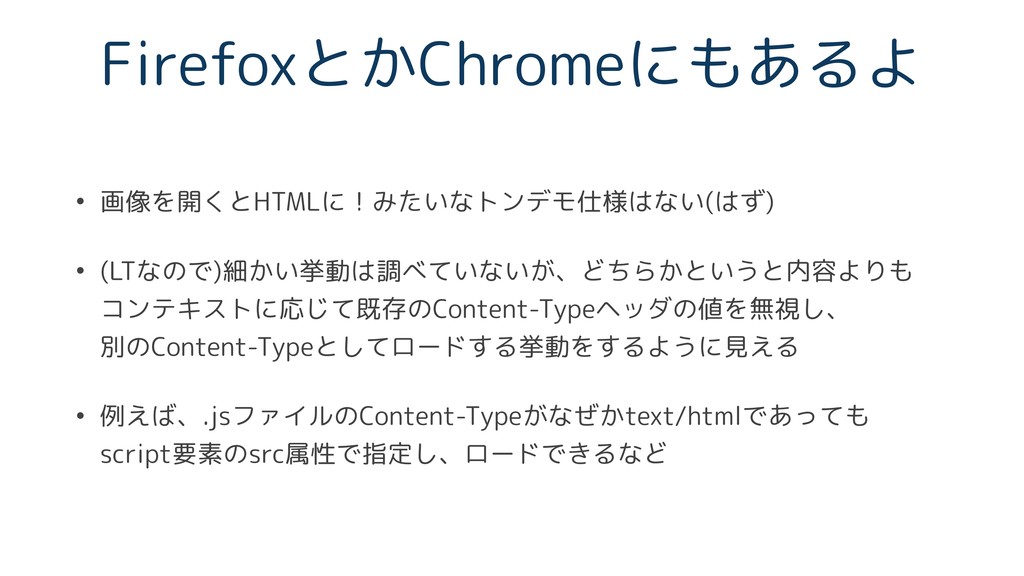
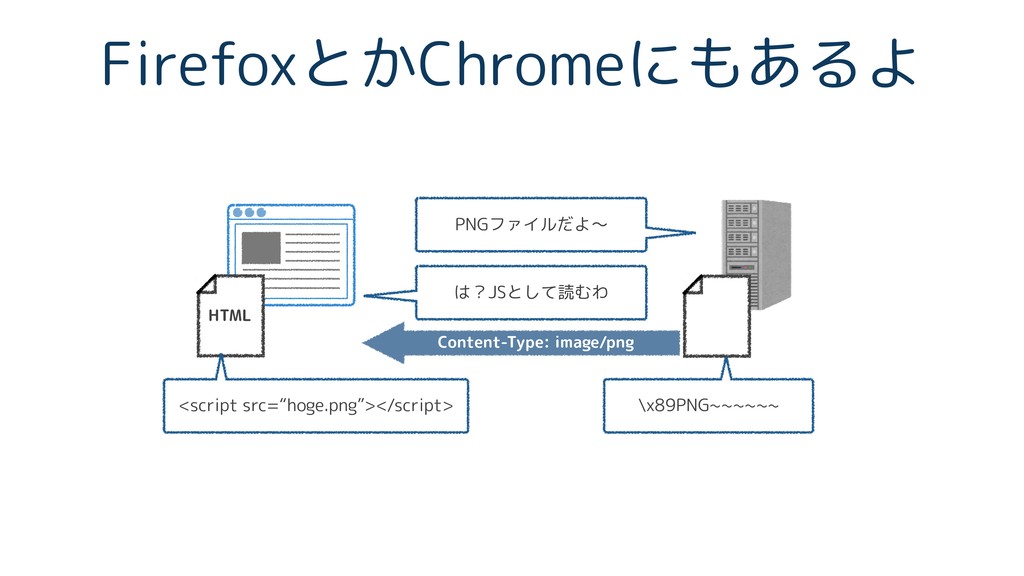
FirefoxとかChromeにもあるよ • 画像を開くとHTMLに!みたいなトンデモ仕様はない(はず) • (LTなので)細かい挙動は調べていないが、どちらかというと内容よりも コンテキストに応じて既存のContent-Typeヘッダの値を無視し、 別のContent-Typeとしてロードする挙動をするように見える • 例えば、.jsファイルのContent-Typeがなぜかtext/htmlであっても script要素のsrc属性で指定し、ロードできるなど
FirefoxとかChromeにもあるよ HTML PNGファイルだよ〜 は?JSとして読むわ <script src=“hoge.png”></script> \x89PNG~~~~~~ Content-Type: image/png
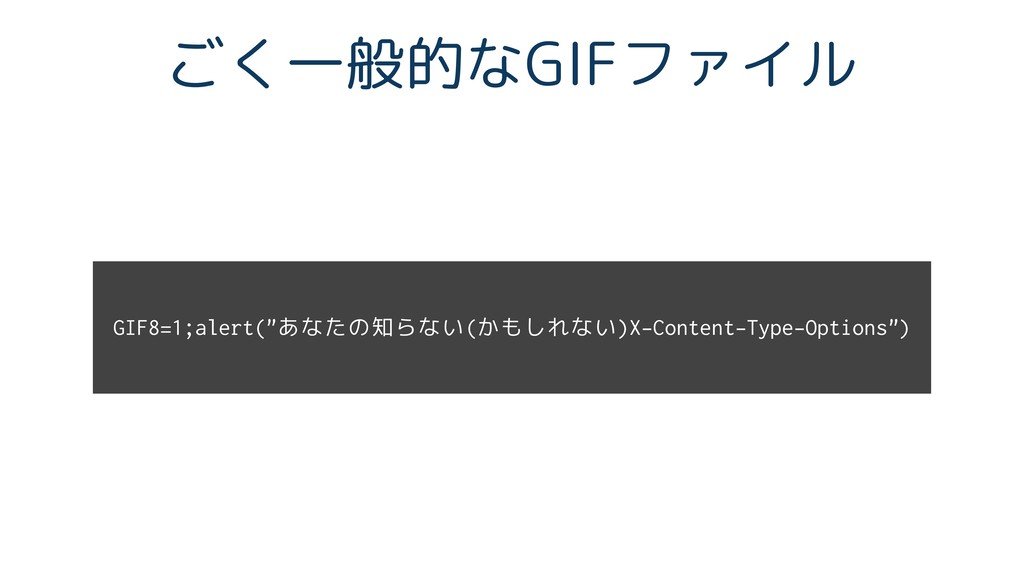
ごく一般的なGIFファイル GIF8=1;alert("あなたの知らない(かもしれない)X-Content-Type-Options")
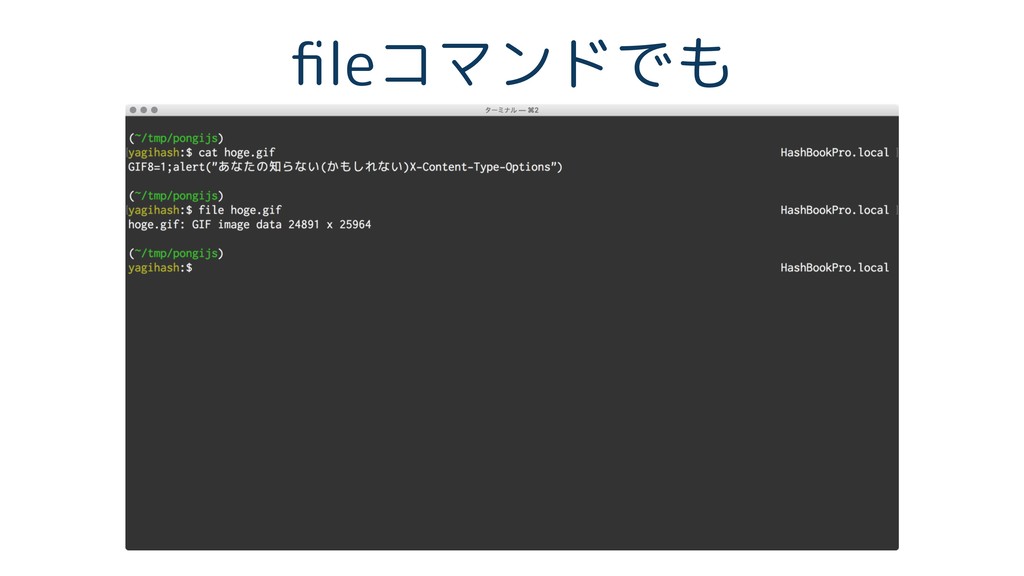
fileコマンドでも
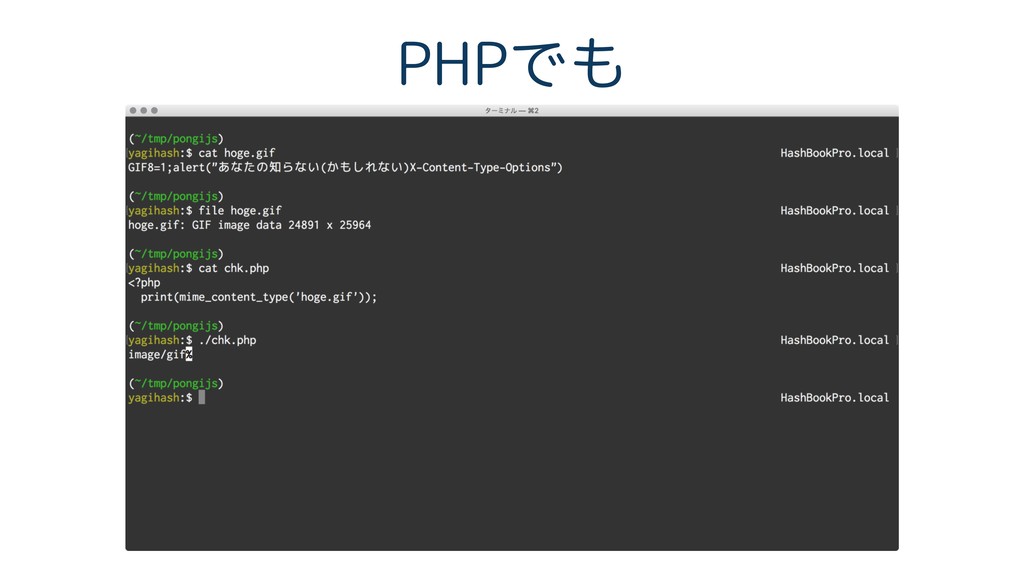
PHPでも
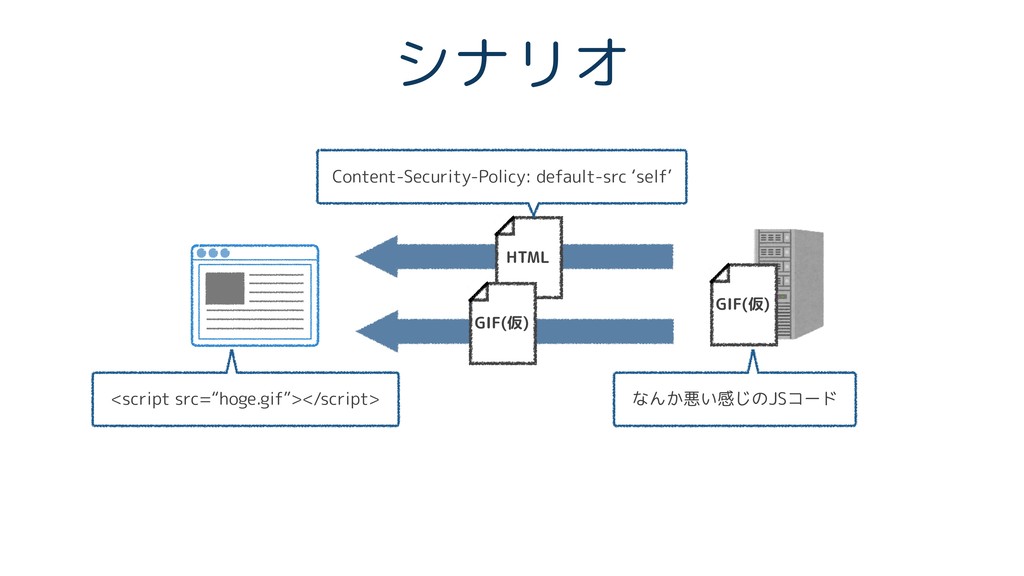
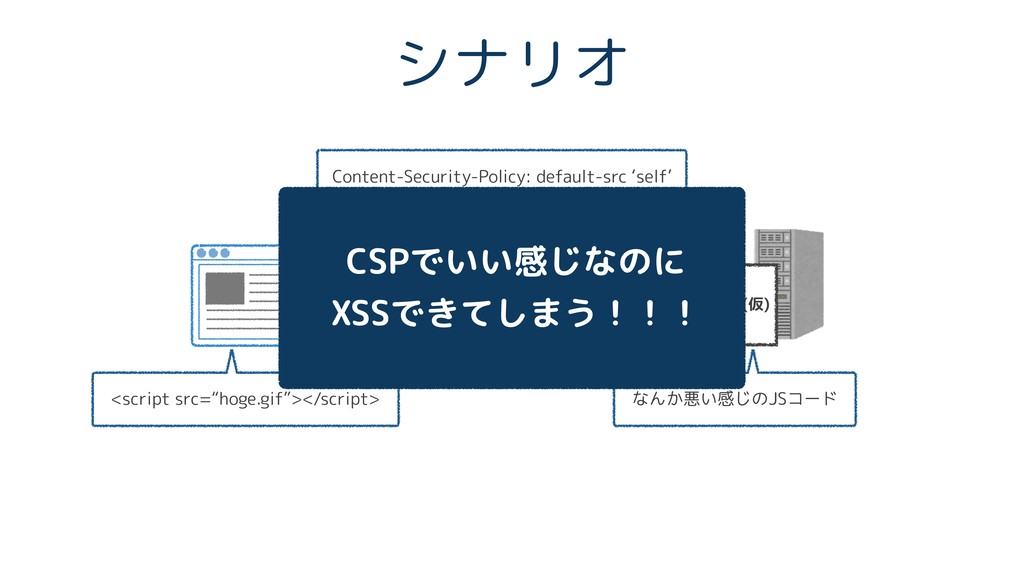
シナリオ HTML Content-Security-Policy: default-src ‘self’ GIF(仮) <script src=“hoge.gif”></script> なんか悪い感じのJSコード GIF(仮)
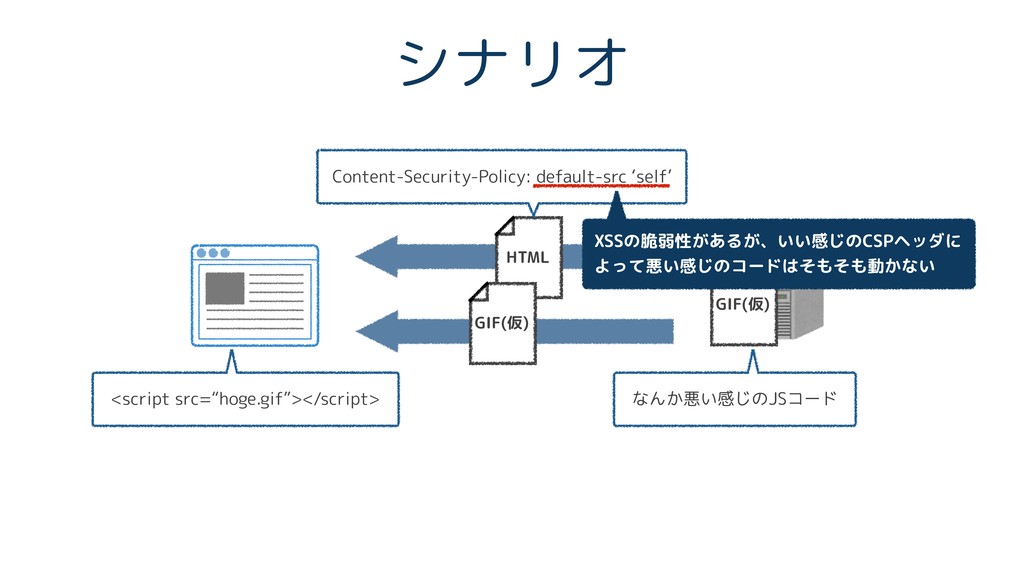
シナリオ HTML Content-Security-Policy: default-src ‘self’ GIF(仮) <script src=“hoge.gif”></script> なんか悪い感じのJSコード GIF(仮)
XSSの脆弱性があるが、いい感じのCSPヘッダに よって悪い感じのコードはそもそも動かない
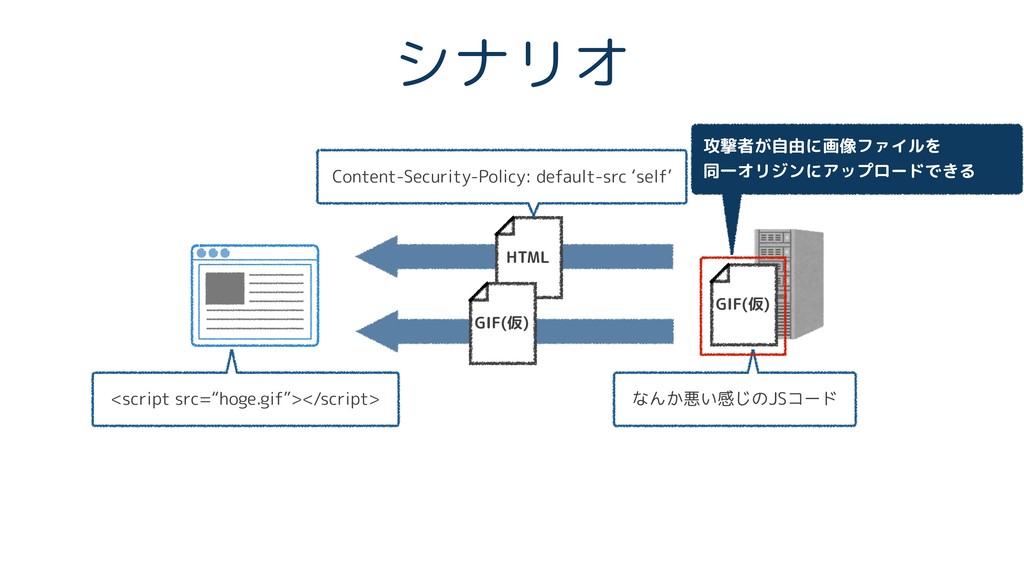
シナリオ HTML Content-Security-Policy: default-src ‘self’ GIF(仮) <script src=“hoge.gif”></script> なんか悪い感じのJSコード GIF(仮)
攻撃者が自由に画像ファイルを 同一オリジンにアップロードできる
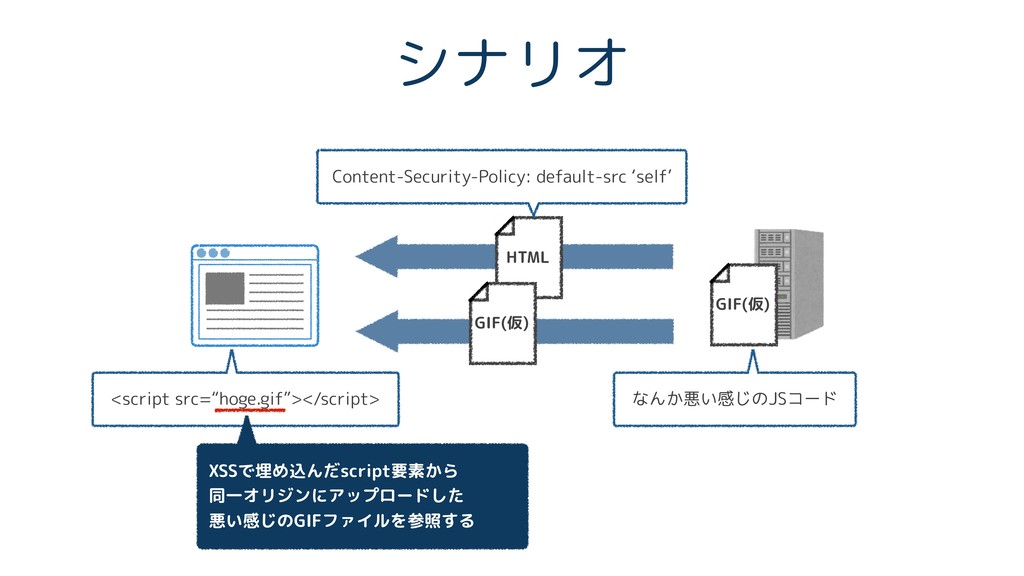
シナリオ HTML Content-Security-Policy: default-src ‘self’ GIF(仮) <script src=“hoge.gif”></script> なんか悪い感じのJSコード GIF(仮)
XSSで埋め込んだscript要素から 同一オリジンにアップロードした 悪い感じのGIFファイルを参照する
シナリオ HTML Content-Security-Policy: default-src ‘self’ GIF(仮) <script src=“hoge.gif”></script> なんか悪い感じのJSコード GIF(仮)
CSPでいい感じなのに XSSできてしまう!!!
さいごに • やることは変わらないです。X-C-T-O: nosniff、ちゃんと付けましょう。


 yagihashoo
 richargh
 yasaichi
 dalinaum
 ktombow
 simas
 raeminkang
 itsmedreamwalker
 iwiwi
 yuta_onishi_97
 ochtum
 sorah
 steliosf
 iamctodd
 smashingmag
 thekraken
 mkilby
 joshbly
 frankvandijk
 danielanewman
 chrislema
 kevinliebholz
 tomoyanonymous
 reverentgeek
 marktimemedia