Share
Embed
Trust Is the Architecture: Global Serverless at Scale
Daniele Frasca
September 15, 2026
Transcript
29 slides
-
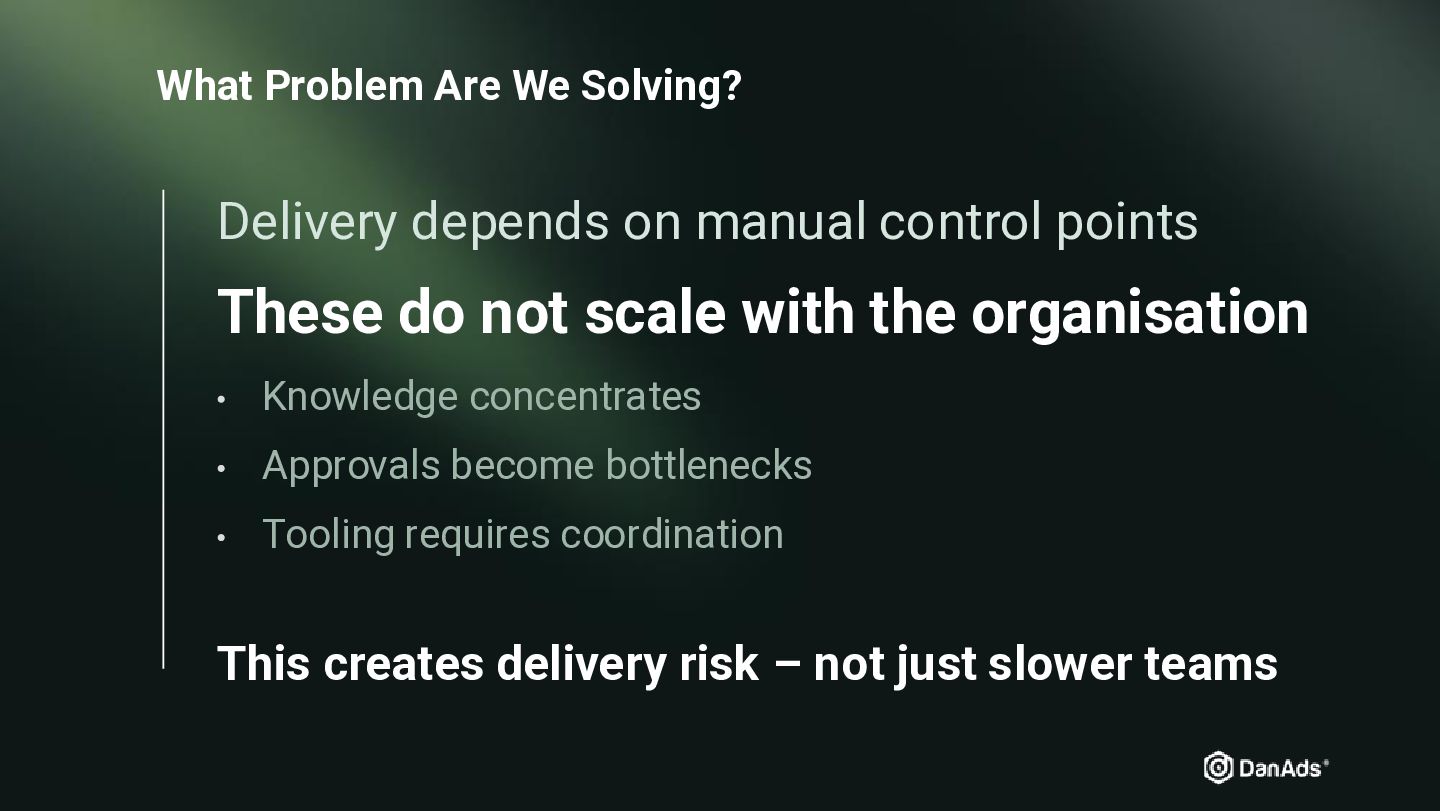
What Problem Are We Solving? Delivery depends on manual control
points These do not scale with the organisation Knowledge concentrates Approvals become bottlenecks Tooling requires coordination This creates delivery risk – not just slower teams -
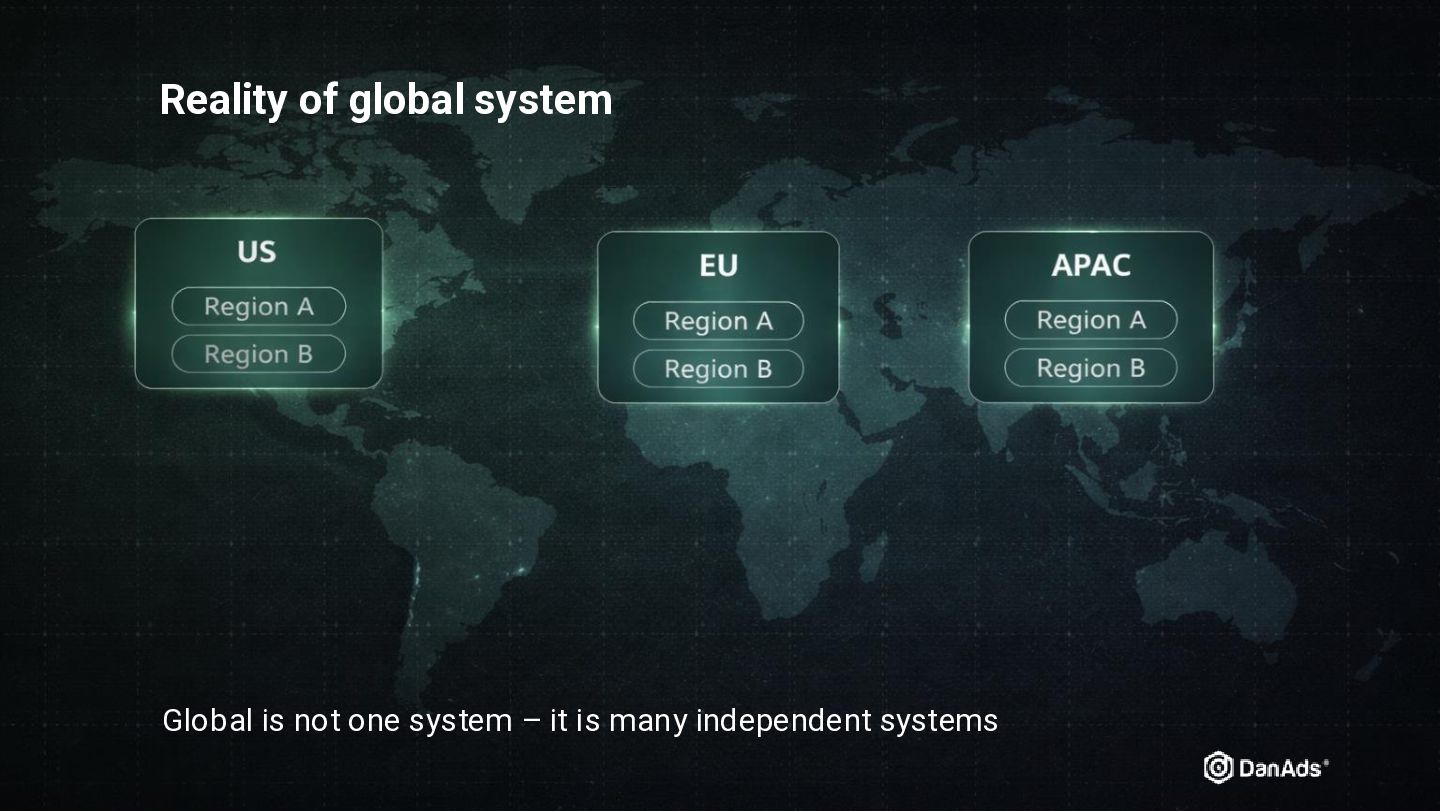
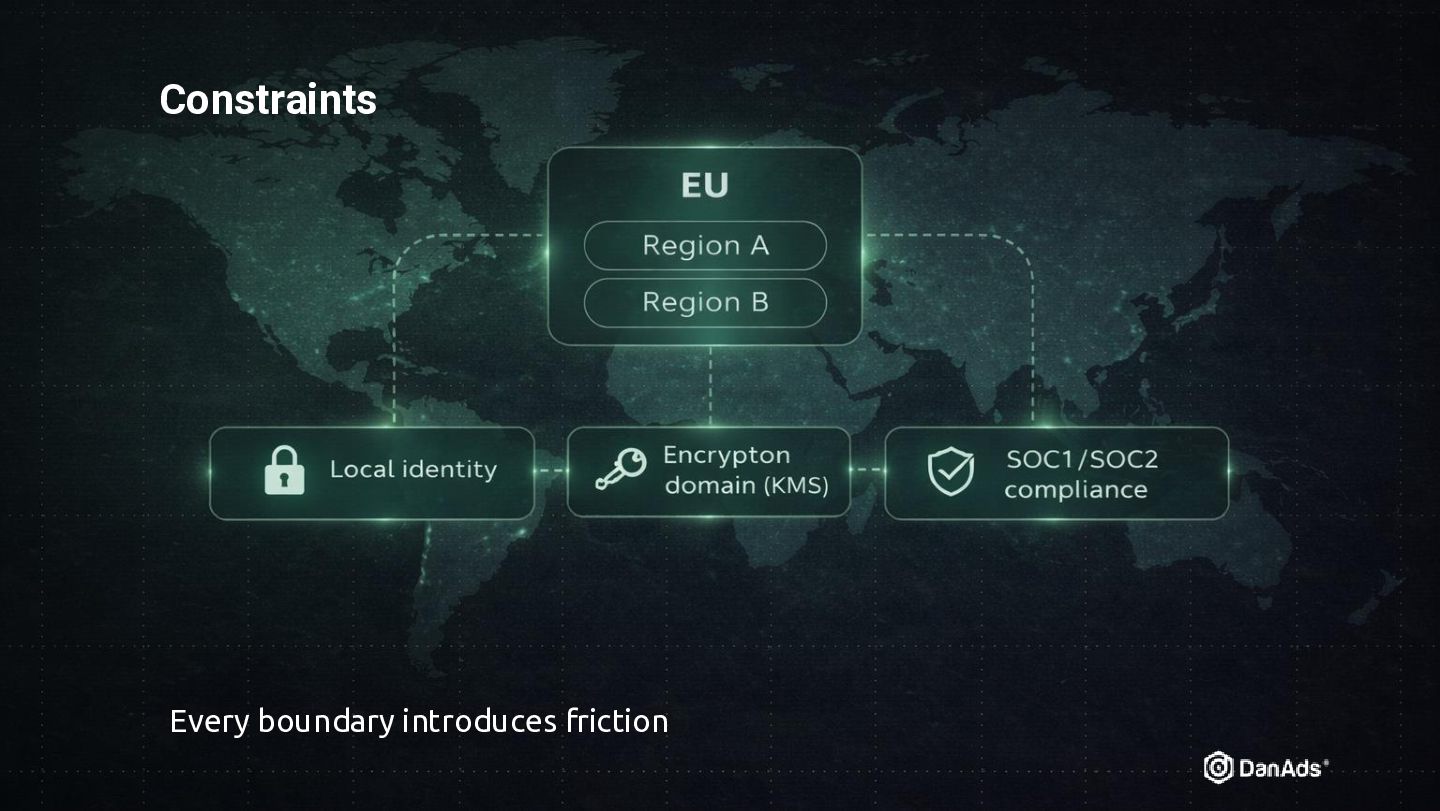
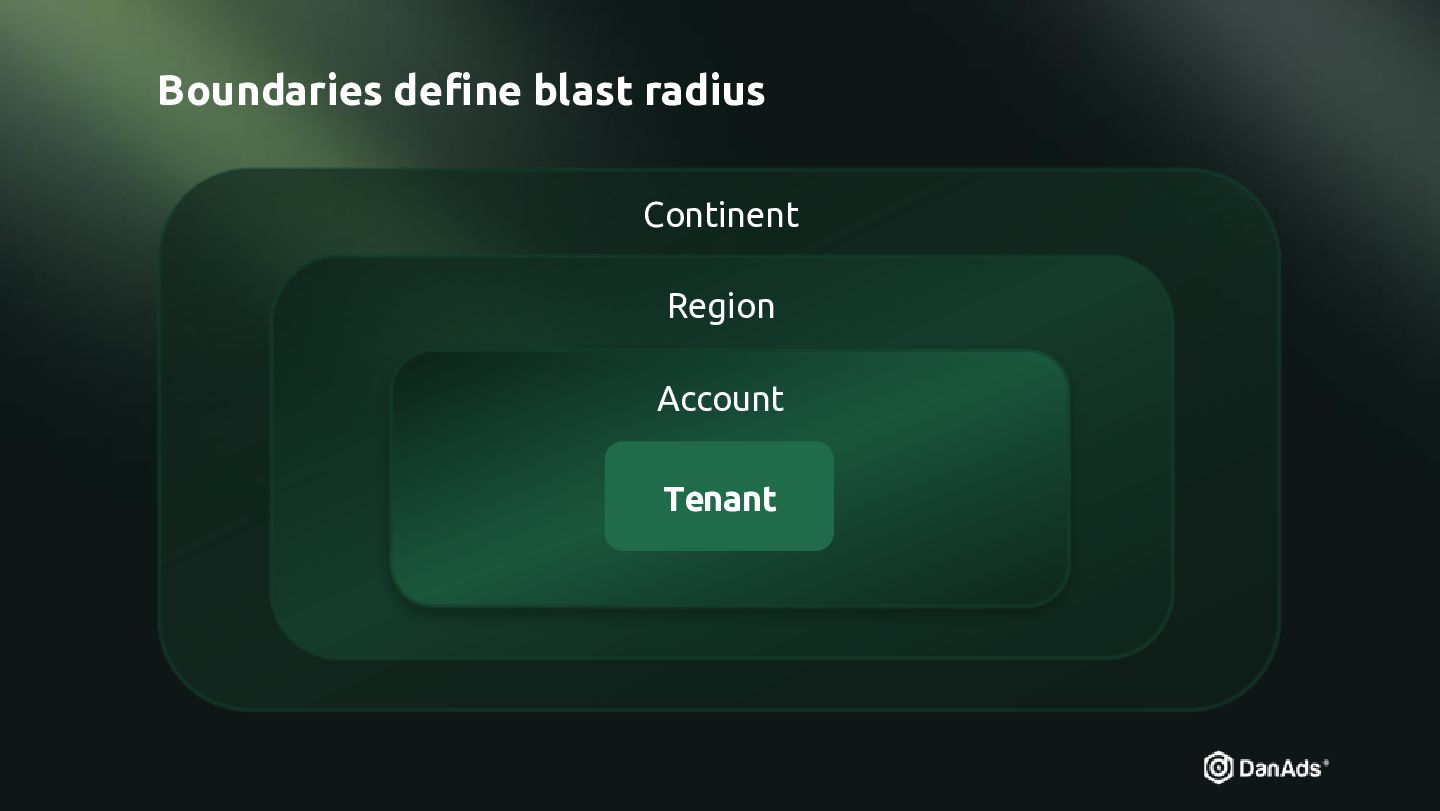
Reality of global system Global is not one system –
it is many independent systems -
What actually breaks → Boundaries → Ownership → Assumptions Complexity
is not technical – it’s systemic -
At scale, the bottleneck changes Speed | Scale TRUST Trust
is what allows speed to survive scale -
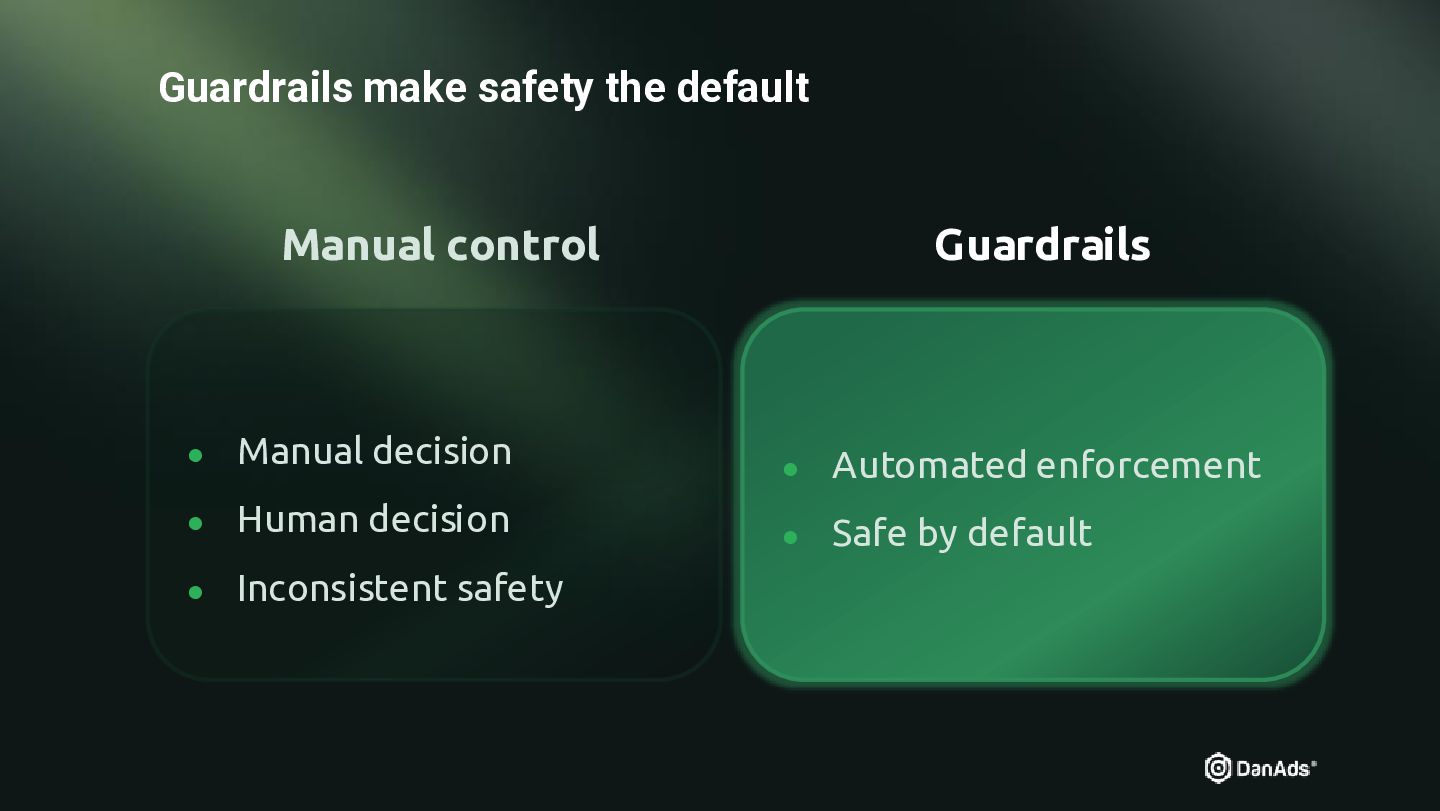
Guardrails make safety the default Manual control Guardrails • Manual
decision • Automated enforcement • Human decision • Safe by default • Inconsistent safety -
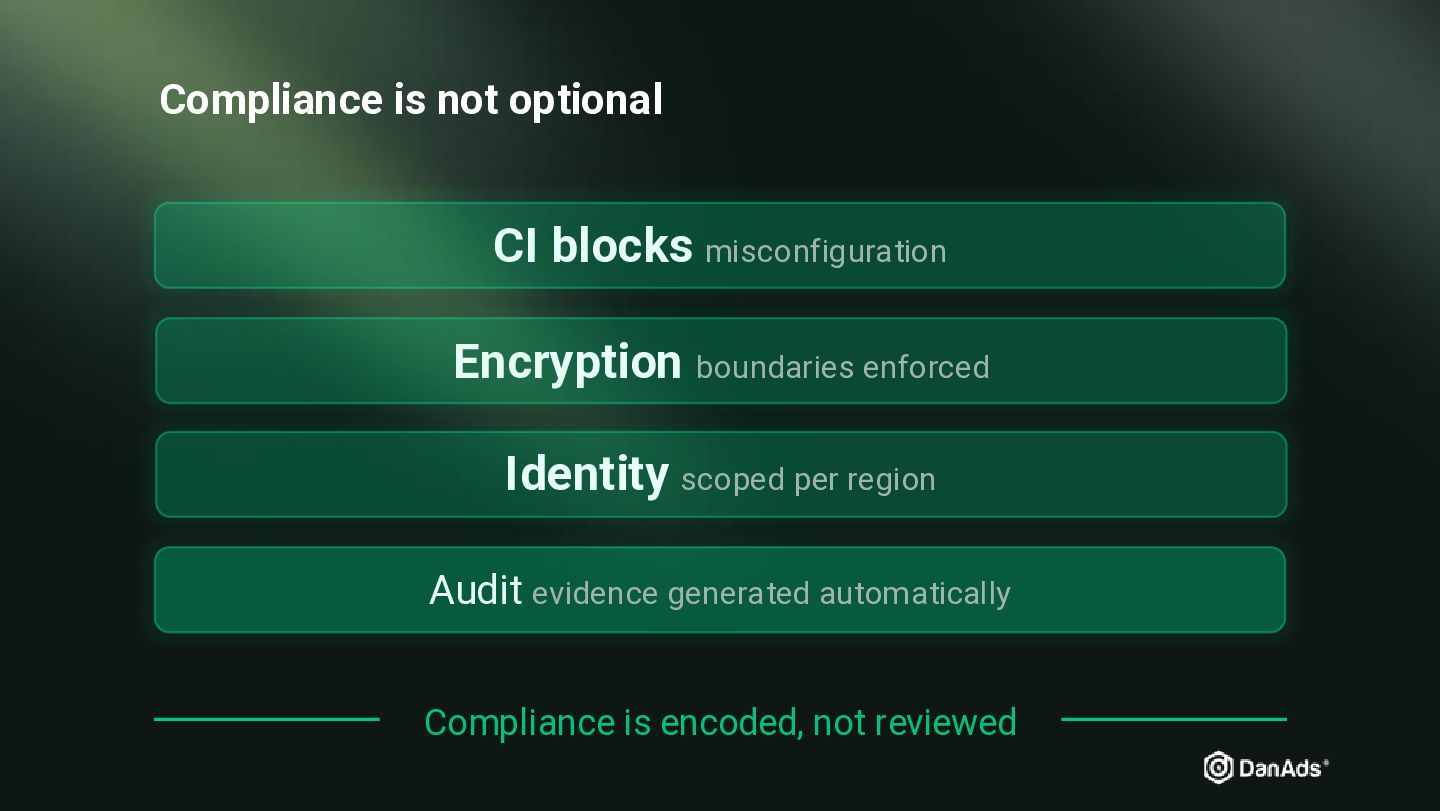
Compliance is not optional CI blocks misconfiguration Encryption boundaries enforced
Identity scoped per region Audit evidence generated automatically Compliance is encoded, not reviewed -
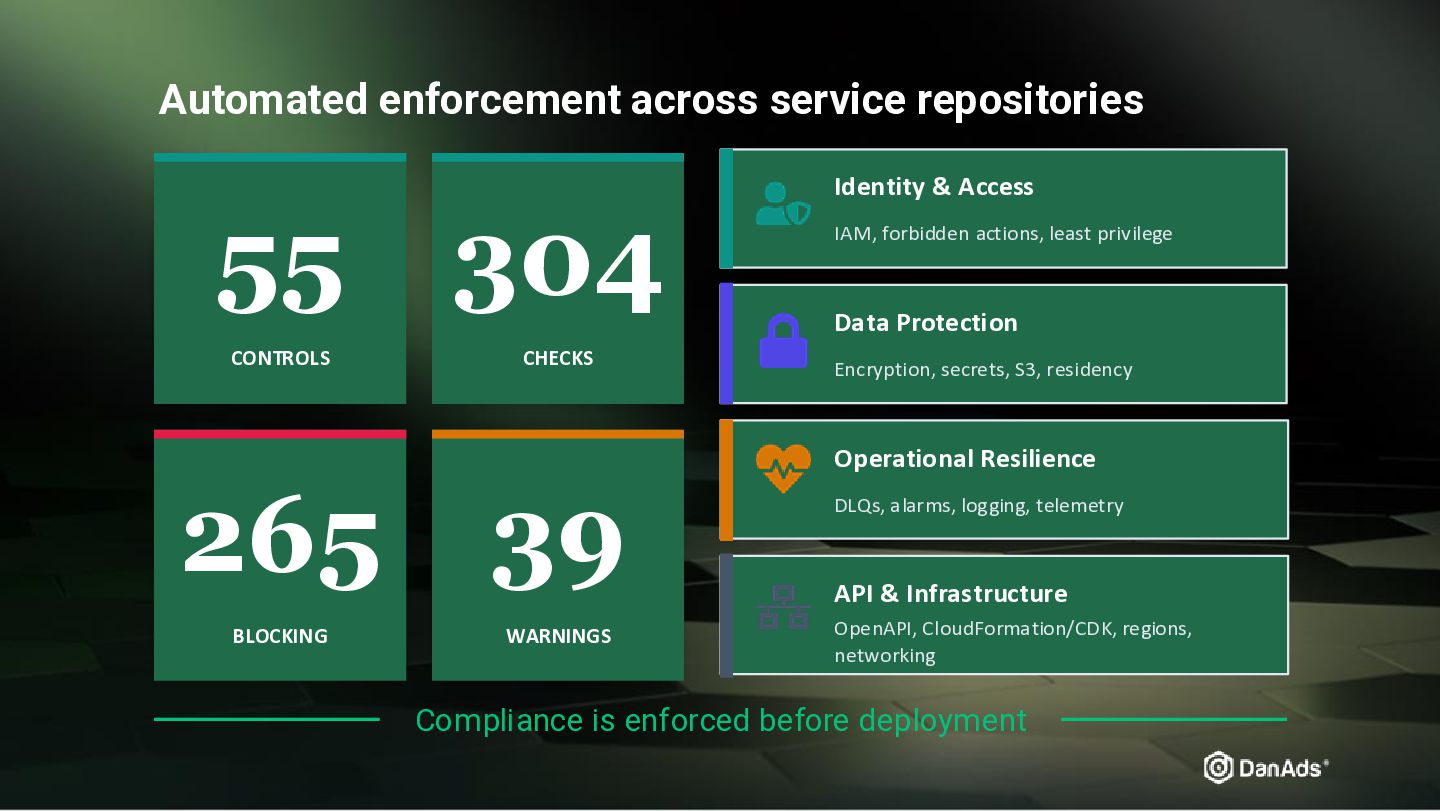
Automated enforcement across service repositories 55 304 CONTROLS CHECKS 265
39 BLOCKING WARNINGS Identity & Access IAM, forbidden actions, least privilege Data Protection Encryption, secrets, S3, residency Operational Resilience DLQs, alarms, logging, telemetry API & Infrastructure OpenAPI, CloudFormation/CDK, regions, networking Compliance is enforced before deployment -
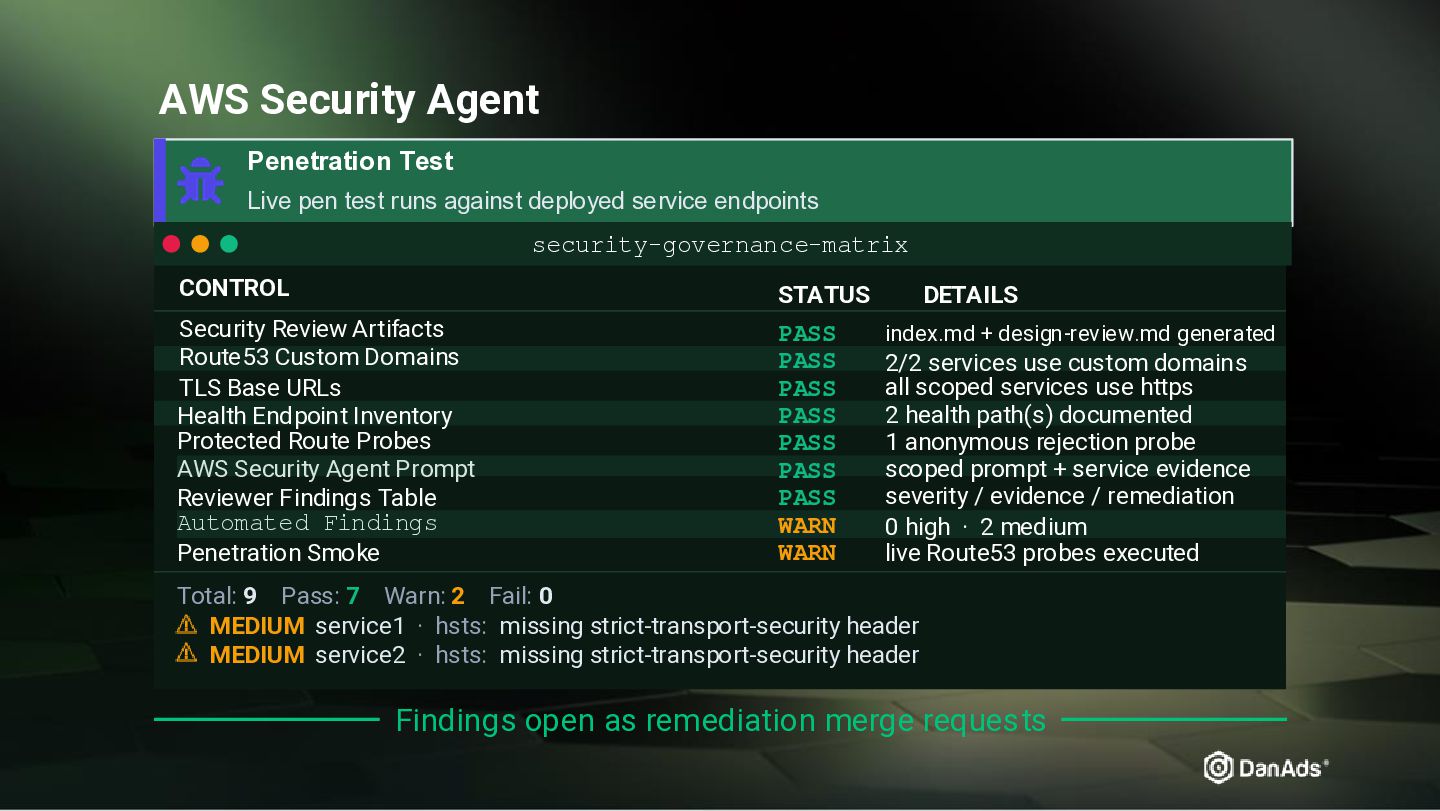
AWS Security Agent Penetration Test Live pen test runs against
deployed service endpoints security-governance-matrix CONTROL STATUS Security Review Artifacts Route53 Custom Domains TLS Base URLs Health Endpoint Inventory Protected Route Probes AWS Security Agent Prompt Reviewer Findings Table Automated Findings Penetration Smoke PASS PASS PASS PASS PASS PASS PASS WARN WARN DETAILS index.md + design-review.md generated 2/2 services use custom domains all scoped services use https 2 health path(s) documented 1 anonymous rejection probe scoped prompt + service evidence severity / evidence / remediation 0 high · 2 medium live Route53 probes executed Total: 9 Pass: 7 Warn: 2 Fail: 0 MEDIUM service1 · hsts: missing strict-transport-security header MEDIUM service2 · hsts: missing strict-transport-security header Findings open as remediation merge requests -
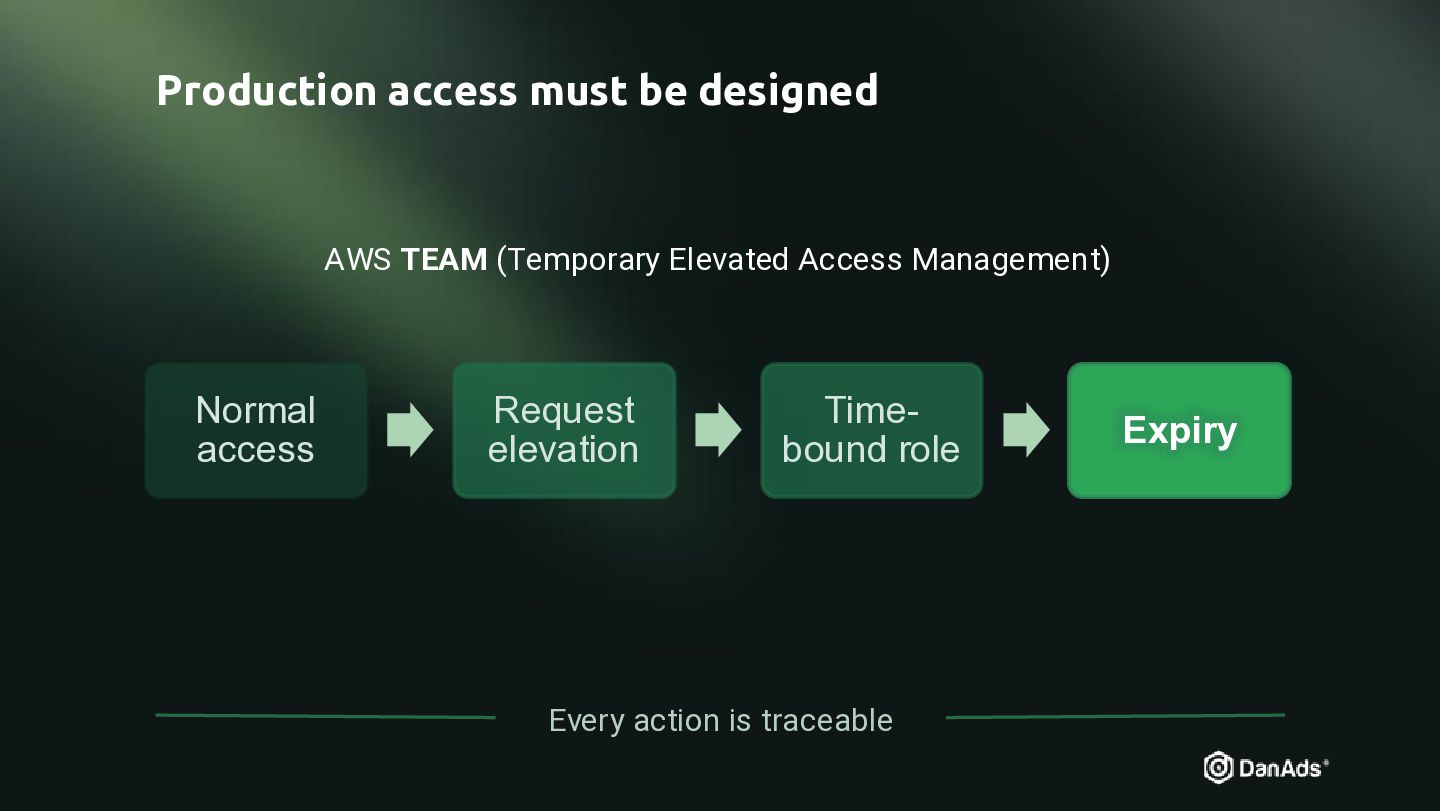
Production access must be designed AWS TEAM (Temporary Elevated Access
Management) Normal access Request elevation Timebound role Every action is traceable Expiry -
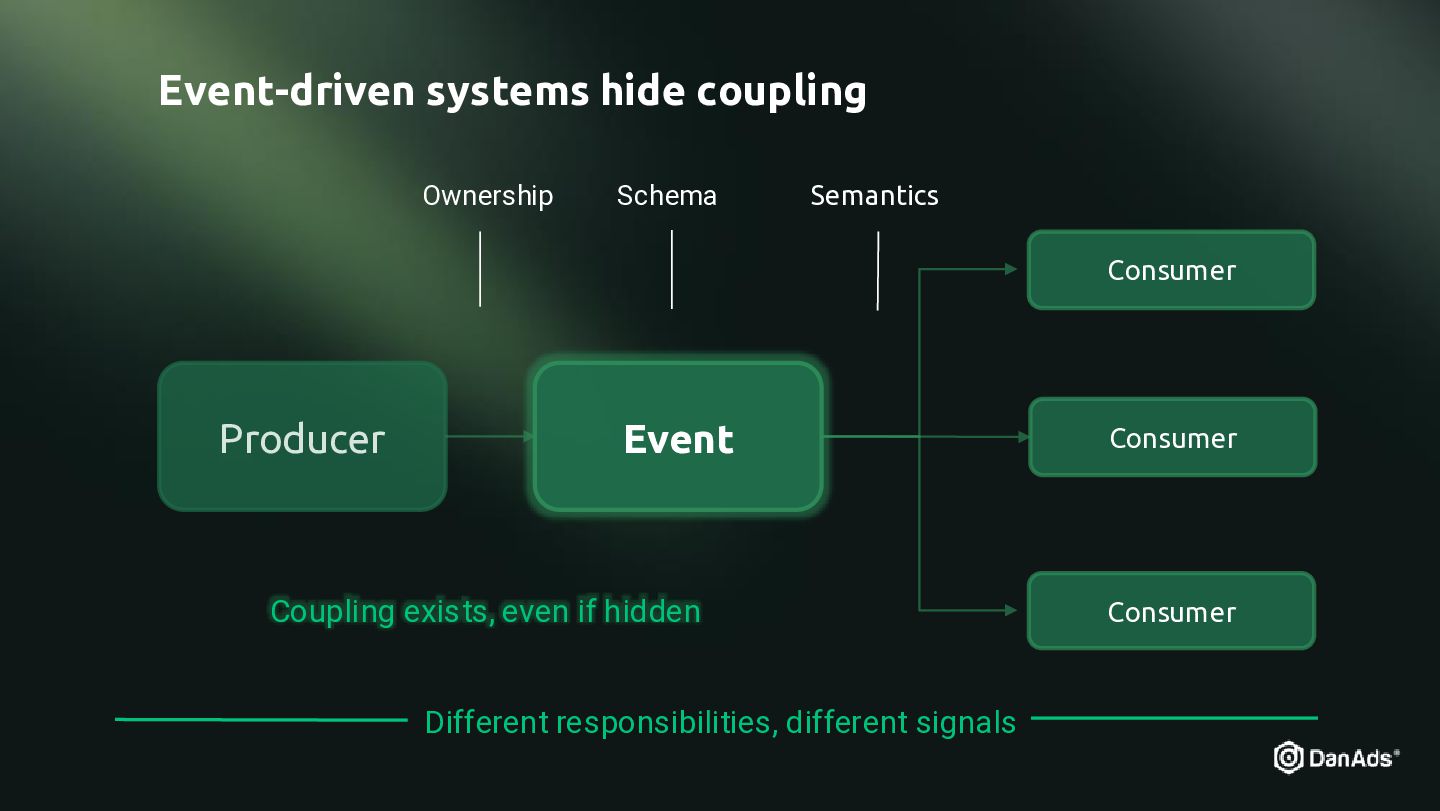
Event-driven systems hide coupling Ownership Schema Semantics Consumer Producer Event
Coupling exists, even if hidden Different responsibilities, different signals Consumer Consumer -
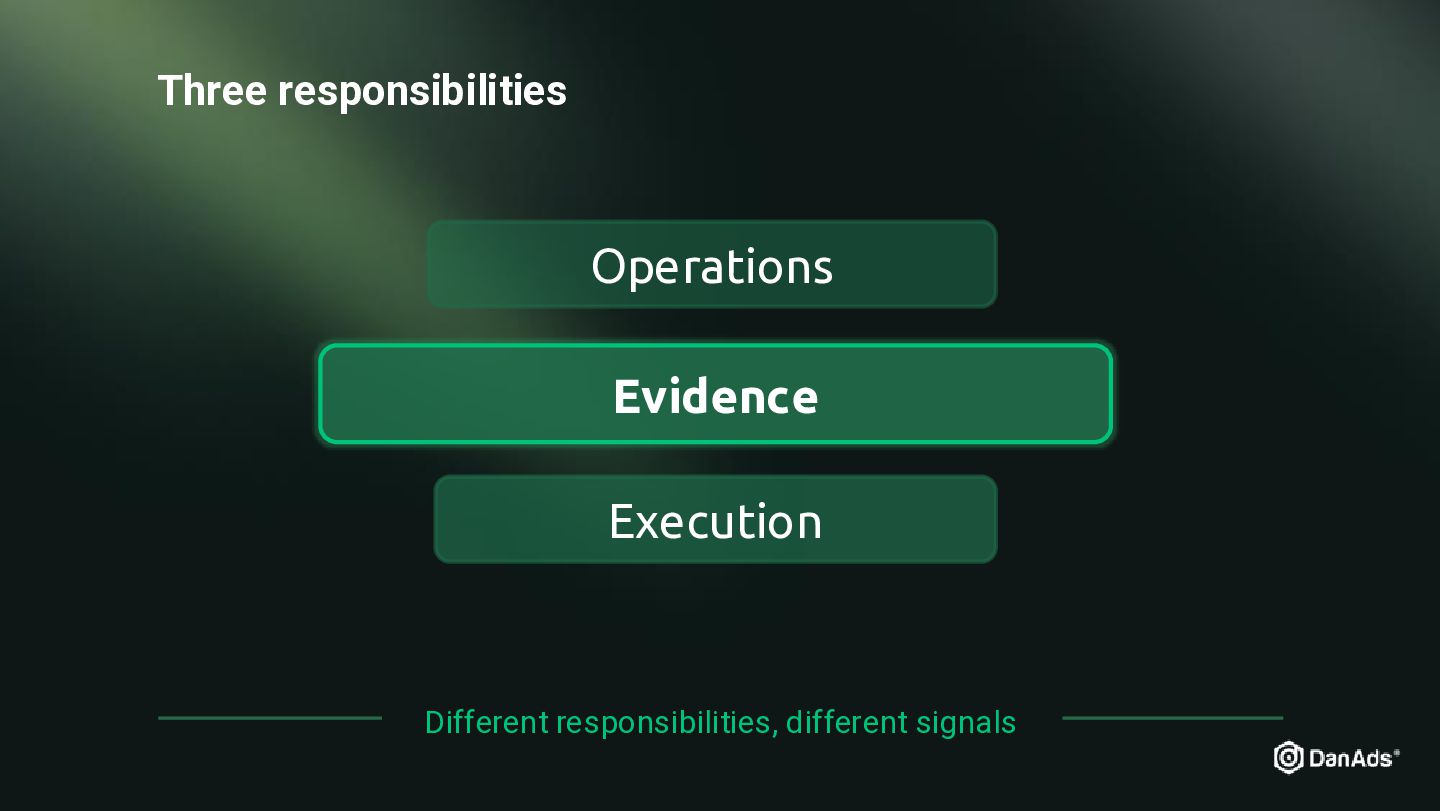
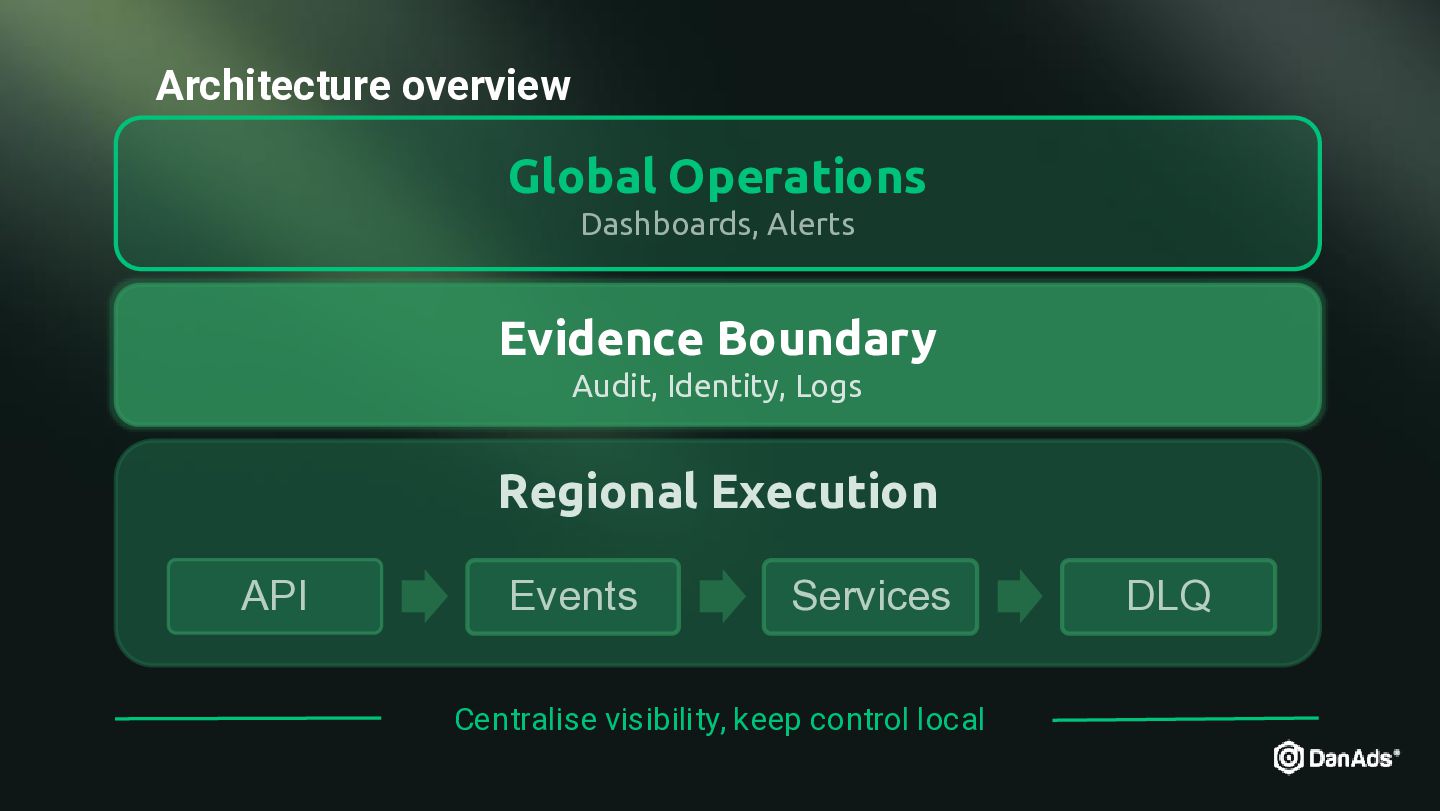
Architecture overview Global Operations Dashboards, Alerts Evidence Boundary Audit, Identity,
Logs Regional Execution API Events Services Centralise visibility, keep control local DLQ -
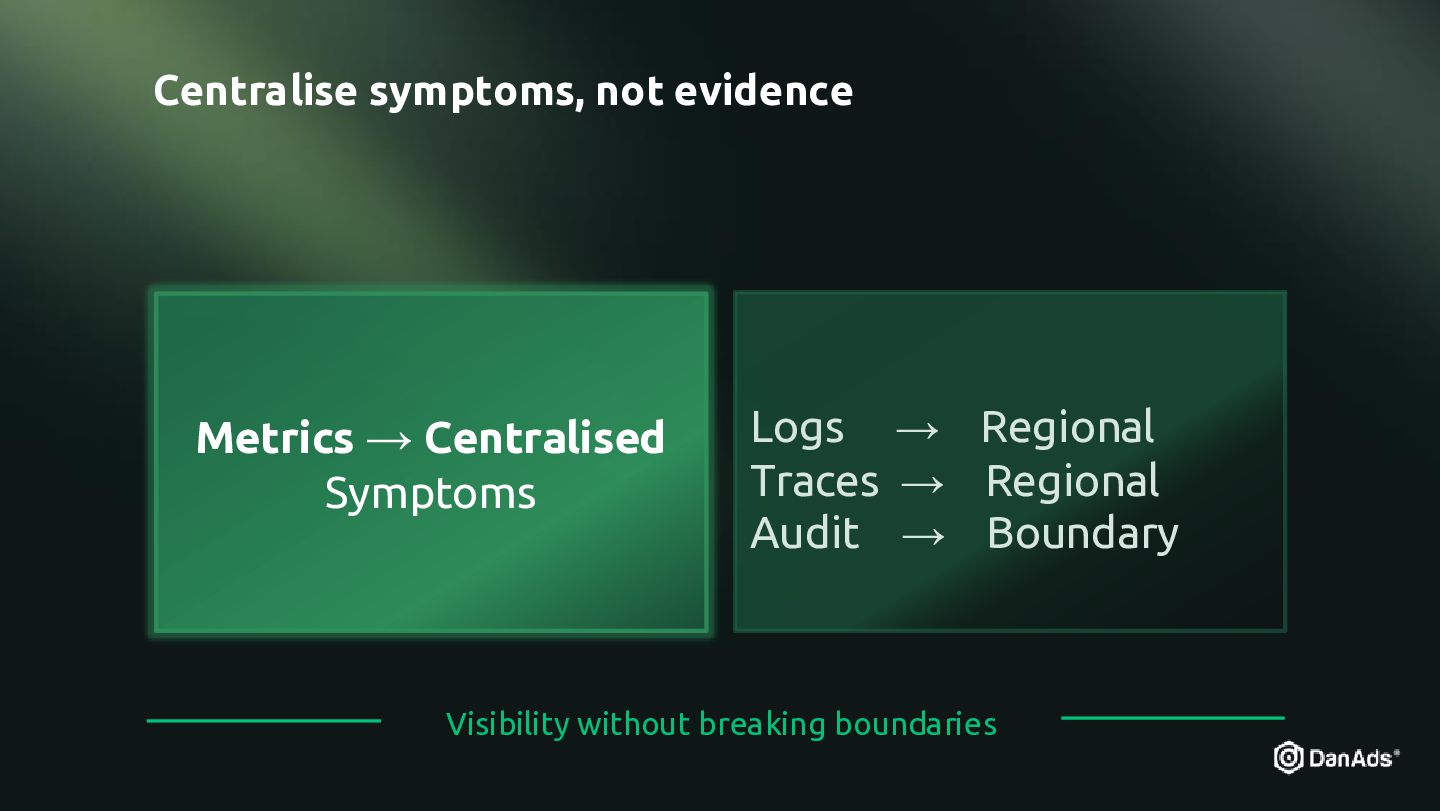
Centralise symptoms, not evidence Metrics → Centralised Symptoms Logs →
Regional Traces → Regional Audit → Boundary Visibility without breaking boundaries -
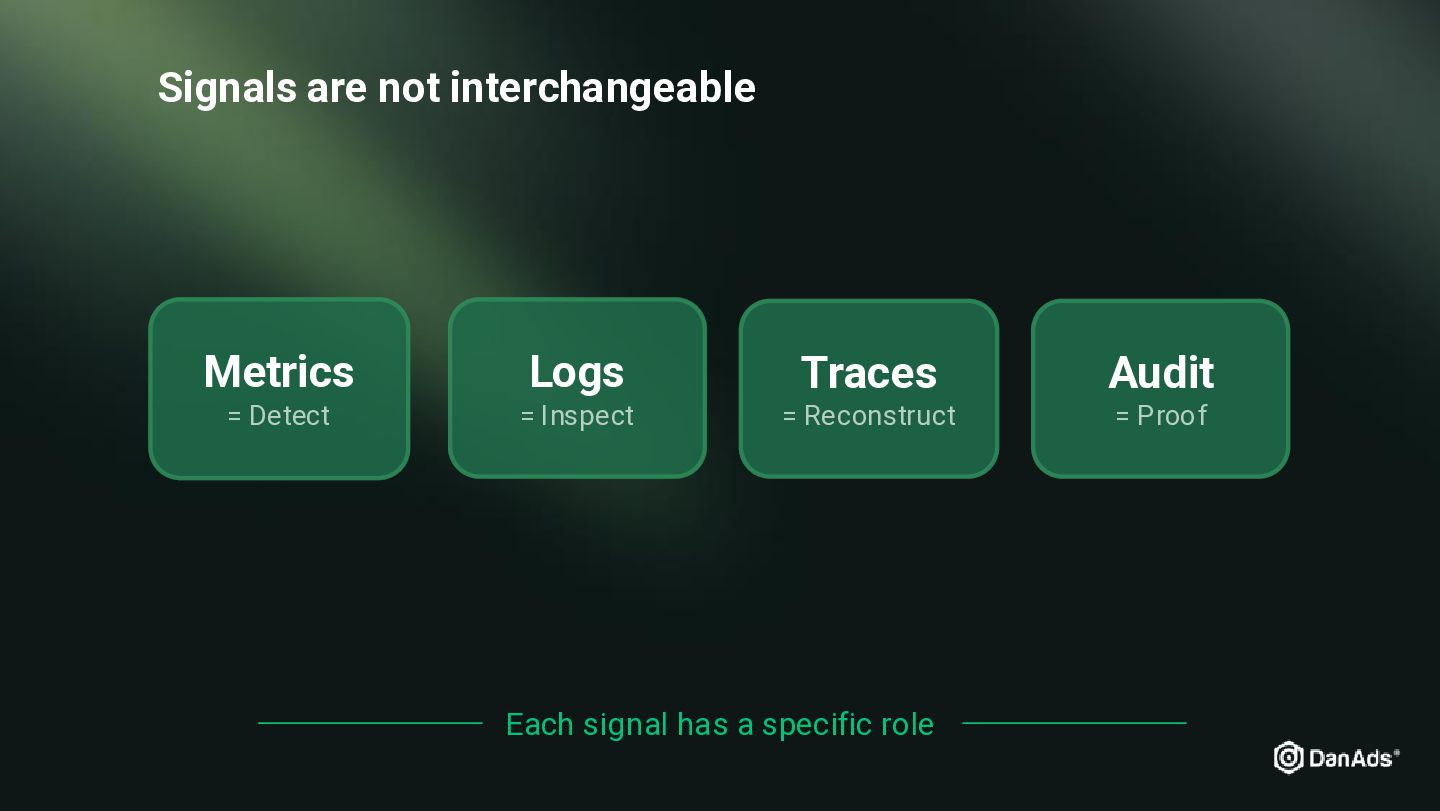
Signals are not interchangeable Metrics Logs Traces Audit = Detect
= Inspect = Reconstruct = Proof Each signal has a specific role -
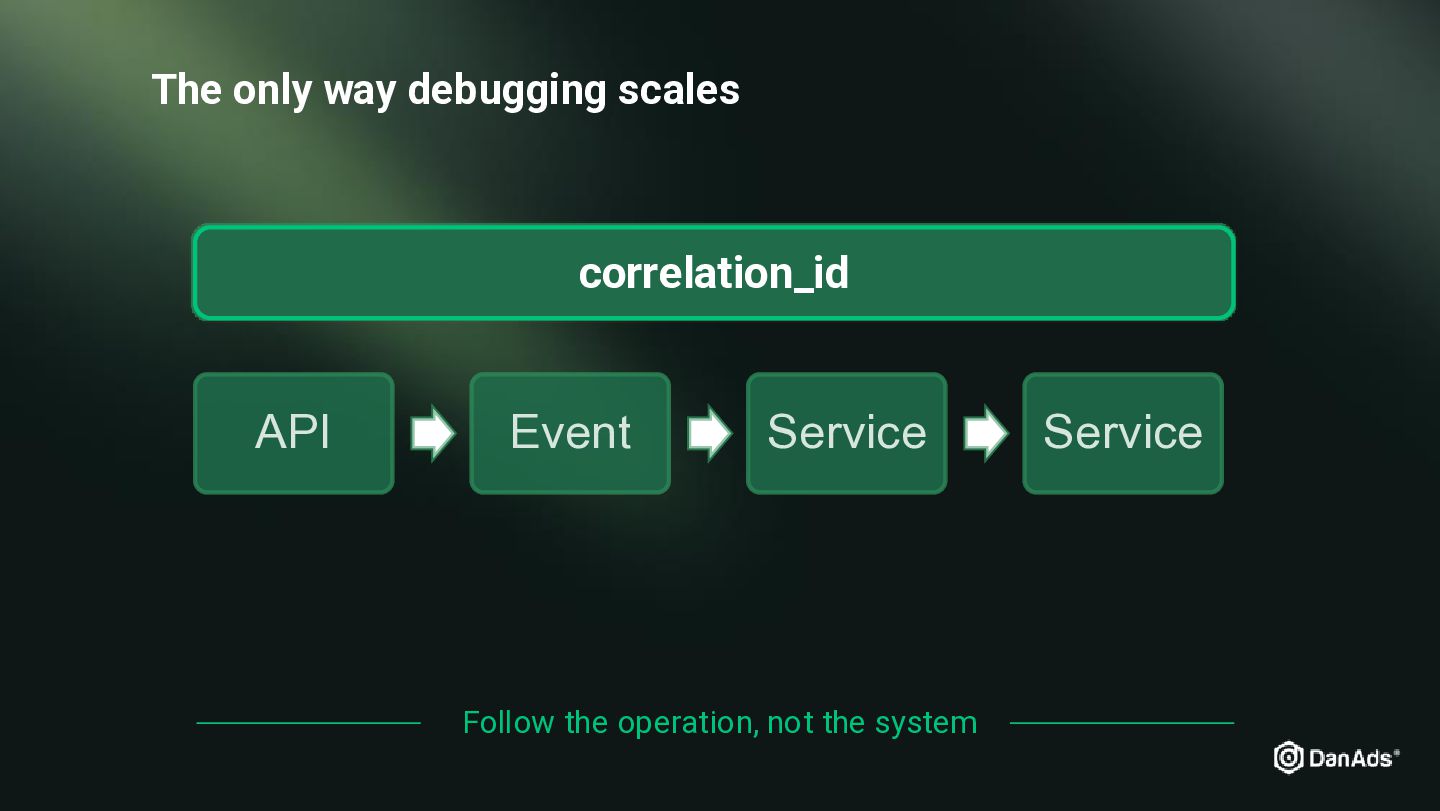
The only way debugging scales correlation_id API Event Service Follow
the operation, not the system Service -
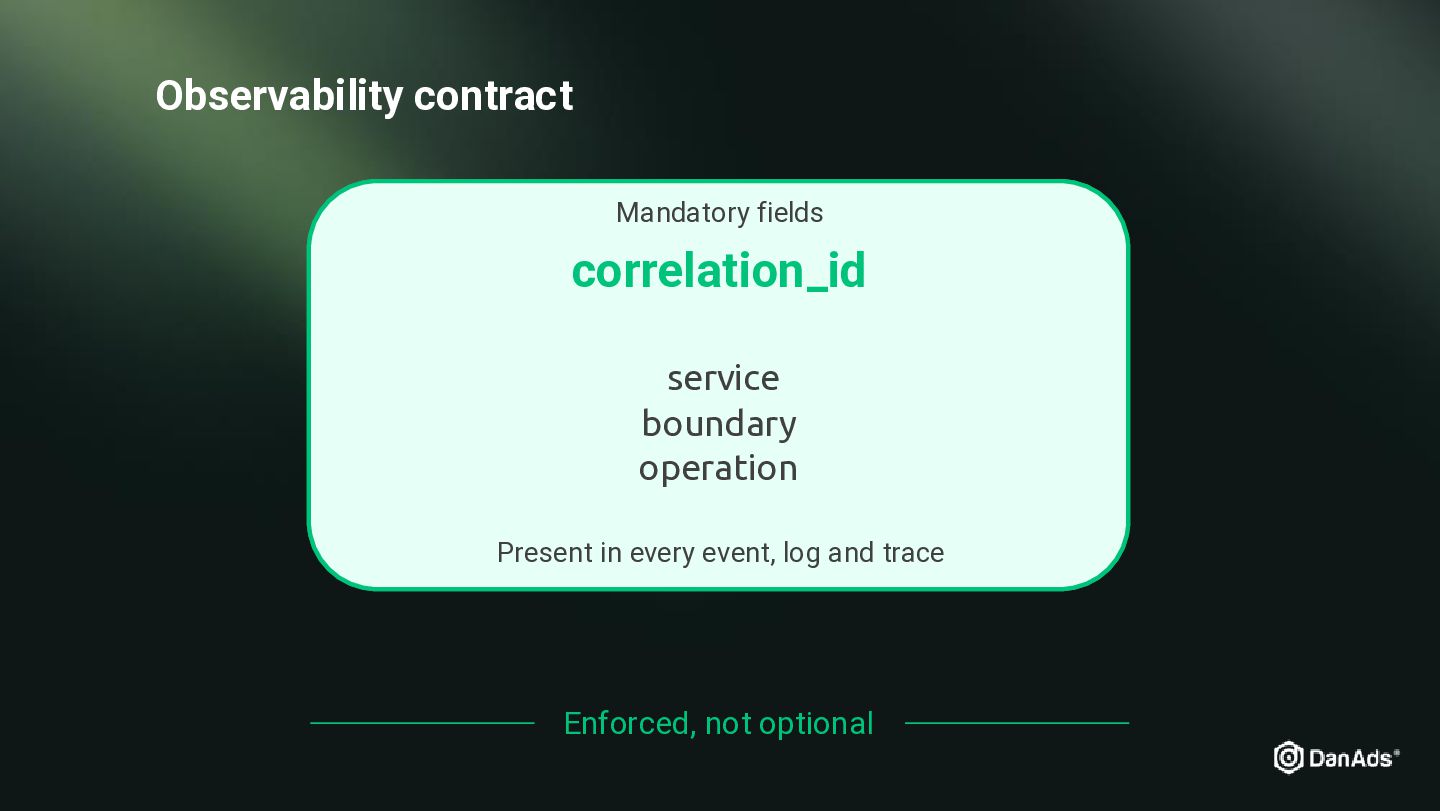
Observability contract Mandatory fields correlation_id service boundary operation Present in
every event, log and trace Enforced, not optional -
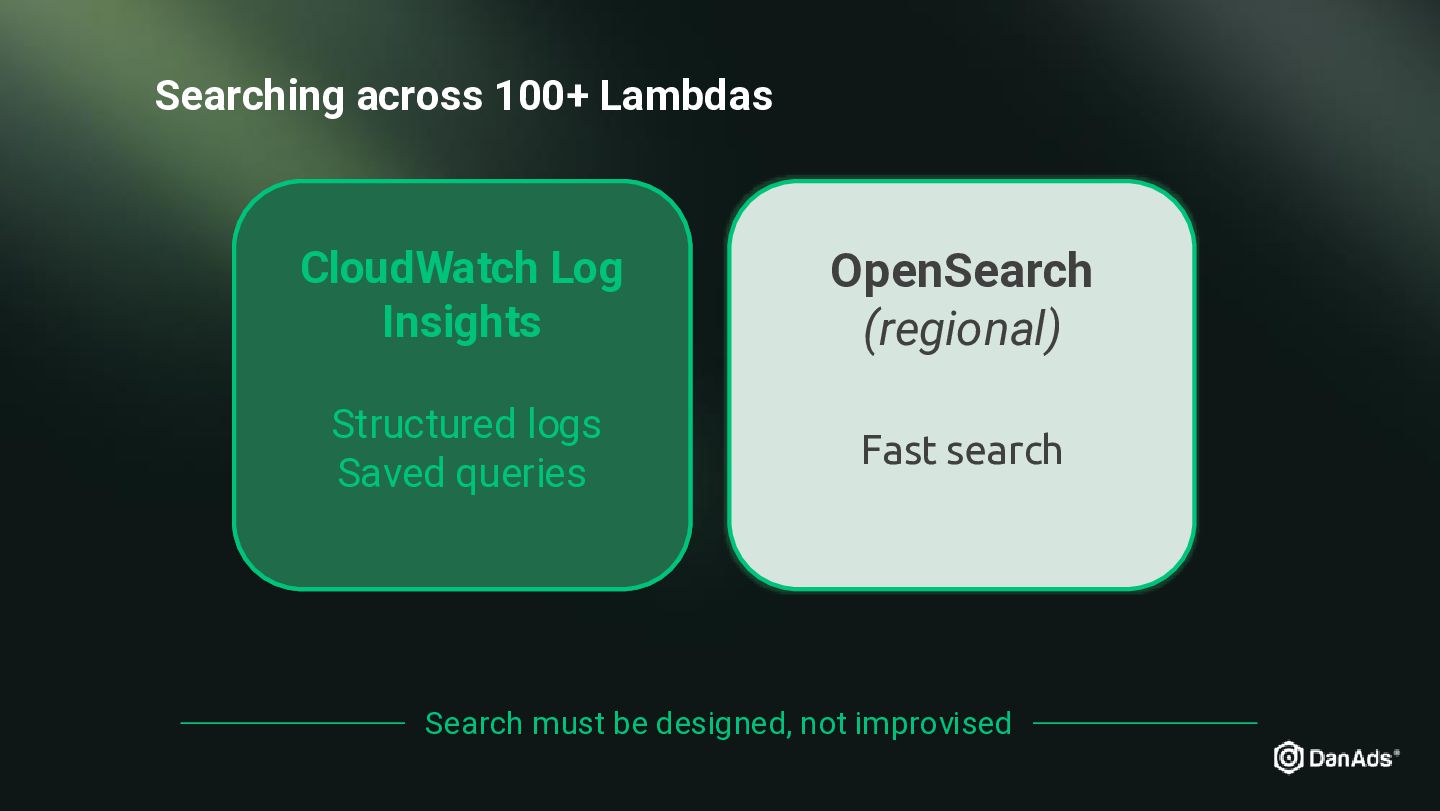
Searching across 100+ Lambdas CloudWatch Log Insights OpenSearch (regional) Structured
logs Saved queries Fast search Search must be designed, not improvised -
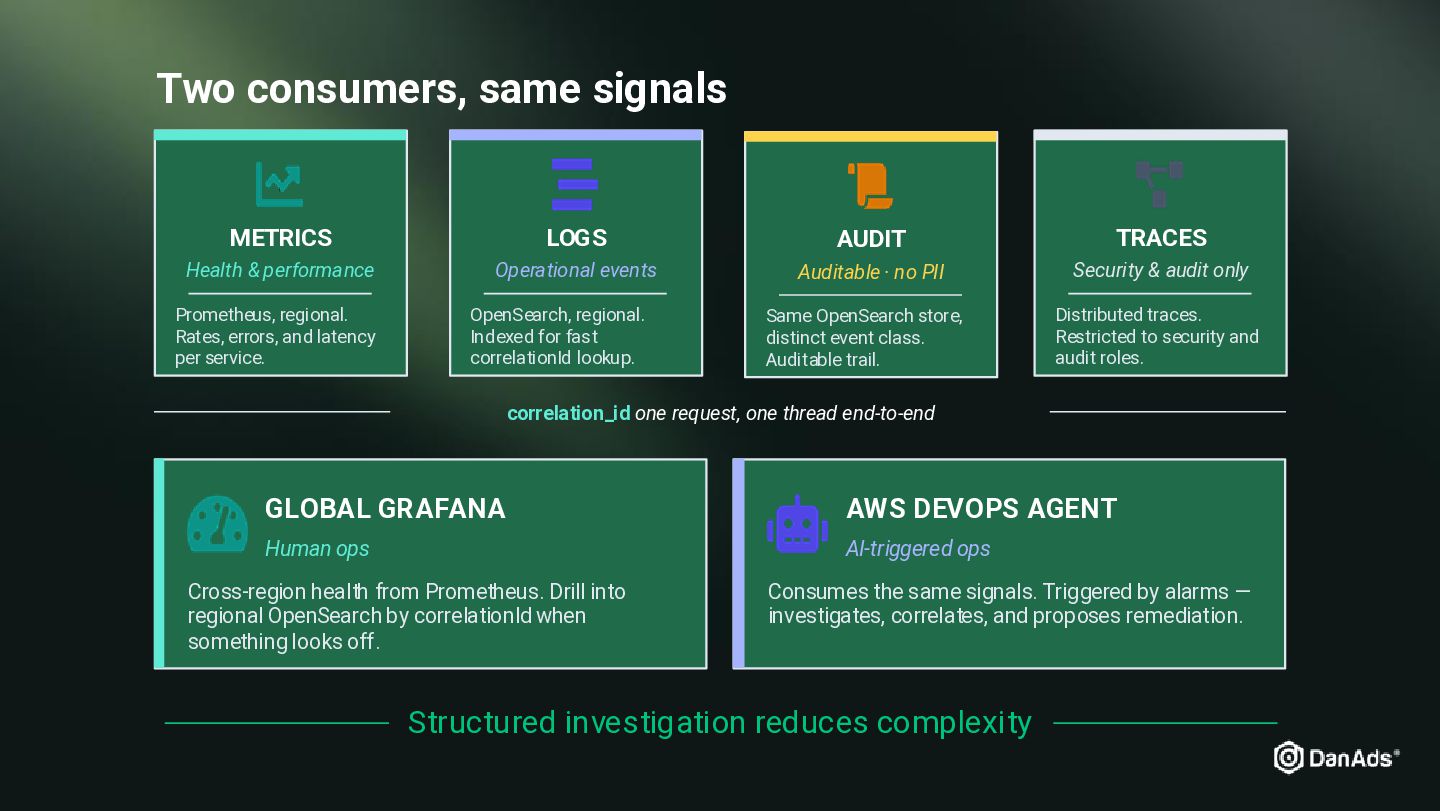
Two consumers, same signals METRICS LOGS AUDIT TRACES Health &
performance Operational events Auditable · no PII Security & audit only Prometheus, regional. Rates, errors, and latency per service. OpenSearch, regional. Indexed for fast correlationId lookup. Same OpenSearch store, distinct event class. Auditable trail. Distributed traces. Restricted to security and audit roles. correlation_id one request, one thread end-to-end GLOBAL GRAFANA AWS DEVOPS AGENT Human ops AI-triggered ops Cross-region health from Prometheus. Drill into regional OpenSearch by correlationId when something looks off. Consumes the same signals. Triggered by alarms — investigates, correlates, and proposes remediation. Structured investigation reduces complexity -
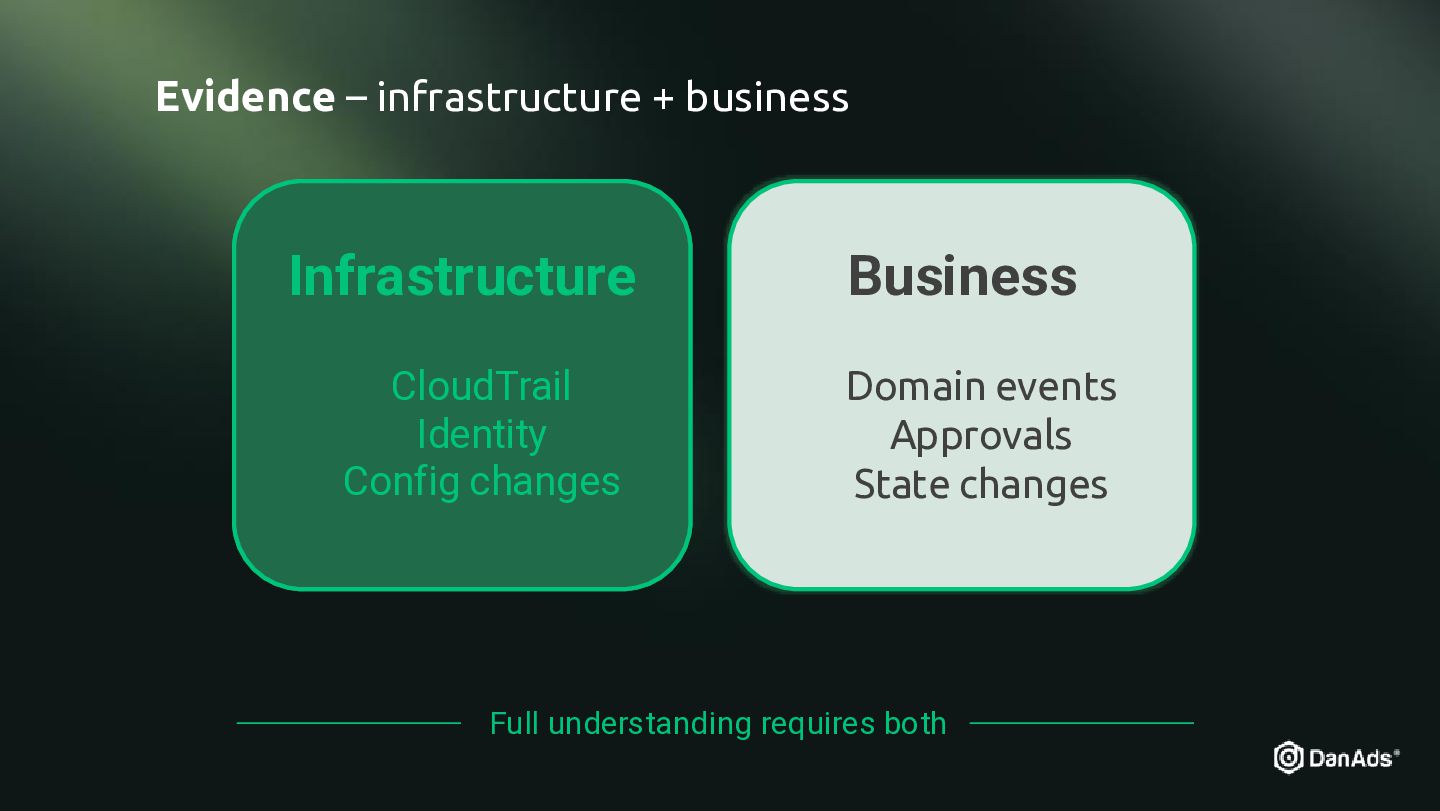
Evidence – infrastructure + business Infrastructure Business CloudTrail Identity Config
changes Domain events Approvals State changes Full understanding requires both -
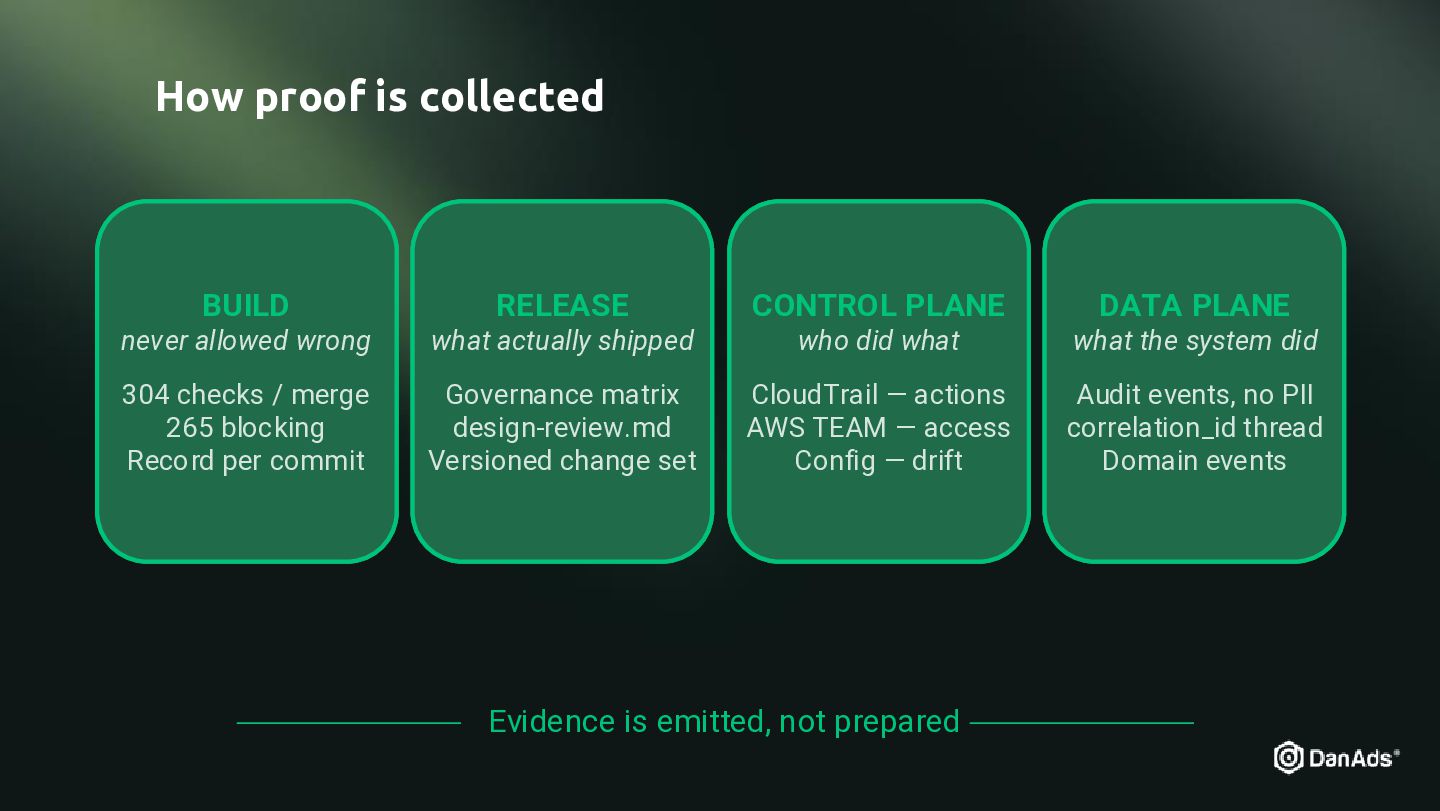
How proof is collected BUILD RELEASE CONTROL PLANE DATA PLANE
never allowed wrong what actually shipped who did what what the system did 304 checks / merge 265 blocking Record per commit Governance matrix design-review.md Versioned change set CloudTrail — actions AWS TEAM — access Config — drift Audit events, no PII correlation_id thread Domain events Evidence is emitted, not prepared -
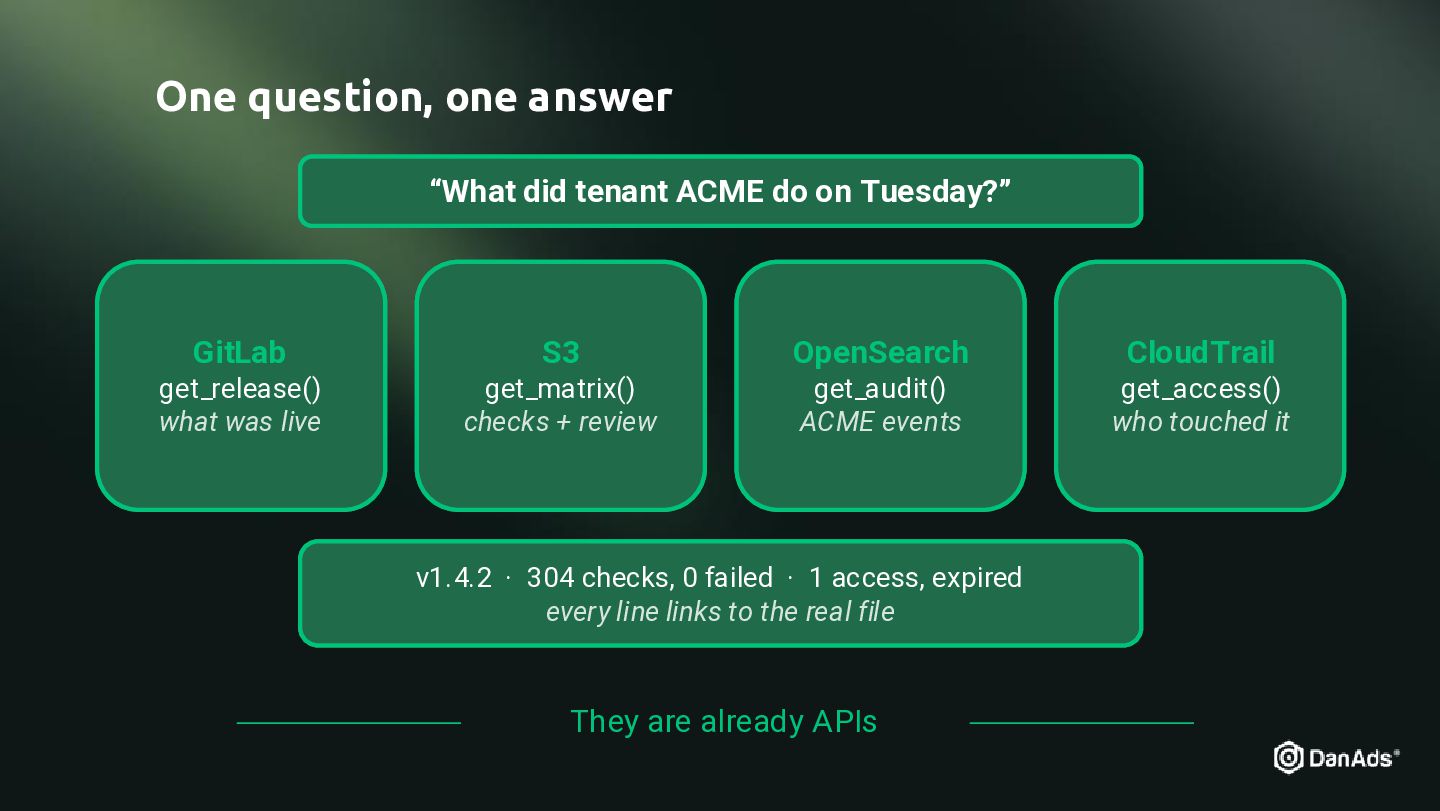
One question, one answer “What did tenant ACME do on
Tuesday?” GitLab S3 OpenSearch CloudTrail get_release() what was live get_matrix() checks + review get_audit() ACME events get_access() who touched it v1.4.2 · 304 checks, 0 failed · 1 access, expired every line links to the real file They are already APIs -
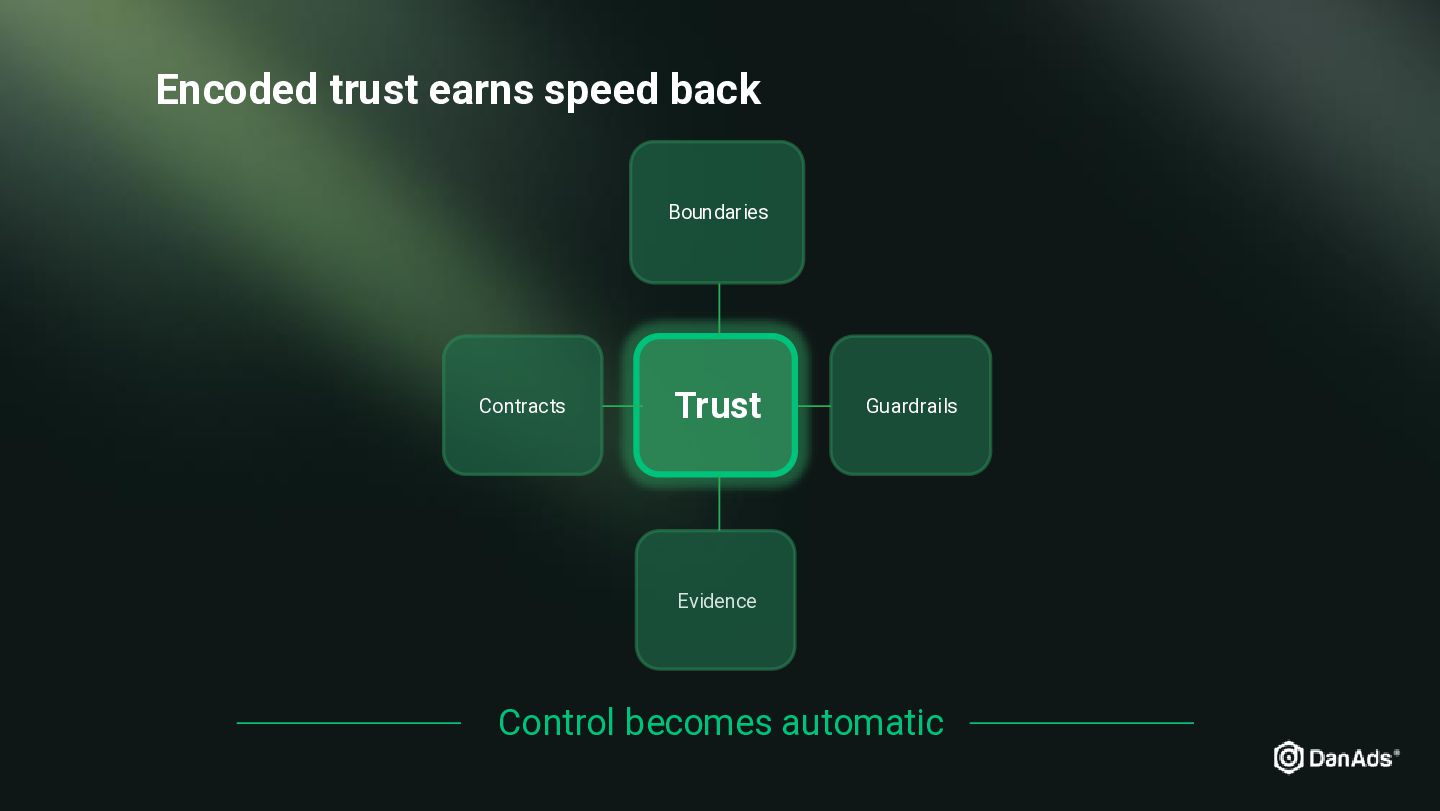
Encoded trust earns speed back Boundaries Contracts Trust Guardrails Evidence
Control becomes automatic -
Trust is the architecture Boundaries | Guardrails | Contracts |
Evidence Trust → Sustainable speed -
Thank you! Let's connect on LinkedIn https://www.feedbackfeijoa.com/e/0JCUYG/tpOWxgZxJj © 2026 Daniele
Frasca Trust Is the Architecture: Global Serverless at Scale Please credit the author when reusing material.