Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Safety first
Search
Ana Baotić
July 28, 2016
Programming
11k
10
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Safety first
Best practices in app security presentation held at the 360AnDev conference in Denver, CO
Ana Baotić
July 28, 2016
More Decks by Ana Baotić
See All by Ana Baotić
Inhibiting the impostor
abaotic
2
350
Sign here, please!
abaotic
1
150
Sign here, please!
abaotic
0
190
Break your app before someone else does
abaotic
1
630
Other Decks in Programming
See All in Programming
市販E-Readerを乗っ取れ 〜Embedded Swiftで電子ペーパーガジェットを制御する〜
trickart
0
230
ゲームコントローラやキーボードのファームウェアをSwiftで書く
kishikawakatsumi
1
270
Intent as Code
shoppingjaws
6
1.1k
ソニーのクラウド共通基盤の変遷と AI時代の開発スタイルに合わせた進化 / The Journey of Sony’s Common Cloud Platform and Its Evolution for AI-Native Development
kenjiyoneyama
0
210
Agents on Rails - Rails at Scale 2026
irinanazarova
0
310
UPDATE をやめる — EF Core でマスタをバージョン管理する
panda728
PRO
0
1.1k
半永久的に提供し続けられるプライベートクラウドを目指して ― 利用者の認知負荷を抑えるAPI抽象化とハードウェア世代交代の基盤設計
tomokon
0
390
TiDB Cloudのカスタムコントローラーによるオートスケール対応
takaidohigasi
0
140
Vue Fes Japan 2026 タイムテーブル徹底解説
448jp
1
590
Androidだけじゃない、DroidKaigiで広がった私の技術スタック
akkeylab
0
110
技術的負債を組織課題として解く-増えすぎたマイクロサービスとの戦い-
reimaru
1
2.6k
WebRTC映像をAirPlayに対応させる挑戦.pdf
monolithic_adam
0
330
Featured
See All Featured
Designing for humans not robots
tammielis
254
26k
How to Build an AI Search Optimization Roadmap - Criteria and Steps to Take #SEOIRL
aleyda
1
2.2k
Color Theory Basics | Prateek | Gurzu
gurzu
1
480
AI Search: Where Are We & What Can We Do About It?
aleyda
0
8k
[Rails World 2026] Durable orchestration on Rails: from continuation to workflow
palkan
1
410
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
Marketing to machines
jonoalderson
1
5.8k
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
300
Navigating the Design Leadership Dip - Product Design Week Design Leaders+ Conference 2024
apolaine
2
450
Kristin Tynski - Automating Marketing Tasks With AI
techseoconnect
PRO
0
530
The MySQL Ecosystem @ GitHub 2015
samlambert
251
13k
The Cost Of JavaScript in 2023
addyosmani
55
10k
Transcript
Safety first Best practices in app security ANA BAOTIĆ TECHNICAL
MANAGER, MOBILE BANKING @ INFINUM @ABAOTIC
We're an independent design & development agency.
None
HOW TO INCREASE SECURITY
BUILD INTEGRITY
ADD A RELEASE KEYSTORE TO YOUR PROJECT
KEYSTORE Can be used for ALL build types You should
NEVER lose it No one should EVER acquire it
KEEP IT SECRET, KEEP IT SAFE
signingConfigs { release { storeFile file("myapp.keystore") storePassword "password123" keyAlias "keyAlias"
keyPassword "password789" } } DO NOT!
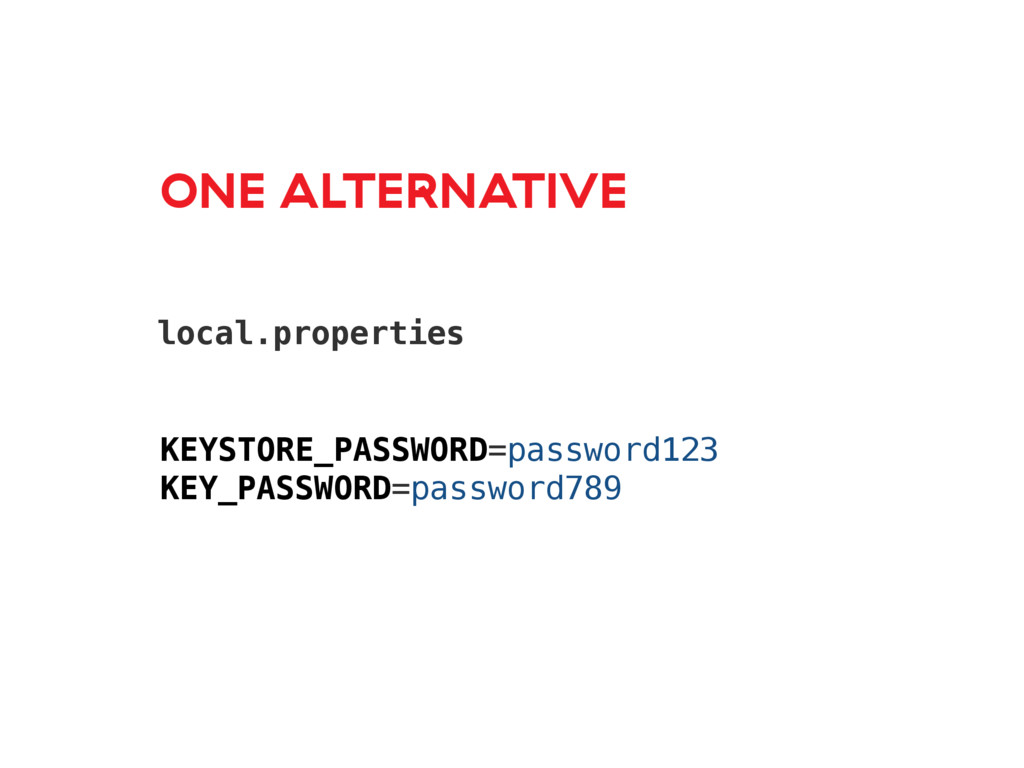
ONE ALTERNATIVE local.properties KEYSTORE_PASSWORD=password123 KEY_PASSWORD=password789
try { storeFile file("myapp.keystore") storePassword KEYSTORE_PASSWORD keyAlias "keyAlias" keyPassword KEY_PASSWORD
} catch (ex) { throw new InvalidUserDataException(“…”) }
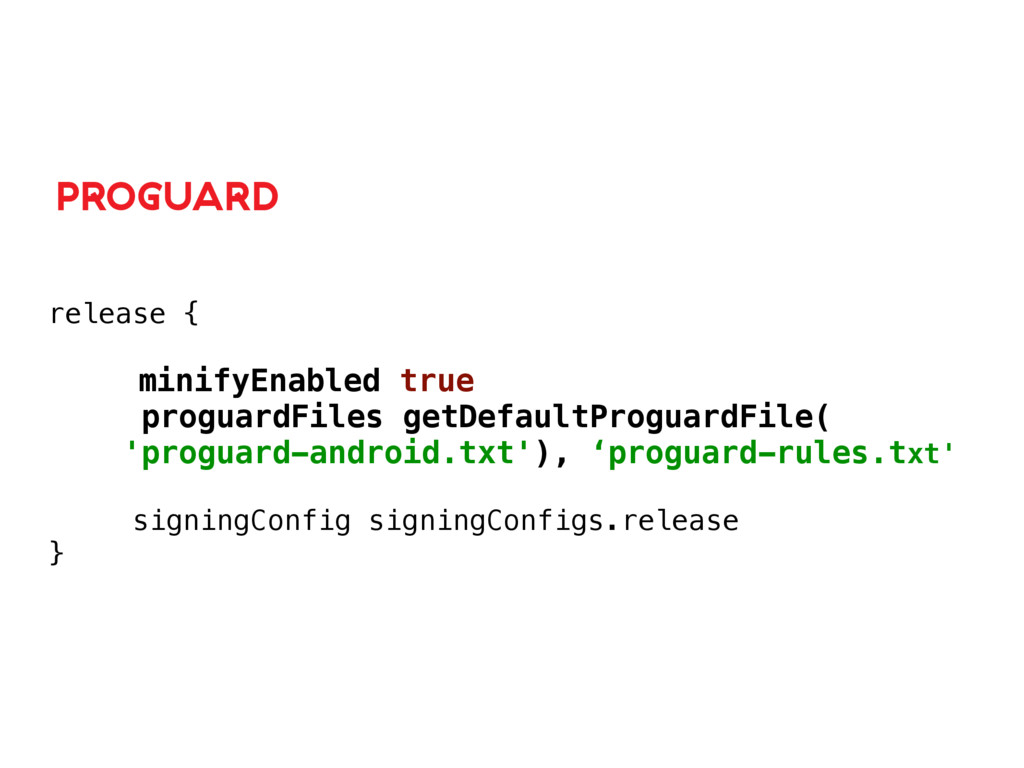
ENABLE OBFUSCATION
release { minifyEnabled true proguardFiles getDefaultProguardFile( 'proguard-android.txt'), ‘proguard-rules.txt'
signingConfig signingConfigs.release } PROGUARD
DOWNSIDES Disliked* Builds fail Staging vs Production
OTHER OPTIONS DexGuard DexProtector
None
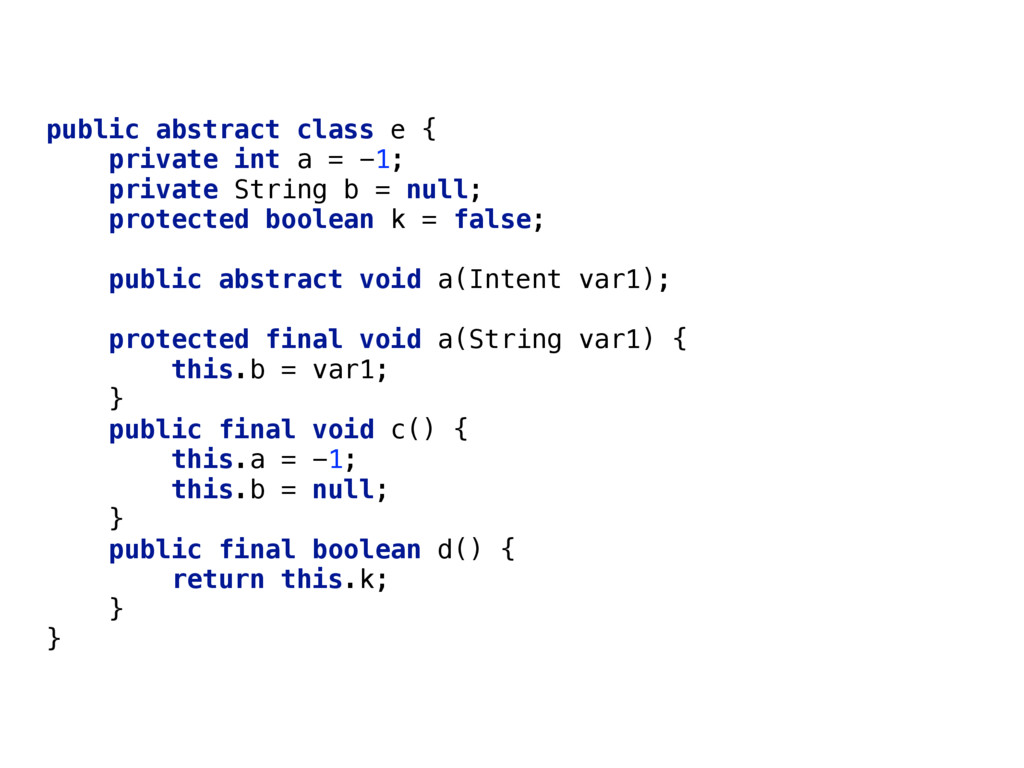
public abstract class e { private int a = -1;
private String b = null; protected boolean k = false; public abstract void a(Intent var1); protected final void a(String var1) { this.b = var1; } public final void c() { this.a = -1; this.b = null; } public final boolean d() { return this.k; } }
WILL THIS KEEP THE APK SAFE?
None
ADD TAMPERING DETECTION
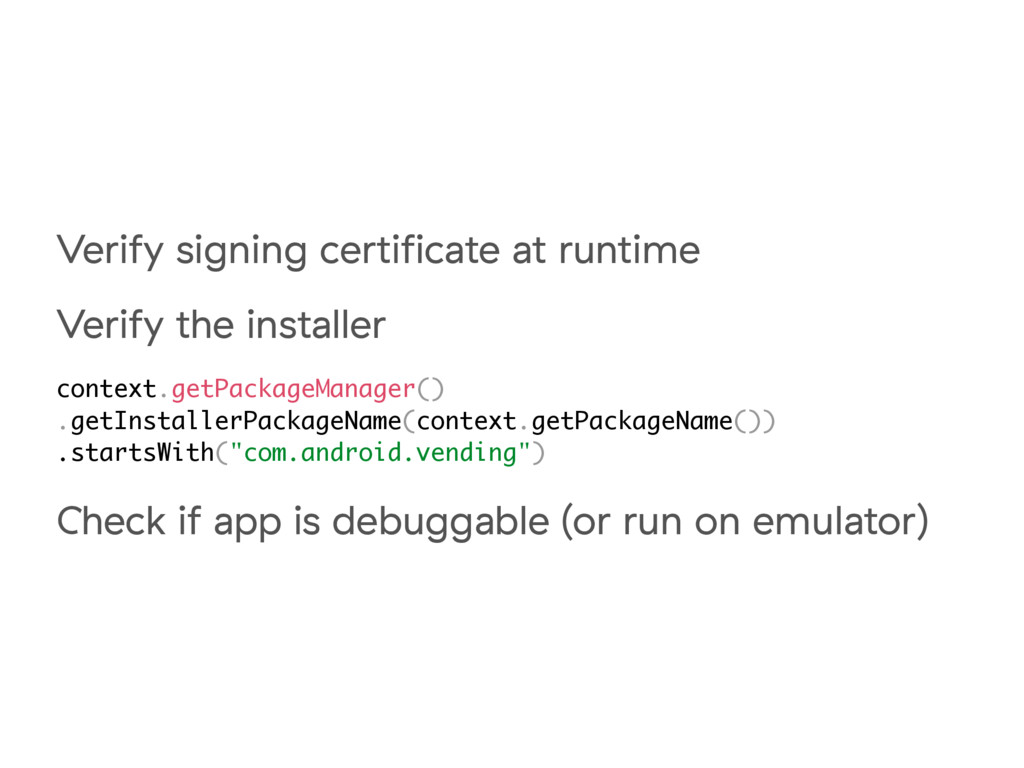
Verify signing certificate at runtime Verify the installer context.getPackageManager() .getInstallerPackageName(context.getPackageName())
.startsWith("com.android.vending") Check if app is debuggable (or run on emulator)
DATA PRIVACY
MY PRECIOUS
WAYS TO STORE (AND RETRIEVE) DATA Internal storage External storage
Content providers*
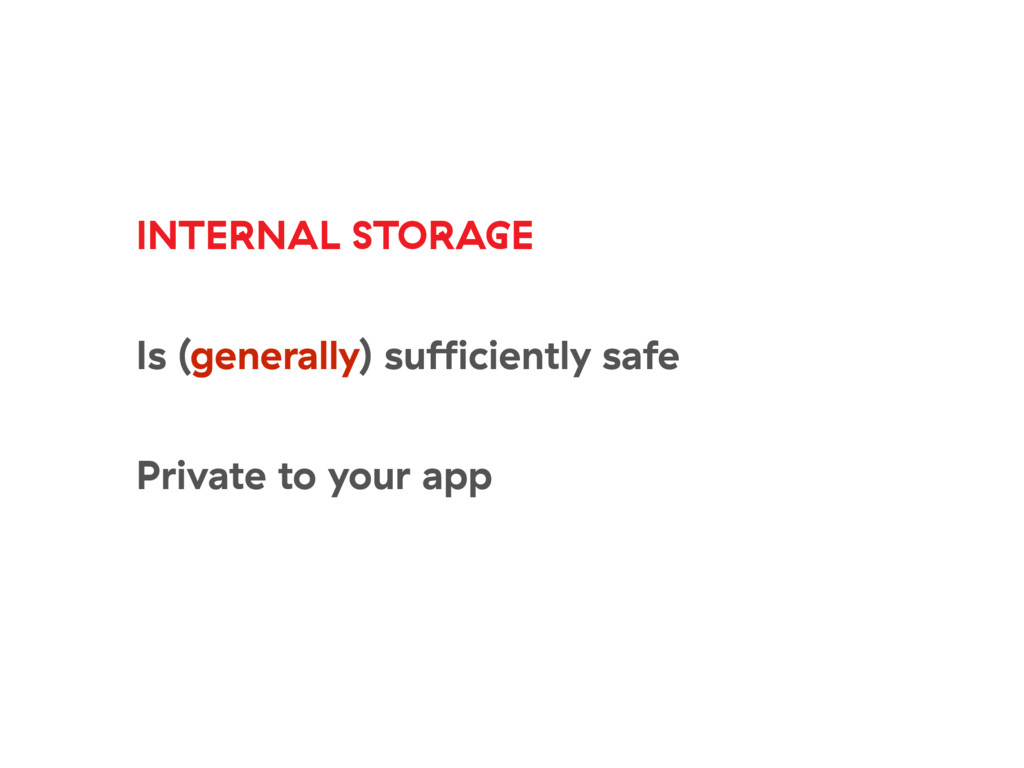
INTERNAL STORAGE Is (generally) sufficiently safe Private to your app
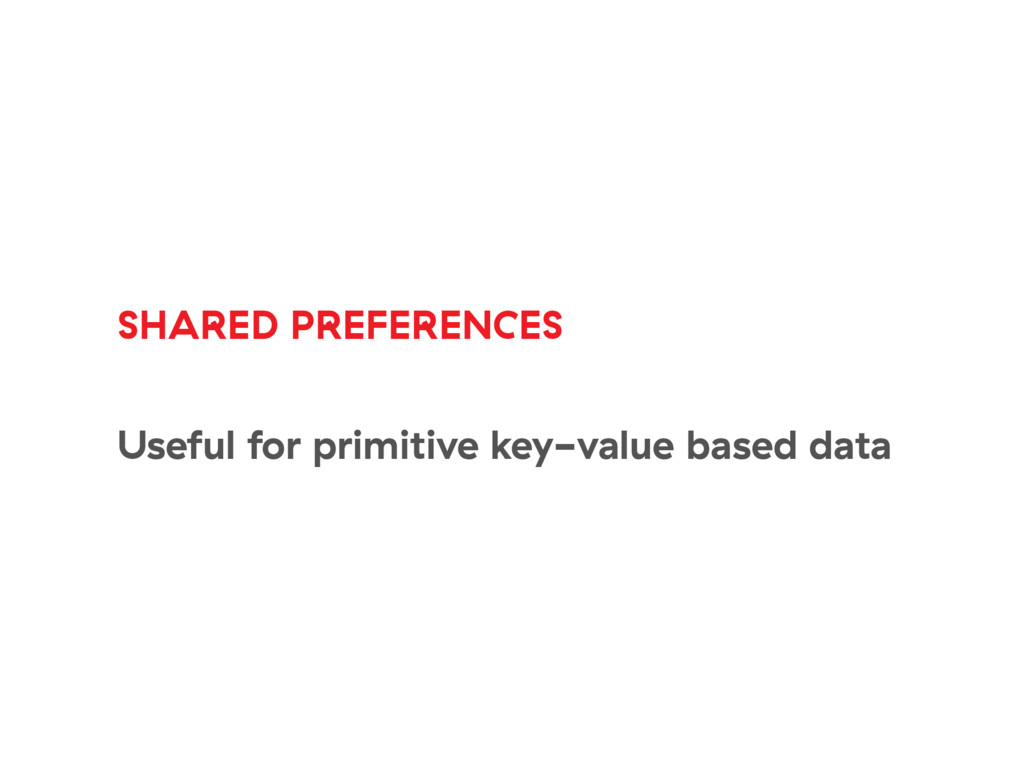
SHARED PREFERENCES Useful for primitive key-value based data
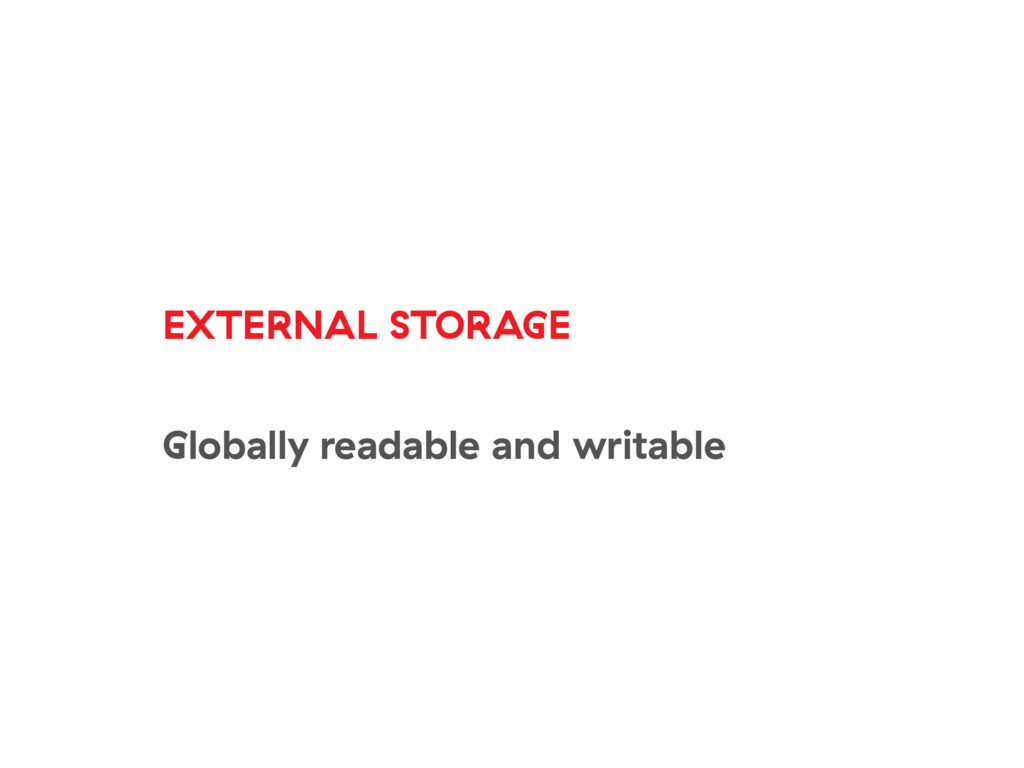
EXTERNAL STORAGE Globally readable and writable
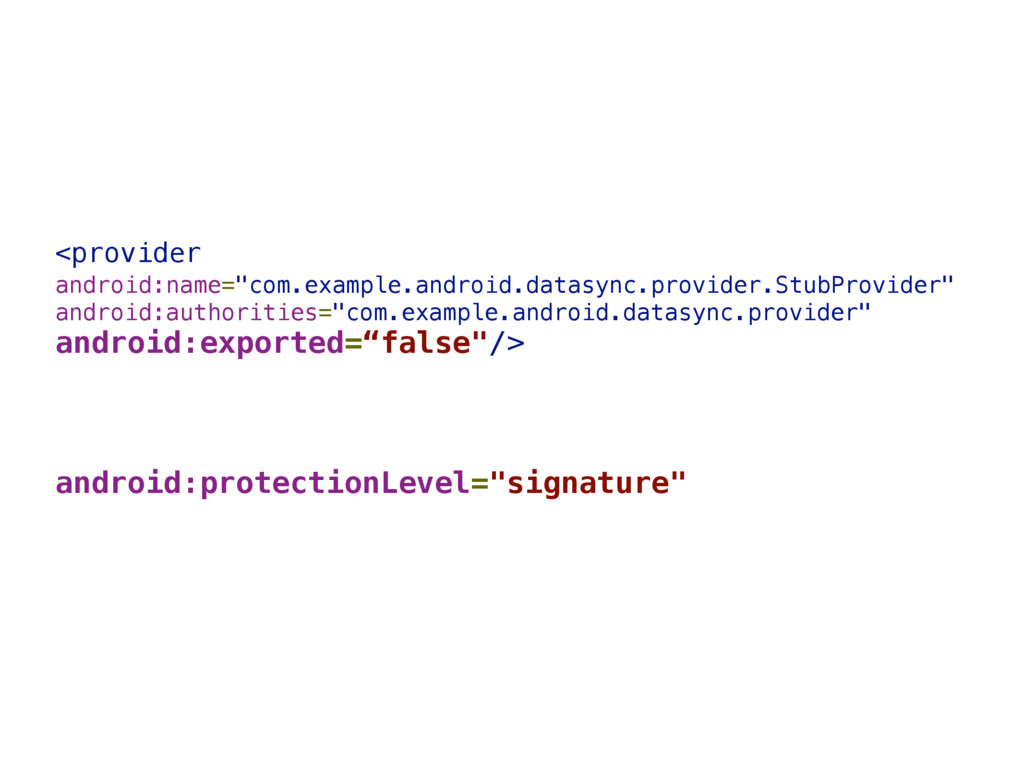
CONTENT PROVIDERS Structured storage mechanism Can be exported (accessed by
other apps)
<provider android:name="com.example.android.datasync.provider.StubProvider" android:authorities="com.example.android.datasync.provider" android:exported=“false"/> android:protectionLevel="signature"
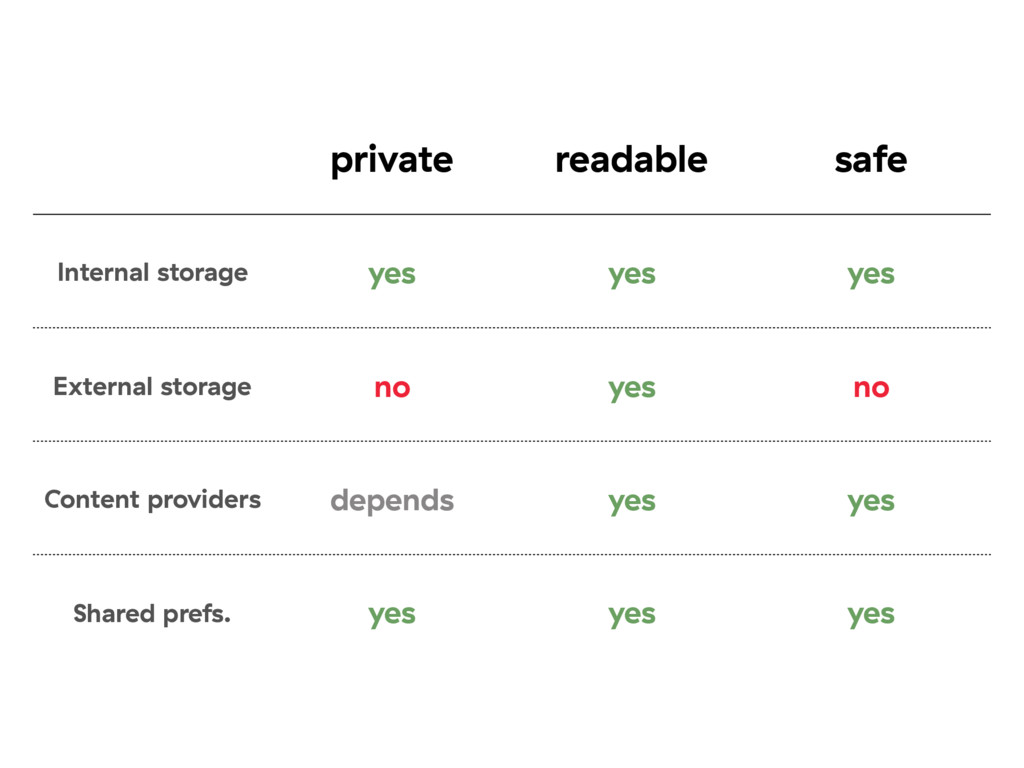
private readable safe Internal storage yes yes yes External storage
no yes no Content providers depends yes yes Shared prefs. yes yes yes
SO EVERYTHING IS FINE?
NOPE.
None
USE LIBRARIES Bouncy Castle Spongy Castle Keyczar AeroGear Crypto Conceal
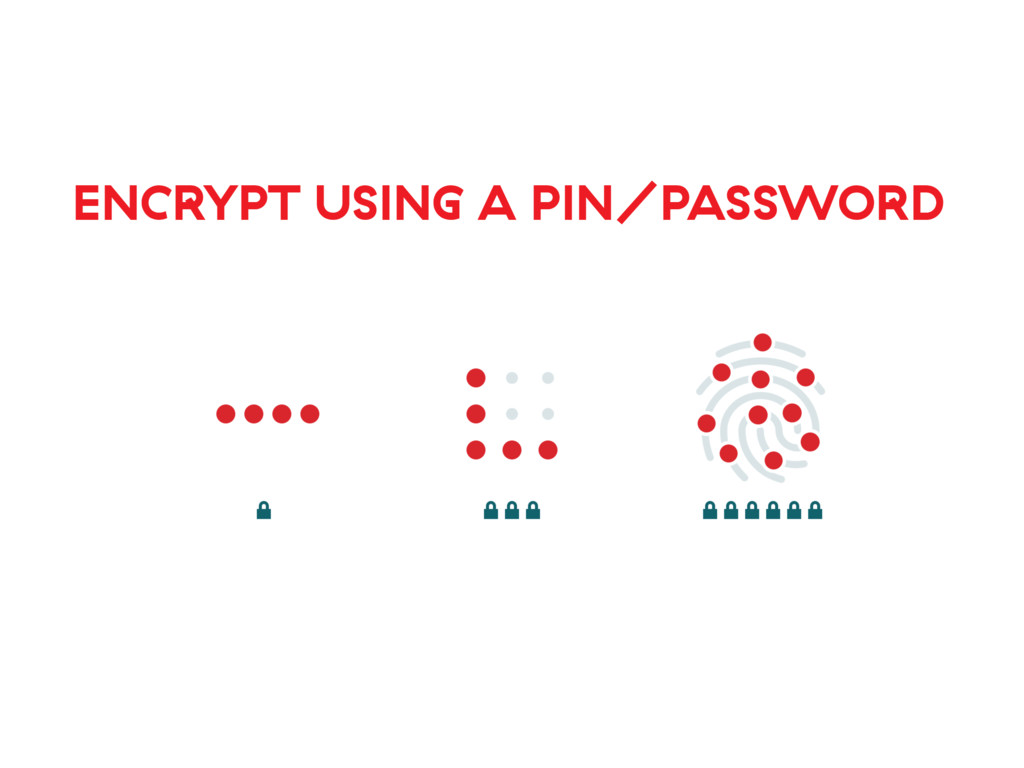
ENCRYPT USING A PIN/PASSWORD
BCRYPT Slow Key derivation function Cost of hash function →
work factor
CAN DATA REMAIN PRIVATE?
Rooting your device allows access Not encrypting allows (mis)use
NETWORK SECURITY
None
HTTP
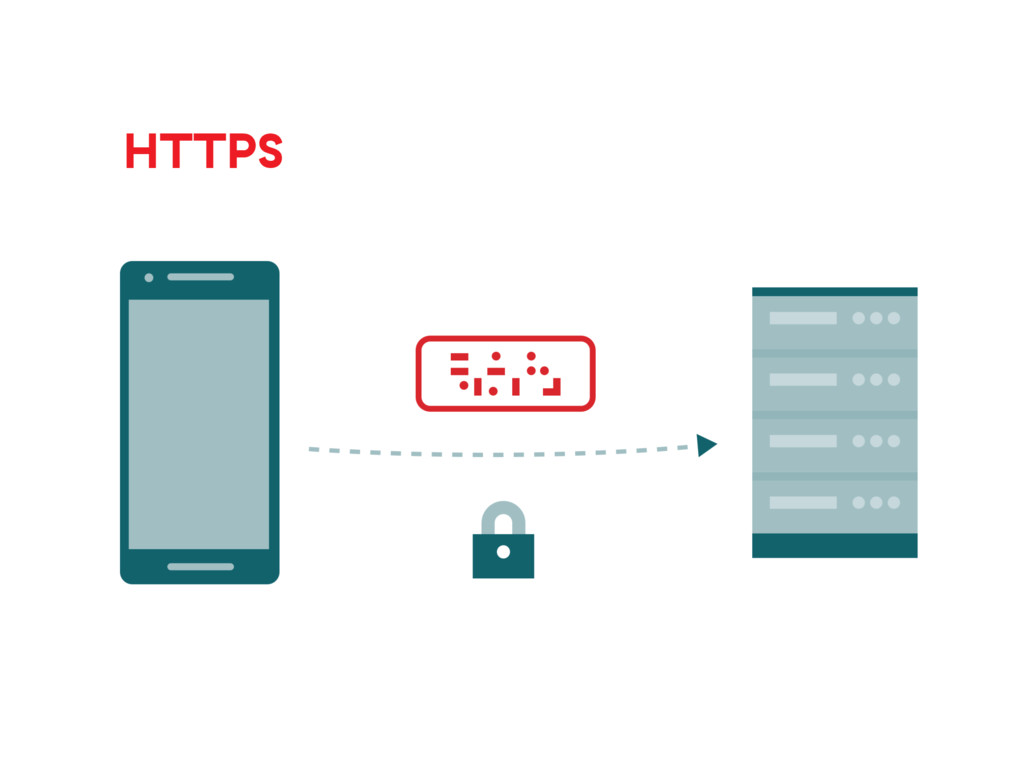
HTTPS
MAN IN THE MIDDLE
None
CERTIFICATE PINNING Defines which CAs are trusted Reduces effectiveness of
the attack
okhttpbuilder .pinClientCertificate(resources, R.raw.client_cert, "pass".toCharArray(), “PKCS12”) .pinServerCertificates(resources, R.raw.server_cert, "pass".toCharArray(), "BKS")
.build(); return new OkClient(client);
WHAT IF (WHEN) THE CERTIFICATES CHANGE?
INFORM YOUR USERS Implement a mechanism for notifying users (GCM)
and forcing updates
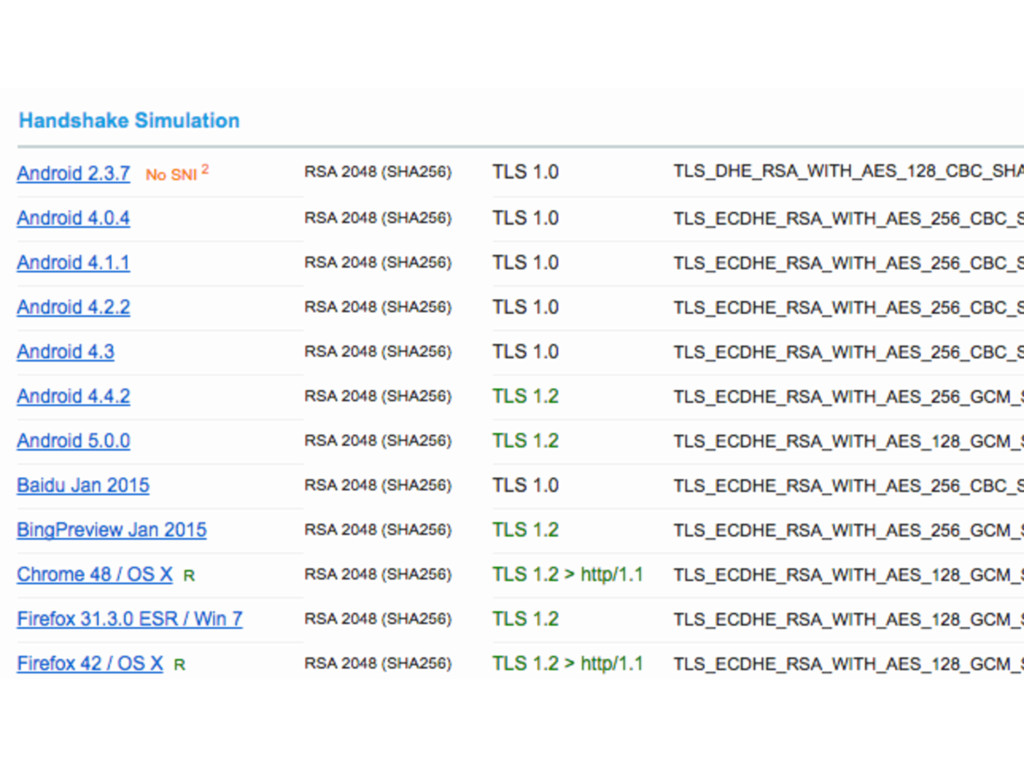
PLAN AHEAD Check server security’s impact on devices https://www.ssllabs.com/
None
USE THE PLATFORM TO YOUR ADVANTAGE
android:usesCleartextTraffic="false" ANDROID M StrictMode.setVmPolicy( new StrictMode.VmPolicy.Builder() .detectCleartextNetwork() .penaltyLog().build());
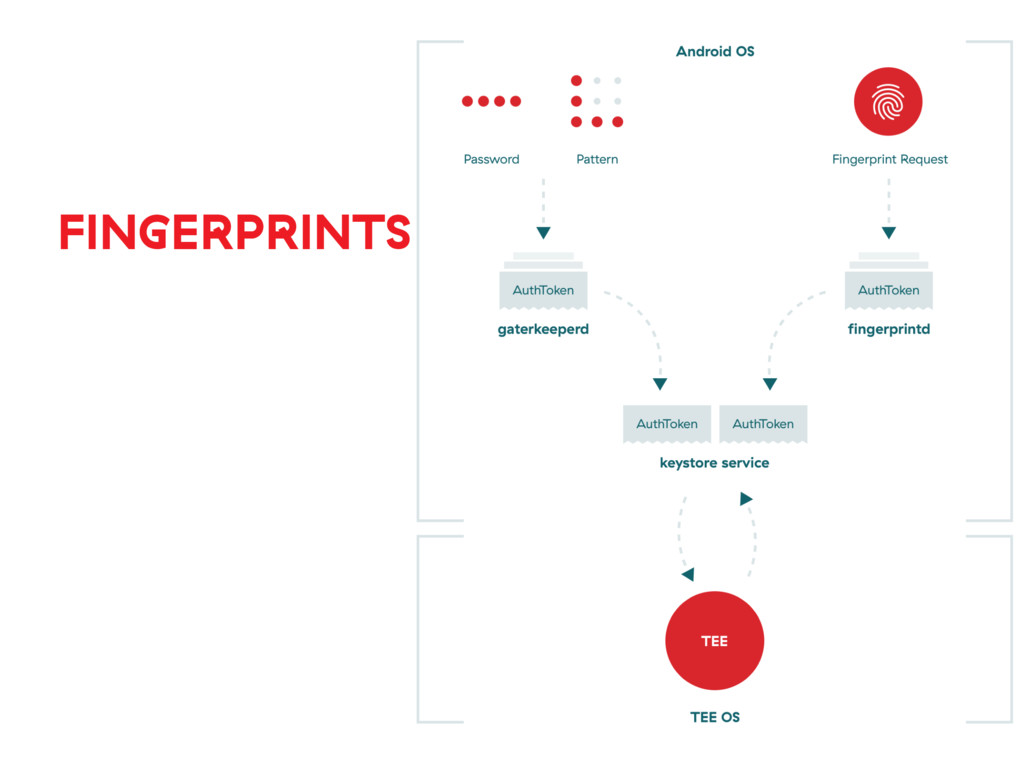
FINGERPRINTS
APP LINKING HTTPS://DOMAIN[:OPT_PORT]/.WELL-KNOWN/ASSETLINKS.JSON [{ "relation": ["delegate_permission/common.handle_all_urls"], "target": { "namespace": "android_app",
"package_name": "com.example", "sha256_cert_fingerprints": ["14:6D:E9:...44:E5"] } }]
ANDROID N Network Security Configuration feature
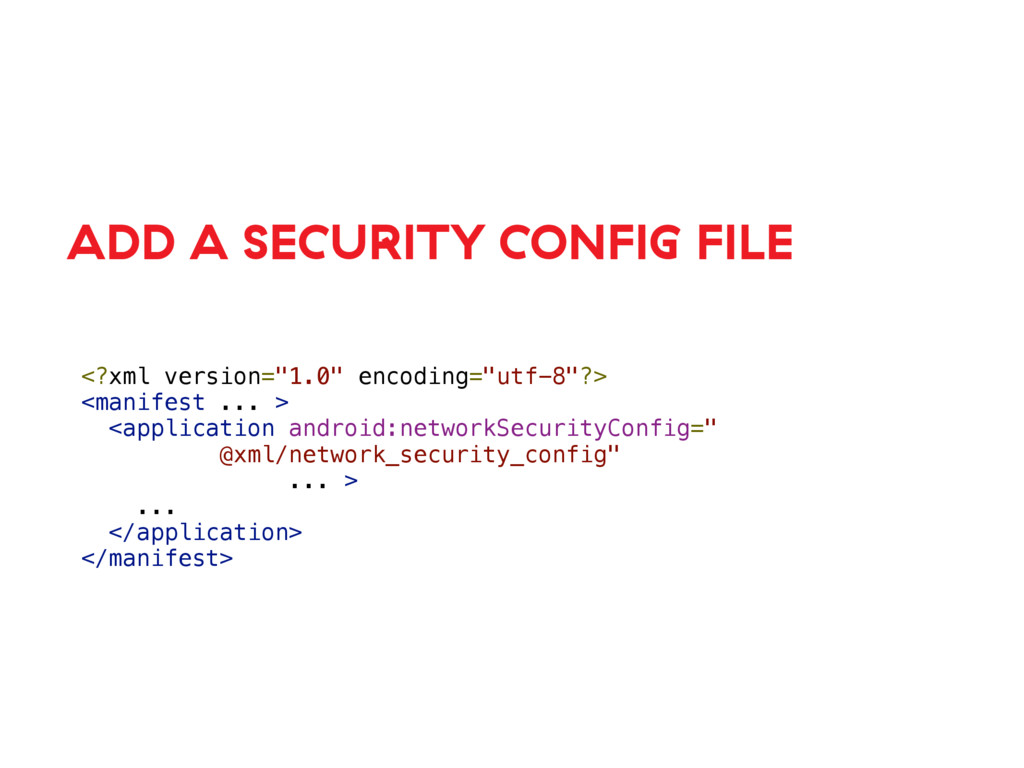
<?xml version="1.0" encoding="utf-8"?> <manifest ... > <application android:networkSecurityConfig=" @xml/network_security_config" ...
> ... </application> </manifest> ADD A SECURITY CONFIG FILE
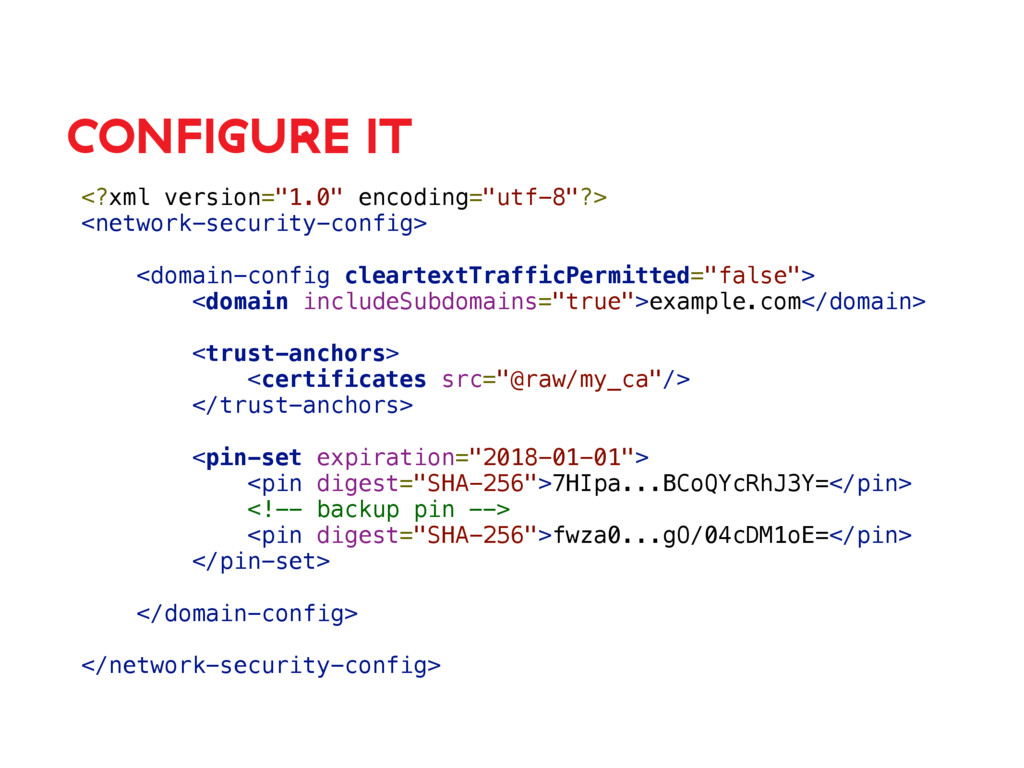
<?xml version="1.0" encoding="utf-8"?> <network-security-config> <domain-config cleartextTrafficPermitted="false"> <domain includeSubdomains="true">example.com</domain> <trust-anchors>
<certificates src="@raw/my_ca"/> </trust-anchors> <pin-set expiration="2018-01-01"> <pin digest="SHA-256">7HIpa...BCoQYcRhJ3Y=</pin> <!-- backup pin --> <pin digest="SHA-256">fwza0...gO/04cDM1oE=</pin> </pin-set> </domain-config> </network-security-config> CONFIGURE IT
INCLUDE YOUR CLIENTS IN THE PROCESS Keep them up-to-date Help
them understand risks and advise them Insist on updates and security patches
THINGS TO REMEMBER Use internal storage if applicable Encrypt data
Use HTTPS Pin certificates Be aware of the update cycle
ANDROID IS NOT SECURE
BUT YOU CAN MAKE IT LESS EASY TO ABUSE
REFERENCES • Gradle configuration • http://developer.android.com/guide/topics/data/data- storage.html#db • https://codahale.com/how-to-safely-store-a-password/ •
http://www.developereconomics.com/android- cryptography-tools-for-beginners/ • https://www.airpair.com/android/posts/adding- tampering-detection-to-your-android-app
REFERENCES • https://www.ssllabs.com/ • http://developer.android.com/preview/features/security- config.html • https://www.ionic.com/mitm-attacks-ssl-pinning-what- is-it-and-why-you-should-care/
REFERENCES • Android fingeprint security • Infinum security articles •
Infinum Android newsletter • Keeping secrets in a Vault
Thank you! Visit www.infinum.co or find us on social networks:
infinum.co infinumco infinumco infinum
[email protected]
@ABAOTIC


 abaotic
 trickart
 kishikawakatsumi
 shoppingjaws
 kenjiyoneyama
 irinanazarova
 panda728
 tomokon
 takaidohigasi
 448jp
 akkeylab
 reimaru
 monolithic_adam
 tammielis
 aleyda
 gurzu
 palkan
 morganepeng
 jonoalderson
 katarinadahlin
 apolaine
 techseoconnect
 samlambert
 addyosmani














![APP LINKING HTTPS://DOMAIN[:OPT_PORT]/.WELL-KNOWN/ASSETLINKS.JSON [{ "relation": ["delegate_permission/common.handle_all_urls"], "target": { "namespace": "android_app",](https://files.speakerdeck.com/presentations/89c19c3081874b5598210ea1bb71fde2/slide_53.jpg)