Share
Embed
DevSecOops - Stories of DevSecOps Failures and Success
Abhay Bhargav
November 15, 2020
Transcript
78 slides
-
Copyright © we45 2020 DevSecOops! Stories of DevSecOps Failures and
Success Abhay Bhargav -
Copyright © we45 2020 abhaybhargav Yours Truly • Founder @
we45 • Chief Architect - Orchestron • AppSec Automation Junkie • Trainer/Speaker at DEF CON, BlackHat, OWASP Events, etc world-wide • Lead Trainer - we45 Training and Workshops • Co-author of Secure Java For Web Application Development • Author of PCI Compliance: A Definitive Guide -
abhaybhargav we45 Today… • Stories. Inspired by Real-Life Events •
Problems of varied size, scale and complexity • Compressed into a single scenario for ease of understanding -
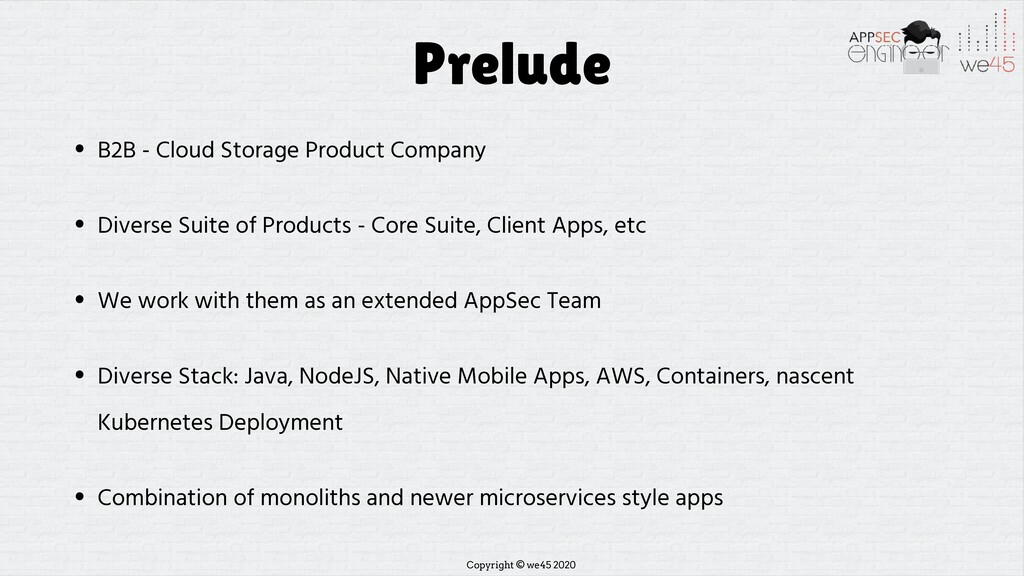
Copyright © we45 2020 Prelude • B2B - Cloud Storage
Product Company • Diverse Suite of Products - Core Suite, Client Apps, etc • We work with them as an extended AppSec Team • Diverse Stack: Java, NodeJS, Native Mobile Apps, AWS, Containers, nascent Kubernetes Deployment • Combination of monoliths and newer microservices style apps -
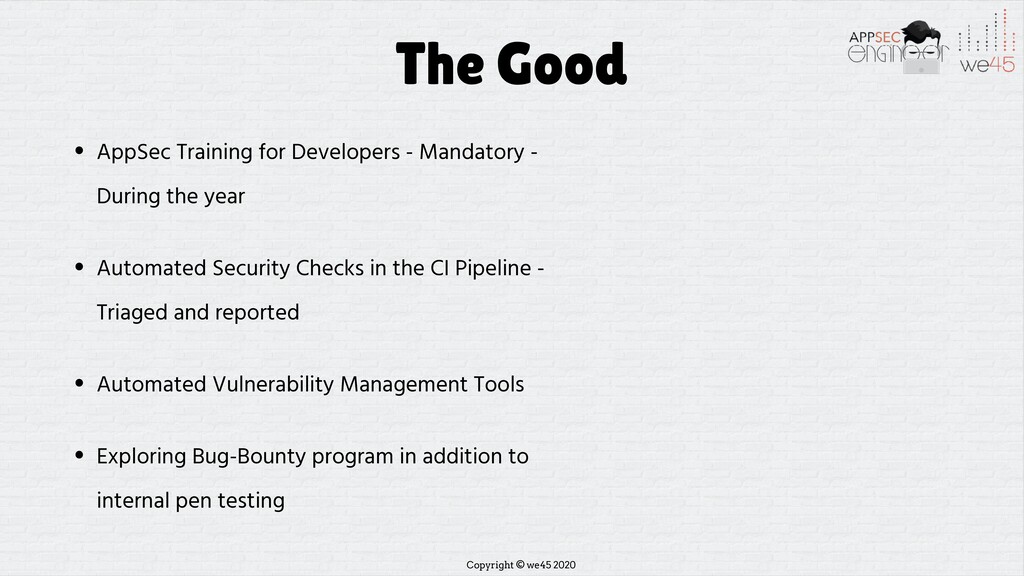
Copyright © we45 2020 The Good • AppSec Training for
Developers - Mandatory - During the year • Automated Security Checks in the CI Pipeline - Triaged and reported • Automated Vulnerability Management Tools • Exploring Bug-Bounty program in addition to internal pen testing -
Copyright © we45 2020 The Good • AppSec Training for
Developers - Mandatory - During the year • Automated Security Checks in the CI Pipeline - Triaged and reported • Automated Vulnerability Management Tools • Exploring Bug-Bounty program in addition to internal pen testing -
Copyright © we45 2020 Problem “We’re finding a LOT of
the same issues again and again” -
Copyright © we45 2020 Breaking down the Problem 1. Similar
classes of AppSec issues cropping up across different products and services 2. Automated Checks in place - But Triaging and fixing would result in delays 3. Architectural Issues not identified soon enough - Resulting in (1) -
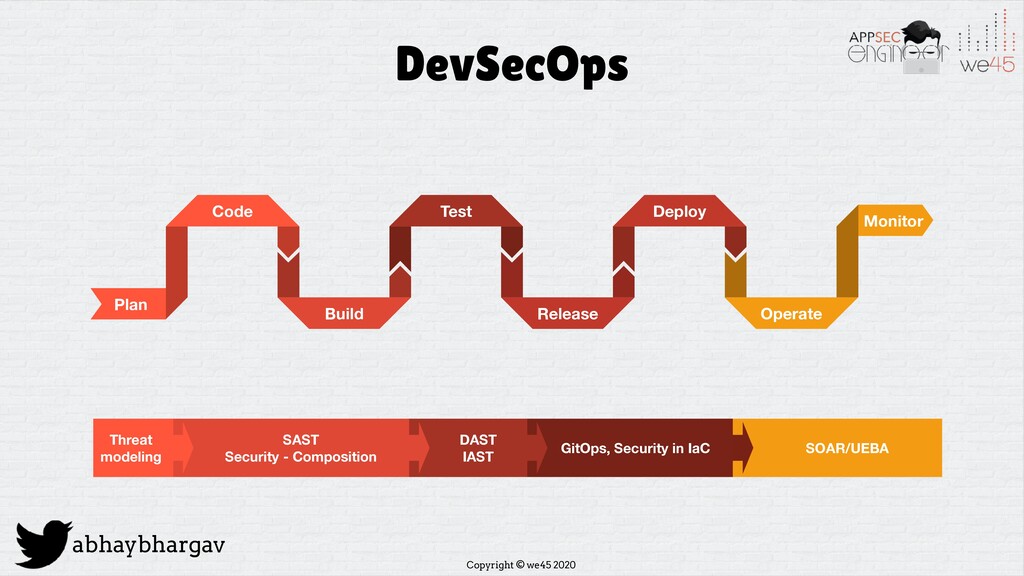
Copyright © we45 2020 abhaybhargav DevSecOps Plan Code Build Test
Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST GitOps, Security in IaC SOAR/UEBA -
Copyright © we45 2020 Developers are our Customers • Devs
have high pressure deadlines like the rest of us • Security being hard is likely to be Security NOT done • Happy Path: Security through HIGHER Dev Productivity -
Copyright © we45 2020 Which means… • Classifying and Baselining
Types of Security Bugs • Security Engineering - Secure Defaults • Better Security Training for Developers -
Copyright © we45 2020 Approach to Mitigation • Most Effective
& Scalable => Scalably Reducing Risk (Classes of Risk) • Effective NOT Scalable => Finding Individual Bugs • Baseline (Eliminate) the easy bugs -
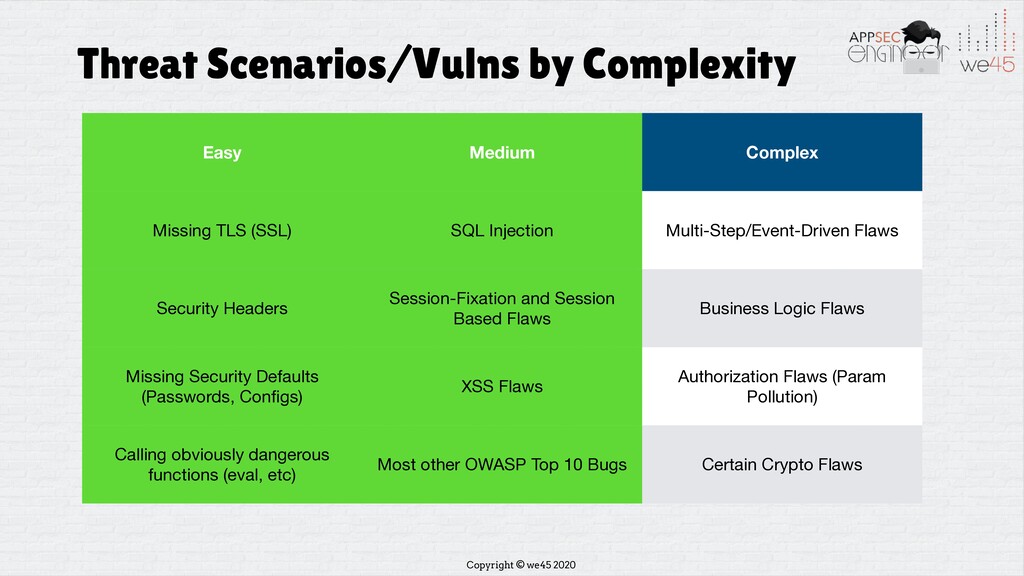
Copyright © we45 2020 Threat Scenarios/Vulns by Complexity Easy Medium
Complex Missing TLS (SSL) SQL Injection Multi-Step/Event-Driven Flaws Security Headers Session-Fixation and Session Based Flaws Business Logic Flaws Missing Security Defaults (Passwords, Configs) XSS Flaws Authorization Flaws (Param Pollution) Calling obviously dangerous functions (eval, etc) Most other OWASP Top 10 Bugs -
Copyright © we45 2020 Threat Scenarios/Vulns by Complexity Easy Medium
Complex Missing TLS (SSL) SQL Injection Multi-Step/Event-Driven Flaws Security Headers Session-Fixation and Session Based Flaws Business Logic Flaws Missing Security Defaults (Passwords, Configs) XSS Flaws Authorization Flaws (Param Pollution) Calling obviously dangerous functions (eval, etc) Most other OWASP Top 10 Bugs Certain Crypto Flaws -
Copyright © we45 2020 Tradeoffs? Safe:Easy • There’s easy ways
to achieve X for any developer • And there’s safe ways for a developer to achieve X • The objective is to make the safe way, as easy as possible -
Copyright © we45 2020 Sec Engineering: Secure Defaults • Falls
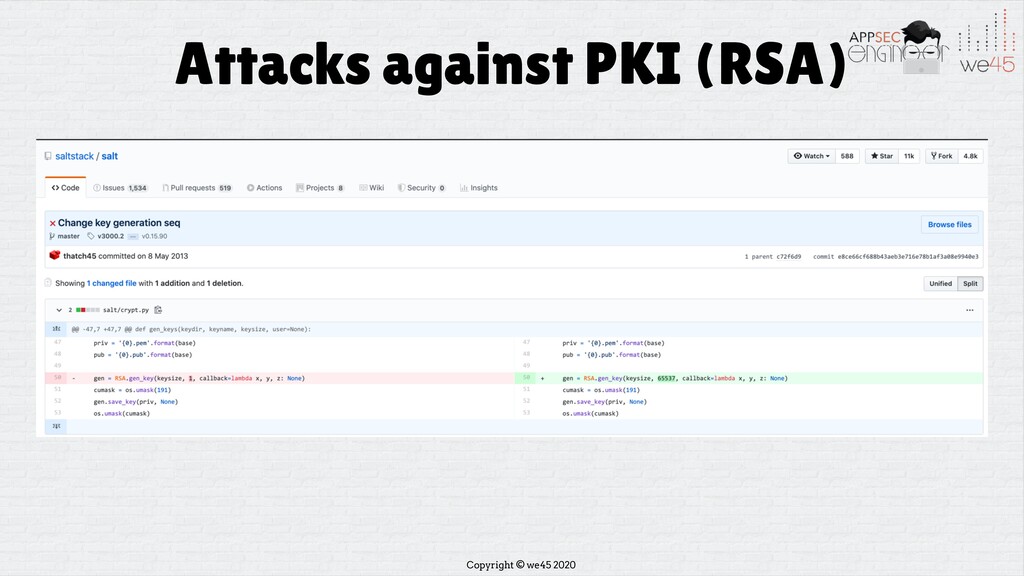
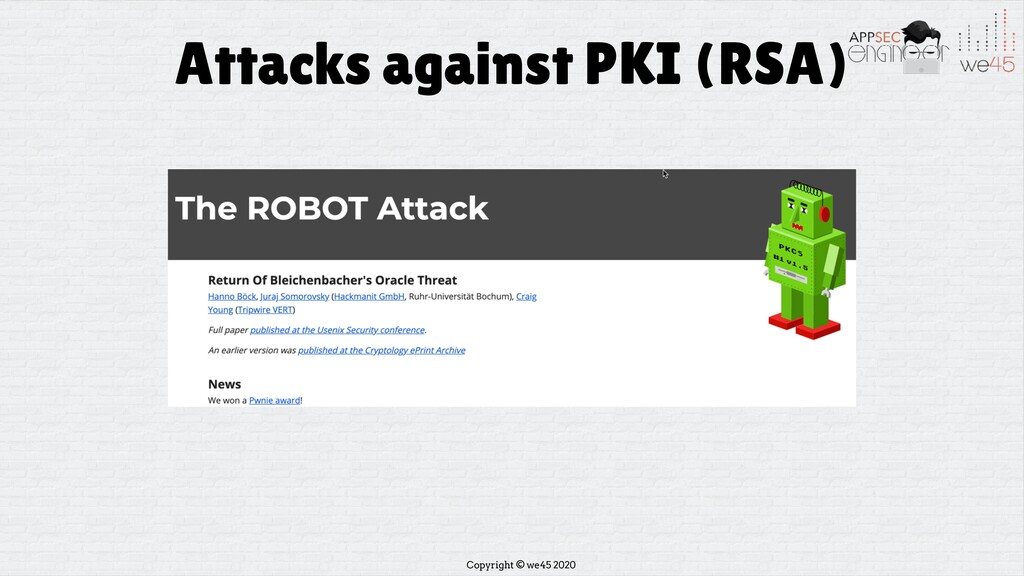
into the Bucket of Security Engineering • Idea is to default to secure behavior rather than teaching folks, complex ways to create secure behavior • Has seen lots of success in: • Secrets and Crypto • Authentication/AuthZ • Injection and XSS -
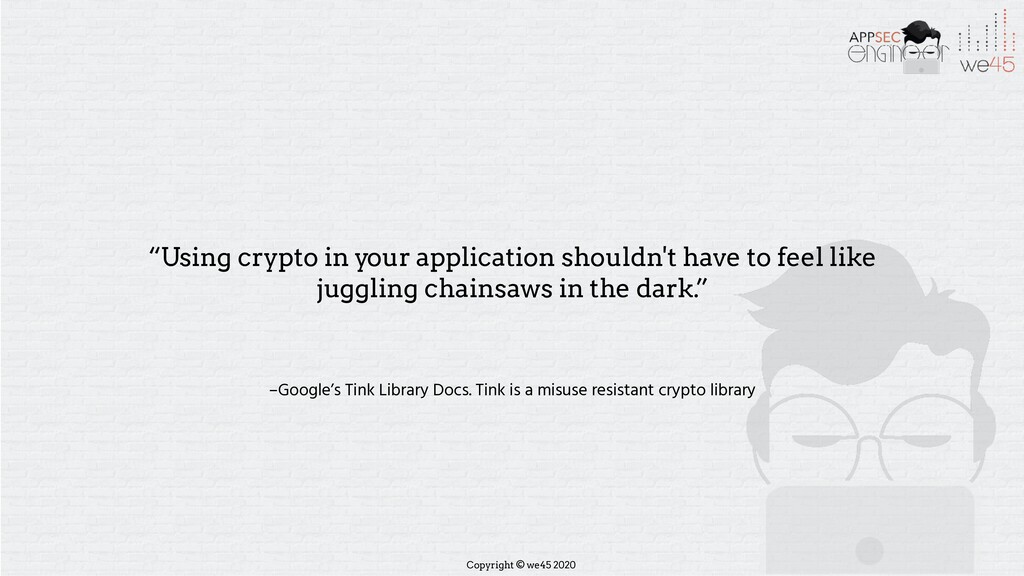
Copyright © we45 2020 –Google’s Tink Library Docs. Tink is
a misuse resistant crypto library “Using crypto in your application shouldn't have to feel like juggling chainsaws in the dark.” -
Copyright © we45 2020 Crypto - Secure Default • Misuse
Resistant • Strong Algos only • Strong padding techniques • Easy to use • No exposure to padding/nonces/IV • Secure by default Functions only • Explicit Insecure Modes only -
Copyright © we45 2020 Other examples of Secure Defaults •
Secure wrapper Libraries to existing Libraries with insecure defaults • Secure-By-Default Libraries and Frameworks • -
Copyright © we45 2020 Secure Defaults: Tooling • SAST rules
to identify use of insecure libraries • Personally love Semgrep, CodeQL for this • Lower false-positives when scanning for specific items -
Copyright © we45 2020 Examples of Feedback Loops • Closer
to Developer: IDE • Git hooks • Pull Requests -
Copyright © we45 2020 Decentralizing Security • Decentralized Security Libraries
and Frameworks: • Open-Policy-Agent • Casbin • -
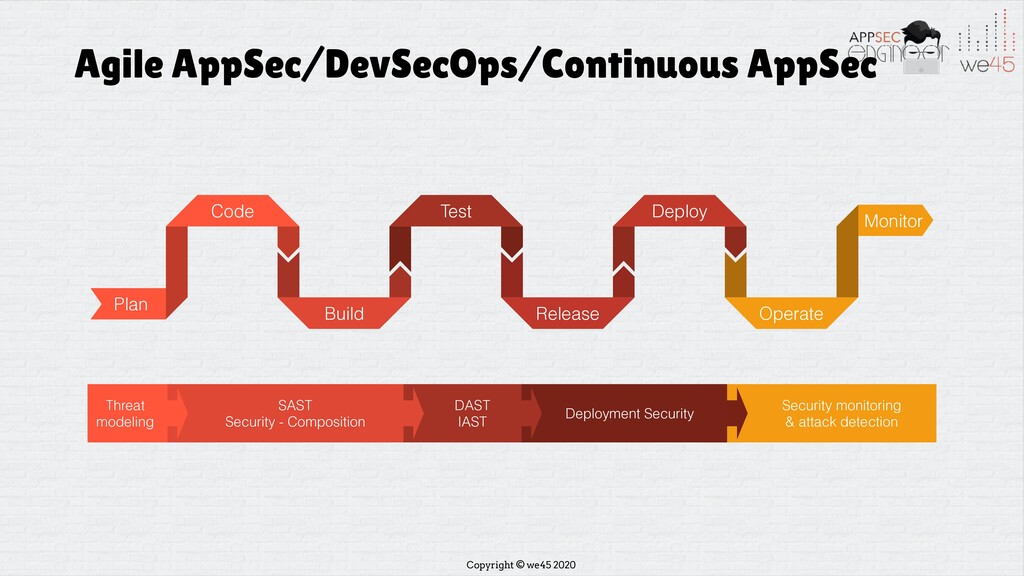
Copyright © we45 2020 Agile AppSec/DevSecOps/Continuous AppSec Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection -
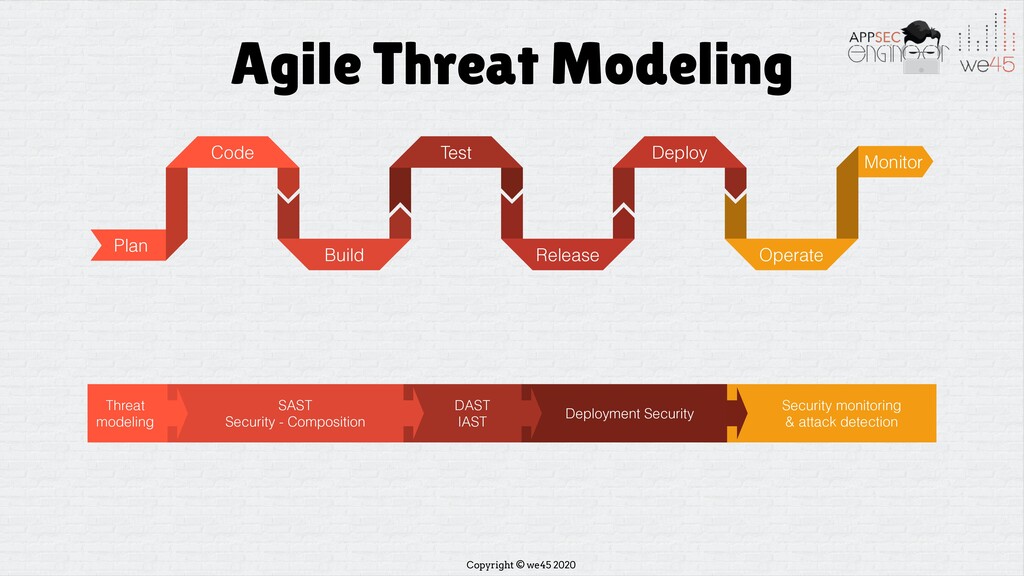
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection -
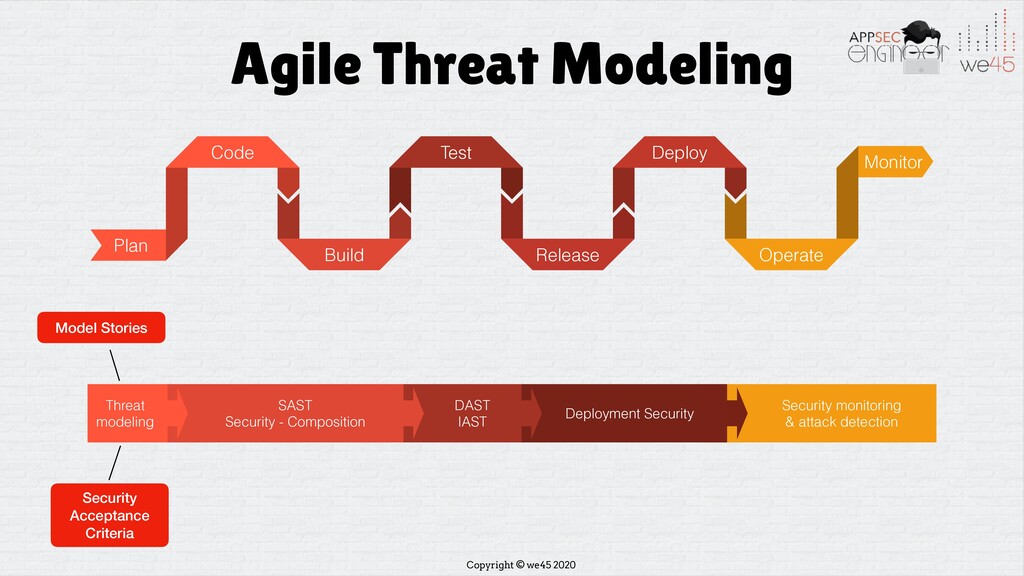
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories -
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories Security Acceptance Criteria -
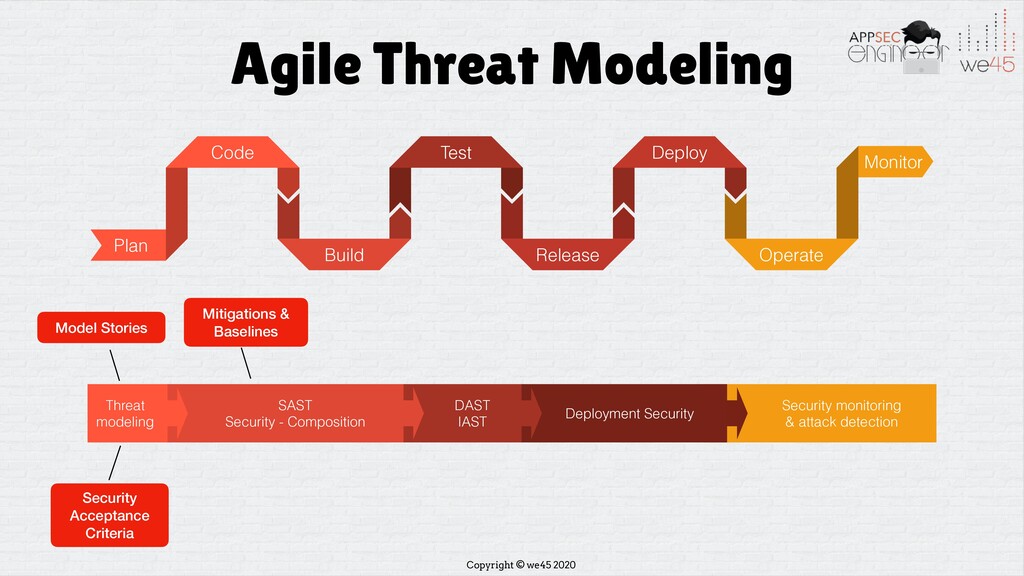
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories Security Acceptance Criteria Mitigations & Baselines -
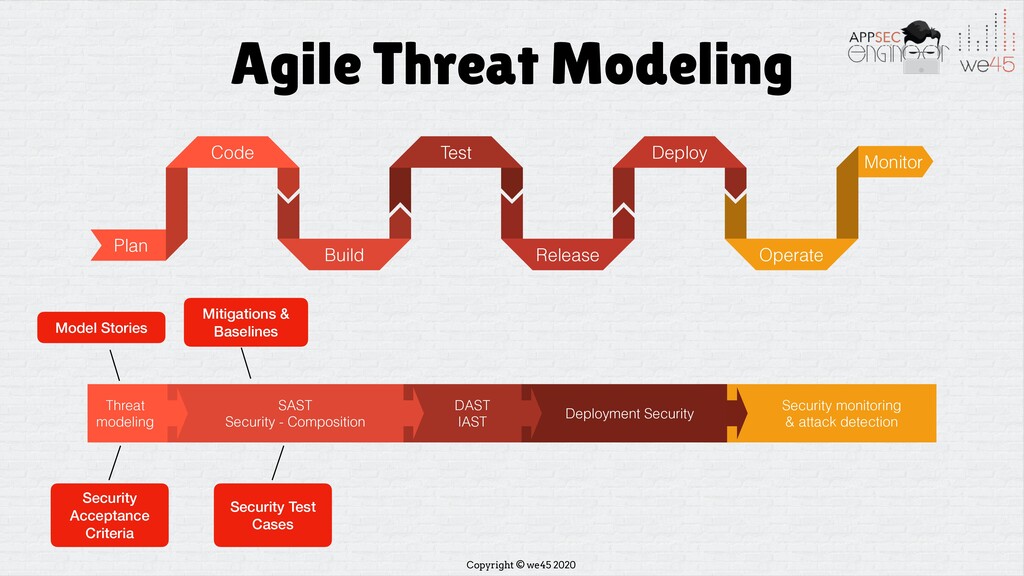
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories Security Acceptance Criteria Mitigations & Baselines Security Test Cases -
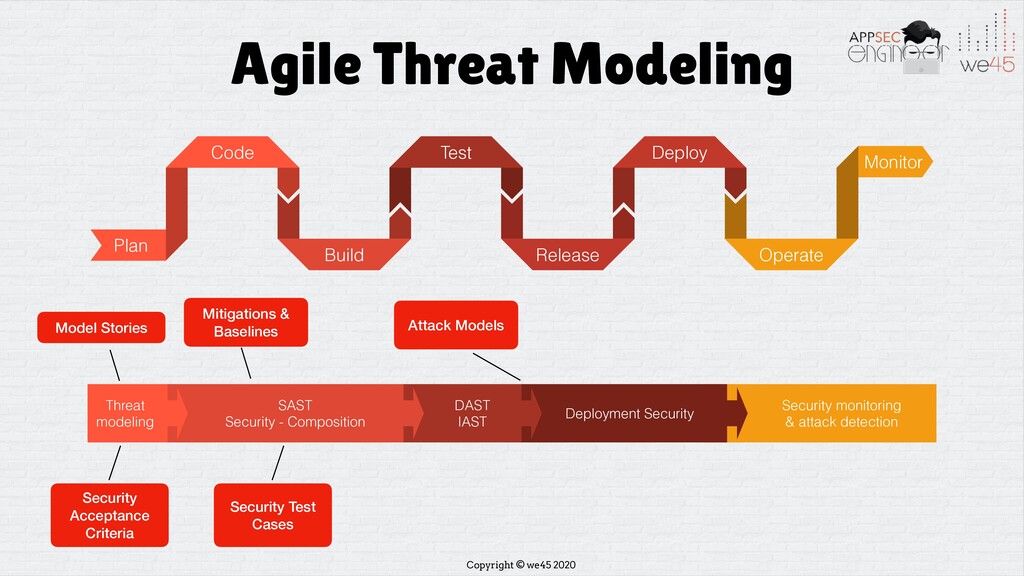
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories Security Acceptance Criteria Mitigations & Baselines Security Test Cases Attack Models -
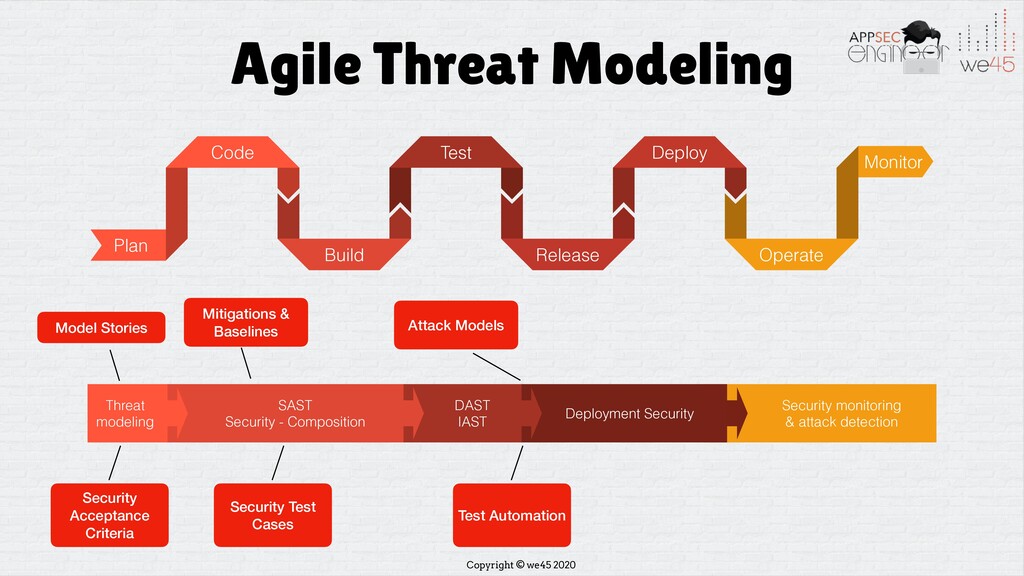
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories Security Acceptance Criteria Mitigations & Baselines Security Test Cases Attack Models Test Automation -
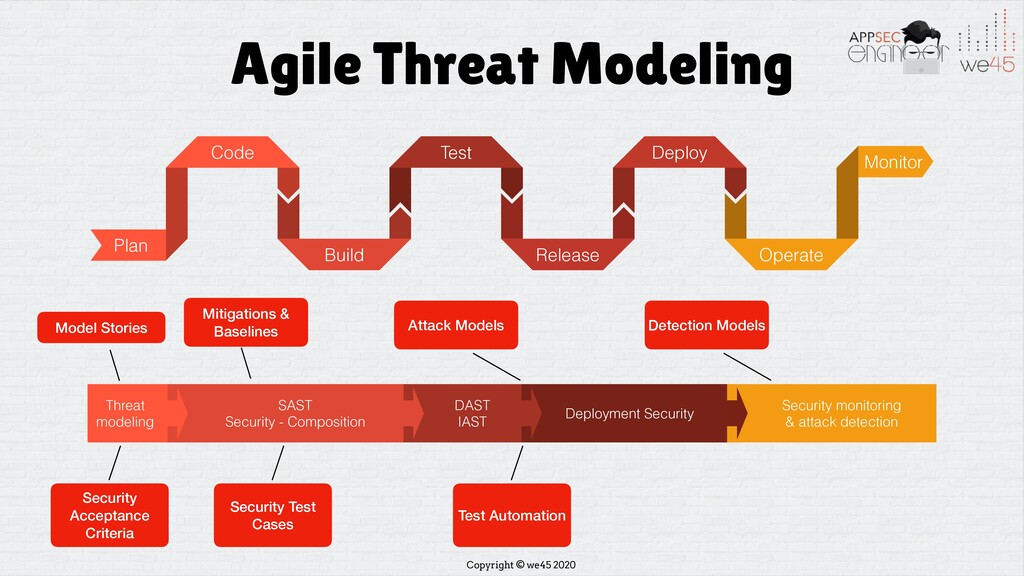
Copyright © we45 2020 Agile Threat Modeling Plan Code Build
Test Release Deploy Operate Monitor Threat modeling SAST Security - Composition DAST IAST Deployment Security Security monitoring & attack detection Model Stories Security Acceptance Criteria Mitigations & Baselines Security Test Cases Attack Models Test Automation Detection Models -
Copyright © we45 2020 Some Background • Story-Driven Threat Modeling
is threat modeling against user stories/ functionality definitions in the sprint. • The idea is to break threat modeling down by feature to produce useful, effective, yet efficient threat models • Not perfect, and still doesn’t negate the need for a system-wide threat model. But most effective in Agile Development -
Copyright © we45 2020 Pre-requisites • Cross-Functional Team running the
Threat Model • Leave your egos at the door • Run in Sprint Planning Meeting • Consider multi-stage approach -
Copyright © we45 2020 Success Factors • Focus on “Good-enough”
Threat Models • Keep the feature in scope - don’t dwell too outside of it • Cross-Functional Team • Just enough Information -
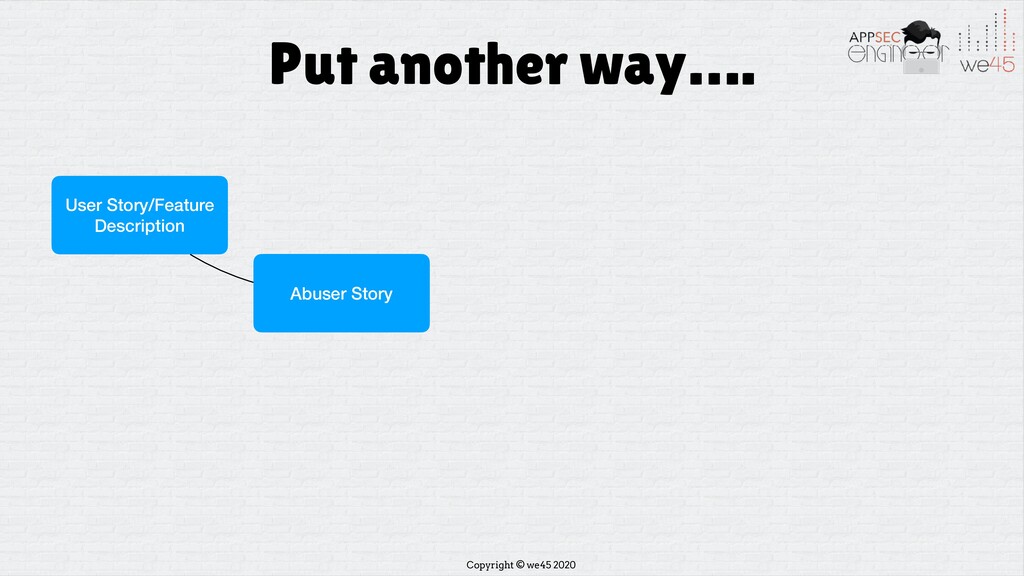
Copyright © we45 2020 Put another way…. User Story/Feature Description
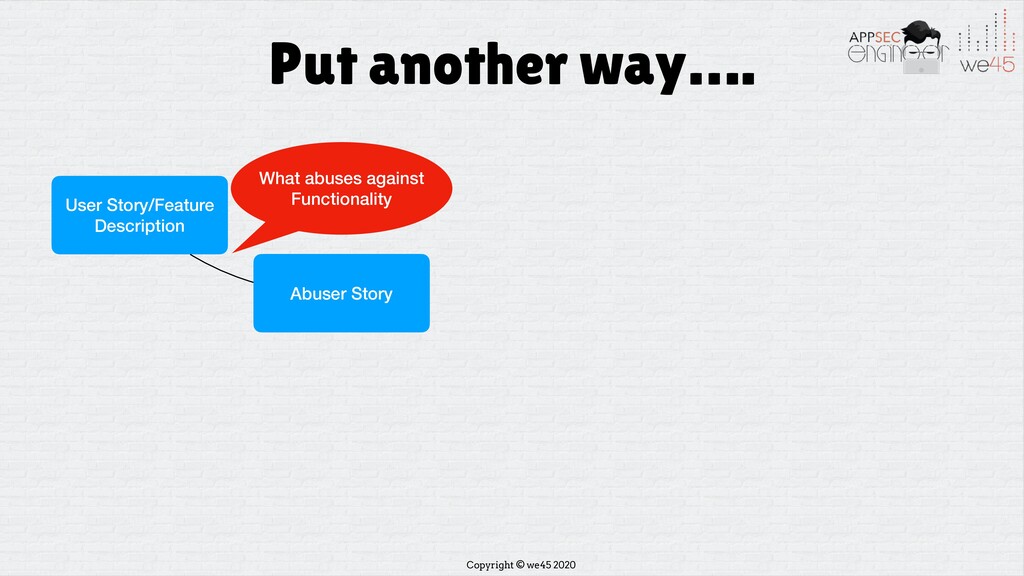
Abuser Story What abuses against Functionality -
Copyright © we45 2020 Put another way…. User Story/Feature Description
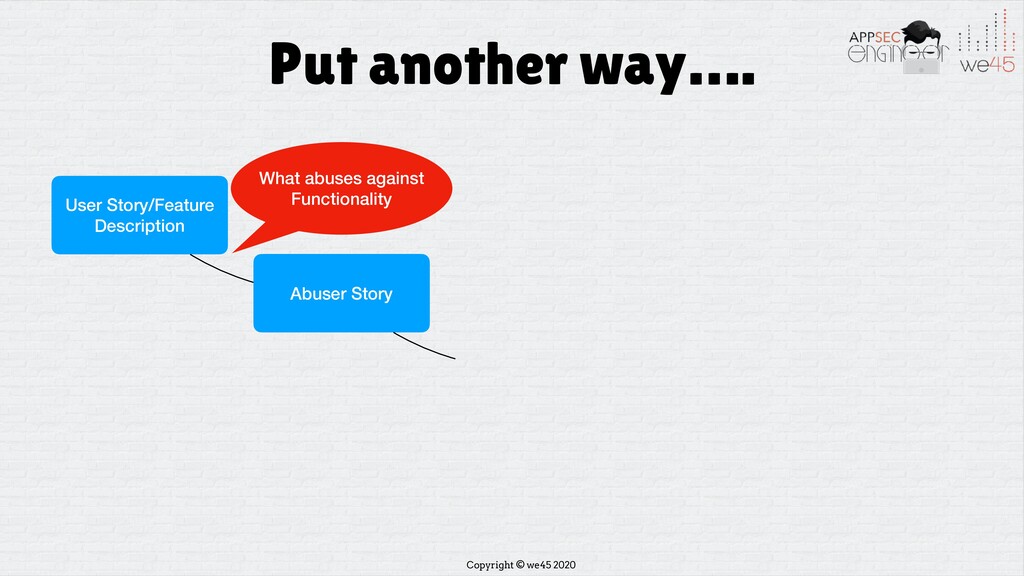
Abuser Story What abuses against Functionality -
Copyright © we45 2020 Put another way…. User Story/Feature Description
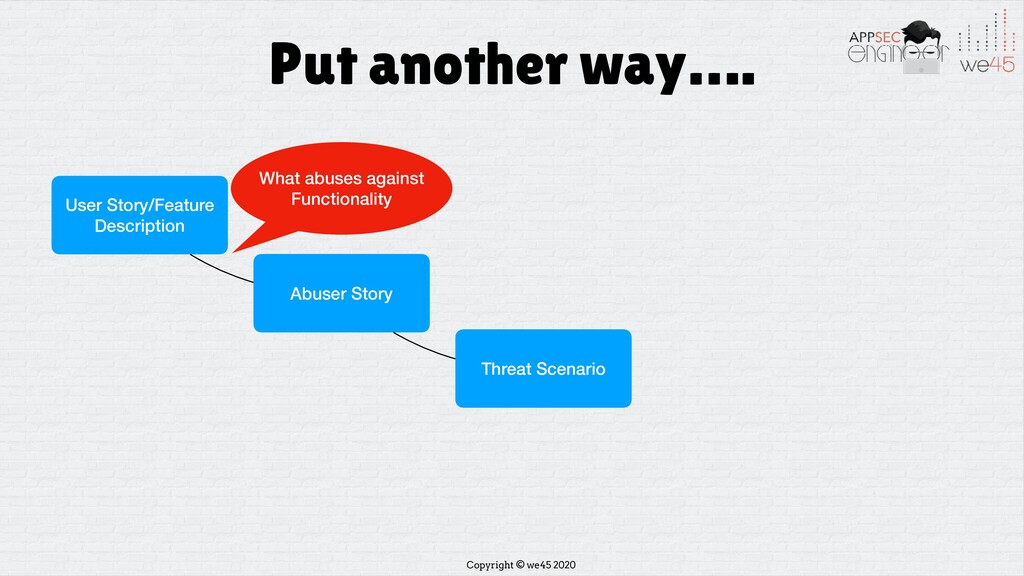
Abuser Story Threat Scenario What abuses against Functionality -
Copyright © we45 2020 Put another way…. User Story/Feature Description
Abuser Story Threat Scenario What abuses against Functionality How Abuse comes to life -
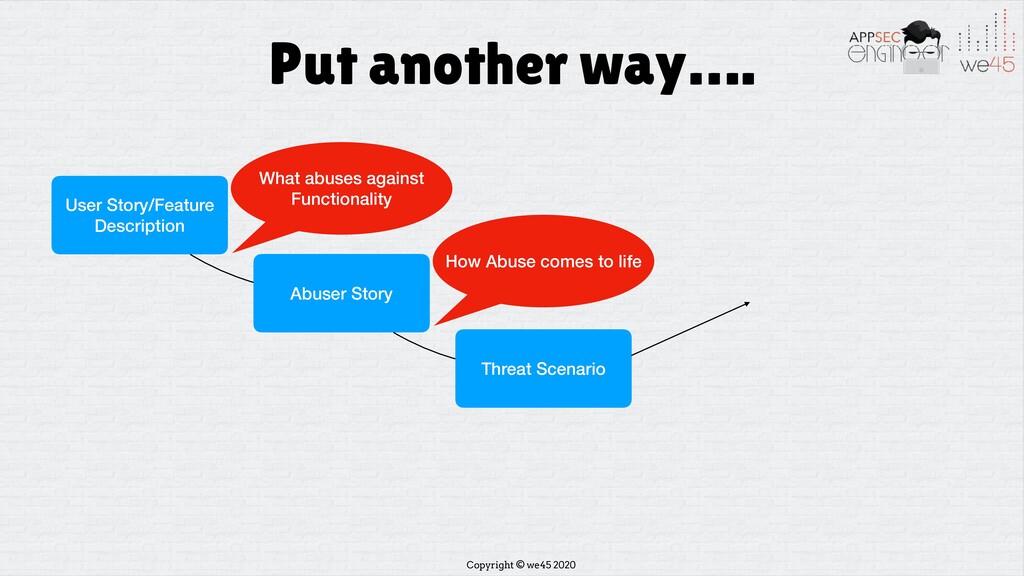
Copyright © we45 2020 Put another way…. User Story/Feature Description
Abuser Story Threat Scenario What abuses against Functionality How Abuse comes to life -
Copyright © we45 2020 Put another way…. User Story/Feature Description
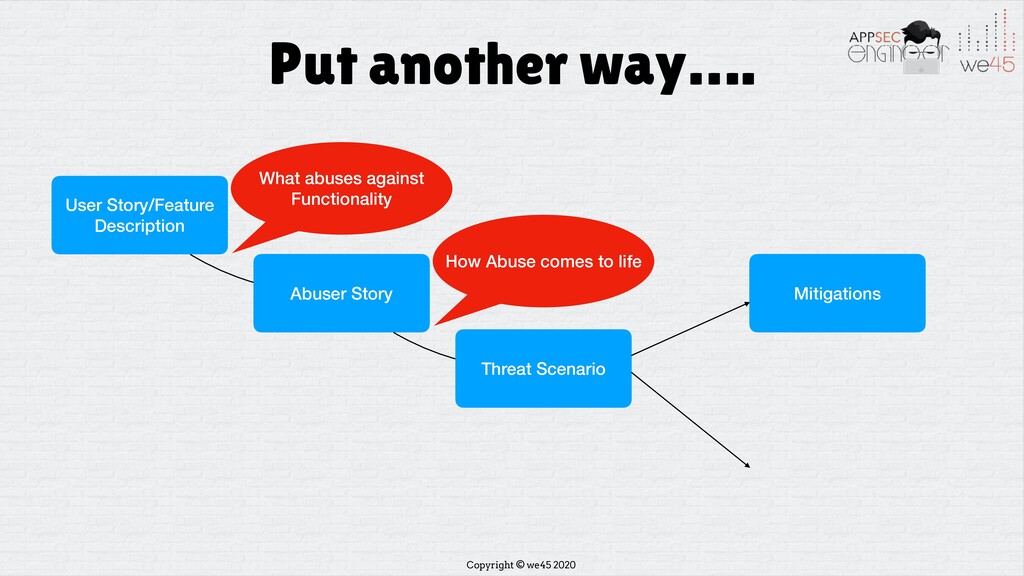
Abuser Story Threat Scenario What abuses against Functionality How Abuse comes to life Mitigations -
Copyright © we45 2020 Put another way…. User Story/Feature Description
Abuser Story Threat Scenario What abuses against Functionality How Abuse comes to life Mitigations -
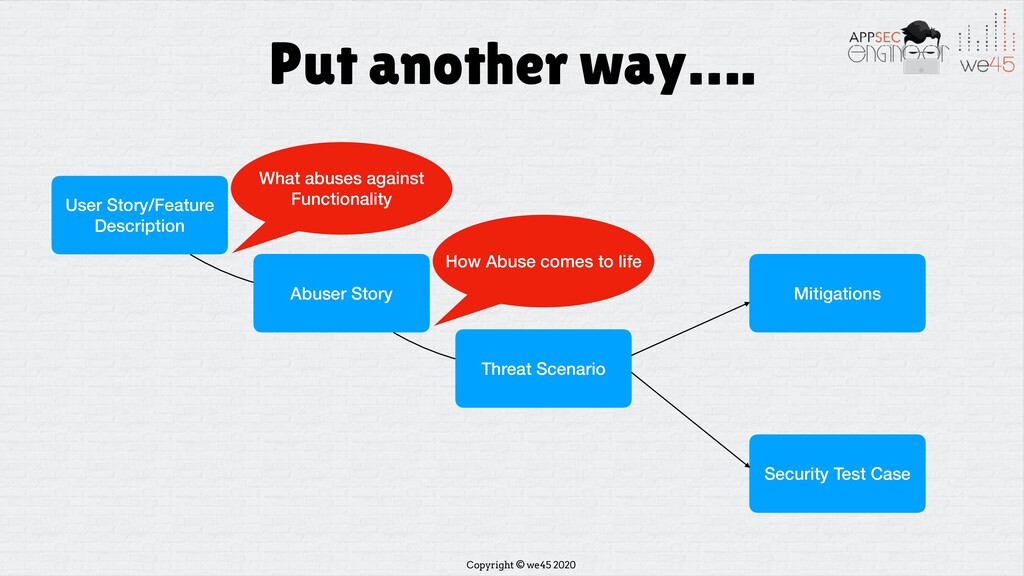
Copyright © we45 2020 Put another way…. User Story/Feature Description
Abuser Story Threat Scenario What abuses against Functionality How Abuse comes to life Mitigations Security Test Case