My presentation about Android Secure Elements and StrongBox as presented at droidcon Lisbon 2026 on October 20, 2026.
Intro
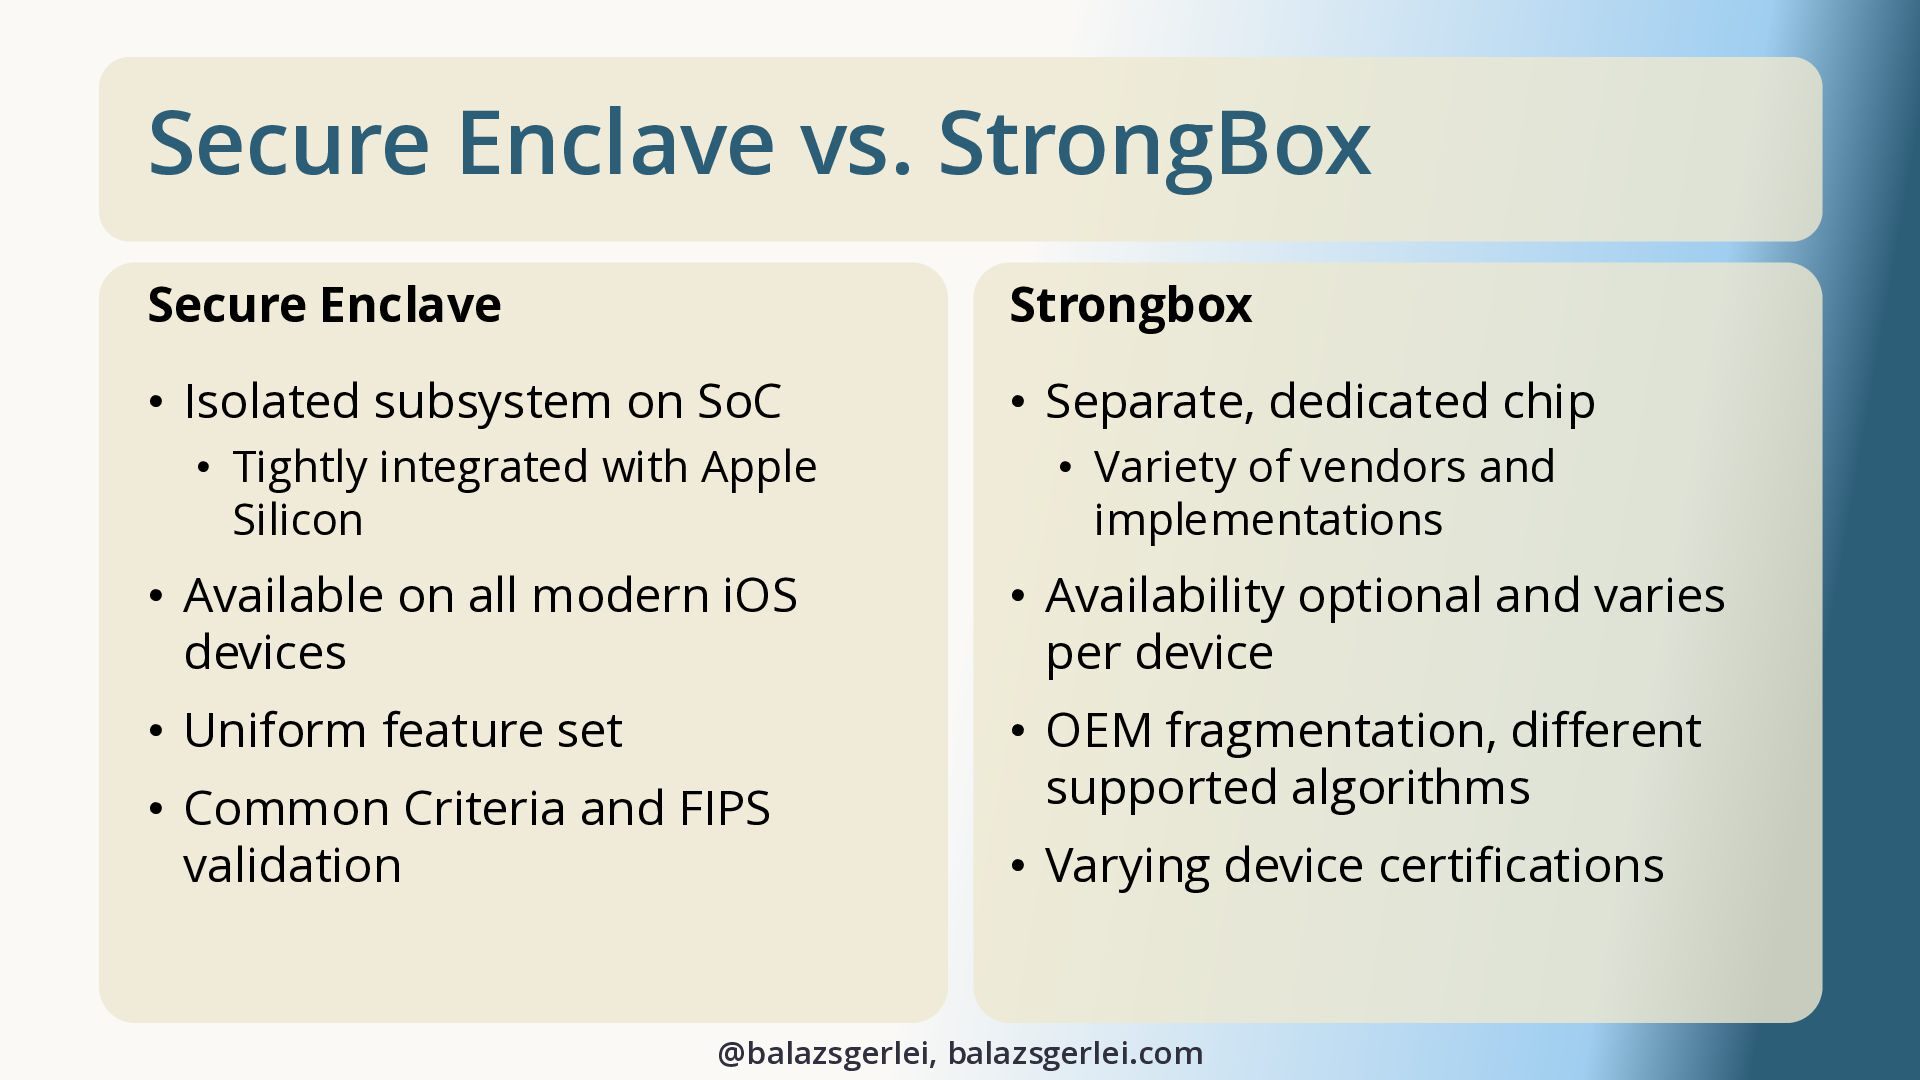
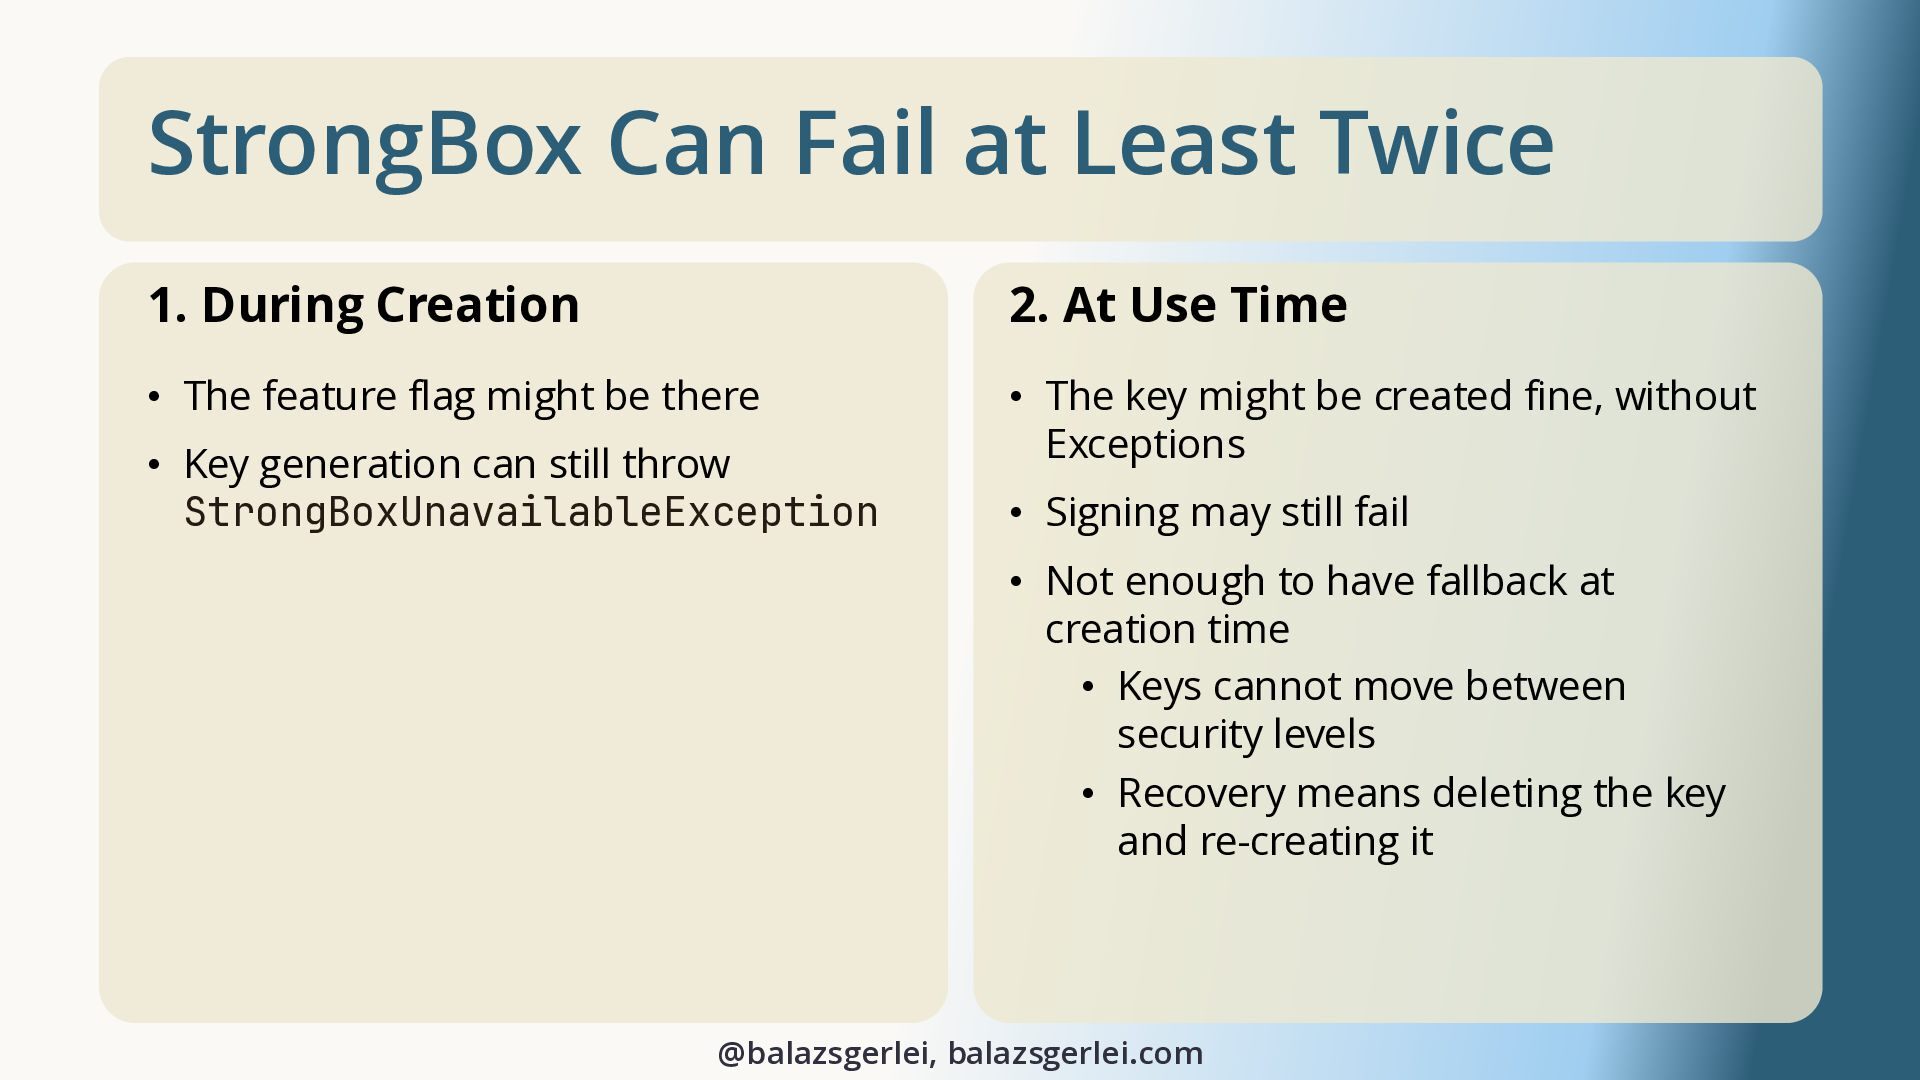
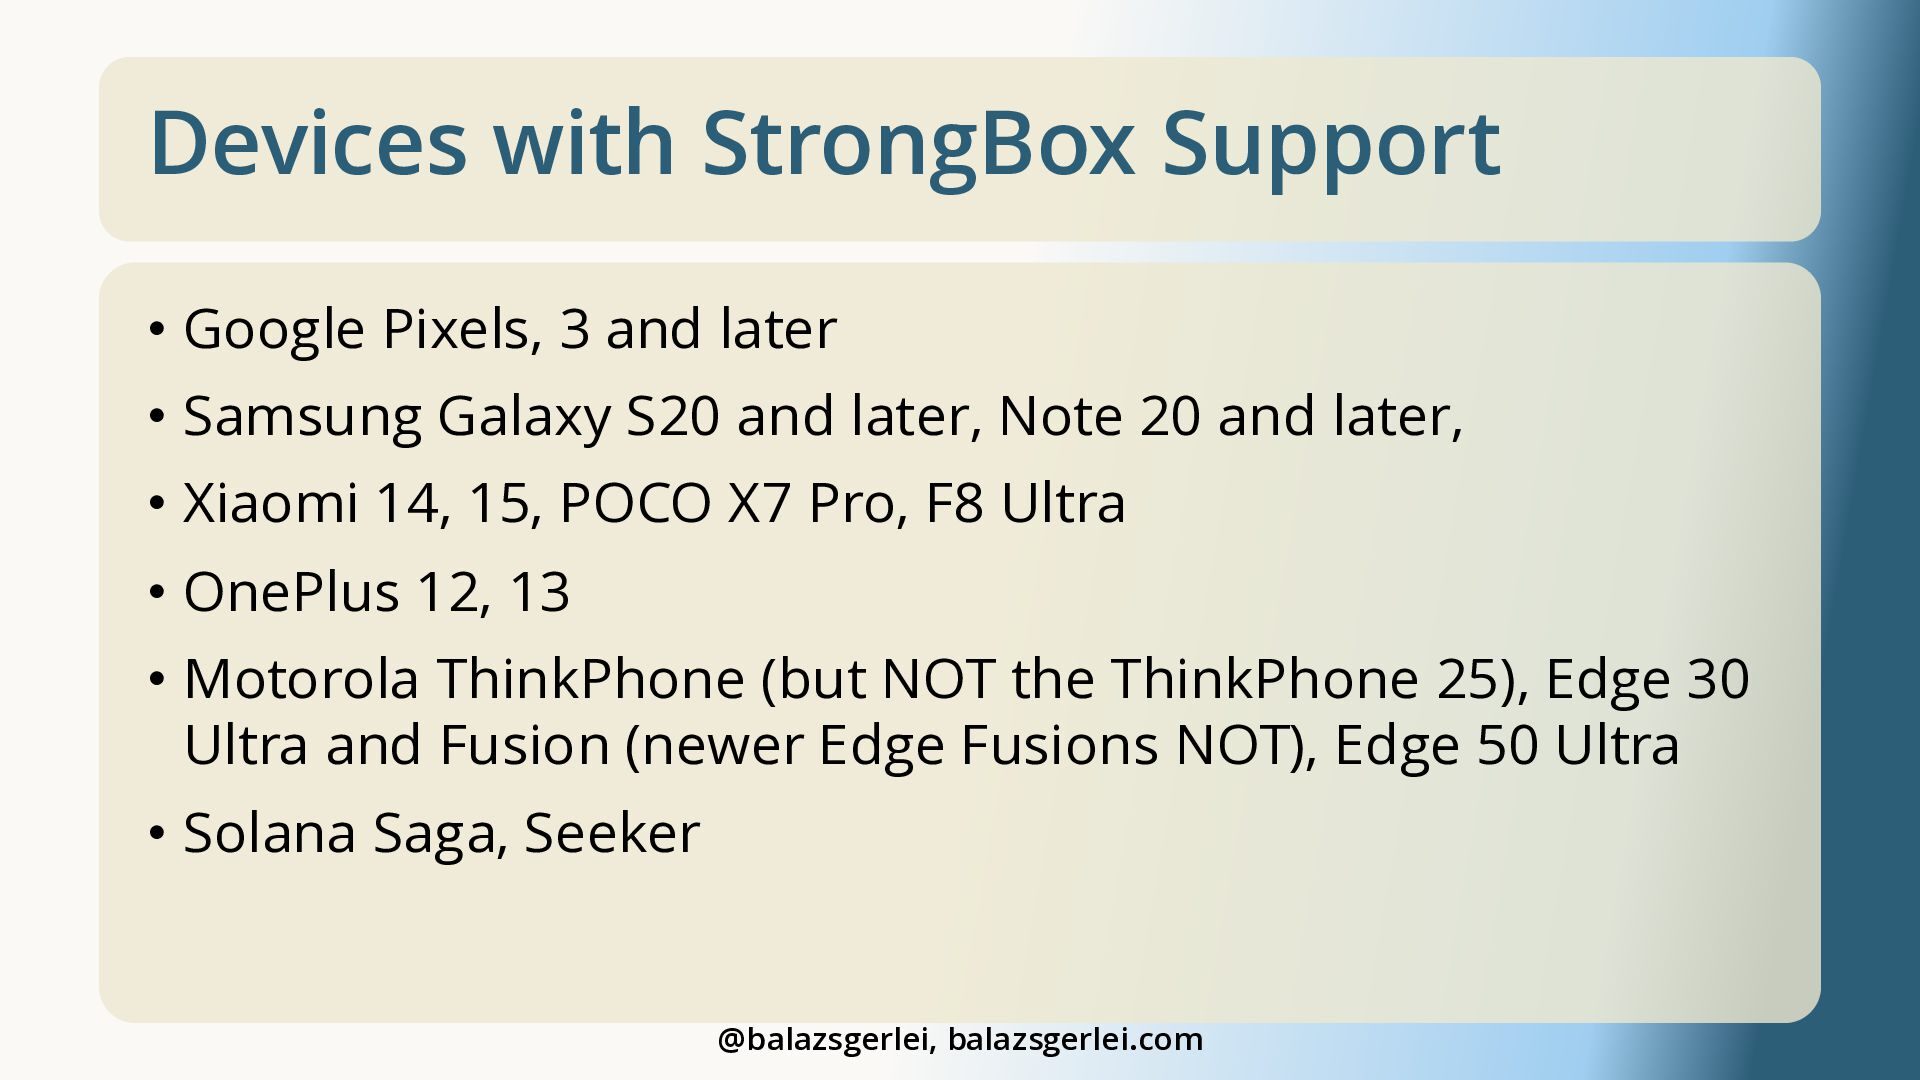
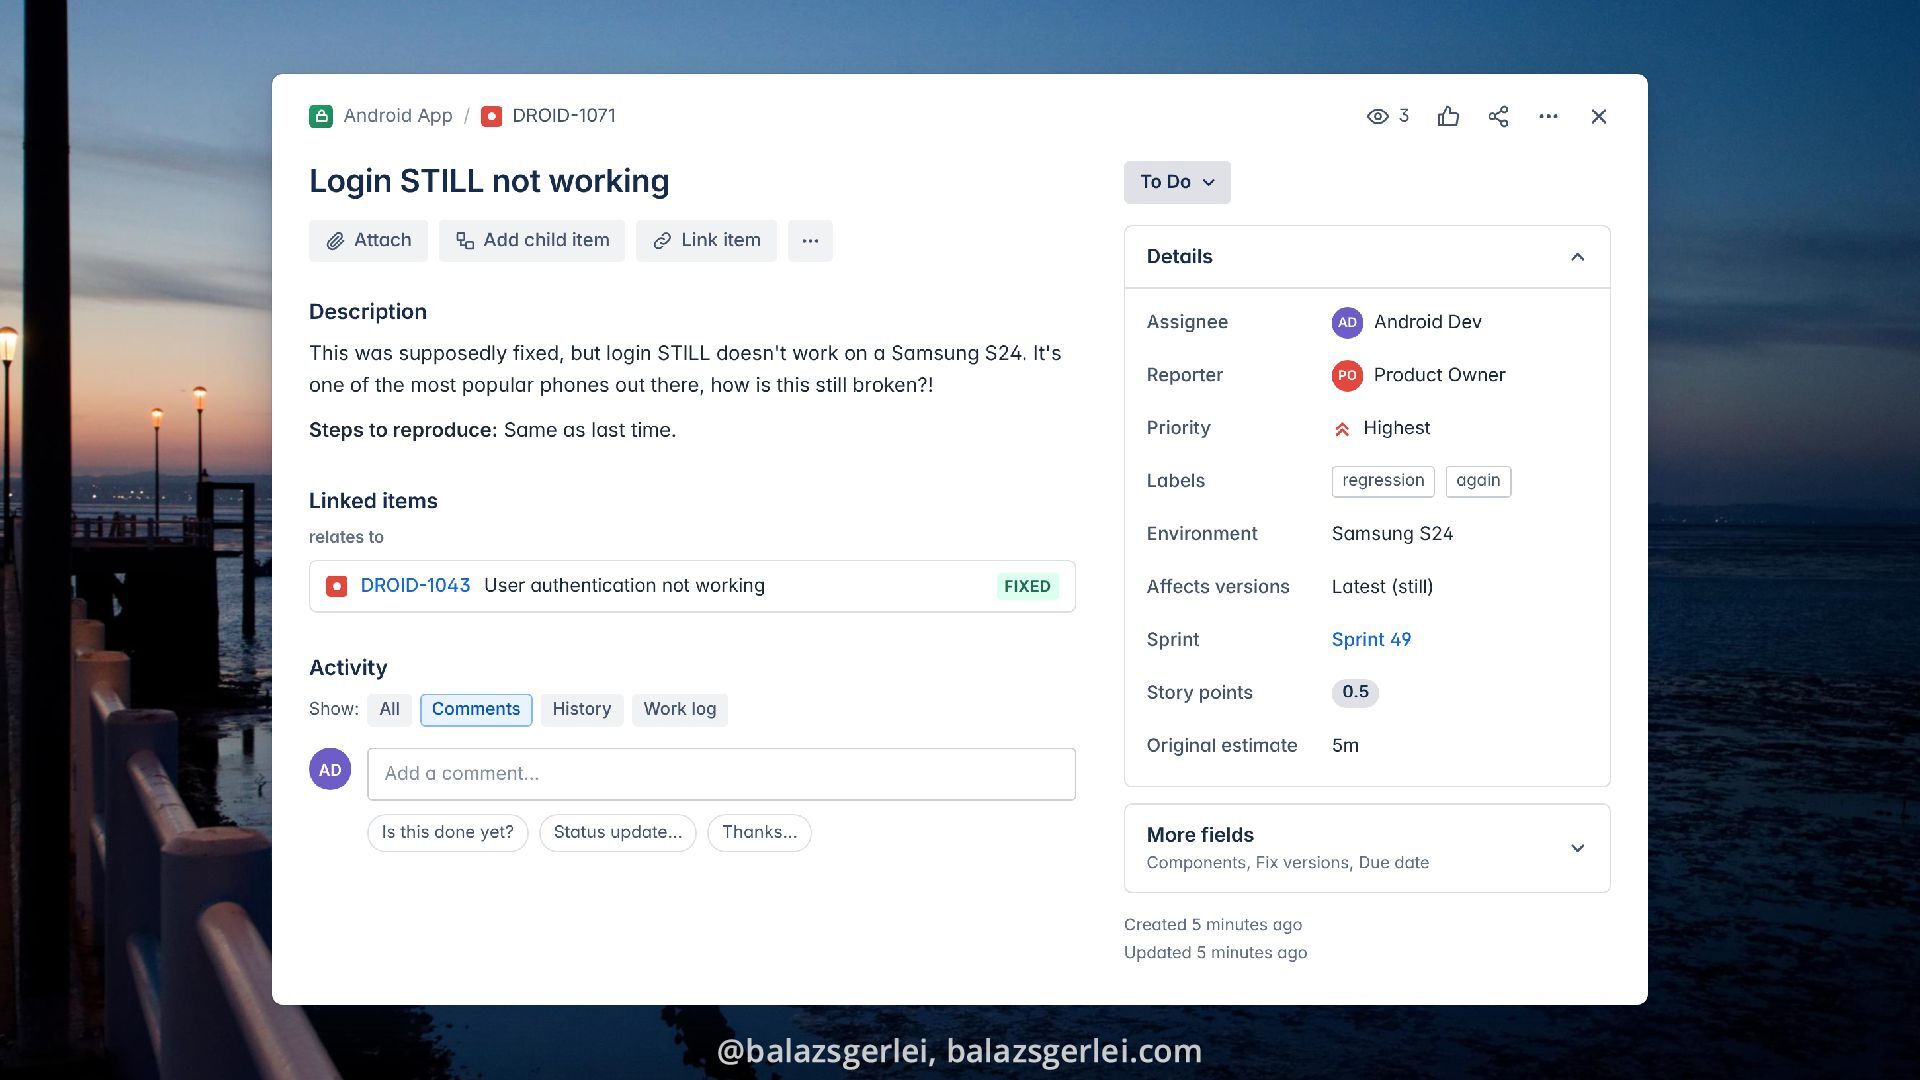
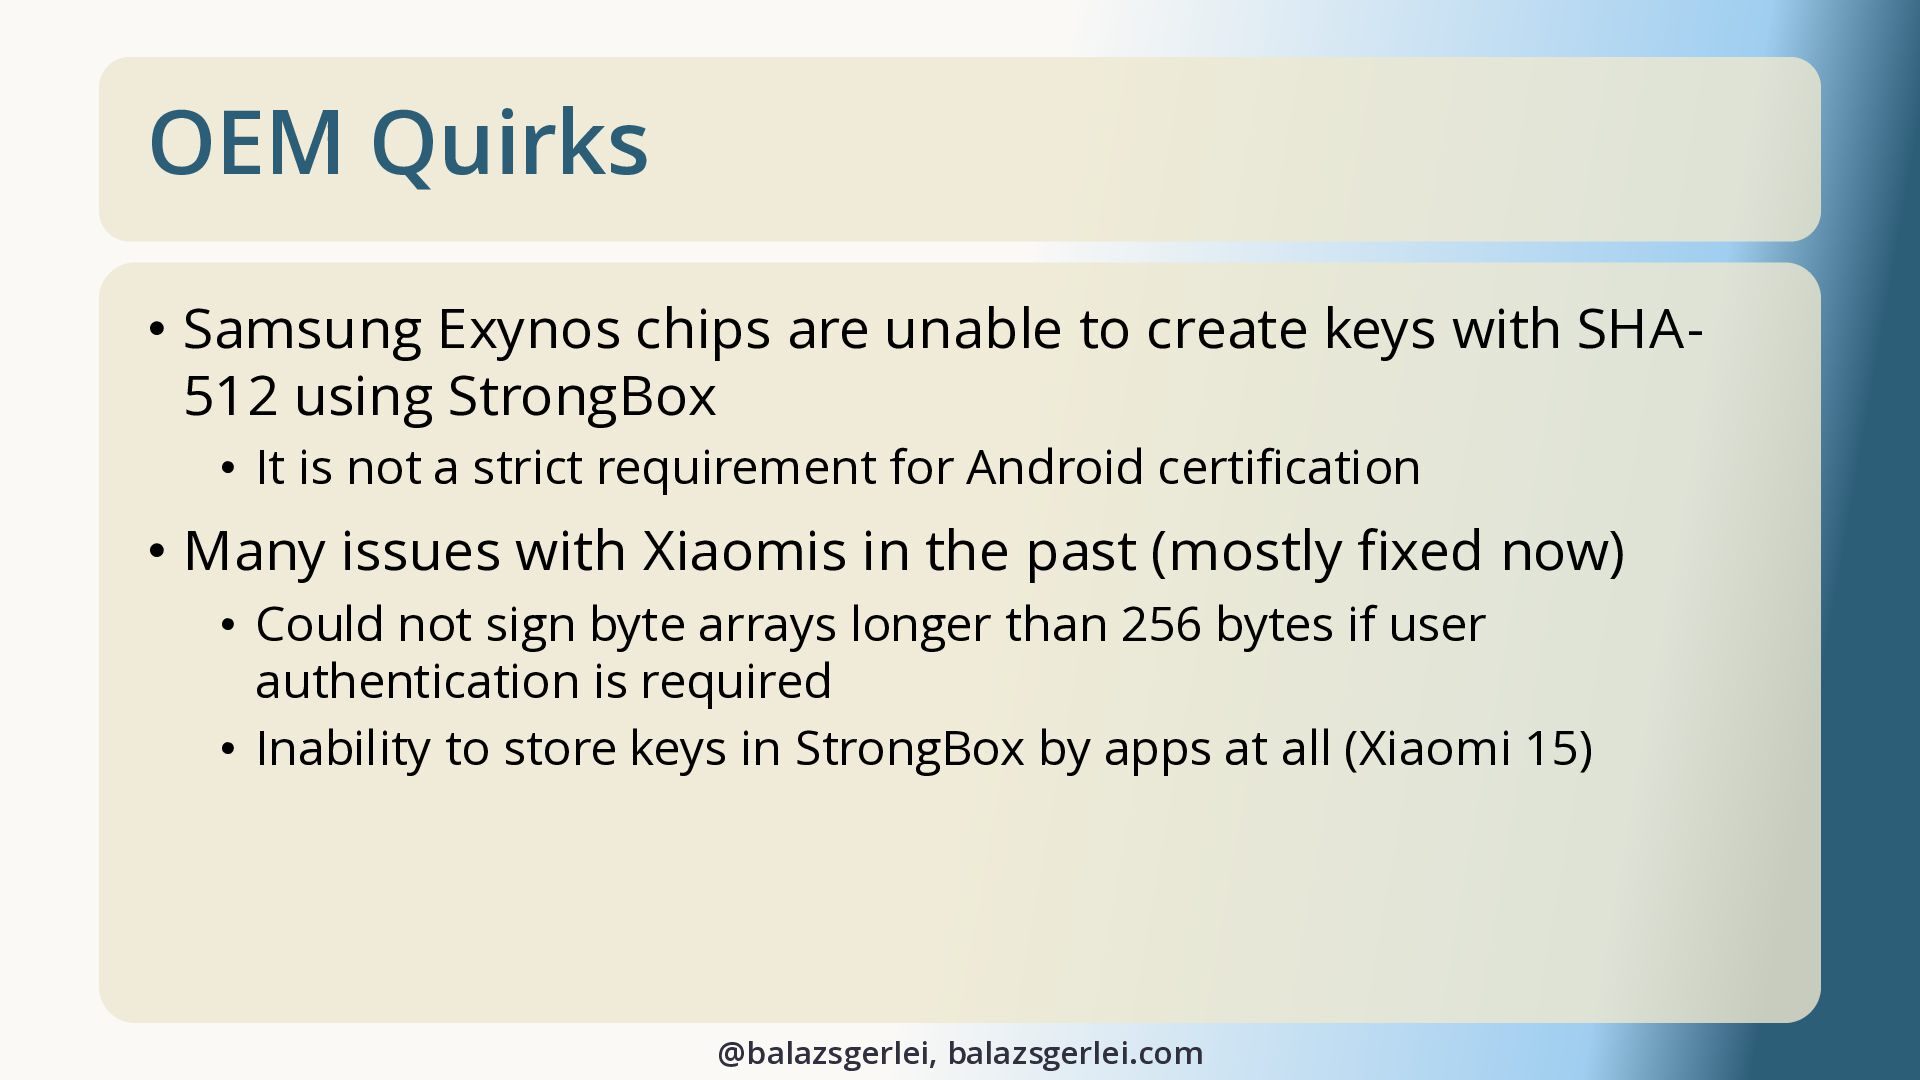
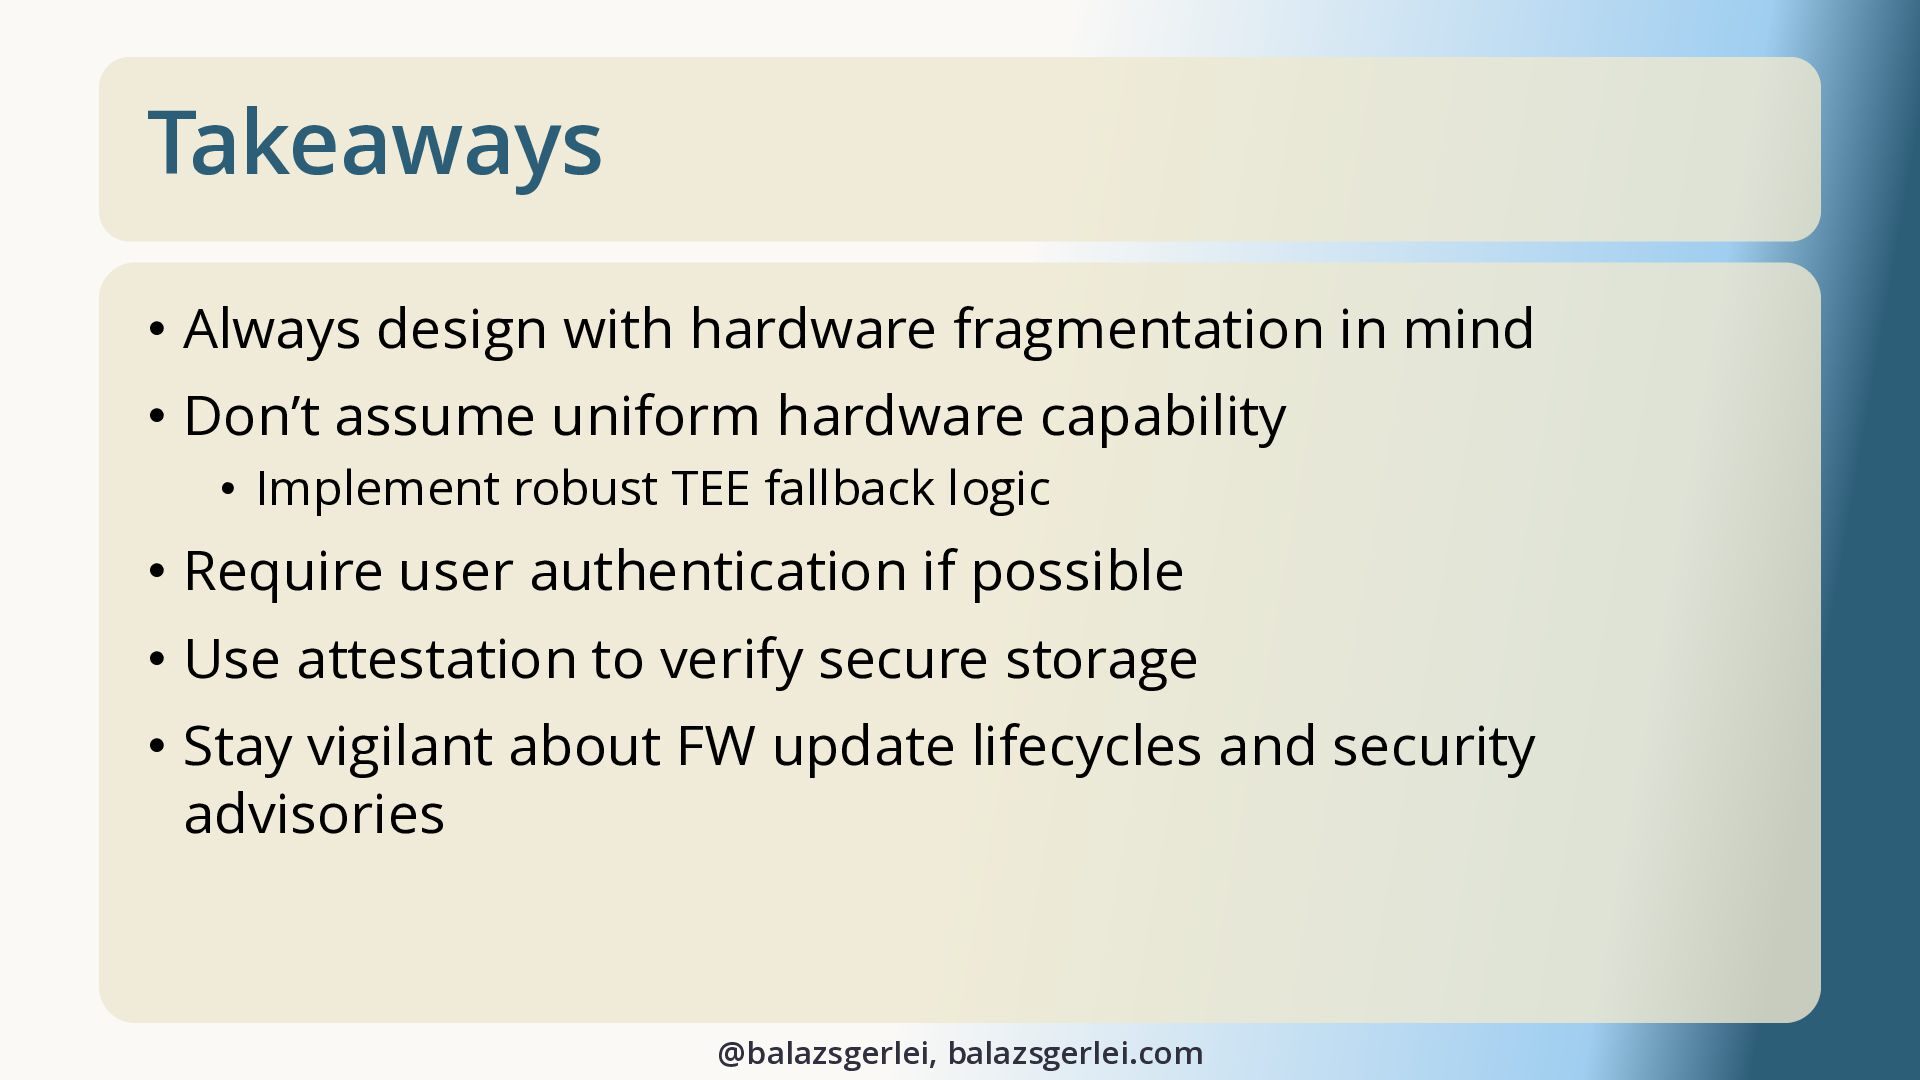
Ever since working on security-sensitive apps, there's been one topic I couldn’t avoid: secure key management. I'm glad to see hardware-backed Keystore and StrongBox adopted more beyond Pixel devices, but reality is full of vendor-specific bugs and quirks (e.g., Exynos only supports SHA-256). Users blame you when they can authenticate with a fingerprint elsewhere but not in your app.
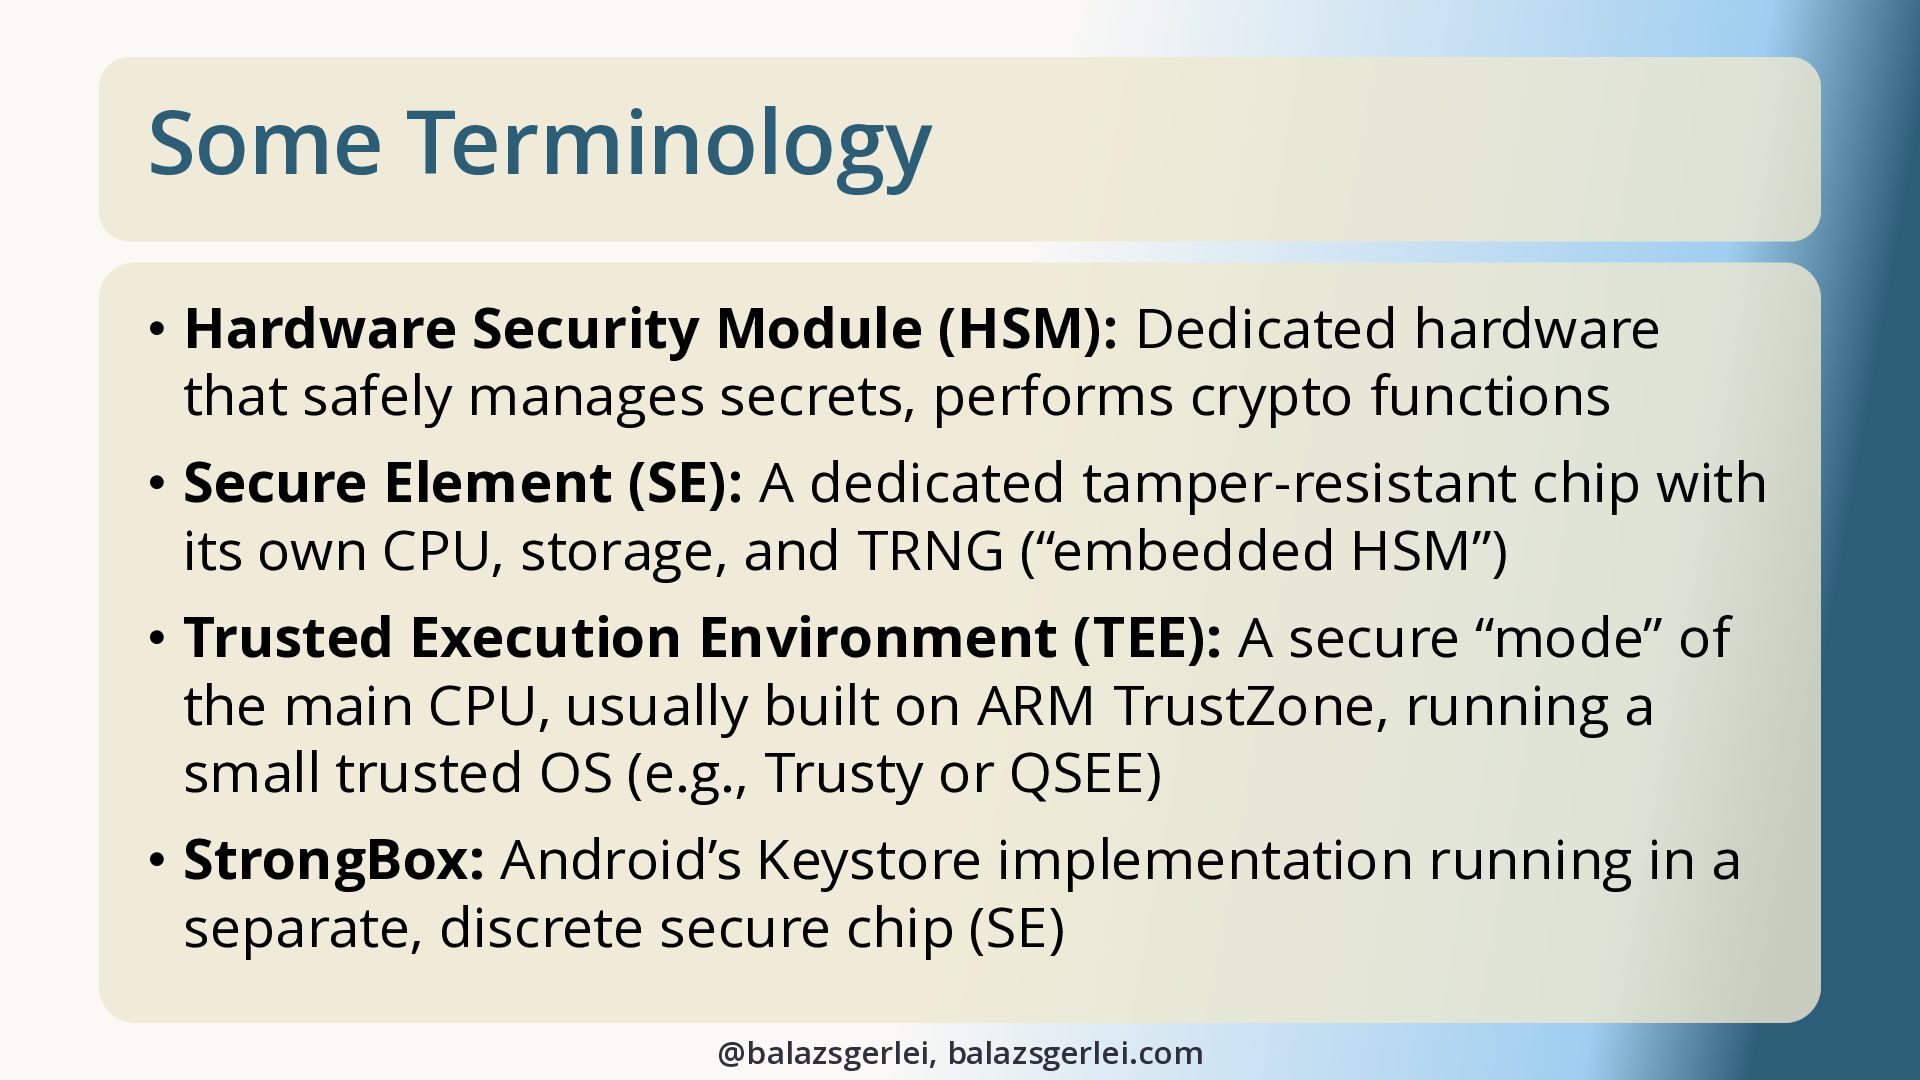
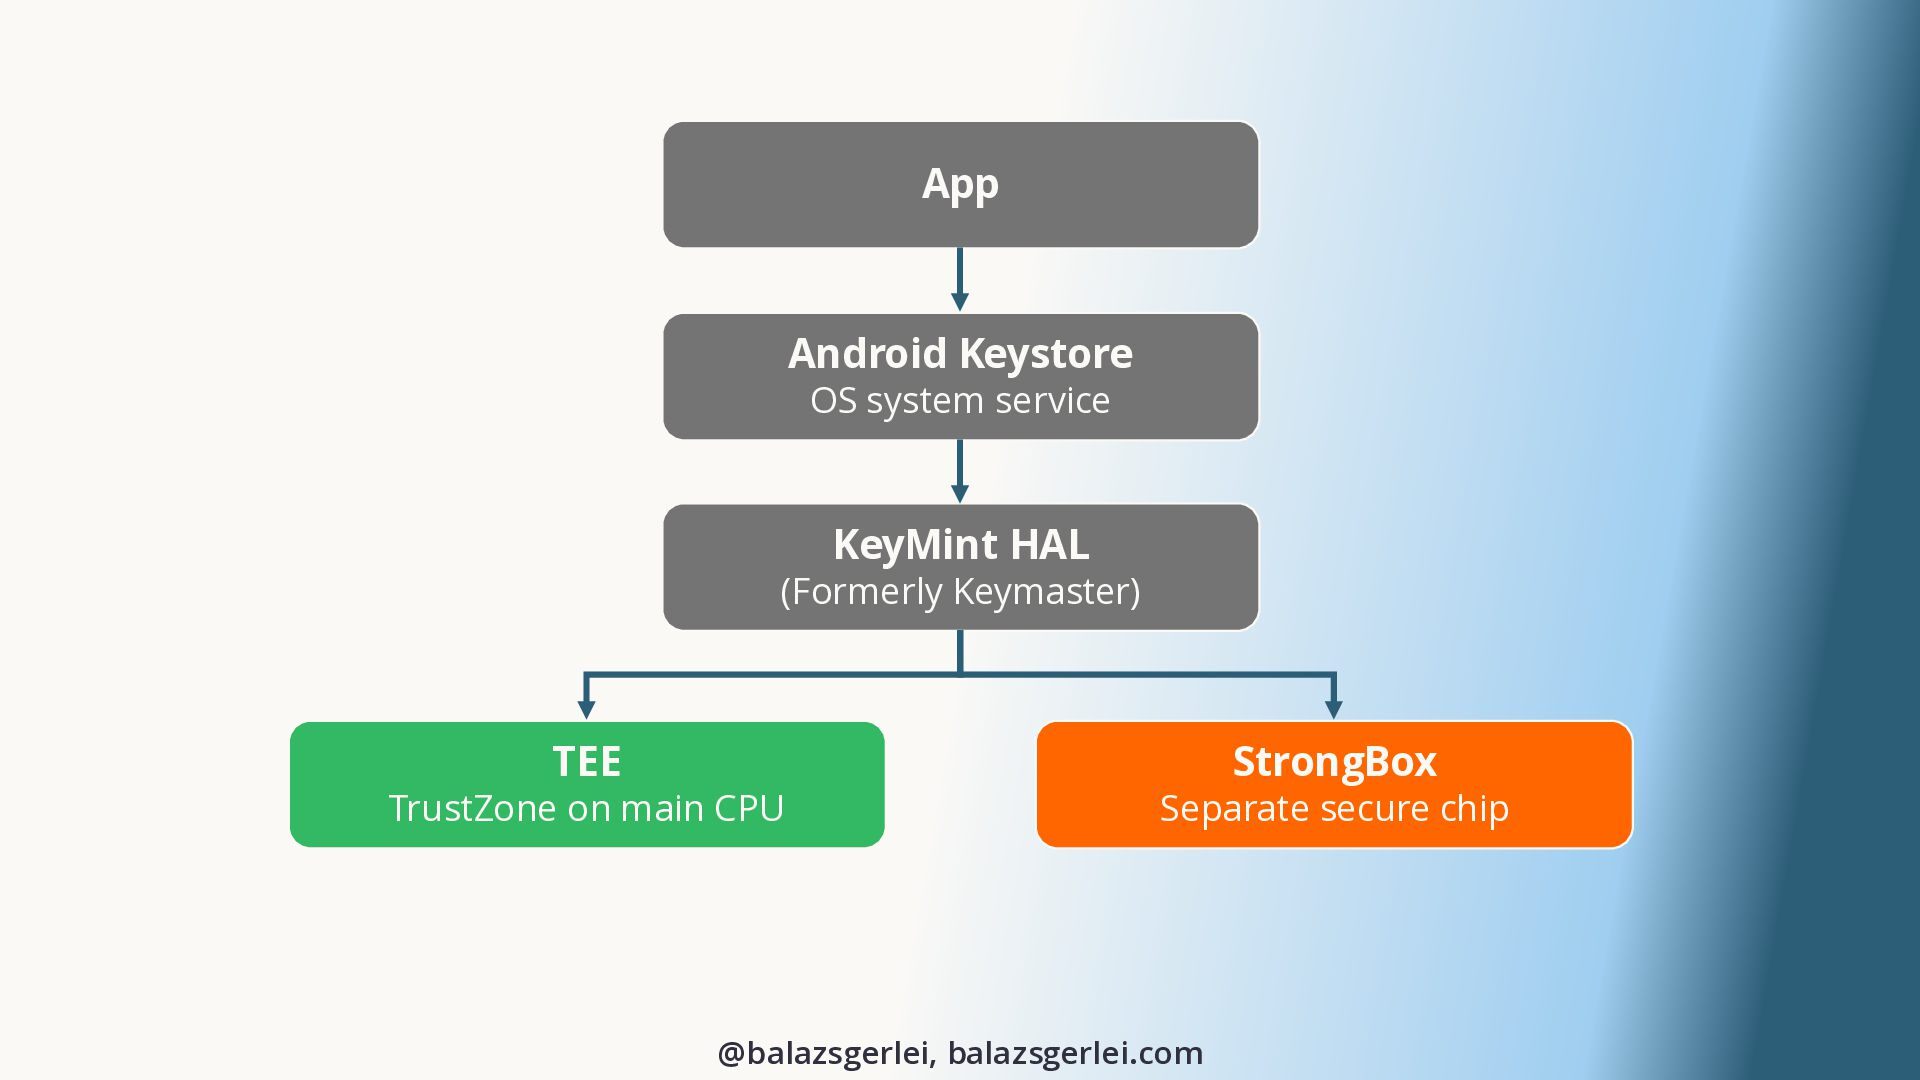
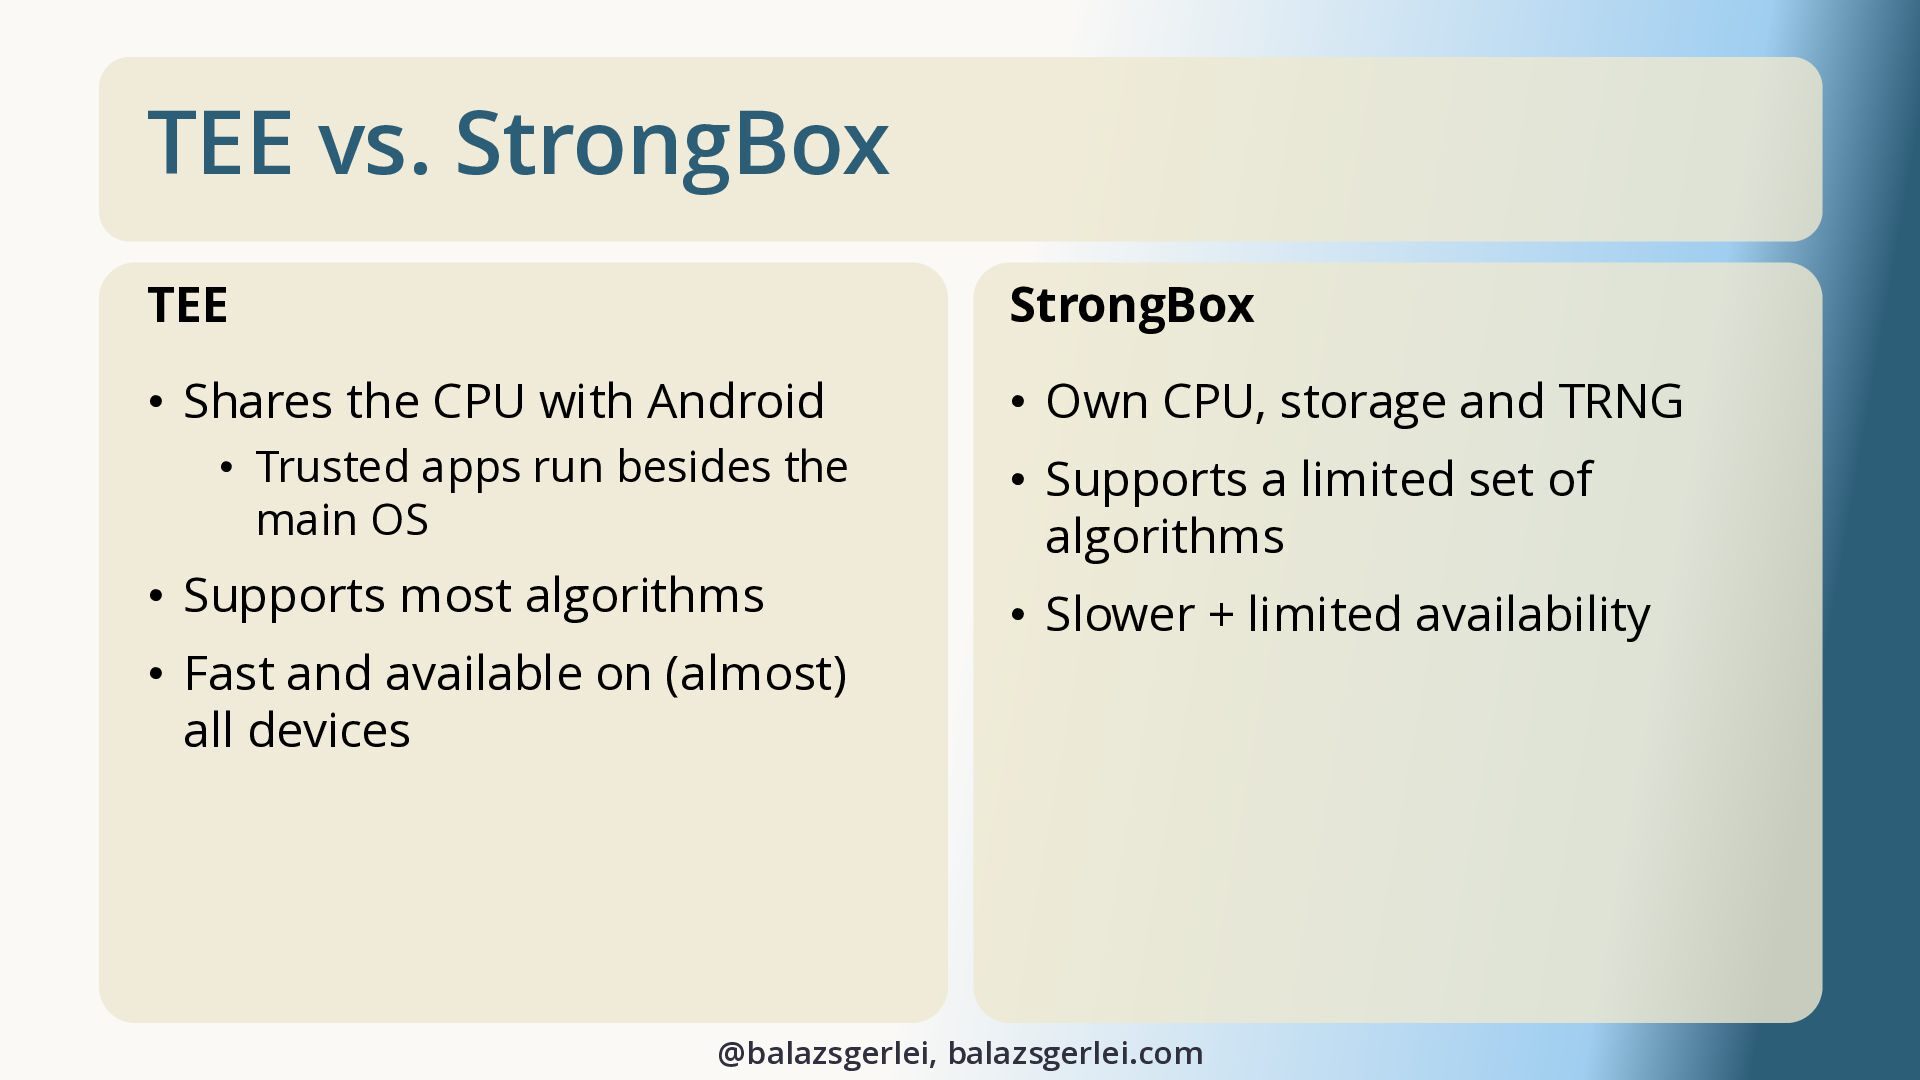
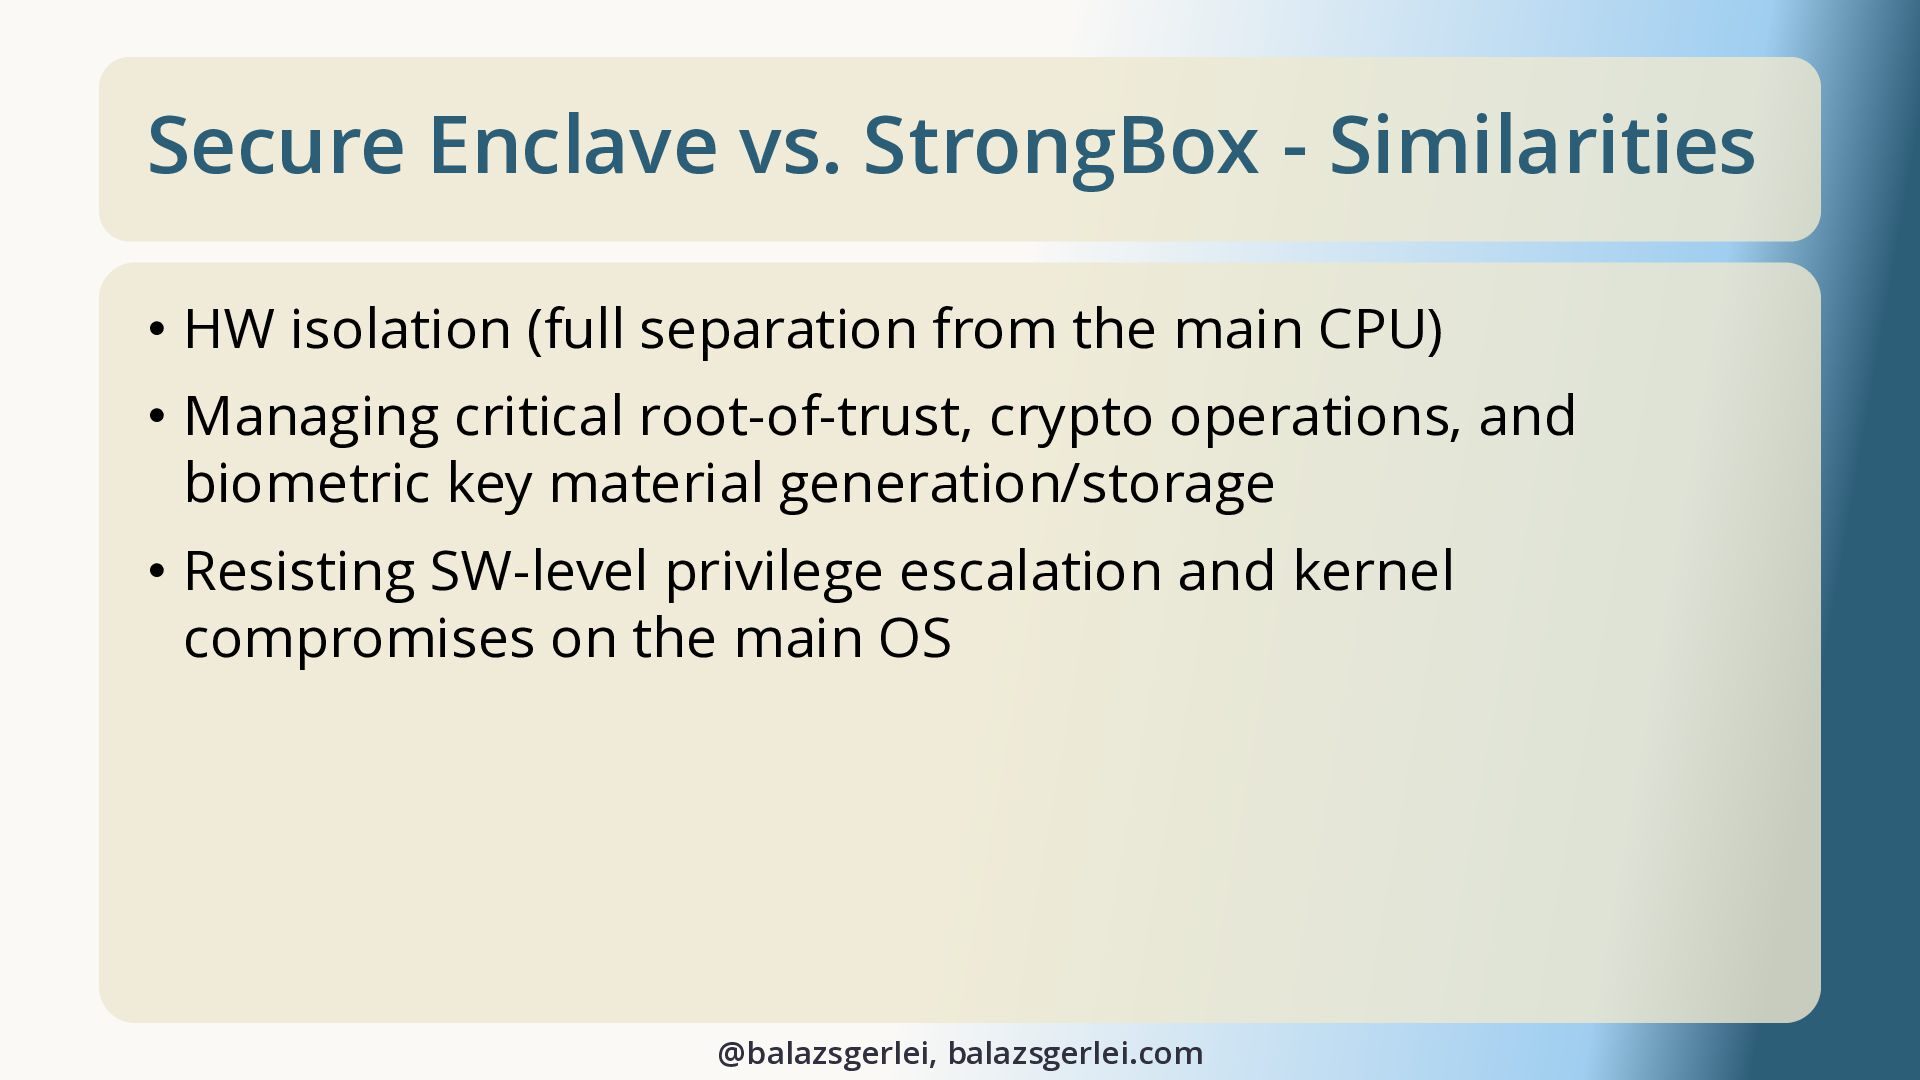
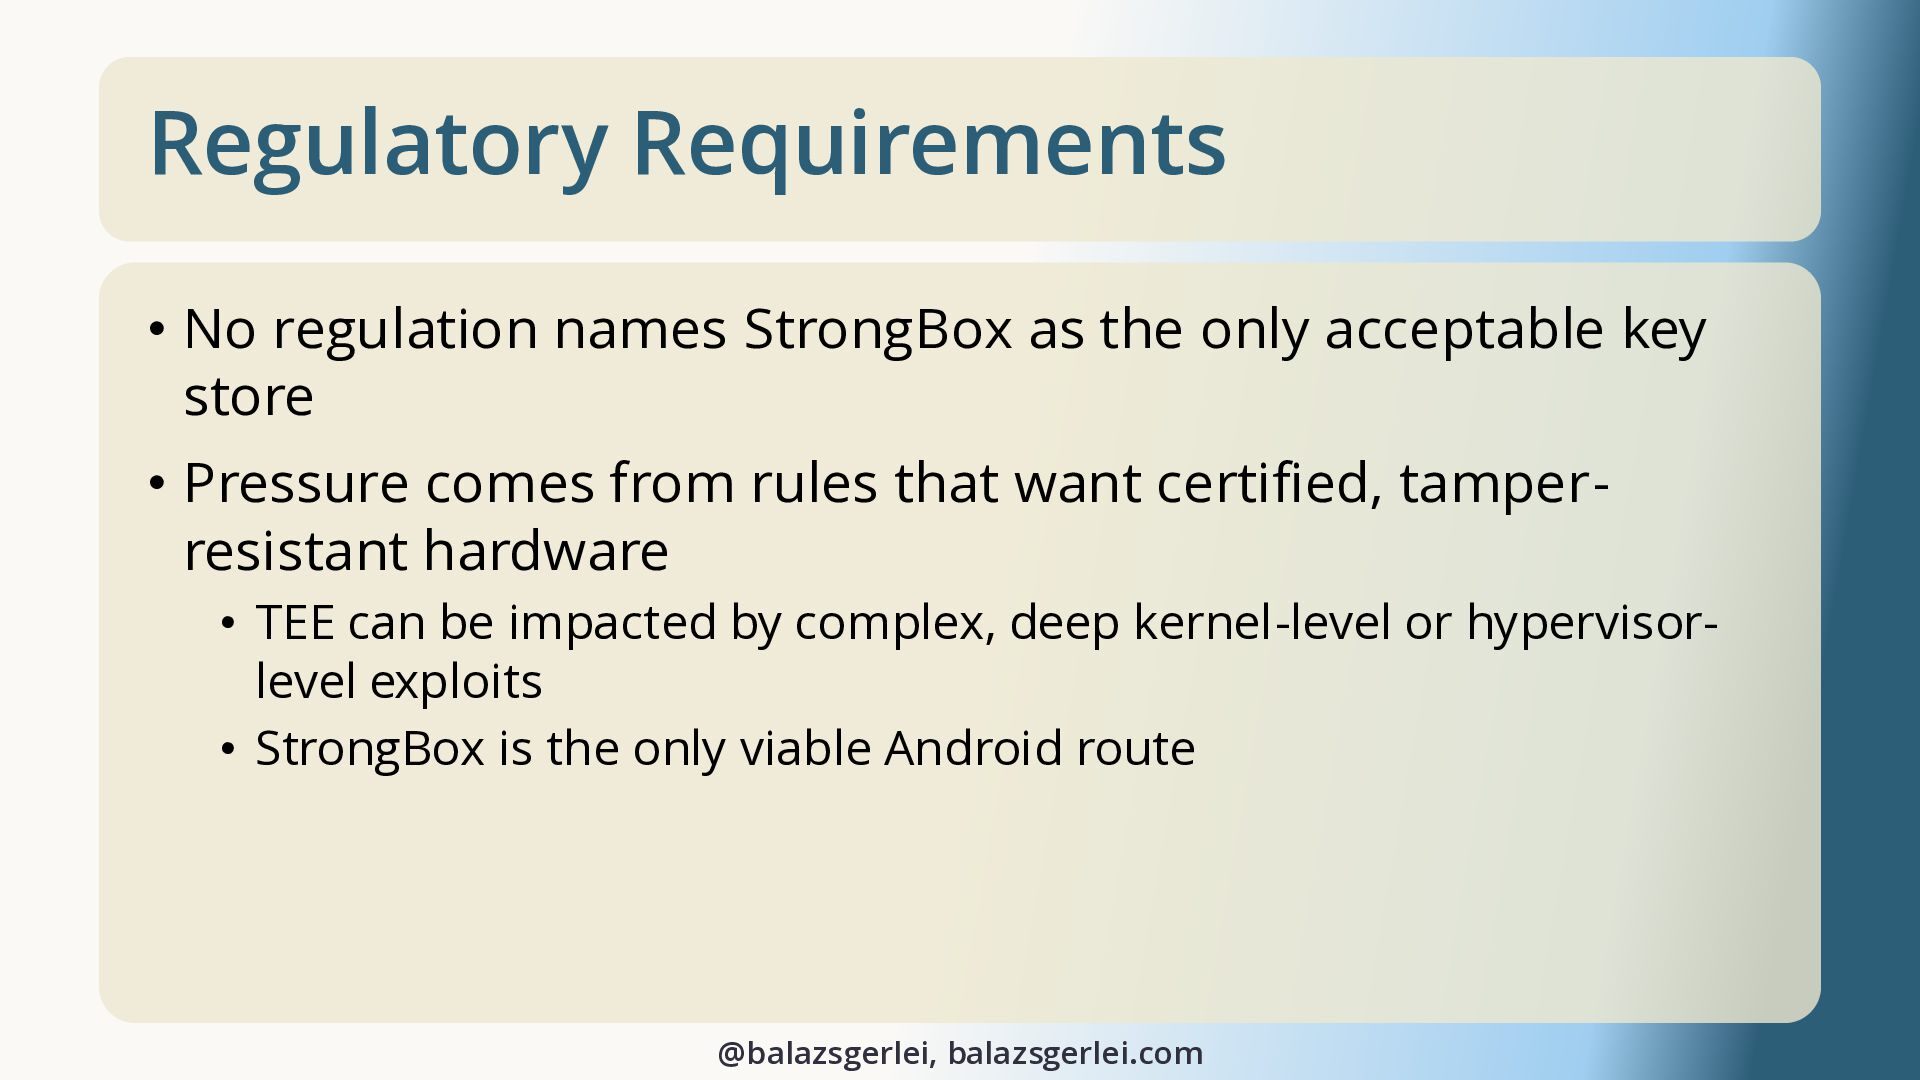
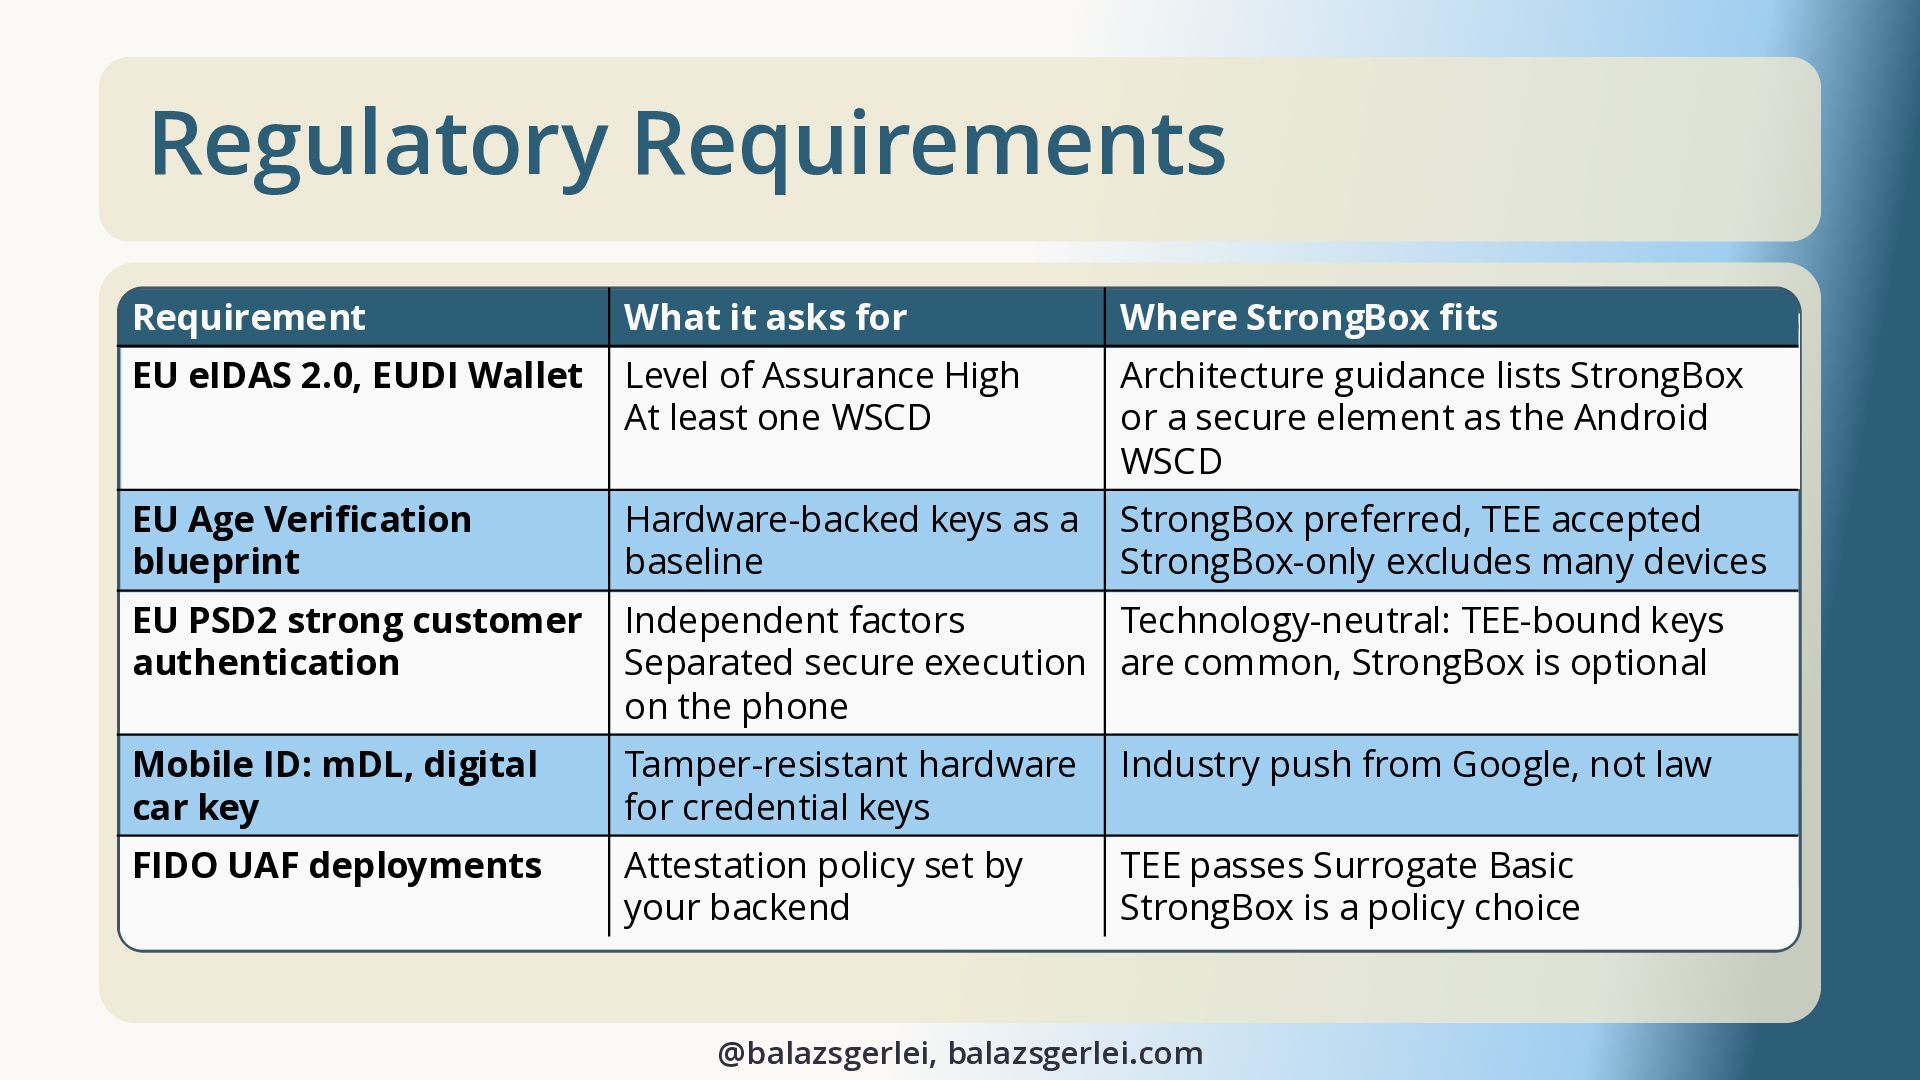
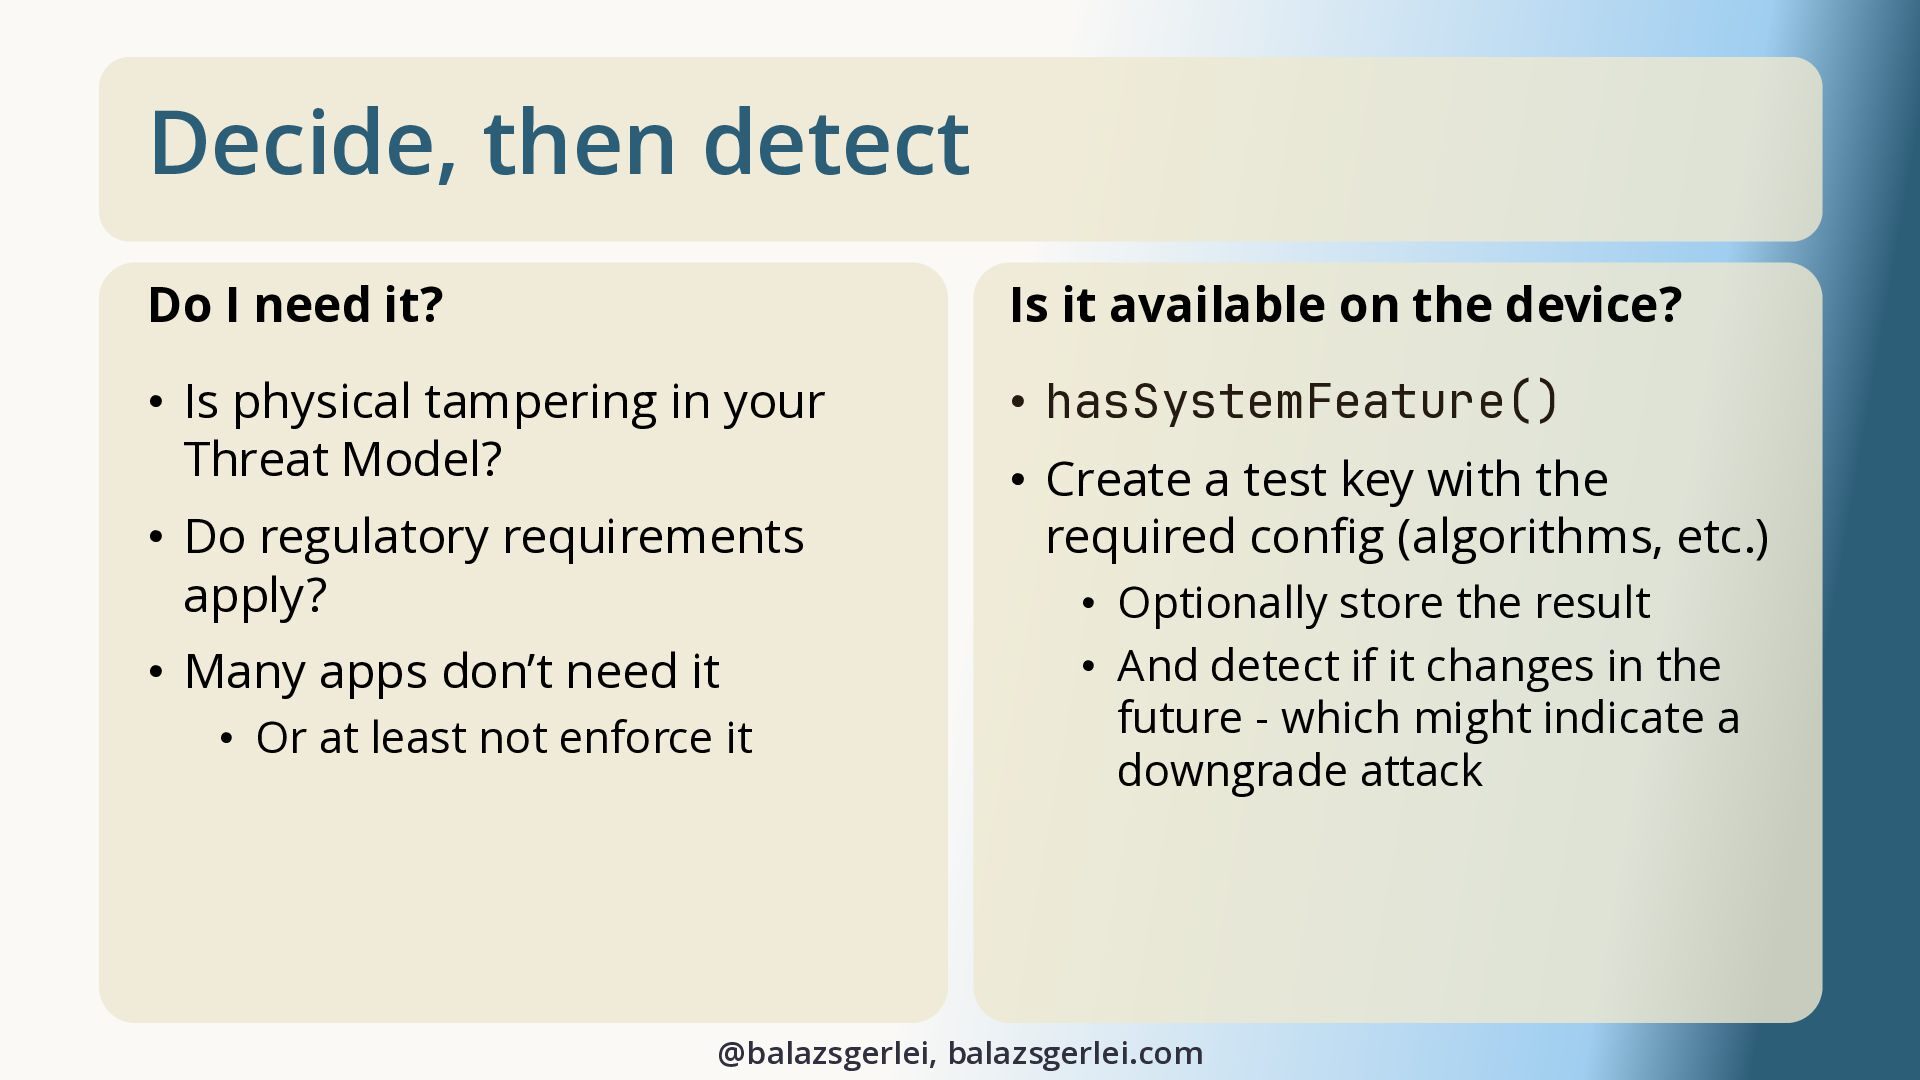
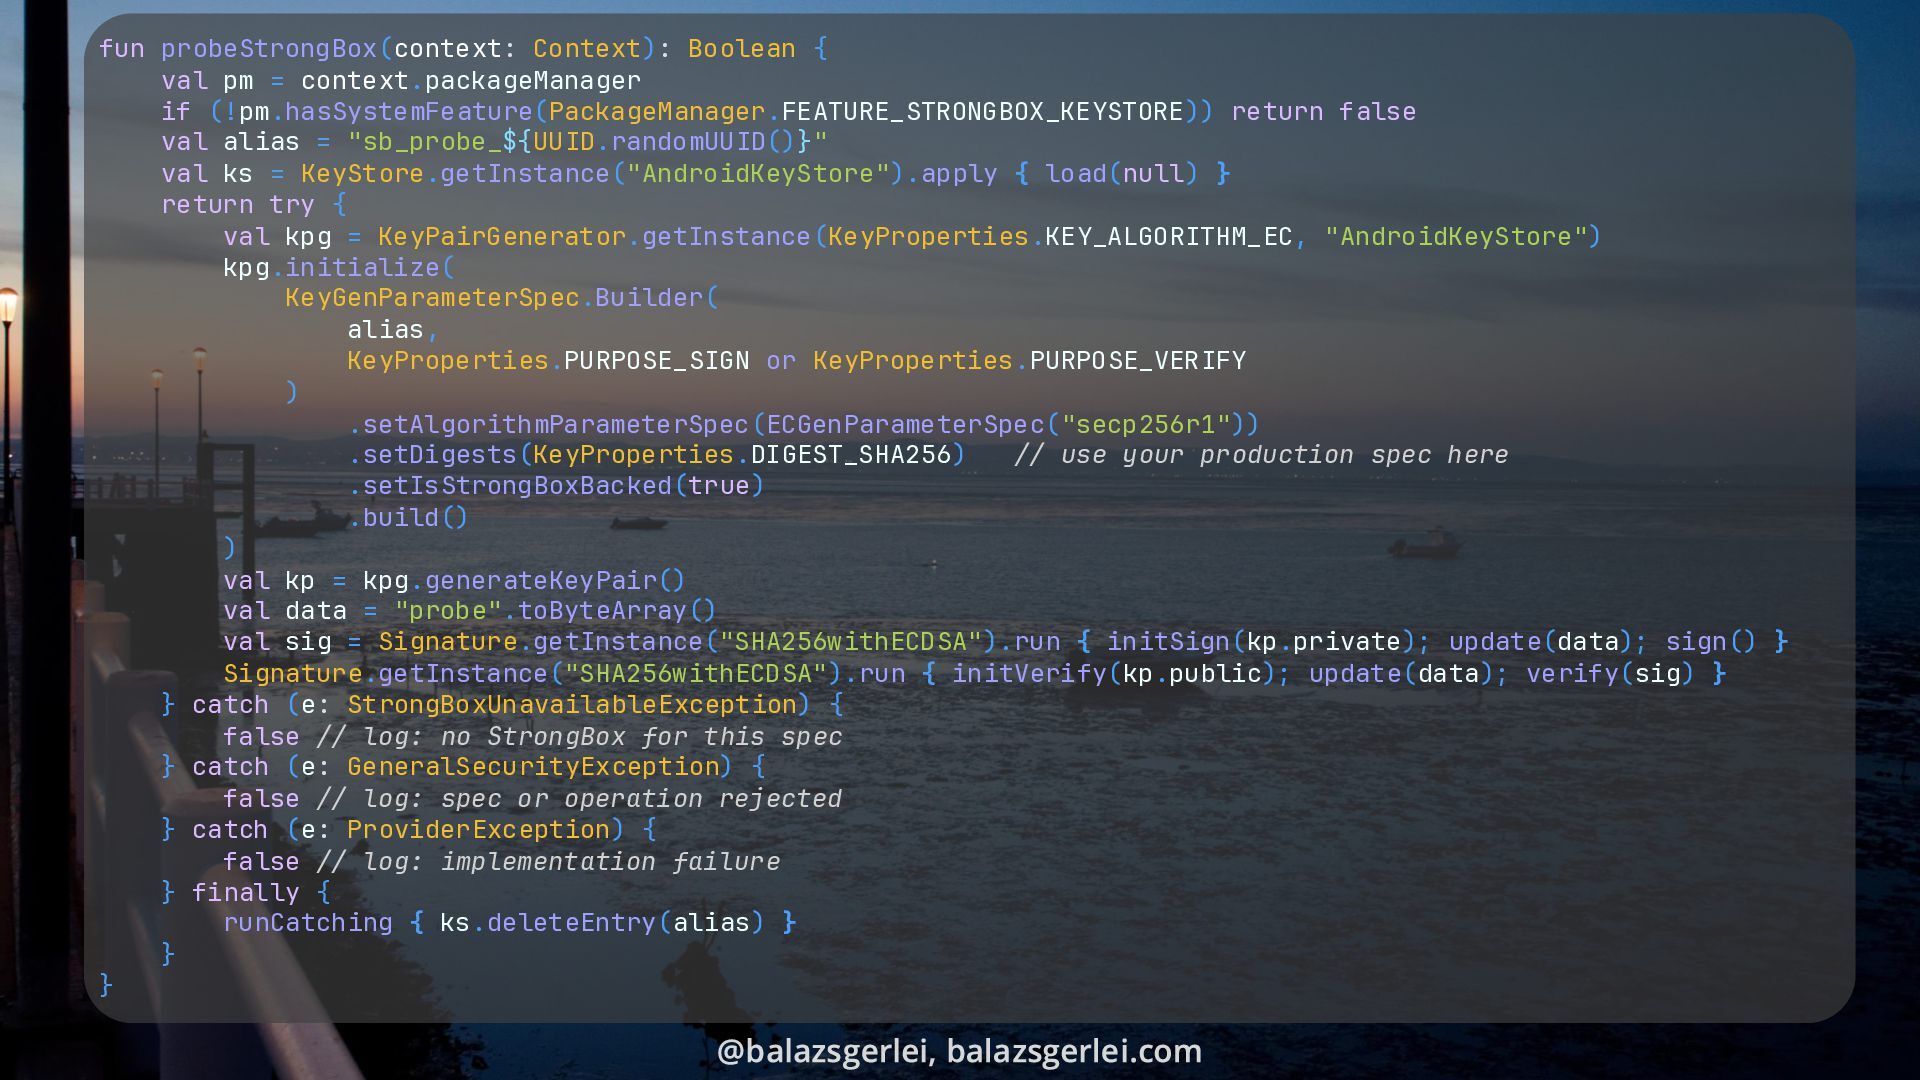
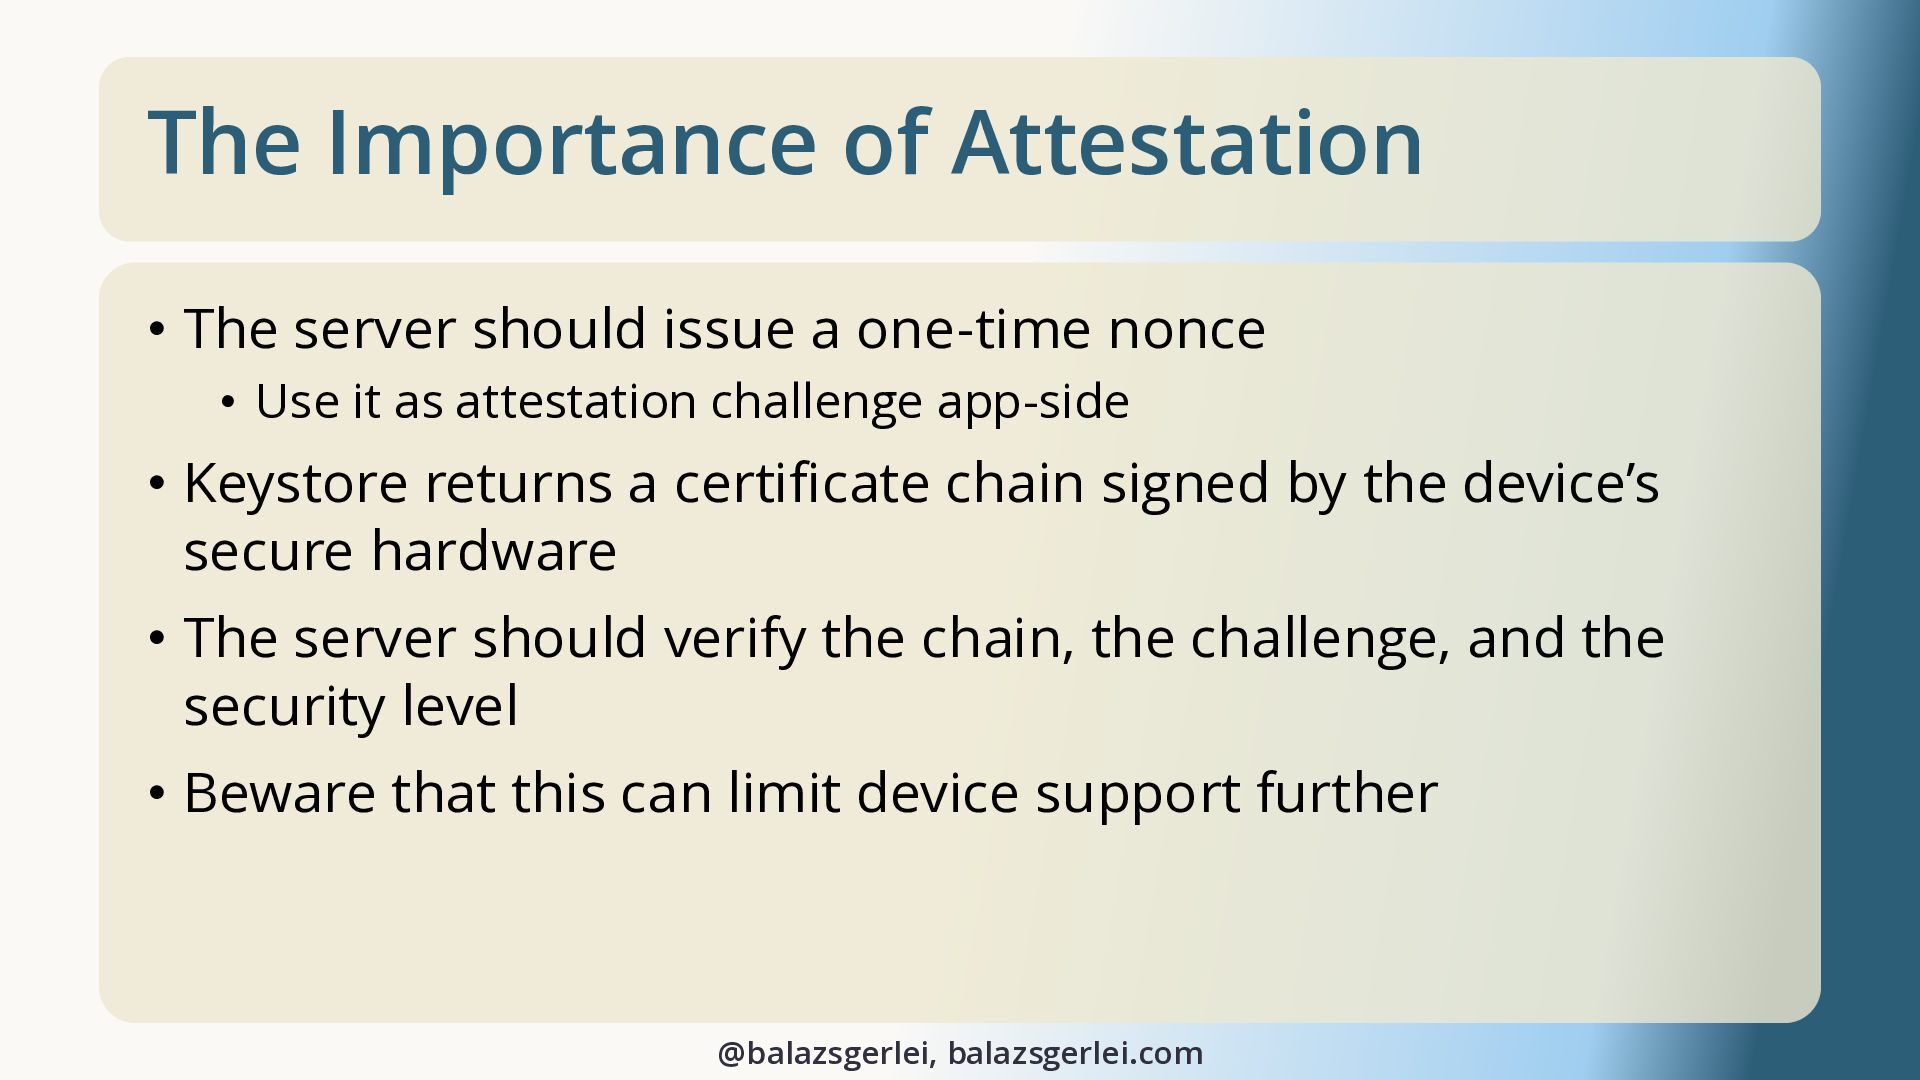
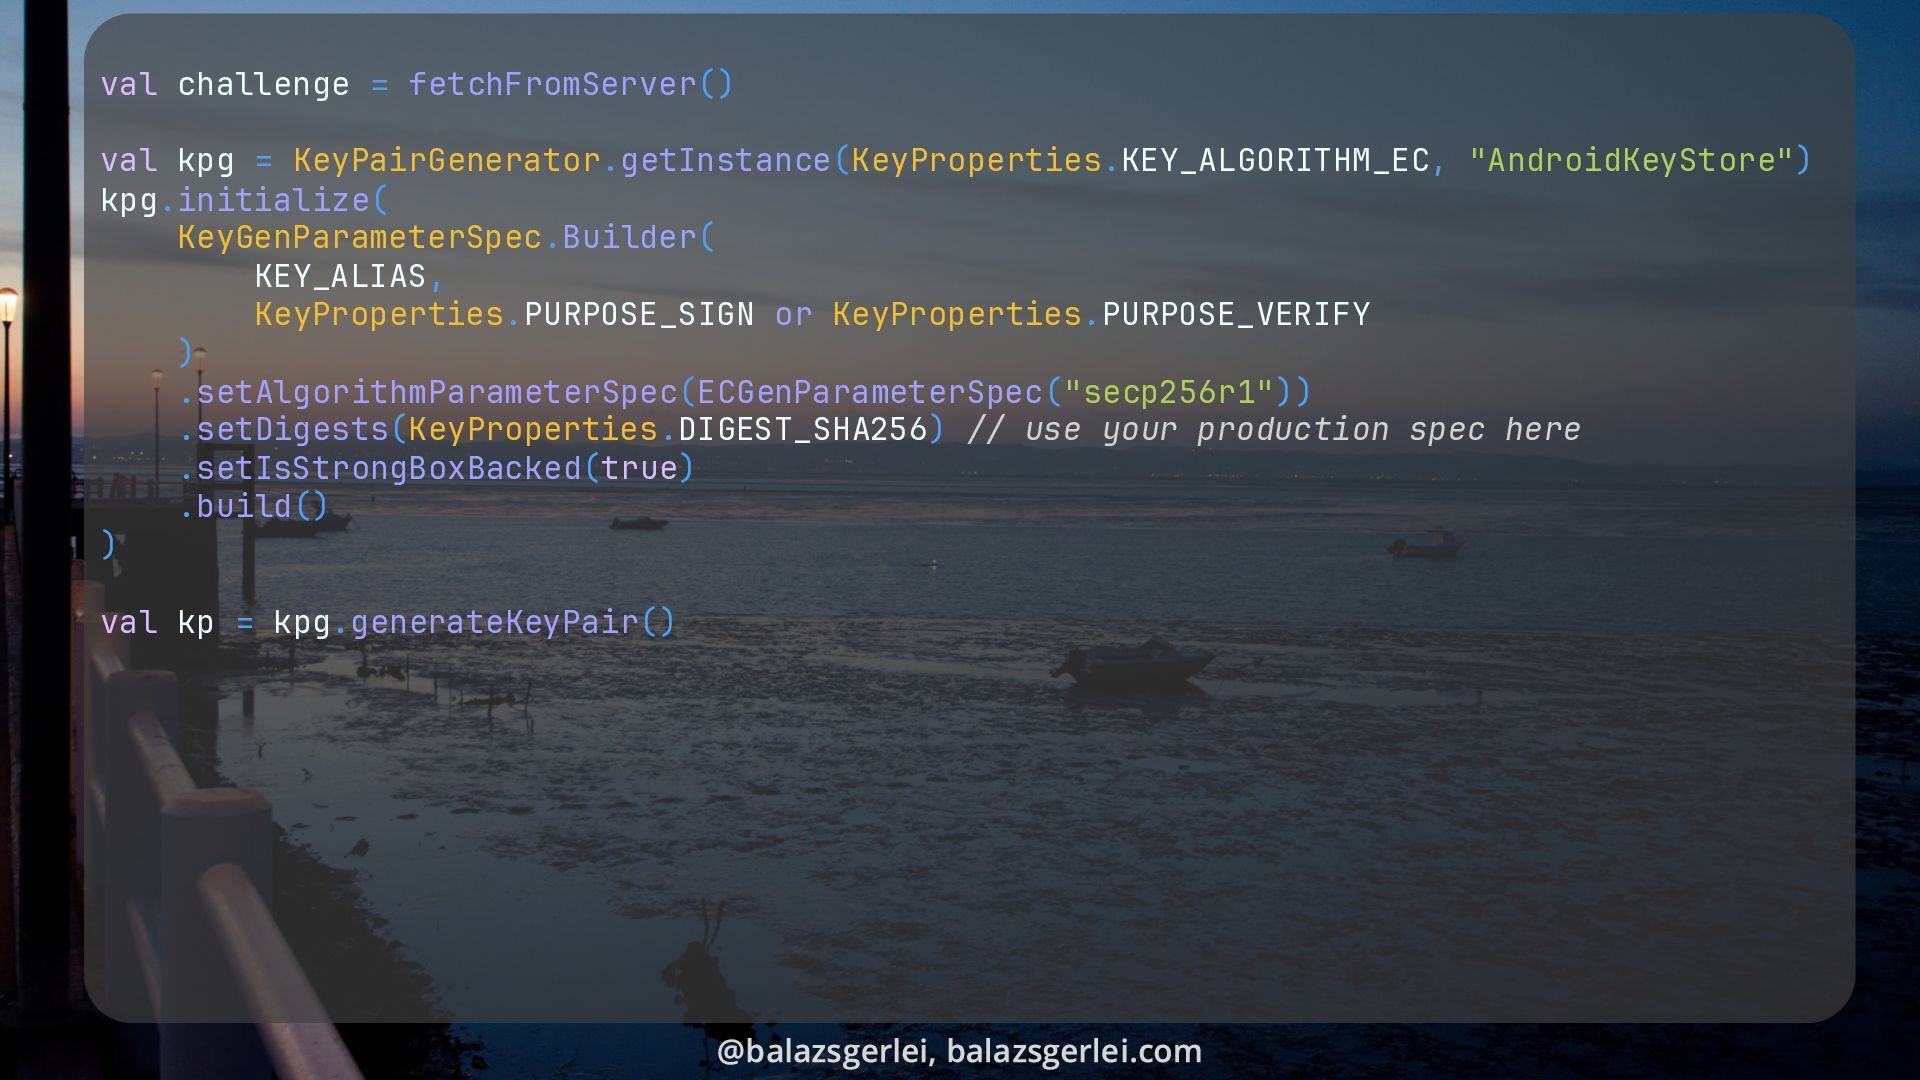
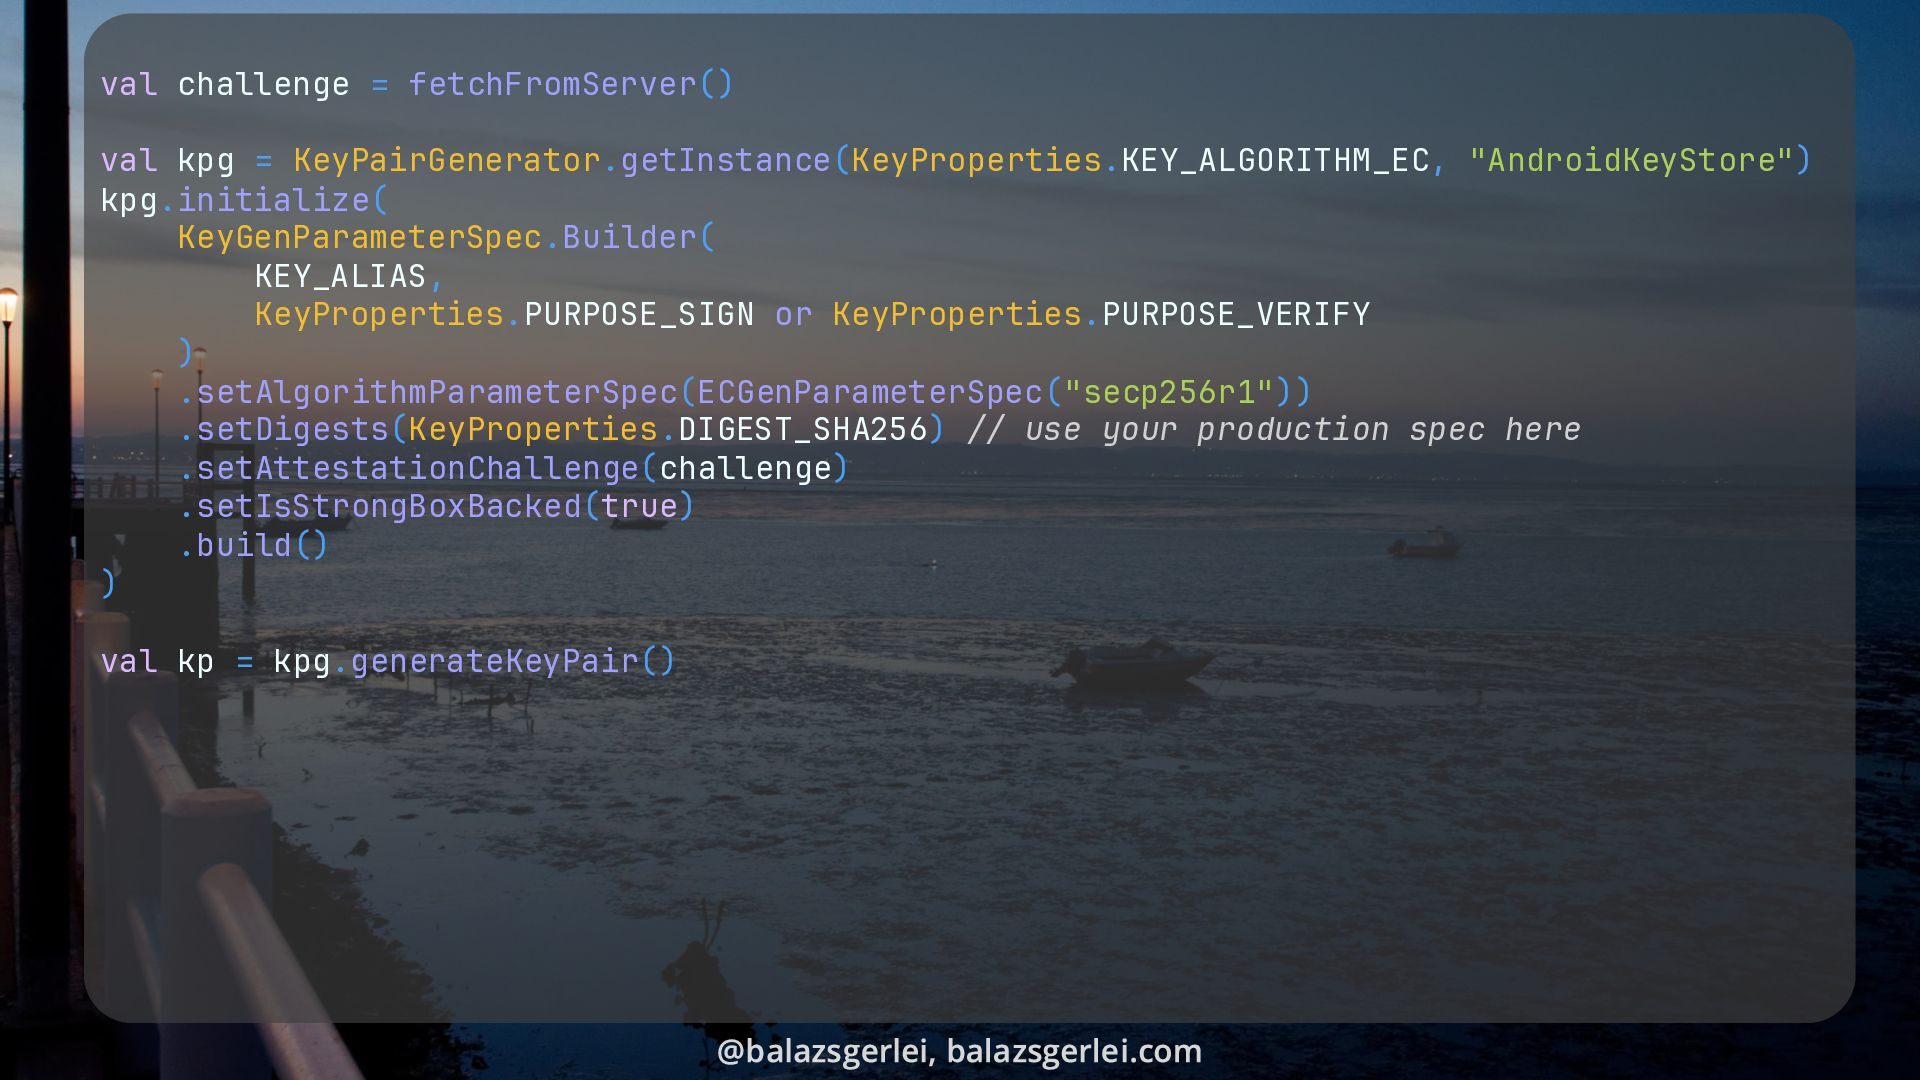
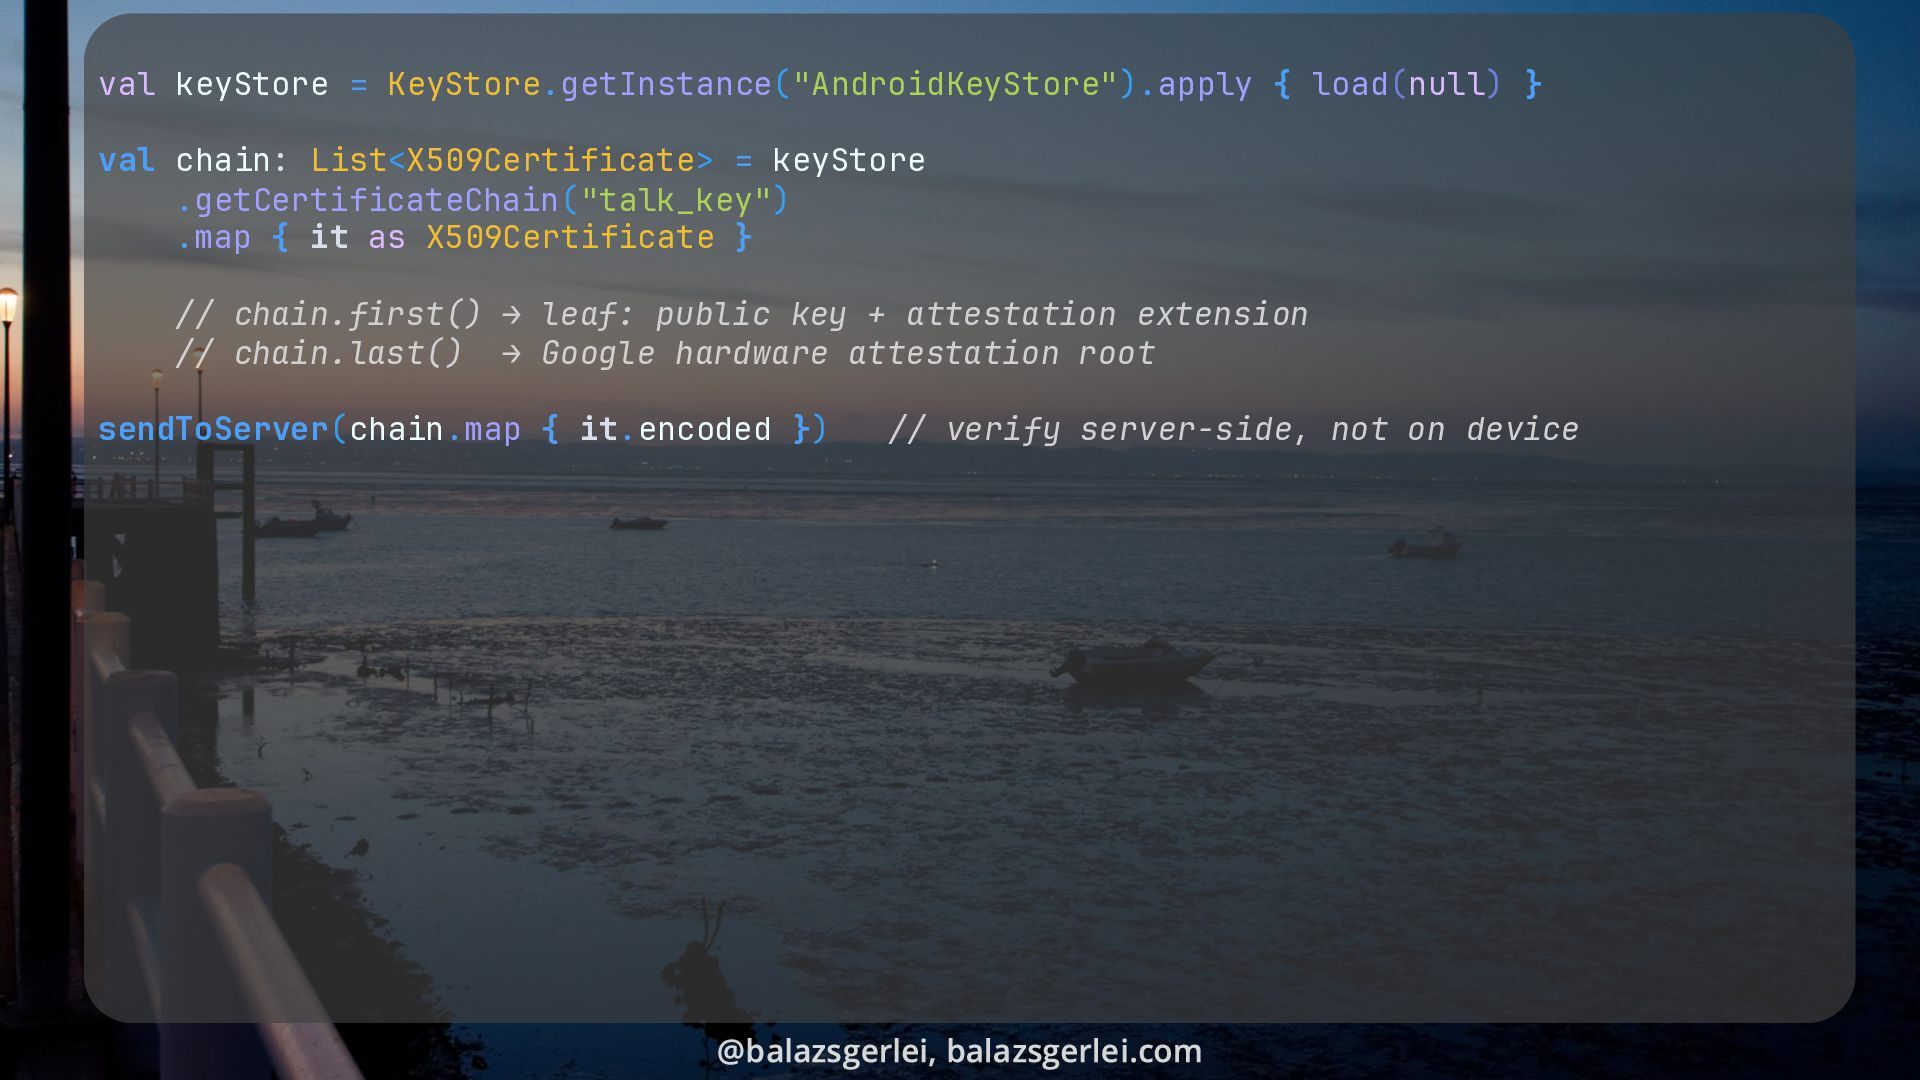
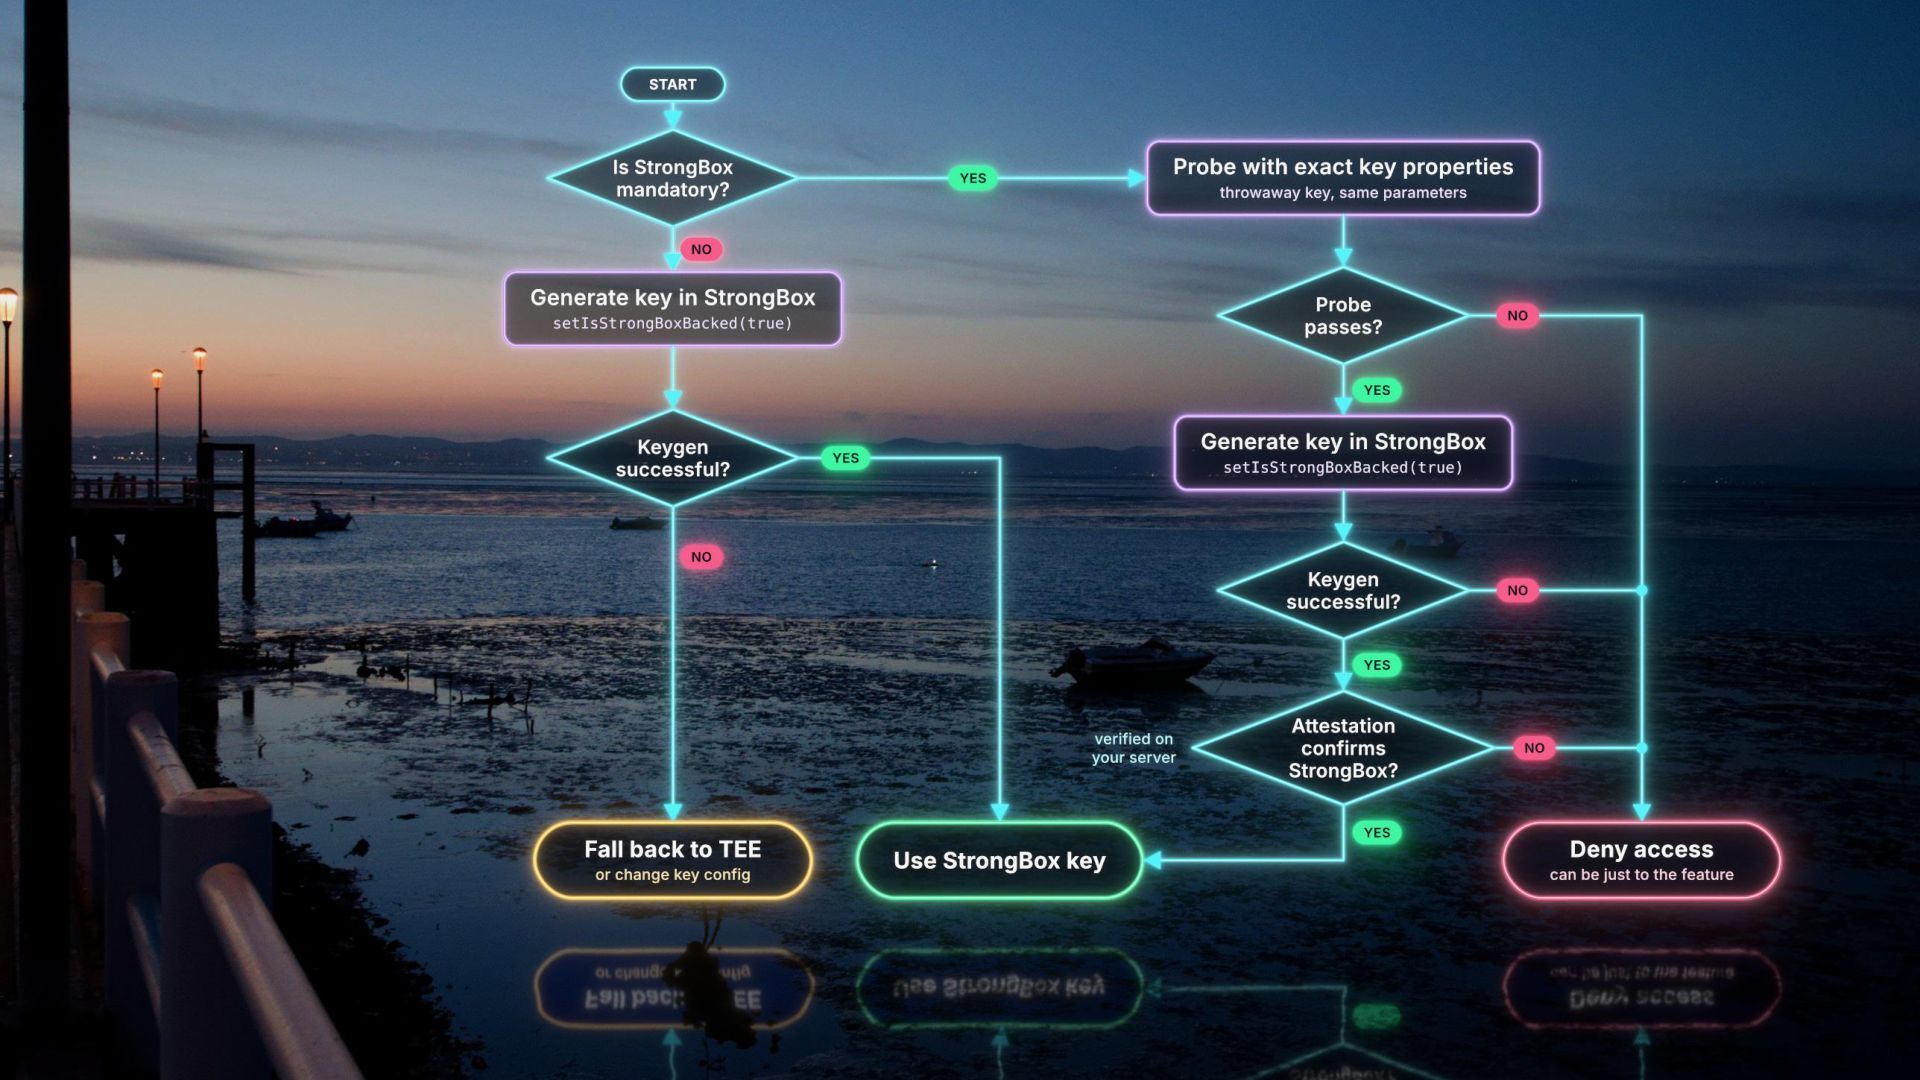
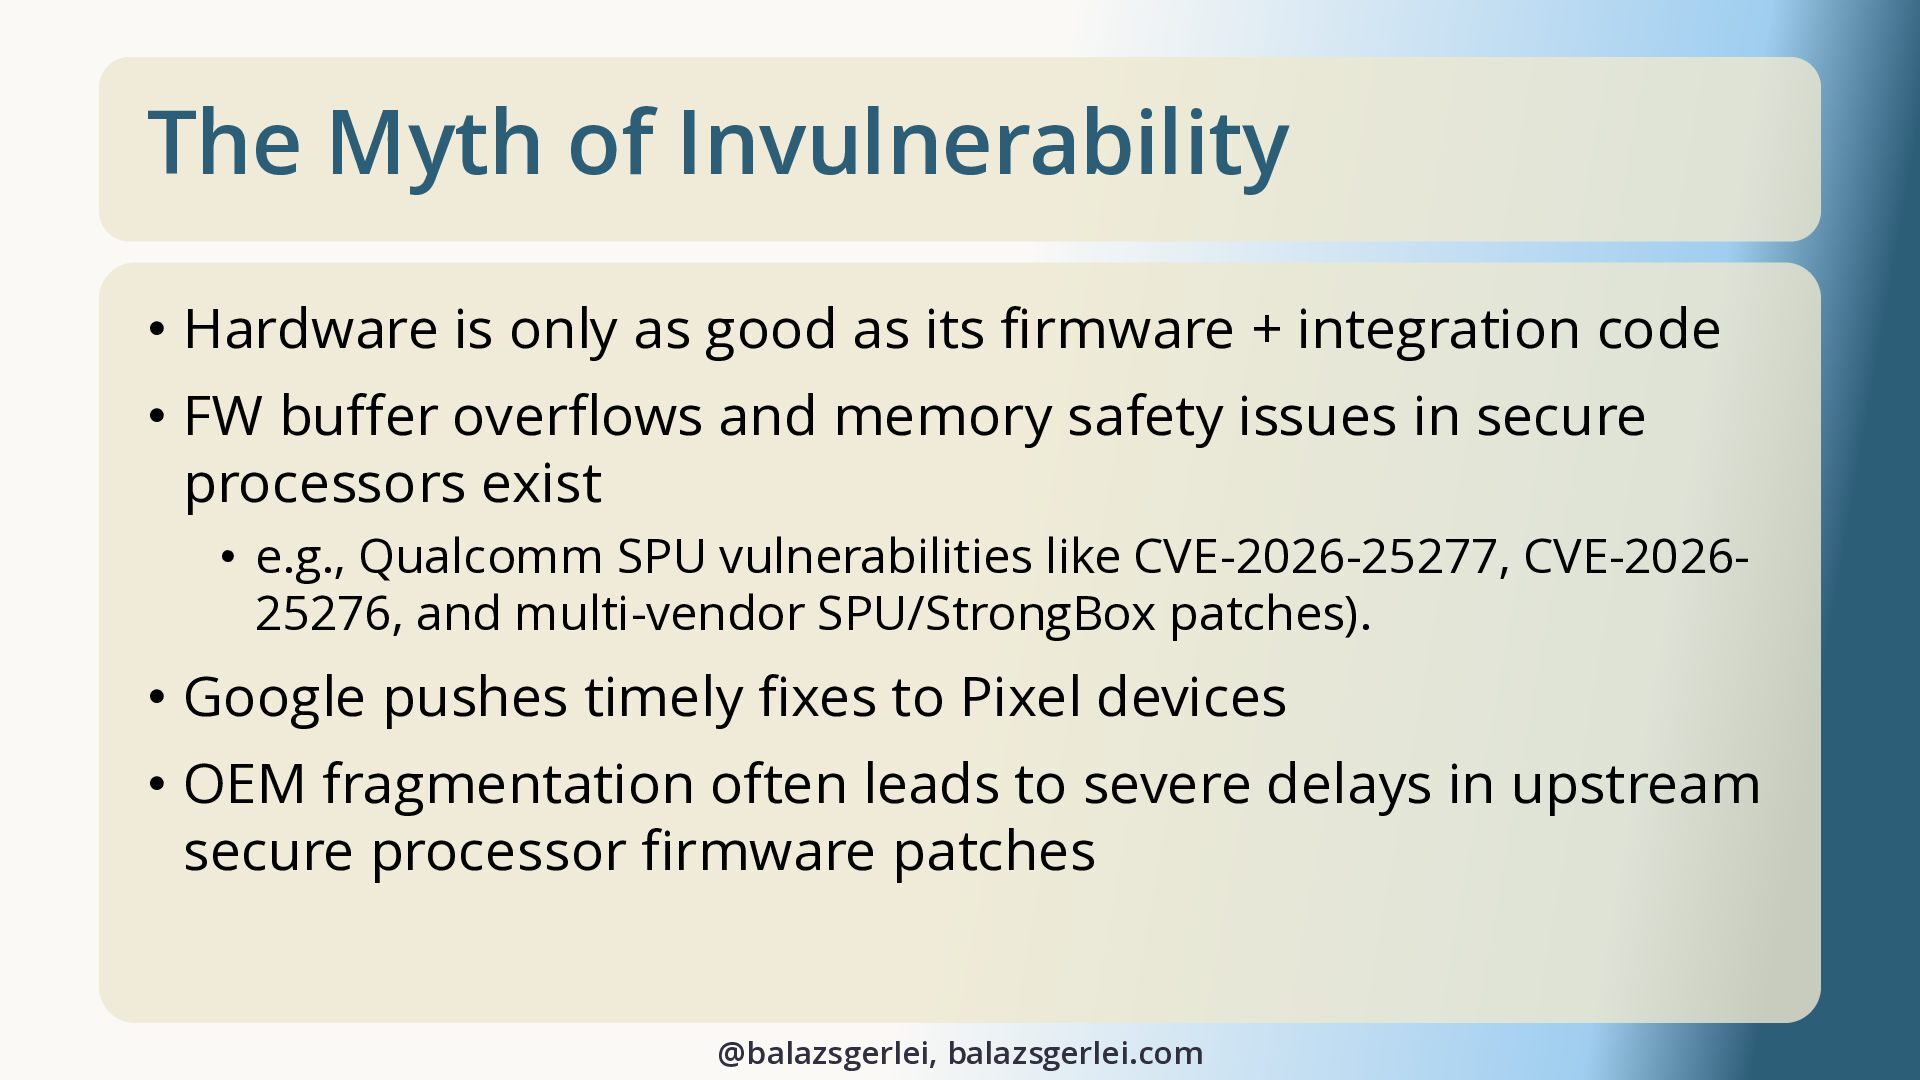
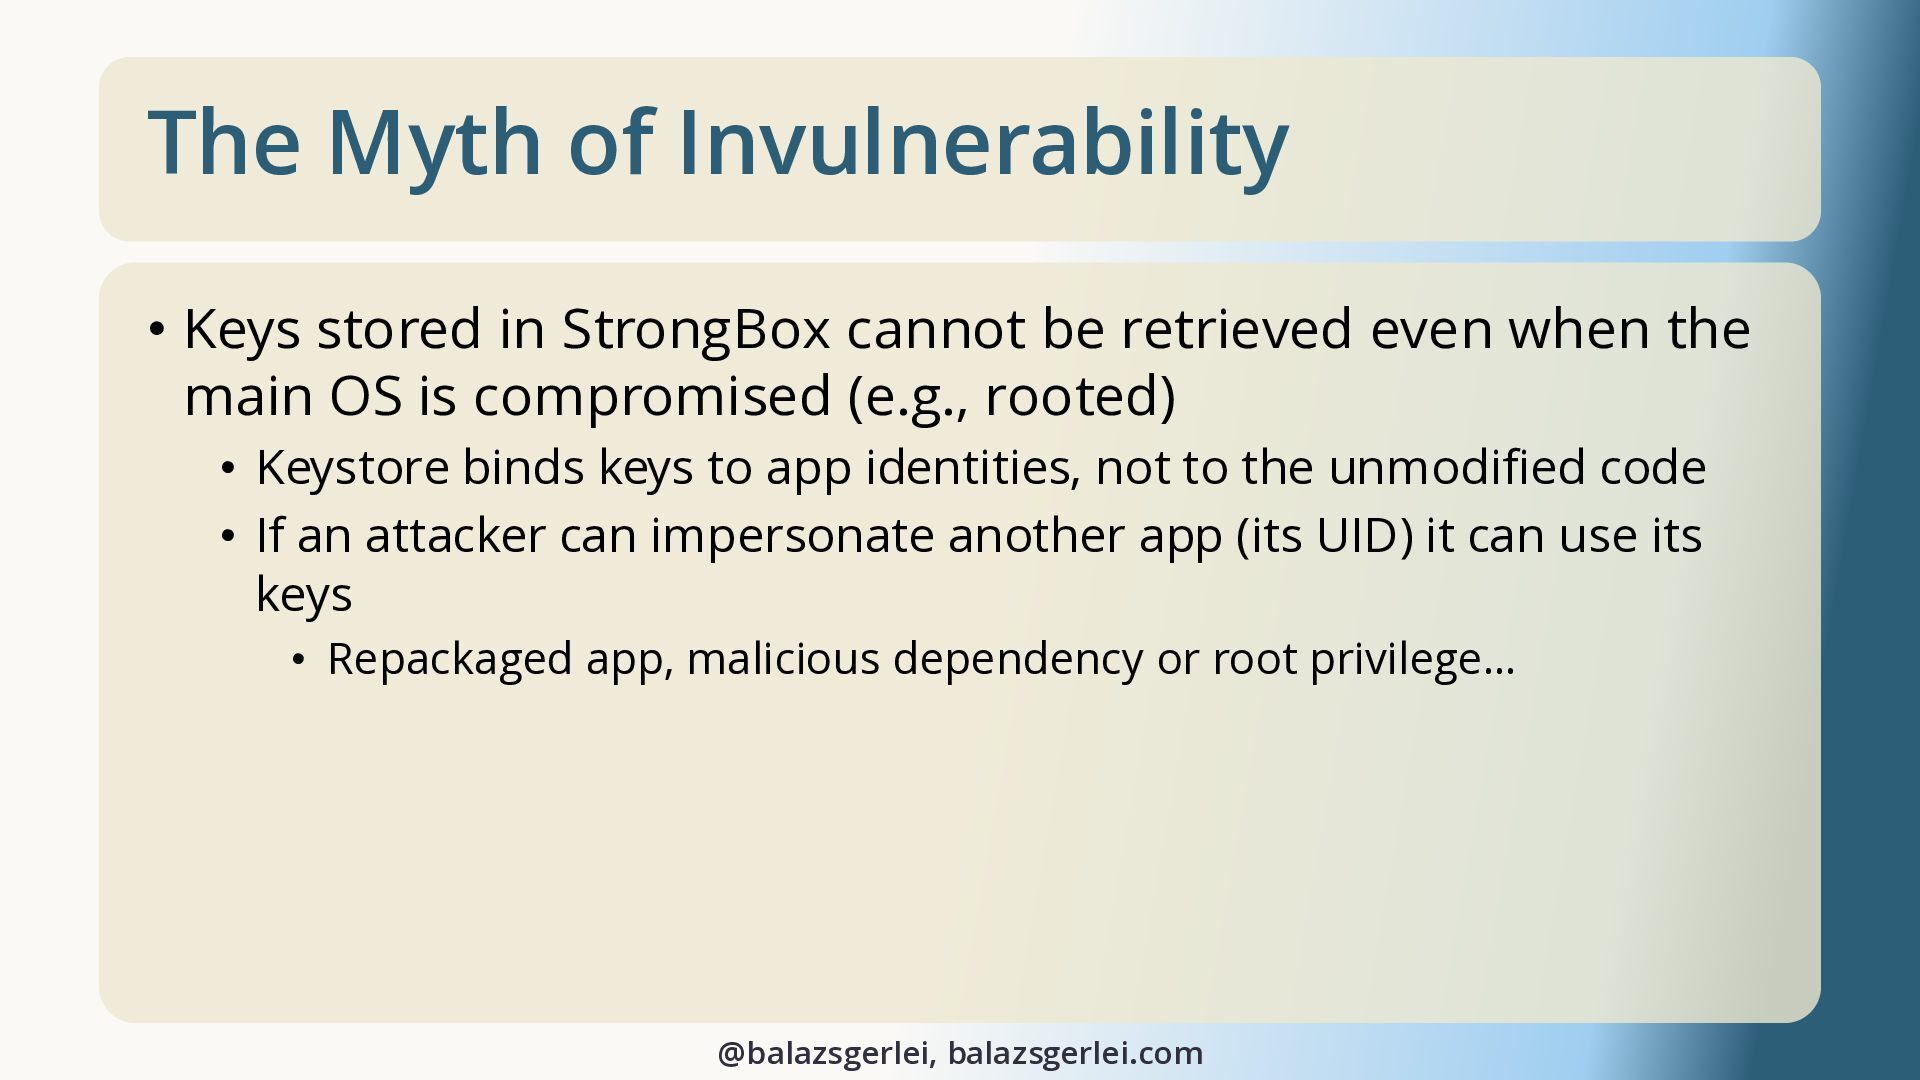
I’ll show you that taming StrongBox is not a mystery, but you should understand that checking FEATURE_STRONGBOX_KEYSTORE support (hasSystemFeature) isn't enough. You need to create test keys to verify if it’s actually usable on the device. You'll see the security/compatibility tradeoffs to decide when to enforce it (e.g., when regulatory compliance requires key attestation) and when gracefully falling back to TEE is the better engineering decision. I'll point out where StrongBox's threat model ends: it prevents key extraction even on rooted devices, but it may not be enough if app identity is compromised.
Links
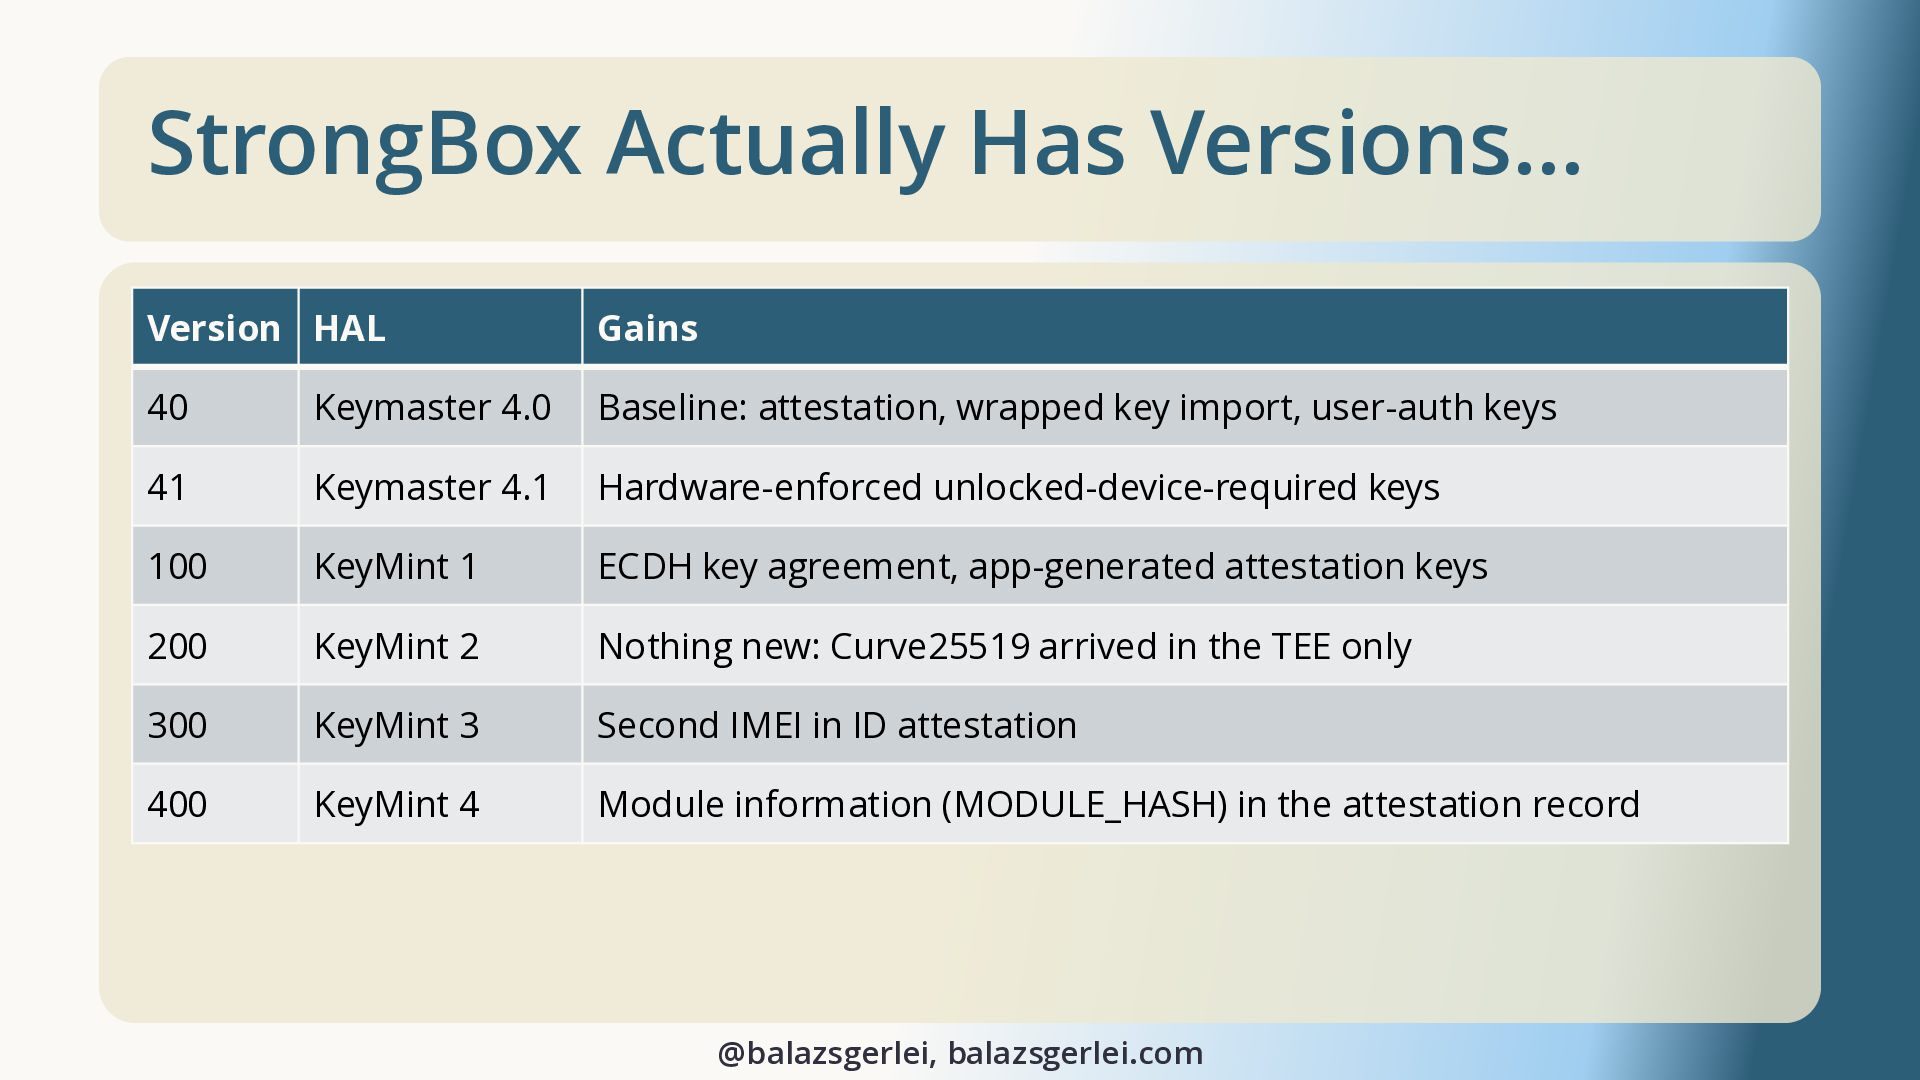
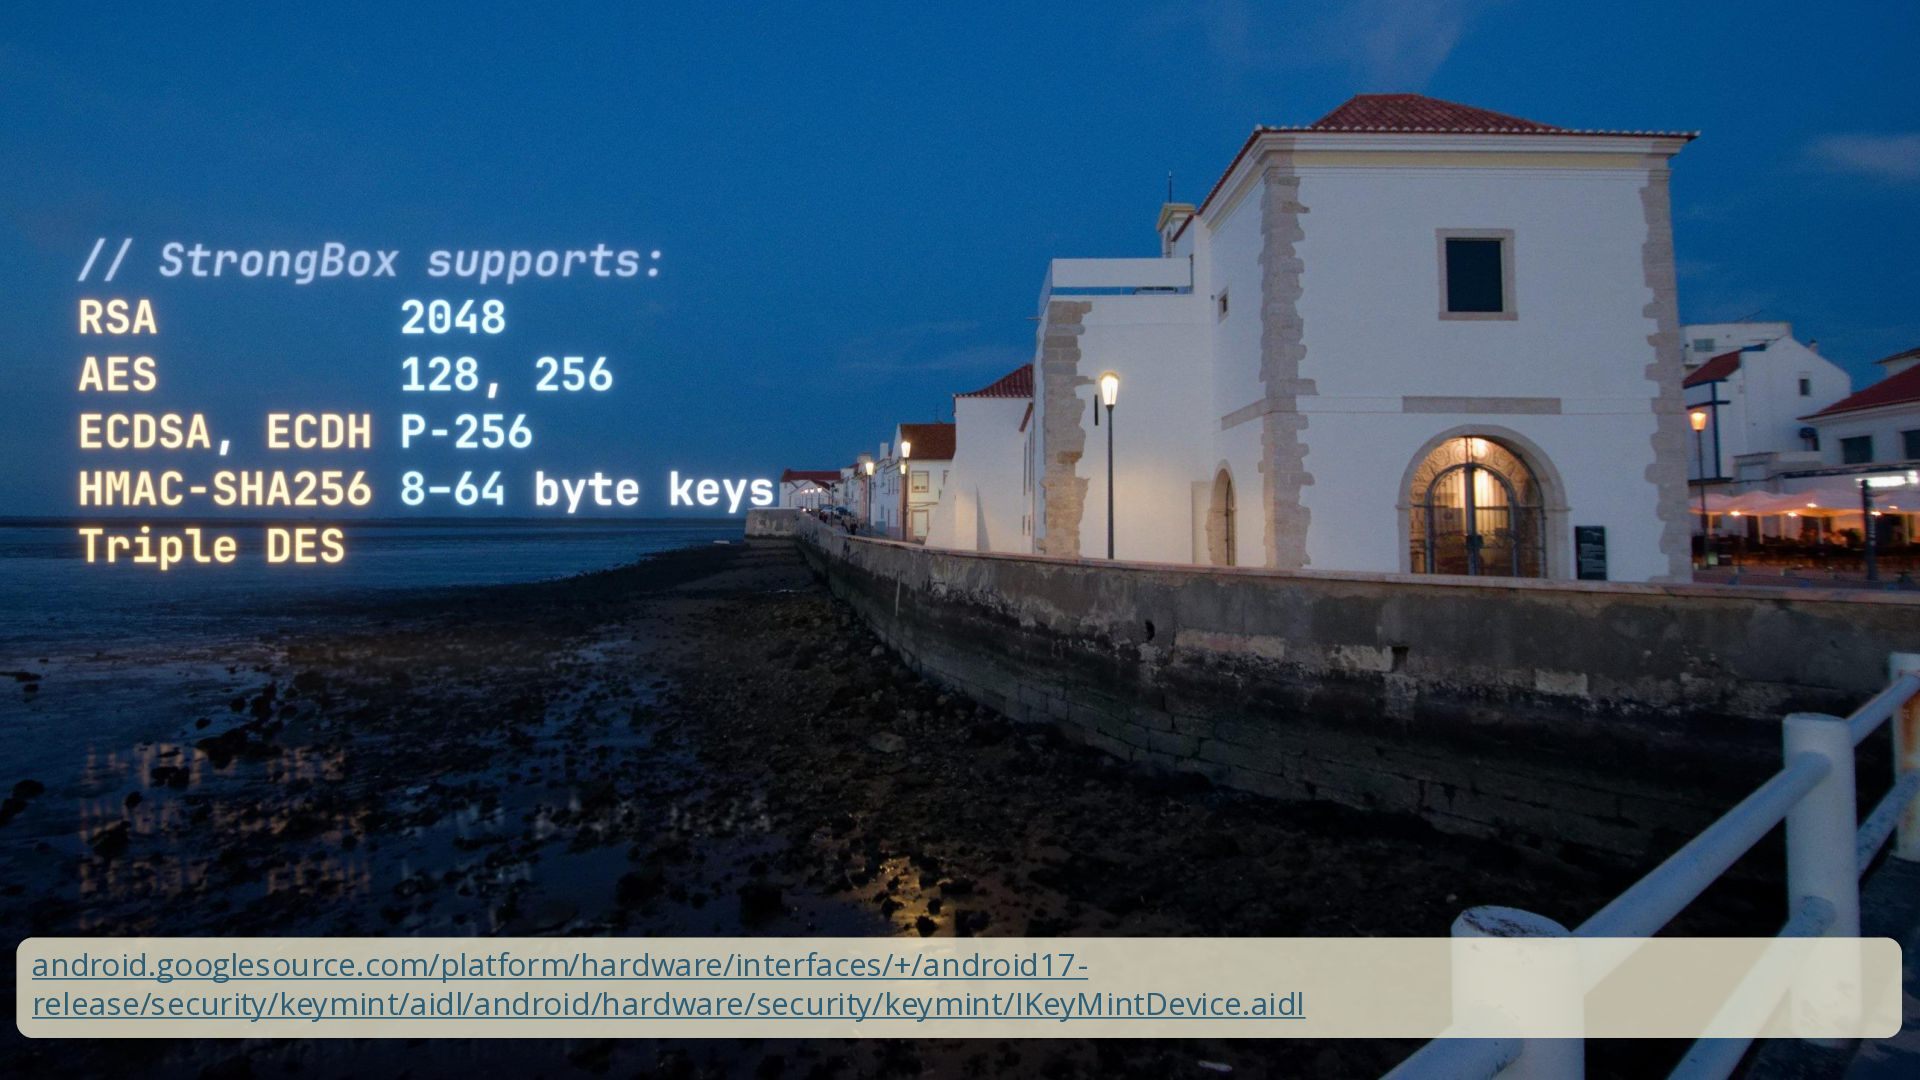
Source of IKeyMintDevice.aidl from AOSP
https://android.googlesource.com/platform/hardware/interfaces/+/android17-release/security/keymint/aidl/android/hardware/security/keymint/IKeyMintDevice.aidl
My Secure Storage Capabilities App
https://play.google.com/store/apps/details?id=dev.gerlot.securestoragecapabilities
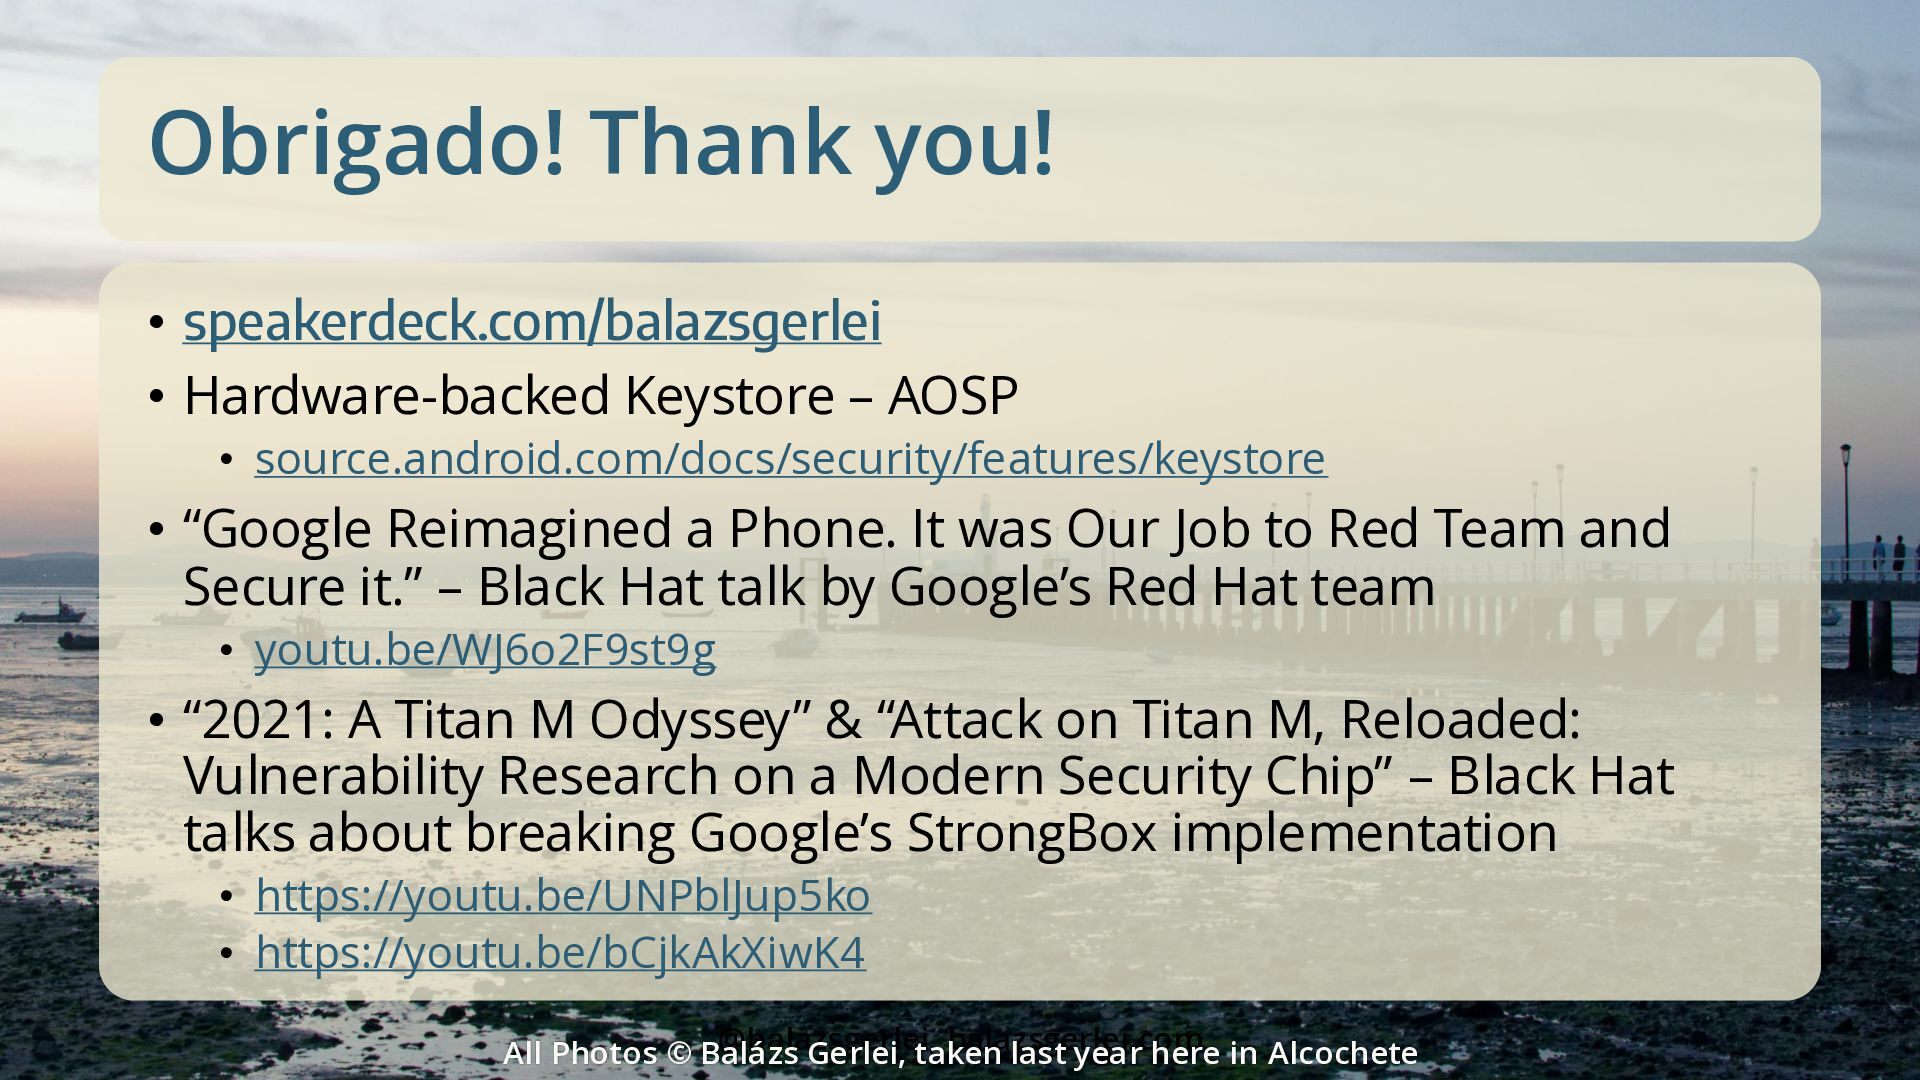
Hardware-backed Keystore – AOSP
https://source.android.com/docs/security/features/keystore
“Google Reimagined a Phone. It was Our Job to Red Team and Secure it.” – Black Hat talk by Google’s Red Hat team
https://youtu.be/WJ6o2F9st9g
“2021: A Titan M Odyssey” - BlackHat talk about breaking Google’s first StrongBox implementation (Titan M)
https://youtu.be/UNPblJup5ko
“Attack on Titan M, Reloaded: Vulnerability Research on a Modern Security Chip” - another BlackHat talk about breaking Google’s first StrongBox implementation (Titan M)
https://youtu.be/bCjkAkXiwK4


 balazsgerlei
 yukiny
 optim
 iwatsukayura
 jame2408
 tmikov2023
 sylph01
 y0hgi
 naokihaba
 tanahiro2010
 rkaga
 utakaha
 inesmontani
 zakiyama
 carmenintech
 tmiket
 mojombo
 jacobian
 geshan
 mza
 deanohume
 tenderlove
 addyosmani
 kastner