Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
API Authorization with OAuth2
Search
Bastian Hofmann
April 18, 2012
Technology
780
4
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
API Authorization with OAuth2
How it works and how to use it
Bastian Hofmann
April 18, 2012
More Decks by Bastian Hofmann
See All by Bastian Hofmann
Monitoring in Kubernetes with Prometheus and Grafana
bastianhofmann
0
380
Creating a fast Kubernetes Development Workflow
bastianhofmann
0
150
Highly available cross-region deployments with Kubernetes
bastianhofmann
1
190
From source to Kubernetes in 30 minutes
bastianhofmann
0
200
Introduction to Kubernetes
bastianhofmann
1
140
CI/CD with Kubernetes
bastianhofmann
0
260
Creating a fast Kubernetes Development Workflow
bastianhofmann
1
300
Deploying your first Micro-Service application to Kubernetes
bastianhofmann
2
220
Creating a fast Kubernetes Development Workflow
bastianhofmann
0
290
Other Decks in Technology
See All in Technology
What Is JetBrains Air
x5gtrn
PRO
0
130
AI導入は済んだ。次は統制を作り替える番だ_AI×開発組織 Summit 2026
techtekt
PRO
0
470
Persisting Massive Data with Rails ~Designing for 60 billion rows, and fighting the bottlenecks~ Railsで挑む大量データ永続化 〜600億件を永続化するための設計とボトルネックとの戦い〜
occhi
0
770
Rustuna: Rustによる高速なOptuna実装
pfn
PRO
0
210
トークン化預金DCJPYの取り組みと活用ユースケース
finengine
0
200
sue445's proposals 2026
sue445
0
120
AI駆動で「他アプリの音を加工できる」アプリを作った
satomasahiro2005
0
180
LLM-as-a-Judgeは本当に信頼できるのか――評価器を評価する話
taka_aki
2
960
OptunaHub: ブラックボックス最適化のためのプラットフォーム
pfn
PRO
0
150
日本語に強いオープンな大規模言語モデル「LLM-jp」
odashi
5
1.2k
⾮構造化データを価値に変える AI エージェント基盤とその組織
ivry_presentationmaterials
0
210
Classmethod Company Deck
satoshi7
1
780
Featured
See All Featured
Tips & Tricks on How to Get Your First Job In Tech
honzajavorek
1
810
Build your cross-platform service in a week with App Engine
jlugia
234
19k
Visualization
eitanlees
153
17k
Learning to Love Humans: Emotional Interface Design
aarron
275
41k
Building Adaptive Systems
keathley
44
3.3k
Git: the NoSQL Database
bkeepers
PRO
433
67k
How to Talk to Developers About Accessibility
jct
2
590
The Language of Interfaces
destraynor
162
27k
Deep Space Network (abreviated)
tonyrice
0
380
We Analyzed 250 Million AI Search Results: Here's What I Found
joshbly
2
2k
DBのスキルで生き残る技術 - AI時代におけるテーブル設計の勘所
soudai
PRO
68
59k
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
Transcript
@BastianHofmann API Authorization with OAuth2 How it works and how
to use it
http://oauth.net/
None
None
None
None
None
None
None
Questions? Ask!
http://speakerdeck.com/u/bastianhofmann
http://oauth.net/
http://tools.ietf.org/html/rfc5849
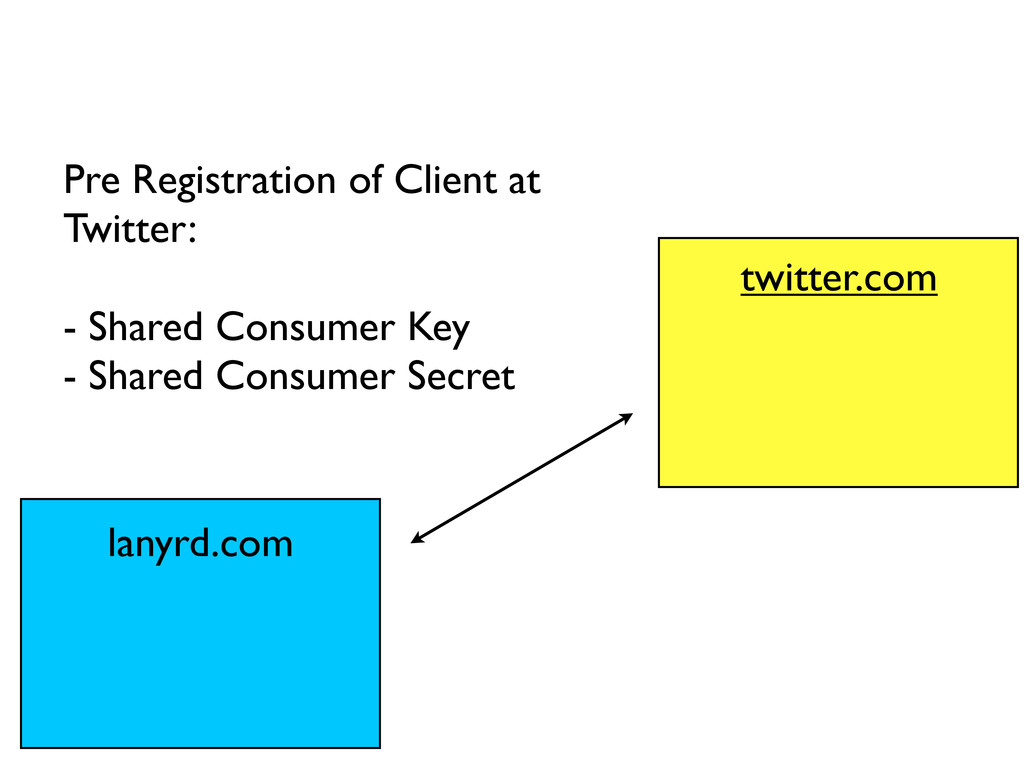
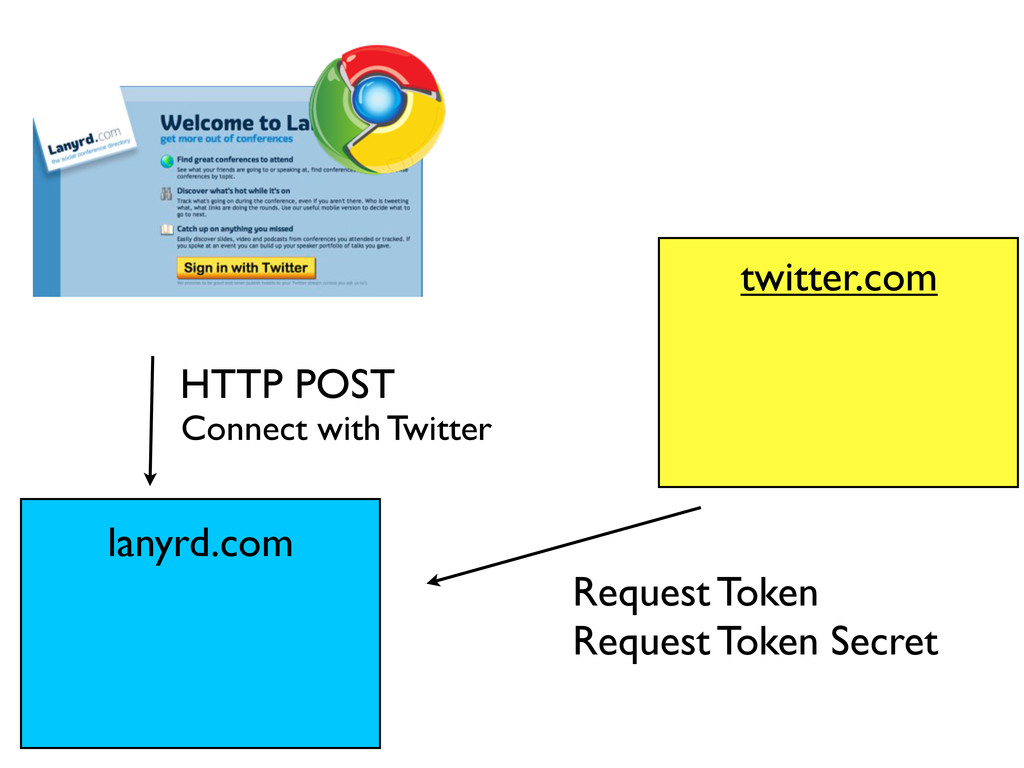
lanyrd.com twitter.com Pre Registration of Client at Twitter: - Shared
Consumer Key - Shared Consumer Secret
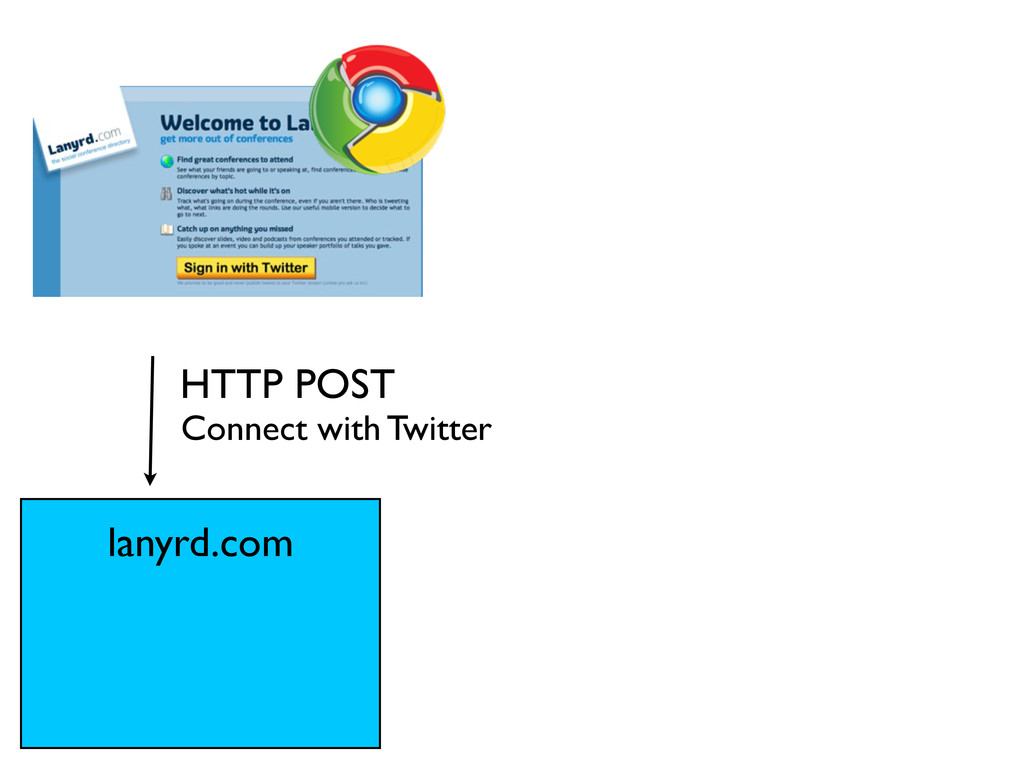
HTTP POST Connect with Twitter lanyrd.com
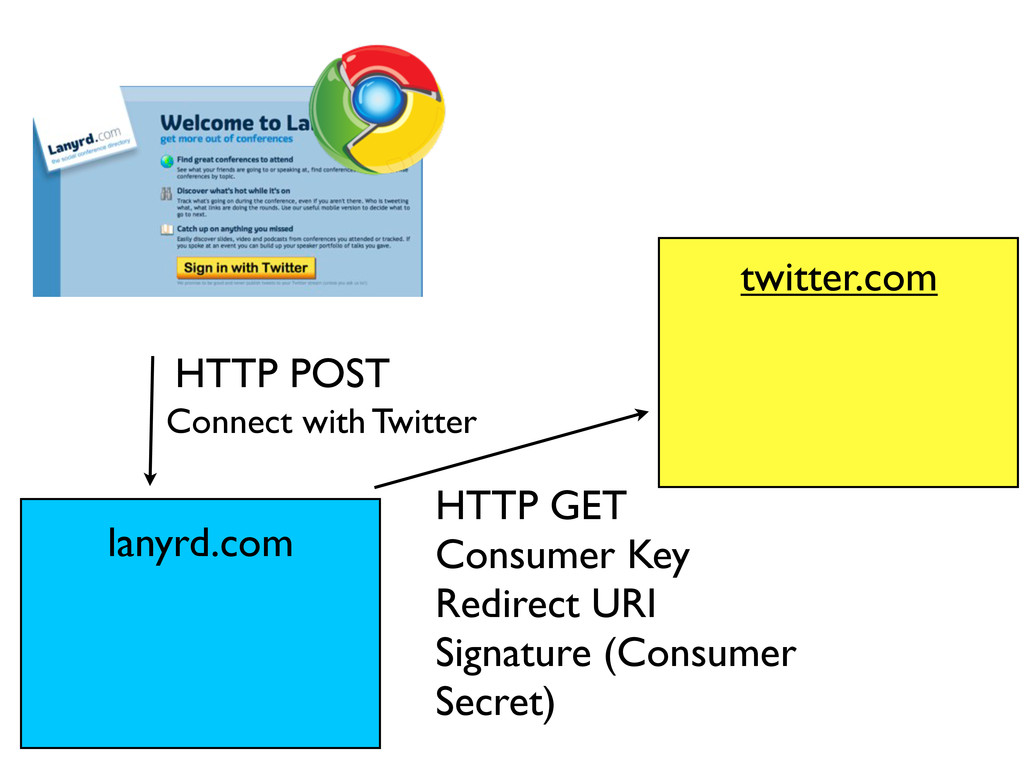
twitter.com HTTP POST Connect with Twitter HTTP GET Consumer Key
Redirect URI Signature (Consumer Secret) lanyrd.com
twitter.com HTTP POST Connect with Twitter Request Token Request Token
Secret lanyrd.com
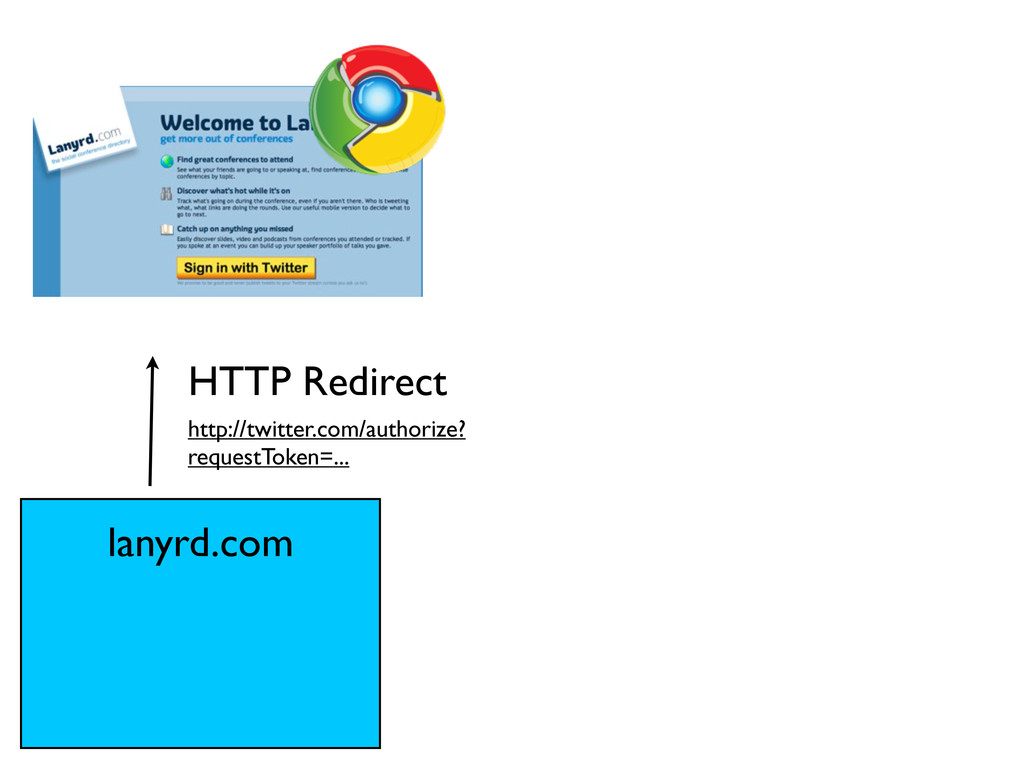
http://twitter.com/authorize? requestToken=... HTTP Redirect lanyrd.com
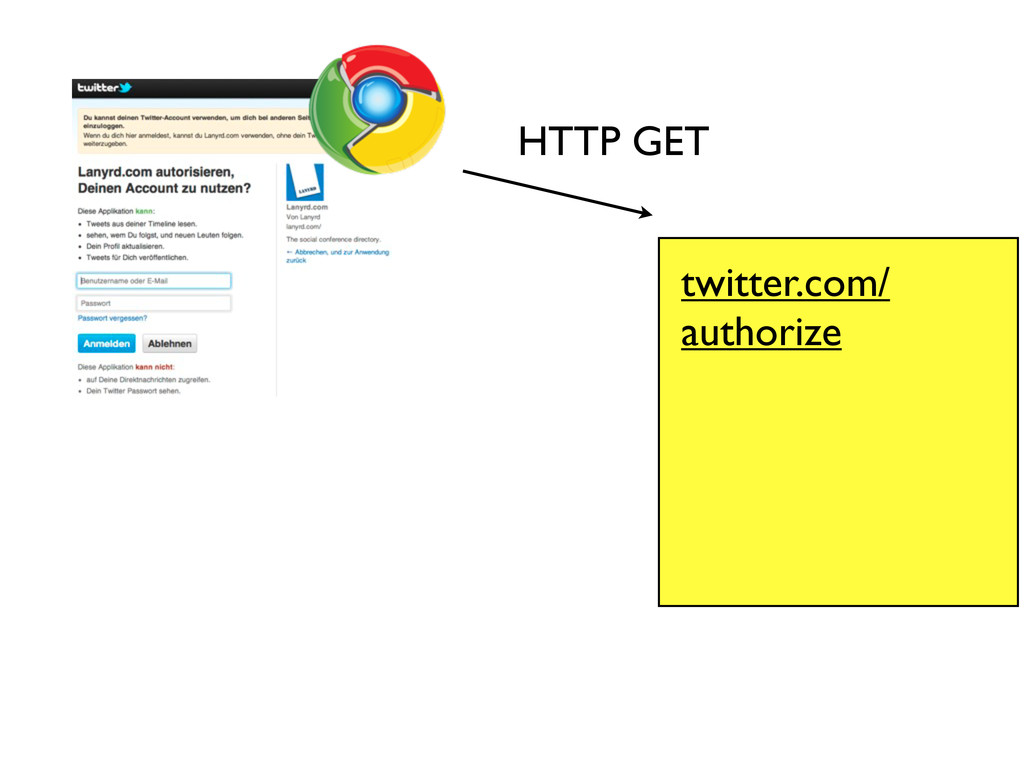
HTTP GET twitter.com/ authorize
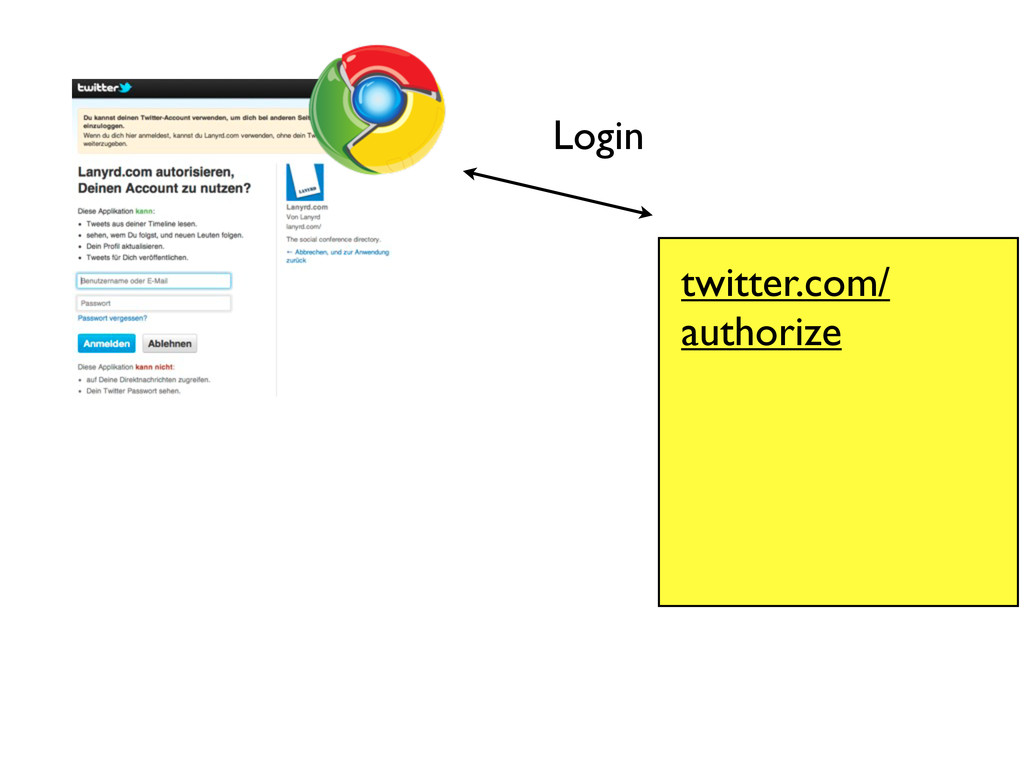
Login twitter.com/ authorize
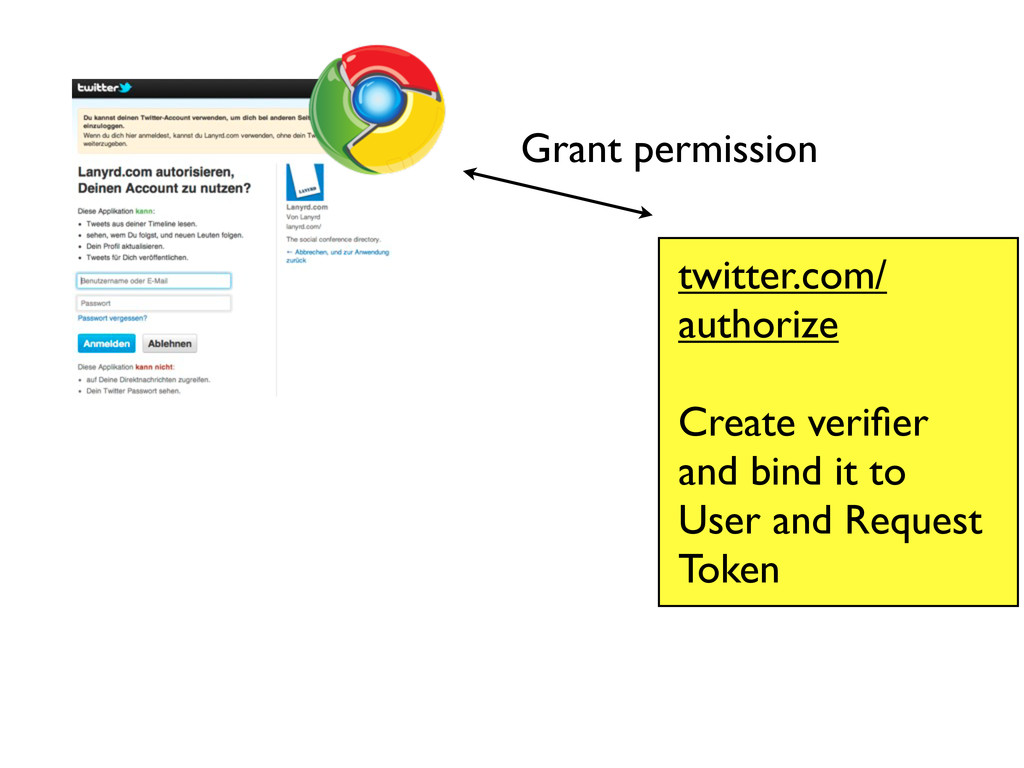
Grant permission twitter.com/ authorize Create verifier and bind it to
User and Request Token
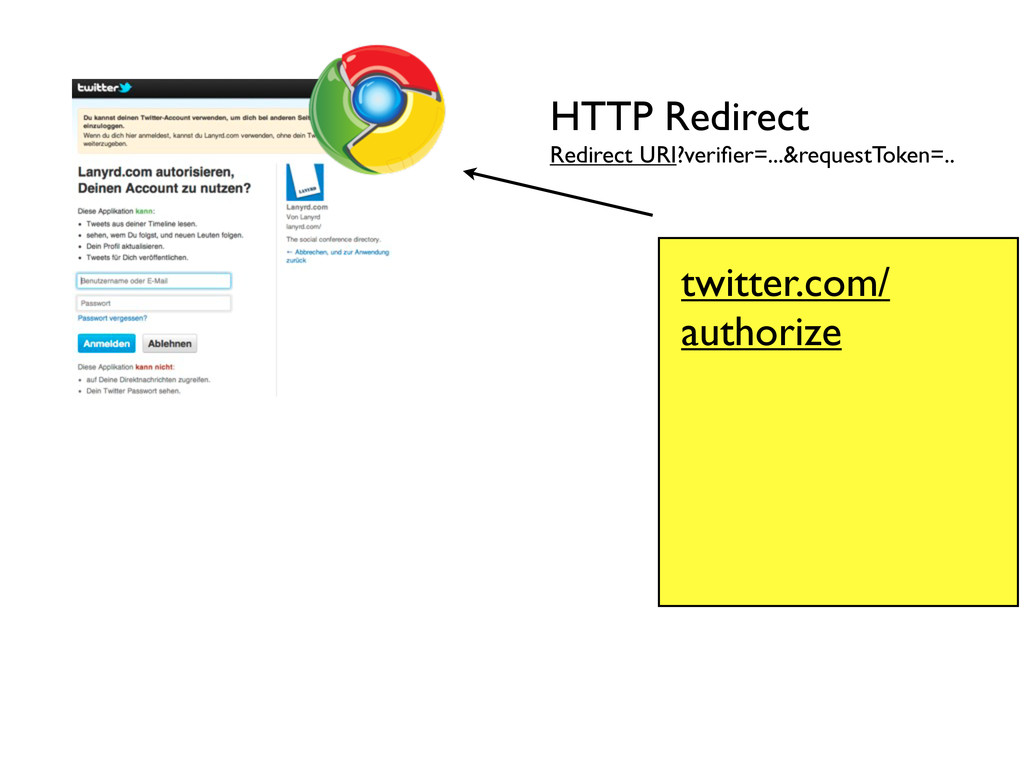
Redirect URI?verifier=...&requestToken=.. HTTP Redirect twitter.com/ authorize
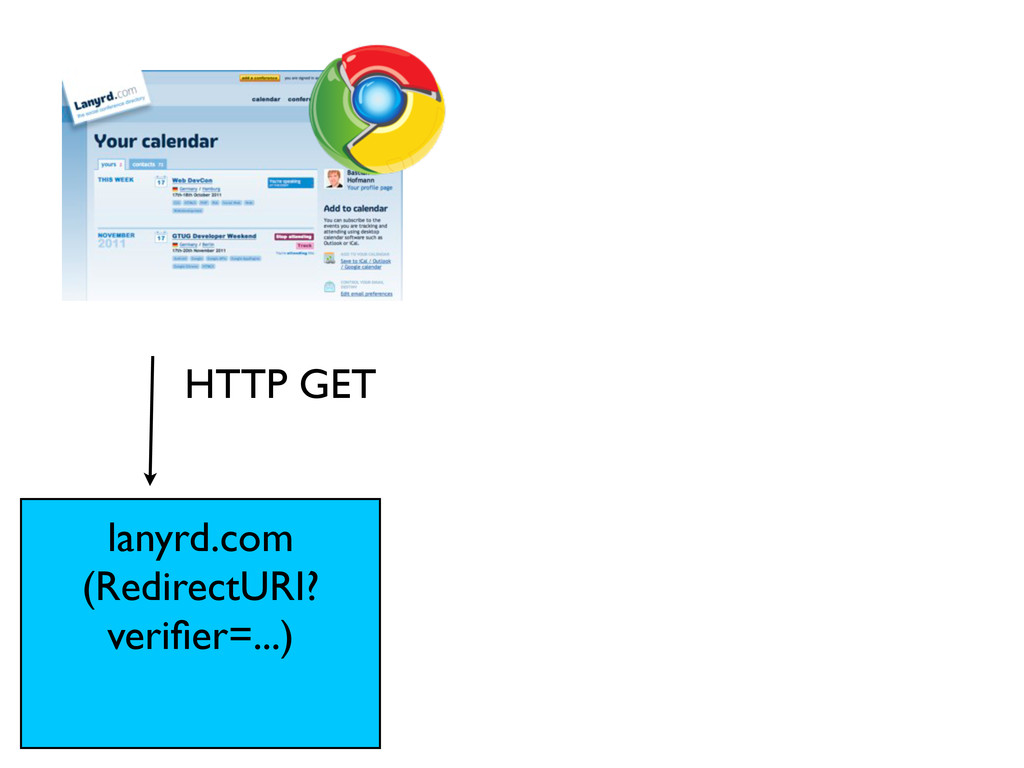
HTTP GET lanyrd.com (RedirectURI? verifier=...)
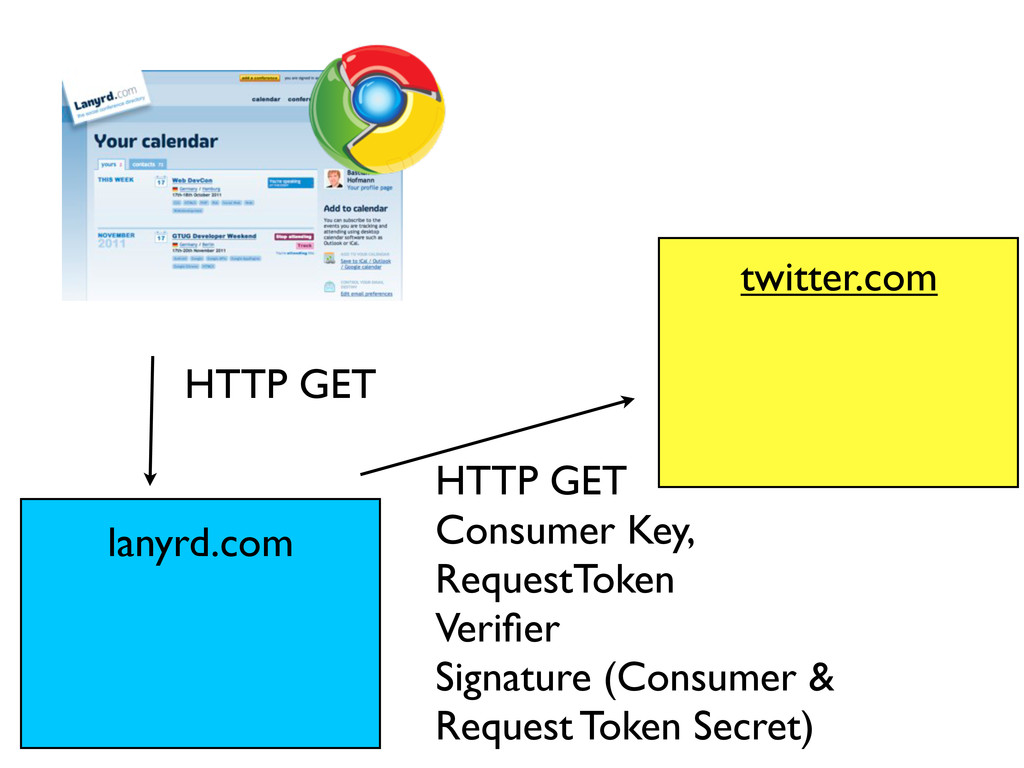
HTTP GET HTTP GET Consumer Key, RequestToken Verifier Signature (Consumer
& Request Token Secret) twitter.com lanyrd.com
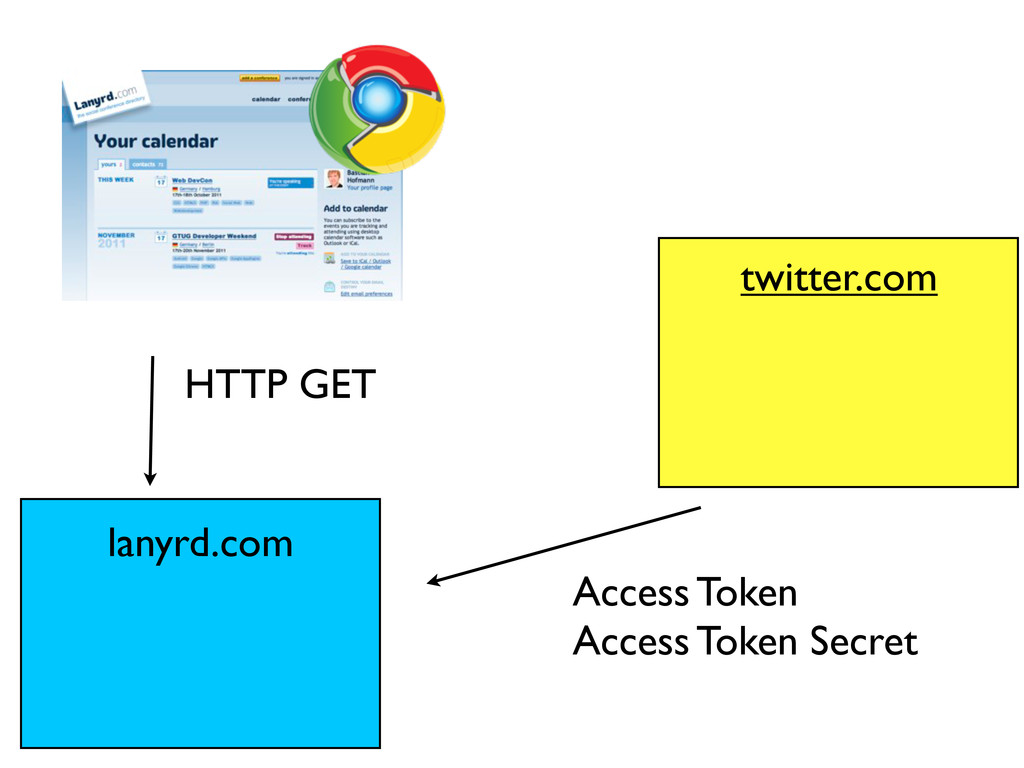
HTTP GET Access Token Access Token Secret twitter.com lanyrd.com
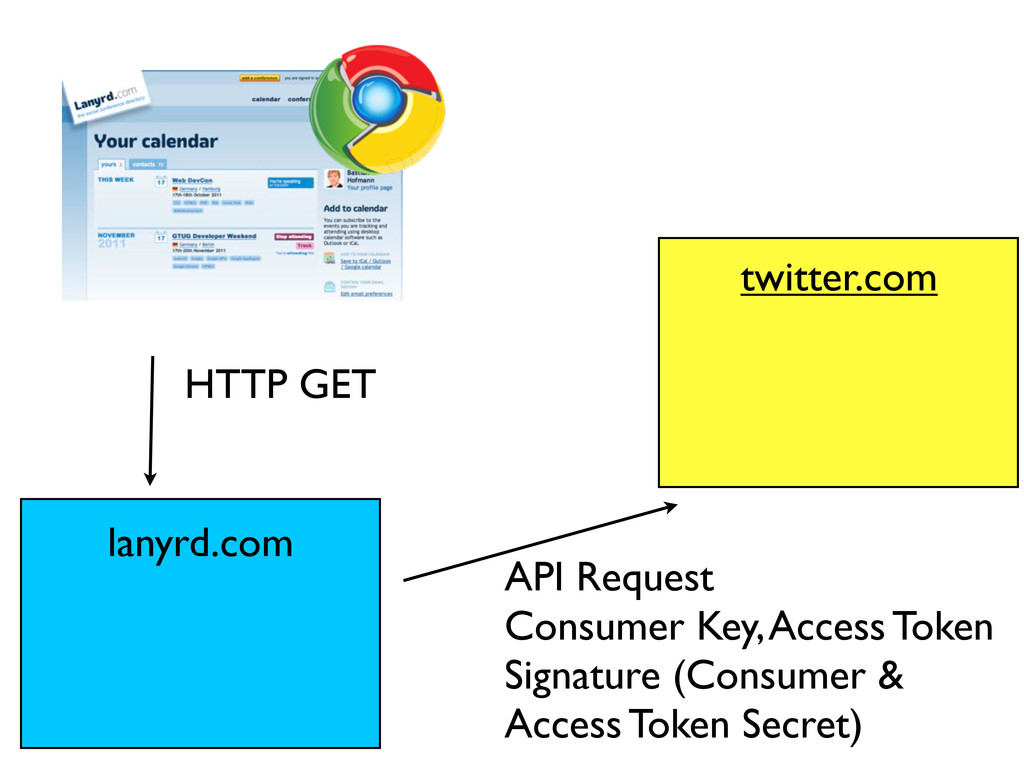
HTTP GET API Request Consumer Key, Access Token Signature (Consumer
& Access Token Secret) twitter.com lanyrd.com
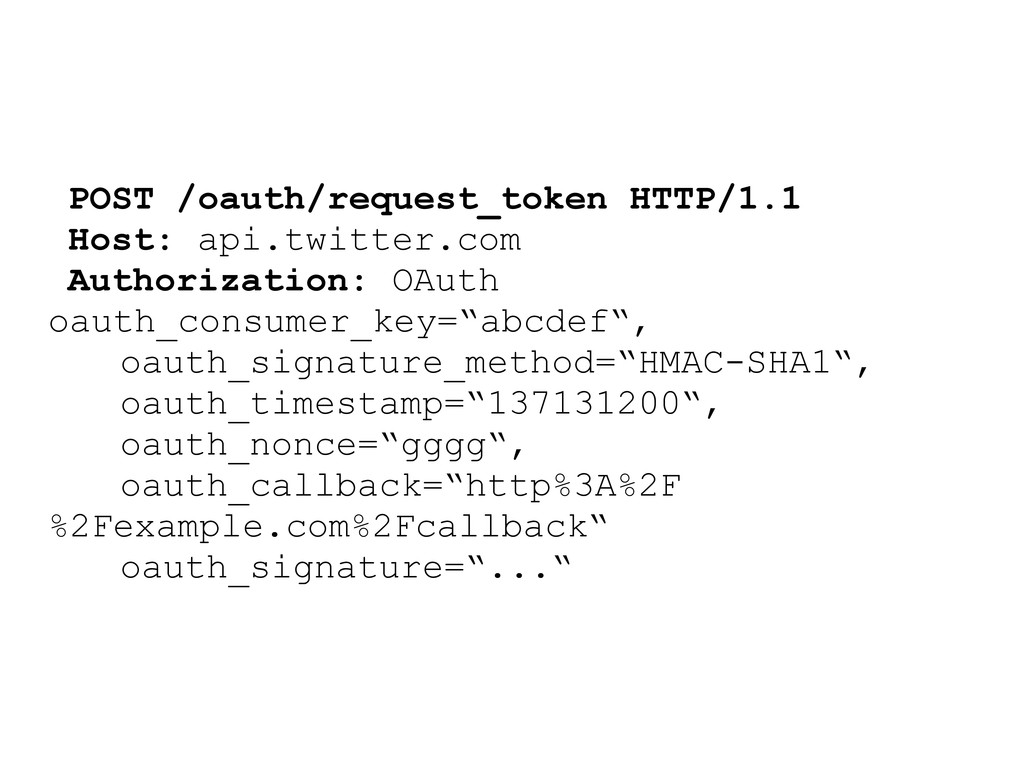
POST /oauth/request_token HTTP/1.1 Host: api.twitter.com Authorization: OAuth oauth_consumer_key=“abcdef“, oauth_signature_method=“HMAC-SHA1“, oauth_timestamp=“137131200“,
oauth_nonce=“gggg“, oauth_callback=“http%3A%2F %2Fexample.com%2Fcallback“ oauth_signature=“...“
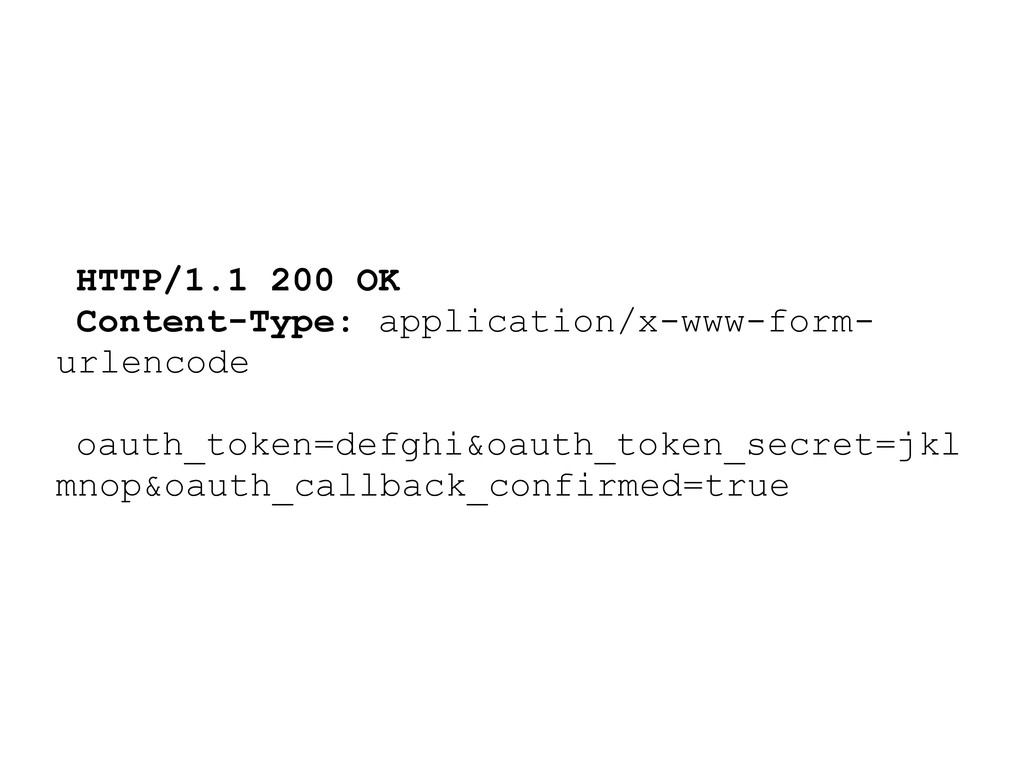
HTTP/1.1 200 OK Content-Type: application/x-www-form- urlencode oauth_token=defghi&oauth_token_secret=jkl mnop&oauth_callback_confirmed=true
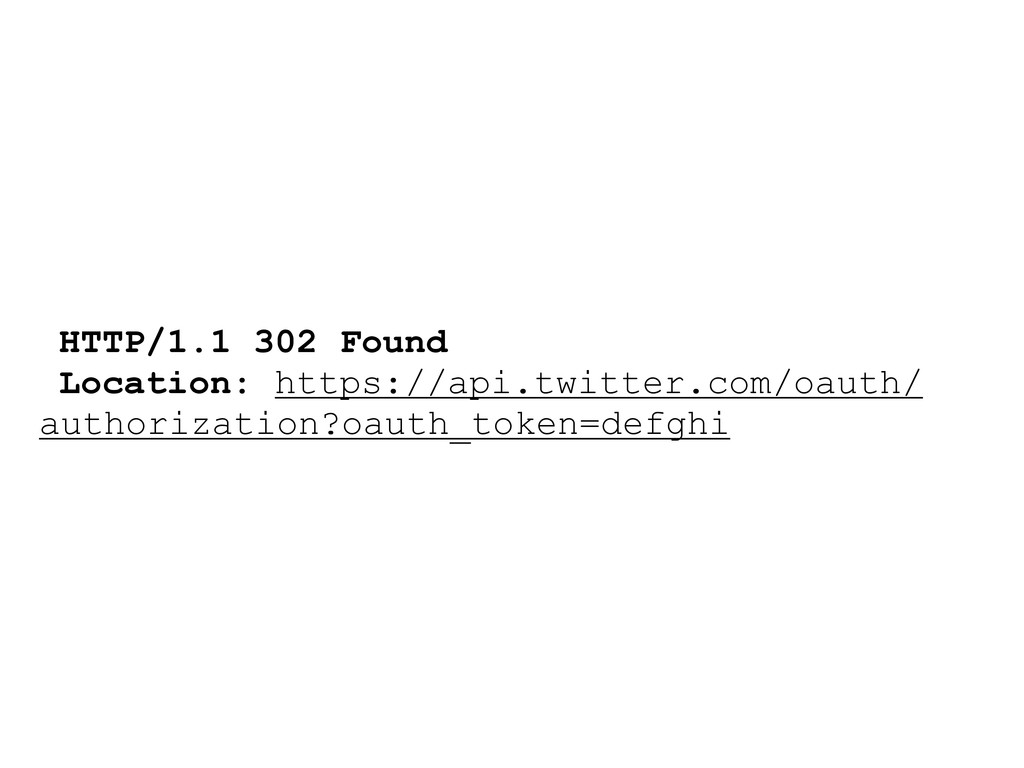
HTTP/1.1 302 Found Location: https://api.twitter.com/oauth/ authorization?oauth_token=defghi
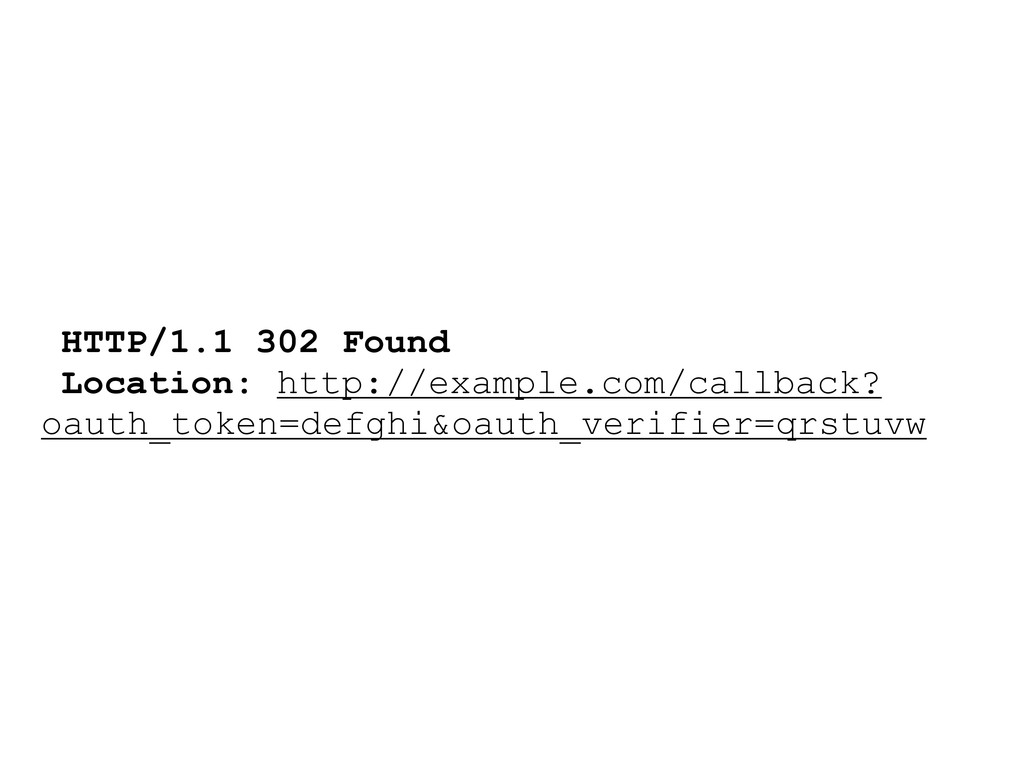
HTTP/1.1 302 Found Location: http://example.com/callback? oauth_token=defghi&oauth_verifier=qrstuvw
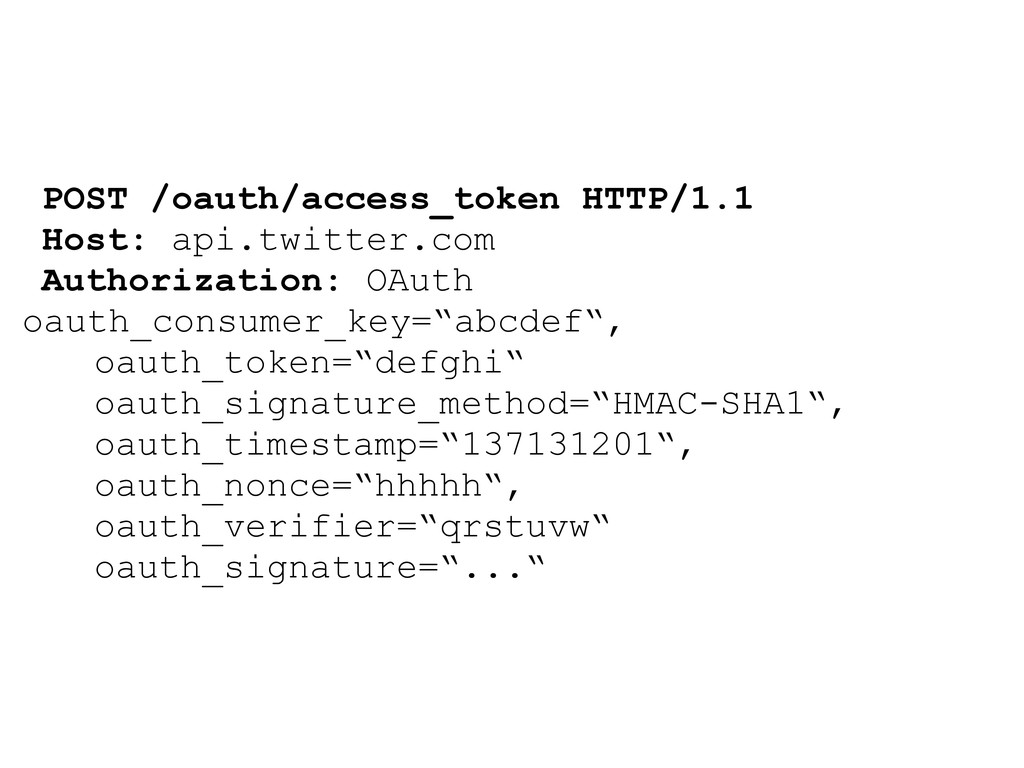
POST /oauth/access_token HTTP/1.1 Host: api.twitter.com Authorization: OAuth oauth_consumer_key=“abcdef“, oauth_token=“defghi“ oauth_signature_method=“HMAC-SHA1“,
oauth_timestamp=“137131201“, oauth_nonce=“hhhhh“, oauth_verifier=“qrstuvw“ oauth_signature=“...“
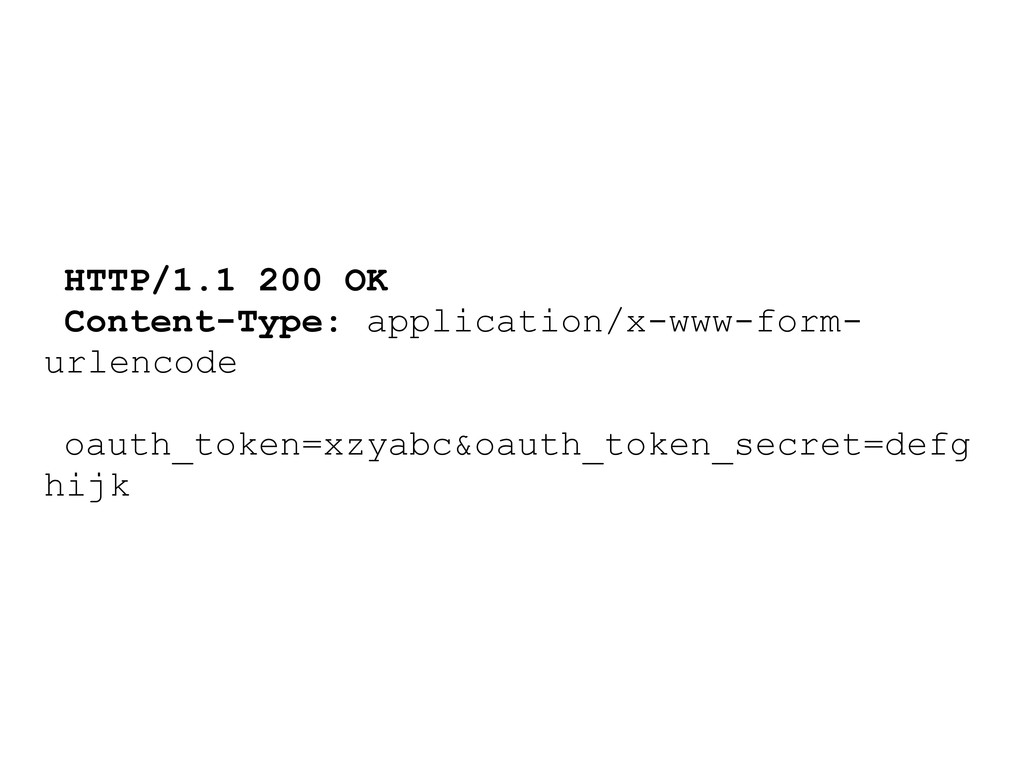
HTTP/1.1 200 OK Content-Type: application/x-www-form- urlencode oauth_token=xzyabc&oauth_token_secret=defg hijk
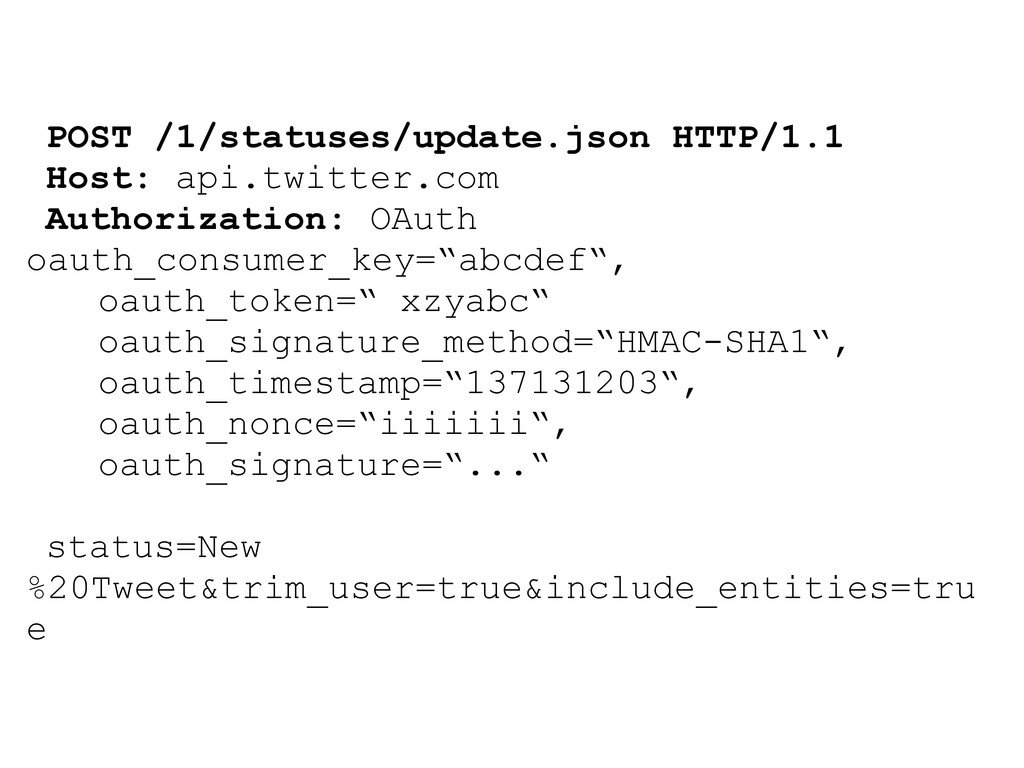
POST /1/statuses/update.json HTTP/1.1 Host: api.twitter.com Authorization: OAuth oauth_consumer_key=“abcdef“, oauth_token=“ xzyabc“
oauth_signature_method=“HMAC-SHA1“, oauth_timestamp=“137131203“, oauth_nonce=“iiiiiii“, oauth_signature=“...“ status=New %20Tweet&trim_user=true&include_entities=tru e
Signatures
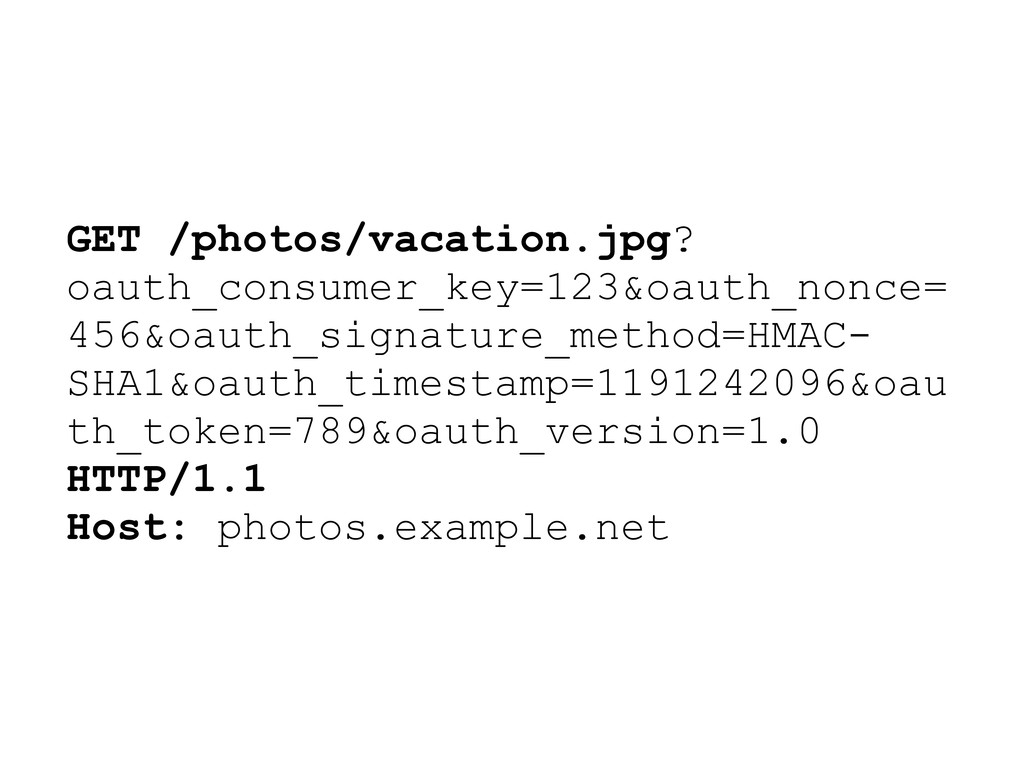
GET /photos/vacation.jpg? oauth_consumer_key=123&oauth_nonce= 456&oauth_signature_method=HMAC- SHA1&oauth_timestamp=1191242096&oau th_token=789&oauth_version=1.0 HTTP/1.1 Host: photos.example.net
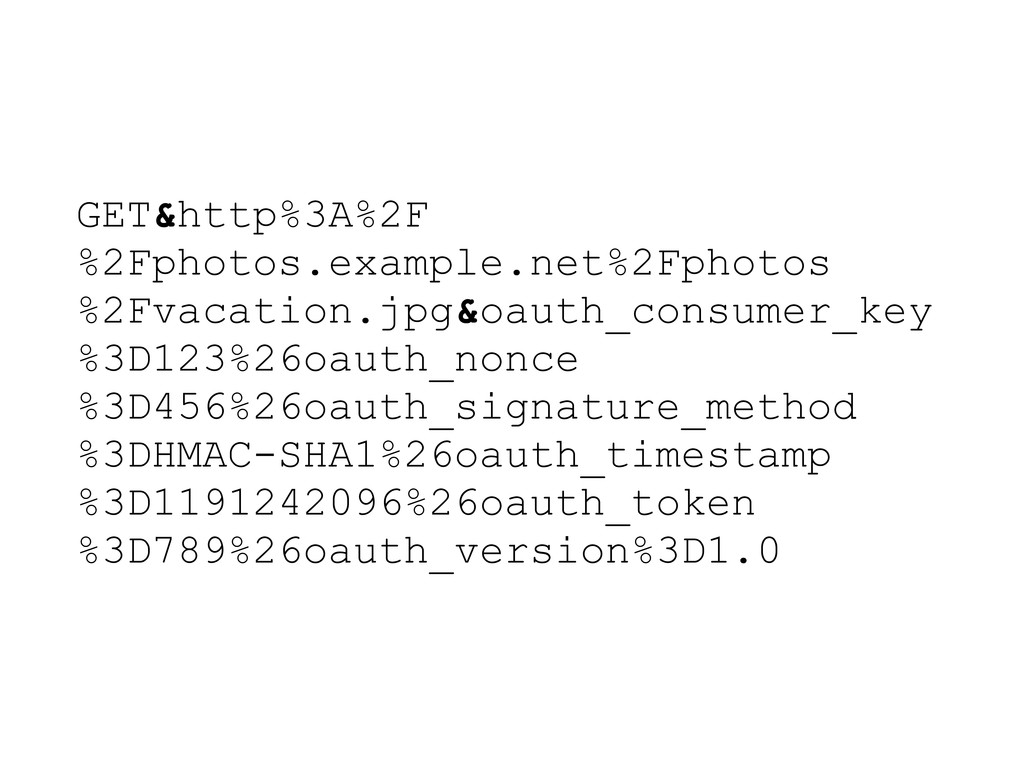
GET&http%3A%2F %2Fphotos.example.net%2Fphotos %2Fvacation.jpg&oauth_consumer_key %3D123%26oauth_nonce %3D456%26oauth_signature_method %3DHMAC-SHA1%26oauth_timestamp %3D1191242096%26oauth_token %3D789%26oauth_version%3D1.0
PLAINTEXT
HMAC-SHA1 Salt: consumerSecret(&tokenSecret)
RSA-SHA1 Public/Private Key
DEMO
http://oauth.googlecode.com/svn/code/java/
Problems Does not work well with non web or JavaScript
based clients The „Invalid Signature“ Problem Complicated Flow, many requests
How to fix it?
http://oauth.net/
http://tools.ietf.org/html/draft-ietf-oauth-v2
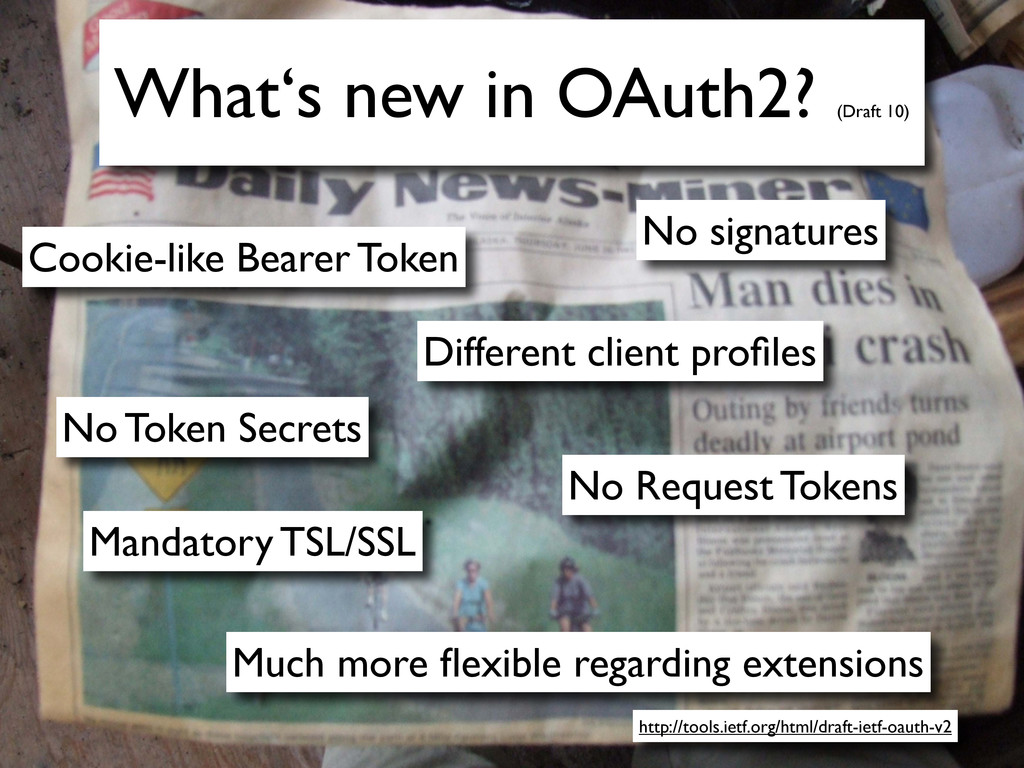
http://tools.ietf.org/html/draft-ietf-oauth-v2 What‘s new in OAuth2? (Draft 10) Different client profiles
No signatures No Token Secrets Cookie-like Bearer Token No Request Tokens Much more flexible regarding extensions Mandatory TSL/SSL
Web-Server Profile
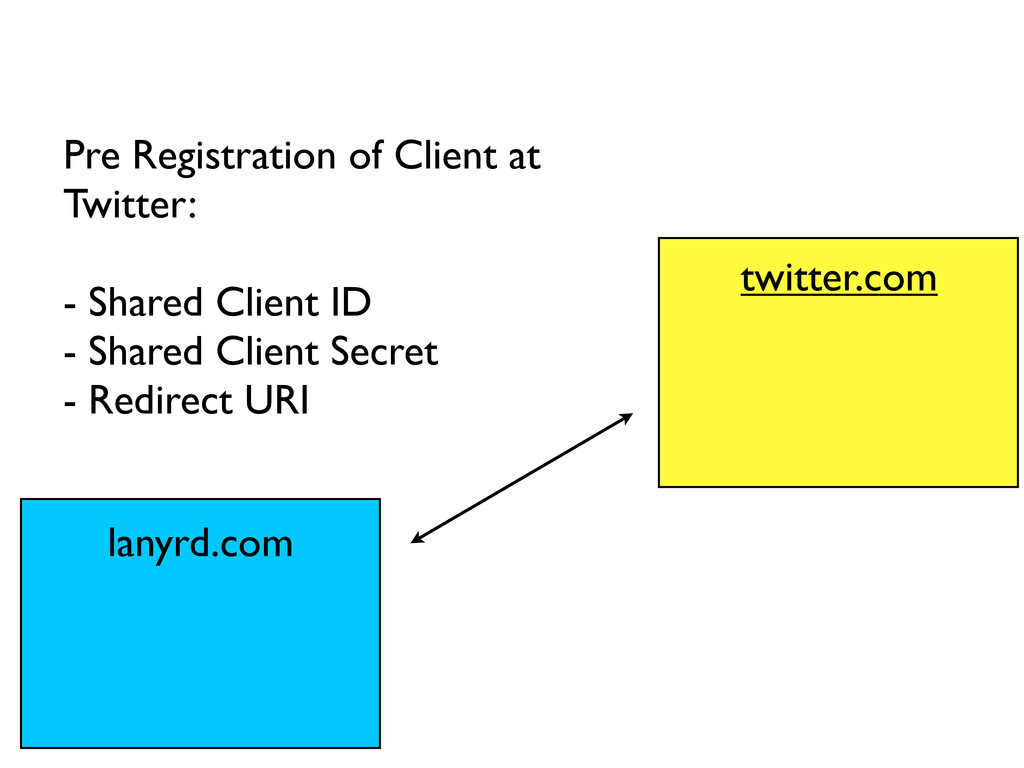
lanyrd.com twitter.com Pre Registration of Client at Twitter: - Shared
Client ID - Shared Client Secret - Redirect URI
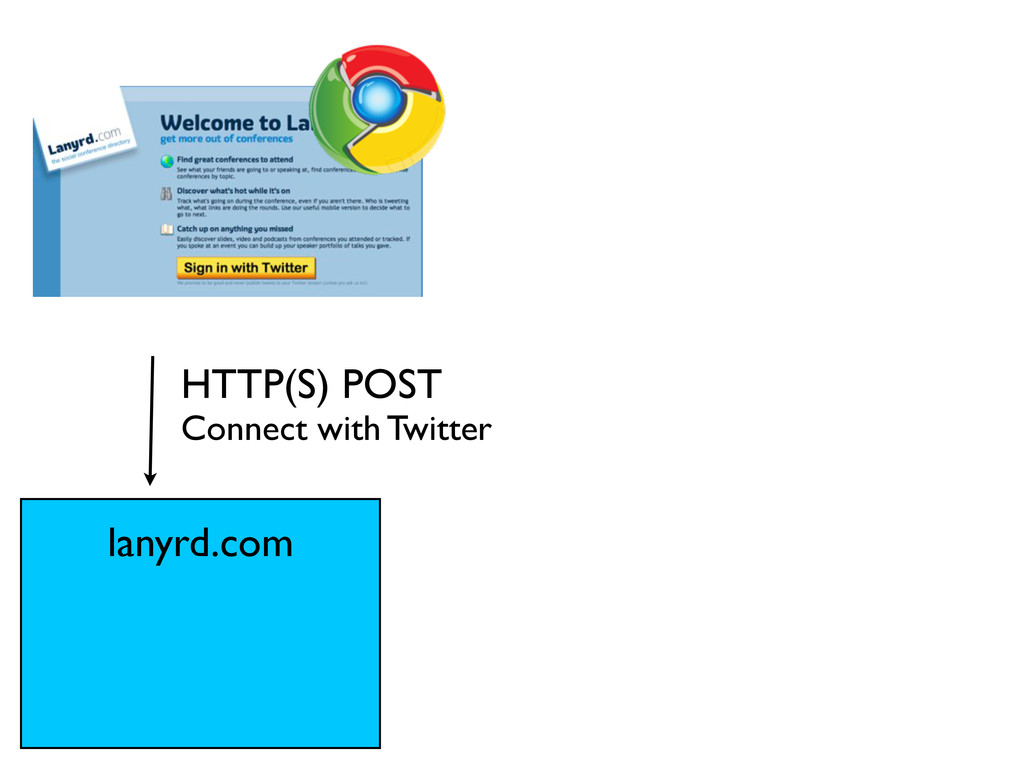
HTTP(S) POST Connect with Twitter lanyrd.com
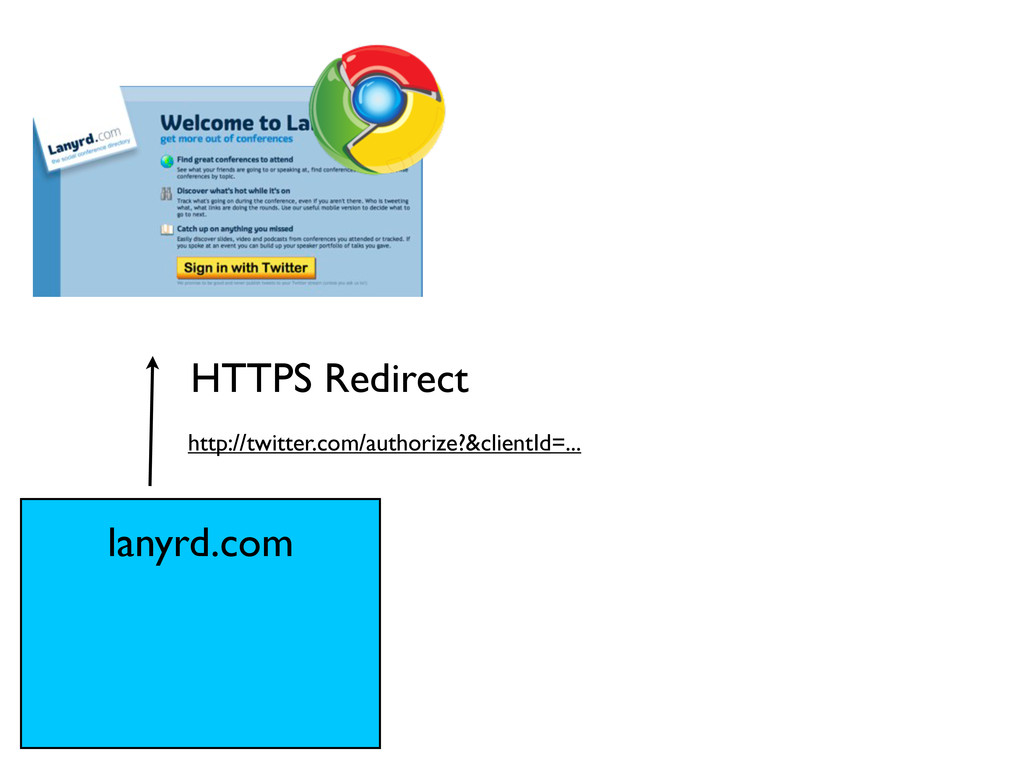
http://twitter.com/authorize?&clientId=... HTTPS Redirect lanyrd.com
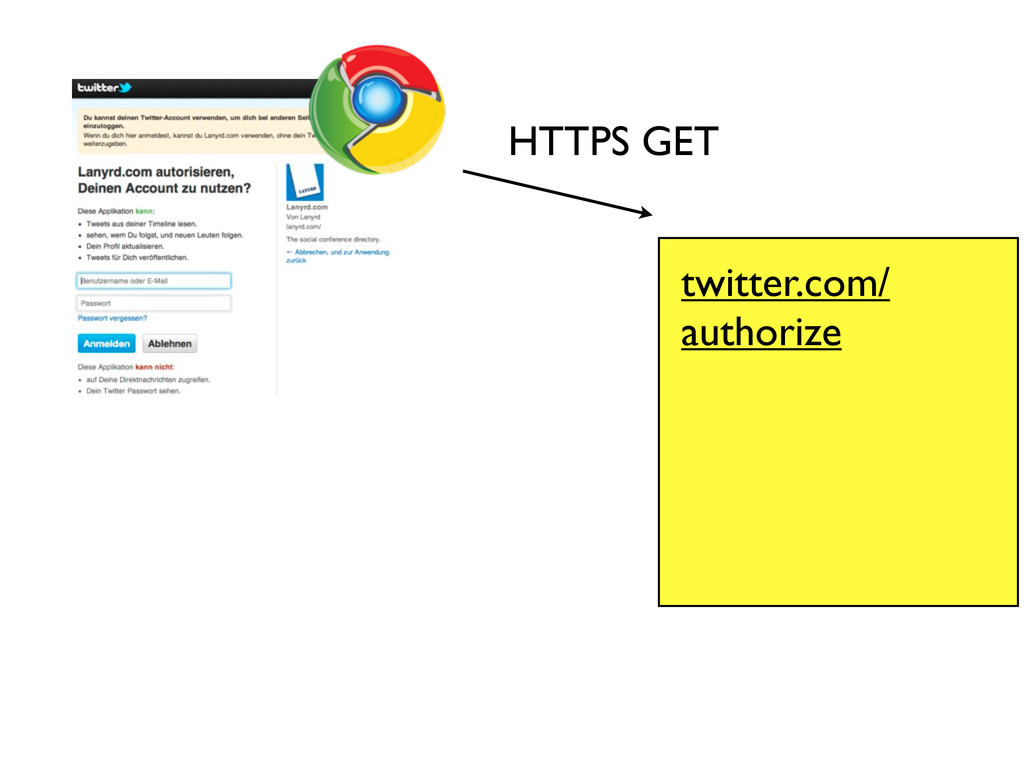
HTTPS GET twitter.com/ authorize
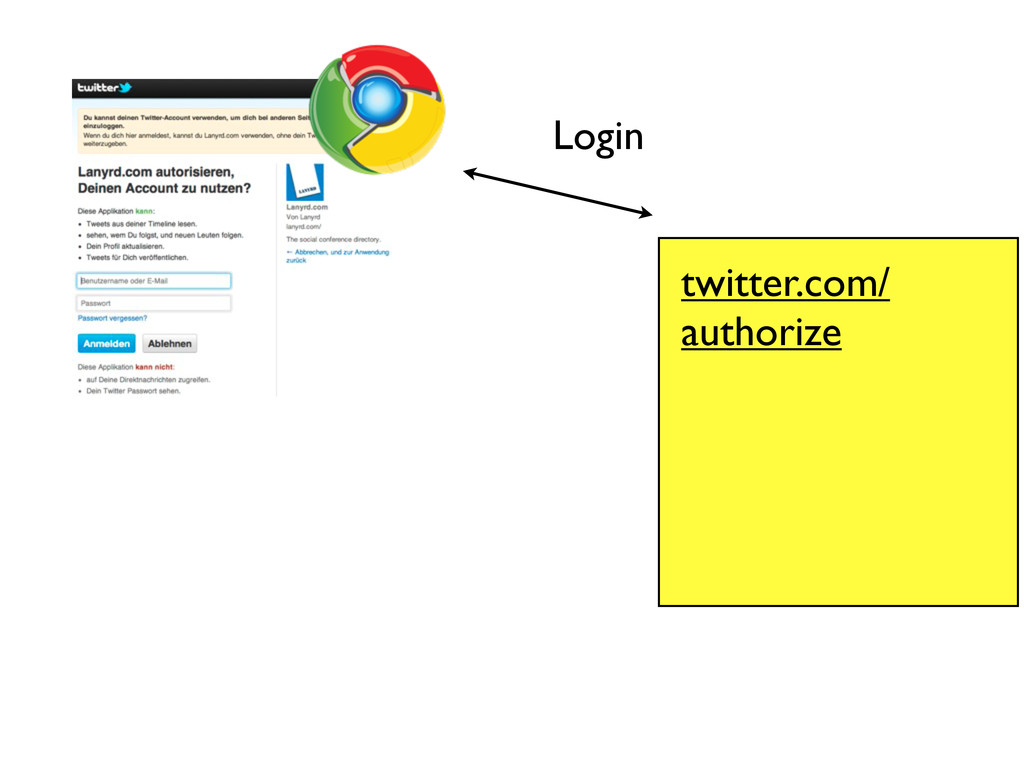
Login twitter.com/ authorize
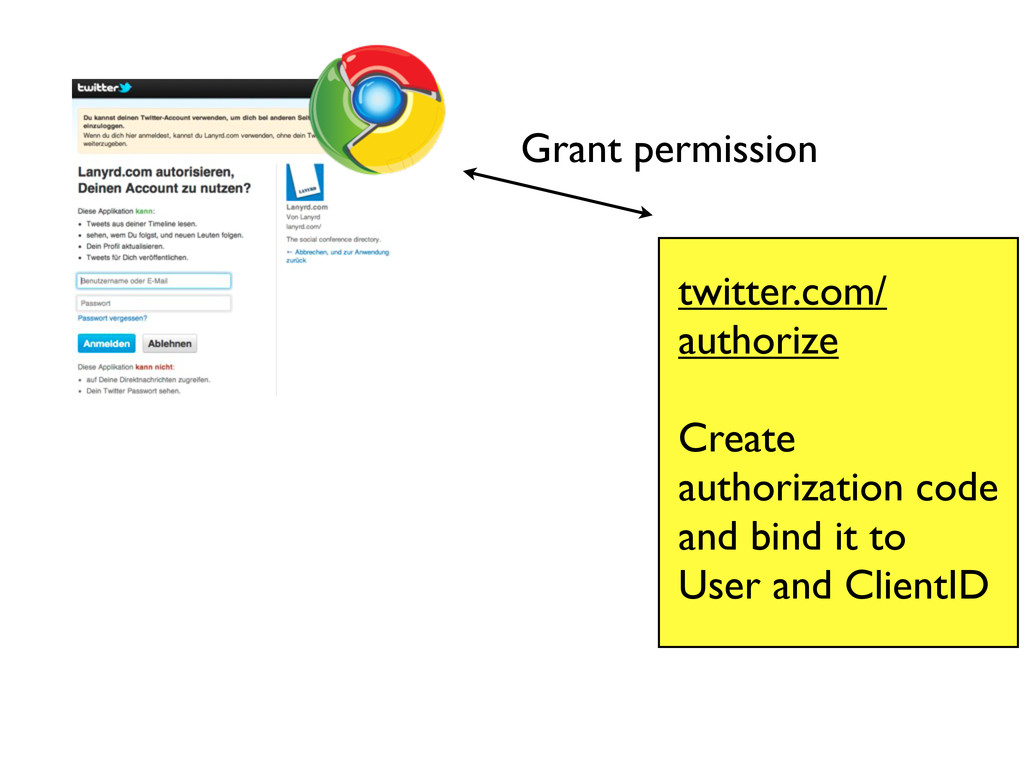
Grant permission twitter.com/ authorize Create authorization code and bind it
to User and ClientID
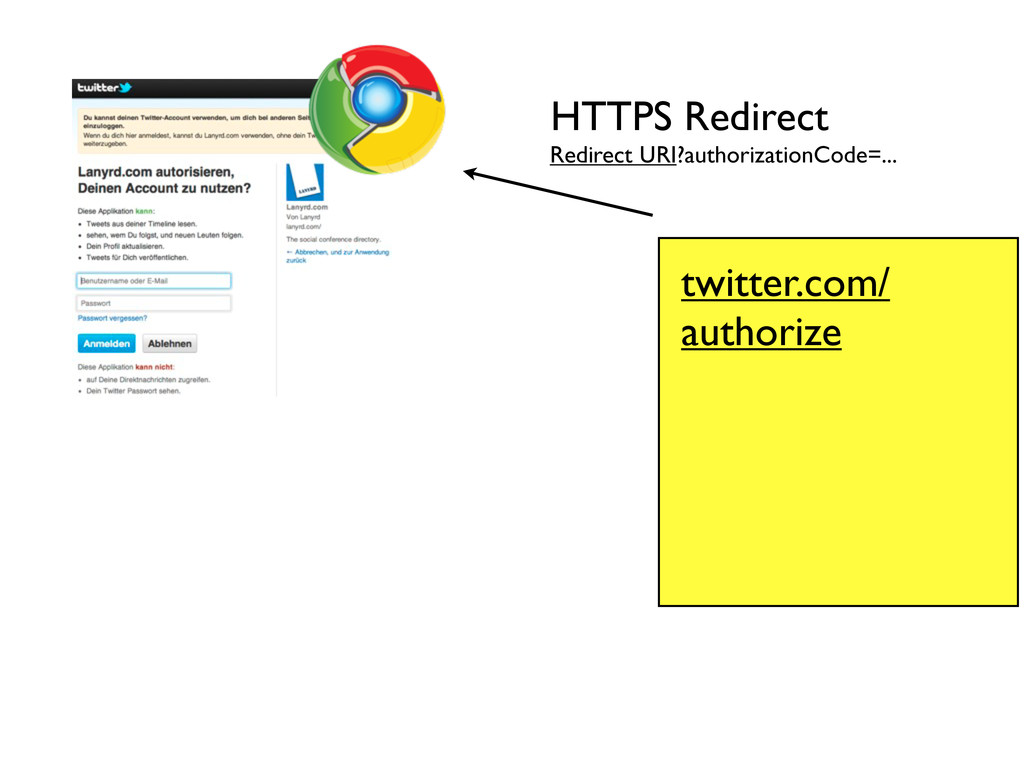
Redirect URI?authorizationCode=... HTTPS Redirect twitter.com/ authorize
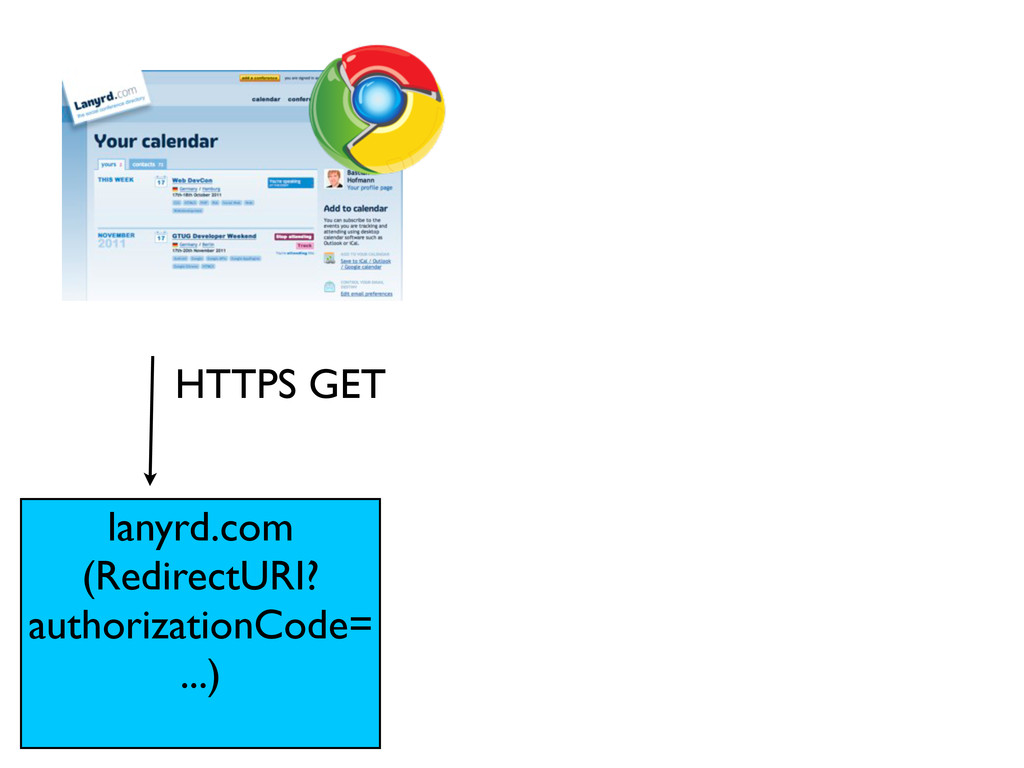
HTTPS GET lanyrd.com (RedirectURI? authorizationCode= ...)
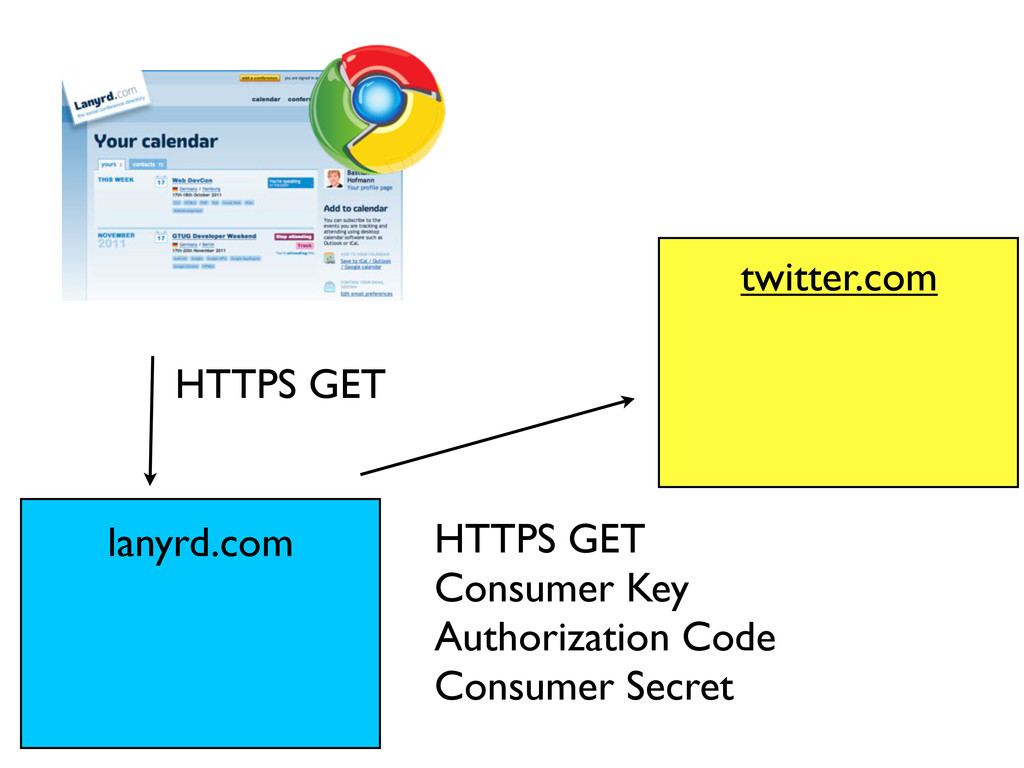
HTTPS GET HTTPS GET Consumer Key Authorization Code Consumer Secret
twitter.com lanyrd.com
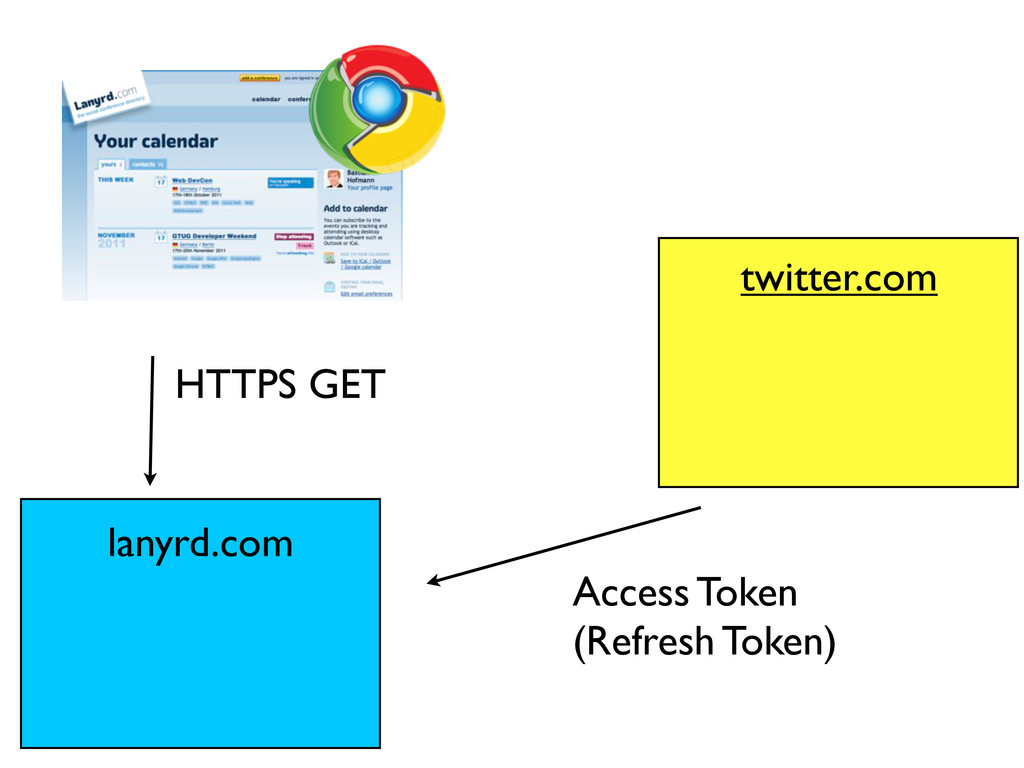
HTTPS GET Access Token (Refresh Token) twitter.com lanyrd.com
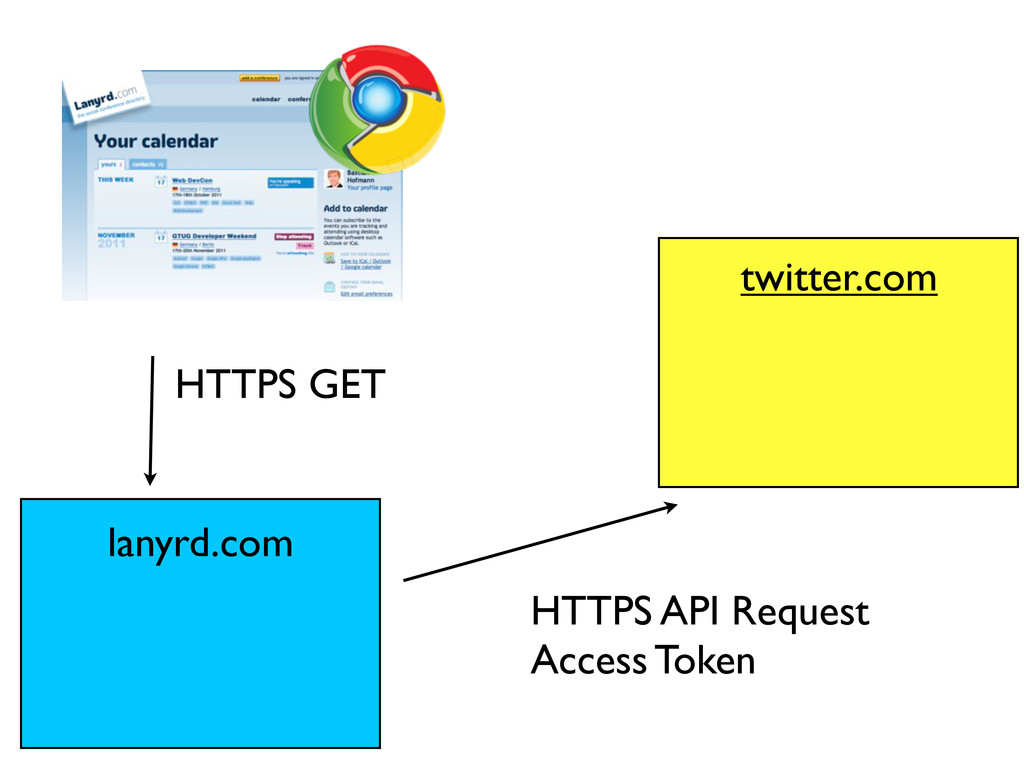
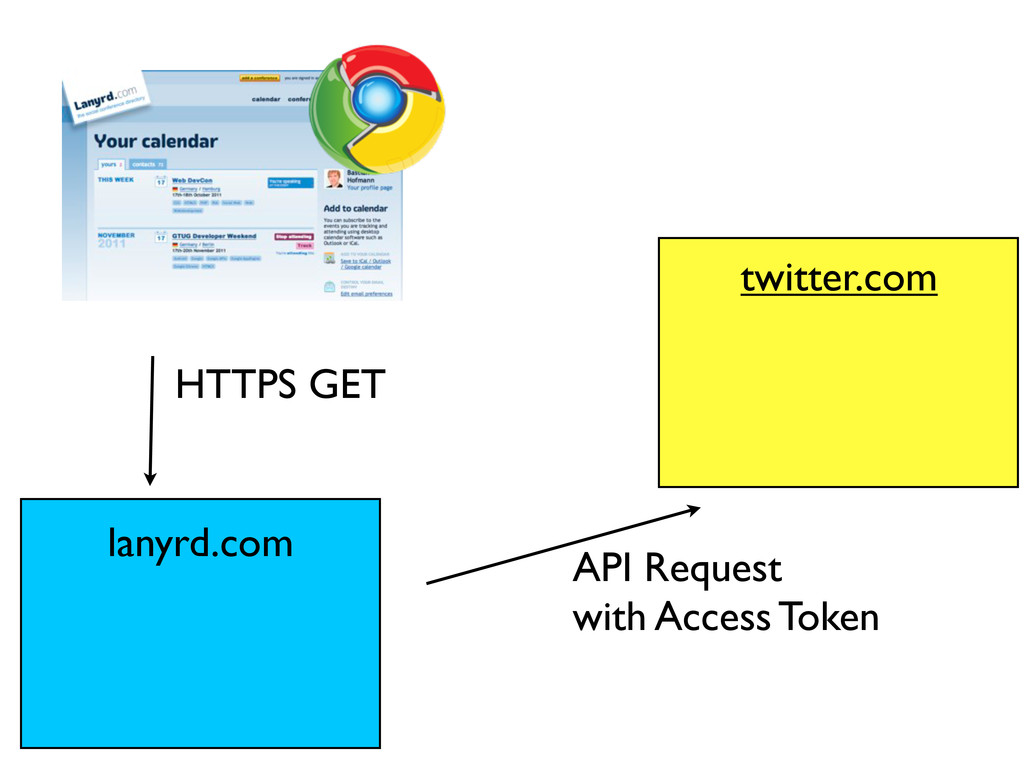
HTTPS GET HTTPS API Request Access Token twitter.com lanyrd.com
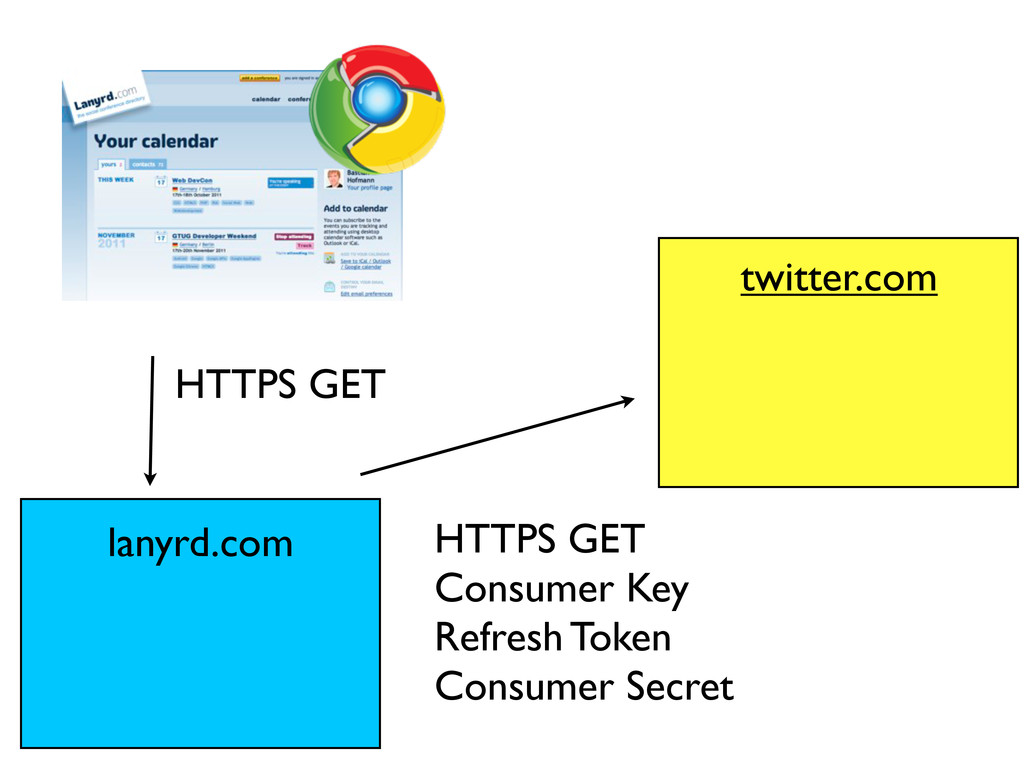
HTTPS GET HTTPS GET Consumer Key Refresh Token Consumer Secret
twitter.com lanyrd.com
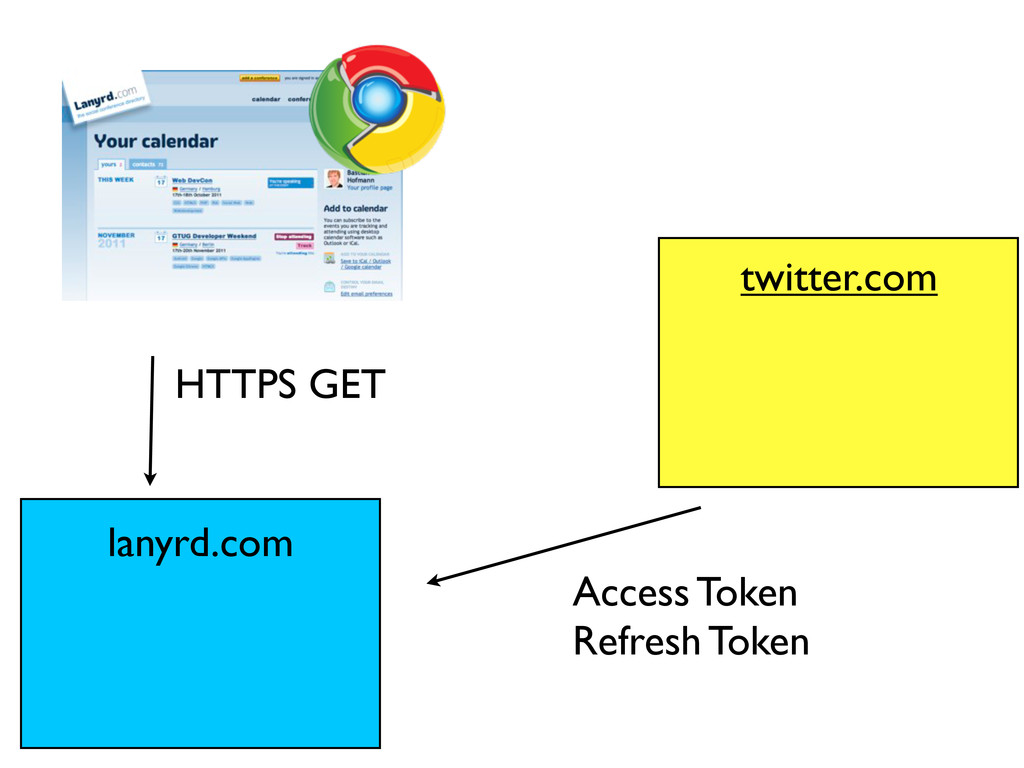
HTTPS GET Access Token Refresh Token twitter.com lanyrd.com
HTTPS GET API Request with Access Token twitter.com lanyrd.com
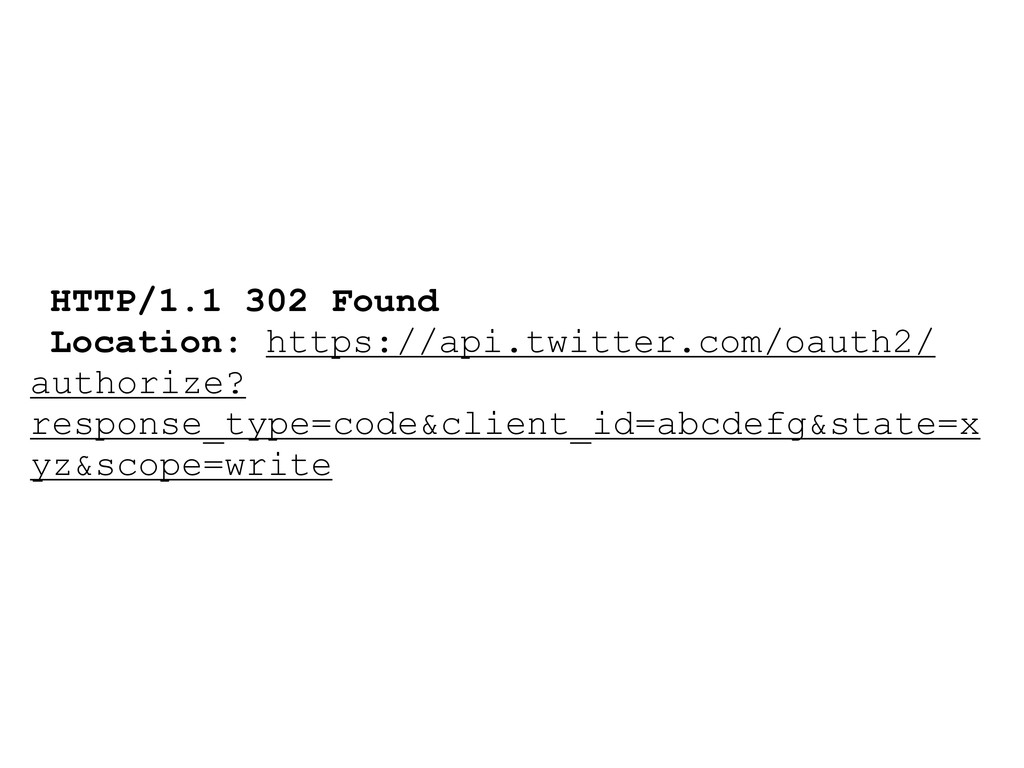
HTTP/1.1 302 Found Location: https://api.twitter.com/oauth2/ authorize? response_type=code&client_id=abcdefg&state=x yz&scope=write
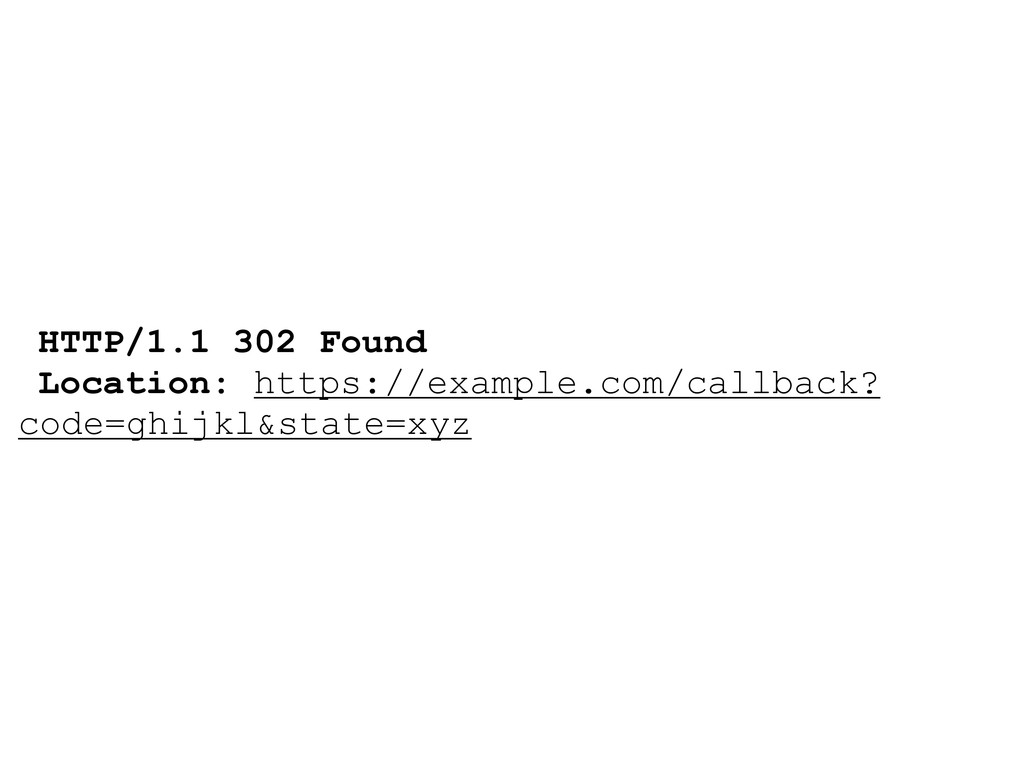
HTTP/1.1 302 Found Location: https://example.com/callback? code=ghijkl&state=xyz
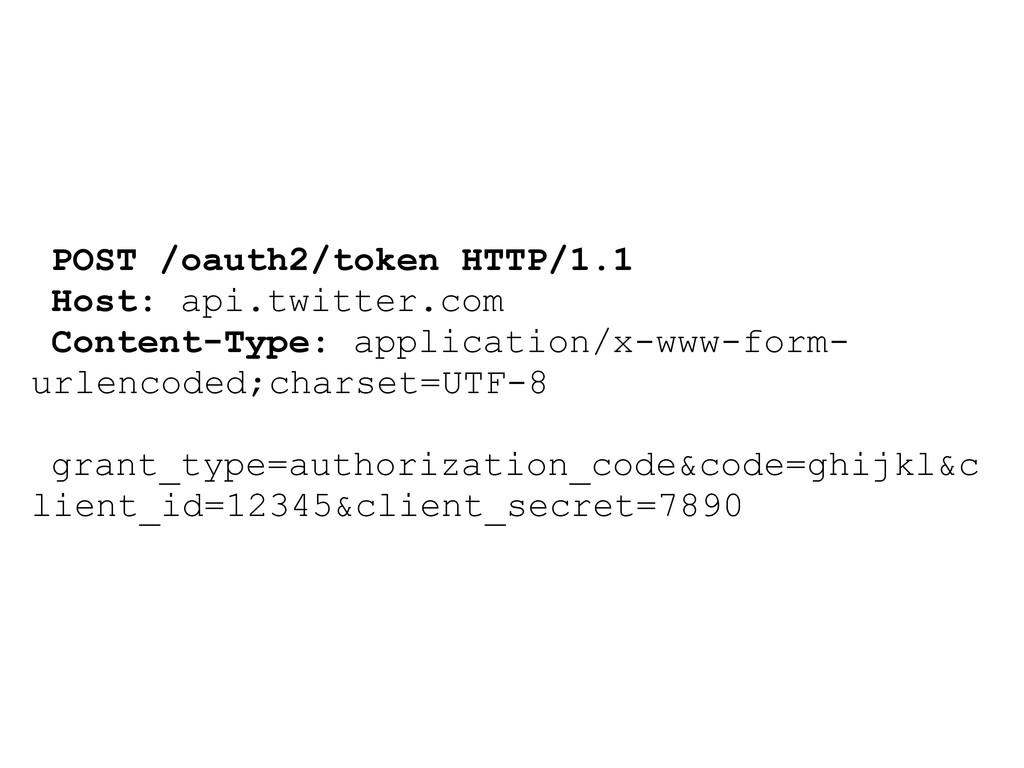
POST /oauth2/token HTTP/1.1 Host: api.twitter.com Content-Type: application/x-www-form- urlencoded;charset=UTF-8 grant_type=authorization_code&code=ghijkl&c lient_id=12345&client_secret=7890
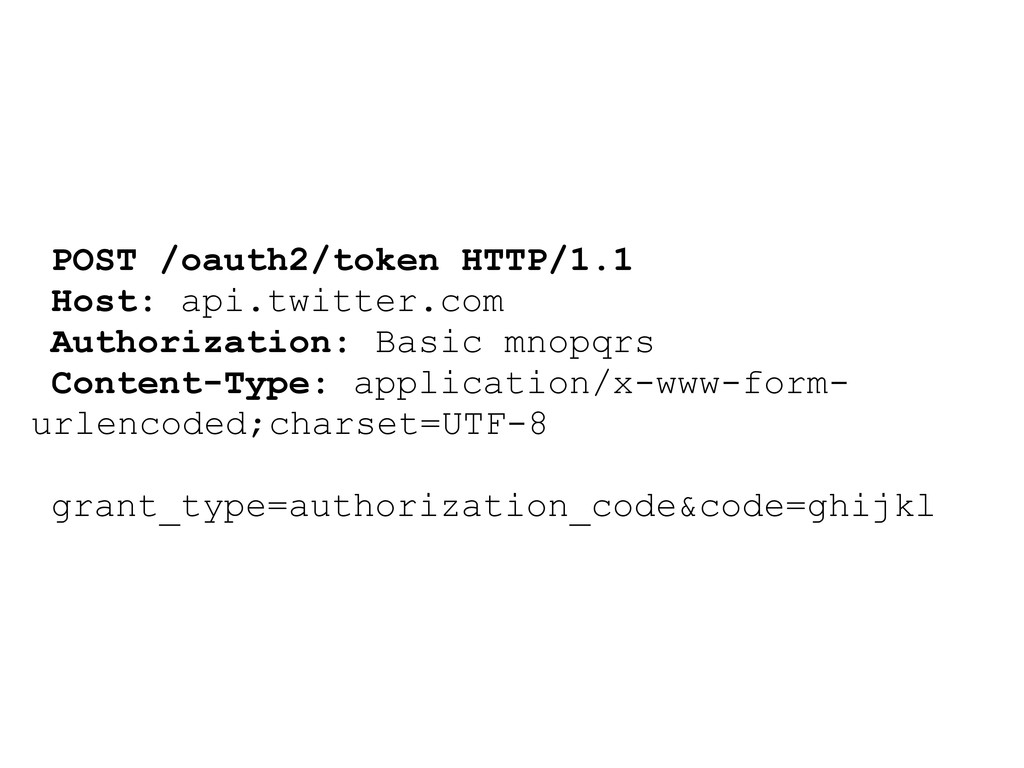
POST /oauth2/token HTTP/1.1 Host: api.twitter.com Authorization: Basic mnopqrs Content-Type: application/x-www-form-
urlencoded;charset=UTF-8 grant_type=authorization_code&code=ghijkl
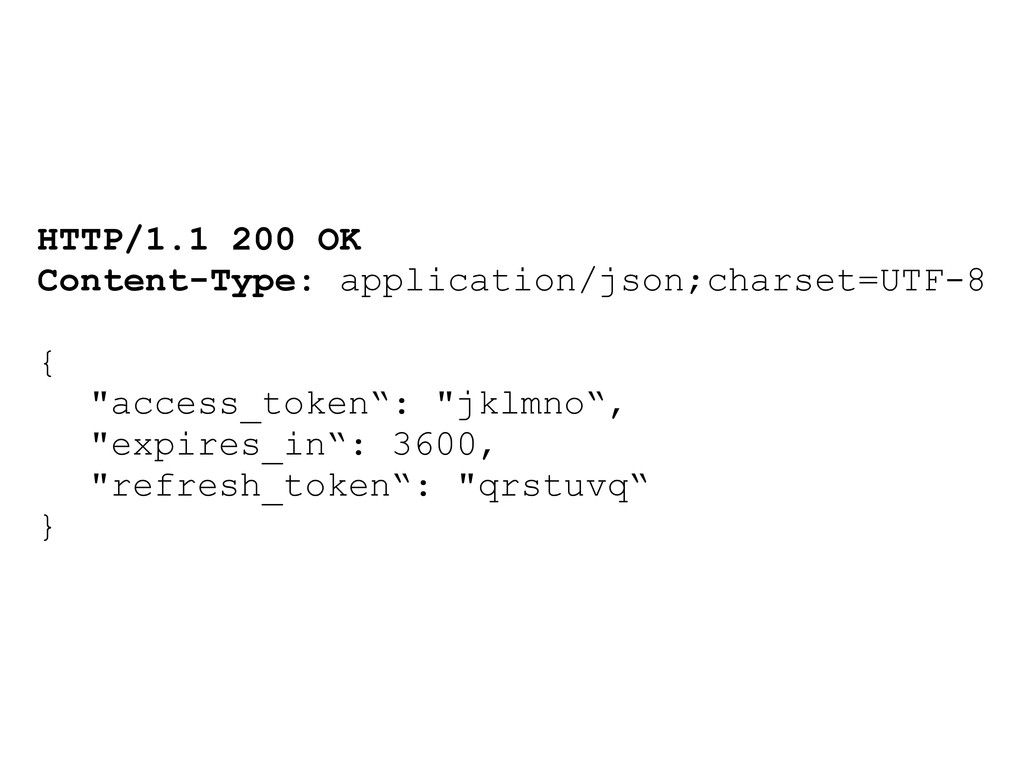
HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 { "access_token“: "jklmno“, "expires_in“: 3600,
"refresh_token“: "qrstuvq“ }
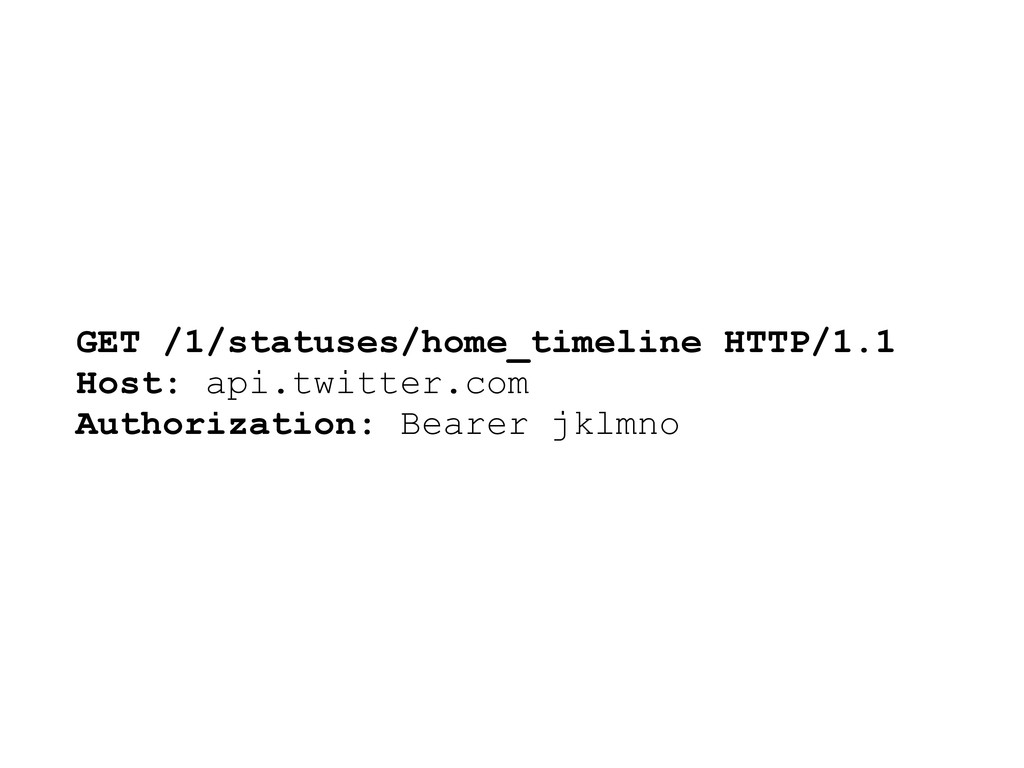
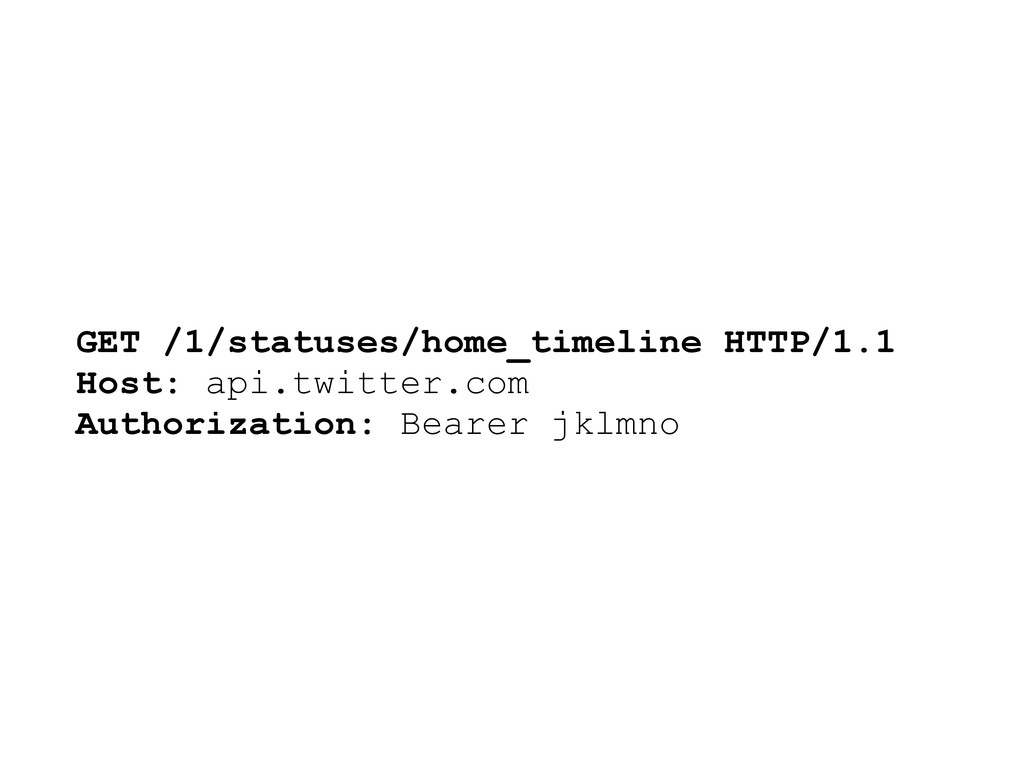
GET /1/statuses/home_timeline HTTP/1.1 Host: api.twitter.com Authorization: Bearer jklmno
DEMO
https://github.com/bashofmann/oauth2_java_webapp_example http://code.google.com/p/google-oauth-java-client/
Refresh Token
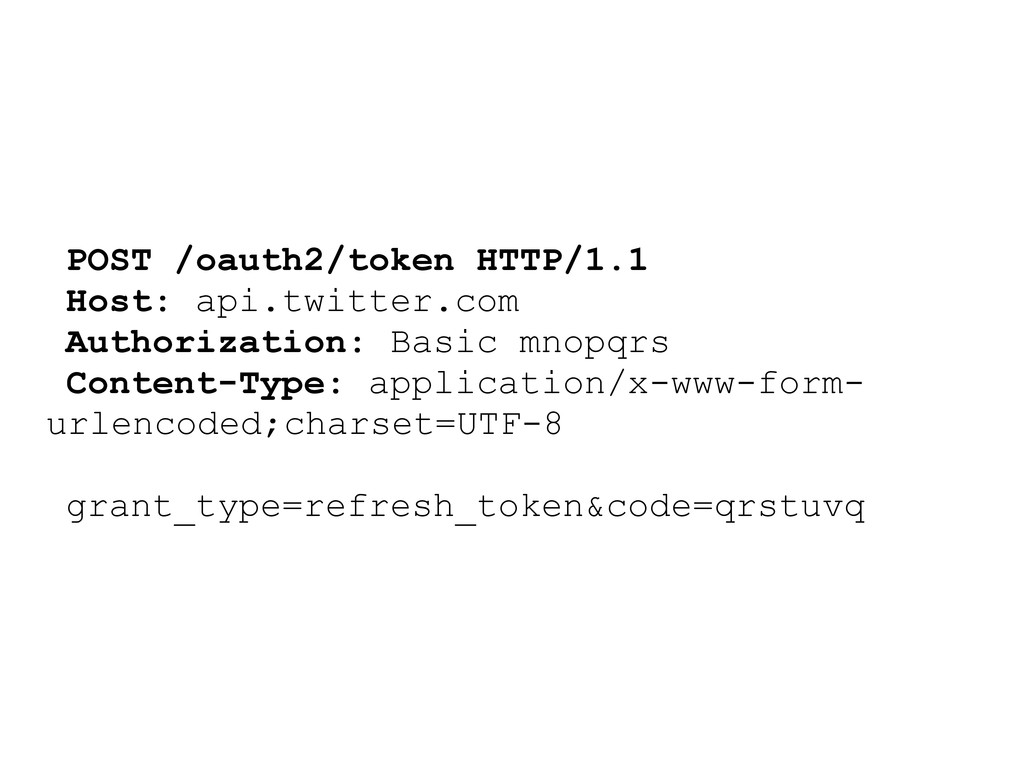
POST /oauth2/token HTTP/1.1 Host: api.twitter.com Authorization: Basic mnopqrs Content-Type: application/x-www-form-
urlencoded;charset=UTF-8 grant_type=refresh_token&code=qrstuvq
Authorization Types
Bearer Tokens
http://tools.ietf.org/html/draft-ietf-oauth-v2-bearer
GET /1/statuses/home_timeline HTTP/1.1 Host: api.twitter.com Authorization: Bearer jklmno
SSL not possible?
Signatures
http://tools.ietf.org/html/draft-ietf-oauth-v2-http-mac
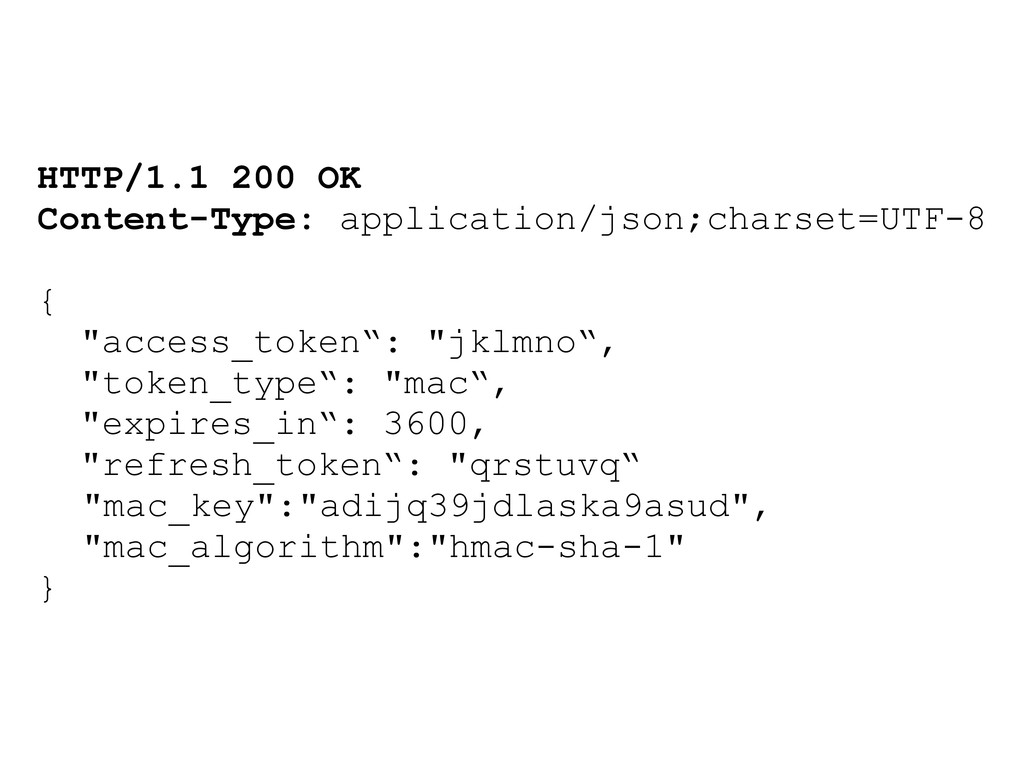
HTTP/1.1 200 OK Content-Type: application/json;charset=UTF-8 { "access_token“: "jklmno“, "token_type“: "mac“,
"expires_in“: 3600, "refresh_token“: "qrstuvq“ "mac_key":"adijq39jdlaska9asud", "mac_algorithm":"hmac-sha-1" }
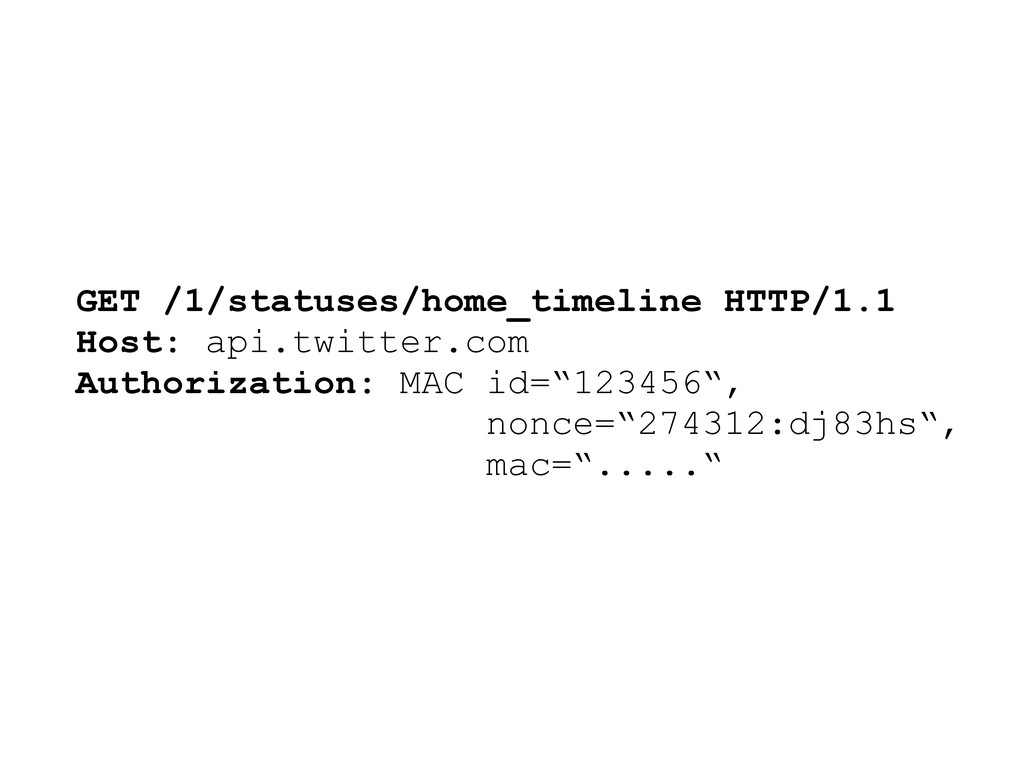
GET /1/statuses/home_timeline HTTP/1.1 Host: api.twitter.com Authorization: MAC id=“123456“, nonce=“274312:dj83hs“, mac=“.....“
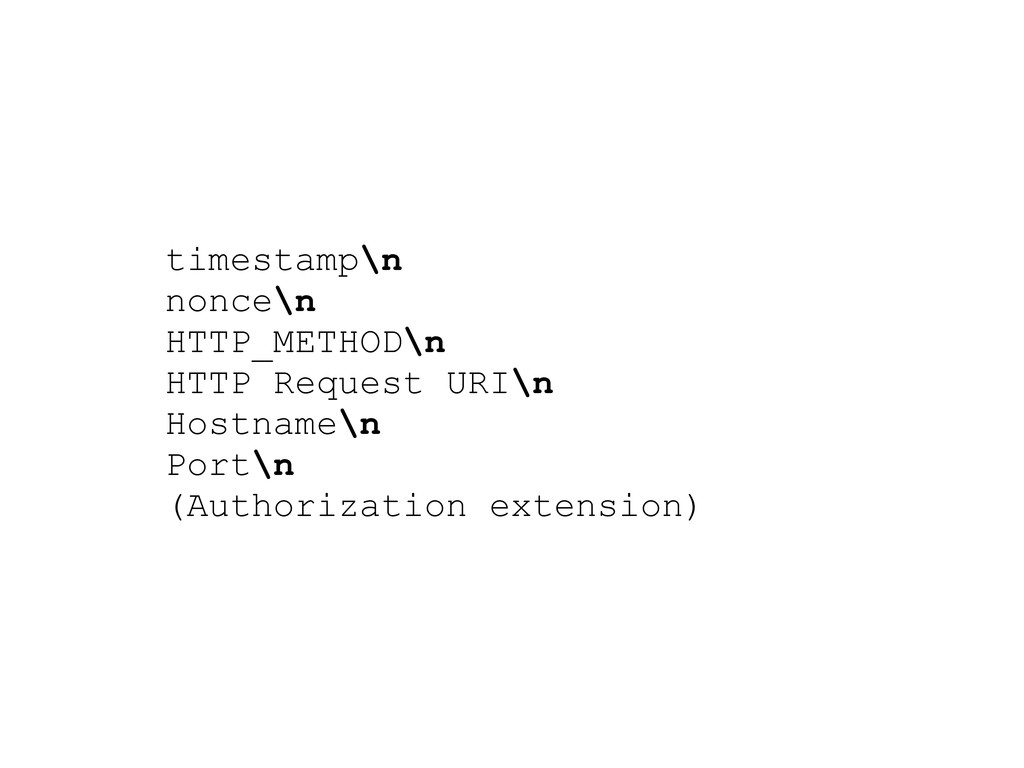
timestamp\n nonce\n HTTP_METHOD\n HTTP Request URI\n Hostname\n Port\n (Authorization extension)
And JavaScript?
User-Agent Profile
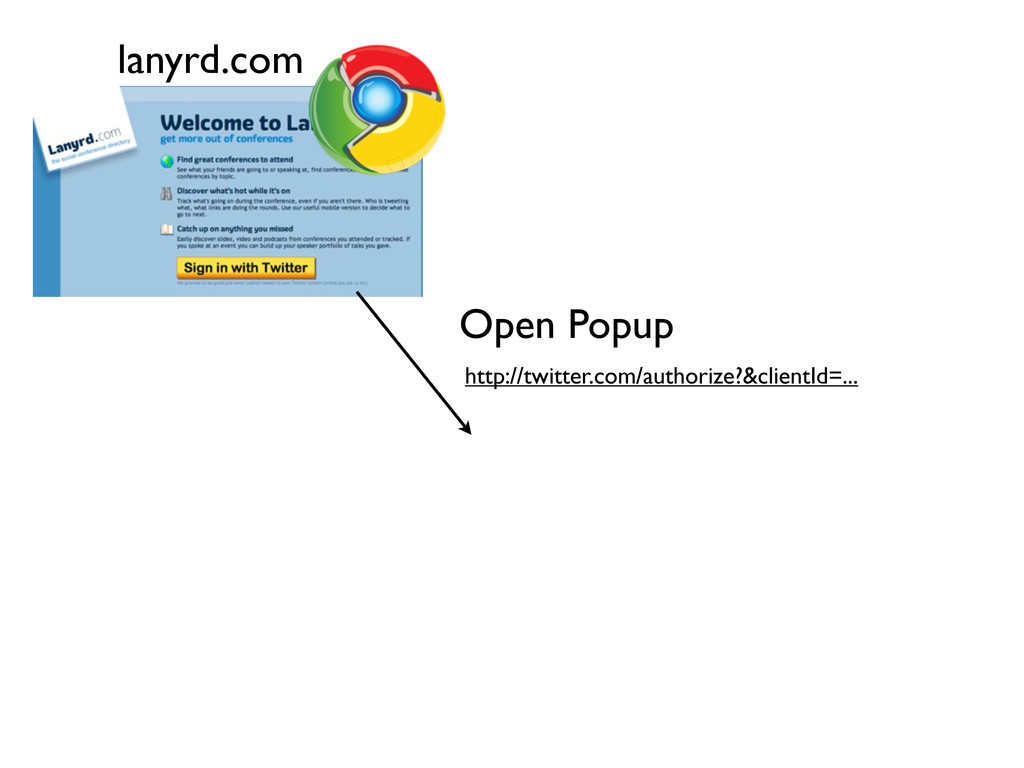
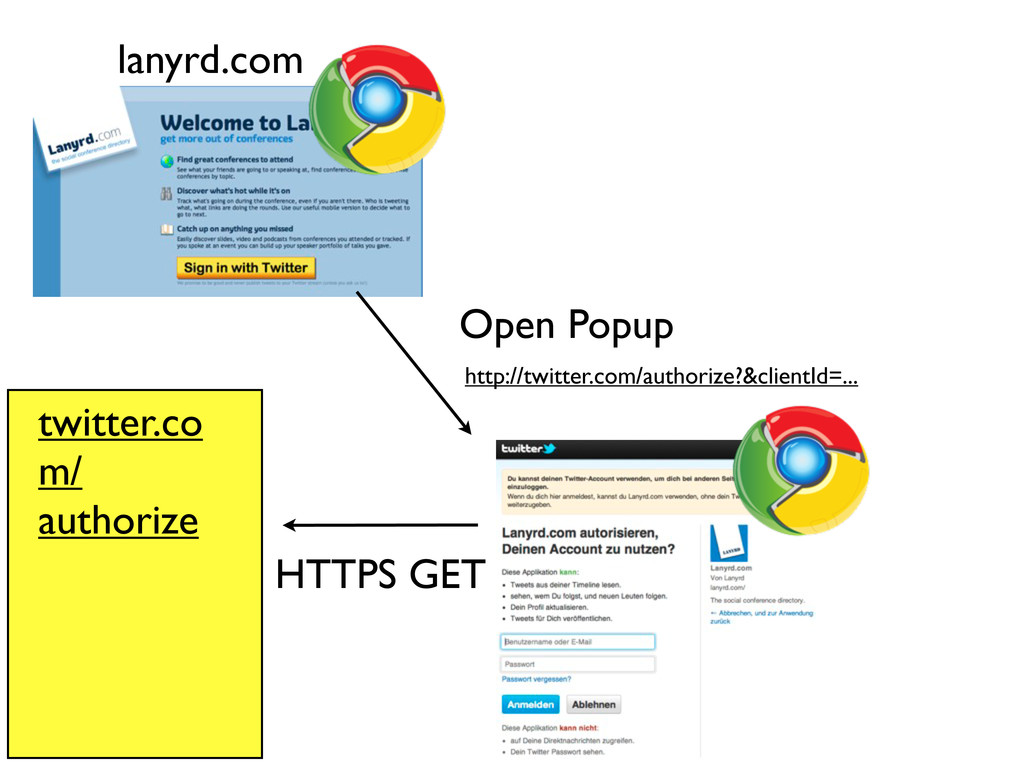
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com HTTPS GET twitter.co m/ authorize
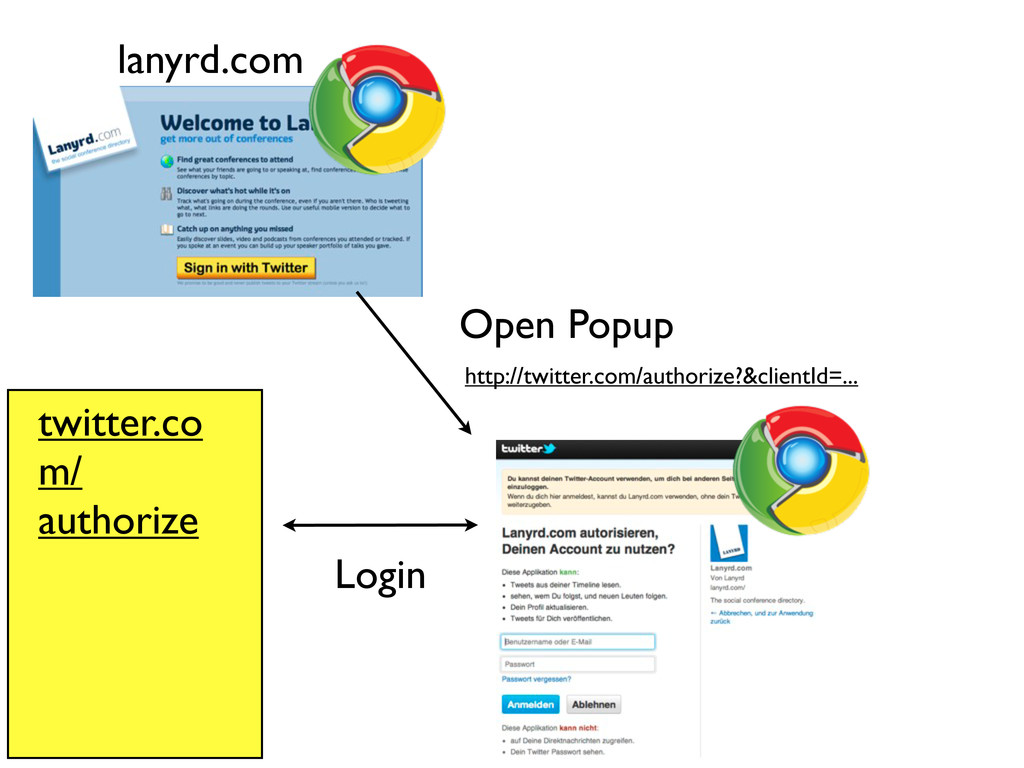
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com Login twitter.co m/ authorize
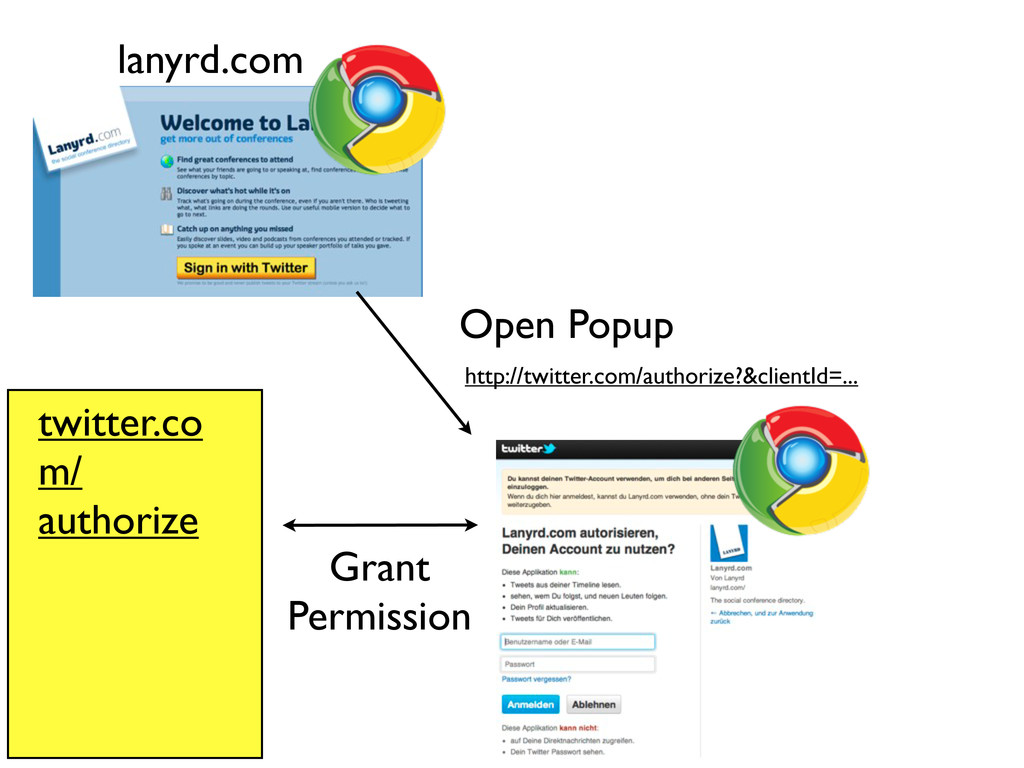
http://twitter.com/authorize?&clientId=... Open Popup lanyrd.com Grant Permission twitter.co m/ authorize
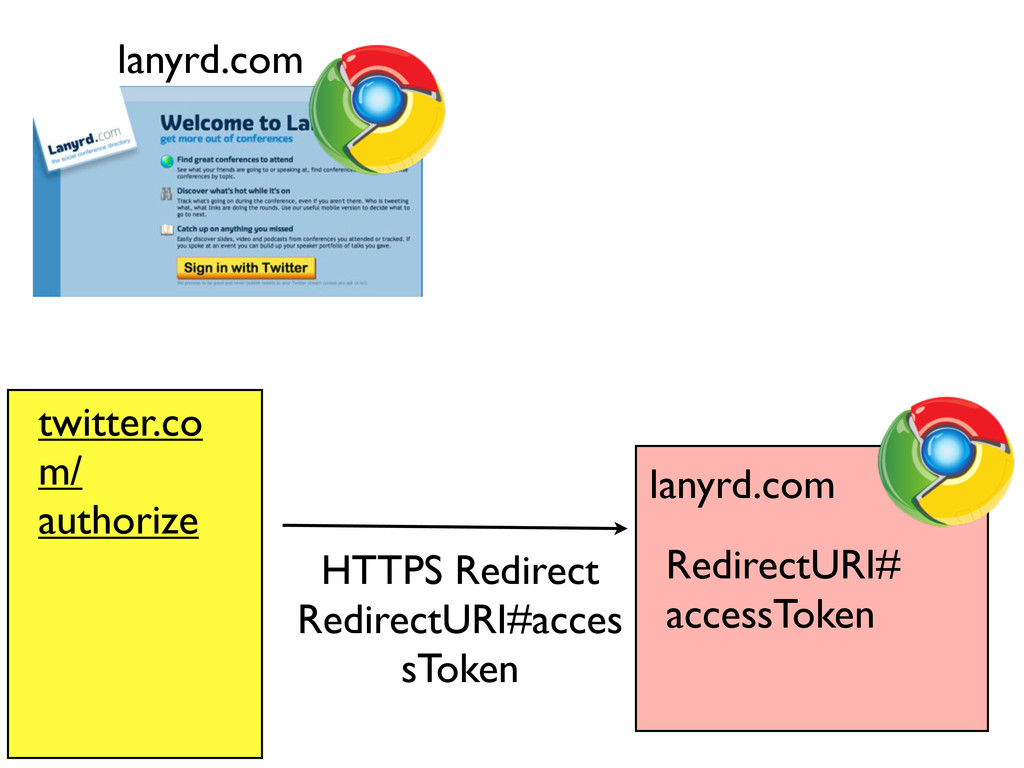
lanyrd.com HTTPS Redirect RedirectURI#acces sToken twitter.co m/ authorize RedirectURI# accessToken
lanyrd.com
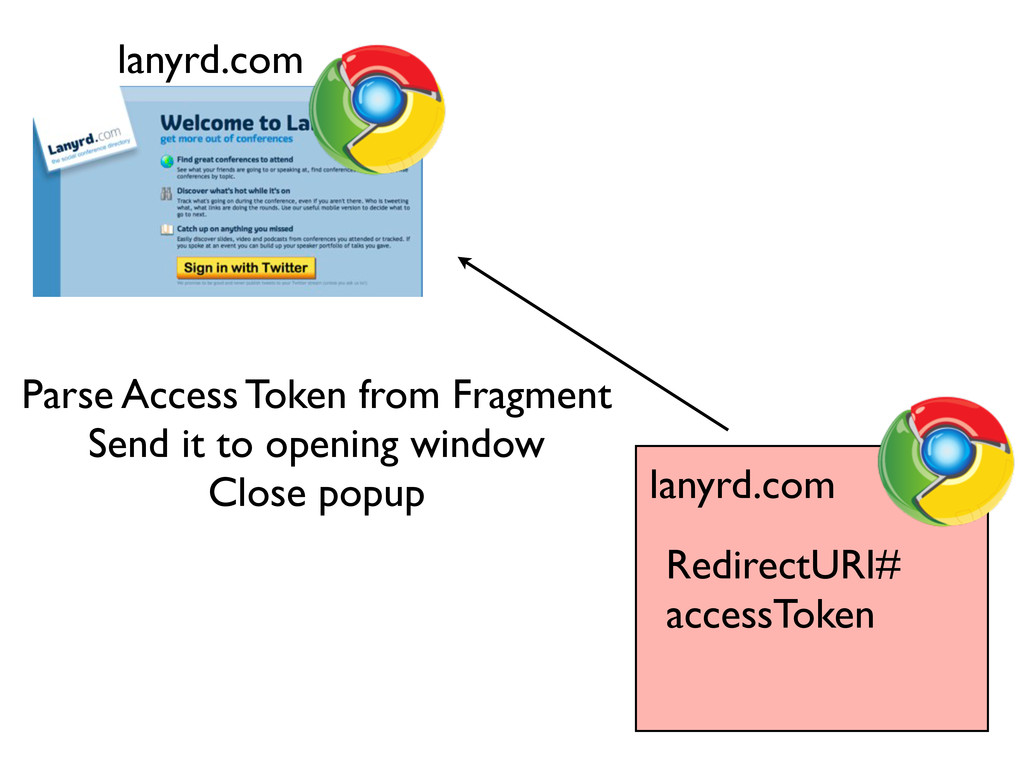
lanyrd.com RedirectURI# accessToken Parse Access Token from Fragment Send it
to opening window Close popup lanyrd.com
Same Origin Policy
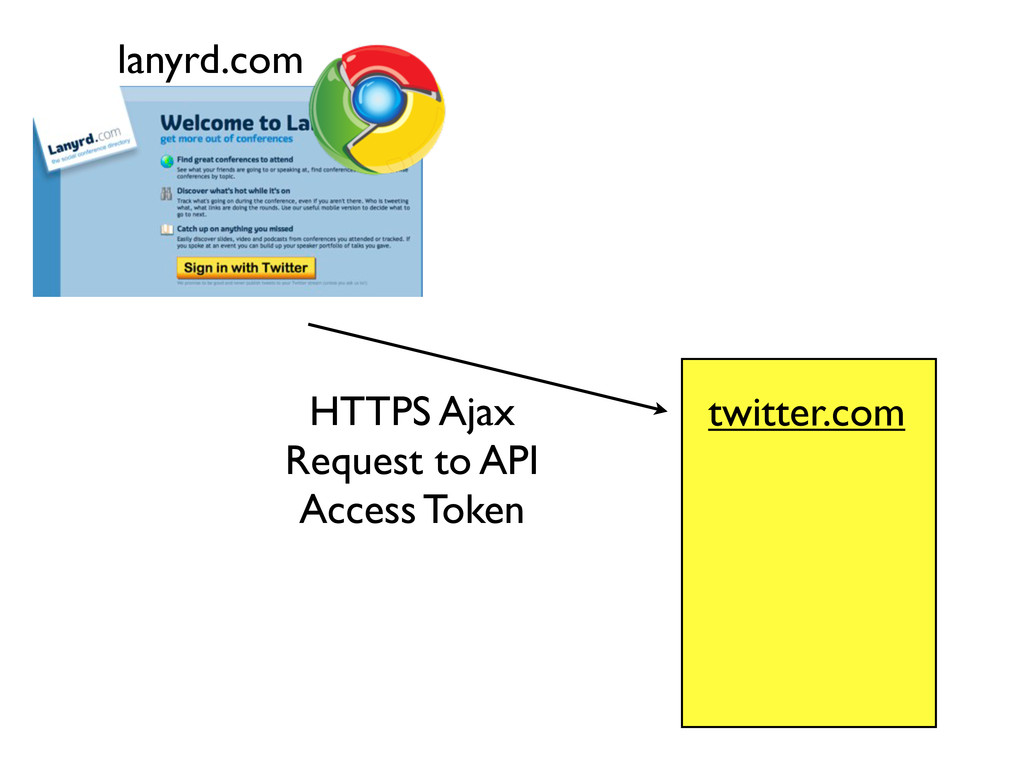
lanyrd.com HTTPS Ajax Request to API Access Token twitter.com
Same Origin Policy
None
JSONP
Cross Origin Request Sharing (CORS)
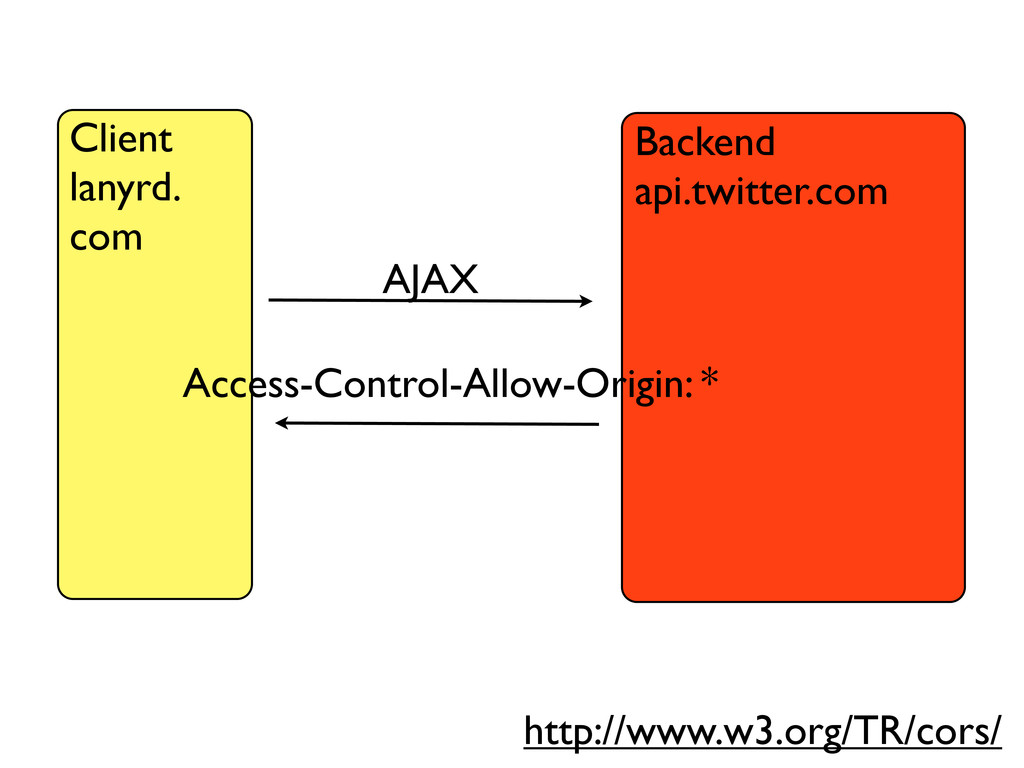
Backend api.twitter.com Client lanyrd. com AJAX Access-Control-Allow-Origin: * http://www.w3.org/TR/cors/
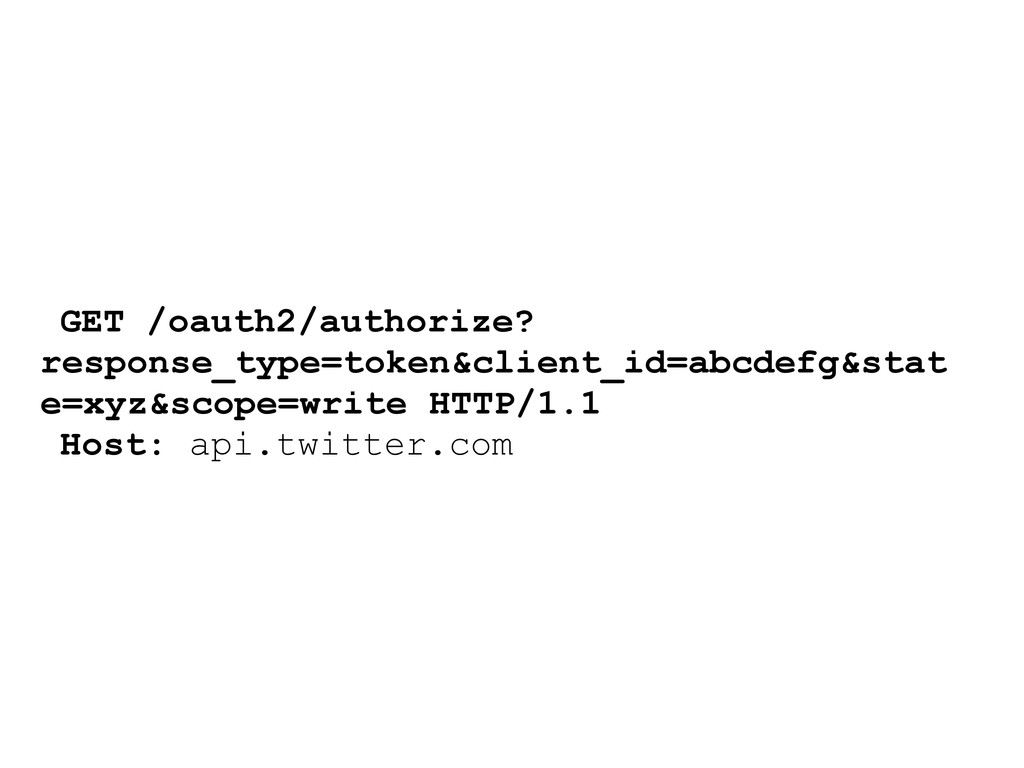
GET /oauth2/authorize? response_type=token&client_id=abcdefg&stat e=xyz&scope=write HTTP/1.1 Host: api.twitter.com
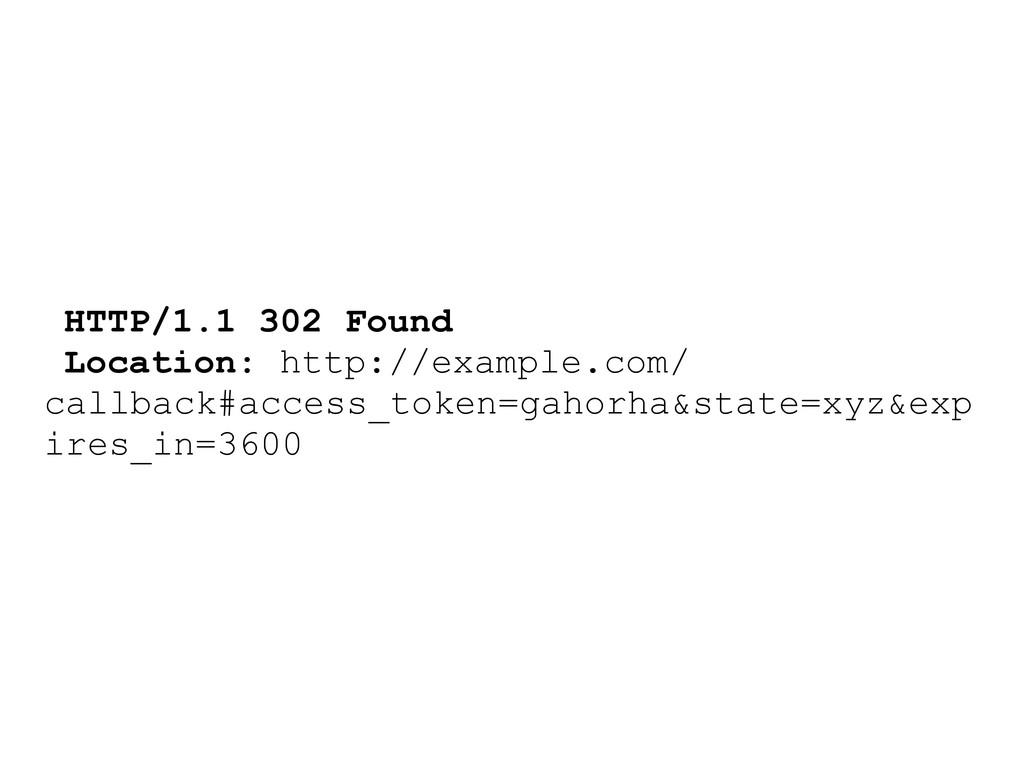
HTTP/1.1 302 Found Location: http://example.com/ callback#access_token=gahorha&state=xyz&exp ires_in=3600
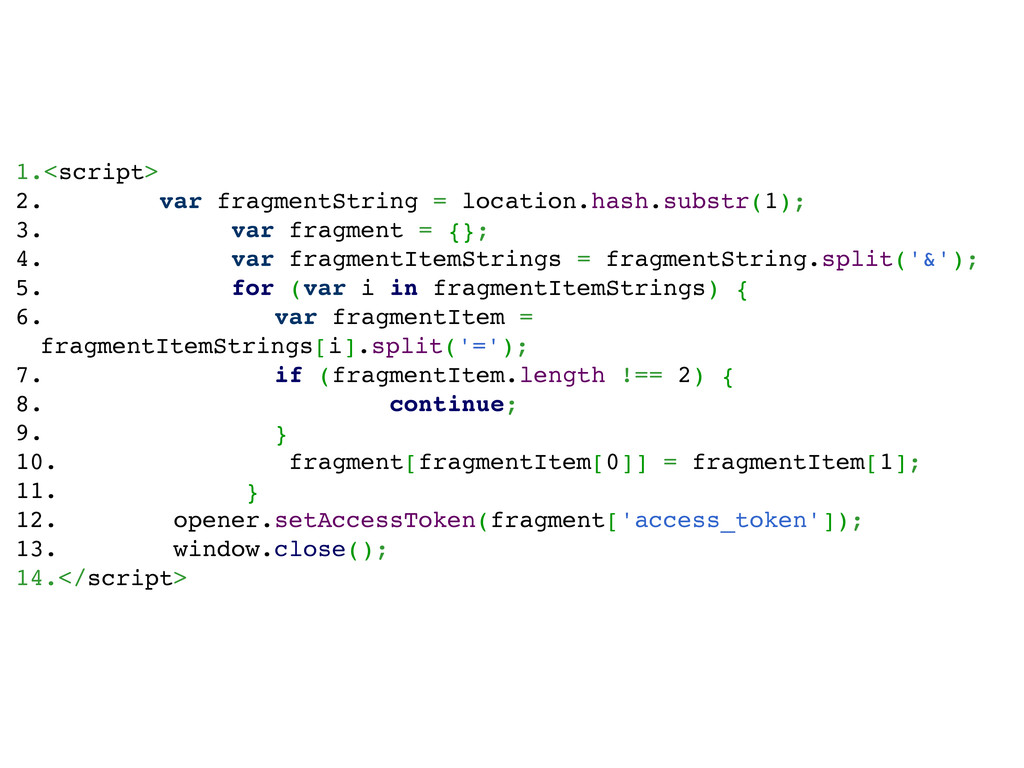
1.<script> 2. var fragmentString = location.hash.substr(1); 3. var fragment =
{}; 4. var fragmentItemStrings = fragmentString.split('&'); 5. for (var i in fragmentItemStrings) { 6. var fragmentItem = fragmentItemStrings[i].split('='); 7. if (fragmentItem.length !== 2) { 8. continue; 9. } 10. fragment[fragmentItem[0]] = fragmentItem[1]; 11. } 12. opener.setAccessToken(fragment['access_token']); 13. window.close(); 14.</script>
DEMO
https://github.com/bashofmann/statusnet_js_mashup_2nd
State
Scopes Optional parameter for provider specific implementations Additional return values
Access Control
http://openidconnect.com/ Scope: „openid“ With access token additional values are returned
UserID: URL to Portable Contacts endpoint Timestamp Signature
Mobile/Desktop
h"p://twi"er.com/Bas2anHofmann h"ps://profiles.google.com/bashofmann h"p://lanyrd.com/people/Bas2anHofmann/ h"p://speakerdeck.com/u/bas2anhofmann
[email protected]


 bastianhofmann
 x5gtrn
 techtekt
 occhi
 pfn
 finengine
 sue445
 satomasahiro2005
 taka_aki
 odashi
 ivry_presentationmaterials
 satoshi7
 honzajavorek
 jlugia
 eitanlees
 aarron
 keathley
 bkeepers
 jct
 destraynor
 tonyrice
 joshbly
 soudai
 cassininazir