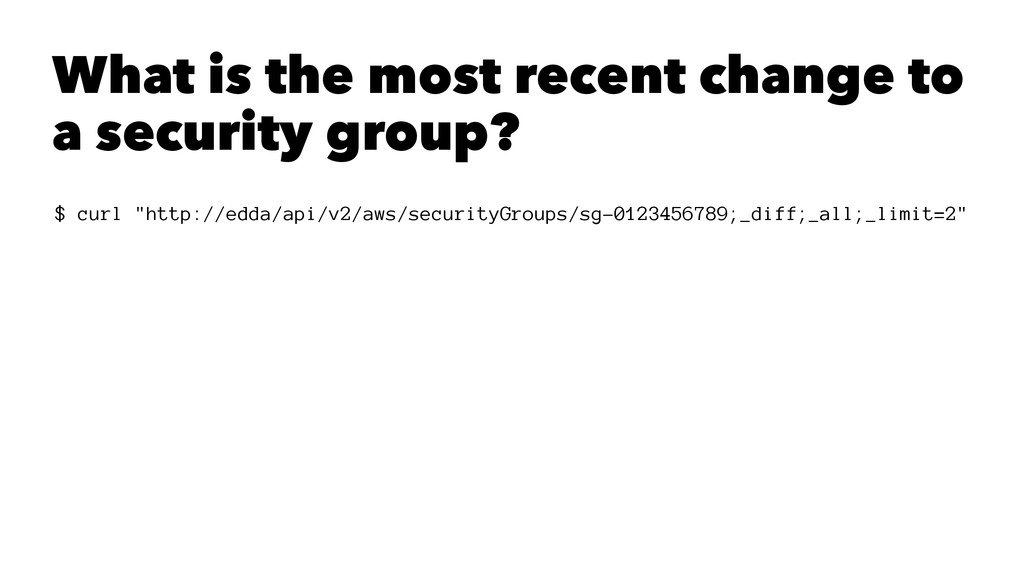Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
AWS Security
Search
Jason Chan
October 22, 2014
Technology
100
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
AWS Security
Talk on AWS Security I gave at SaintCon 2014.
Jason Chan
October 22, 2014
More Decks by Jason Chan
See All by Jason Chan
Cloud Security @ Netflix
chanj
0
52
Other Decks in Technology
See All in Technology
V8のArray.prototype.flatを最大約20倍速くするまでと、巨大OSSへの大規模コミットの道のり
riyaamemiya
0
290
『SAR衛星データ解析入門』の ご紹介とその応用
syuchimu
0
120
アウトプット初心者、半年間のふりかえり
4o1sobblue
0
430
Temporal 最高!でも改めて「日付」について調べたら人類の負債すぎる件
riyaamemiya
0
150
AI導入は済んだ。次は統制を作り替える番だ_AI×開発組織 Summit 2026
techtekt
PRO
0
210
触りたくないデータに、どう触るか AI時代のRBACアクセスガバナンス
ivry_presentationmaterials
0
260
Kiro Crewをはじめよう
kizawa2020
1
160
二歩目のフロントエンド・ウェブアクセシビリティ
camiha
2
570
Webの常識が通じないHTMLメールのダークモード
teamlab
PRO
0
120
オントロジーって 結局なにもの? AI エージェントに「意味」を渡す知識設計の話
greenmidori
0
190
ソフトウェア ファクトリー - 再現性のあるソフトウェアの工場づくり / Software factory
iktakahiro
6
4.9k
QA4AI 2026-Oct 生成AI時代の品質保証
tokuty
1
860
Featured
See All Featured
A designer walks into a library…
pauljervisheath
211
25k
Google's AI Overviews - The New Search
badams
0
1.6k
Darren the Foodie - Storyboard
khoart
PRO
4
4k
How Fast Is Fast Enough? [PerfNow 2025]
tammyeverts
3
940
Dominate Local Search Results - an insider guide to GBP, reviews, and Local SEO
greggifford
PRO
0
370
The Illustrated Children's Guide to Kubernetes
chrisshort
51
53k
Designing Experiences People Love
moore
143
24k
How to audit for AI Accessibility on your Front & Back End
davetheseo
0
600
Why You Should Never Use an ORM
jnunemaker
PRO
61
10k
コードの90%をAIが書く世界で何が待っているのか / What awaits us in a world where 90% of the code is written by AI
rkaga
63
46k
My Coaching Mixtape
mlcsv
0
360
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.6k
Transcript
AWS Security Jason Chan
[email protected]
: @chanjbs SAINTCON 2014
Quick Survey AWS Experience 1-4
None
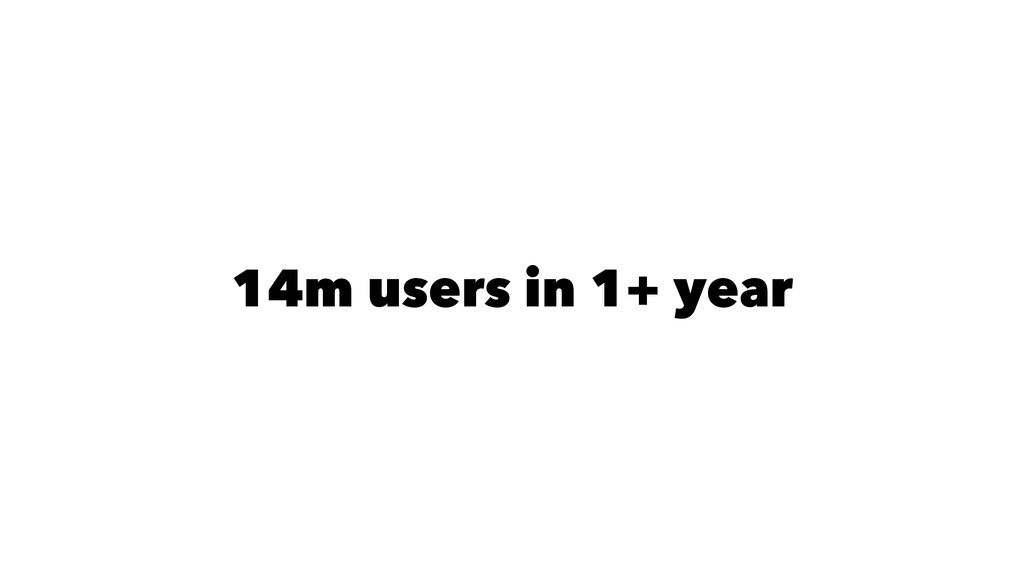
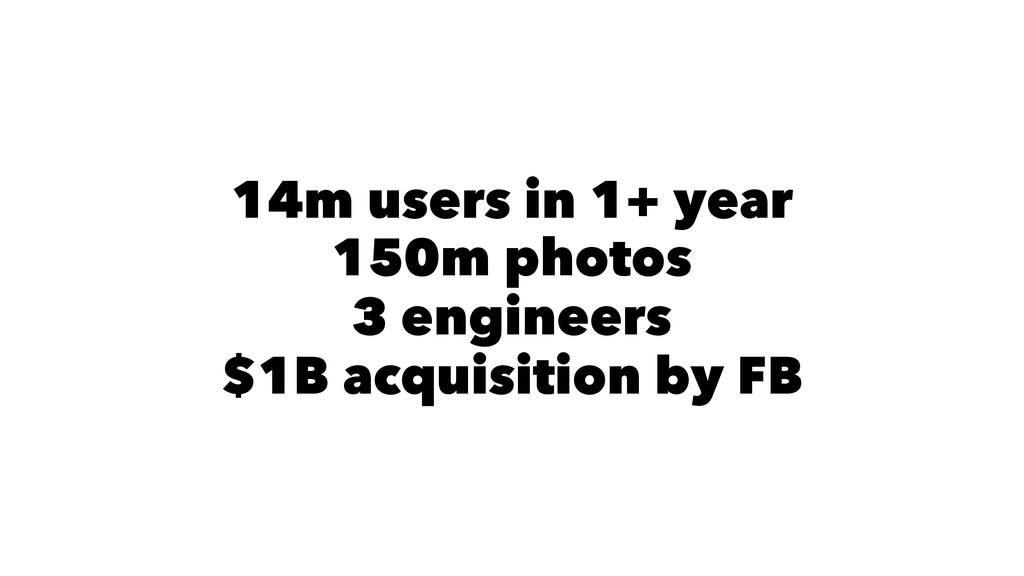
14m users in 1+ year
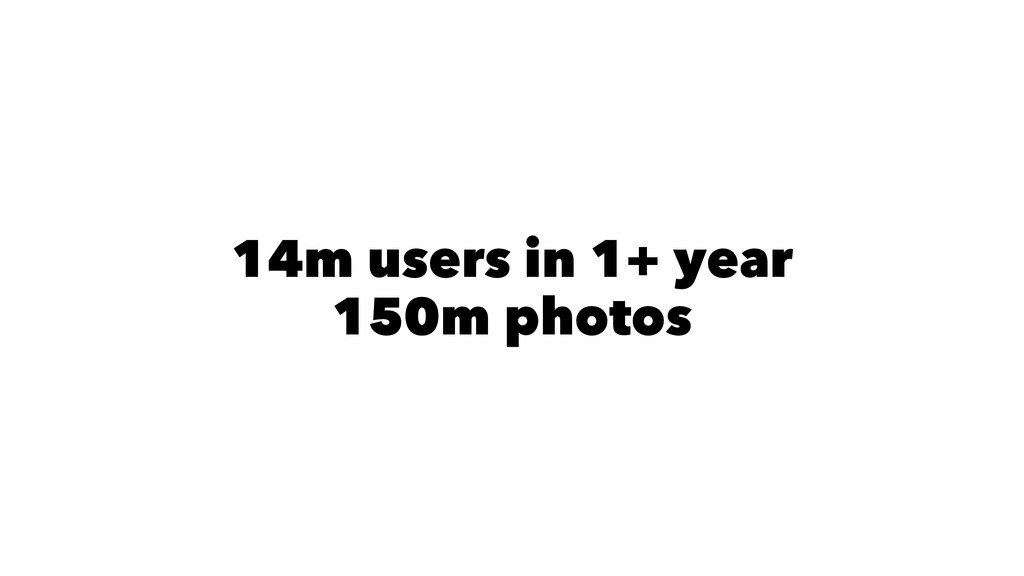
14m users in 1+ year 150m photos
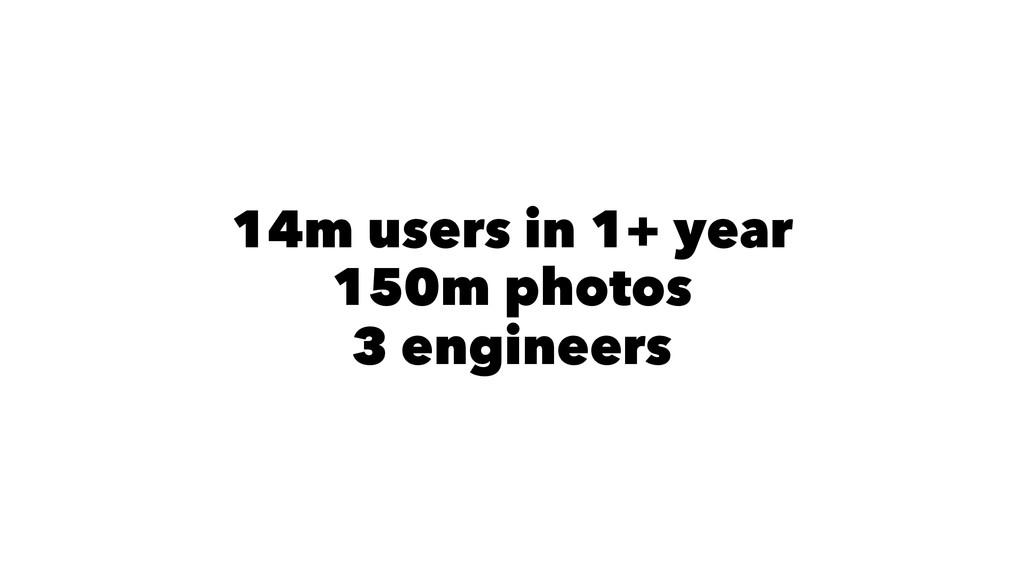
14m users in 1+ year 150m photos 3 engineers
14m users in 1+ year 150m photos 3 engineers $1B
acquisition by FB
None
So . . .
idea + cloud = profit!
None
None
So . . .
None
Goal: AWS benefits, securely
AWS Intro Typical Setup Thinking about AWS Security Tips and
Traps Other Resources
Me Now: Security @ Netflix Before: Security @ VMware Before:
@stake, iSEC
None
AWS
IaaS Undifferentiated heavy lifting
API-driven building blocks Customer control
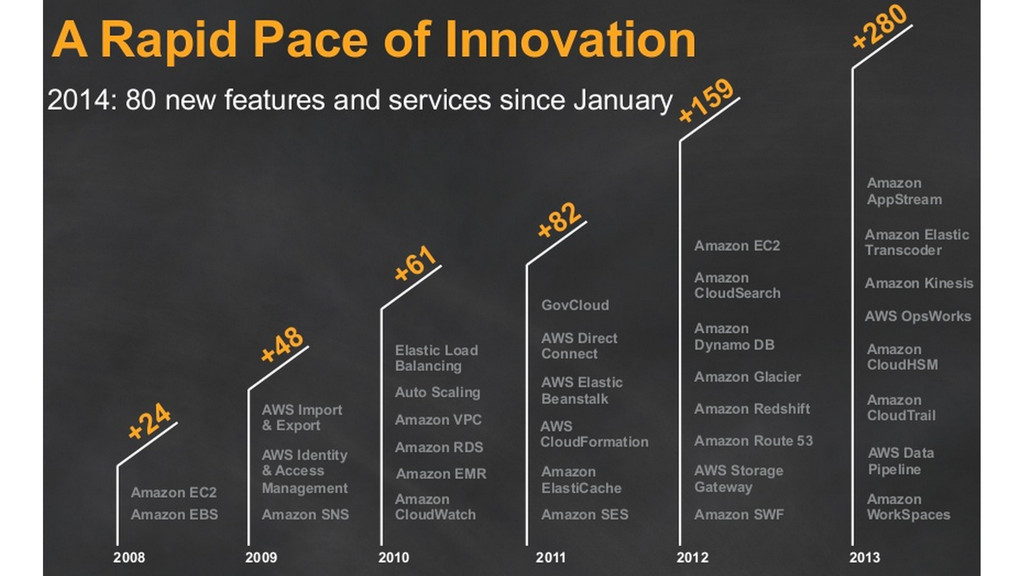
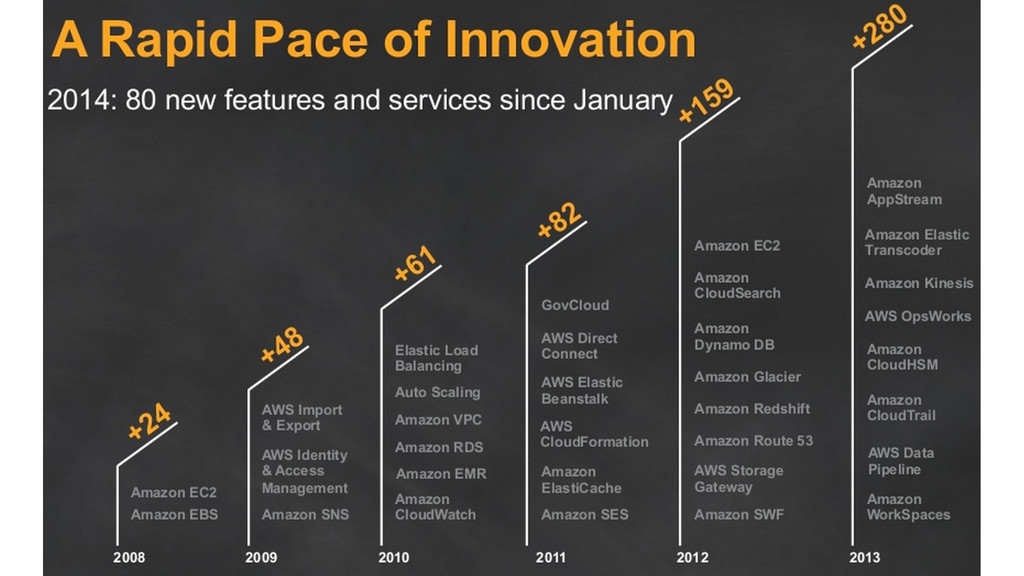
Evolving quickly
None
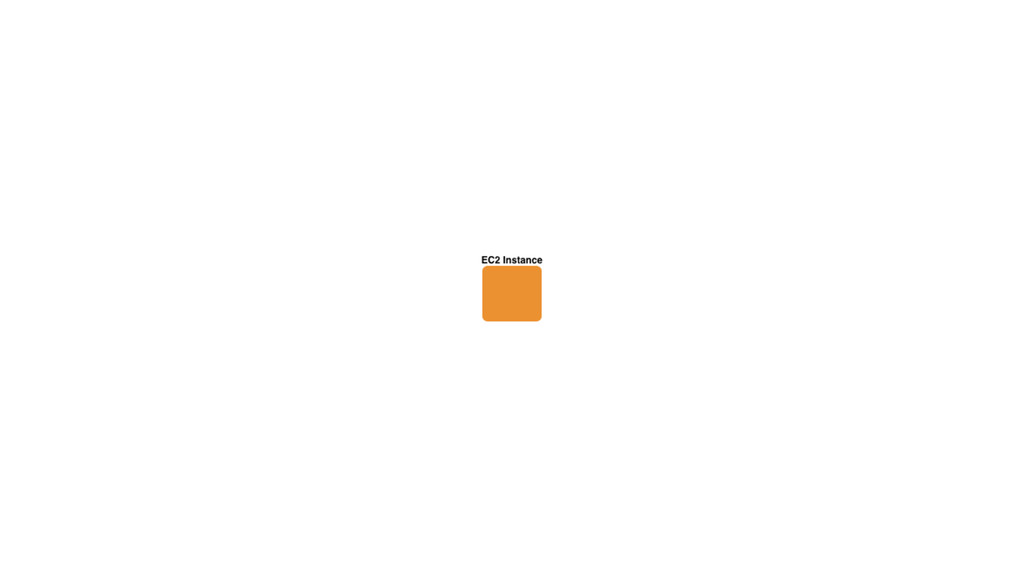
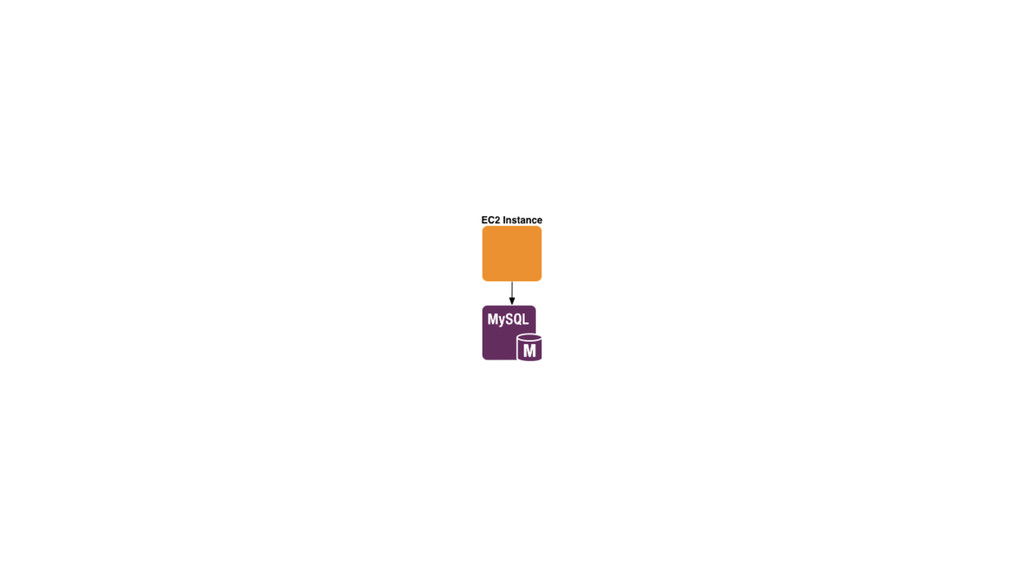
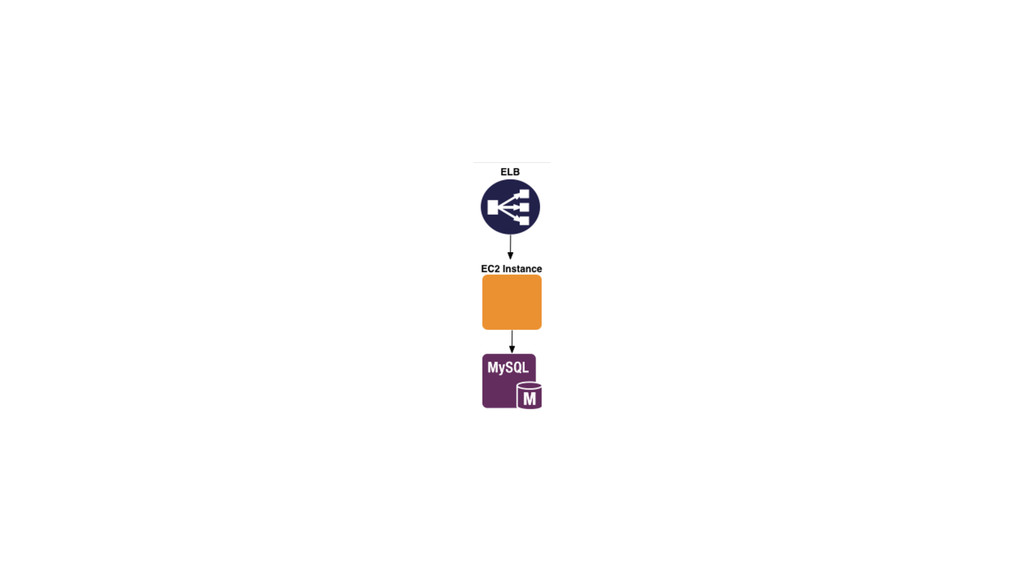
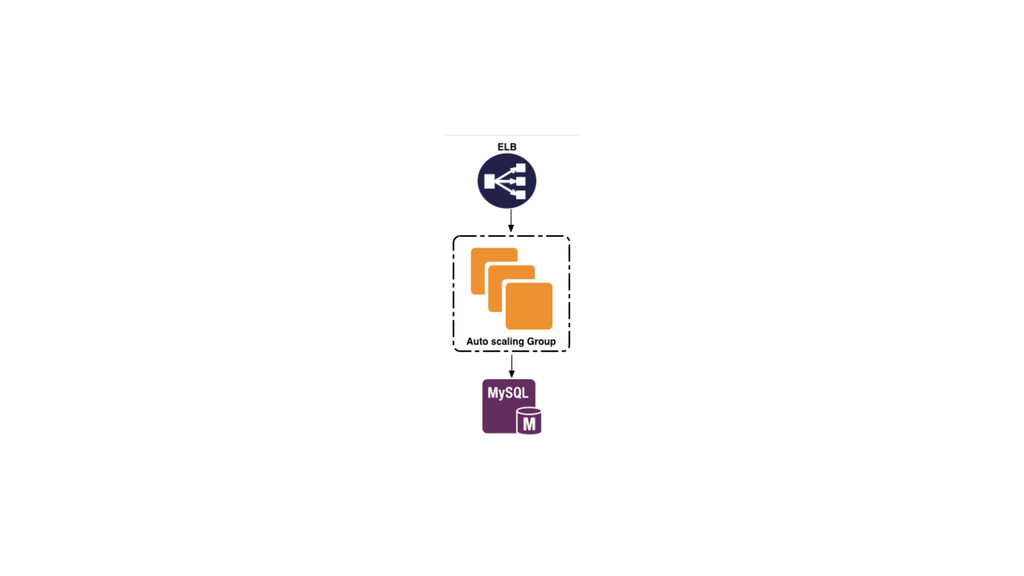
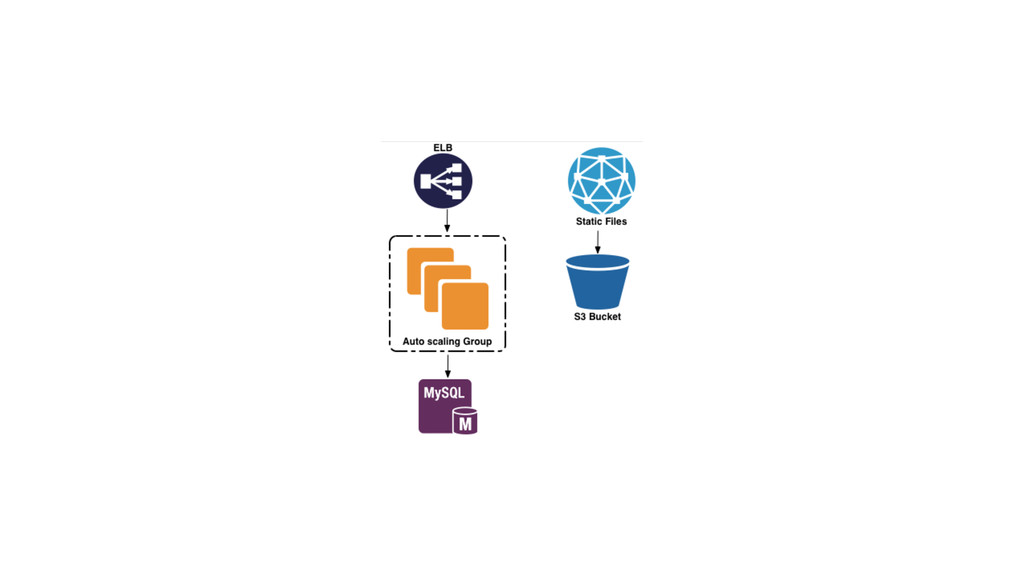
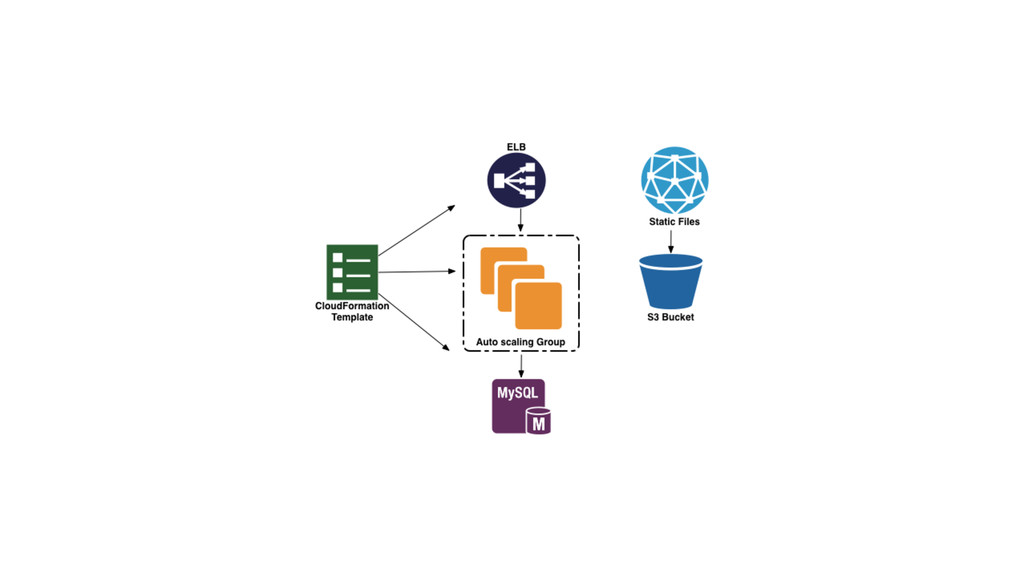
Typical AWS Setup
None
None
None
None
None
None
None
Thinking About AWS Security
Philosophy
None
None
A note on security automation
None
None
Typically, how do you:
Create a user account
Create a user account Inventory your systems
Create a user account Inventory your systems Update a firewall
config
Create a user account Inventory your systems Update a firewall
config Make a forensic image
Create a user account Inventory your systems Update a firewall
config Make a forensic image Disable a MFA token
In AWS . . .
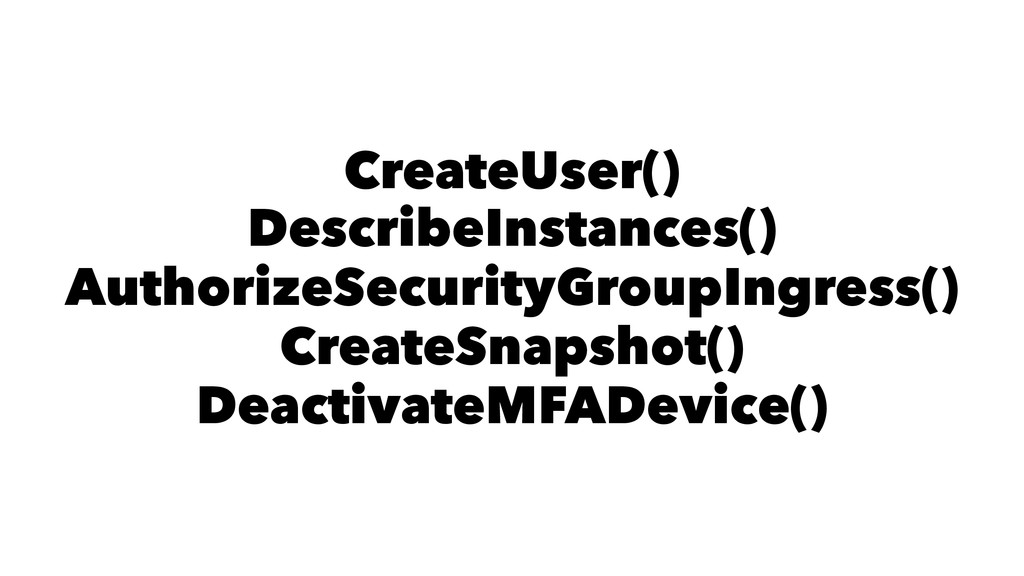
CreateUser() DescribeInstances() AuthorizeSecurityGroupIngress() CreateSnapshot() DeactivateMFADevice()
None
Three Areas of Focus
None
None
None
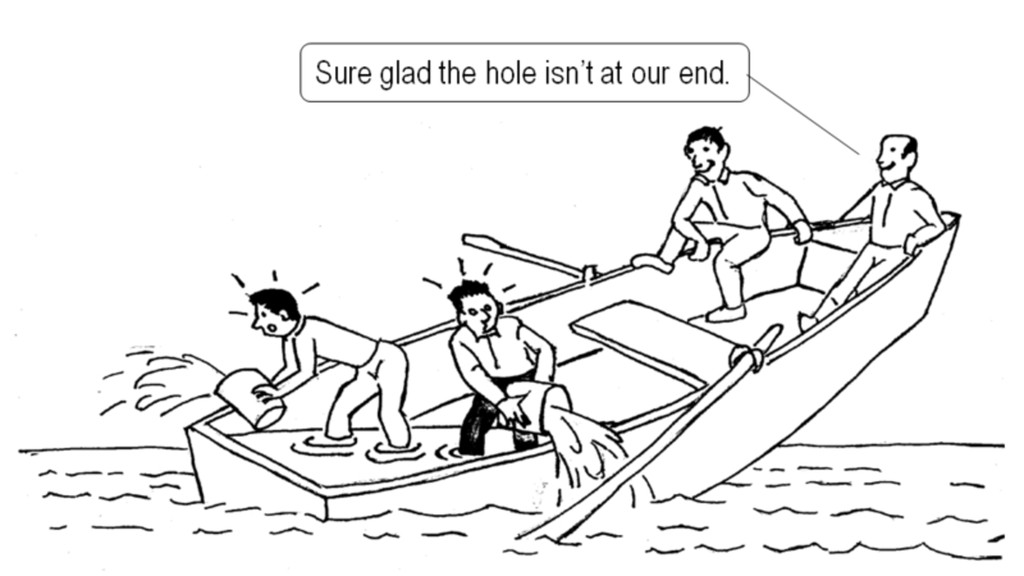
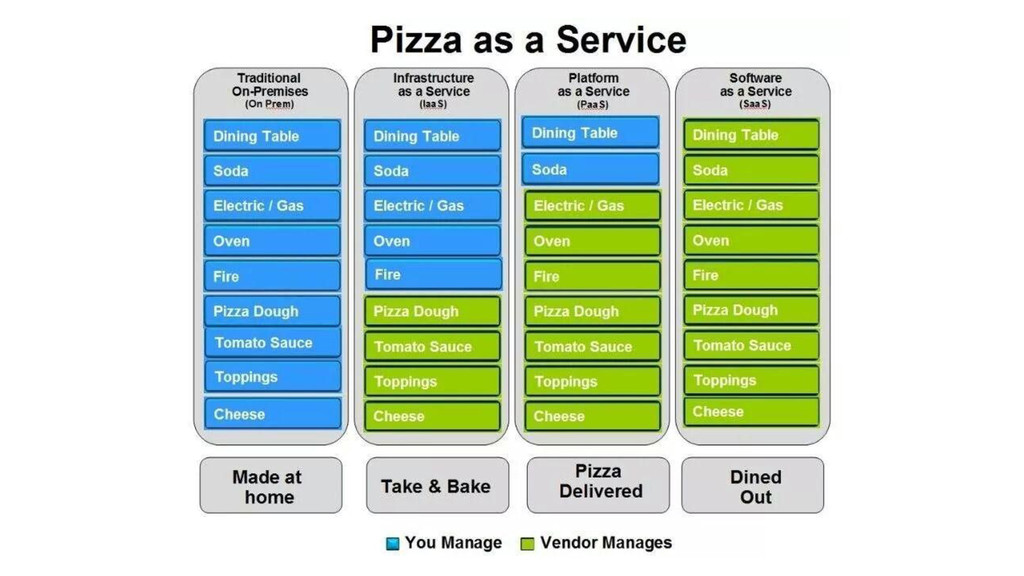
Shared Responsibility
None
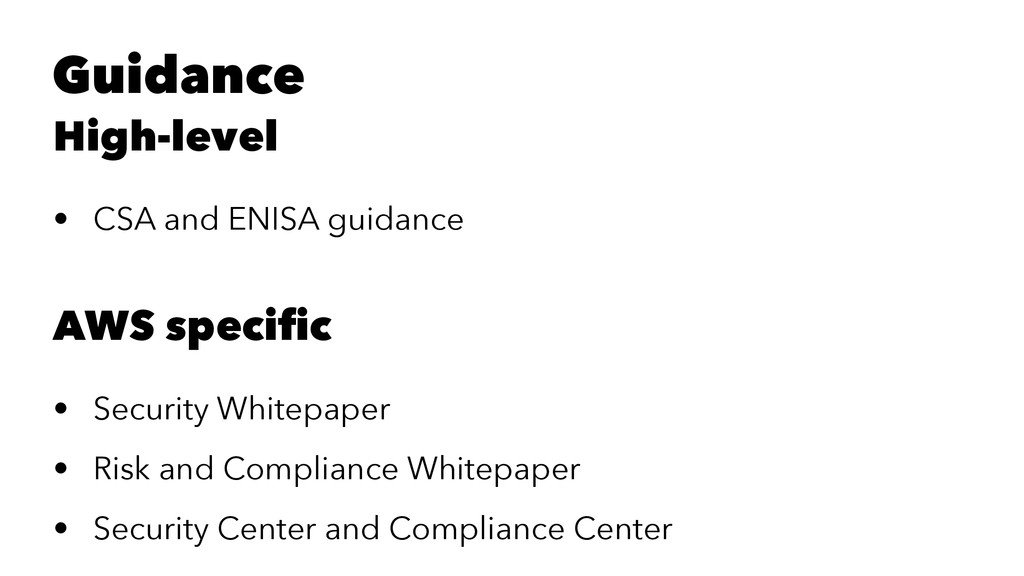
Guidance High-level • CSA and ENISA guidance AWS specific •
Security Whitepaper • Risk and Compliance Whitepaper • Security Center and Compliance Center
Shared responsibility tips Understand the model, and what AWS can't
do Engage AWS for support - SSAE 16, PCI, etc.
Shared responsibility traps AWS can help, but you're ultimately responsible
Contract, Ts & Cs are not a firewall
Segregation and Access Control
"Users/Accounts" in AWS
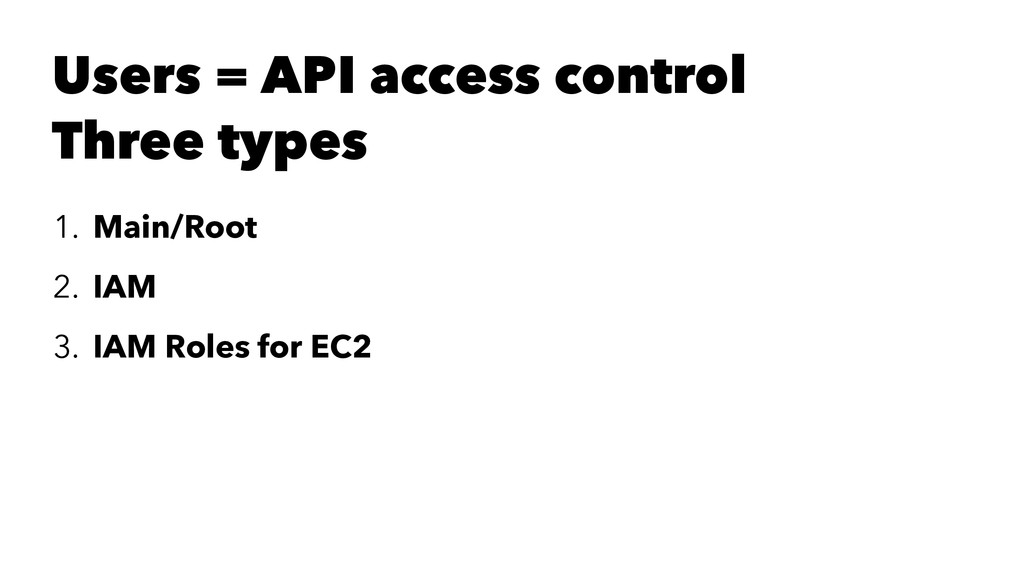
Users = API access control Three types 1. Main/Root 2.
IAM 3. IAM Roles for EC2
None
IAM user (accounts for humans)
Keys are static Must be protected
None
IAM role (accounts for services)
Keys are short-lived Difficult to protect
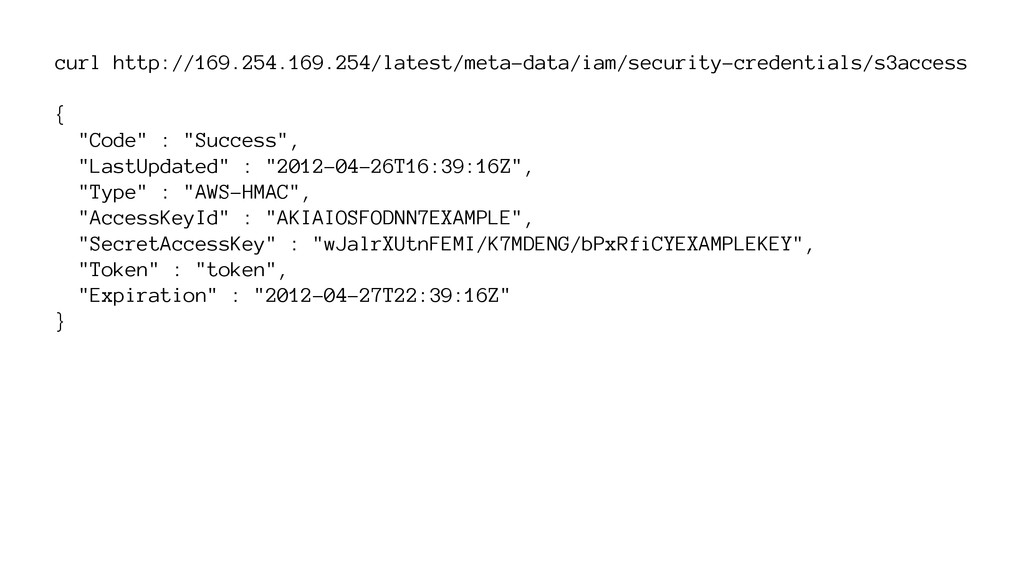
curl http://169.254.169.254/latest/meta-data/iam/security-credentials/s3access { "Code" : "Success", "LastUpdated" : "2012-04-26T16:39:16Z", "Type"
: "AWS-HMAC", "AccessKeyId" : "AKIAIOSFODNN7EXAMPLE", "SecretAccessKey" : "wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY", "Token" : "token", "Expiration" : "2012-04-27T22:39:16Z" }
None
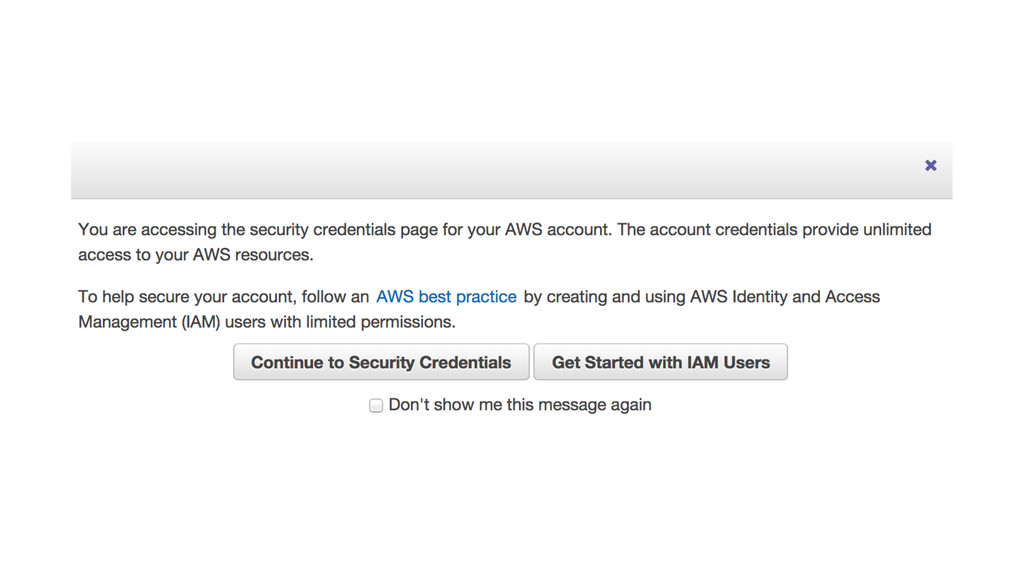
Users in AWS - Tips Don't use the root account
Protect IAM keys Use IAM roles for EC2
Users in AWS - Traps Keys have a way of
finding themselves in GitHub No way to control access to EC2 metadata
Permissions and Policies
Suggested homework Read the API docs
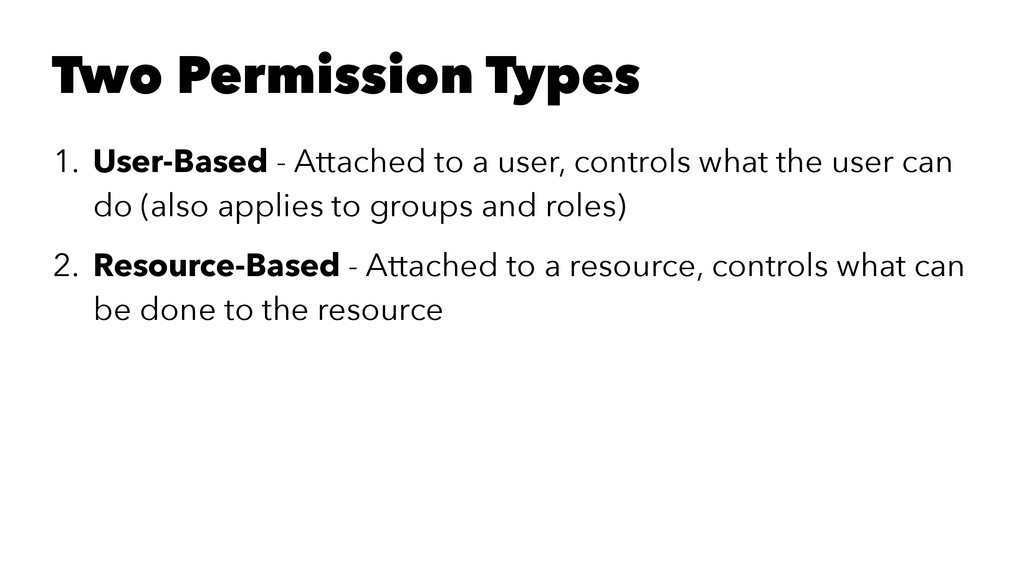
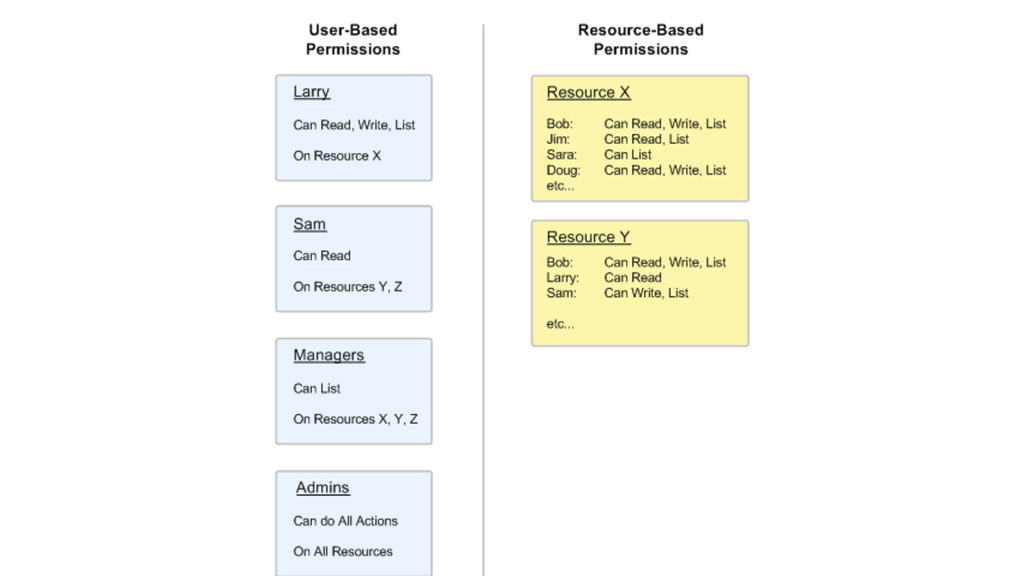
Two Permission Types 1. User-Based - Attached to a user,
controls what the user can do (also applies to groups and roles) 2. Resource-Based - Attached to a resource, controls what can be done to the resource
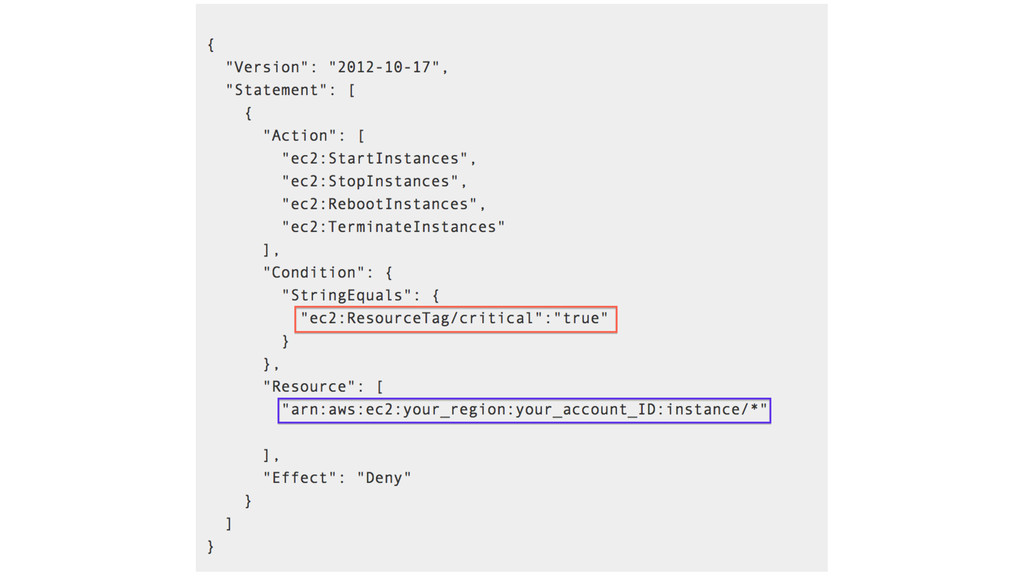
Bonus, Confusing Third Type • Resource-Level - Attached to a
user, controls what the user can do, to which resource
None
None
User policies
{ "Statement": [ { "Action": [ "ses:SendEmail" ], "Effect": "Allow",
"Resource": "*", "Condition": { "IpAddress": { "aws:SourceIp": "1.1.1.1" } } } ] }
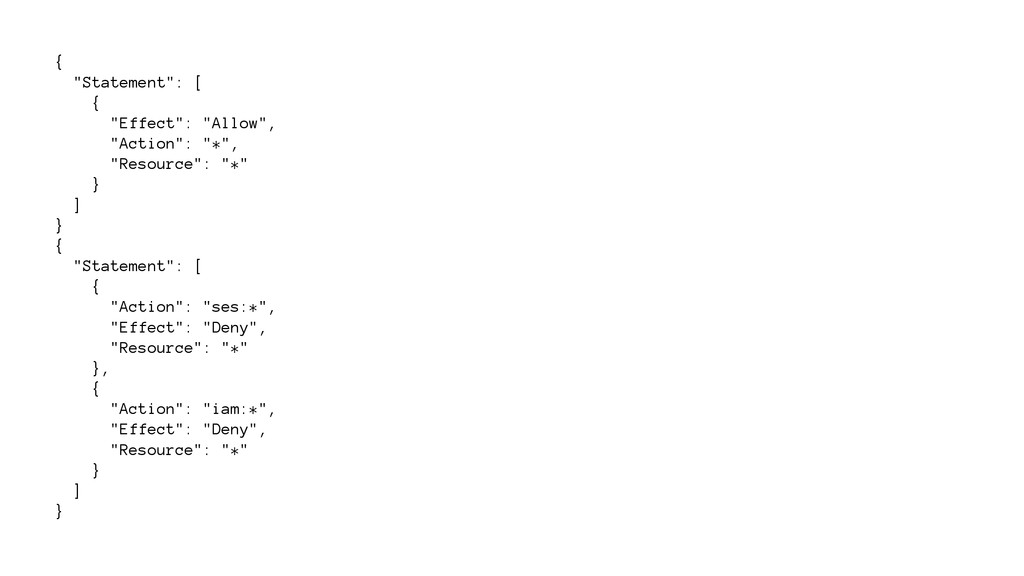
Common approach - blacklisting
{ "Statement": [ { "Effect": "Allow", "Action": "*", "Resource": "*"
} ] } { "Statement": [ { "Action": "ses:*", "Effect": "Deny", "Resource": "*" }, { "Action": "iam:*", "Effect": "Deny", "Resource": "*" } ] }
None
Creating policies • AWS has dozens of services • Hundreds
of API calls across those services • Resource-level control and conditions provides tremendous granularity
Sounds great! Sign me up!
None
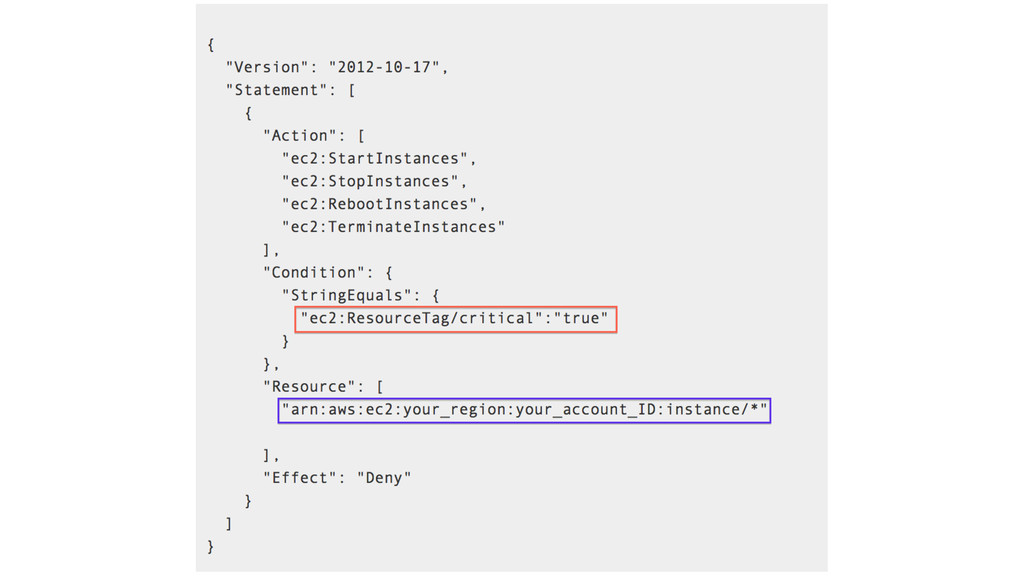
Looking at resource- level policies again
None
Who (or what) can apply (or delete) tags?
Permissions and policies - Tips Think least-privilege Think traditional RBAC
Permissions and policies - Traps Be careful with tag-based security
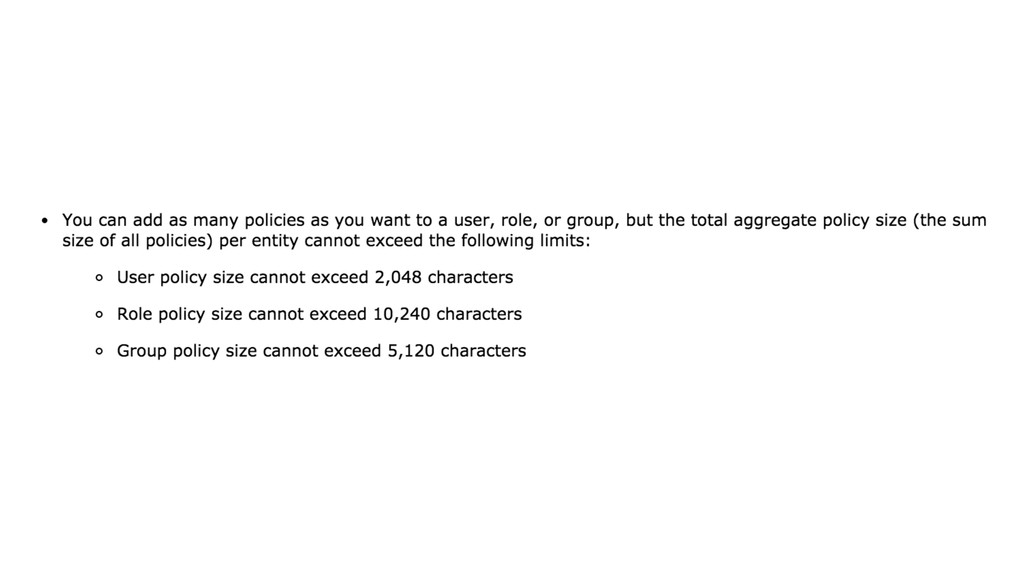
Be careful with policy size limitations Be careful with non-specific policies
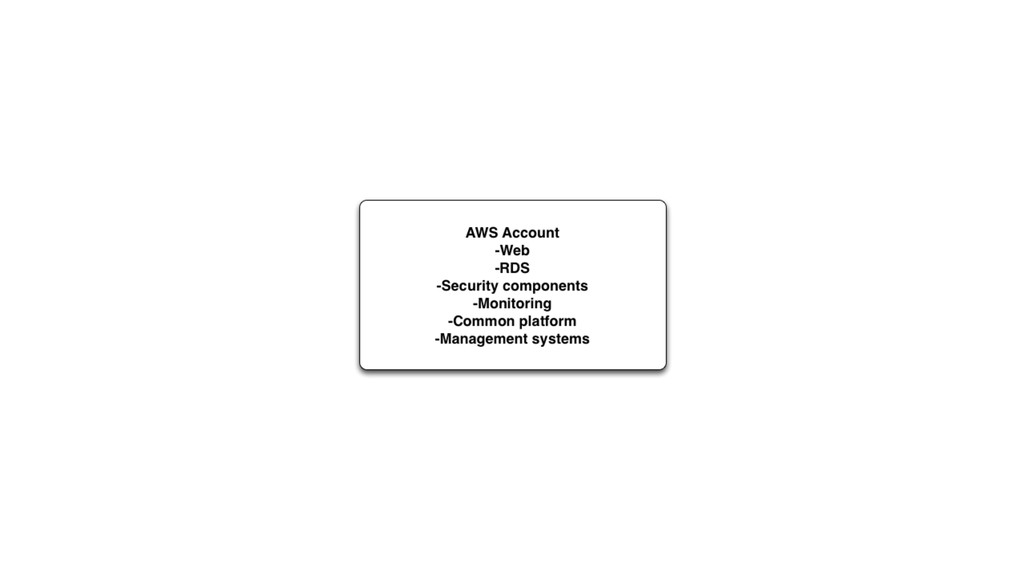
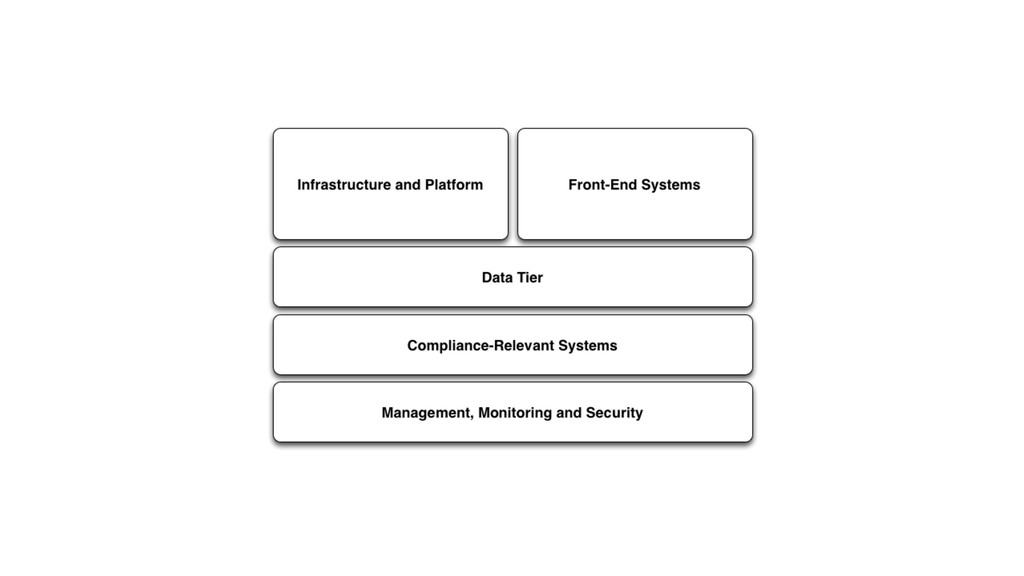
Account-Level Strongest separation
None
None
Account segregation - Tips Test / Dev / Staging /
Prod Compliance requirements Business units (billing boundaries) Core/platform vs. end-user
Account segregation - Traps Cross-account limitations (VPC security groups, S3)
Logistics and planning - AZ mapping, reservations and limits
Monitoring AWS Security
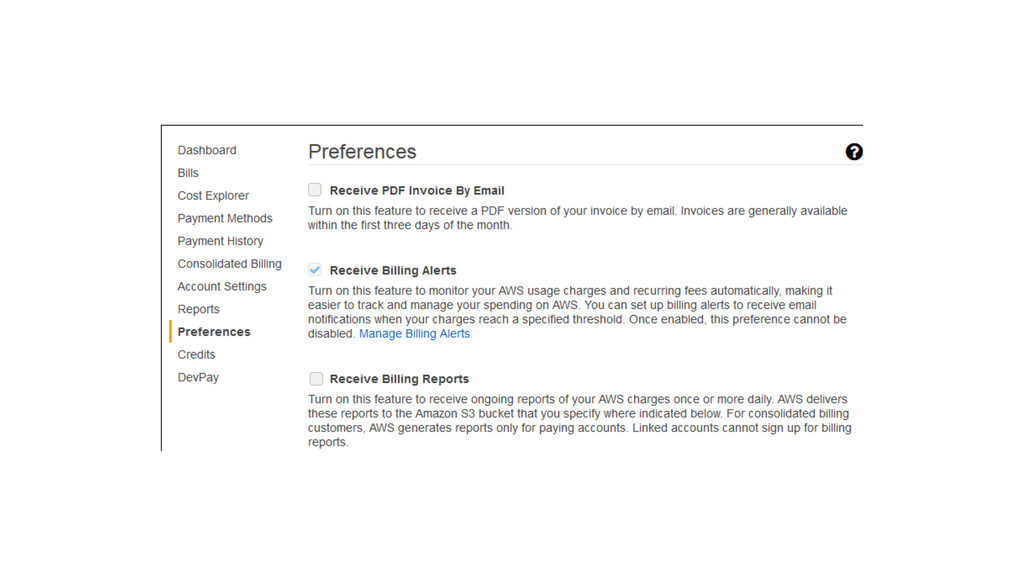
Bill as IDS AWS Billing Alerts
None
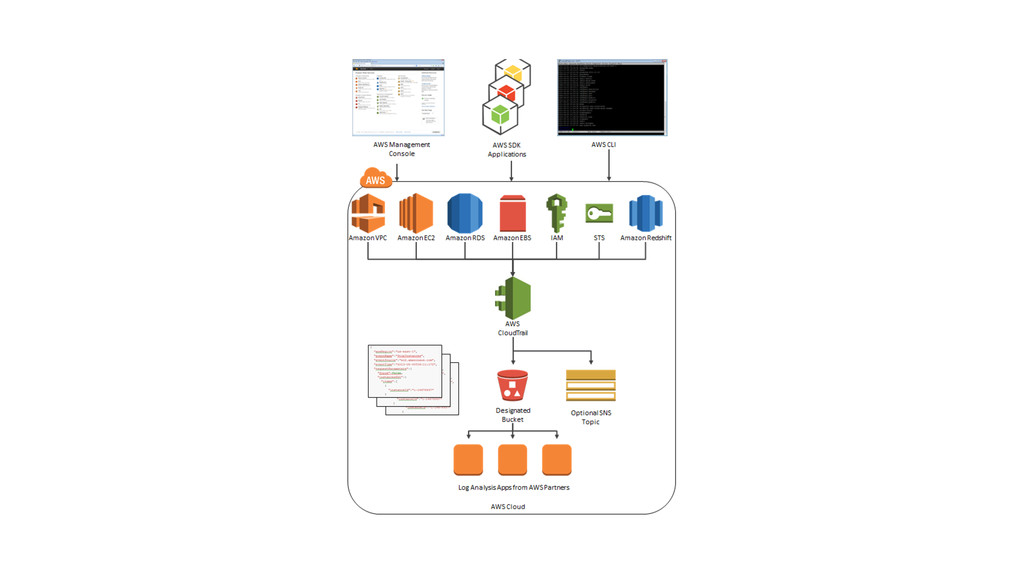
CloudTrail Logging of API calls
None
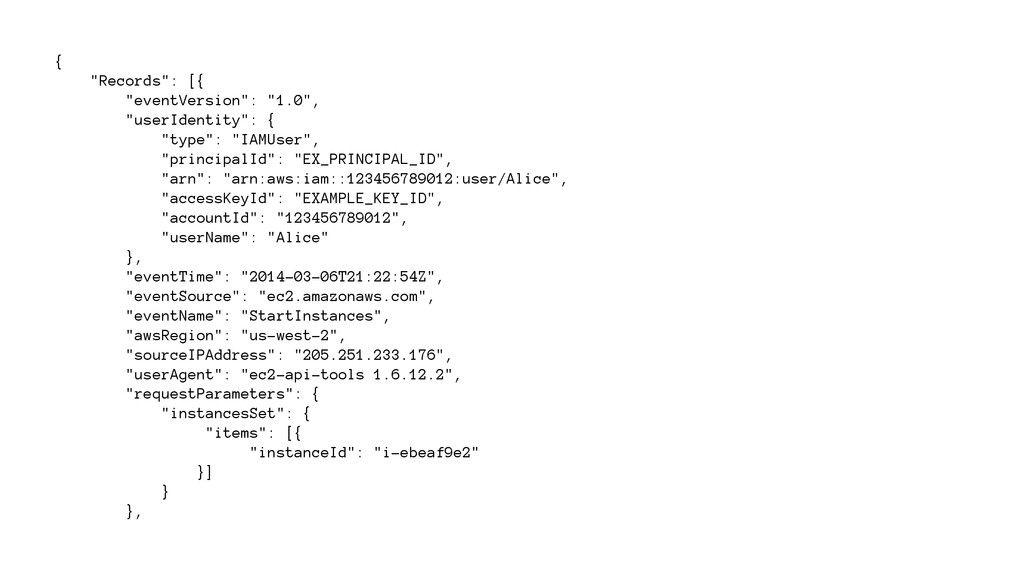
{ "Records": [{ "eventVersion": "1.0", "userIdentity": { "type": "IAMUser", "principalId":
"EX_PRINCIPAL_ID", "arn": "arn:aws:iam::123456789012:user/Alice", "accessKeyId": "EXAMPLE_KEY_ID", "accountId": "123456789012", "userName": "Alice" }, "eventTime": "2014-03-06T21:22:54Z", "eventSource": "ec2.amazonaws.com", "eventName": "StartInstances", "awsRegion": "us-west-2", "sourceIPAddress": "205.251.233.176", "userAgent": "ec2-api-tools 1.6.12.2", "requestParameters": { "instancesSet": { "items": [{ "instanceId": "i-ebeaf9e2" }] } },
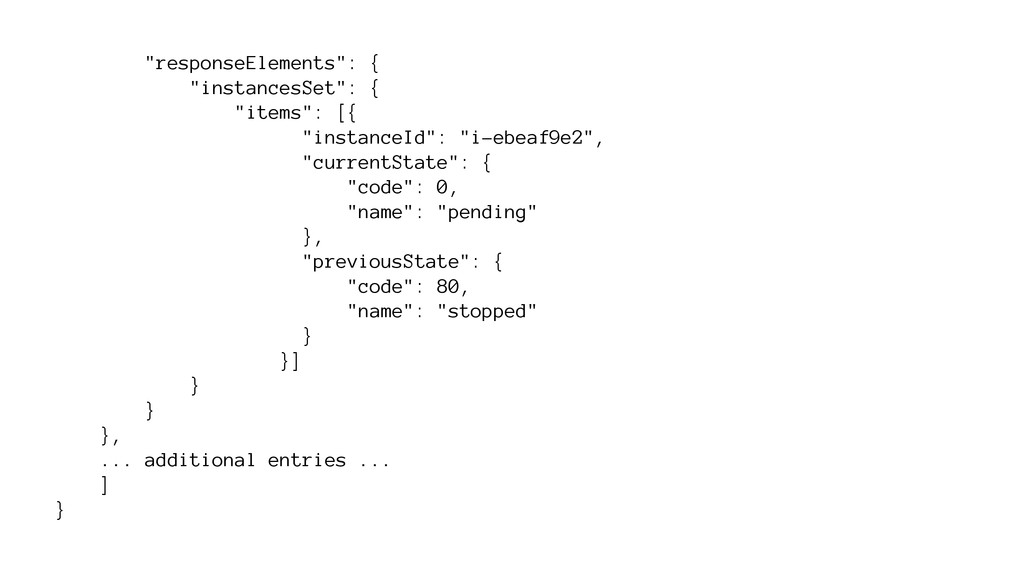
"responseElements": { "instancesSet": { "items": [{ "instanceId": "i-ebeaf9e2", "currentState": {
"code": 0, "name": "pending" }, "previousState": { "code": 80, "name": "stopped" } }] } } }, ... additional entries ... ] }
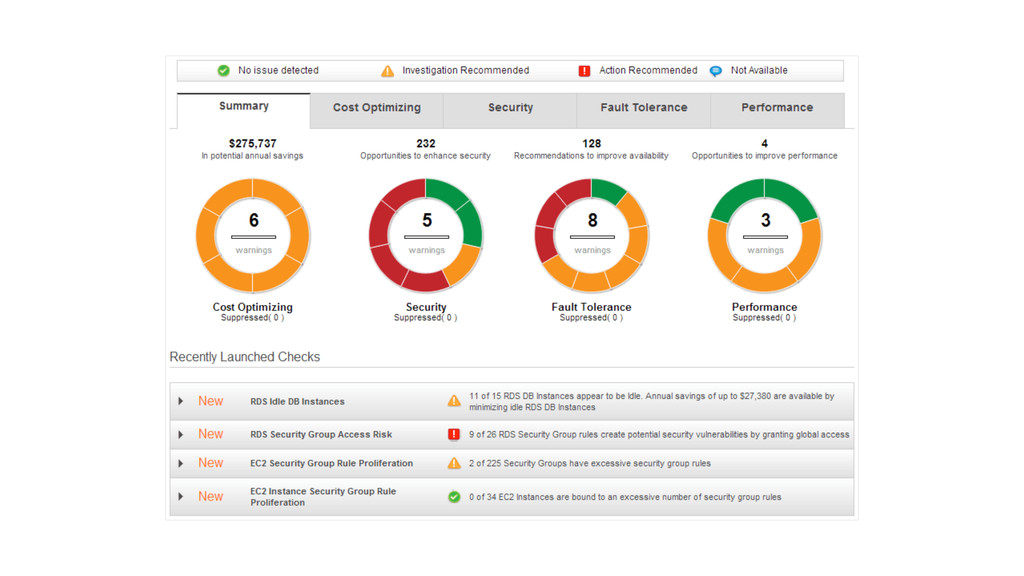
Trusted Advisor Checks config vs. best practices
None
None
Shameless Plug Section of the Talk
Edda AWS config history
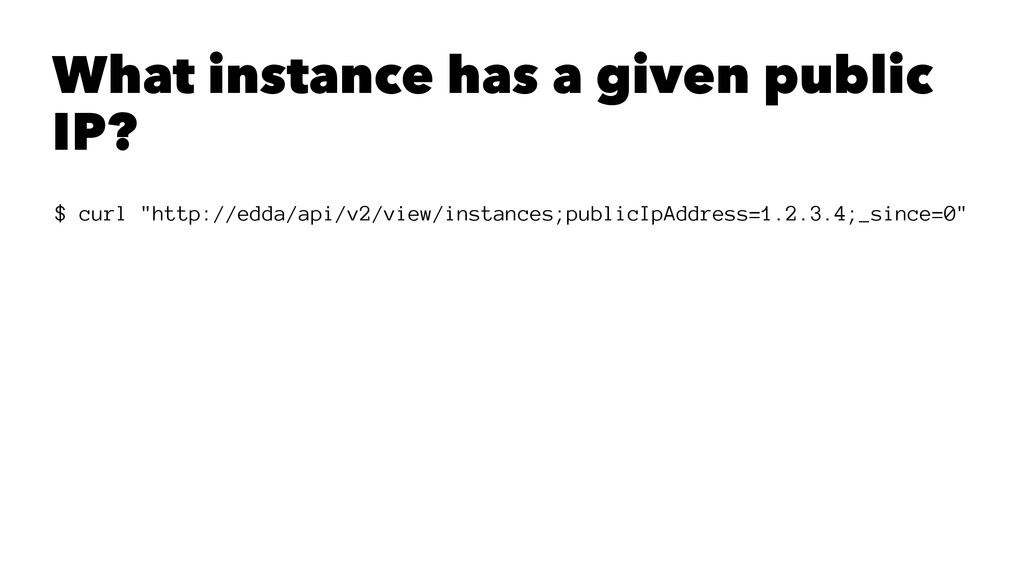
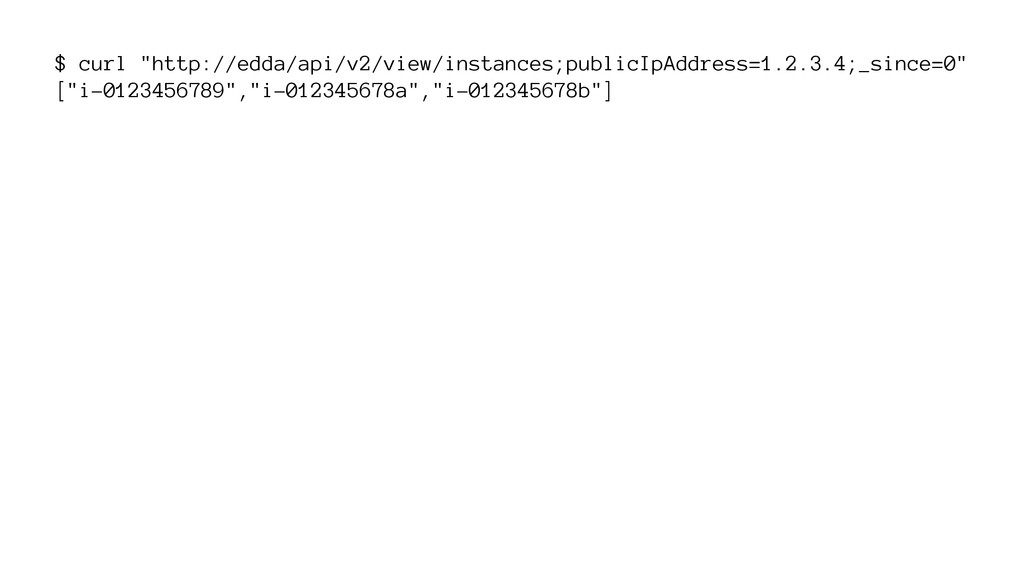
What instance has a given public IP? $ curl "http://edda/api/v2/view/instances;publicIpAddress=1.2.3.4;_since=0"
$ curl "http://edda/api/v2/view/instances;publicIpAddress=1.2.3.4;_since=0" ["i-0123456789","i-012345678a","i-012345678b"]
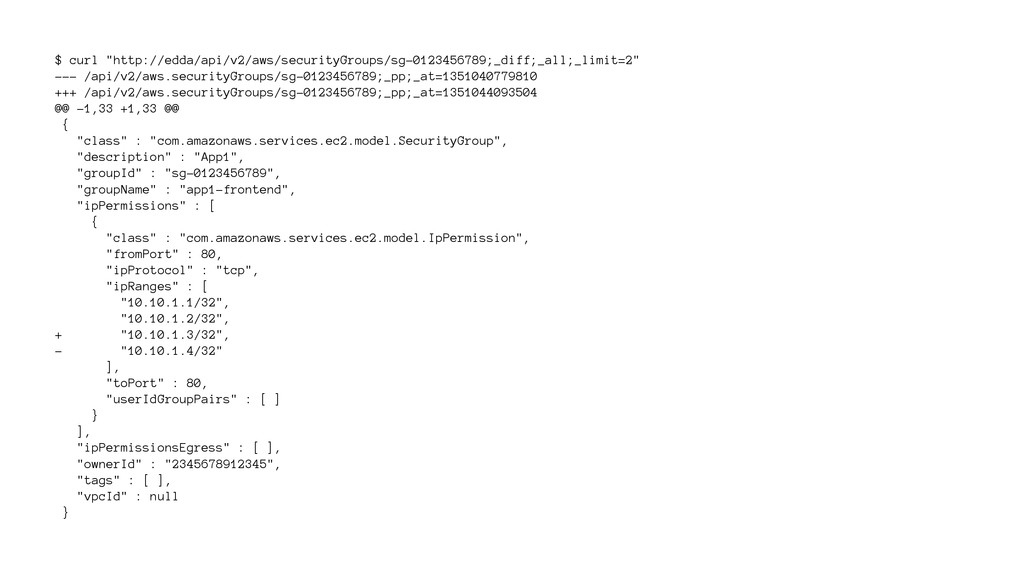
What is the most recent change to a security group?
$ curl "http://edda/api/v2/aws/securityGroups/sg-0123456789;_diff;_all;_limit=2"
$ curl "http://edda/api/v2/aws/securityGroups/sg-0123456789;_diff;_all;_limit=2" --- /api/v2/aws.securityGroups/sg-0123456789;_pp;_at=1351040779810 +++ /api/v2/aws.securityGroups/sg-0123456789;_pp;_at=1351044093504 @@ -1,33 +1,33
@@ { "class" : "com.amazonaws.services.ec2.model.SecurityGroup", "description" : "App1", "groupId" : "sg-0123456789", "groupName" : "app1-frontend", "ipPermissions" : [ { "class" : "com.amazonaws.services.ec2.model.IpPermission", "fromPort" : 80, "ipProtocol" : "tcp", "ipRanges" : [ "10.10.1.1/32", "10.10.1.2/32", + "10.10.1.3/32", - "10.10.1.4/32" ], "toPort" : 80, "userIdGroupPairs" : [ ] } ], "ipPermissionsEgress" : [ ], "ownerId" : "2345678912345", "tags" : [ ], "vpcId" : null }
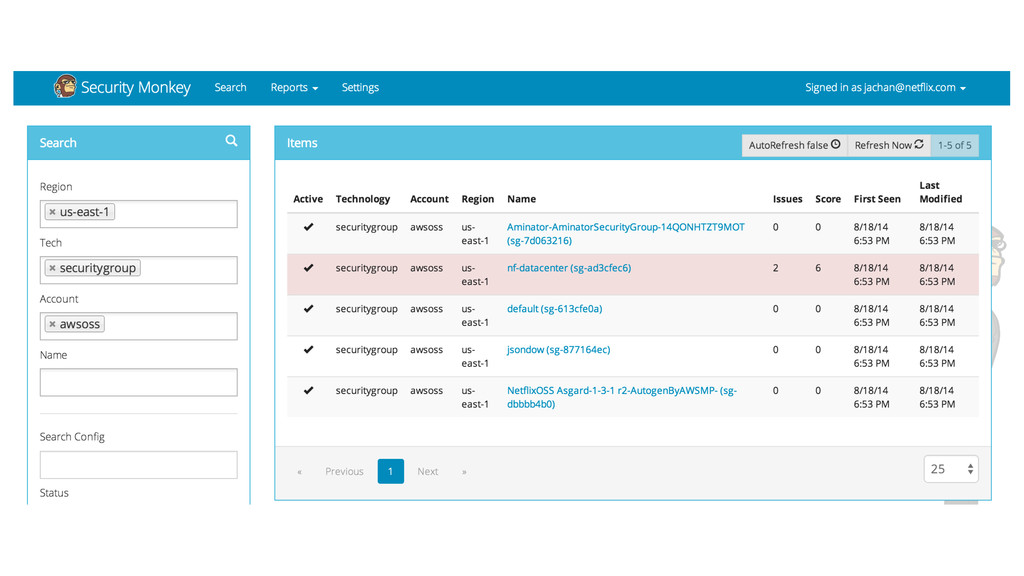
Security Monkey
None
Monitoring - Tips Know your options Ideal place to drive
automation
Monitoring - Traps There is no configuration history CloudTrail logs
are complex
AWS Security Resources http://tiny.cc/awssecurity
Thank you!
[email protected]
: @chanjbs


 chanj
 riyaamemiya
 syuchimu
 4o1sobblue
 techtekt
 ivry_presentationmaterials
 kizawa2020
 camiha
 teamlab
 greenmidori
 iktakahiro
 tokuty
 pauljervisheath
 badams
 khoart
 tammyeverts
 greggifford
 chrisshort
 moore
 davetheseo
 jnunemaker
 rkaga
 mlcsv
 charlesmeaden
![{ "Statement": [ { "Action": [ "ses:SendEmail" ], "Effect": "Allow",](https://files.speakerdeck.com/presentations/20e6c3d03dfb0132b6be56cb37b563fb/slide_76.jpg)