Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
DFIR with Sysinternals
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
dvirus
August 16, 2017
Technology
390
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
DFIR with Sysinternals
Basic malware analysis with sysinternals suite
dvirus
August 16, 2017
More Decks by dvirus
See All by dvirus
Taller Análisis Básico de Malware
dvirus
0
180
Captura y Análisis de paquetes de Red
dvirus
0
1.9k
Guía TCPDump
dvirus
0
130
Netcat
dvirus
0
81
Introducción al Análisis Forense Digital
dvirus
1
720
Taller Suricata IDS | Habemus Hacking
dvirus
0
510
SecZone 2012 - Introducing VUSF - VoIP & Unified Communications Security Framework
dvirus
1
99
Iniciativas y Comunidades para la educación en Internet
dvirus
0
60
VoIP Malware
dvirus
0
130
Other Decks in Technology
See All in Technology
Conditional PED-ANOVA: Hyperparameter Importance in Hierarchical & Dynamic Search Spaces
pfn
PRO
0
130
1つのリクエストを追って理解する - llm-dのP/D分離
akhino
1
160
スキマバイトという雇用形態は存在しないので、雇用期間1日のアルバイト契約を事業者とワーカーが結ぶ手続きを支えるのがタイミーなんです
akitoshiga
0
200
Browser Spec: Testing Hotwire with Ruby
takahashim
1
120
その Valkey 使いこなしていますか?
onk
PRO
5
1.5k
UniFi(ユニファイ)AIカメラの現場活用
ludicmind
1
440
AI駆動で「他アプリの音を加工できる」アプリを作った
satomasahiro2005
0
150
Getting Started with Google Antigravity
glaforge
0
300
OptunaHub: ブラックボックス最適化のためのプラットフォーム
pfn
PRO
0
140
エンタメ企業のM&Aを支えるデータ基盤 ― 統合から店舗のリアルタイム分析まで / Data Engineering Summit 2026
genda
0
170
大型犬好きによるPugの紹介
yamanoku
1
160
DevelopersIO 2026 知識の地図を描く ─ オントロジーとは何か?
ishikawa_satoru
1
1.7k
Featured
See All Featured
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
620
StorybookのUI Testing Handbookを読んだ
zakiyama
31
7k
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
67k
Getting science done with accelerated Python computing platforms
jacobtomlinson
2
540
Claude Code のすすめ
schroneko
67
230k
Visual Storytelling: How to be a Superhuman Communicator
reverentgeek
2
710
Digital Ethics as a Driver of Design Innovation
axbom
PRO
1
460
No one is an island. Learnings from fostering a developers community.
thoeni
21
3.9k
How to make the Groovebox
asonas
2
2.5k
Dominate Local Search Results - an insider guide to GBP, reviews, and Local SEO
greggifford
PRO
0
370
AI Search: Implications for SEO and How to Move Forward - #ShenzhenSEOConference
aleyda
1
1.4k
ラッコキーワード サービス紹介資料
rakko
1
5.3M
Transcript
Incident Response with Sysinternals WannaCry Edition @ShieldNow
About Me @dvirus Daniel Rodríguez Chief Information Security Officer -
O4IT
Agenda • Incident Response • Malware Analysis • Setting Up
the Virtual Lab • Basic Static Analysis • Basic Dynamic Analysis • WannaCry Demo
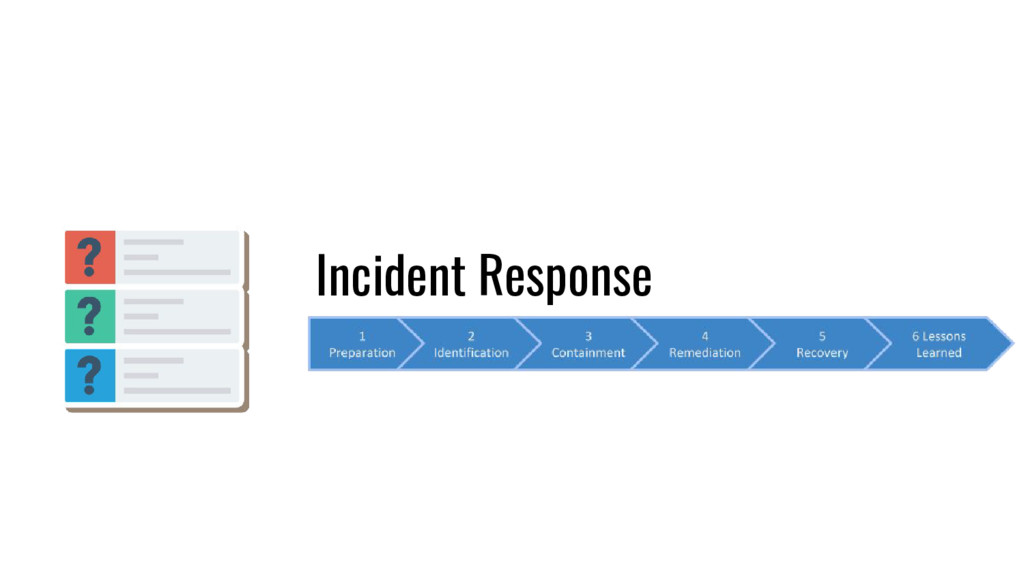
Incident Response
Malware Analysis
Setting Up Your Virtual Lab https://dvirus.training/lessons/configuracion-de-laboratorio/
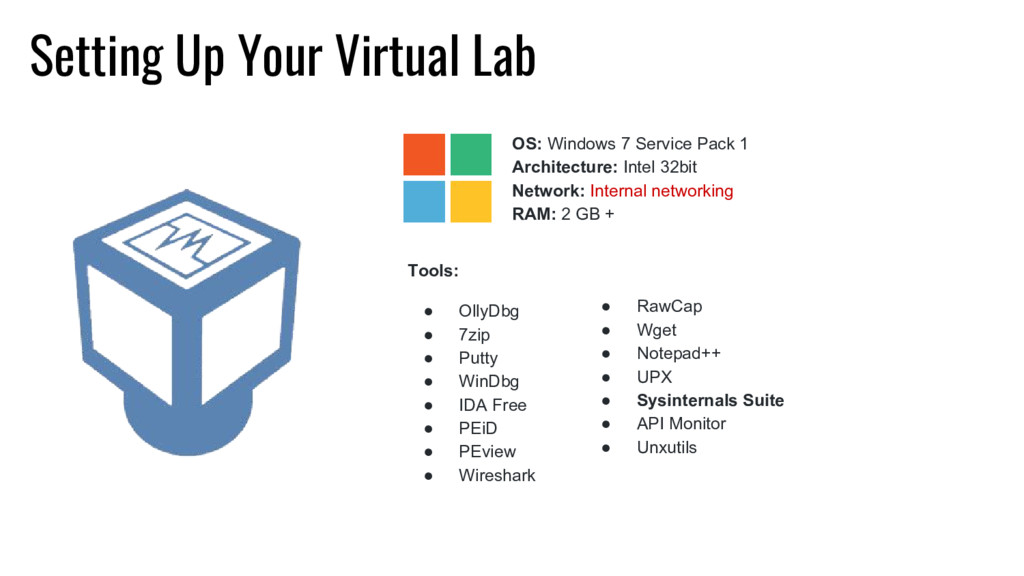
OS: Windows 7 Service Pack 1 Architecture: Intel 32bit Network:
Internal networking RAM: 2 GB + Tools: • OllyDbg • 7zip • Putty • WinDbg • IDA Free • PEiD • PEview • Wireshark • RawCap • Wget • Notepad++ • UPX • Sysinternals Suite • API Monitor • Unxutils Setting Up Your Virtual Lab
Basic Static Analysis Examines malware without actually running it.
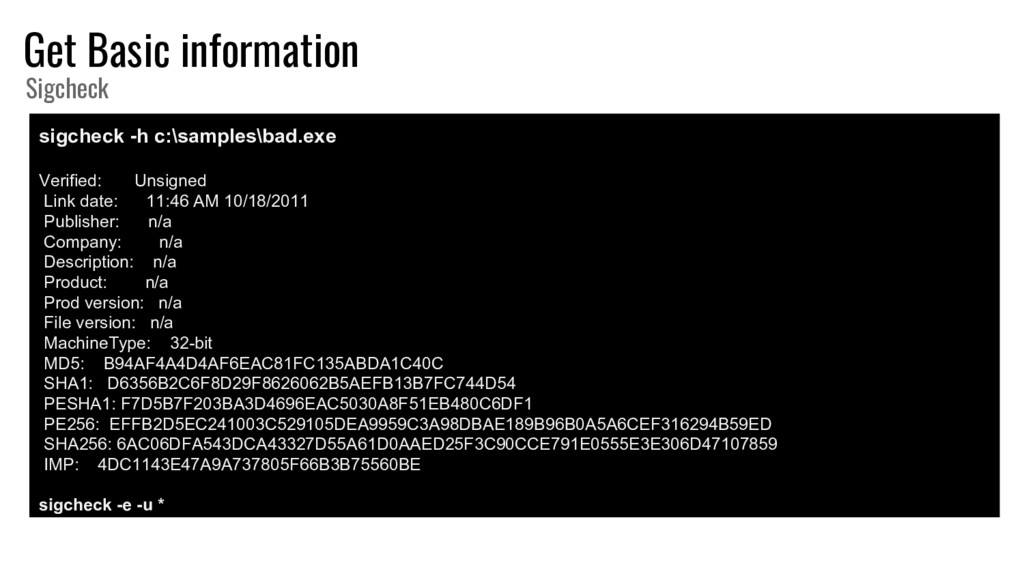
Get Basic information Sigcheck sigcheck -h c:\samples\bad.exe Verified: Unsigned Link
date: 11:46 AM 10/18/2011 Publisher: n/a Company: n/a Description: n/a Product: n/a Prod version: n/a File version: n/a MachineType: 32-bit MD5: B94AF4A4D4AF6EAC81FC135ABDA1C40C SHA1: D6356B2C6F8D29F8626062B5AEFB13B7FC744D54 PESHA1: F7D5B7F203BA3D4696EAC5030A8F51EB480C6DF1 PE256: EFFB2D5EC241003C529105DEA9959C3A98DBAE189B96B0A5A6CEF316294B59ED SHA256: 6AC06DFA543DCA43327D55A61D0AAED25F3C90CCE791E0555E3E306D47107859 IMP: 4DC1143E47A9A737805F66B3B75560BE sigcheck -e -u *
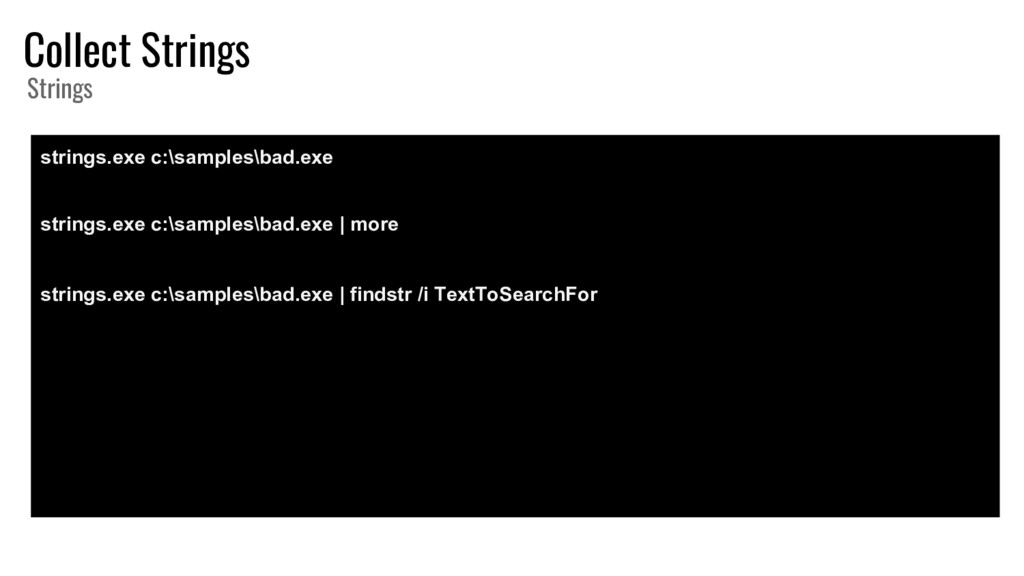
Collect Strings Strings strings.exe c:\samples\bad.exe strings.exe c:\samples\bad.exe | more strings.exe
c:\samples\bad.exe | findstr /i TextToSearchFor
Basic Dynamic Analysis Running the malware and observing its behavior
on the system
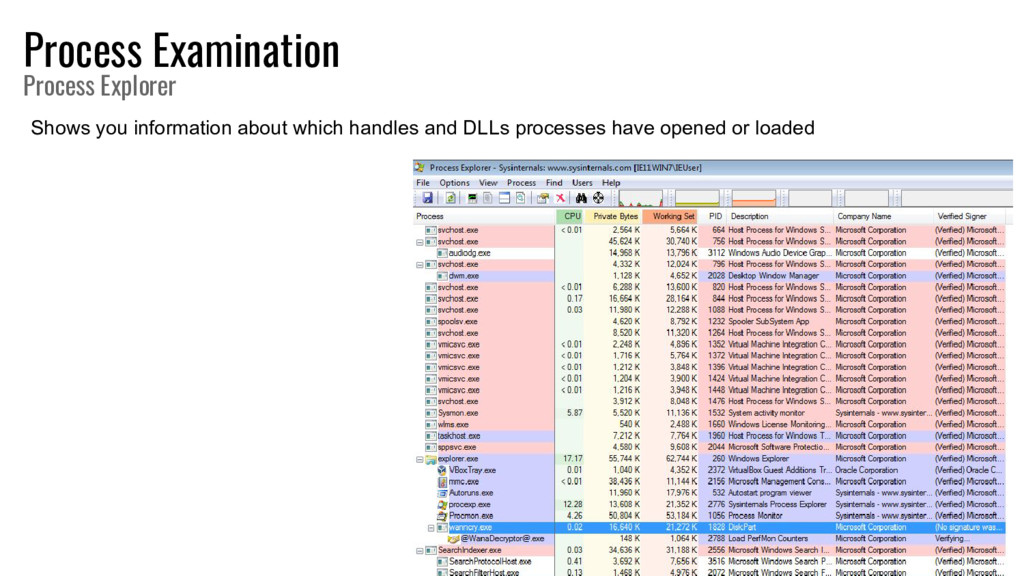
Process Examination Process Explorer Shows you information about which handles
and DLLs processes have opened or loaded
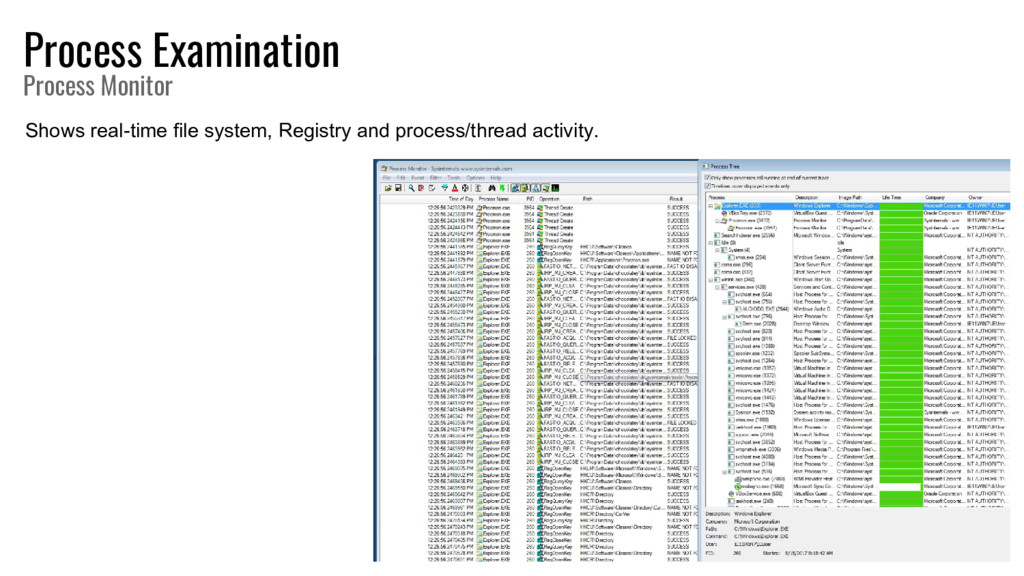
Process Examination Process Monitor Shows real-time file system, Registry and
process/thread activity.
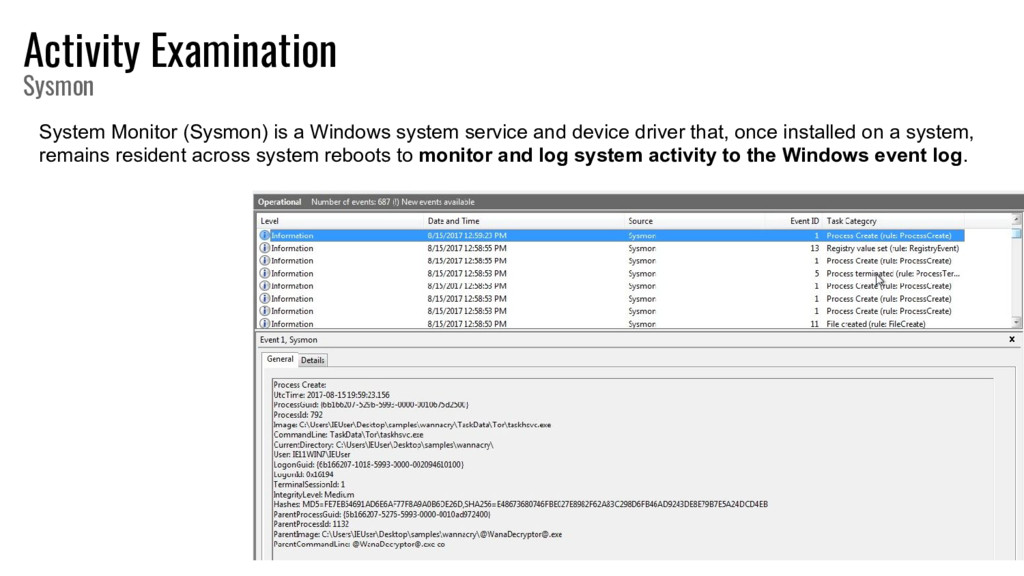
Activity Examination Sysmon System Monitor (Sysmon) is a Windows system
service and device driver that, once installed on a system, remains resident across system reboots to monitor and log system activity to the Windows event log.
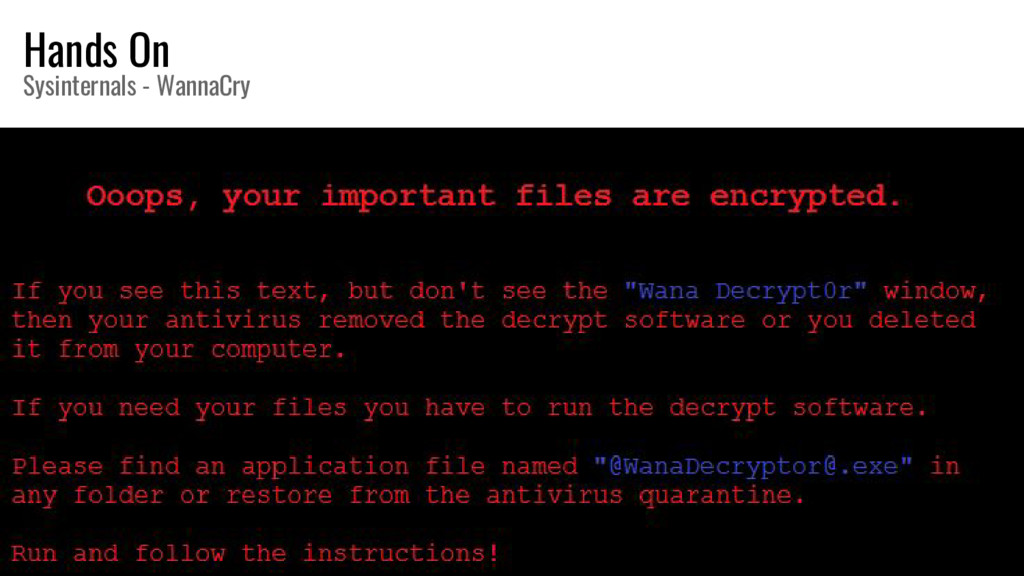
Hands On Sysinternals - WannaCry
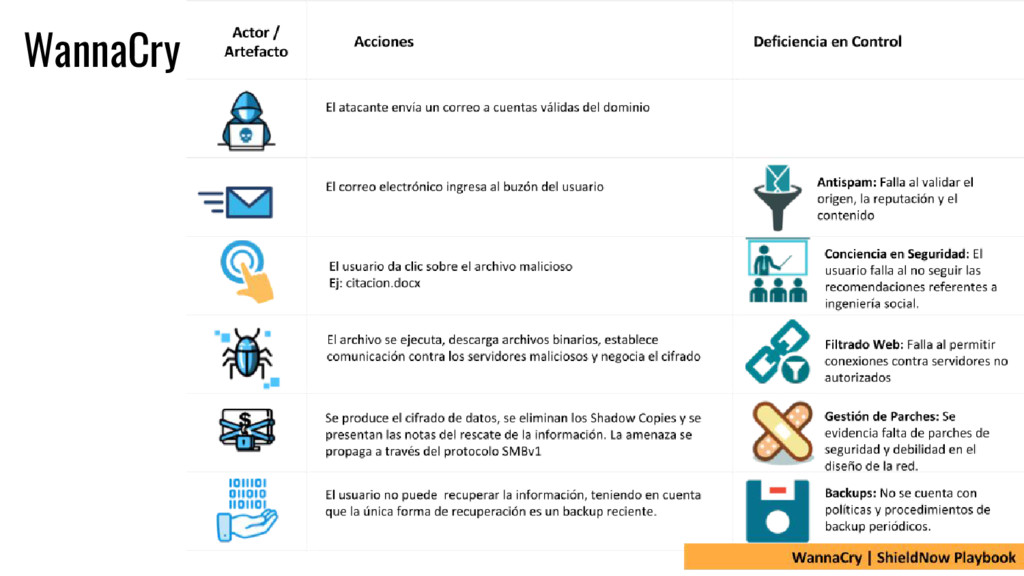
WannaCry
Recursos • Malware Hunting with the Sysinternals Tools - Mark
Russinovich RSA Conference 2015 • Sysmon - DFIR https://github.com/MHaggis/sysmon-dfir • WannaCry – Lecciones aprendidas https://shieldnow.co/2017/05/13/wannacry-lecciones-aprendidas/ • https://dvirus.training/courses/analisis-de-malware-101/ • https://dvirus.training/windows-sysinternals/
Incident Response with Sysinternals WannaCry Edition @ShieldNow - @dvirus


 dvirus
 pfn
 akhino
 akitoshiga
 takahashim
 onk
 ludicmind
 satomasahiro2005
 glaforge
 genda
 yamanoku
 ishikawa_satoru
 konakalab
 zakiyama
 madoxten
 jacobtomlinson
 schroneko
 reverentgeek
 axbom
 thoeni
 asonas
 greggifford
 aleyda
 rakko