Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
How We Built a Secure Sandbox Platform for AI A...
Search
GMO Flatt Security
November 17, 2025
Technology
740
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
How We Built a Secure Sandbox Platform for AI Agents
GMO Flatt Security
November 17, 2025
More Decks by GMO Flatt Security
See All by GMO Flatt Security
AIエージェントの開発・提供におけるセキュリティリスクの論点と対策
flatt_security
2
740
Claude Mythos、Fable...フロンティアAIの最新動向と企業のセキュリティ対策
flatt_security
1
320
インシデント事例と パッケージの全量解析に学ぶ ソフトウェアサプライチェーンの守り方 / supply-chain-attack-defense
flatt_security
1
4.3k
コードを読まない時代の死角: 検出から検証へ、脆弱性診断AIエージェントの現在地 / state-of-vulnerability-ai-agents
flatt_security
4
1.4k
セキュアなコンテナイメージをつくろう 〜CVE-free コンテナイメージ「Takumi Images」の概要と裏話〜
flatt_security
3
390
AI Agent SaaS を支える自社仮想化基盤への挑戦と実運用 / ai-agent-saas-virtualization
flatt_security
3
6.4k
Mastra ソフトウェアサプライチェーン攻撃の概要と対応指針
flatt_security
1
140
ソフトウェアサプライチェーン攻撃対策として今からサクッとできること
flatt_security
2
360
更なる npm パッケージ侵害事件「Mini Shai-Hulud」徹底解説
flatt_security
1
670
Other Decks in Technology
See All in Technology
AI時代に必要な脅威モデリング― 変化の速度に負けない理解とリスク判断
masakane55
5
1.3k
WasmをRustにする
sansantech
PRO
0
200
OSC2026on_the-world-is-waiting-for-your-voice.pdf
naruoga
0
370
実践! SRE × AI - ABEMA における AIOps -
tetsuya28
7
3k
⾮構造化データを価値に変える AI エージェント基盤とその組織
ivry_presentationmaterials
0
140
QA4AI 2026-Oct 生成AI時代の品質保証
tokuty
0
570
事業活動を AI Ready にする攻めと守りのデータエンジニアリング / data-engineering-for-ai-ready-business
pei0804
7
2.7k
10年後、Engineering 行為を剥奪されるとして、わたしたちは、どう、何を創ればいいだろうか。 / If Engineering Is Taken Away in 10 Years, How and What Should We Create?
bitkey
PRO
1
130
[AWS 秋のクラウドオペレーション祭り 2026]AWS DevOps Agentで変わる リリースと運用対応 ~リリース管理機能と Directed actions のご紹介~
furuton
4
1.2k
Kiro Crewをはじめよう
kizawa2020
1
150
初対面のメンバーがチームを組み、Claude Codeでゼロからサービスをリリース
mkdev10
1
120
ai_cording_with_k8s_knowledge.pdf
mochizuki875
1
340
Featured
See All Featured
Chasing Engaging Ingredients in Design
codingconduct
0
360
A Soul's Torment
seathinner
8
3.7k
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
Reality Check: Gamification 10 Years Later
codingconduct
0
2.3k
The World Runs on Bad Software
bkeepers
PRO
72
12k
Joys of Absence: A Defence of Solitary Play
codingconduct
1
550
HTML-Aware ERB: The Path to Reactive Rendering @ RubyCon 2026, Rimini, Italy
marcoroth
5
800
ラッコキーワード サービス紹介資料
rakko
1
5.3M
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
世界の人気アプリ100個を分析して見えたペイウォール設計の心得
akihiro_kokubo
PRO
74
43k
Jamie Indigo - Trashchat’s Guide to Black Boxes: Technical SEO Tactics for LLMs
techseoconnect
PRO
0
700
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
490
Transcript
How We Built a Secure Sandbox Platform for AI Agents
AIエージェントSaaSを安全に 提供するための自社サンドボックス基盤 CODE BLUE 2025 Software Engineer @pizzacat83
© 2025 GMO Flatt Security Inc. All Rights Reserved. $
whoami @pizzacat83 SWE @ GMO Flatt Security Inc. Developing “Takumi byGMO” Formerly security engineer セキュリティ若手の会 幹事 (第1期) seccamp ‘20 alumnus
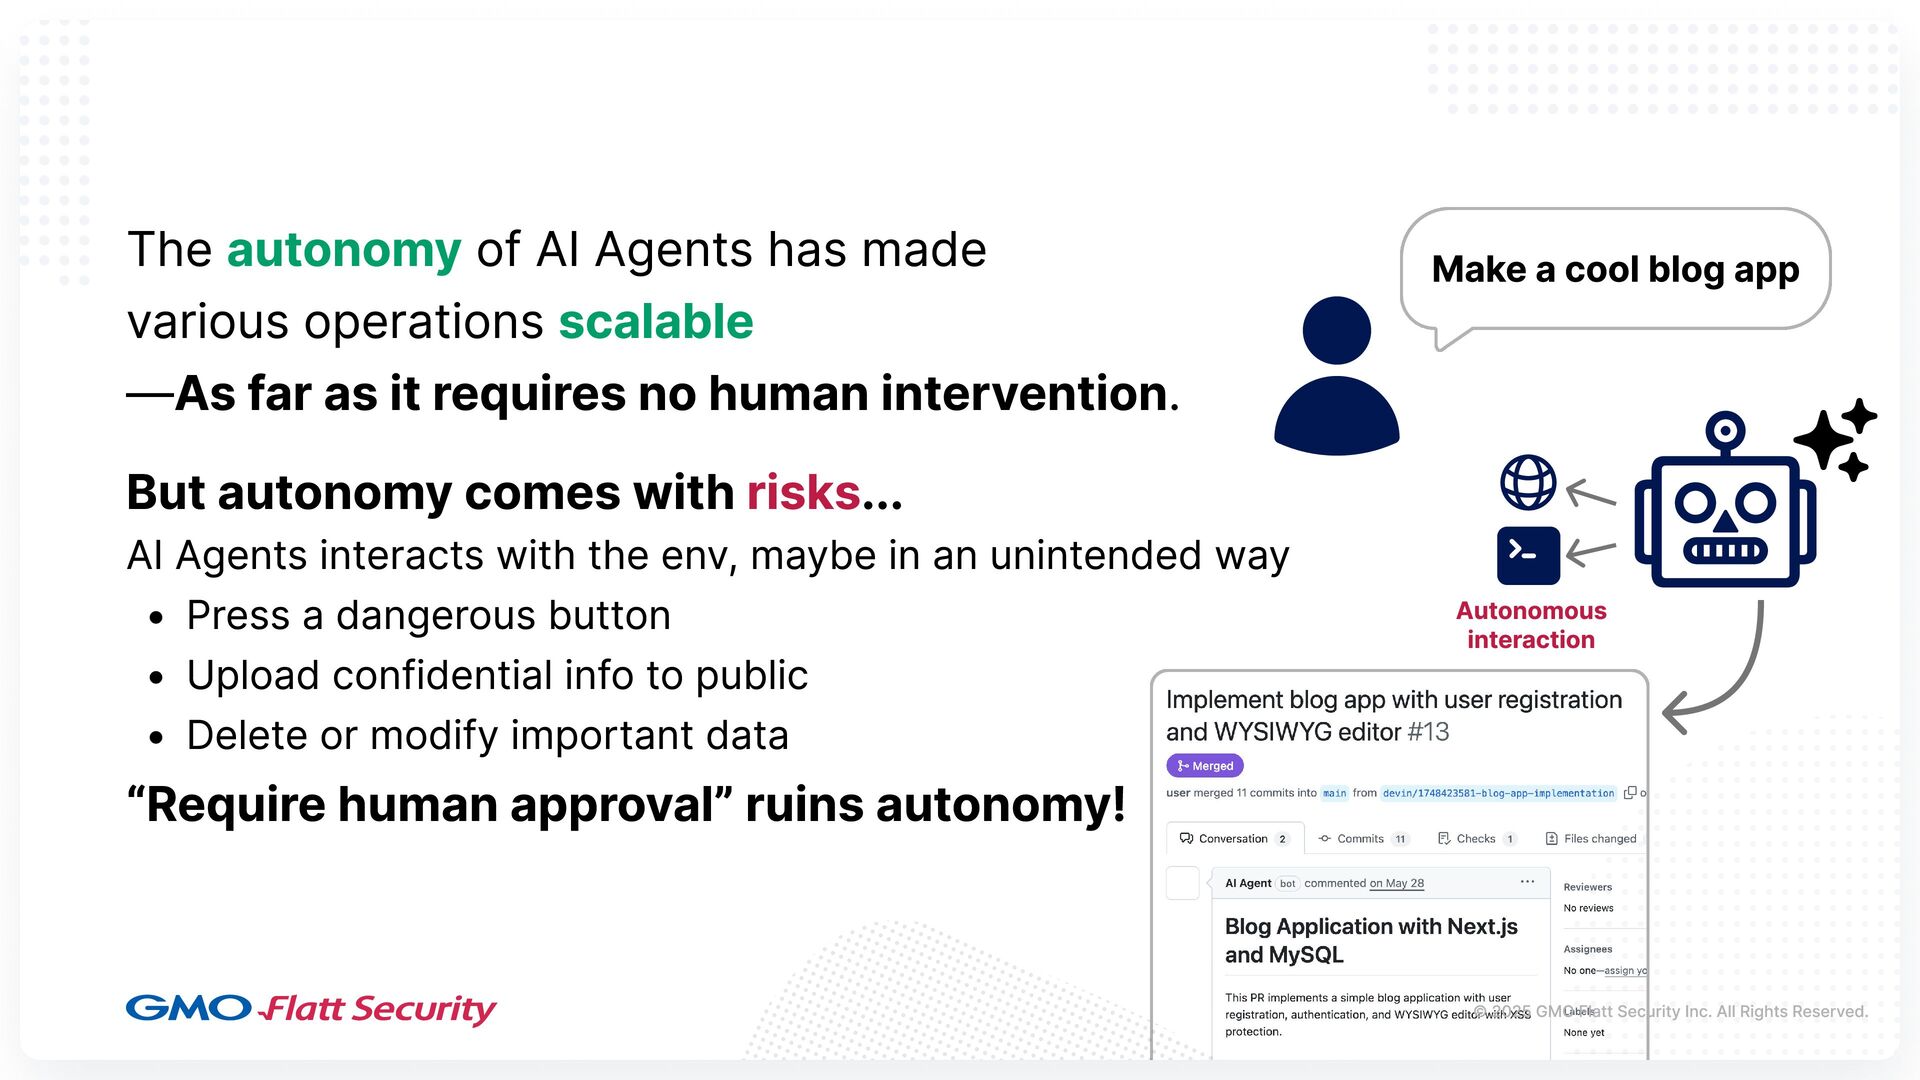
🤖 Make a cool blog app The of AI Agents
has made various operations ––As far as it requires no human intervention. But autonomy comes with ... AI Agents interacts with the env, maybe in an unintended way Press a dangerous button Upload confidential info to public Delete or modify important data “Require human approval” ruins autonomy! autonomy scalable risks Autonomous interaction © 2025 GMO Flatt Security Inc. All Rights Reserved.
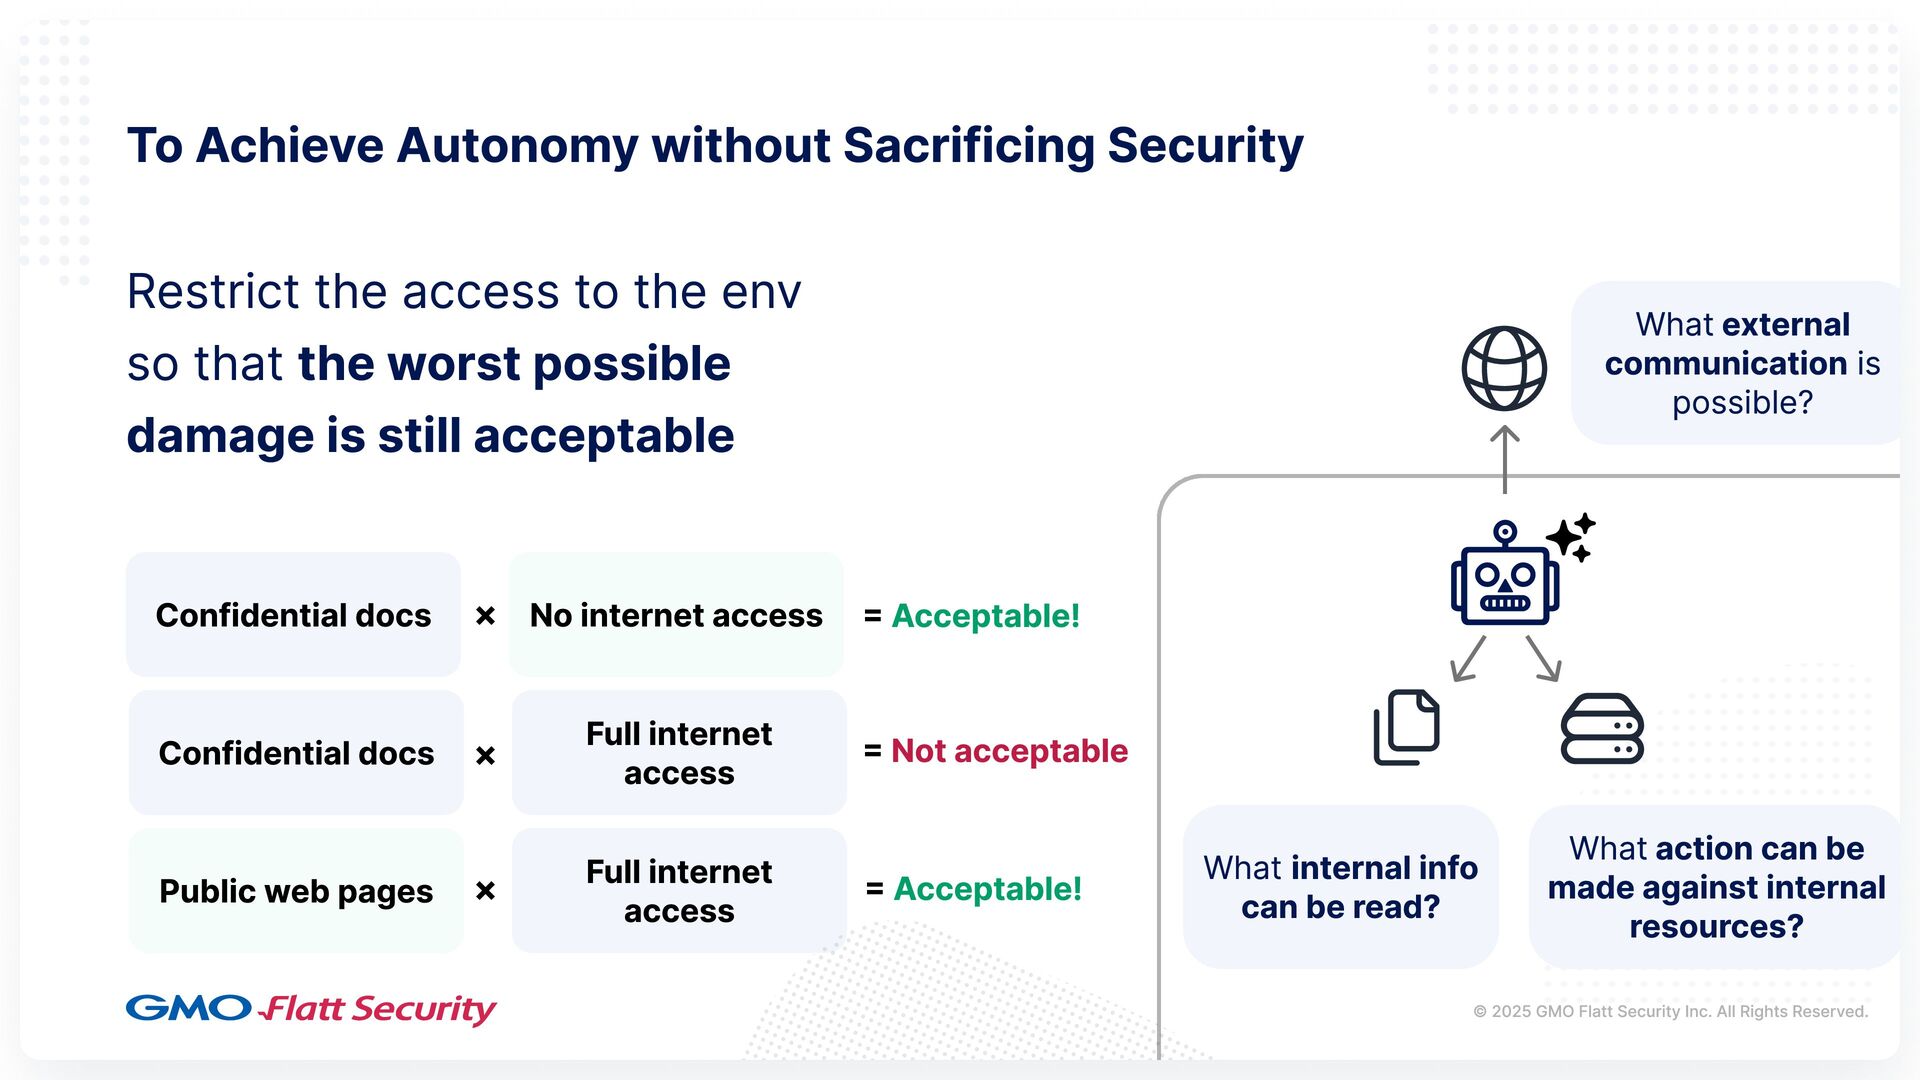
Restrict the access to the env so that the worst
possible damage is still acceptable 🤖 What internal info can be read? What external communication is possible? Confidential docs Public web pages Confidential docs Full internet access Full internet access No internet access = Acceptable! = Not acceptable × × × = Acceptable! © 2025 GMO Flatt Security Inc. All Rights Reserved. To Achieve Autonomy without Sacrificing Security What action can be made against internal resources?
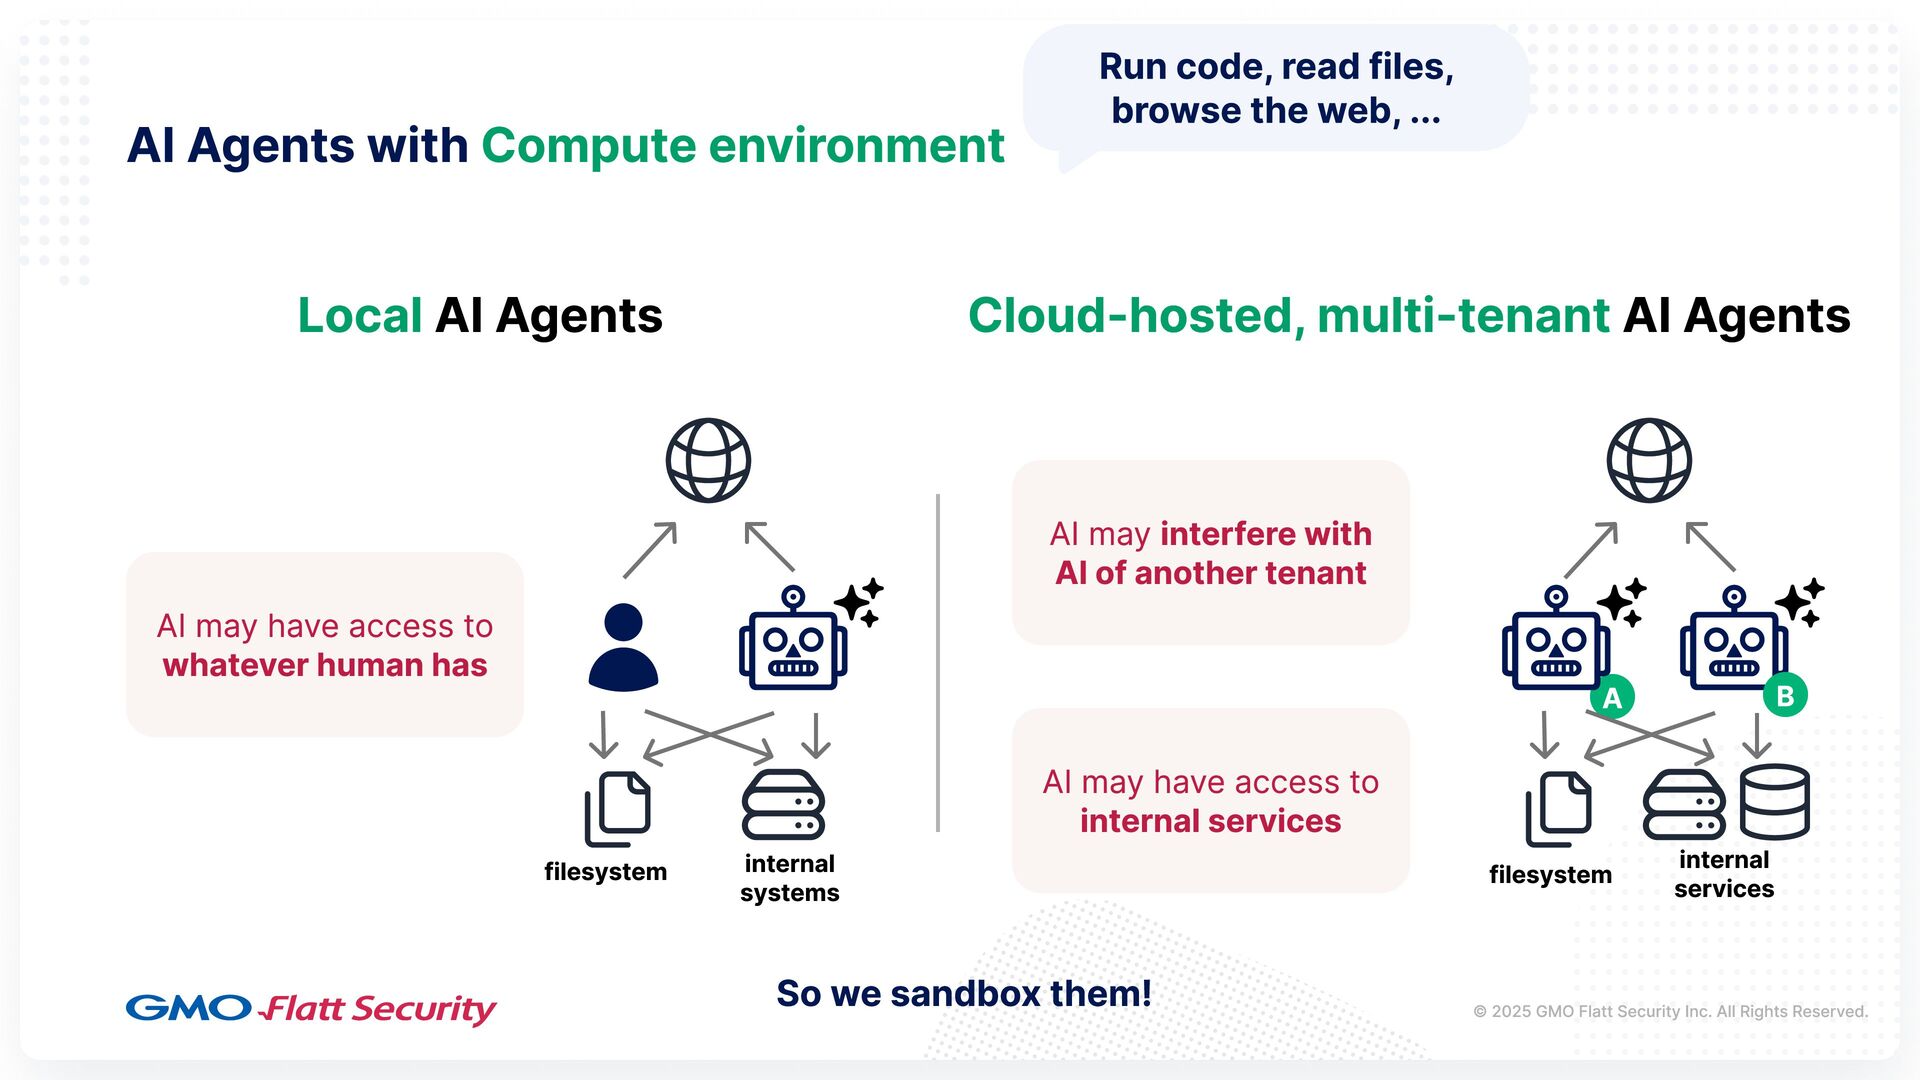
Local AI Agents Cloud-hosted, multi-tenant AI Agents AI may have
access to whatever human has AI may interfere with AI of another tenant AI may have access to internal services filesystem filesystem internal systems A internal services © 2025 GMO Flatt Security Inc. All Rights Reserved. AI Agents with Compute environment Run code, read files, browse the web, ... So we sandbox them! 🤖 🤖 B 🤖
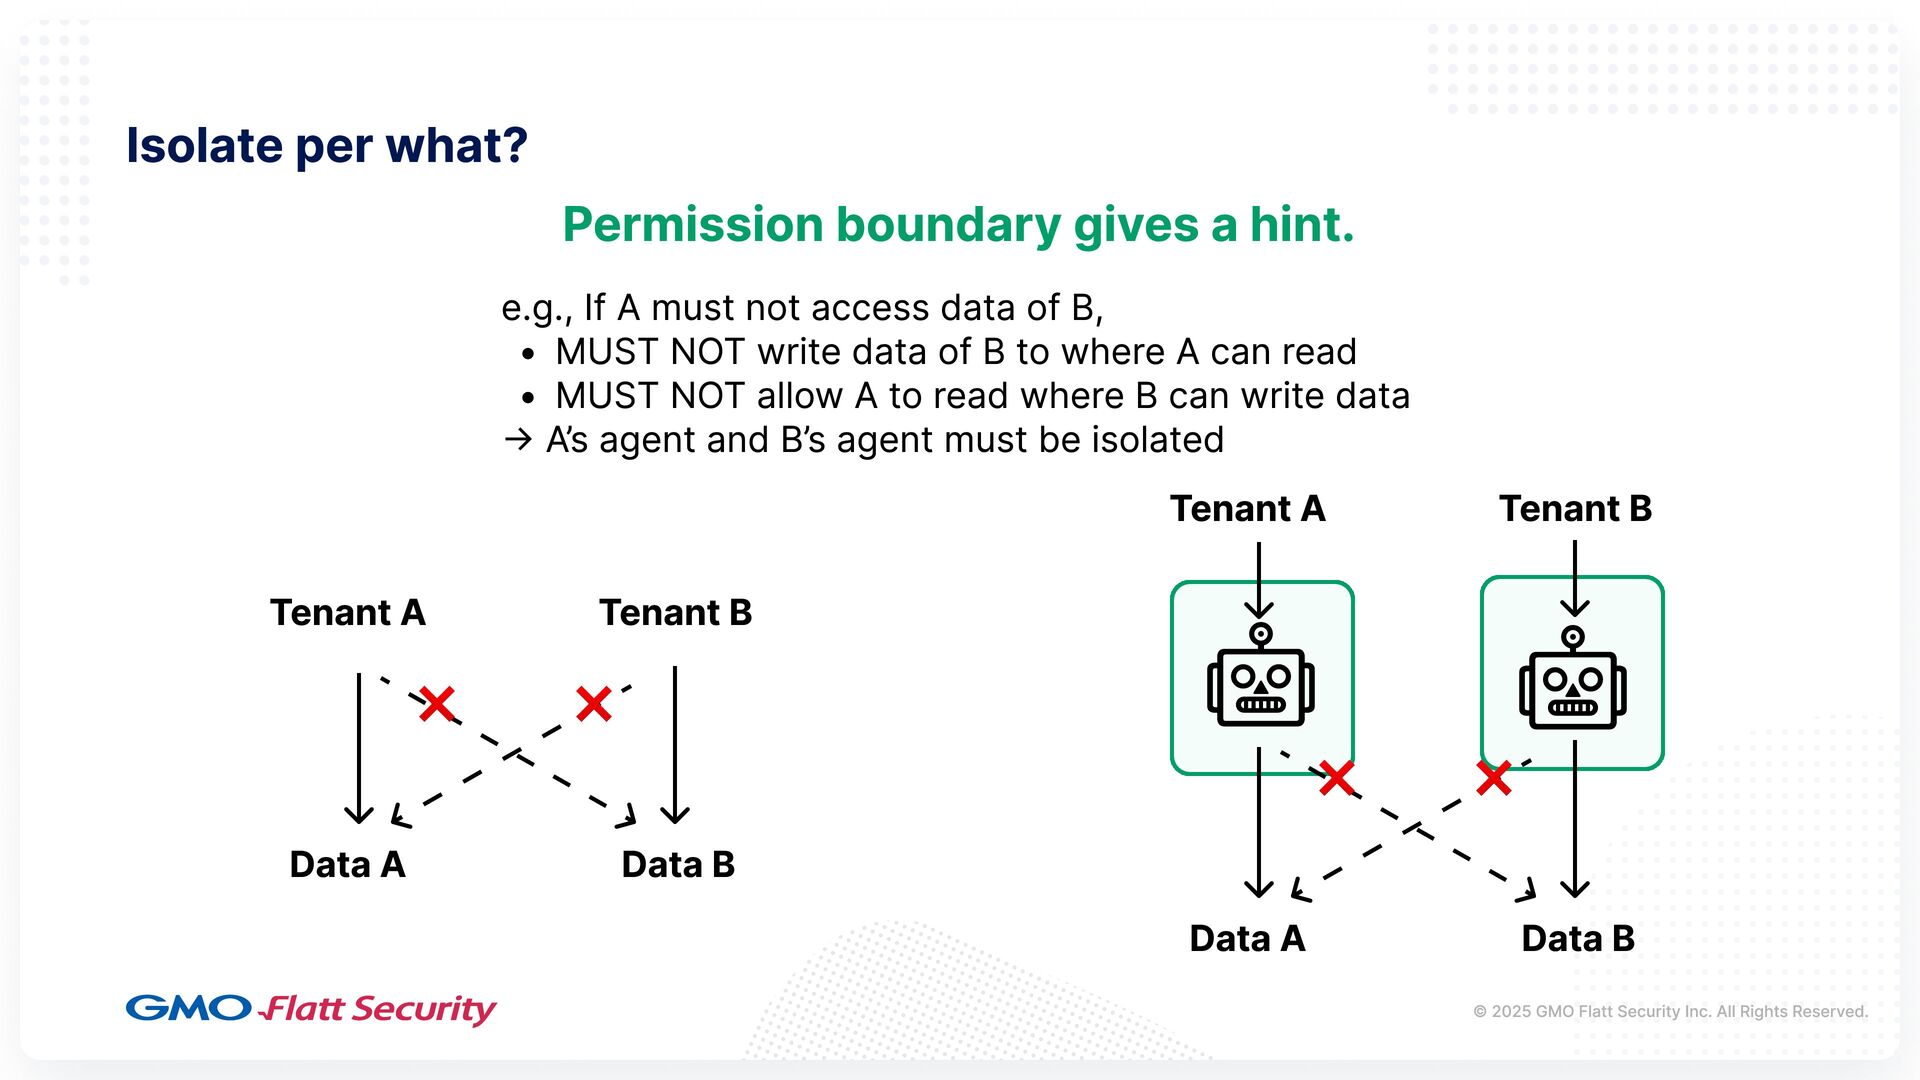
Tenant A Tenant A Data A Data A Data B
Data B Tenant B Tenant B 🤖 🤖 e.g., If A must not access data of B, MUST NOT write data of B to where A can read MUST NOT allow A to read where B can write data → A’s agent and B’s agent must be isolated Permission boundary gives a hint. © 2025 GMO Flatt Security Inc. All Rights Reserved. Isolate per what?
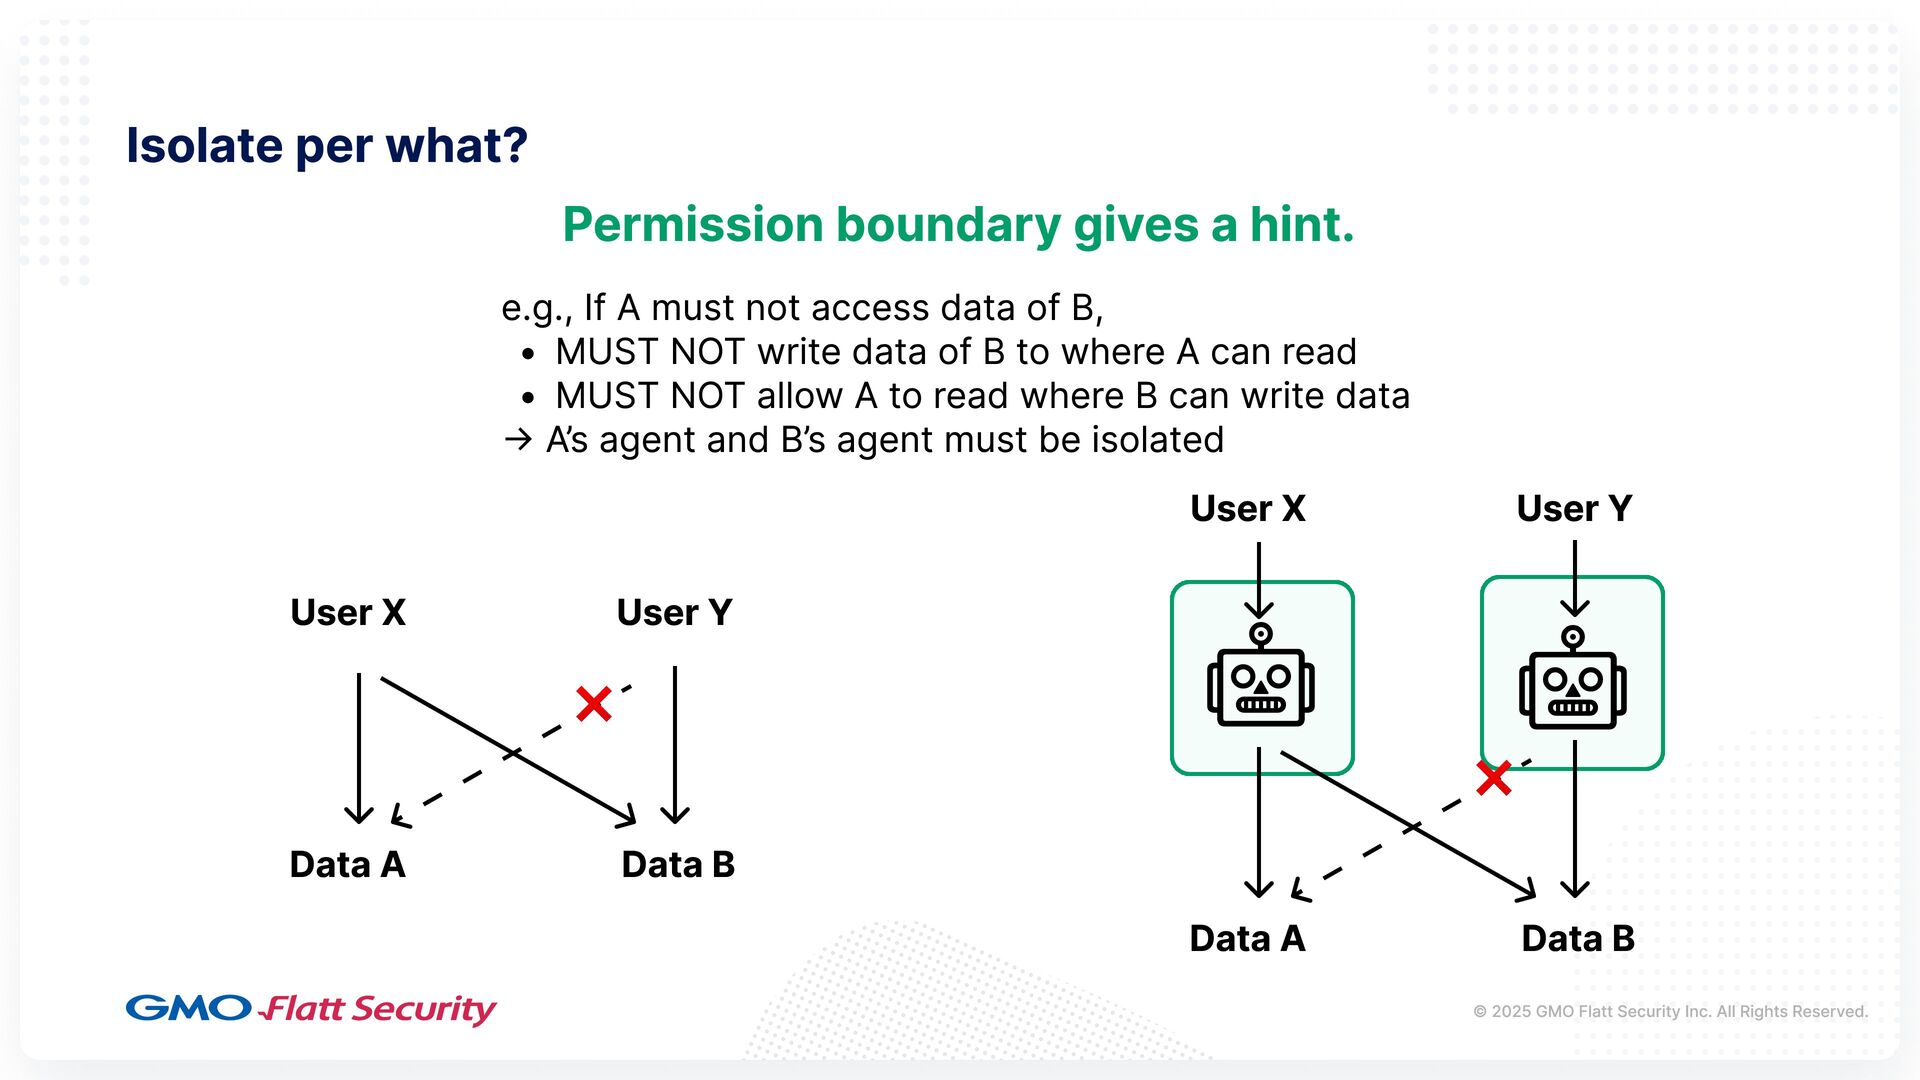
User X User X Data A Data A Data B
Data B User Y User Y 🤖 🤖 © 2025 GMO Flatt Security Inc. All Rights Reserved. Isolate per what? e.g., If A must not access data of B, MUST NOT write data of B to where A can read MUST NOT allow A to read where B can write data → A’s agent and B’s agent must be isolated Permission boundary gives a hint.
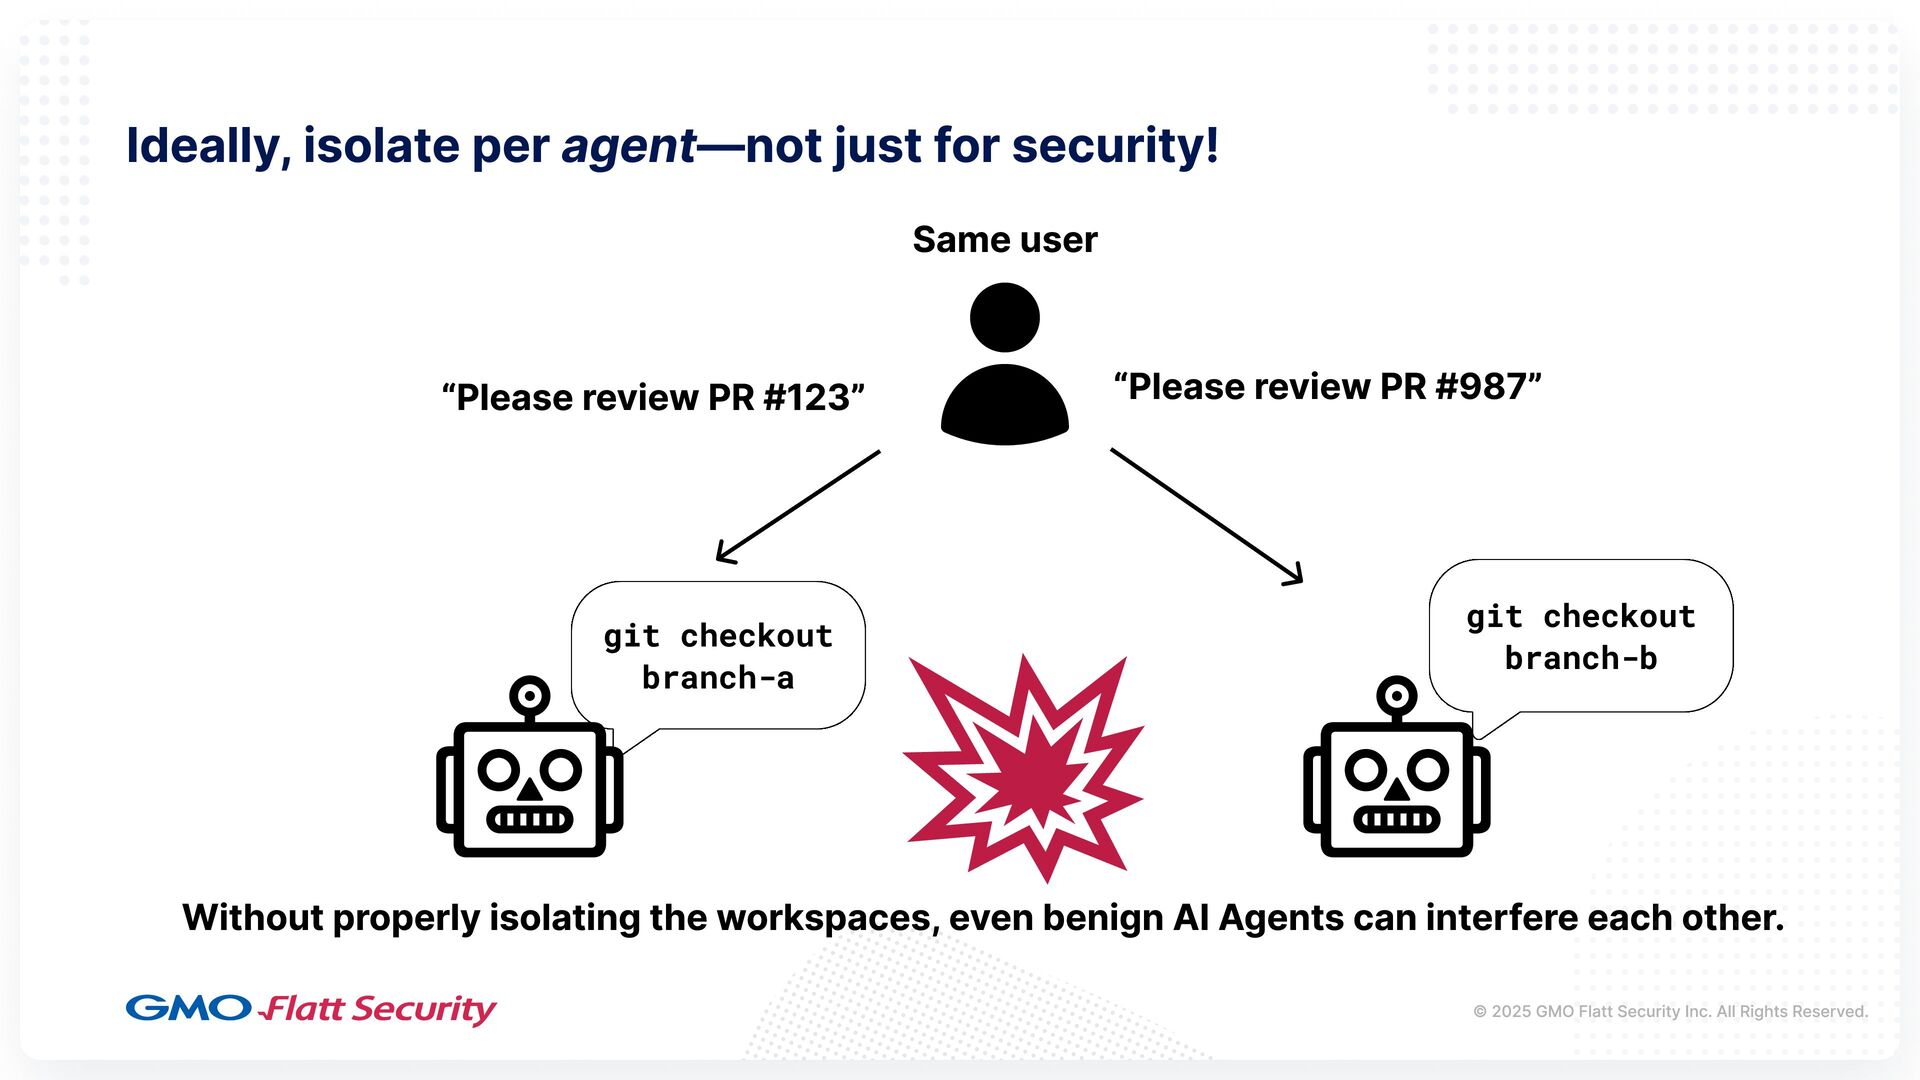
git checkout branch-a git checkout branch-b Same user “Please review
PR #123” “Please review PR #987” Without properly isolating the workspaces, even benign AI Agents can interfere each other. © 2025 GMO Flatt Security Inc. All Rights Reserved. Ideally, isolate per agent––not just for security! 🤖 💥 🤖
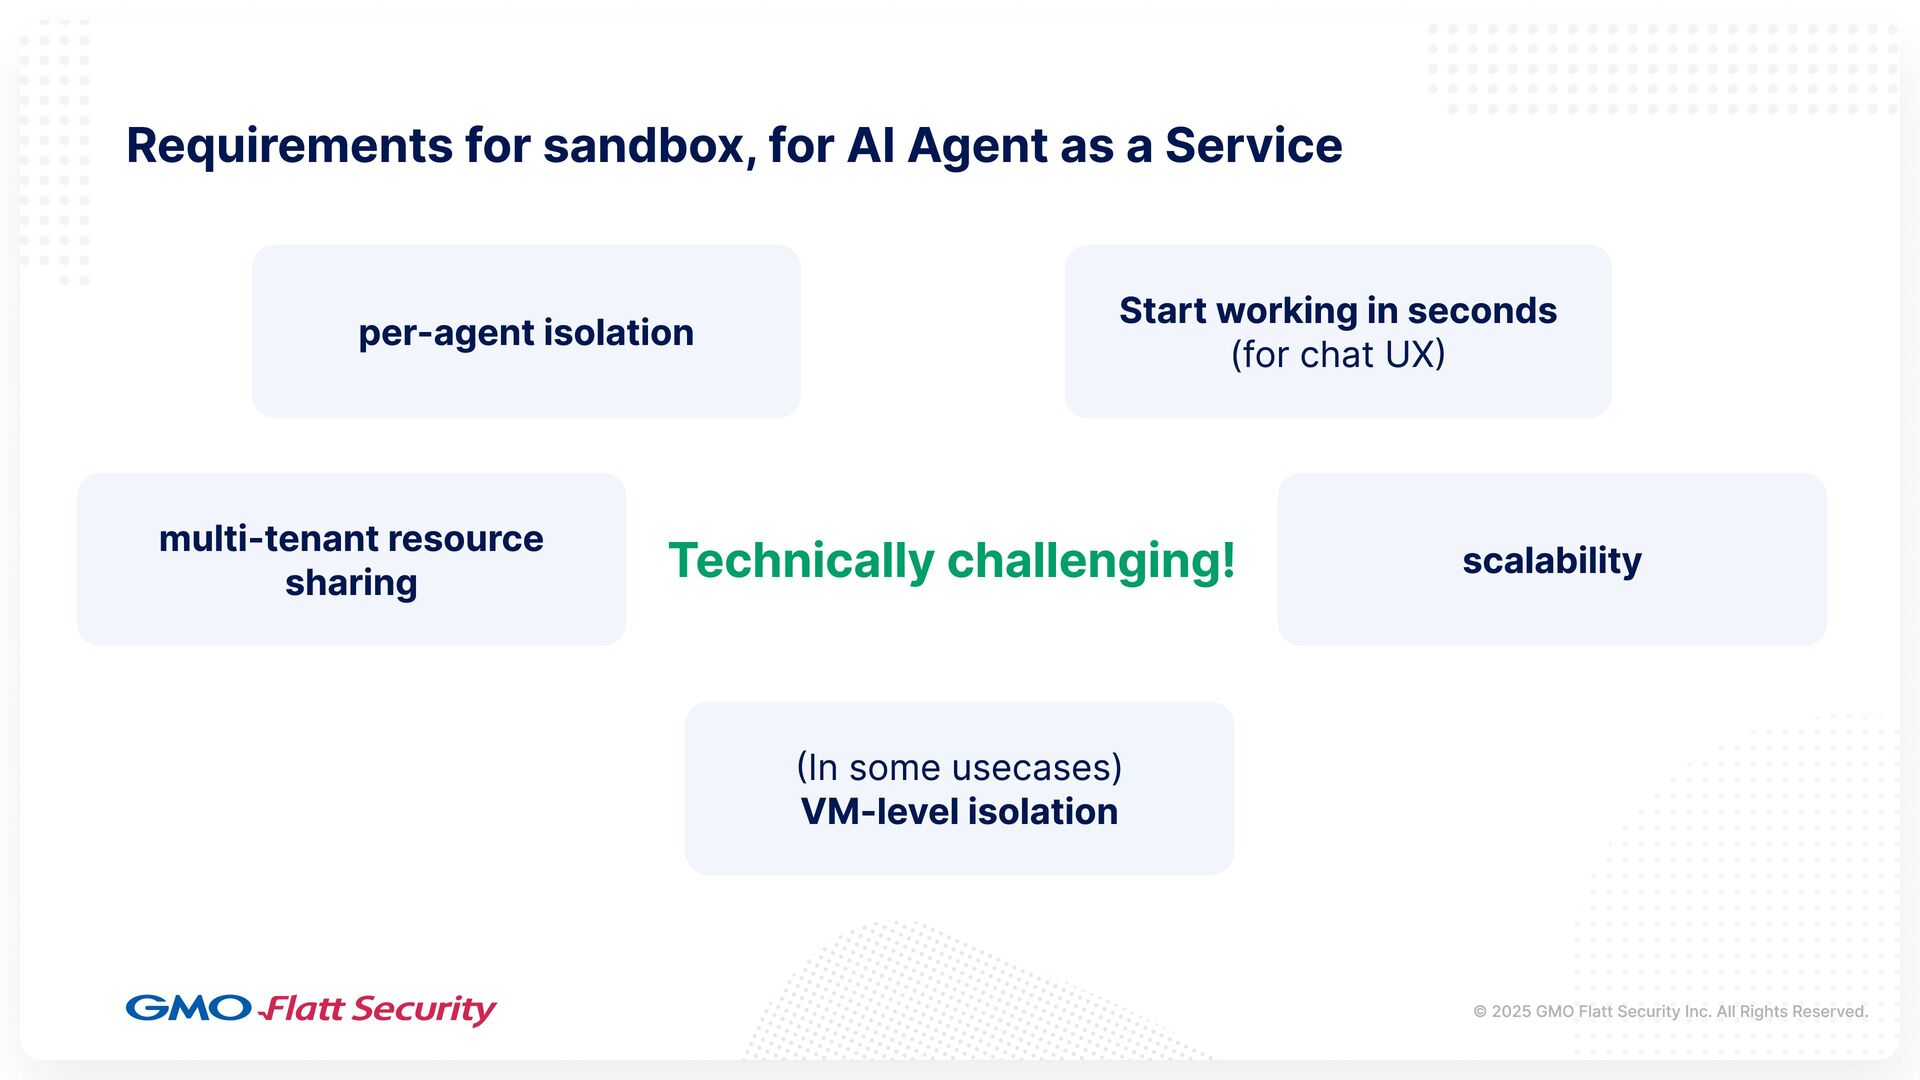
per-agent isolation (In some usecases) VM-level isolation multi-tenant resource sharing
scalability Technically challenging! Start working in seconds (for chat UX) © 2025 GMO Flatt Security Inc. All Rights Reserved. Requirements for sandbox, for AI Agent as a Service
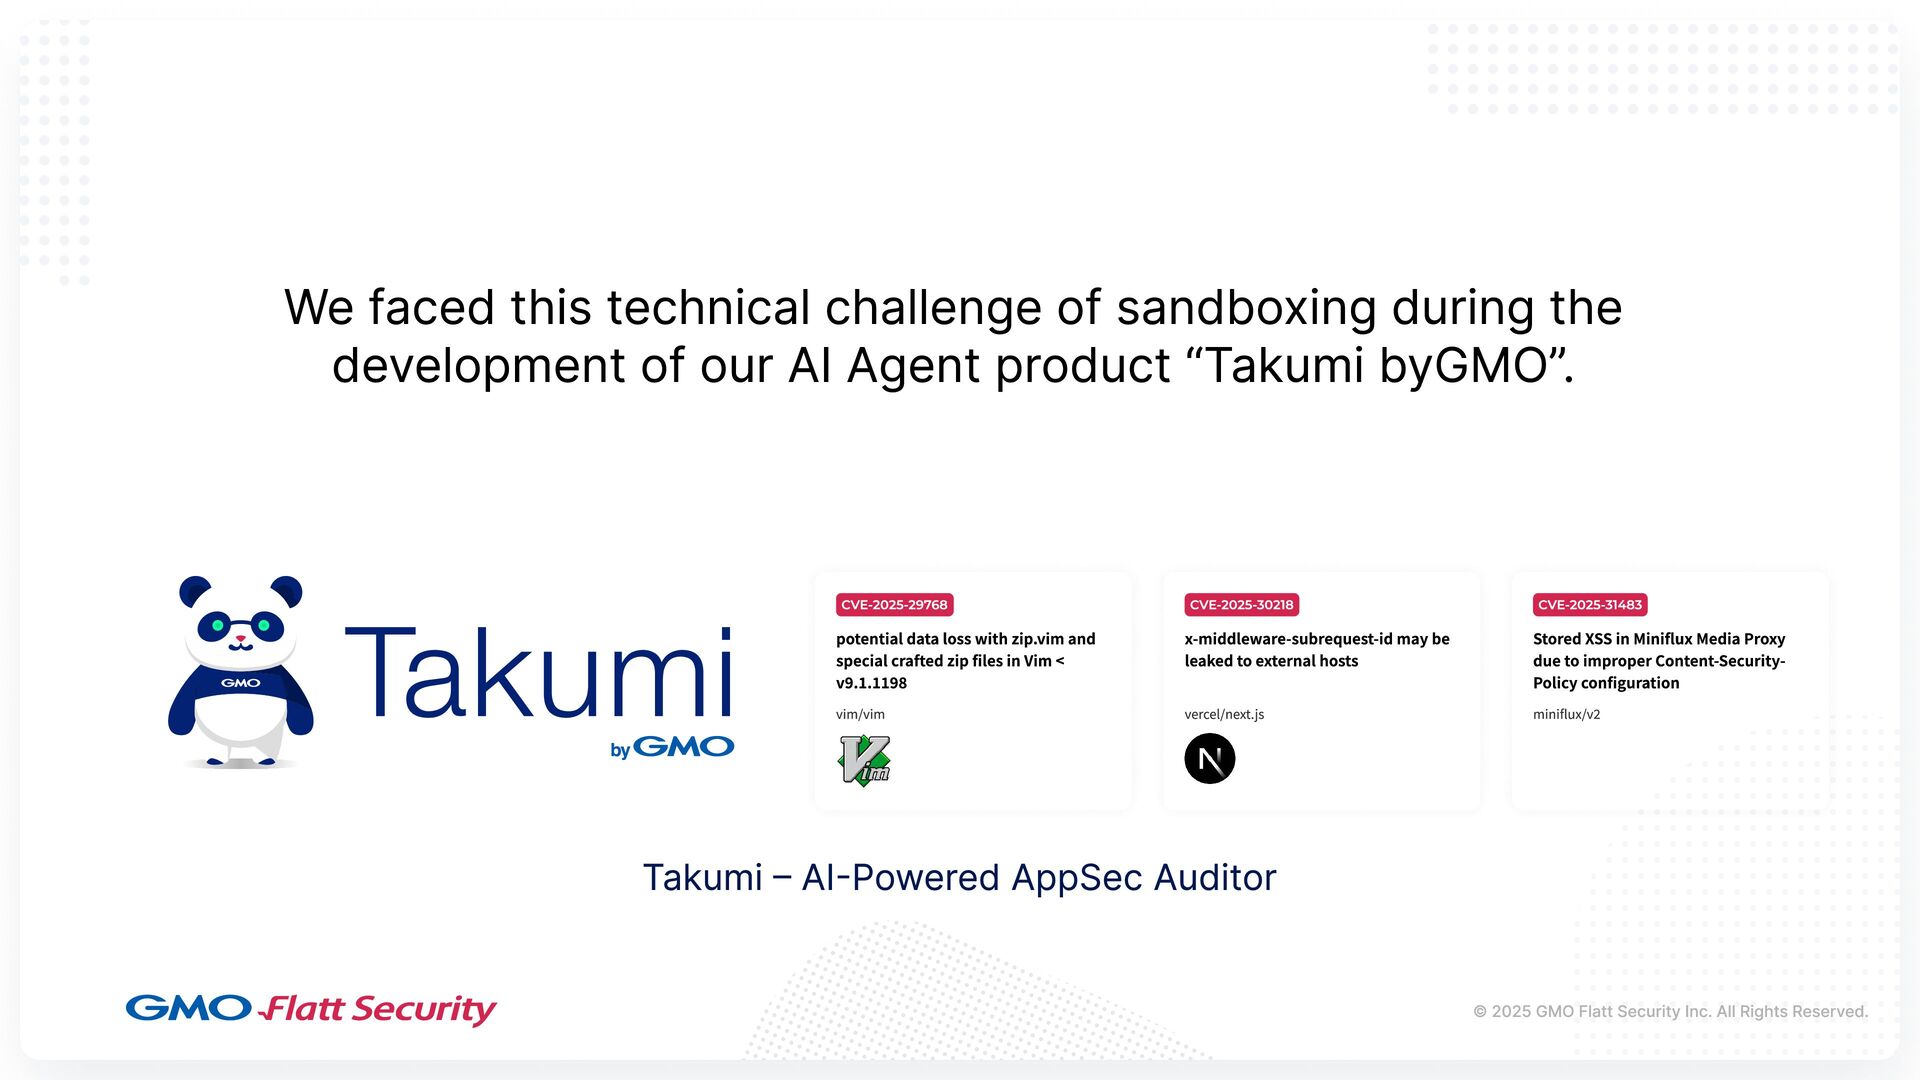
Takumi – AI-Powered AppSec Auditor CVE-2025-29768 potential data loss with
zip.vim and special crafted zip files in Vim < v9.1.1198 vim/vim CVE-2025-30218 x-middleware-subrequest-id may be leaked to external hosts vercel/next.js CVE-2025-31483 Stored XSS in Miniflux Media Proxy due to improper Content-Security- Policy configuration miniflux/v2 We faced this technical challenge of sandboxing during the development of our AI Agent product “Takumi byGMO”. © 2025 GMO Flatt Security Inc. All Rights Reserved.
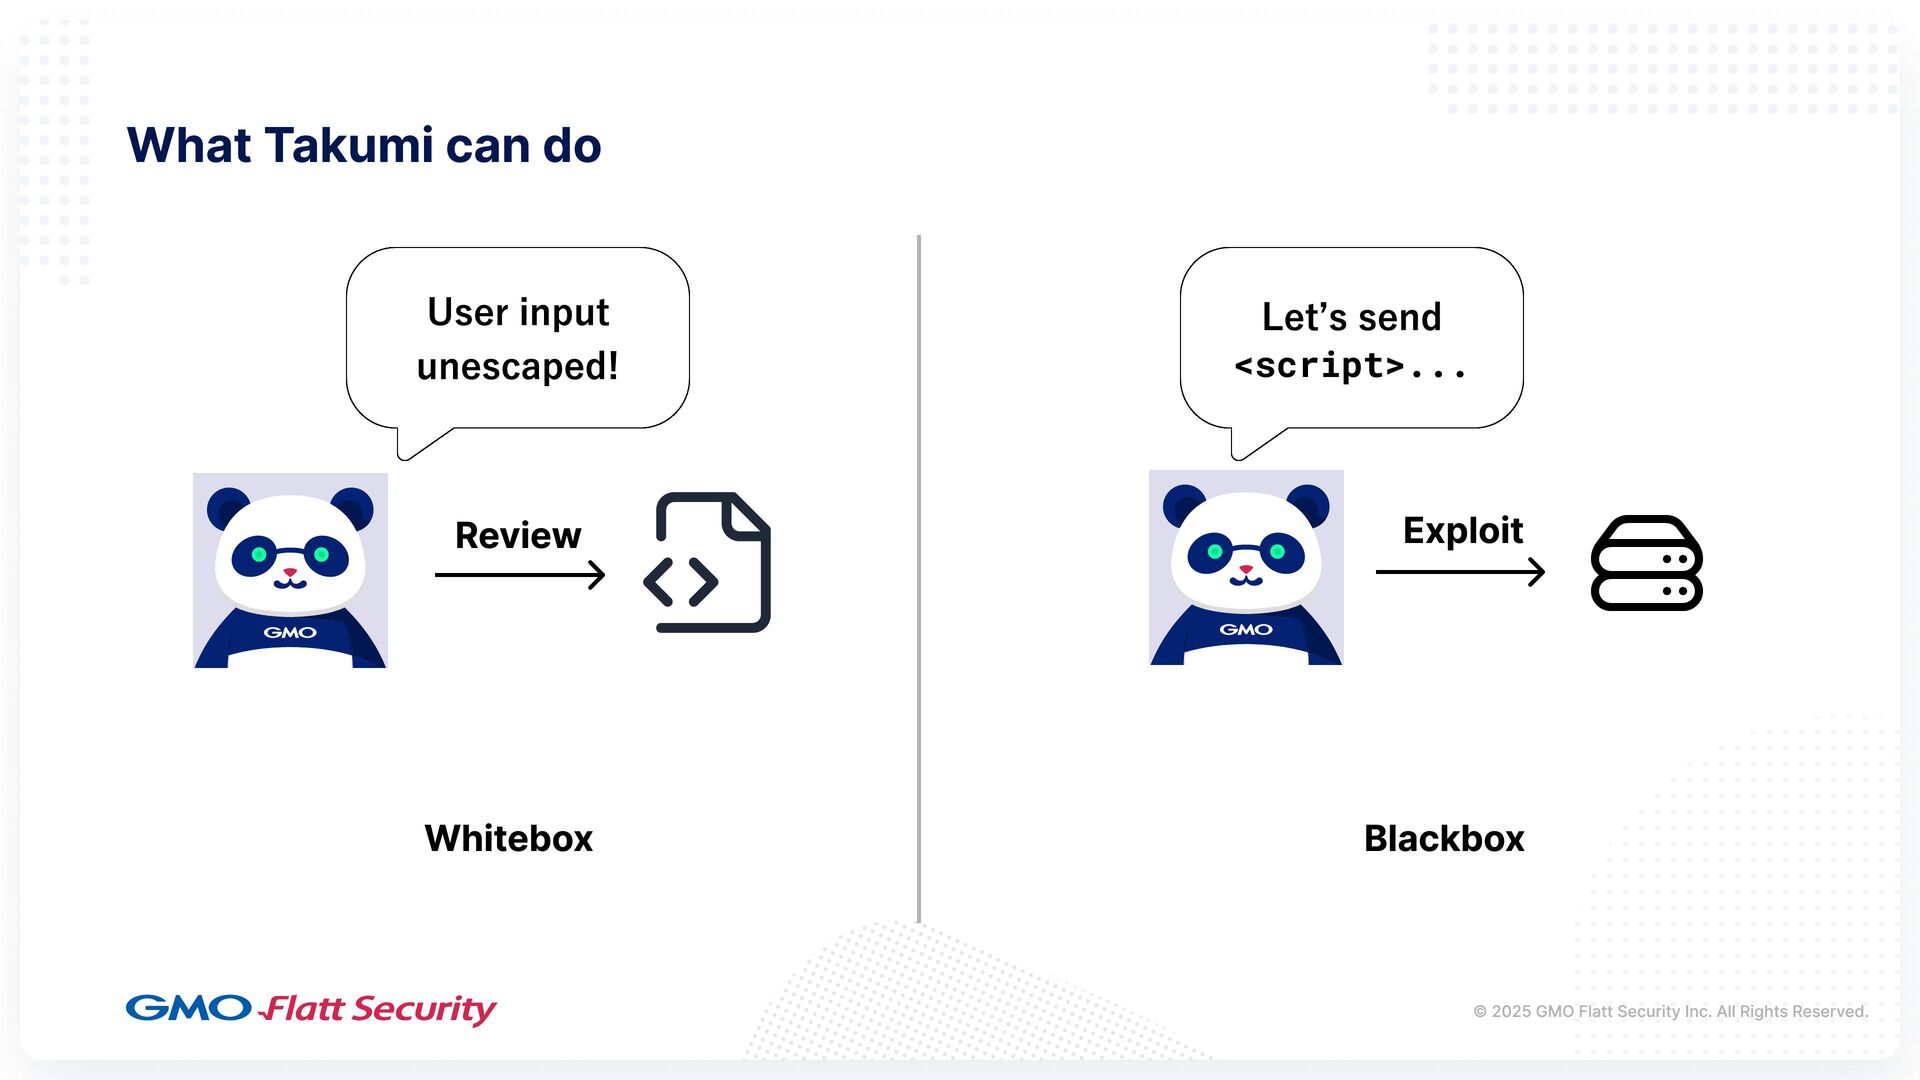
Whitebox Blackbox Review Exploit User input unescaped! Let’s send <script>...
© 2025 GMO Flatt Security Inc. All Rights Reserved. What Takumi can do
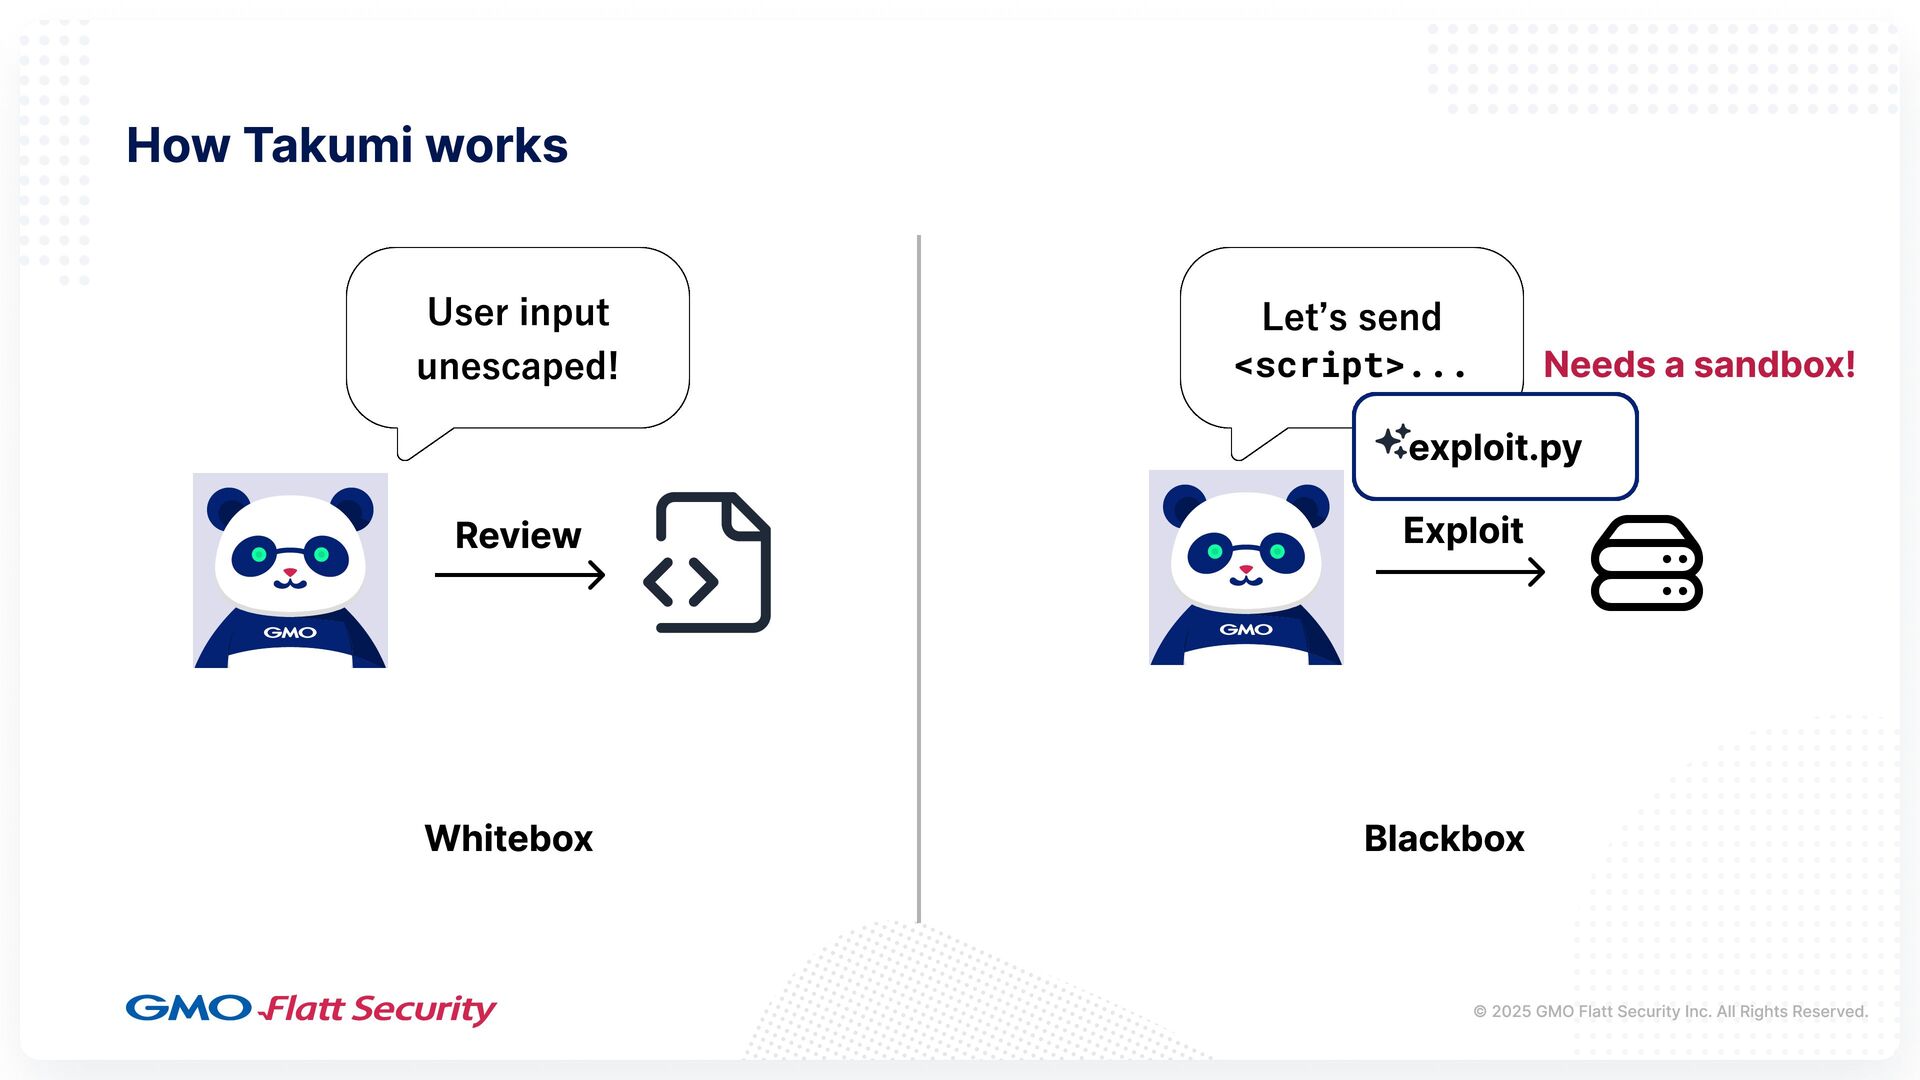
Whitebox Blackbox Review Exploit User input unescaped! Let’s send <script>...
exploit.py Needs a sandbox! © 2025 GMO Flatt Security Inc. All Rights Reserved. How Takumi works
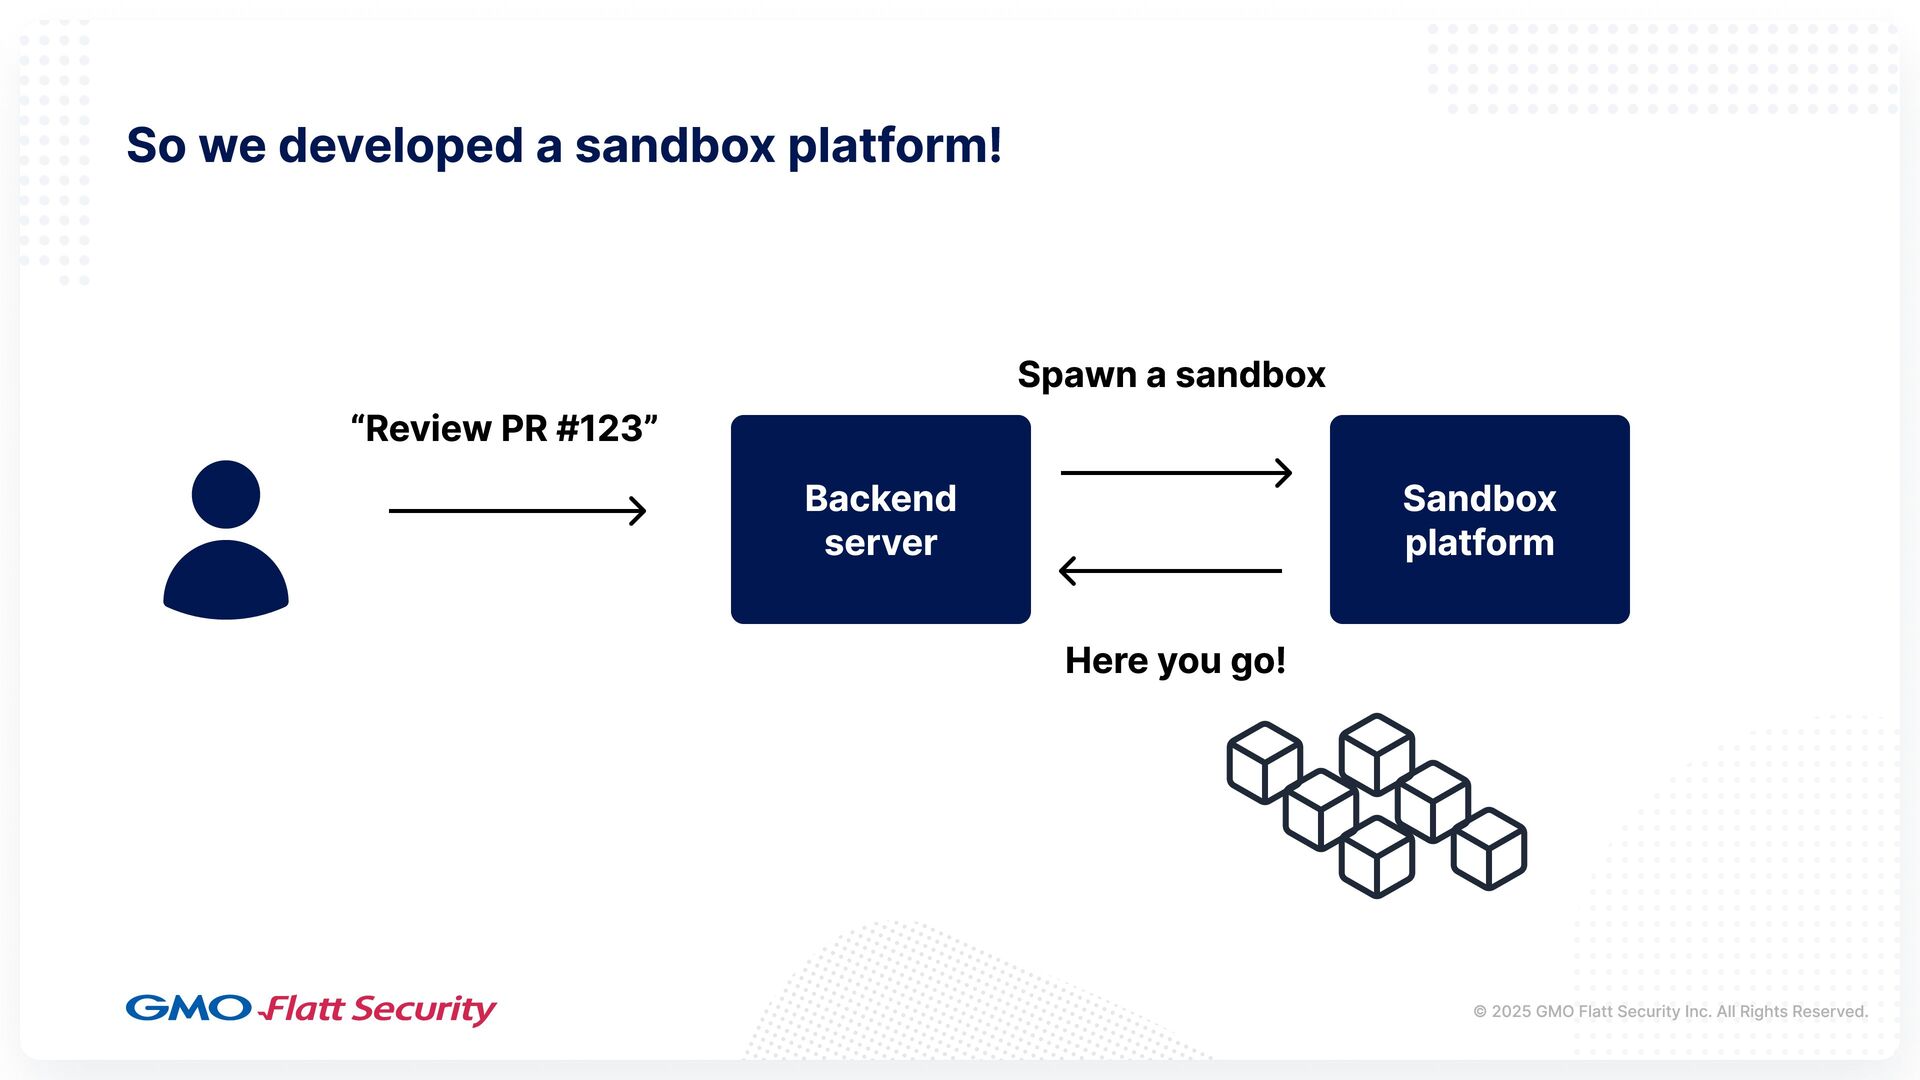
“Review PR #123” Spawn a sandbox Here you go! ©
2025 GMO Flatt Security Inc. All Rights Reserved. So we developed a sandbox platform! Sandbox platform Backend server
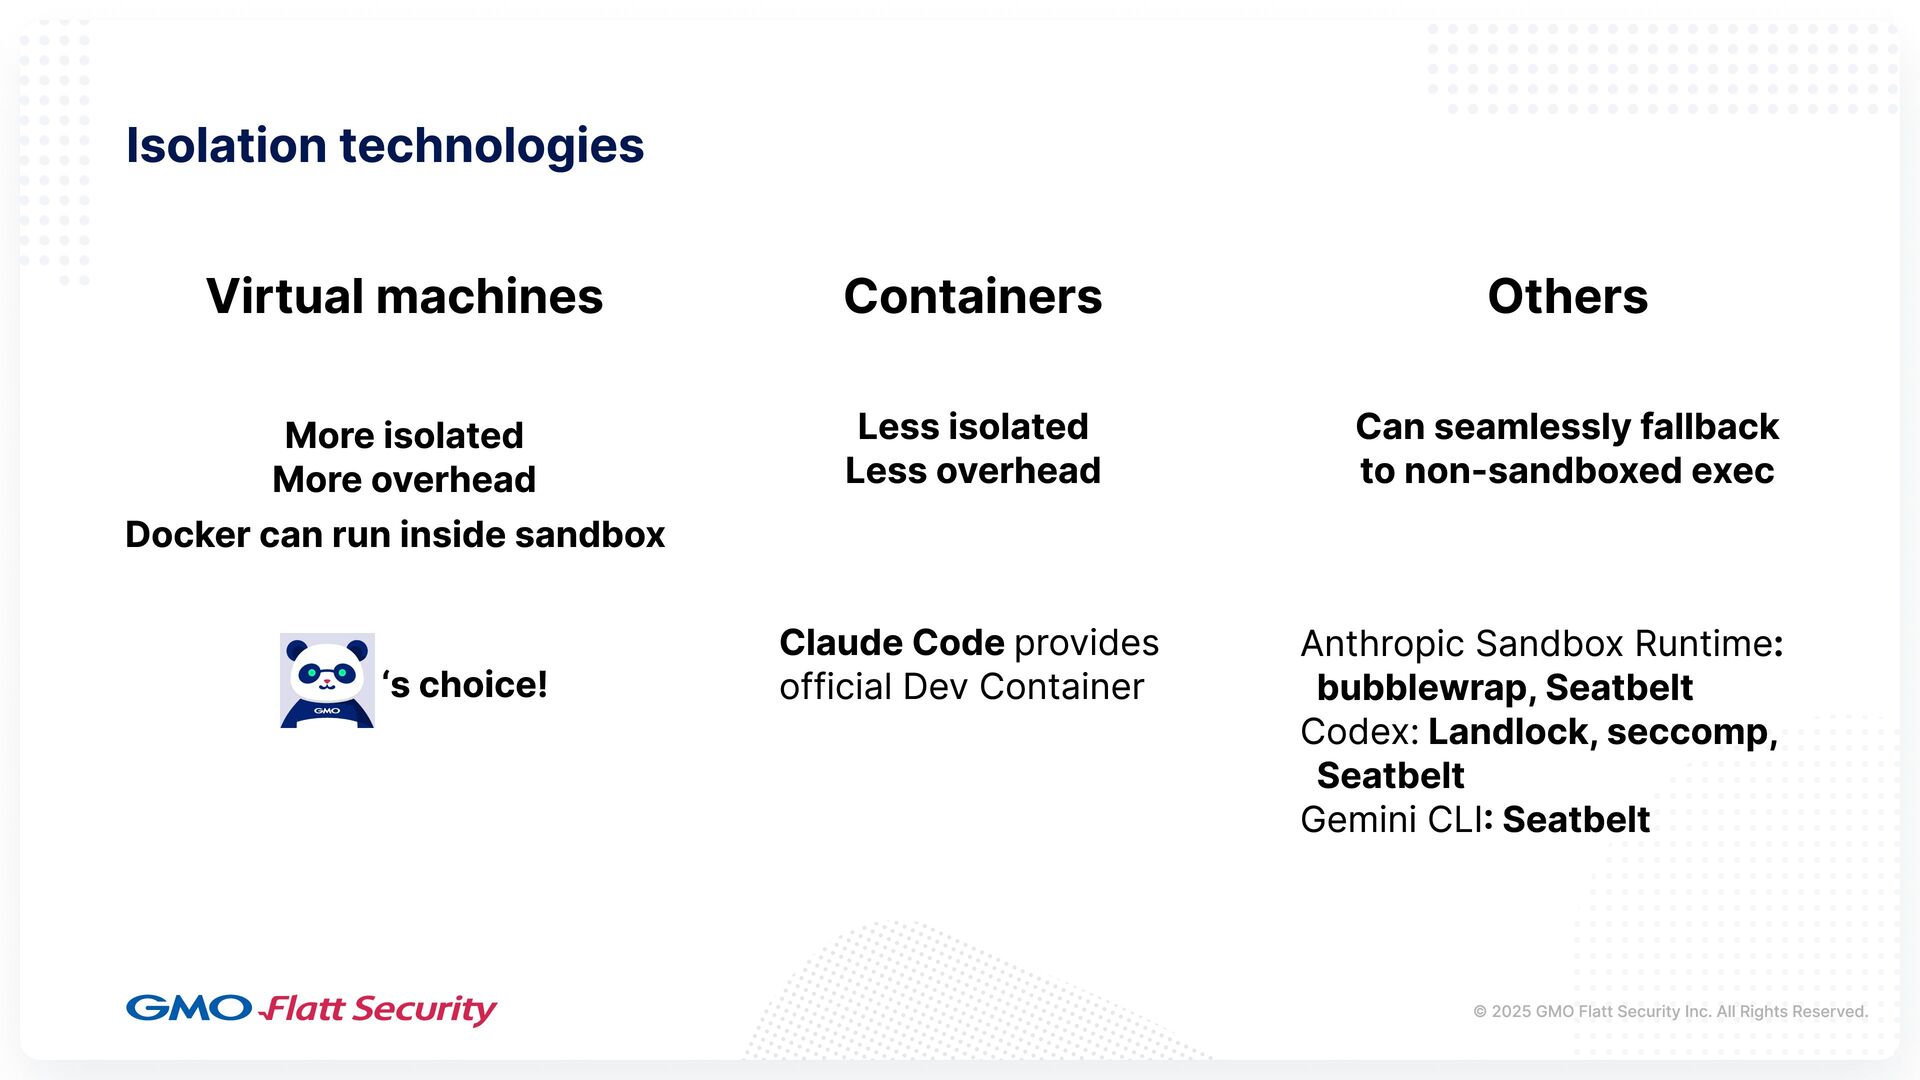
More isolated More overhead Docker can run inside sandbox Less
isolated Less overhead Can seamlessly fallback to non-sandboxed exec ‘s choice! © 2025 GMO Flatt Security Inc. All Rights Reserved. Isolation technologies Anthropic Sandbox Runtime: bubblewrap, Seatbelt Codex: Landlock, seccomp, Seatbelt Gemini CLI: Seatbelt Virtual machines Containers Others Claude Code provides official Dev Container
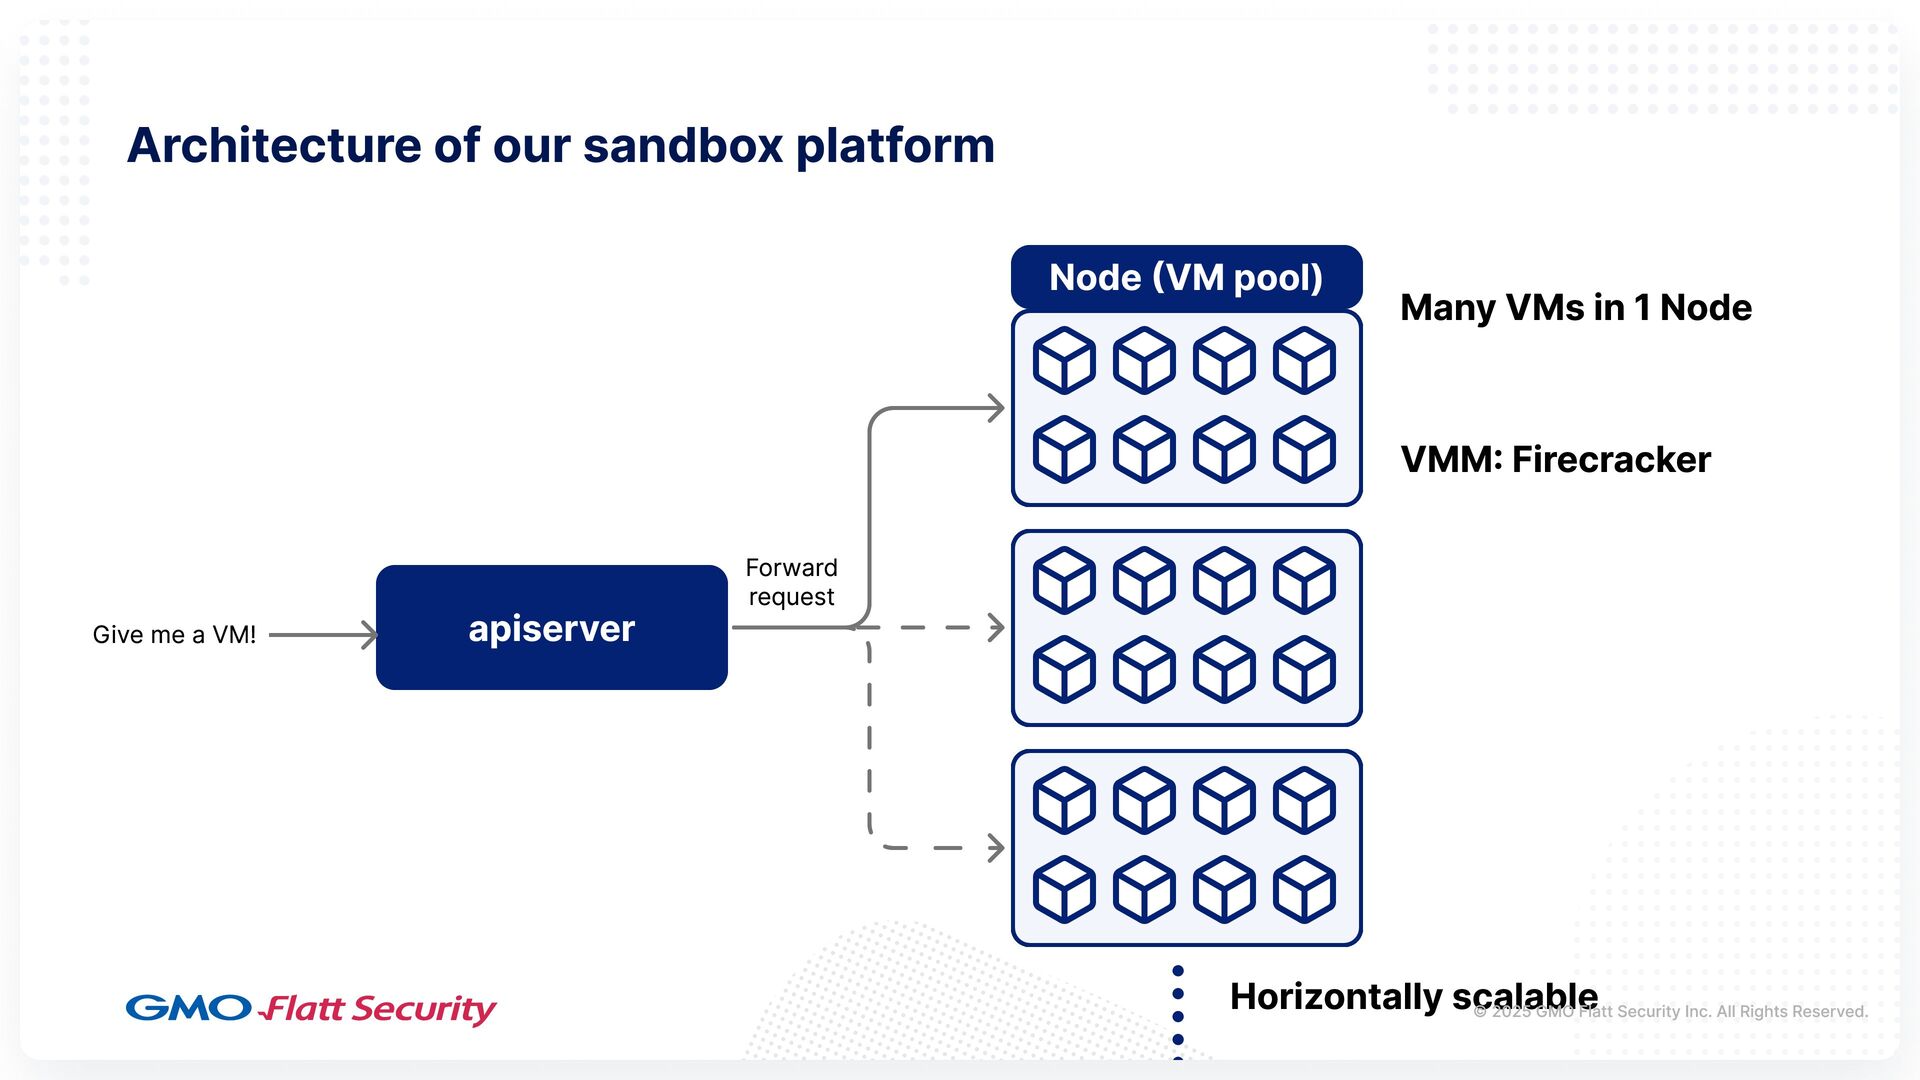
Node (VM pool) apiserver VMM: Firecracker Many VMs in 1
Node Forward request Give me a VM! Horizontally scalable …… © 2025 GMO Flatt Security Inc. All Rights Reserved. Architecture of our sandbox platform
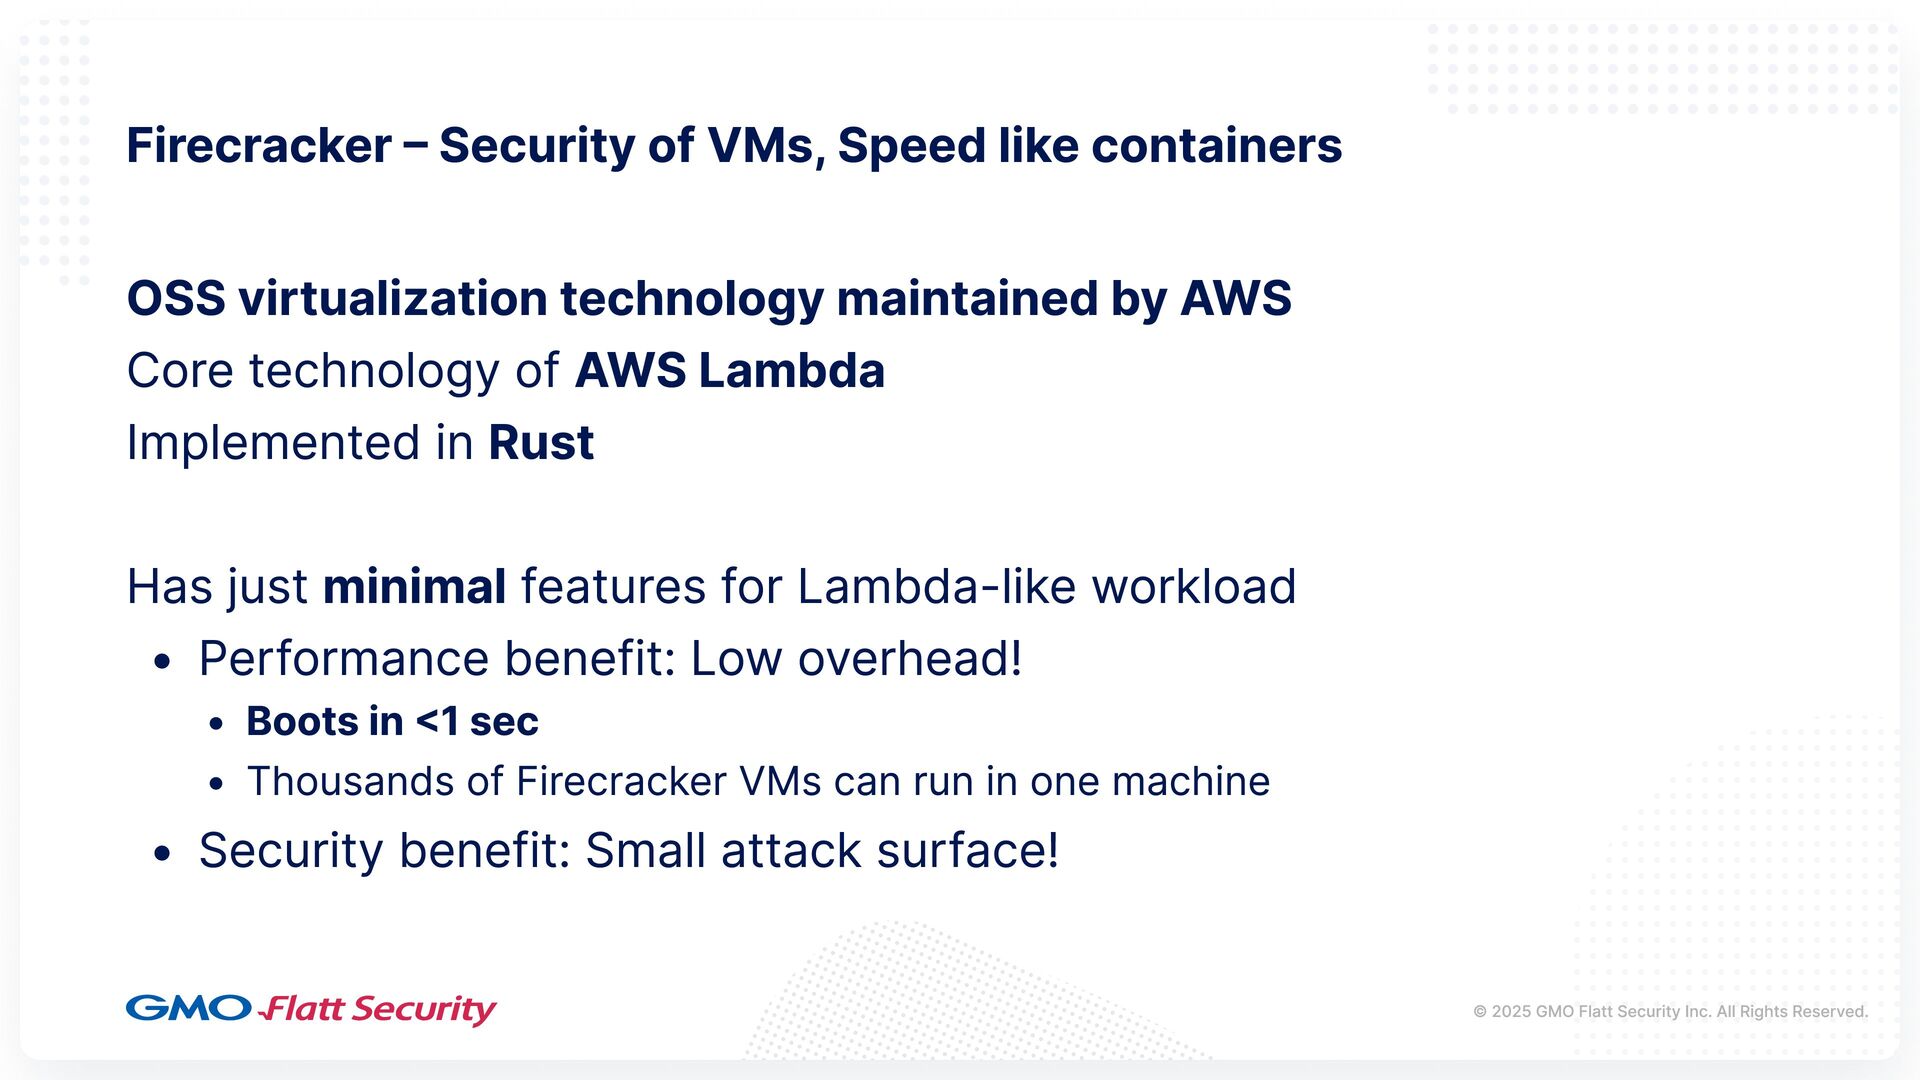
OSS virtualization technology maintained by AWS Core technology of AWS
Lambda Implemented in Rust Has just minimal features for Lambda-like workload Performance benefit: Low overhead! Boots in <1 sec Thousands of Firecracker VMs can run in one machine Security benefit: Small attack surface! © 2025 GMO Flatt Security Inc. All Rights Reserved. Firecracker – Security of VMs, Speed like containers
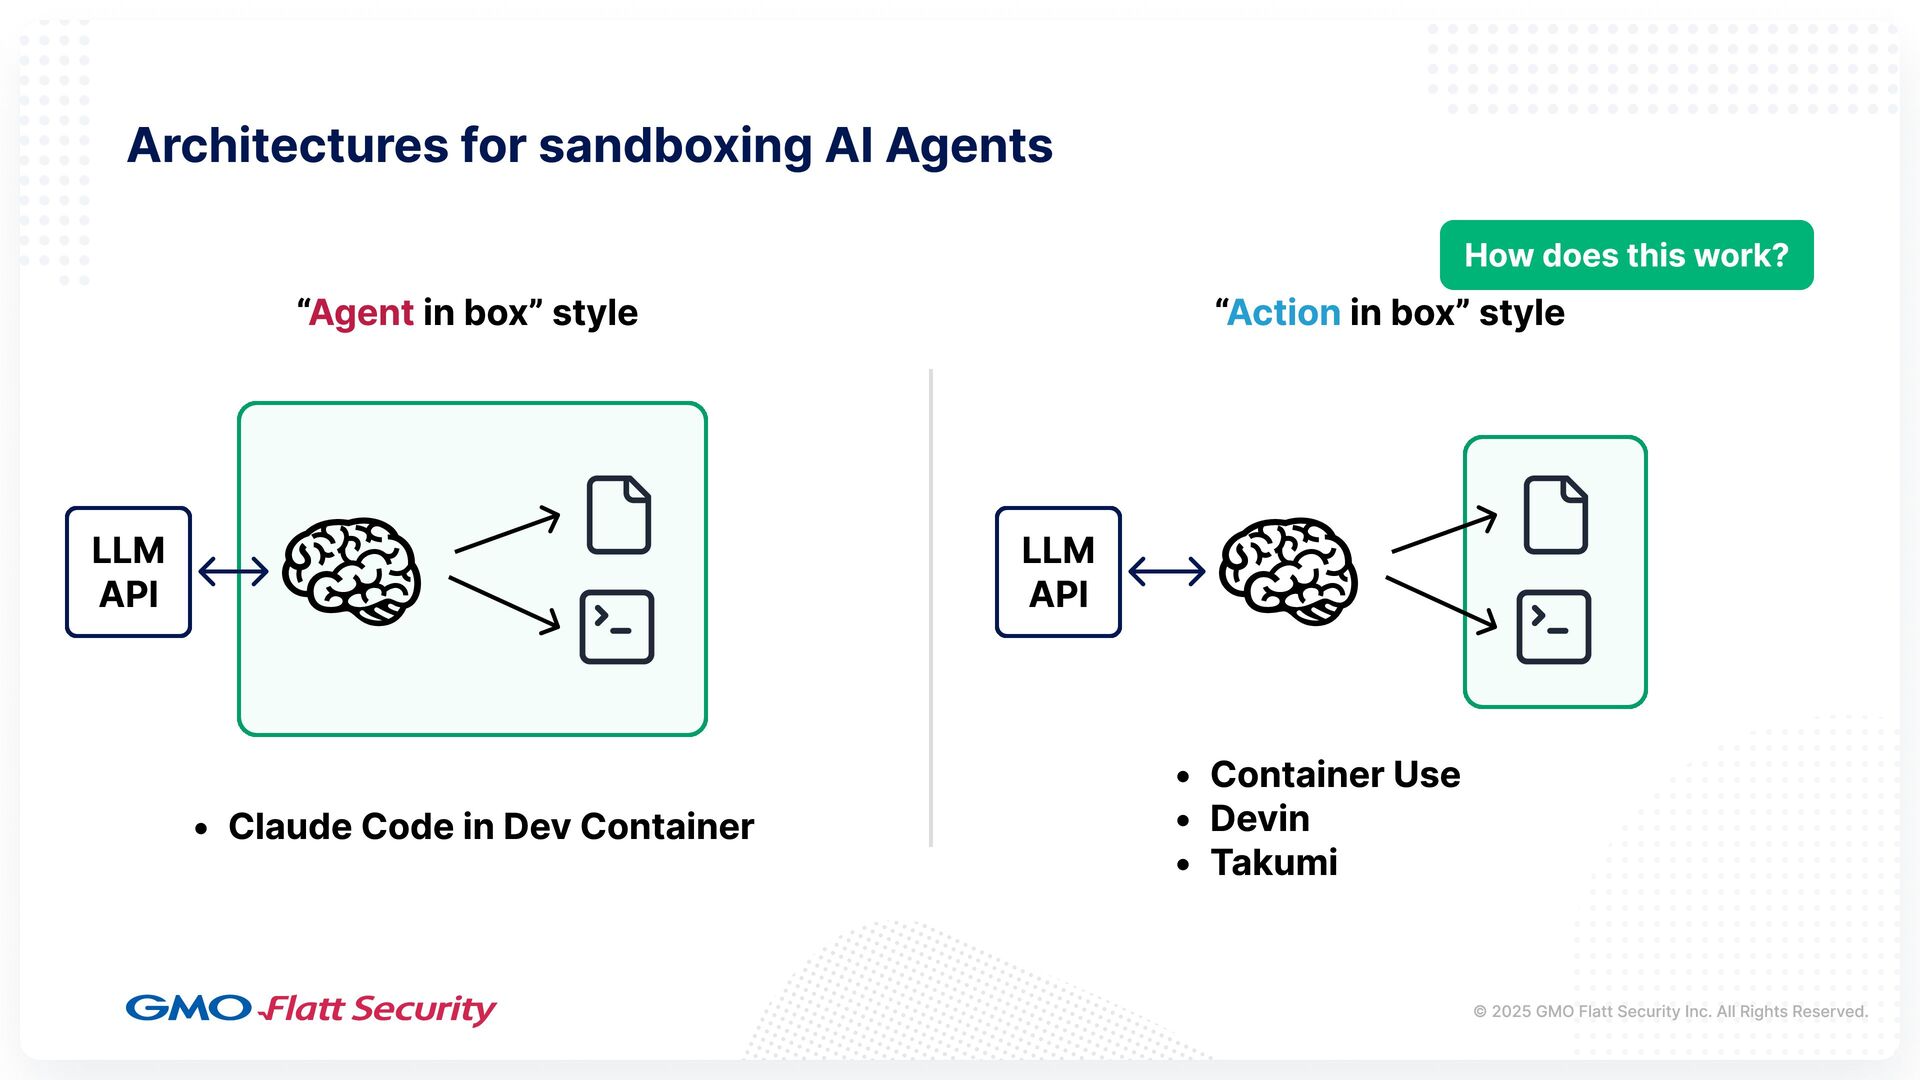
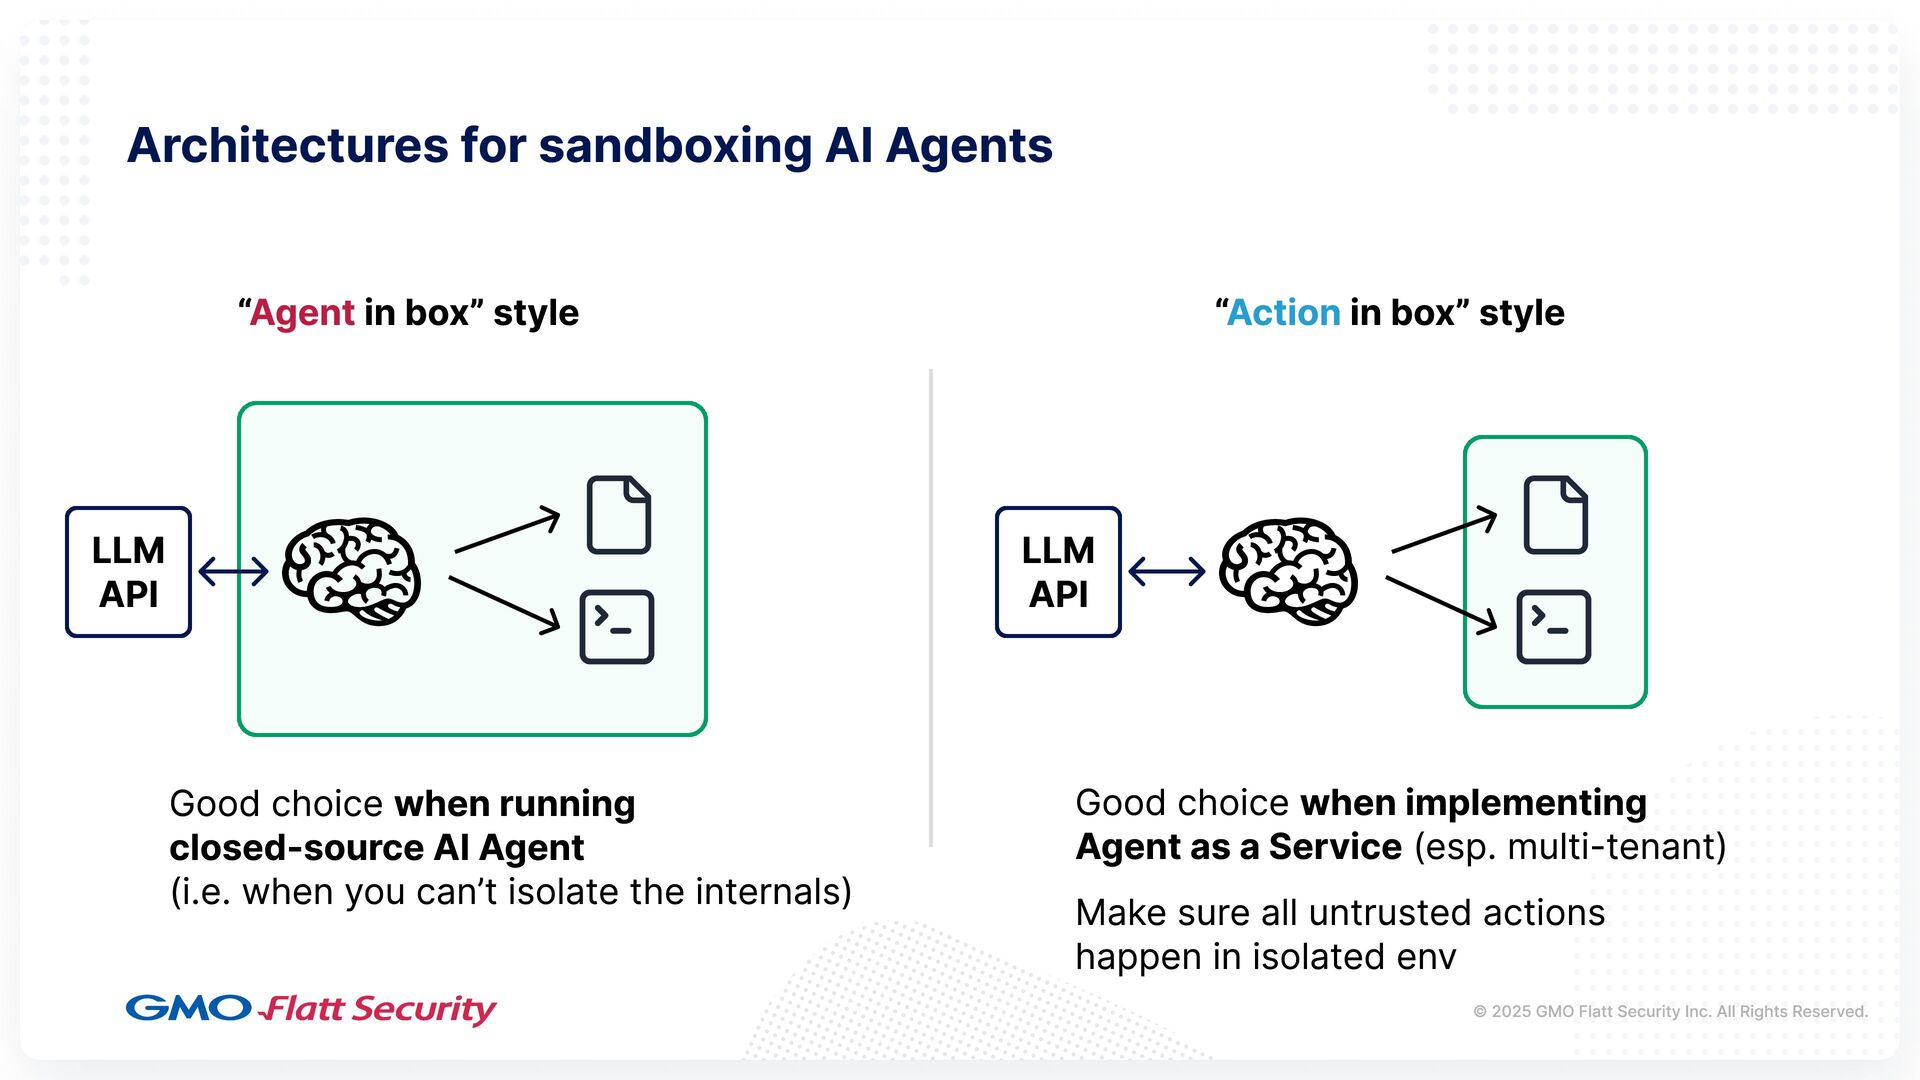
“ in box” style Agent “ in box” style Action
🧠 🧠 Container Use Devin Takumi Claude Code in Dev Container © 2025 GMO Flatt Security Inc. All Rights Reserved. Architectures for sandboxing AI Agents LLM API LLM API How does this work?
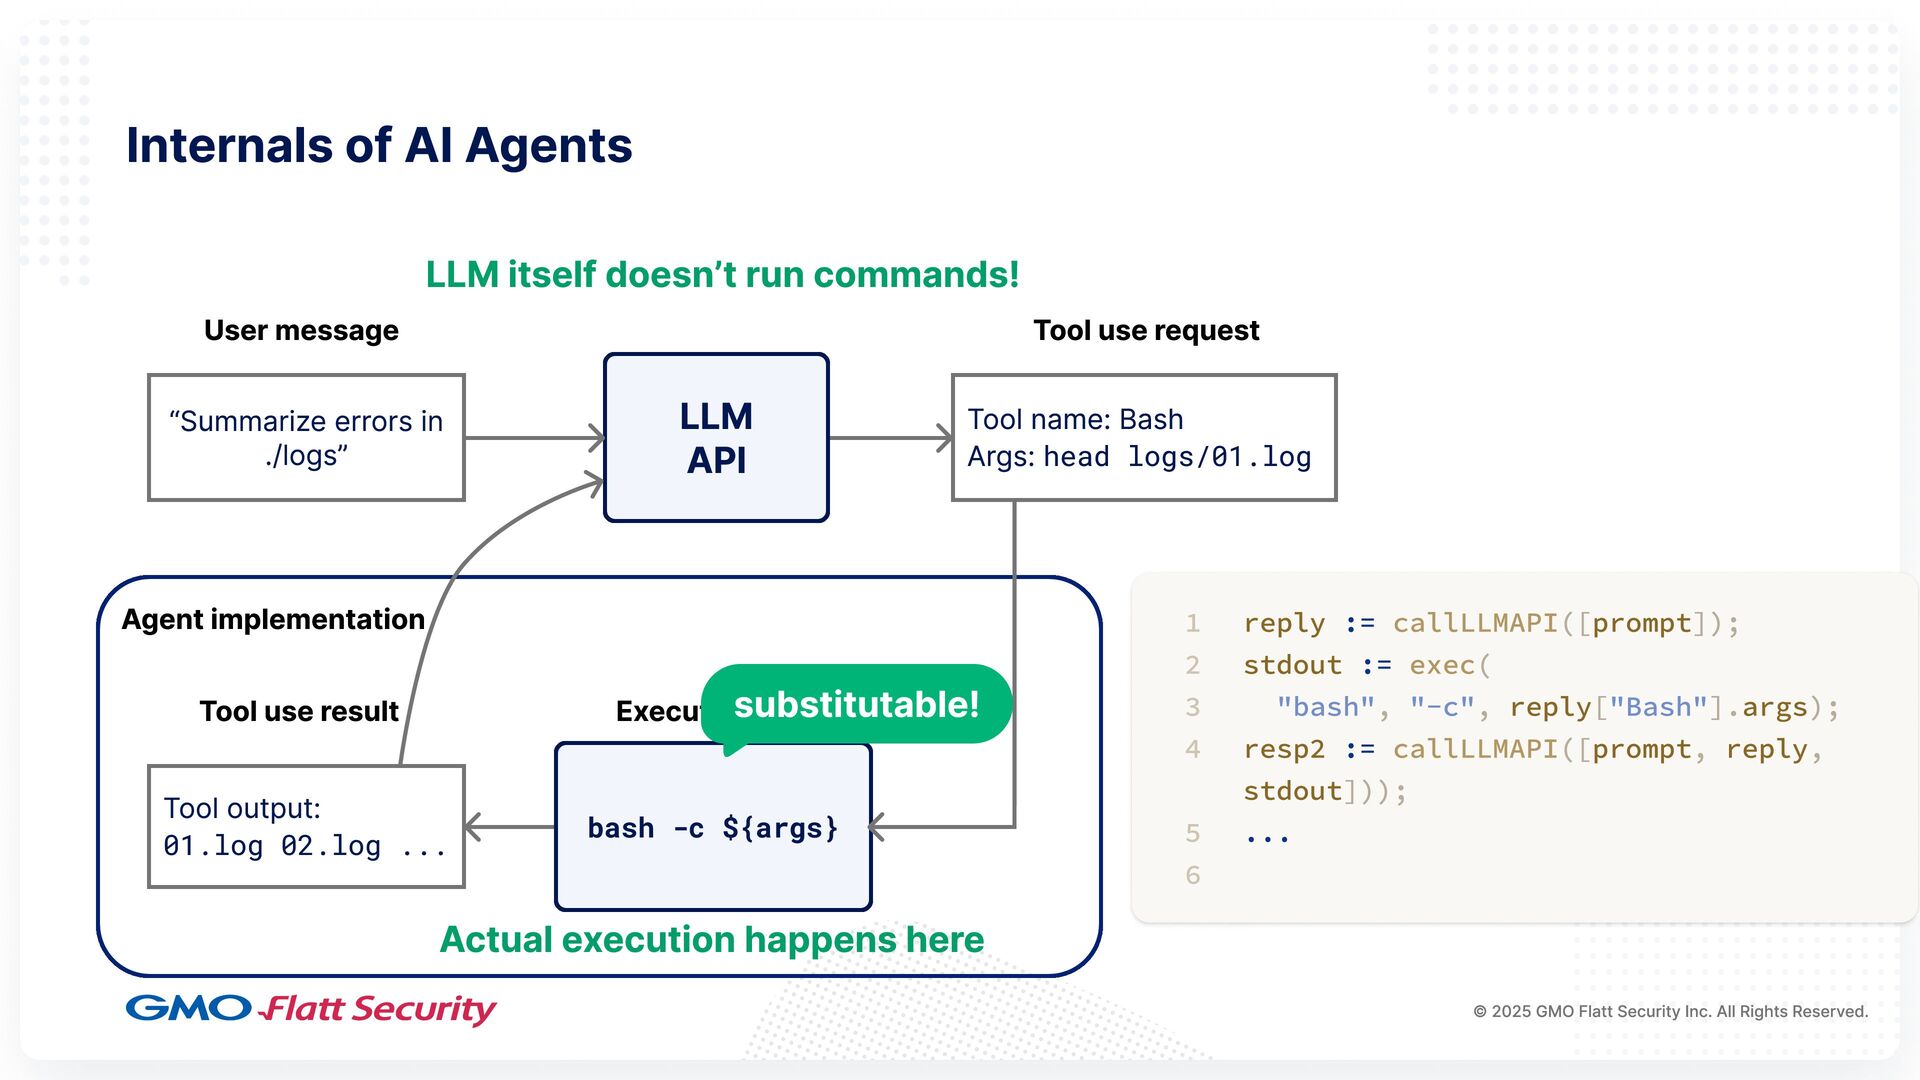
User message Tool use request Execute tool Tool use result
Agent implementation © 2025 GMO Flatt Security Inc. All Rights Reserved. Internals of AI Agents LLM API “Summarize errors in ./logs” Tool name: Bash Args: ls ./logs Tool name: Bash Args: head logs/01.log bash -c ${args} Tool output: 01.log 02.log ... LLM itself doesn’t run commands! Actual execution happens here 1 2 3 4 5 6 reply prompt stdout reply args resp2 prompt reply stdout := := := ... callLLMAPI exec callLLMAPI ([ ]); ( , , [ ]. ); ([ , , ])); "bash" "-c" "Bash" substitutable!
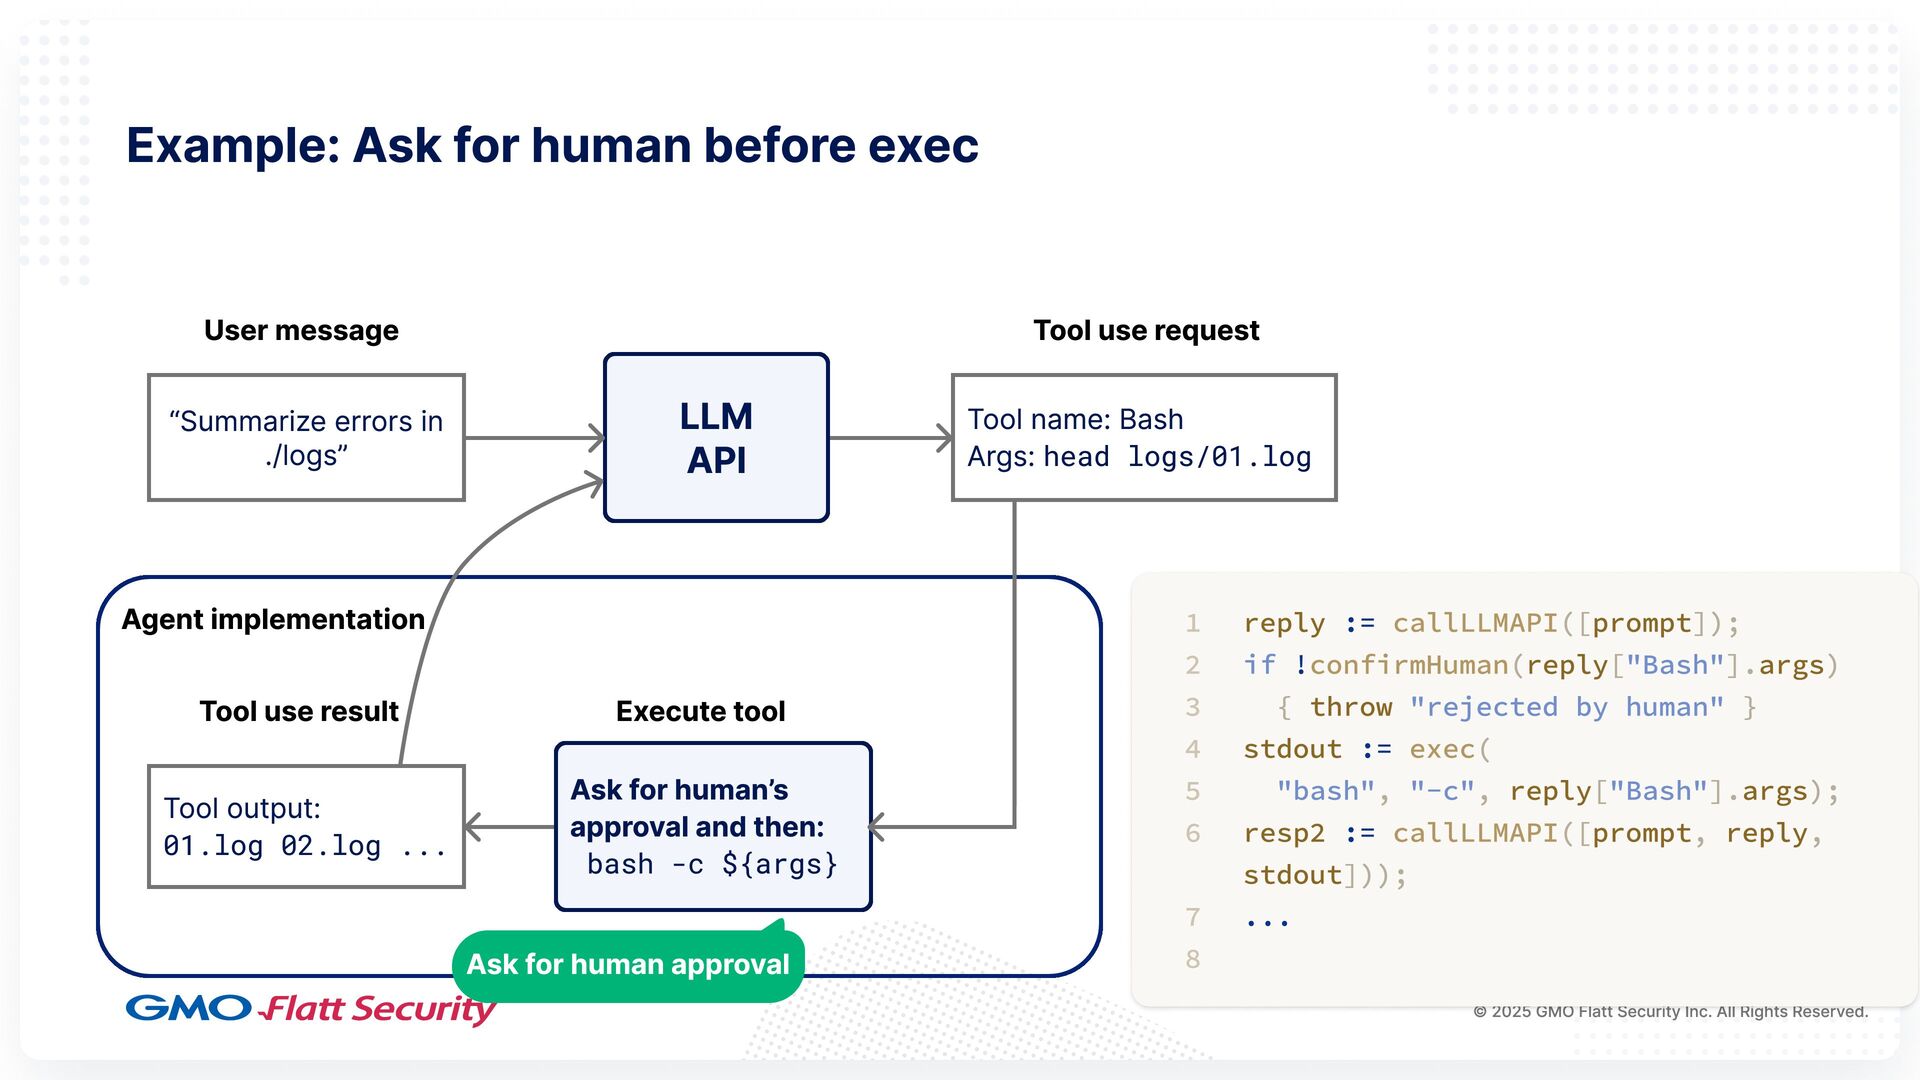
User message Tool use request Execute tool Tool use result
Agent implementation © 2025 GMO Flatt Security Inc. All Rights Reserved. Example: Ask for human before exec LLM API “Summarize errors in ./logs” Tool name: Bash Args: head logs/01.log Ask for human’s approval and then: bash -c ${args} Tool output: 01.log 02.log ... 1 2 3 4 5 6 7 8 reply prompt reply args throw stdout reply args resp2 prompt reply stdout := ! := := ... callLLMAPI confirmHuman exec callLLMAPI ([ ]); ( [ ]. ) { } ( , , [ ]. ); ([ , , ])); if "Bash" "rejected by human" "bash" "-c" "Bash" Ask for human approval
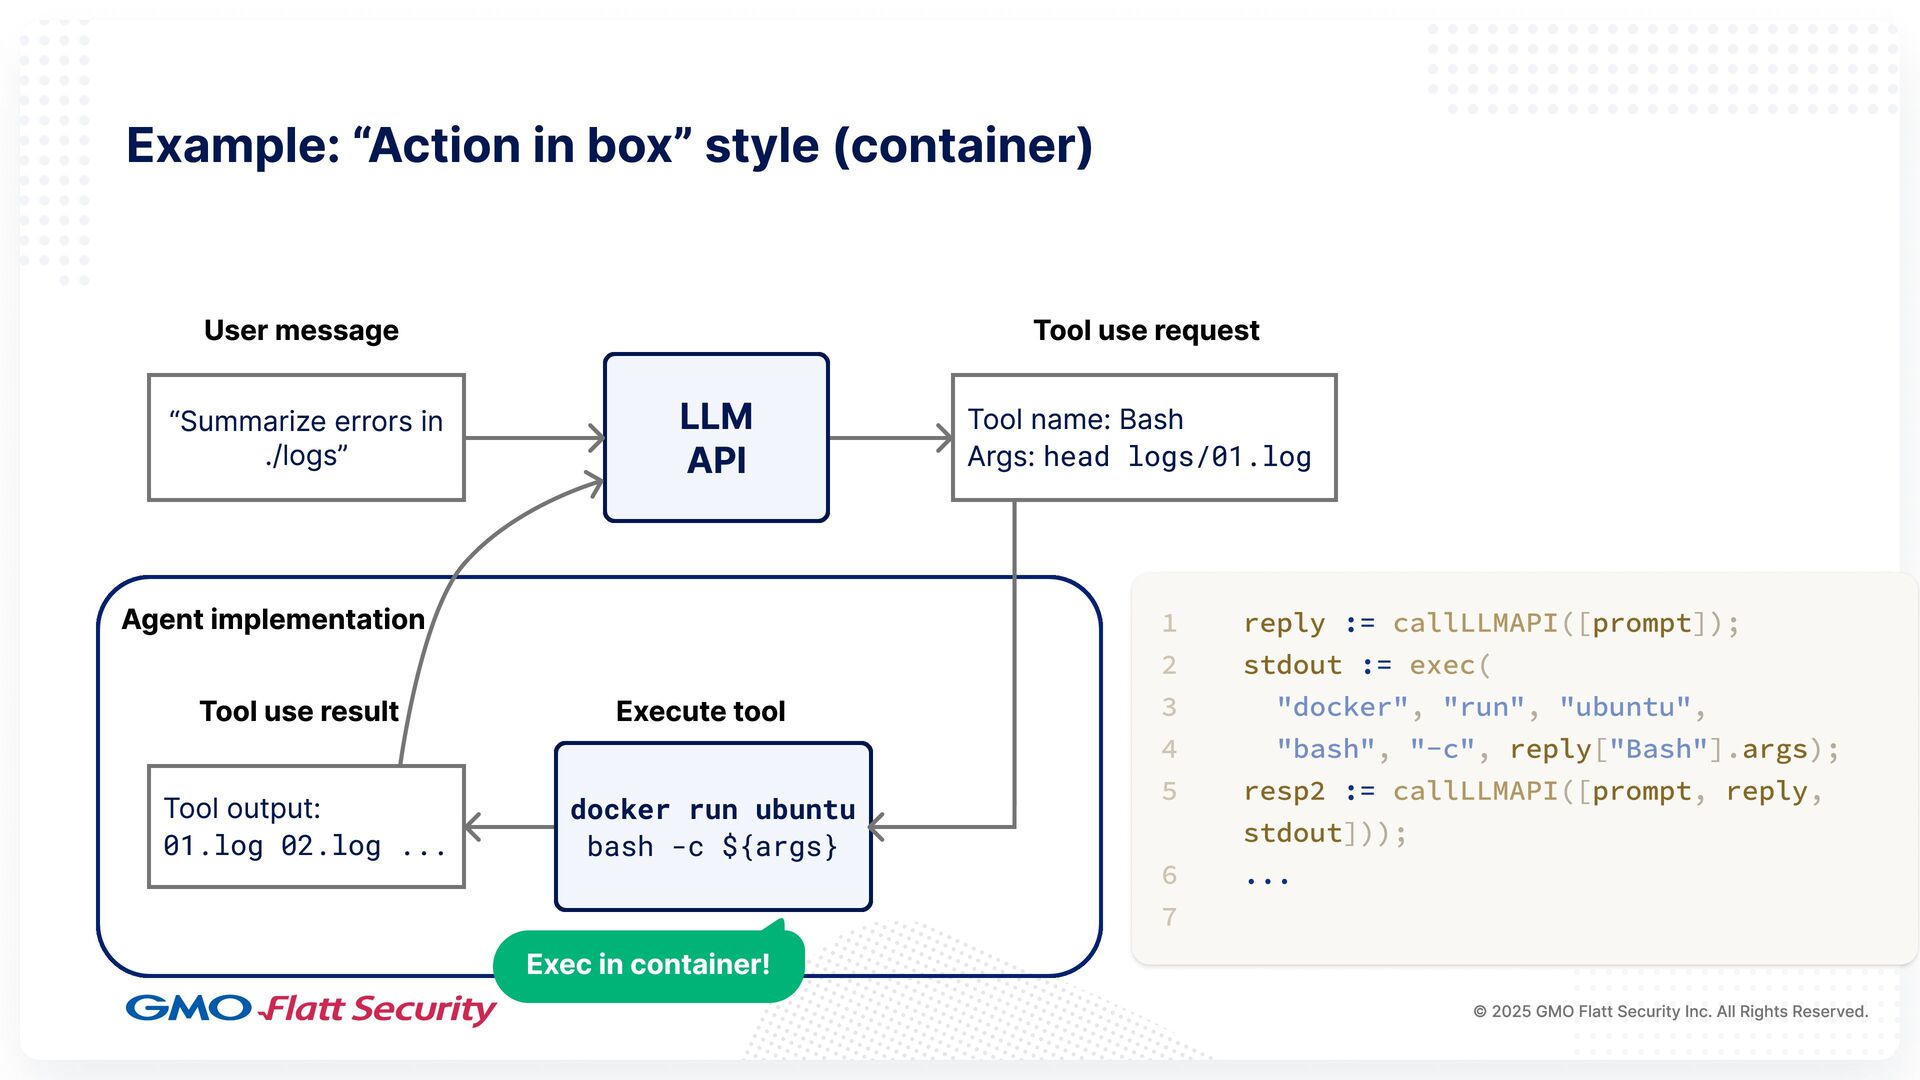
User message Tool use request Execute tool Tool use result
Agent implementation © 2025 GMO Flatt Security Inc. All Rights Reserved. Example: “Action in box” style (container) LLM API “Summarize errors in ./logs” Tool name: Bash Args: head logs/01.log docker run ubuntu bash -c ${args} Tool output: 01.log 02.log ... 1 2 3 4 5 6 7 reply prompt stdout reply args resp2 prompt reply stdout := := := ... callLLMAPI exec callLLMAPI ([ ]); ( , , , , , [ ]. ); ([ , , ])); "docker" "run" "ubuntu" "bash" "-c" "Bash" Exec in container!
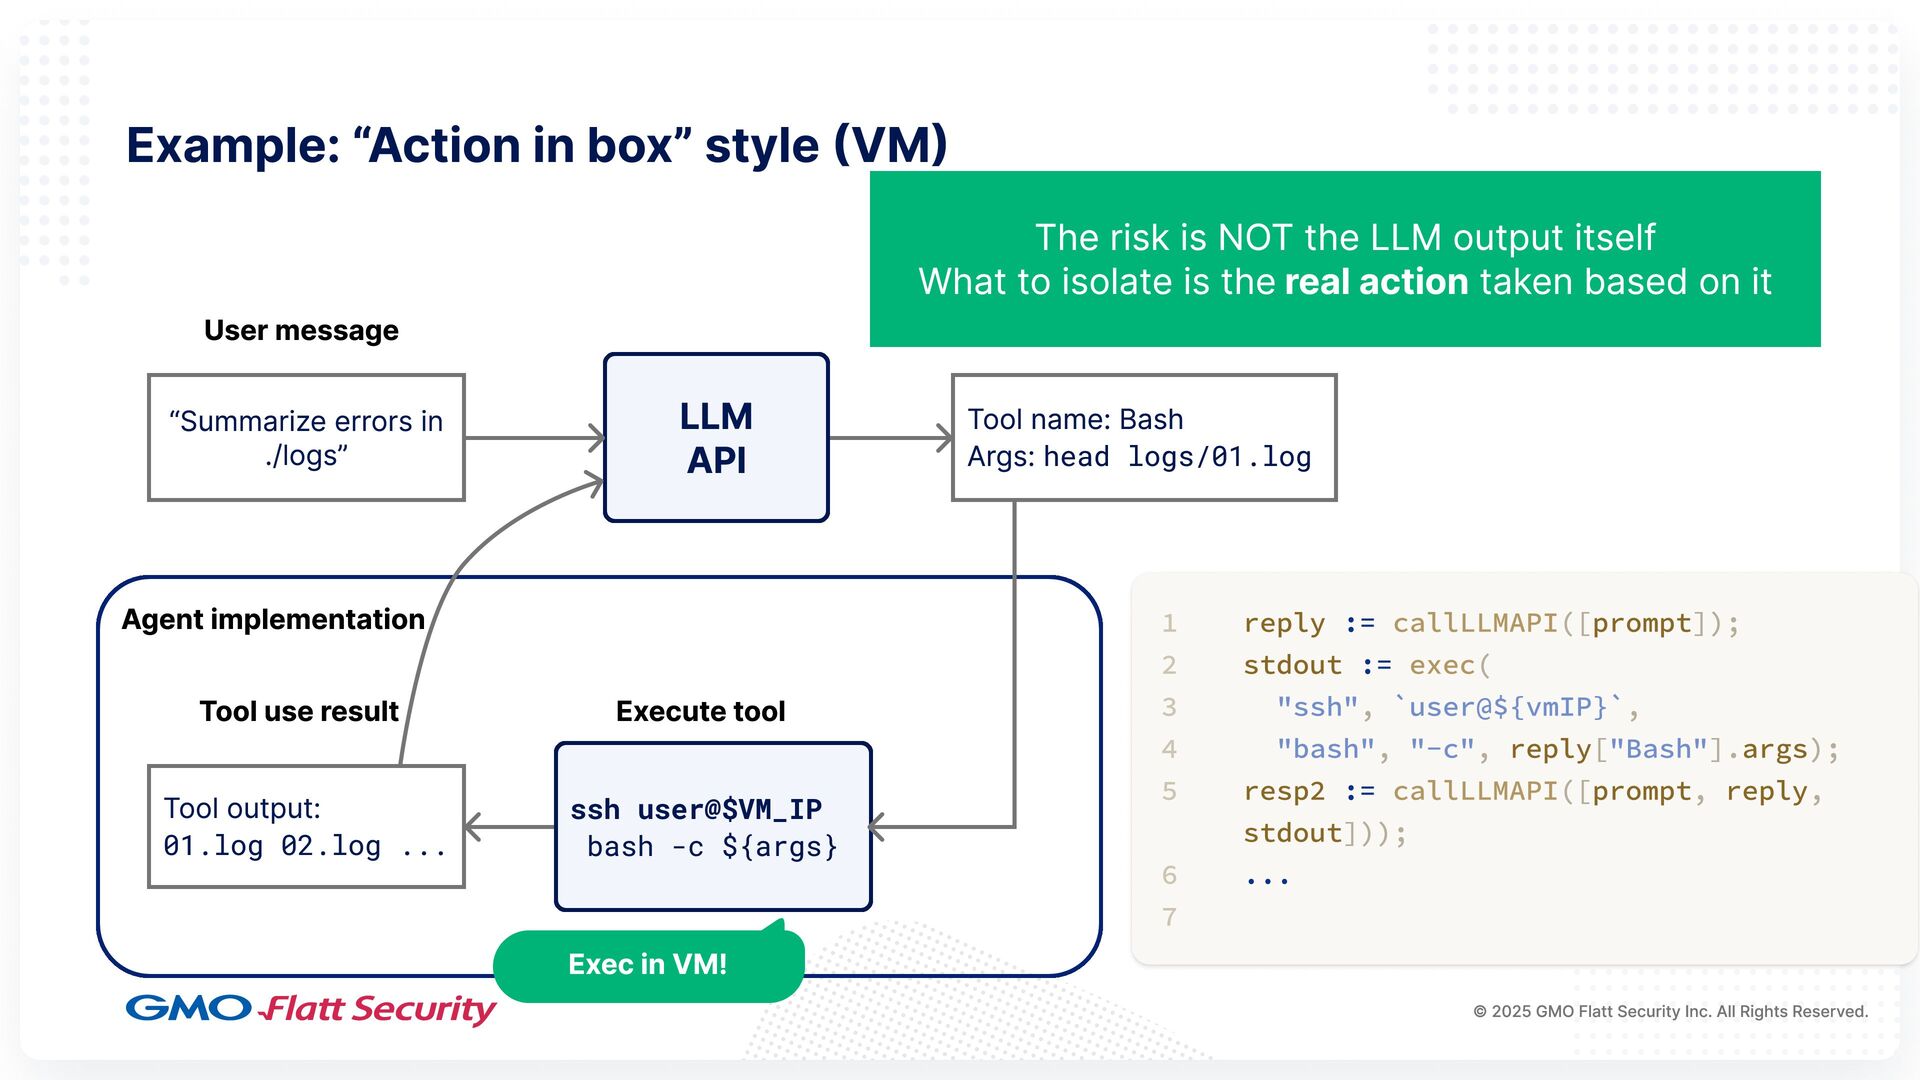
User message Tool use request Execute tool Tool use result
Agent implementation The risk is NOT the LLM output itself What to isolate is the real action taken based on it © 2025 GMO Flatt Security Inc. All Rights Reserved. Example: “Action in box” style (VM) LLM API “Summarize errors in ./logs” Tool name: Bash Args: head logs/01.log ssh user@$VM_IP bash -c ${args} Tool output: 01.log 02.log ... 1 2 3 4 5 6 7 reply prompt stdout reply args resp2 prompt reply stdout := := := ... callLLMAPI exec callLLMAPI ([ ]); ( , , , , [ ]. ); ([ , , ])); "ssh" `user@${vmIP}` "bash" "-c" "Bash" Exec in VM!
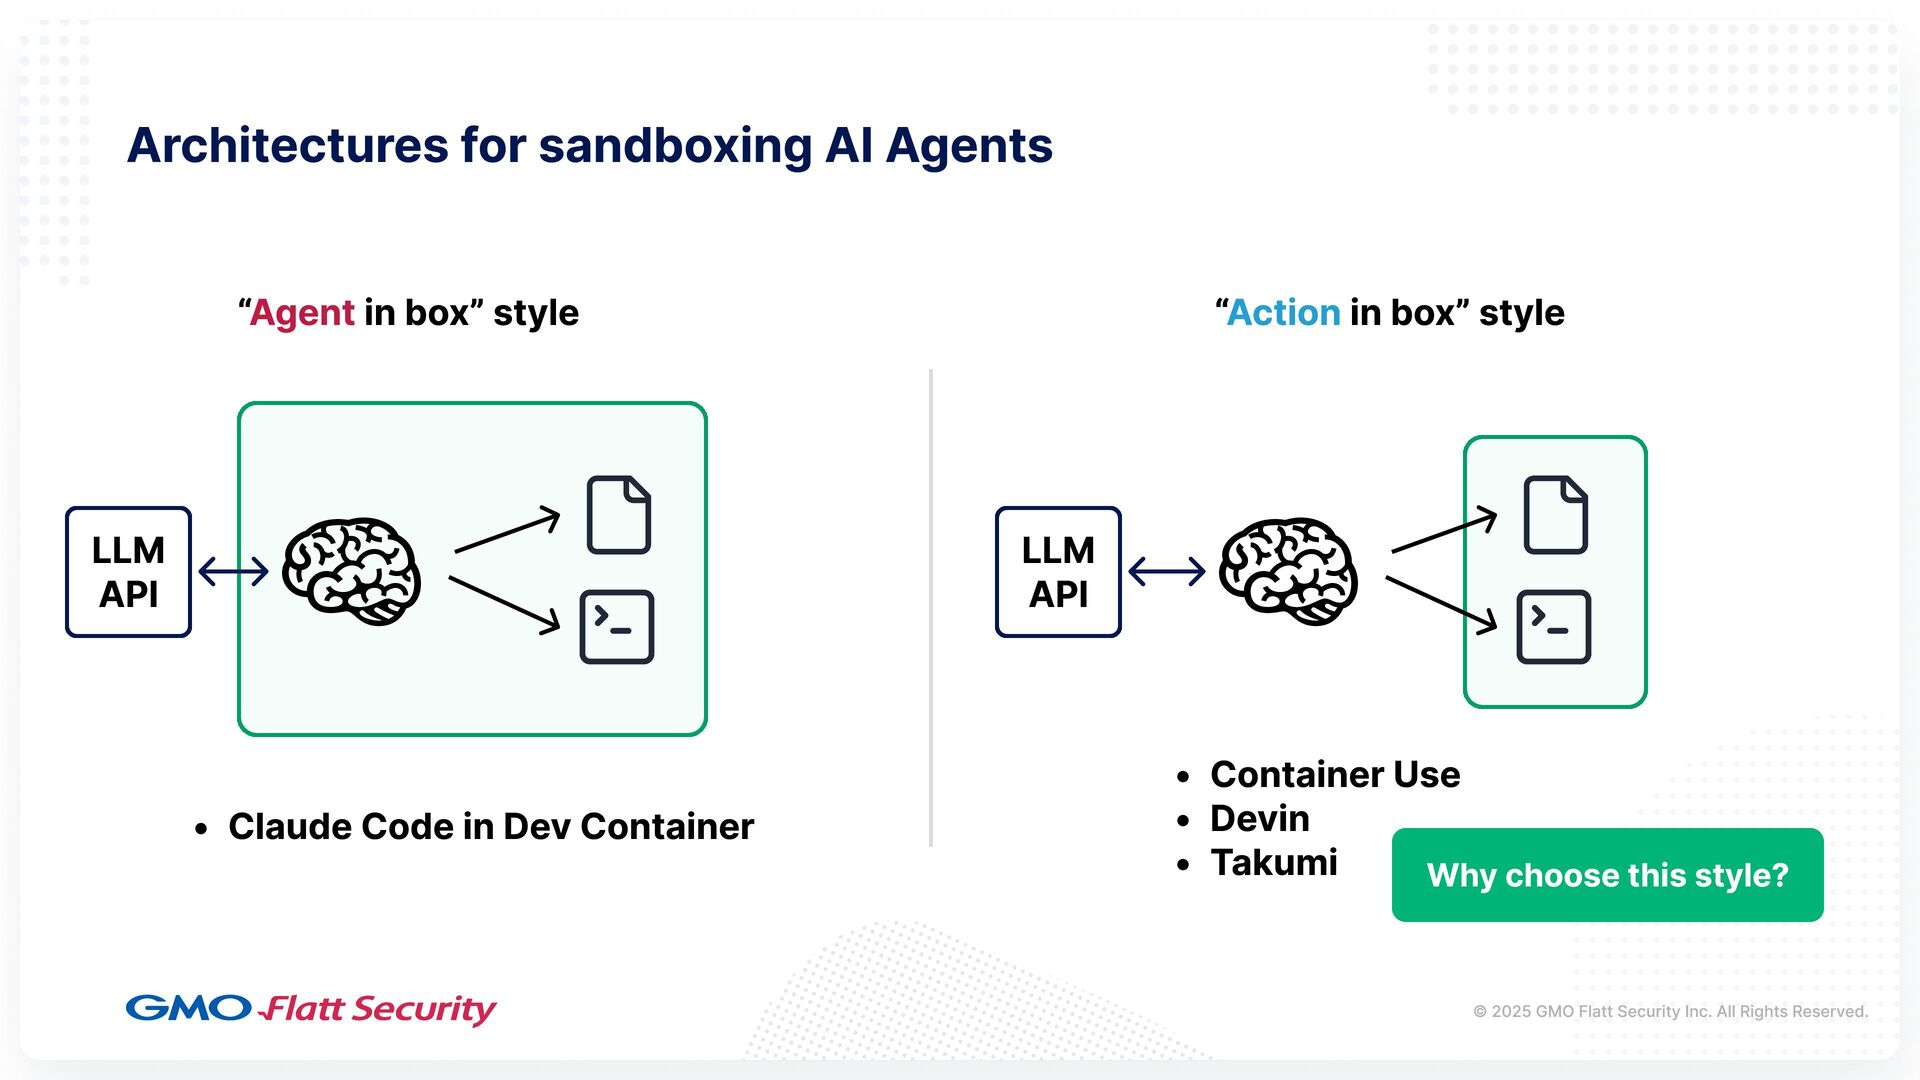
“ in box” style Agent “ in box” style Action
🧠 🧠 Container Use Devin Takumi Claude Code in Dev Container © 2025 GMO Flatt Security Inc. All Rights Reserved. Architectures for sandboxing AI Agents LLM API LLM API Why choose this style?
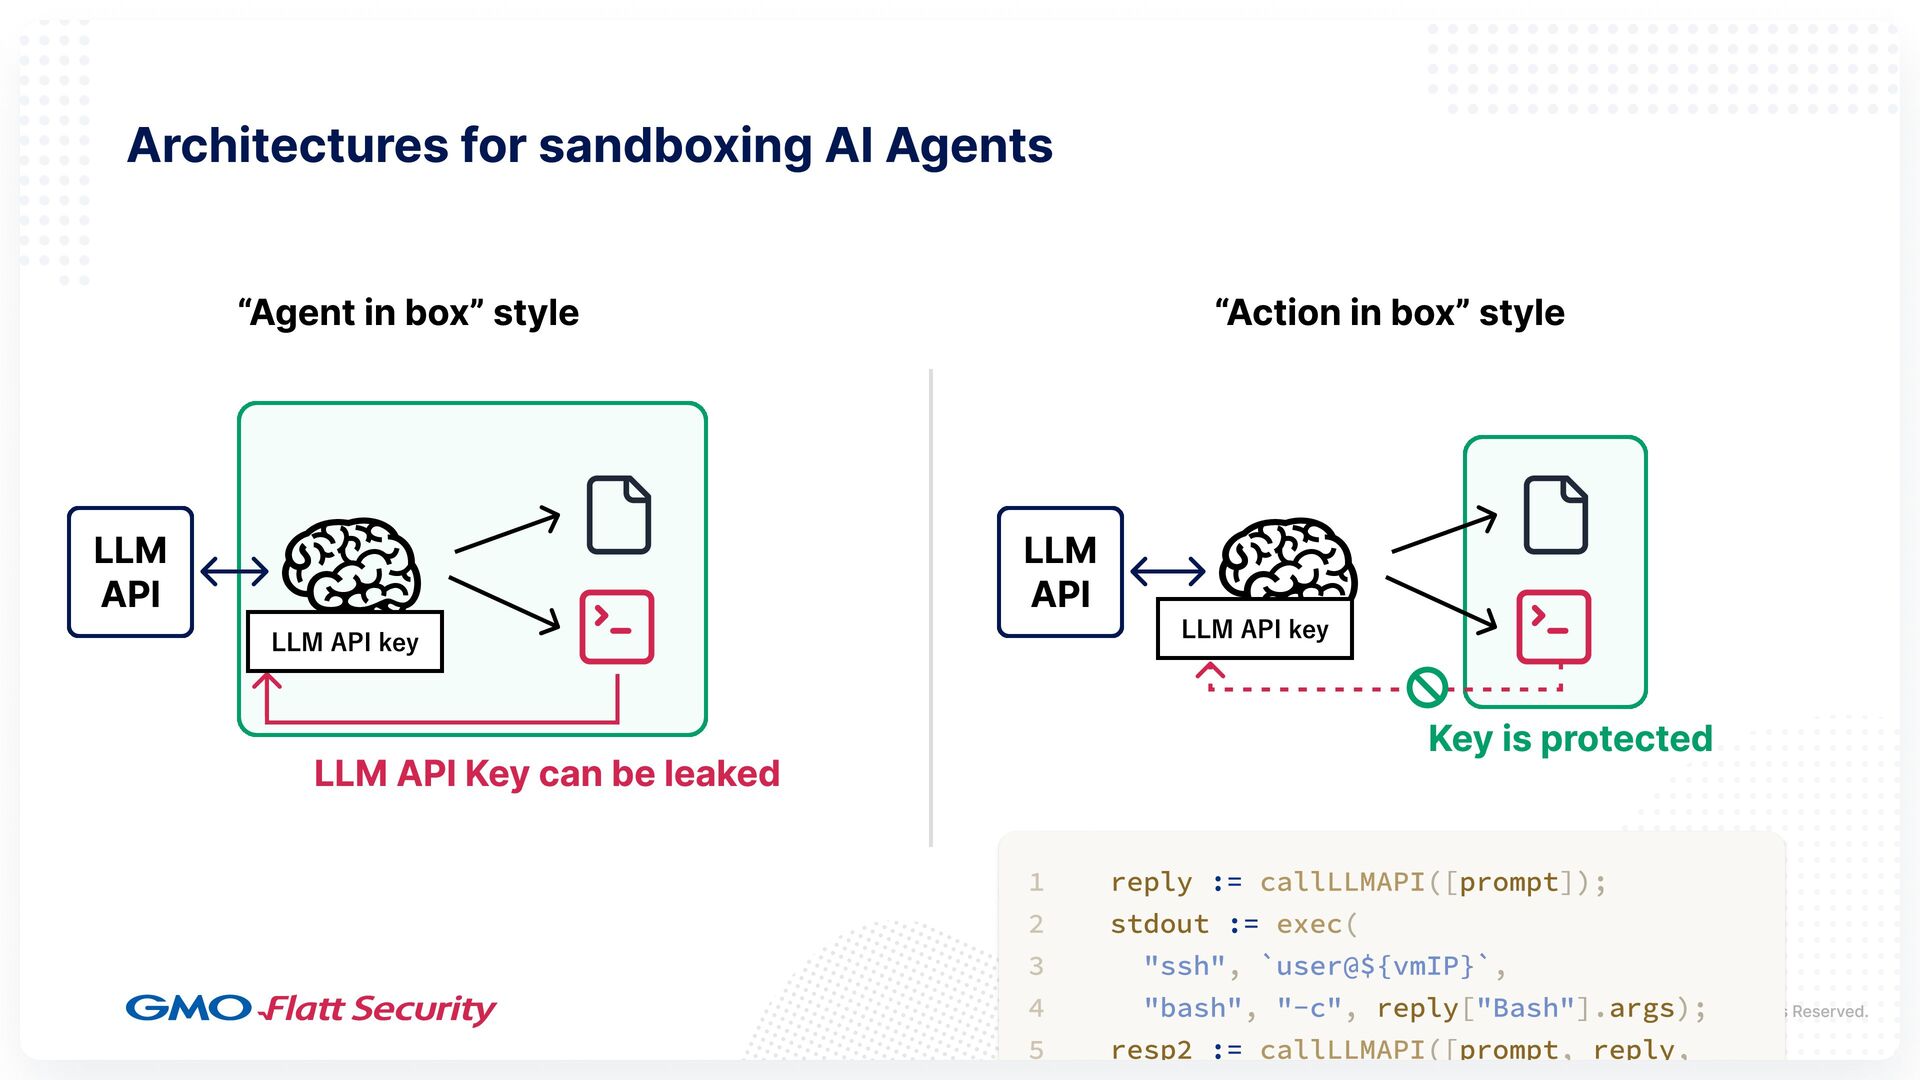
“Agent in box” style “Action in box” style 🧠 🧠
LLM API Key can be leaked Key is protected © 2025 GMO Flatt Security Inc. All Rights Reserved. Architectures for sandboxing AI Agents 1 2 3 4 5 reply prompt stdout reply args resp2 prompt reply := := := callLLMAPI exec callLLMAPI ([ ]); ( , , , , [ ]. ); ([ , , "ssh" `user@${vmIP}` "bash" "-c" "Bash" LLM API key LLM API key LLM API LLM API
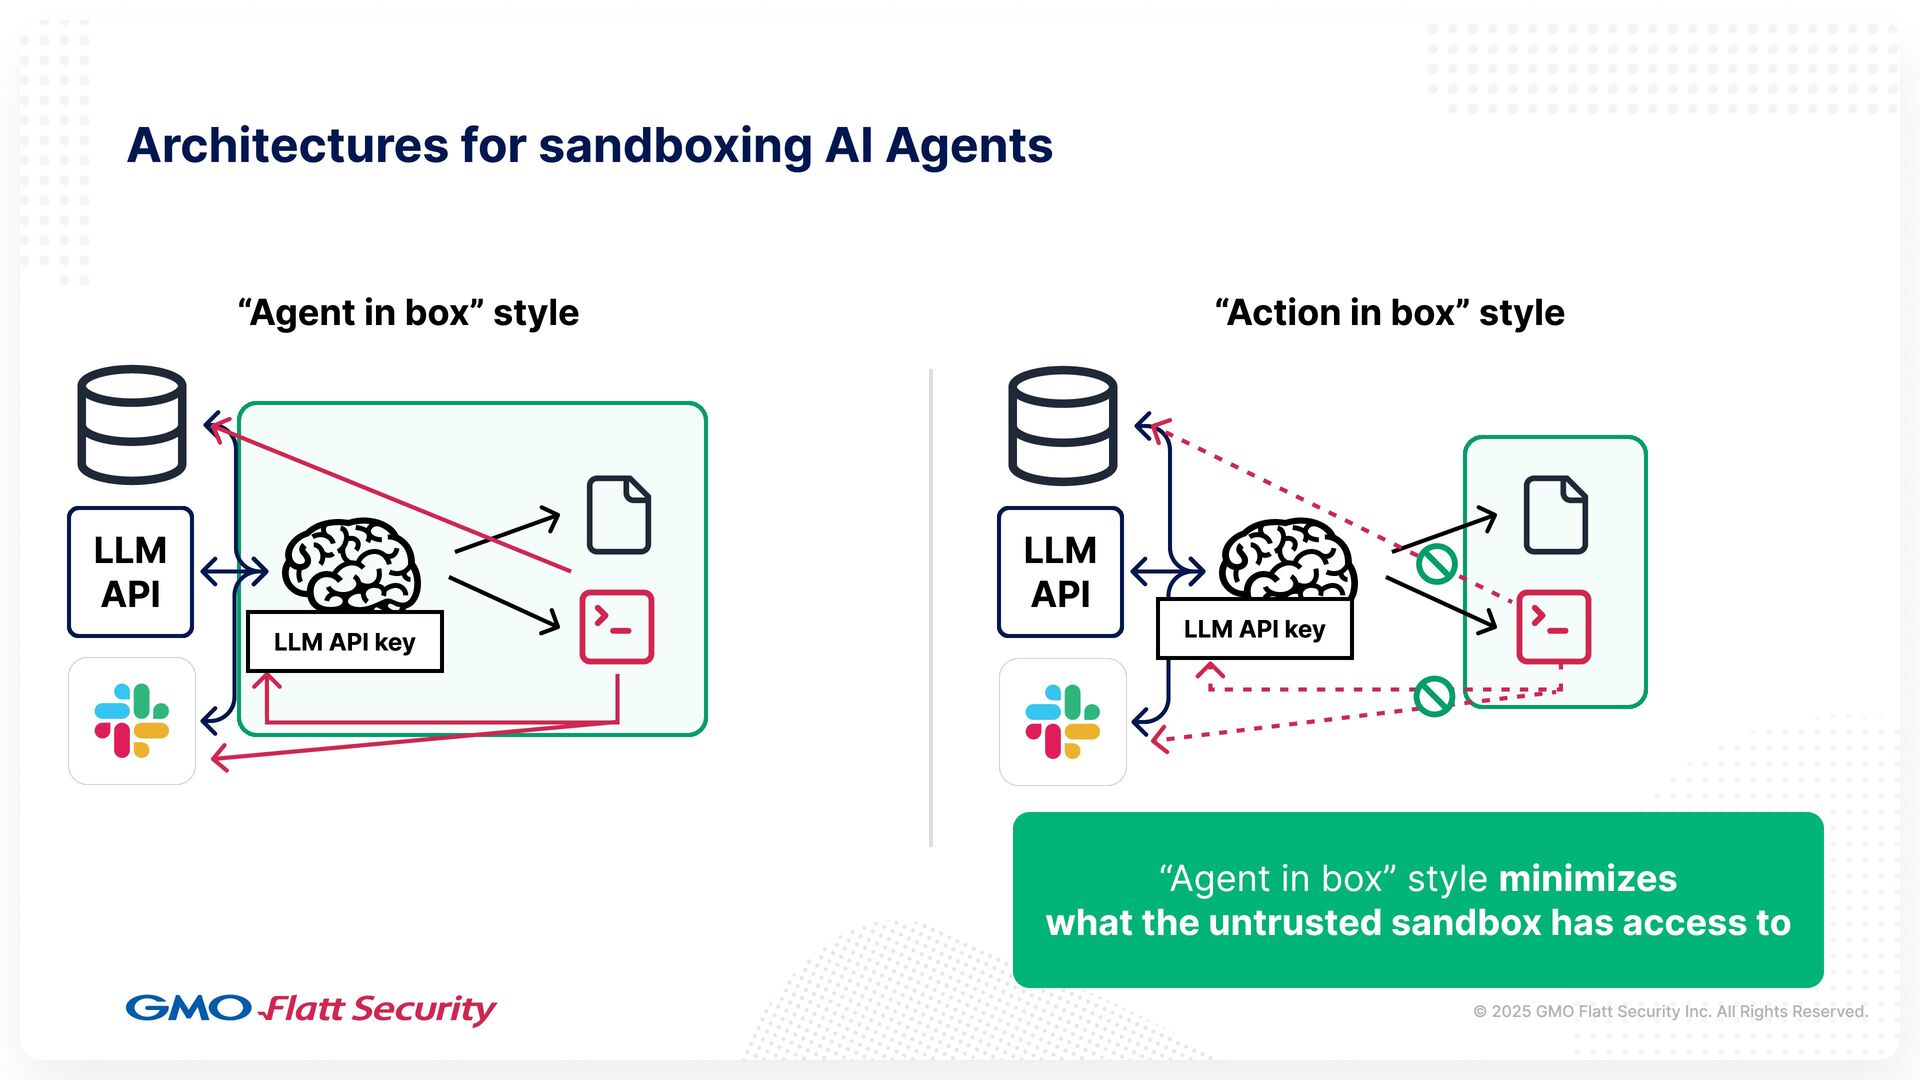
“Agent in box” style “Action in box” style 🧠 🧠
© 2025 GMO Flatt Security Inc. All Rights Reserved. Architectures for sandboxing AI Agents LLM API key LLM API key LLM API LLM API “Agent in box” style minimizes what the untrusted sandbox has access to
“ in box” style Agent “ in box” style Action
🧠 🧠 Good choice when implementing Agent as a Service (esp. multi-tenant) Good choice when running closed-source AI Agent (i.e. when you can’t isolate the internals) © 2025 GMO Flatt Security Inc. All Rights Reserved. Architectures for sandboxing AI Agents LLM API LLM API Make sure all untrusted actions happen in isolated env
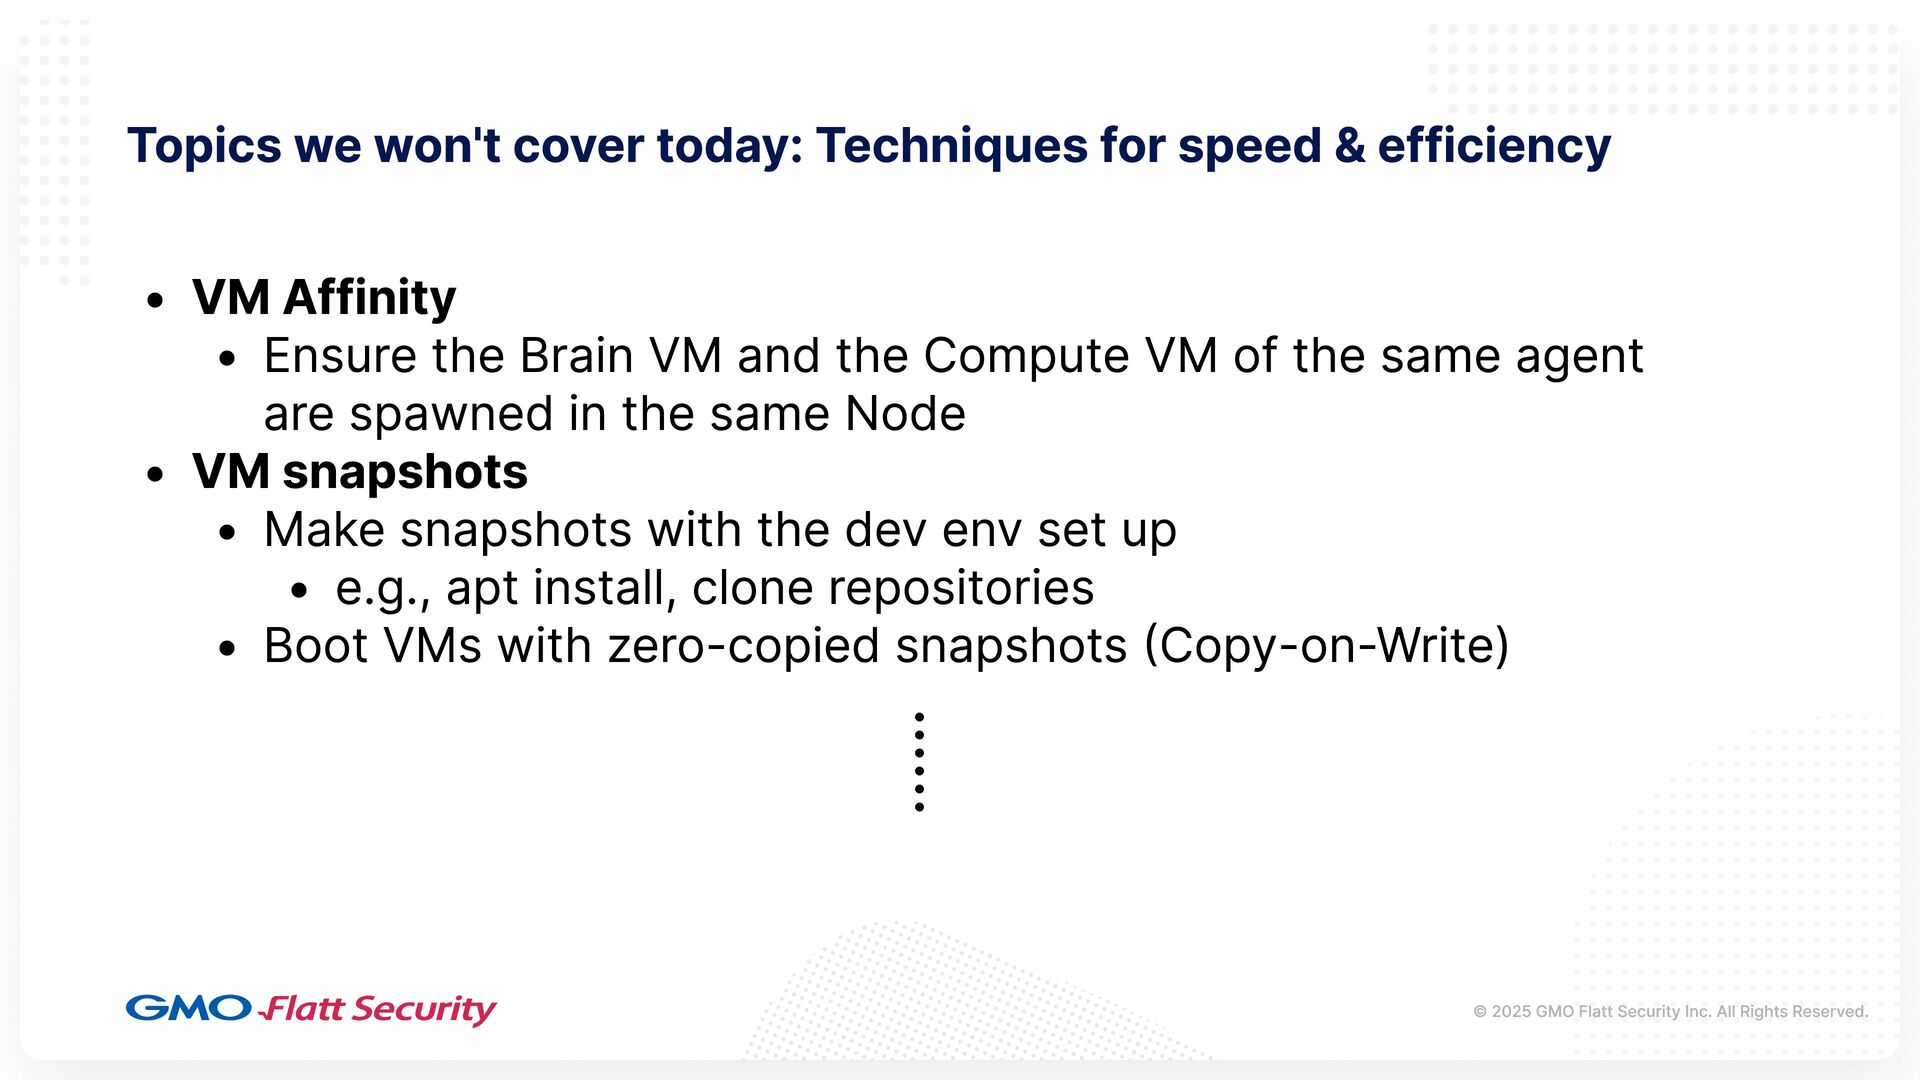
VM Affinity Ensure the Brain VM and the Compute VM
of the same agent are spawned in the same Node VM snapshots Make snapshots with the dev env set up e.g., apt install, clone repositories Boot VMs with zero-copied snapshots (Copy-on-Write) …… © 2025 GMO Flatt Security Inc. All Rights Reserved. Topics we won't cover today: Techniques for speed & efficiency
Isolation is critical for AI Agents, for security, and more
We showed various approaches to isolation, and when to choose which Provisioning sandboxes for multi-tenant, cloud-hosted AI Agents is technically challenging, and we built a secure and performant sandbox platform © 2025 GMO Flatt Security Inc. All Rights Reserved. Conclusion
We are the backbone of engineers. GMO Flatt Security, based
in Tokyo, offers expert security assessments and penetration testing for software. Our seasoned professionals deliver proven, top-tier services. We also provide tools to help you internalize cutting edge, state of the art security practices.
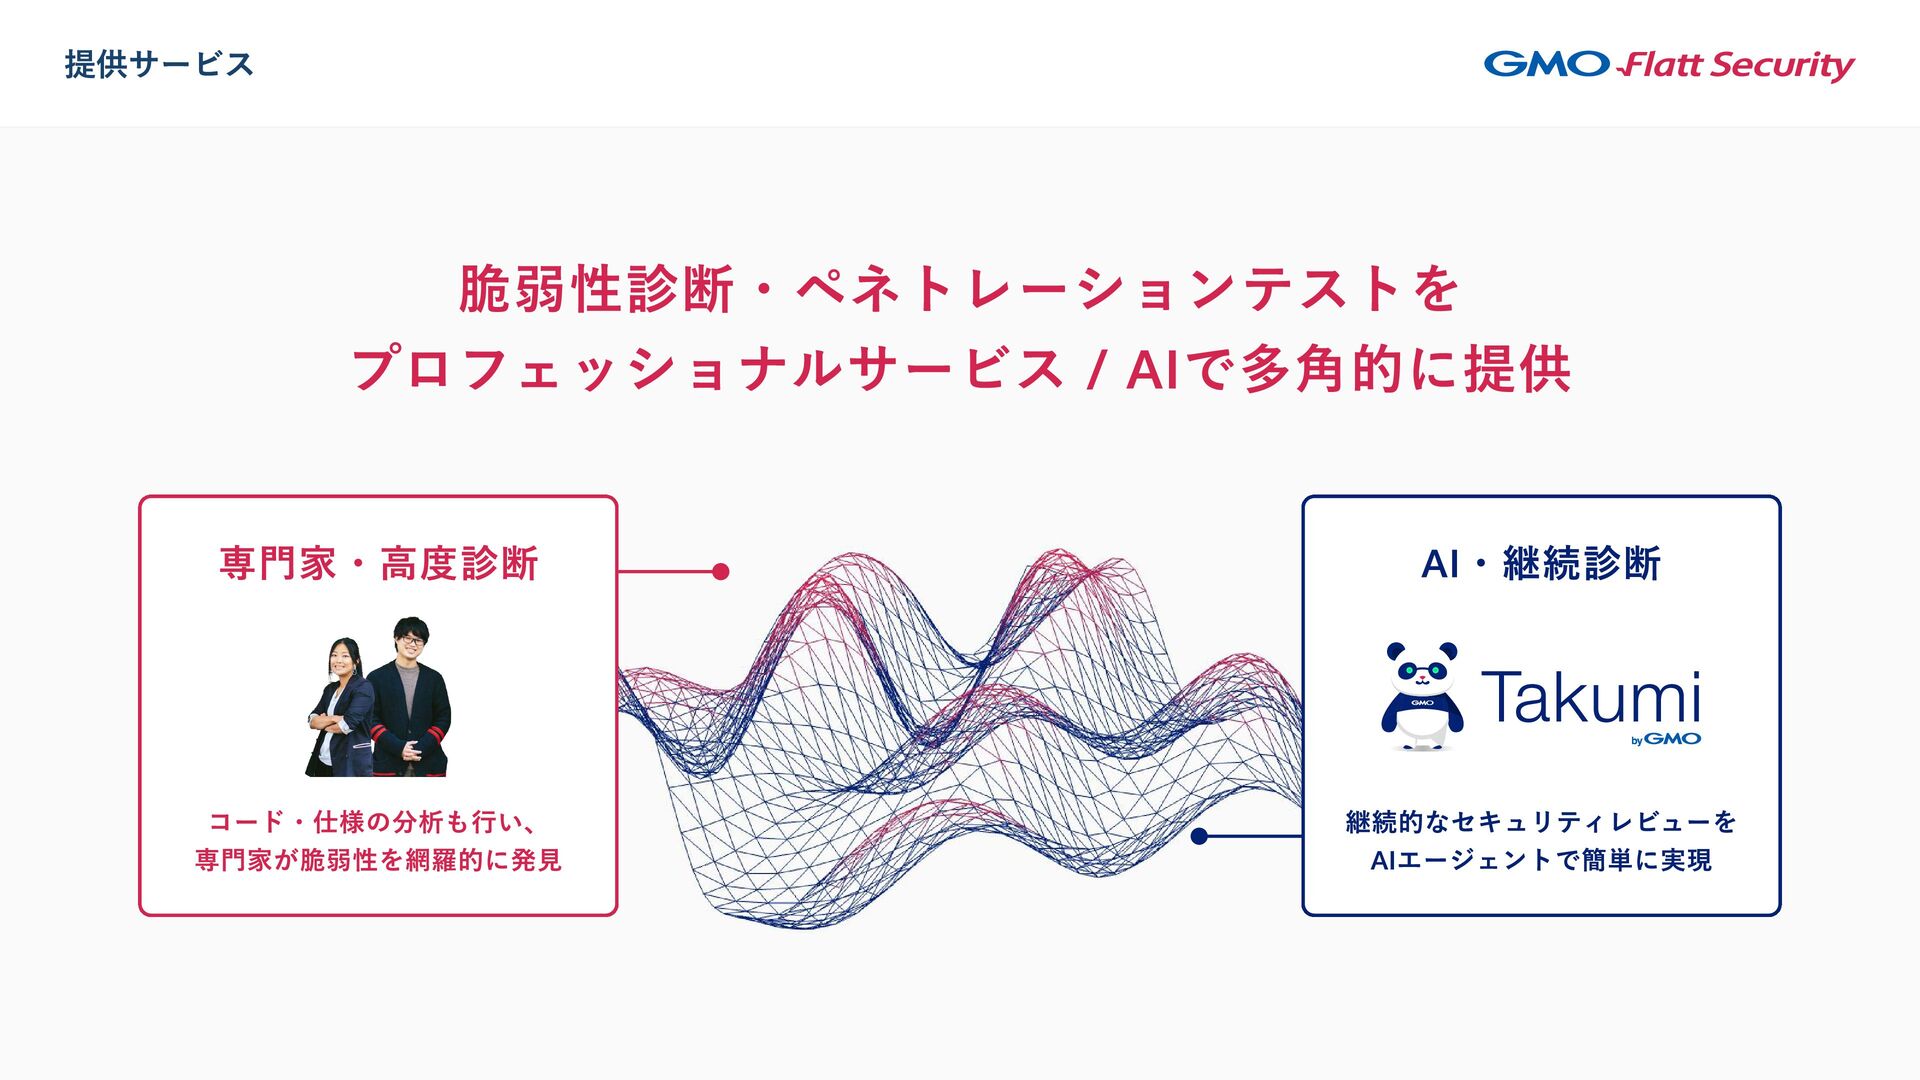
脆弱性診断・ペネトレーションテストを プロフェッショナルサービス / AIで多角的に提供 専門家・高度診断 コード・仕様の分析も行い、 専門家が脆弱性を網羅的に発見 AI・継続診断 継続的なセキュリティレビューを AIエージェントで簡単に実現
提供サービス 提供サービス
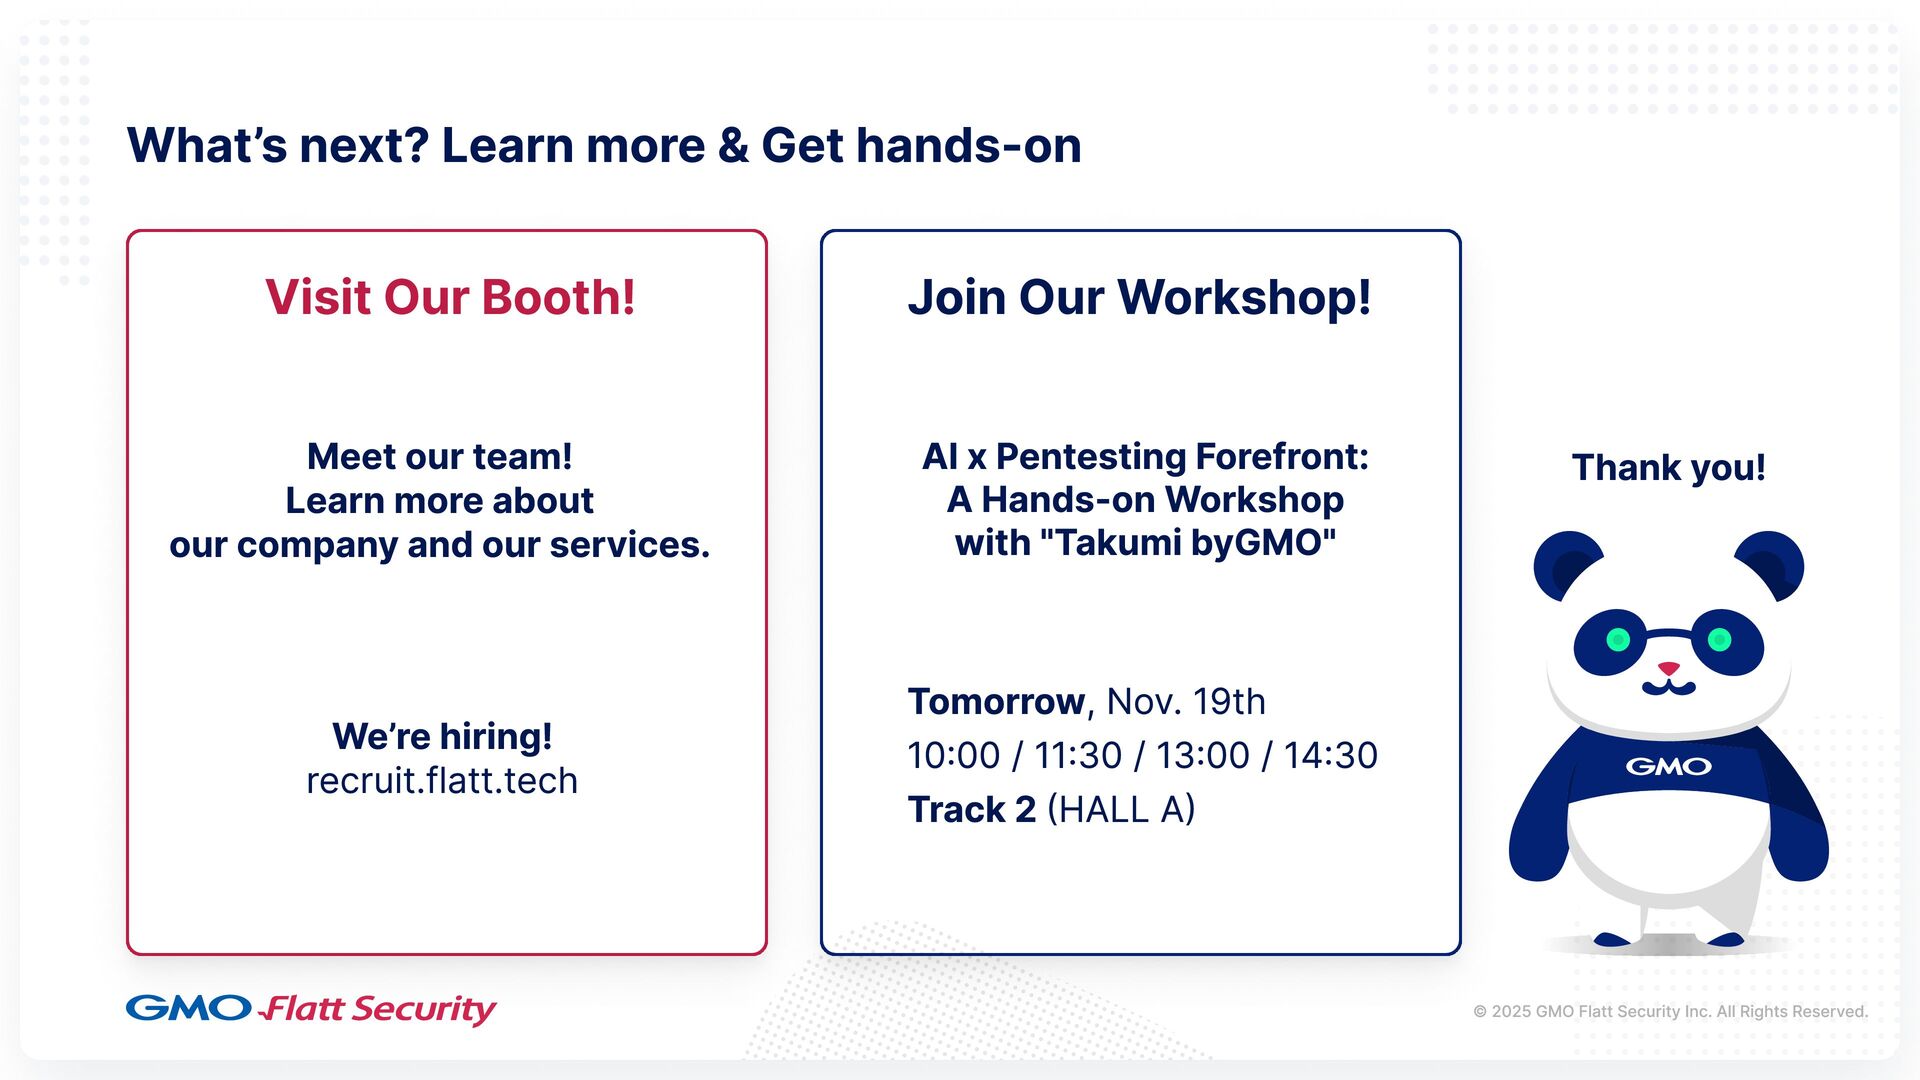
Tomorrow, Nov. 19th 10:00 / 11:30 / 13:00 / 14:30
Track 2 (HALL A) Visit Our Booth! Join Our Workshop! Thank you! AI x Pentesting Forefront: A Hands-on Workshop with "Takumi byGMO" Meet our team! Learn more about our company and our services. We’re hiring! recruit.flatt.tech © 2025 GMO Flatt Security Inc. All Rights Reserved. What’s next? Learn more & Get hands-on


 flatt_security
 masakane55
 sansantech
 naruoga
 tetsuya28
 ivry_presentationmaterials
 tokuty
 pei0804
 bitkey
 furuton
 kizawa2020
 mkdev10
 mochizuki875
 codingconduct
 seathinner
 aleyda
 bkeepers
 marcoroth
 rakko
 morganepeng
 akihiro_kokubo
 techseoconnect