Share
Embed
Transcript
27 slides
-
Identity silos Don’t build your apps as identity silos python-social-auth
and allauth solve this for the open web Not all apps are (deployed) for public consumption. . . -
Identity management Solutions: FreeIPA, Active Directory, LDAP Used by corporations,
open-source projects Define users, groups, role-based access policies Authentication and authorisation services -
SSO protocols Kerberos Ticket-based authentication protocol Active Directory, MIT Kerberos,
Heimdal Browser suppport via HTTP Negotiate (RFC 4559) Security Assertion Markup Language (SAML) XML format Service provider receives assertions containing attributes -
FreeIPA and SSSD FreeIPA is a centralised IdM Users, groups,
services Kerberos Key Distribution Centre (KDC) Host-based Access Control (HBAC) System Security Services Daemon PAM responder and user info lookup Enforce access policies defined in FreeIPA or AD DBus interface -
Demo Manage identities with FreeIPA Kerberos SSO Only django group
can access app (HBAC) Load additional user attributes Map external groups to app groups Let’s onboard Alice -
REMOTE USER Standard request environment variable to identify remote users
Web server sets it Many apps observe it (yours should, too!) In practice REMOTE USER is not enough -
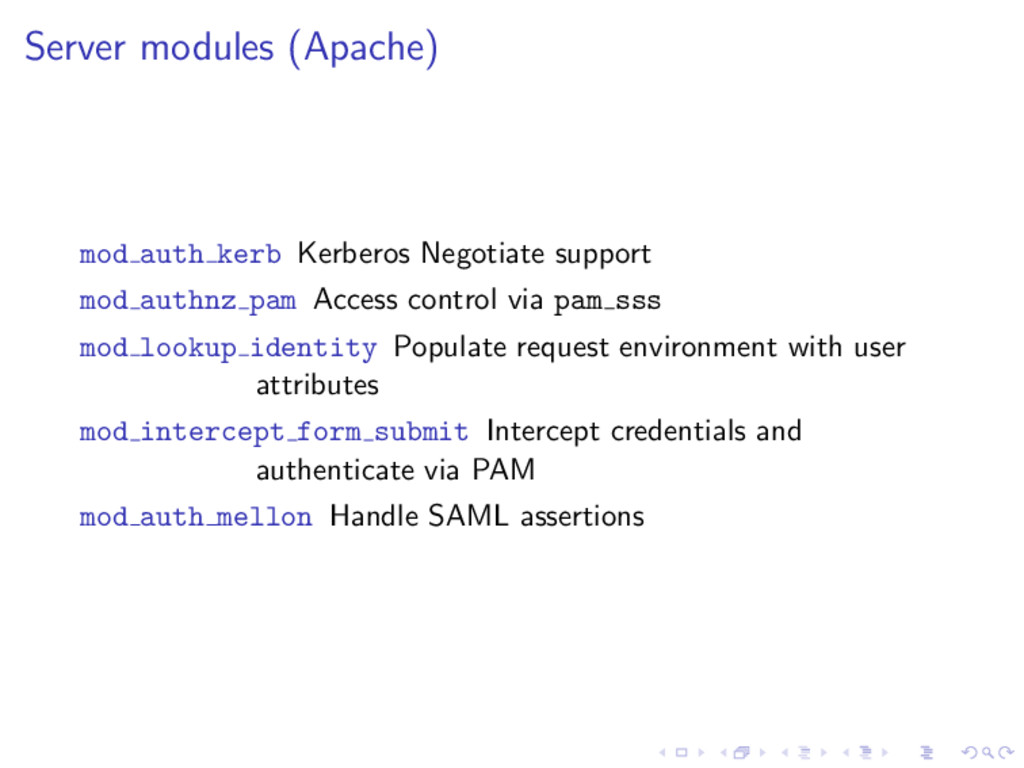
Server modules (Apache) mod auth kerb Kerberos Negotiate support mod
authnz pam Access control via pam sss mod lookup identity Populate request environment with user attributes mod intercept form submit Intercept credentials and authenticate via PAM mod auth mellon Handle SAML assertions -
Middleware and backend (Django) RemoteUserMiddleware observes REMOTE USER and logs
in PersistentRemoteUserMiddleware for persistent sessions RemoteUserAttrMiddleware reads mod lookup identity variables and updates user object Not accepted by Django upstream -> 3rd party package RemoteUserBackend creates users by default -
Not using Django? Use middleware(s) to interpret request environment Implement
system to map remote groups to app groups / roles Users: transient or persisted to app’s database? Tweak views as needed -
Why Apache / why not Python? Python makes sense if
you only deal with Python and need to be server-agnostic. In heterogeneous environments Apache modules mean: don’t have to implement authnz logic in N languages apps have less configuration and do less I/O -
Resources Django REMOTE USER auth HOWTO: http://is.gd/y630Yr http://www.adelton.com/django/ external-authentication-for-django-projects FreeIPA
Web App Authentication wiki page: http://is.gd/w9qZj0 [email protected], #freeipa on Freenode -
Conclusion Identity silos -> duplicate data and effort, password fatigue
If your org has centralised IdM, use it! If it doesn’t, start planning! Evaluate FreeIPA Web server can do the heavy lifting -
Fin Copyright 2015 Red Hat, Inc. This work is licensed
under the Creative Commons Attribution 4.0 International License. To view a copy of this license, visit http://creativecommons.org/licenses/by/4.0/. Slides https://github.com/frasertweedale/talks/ Email [email protected] Twitter @hackuador -
mod auth kerb Implements Kerberos Negotiate method Browser obtains service
ticket and transmits to server Server verifies ticket See also: mod auth gssapi -
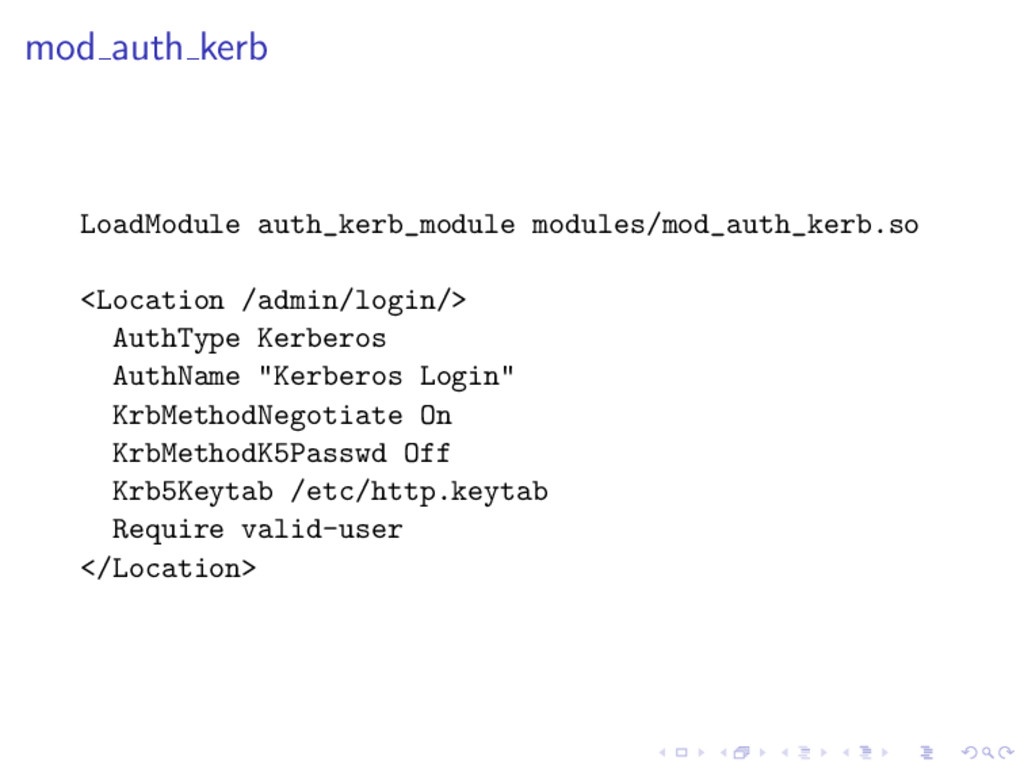
mod auth kerb LoadModule auth_kerb_module modules/mod_auth_kerb.so <Location /admin/login/> AuthType Kerberos
AuthName "Kerberos Login" KrbMethodNegotiate On KrbMethodK5Passwd Off Krb5Keytab /etc/http.keytab Require valid-user </Location> -
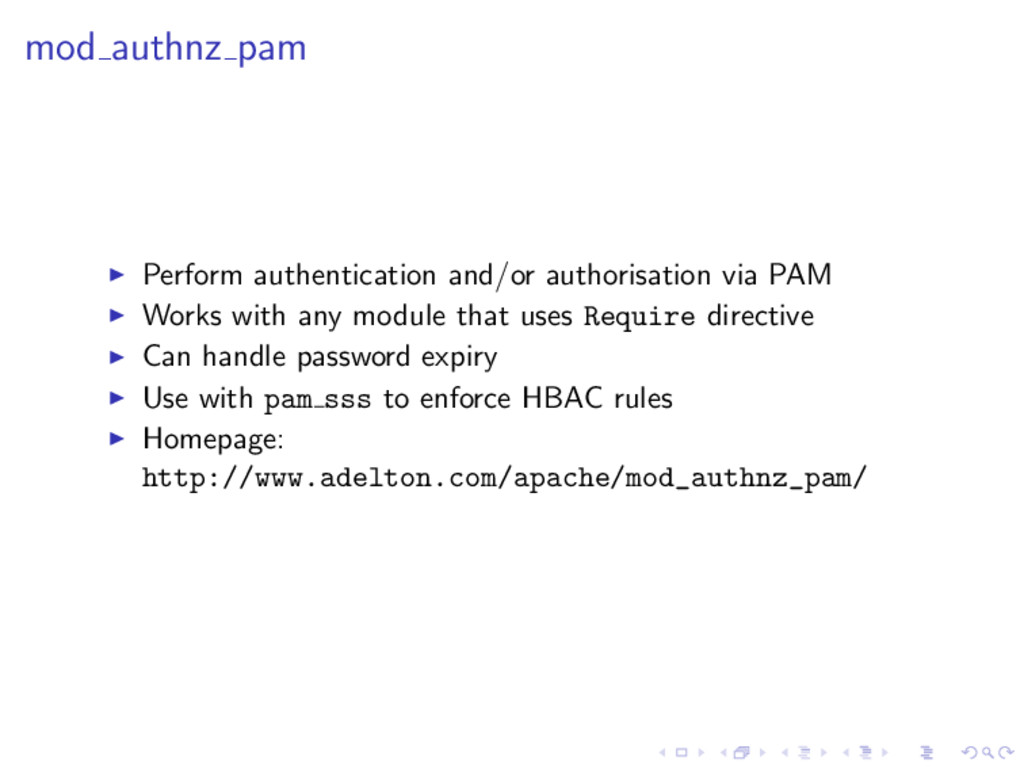
mod authnz pam Perform authentication and/or authorisation via PAM Works
with any module that uses Require directive Can handle password expiry Use with pam sss to enforce HBAC rules Homepage: http://www.adelton.com/apache/mod_authnz_pam/ -
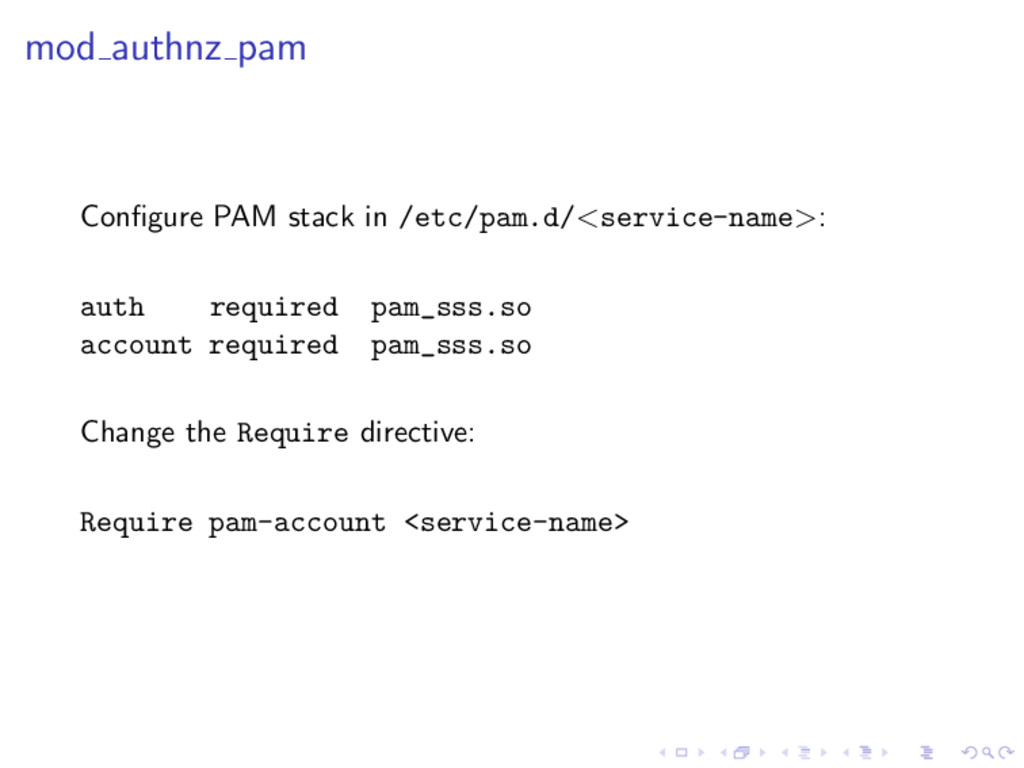
mod authnz pam Configure PAM stack in /etc/pam.d/<service-name>: auth required
pam_sss.so account required pam_sss.so Change the Require directive: Require pam-account <service-name> -
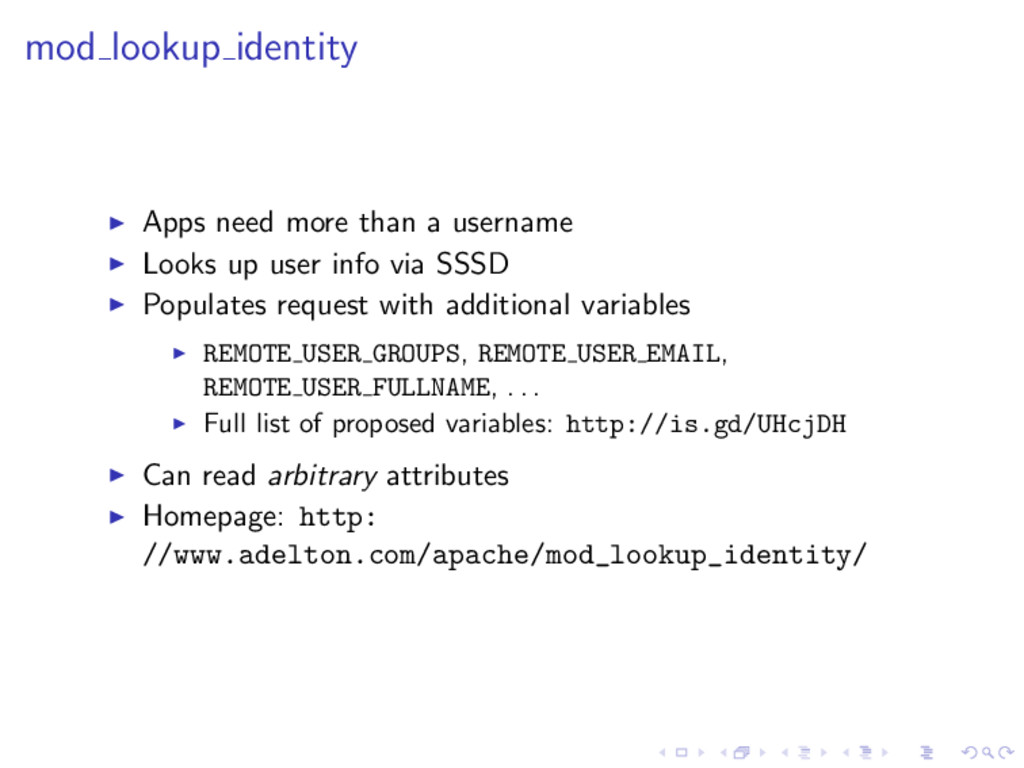
mod lookup identity Apps need more than a username Looks
up user info via SSSD Populates request with additional variables REMOTE USER GROUPS, REMOTE USER EMAIL, REMOTE USER FULLNAME, . . . Full list of proposed variables: http://is.gd/UHcjDH Can read arbitrary attributes Homepage: http: //www.adelton.com/apache/mod_lookup_identity/ -
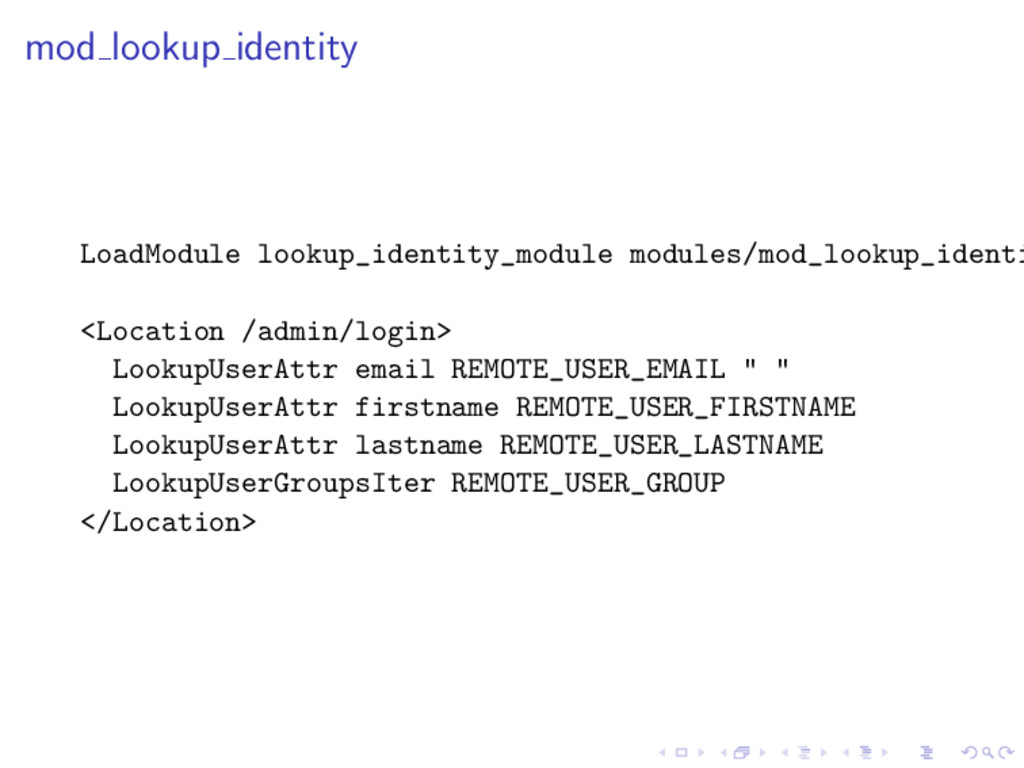
mod lookup identity LoadModule lookup_identity_module modules/mod_lookup_identi <Location /admin/login> LookupUserAttr email
REMOTE_USER_EMAIL " " LookupUserAttr firstname REMOTE_USER_FIRSTNAME LookupUserAttr lastname REMOTE_USER_LASTNAME LookupUserGroupsIter REMOTE_USER_GROUP </Location> -
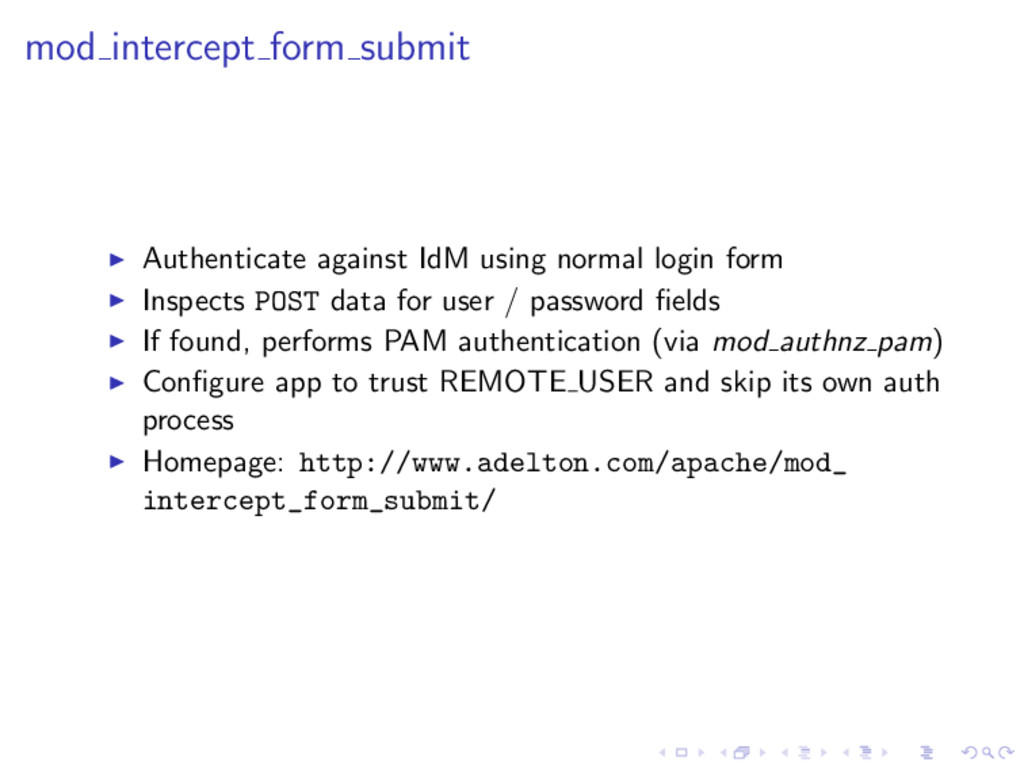
mod intercept form submit Authenticate against IdM using normal login
form Inspects POST data for user / password fields If found, performs PAM authentication (via mod authnz pam) Configure app to trust REMOTE USER and skip its own auth process Homepage: http://www.adelton.com/apache/mod_ intercept_form_submit/ -
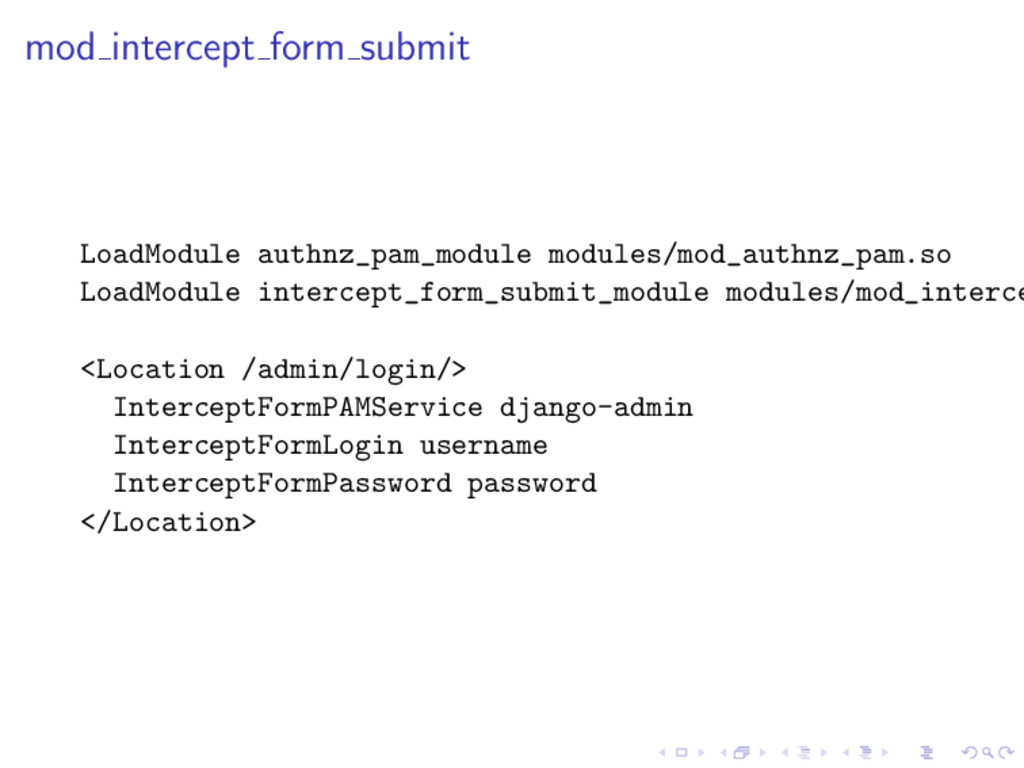
mod intercept form submit LoadModule authnz_pam_module modules/mod_authnz_pam.so LoadModule intercept_form_submit_module modules/mod_interce
<Location /admin/login/> InterceptFormPAMService django-admin InterceptFormLogin username InterceptFormPassword password </Location>