Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
logstash - devopsfinland
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Ramez Hanna
April 25, 2014
Technology
3.6k
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
logstash - devopsfinland
Ramez Hanna
April 25, 2014
More Decks by Ramez Hanna
See All by Ramez Hanna
building_teams.pdf
informatiq
0
24
Observability
informatiq
0
82
What is a teachnical team lead
informatiq
0
200
Provisioning AWS with ansible <our story>
informatiq
3
210
Docker hype
informatiq
2
220
Introduction to Ansible
informatiq
0
230
Other Decks in Technology
See All in Technology
【データ横丁主催】AI Agentがコンテキストを使って仕事をした後、何が残るのか― 組織の経験を次の判断に引き継ぐ「Agent Memory」
shisyu_gaku
2
320
高負荷プロダクション環境におけるAWS Lambdaのリアル 〜スケールとコストを左右する実行ライフサイクルの技術仕様〜
maimyyym
2
850
2026-09-26 Platform Engineering Kaigi 2026 インフラとアプリの境界線と委譲の設計 / Drawing the Infra and App Line
masasuzu
0
610
組み立てて楽しむ AWS Blocks 入門
kmiya84377
0
160
メルカリにおけるAI時代の高速プロトタイピング基盤「Arca」
ryotarai
18
14k
Oracle Base Database Service 技術詳細
oracle4engineer
PRO
16
120k
自律型 AI をセキュアに実装!Gemini と MIG で作る動的コード実行環境
recruitengineers
PRO
1
150
BedrockとLambdaで作る リアルタイム進行型推理ゲーム
kawametho
0
170
[2026-09-30]ロックンロールは鳴り止まないっ - 信頼性かまってちゃん - 「データ駆動を投げ捨ててまで。」追いかける信頼性改善に向けた取り組みの話
tosite
0
190
[2026 Oracle Technical Deep Dive] オンプレミスDBのCloud移行アプローチ:移行計画に基づくメソッドとツールの選択 (2026年9月17日開催)
oracle4engineer
PRO
0
110
1万名の社員が使う認証基盤で どう信頼性を担保するか?
kairim0
0
180
Databricksメトリクスビューはじめてのもくもく会
taka_aki
0
180
Featured
See All Featured
Lightning talk: Run Django tests with GitHub Actions
sabderemane
0
290
How to make the Groovebox
asonas
2
2.5k
Applied NLP in the Age of Generative AI
inesmontani
PRO
4
2.5k
Building a Modern Day E-commerce SEO Strategy
aleyda
45
9.2k
Side Projects
sachag
456
43k
Building AI with AI
inesmontani
PRO
1
1.3k
Paper Plane
katiecoart
PRO
4
53k
Lightning Talk: Beautiful Slides for Beginners
inesmontani
PRO
2
710
Claude Code のすすめ
schroneko
67
230k
StorybookのUI Testing Handbookを読んだ
zakiyama
31
6.9k
HTML-Aware ERB: The Path to Reactive Rendering @ RubyCon 2026, Rimini, Italy
marcoroth
5
760
BBQ
matthewcrist
89
10k
Transcript
Logstash A Real Life Design
Ramez Hanna Husband and Father Sys Admin Get It Done
@informatiq
Disclaimer I am not affiliated with Logstash in any way
I am a happy user
Stages of a log system
Collection Bring order to chaos
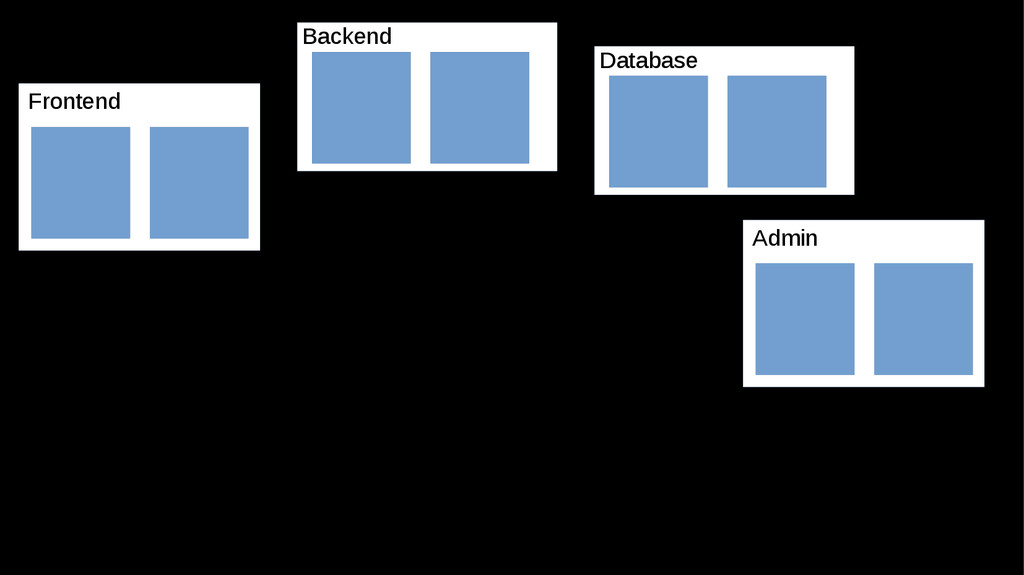
Frontend Backend Admin Database
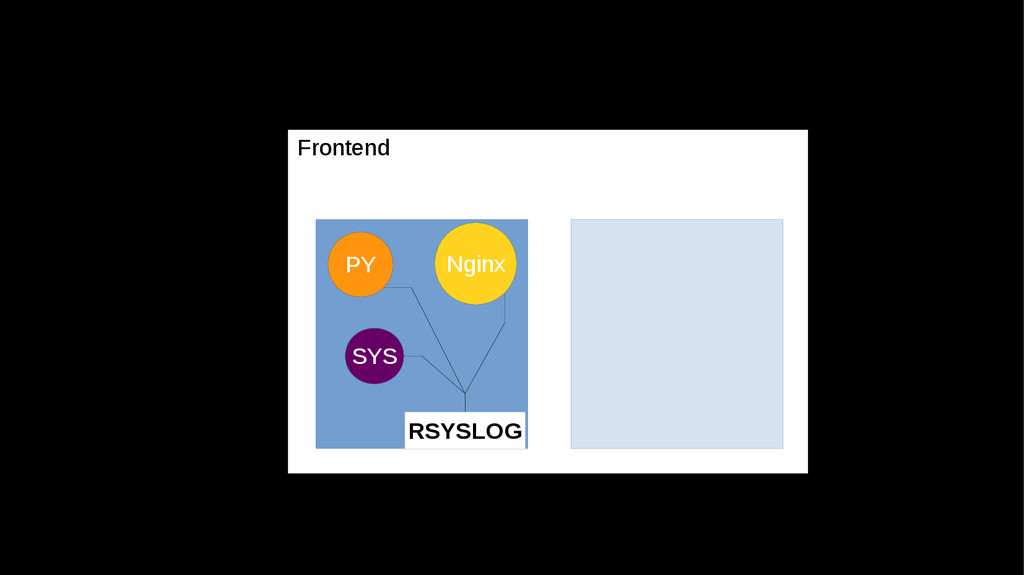
Frontend PY Nginx SYS RSYSLOG
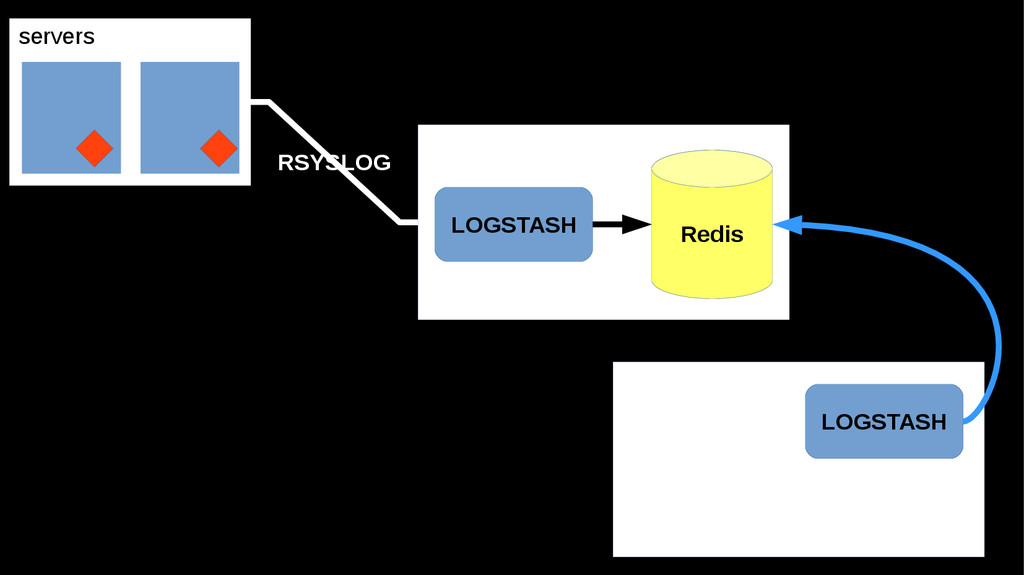
Transport Get it somewhere
servers Redis RSYSLOG LOGSTASH LOGSTASH
Process Make sense of your logs
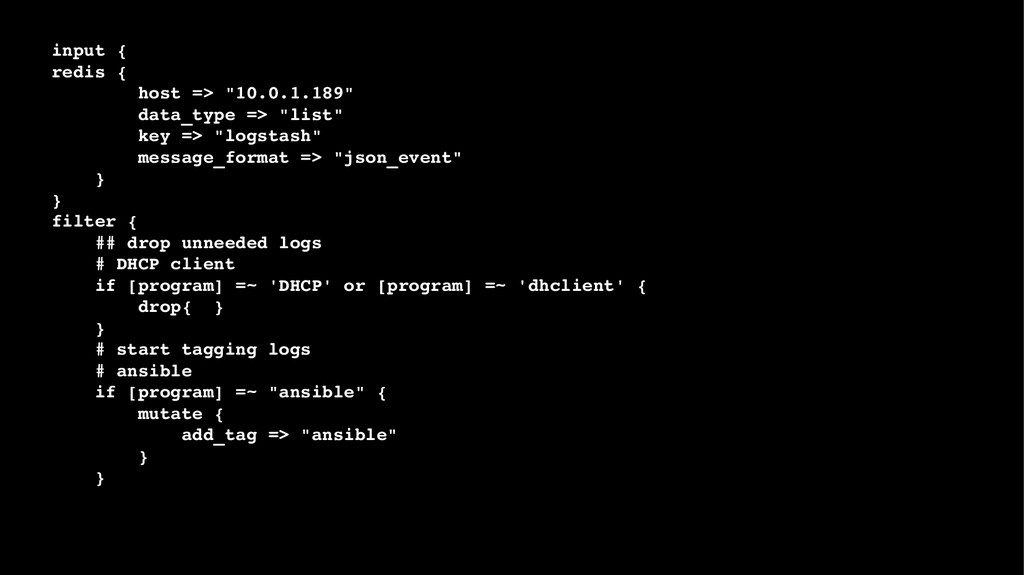
input { redis { host => "10.0.1.189" data_type => "list"
key => "logstash" message_format => "json_event" } } filter { ## drop unneeded logs # DHCP client if [program] =~ 'DHCP' or [program] =~ 'dhclient' { drop{ } } # start tagging logs # ansible if [program] =~ "ansible" { mutate { add_tag => "ansible" } }
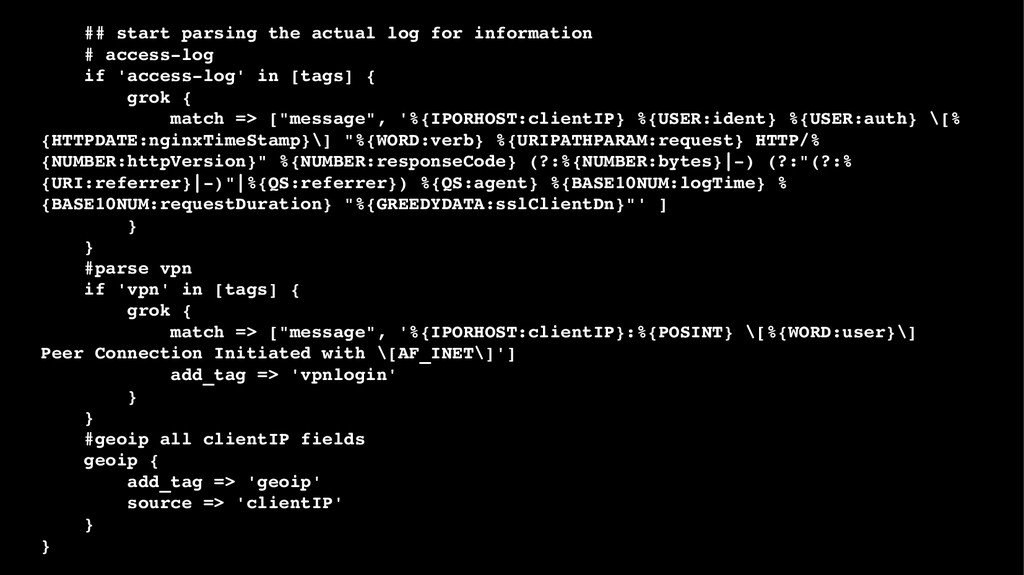
## start parsing the actual log for information # accesslog
if 'accesslog' in [tags] { grok { match => ["message", '%{IPORHOST:clientIP} %{USER:ident} %{USER:auth} \[% {HTTPDATE:nginxTimeStamp}\] "%{WORD:verb} %{URIPATHPARAM:request} HTTP/% {NUMBER:httpVersion}" %{NUMBER:responseCode} (?:%{NUMBER:bytes}|) (?:"(?:% {URI:referrer}|)"|%{QS:referrer}) %{QS:agent} %{BASE10NUM:logTime} % {BASE10NUM:requestDuration} "%{GREEDYDATA:sslClientDn}"' ] } } #parse vpn if 'vpn' in [tags] { grok { match => ["message", '%{IPORHOST:clientIP}:%{POSINT} \[%{WORD:user}\] Peer Connection Initiated with \[AF_INET\]'] add_tag => 'vpnlogin' } } #geoip all clientIP fields geoip { add_tag => 'geoip' source => 'clientIP' } }
Store
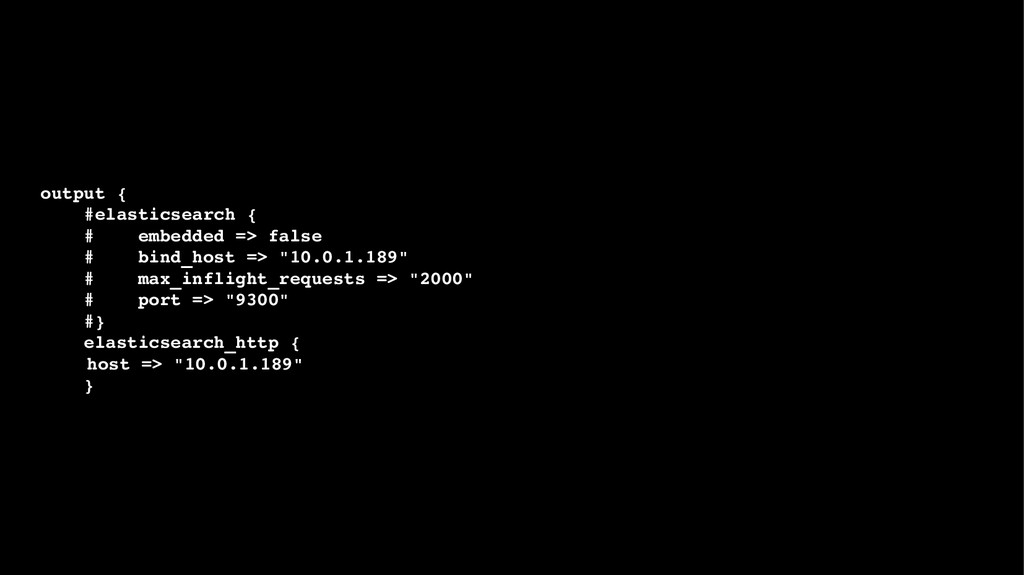
output { #elasticsearch { # embedded => false # bind_host
=> "10.0.1.189" # max_inflight_requests => "2000" # port => "9300" #} elasticsearch_http { host => "10.0.1.189" }
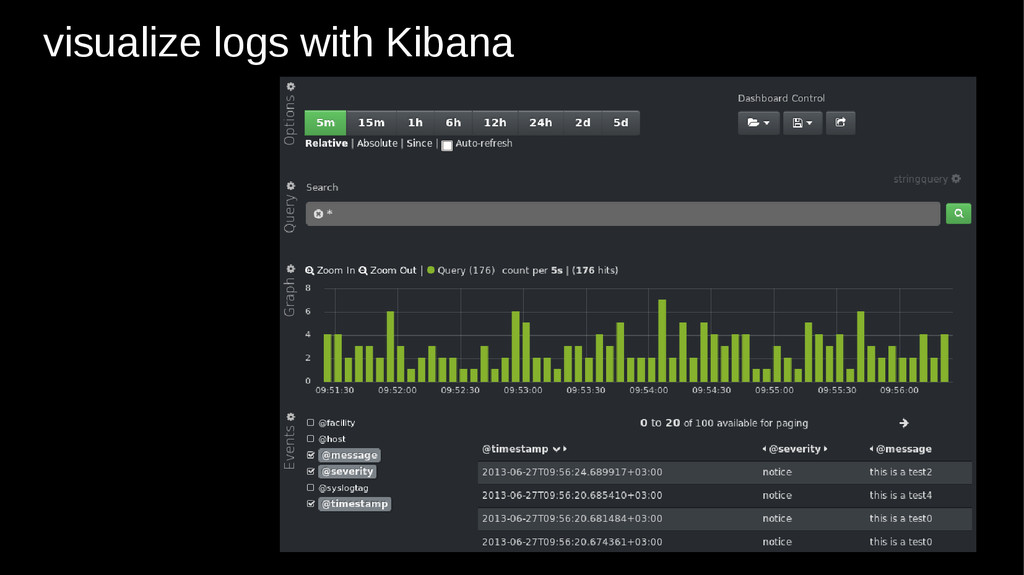
visualize logs with Kibana
Action Time
Output { if "accesslog" in [tags] { if [request] =~
"login" { statsd { host => "10.0.1.196" port => 8125 namespace => "holvi_com" sender => "%{logsource}" increment => "login" } } statsd { host => "10.0.1.196" port => 8125 namespace => "holvi_com" sender => "%{logsource}" increment => "response.%{responseCode}" timing => [ "ResponseTime", "%{requestDuration}" ] count => [ "bytes", "%{bytes}" ] } }


 informatiq
 shisyu_gaku
 maimyyym
 masasuzu
 kmiya84377
 ryotarai
 oracle4engineer
 recruitengineers
 kawametho
 tosite
 kairim0
 taka_aki
 sabderemane
 asonas
 inesmontani
 aleyda
 sachag
 katiecoart
 schroneko
 zakiyama
 marcoroth
 matthewcrist