Upgrade to Pro — share decks privately, control downloads, hide ads and more …

What a time to be a builder

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →
Avatar for Irene Aguilar Irene Aguilar
October 20, 2026
3

What a time to be a builder

NTTDATA talk for AWS Community Day Spain:
We are living through a rare moment in technology: AI is moving from answering questions to taking action, and many of the patterns, platforms and best practices are still being defined. For builders, this creates a unique opportunity to learn while the future is still being built—designing not only agents, but the platforms around them: runtime, identity, context, tools, durable execution, observability, evals, routing, cost control and human approval. As AI becomes more capable, the real challenge is no longer just choosing the best model, but building systems that are reliable, governed and useful in production. And while AI can take on more work, it does not remove human responsibility—so the advantage of being early is not just access to the technology, but the chance to shape how we use it, learn from it and build it together.

Avatar for Irene Aguilar

Irene Aguilar

October 20, 2026

Transcript

  1. What a Time to Be a Builder AWS Community Day

    Spain 2026 Irene Aguilar & Alejandro Lazaro AWS Ambassadors at NTTDATA
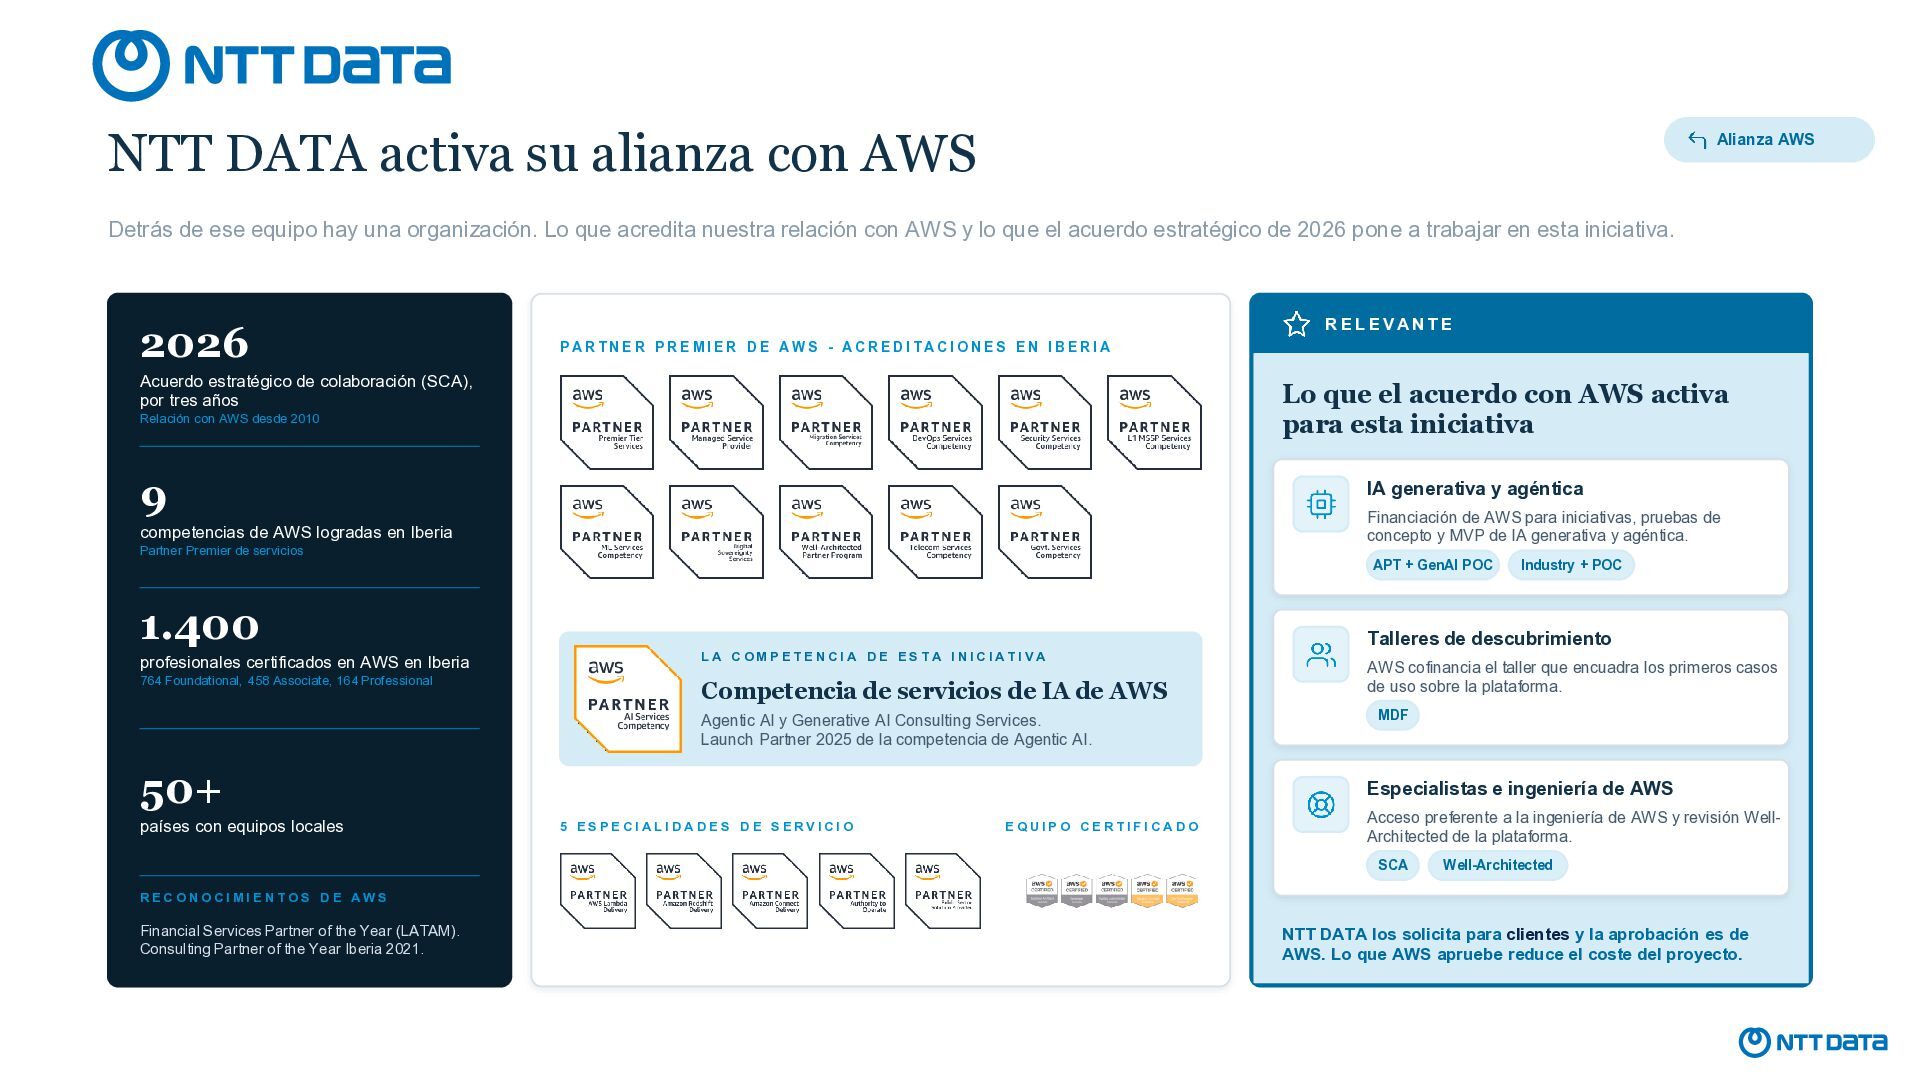
  2. NTT DATA activa su alianza con AWS Alianza AWS Detrás

    de ese equipo hay una organización. Lo que acredita nuestra relación con AWS y lo que el acuerdo estratégico de 2026 pone a trabajar en esta iniciativa. 2026 RELEVANT E PARTNER PREMIER DE AWS - ACREDITACIONES EN IBERIA Acuerdo estratégico de colaboración (SCA), por tres años Lo que el acuerdo con AWS activa para esta iniciativa Relación con AWS desde 2010 9 IA generativa y agéntica Financiación de AWS para iniciativas, pruebas de concepto y MVP de IA generativa y agéntica. competencias de AWS logradas en Iberia Partner Premier de servicios APT + GenAI POC 1.400 profesionales certificados en AWS en Iberia LA COMPETENCIA DE ESTA INICIATIVA 764 Foundational, 458 Associate, 164 Professional Competencia de servicios de IA de AWS Agentic AI y Generative AI Consulting Services. Launch Partner 2025 de la competencia de Agentic AI. 50+ países con equipos locales Industry + POC Talleres de descubrimiento AWS cofinancia el taller que encuadra los primeros casos de uso sobre la plataforma. MDF Especialistas e ingeniería de AWS 5 ESPECIALIDADES DE SERVICIO EQUIPO CERTIFICADO Acceso preferente a la ingeniería de AWS y revisión WellArchitected de la plataforma. SCA Well-Architected RECONO CIMI EN TO S DE AWS Financial Services Partner of the Year (LATAM). Consulting Partner of the Year Iberia 2021. NTT DATA los solicita para clientes y la aprobación es de AWS. Lo que AWS apruebe reduce el coste del proyecto.
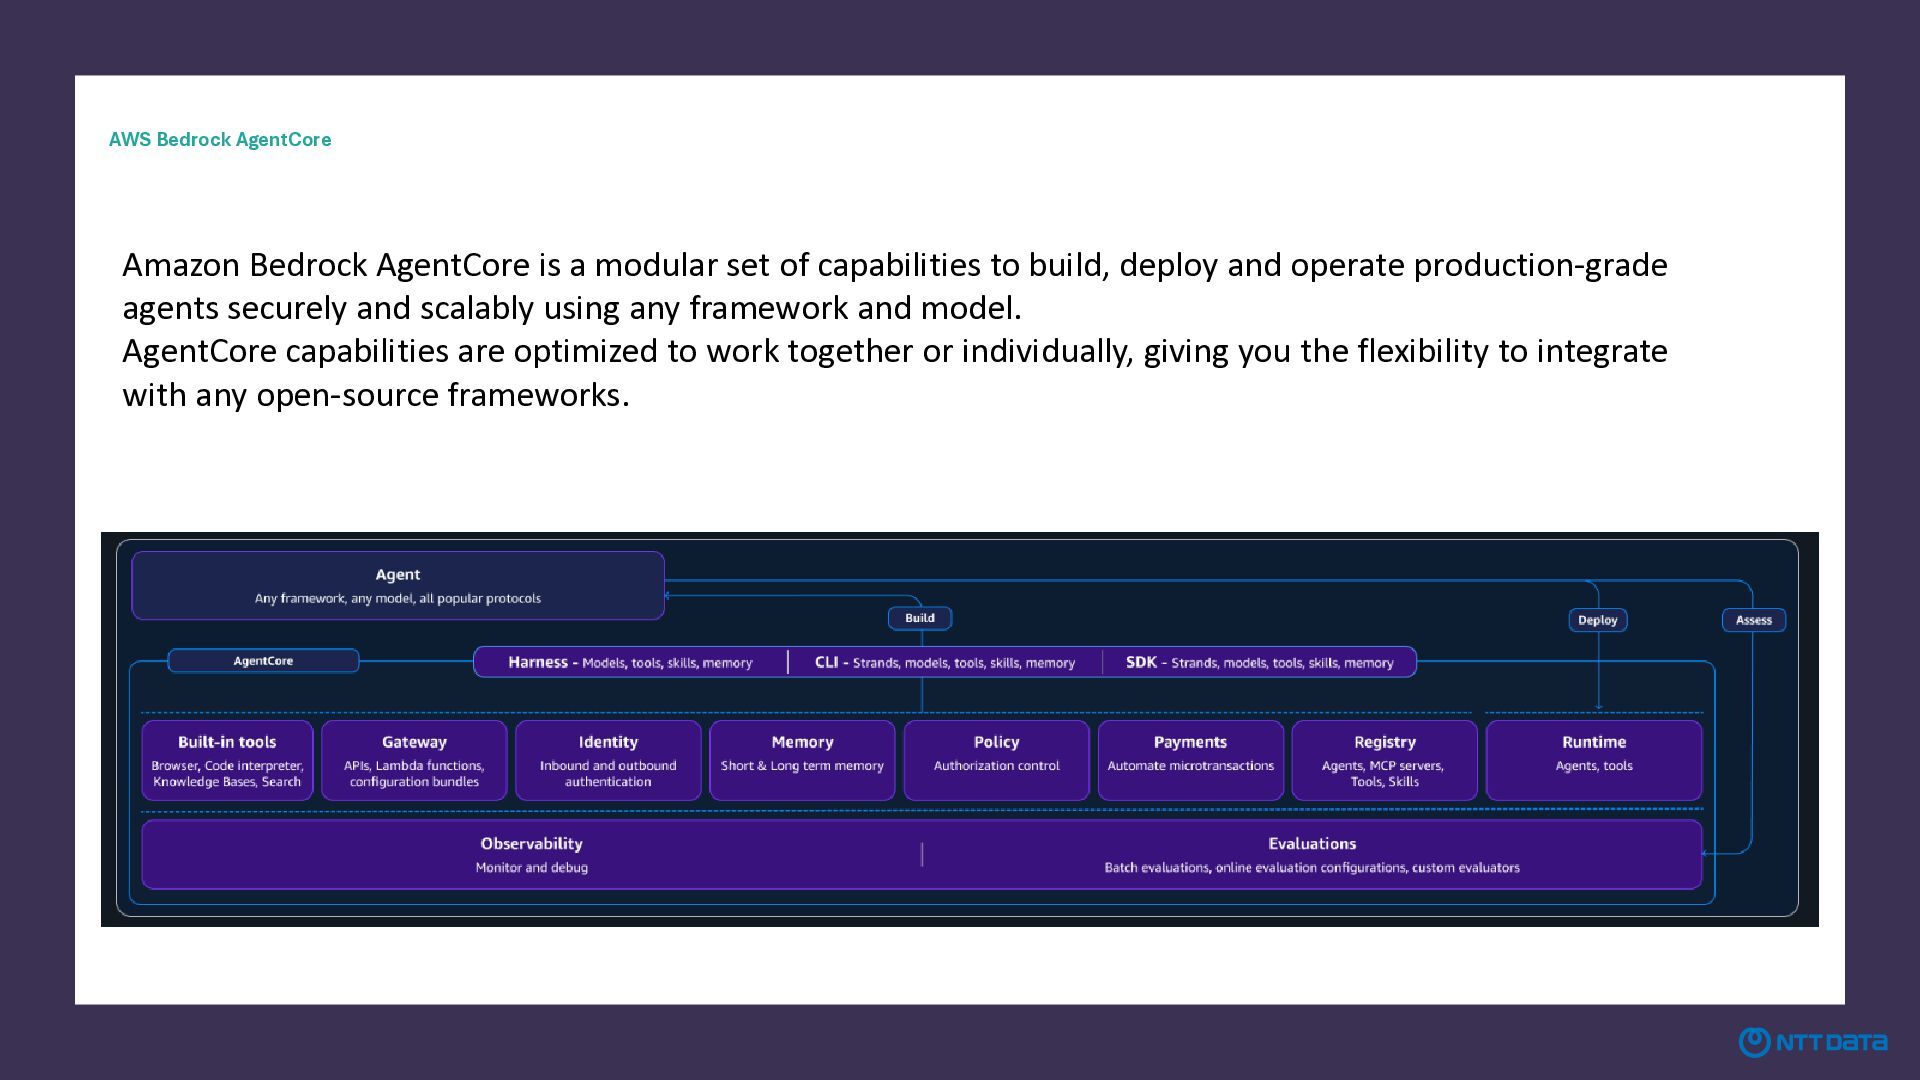
  3. AWS Bedrock AgentCore Amazon Bedrock AgentCore is a modular set

    of capabilities to build, deploy and operate production-grade agents securely and scalably using any framework and model. AgentCore capabilities are optimized to work together or individually, giving you the flexibility to integrate with any open-source frameworks.
  4. AWS AGENTIC PLATFORM • SECURITY DESIGN What a Time to

    Be a Builder Secure ingress for an Agentic Platform on AWS Different exposure levels. Controlled runtime access. Amazon Bedrock AgentCore Runtime & Gateway 1
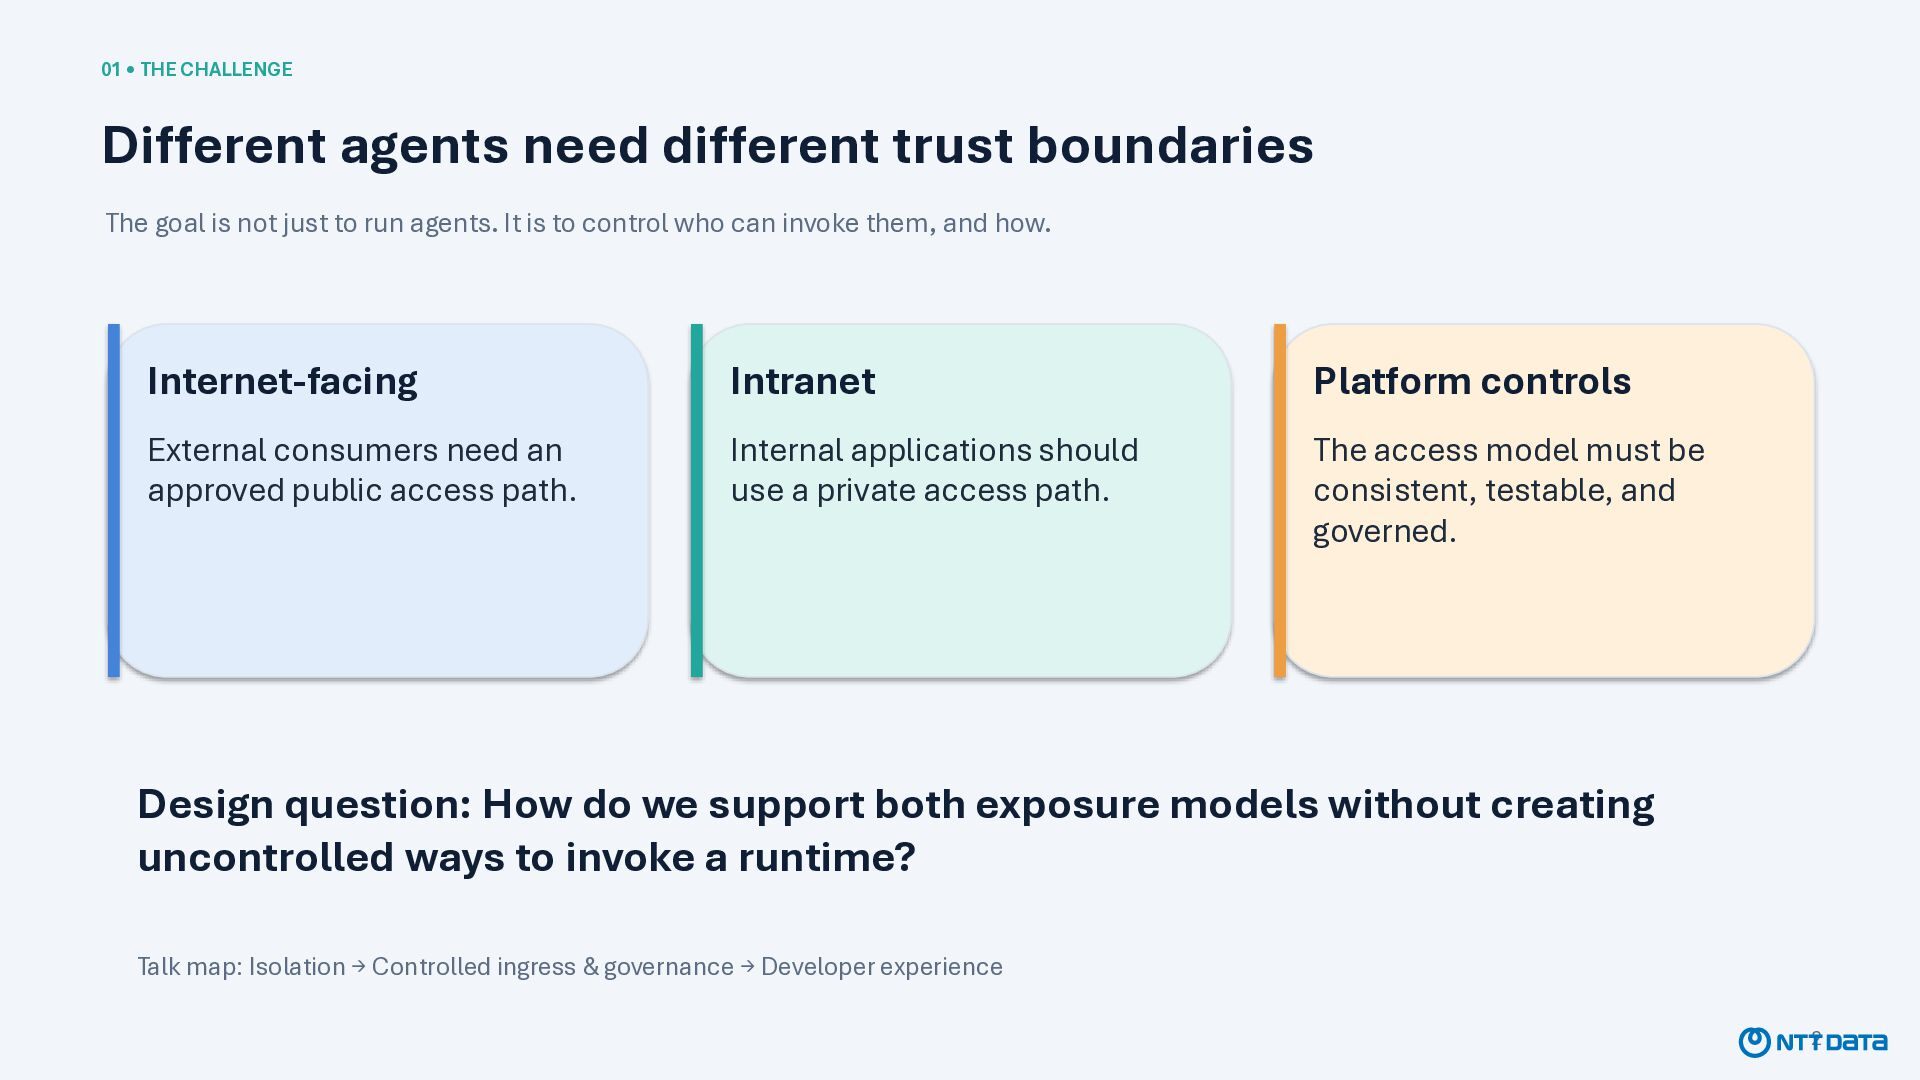
  5. 01 • THE CHALLENGE Different agents need different trust boundaries

    The goal is not just to run agents. It is to control who can invoke them, and how. Internet-facing Intranet Platform controls External consumers need an approved public access path. Internal applications should use a private access path. The access model must be consistent, testable, and governed. Design question: How do we support both exposure models without creating uncontrolled ways to invoke a runtime? Talk map: Isolation → Controlled ingress & governance → Developer experience 2
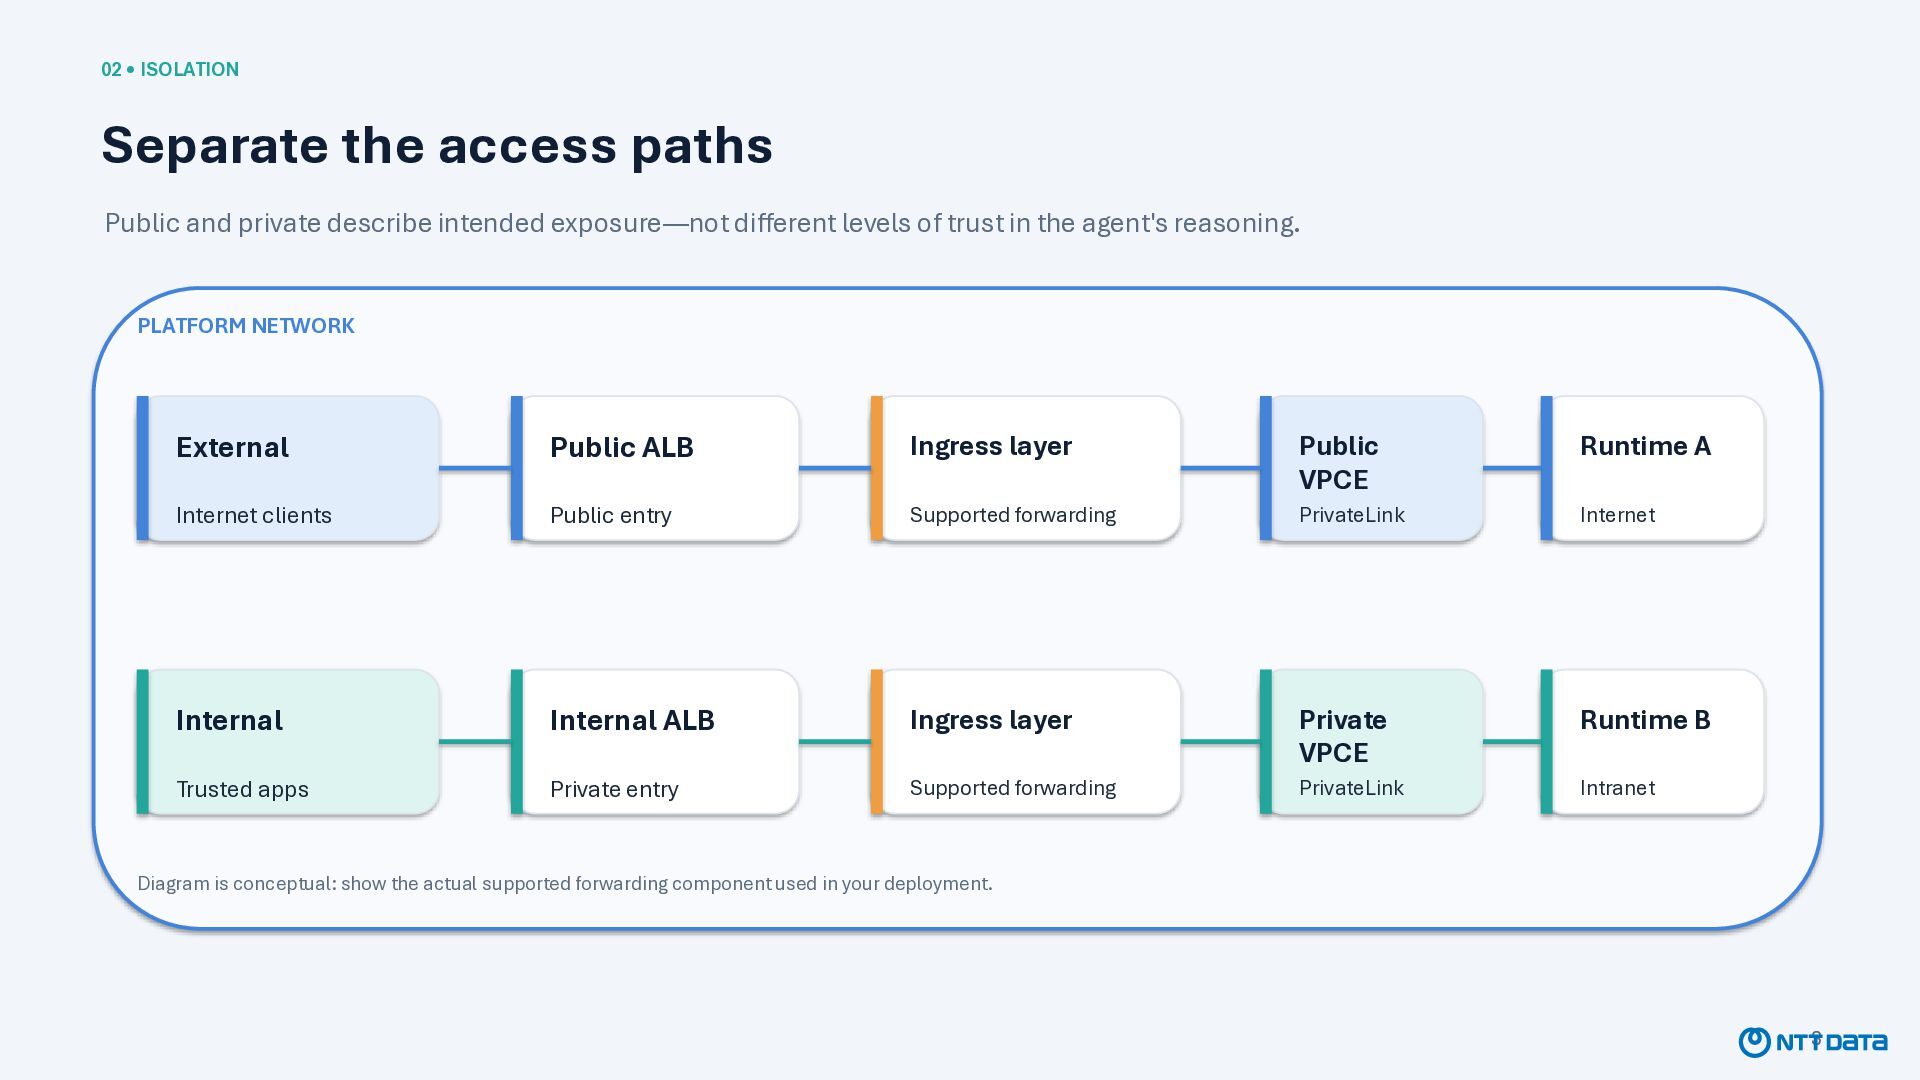
  6. 02 • ISOLATION Separate the access paths Public and private

    describe intended exposure—not different levels of trust in the agent's reasoning. PLATFORM NETWORK External Public ALB Ingress layer Public VPCE Runtime A Internet clients Public entry Supported forwarding PrivateLink Internet Internal Internal ALB Ingress layer Private VPCE Runtime B Trusted apps Private entry Supported forwarding PrivateLink Intranet Diagram is conceptual: show the actual supported forwarding component used in your deployment. 3
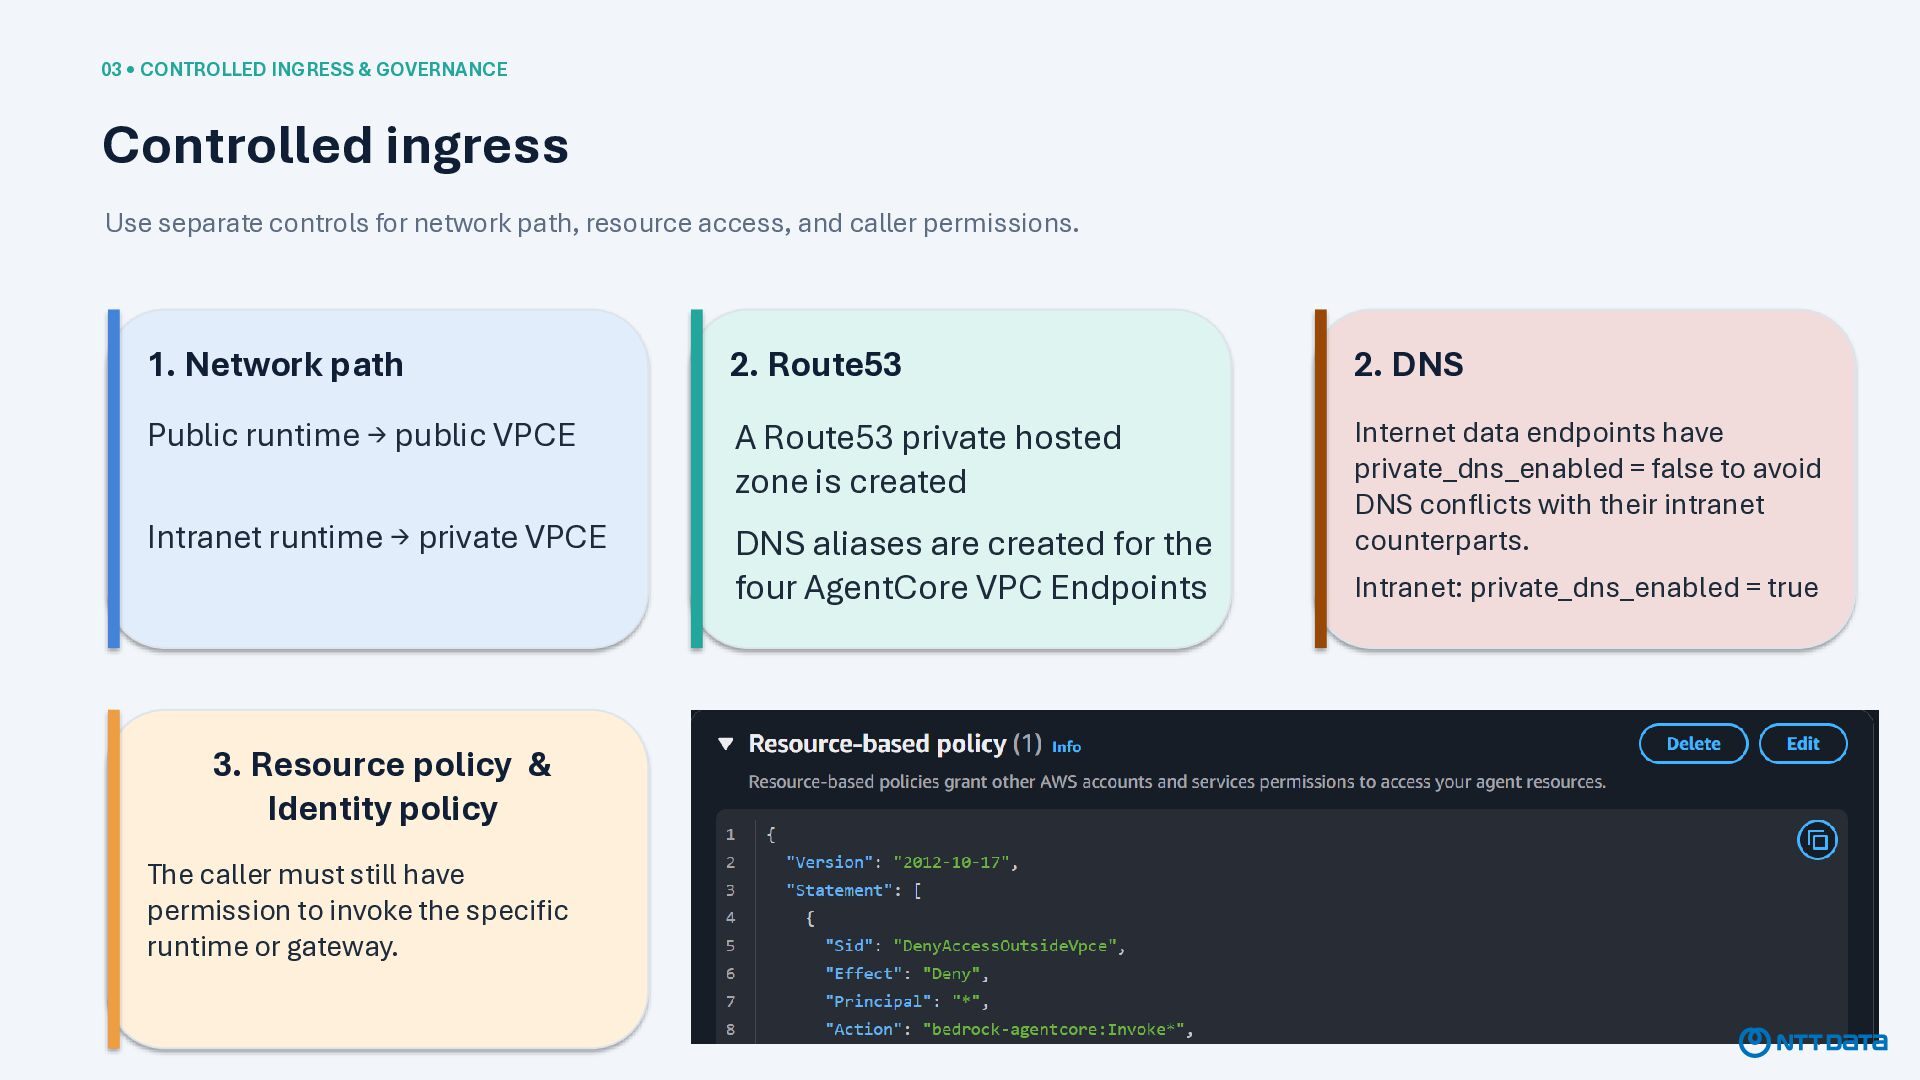
  7. 03 • CONTROLLED INGRESS & GOVERNANCE Controlled ingress Use separate

    controls for network path, resource access, and caller permissions. 1. Network path 2. Route53 2. DNS Public runtime → public VPCE A Route53 private hosted zone is created Intranet runtime → private VPCE DNS aliases are created for the four AgentCore VPC Endpoints Internet data endpoints have private_dns_enabled = false to avoid DNS conflicts with their intranet counterparts. Intranet: private_dns_enabled = true 3. Resource policy & Identity policy The caller must still have permission to invoke the specific runtime or gateway. 4
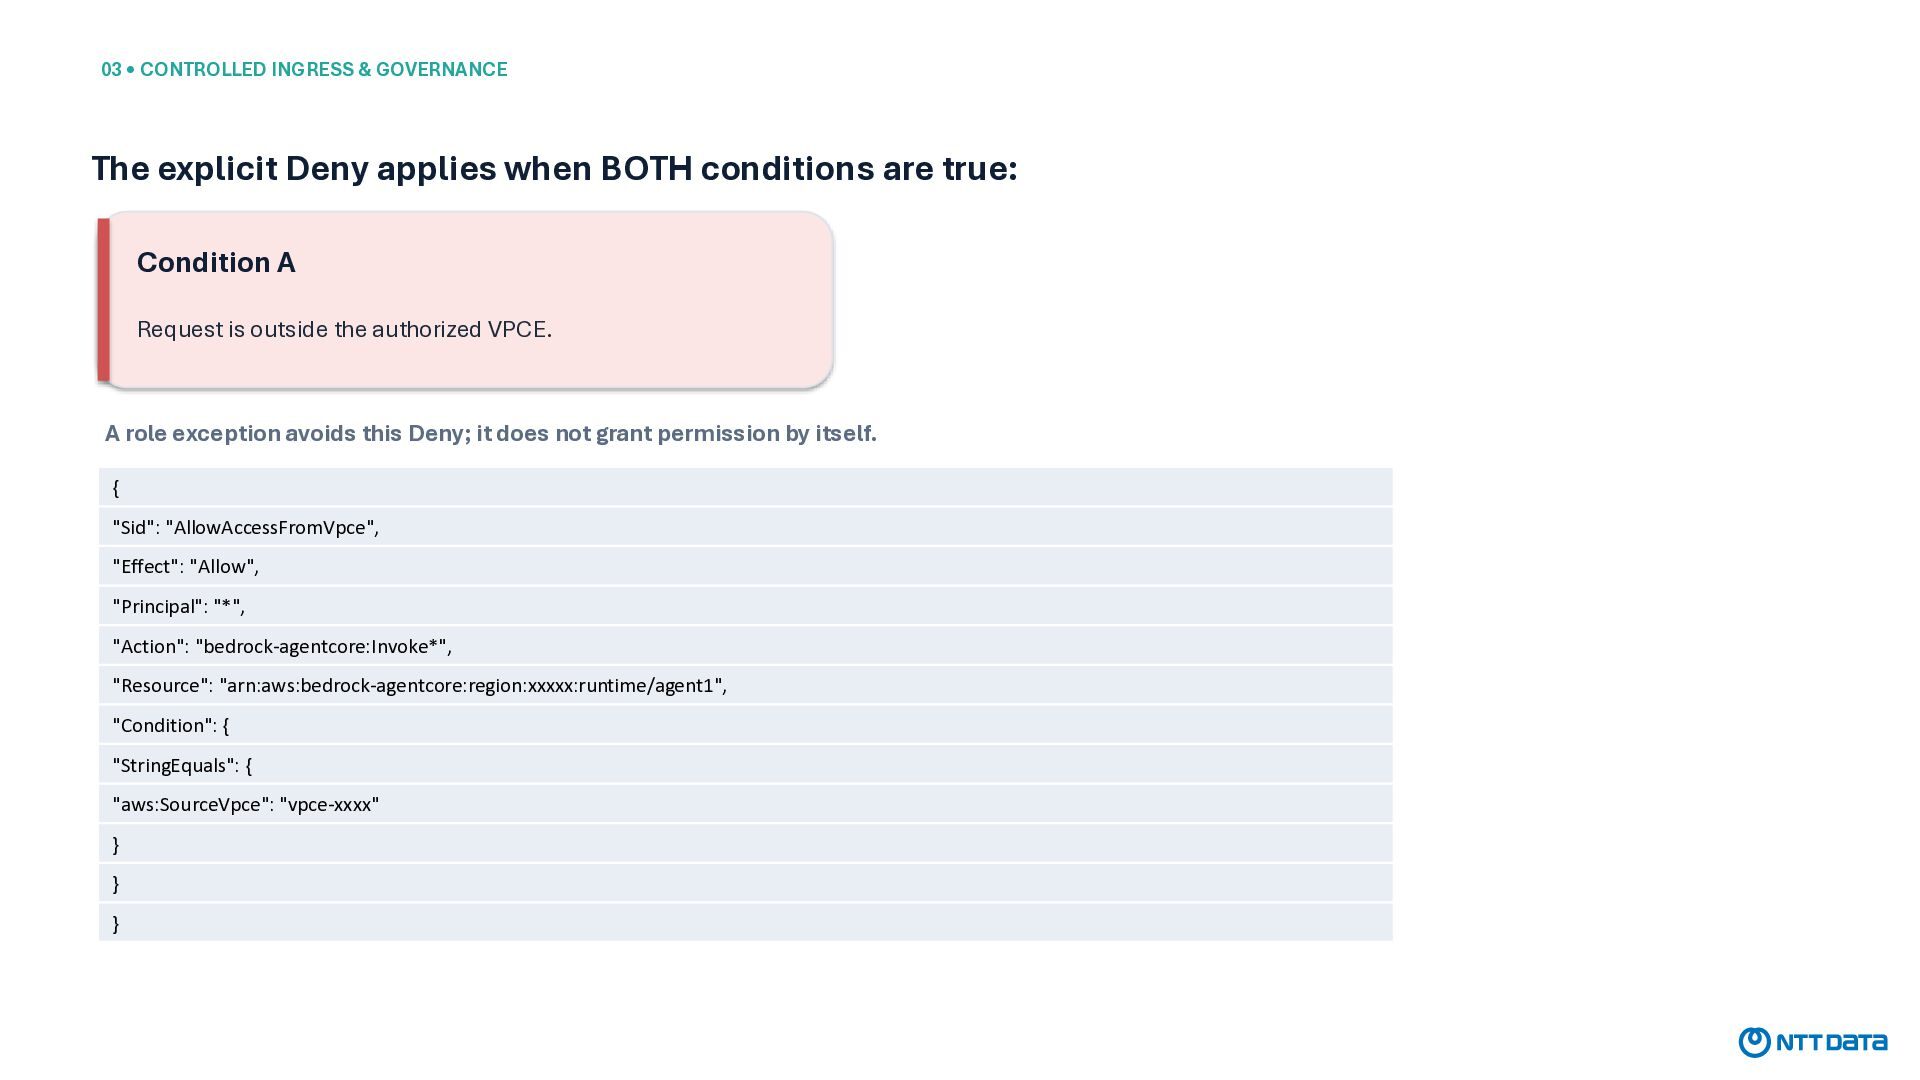
  8. 03 • CONTROLLED INGRESS & GOVERNANCE The explicit Deny applies

    when BOTH conditions are true: Condition A Request is outside the authorized VPCE. A role exception avoids this Deny; it does not grant permission by itself. { "Sid": "AllowAccessFromVpce", "Effect": "Allow", "Principal": "*", "Action": "bedrock-agentcore:Invoke*", "Resource": "arn:aws:bedrock-agentcore:region:xxxxx:runtime/agent1", "Condition": { "StringEquals": { "aws:SourceVpce": "vpce-xxxx" } } }
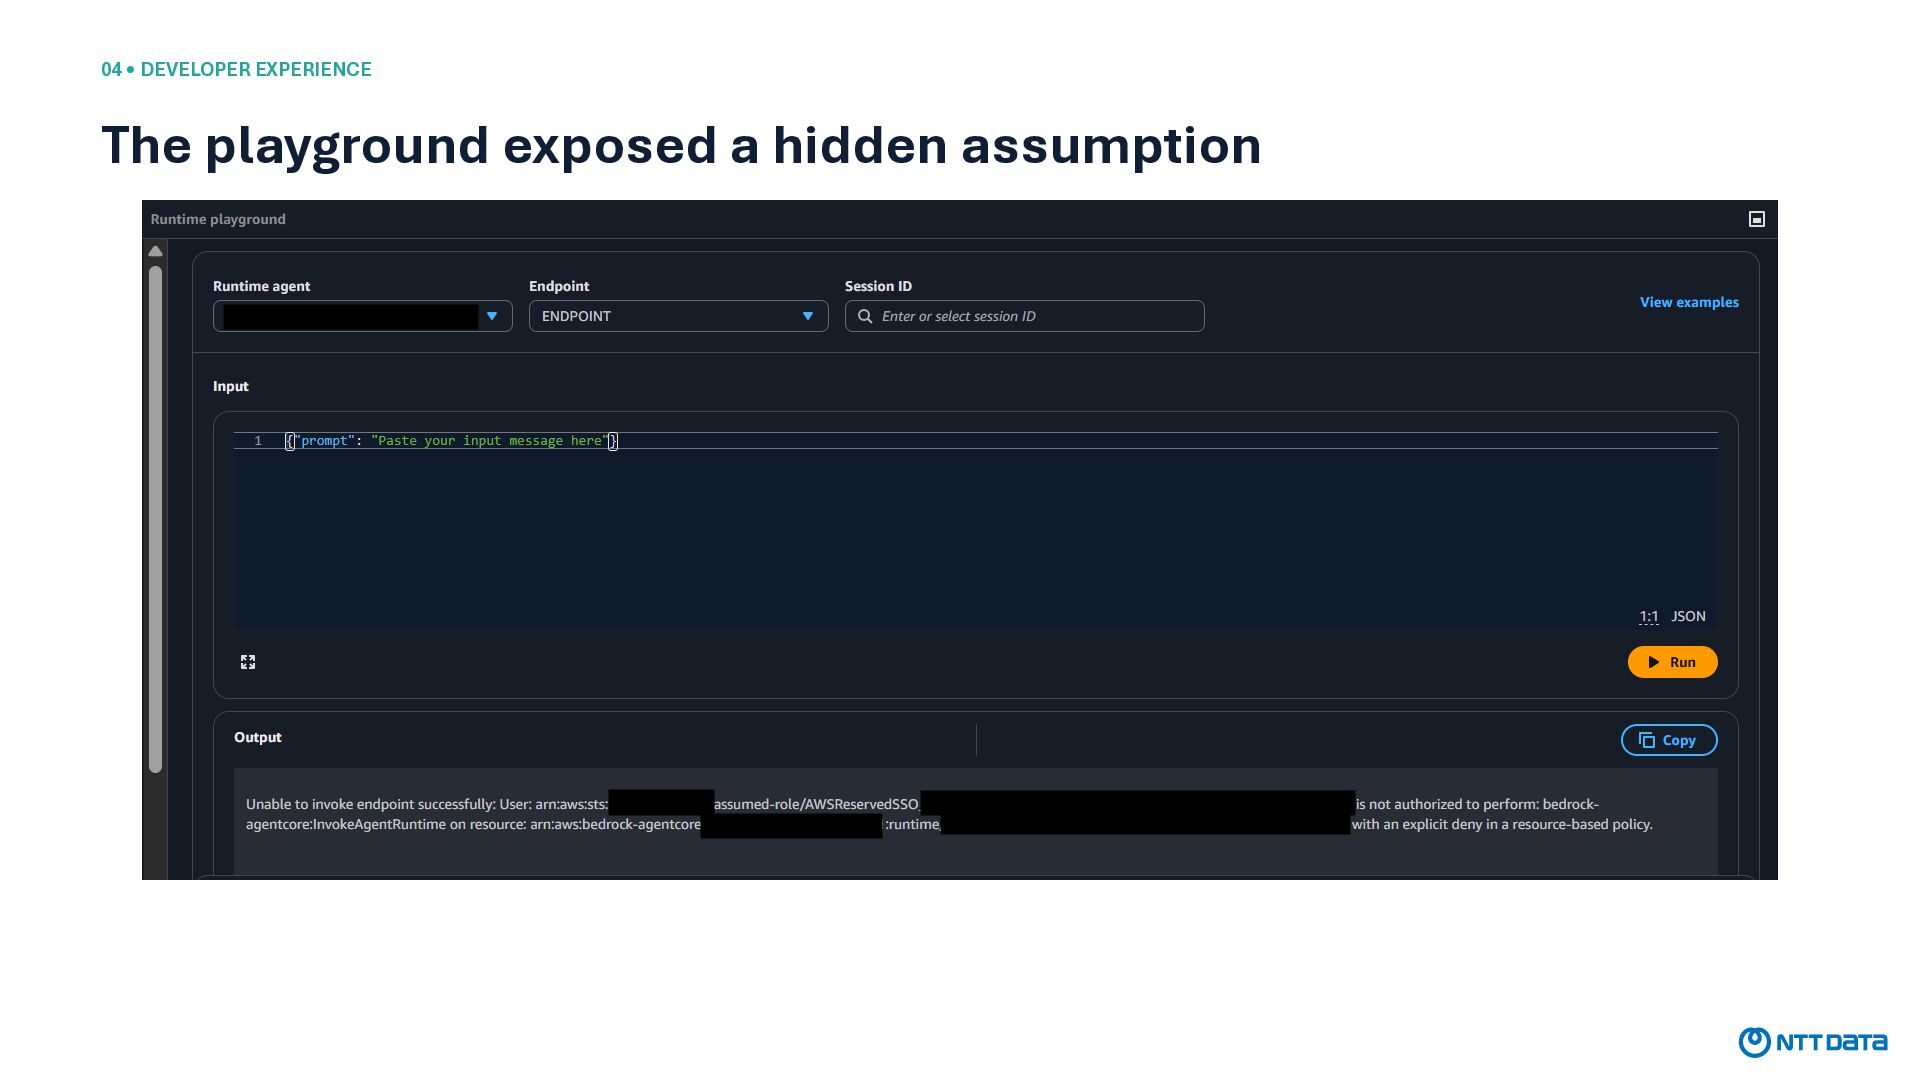
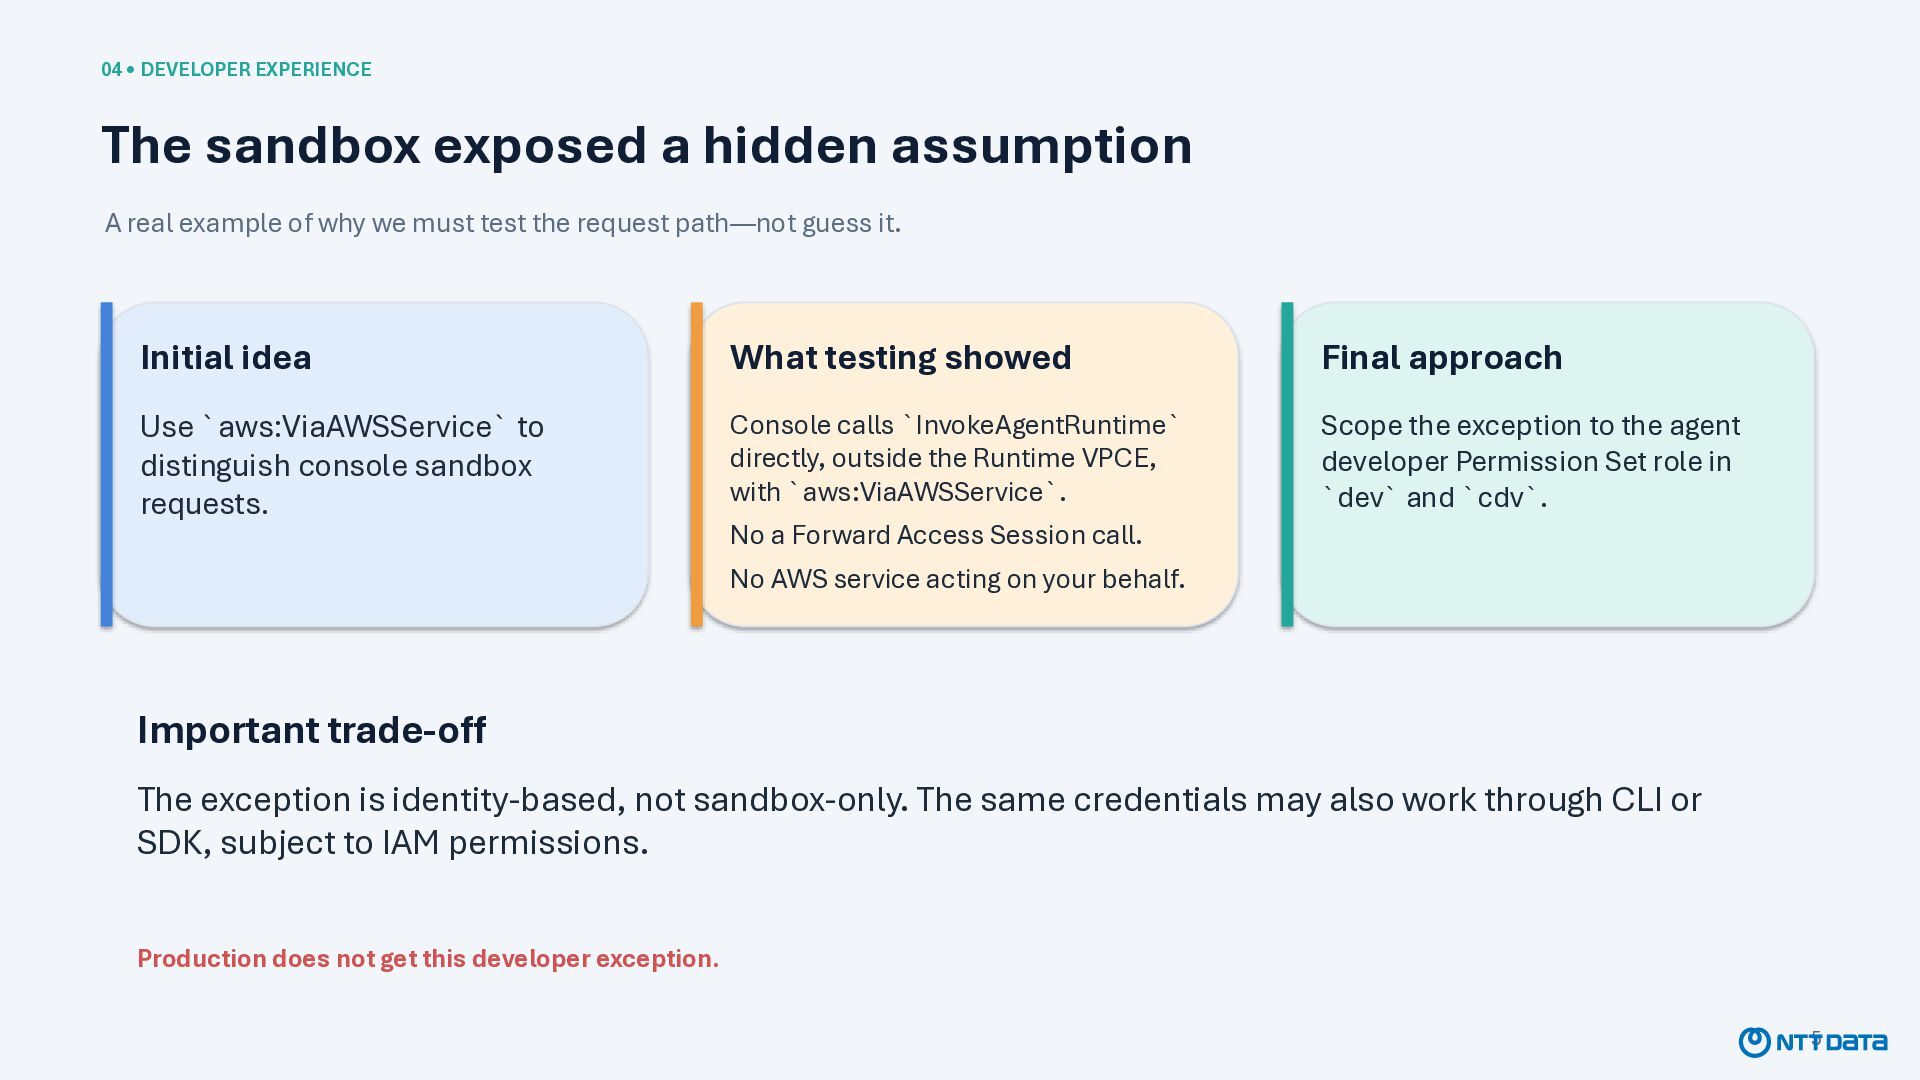
  9. 04 • DEVELOPER EXPERIENCE The sandbox exposed a hidden assumption

    A real example of why we must test the request path—not guess it. Initial idea What testing showed Final approach Use `aws:ViaAWSService` to distinguish console sandbox requests. Console calls `InvokeAgentRuntime` directly, outside the Runtime VPCE, with `aws:ViaAWSService`. Scope the exception to the agent developer Permission Set role in `dev` and `cdv`. No a Forward Access Session call. No AWS service acting on your behalf. Important trade-off The exception is identity-based, not sandbox-only. The same credentials may also work through CLI or SDK, subject to IAM permissions. Production does not get this developer exception. 5
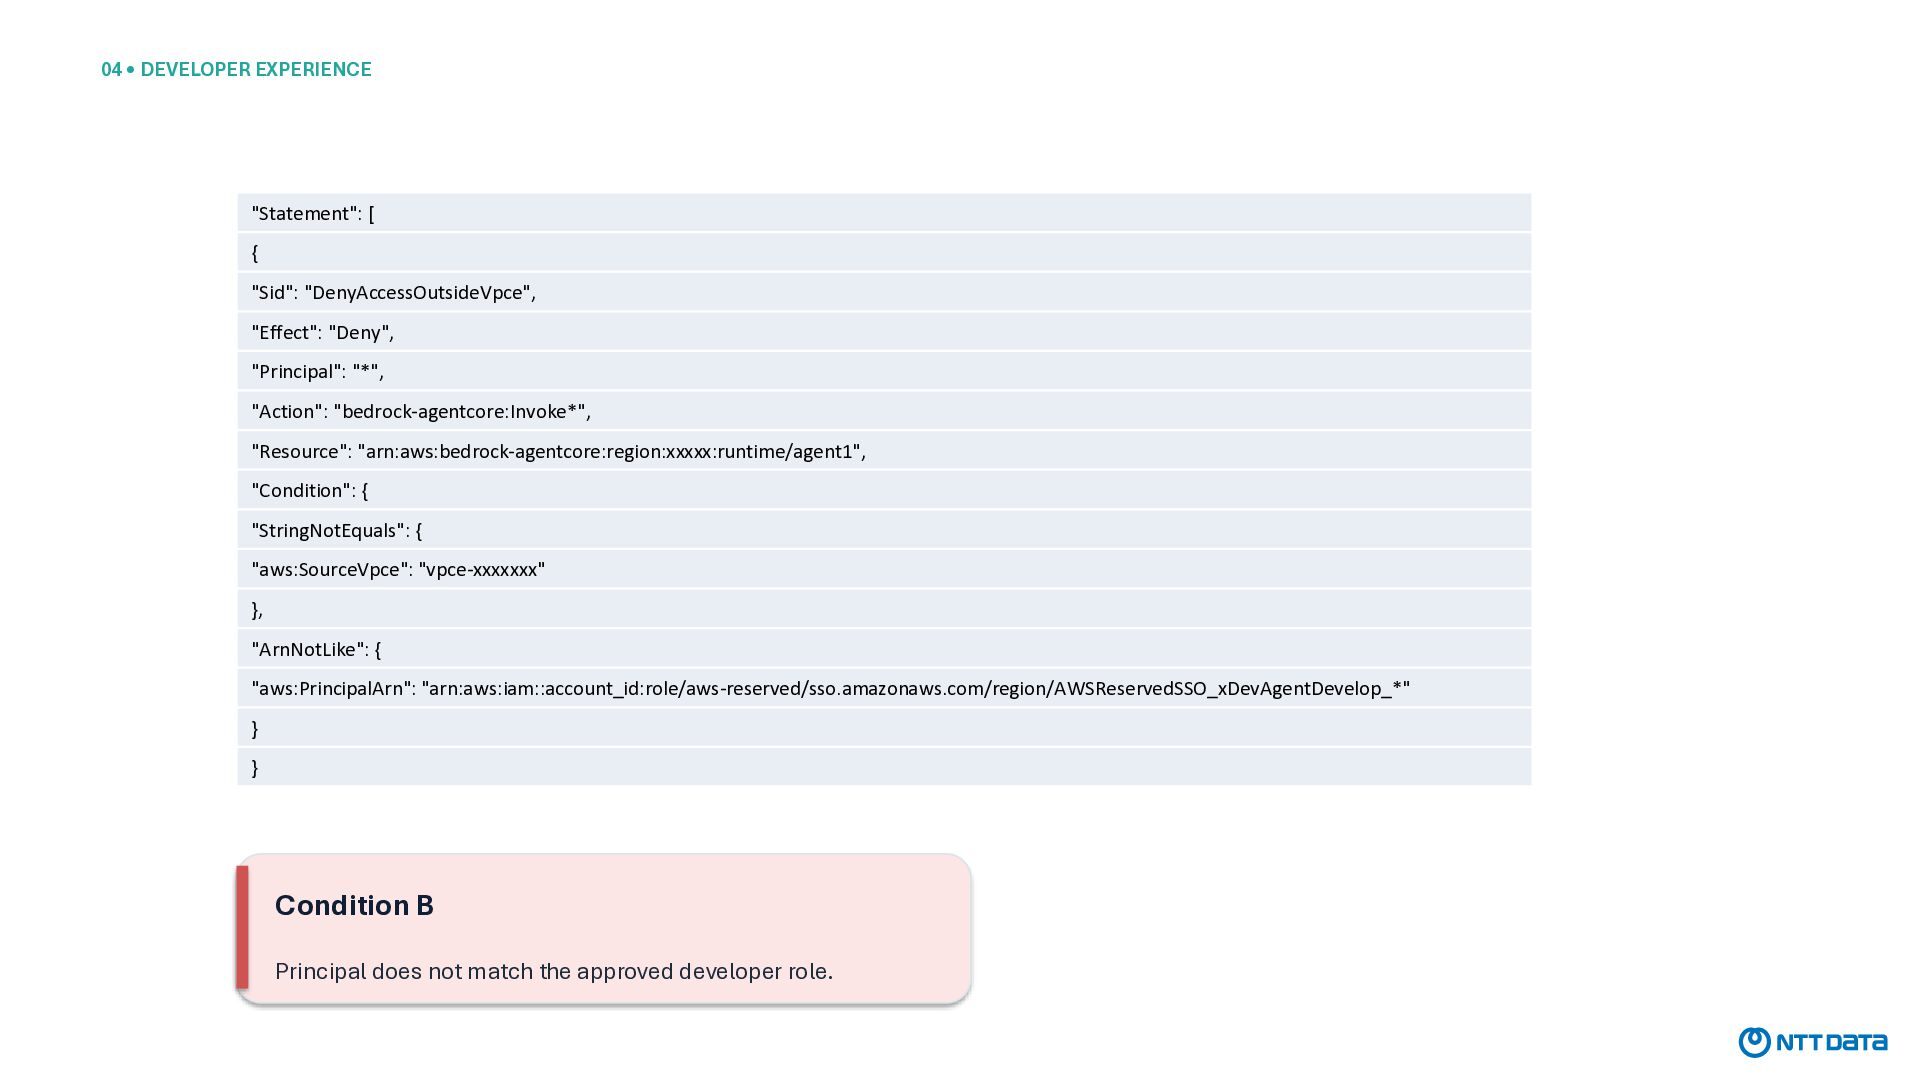
  10. 04 • DEVELOPER EXPERIENCE "Statement": [ { "Sid": "DenyAccessOutsideVpce", "Effect":

    "Deny", "Principal": "*", "Action": "bedrock-agentcore:Invoke*", "Resource": "arn:aws:bedrock-agentcore:region:xxxxx:runtime/agent1", "Condition": { "StringNotEquals": { "aws:SourceVpce": "vpce-xxxxxxx" }, "ArnNotLike": { "aws:PrincipalArn": "arn:aws:iam::account_id:role/aws-reserved/sso.amazonaws.com/region/AWSReservedSSO_xDevAgentDevelop_*" } } Condition B Principal does not match the approved developer role.
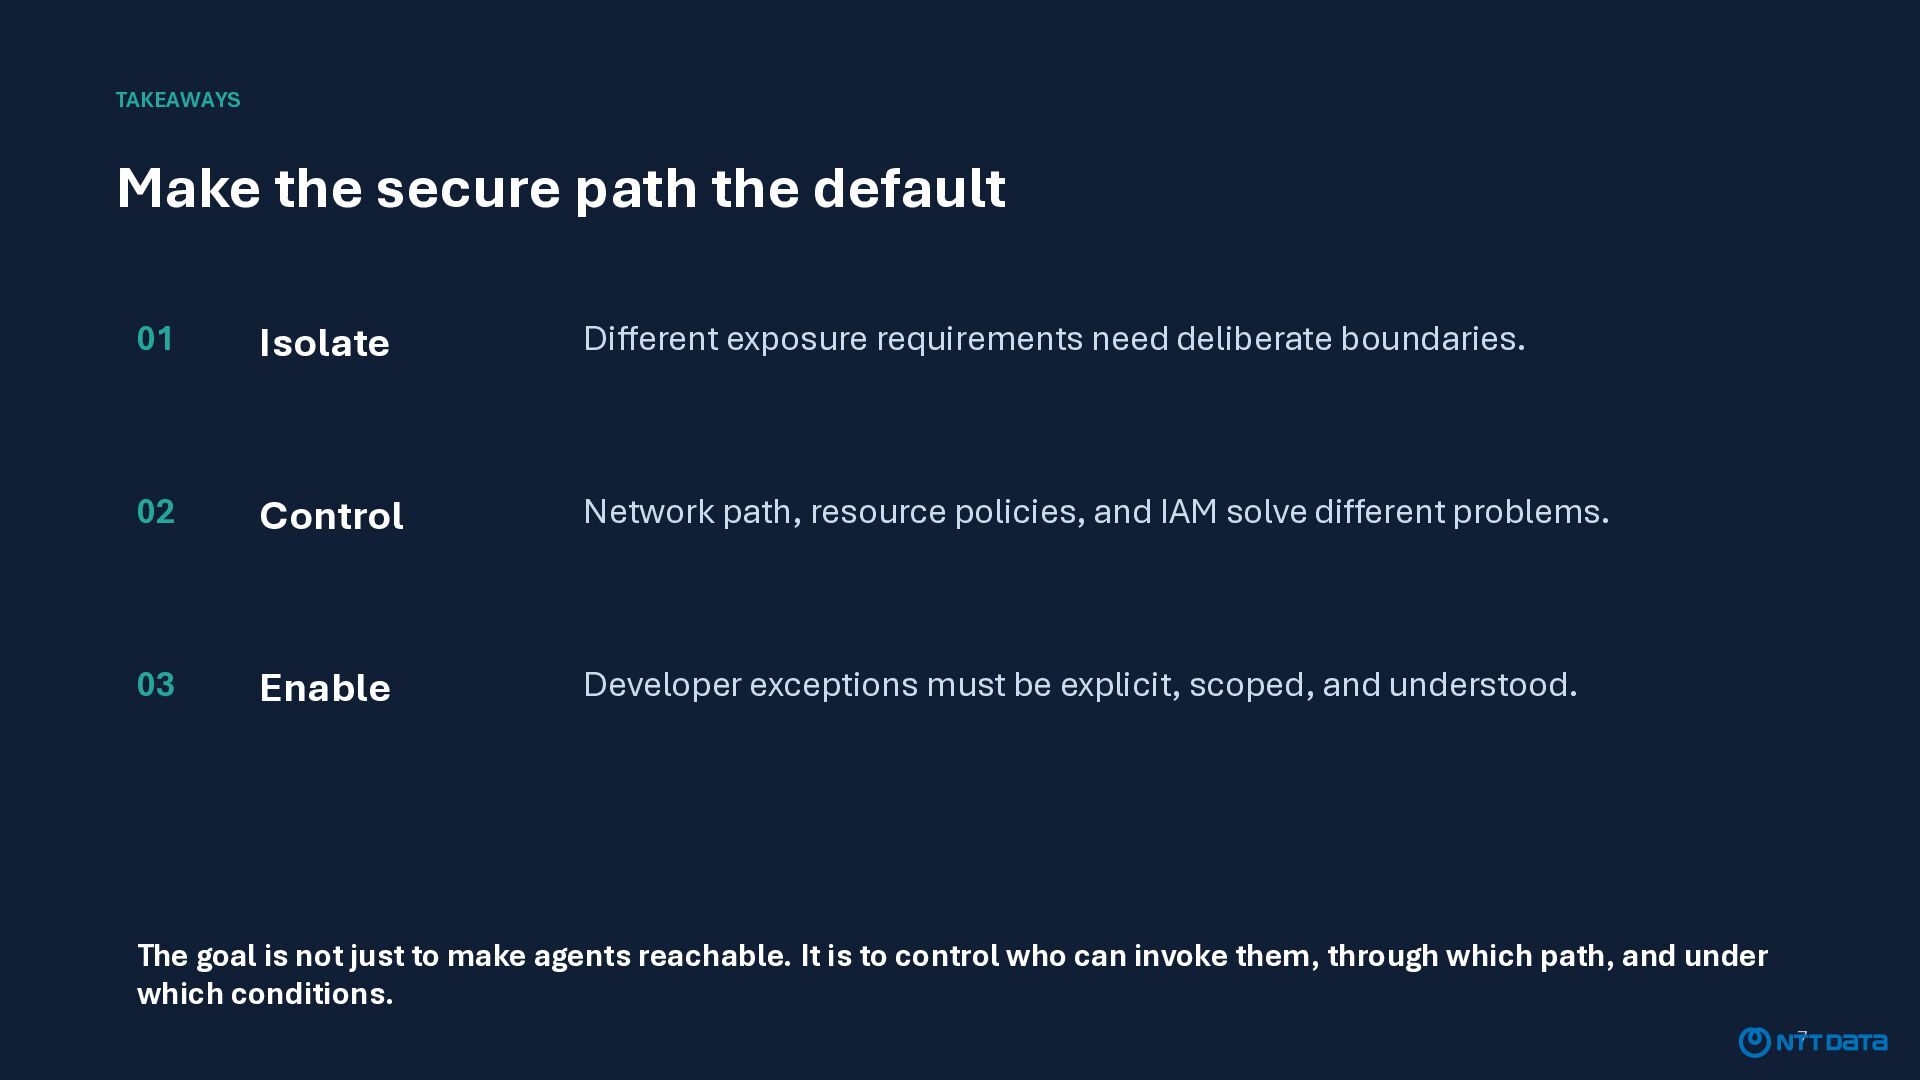
  11. TAKEAWAYS Make the secure path the default 01 Isolate Different

    exposure requirements need deliberate boundaries. 02 Control Network path, resource policies, and IAM solve different problems. 03 Enable Developer exceptions must be explicit, scoped, and understood. The goal is not just to make agents reachable. It is to control who can invoke them, through which path, and under which conditions. 7