years ▪Helped architect and build Creative Cloud @ Adobe ▪Cut my teeth on “the cloud” at Netflix ▪UNIX and Linux throat beard for >20 years ▪Have been involved in countless security and production incidents, most at 2:00 AM ▪I now talk to people about security for a living ▪Live in Silicon Valley ▪I’m completely addicted to building Raspberry Pi 2’s for random things around the house 3
have started at least once EC2 instance ▪You have basic familiarity with AWS IAM ▪You have a browser open to the AWS Console and/or have a Terminal open with aws-‐cli installed, configured and ready to go ▪Hacking in class is not only allowed, it’s encouraged! ▪And above all else, PLEASE INTERRUPT ME 8
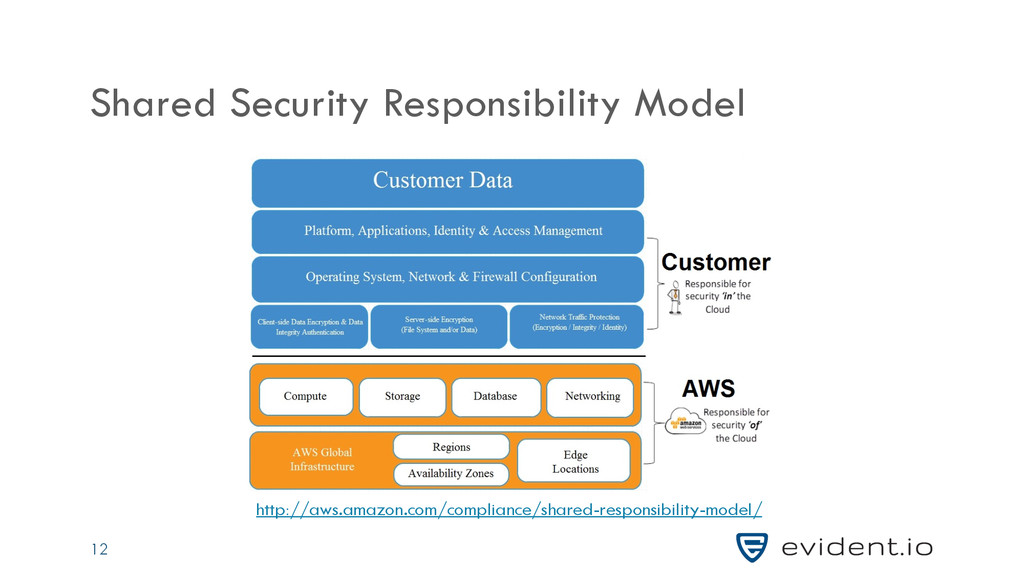
things physical ▪They build the services and APIs you need to deploy and run your applications on AWS ▪They deliver to their customers the ability to create identity credentials to access AWS services and resources ▪They secure the hypervisor and the network below layer 7 13
and their authentication tokens ▪Creating and managing IAM access policies ▪Creating and managing network access to EC2 instances and VPC networks ▪Deploying applications and creating virtual infrastructure ▪OS Patching and Maintenance ▪Monitoring activity and collecting data ▪Designing for failure 14
best ally if you don’t have an explicit “Cloud Security” Architect/Engineer ▪DevOps can play a major role ▪Engage AWS Support often and early (more on that later) ▪Come armed with data (also more on that later) ▪Download latest CSA Guidance, Domain 9 “Incident Response” https://cloudsecurityalliance.org/research/security-guidance/ 22
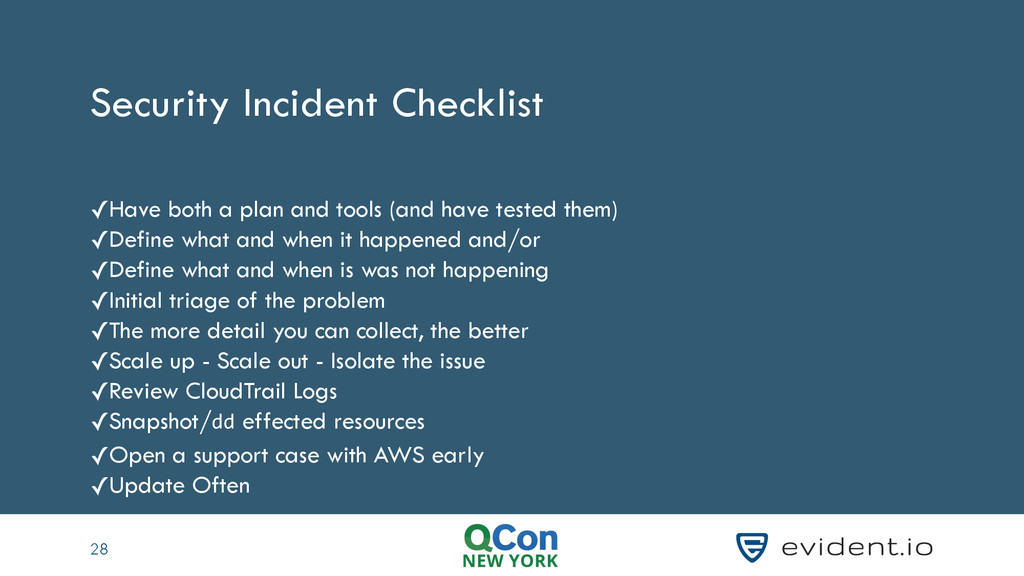
have tested them) ✓Define what and when it happened and/or ✓Define what and when is was not happening ✓Initial triage of the problem ✓The more detail you can collect, the better ✓Scale up - Scale out - Isolate the issue ✓Review CloudTrail Logs ✓Snapshot/dd effected resources ✓Open a support case with AWS early ✓Update Often 28
likely, you don’t even know it’s going on ▪Sometimes, an email from the AWS Security will come in that an attack is originating from one of your EC2 instances ▪Preventative tools like Evident.io can help reduce the amount of surprises ▪Dev accounts are just as important to secure as production 30
▪Most common type of attack ▪EC2 IP address space is public https://ip-ranges.amazonaws.com/ip-ranges.json ▪Security Group rules are too open ▪Vulnerable applications ▪Vulnerable operating systems ▪Instances in unused regions (look for micros) ▪AutoScaling gone wild 31
▪Exposed and compromised API Access Keys ▪New users/roles ▪Deleted users/roles ▪IAM policy changes ▪Root user locked out ▪AWS resources being created or deleted ▪Costs going up trough the roof 32
▪Can provide you guidance on ▪Scaling up ▪Scaling out ▪Isolating the issue ▪May shift traffic to help ▪Can provide you forensic image for analysis in AWS 37
Support in your incident response program ▪If you are an Enterprise Support customer, include your TAM ▪On occasion, an AWS Support person can be on your call ▪Always report abuse and security issues to AWS Support, their support center is bigger than yours! 38
sure you have data for ▪AWS infrastructure and resource state (Evident.io can help) ▪AWS Activity and events (CloudTrail) ▪OS and Application state (FIM) ▪S3 buckets (S3 Logs) ▪ELBs (ELB Logs) 41
for events on AWS resources ▪CloudTrail produces tons of data, be prepared to sift through it ▪Send CloudTrail data to a centralized bucket for easy consumption into log aggregation systems ▪AWS may request CloudTrail data during an incident ▪Protect your CloudTrail buckets as if they had customer sensitive PII 42
enforcement may want later ▪Create EBS snapshot or AMI from affected instance ▪Use an isolated VPC with no route to the internet to bring up and test 43
the last known good state ▪Immutable AMIs are also helpful in restoring operating systems and applications ▪CloudFormation templates for infrastructure management ▪Test your CI/CD pipeline 46
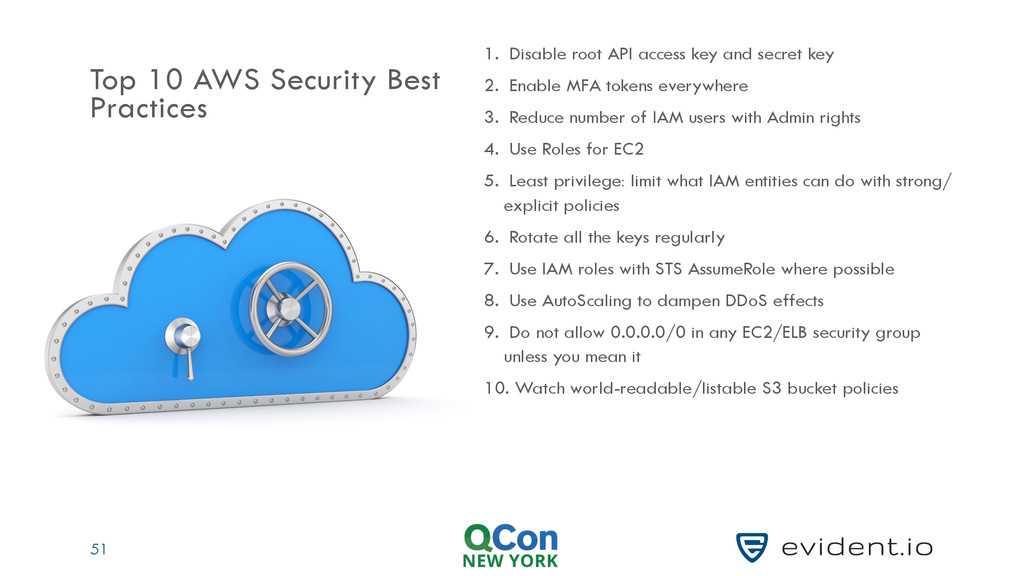
API access key and secret key 2. Enable MFA tokens everywhere 3. Reduce number of IAM users with Admin rights 4. Use Roles for EC2 5. Least privilege: limit what IAM entities can do with strong/ explicit policies 6. Rotate all the keys regularly 7. Use IAM roles with STS AssumeRole where possible 8. Use AutoScaling to dampen DDoS effects 9. Do not allow 0.0.0.0/0 in any EC2/ELB security group unless you mean it 10. Watch world-readable/listable S3 bucket policies
has no restrictions ▪Create administrative IAM users ▪Use Roles for EC2 (#4) ▪Make sure billing and contact questions are filled out ▪Bonus: Set up MFA on root and throw away the key! 52
factor to the authentication step ▪MFA is assigned to root account and IAM users ▪Can be assigned to roles ▪Physical or virtual ▪Virtual has choices (Google Authenticator, Authy, etc.) 53
many people have the keys to your kingdom? ▪Not just people - apps ▪Review IAM policies on Users, Groups and Roles ▪Remember #1 ▪Consider Identity Federation 54
need to contact other AWS Services? ▪AWS SDKs and aws-cli support EC2 Roles ▪Reduced attack surface area ▪Secure DevOps on EC2 ▪Create an EC2 specific role ▪Assign a specific policy to that role ▪Launch an EC2 instance with that role ▪Easy to test with aws-cli on EC2 55
amount of privilege to get the job done ▪IAM can get very granular ▪Works in tandem with #4 on EC2 ▪Should be applied to all automated workflows, too ▪Very specific IAM policies - only allow what you mean ▪IAM managed policies make this easier ▪Use the IAM policy generator and policy simulator to help 56
are very annoying and can cost your business dearly ▪IAM users should have keys rotated every 90 days minimum ▪Mostly useful for when Roles for EC2 won’t work in automated workflows Sample process: ▪Track age of Access Keys ▪Create new key ▪Supply key to automation process ▪Test ▪Deactivate old key 57
EC2 Roles ▪Can be used in place of privileged IAM user Access Keys ▪Temporary credentials ▪Allows for 3rd parties such as Evident.io to access your AWS accounts more securely ▪Extended version of AssumeRole allows for Identity Federation 58
to increase number of EC2 instances automatically ▪More instances means site stays up ▪Small price to pay for site reliability ▪You may need a temporary increase in EC2 limits ▪You may need to temporarily increase desired number of instances in ASG ▪Work with AWS, they may be able to help you on the network edge 59
you really mean it ▪Like leaving the door wide open ▪EC2 IP address range is a favorite for scanners ▪Monitor Security Groups regularly (HINT: Evident.io can help) ▪Affects not just EC2 instances, but: ▪ELBs ▪RDS Database Servers ▪ElastiCache Clusters ▪EMR Nodes ▪and others… 60
buckets a favorite for trolling for API Access Keys ▪Check your Bucket ACLs regularly ▪Watch for all grantees, including AuthenticatedUsers ▪Check your Bucket Policies regularly 61


 johnmartinez
 kasada
 yama3133
 knwoop
 nejumi
 yusuke427
 junjikoide
 oidfj
 a_suenami
 kubell_hr
 kaminashi
 sue445
 jackojacko_
 destraynor
 inesmontani
 rakko
 lynnandtonic
 sachag
 baasie
 sstephenson
 katiecoart
 chriscoyier
 tammyeverts
 lara
 nikkihalliwell