Share
Embed

Transcript
83 slides
-
> • Background – Autonomous vehicle – Instances – Protocols
• OMA DM – Parser problems – Self-defined – Inconsistency • Summary – Recap – Suggestion – Resource -
> NotSurprised Intro • UCCU Hacker • AIS3 2016 trainee
• HITCON Defend 2018 3rd (etc.) • SITCON 2019 speaker • HITCON 2019 training • ITRI Engineer (serve my country) • 5-years Bachelor & Master of NSYSU Email : [email protected] Skill • Windows Kernel Driver (Minifilter) • Penetration Test (Web) • Malware Analysis (Ransomware) • Ethereum Smart Contract (Solidity) • Car Security (OMA DM) -
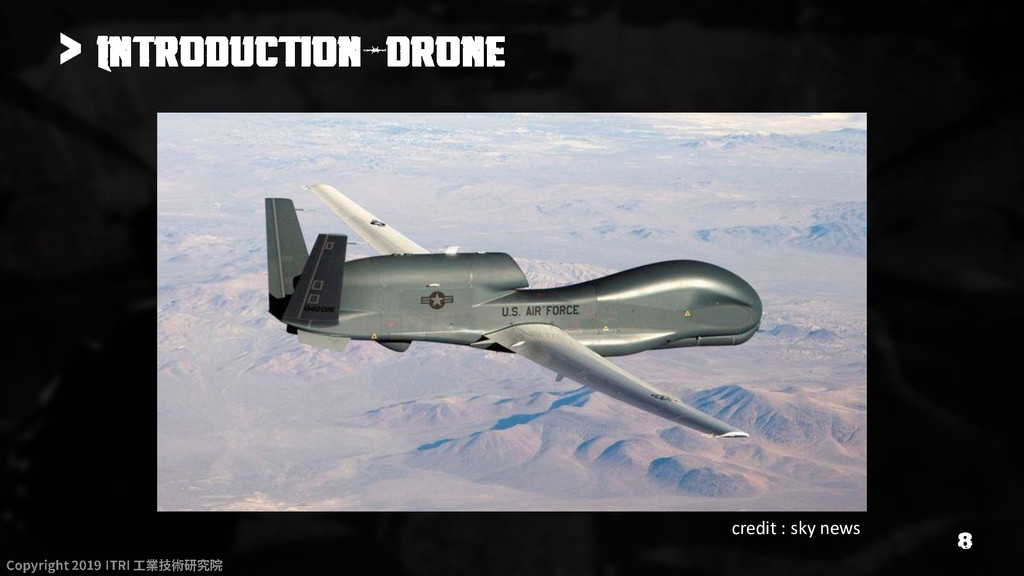
> Drone, IoT, AI Manufacture, AI Car(VANET) sounds great, but…
Are They Secure? -
> • G-force – Ace pilot should tolerate 9G for
15s – If pilot cannot keep blood in head • Greyout • Tunnel vision • Blackout • G-LOC • Spoofing IFF (Identification, friend or foe) affiliation to single aircraft or AWACS -
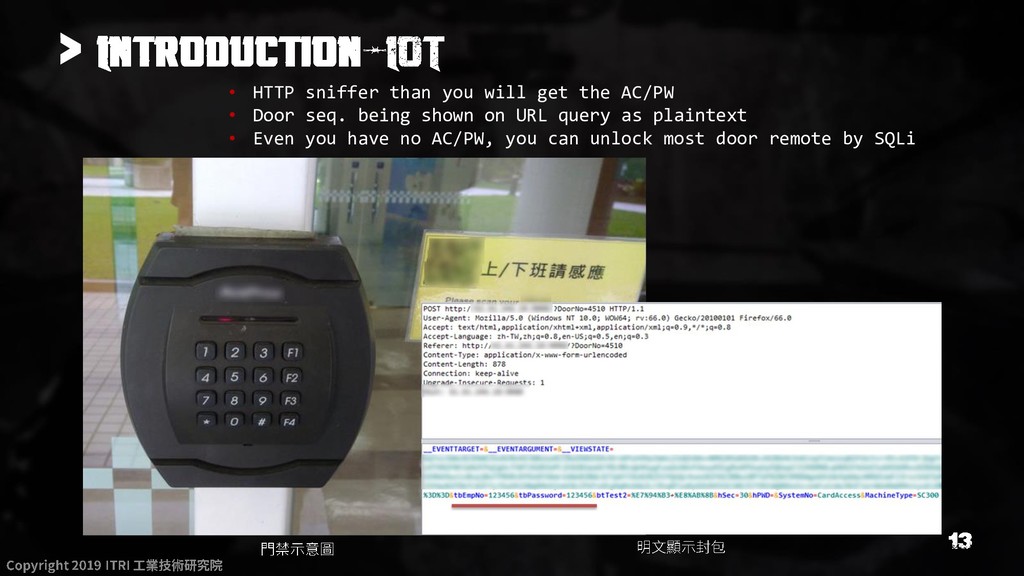
> • HTTP sniffer than you will get the AC/PW
• Door seq. being shown on URL query as plaintext • Even you have no AC/PW, you can unlock most door remote by SQLi -
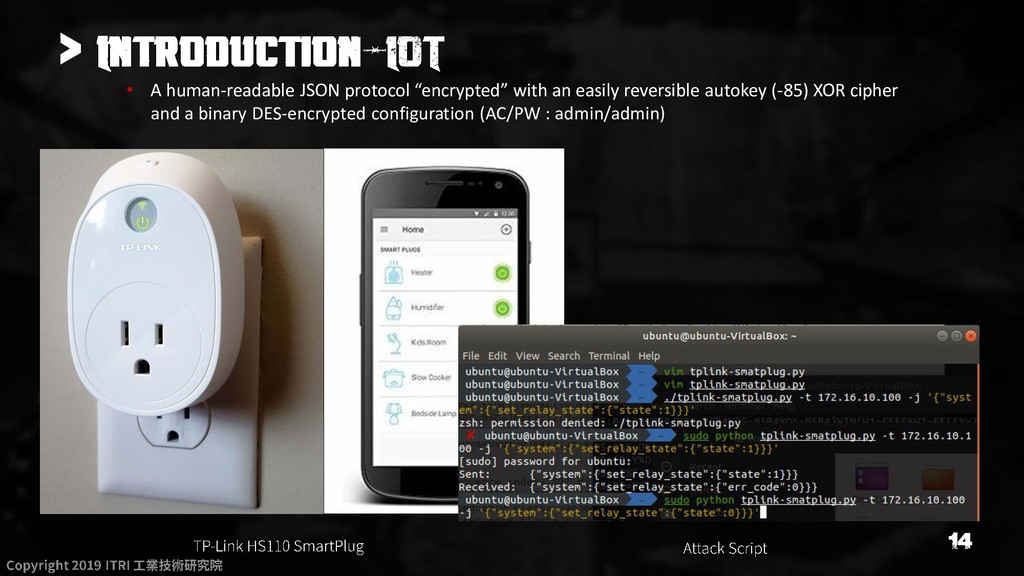
> • A human-readable JSON protocol “encrypted” with an easily
reversible autokey (-85) XOR cipher and a binary DES-encrypted configuration (AC/PW : admin/admin) -
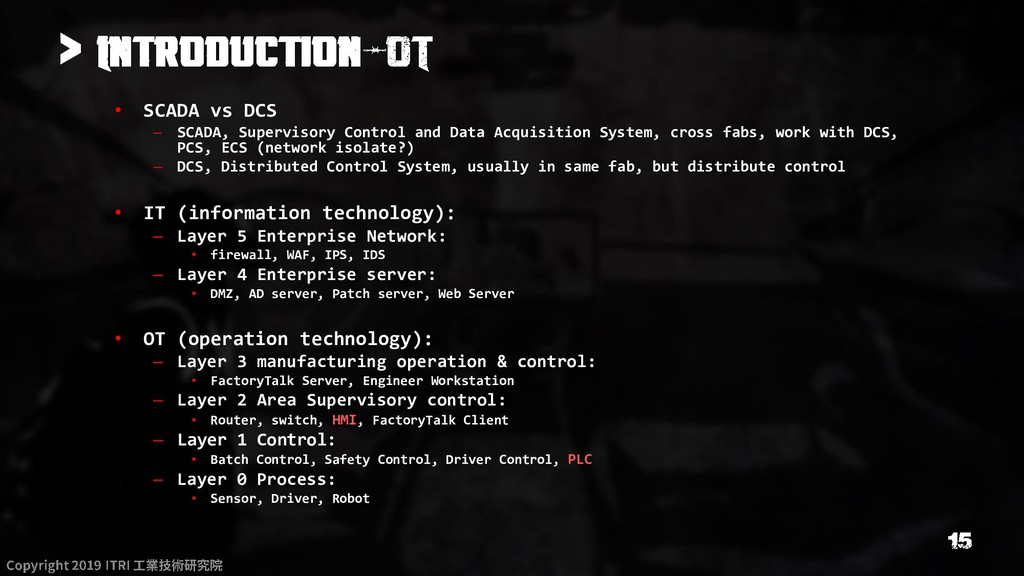
> • SCADA vs DCS – SCADA, Supervisory Control and
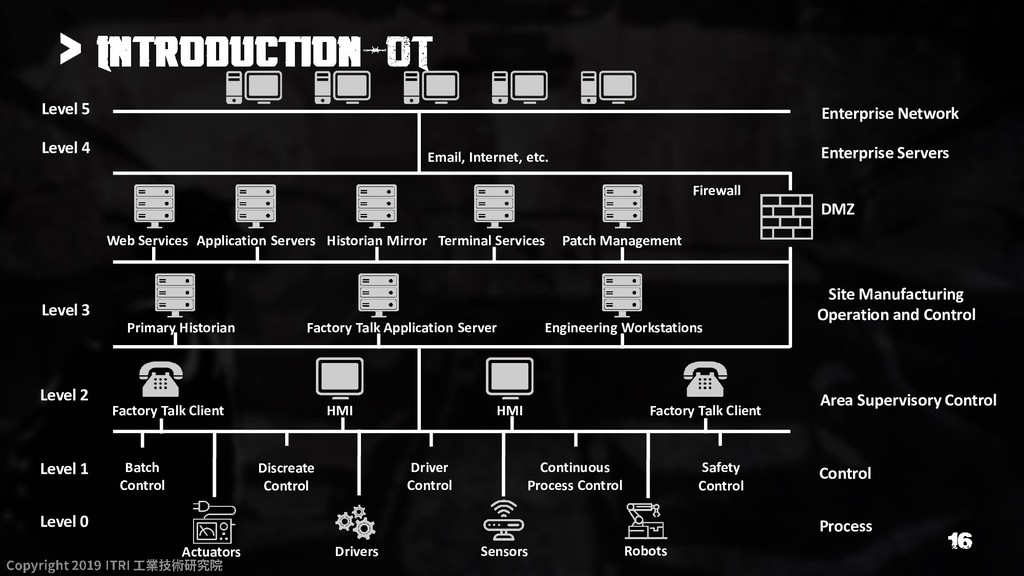
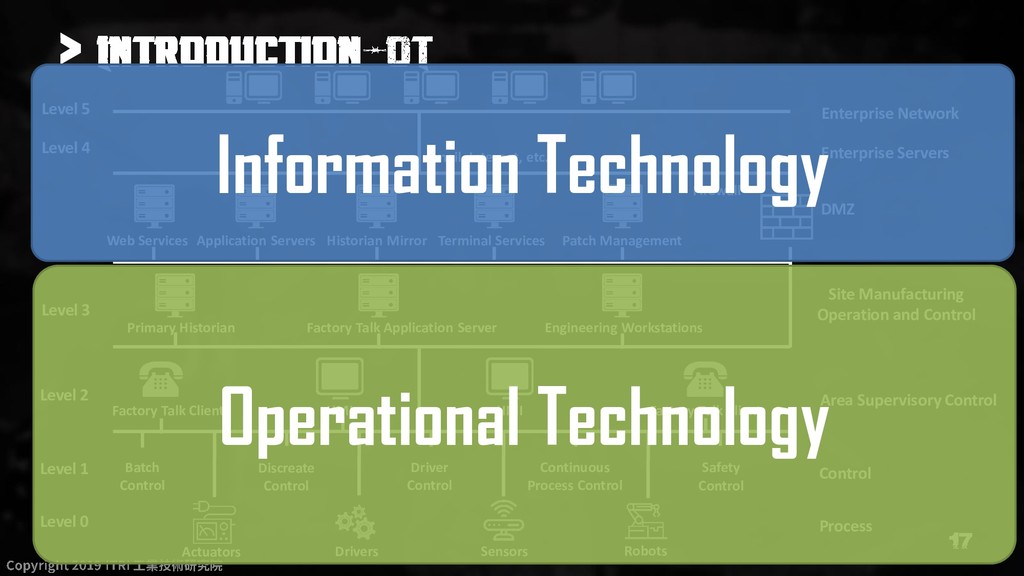
Data Acquisition System, cross fabs, work with DCS, PCS, ECS (network isolate?) – DCS, Distributed Control System, usually in same fab, but distribute control • IT (information technology): – Layer 5 Enterprise Network: • firewall, WAF, IPS, IDS – Layer 4 Enterprise server: • DMZ, AD server, Patch server, Web Server • OT (operation technology): – Layer 3 manufacturing operation & control: • FactoryTalk Server, Engineer Workstation – Layer 2 Area Supervisory control: • Router, switch, HMI, FactoryTalk Client – Layer 1 Control: • Batch Control, Safety Control, Driver Control, PLC – Layer 0 Process: • Sensor, Driver, Robot -
> Level 5 Level 4 Level 3 Level 2 Level
1 Level 0 Enterprise Network Enterprise Servers Site Manufacturing Operation and Control Area Supervisory Control Control Process DMZ Email, Internet, etc. Web Services Application Servers Historian Mirror Firewall Terminal Services Patch Management Primary Historian Factory Talk Application Server Engineering Workstations Factory Talk Client HMI Factory Talk Client HMI Batch Control Discreate Control Driver Control Continuous Process Control Safety Control Actuators Drivers Sensors Robots -
> Level 5 Level 4 Level 3 Level 2 Level
1 Level 0 Enterprise Network Enterprise Servers Site Manufacturing Operation and Control Area Supervisory Control Control Process DMZ Email, Internet, etc. Web Services Application Servers Historian Mirror Firewall Terminal Services Patch Management Primary Historian Factory Talk Application Server Engineering Workstations Factory Talk Client HMI Factory Talk Client HMI Batch Control Discreate Control Driver Control Continuous Process Control Safety Control Actuators Drivers Sensors Robots Information Technology Operational Technology -
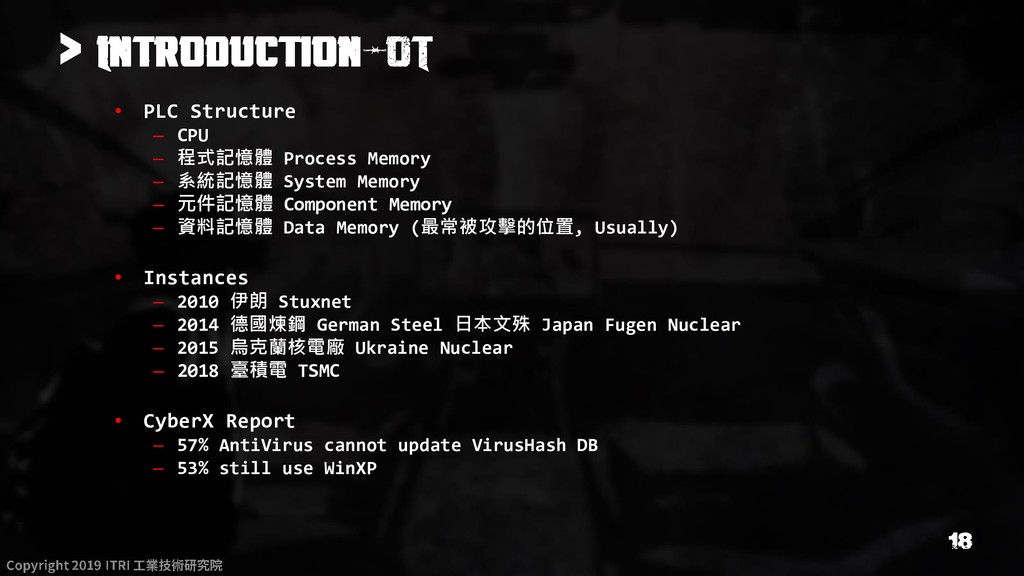
> • PLC Structure – CPU – 程式記憶體 Process Memory
– 系統記憶體 System Memory – 元件記憶體 Component Memory – 資料記憶體 Data Memory (最常被攻擊的位置, Usually) • Instances – 2010 伊朗 Stuxnet – 2014 德國煉鋼 German Steel 日本文殊 Japan Fugen Nuclear – 2015 烏克蘭核電廠 Ukraine Nuclear – 2018 臺積電 TSMC • CyberX Report – 57% AntiVirus cannot update VirusHash DB – 53% still use WinXP -
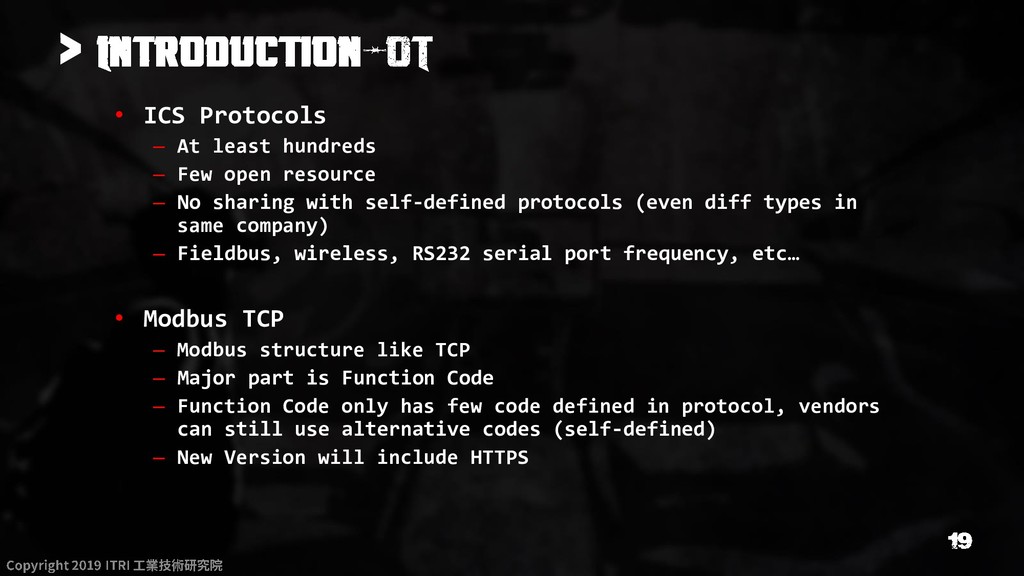
> • ICS Protocols – At least hundreds – Few
open resource – No sharing with self-defined protocols (even diff types in same company) – Fieldbus, wireless, RS232 serial port frequency, etc… • Modbus TCP – Modbus structure like TCP – Major part is Function Code – Function Code only has few code defined in protocol, vendors can still use alternative codes (self-defined) – New Version will include HTTPS -
> • Charlie Miller Jeep Cherokee – Charlie Miller share
series attack vectors • Tencent KeenLab Tesla Model S • ADCD Key Signal repeat – Proof that signals can be simply trigger and enhance to repeat received signals • PWN2OWN 2019 Tesla Model 3 • Car2go Auto Review Application in Chicago – This connect to server problem, review mechanism can be fraud and unlock the car with fake person id -
> • RFID • CAN Bus • Bluetooth • Internet
• VANET • OMA DM -
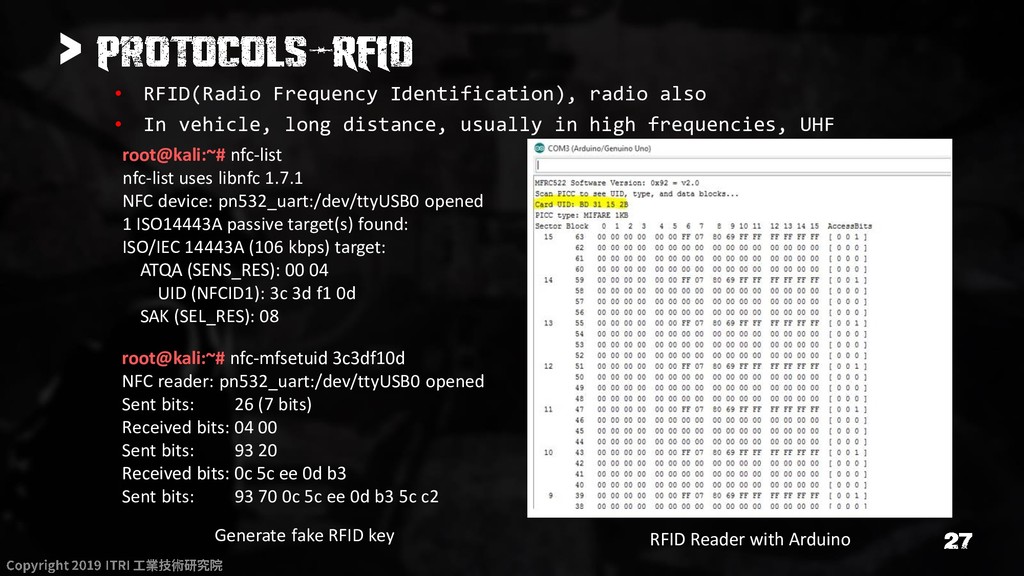
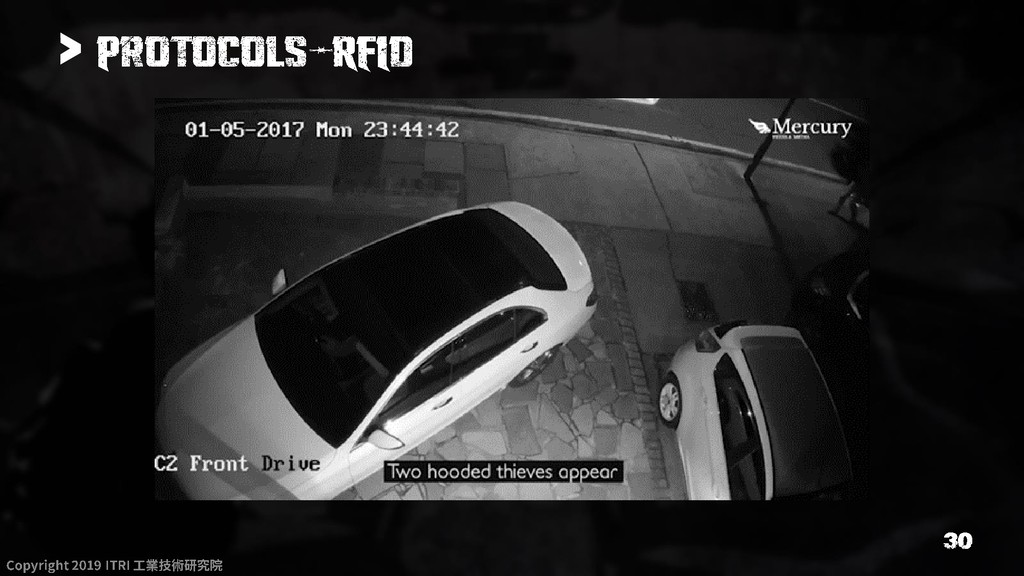
> • RFID(Radio Frequency Identification), radio also • In vehicle,
long distance, usually in high frequencies, UHF root@kali:~# nfc-list nfc-list uses libnfc 1.7.1 NFC device: pn532_uart:/dev/ttyUSB0 opened 1 ISO14443A passive target(s) found: ISO/IEC 14443A (106 kbps) target: ATQA (SENS_RES): 00 04 UID (NFCID1): 3c 3d f1 0d SAK (SEL_RES): 08 root@kali:~# nfc-mfsetuid 3c3df10d NFC reader: pn532_uart:/dev/ttyUSB0 opened Sent bits: 26 (7 bits) Received bits: 04 00 Sent bits: 93 20 Received bits: 0c 5c ee 0d b3 Sent bits: 93 70 0c 5c ee 0d b3 5c c2 Generate fake RFID key RFID Reader with Arduino -
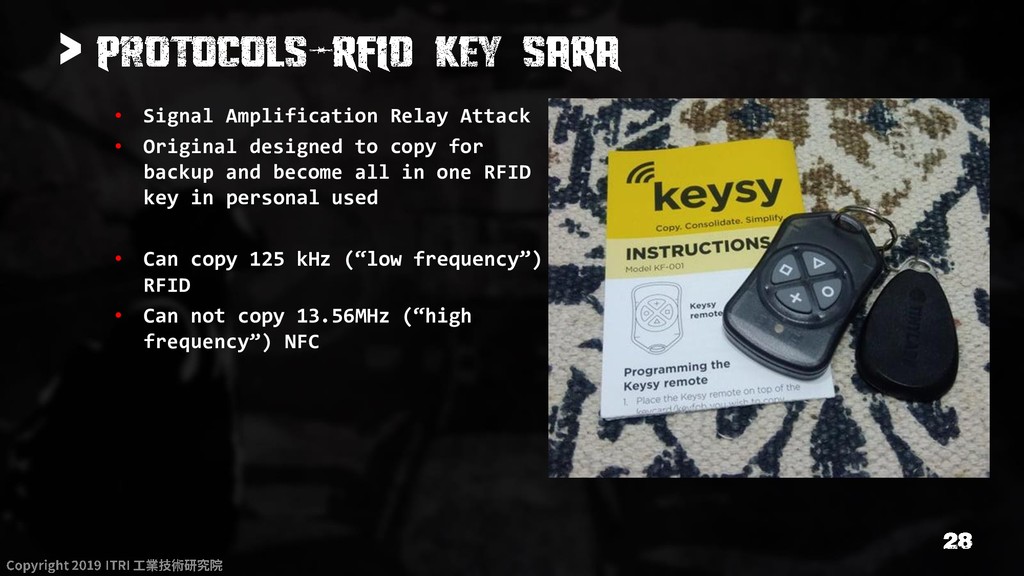
> • Signal Amplification Relay Attack • Original designed to
copy for backup and become all in one RFID key in personal used • Can copy 125 kHz (“low frequency”) RFID • Can not copy 13.56MHz (“high frequency”) NFC -
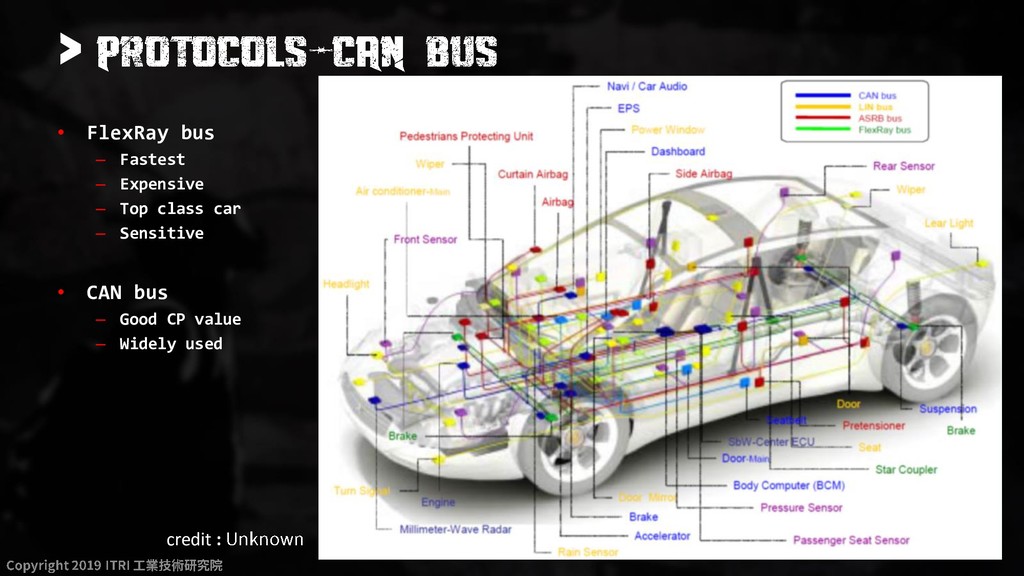
> • FlexRay bus – Fastest – Expensive – Top
class car – Sensitive • CAN bus – Good CP value – Widely used credit : -
> • Best way to get into CAN bus –
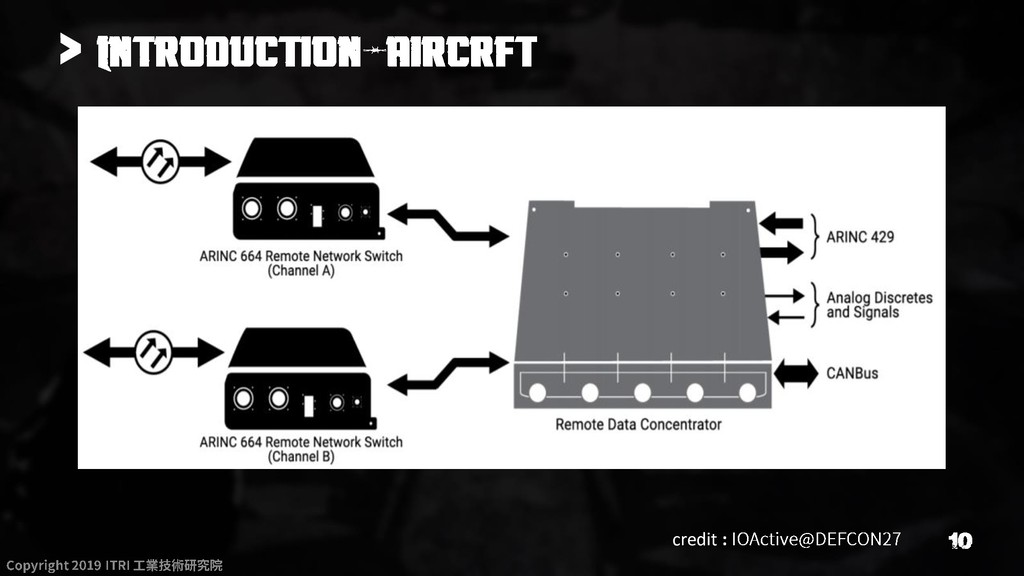
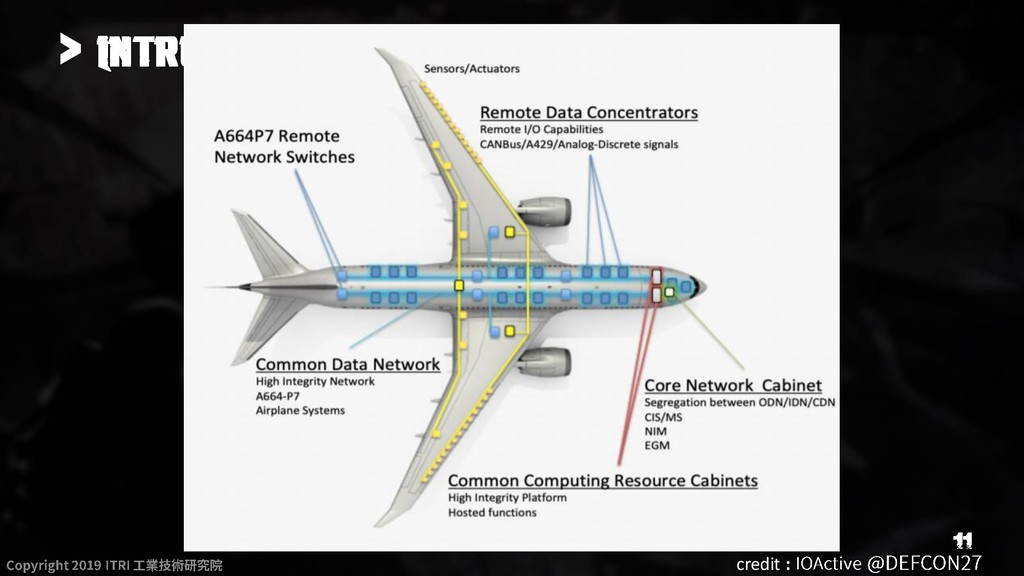
Compromise the car’s mini computer ( OS: QNX ) – As a component in car, mini computer connect to CAN bus and dash board • Message on CAN bus system – CAN message format • ISO 11519-2 / ISO 11898:1993 / ISO 11898:1995 • Make largest privilege code in your broadcast packet – Diagnostic trouble code format • Sometime trigger automatic reaction • Aircraft also use CAN bus – Same problem that microcontroller is the last defend line in simple aircraft -
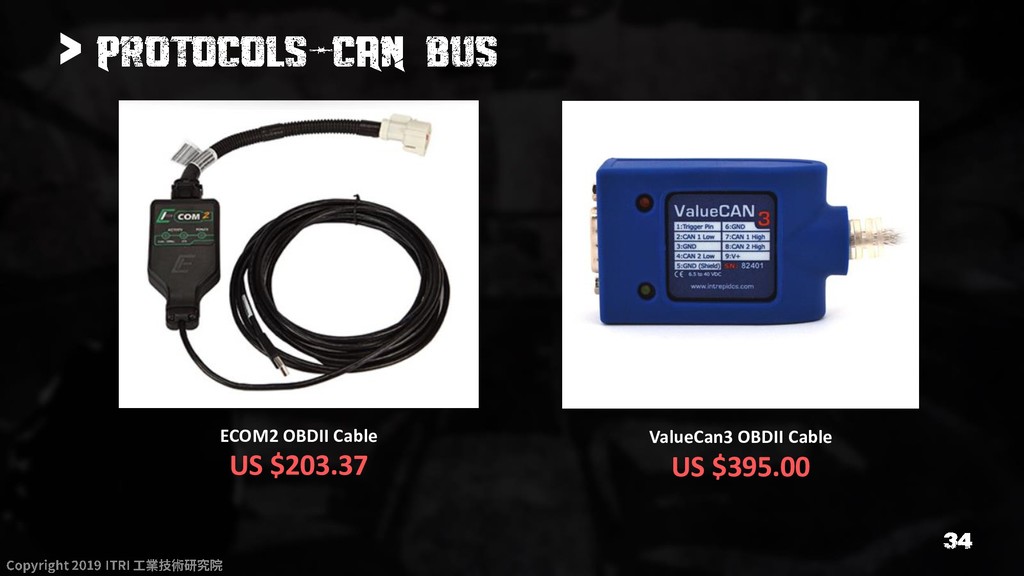
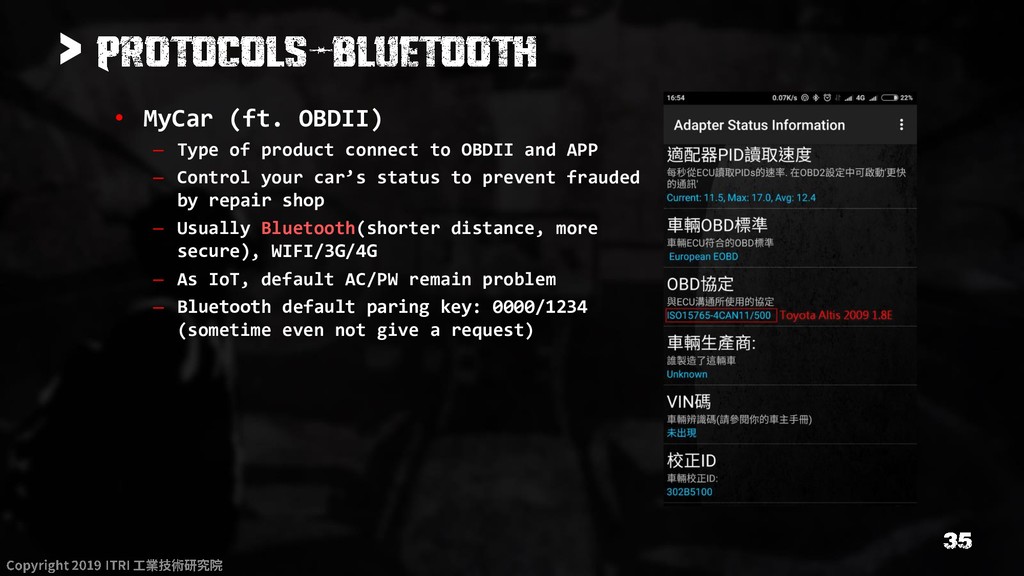
> • MyCar (ft. OBDII) – Type of product connect
to OBDII and APP – Control your car’s status to prevent frauded by repair shop – Usually Bluetooth(shorter distance, more secure), WIFI/3G/4G – As IoT, default AC/PW remain problem – Bluetooth default paring key: 0000/1234 (sometime even not give a request) -
> • Using uuid and handle (company identifier) primary and
characteristic command. • Sometime you can brutal force it or OSINT for hint. • MiBand2 no auth key, MiBand3 has breakable auth key. -
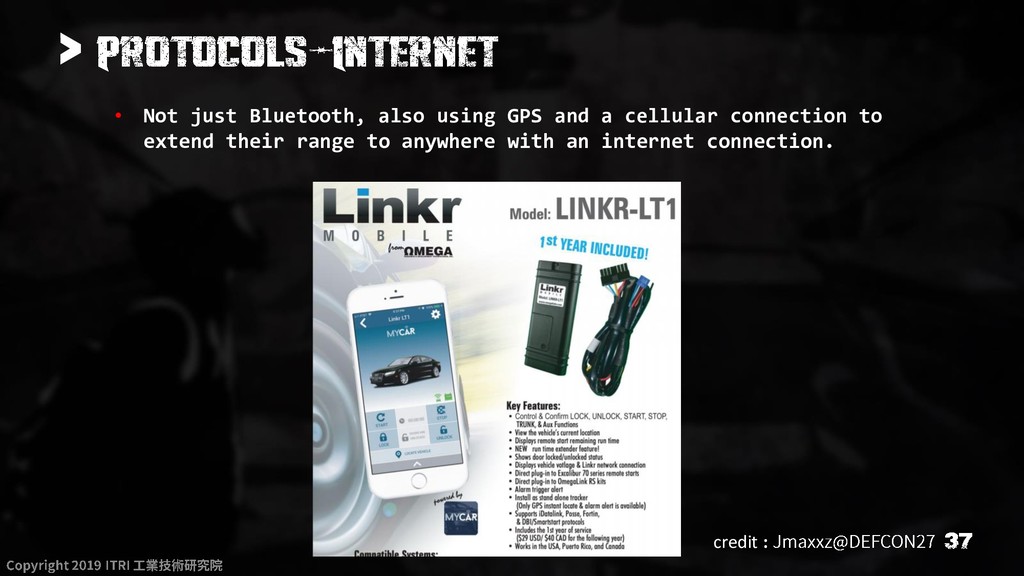
> • Not just Bluetooth, also using GPS and a
cellular connection to extend their range to anywhere with an internet connection. credit : -
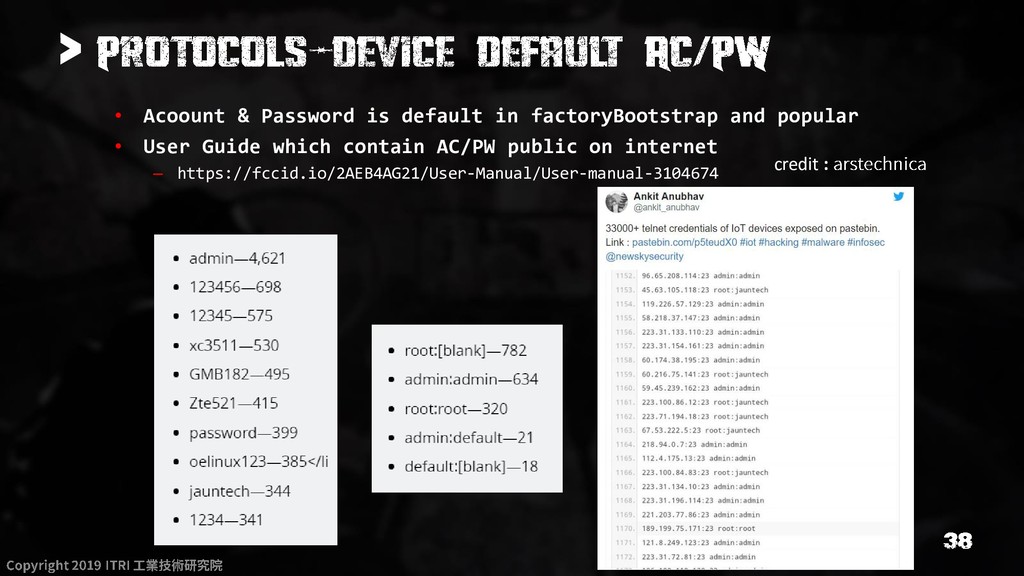
> • Acoount & Password is default in factoryBootstrap and
popular • User Guide which contain AC/PW public on internet – https://fccid.io/2AEB4AG21/User-Manual/User-manual-3104674 credit : -
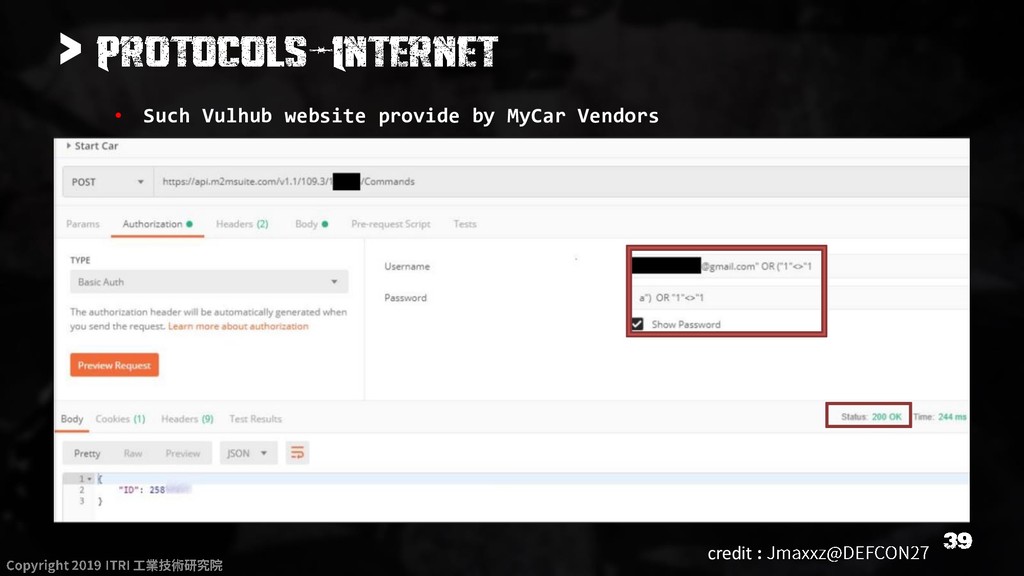
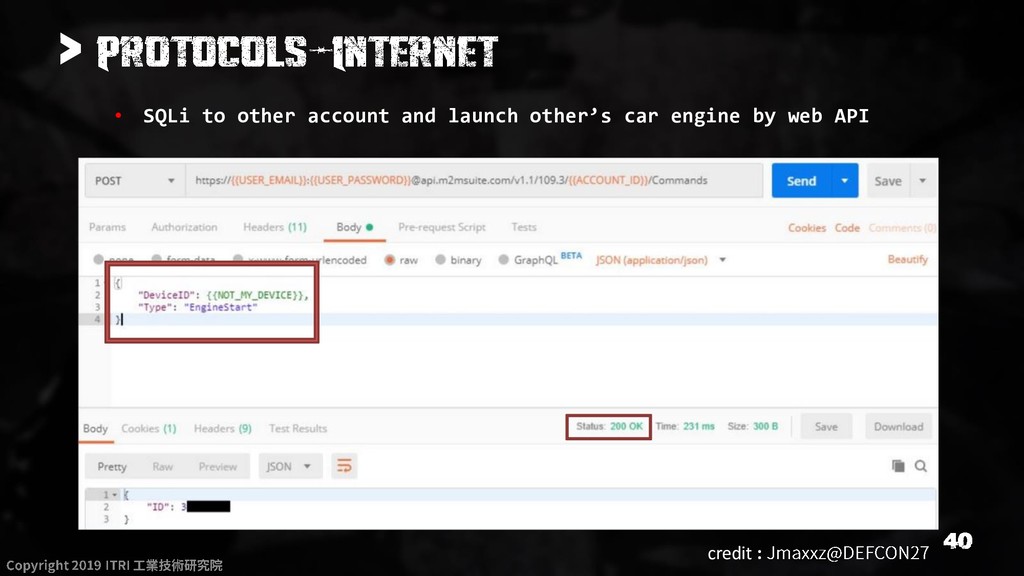
> • SQLi to other account and launch other’s car
engine by web API credit : -
credit : BUG BUG CVE CVE MyCar Vendor MyCar Vendor
MyCar Vendor MyCar Vendor -
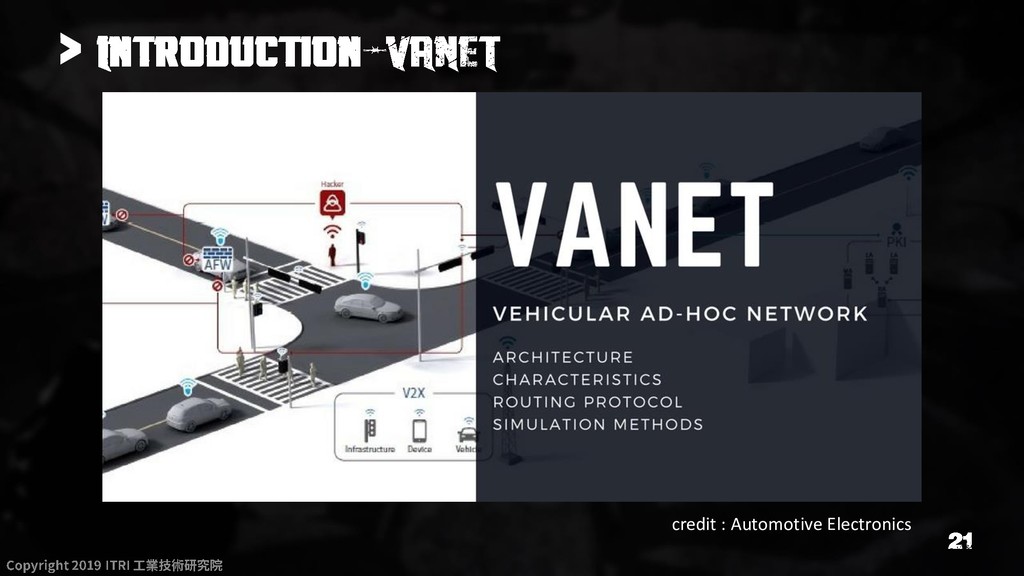
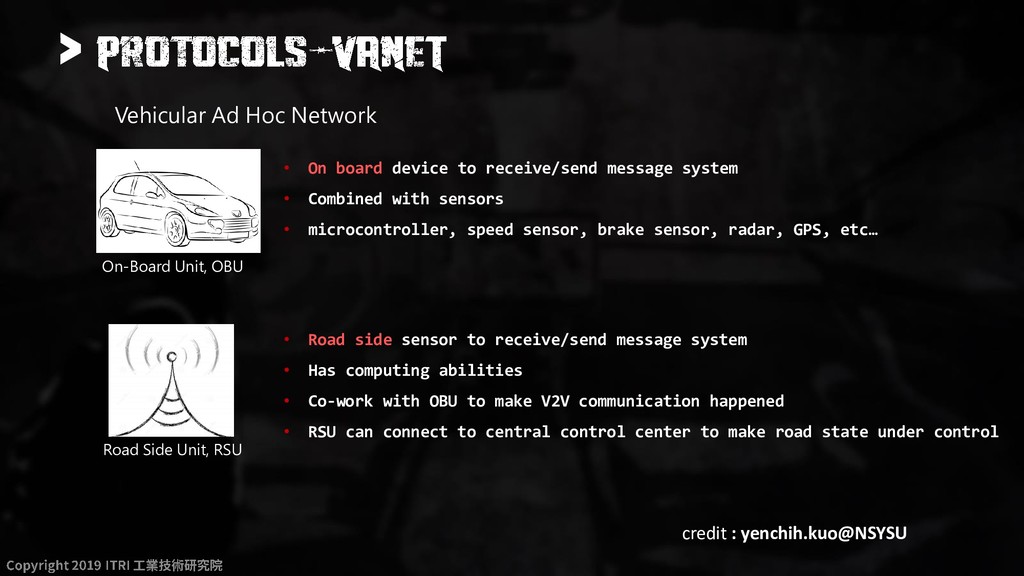
Vehicular Ad Hoc Network On-Board Unit, OBU Road Side Unit,
RSU • On board device to receive/send message system • Combined with sensors • microcontroller, speed sensor, brake sensor, radar, GPS, etc… • Road side sensor to receive/send message system • Has computing abilities • Co-work with OBU to make V2V communication happened • RSU can connect to central control center to make road state under control > credit : yenchih.kuo@NSYSU -
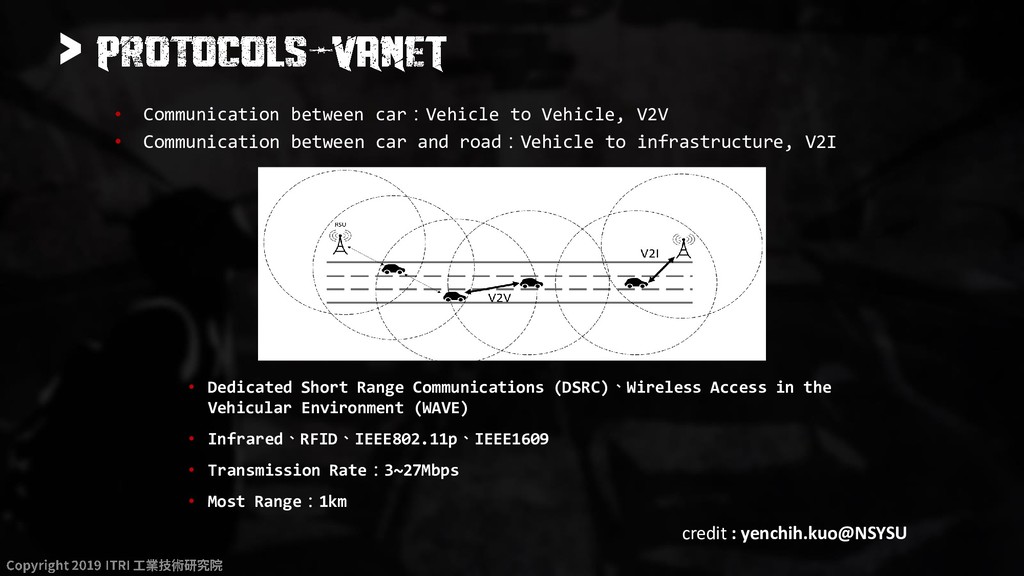
• Communication between car:Vehicle to Vehicle, V2V • Communication between
car and road:Vehicle to infrastructure, V2I • Dedicated Short Range Communications (DSRC)、Wireless Access in the Vehicular Environment (WAVE) • Infrared、RFID、IEEE802.11p、IEEE1609 • Transmission Rate:3~27Mbps • Most Range:1km > credit : yenchih.kuo@NSYSU -
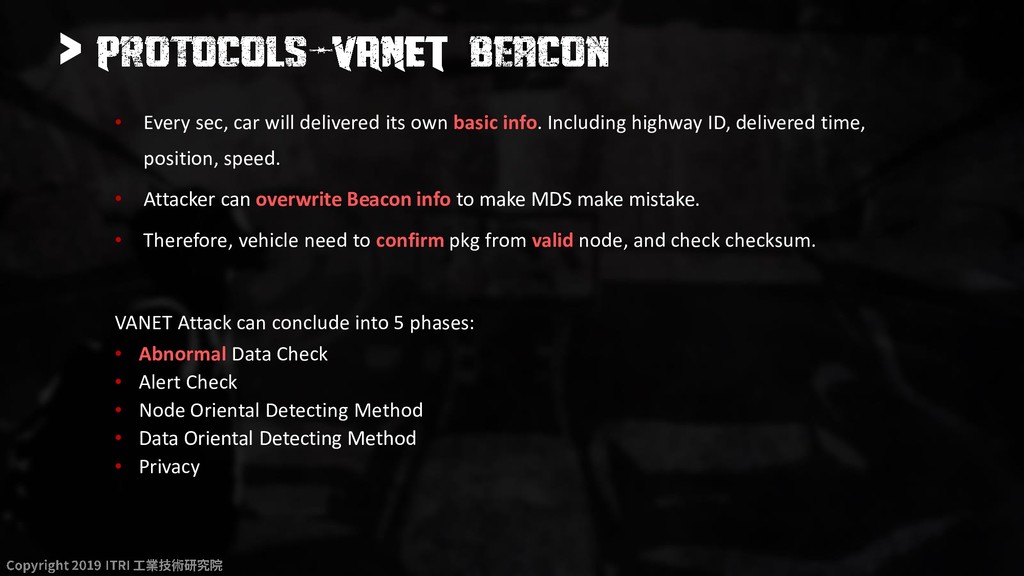
> • Every sec, car will delivered its own basic
info. Including highway ID, delivered time, position, speed. • Attacker can overwrite Beacon info to make MDS make mistake. • Therefore, vehicle need to confirm pkg from valid node, and check checksum. VANET Attack can conclude into 5 phases: • Abnormal Data Check • Alert Check • Node Oriental Detecting Method • Data Oriental Detecting Method • Privacy -
> MobilePhone / Server HMI MicroController HTTP Modbus Canbus Device
PLC ECU No No / TLS1.2 No Strong Normal Weak Lots Few Few *Public Private *Public *Few *Few Lots Remote / Extranet Remote / Extranet Physical / Short-dist / Remote -
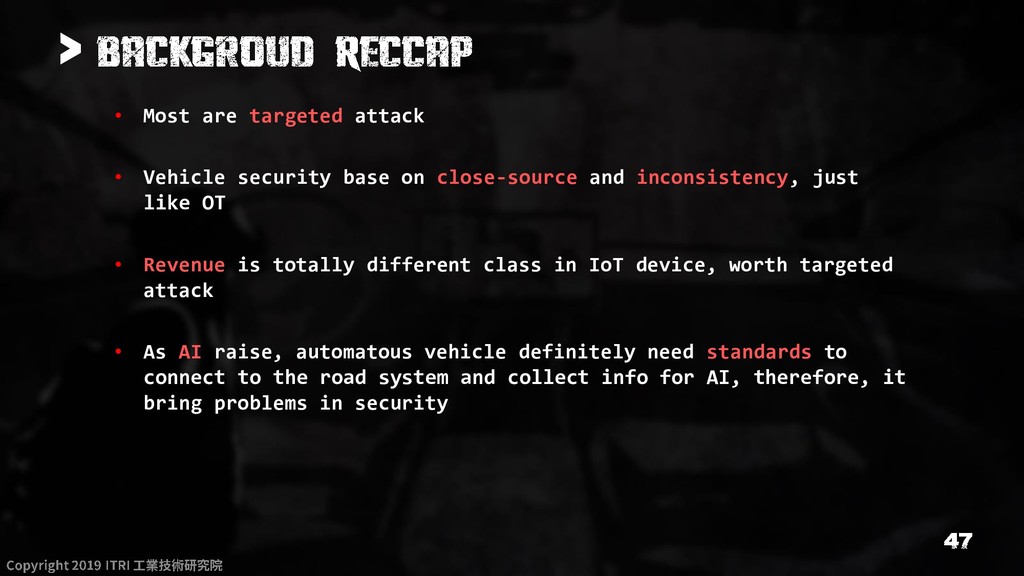
> • Most are targeted attack • Vehicle security base
on close-source and inconsistency, just like OT • Revenue is totally different class in IoT device, worth targeted attack • As AI raise, automatous vehicle definitely need standards to connect to the road system and collect info for AI, therefore, it bring problems in security -
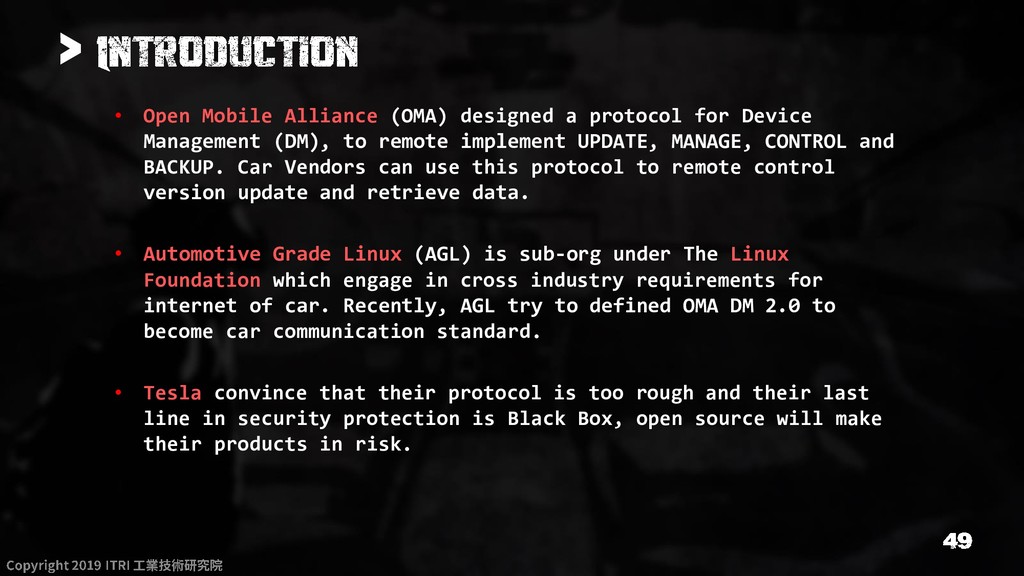
> • Open Mobile Alliance (OMA) designed a protocol for
Device Management (DM), to remote implement UPDATE, MANAGE, CONTROL and BACKUP. Car Vendors can use this protocol to remote control version update and retrieve data. • Automotive Grade Linux (AGL) is sub-org under The Linux Foundation which engage in cross industry requirements for internet of car. Recently, AGL try to defined OMA DM 2.0 to become car communication standard. • Tesla convince that their protocol is too rough and their last line in security protection is Black Box, open source will make their products in risk. -
> • OMA DM is a device management protocol for
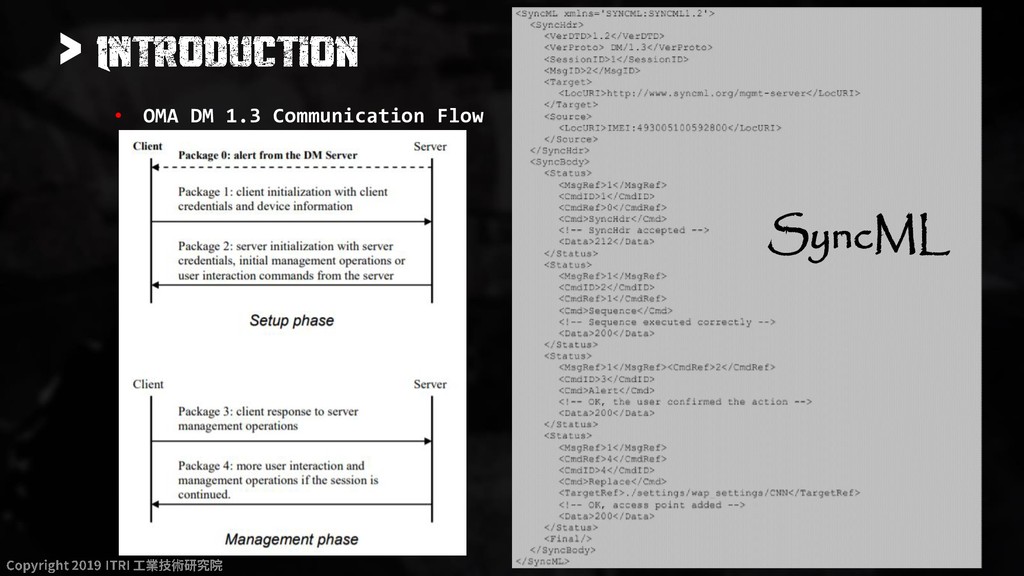
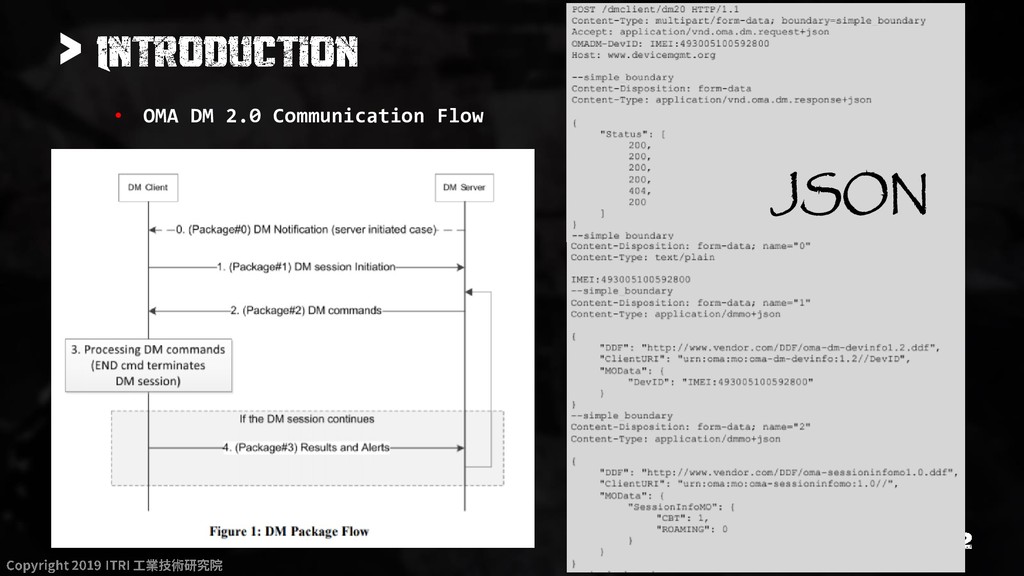
server to control the client device. • OMA DM include following major phases: – Generic device information maintain (DevInfoMO, DmAccMO, DCMO) – Firmware maintain (FUMO) – Software maintain (SCOMO) • OMA DM now has two version release: – OMA DM I (complete) • base on SyncML (Synchronization Markup Language) data format, OMA also give a project as syncml rtk which plays as communication protocol of SyncML – OMA DM II (uncomplete) • base on JSON data format, it simply use HTTP as communicate protocol • only main protocol update to version II, not FUMO, SCOMO, or any else -
> • How to Registration? How to identify response with
Async Report? -
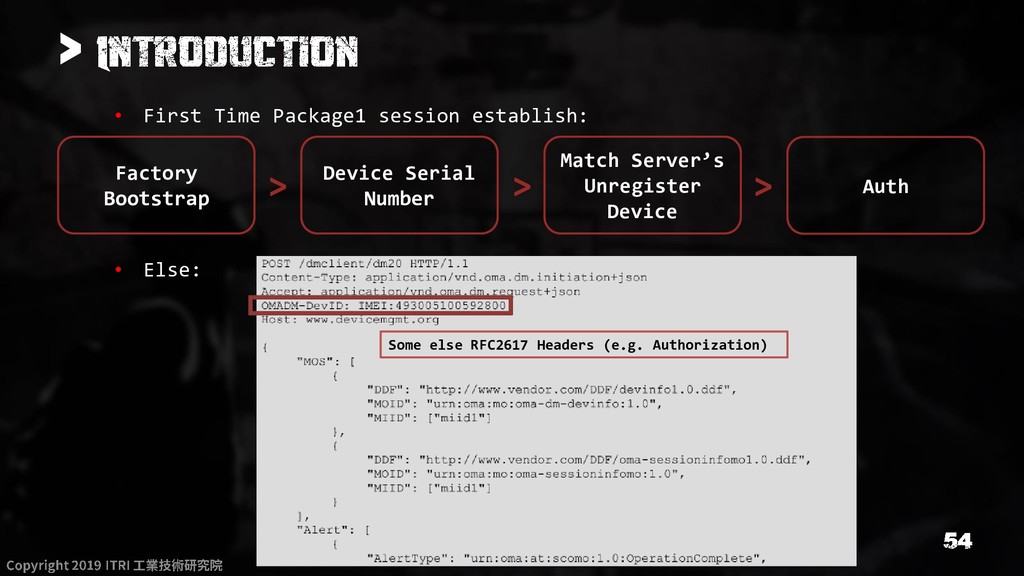
> • First Time Package1 session establish: • Else: Factory
Bootstrap Device Serial Number Match Server’s Unregister Device Auth > > > Some else RFC2617 Headers (e.g. Authorization) -
> • That means registration key is store on microcontroller
DB as un-encrypted state and can be inferred • You can register a fake client just like which we infer door number that mentioned in Section 1 -
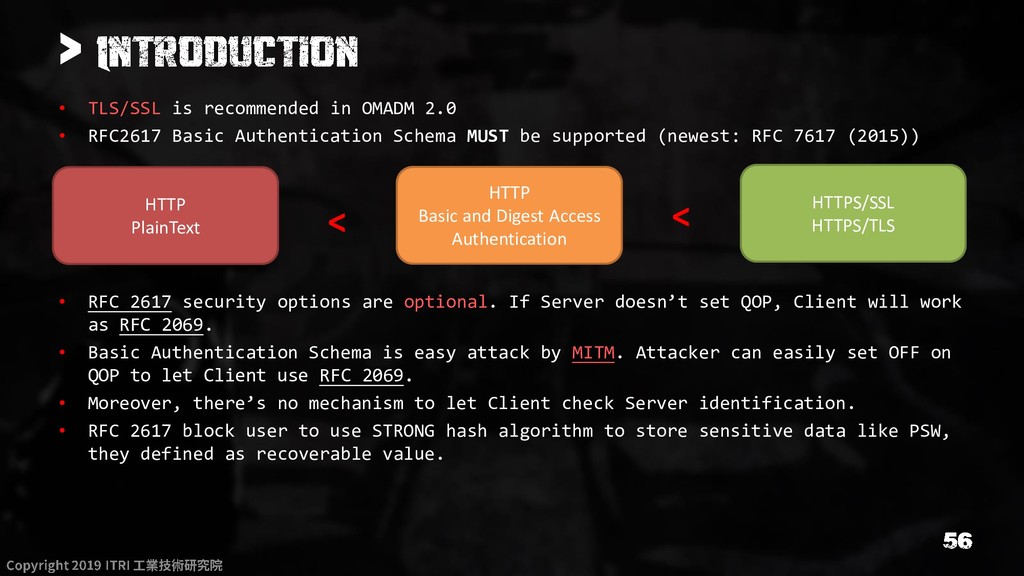
> • TLS/SSL is recommended in OMADM 2.0 • RFC2617
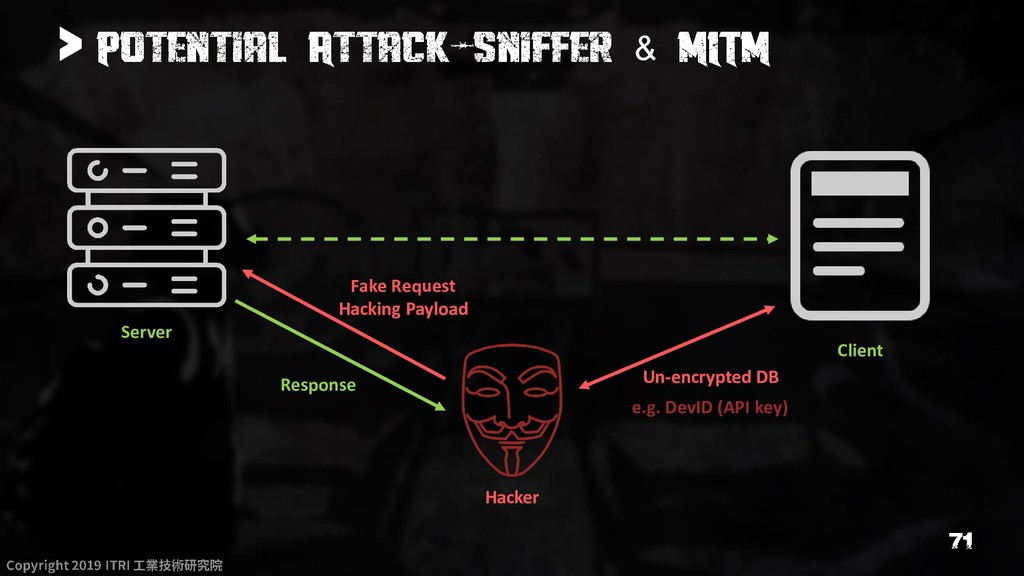
Basic Authentication Schema MUST be supported (newest: RFC 7617 (2015)) • RFC 2617 security options are optional. If Server doesn’t set QOP, Client will work as RFC 2069. • Basic Authentication Schema is easy attack by MITM. Attacker can easily set OFF on QOP to let Client use RFC 2069. • Moreover, there’s no mechanism to let Client check Server identification. • RFC 2617 block user to use STRONG hash algorithm to store sensitive data like PSW, they defined as recoverable value. HTTP PlainText HTTP Basic and Digest Access Authentication HTTPS/SSL HTTPS/TLS < < -
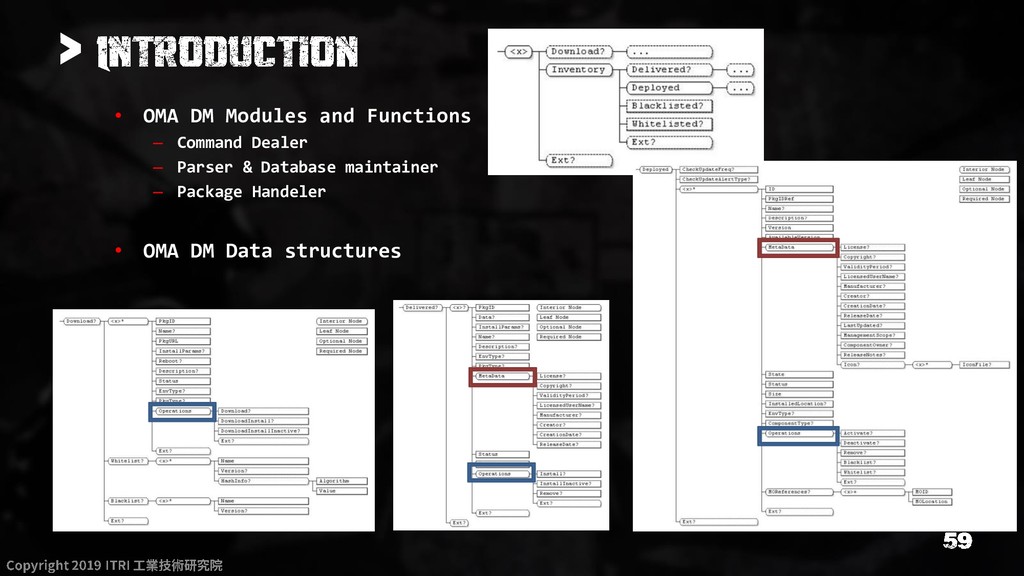
> • OMA DM Modules and Functions – Command Dealer
– Parser & Database maintainer – Package Handeler • OMA DM Data structures -
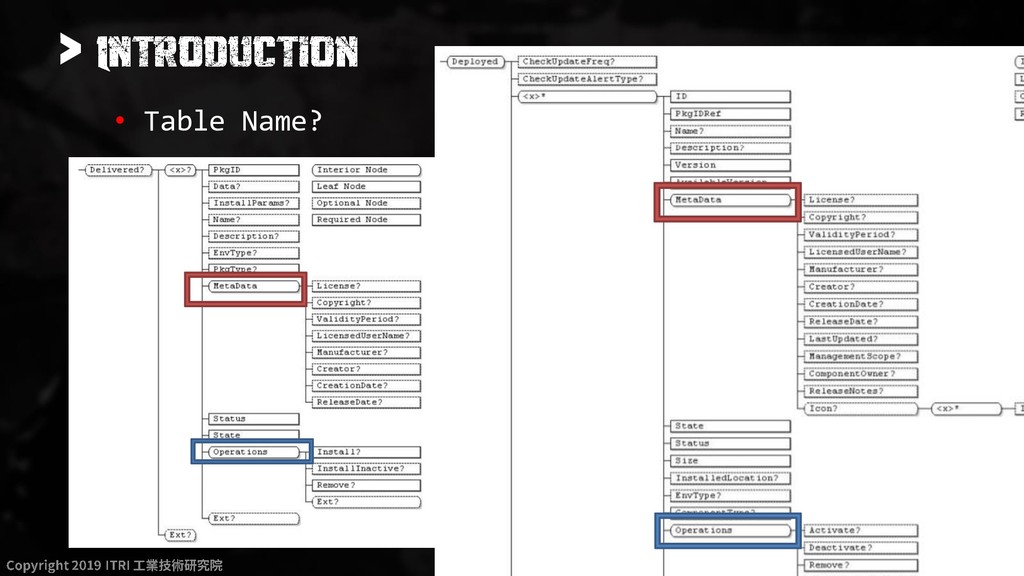
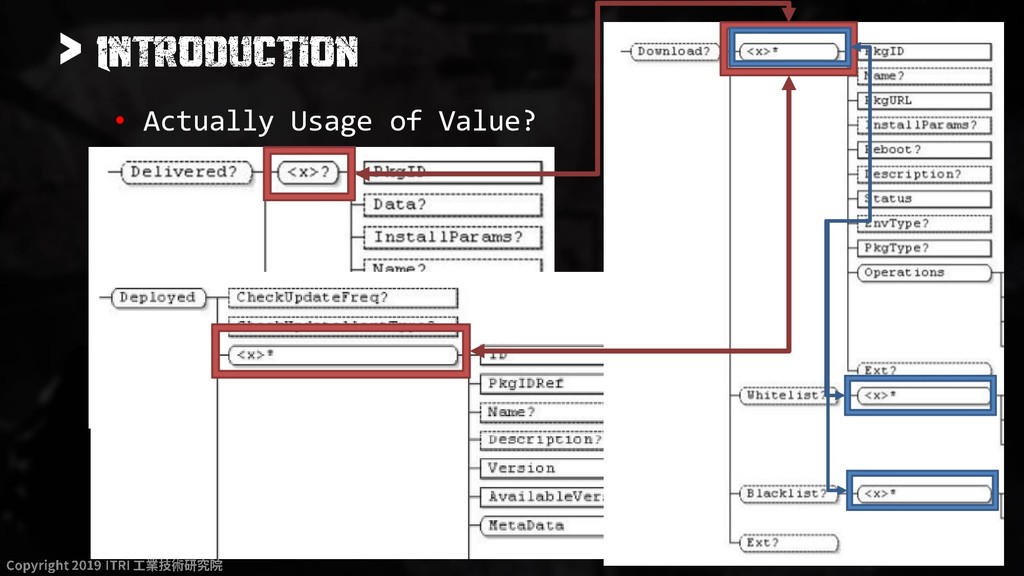
> • Database type storage in OMA DM – Pros
• Insert / Update / Parse can easily use database schema mechanism to check DDF invalid – Cons • Need more designing on table name also reach the consensus between Server & Client • XML type storage in OMA DM – Pros • easily fit the document designing – Cons • Insert a new MO tree will be hard to check if is valid DDF -
> • Cross Protocol Version: – DataBuffer stream boundary different
in SML & HTTP (1st command result following with 1st data /1st command result code with 2nd command result code) – Command method not backward compatible (Ver2 not support REPLACE command) • OMA DM NodeName & SQL Syntax conflict: – urn:oma:mo:fumo:1.0/<x>/update • A lot of Extension in OMA DM tree: (there can not be multiple tables in same name) – urn:oma:mo:oma-dm-devinfo:1.2/<x>/Ext – urn:oma:mo:oma-dm-dmacc:1.2/<x>/Push/GCM/Ext – urn:oma:mo:fumo:1.0/<x>/Ext • Result Code inconsistency: – Sometime diff MO module use same result code, sometime not. • Same MO module, different DDF -
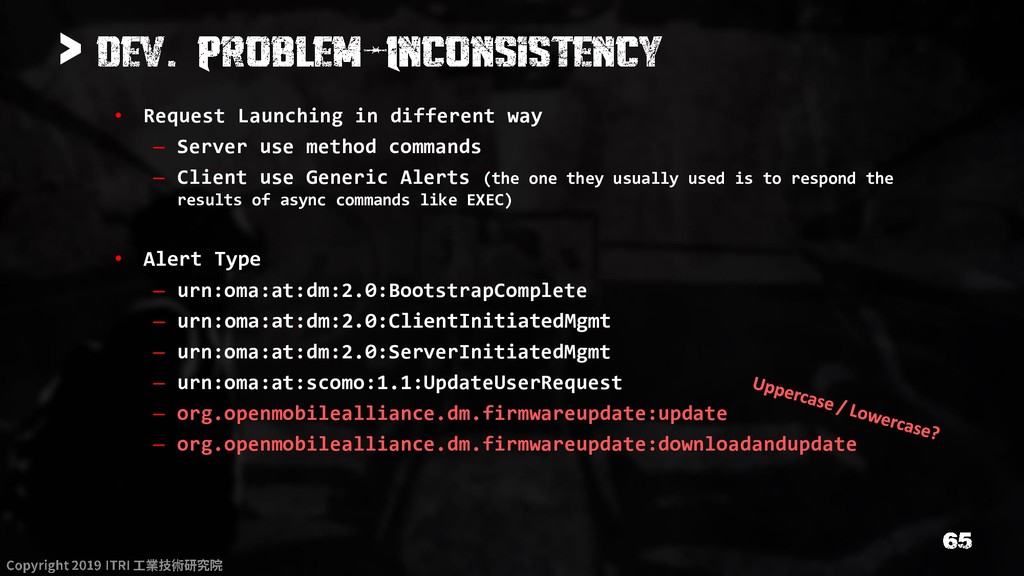
> • Request Launching in different way – Server use
method commands – Client use Generic Alerts (the one they usually used is to respond the results of async commands like EXEC) • Alert Type – urn:oma:at:dm:2.0:BootstrapComplete – urn:oma:at:dm:2.0:ClientInitiatedMgmt – urn:oma:at:dm:2.0:ServerInitiatedMgmt – urn:oma:at:scomo:1.1:UpdateUserRequest – org.openmobilealliance.dm.firmwareupdate:update – org.openmobilealliance.dm.firmwareupdate:downloadandupdate -
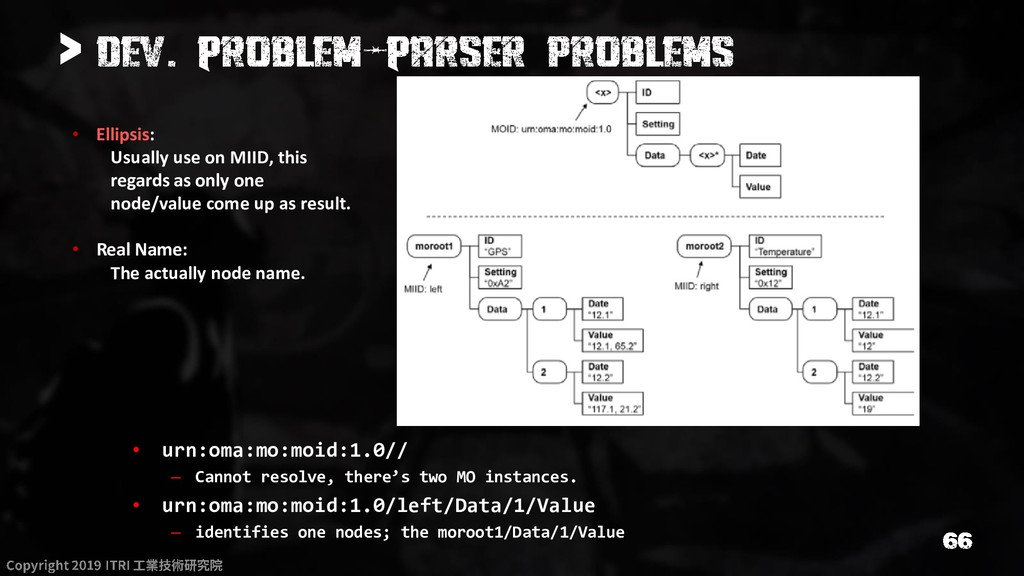
> • urn:oma:mo:moid:1.0// – Cannot resolve, there’s two MO instances.
• urn:oma:mo:moid:1.0/left/Data/1/Value – identifies one nodes; the moroot1/Data/1/Value • Ellipsis: Usually use on MIID, this regards as only one node/value come up as result. • Real Name: The actually node name. -
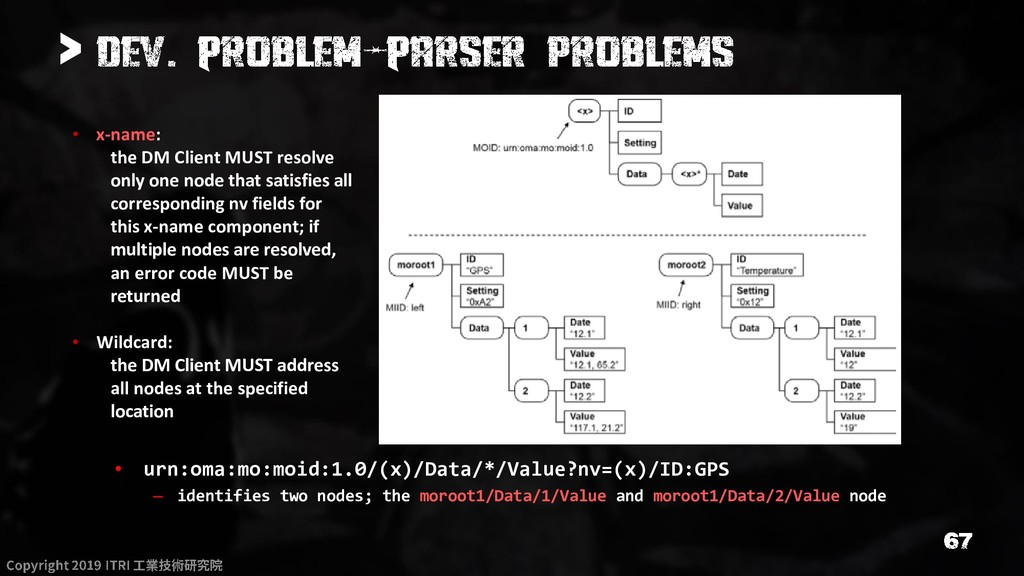
> • urn:oma:mo:moid:1.0/(x)/Data/*/Value?nv=(x)/ID:GPS – identifies two nodes; the moroot1/Data/1/Value and
moroot1/Data/2/Value node • x-name: the DM Client MUST resolve only one node that satisfies all corresponding nv fields for this x-name component; if multiple nodes are resolved, an error code MUST be returned • Wildcard: the DM Client MUST address all nodes at the specified location -
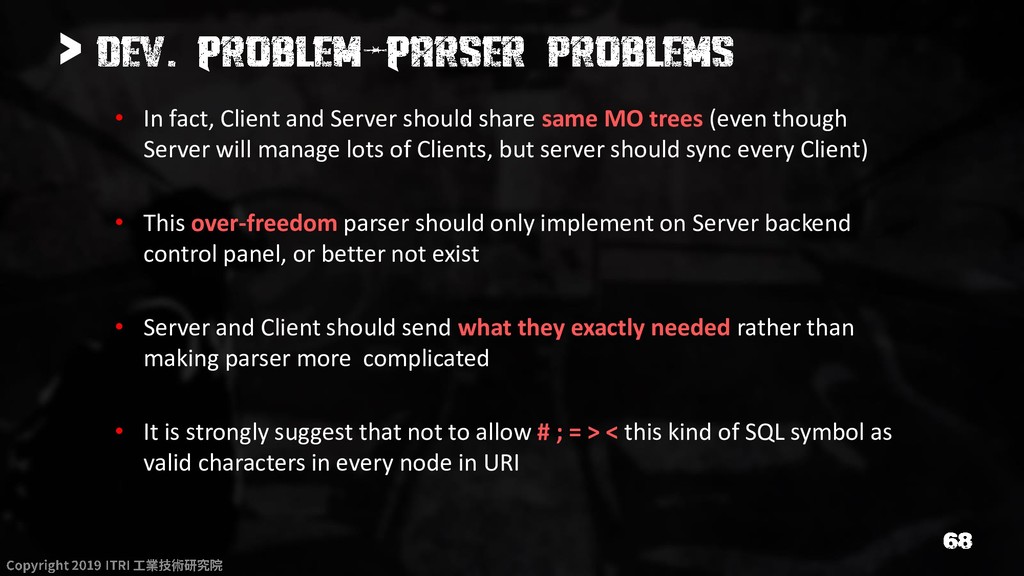
> • In fact, Client and Server should share same
MO trees (even though Server will manage lots of Clients, but server should sync every Client) • This over-freedom parser should only implement on Server backend control panel, or better not exist • Server and Client should send what they exactly needed rather than making parser more complicated • It is strongly suggest that not to allow # ; = > < this kind of SQL symbol as valid characters in every node in URI -
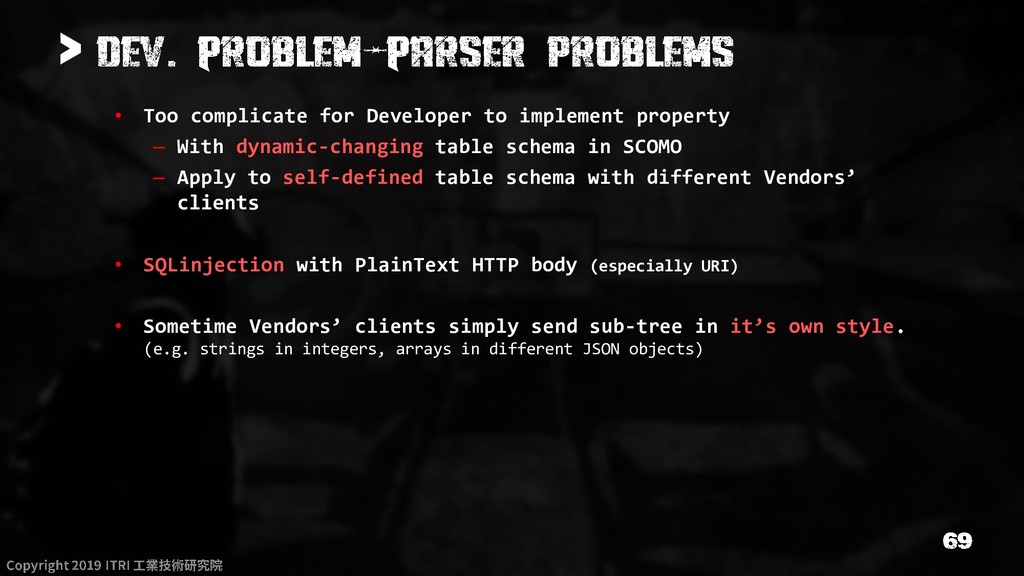
> • Too complicate for Developer to implement property –
With dynamic-changing table schema in SCOMO – Apply to self-defined table schema with different Vendors’ clients • SQLinjection with PlainText HTTP body (especially URI) • Sometime Vendors’ clients simply send sub-tree in it’s own style. (e.g. strings in integers, arrays in different JSON objects) -
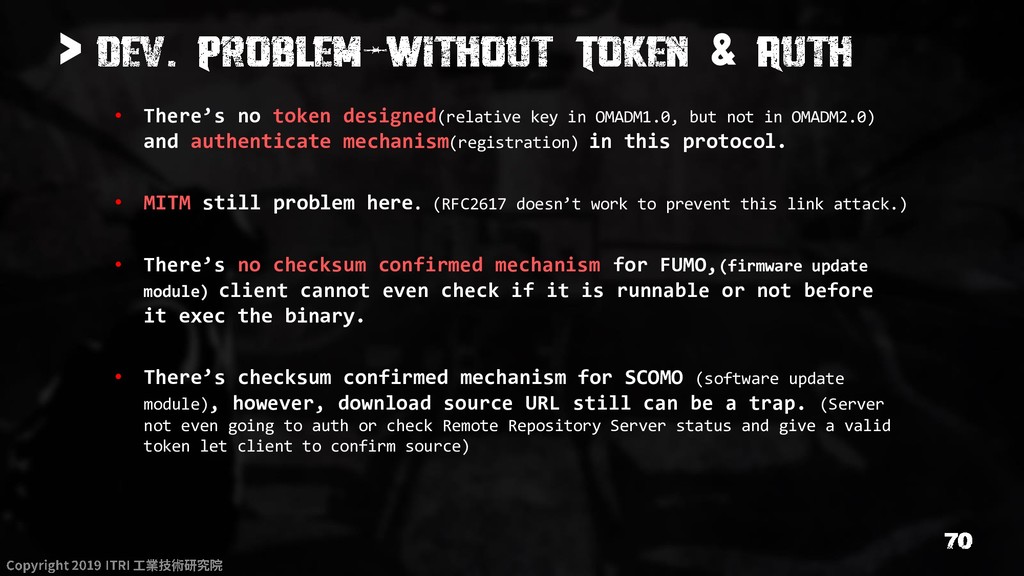
> & • There’s no token designed(relative key in OMADM1.0,
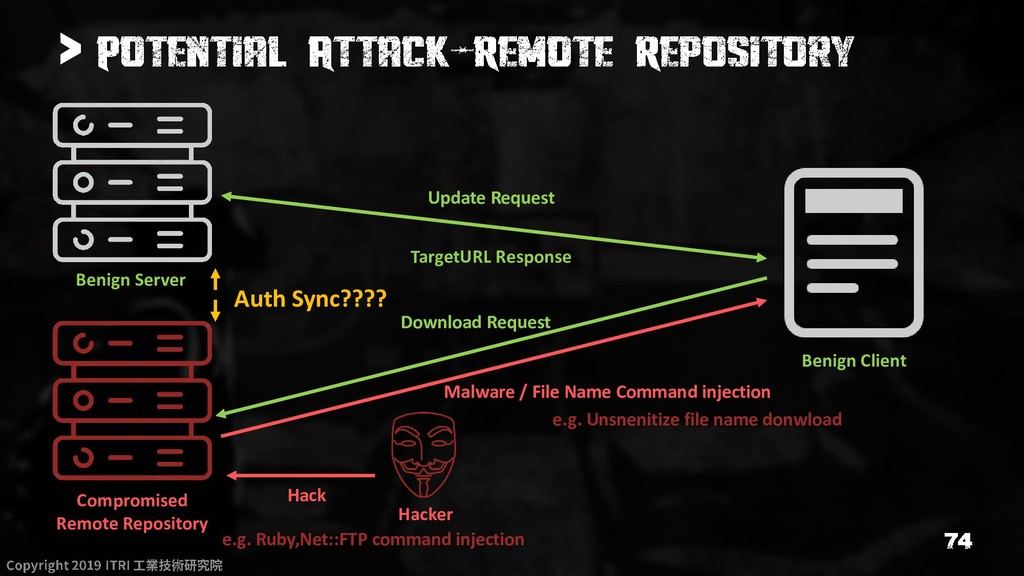
but not in OMADM2.0) and authenticate mechanism(registration) in this protocol. • MITM still problem here. (RFC2617 doesn’t work to prevent this link attack.) • There’s no checksum confirmed mechanism for FUMO,(firmware update module) client cannot even check if it is runnable or not before it exec the binary. • There’s checksum confirmed mechanism for SCOMO (software update module), however, download source URL still can be a trap. (Server not even going to auth or check Remote Repository Server status and give a valid token let client to confirm source) -
> & Server Client Hacker Un-encrypted DB Fake Request Hacking
Payload Response e.g. DevID (API key) -
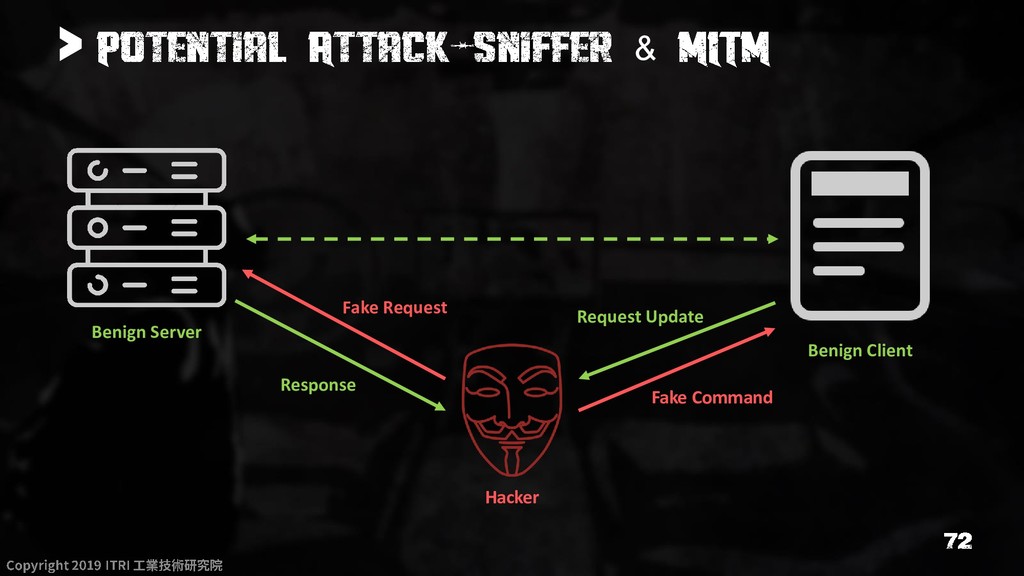
> & Benign Server Benign Client Hacker Request Update Fake
Command Fake Request Response -
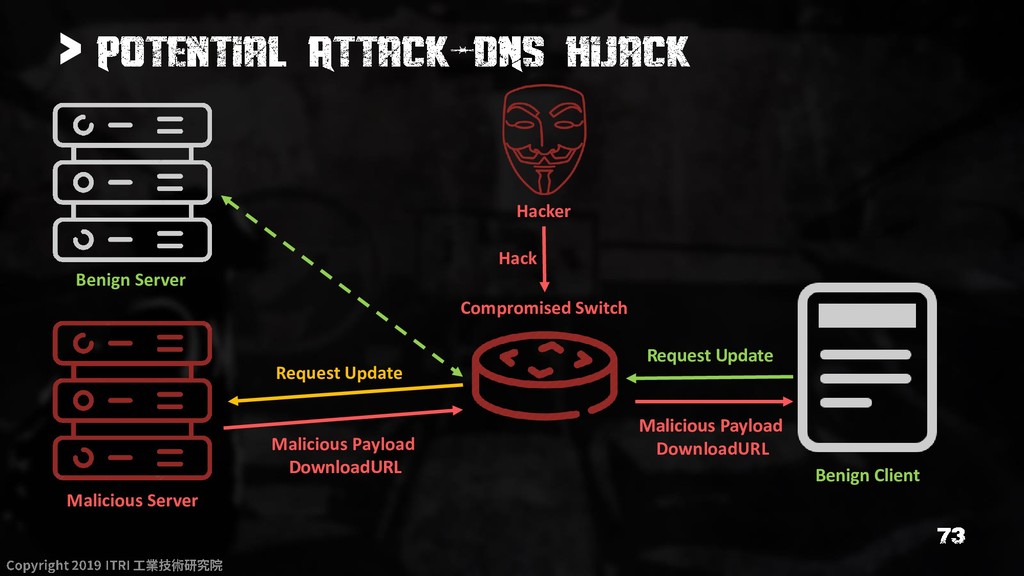
> Hacker Request Update Malicious Server Benign Server Benign Client
Compromised Switch Hack Request Update Malicious Payload DownloadURL Malicious Payload DownloadURL -
> Hacker Compromised Remote Repository Benign Server Benign Client Hack
Auth Sync???? Update Request TargetURL Response Download Request Malware / File Name Command injection e.g. Ruby,Net::FTP command injection e.g. Unsnenitize file name donwload -
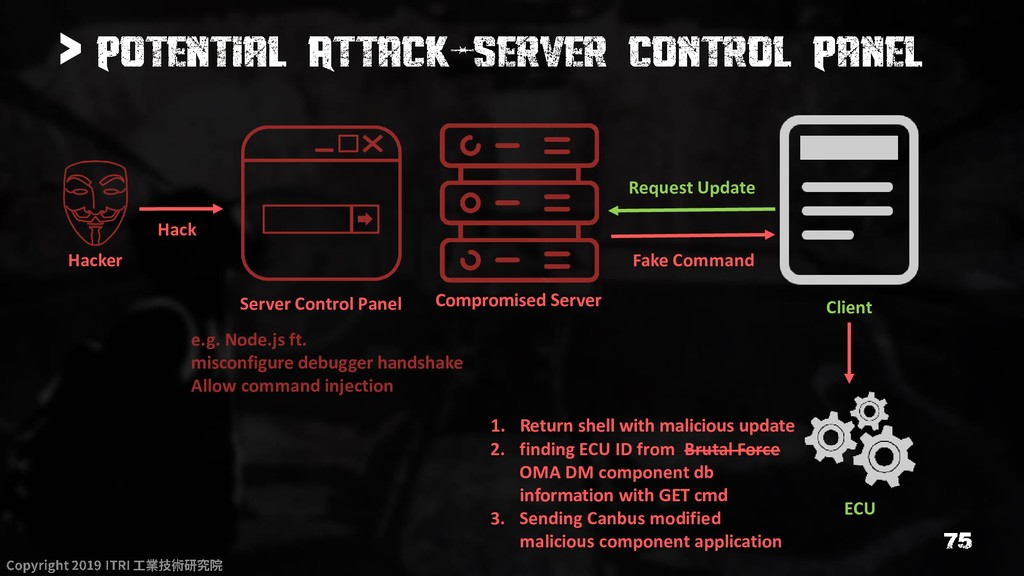
> Hacker Request Update Compromised Server Client Fake Command Server
Control Panel Hack ECU 1. Return shell with malicious update 2. finding ECU ID from Brutal Force OMA DM component db information with GET cmd 3. Sending Canbus modified malicious component application e.g. Node.js ft. misconfigure debugger handshake Allow command injection -
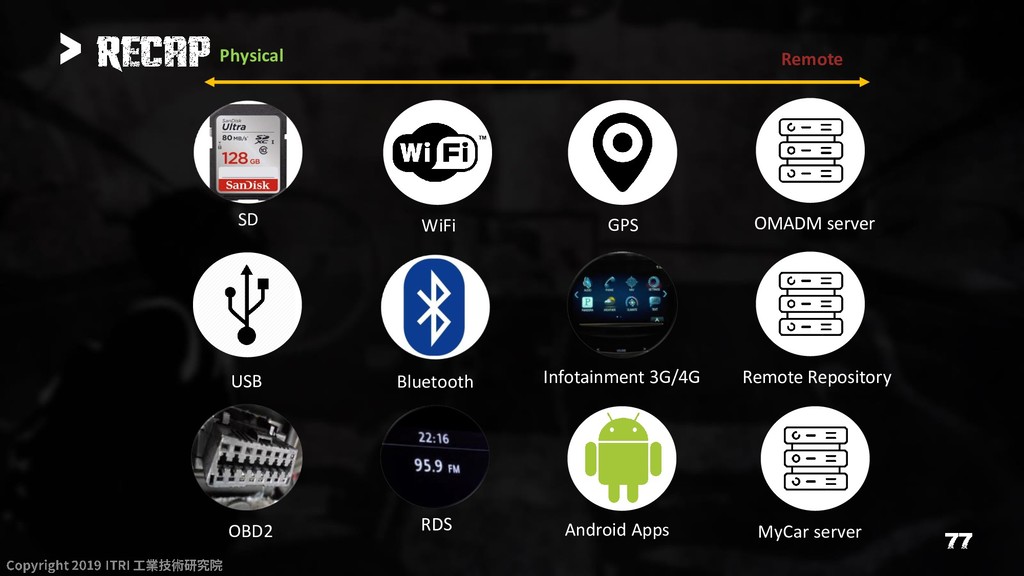
> RDS Bluetooth WiFi SD USB GPS Infotainment 3G/4G OBD2
Physical Remote Android Apps Remote Repository MyCar server OMADM server -
> • In IoT, OT, and Vehicle communication, plaintext and
default AC/PW still make serious problems • Latest Cross-Industry features (AI manufacture, AI medication, AI car) still not take Information Security as a serious problem, then come out with lots of vulnerabilities application • In past, low revenues device (PC, IoT) can be find out exploit value by black industry. Apparently, vehicle with its high value can earn its own targeting attack, and it’s worthy • Vehicle security can be a research draft of aircraft, it’s really sensitive to country security • OMA DM 2.0 is a protocol that need to enhance. Should take serious concern on security issue beyond the document -
> • Supply chain attack make vendors pay attention on
every third-party libraries (& Remote Repository Server) • Make sure to use BL/WL mechanism and Hash check • Cipher and CA always enhance your communication, use them • Physical attack cannot avoid, but take care every addon on your car and make sure to change your AC/PW • Every remote access to Canbus components (OBDII, MyCar, ECU component in OMADM) should apply auth confirm & encrypted communication. Vendor Web should apply vulnerabilities scanning to fix bugs, avoid brutal force and information leak. • Mini computer is the major component in all attack vectors, Application Whitelist can ease the lost after compromised by hacking -
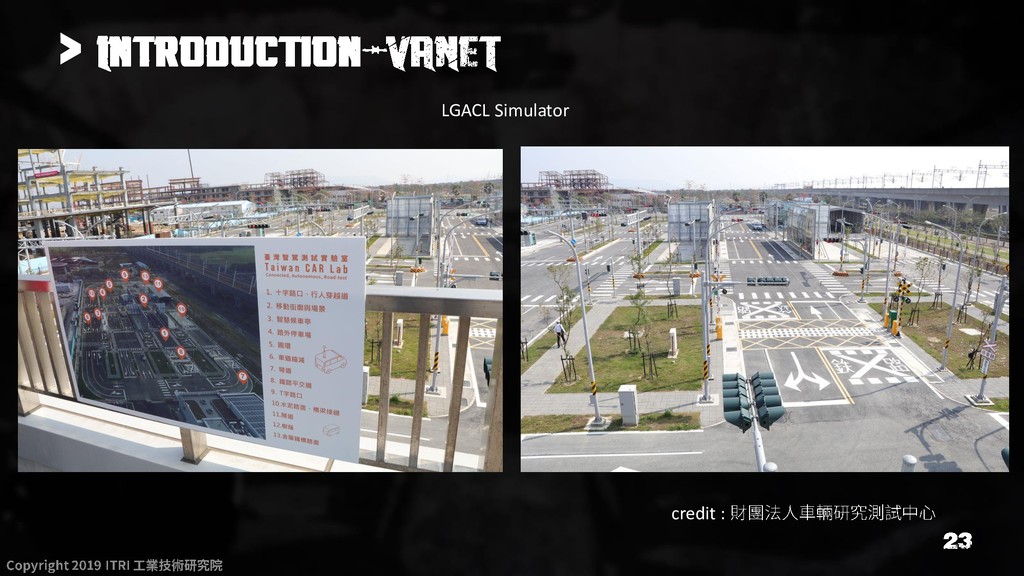
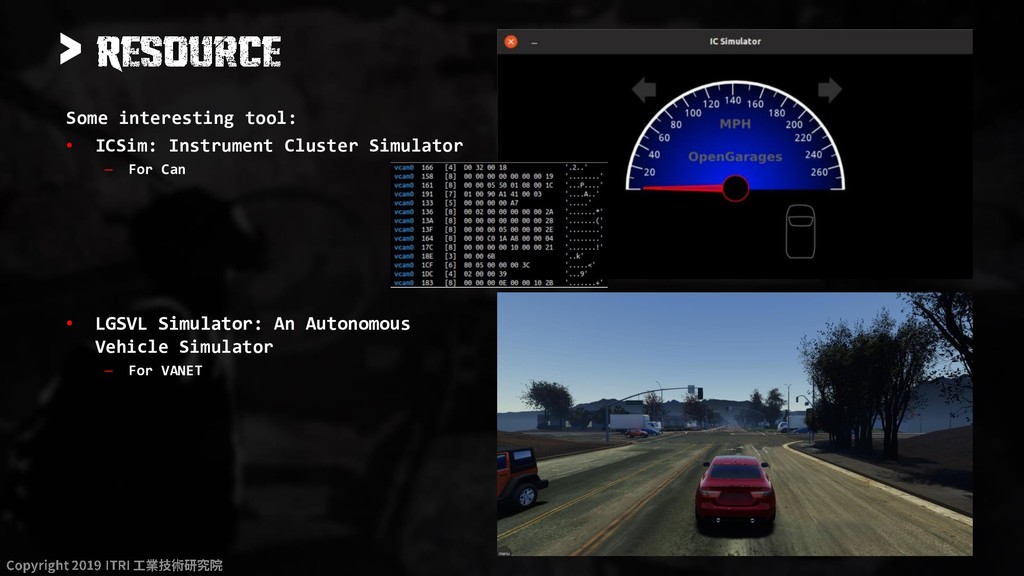
> Some interesting tool: • ICSim: Instrument Cluster Simulator –
For Can • LGSVL Simulator: An Autonomous Vehicle Simulator – For VANET -
> • http://www.openmobilealliance.org/ • http://illmatics.com/Remote%20Car%20Hacking.pdf • https://ioactive.com/pdfs/IOActive_Adventures_in_Automotive_Networks_and_Control_Units.pdf • https://www.sans.org/reading-room/whitepapers/threats/hacking-bus-basic-manipulation-modern- automobile-through-bus-reverse-engineering-37825
• http://www.aut.upt.ro/~pal-stefan.murvay/papers/dos-attacks-controller-area-networks-fault- injections-from-software-layer.pdf • https://media.defcon.org/DEF%20CON%2027/DEF%20CON%2027%20presentations/DEFCON-27-Jmaxxz- Your-Car-is-My-Car-Code-6e0e599/ • https://www.shs.edu.tw/works/essay/2012/11/2012111421572430.pdf • https://hackaday.com/2019/06/10/takatas-deadly-airbags-an-engineering-omnishambles • https://blog.avast.com/hacker-breaches-gps-service-of-27000-cars • https://www.zdnet.com/article/dhs-warns-about-can-bus-vulnerabilities-in-small-aircraft
 notsurprised
 hirachan
 institutdelelevage
 taniai
 yumulab
 ftakahashi
 satai
 tkng
 tattaka
 productmarketing
 speakerdeck
 tanoku
 katarinadahlin
 oripsolob
 nikkihalliwell
 skoyamalab
 baasie
 letsgokoyo
 aleyda
 jonoalderson
 jdejongh