Share
Embed
The Cyber Legislation Changes Around the Globe in Five Minutes
Software is operated globally but it falls under the legislation of different countries. Do you know everything you need to know about cybersecurity legal obligations around the world?
We will go together through all the legislative changes that happened in the last months around the globe and bring you up to speed about everything that you need to know when operating globally or regionally. From the EU CRA, and EU AI Act to the changes proposed by the US or even by Japan.
Olimpiu Pop
May 07, 2024
Transcript
20 slides
-
The World Is Changing …and cyber legislation is changing too
ignite - edition -
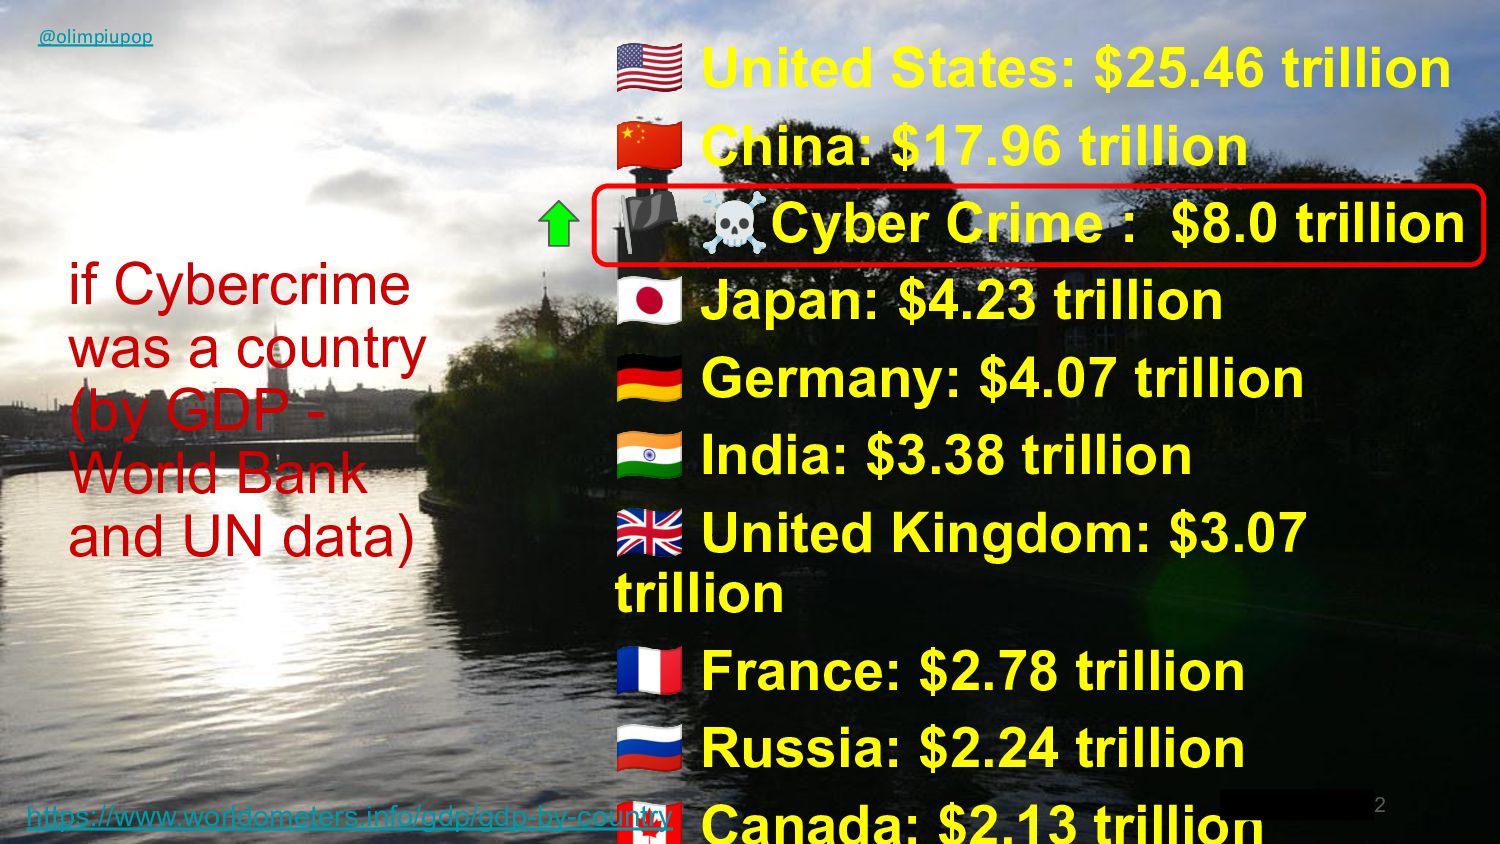
@spoole167 United States: $25.46 trillion China: $17.96 trillion
🏴 ☠Cyber Crime : $8.0 trillion Japan: $4.23 trillion Germany: $4.07 trillion India: $3.38 trillion United Kingdom: $3.07 trillion France: $2.78 trillion Russia: $2.24 trillion 2 if Cybercrime was a country (by GDP - World Bank and UN data) https://www.worldometers.info/gdp/gdp-by-country @olimpiupop -
@spoole167 7 @olimpiupop United States of America • National
Cybersecurity Strategy - foundational cyber security document, addressing wide areas from infrastructure to software supply-chain security (SBOM) • Executive Order 14028 • Securing Open Source Act 2023 • AI National Security Act • FDA - Cybersecurity of Medical Devices • SEC (33-11028, 33-11038, 34-91742) - transparency • Secure Software Attestation Form • National Cybersecurity Strategy Implementation Plan • CISA’s Open Source Security Roadmap • National Highway Traffic Safety Administration published Cybersecurity of Modern Vehicles -
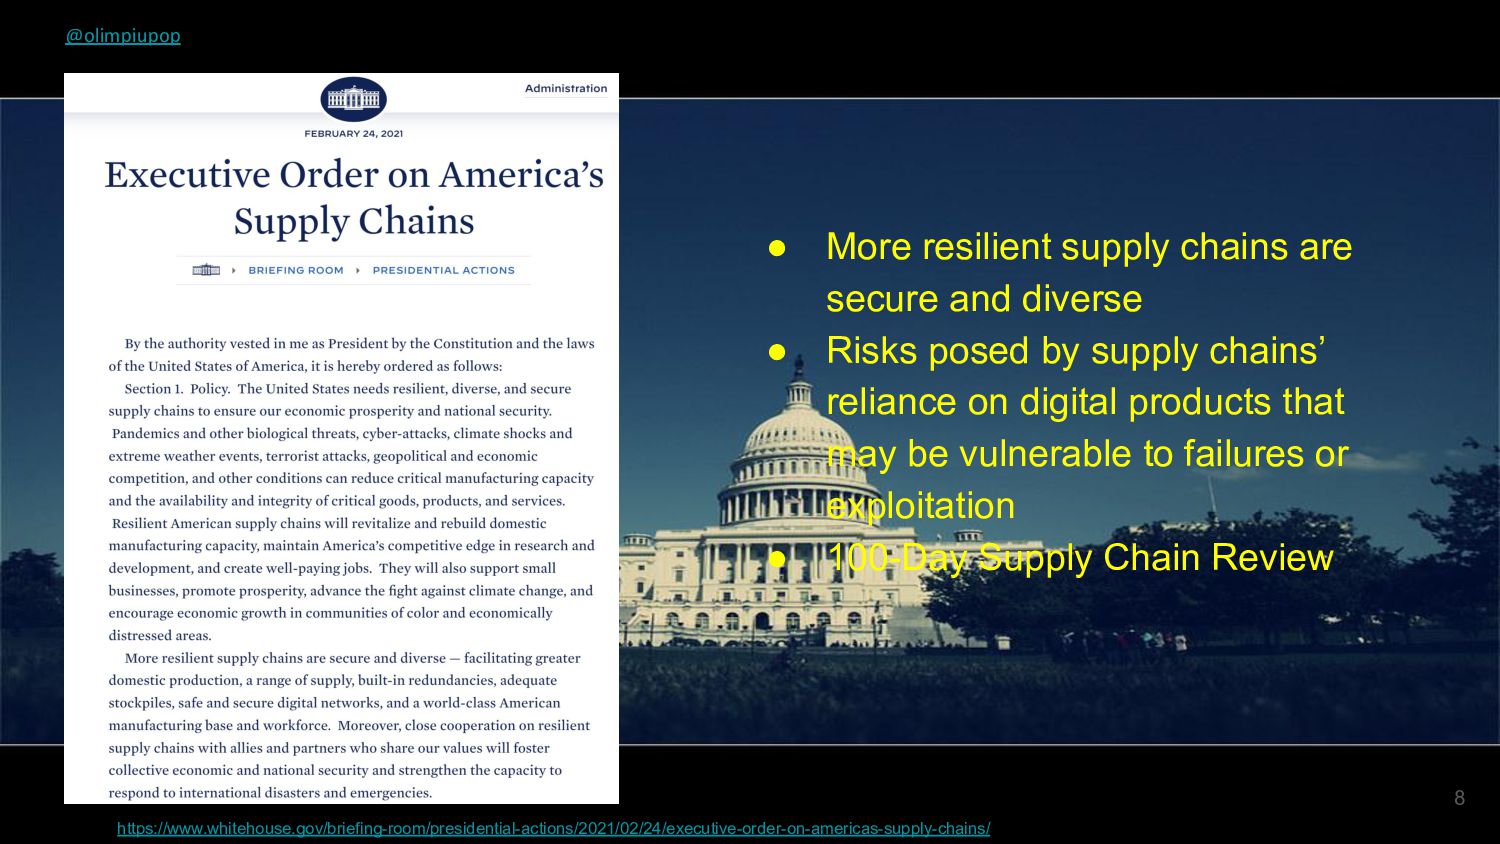
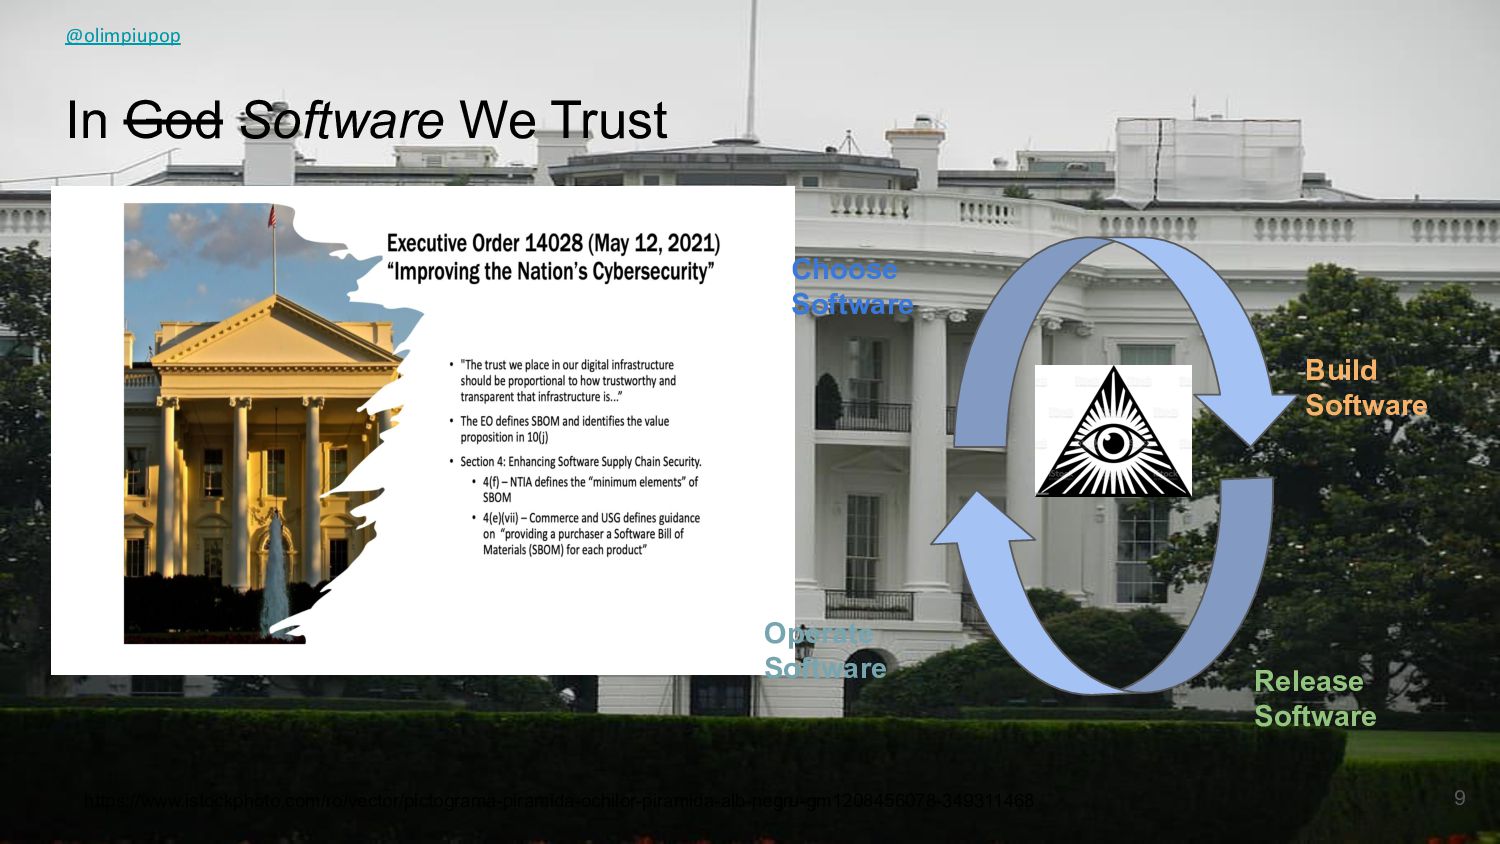
8 @olimpiupop • More resilient supply chains are secure and
diverse • Risks posed by supply chains’ reliance on digital products that may be vulnerable to failures or exploitation • 100-Day Supply Chain Review https://www.whitehouse.gov/briefing-room/presidential-actions/2021/02/24/executive-order-on-americas-supply-chains/ -
In God Software We Trust Choose Software Build Software Operate
Software Release Software 9 @olimpiupop https://www.istockphoto.com/ro/vector/pictograma-piramida-ochilor-piramida-alb-negru-gm1208456078-349311468 -
@spoole167 10 @olimpiupop European Union - Cybersecurity • Cyber
Resilience Act (March ‘23 - 2027) ◦ Secure Software Supply Chain ◦ Any internet connected should be up to date ◦ Adapted based on recommendations from not-for profit foundations (open source stewards) ◦ Foundations working to “connect the dots” and close the gap between industry best practices and regulation • NIS2 Directive (Jan 16th ‘23/ Oct 17th ‘24) ◦ Different compliance levels for Essential Entities, Important Entities ◦ Harmonize best practices EU wide (business continuity, incident response, vulnerability management etc) ◦ EU vulnerability registry and state of cybersecurity • Product Liability Directive ◦ Proposed updated in September 2022 to include software defects too ◦ Might transfer vulnerabilities’ liability to open source distributors -
@spoole167 11 @olimpiupop European Union - Privacy/ Data •
GDPR (May 4th 2016) ◦ Keep just the needed amount of data ◦ No more than you need to keep the data ◦ Delete private data on request ◦ Auditable • eIDAS2 (May 20th 2024) ◦ First digital identity wallet to keep identity and attestations proofs digitally across borders (ID, driver’s license, diplomas etc) ◦ Access public services without losing control to private data ◦ Global standard for privacy, security and interoperability in the public sector • AI Act (March 13th 2024) ◦ Risk classification of AI systems ◦ Obligations mostly for AI developers - transparency ◦ Most of the existing AI systems untouched ◦ Banned: social scoring, identification, manipulation, biometric etc -
12 @olimpiupop https://www.gov.uk/government/consultations/proposal-for-legislation-to-improve-the-uks-cyber-resilience/proposal-for-legislation-to-improve-the-uks-cyber-resilience https://www.gov.uk/government/cyber-security United Kingdom • 3rd most targeted
country after US and UA • National Cyber Strategy 2022 and Government Cyber Strategy 2022-2030 • Hardening all the public services until no later than 2030 • Coordination and Transparency • Public-Private Defence and Security Accelerator • AI Regulation -
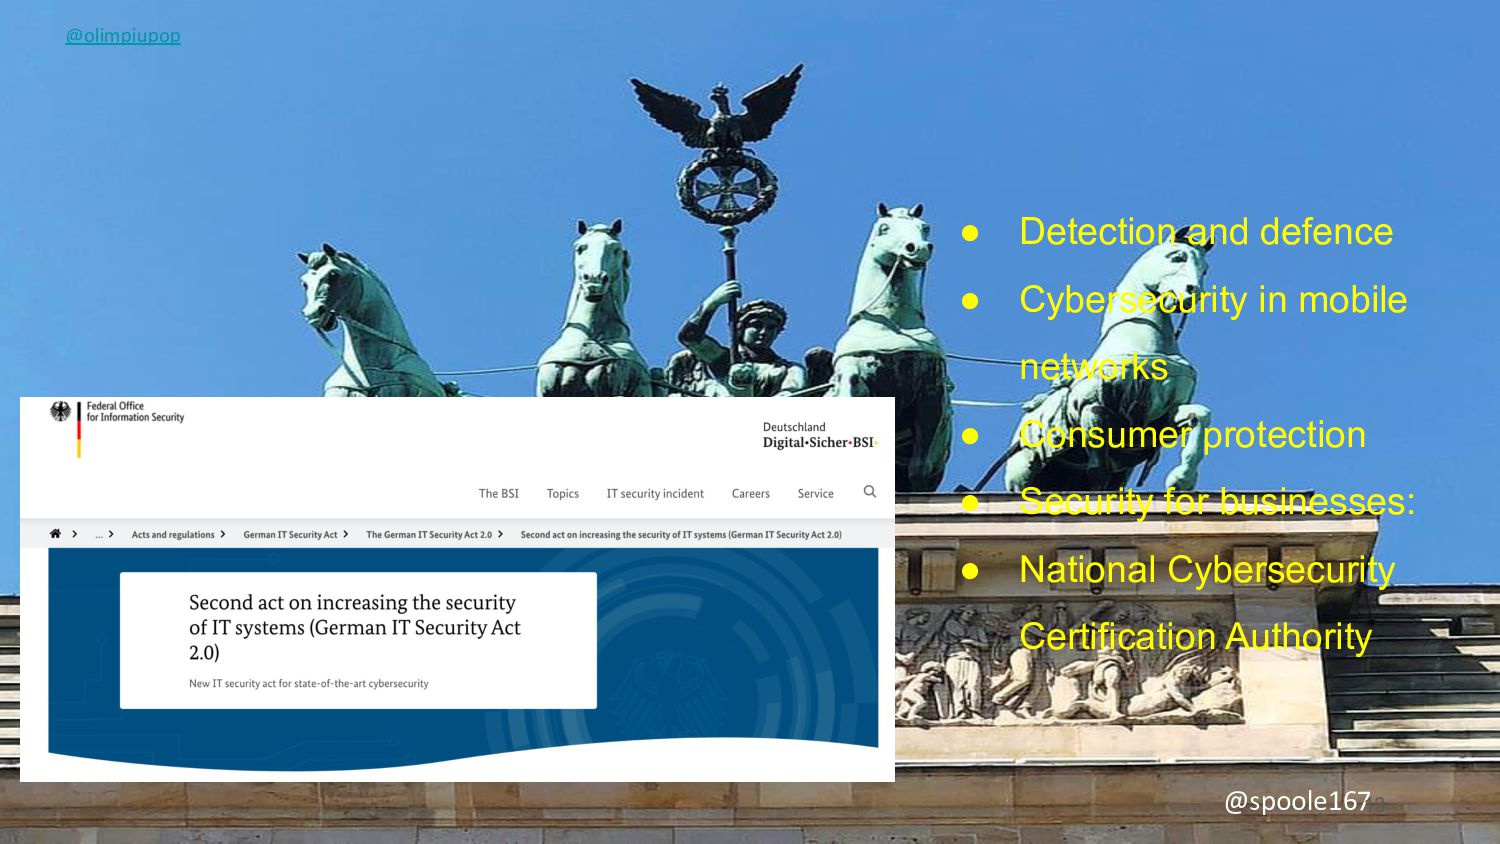
@spoole167 13 @olimpiupop • Detection and defence • Cybersecurity in
mobile networks • Consumer protection • Security for businesses: • National Cybersecurity Certification Authority -
@spoole167 14 @olimpiupop Canada • 2022 National Cyber Threat
Assessment: warns about state sponsored cyber criminals targeting Canada ◦ Ransomware ◦ Attacks on Critical Infrastructure ◦ State Sponsored Attacks ◦ Disinformation and Influence of Operations ◦ Disruptive Technologies • 2023 Guidance for protecting organisations ◦ Minimise software supply chain risk ◦ Malware compromised updates ◦ Open-Source Vulnerabilities Fixing ◦ Business Continuity Recommendations for minimising the impact of attacks -
@spoole167 15 @olimpiupop Australia • Cybersecurity strategy: become world
leader by 2030 • Support the Pacific nations family • Rely on 6 shields ◦ Strong businesses and citizens ◦ Safe technology ◦ World class threat sharing and blocking ◦ Protected critical infrastructure ◦ Sovereign Capabilities ◦ Resilient regional and global leadership https://www.homeaffairs.gov.au/cyber-security-subsite/files/2023-cyber-security-strategy.pdf -
@spoole167 16 @olimpiupop People Republic of China • Privacy
and security principles are rooted in the constitution, Civil Code and National Security Law • Cybersecurity Law, Data Security Law and Personal Information Law • Punishment of any data or personal information processing outside of China • Special rules for medical and health, finance, automobile, and internet information services • Everything data or privacy needs to be cross checked by Chinese authorities • Any vulnerability discovered needs to be disclosed to Chinese authorities before being made publicly available https://www.pwc.com/id/en/pwc-publications/services-publications/legal-publications/a-comparison-of-cybersecu rity-regulations/china.html -
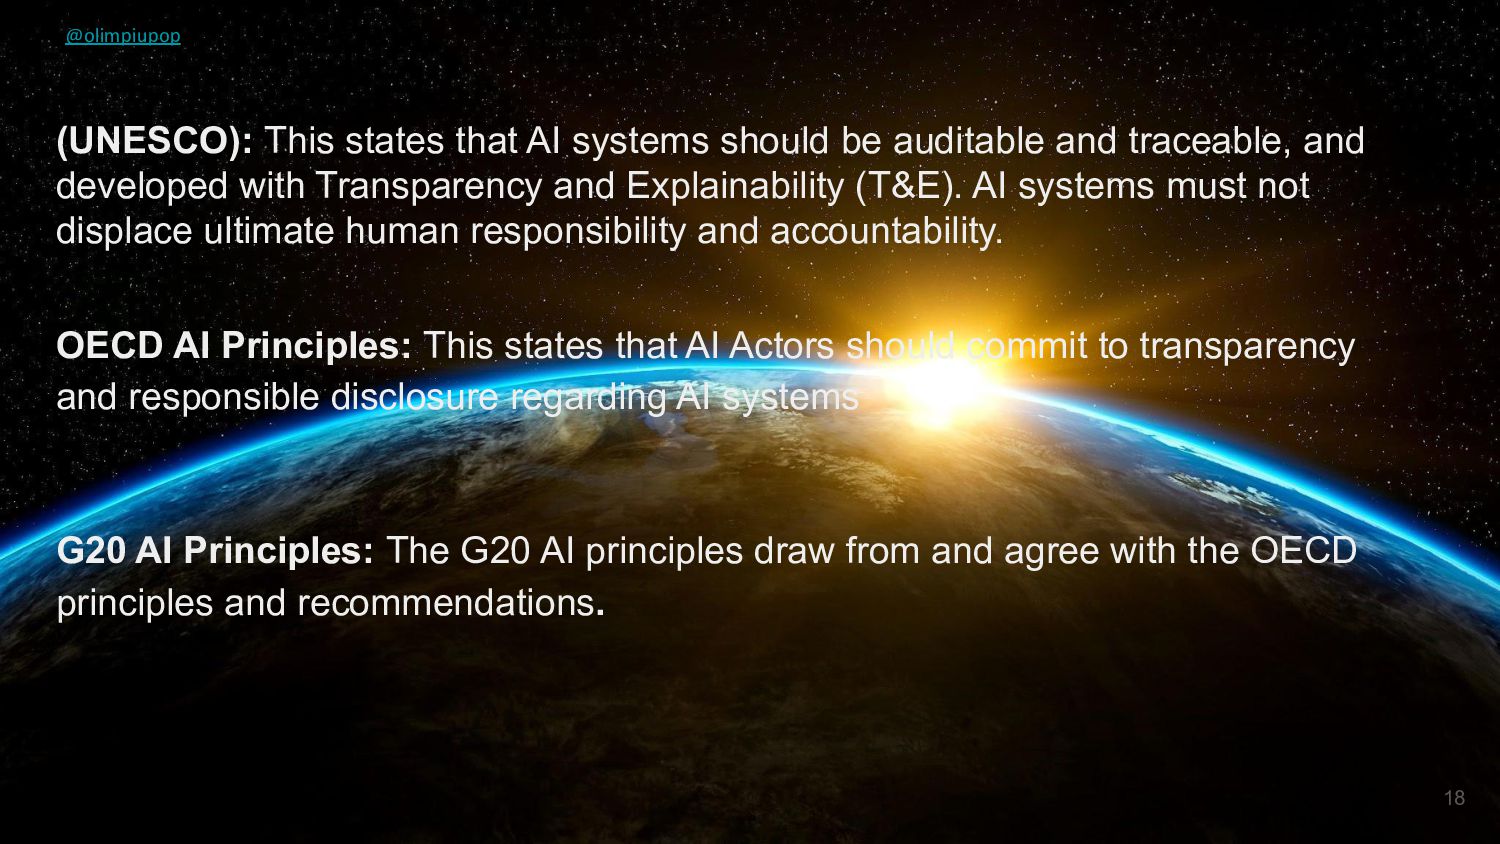
18 @olimpiupop (UNESCO): This states that AI systems should be
auditable and traceable, and developed with Transparency and Explainability (T&E). AI systems must not displace ultimate human responsibility and accountability. OECD AI Principles: This states that AI Actors should commit to transparency and responsible disclosure regarding AI systems G20 AI Principles: The G20 AI principles draw from and agree with the OECD principles and recommendations.