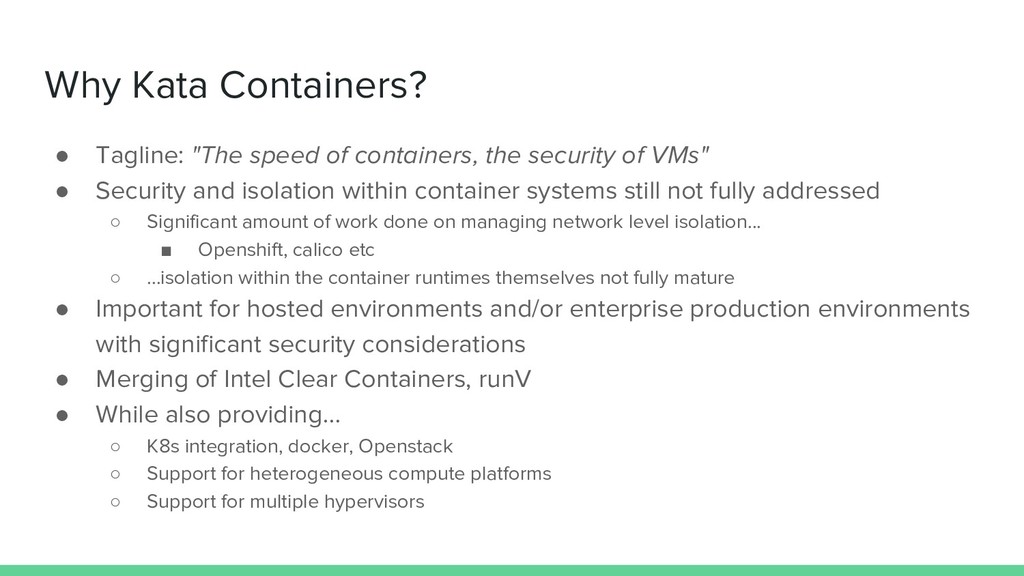
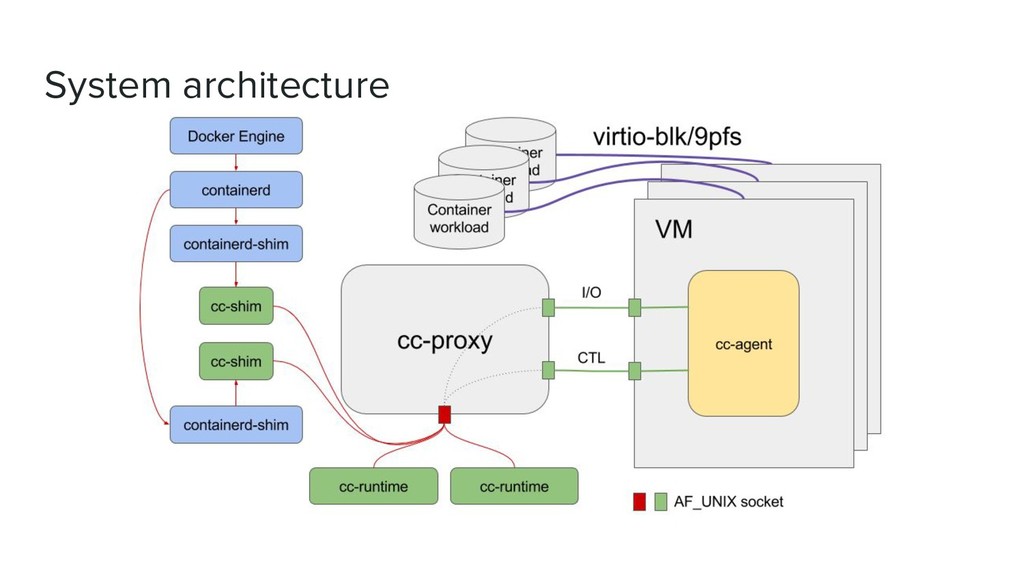
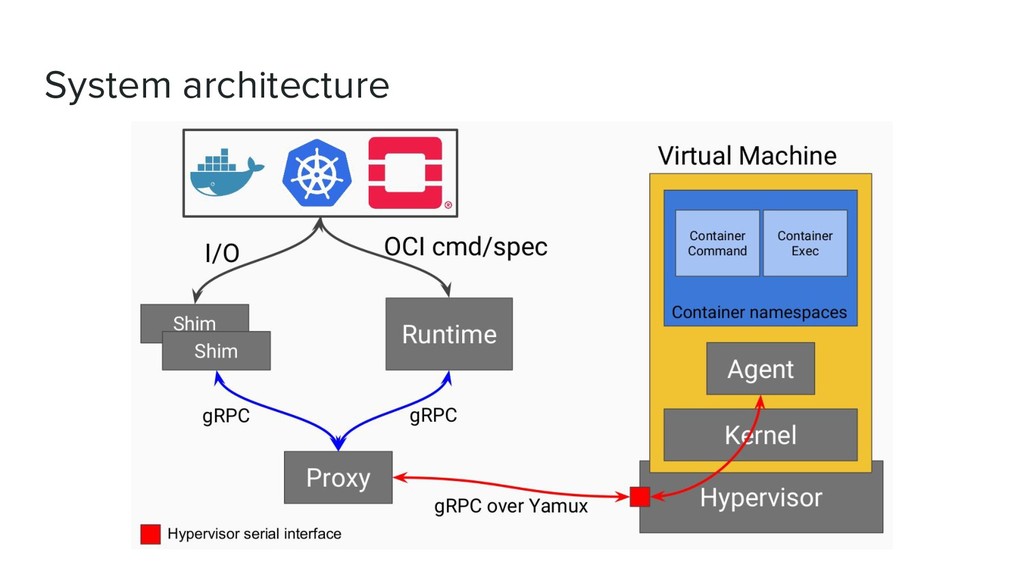
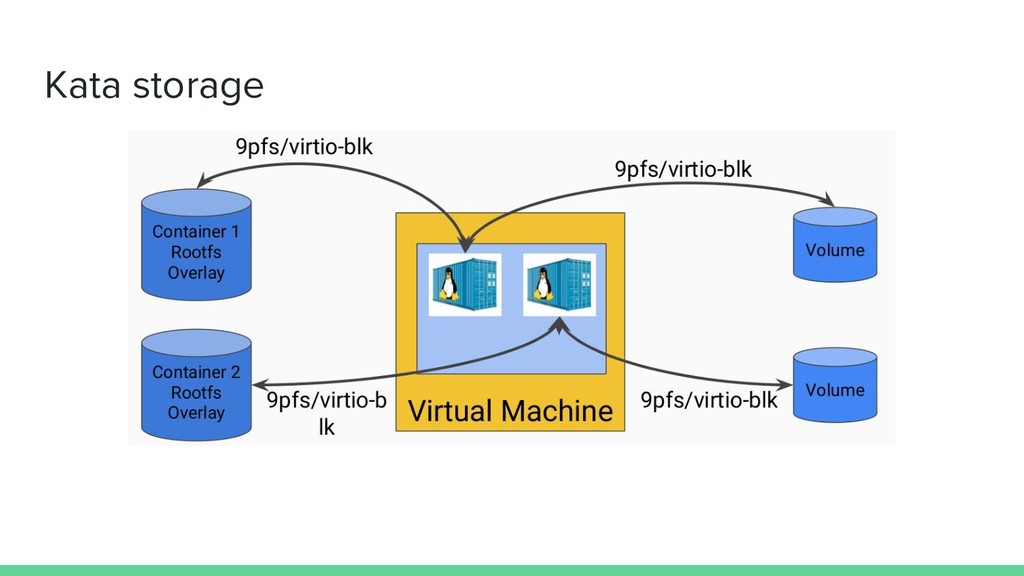
security of VMs" • Security and isolation within container systems still not fully addressed ◦ Significant amount of work done on managing network level isolation... ▪ Openshift, calico etc ◦ ...isolation within the container runtimes themselves not fully mature • Important for hosted environments and/or enterprise production environments with significant security considerations • Merging of Intel Clear Containers, runV • While also providing… ◦ K8s integration, docker, Openstack ◦ Support for heterogeneous compute platforms ◦ Support for multiple hypervisors
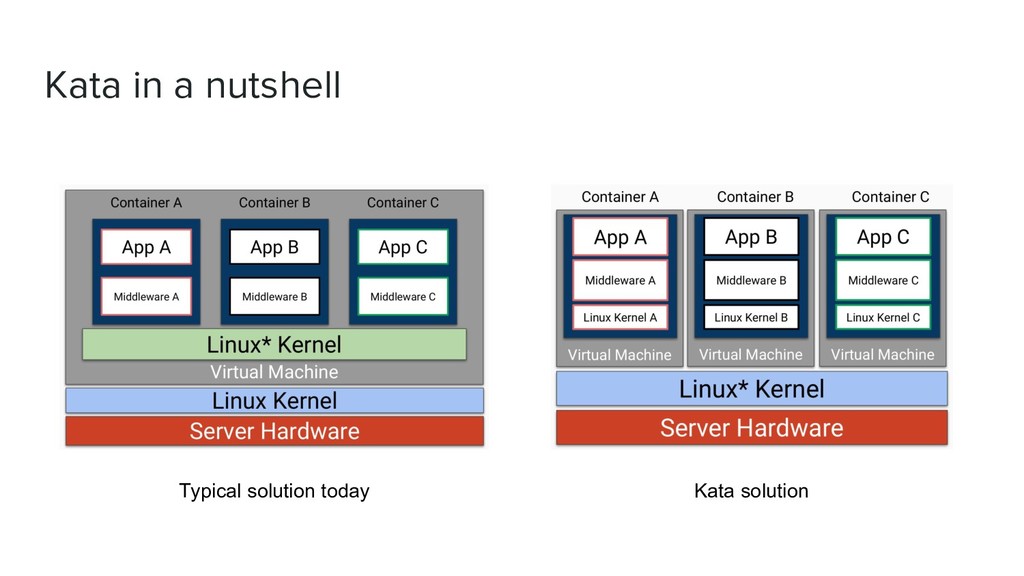
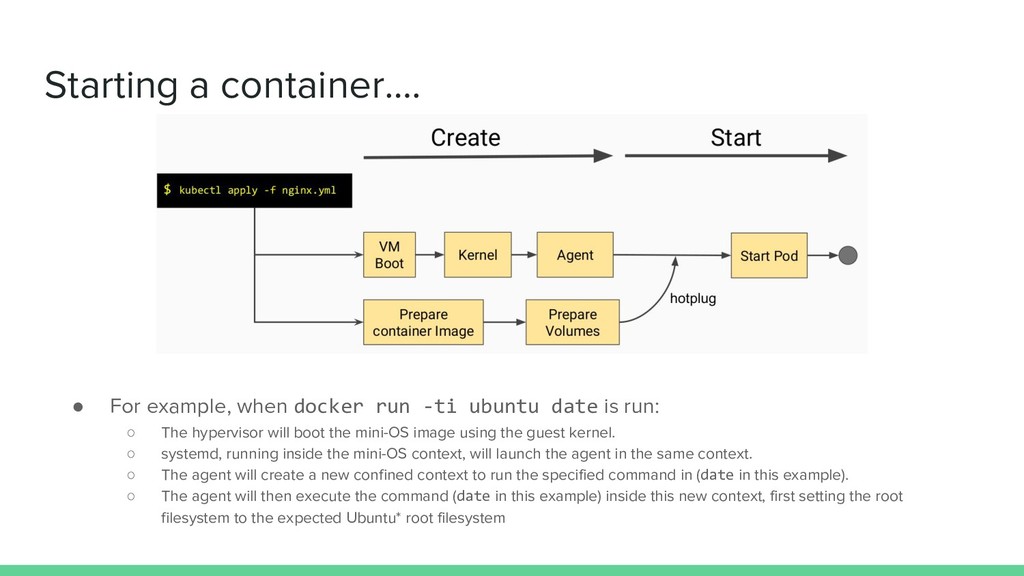
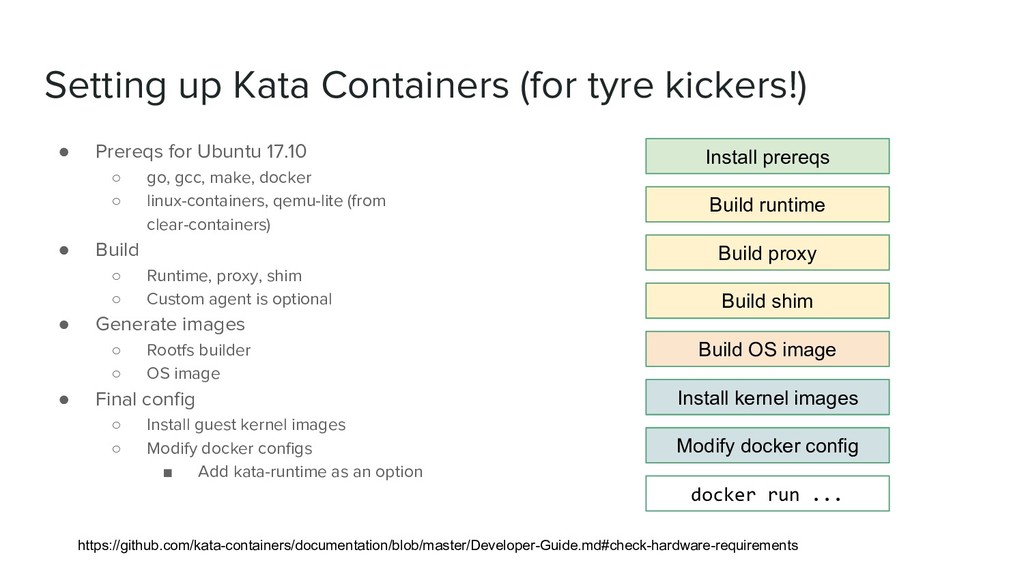
ubuntu date is run: ◦ The hypervisor will boot the mini-OS image using the guest kernel. ◦ systemd, running inside the mini-OS context, will launch the agent in the same context. ◦ The agent will create a new confined context to run the specified command in (date in this example). ◦ The agent will then execute the command (date in this example) inside this new context, first setting the root filesystem to the expected Ubuntu* root filesystem
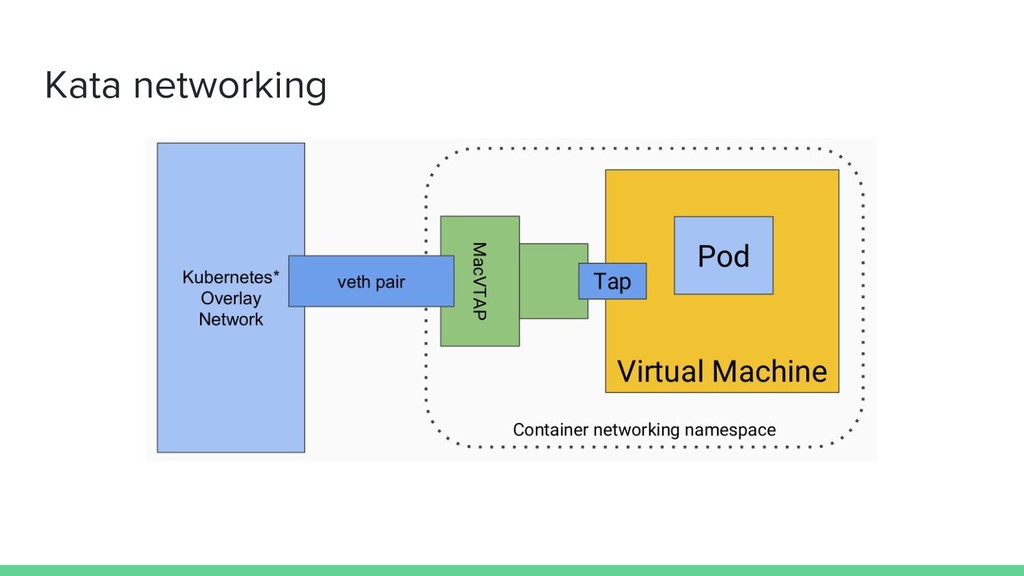
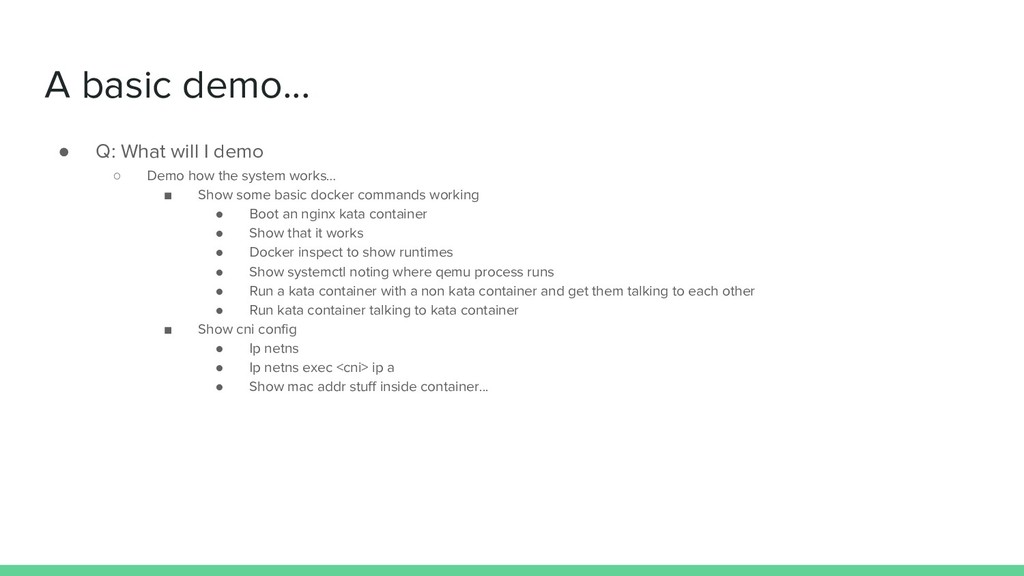
Demo how the system works… ▪ Show some basic docker commands working • Boot an nginx kata container • Show that it works • Docker inspect to show runtimes • Show systemctl noting where qemu process runs • Run a kata container with a non kata container and get them talking to each other • Run kata container talking to kata container ▪ Show cni config • Ip netns • Ip netns exec <cni> ip a • Show mac addr stuff inside container...
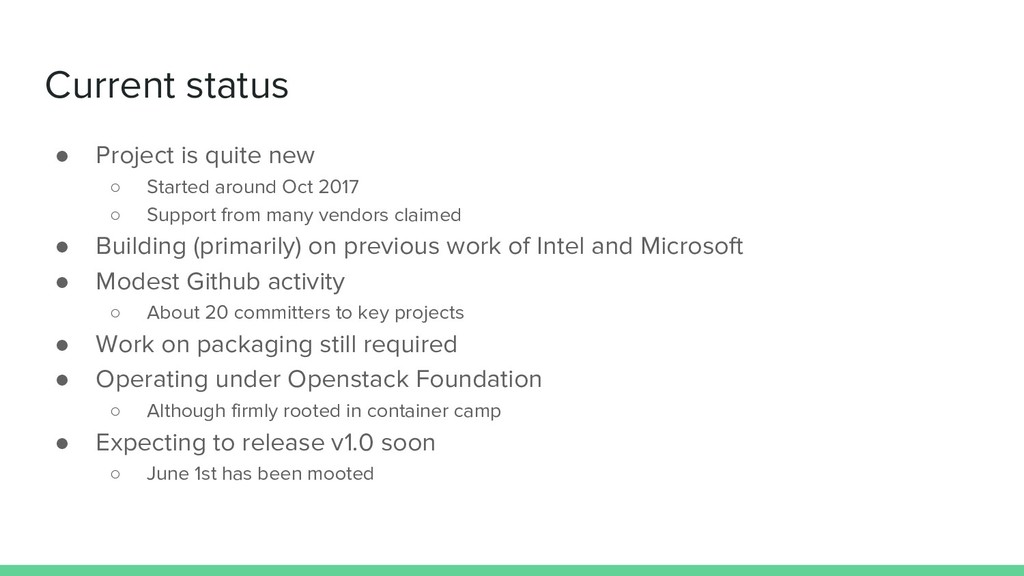
Oct 2017 ◦ Support from many vendors claimed • Building (primarily) on previous work of Intel and Microsoft • Modest Github activity ◦ About 20 committers to key projects • Work on packaging still required • Operating under Openstack Foundation ◦ Although firmly rooted in container camp • Expecting to release v1.0 soon ◦ June 1st has been mooted
into existing container platforms ◦ Work on Openshift, swarm integration ongoing • Good solution addressing VM-container middleground ◦ Interesting from perspective of VM world and container world... • Why do I care? ◦ We're setting up a heterogeneous edge computing testbed ▪ Mixing containers, VMs over distributed infra ▪ Network isolation and runtime isolation is interesting

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 raspython3
 usanchuu
 shumei_ito
 kzkhykw1991
 kenichiodo
 pfn
 persolserverworks
 akhino
 glaforge
 odashi
 teamlab
 minorun365
 eitanlees
 kimpetersen
 jacobtomlinson
 akashhashmi
 maltzj
 trallard
 ryanjones
 aleyda
 jcasabona
 philnash
 palkan
 scottboms