Upgrade to Pro — share decks privately, control downloads, hide ads and more …

JAWS-UG EXPERT ONLINE: Identity and Access Mana...

JAWS-UG EXPERT ONLINE: Identity and Access Management (IAM) で困らないために

サポート現場から見たIAMあるあると対策

Avatar for Shun Kushigami

Shun Kushigami

July 08, 2026

More Decks by Shun Kushigami

Other Decks in Technology

Transcript

  1. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Identity and Access Management (IAM) で困らないために JAWS-UG EXPERT ONLINE / 2026年7⽉ 〜 サポート現場から⾒たIAMあるあると対策 〜 串上 俊(Shun Kushigami), Sr. Cloud Support Engineer
  2. © 2026, Amazon Web Services, Inc. or its affiliates. All

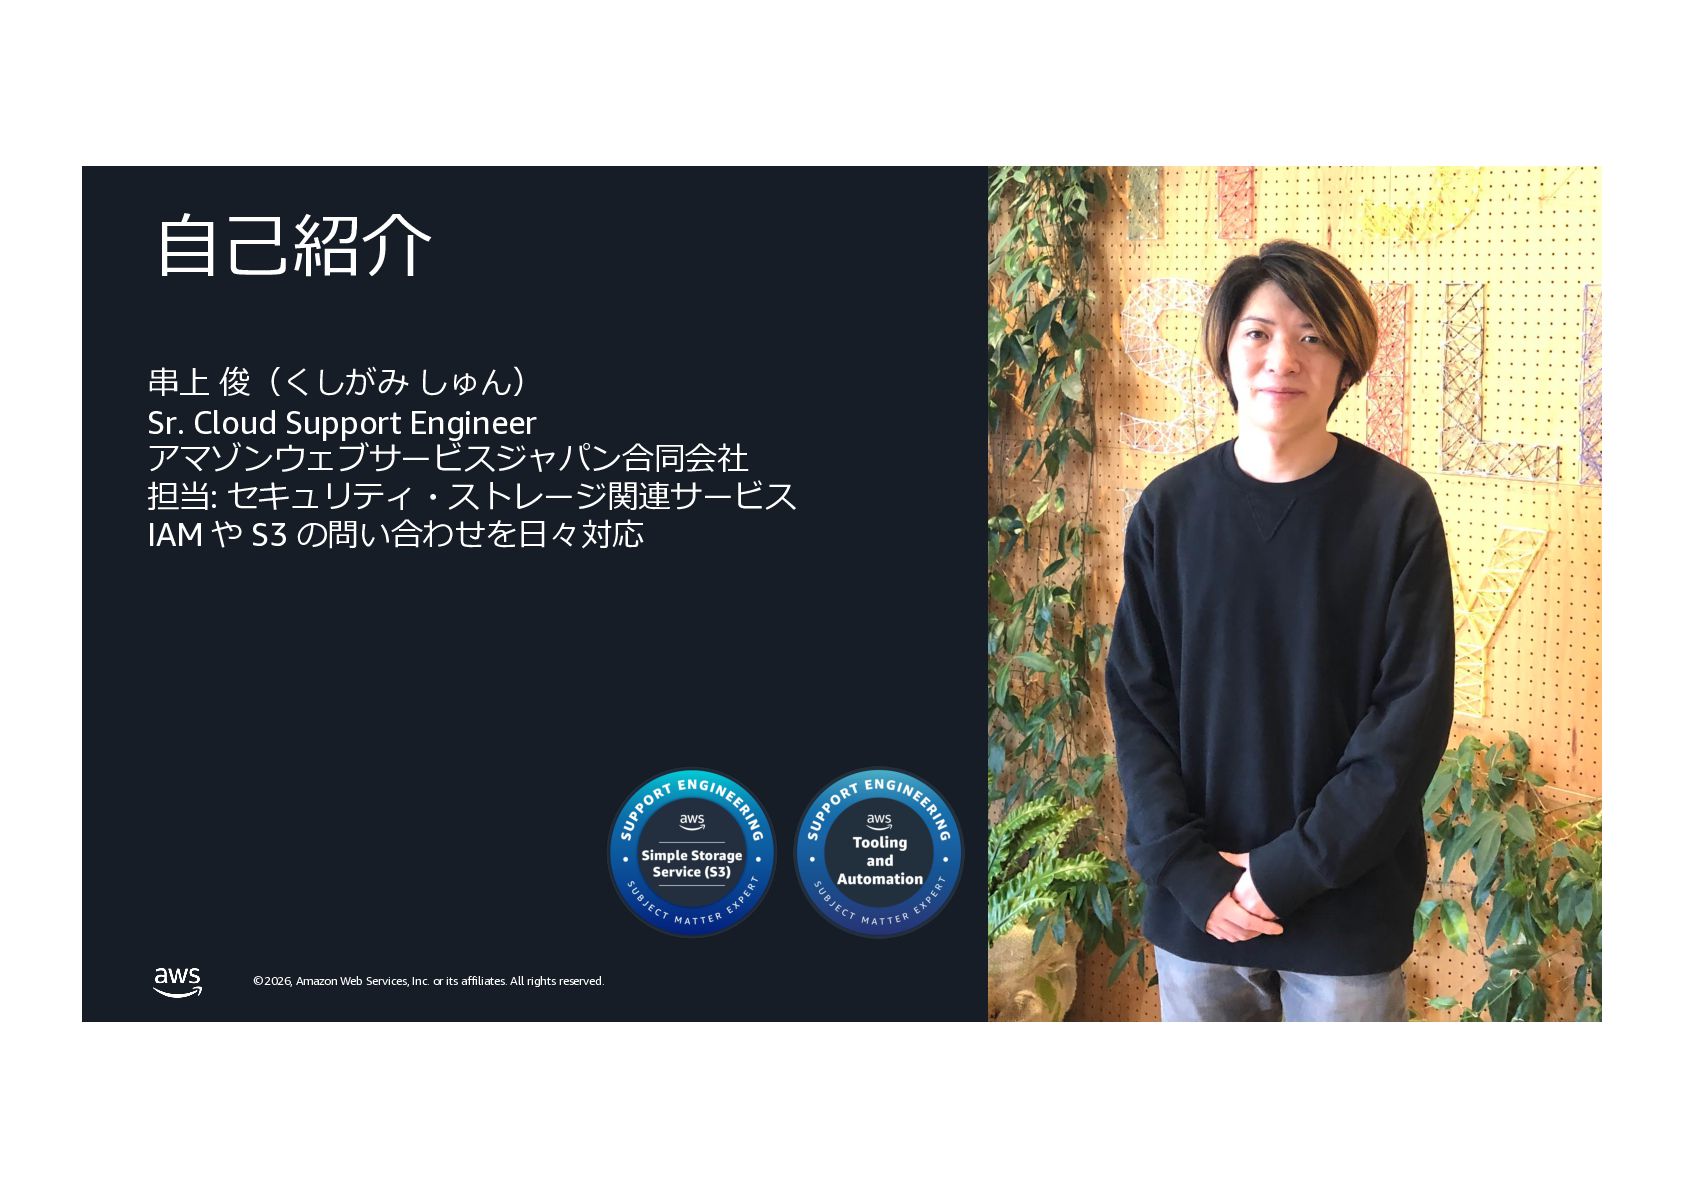
    rights reserved. ⾃⼰紹介 串上 俊(くしがみ しゅん) Sr. Cloud Support Engineer アマゾンウェブサービスジャパン合同会社 担当: セキュリティ・ストレージ関連サービス IAM や S3 の問い合わせを⽇々対応
  3. © 2026, Amazon Web Services, Inc. or its affiliates. All

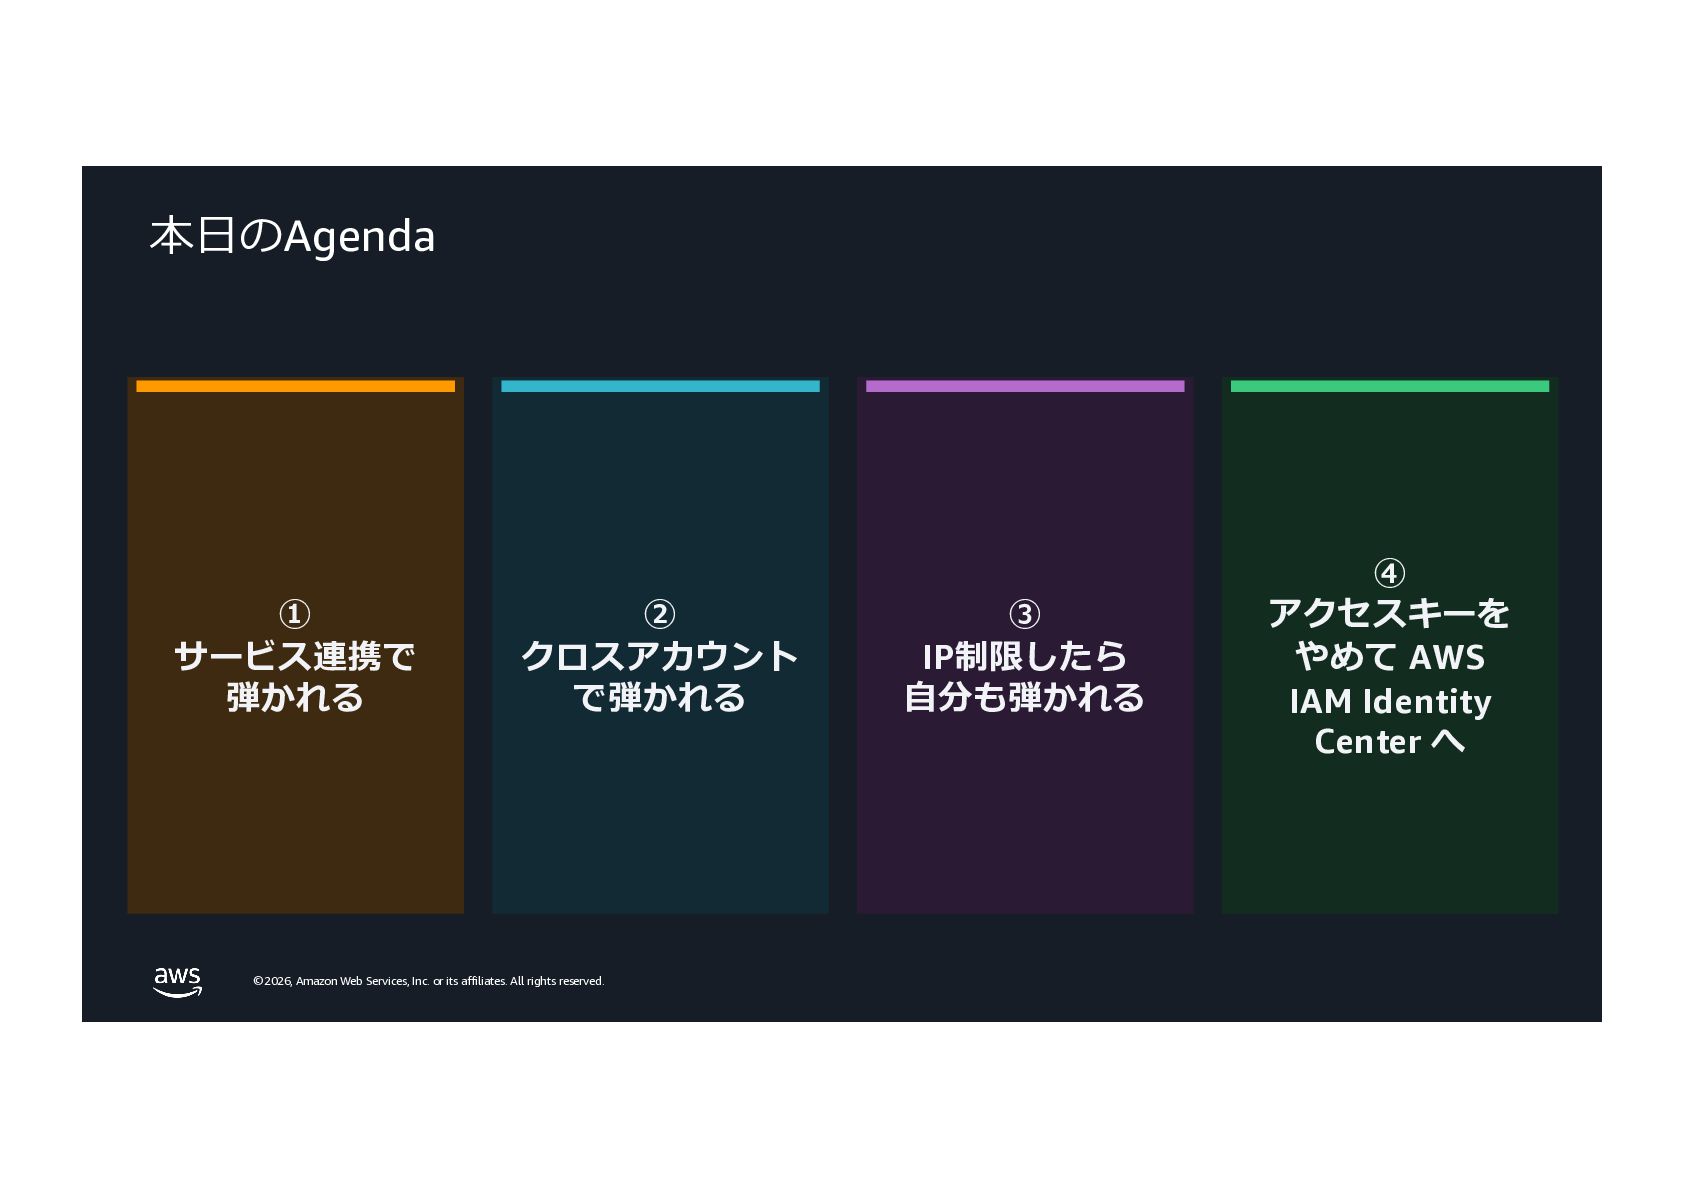
    rights reserved. 本⽇のAgenda ① サービス連携で 弾かれる ② クロスアカウント で弾かれる ③ IP制限したら ⾃分も弾かれる ④ アクセスキーを やめて AWS IAM Identity Center へ
  4. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. あるある #1: サービス連携で弾かれる
  5. © 2026, Amazon Web Services, Inc. or its affiliates. All

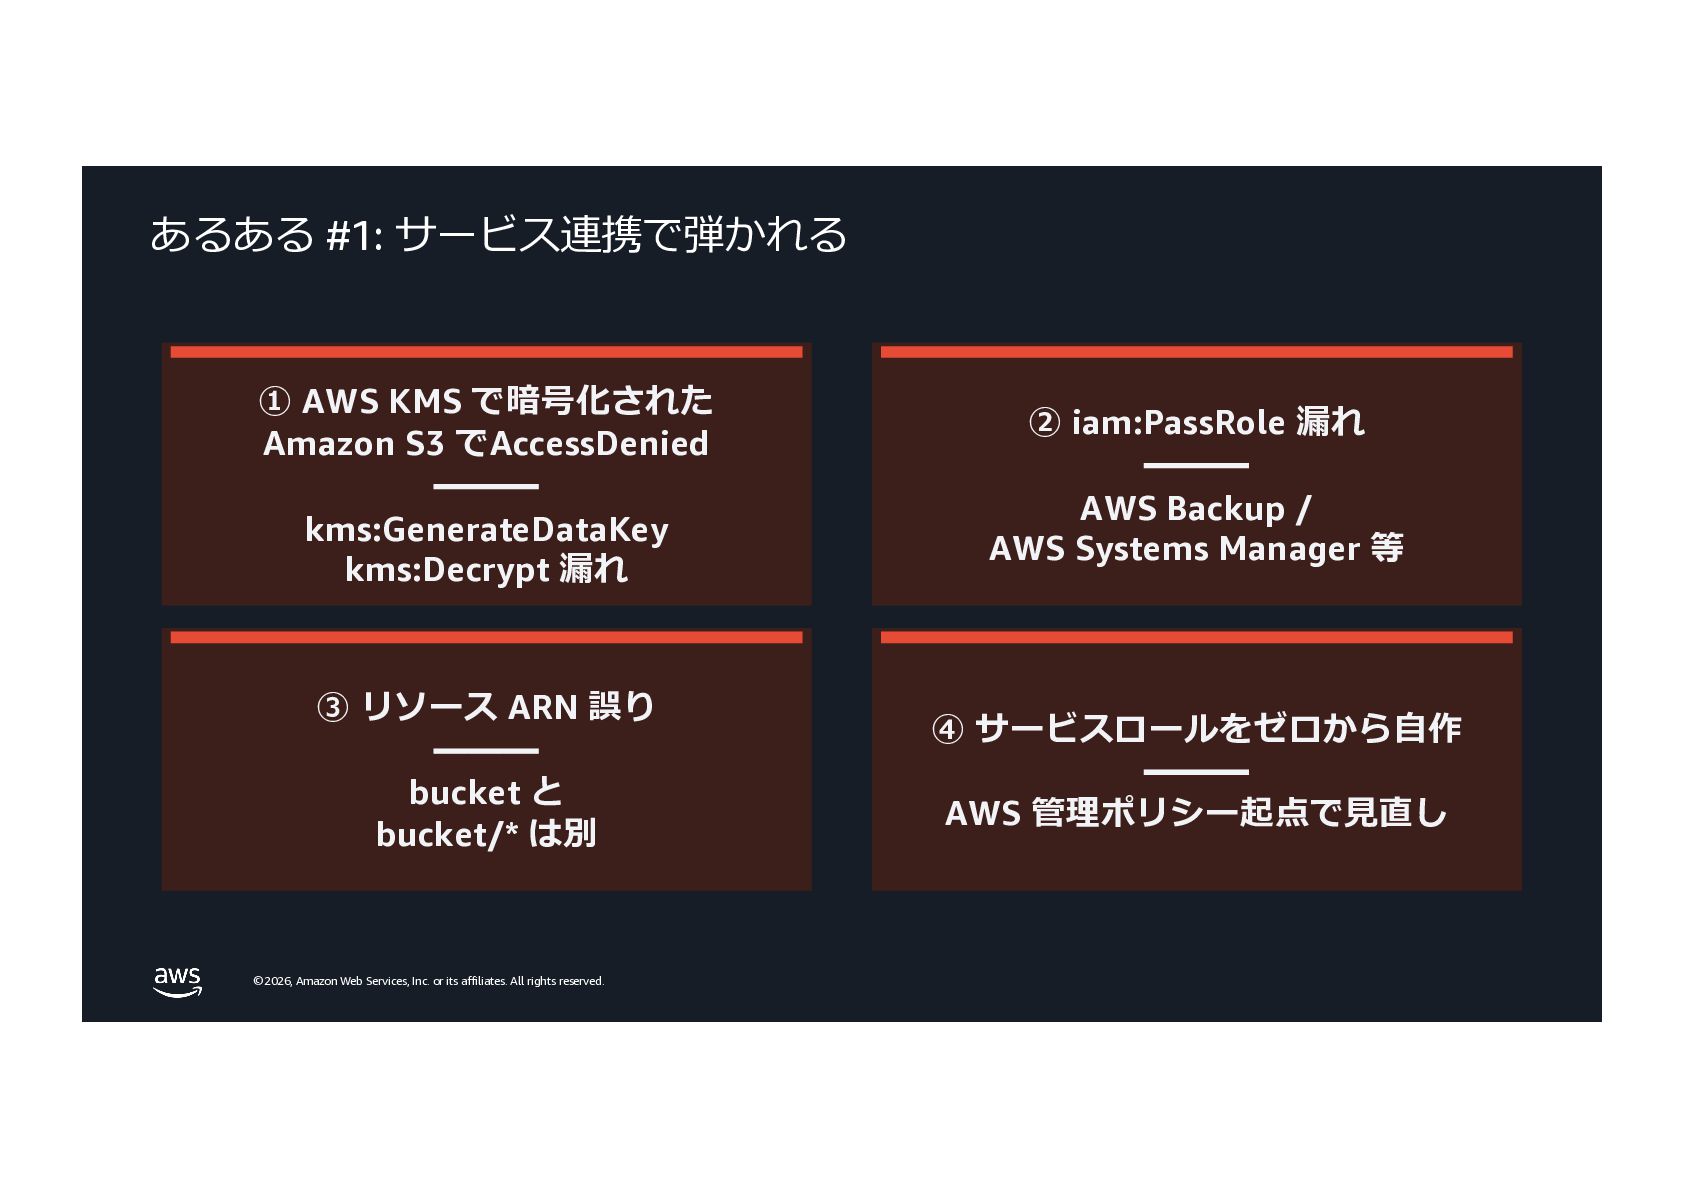
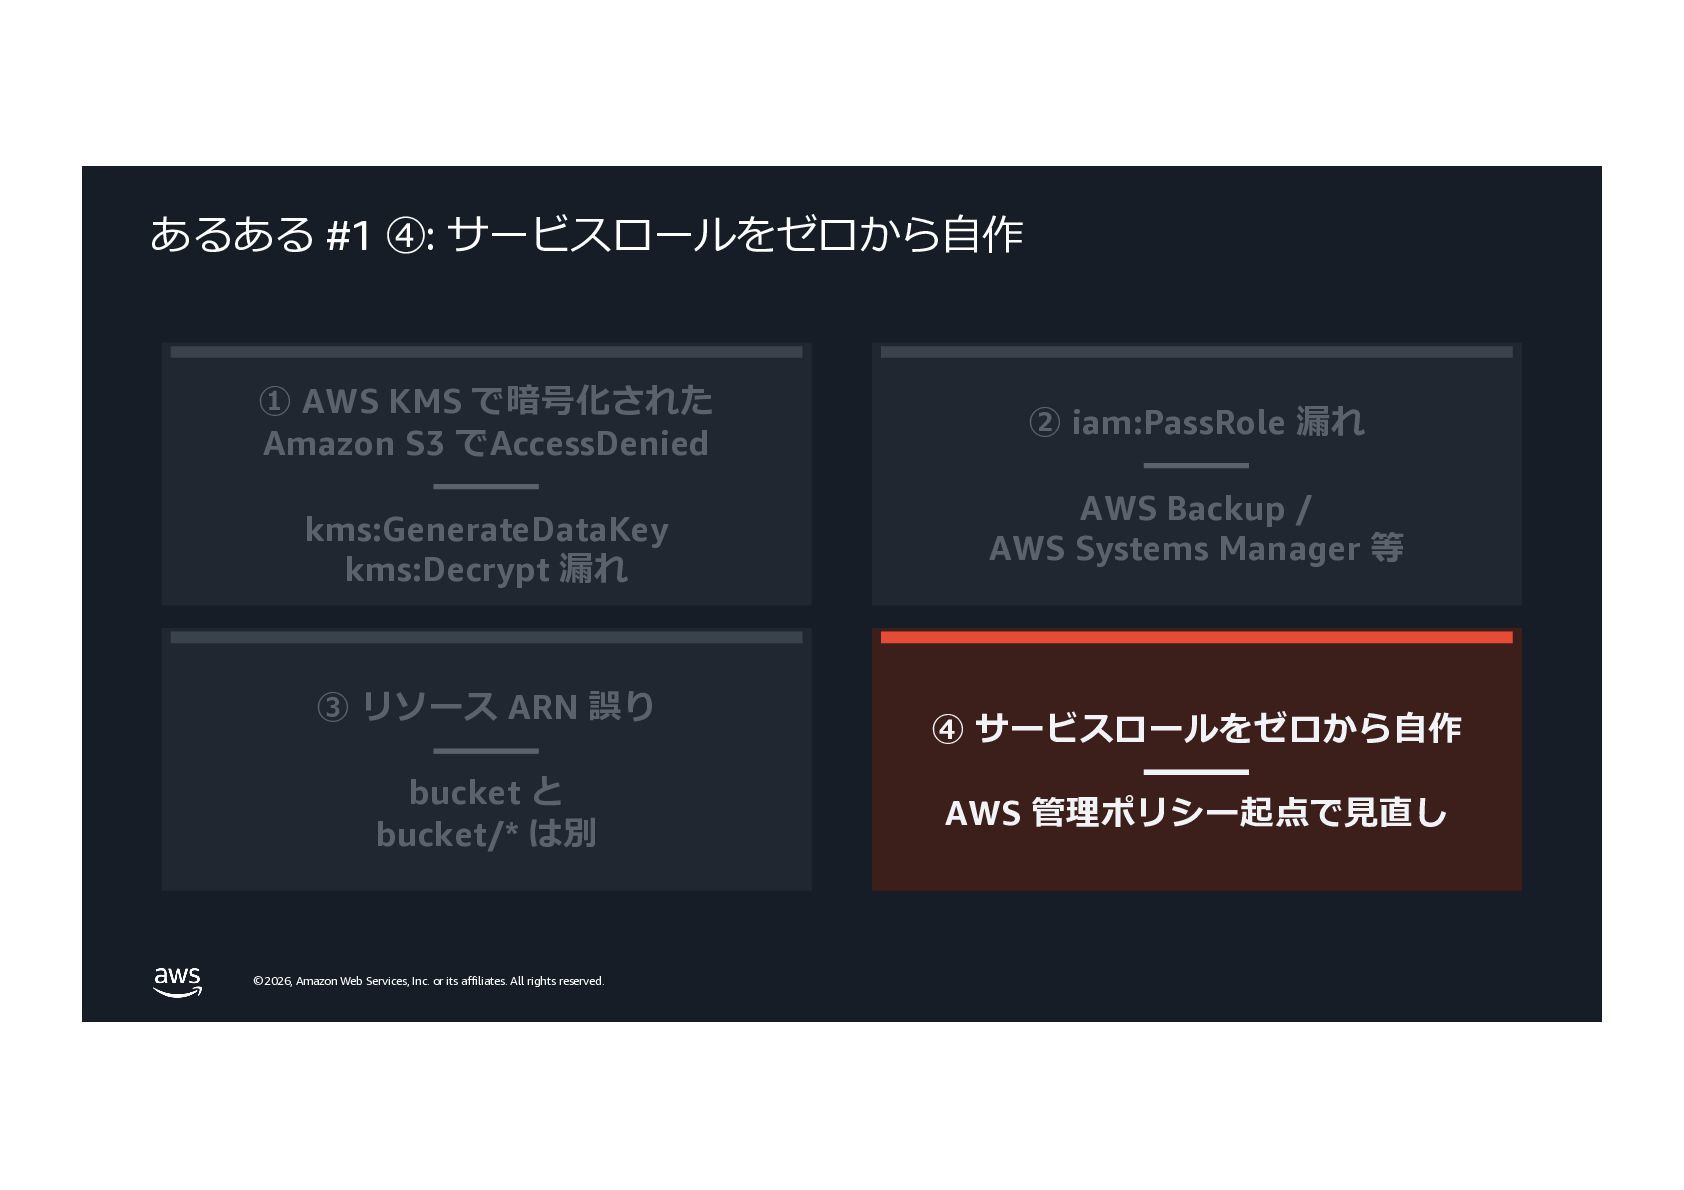
    rights reserved. あるある #1: サービス連携で弾かれる ① AWS KMS で暗号化された Amazon S3 でAccessDenied ━━━ kms:GenerateDataKey kms:Decrypt 漏れ ② iam:PassRole 漏れ ━━━ AWS Backup / AWS Systems Manager 等 ③ リソース ARN 誤り ━━━ bucket と bucket/* は別 ④ サービスロールをゼロから⾃作 ━━━ AWS 管理ポリシー起点で⾒直し
  6. © 2026, Amazon Web Services, Inc. or its affiliates. All

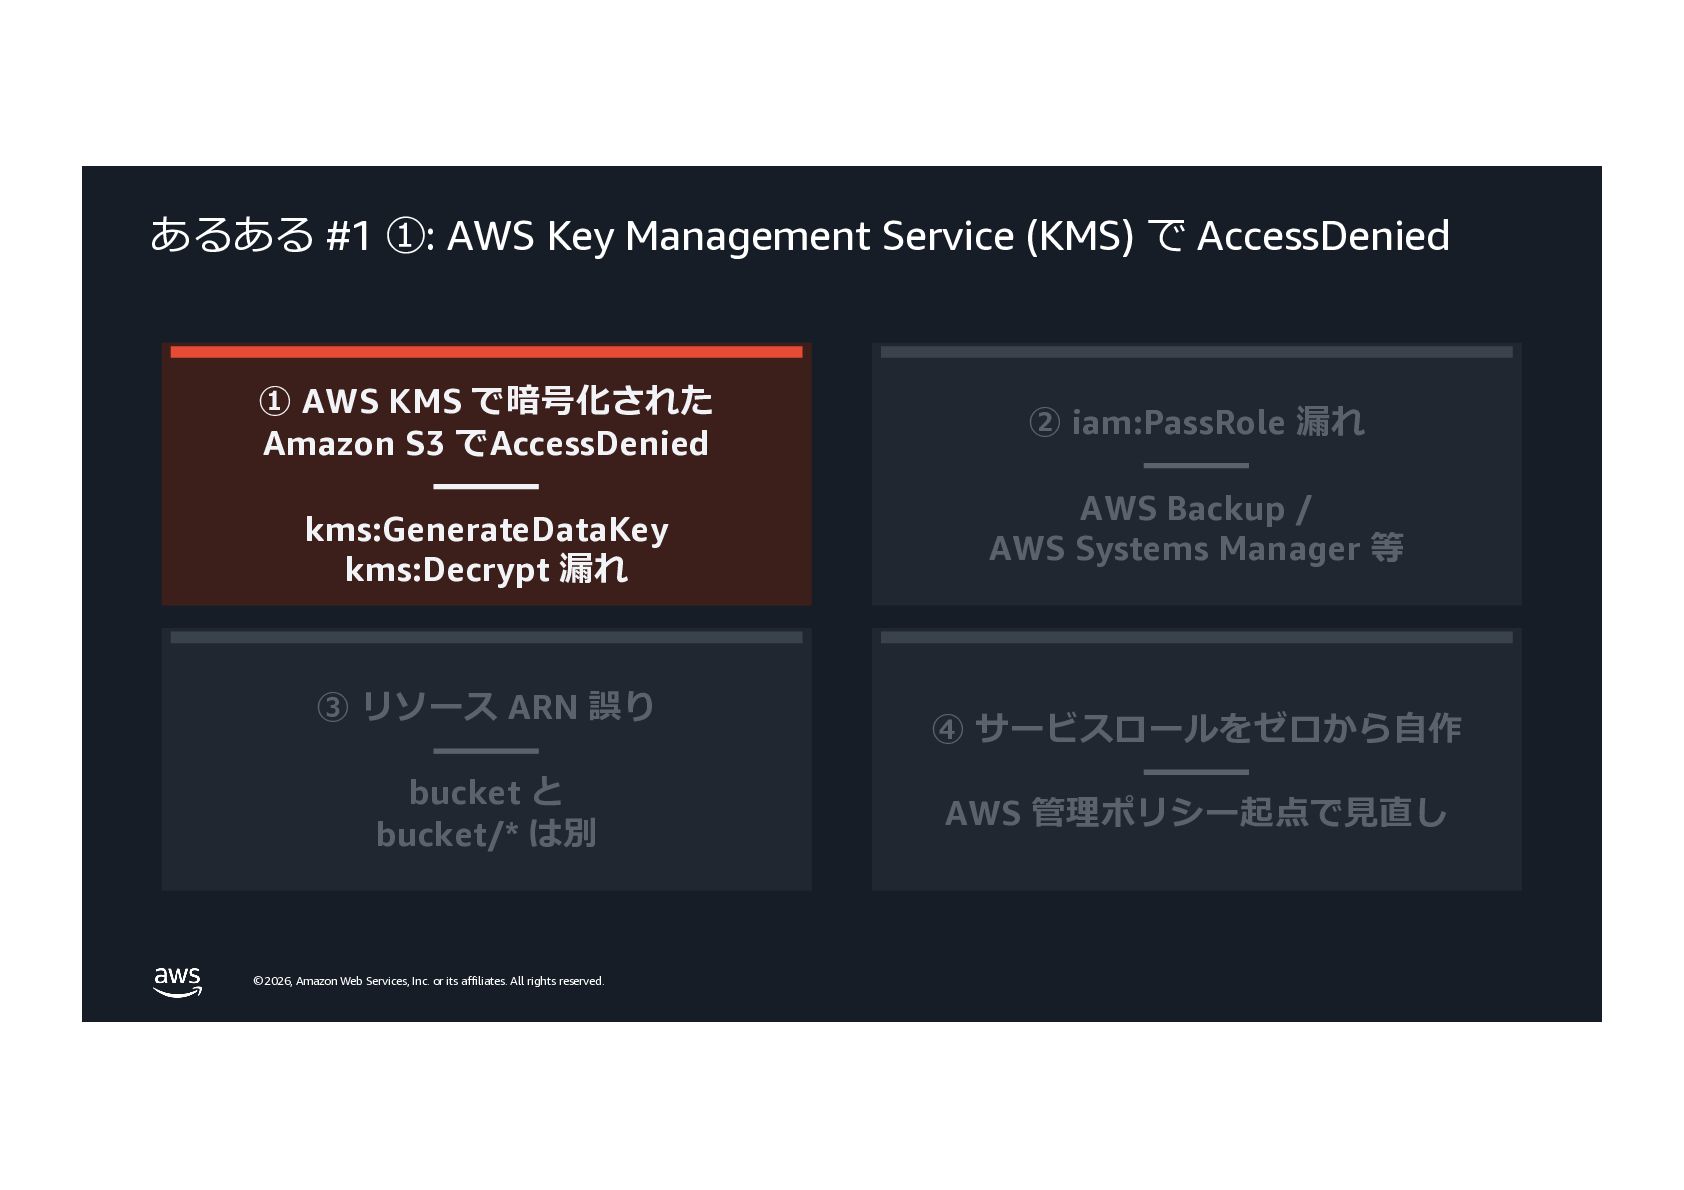
    rights reserved. あるある #1 ①: AWS Key Management Service (KMS) で AccessDenied ① AWS KMS で暗号化された Amazon S3 でAccessDenied ━━━ kms:GenerateDataKey kms:Decrypt 漏れ ② iam:PassRole 漏れ ━━━ AWS Backup / AWS Systems Manager 等 ③ リソース ARN 誤り ━━━ bucket と bucket/* は別 ④ サービスロールをゼロから⾃作 ━━━ AWS 管理ポリシー起点で⾒直し
  7. © 2026, Amazon Web Services, Inc. or its affiliates. All

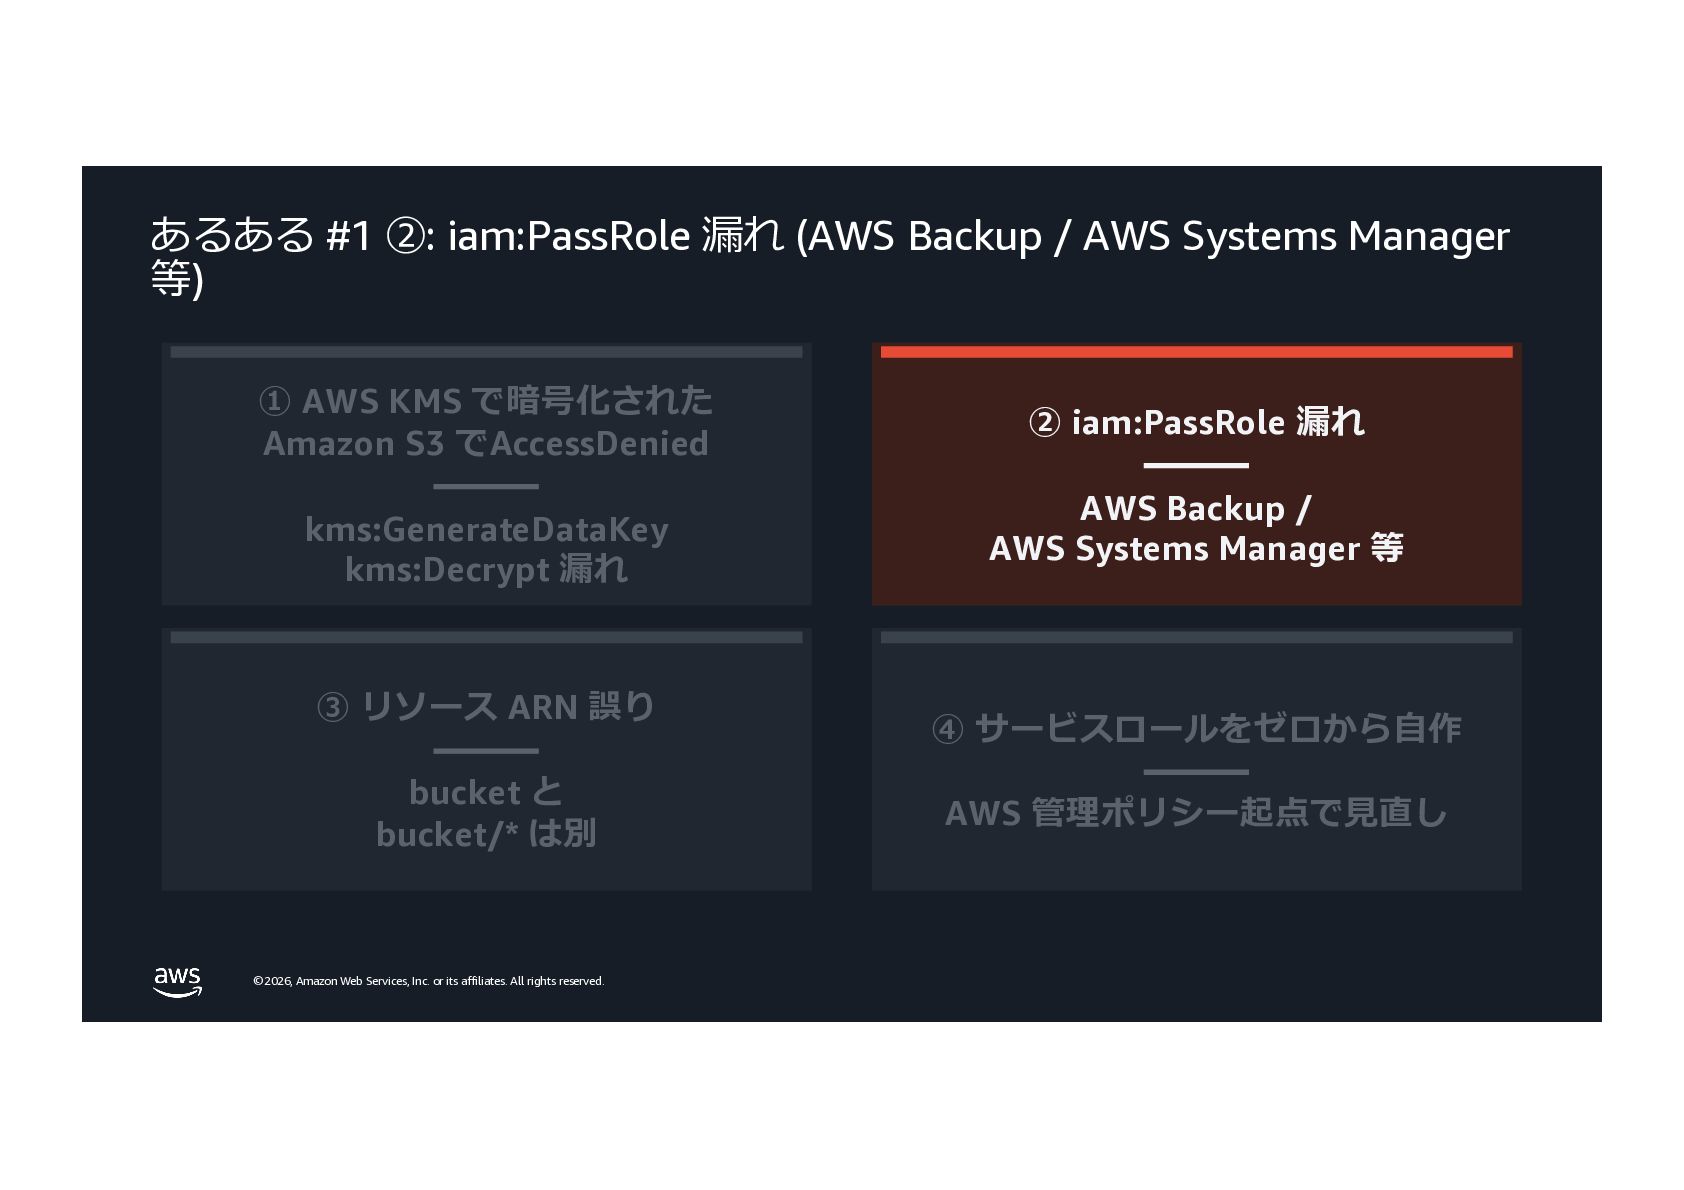
    rights reserved. あるある #1 ②: iam:PassRole 漏れ (AWS Backup / AWS Systems Manager 等) ① AWS KMS で暗号化された Amazon S3 でAccessDenied ━━━ kms:GenerateDataKey kms:Decrypt 漏れ ② iam:PassRole 漏れ ━━━ AWS Backup / AWS Systems Manager 等 ③ リソース ARN 誤り ━━━ bucket と bucket/* は別 ④ サービスロールをゼロから⾃作 ━━━ AWS 管理ポリシー起点で⾒直し
  8. © 2026, Amazon Web Services, Inc. or its affiliates. All

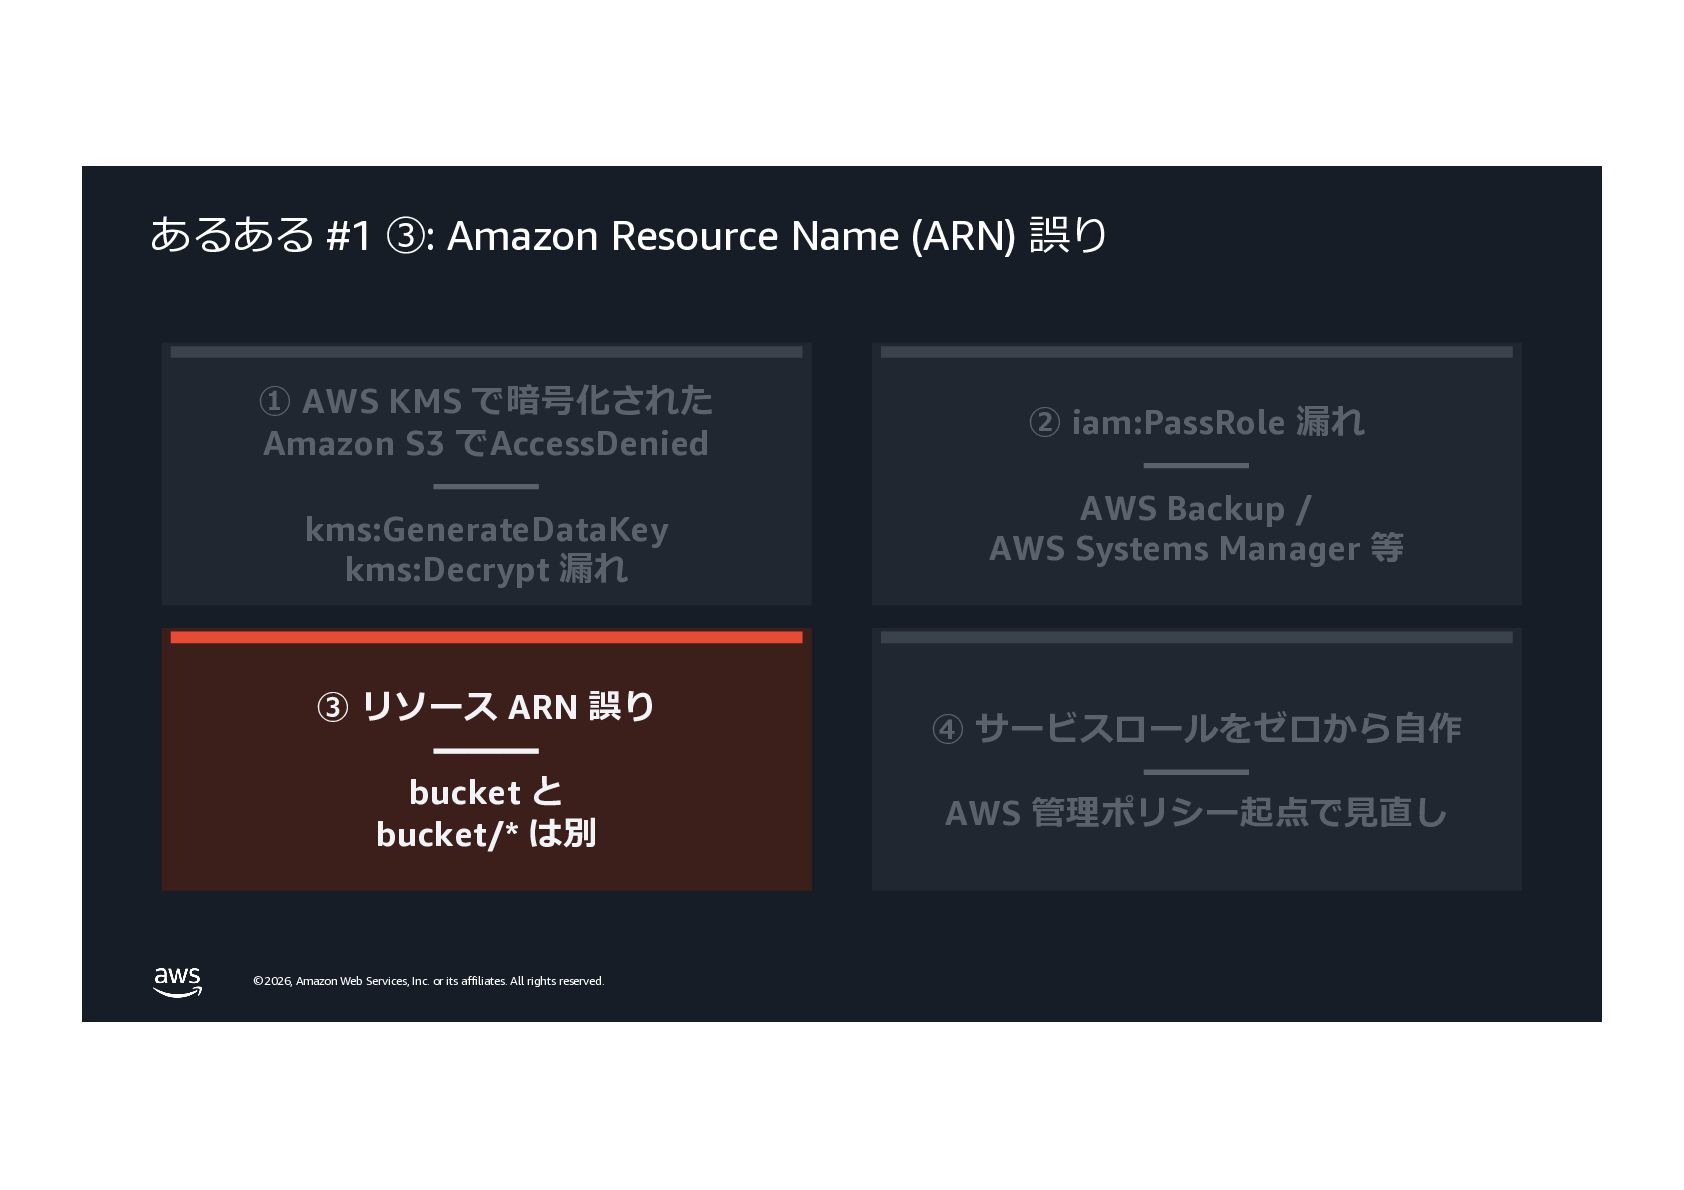
    rights reserved. あるある #1 ③: Amazon Resource Name (ARN) 誤り ① AWS KMS で暗号化された Amazon S3 でAccessDenied ━━━ kms:GenerateDataKey kms:Decrypt 漏れ ② iam:PassRole 漏れ ━━━ AWS Backup / AWS Systems Manager 等 ③ リソース ARN 誤り ━━━ bucket と bucket/* は別 ④ サービスロールをゼロから⾃作 ━━━ AWS 管理ポリシー起点で⾒直し
  9. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. あるある #1 ④: サービスロールをゼロから⾃作 ① AWS KMS で暗号化された Amazon S3 でAccessDenied ━━━ kms:GenerateDataKey kms:Decrypt 漏れ ② iam:PassRole 漏れ ━━━ AWS Backup / AWS Systems Manager 等 ③ リソース ARN 誤り ━━━ bucket と bucket/* は別 ④ サービスロールをゼロから⾃作 ━━━ AWS 管理ポリシー起点で⾒直し
  10. © 2026, Amazon Web Services, Inc. or its affiliates. All

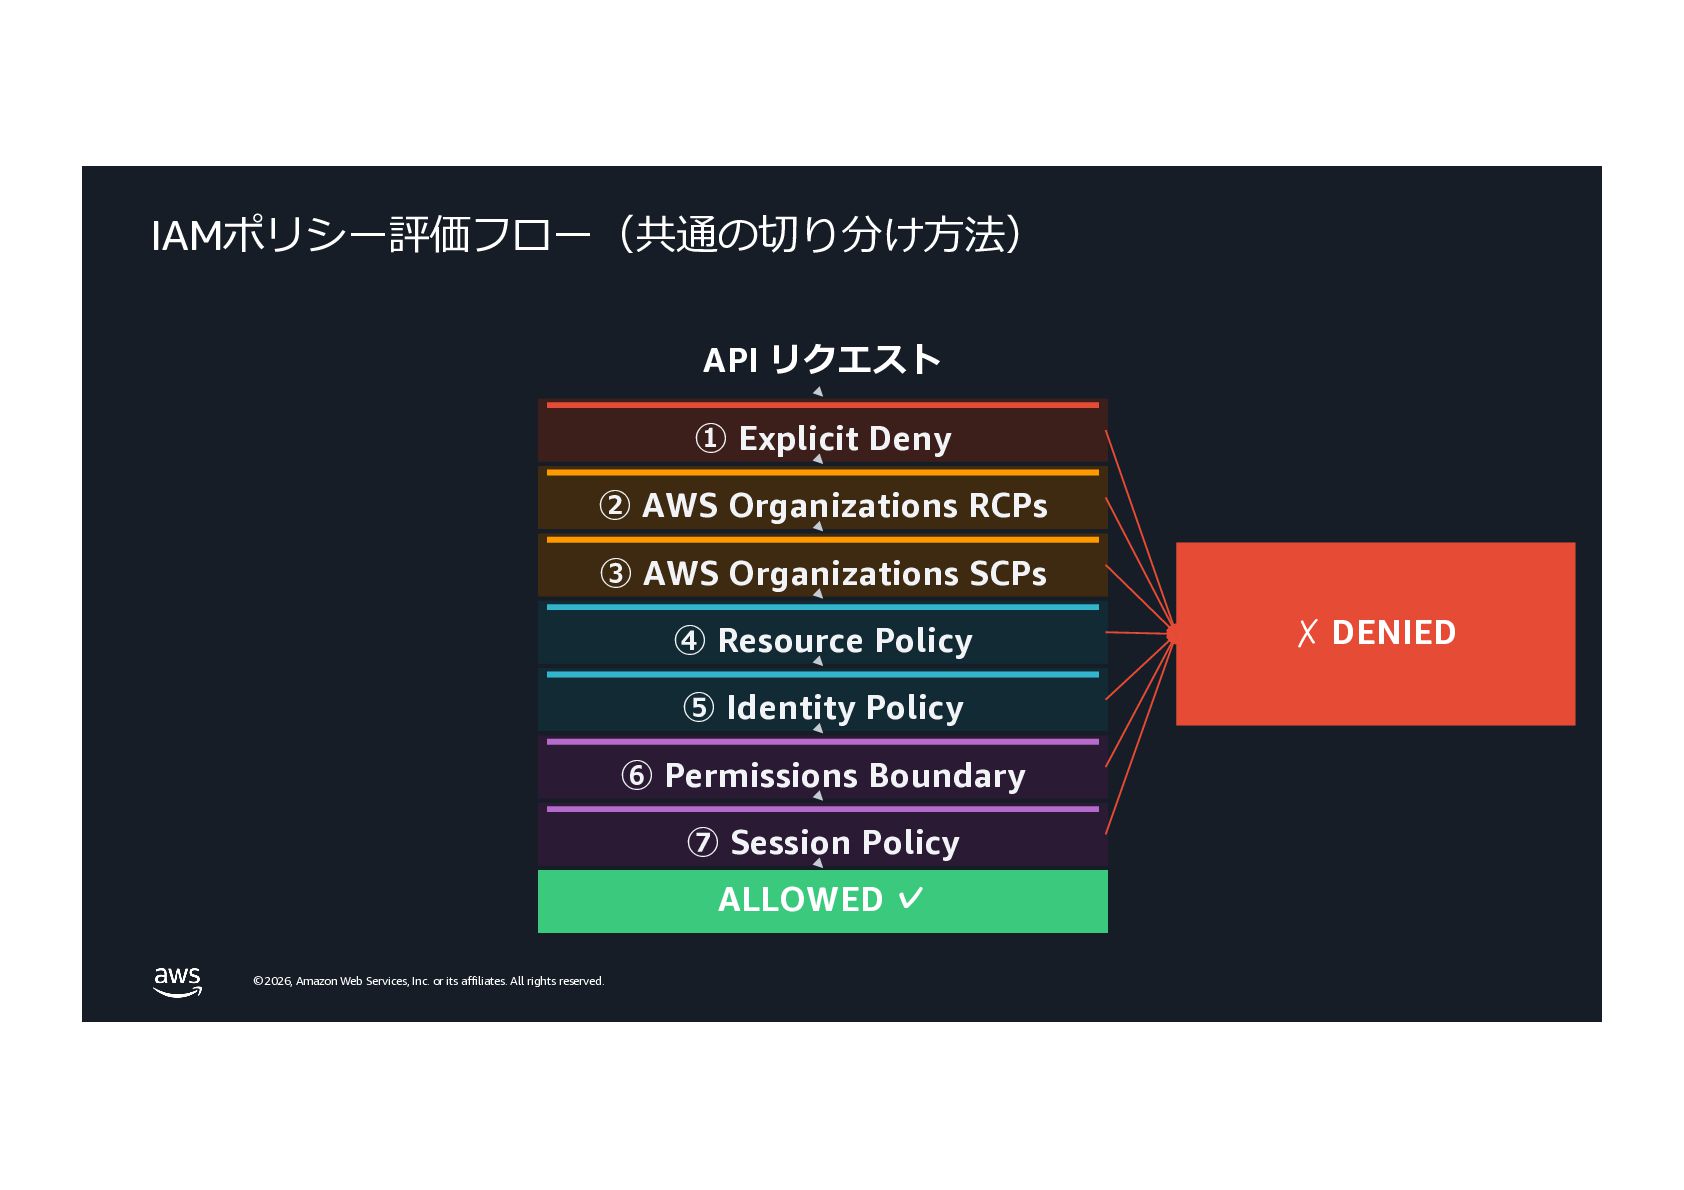
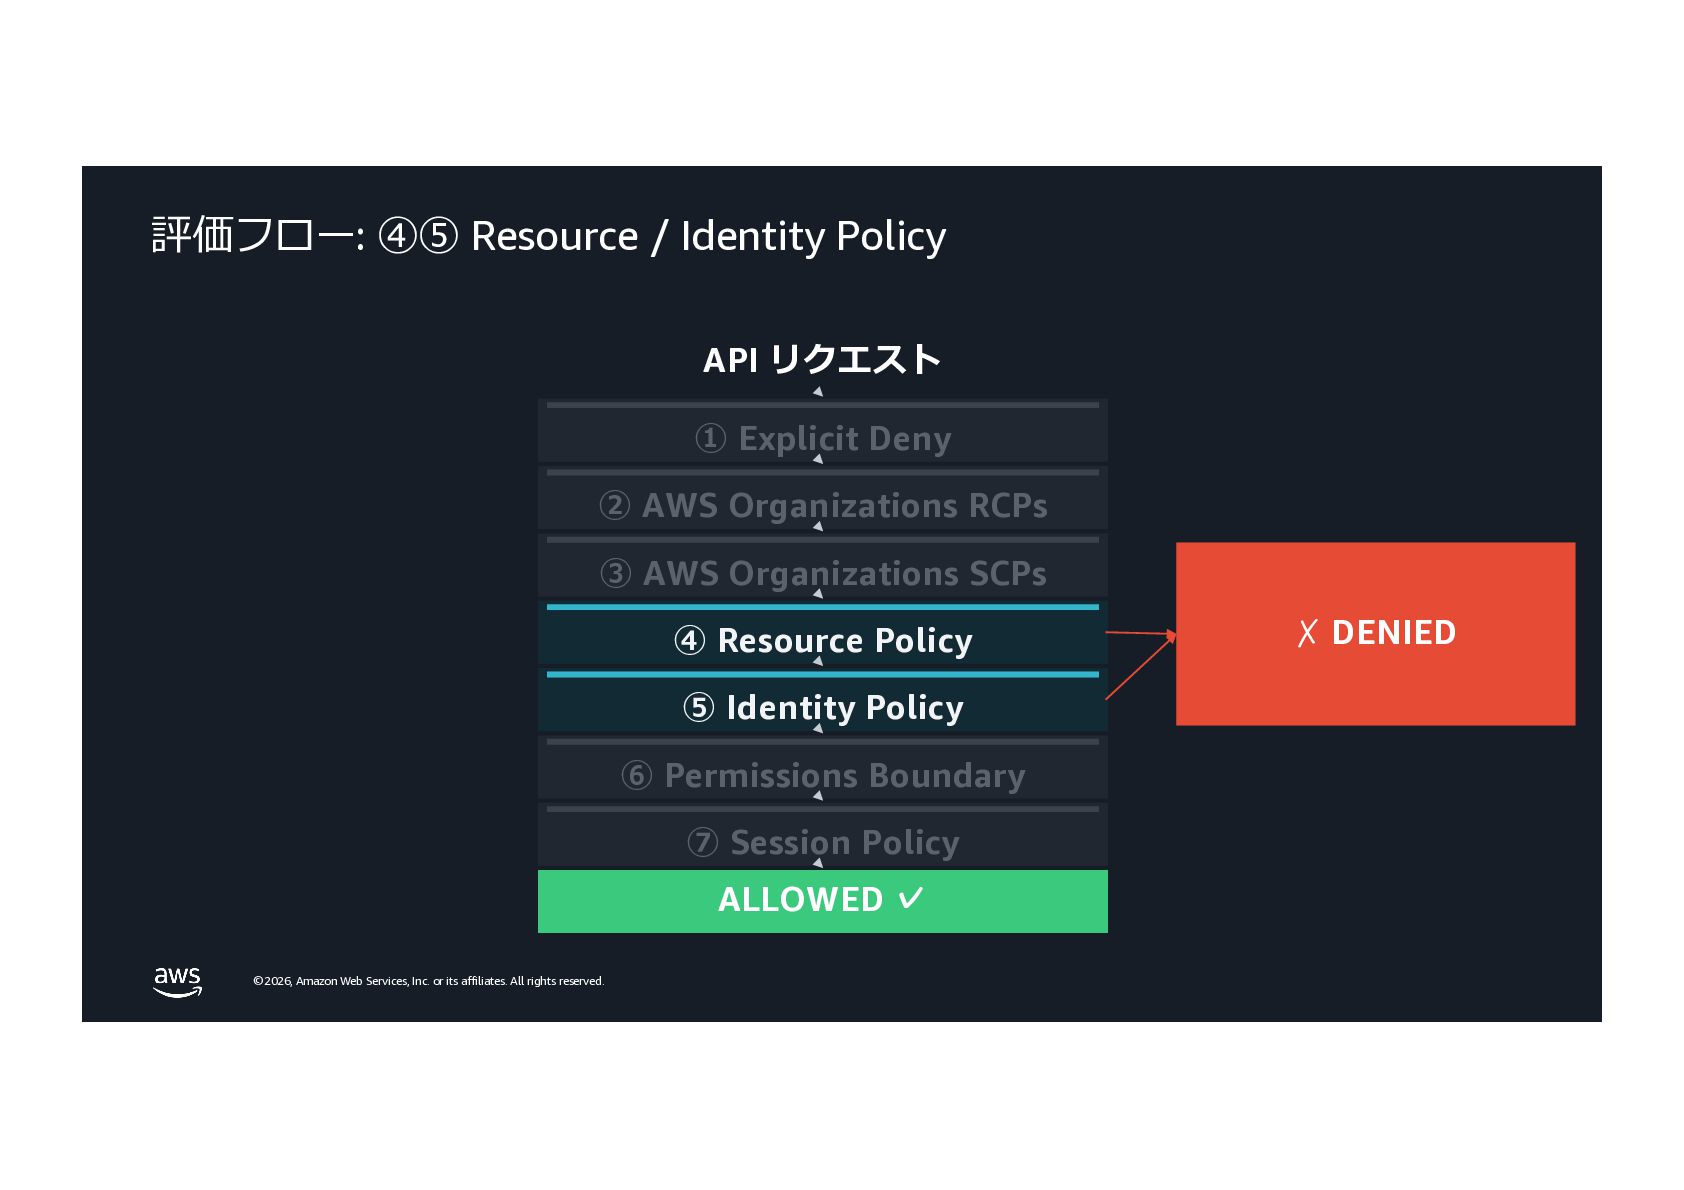
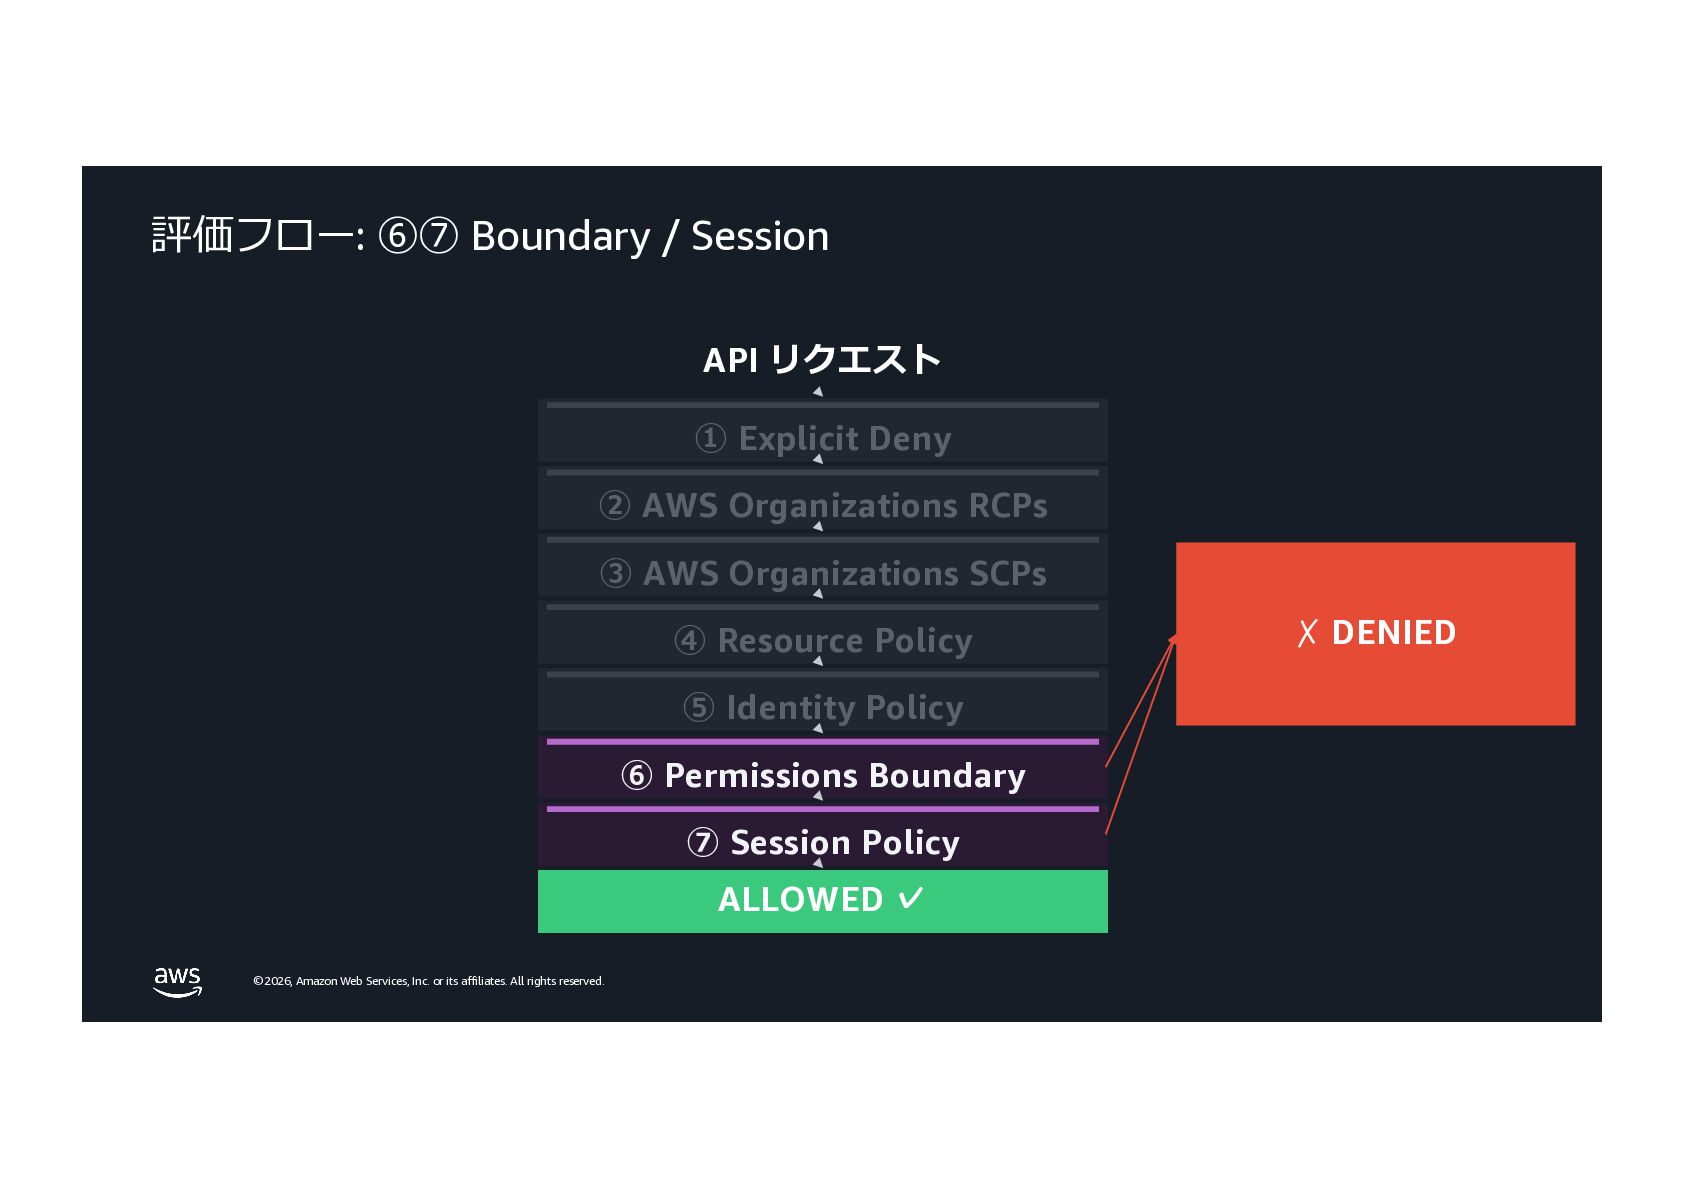
    rights reserved. IAMポリシー評価フロー(共通の切り分け⽅法) API リクエスト ① Explicit Deny ② AWS Organizations RCPs ③ AWS Organizations SCPs ④ Resource Policy ⑤ Identity Policy ⑥ Permissions Boundary ⑦ Session Policy ALLOWED ✓ ✗ DENIED
  11. © 2026, Amazon Web Services, Inc. or its affiliates. All

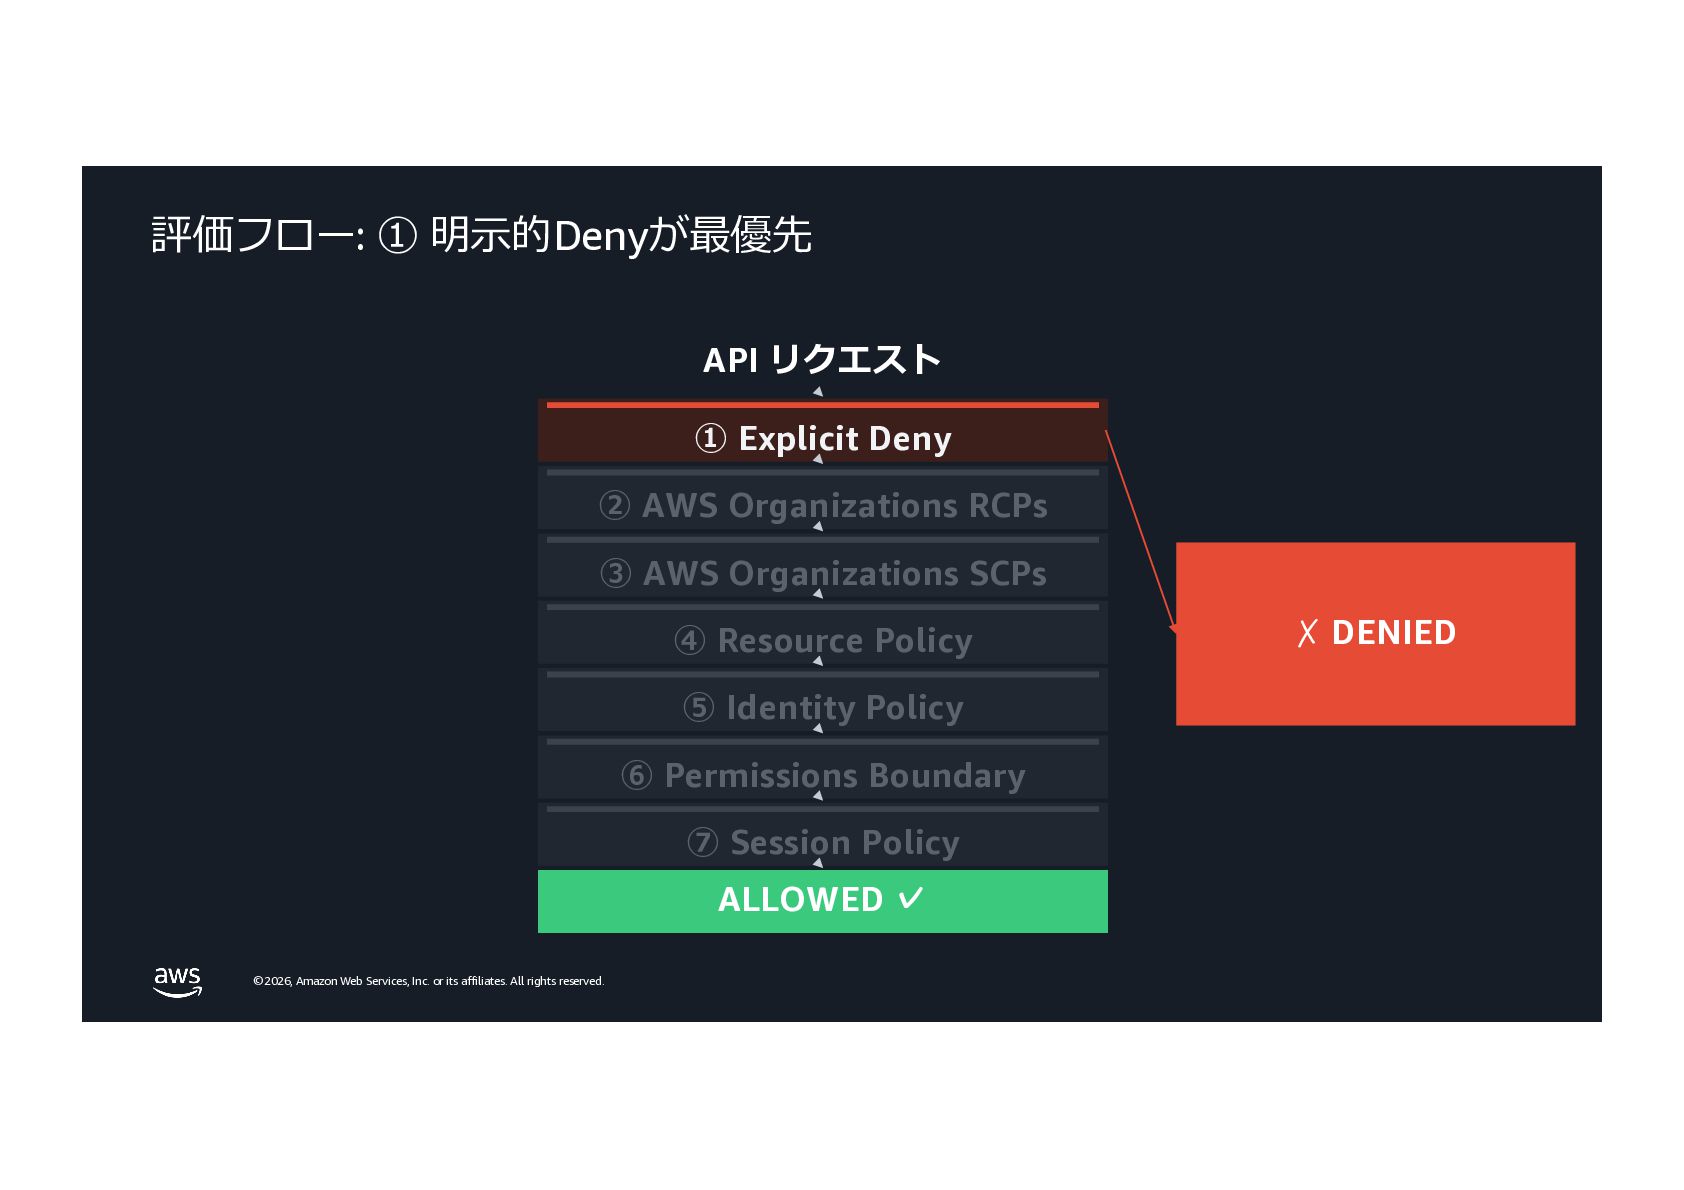
    rights reserved. 評価フロー: ① 明⽰的Denyが最優先 API リクエスト ① Explicit Deny ② AWS Organizations RCPs ③ AWS Organizations SCPs ④ Resource Policy ⑤ Identity Policy ⑥ Permissions Boundary ⑦ Session Policy ALLOWED ✓ ✗ DENIED
  12. © 2026, Amazon Web Services, Inc. or its affiliates. All

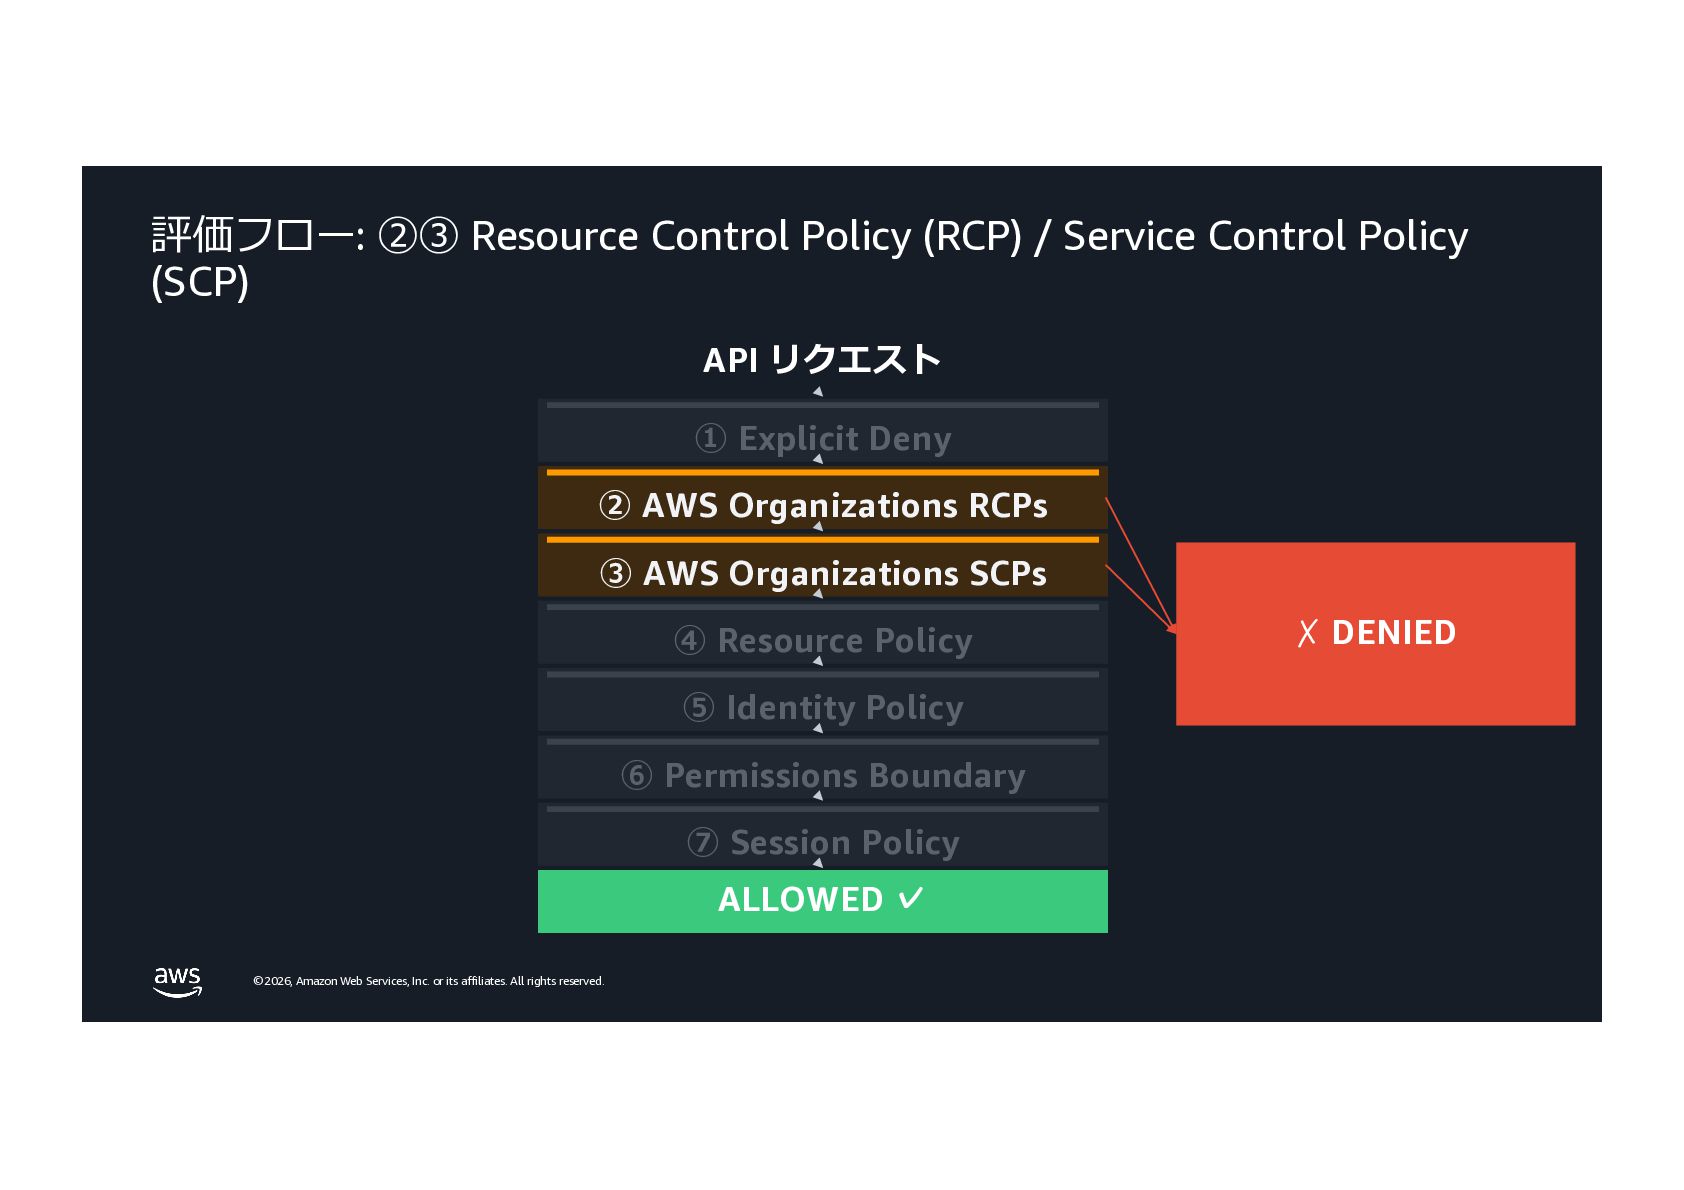
    rights reserved. 評価フロー: ②③ Resource Control Policy (RCP) / Service Control Policy (SCP) API リクエスト ① Explicit Deny ② AWS Organizations RCPs ③ AWS Organizations SCPs ④ Resource Policy ⑤ Identity Policy ⑥ Permissions Boundary ⑦ Session Policy ALLOWED ✓ ✗ DENIED
  13. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. 評価フロー: ④⑤ Resource / Identity Policy API リクエスト ① Explicit Deny ② AWS Organizations RCPs ③ AWS Organizations SCPs ④ Resource Policy ⑤ Identity Policy ⑥ Permissions Boundary ⑦ Session Policy ALLOWED ✓ ✗ DENIED
  14. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. 評価フロー: ⑥⑦ Boundary / Session API リクエスト ① Explicit Deny ② AWS Organizations RCPs ③ AWS Organizations SCPs ④ Resource Policy ⑤ Identity Policy ⑥ Permissions Boundary ⑦ Session Policy ALLOWED ✓ ✗ DENIED
  15. © 2026, Amazon Web Services, Inc. or its affiliates. All

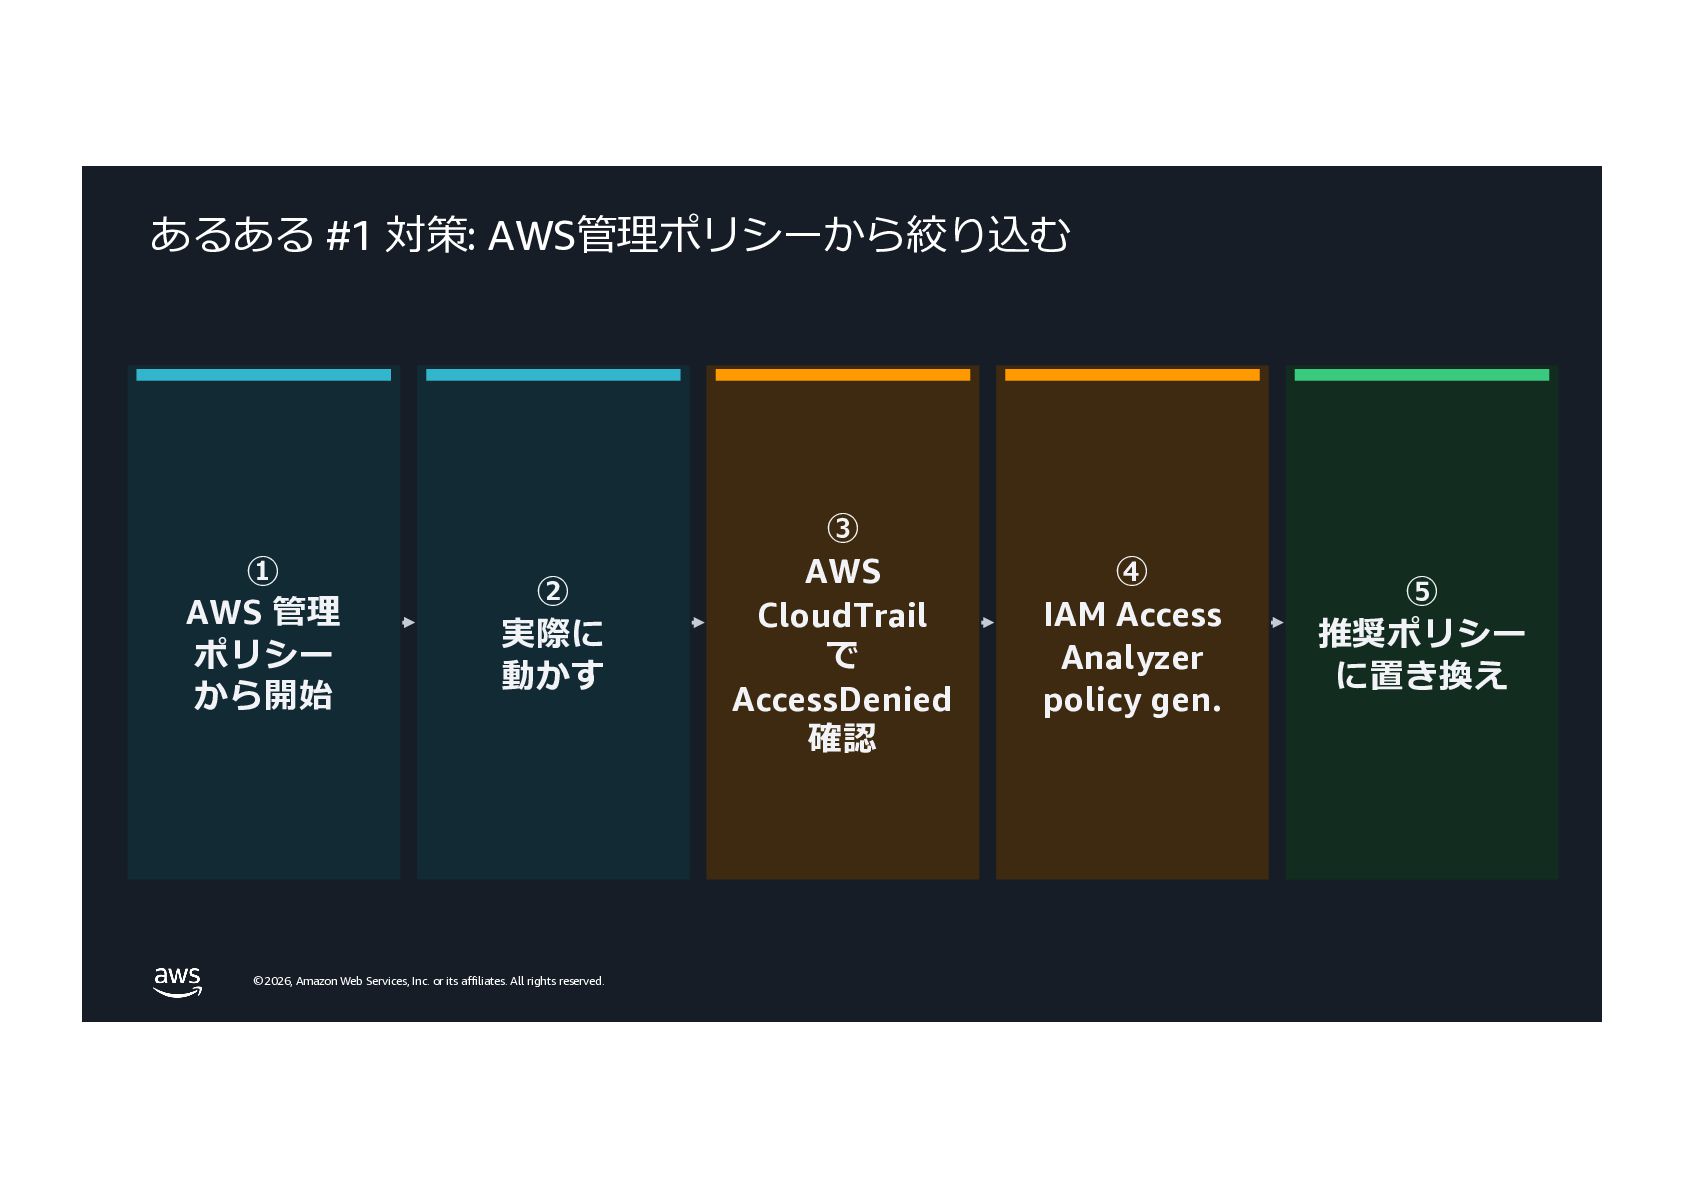
    rights reserved. あるある #1 対策: AWS管理ポリシーから絞り込む ① AWS 管理 ポリシー から開始 ② 実際に 動かす ③ AWS CloudTrail で AccessDenied 確認 ④ IAM Access Analyzer policy gen. ⑤ 推奨ポリシー に置き換え
  16. © 2026, Amazon Web Services, Inc. or its affiliates. All

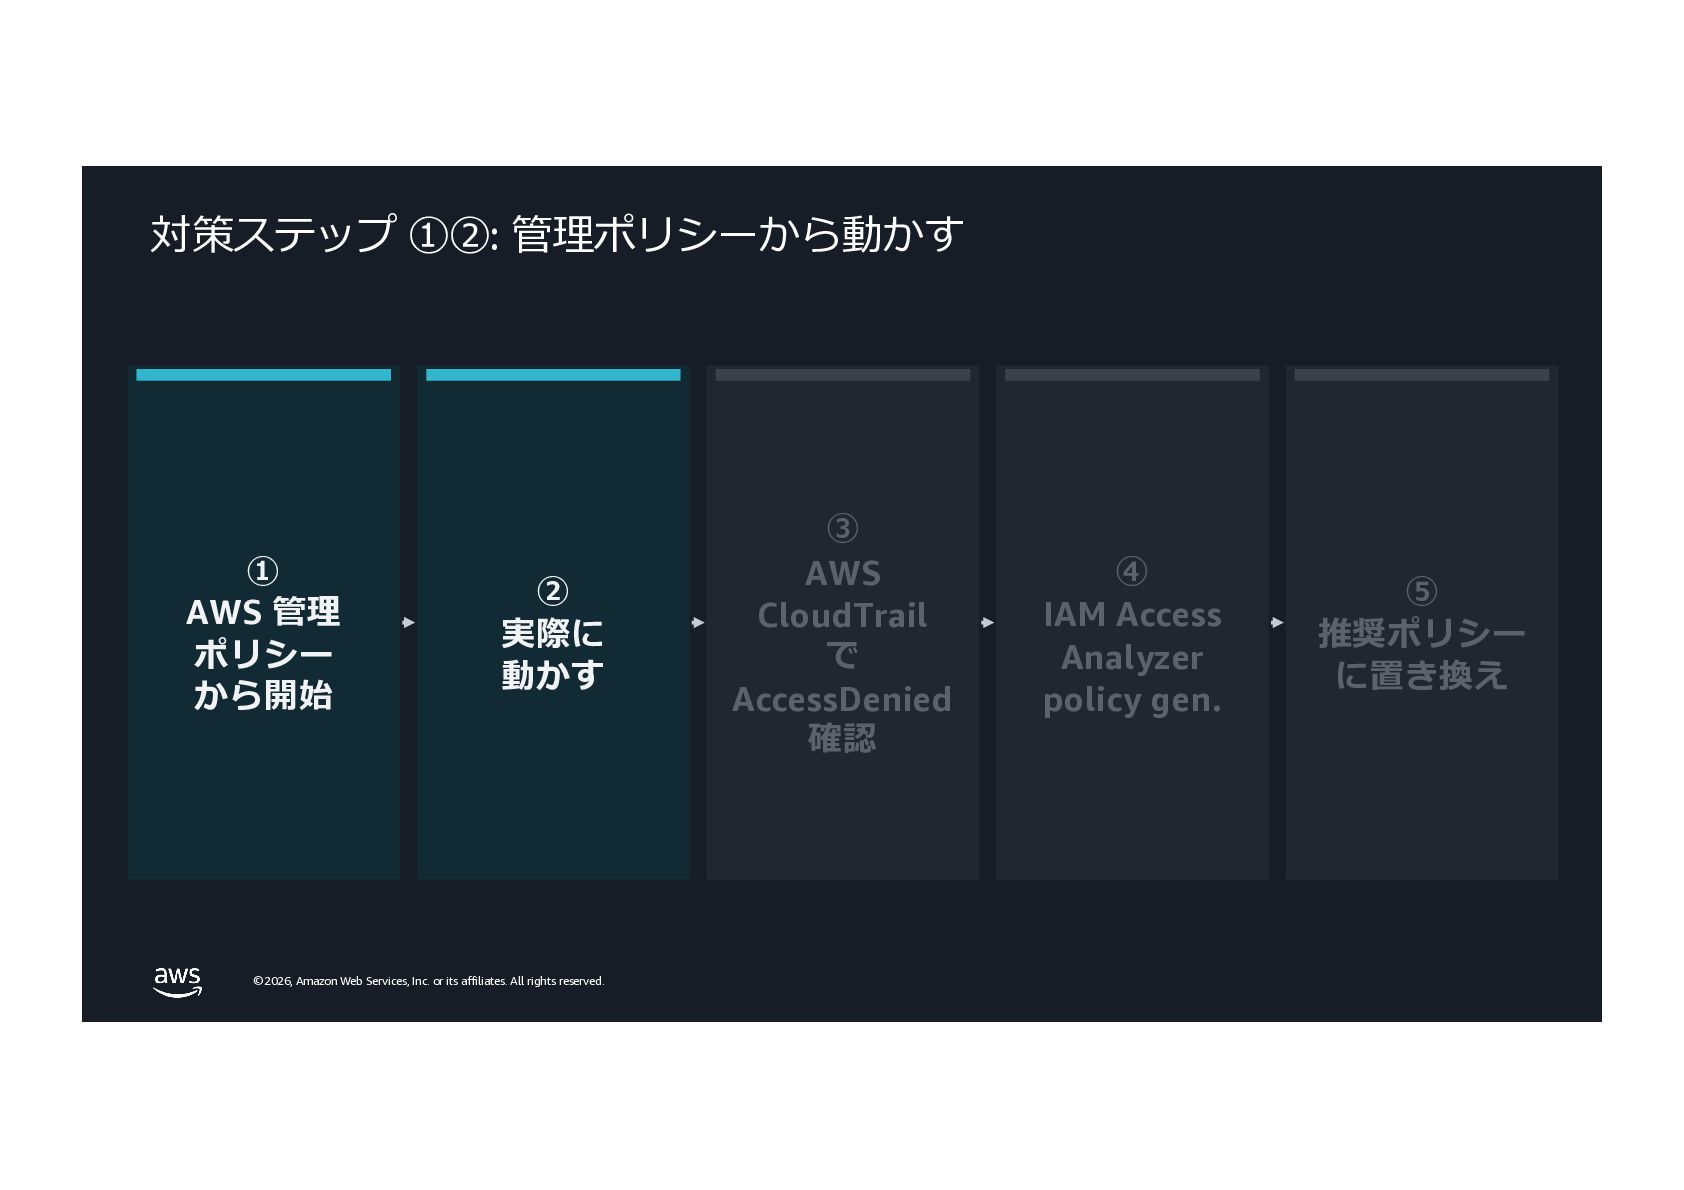
    rights reserved. 対策ステップ ①②: 管理ポリシーから動かす ① AWS 管理 ポリシー から開始 ② 実際に 動かす ③ AWS CloudTrail で AccessDenied 確認 ④ IAM Access Analyzer policy gen. ⑤ 推奨ポリシー に置き換え
  17. © 2026, Amazon Web Services, Inc. or its affiliates. All

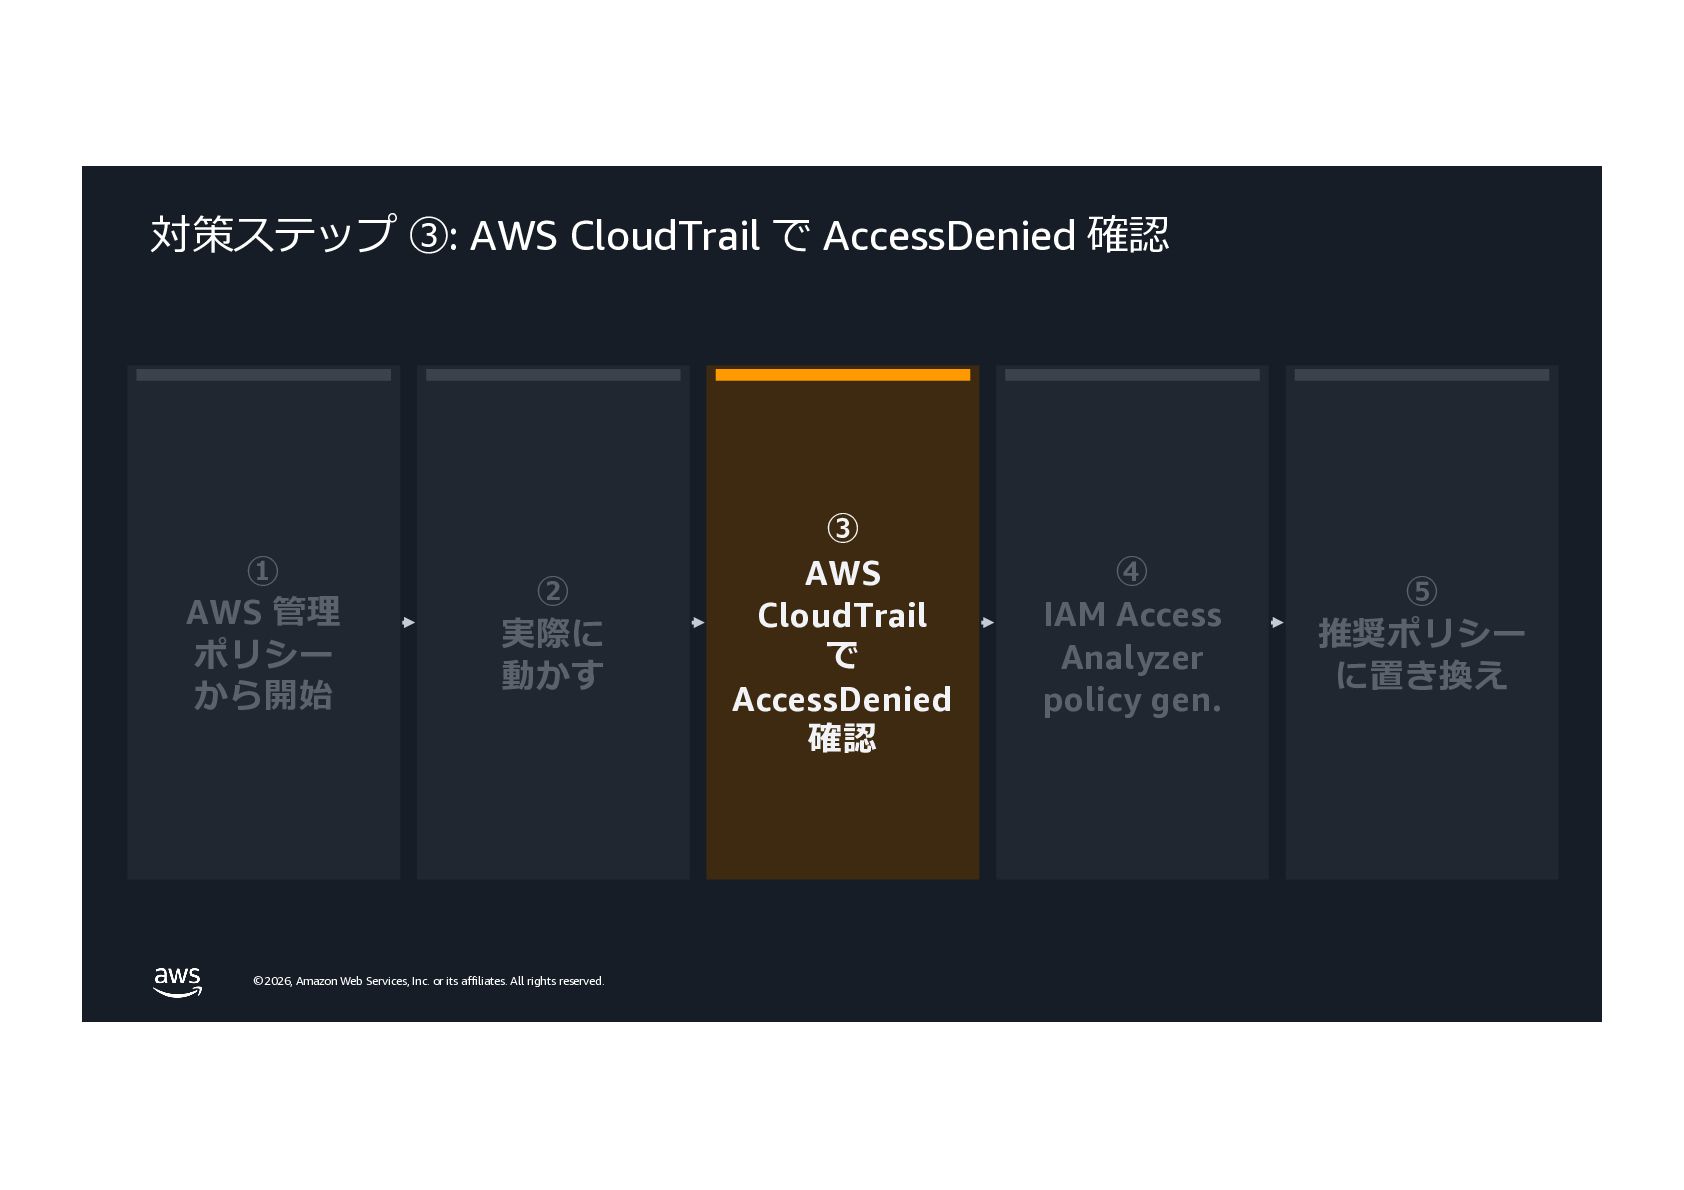
    rights reserved. 対策ステップ ③: AWS CloudTrail で AccessDenied 確認 ① AWS 管理 ポリシー から開始 ② 実際に 動かす ③ AWS CloudTrail で AccessDenied 確認 ④ IAM Access Analyzer policy gen. ⑤ 推奨ポリシー に置き換え
  18. © 2026, Amazon Web Services, Inc. or its affiliates. All

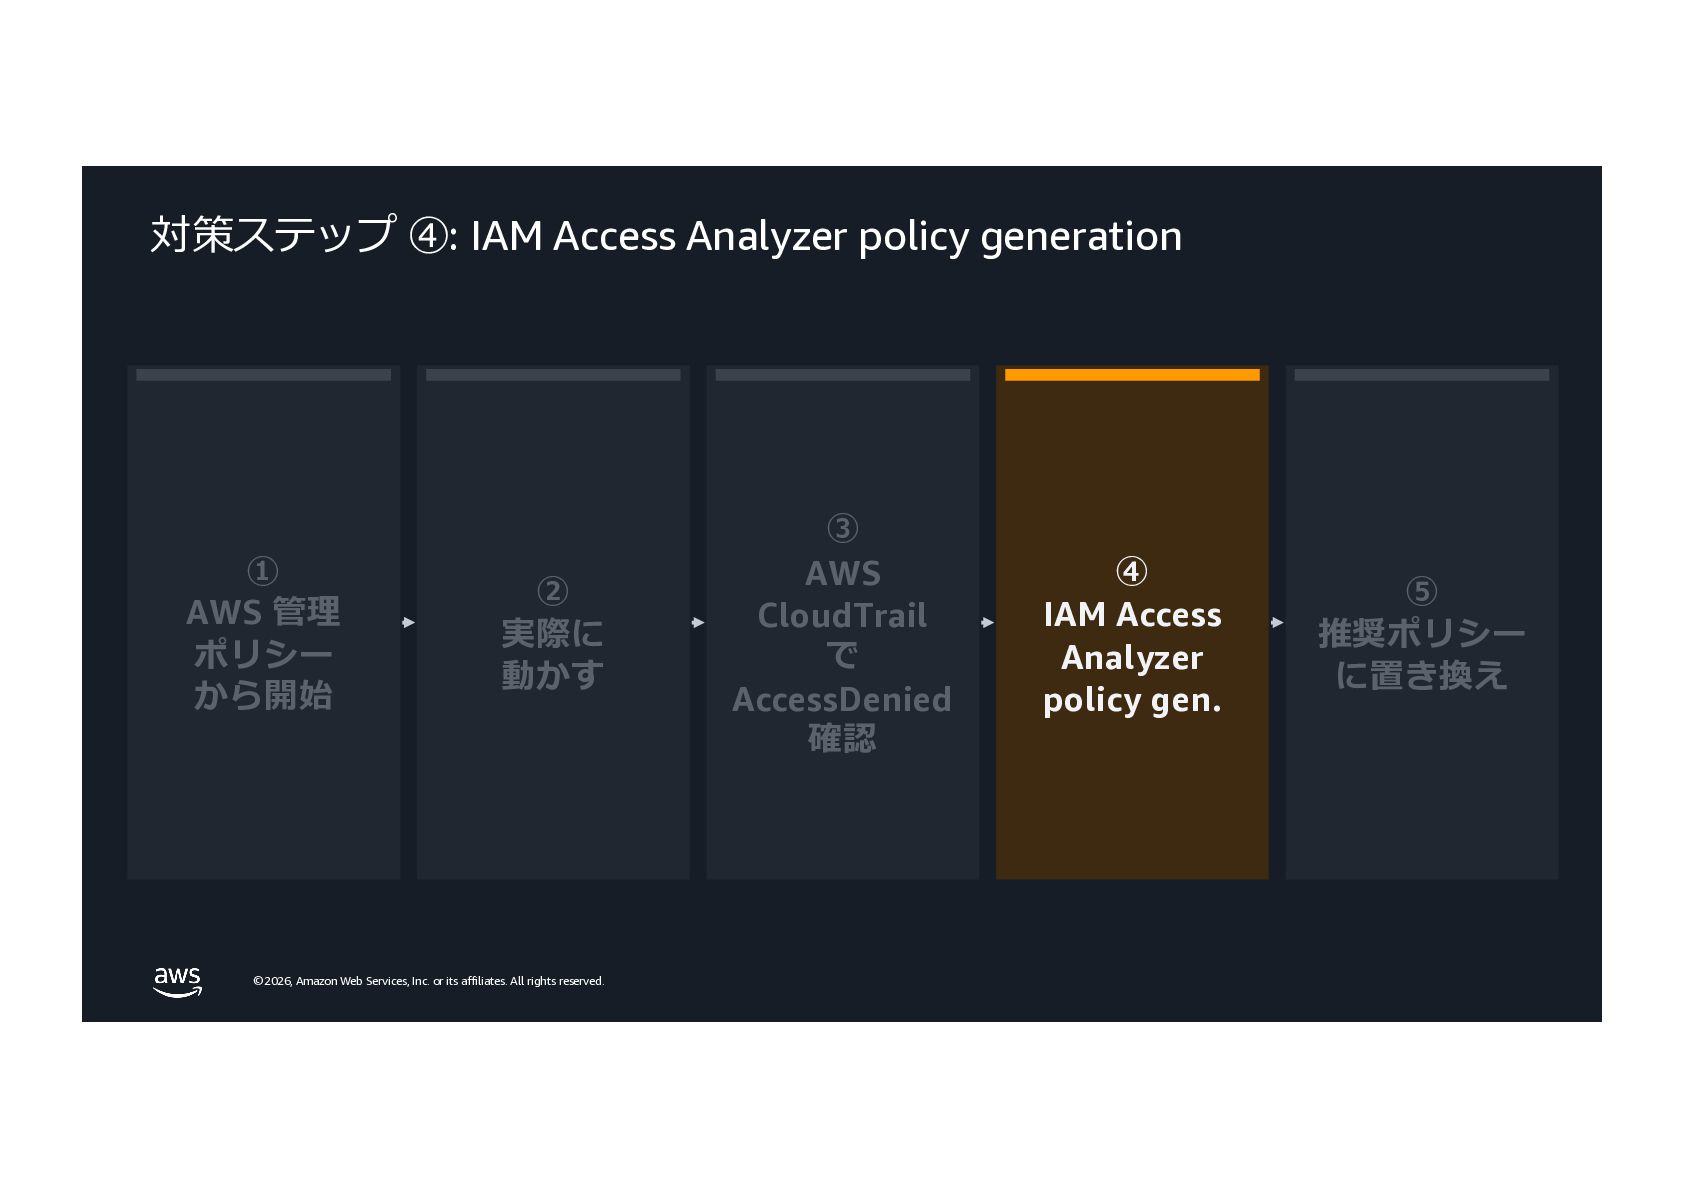
    rights reserved. 対策ステップ ④: IAM Access Analyzer policy generation ① AWS 管理 ポリシー から開始 ② 実際に 動かす ③ AWS CloudTrail で AccessDenied 確認 ④ IAM Access Analyzer policy gen. ⑤ 推奨ポリシー に置き換え
  19. © 2026, Amazon Web Services, Inc. or its affiliates. All

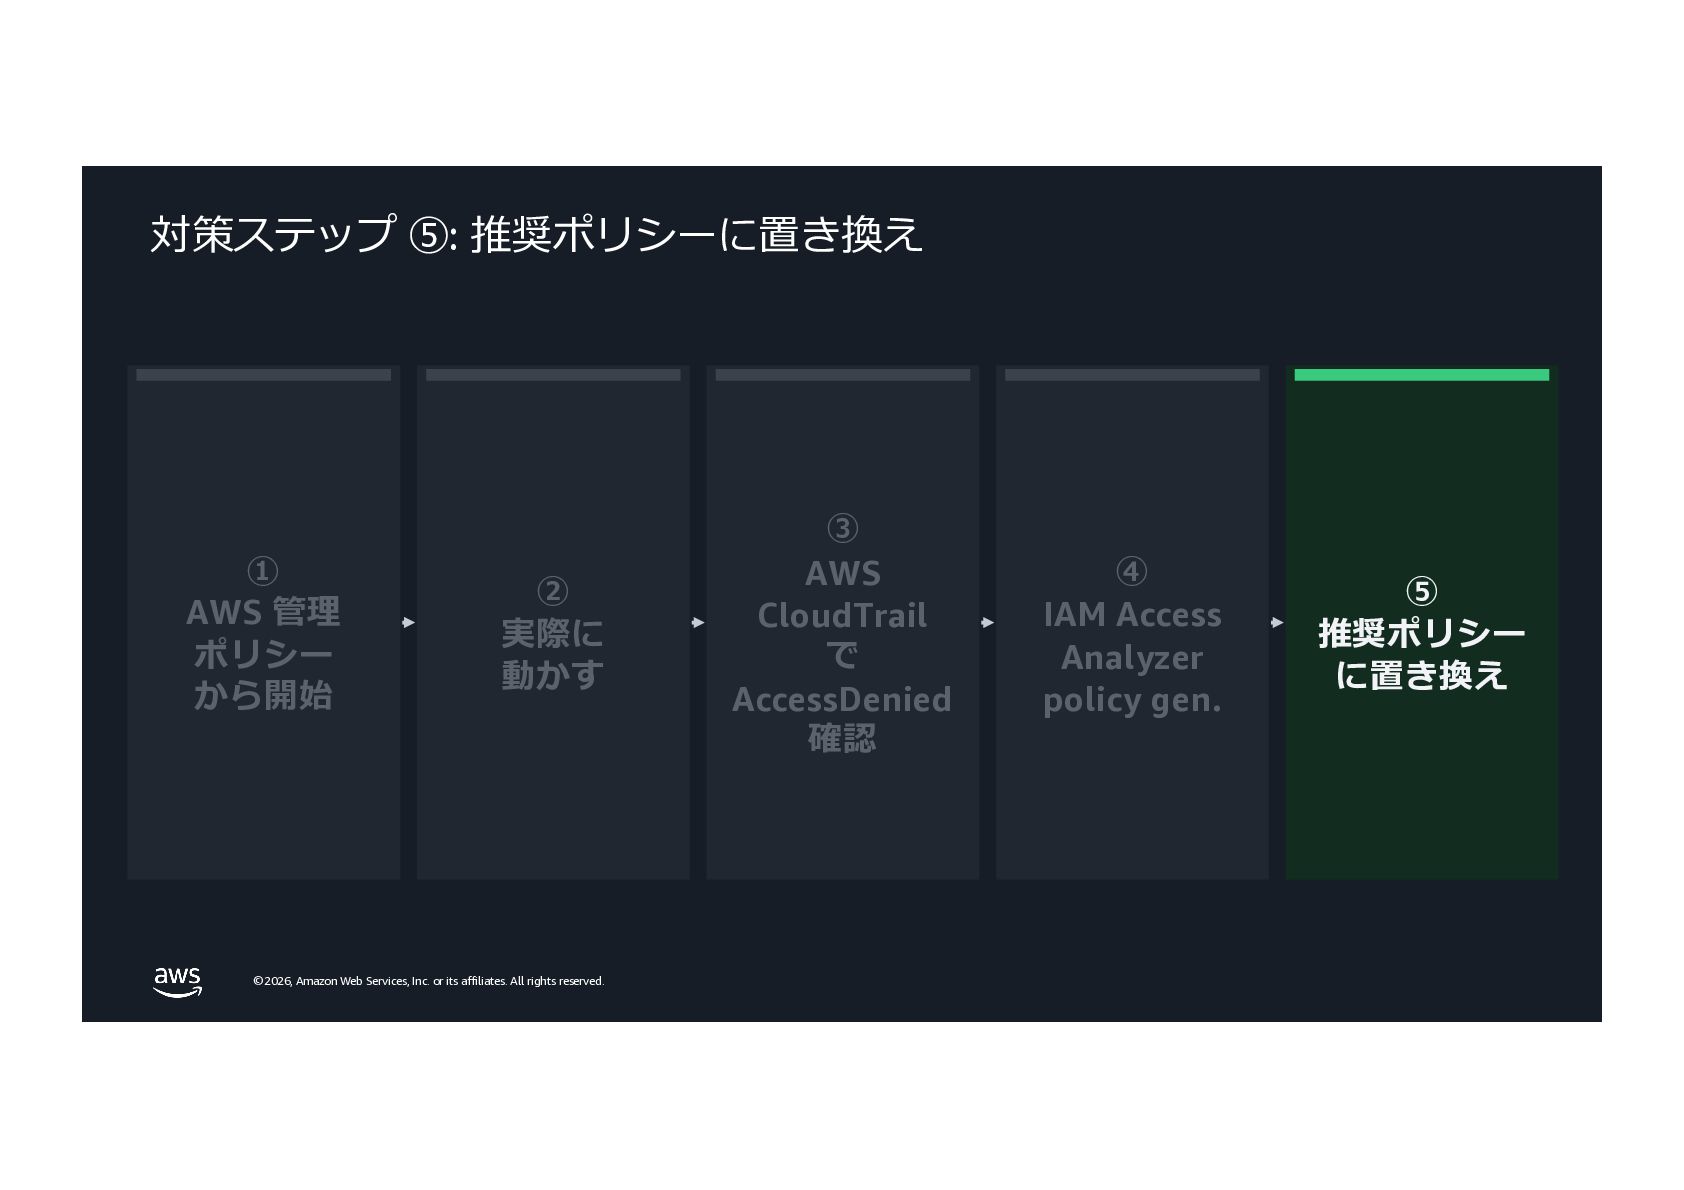
    rights reserved. 対策ステップ ⑤: 推奨ポリシーに置き換え ① AWS 管理 ポリシー から開始 ② 実際に 動かす ③ AWS CloudTrail で AccessDenied 確認 ④ IAM Access Analyzer policy gen. ⑤ 推奨ポリシー に置き換え
  20. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. あるある #2: クロスアカウントで弾かれる
  21. © 2026, Amazon Web Services, Inc. or its affiliates. All

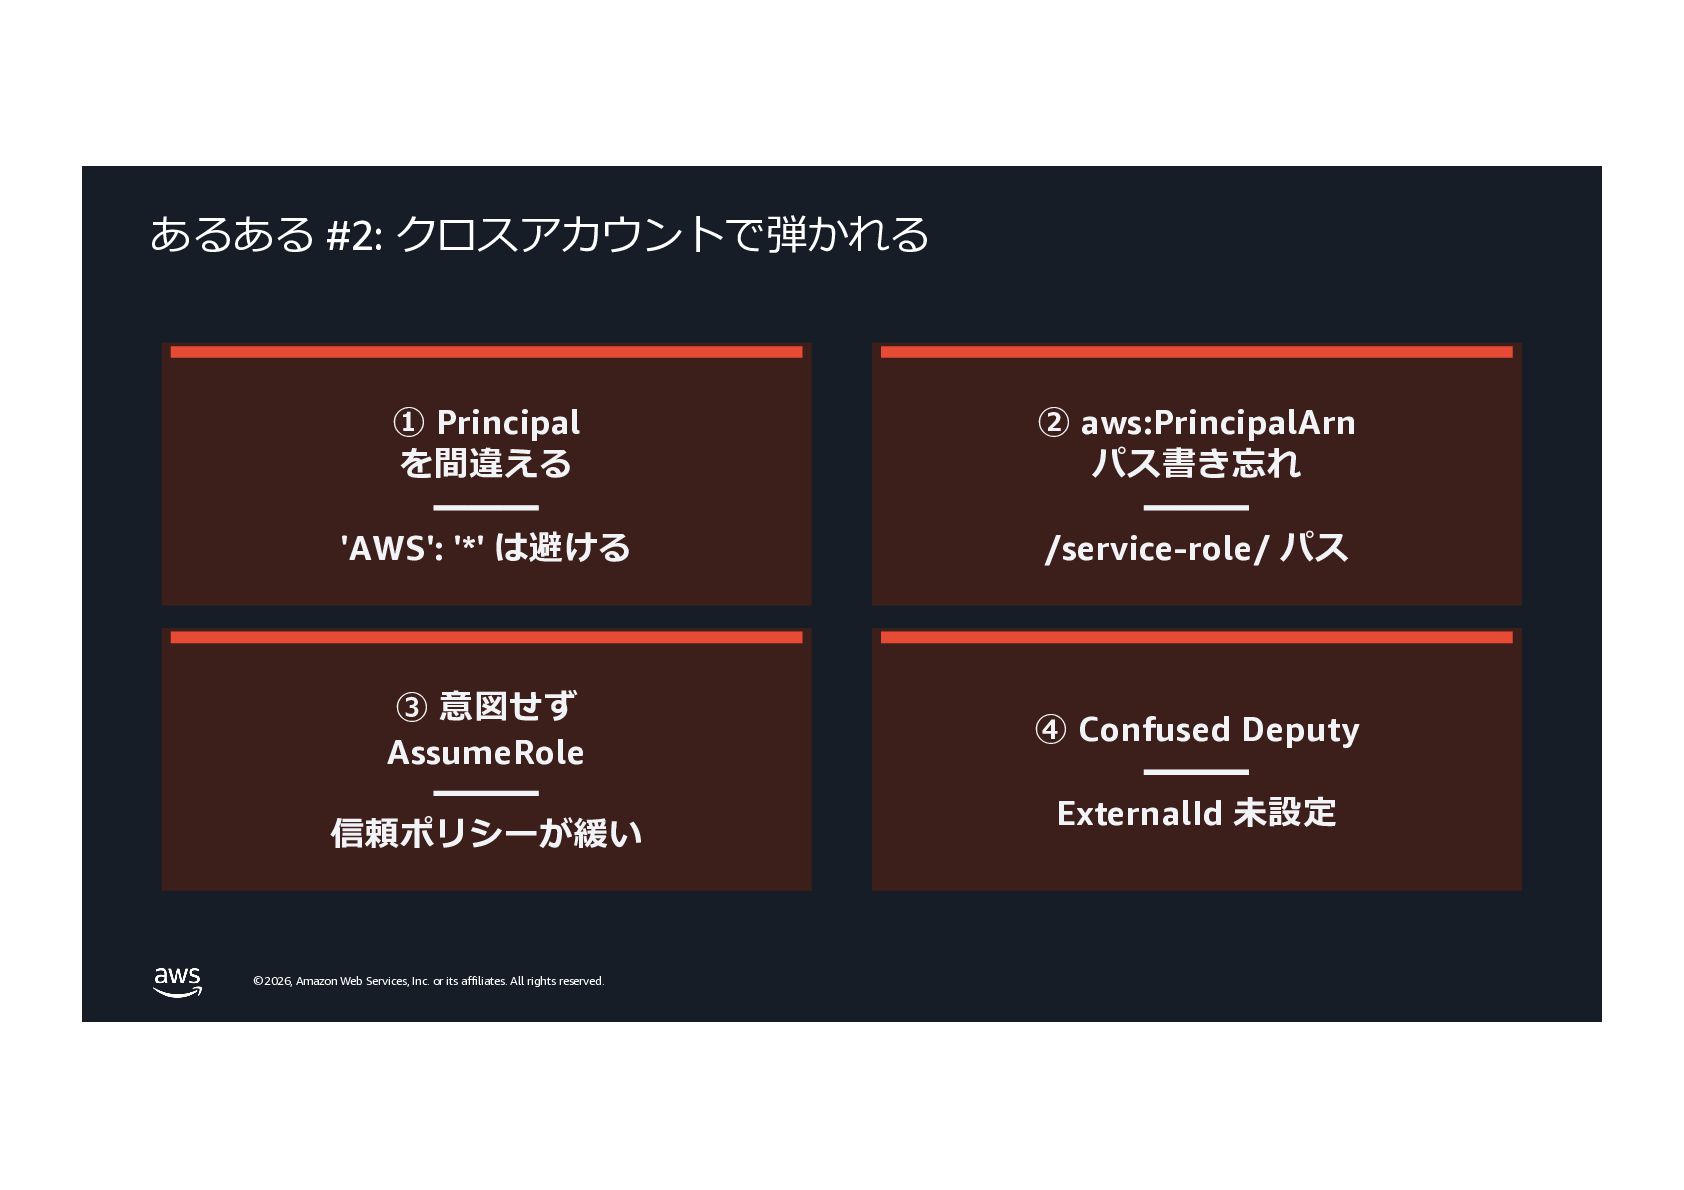
    rights reserved. あるある #2: クロスアカウントで弾かれる ① Principal を間違える ━━━ 'AWS': '*' は避ける ② aws:PrincipalArn パス書き忘れ ━━━ /service-role/ パス ③ 意図せず AssumeRole ━━━ 信頼ポリシーが緩い ④ Confused Deputy ━━━ ExternalId 未設定
  22. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. あるある #2 ①: Principal を間違える ① Principal を間違える ━━━ 'AWS': '*' は避ける ② aws:PrincipalArn パス書き忘れ ━━━ /service-role/ パス ③ 意図せず AssumeRole ━━━ 信頼ポリシーが緩い ④ Confused Deputy ━━━ ExternalId 未設定
  23. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. あるある #2 ②: aws:PrincipalArn パス書き忘れ ① Principal を間違える ━━━ 'AWS': '*' は避ける ② aws:PrincipalArn パス書き忘れ ━━━ /service-role/ パス ③ 意図せず AssumeRole ━━━ 信頼ポリシーが緩い ④ Confused Deputy ━━━ ExternalId 未設定
  24. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. あるある #2 ③: 同⼀アカウント内で意図せず AssumeRole ① Principal を間違える ━━━ 'AWS': '*' は避ける ② aws:PrincipalArn パス書き忘れ ━━━ /service-role/ パス ③ 意図せず AssumeRole ━━━ 信頼ポリシーが緩い ④ Confused Deputy ━━━ ExternalId 未設定
  25. © 2026, Amazon Web Services, Inc. or its affiliates. All

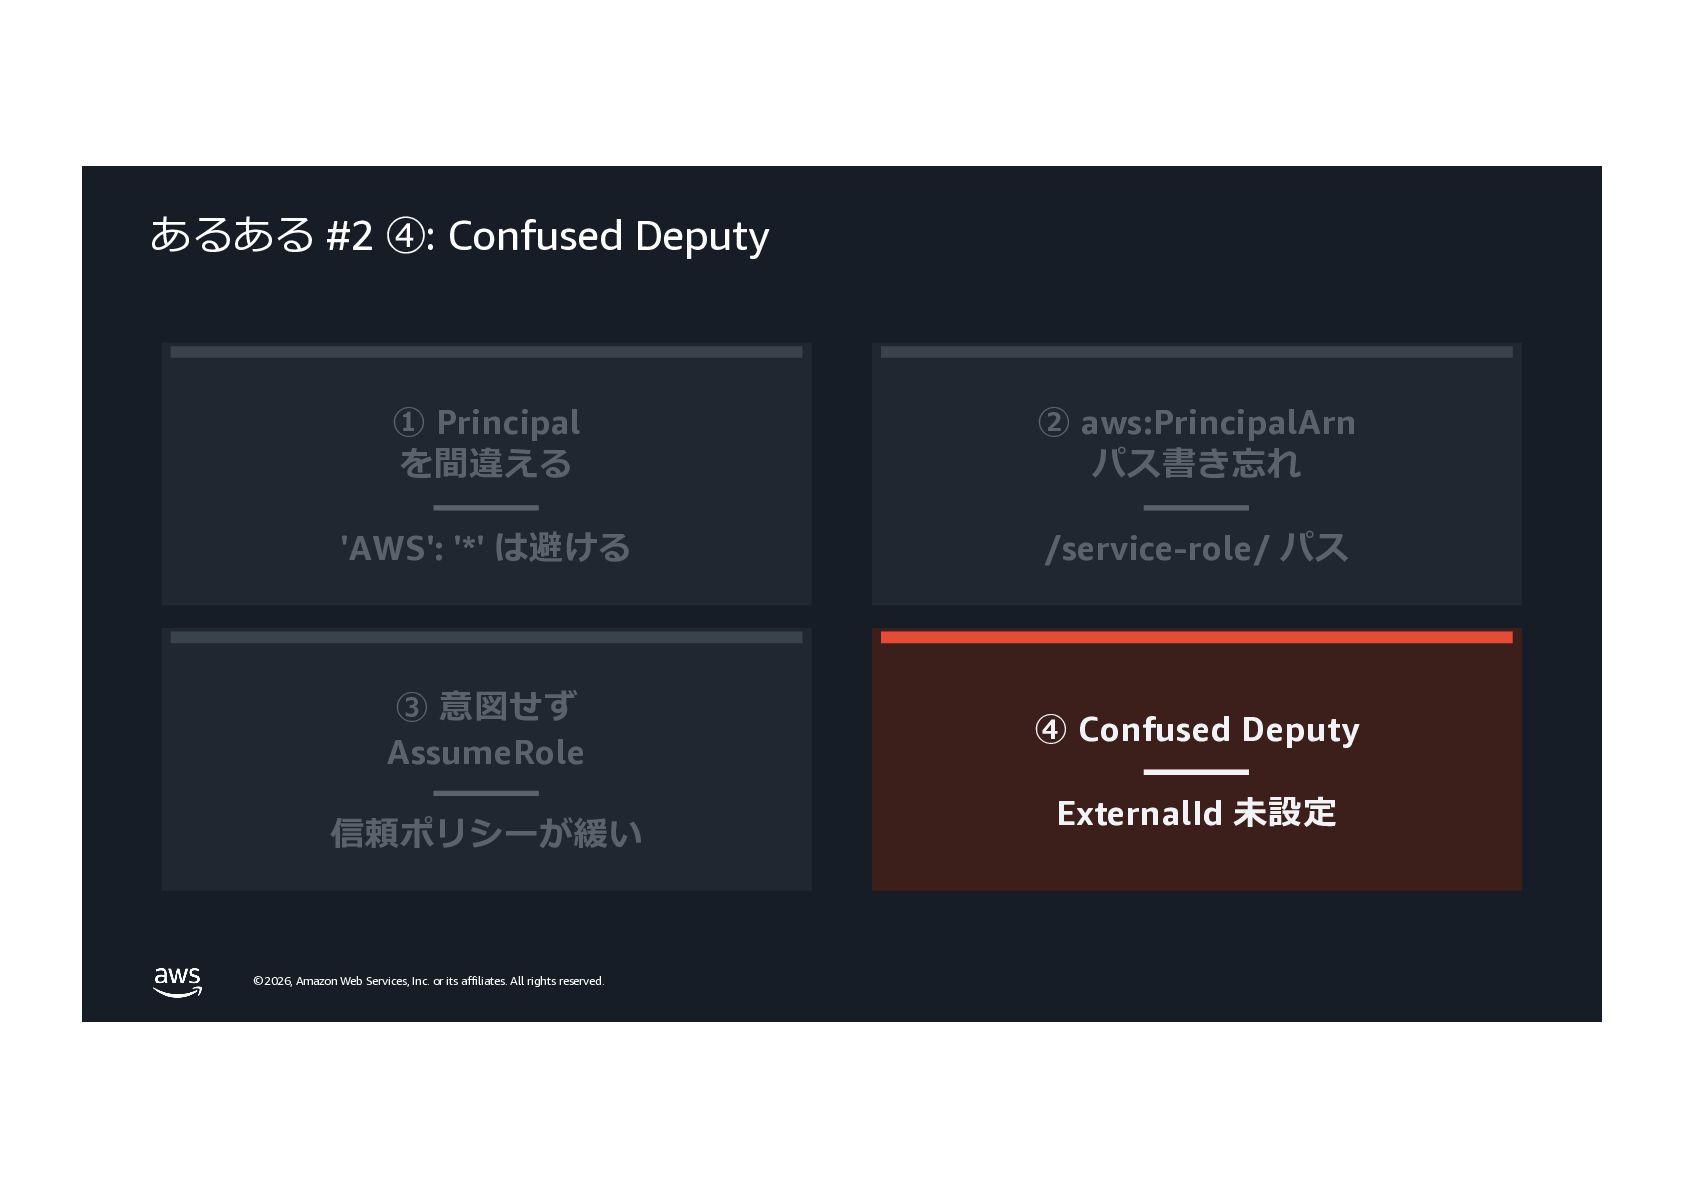
    rights reserved. あるある #2 ④: Confused Deputy ① Principal を間違える ━━━ 'AWS': '*' は避ける ② aws:PrincipalArn パス書き忘れ ━━━ /service-role/ パス ③ 意図せず AssumeRole ━━━ 信頼ポリシーが緩い ④ Confused Deputy ━━━ ExternalId 未設定
  26. © 2026, Amazon Web Services, Inc. or its affiliates. All

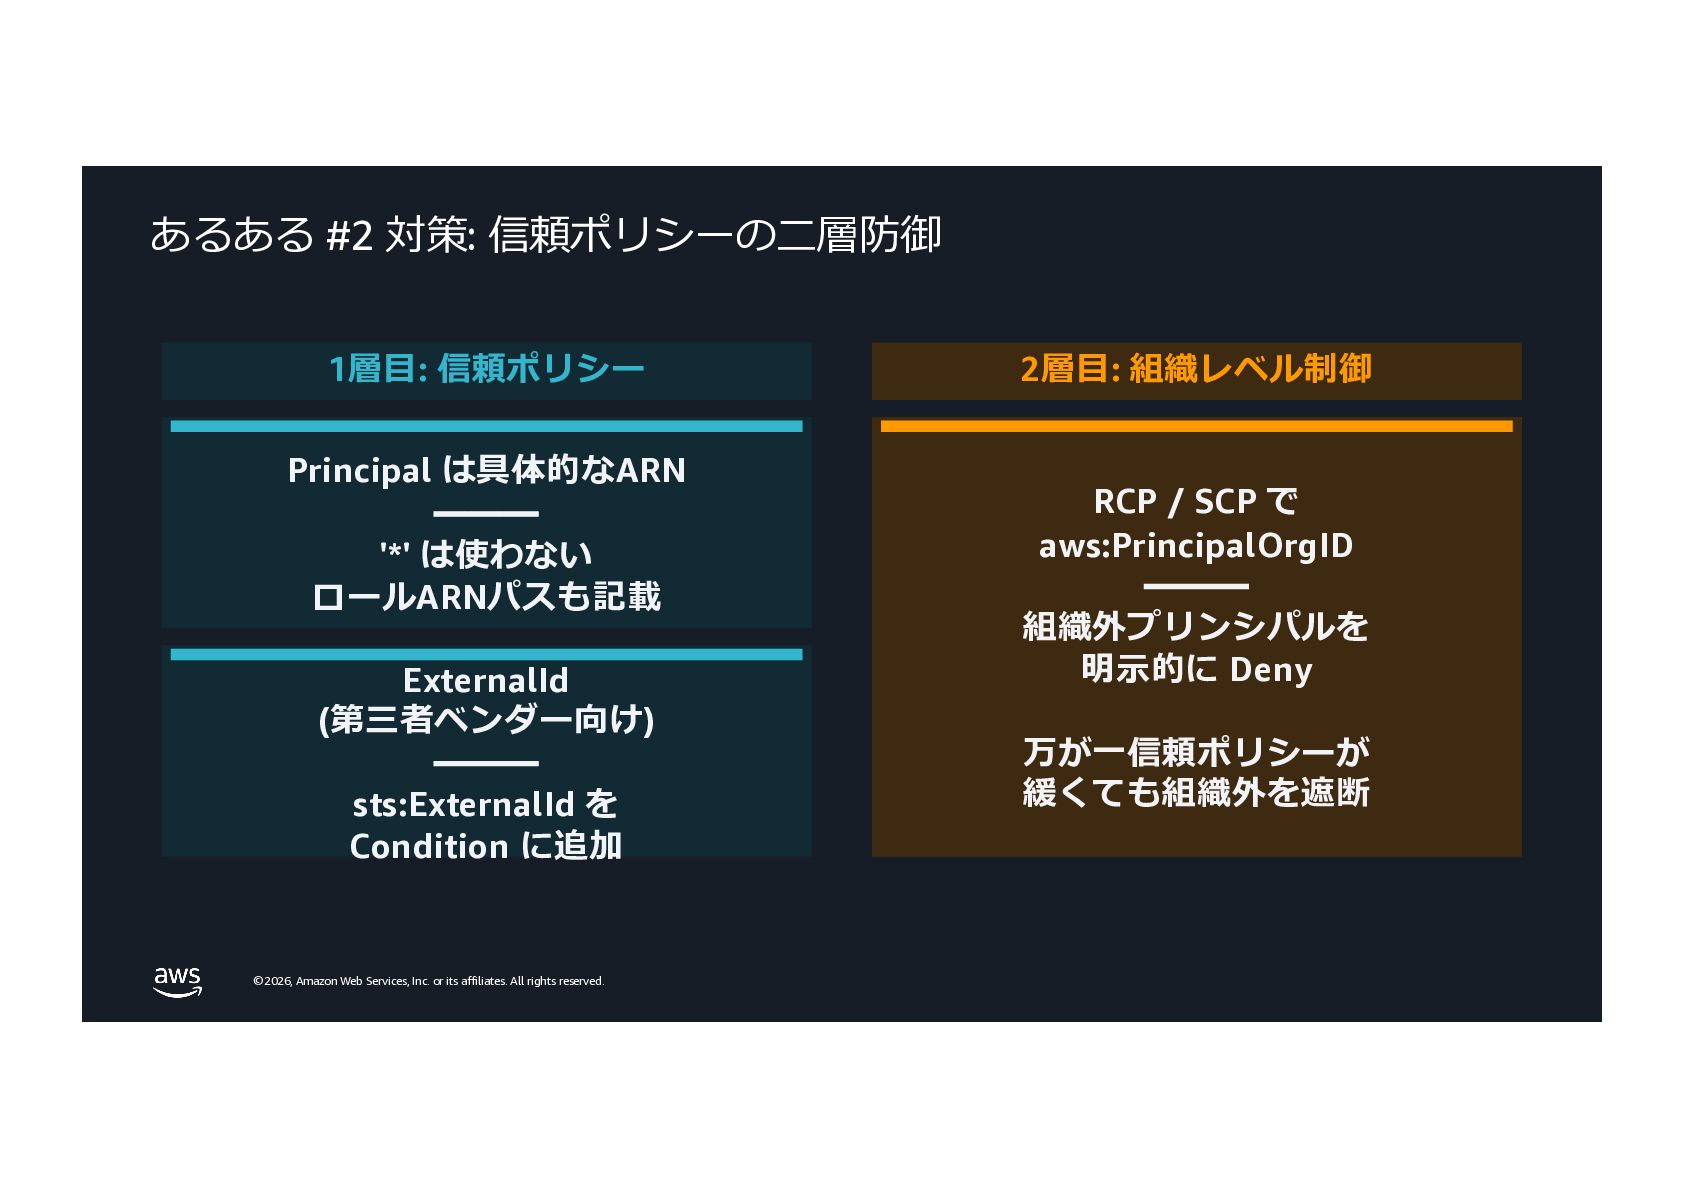
    rights reserved. あるある #2 対策: 信頼ポリシーの⼆層防御 1層⽬: 信頼ポリシー Principal は具体的なARN ━━━ '*' は使わない ロールARNパスも記載 ExternalId (第三者ベンダー向け) ━━━ sts:ExternalId を Condition に追加 2層⽬: 組織レベル制御 RCP / SCP で aws:PrincipalOrgID ━━━ 組織外プリンシパルを 明⽰的に Deny 万が⼀信頼ポリシーが 緩くても組織外を遮断
  27. © 2026, Amazon Web Services, Inc. or its affiliates. All

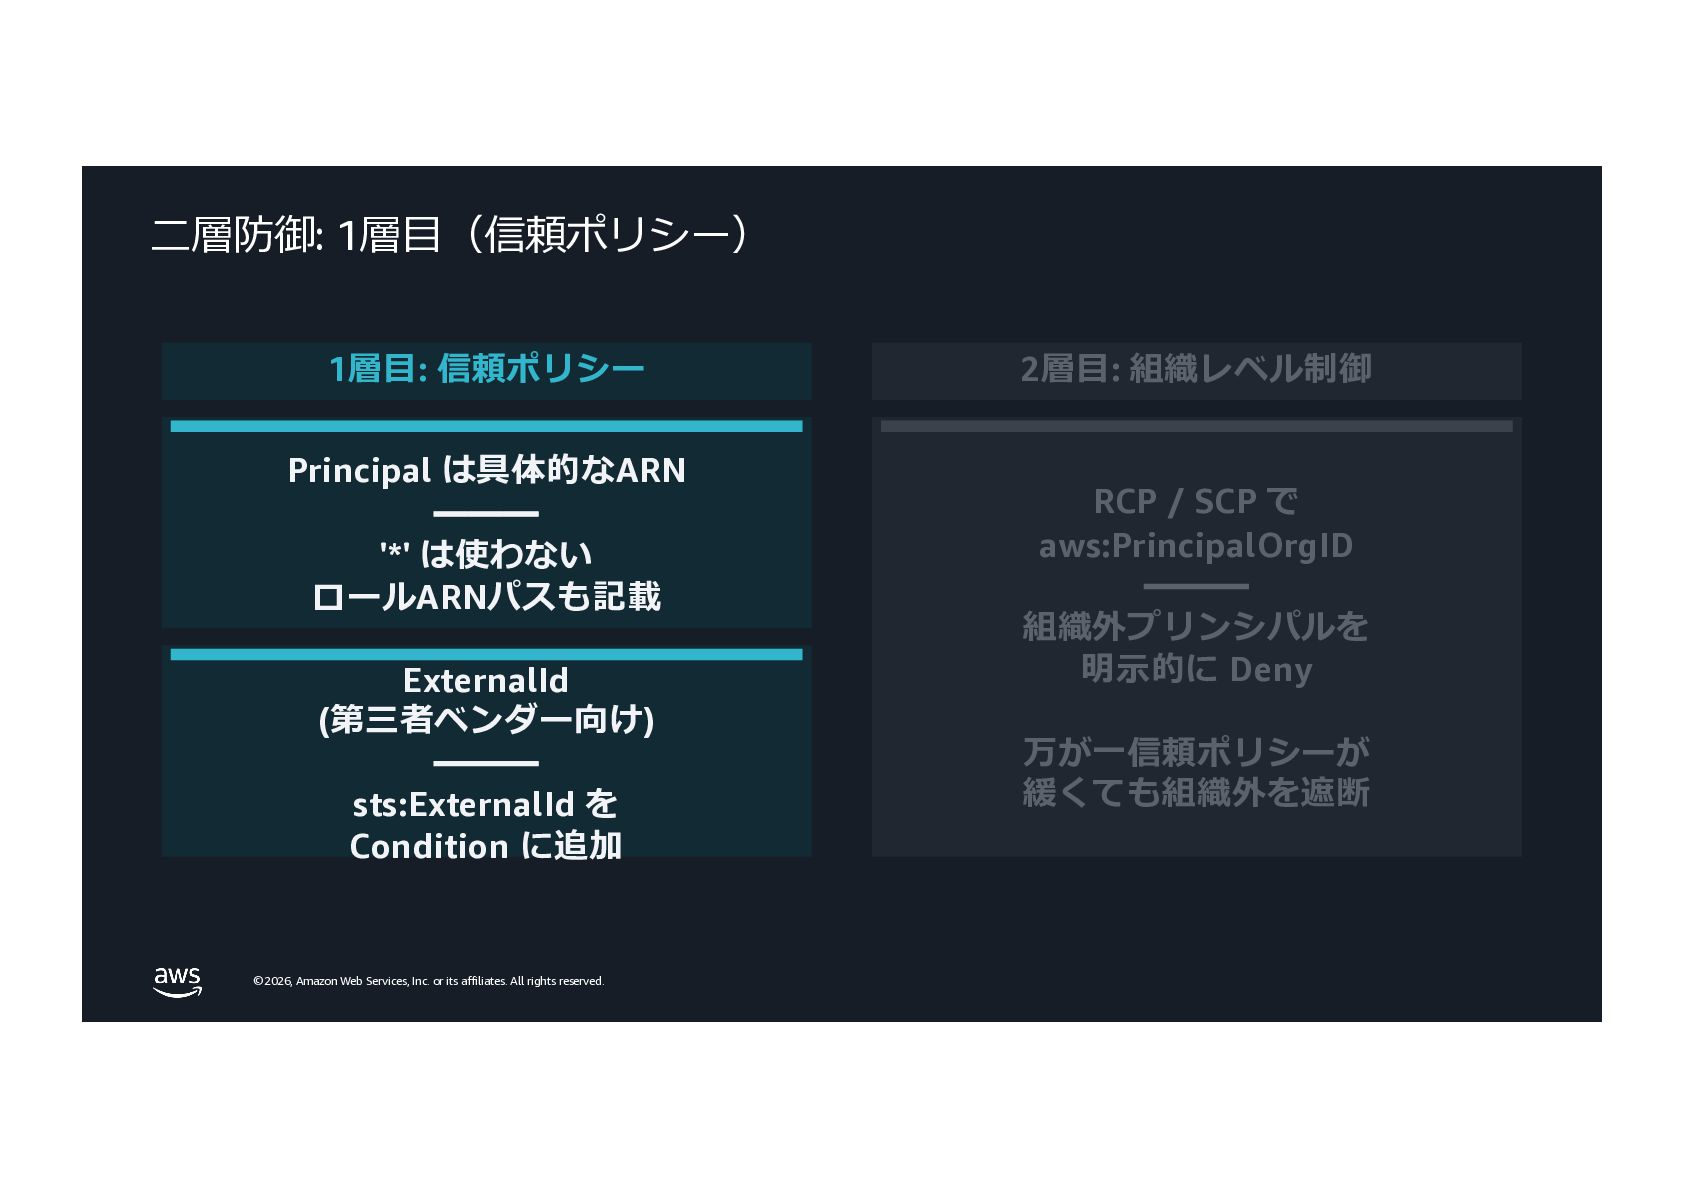
    rights reserved. ⼆層防御: 1層⽬(信頼ポリシー) 1層⽬: 信頼ポリシー Principal は具体的なARN ━━━ '*' は使わない ロールARNパスも記載 ExternalId (第三者ベンダー向け) ━━━ sts:ExternalId を Condition に追加 2層⽬: 組織レベル制御 RCP / SCP で aws:PrincipalOrgID ━━━ 組織外プリンシパルを 明⽰的に Deny 万が⼀信頼ポリシーが 緩くても組織外を遮断
  28. © 2026, Amazon Web Services, Inc. or its affiliates. All

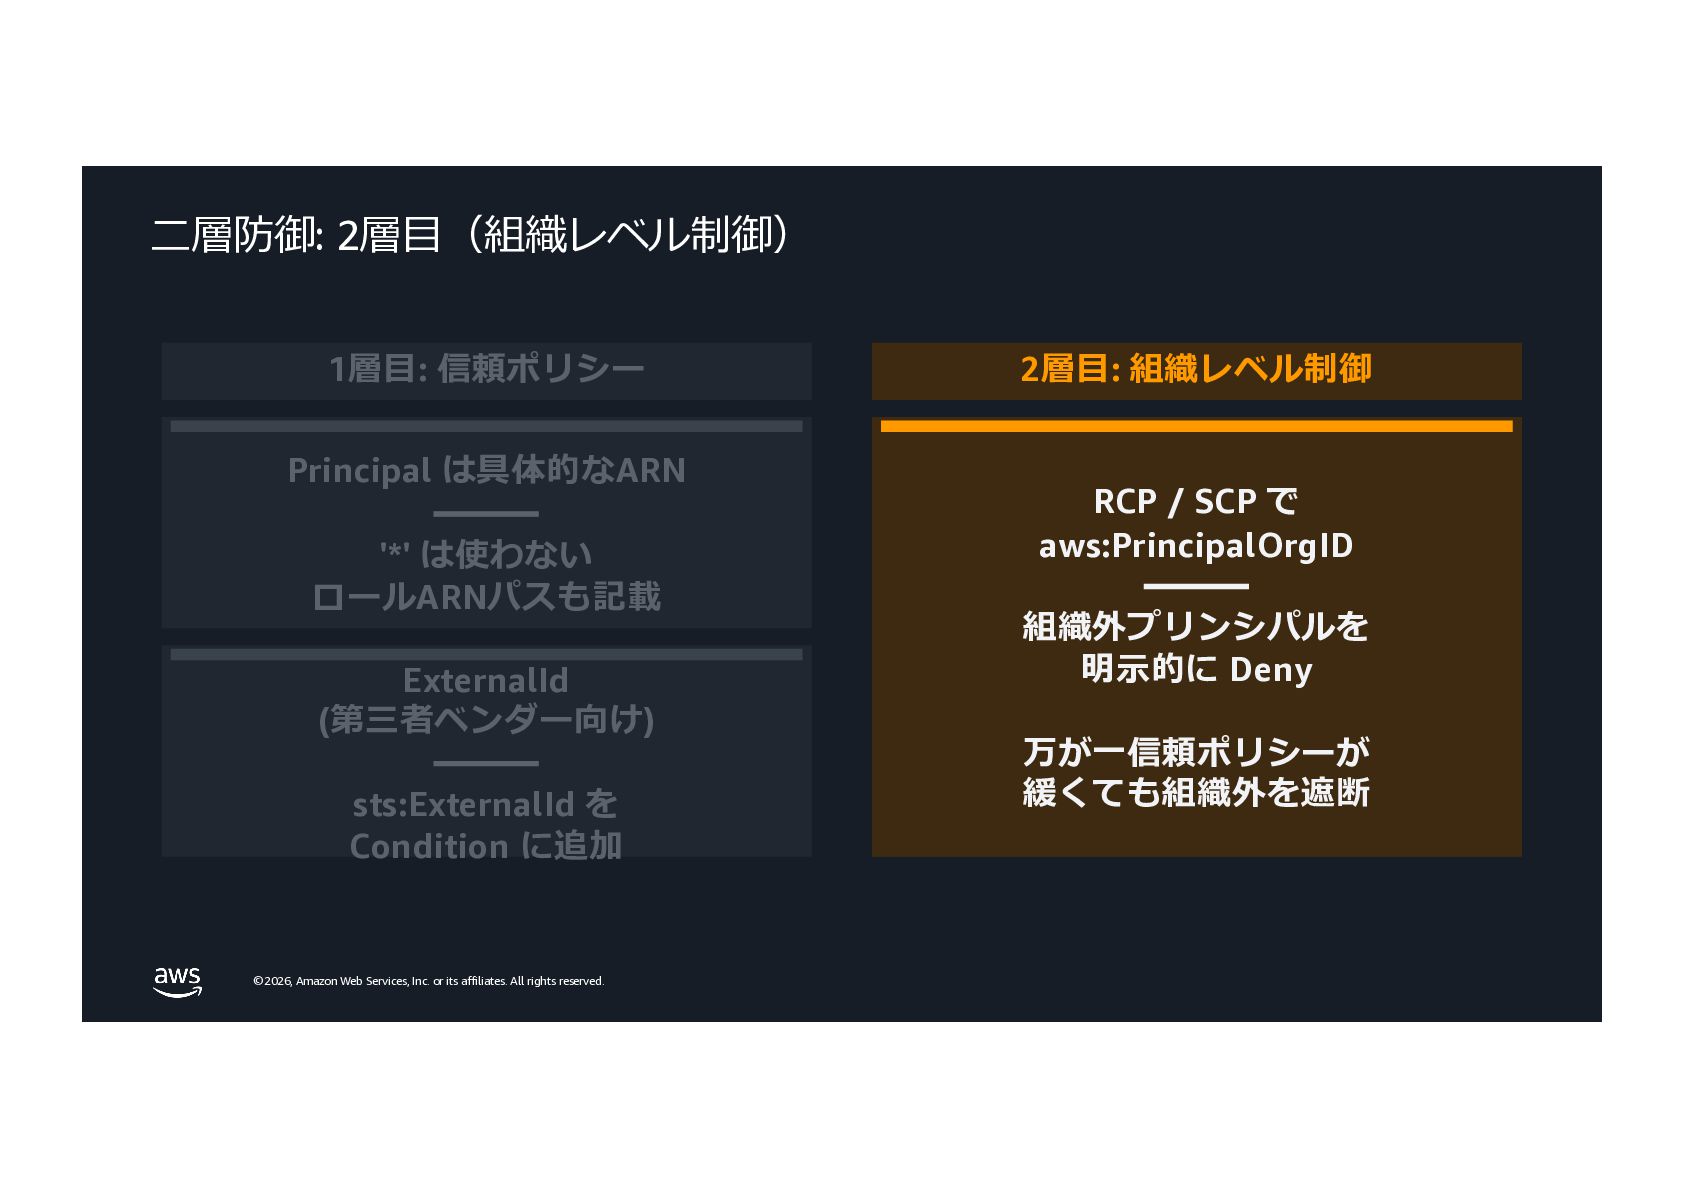
    rights reserved. ⼆層防御: 2層⽬(組織レベル制御) 1層⽬: 信頼ポリシー Principal は具体的なARN ━━━ '*' は使わない ロールARNパスも記載 ExternalId (第三者ベンダー向け) ━━━ sts:ExternalId を Condition に追加 2層⽬: 組織レベル制御 RCP / SCP で aws:PrincipalOrgID ━━━ 組織外プリンシパルを 明⽰的に Deny 万が⼀信頼ポリシーが 緩くても組織外を遮断
  29. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. あるある #3: IP制限したら自分も弾かれる
  30. © 2026, Amazon Web Services, Inc. or its affiliates. All

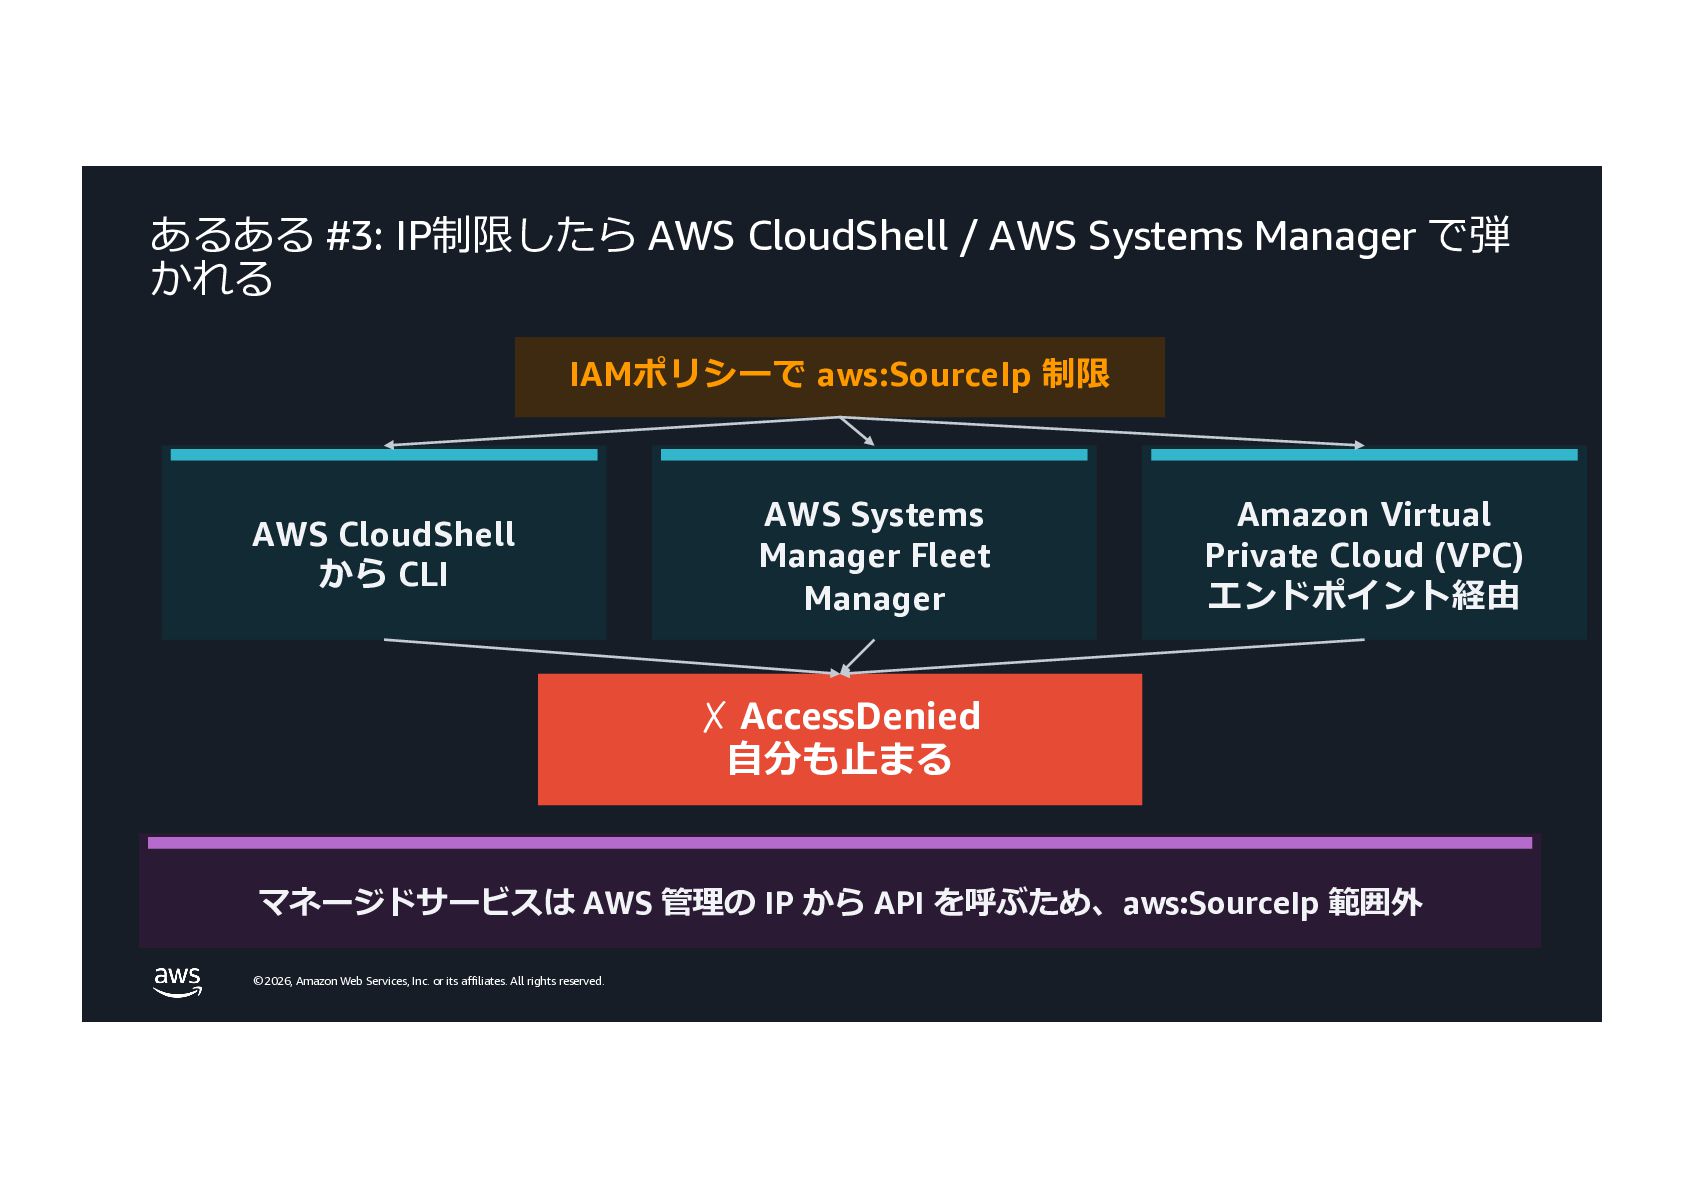
    rights reserved. あるある #3: IP制限したら AWS CloudShell / AWS Systems Manager で弾 かれる IAMポリシーで aws:SourceIp 制限 AWS CloudShell から CLI AWS Systems Manager Fleet Manager Amazon Virtual Private Cloud (VPC) エンドポイント経由 ✗ AccessDenied ⾃分も⽌まる マネージドサービスは AWS 管理の IP から API を呼ぶため、aws:SourceIp 範囲外
  31. © 2026, Amazon Web Services, Inc. or its affiliates. All

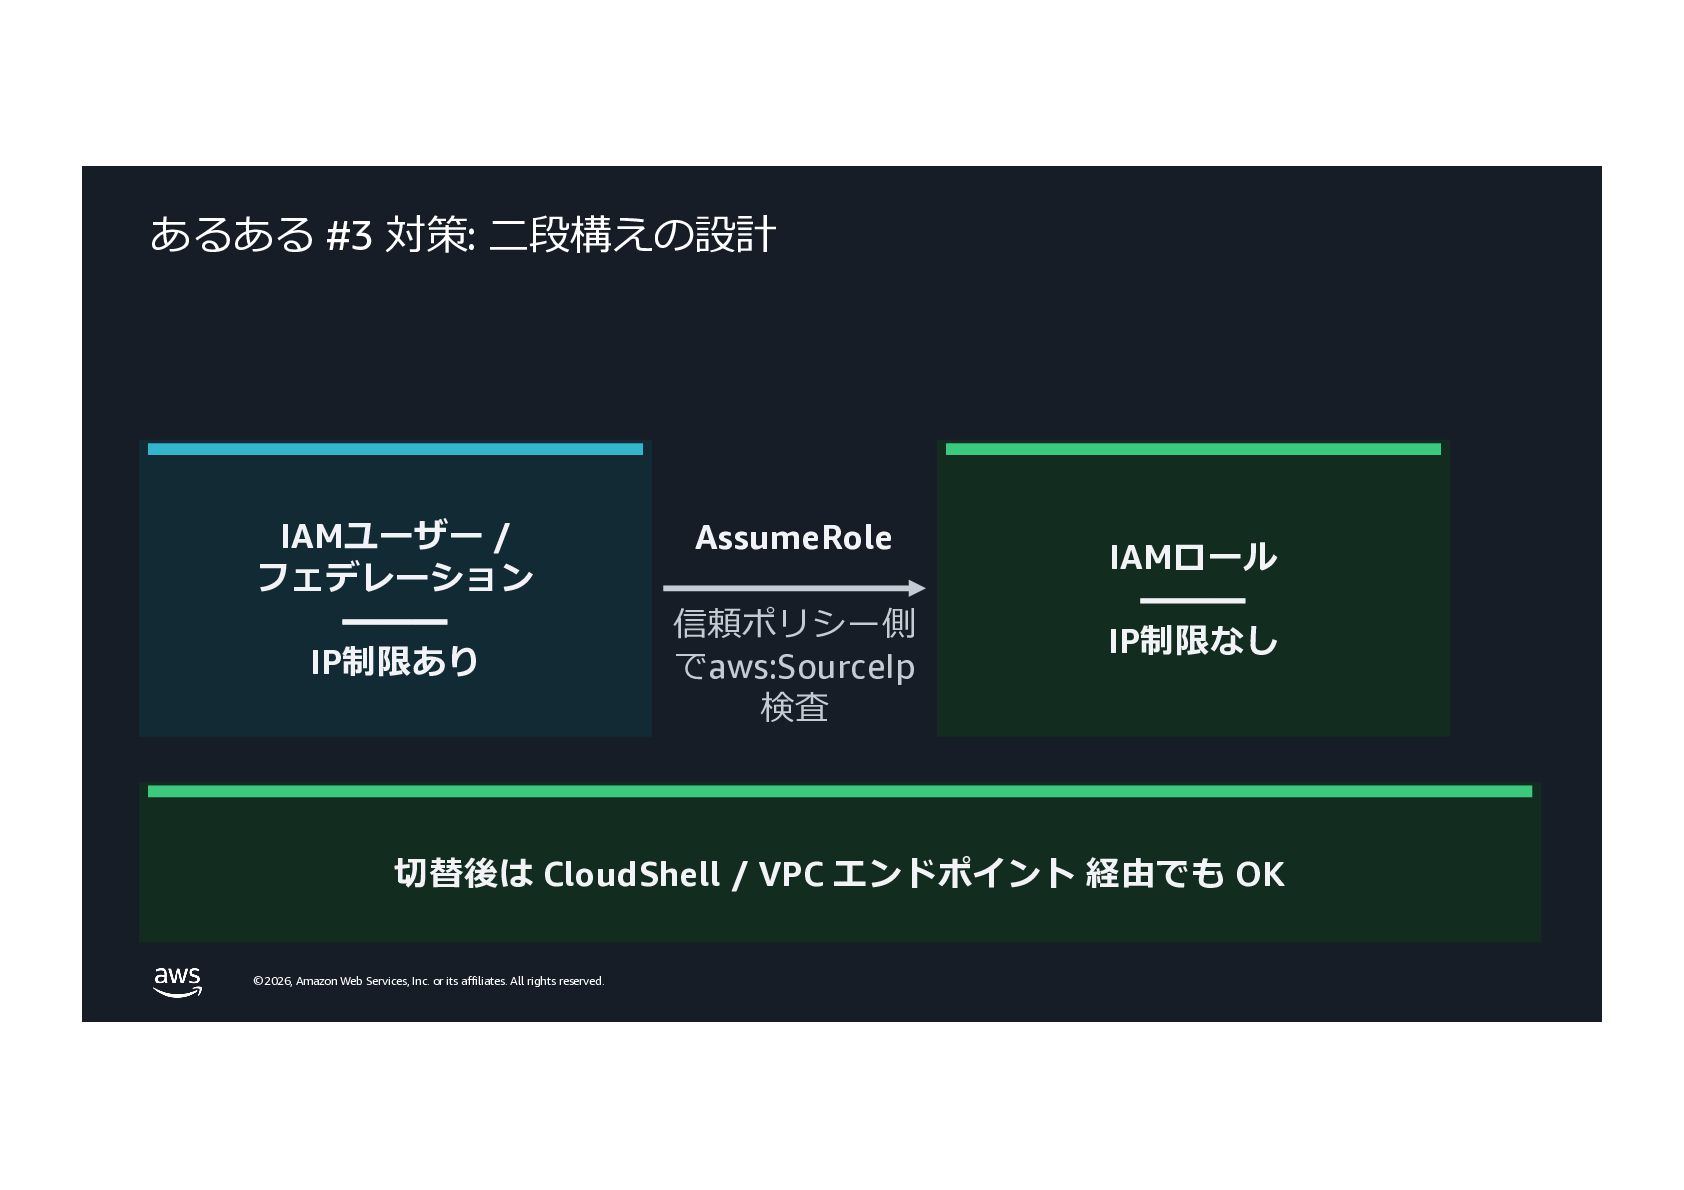
    rights reserved. あるある #3 対策: ⼆段構えの設計 IAMユーザー / フェデレーション ━━━ IP制限あり AssumeRole 信頼ポリシー側 でaws:SourceIp 検査 IAMロール ━━━ IP制限なし 切替後は CloudShell / VPC エンドポイント 経由でも OK
  32. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. あるある #4: アクセスキーをやめて AWS Identity Center へ
  33. © 2026, Amazon Web Services, Inc. or its affiliates. All

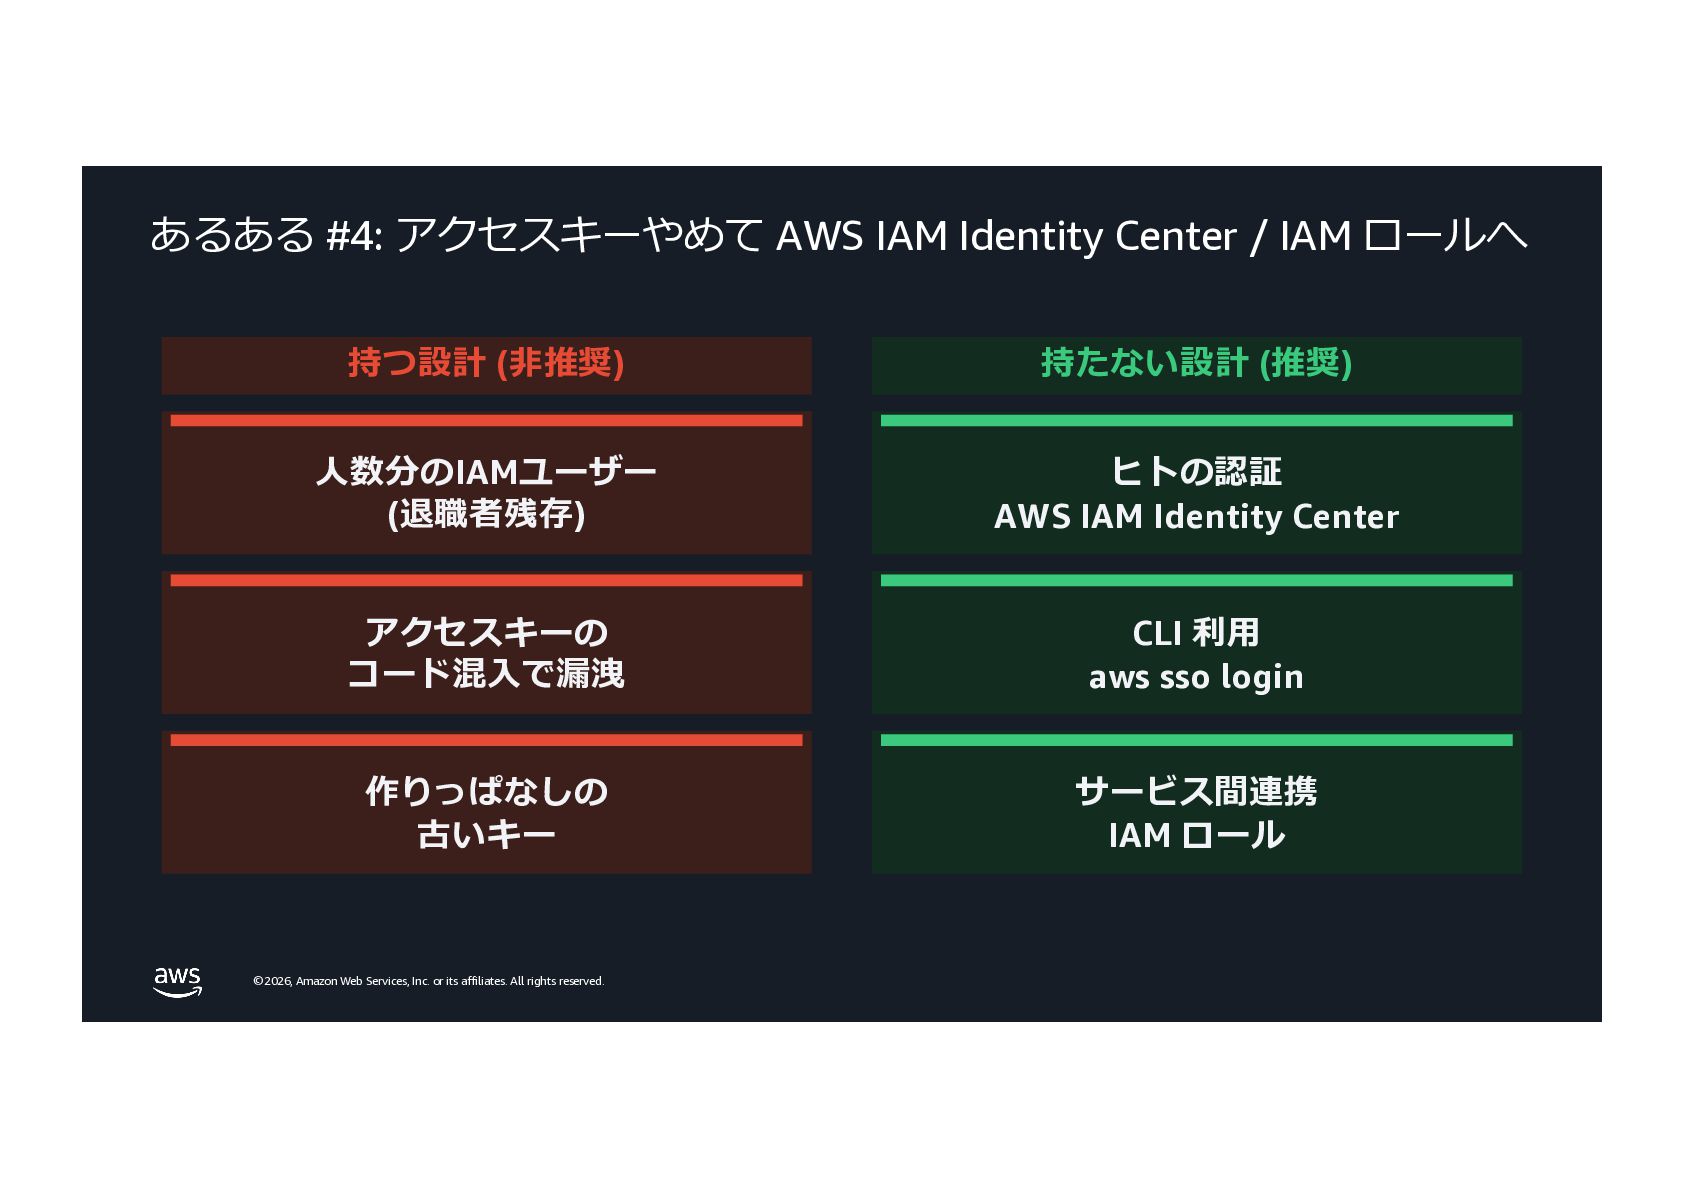
    rights reserved. あるある #4: アクセスキーやめて AWS IAM Identity Center / IAM ロールへ 持つ設計 (⾮推奨) ⼈数分のIAMユーザー (退職者残存) アクセスキーの コード混⼊で漏洩 作りっぱなしの 古いキー 持たない設計 (推奨) ヒトの認証 AWS IAM Identity Center CLI 利⽤ aws sso login サービス間連携 IAM ロール
  34. © 2026, Amazon Web Services, Inc. or its affiliates. All

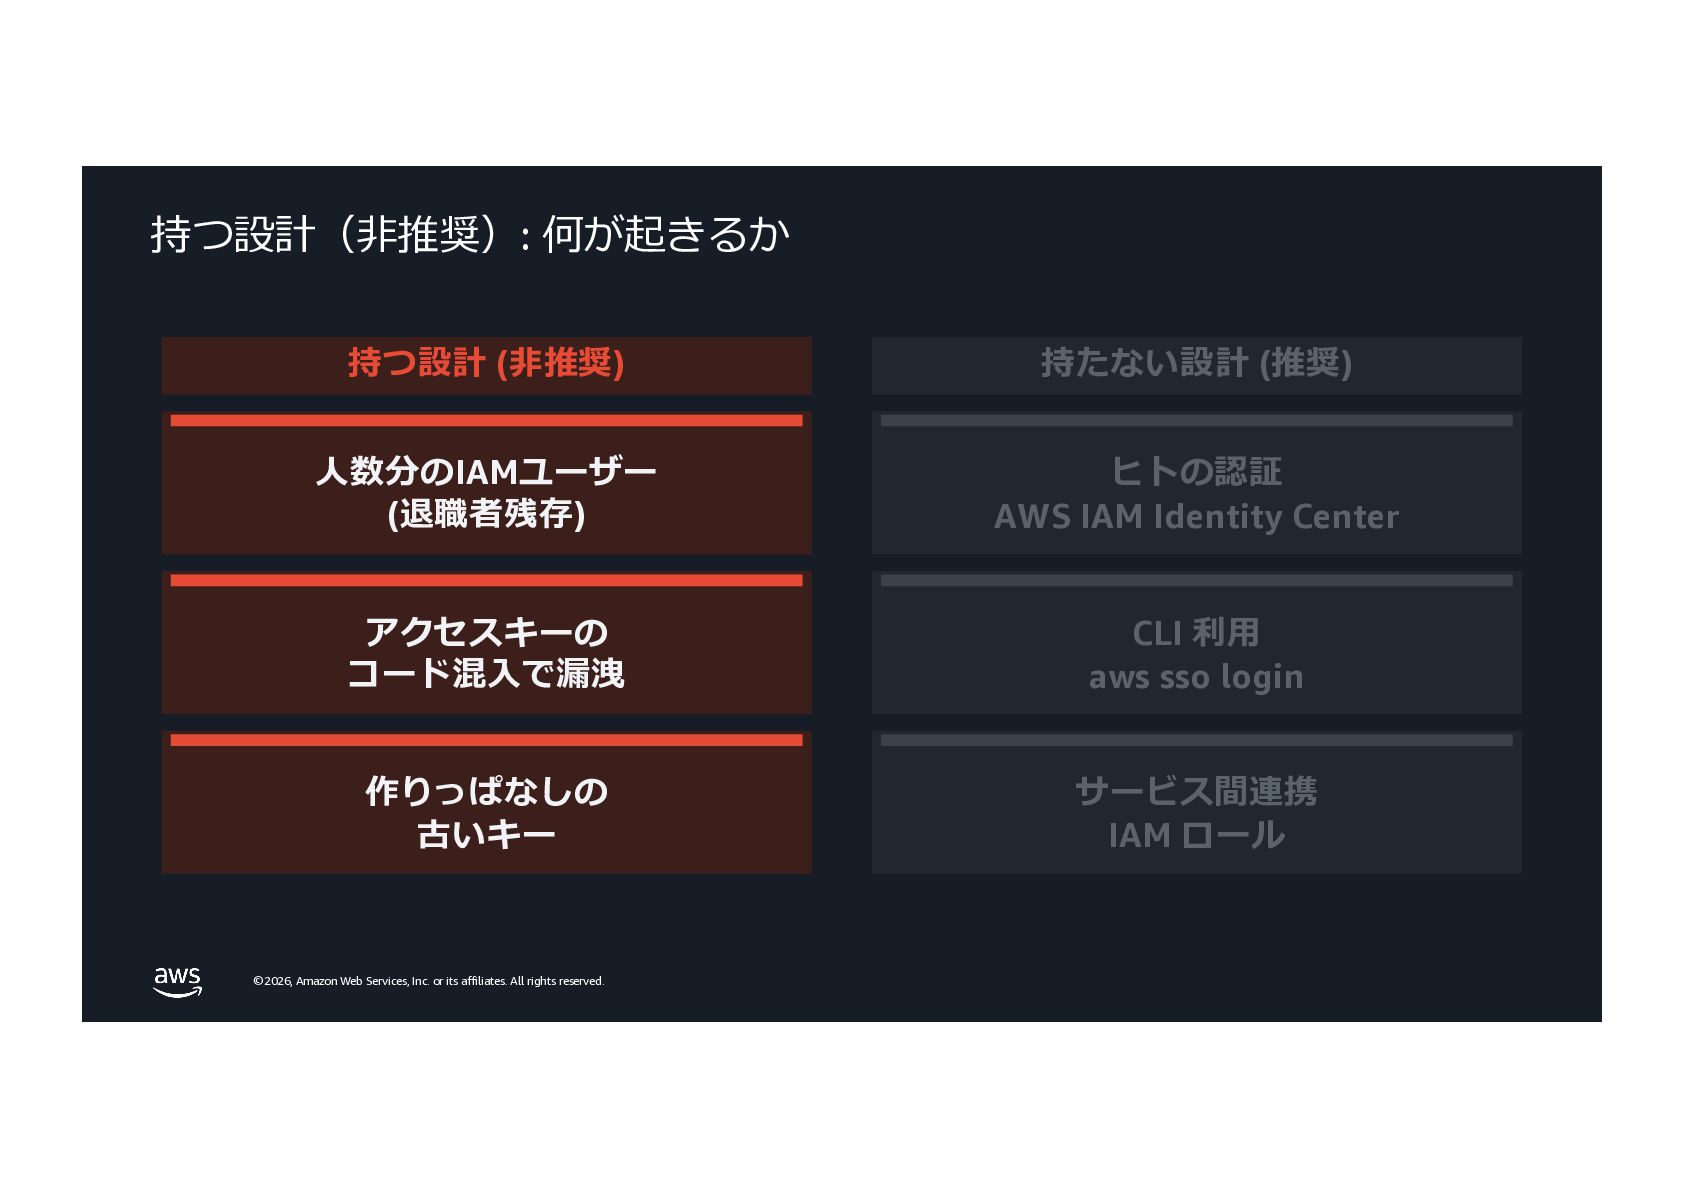
    rights reserved. 持つ設計(⾮推奨): 何が起きるか 持つ設計 (⾮推奨) ⼈数分のIAMユーザー (退職者残存) アクセスキーの コード混⼊で漏洩 作りっぱなしの 古いキー 持たない設計 (推奨) ヒトの認証 AWS IAM Identity Center CLI 利⽤ aws sso login サービス間連携 IAM ロール
  35. © 2026, Amazon Web Services, Inc. or its affiliates. All

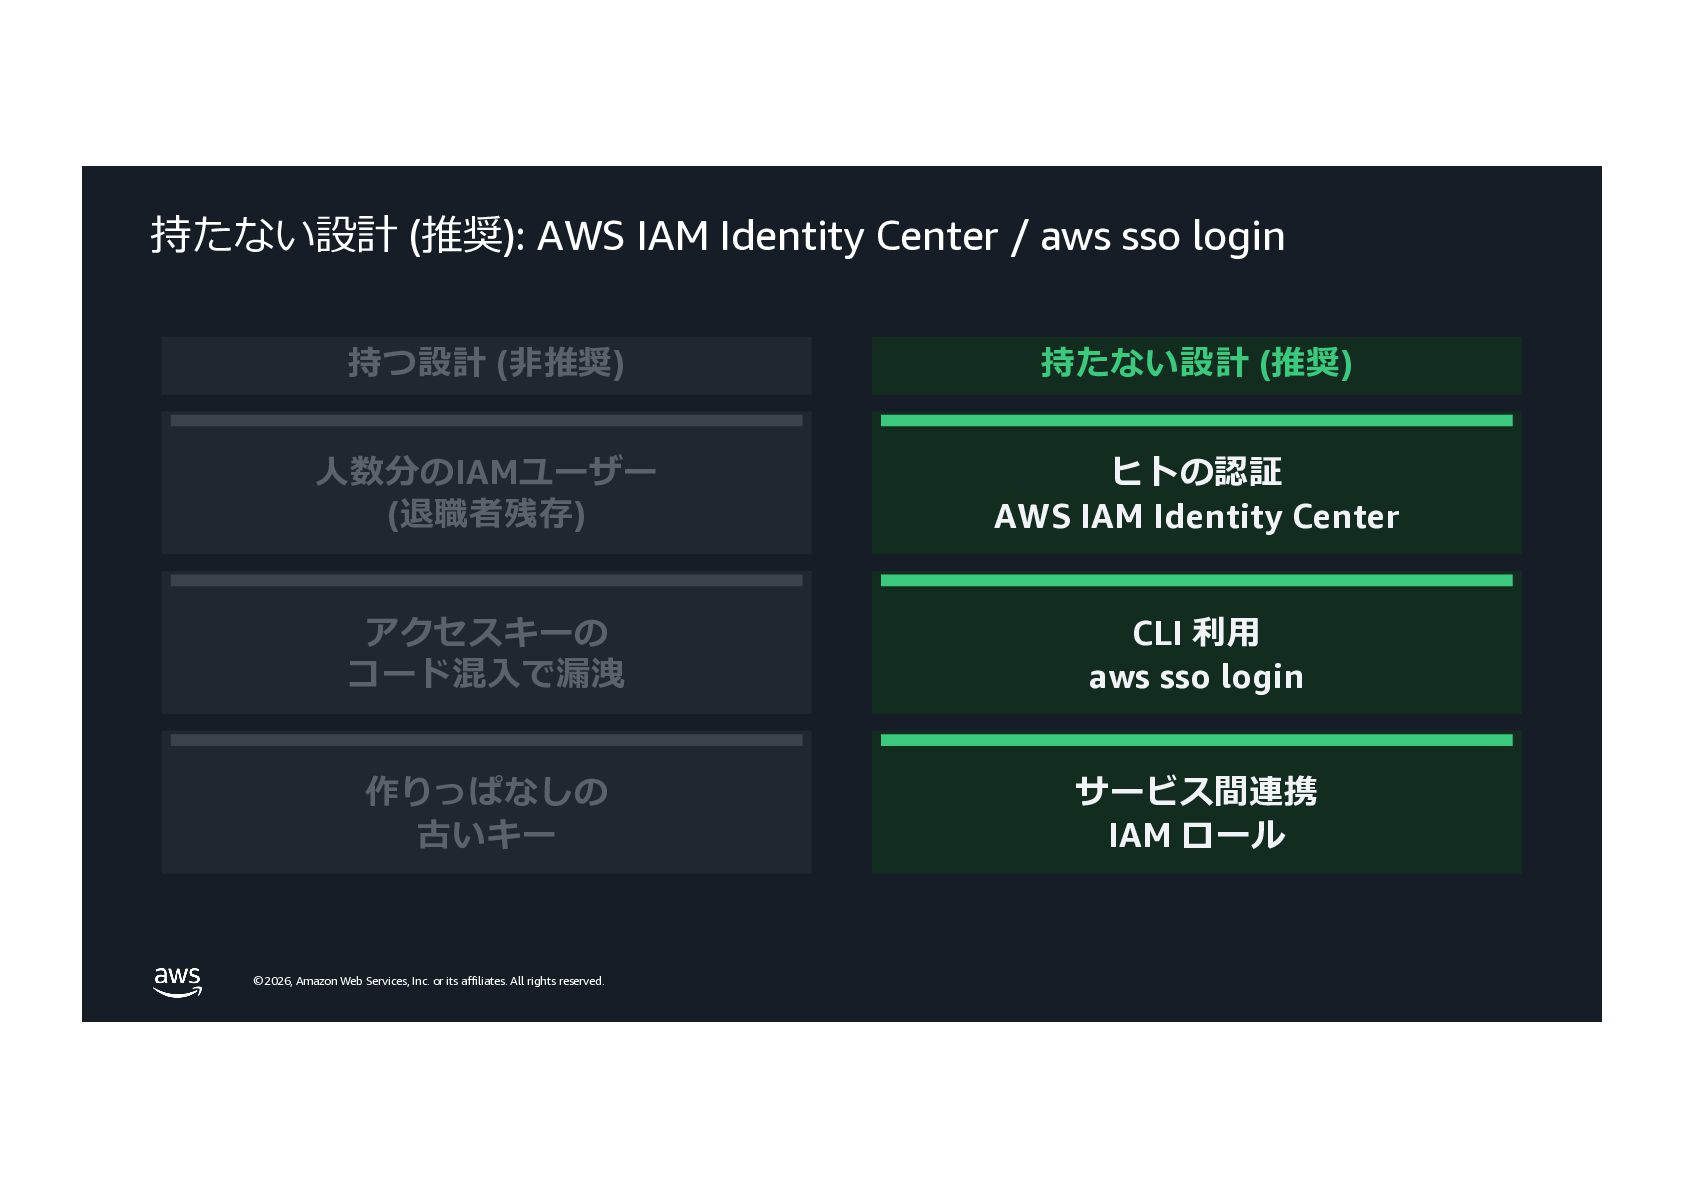
    rights reserved. 持たない設計 (推奨): AWS IAM Identity Center / aws sso login 持つ設計 (⾮推奨) ⼈数分のIAMユーザー (退職者残存) アクセスキーの コード混⼊で漏洩 作りっぱなしの 古いキー 持たない設計 (推奨) ヒトの認証 AWS IAM Identity Center CLI 利⽤ aws sso login サービス間連携 IAM ロール
  36. © 2026, Amazon Web Services, Inc. or its affiliates. All

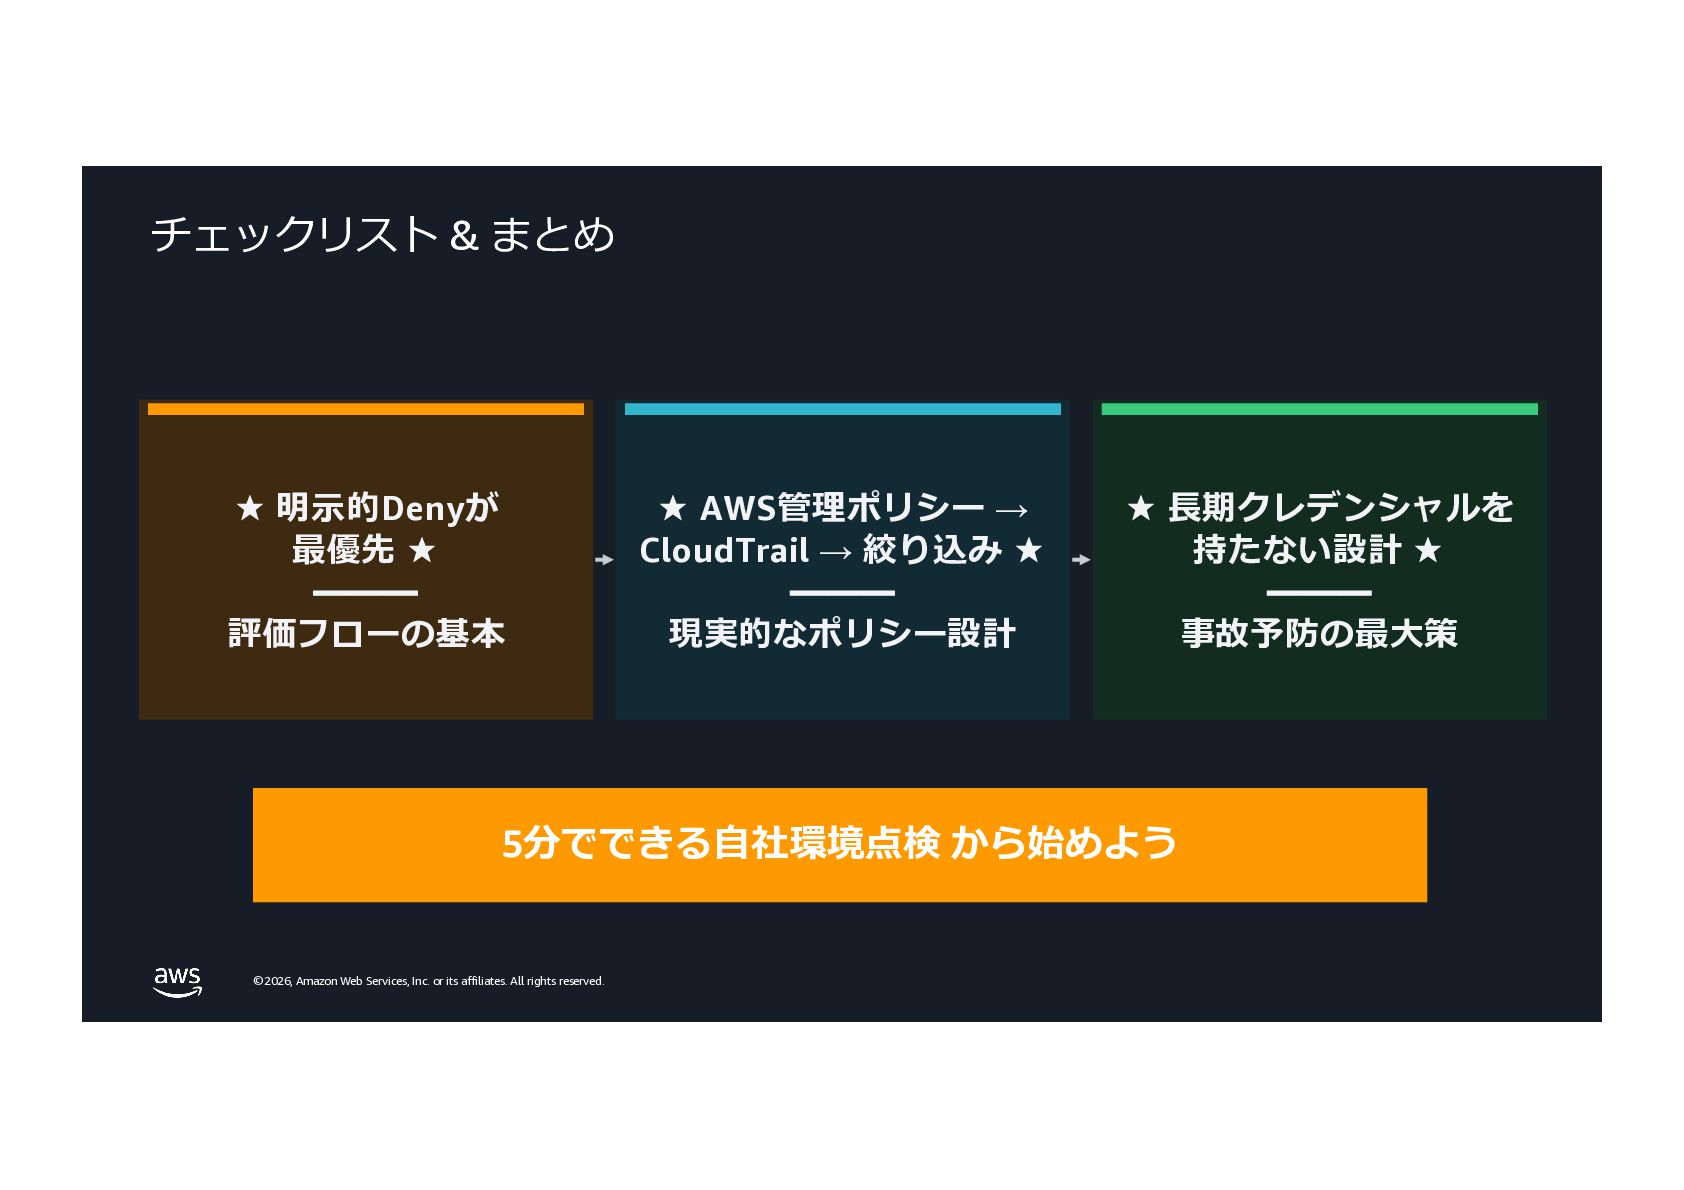
    rights reserved. チェックリスト & まとめ ★ 明⽰的Denyが 最優先 ★ ━━━ 評価フローの基本 ★ AWS管理ポリシー → CloudTrail → 絞り込み ★ ━━━ 現実的なポリシー設計 ★ ⻑期クレデンシャルを 持たない設計 ★ ━━━ 事故予防の最⼤策 5分でできる⾃社環境点検 から始めよう
  37. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. Q&A Q&A 今⽇の内容をさらに深掘りしたい⽅へ IAM ベスト プラクティス (公式) IAM Access Analyzer policy generation
  38. © 2026, Amazon Web Services, Inc. or its affiliates. All

    rights reserved. © 2026, Amazon Web Services, Inc. or its affiliates. All rights reserved. Thank you!