Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Secure Communication over insecure network

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →

Secure Communication over insecure network

A look at the land of Cryptography and how it affects our online life. We won't be diving into cryptography algorithms - instead we will treat them as “black boxes” - and see how they fit together given the right input. A bird's eye look at TLS handshake.

Mostly requires just logical thinking of how all these different pieces fit together.

Tejas Bubane

February 12, 2019

Transcript

73 slides
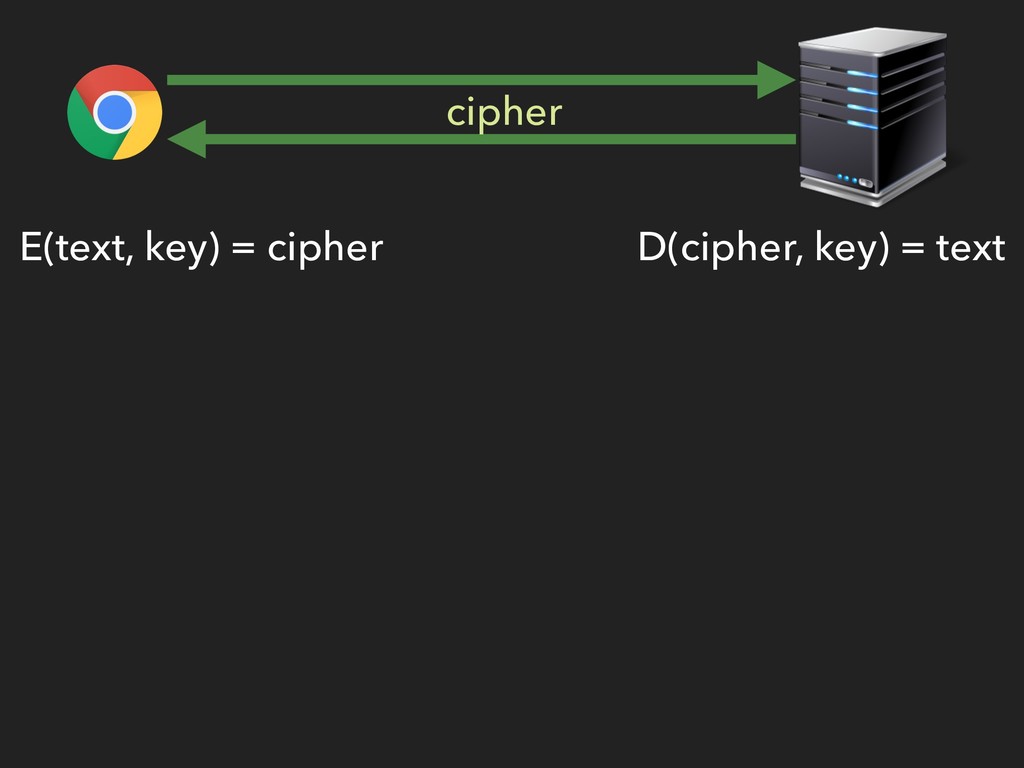
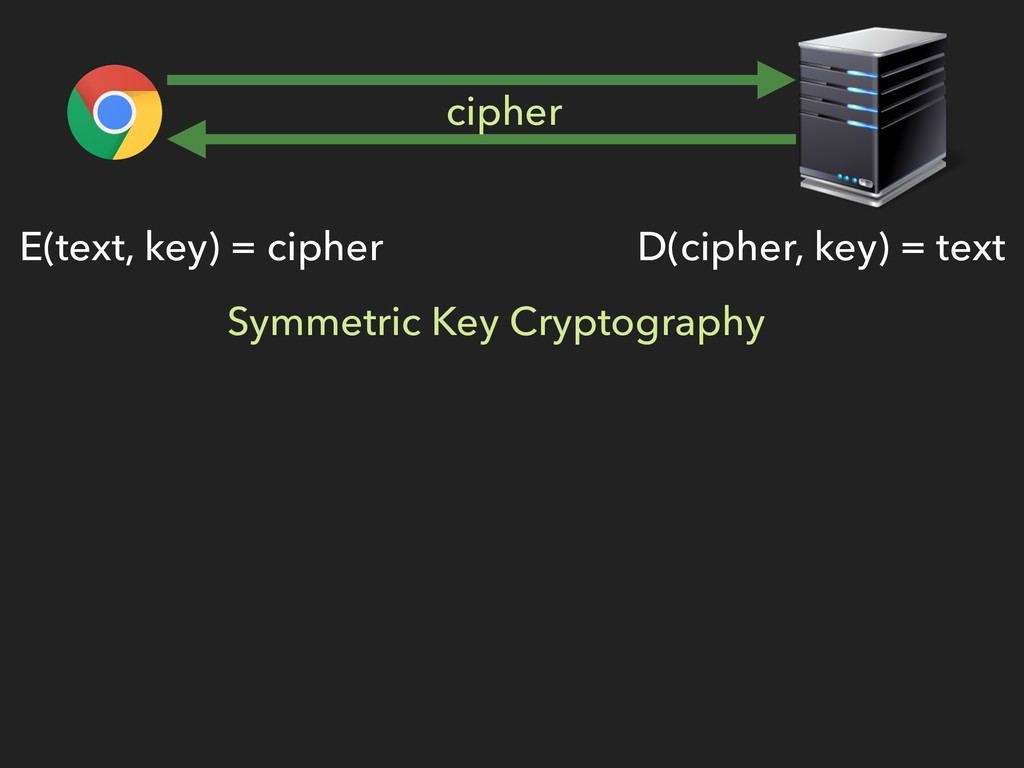
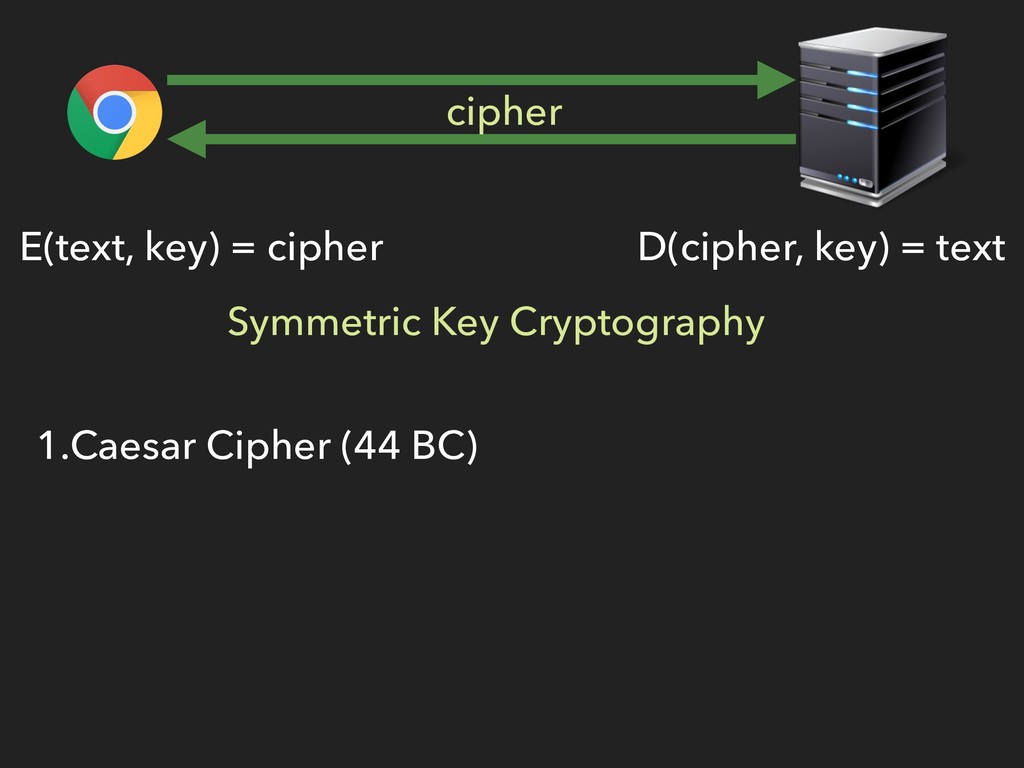
  1. E(text, key) = cipher D(cipher, key) = text cipher Symmetric

    Key Cryptography 1.Caesar Cipher (44 BC)
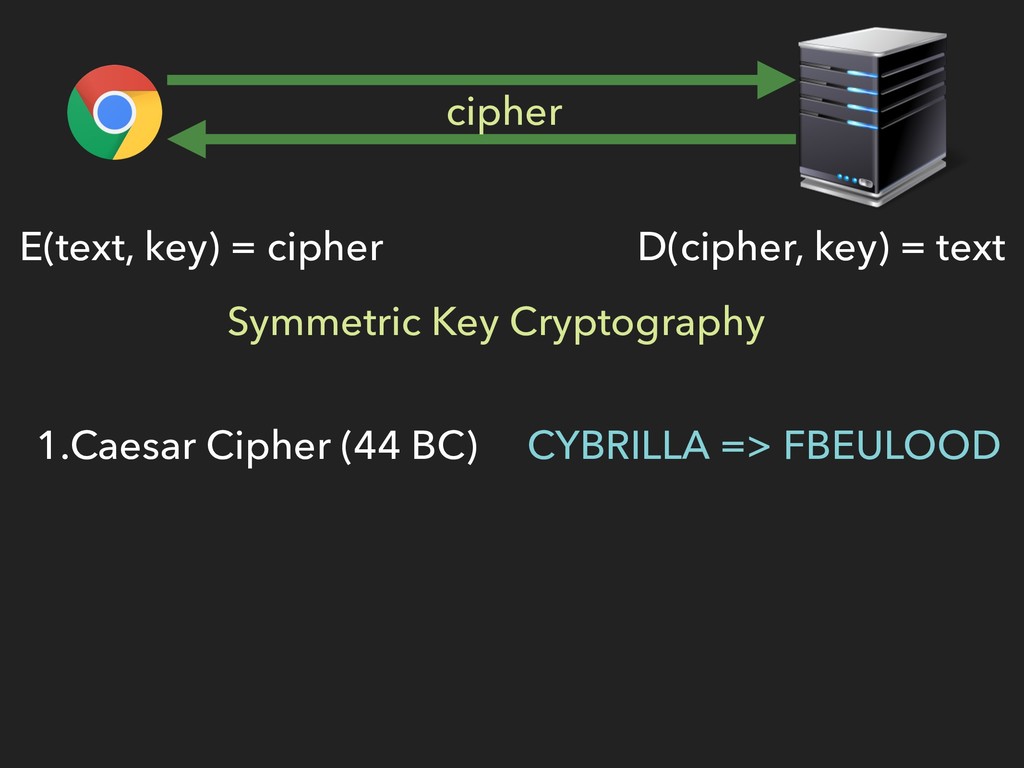
  2. E(text, key) = cipher D(cipher, key) = text cipher Symmetric

    Key Cryptography 1.Caesar Cipher (44 BC) CYBRILLA => FBEULOOD
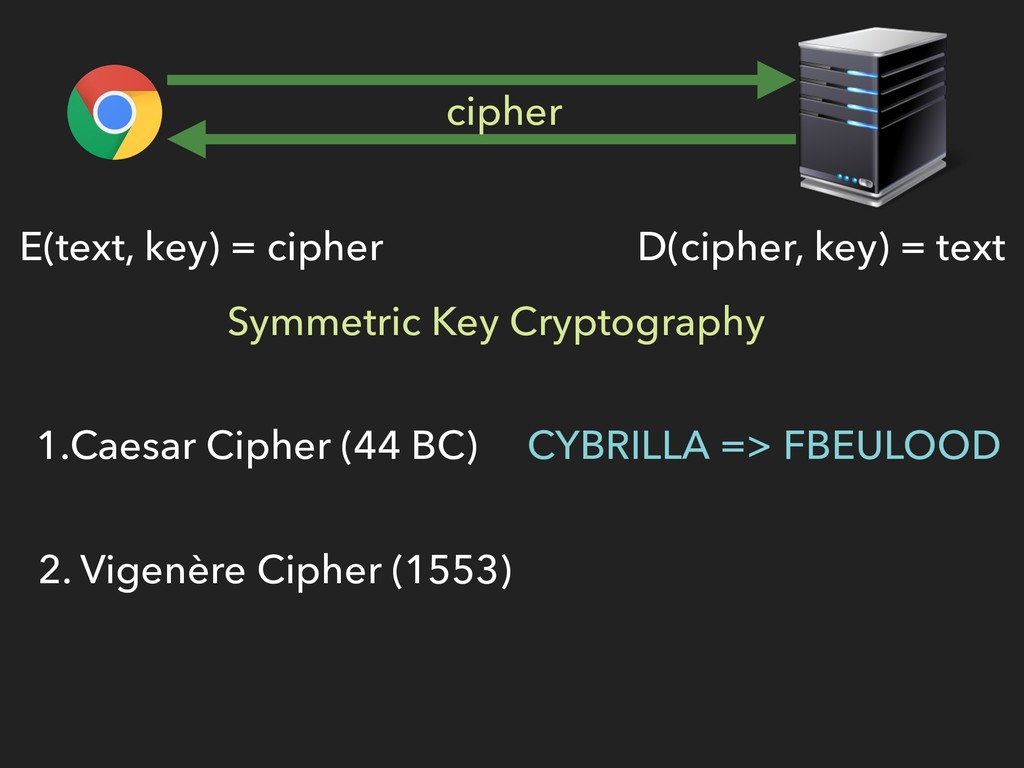
  3. E(text, key) = cipher D(cipher, key) = text cipher Symmetric

    Key Cryptography 1.Caesar Cipher (44 BC) CYBRILLA => FBEULOOD 2. Vigenère Cipher (1553)
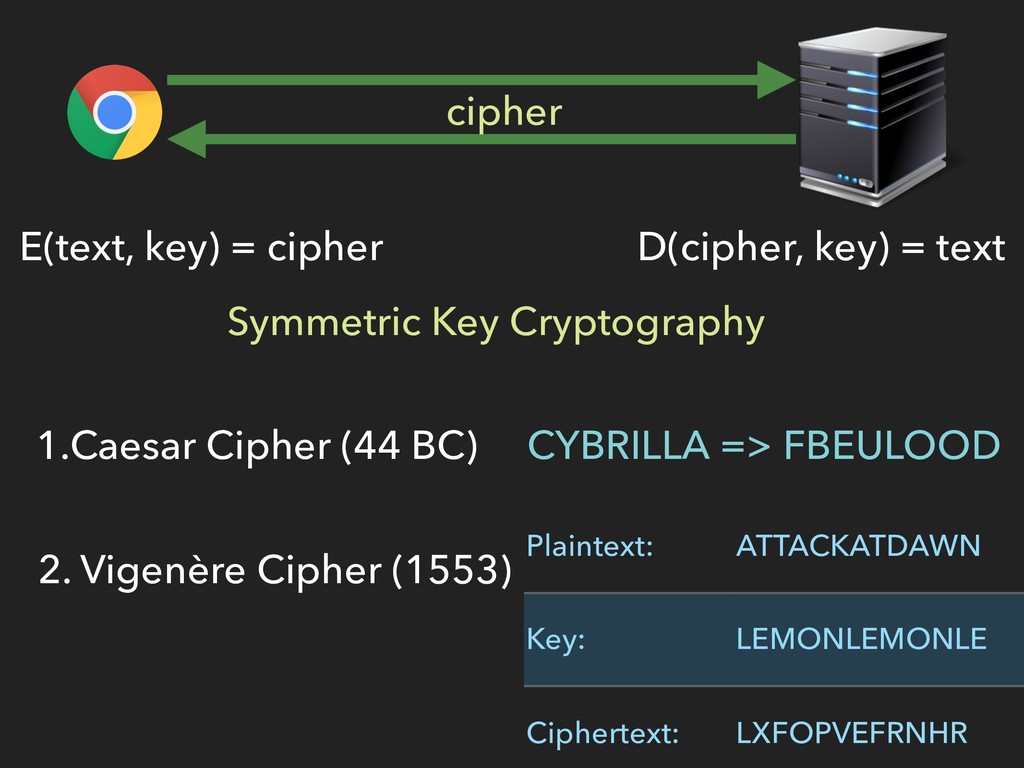
  4. E(text, key) = cipher D(cipher, key) = text cipher Symmetric

    Key Cryptography 1.Caesar Cipher (44 BC) CYBRILLA => FBEULOOD 2. Vigenère Cipher (1553) Plaintext: ATTACKATDAWN Key: LEMONLEMONLE Ciphertext: LXFOPVEFRNHR
  5. SSL/TLS •SSL (Netscape, 1995) •TLS 1.0 (IETF 1999) •TLS 1.1

    (2006) •TLS 1.2 (2008) •TLS 1.3 (2018) Cryptographic Protocol
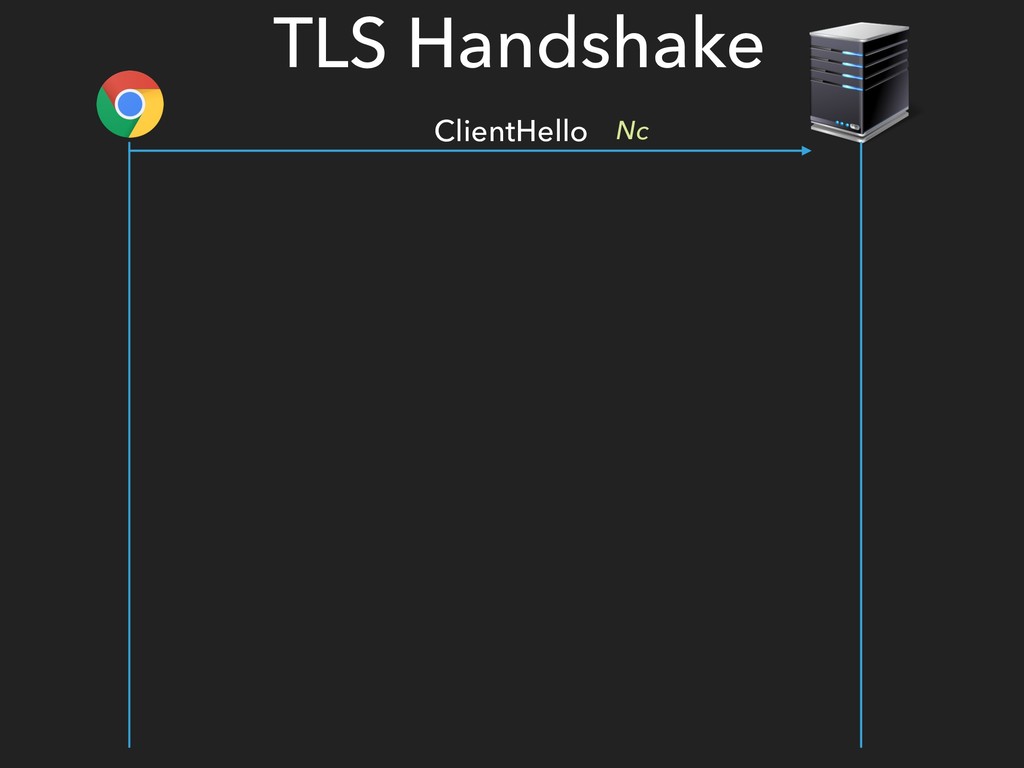
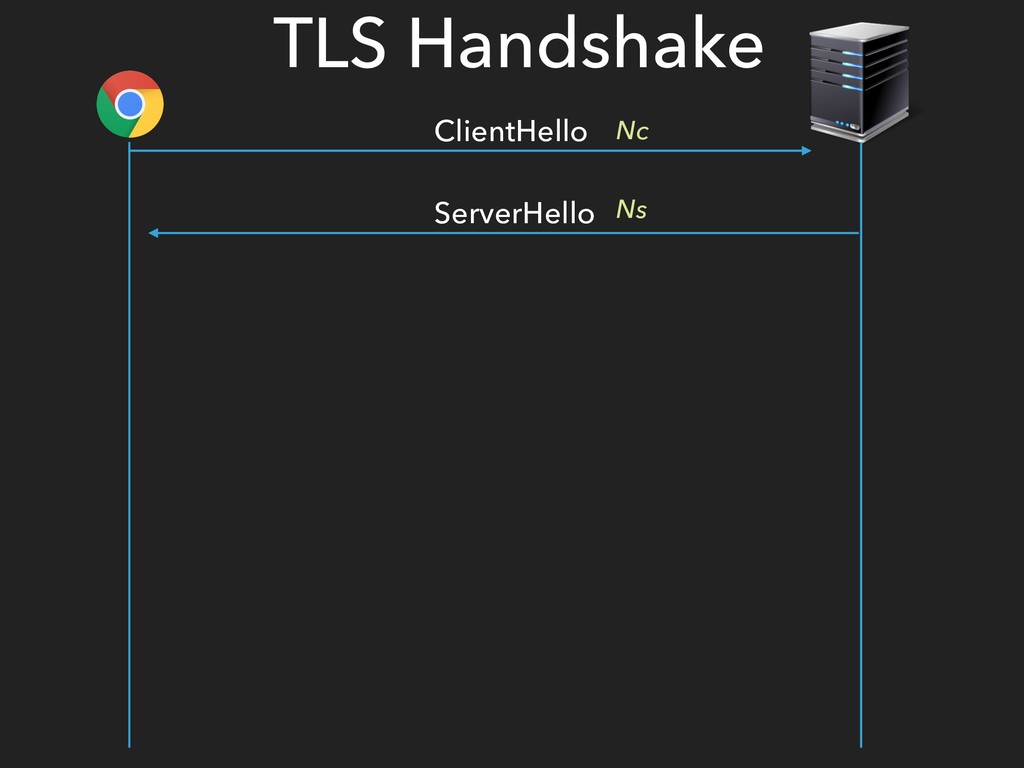
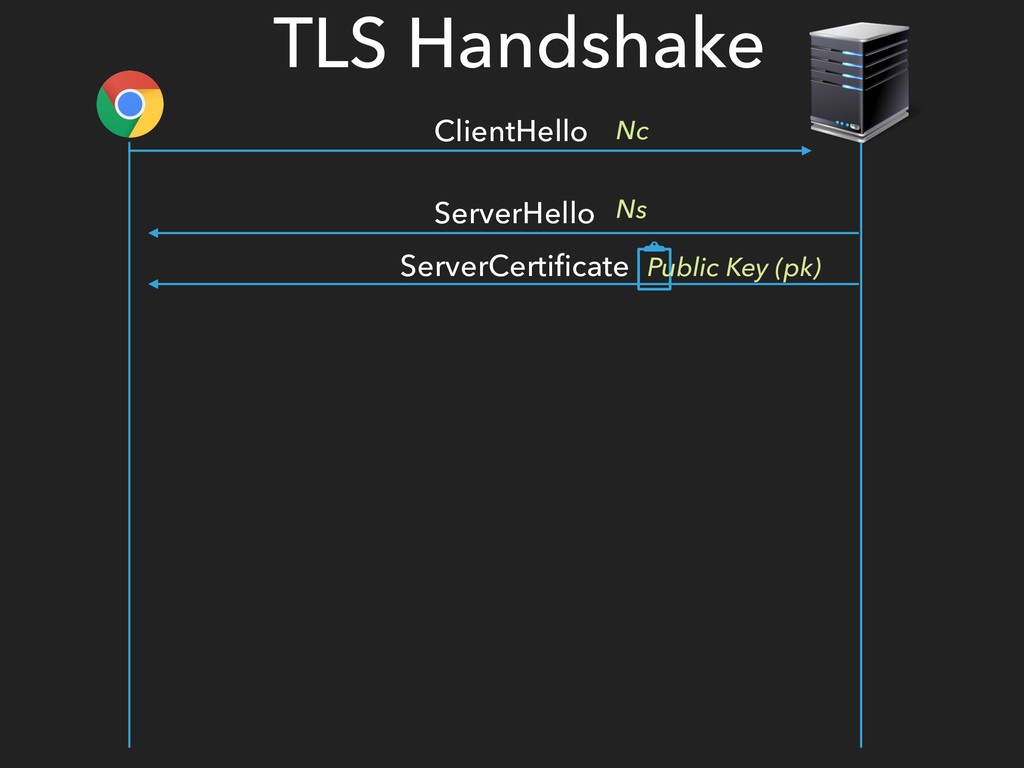
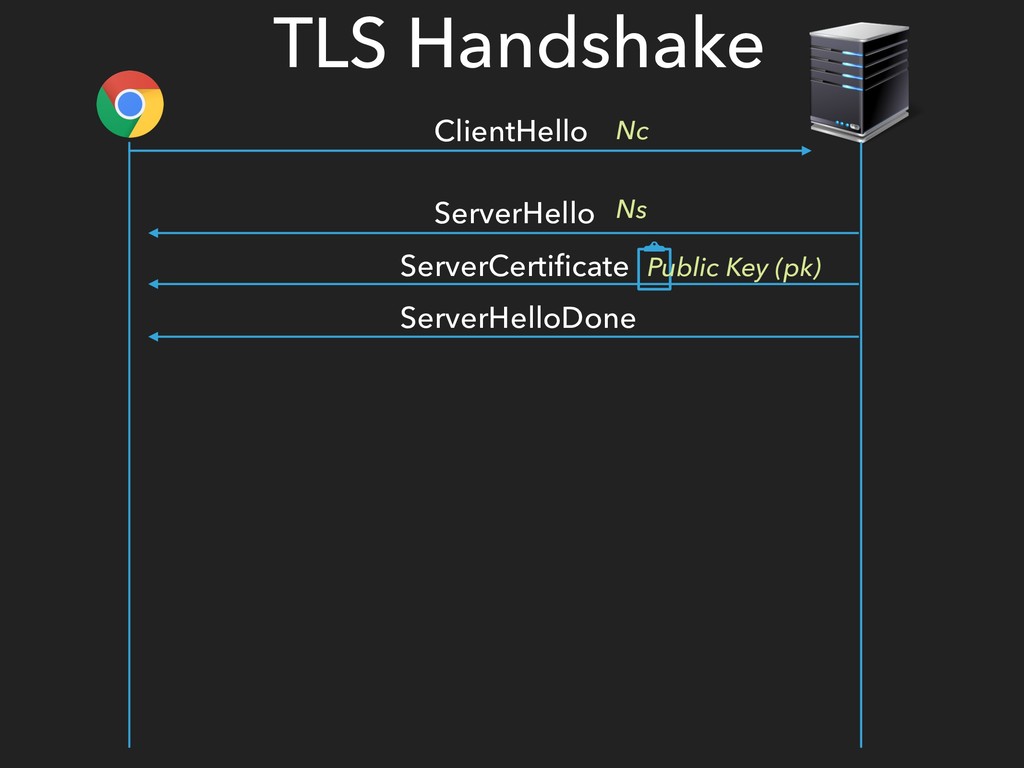
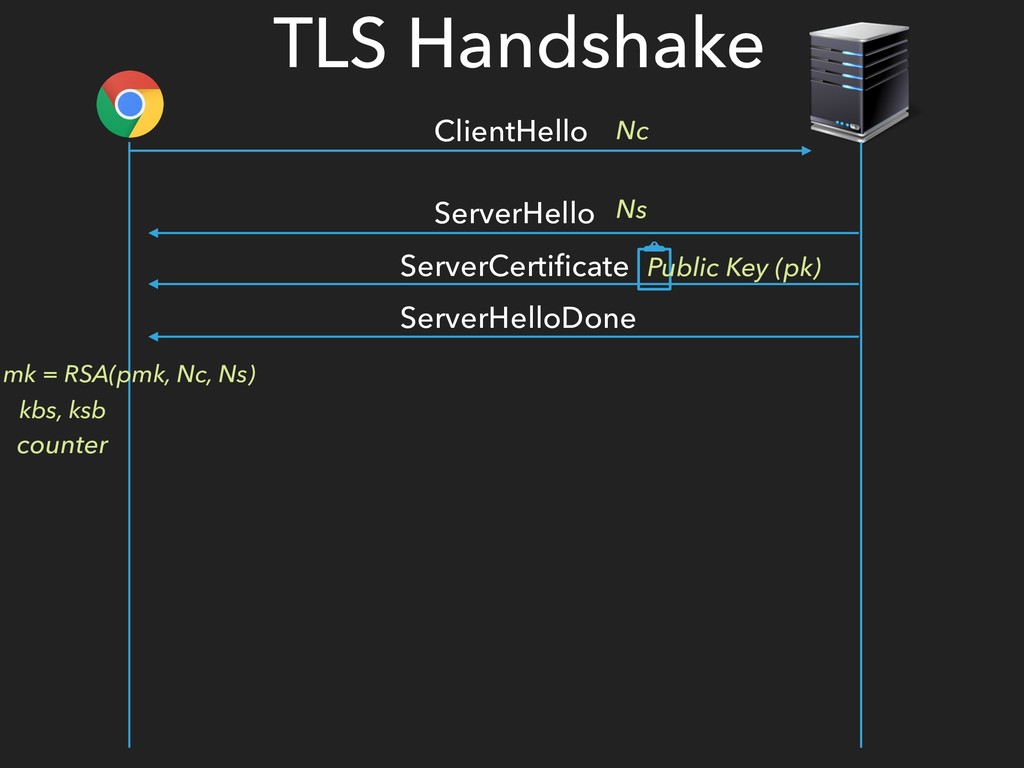
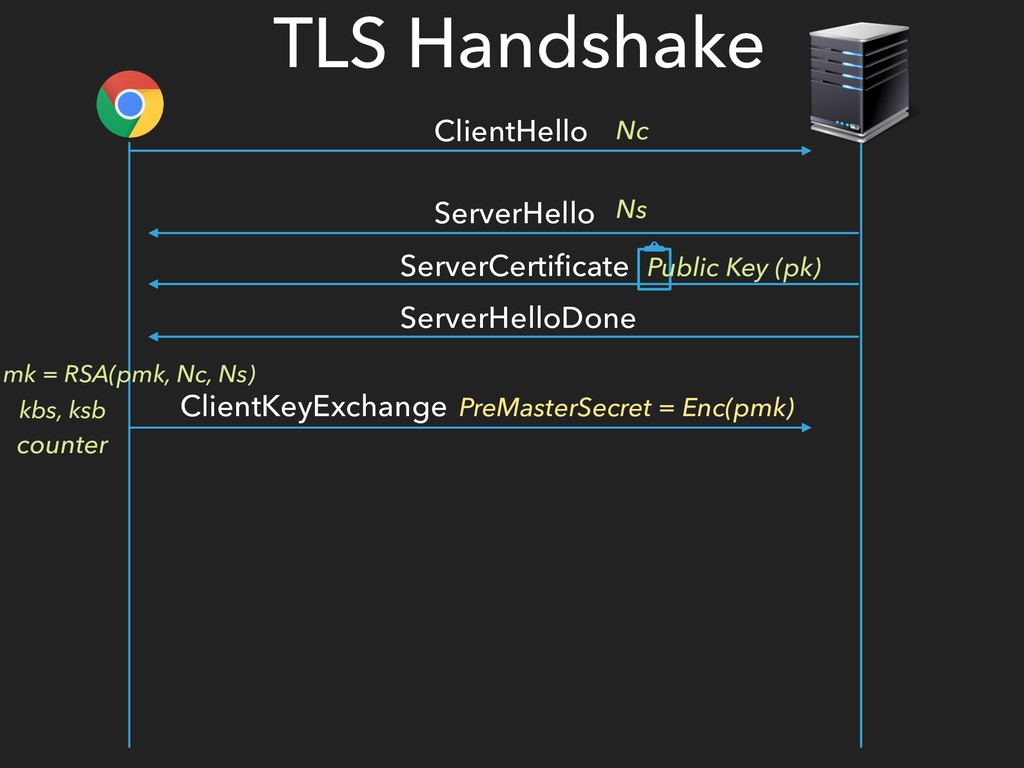
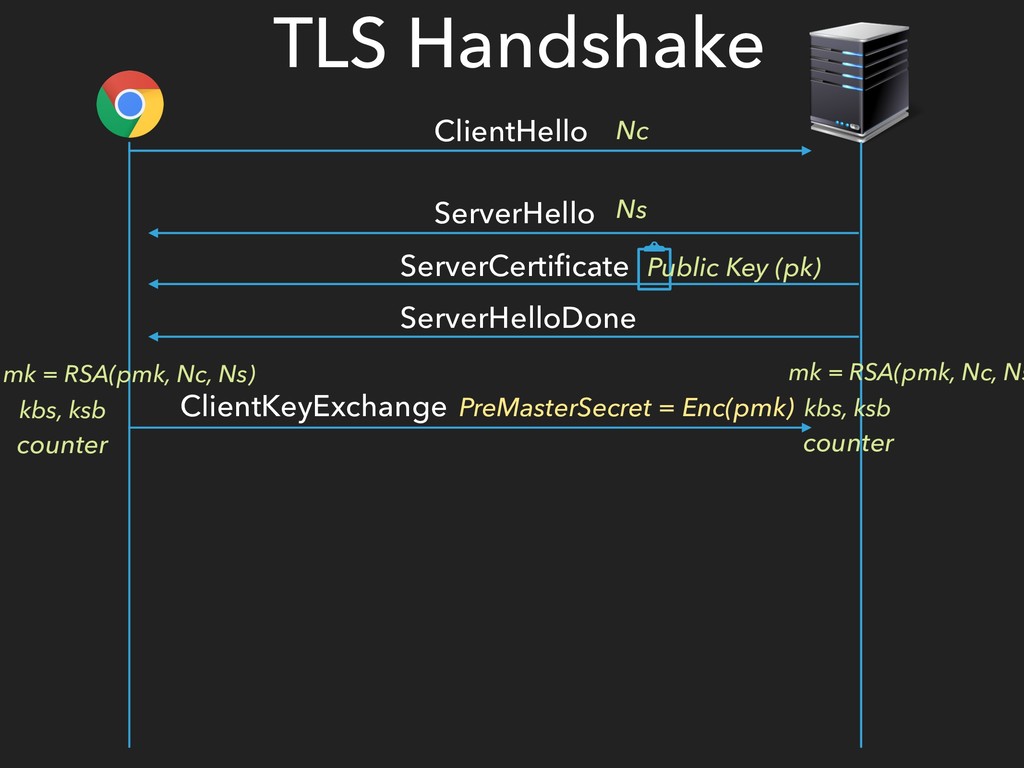
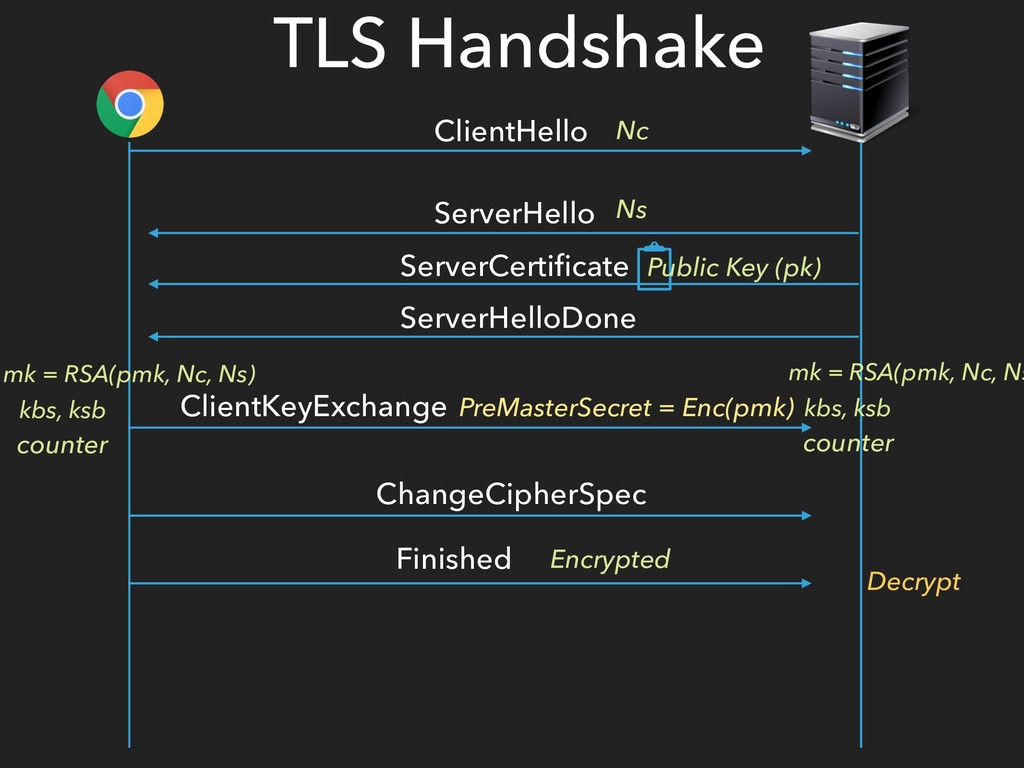
  6. ClientHello ServerHello ServerCertificate ServerHelloDone ClientKeyExchange PreMasterSecret = Enc(pmk) TLS Handshake

    Public Key (pk) kbs, ksb counter mk = RSA(pmk, Nc, Ns) Nc Ns kbs, ksb counter mk = RSA(pmk, Nc, Ns
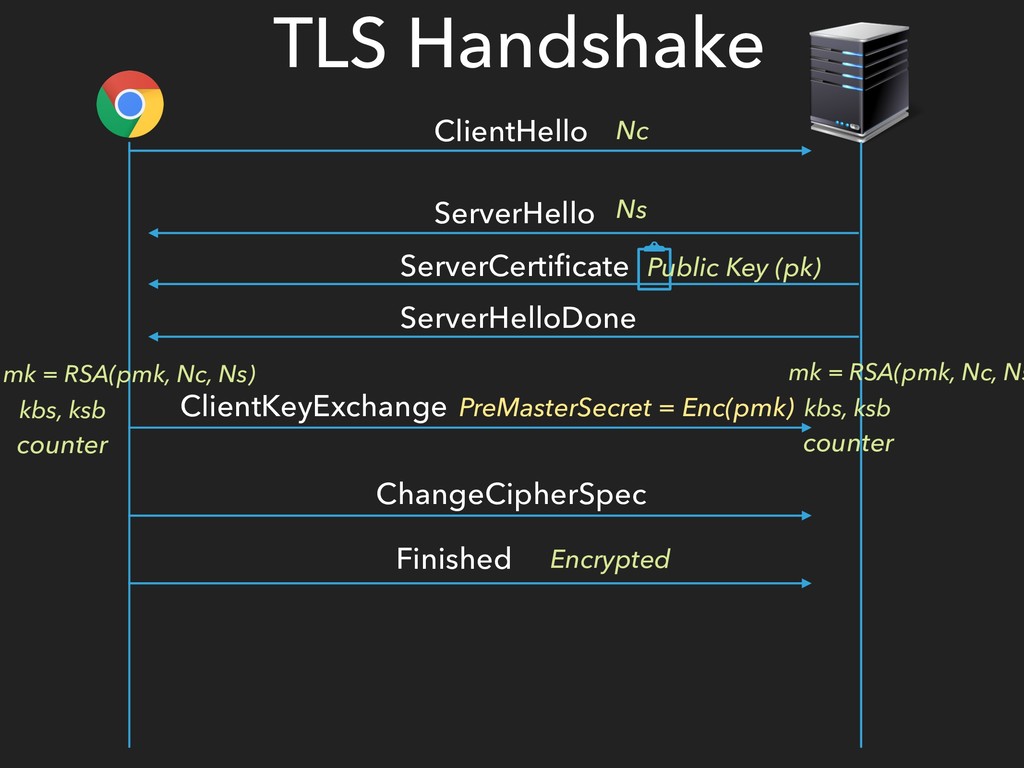
  7. ClientHello ServerHello ServerCertificate ServerHelloDone ClientKeyExchange PreMasterSecret = Enc(pmk) Finished Encrypted

    ChangeCipherSpec TLS Handshake Public Key (pk) kbs, ksb counter mk = RSA(pmk, Nc, Ns) Nc Ns kbs, ksb counter mk = RSA(pmk, Nc, Ns
  8. ClientHello ServerHello ServerCertificate ServerHelloDone ClientKeyExchange PreMasterSecret = Enc(pmk) Finished Encrypted

    ChangeCipherSpec Decrypt TLS Handshake Public Key (pk) kbs, ksb counter mk = RSA(pmk, Nc, Ns) Nc Ns kbs, ksb counter mk = RSA(pmk, Nc, Ns
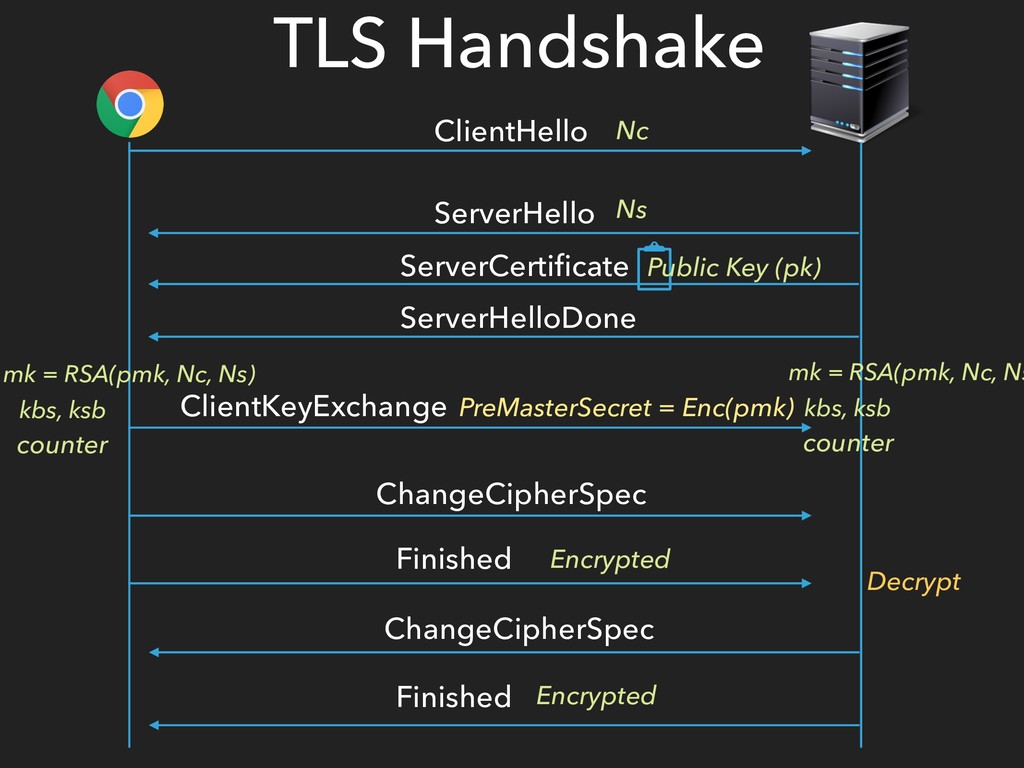
  9. ClientHello ServerHello ServerCertificate ServerHelloDone ClientKeyExchange PreMasterSecret = Enc(pmk) ChangeCipherSpec Finished

    Encrypted ChangeCipherSpec Decrypt Finished Encrypted TLS Handshake Public Key (pk) kbs, ksb counter mk = RSA(pmk, Nc, Ns) Nc Ns kbs, ksb counter mk = RSA(pmk, Nc, Ns
  10. What now? ‣Client & Server both have has ksb, kbs

    ‣Use symmetric key encryption (AES) for all further communications
  11. What now? ‣Client & Server both have has ksb, kbs

    ‣Use symmetric key encryption (AES) for all further communications ‣Why not use public key everywhere?
  12. What now? ‣Client & Server both have has ksb, kbs

    ‣Use symmetric key encryption (AES) for all further communications ‣Why not use public key everywhere? ‣Public key encryption is slow - use it for key exchange (handshake) and use fast symmetric encryption thereafter
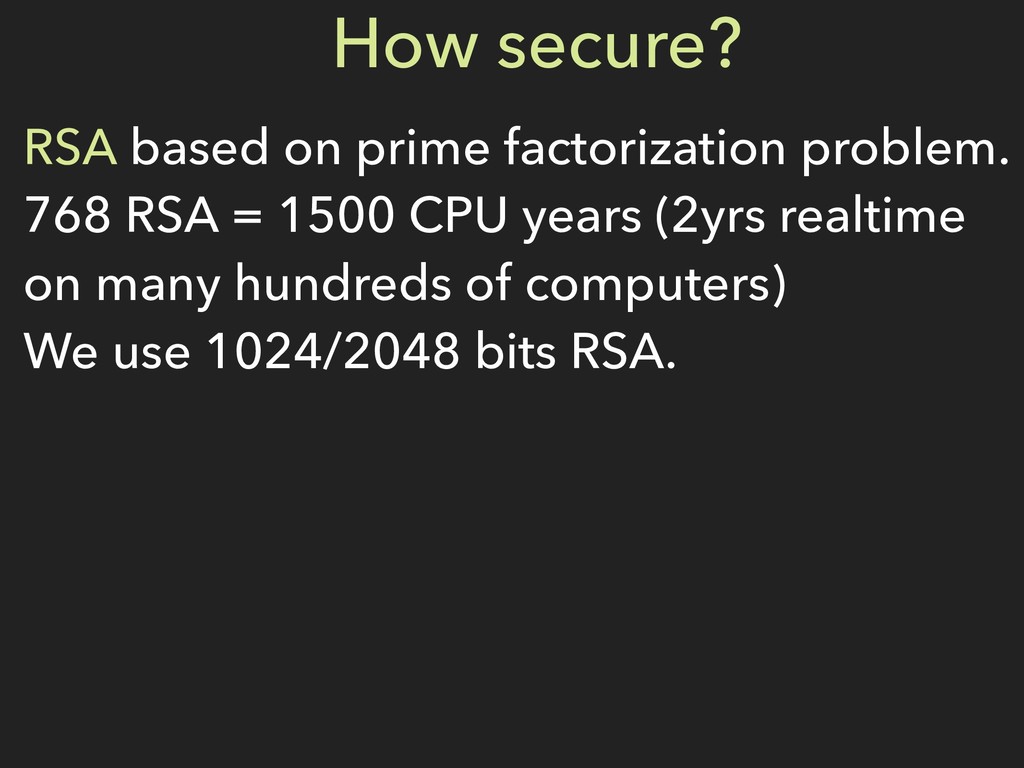
  13. How secure? RSA based on prime factorization problem. 768 RSA

    = 1500 CPU years (2yrs realtime on many hundreds of computers) We use 1024/2048 bits RSA.
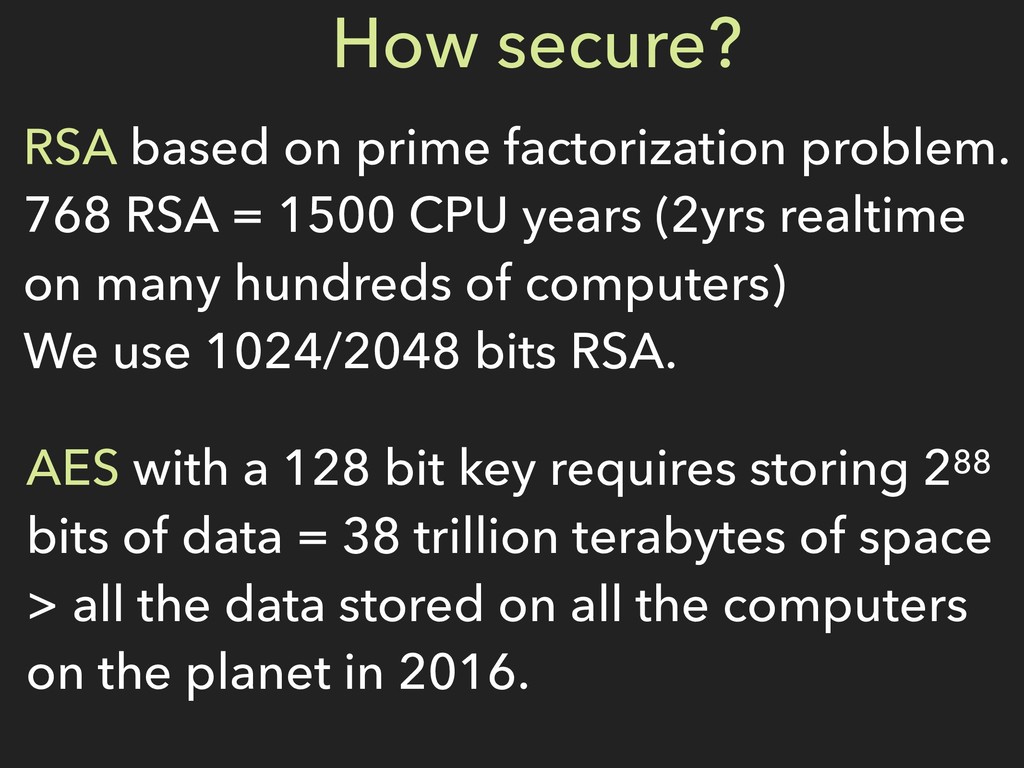
  14. How secure? RSA based on prime factorization problem. 768 RSA

    = 1500 CPU years (2yrs realtime on many hundreds of computers) We use 1024/2048 bits RSA. AES with a 128 bit key requires storing 288 bits of data = 38 trillion terabytes of space > all the data stored on all the computers on the planet in 2016.
More Decks by Tejas Bubane

Other Decks in Programming