Share
Embed
Python Language Summit 2016: The Future Of The SSL Module
Presentation at Python Language Summit 2016 about Python's ssl stdlib module.
Christian Heimes
May 28, 2016
Transcript
19 slides
-
The Future Of The SSL Module Python Language Summit 2016
Cory Benfield <[email protected]> Christian Heimes <[email protected]> -
Cory Benfield ❏ hyper (HTTP/2 for Python) ❏ PyOpenSSL ❏
requests ❏ urllib3 ❏ Employed by Hewlett Packard Enterprise to work on HTTP and HTTP/2 in Python -
Christian Heimes ❏ Python core contributor ❏ co-maintainer of Python’s
ssl module ❏ employed by Red Hat to work on Identity Management and Public Key Infrastructure -
What is the SSL module ❏ provides TLS/SSL support for
Python ❏ basic TLS server and client support ❏ no S/MIME or code signing ❏ uses OpenSSL internally ❏ vital for PIP to download packages for PyPI -
Alternative packages ❏ PyOpenSSL (OpenSSL, based on PyCA cryptography) ❏
python-nss (Mozilla NSS, heavily used in Red Hat) ❏ python-gnutls (GnuTLS) ❏ QSslSocket (pyqt) ❏ javax.net.ssl (Jython) ❏ System.Security.Cryptography (IronPython) ❏ ... -
SSL module is in a bad state ❏ “naturally grown”
over many years ❏ complicated ❏ _ssl._SSLSocket is wrapped by ssl.SSLObject, which is wrapped again by ssl.SSLSocket, which is a subclass of socket.socket. ❏ insane, footgunny legacy API ❏ SSLSocket.getpeercert() returns empty dict for CERT_NONE ❏ SSLContext() defaults to no verification, must use custom factory ❏ stdlib modules accept context or cert/key/verify args -
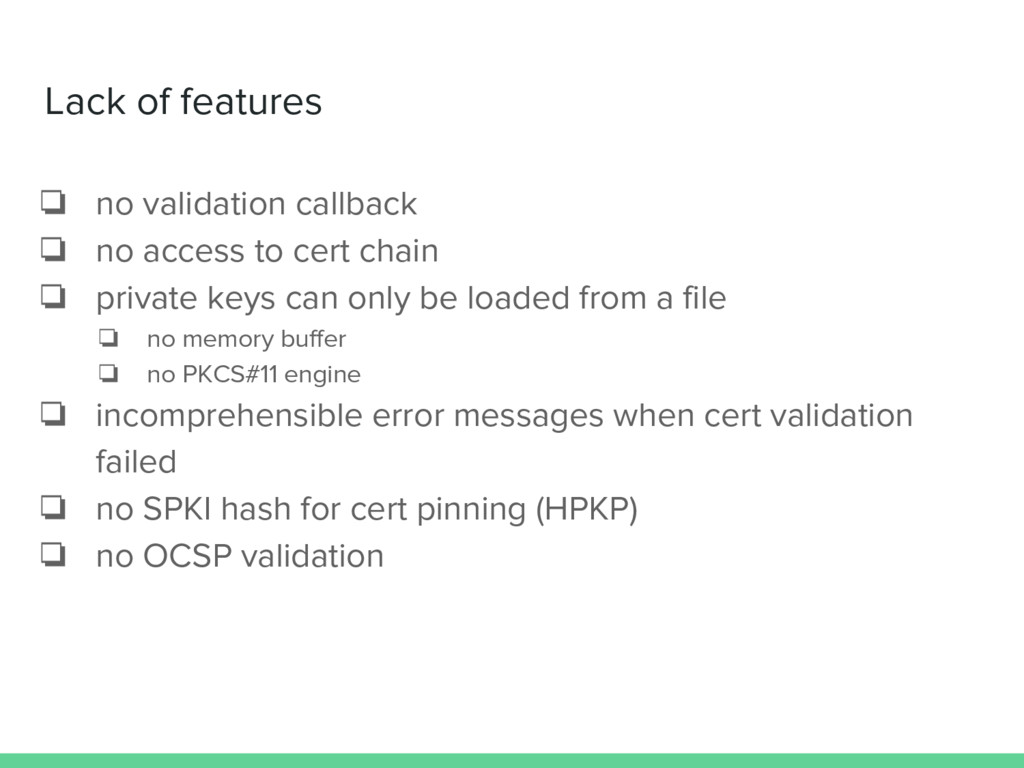
Lack of features ❏ no validation callback ❏ no access
to cert chain ❏ private keys can only be loaded from a file ❏ no memory buffer ❏ no PKCS#11 engine ❏ incomprehensible error messages when cert validation failed ❏ no SPKI hash for cert pinning (HPKP) ❏ no OCSP validation -
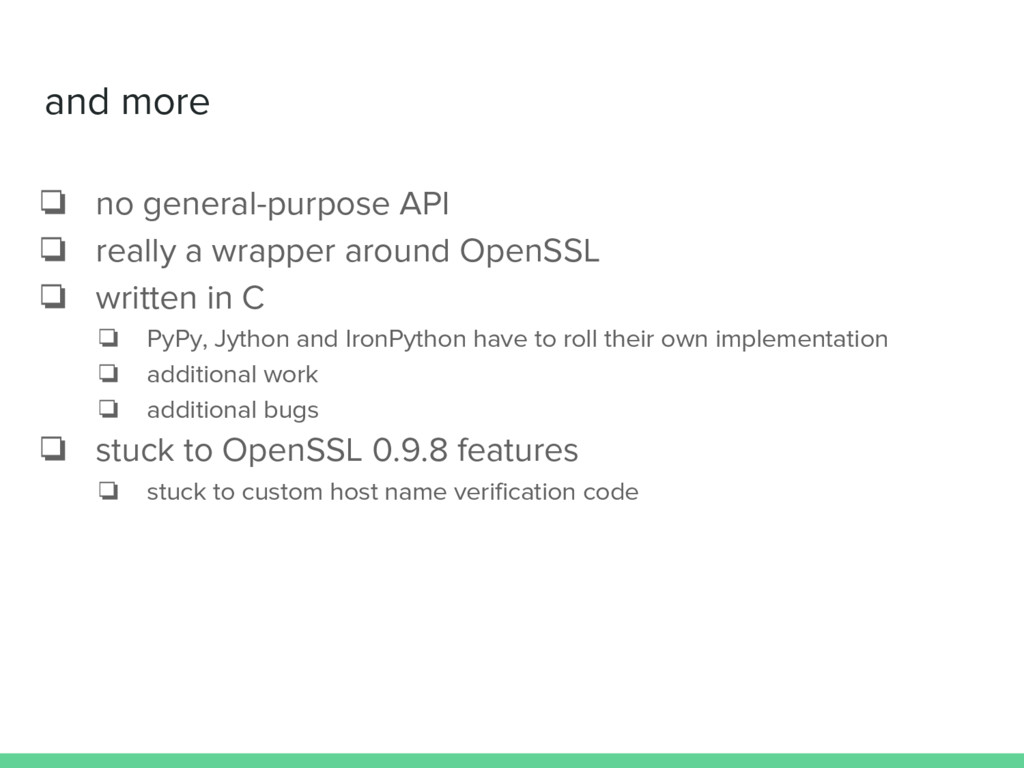
and more ❏ no general-purpose API ❏ really a wrapper
around OpenSSL ❏ written in C ❏ PyPy, Jython and IronPython have to roll their own implementation ❏ additional work ❏ additional bugs ❏ stuck to OpenSSL 0.9.8 features ❏ stuck to custom host name verification code -
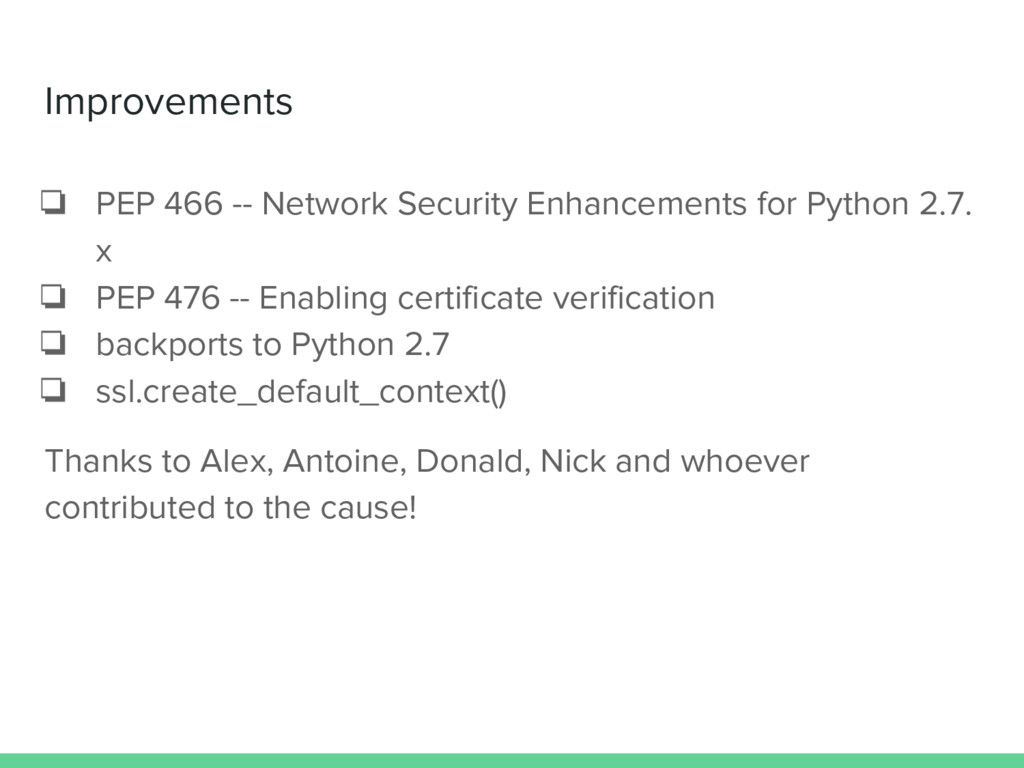
Improvements ❏ PEP 466 -- Network Security Enhancements for Python
2.7. x ❏ PEP 476 -- Enabling certificate verification ❏ backports to Python 2.7 ❏ ssl.create_default_context() Thanks to Alex, Antoine, Donald, Nick and whoever contributed to the cause! -
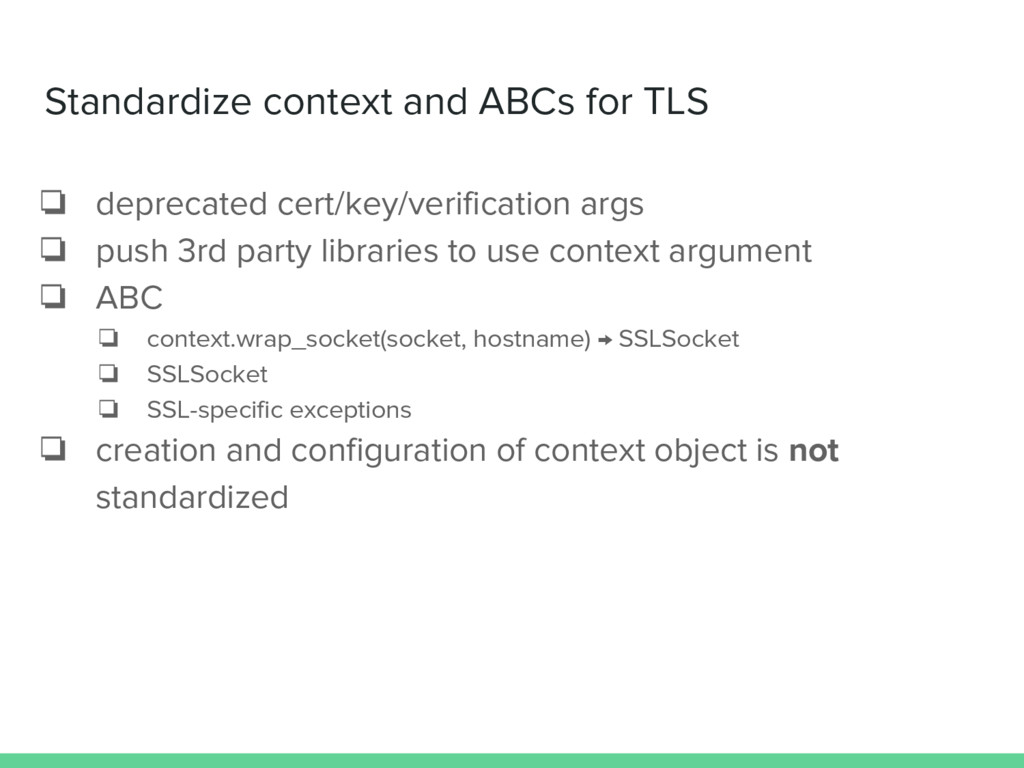
Standardize context and ABCs for TLS ❏ deprecated cert/key/verification args
❏ push 3rd party libraries to use context argument ❏ ABC ❏ context.wrap_socket(socket, hostname) → SSLSocket ❏ SSLSocket ❏ SSL-specific exceptions ❏ creation and configuration of context object is not standardized -
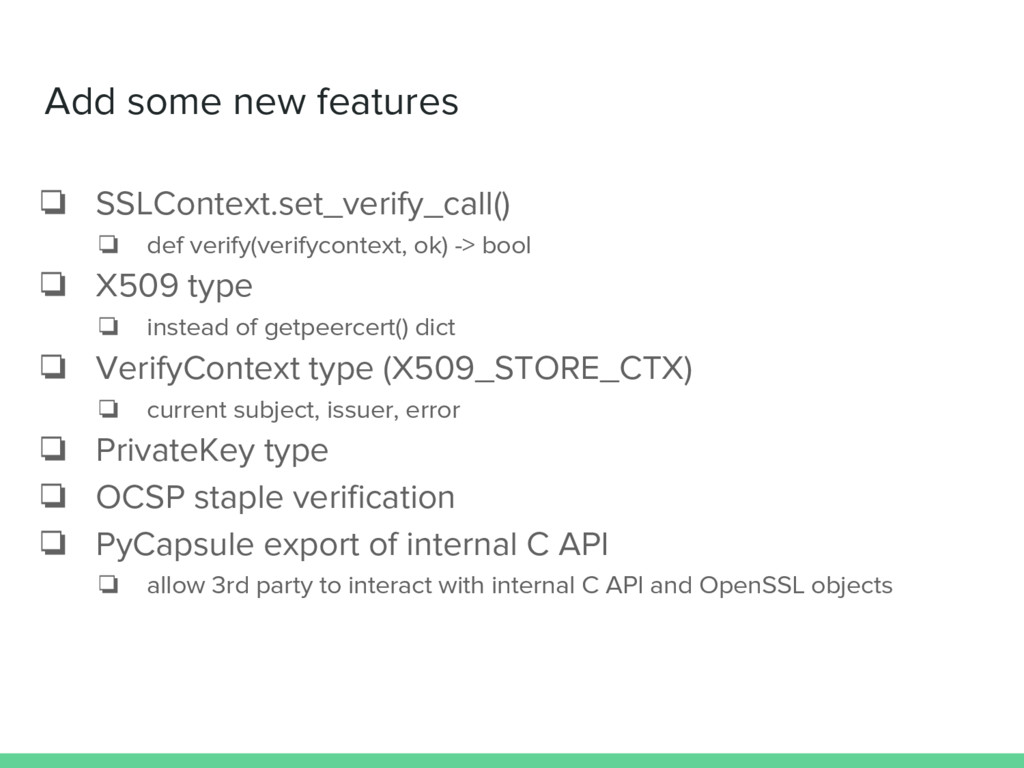
Add some new features ❏ SSLContext.set_verify_call() ❏ def verify(verifycontext, ok)
-> bool ❏ X509 type ❏ instead of getpeercert() dict ❏ VerifyContext type (X509_STORE_CTX) ❏ current subject, issuer, error ❏ PrivateKey type ❏ OCSP staple verification ❏ PyCapsule export of internal C API ❏ allow 3rd party to interact with internal C API and OpenSSL objects -
Feature moratorium ❏ SSL module should provide basic features for
stdlib and PIP ❏ some new and security-relevant features ❏ push users to 3rd party software for advanced use cases ❏ PyOpenSSL ❏ cryptography.tls ? -
Go OpenSSL 1.1.0 ❏ OpenSSL 1.1.0 made struct opaque and
has cleaner API ❏ provide 1.0.2 compatibility layer (implemented in #26470) ❏ deprecate OpenSSL 1.0.1 and 0.9.8 ❏ use OpenSSL to verify host names ❏ backward compatibility? ❏ OSX? ❏ LibreSSL? -
Root CA certificates (trust anchors) ❏ requests comes with certifi
❏ Python must never ever ship its own root certificate bundle. Period. ❏ Trust the operating system and use its root store. ❏ OSX? ❏ Windows implementation is semi-broken. SChannel fetch unknown root certs from MS, Python doesn’t. ❏ Libraries should provide SSLContext argument so users can customize trust settings or use env var SSL_CERT_FILE.