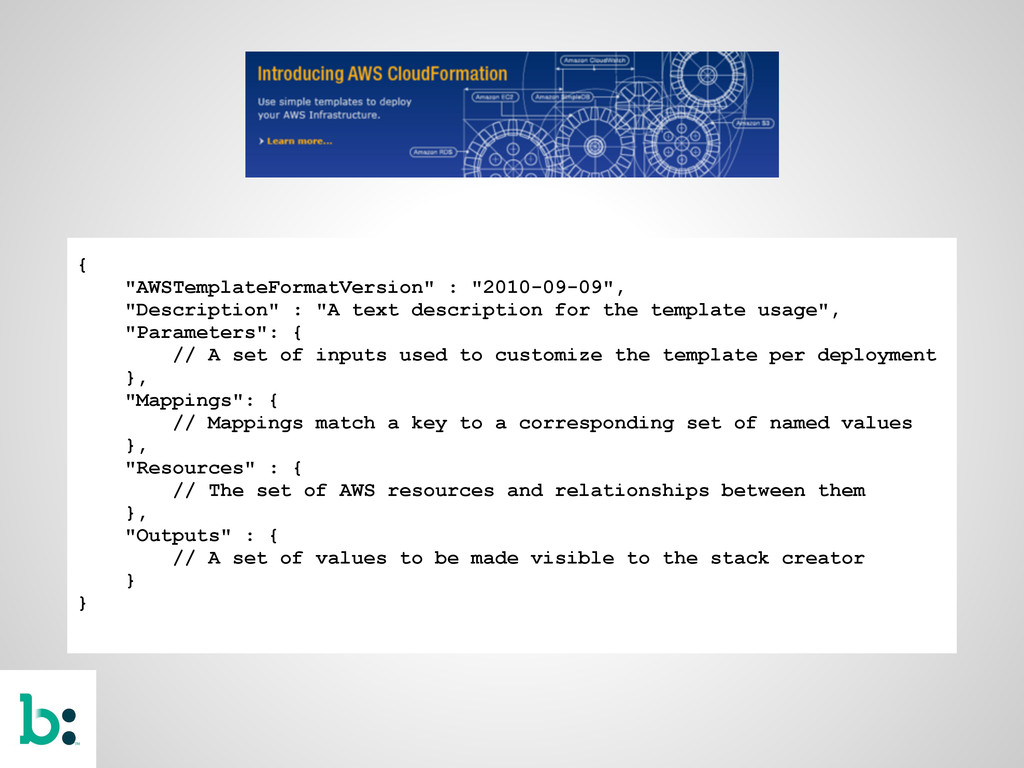
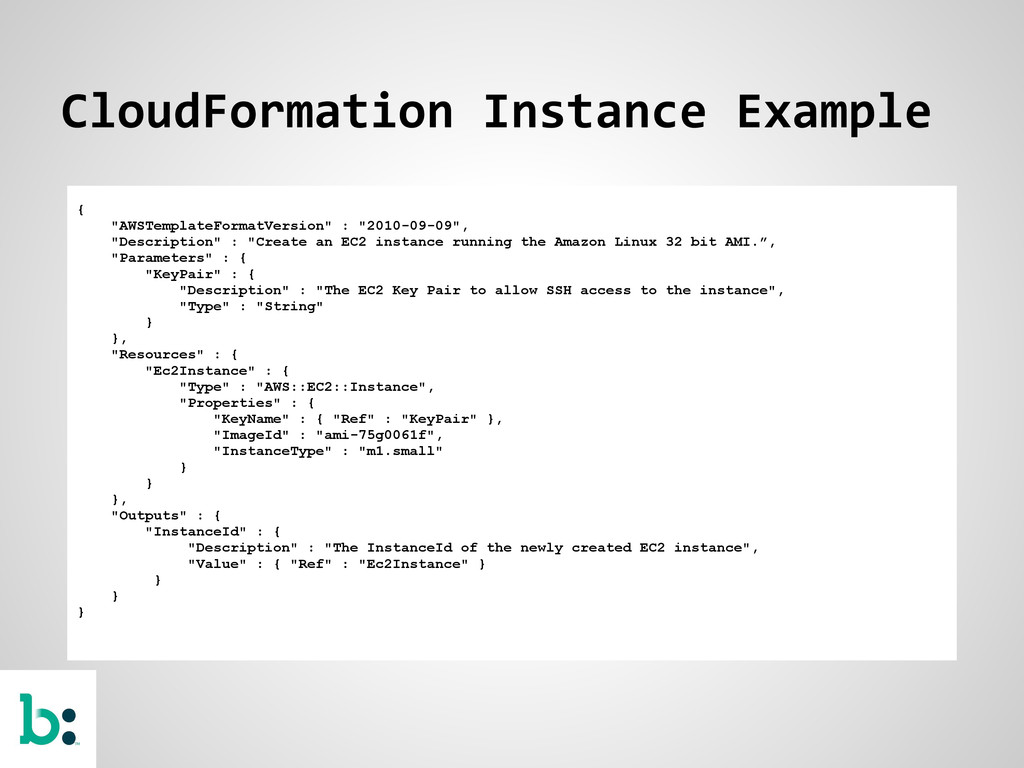
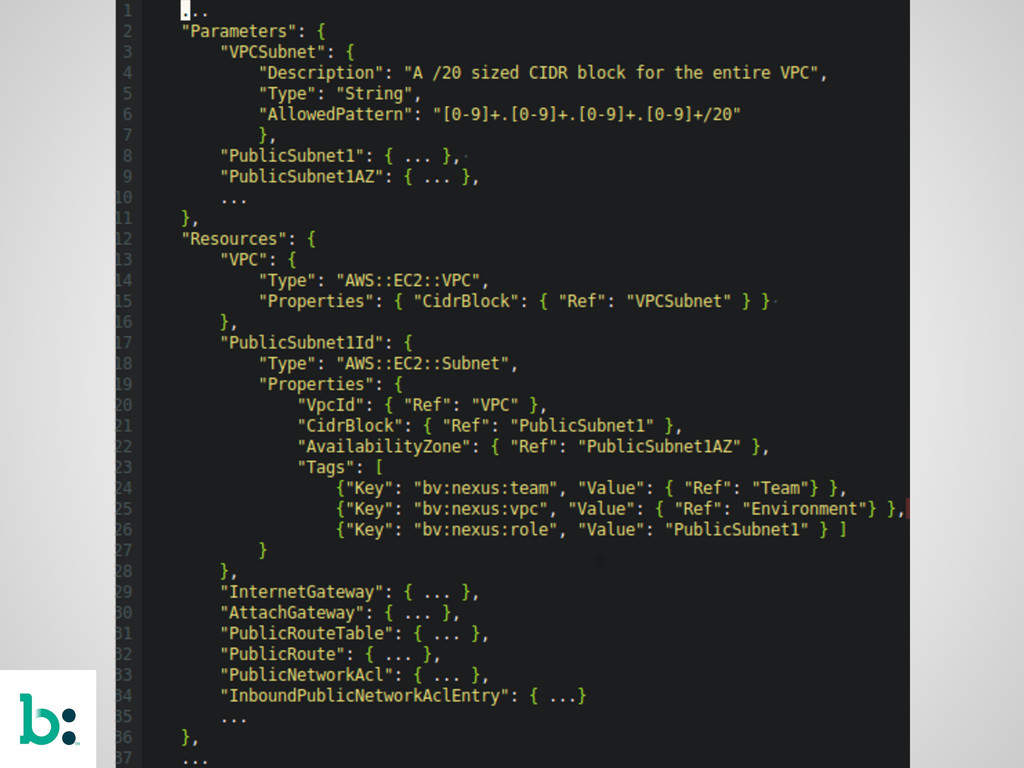
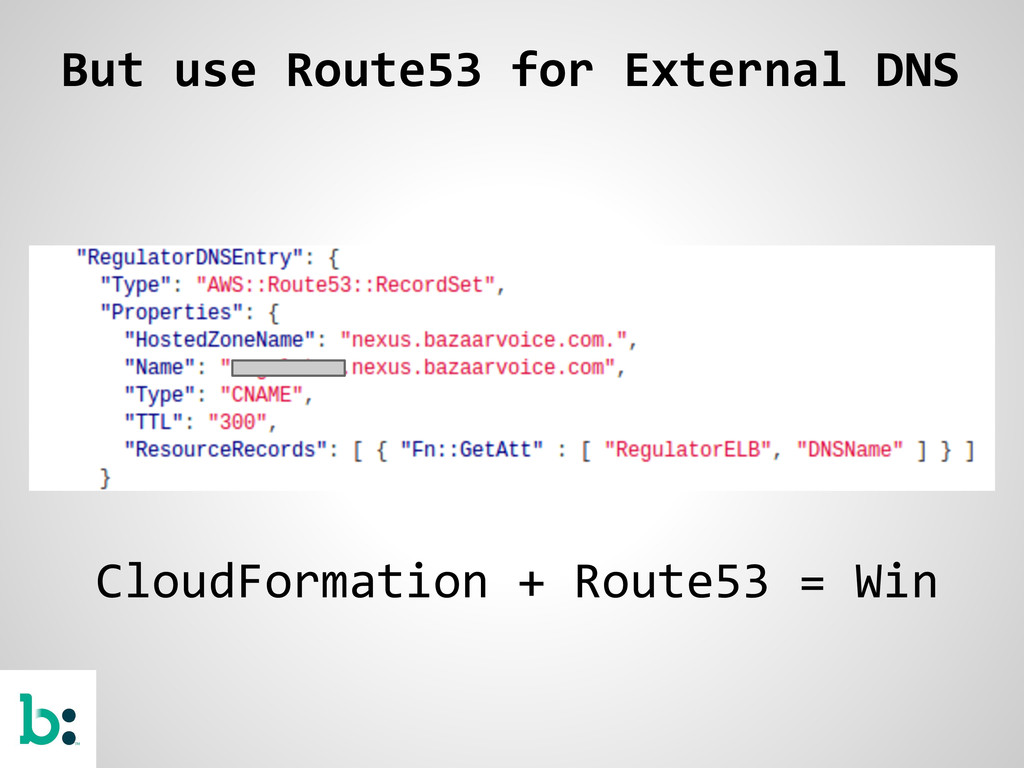
the template usage", "Parameters": { // A set of inputs used to customize the template per deployment }, "Mappings": { // Mappings match a key to a corresponding set of named values }, "Resources" : { // The set of AWS resources and relationships between them }, "Outputs" : { // A set of values to be made visible to the stack creator } }
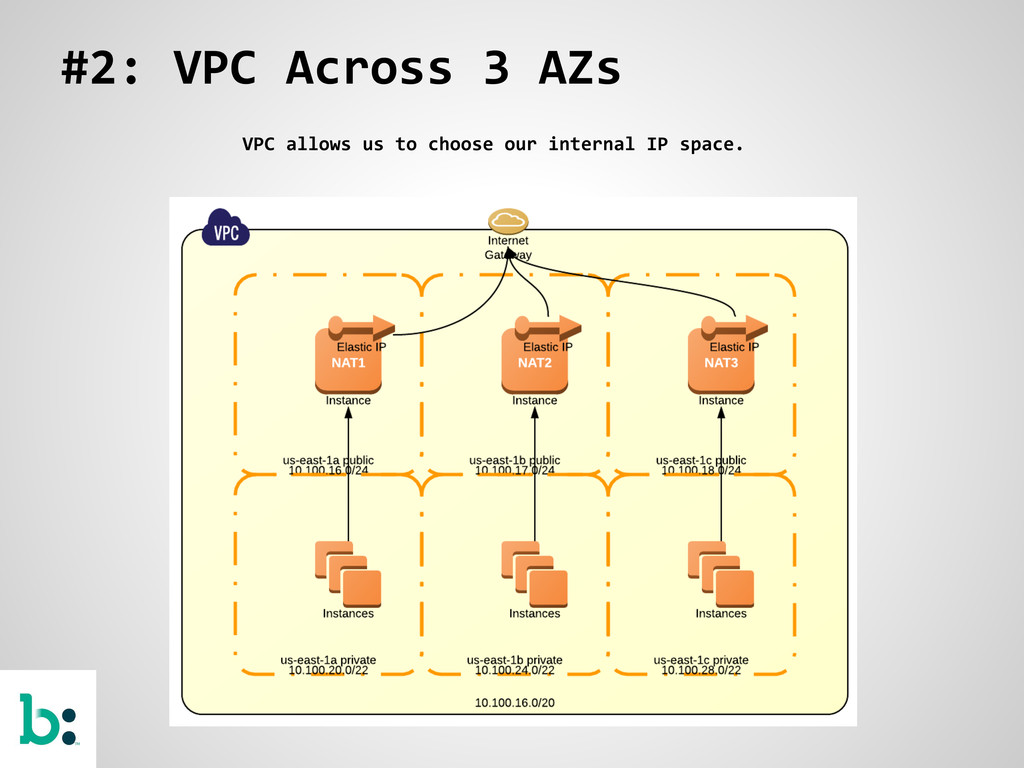
our internal IP space. Default Route for All Subnets to IGW • Let's call these subnets all "Public" • Requires all instances to have EIPs before talking to the internet • EIPs are a limited resource Public: Default route via IGW Private: Default route via instance(s) in Public Subnets Advantage: Most instances in the private subnet can talk to the internet without dealing with an EIP.
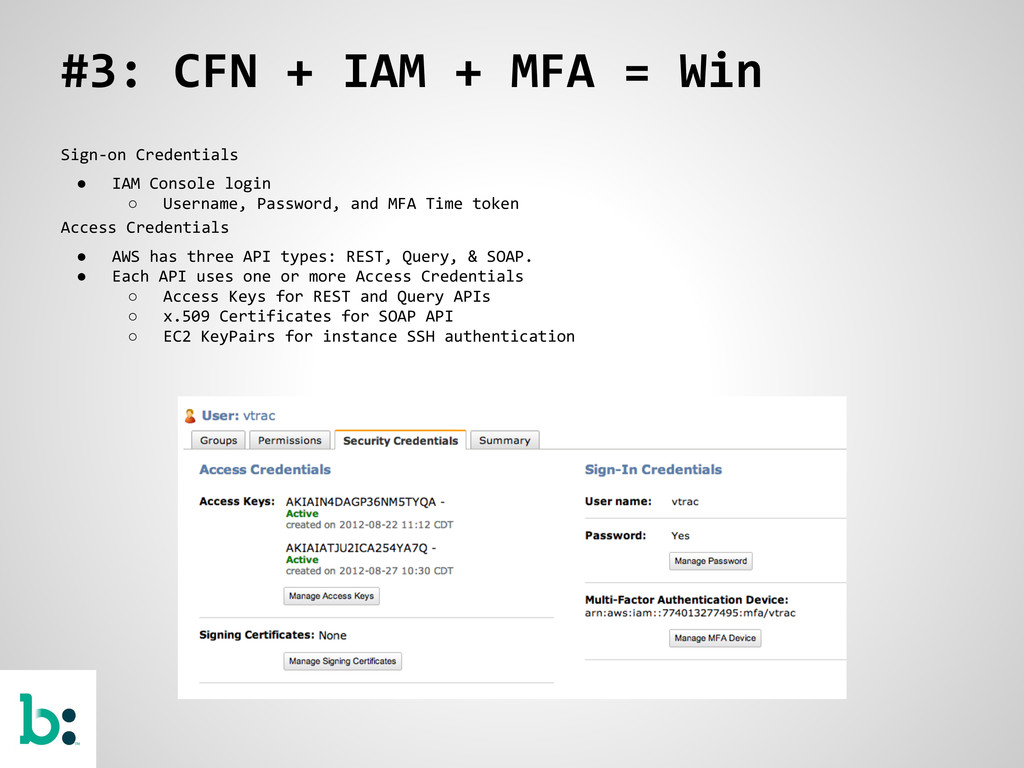
• IAM Console login ◦ Username, Password, and MFA Time token Access Credentials • AWS has three API types: REST, Query, & SOAP. • Each API uses one or more Access Credentials ◦ Access Keys for REST and Query APIs ◦ x.509 Certificates for SOAP API ◦ EC2 KeyPairs for instance SSH authentication
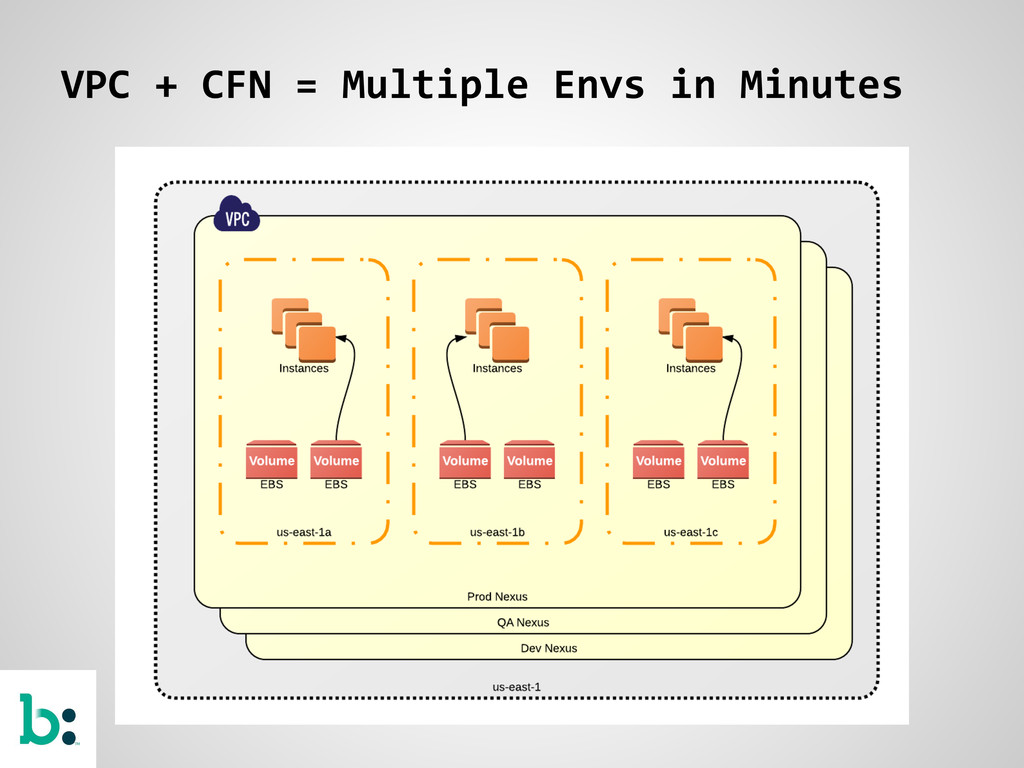
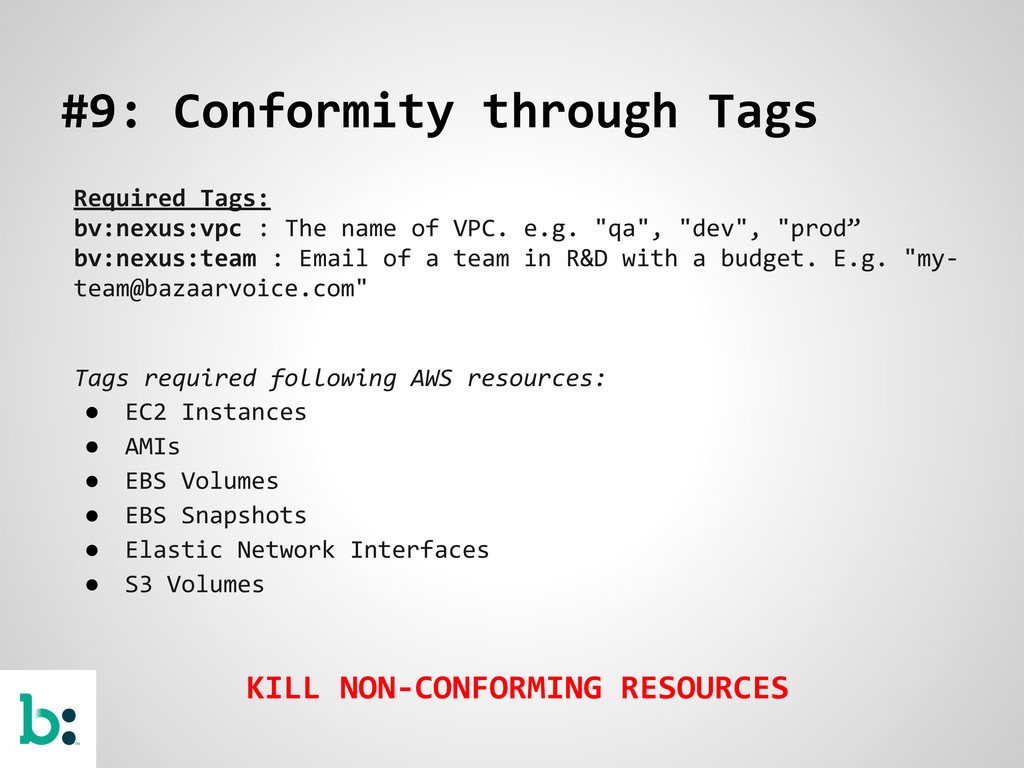
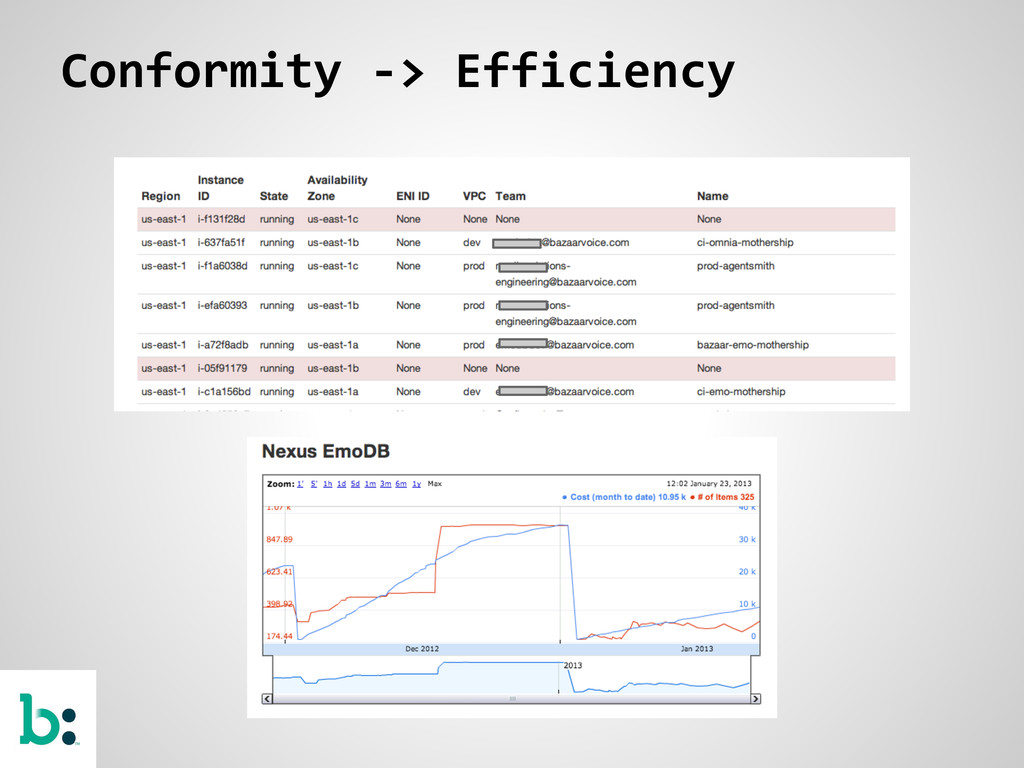
of VPC. e.g. "qa", "dev", "prod” bv:nexus:team : Email of a team in R&D with a budget. E.g. "my- [email protected]" Tags required following AWS resources: • EC2 Instances • AMIs • EBS Volumes • EBS Snapshots • Elastic Network Interfaces • S3 Volumes KILL NON-CONFORMING RESOURCES


 minodriven
 hollycummins
 kmars0605
 yukiny
 tosite
 timakin
 yub0n
 rkaga
 akit37
 shihochan
 marcoroth
 nao_randd
 dougneiner
 danielanewman
 akademiya2063
 rkendrick25
 watany
 kevinliebholz
 pauljervisheath
 reverentgeek
 deanohume
 mza
 retrage
 addyosmani