Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Memory Safety and the Future of Vulnerabilities
Search
Andrew Lilley Brinker
April 15, 2025
Programming
86
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Memory Safety and the Future of Vulnerabilities
Presented at the Cal Poly Pomona SWIFT Tech Symposium 2025.
Andrew Lilley Brinker
April 15, 2025
More Decks by Andrew Lilley Brinker
See All by Andrew Lilley Brinker
Hello and Welcome: Documentation in the Rust Ecosystem
alilleybrinker
0
50
A Tale of Teaching Rust
alilleybrinker
0
69
Efficient Nimber Calculation in Dots and Boxes
alilleybrinker
0
140
Other Decks in Programming
See All in Programming
月間100万人のサービス刷新で、 技術選定をHonoに振り切った話
yutobara
8
6.6k
TechTown - Creating Composable Callables in Contemporary C++
rollbear
0
130
Kotlinの15年とServer-Side Kotlin
n_takehata
1
150
APNsからLive Activityを開始する話
yumnumm
0
170
Apple Intelligence を用いた個人情報誤送信防止、及びユーザーリクエスト体験の改善について
yukiny
0
350
見えないものを探る要求要件定義に必要な基本的思考 / invisible-requirement-thinking
minodriven
15
8.5k
Verilogで学ぶCPU自作入門
uyuki234
8
4.1k
ActionController meets Protocol Buffers
sorah
0
520
Optunaを作ったときにやりたかったこと、その後 (2026/10/16, Optuna Meetup #3)
iwiwi
1
430
個人開発者よ、Honoを使え(おじさんver)
tanahiro2010
2
260
3回つくってわかった、 定期実行ジョブ基盤の本質情報
takai
0
450
カツオ、ご期待ください
suneo3476
0
190
Featured
See All Featured
Typedesign – Prime Four
hannesfritz
42
3.2k
Redefining SEO in the New Era of Traffic Generation
szymonslowik
1
480
Designing for Performance
lara
612
70k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Ethics towards AI in product and experience design
skipperchong
2
430
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
67k
Jamie Indigo - Trashchat’s Guide to Black Boxes: Technical SEO Tactics for LLMs
techseoconnect
PRO
0
710
Amusing Abliteration
ianozsvald
1
350
GraphQLとの向き合い方2022年版
quramy
50
15k
Are puppies a ranking factor?
jonoalderson
2
4.1k
Building the Perfect Custom Keyboard
takai
2
910
Future Trends and Review - Lecture 12 - Web Technologies (1019888BNR)
signer
PRO
0
3.8k
Transcript
Memory safety and the future of vulnerabilities A talk by
Andrew Lilley Brinker Approved for Public Release; Distribution Unlimited. Public Release Case Number 251031. The author’s affiliation with The MITRE Corporation is provided for identification purposes only, and is not intended to convey or imply MITRE’s concurrence with, or support for, the positions, opinions, or viewpoints expressed by the author. ©2025 The MITRE Corporation. ALL RIGHTS RESERVED.
I’m Andrew Principal Cyber Security Engineer MITRE Rustacean for
11 years I am not speaking for MITRE today.
What is memory safety?
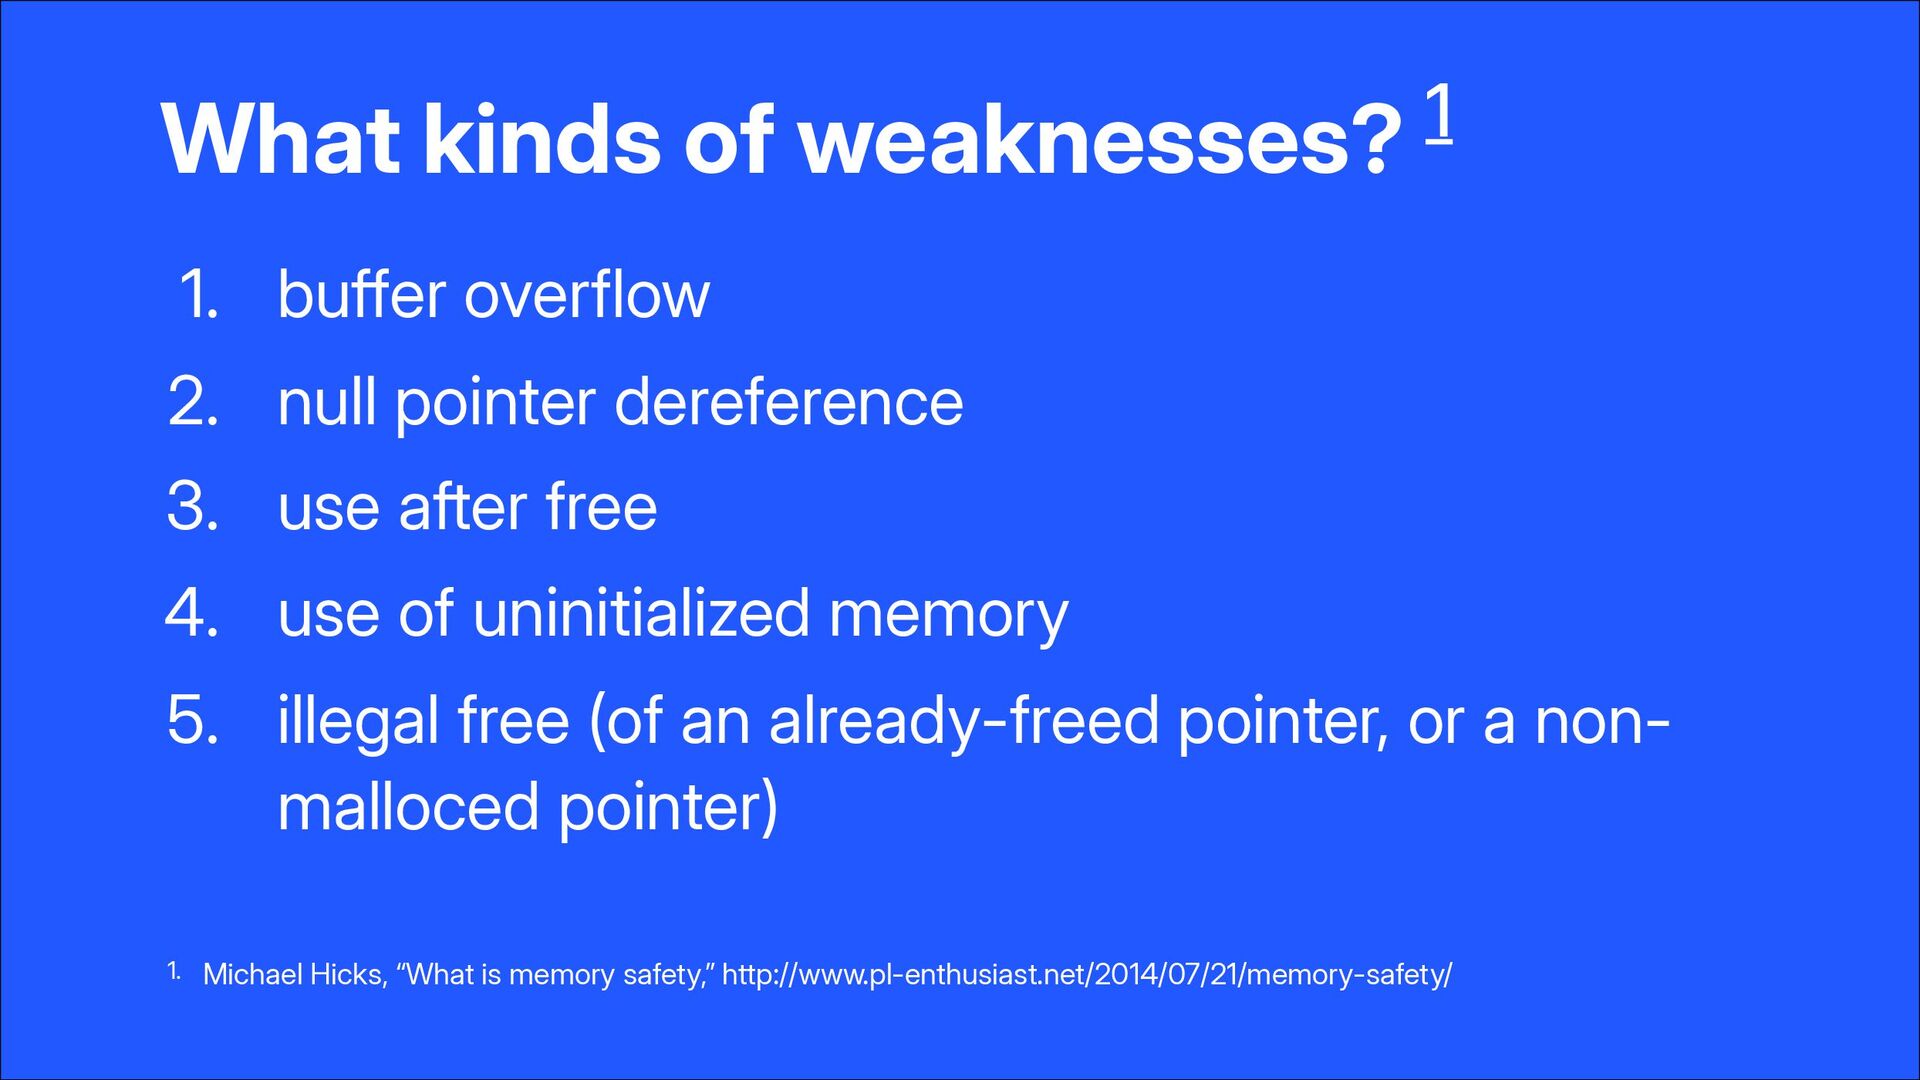
What kinds of weaknesses? 1 buffer overflow 1. null pointer
dereference 2. use after free 3. use of uninitialized memory 4. illegal free (of an already-freed pointer, or a non- malloced pointer) 5. Michael Hicks, “What is memory safety,” http://www.pl-enthusiast.net/2014/07/21/memory-safety/ 1.
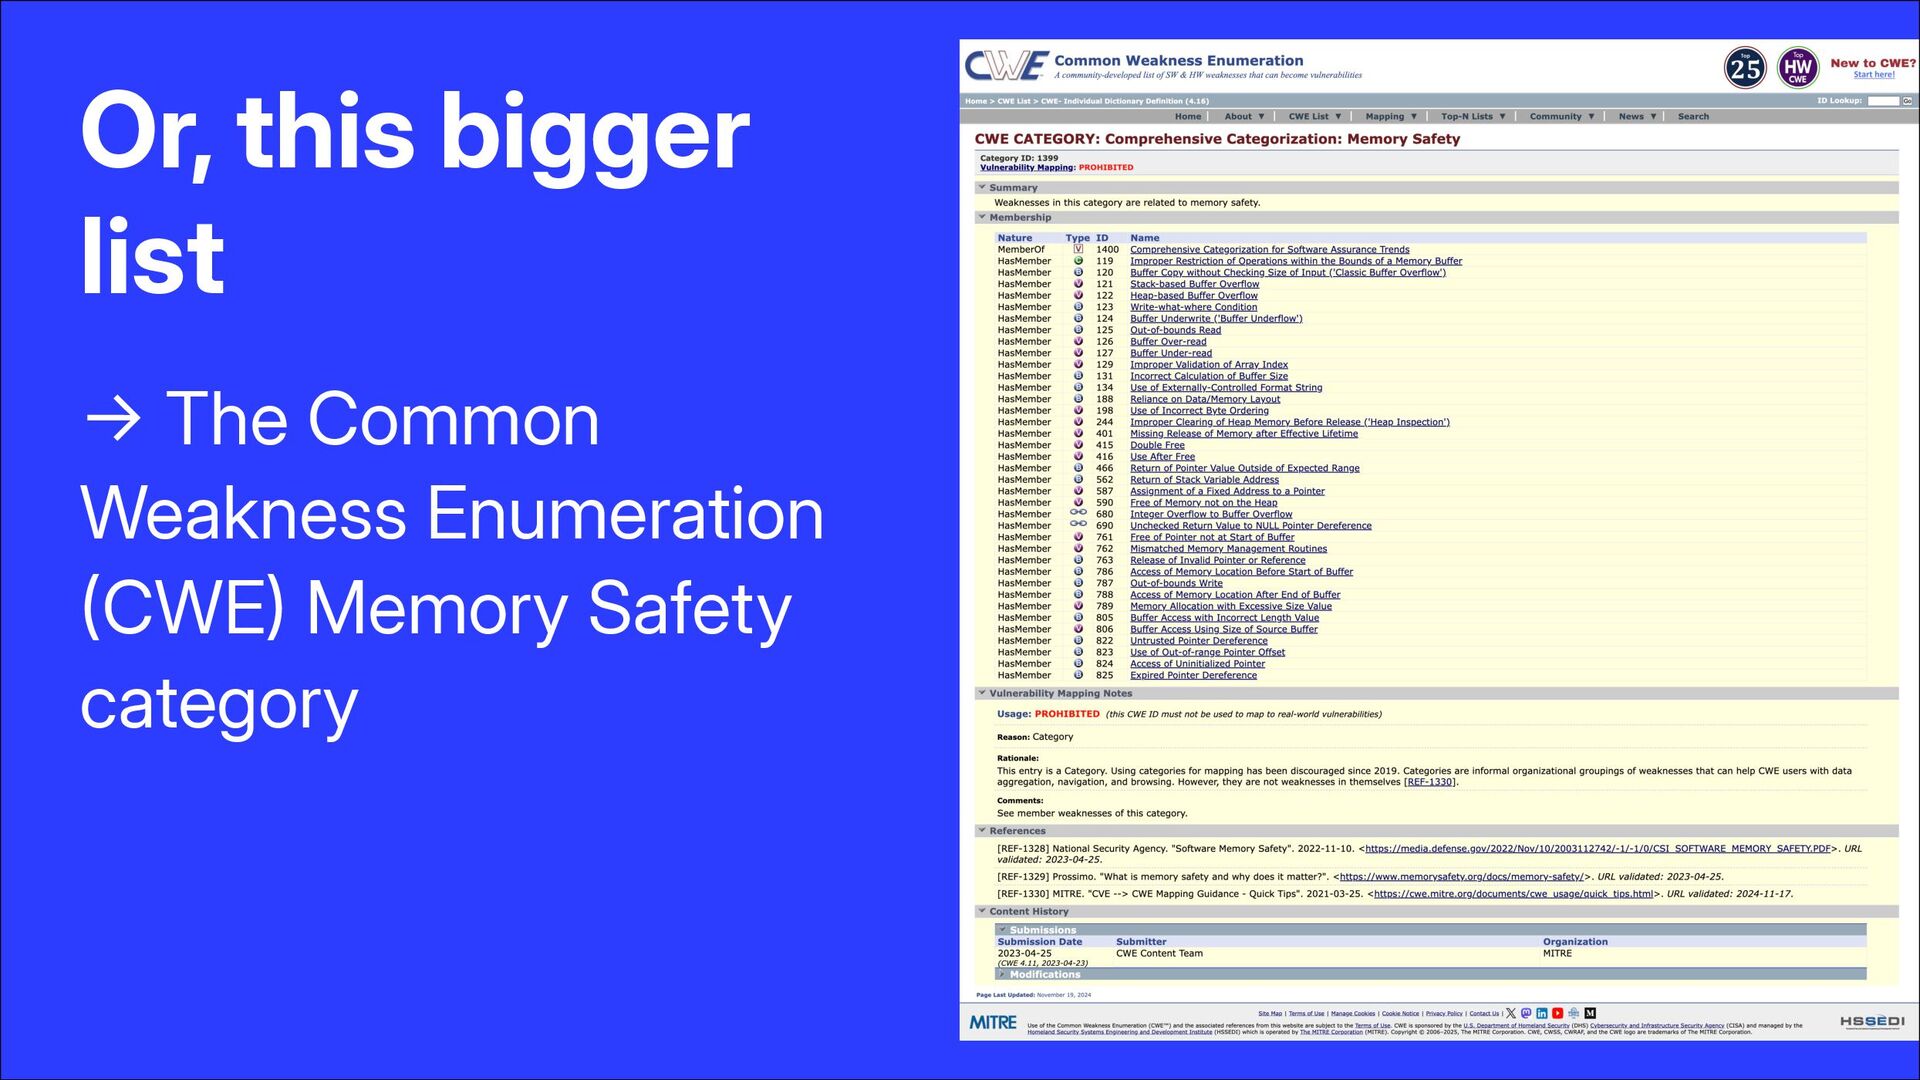
Or, this bigger list The Common Weakness Enumeration CWE
Memory Safety category
Spatial Memory Safety Out-of-bounds accesses Reads or writes, under or
over 1 Yoshua Wuyts, “What are temporal and spatial memory safety?” https://blog.yoshuawuyts.com/temporal-spatial-memory- safety/ 1.
Heartbleed was a spatial memory safety vulnerability
Why is that bad? Client: heartbeat “Hello” length 1,000 bytes
Server: heartbeat “HellobfsfhgafSocial Security Number 123456789…”
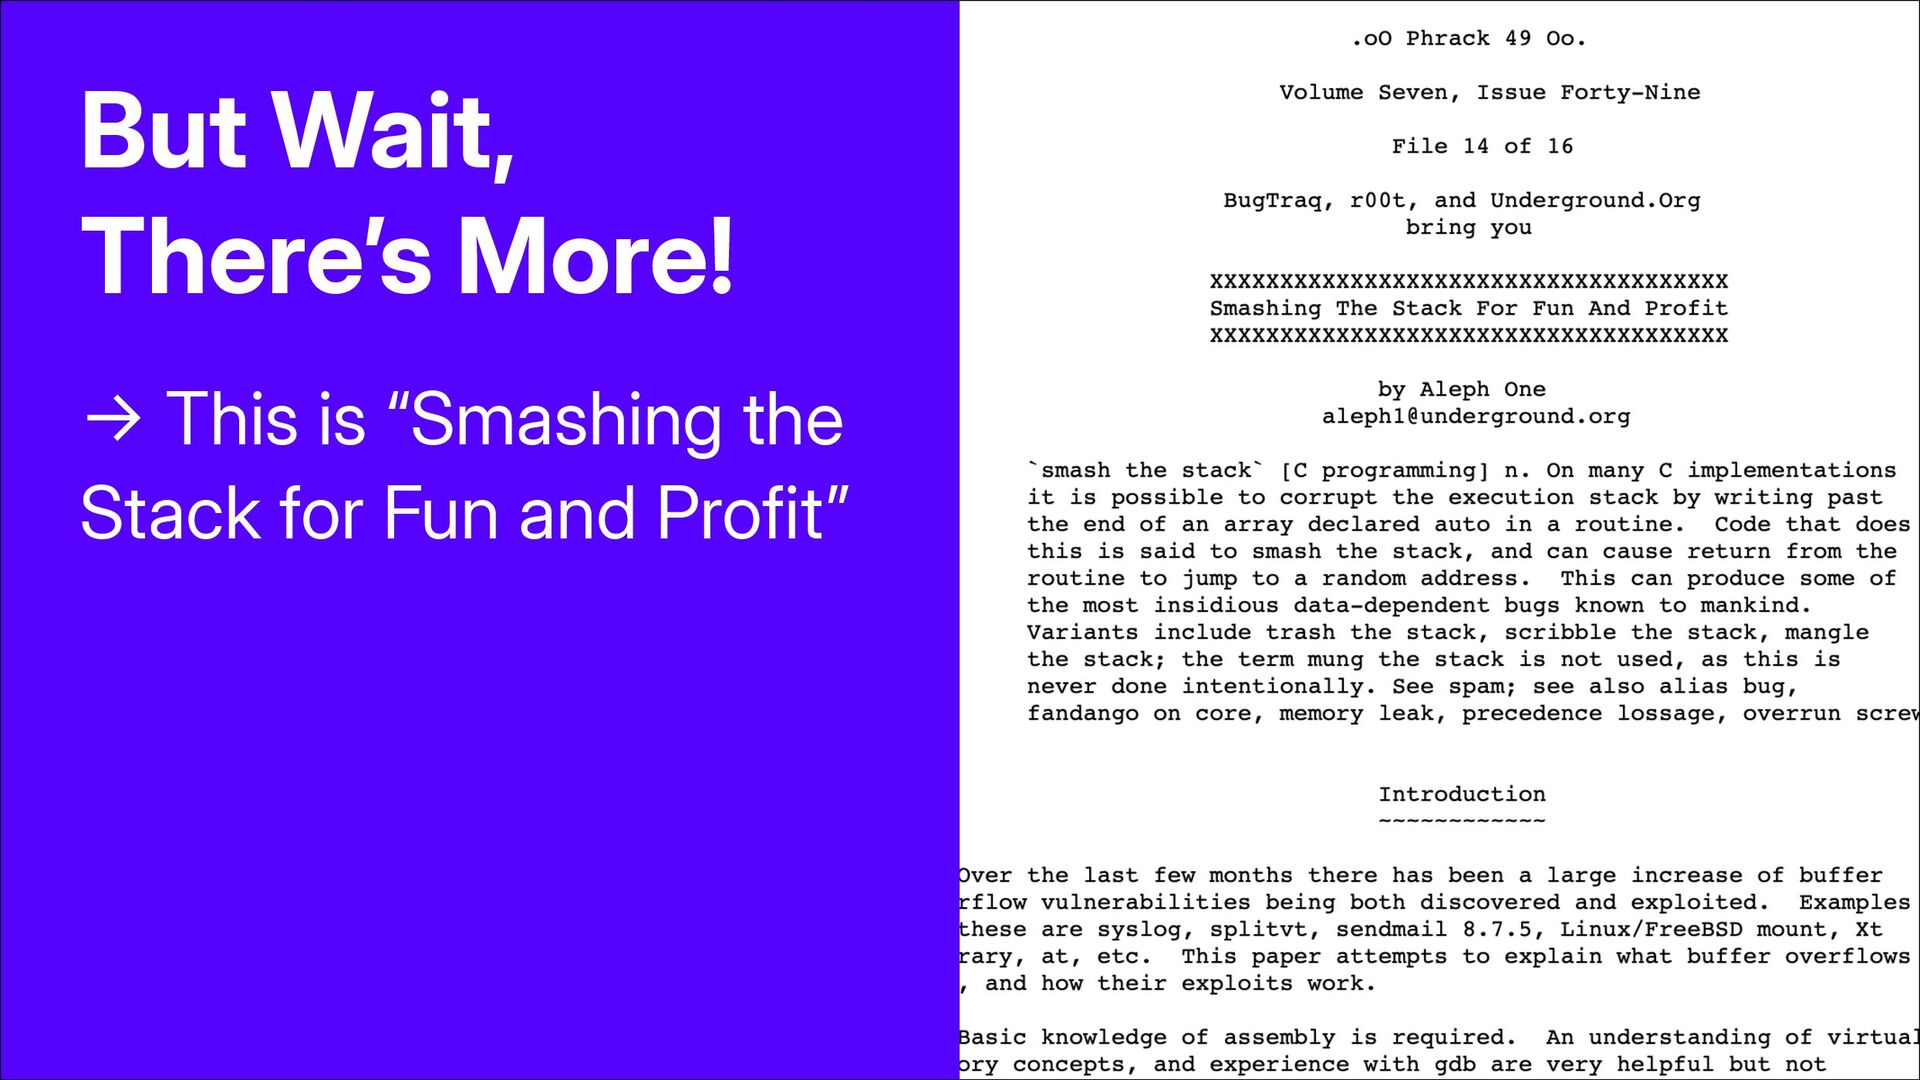
But Wait, There’s More! This is “Smashing the Stack
for Fun and Profit”
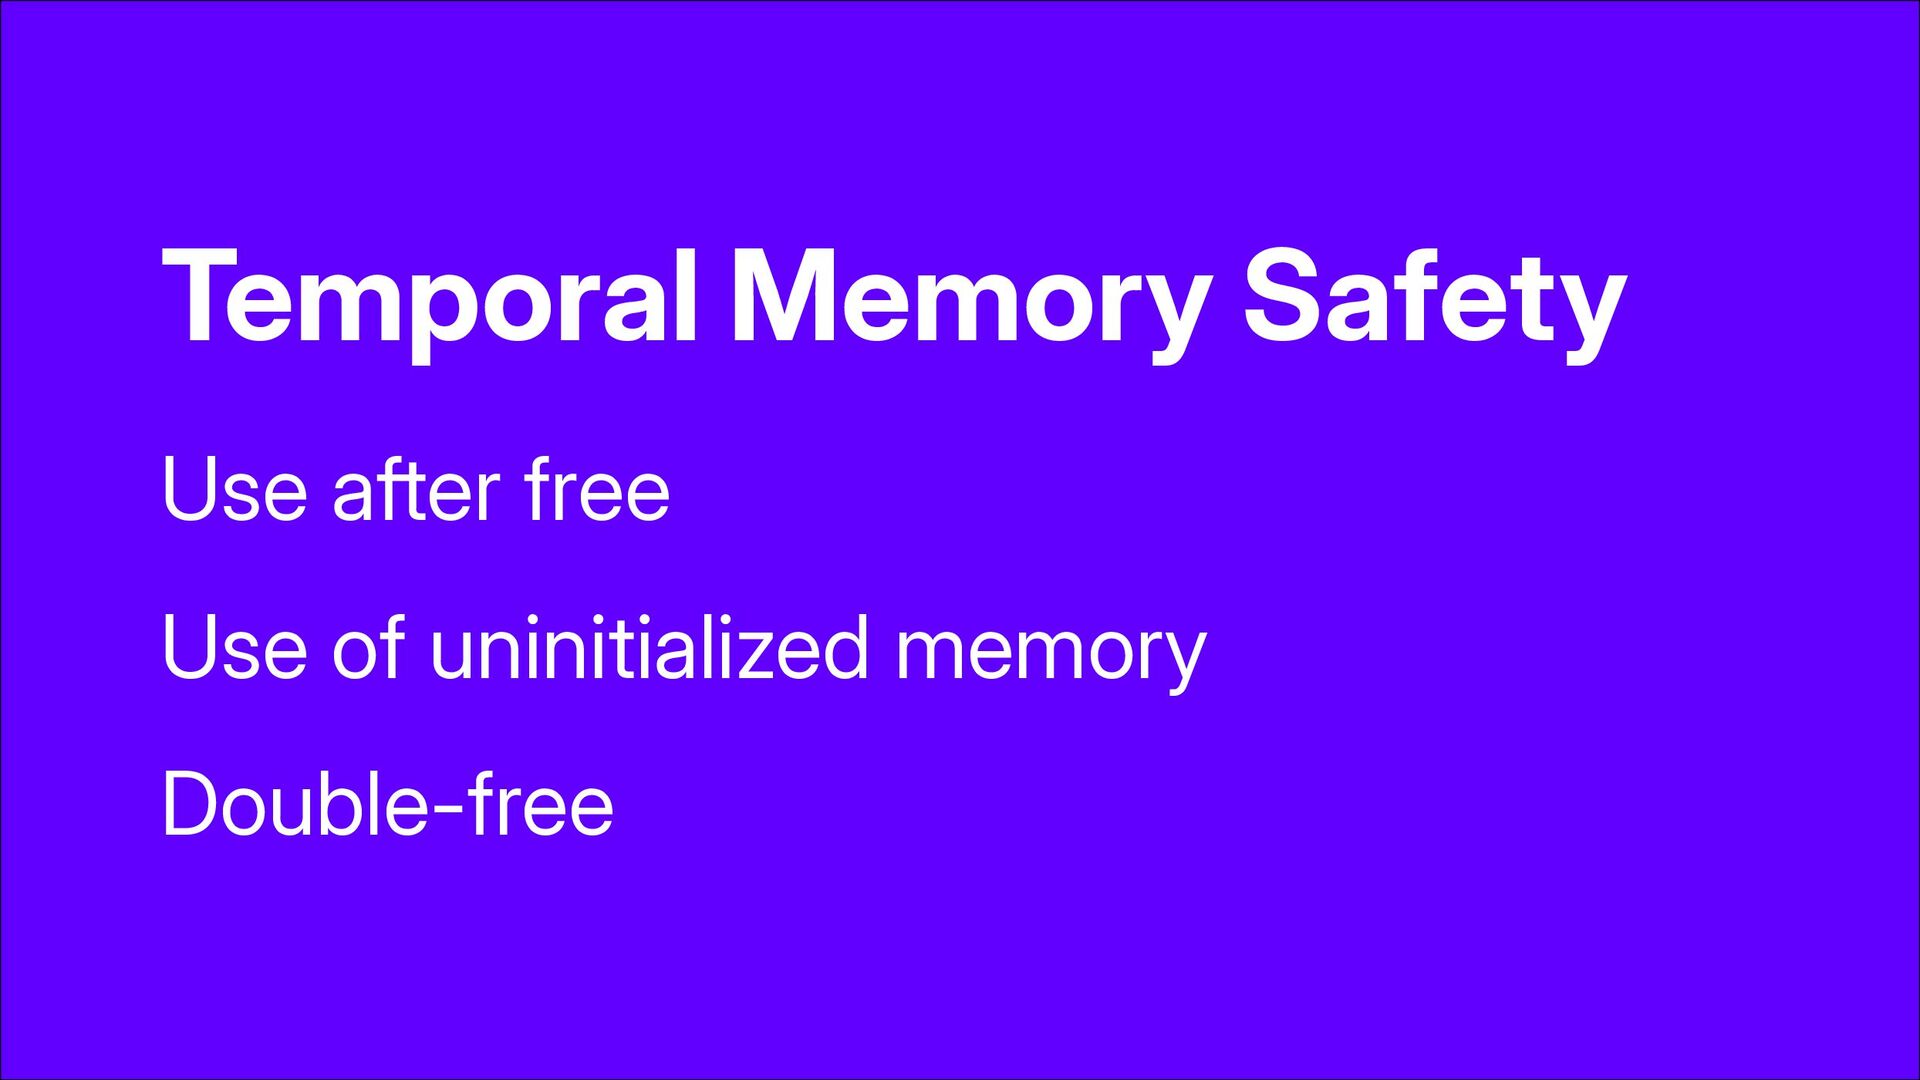
Temporal Memory Safety Use after free Use of uninitialized memory
Double-free
Memory safety is when these problems don’t happen Memory safe
languages stop memory safety problems
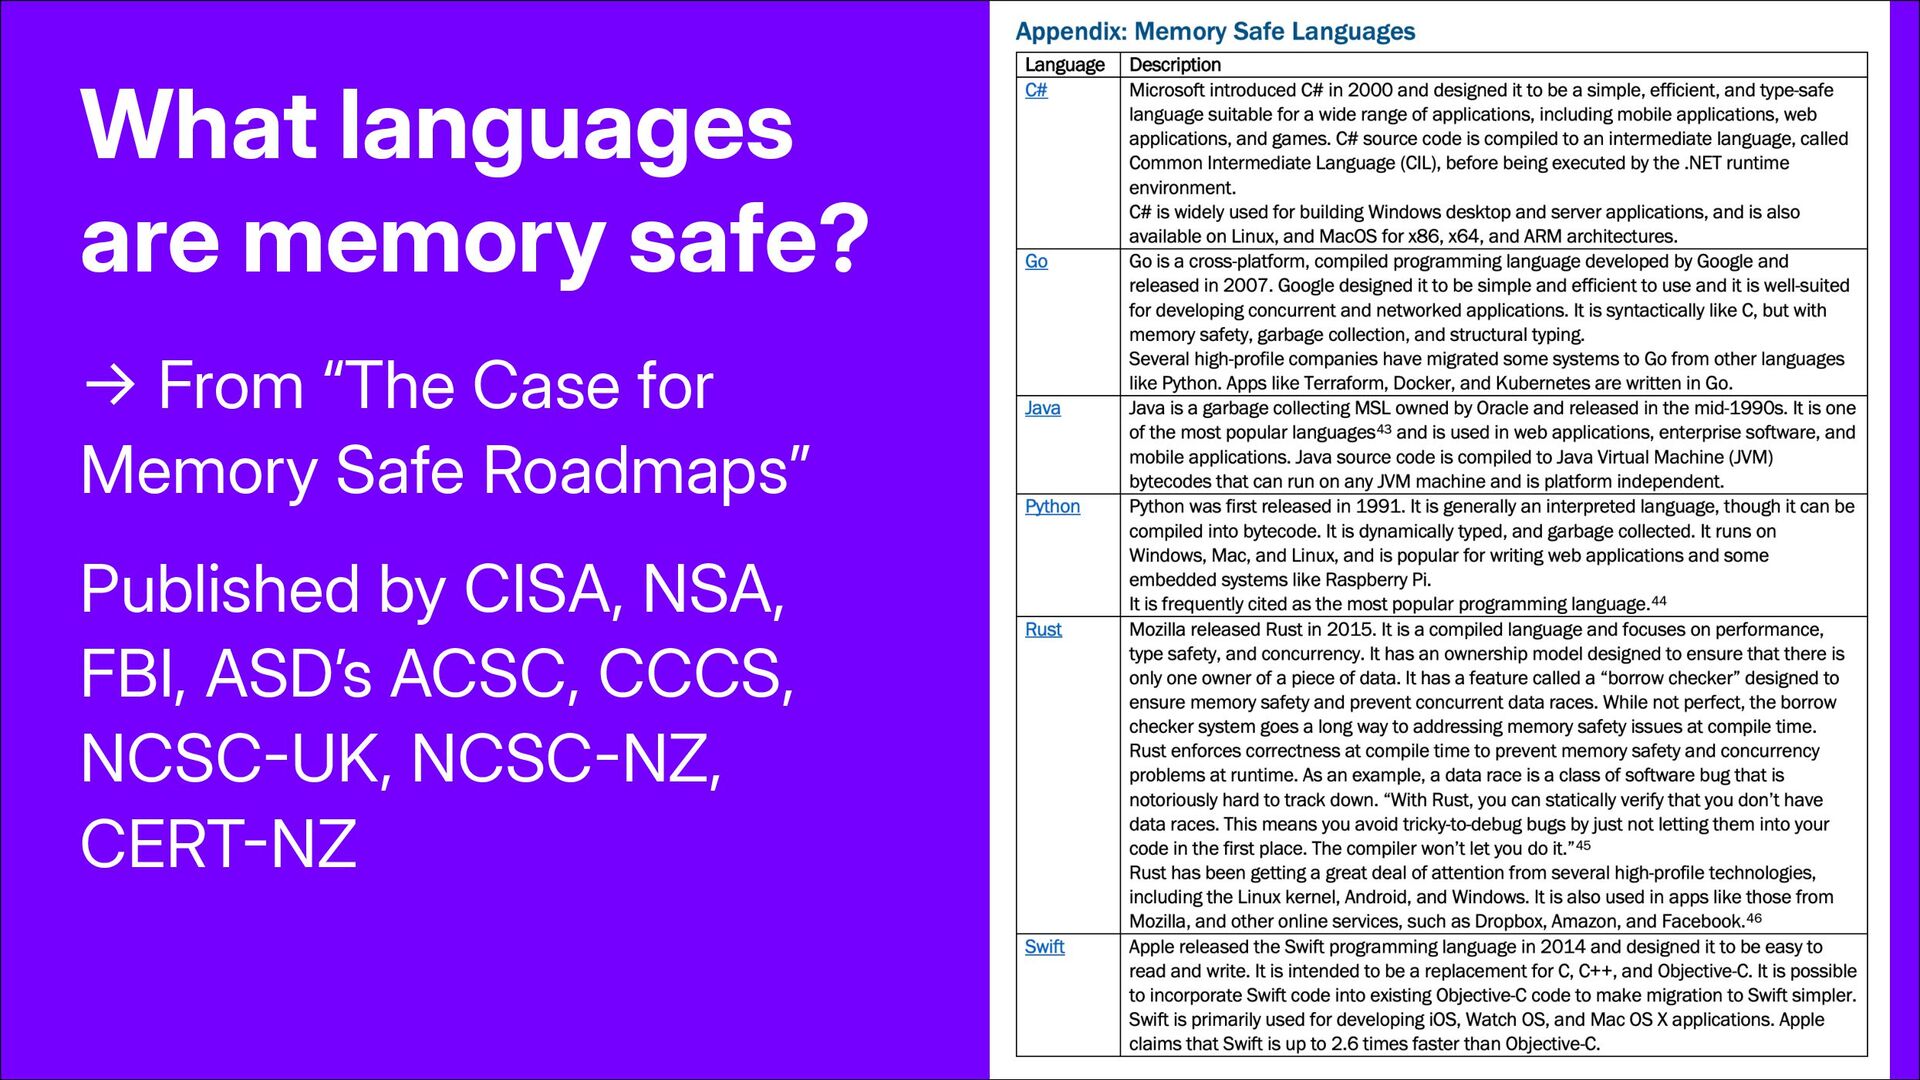
What languages are memory safe? From “The Case for
Memory Safe Roadmaps” Published by CISA, NSA, FBI, ASD’s ACSC, CCCS, NCSCUK, NCSCNZ, CERTNZ
Which ones aren’t? C and C
None
Rust 1.0 was May 15, 2015 Also the day of
my first date with my wife)
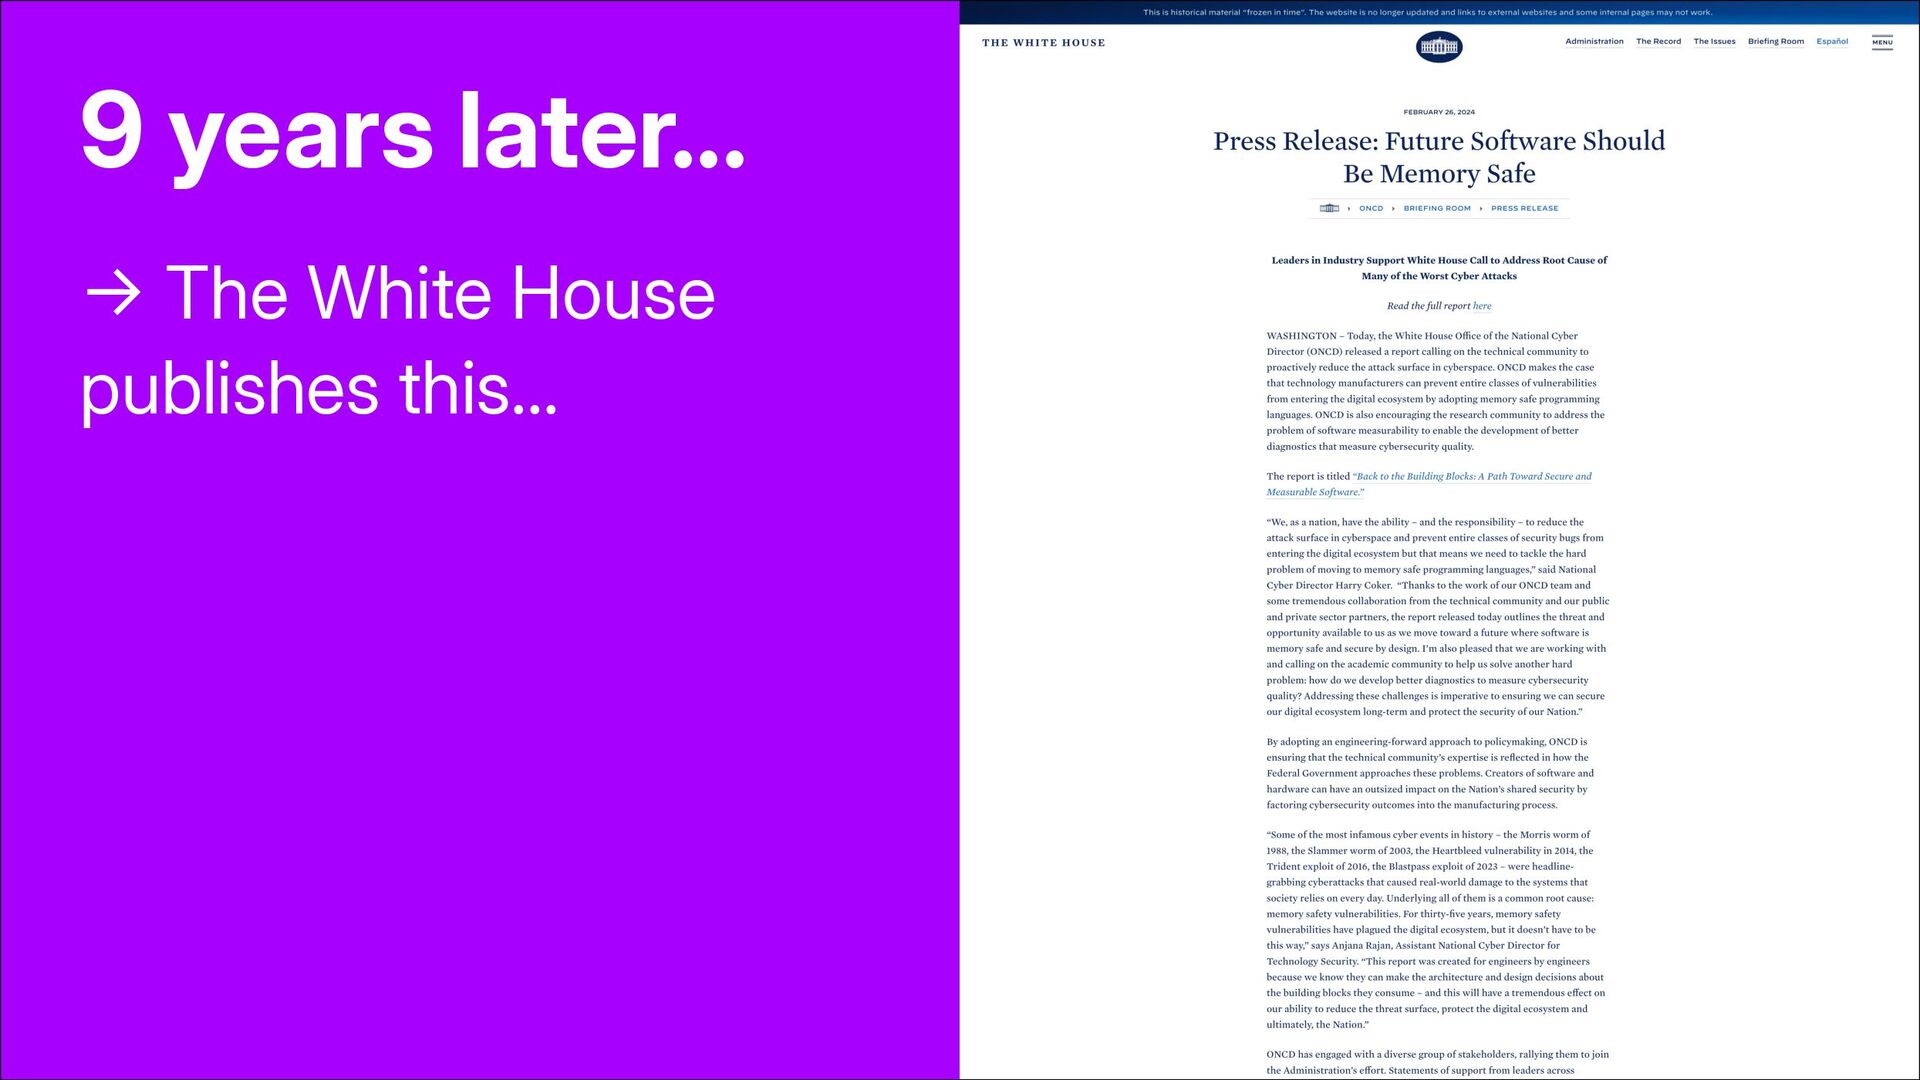
9 years later… The White House publishes this…
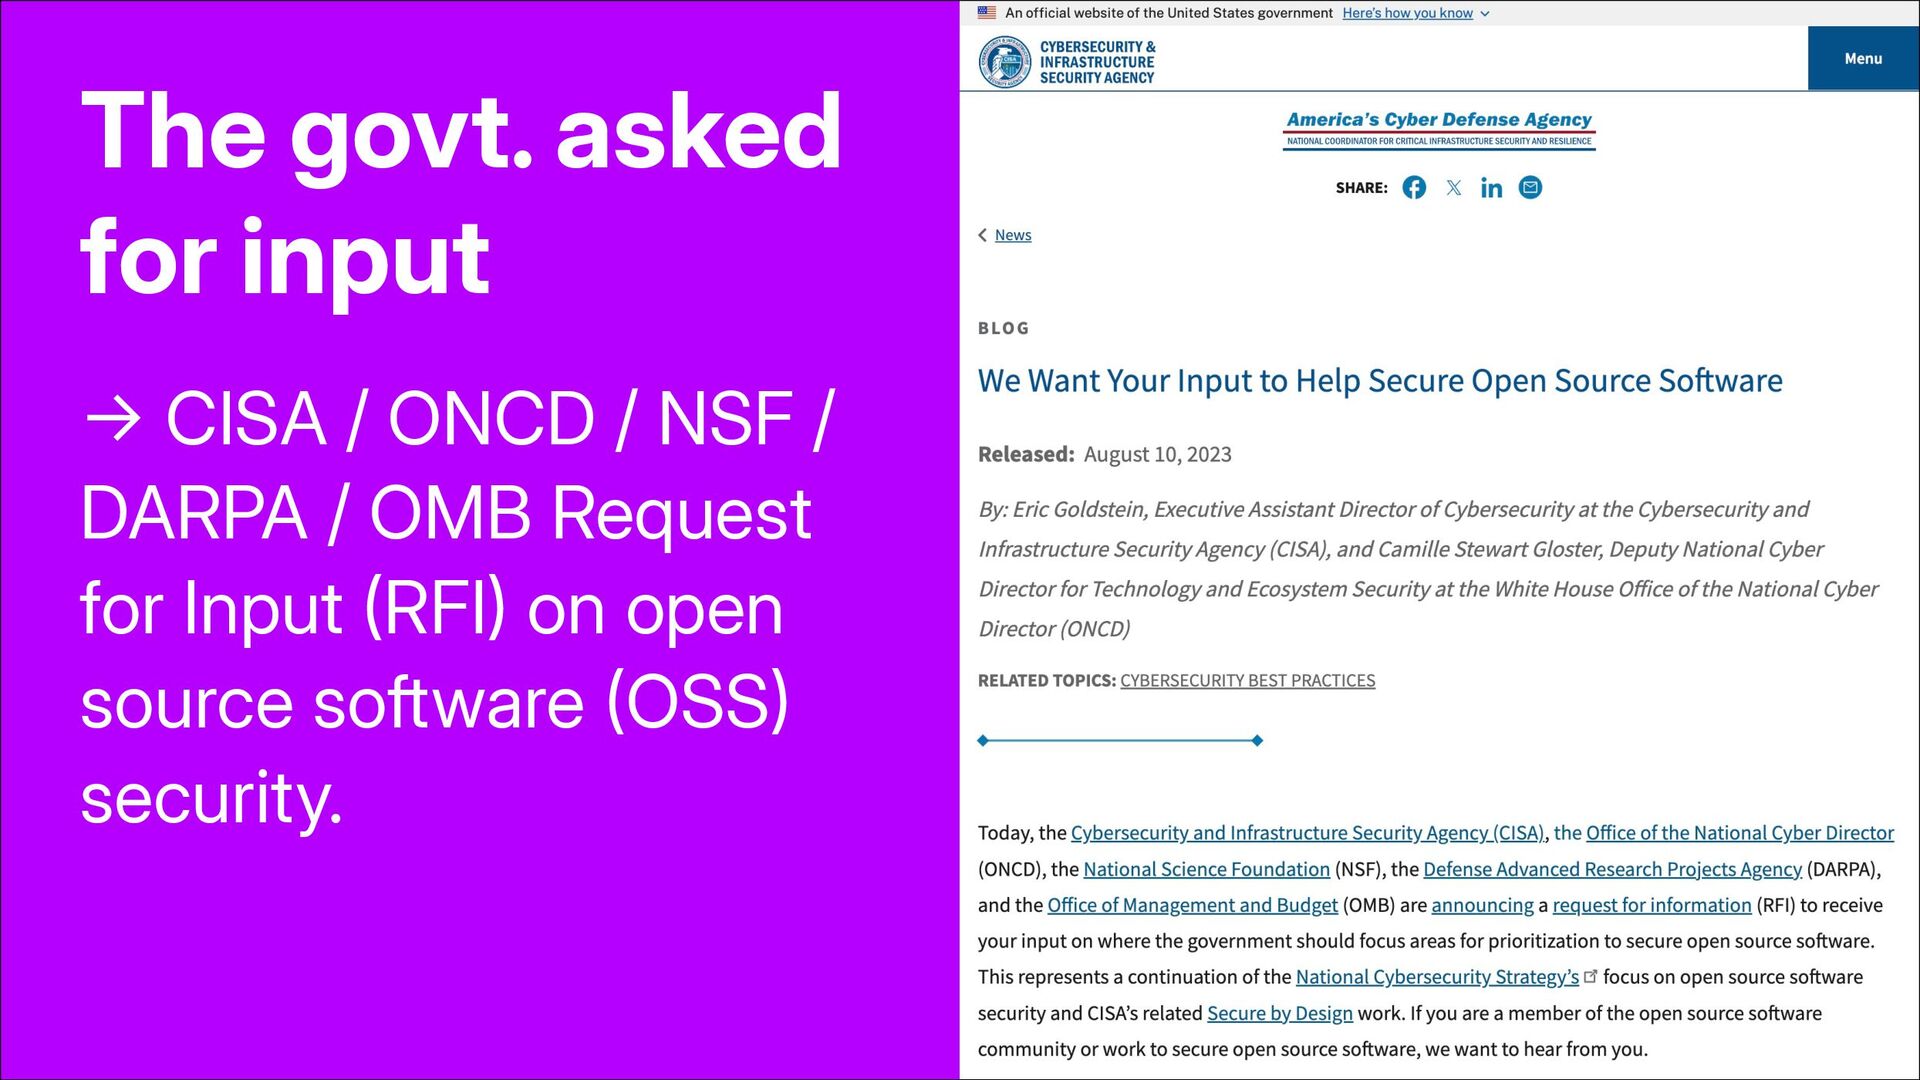
The govt. asked for input CISA / ONCD /
NSF / DARPA / OMB Request for Input RFI on open source software OSS security.
In the responses… Microsoft, Google, Cloudflare, GitHub, IBM, and many
others recommend moving to memory safe languages.
The move to memory safe languages is happening What does
this mean for vulnerabilities?
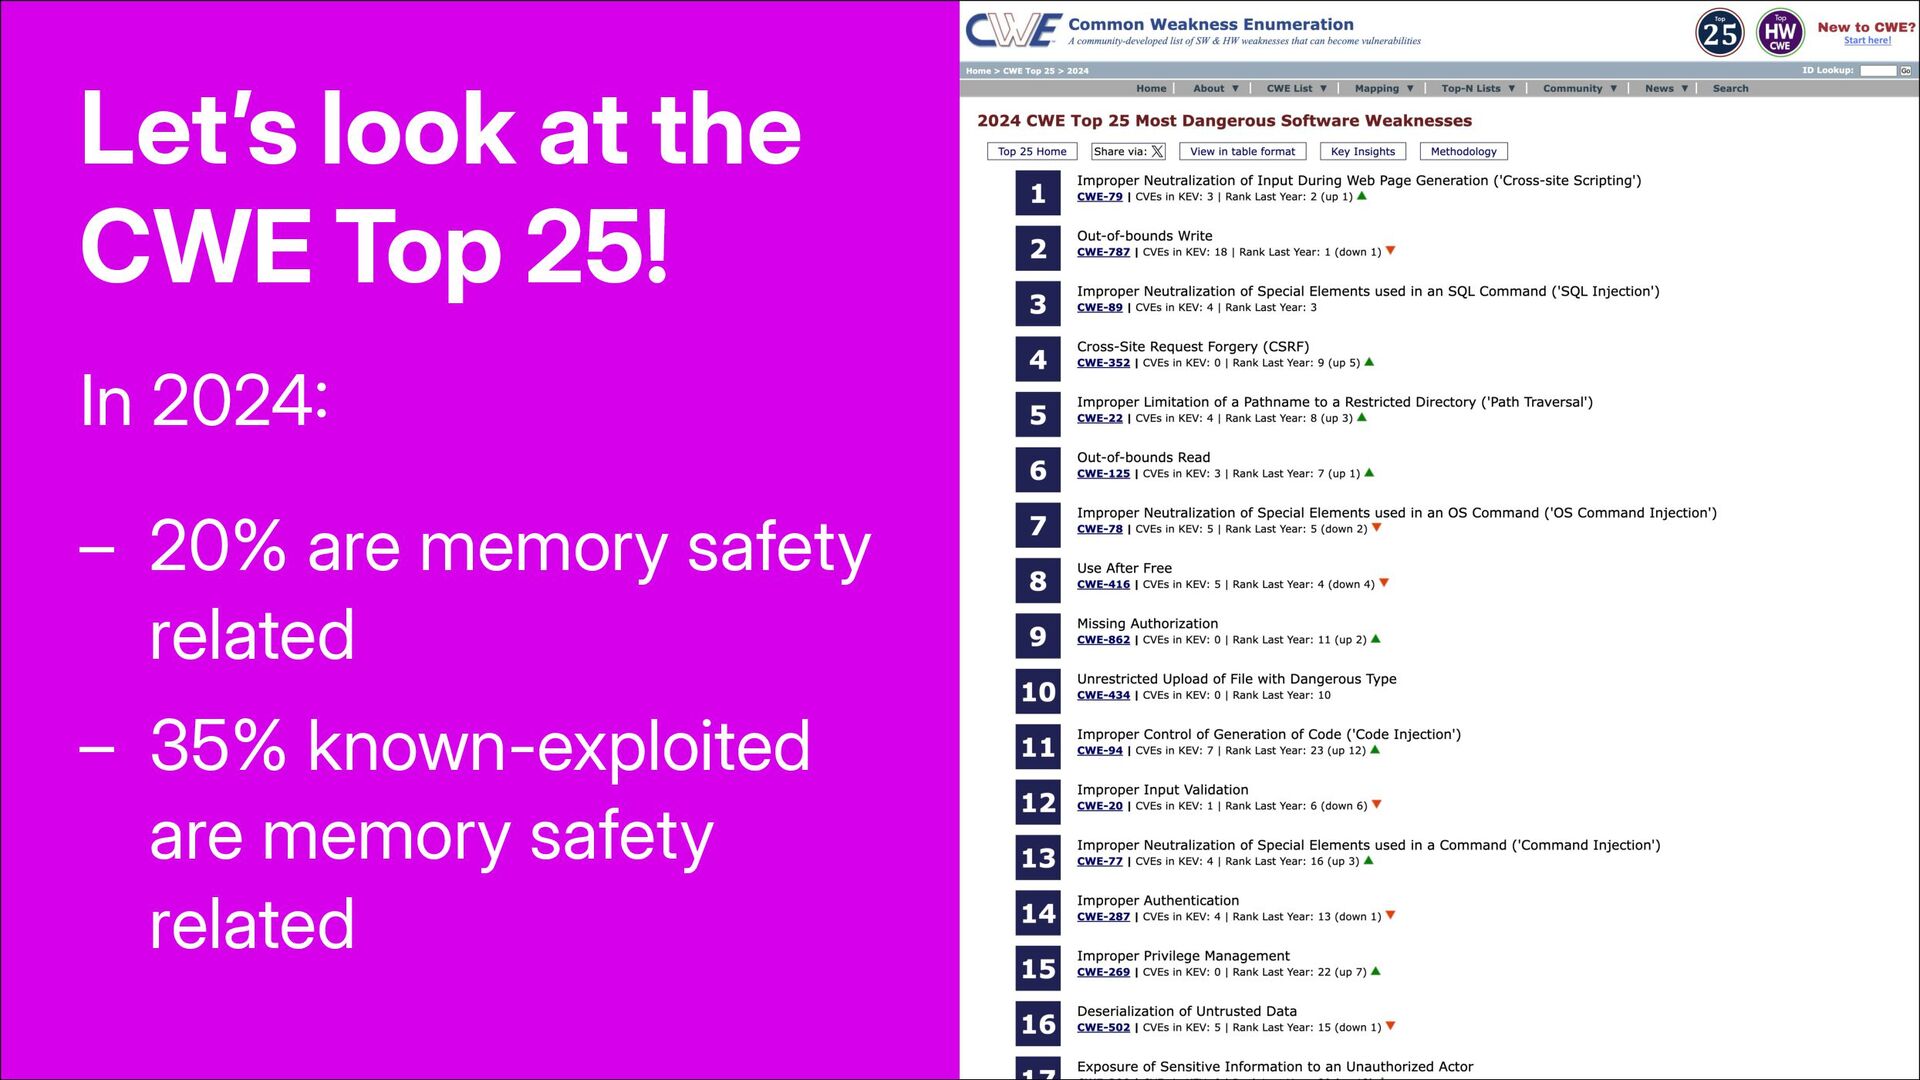
Let’s look at the CWE Top 25! In 2024 20%
are memory safety related – 35% known-exploited are memory safety related –
We’ll always have… Bad authentication / authorization – Bad neutralization
of user input – Resource exhaustion But what else? –
Micro- architectural vulnerabilities
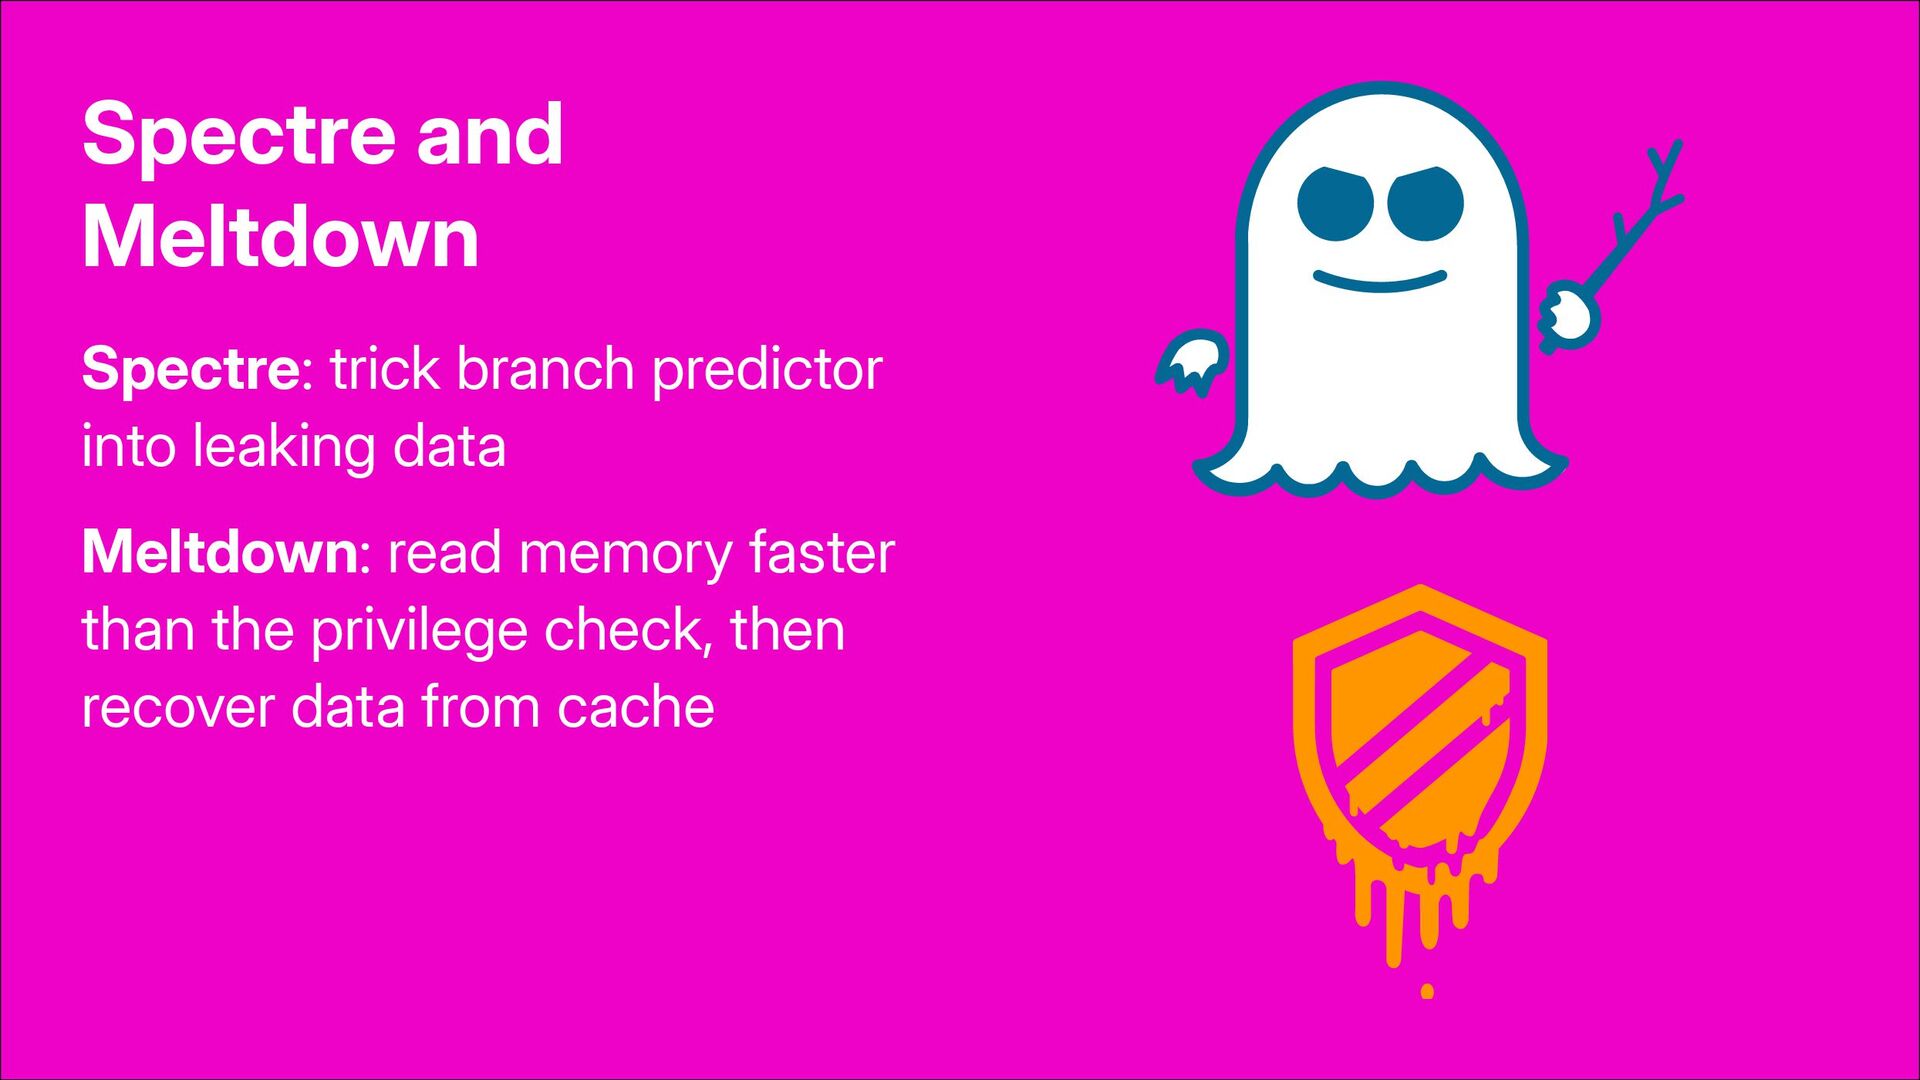
Spectre and Meltdown Spectre: trick branch predictor into leaking data
Meltdown: read memory faster than the privilege check, then recover data from cache
These affected every Intel processor from 1995 to 2018
The hits start coming and they don’t stop coming Spectre,
Meltdown, Spectre-NG, SpectreRSB, Foreshadow, Zombieload, CROSStalk, Phantom, Zenbleed, Inception, Downfall
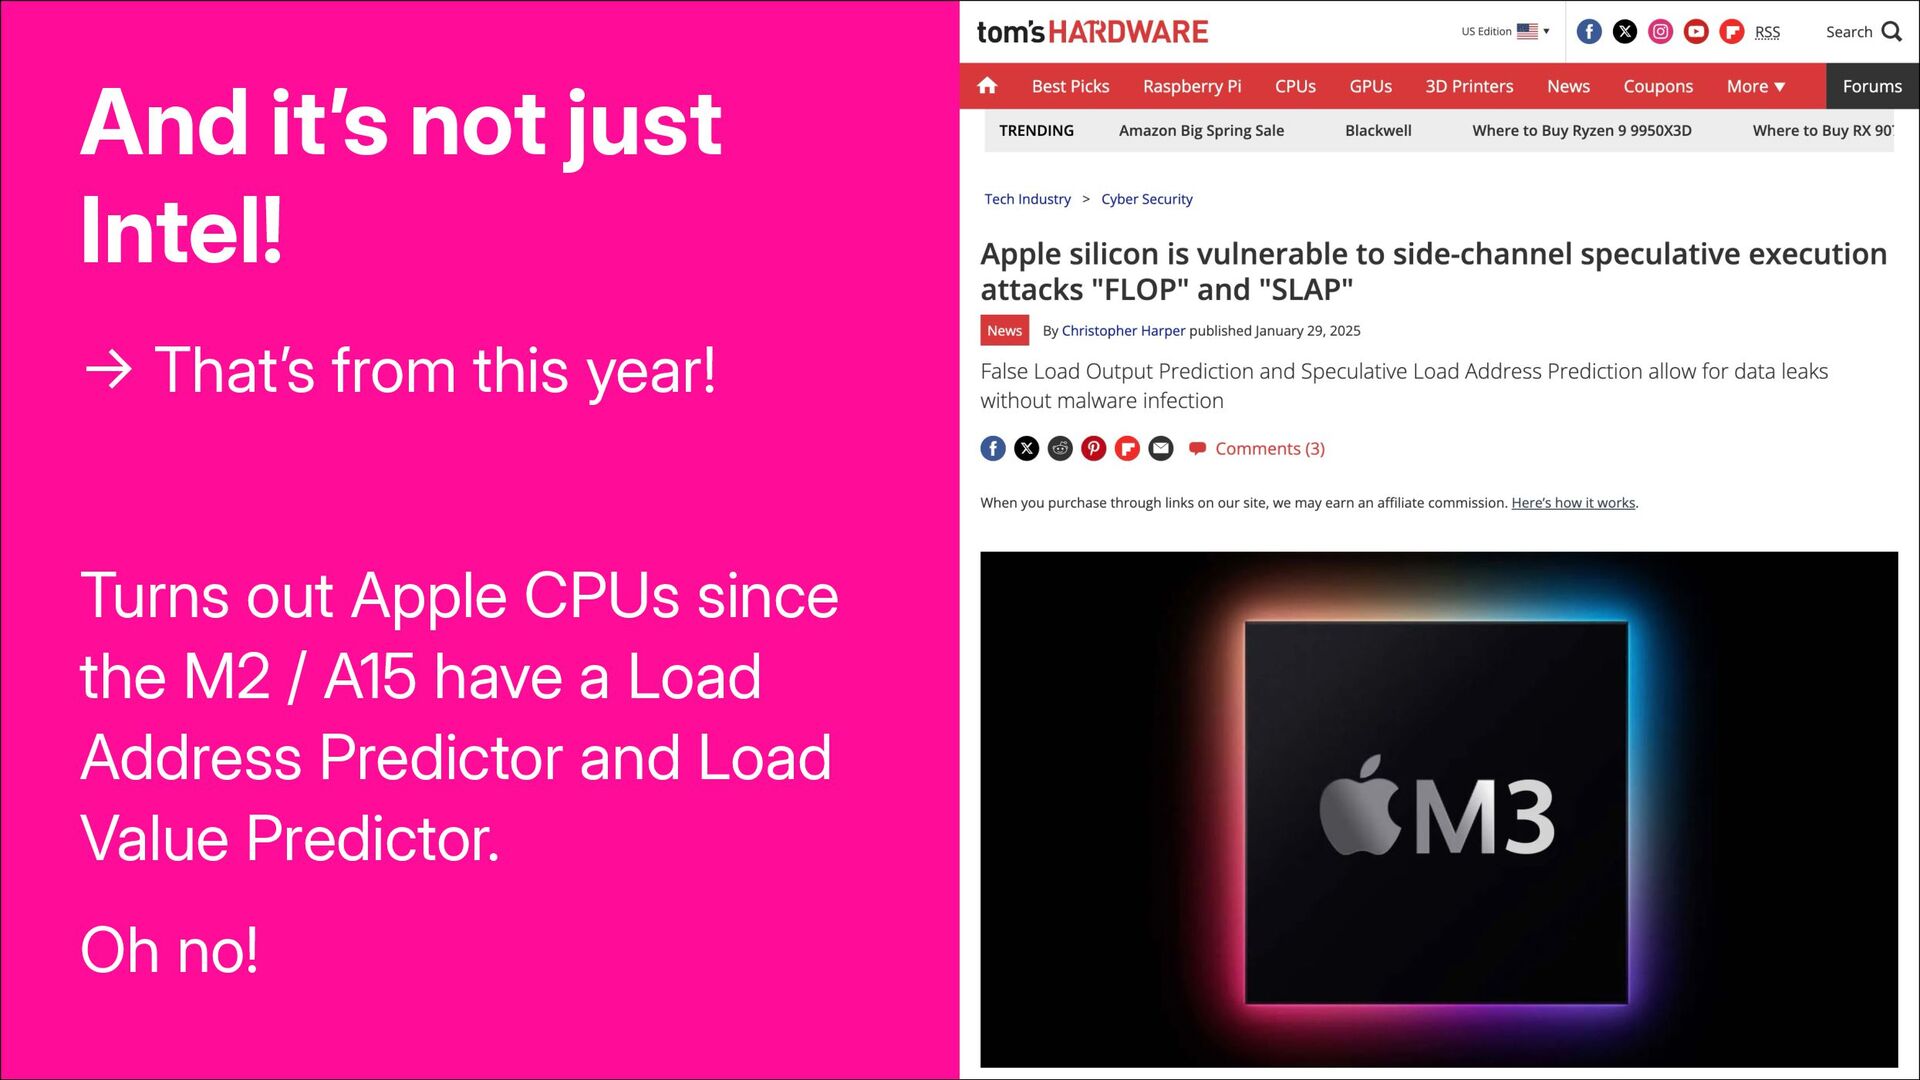
And it’s not just Intel! That’s from this year!
Turns out Apple CPUs since the M2 / A15 have a Load Address Predictor and Load Value Predictor. Oh no!
Problem: how to have fast processors that aren’t full of
speculative execution vulnerabilities
Cryptographic vulnerabilities
Cryptography libraries are better than they used to be
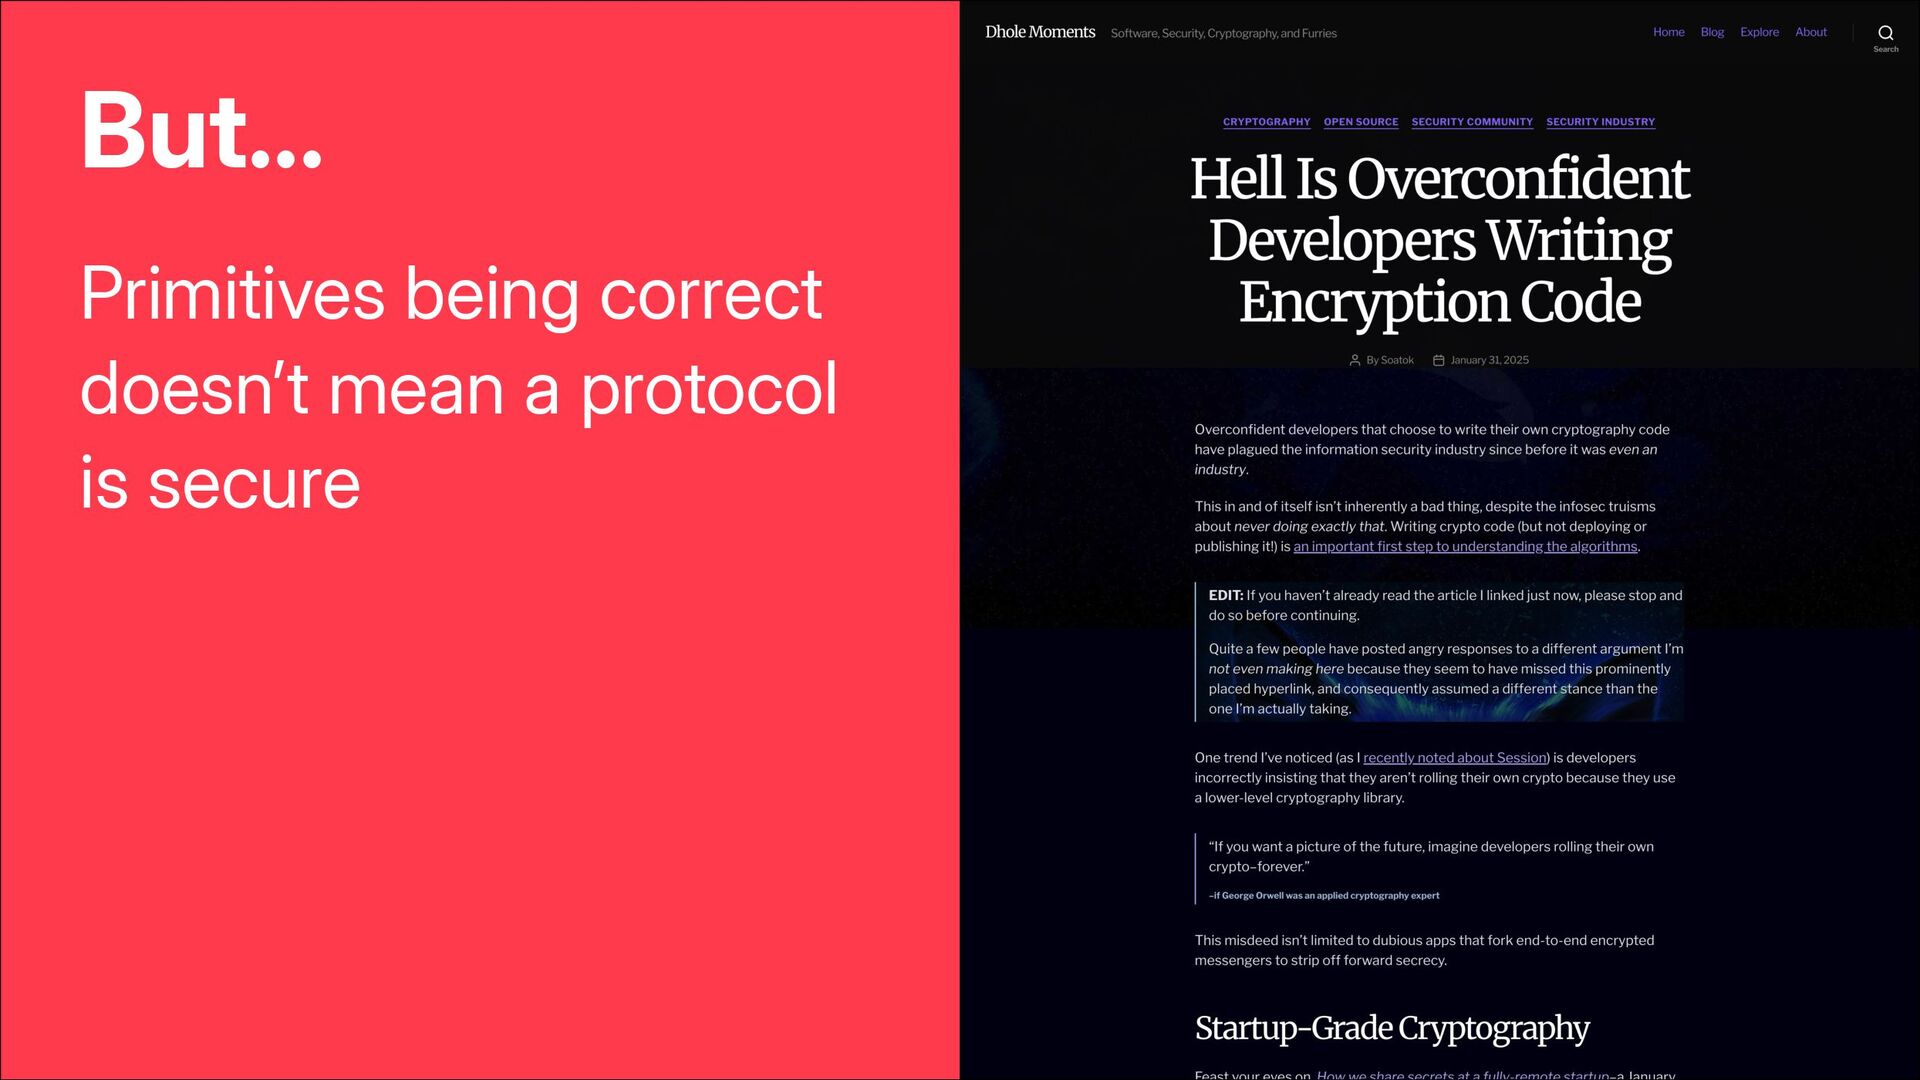
But… Primitives being correct doesn’t mean a protocol is secure
We need post-quantum cryptography Harvest now, decrypt later
Problem: many existing protocols can’t easily adapt to post-quantum cryptography
Supply Chain Vulnerabilities
Code reuse is good!
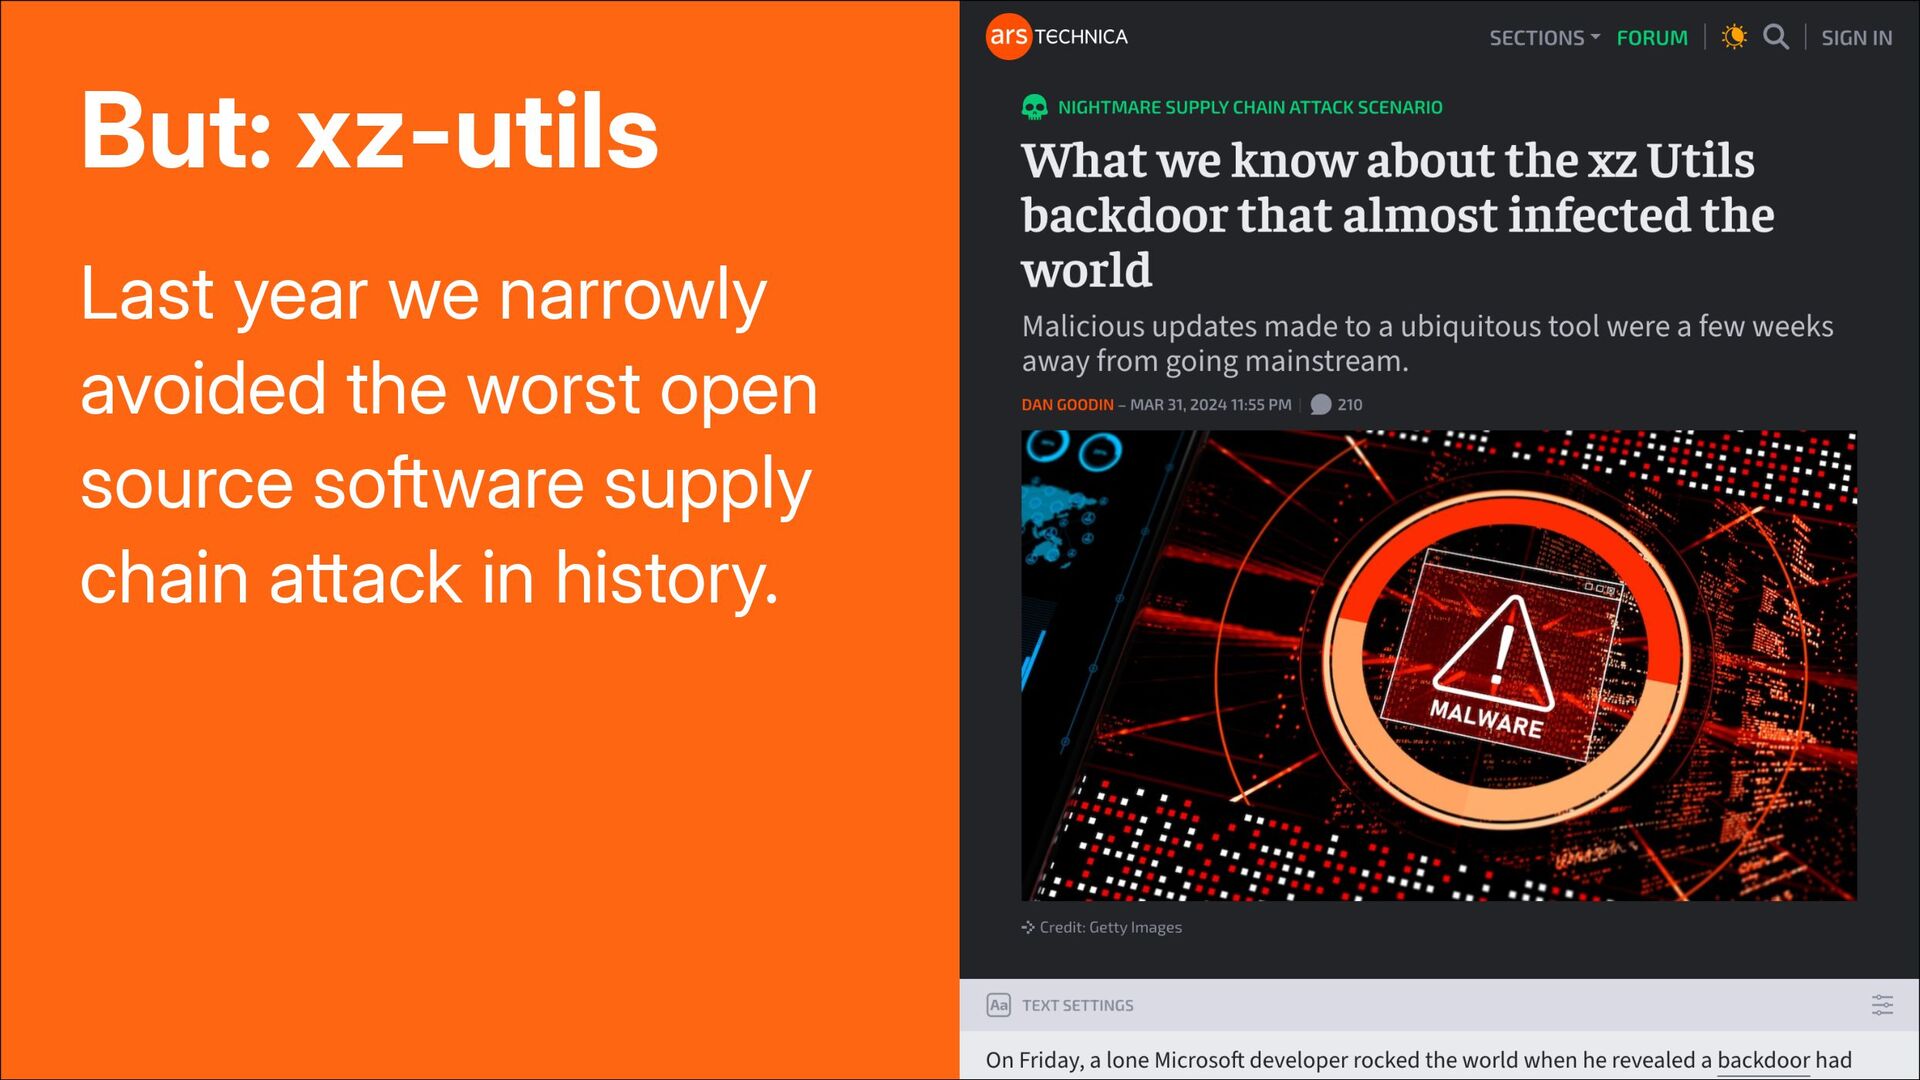
But: xz-utils Last year we narrowly avoided the worst open
source software supply chain attack in history.
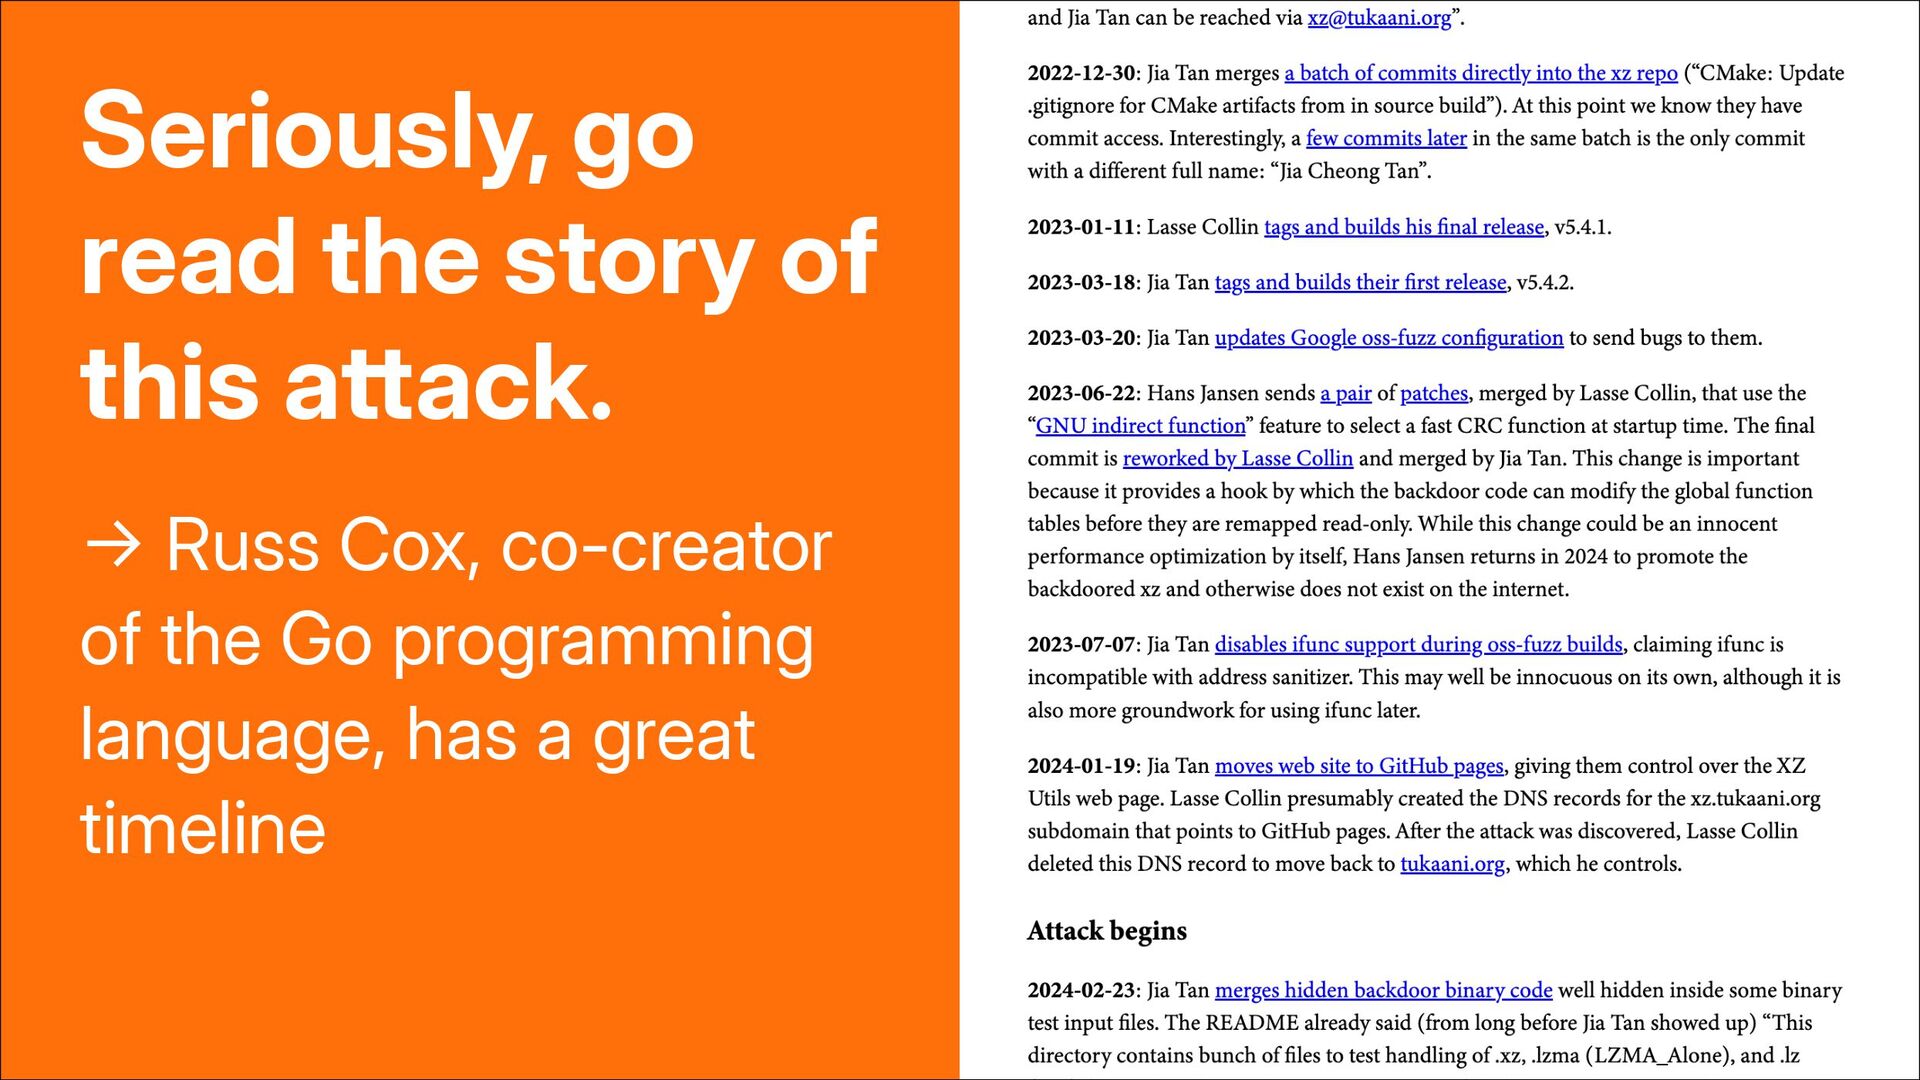
Seriously, go read the story of this attack. Russ
Cox, co-creator of the Go programming language, has a great timeline
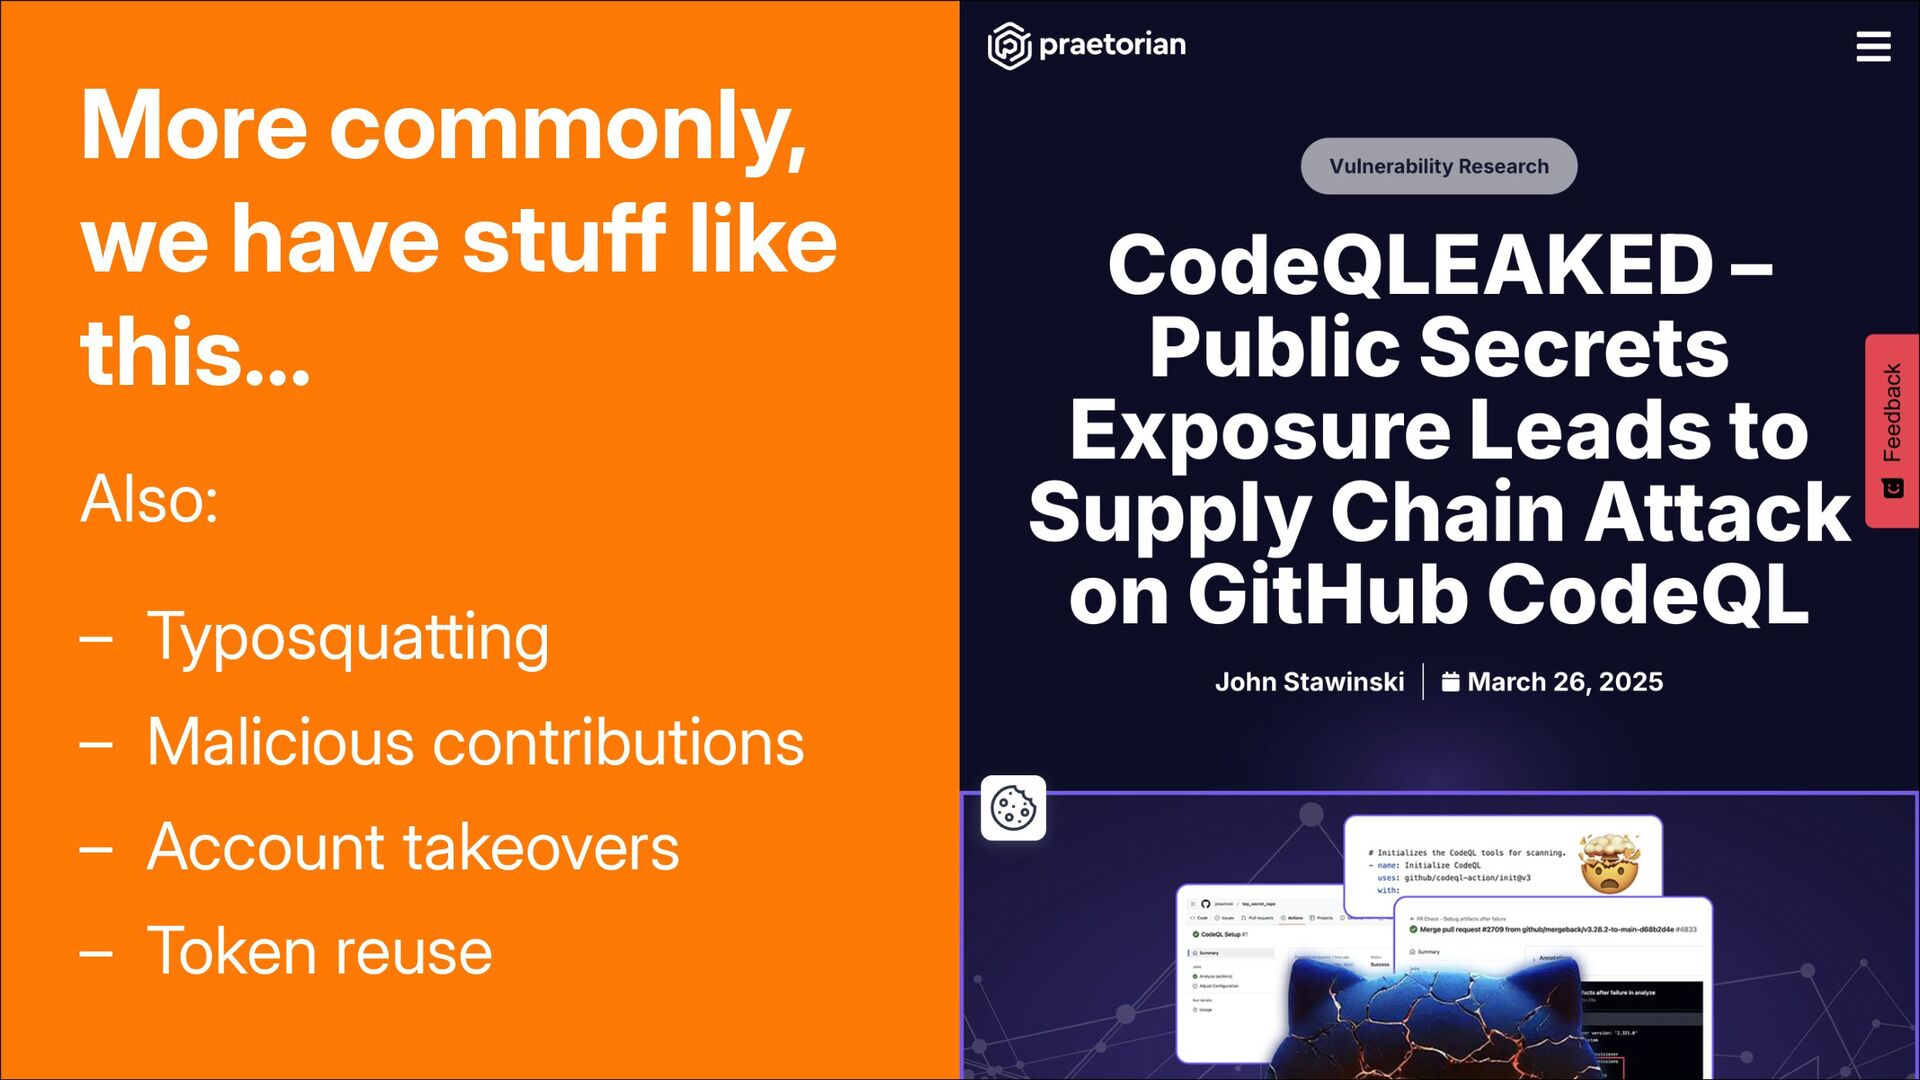
More commonly, we have stuff like this… Also: Typosquatting –
Malicious contributions – Account takeovers – Token reuse –
Conclusions
Memory safety vulns won’t disappear But they will become less
common
There’s still a lot to secure
Be Curious!
How to Reach Me Bluesky: LinkedIn: @alilleybrinker.com @alilleybrinker


 alilleybrinker
 yutobara
 rollbear
 n_takehata
 yumnumm
 yukiny
 minodriven
 uyuki234
 sorah
 iwiwi
 tanahiro2010
 takai
 suneo3476
 hannesfritz
 szymonslowik
 lara
 aki_iinuma
 skipperchong
 madoxten
 techseoconnect
 ianozsvald
 quramy
 jonoalderson
 signer