Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Step by step AWS Cloud Hacking
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
andresriancho
September 25, 2020
Technology
650
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Step by step AWS Cloud Hacking
andresriancho
September 25, 2020
More Decks by andresriancho
See All by andresriancho
Step by step AWS Cloud Hacking
andresriancho
2
3k
Internet-Scale analysis of AWS Cognito Security
andresriancho
1
13k
Threat Modelling
andresriancho
0
1.7k
Automated Security Analysis AWS Clouds
andresriancho
1
3.5k
Injecting into URLs / Breaking URL-Encoding
andresriancho
0
300
Galería de Fallos en Unicornios
andresriancho
1
280
Esoteric Web Application Vulnerabilities
andresriancho
0
1.2k
String Compare Timing Attacks
andresriancho
0
710
Timing Attacks
andresriancho
1
450
Other Decks in Technology
See All in Technology
これからのデータエンジニアの役割について考える / Rethinking the Role of Data Engineers in the AI Era
okiyuki99
0
340
サボる子はいねぇがー!AgentCoreハーネスの脆弱性に学ぶ、エージェントの入力バリデーション
iwamot
PRO
5
320
Kiro IDE 入門 (画面の各部から、頼み方、任せ方、戻し方まで) | 目指せ Kiro マスター 02
inariku
PRO
4
200
現場を動かすAIエージェント#2_製造業現場でのAI活用から見た、ハマる罠と実践知
kintotechdev
2
210
ゼロから作るWebアプリの新定番!?Amplify Gen 2 × AWS Blocksで実現する「開発速度とRDBの柔軟性のいいとこ取り」
amixedcolor
1
230
長い仕事を任せる (Workflows、クラウドセッション、Kiro Web) | 目指せ Kiro マスター 10
inariku
PRO
3
170
AI時代に求められる優秀なTechLeadの振る舞い
pospome
11
16k
Microsoft Entra Kerberos で実現するクラウド デバイス管理
tamaiyutaro
2
660
AWS構成から考えるWebセキュリティ ― WordPressの構築経験から考える公開範囲と更新運用【JAWS FESTA 2026 in AKITA】
cscengineer
PRO
2
400
Kiro Crew 入門 (手を離しても進む仕事) | 目指せ Kiro マスター 11
inariku
PRO
4
680
少ない人手 限られた予算 それでも守る 消せない・見つける・戻れる オールハザード型BCP on AWS / 20261107 Mitsutoshi Matsuo
shift_evolve
PRO
0
350
Cloudflareの向き先
chimame
1
290
Featured
See All Featured
The Success of Rails: Ensuring Growth for the Next 100 Years
eileencodes
47
8.4k
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
Data-driven link building: lessons from a $708K investment (BrightonSEO talk)
szymonslowik
1
1.4k
Tell your own story through comics
letsgokoyo
1
1.1k
A better future with KSS
kneath
240
18k
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
760
How to Think Like a Performance Engineer
csswizardry
28
2.9k
DBのスキルで生き残る技術 - AI時代におけるテーブル設計の勘所
soudai
PRO
68
60k
Marketing Yourself as an Engineer | Alaka | Gurzu
gurzu
0
370
Context Engineering - Making Every Token Count
addyosmani
9
1.3k
Reality Check: Gamification 10 Years Later
codingconduct
0
2.4k
Agile that works and the tools we love
rasmusluckow
331
22k
Transcript
Ekoparty 2020 Andrés Riancho
2
3
None
5
need credentials • • • 6
7
IAM permissions 8
9 http://169.254.169.254/ /latest/meta-data/iam/security-credentials/ /latest/meta-data/iam/security-credentials/{role-name}
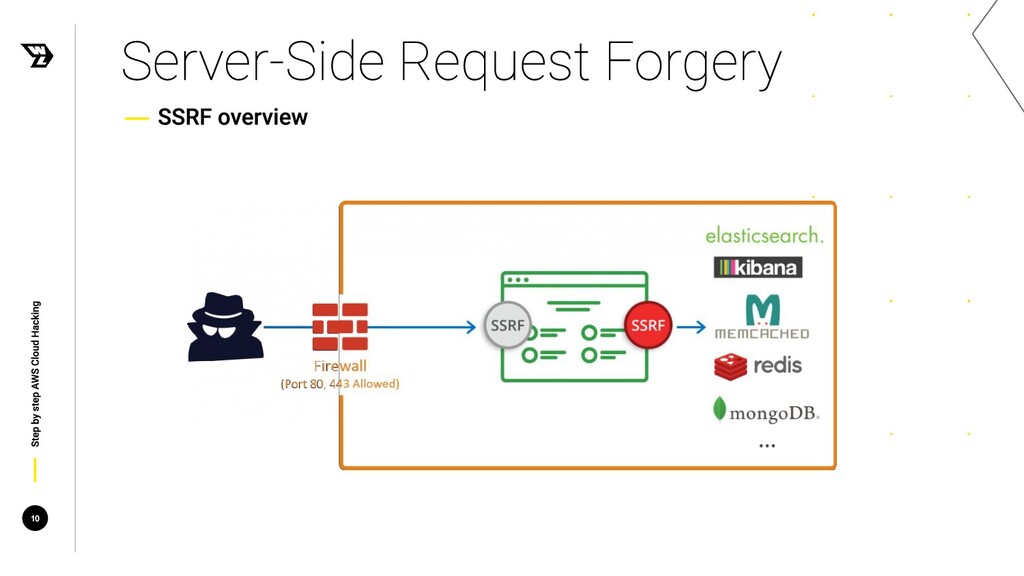
10
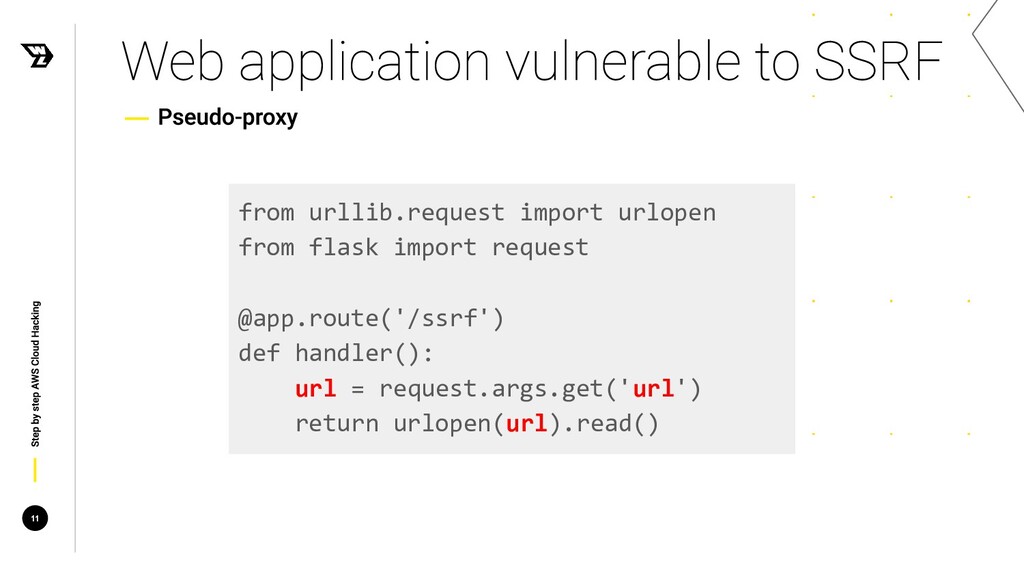
11 from urllib.request import urlopen from flask import request @app.route('/ssrf')
def handler(): url = request.args.get('url') return urlopen(url).read()
Instance metadata and S3 compromise
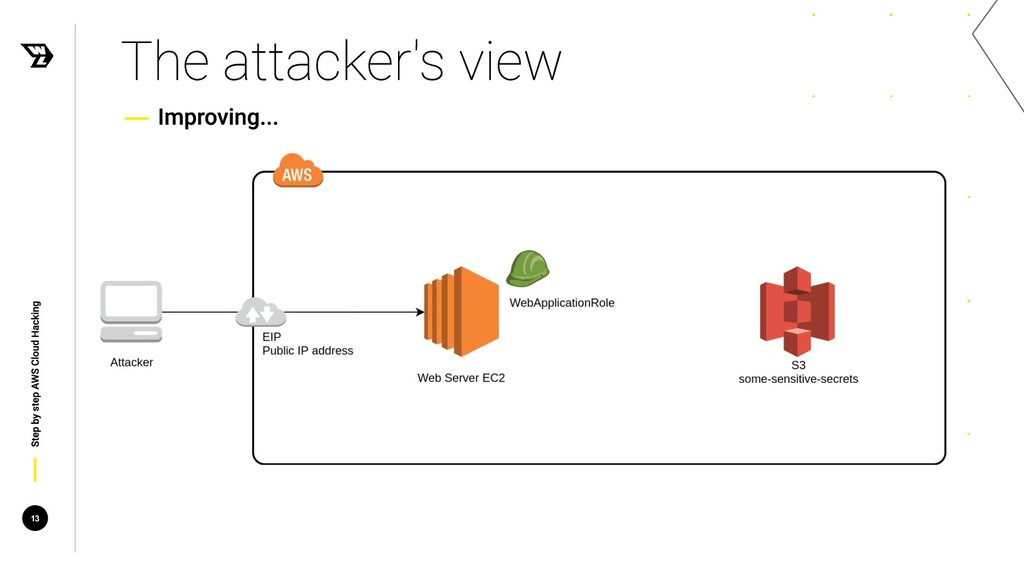
13
None
two ways to enumerate permissions IAM service In most cases
this will fail brute-force 15
Get* / List* / Describe* DryRun parameter 16
17 SUPPORTED_SERVICES = [ 'ec2', 's3' ]
18
./enumerate-iam.py
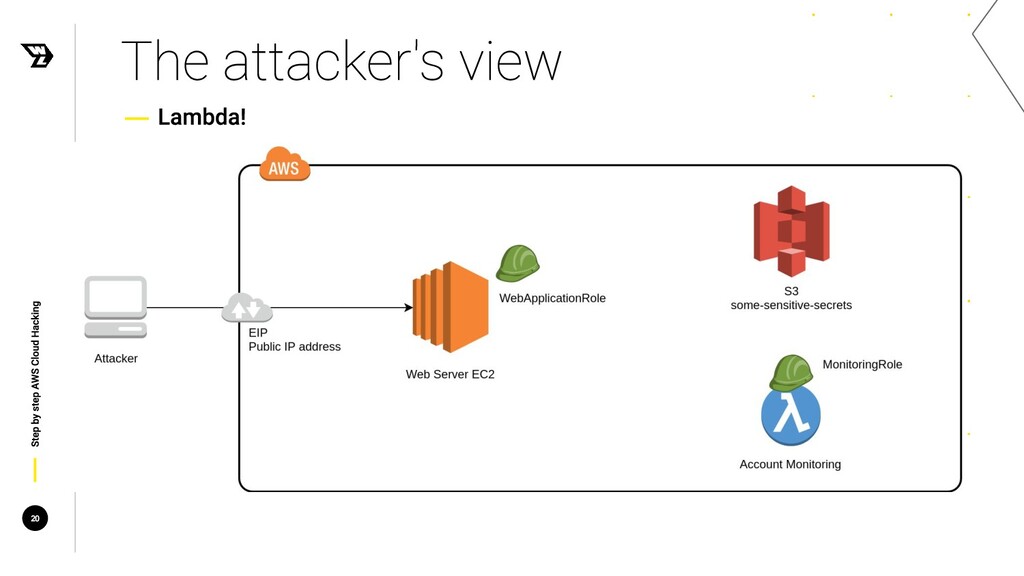
20
many things the attacker doesn't know. 21 { "Statement":[ {
"Effect":"Allow", "Action":[ "s3:*", "lambda:*", "..." ], "Resource":"*" } ] }
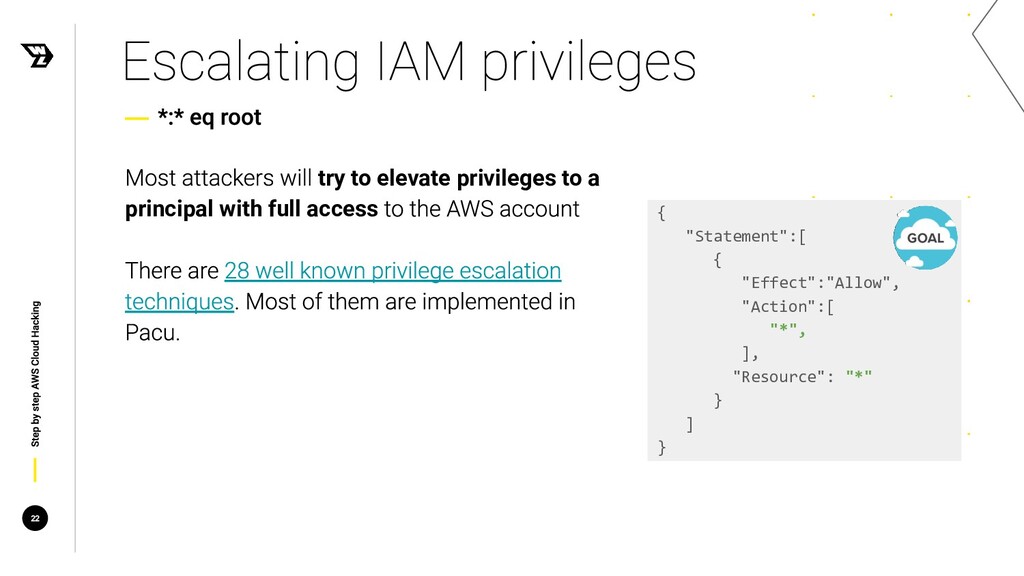
try to elevate privileges to a principal with full access
22 { "Statement":[ { "Effect":"Allow", "Action":[ "*", ], "Resource": "*" } ] }
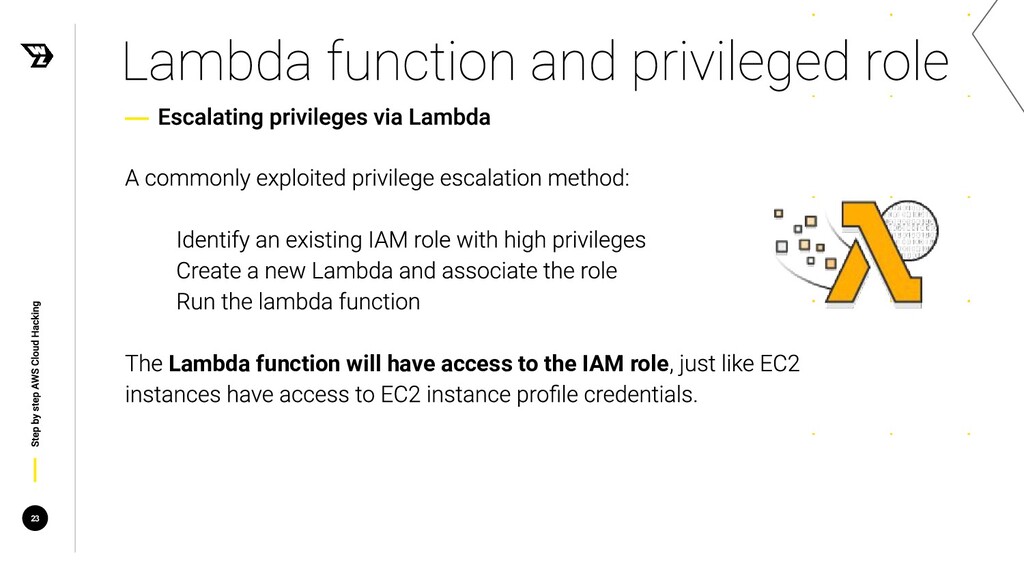
Lambda function will have access to the IAM role 23
Getting * on *
None
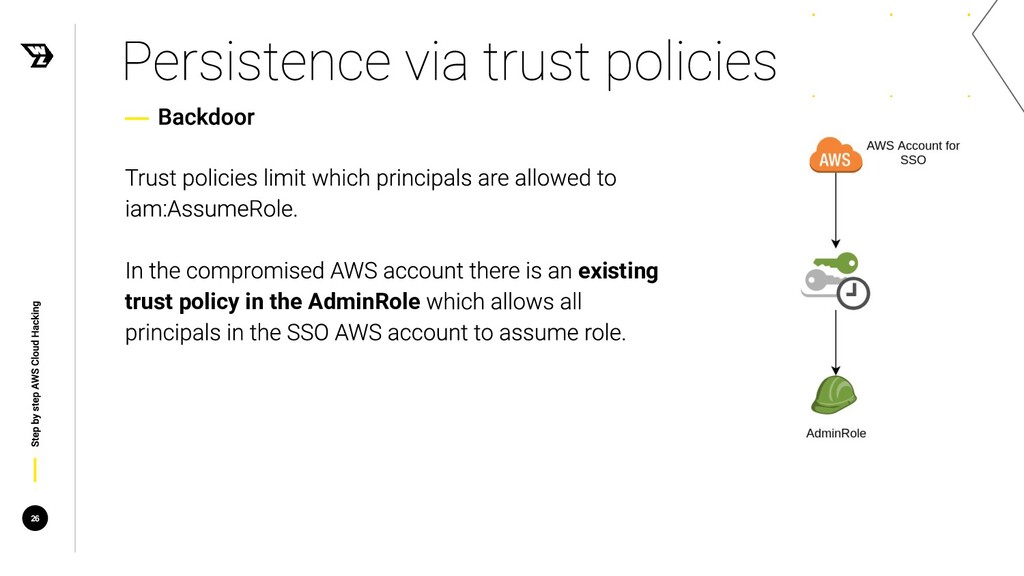
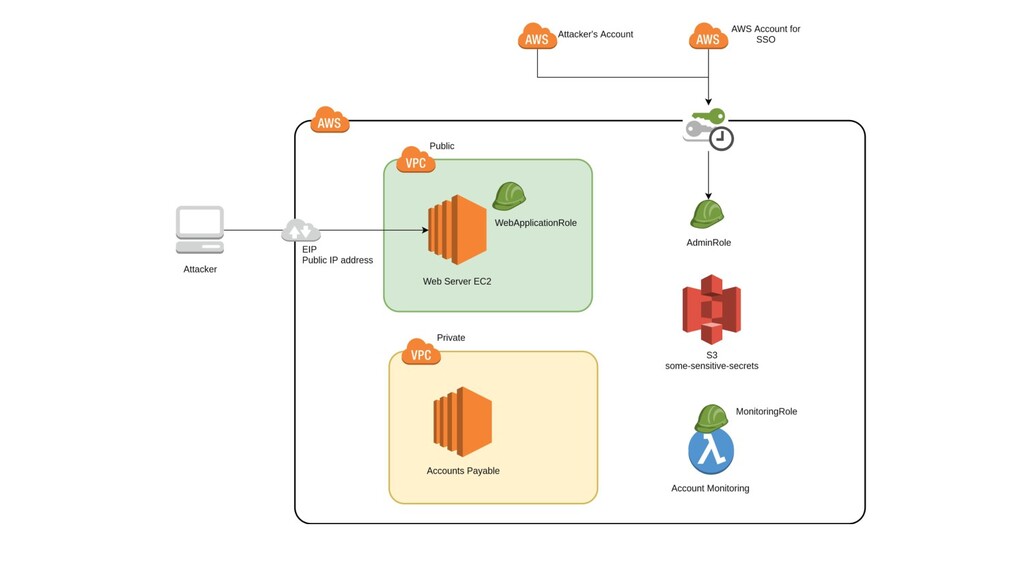
existing trust policy in the AdminRole 26
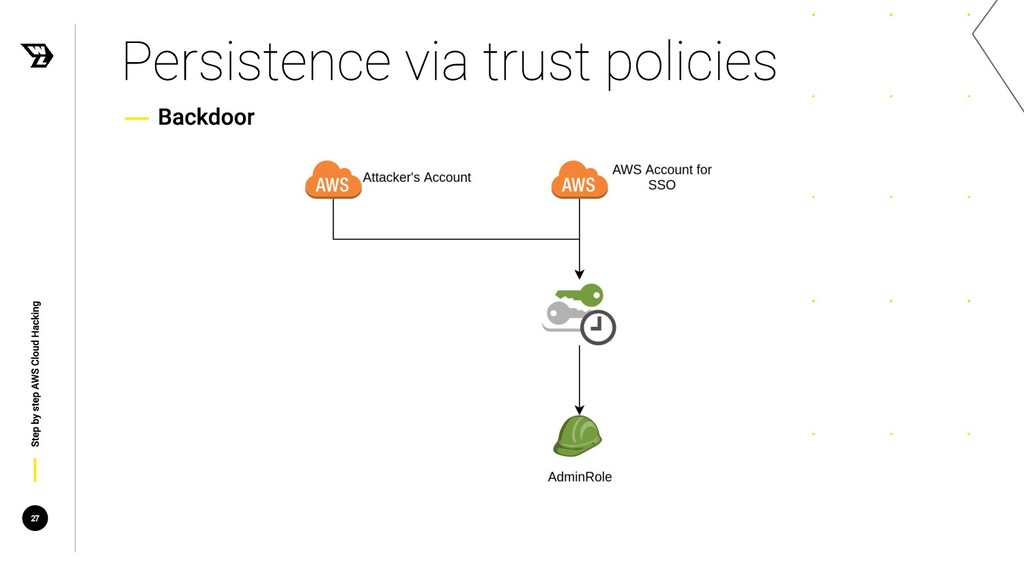
27
28 { "Effect": "Allow", "Principal": { "AWS": "arn:aws:iam::925877178748:root" }, "Action":
"sts:AssumeRole" } { "Effect": "Allow", "Principal": { "AWS": ["arn:aws:iam::925877178748:root", "arn:aws:iam::320222540496:root"] }, "Action": "sts:AssumeRole" }
Never trust the trust policy
30 ARN for the backdoored role
None
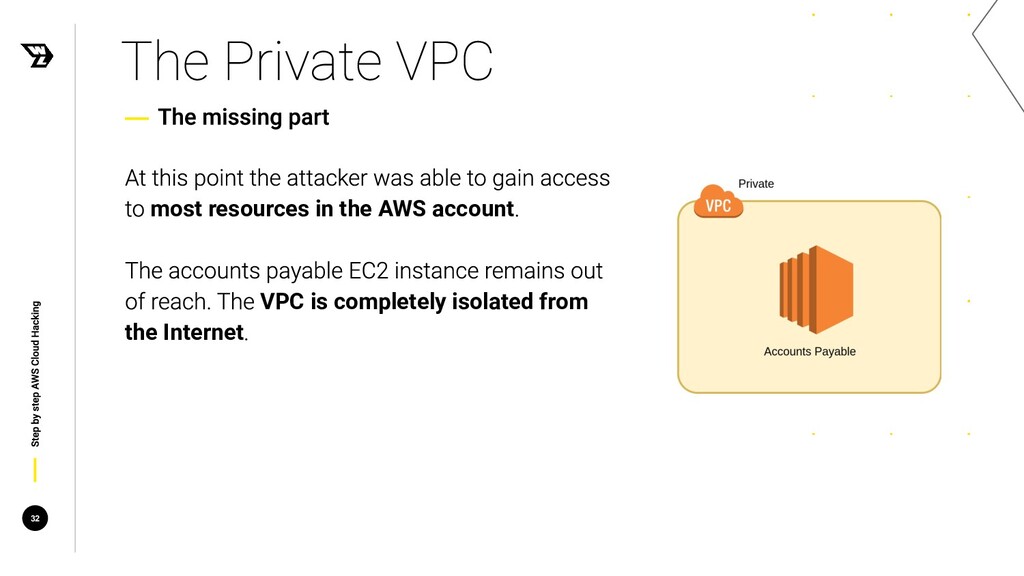
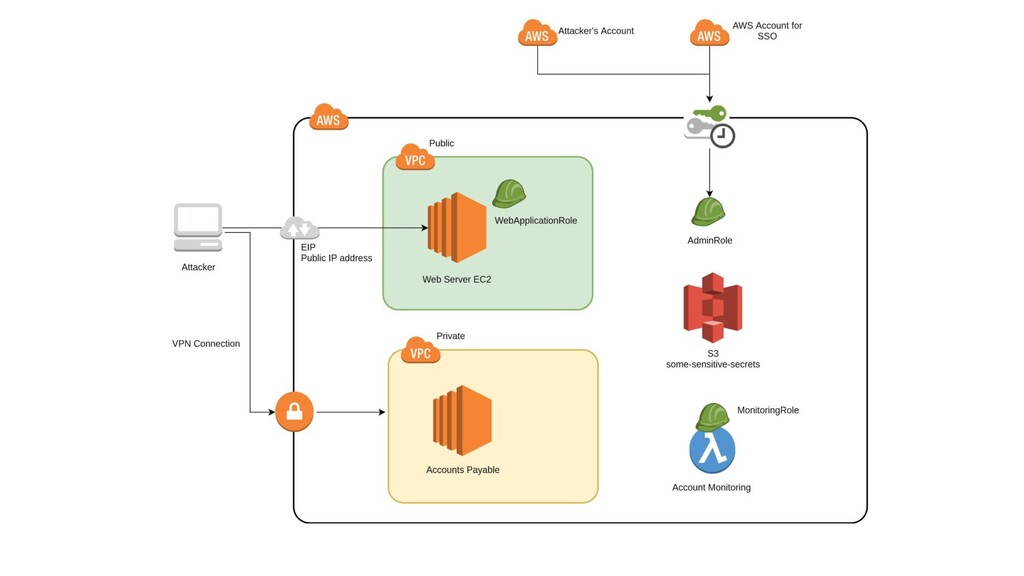
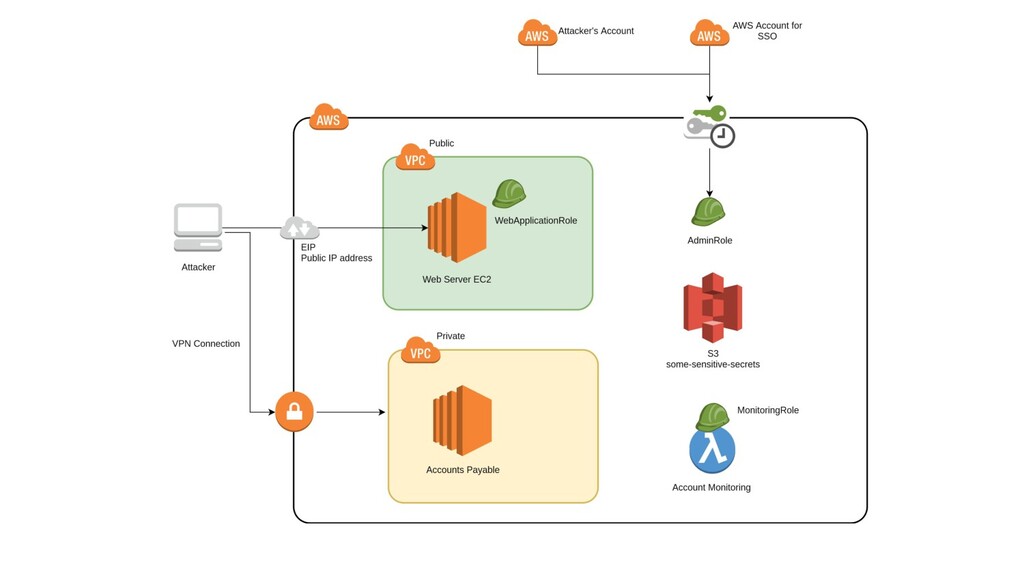
32 most resources in the AWS account VPC is completely
isolated from the Internet
None
34 VPN between the attacker's workstation and a VPC
35
vpc-vpn-pivot
None
From zero to full pwn
None
40 • enumerate-iam • pacu • vpc-vpn-pivot Follow @AndresRiancho
None

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 andresriancho
 okiyuki99
 iwamot
 inariku
 kintotechdev
 amixedcolor
 pospome
 tamaiyutaro
 cscengineer
 shift_evolve
 chimame
 eileencodes
 mraible
 szymonslowik
 letsgokoyo
 kneath
 baasie
 csswizardry
 soudai
 gurzu
 addyosmani
 codingconduct
 rasmusluckow