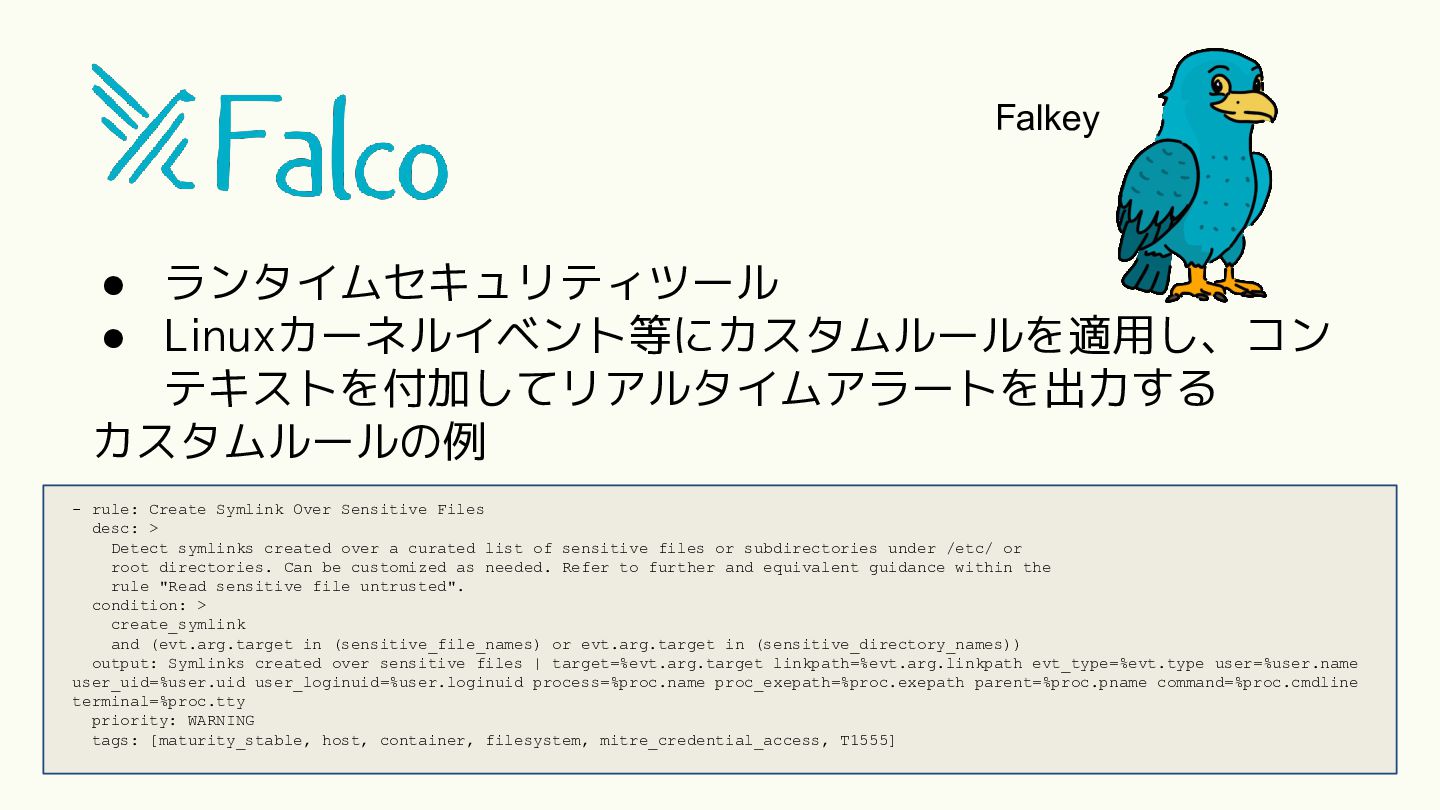
Symlink Over Sensitive Files desc: > Detect symlinks created over a curated list of sensitive files or subdirectories under /etc/ or root directories. Can be customized as needed. Refer to further and equivalent guidance within the rule "Read sensitive file untrusted". condition: > create_symlink and (evt.arg.target in (sensitive_file_names) or evt.arg.target in (sensitive_directory_names)) output: Symlinks created over sensitive files | target=%evt.arg.target linkpath=%evt.arg.linkpath evt_type=%evt.type user=%user.name user_uid=%user.uid user_loginuid=%user.loginuid process=%proc.name proc_exepath=%proc.exepath parent=%proc.pname command=%proc.cmdline terminal=%proc.tty priority: WARNING tags: [maturity_stable, host, container, filesystem, mitre_credential_access, T1555]


 aoi1
 cdataj
 soudai
 uhyo
 civitaspo
 pauli
 you
 yukiogawa
 jinwatanabe
 bqnq
 kishima
 visional_engineering_and_design
 yutashigemura
 tmiket
 axbom
 frankvandijk
 minecr
 marktimemedia
 sstephenson
 cassininazir
 takai
 chriscoyier
 tammielis
 orderedlist