Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Intrusions and the Modern Web
Search
Benjamin Scott
November 23, 2015
Technology
140
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Intrusions and the Modern Web
how and why bad guys break into servers
Benjamin Scott
November 23, 2015
More Decks by Benjamin Scott
See All by Benjamin Scott
Practical Cross-Side Request Forgery
benjaminxscott
0
59
Starting your Infosec Career
benjaminxscott
0
410
Lie To Me: Mitigating Intrusions using Deception
benjaminxscott
0
84
Internet Security for Everyone
benjaminxscott
1
73
Beneath the Radar: covert traffic on the web
benjaminxscott
0
99
Securing your company's networks
benjaminxscott
0
84
Internet Forensics 101
benjaminxscott
0
82
Intro to Binary Analysis
benjaminxscott
0
61
Analyzing Evil PDF Files with peepdf
benjaminxscott
0
230
Other Decks in Technology
See All in Technology
アプリをもっと"iOSアプリっぽく"する小さな工夫 / Small Touches That Make Your App Feel More Like an iOS App
matsuji
1
900
Claude Code本って、 読む必要あるの?
oikon48
2
460
omasushiというライブラリを作った
polidog
PRO
0
230
Reactの設計論
uhyo
24
13k
10Xに技術的負債をもたらした「2つの境界の歪み」その構造と解消への営み
10xinc
0
1.9k
Deployment の 先にある AI Agent 基盤 - kagent vNext、Agent Substrate、Hermes から読み解く Agent Runtime の現在地 / k8s-matsuri-2-ai-agent-platform-amsy810
masayaaoyama
3
560
日経電子版を支えていく Kasane Design System/fec_fukuoka
nikkei_engineer_recruiting
0
1.5k
AIによるクリエイティブ生成を行う上での試行錯誤
plaidtech
PRO
0
150
絵ではじめるKubernetesセキュリティ
aoi1
3
570
HHKBエバンジェリストになる方法
941
0
100
おい、エージェントを使って終わらせろ
nwiizo
0
250
[2026-09-11]SREは誰のもの?運用エンジニアが始める 「SRE領域への越境」とチームの進化の軌跡 〜Road to NEXT CRE
tosite
0
250
Featured
See All Featured
How to Talk to Developers About Accessibility
jct
2
550
Learning to Love Humans: Emotional Interface Design
aarron
275
41k
Building Adaptive Systems
keathley
44
3.2k
SEO in 2025: How to Prepare for the Future of Search
ipullrank
3
3.8k
Groundhog Day: Seeking Process in Gaming for Health
codingconduct
0
350
Breaking role norms: Why Content Design is so much more than writing copy - Taylor Woolridge
uxyall
1
410
Technical Leadership for Architectural Decision Making
baasie
3
570
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Discover your Explorer Soul
emna__ayadi
2
1.3k
brightonSEO & MeasureFest 2025 - Christian Goodrich - Winning strategies for Black Friday CRO & PPC
cargoodrich
3
840
Navigating Algorithm Shifts & AI Overviews - #SMXNext
aleyda
1
1.6k
Ruling the World: When Life Gets Gamed
codingconduct
0
330
Transcript
Intrusions and the Modern Web Benjamin Scott
[email protected]
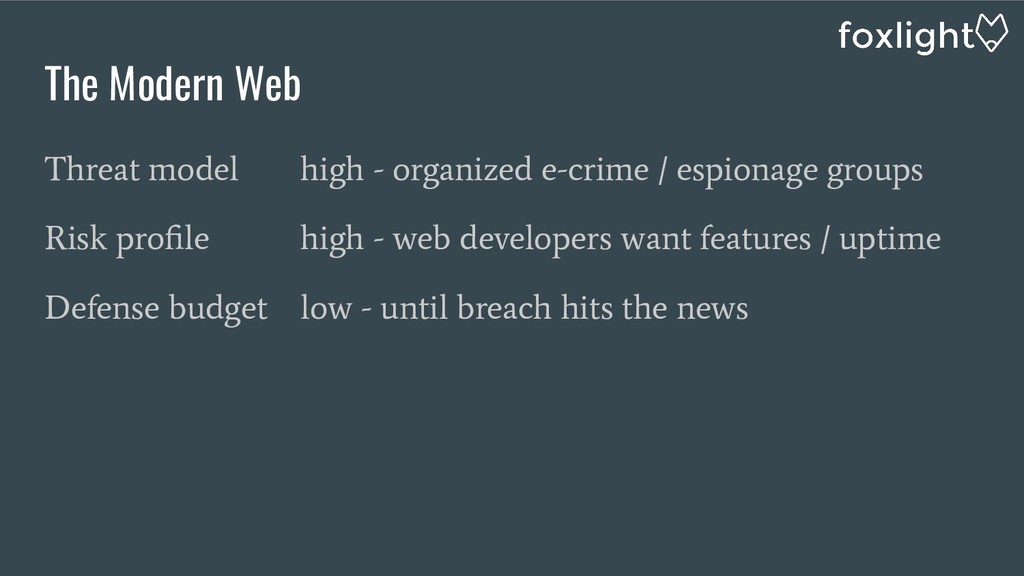
The Modern Web Threat model high - organized e-crime /
espionage groups Risk profile high - web developers want features / uptime Defense budget low - until breach hits the news
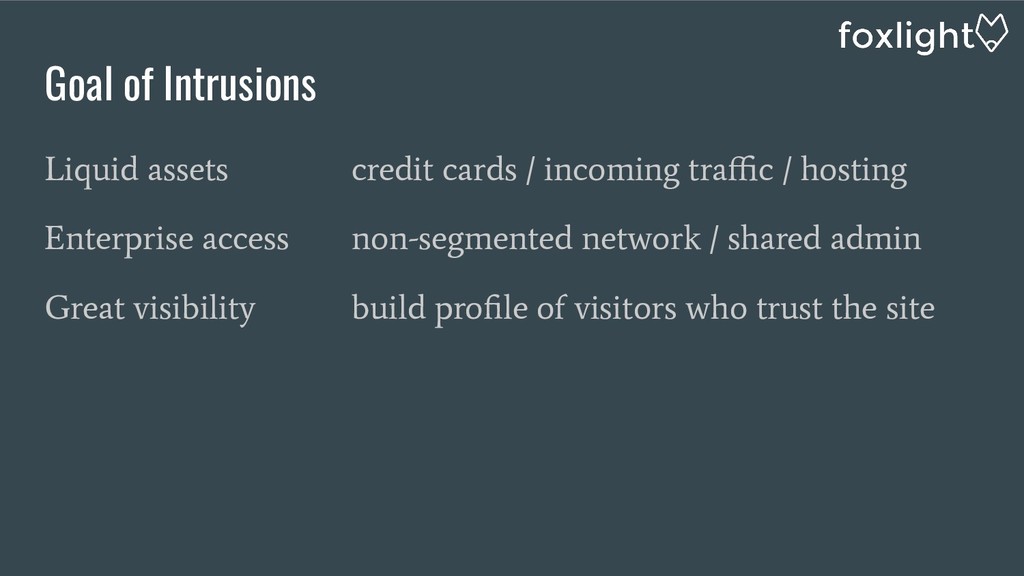
Goal of Intrusions Liquid assets credit cards / incoming traffic
/ hosting Enterprise access non-segmented network / shared admin Great visibility build profile of visitors who trust the site
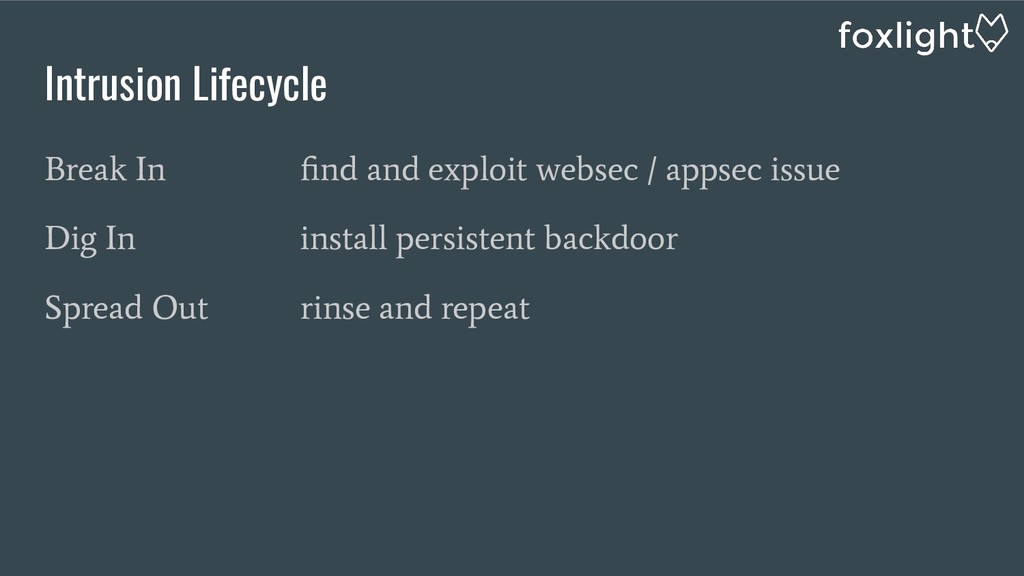
Intrusion Lifecycle Break In find and exploit websec / appsec
issue Dig In install persistent backdoor Spread Out rinse and repeat
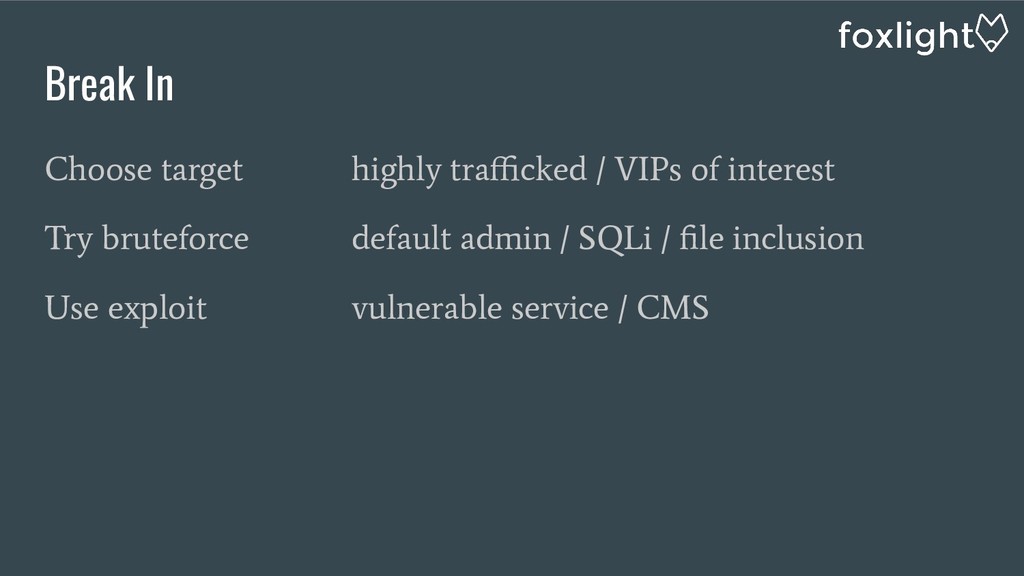
Break In Choose target highly trafficked / VIPs of interest
Try bruteforce default admin / SQLi / file inclusion Use exploit vulnerable service / CMS
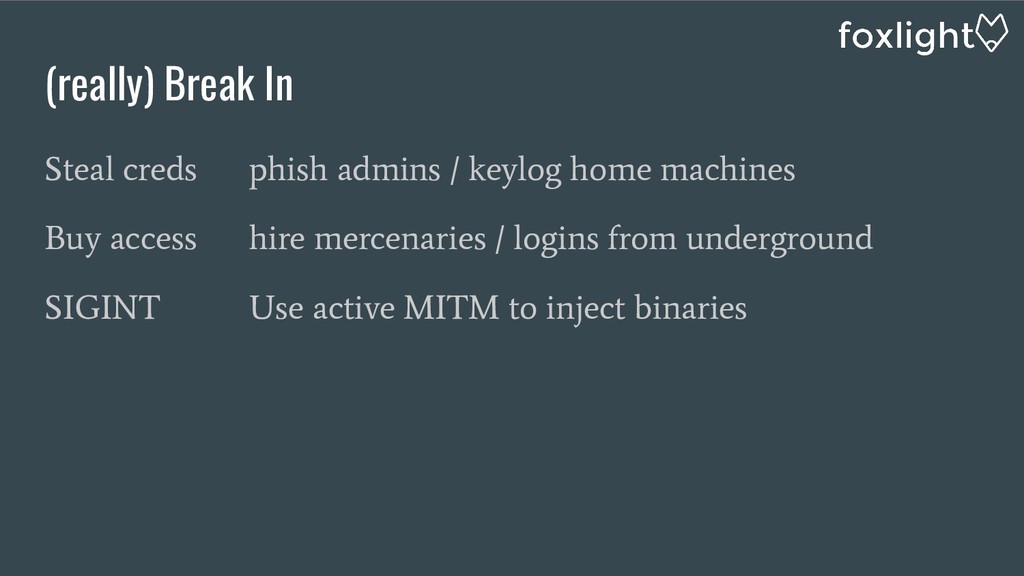
(really) Break In Steal creds phish admins / keylog home
machines Buy access hire mercenaries / logins from underground SIGINT Use active MITM to inject binaries
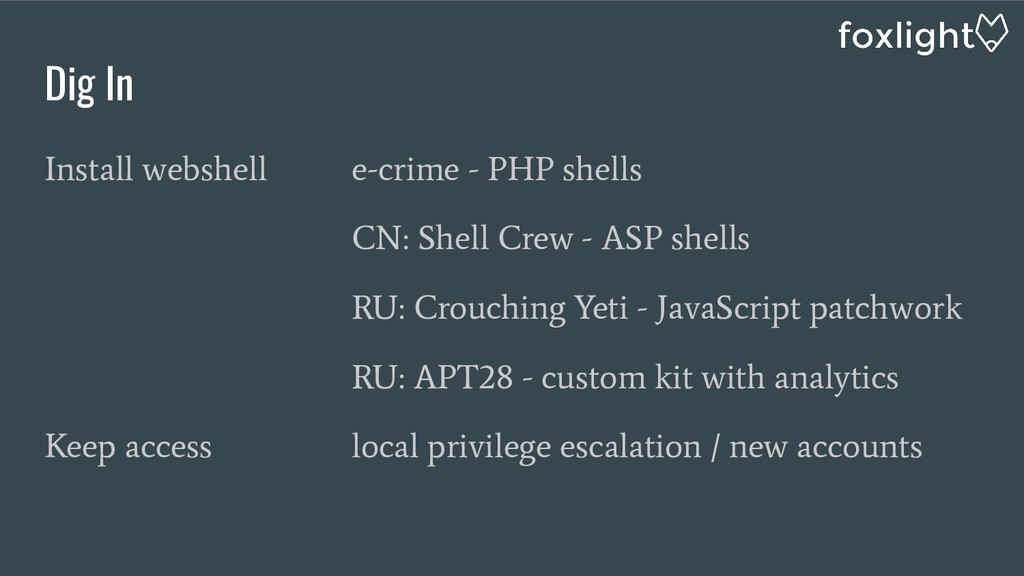
Dig In Install webshell e-crime - PHP shells CN: Shell
Crew - ASP shells RU: Crouching Yeti - JavaScript patchwork RU: APT28 - custom kit with analytics Keep access local privilege escalation / new accounts
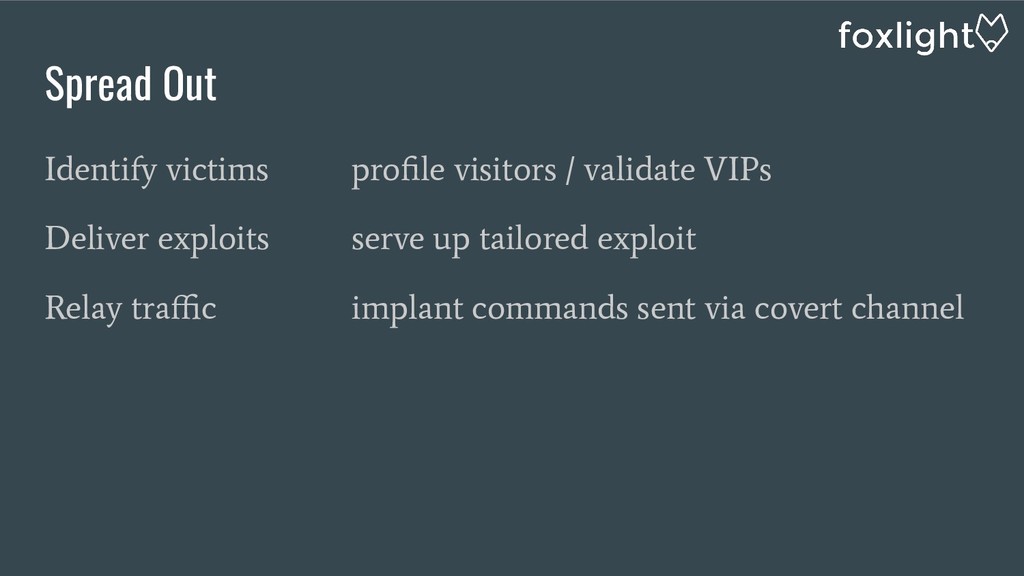
Spread Out Identify victims profile visitors / validate VIPs Deliver
exploits serve up tailored exploit Relay traffic implant commands sent via covert channel
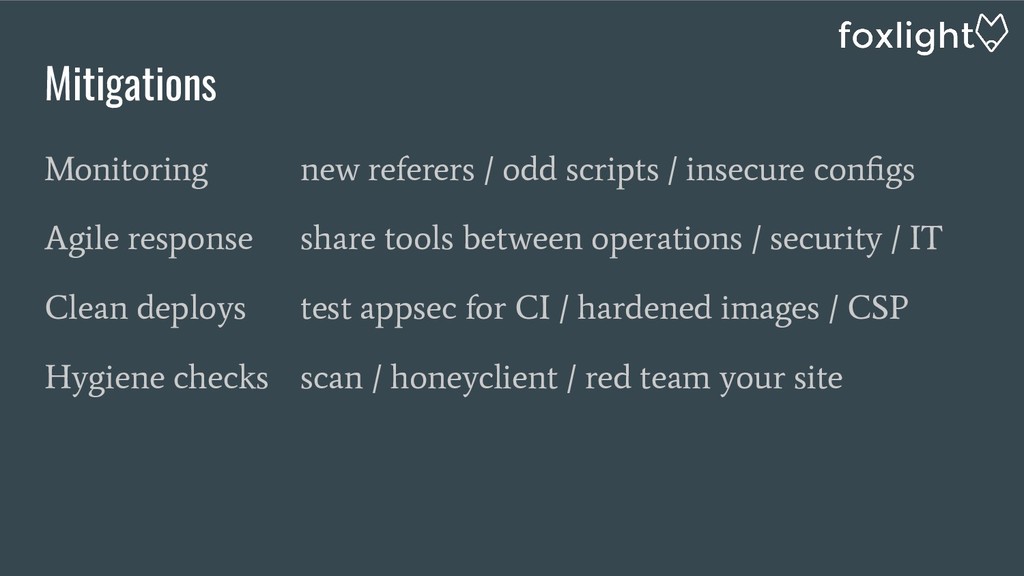
Mitigations Monitoring new referers / odd scripts / insecure configs
Agile response share tools between operations / security / IT Clean deploys test appsec for CI / hardened images / CSP Hygiene checks scan / honeyclient / red team your site
Thanks for listening Benjamin Scott
[email protected]
github.com/benjaminxscott about.me/benjaminxscott


 benjaminxscott
 matsuji
 oikon48
 polidog
 uhyo
 10xinc
 masayaaoyama
 nikkei_engineer_recruiting
 plaidtech
 aoi1
 941
 nwiizo
 tosite
 jct
 aarron
 keathley
 ipullrank
 codingconduct
 uxyall
 baasie
 caitiem20
 emna__ayadi
 cargoodrich
 aleyda