Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Shifting Application Security Left

Shifting Application Security Left

Many people agree the best way to avoid security problems in an application is to design security into the architecture from the beginning instead of doing blackbox testing after development is finished. But what does that actually look like in a real-world application development lifecycle? Checklists like the OWASP Top 10 do not tell architects how to best work with infosec professionals or singlehandedly build an application on a secure foundation. Where should a developer even begin? How do you design security into applications based on next week's JavaScript framework, for which no "best practices" exist? The Information Security Practice Principles, developed by Indiana University’s Center for Applied Cybersecurity Research, provide both a foundation for application security independent of specific technology decisions as well as a means for establishing a common language between designers and defenders. We will work through an example of how to apply the principles build a threat model and an application design, and what this looks like in an "agile" software development lifecycle. Security teams can be an enabler for good design, not just a gateway to block mistakes!

Craig Stuntz

March 02, 2018

Transcript

87 slides
  1. S H I F T I N G A P

    P L I C A T I O N S E C U R I T Y L E F T Craig Stuntz ∈ Improving https://speakerdeck.com/craigstuntz
  2. 2 0 1 7 the “Norton Secured” logo. §15.2.3 OWASP

    Training All developers on the project shall receive OWASP training. §15.3 Payment Terms
  3. « C L I E N T » S E

    C U R I T Y B R I E F I N G
  4. P R E V I E W • What does

    application security mean? • Developer checklists don’t work • Threat modeling & security f rom f irst principles • Security as a f irst class part of the software design & development lifecycle
  5. – H i p p o c r a t

    i c O a t h ( 1 9 6 4 L o u i s L a s a g n a v e r s i o n ) “I will remember that I do not treat a fever chart, a cancerous growth, but a sick human being, whose illness may affect the person’s family and economic stability.”
  6. W H A T W O U L D S

    O F T W A R E D E V E L O P M E N T L O O K L I K E I F H U M A N S A F E T Y W A S A LW A Y S T H E F I R S T C O N S I D E R A T I O N ? https://www.flickr.com/photos/wocintechchat/25900776992/
  7. – A C M C o d e o f

    E t h i c s a n d P r o f e s s i o n a l C o n d u c t ( p r o p o s e d ) “A computing professional should contribute to society and to human well-being, acknowledging that all people are stakeholders in computing.”
  8. – A l l i s o n M i

    l l e r “I don't think humans are the problem, the problem is that humans are the target.” https://www.scmagazineuk.com/news-feature-google-security-interview-human-solutions--the-way-to-go/article/701976/
  9. W H A T I S S E C U

    R I T Y , R E A L LY ? https://commons.wikimedia.org/wiki/File:Airport_Frankfurt_-_Fraport_-_Flughafen_Frankfurt_-_barbed_wire_and_fence_-_Stacheldraht_und_Zaun_-_05.jpg https://www.flickr.com/photos/captkodak/37054929956/
  10. D O M A I N S P E C

    I F I C Q A
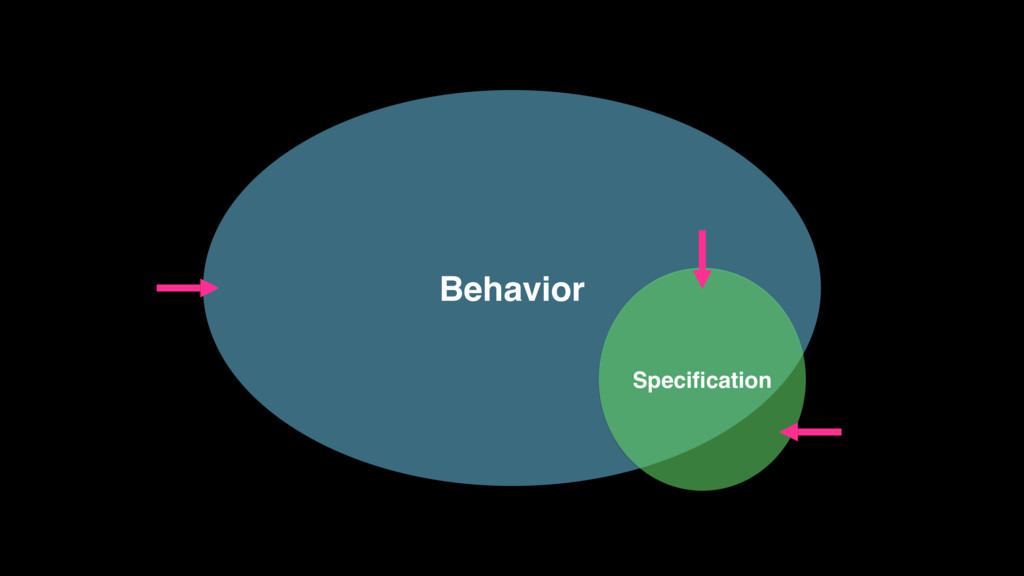
  11. Q A : D O E S T H E

    S O F T W A R E D O W H A T I T S H O U L D ?
  12. S E C U R I T Y : D

    O E S I T A L S O D O A N Y T H I N G E L S E ?
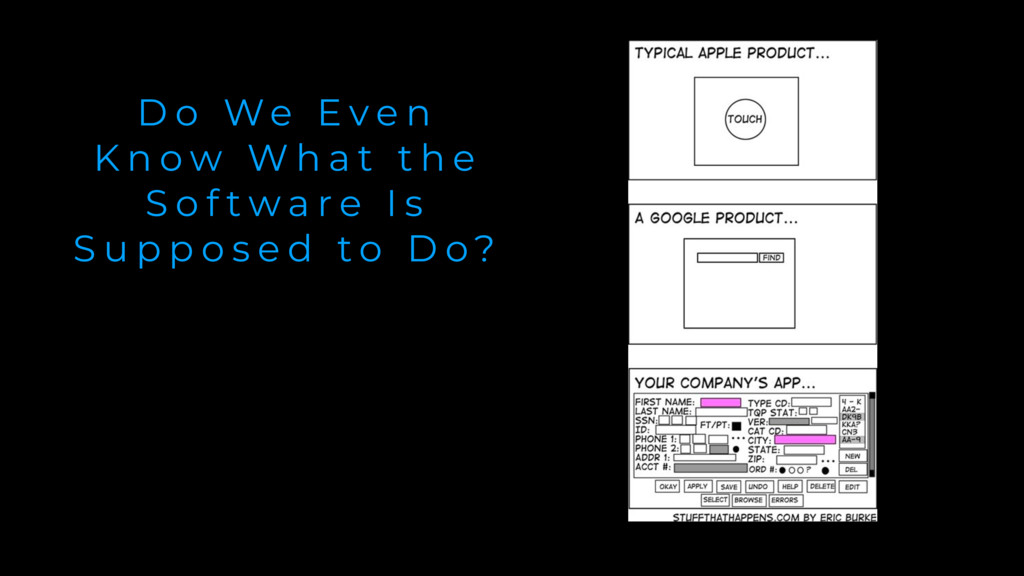
  13. D o We E v e n K n o

    w W h a t t h e S o f t w a r e I s S u p p o s e d t o D o ?
  14. “In order to write secure applications, developers must • Take

    OWASP Top 10 training • Use Veracode • Have application pentested • Use two factor authentication on source control and hosts • Use off-the-shelf crypto libraries • Monitor production • Use memory-safe languages • Do code review • HTTPS everywhere!
  15. B U I L D A R E C I

    P E , N O T A G R O C E R Y S T O R E
  16. L E A R N Y O U R D

    O M A I N https://commons.wikimedia.org/wiki/File:Domain,_Atrium_(Hong_Kong).jpg
  17. – M a t t Ta i t “The underlying

    problem is folks think in terms of ‘secure’ versus ‘insecure.’ But in reality, it's ‘in/secure vs. X threat in Y threat model.’” https://twitter.com/pwnallthethings/status/922009773352120320
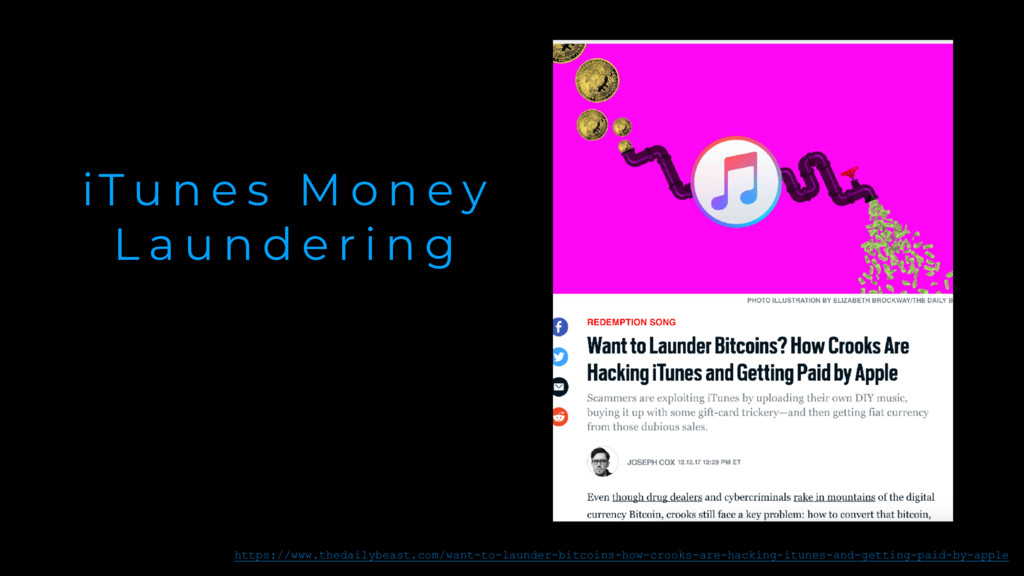
  18. iT u n e s M o n e y

    L a u n d e r i n g https://www.thedailybeast.com/want-to-launder-bitcoins-how-crooks-are-hacking-itunes-and-getting-paid-by-apple
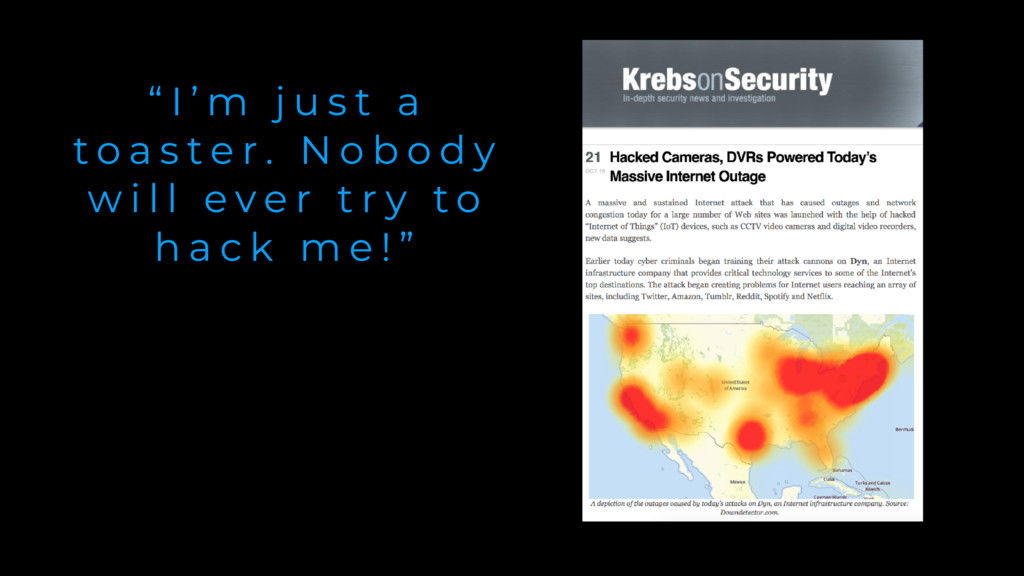
  19. “ I ’ m j u s t a t

    o a s t e r . N o b o d y w i l l e v e r t r y t o h a c k m e ! ”
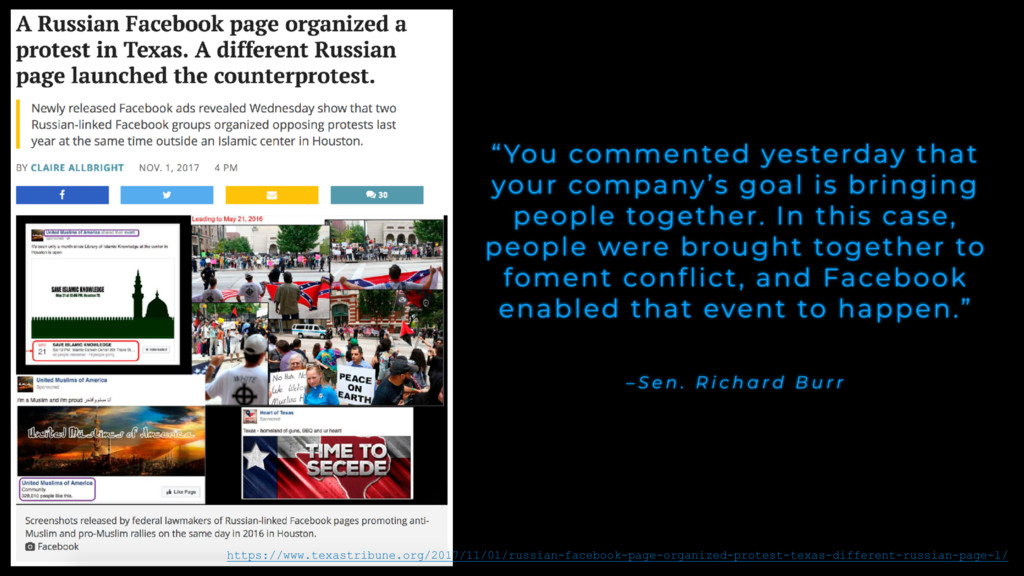
  20. – S e n . R i c h a

    r d B u r r “You commented yesterday that your company’s goal is bringing people together. In this case, people were brought together to foment conflict, and Facebook enabled that event to happen.” https://www.texastribune.org/2017/11/01/russian-facebook-page-organized-protest-texas-different-russian-page-l/
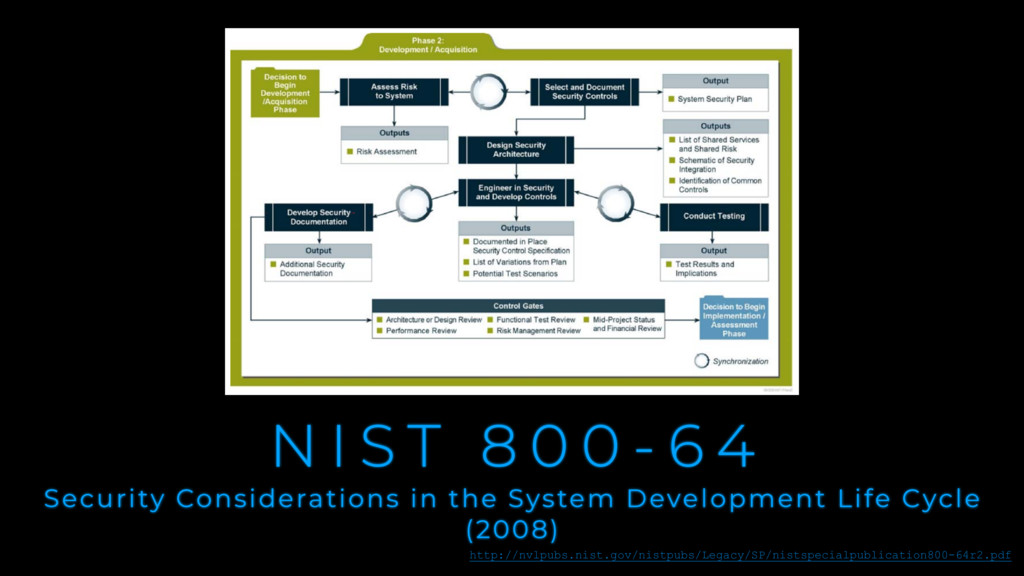
  21. N I S T 8 0 0 - 6 4

    Security Considerations in the System Development Life Cycle (2008) http://nvlpubs.nist.gov/nistpubs/Legacy/SP/nistspecialpublication800-64r2.pdf
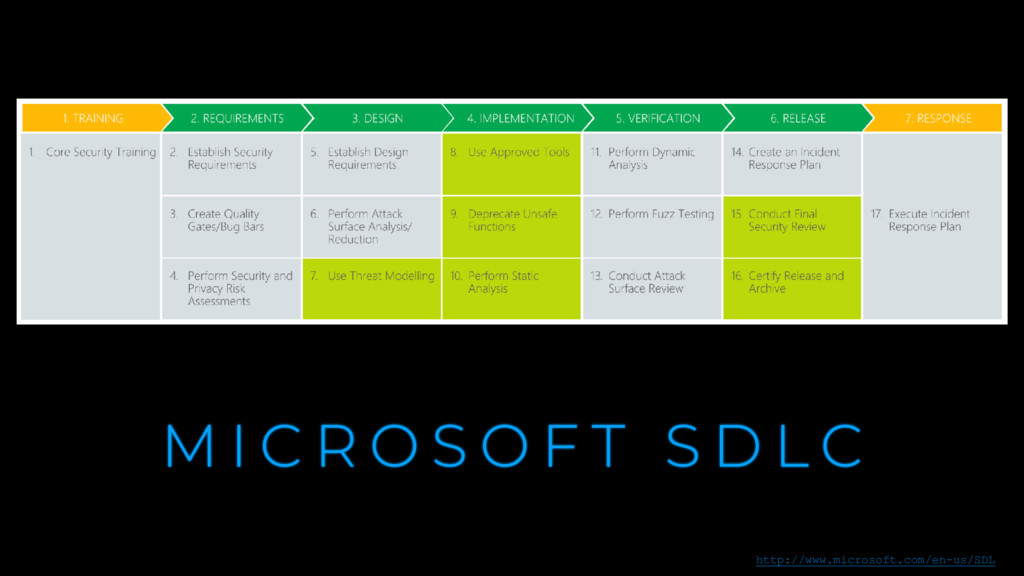
  22. M I C R O S O F T S

    D L C http://www.microsoft.com/en-us/SDL
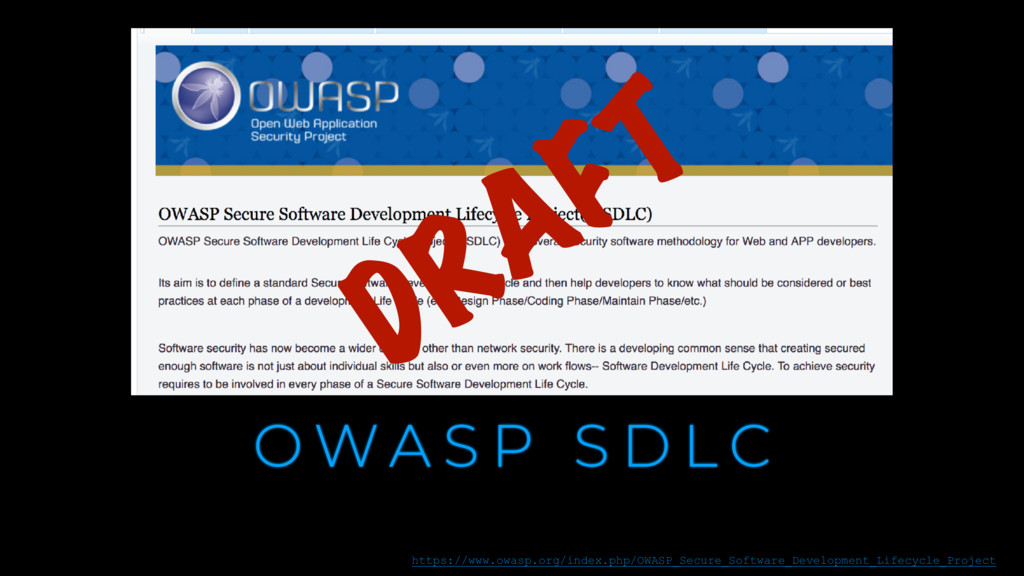
  23. O W A S P S D L C DRAFT

    https://www.owasp.org/index.php/OWASP_Secure_Software_Development_Lifecycle_Project
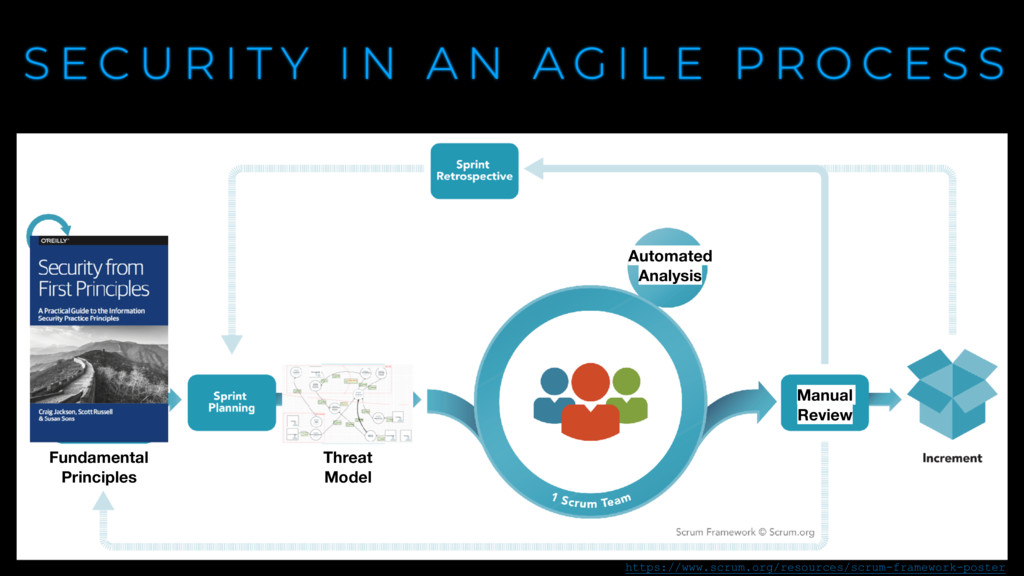
  24. S E C U R I T Y I N

    A N A G I L E P R O C E S S https://www.scrum.org/resources/scrum-framework-poster Fundamental Principles Threat Model Automated Analysis Manual Review
  25. S I X D E G R E E S

    Who is affected by the software you create? https://www.flickr.com/photos/wocintechchat/25388897014/
  26. C u s t o m e r s https://www.flickr.com/photos/wocintechchat/25703122741/

    https://www.flickr.com/photos/wocintechchat/25926791491/
  27. S t a k e h o l d e

    r s https://www.flickr.com/photos/wocintechchat/25388889234/
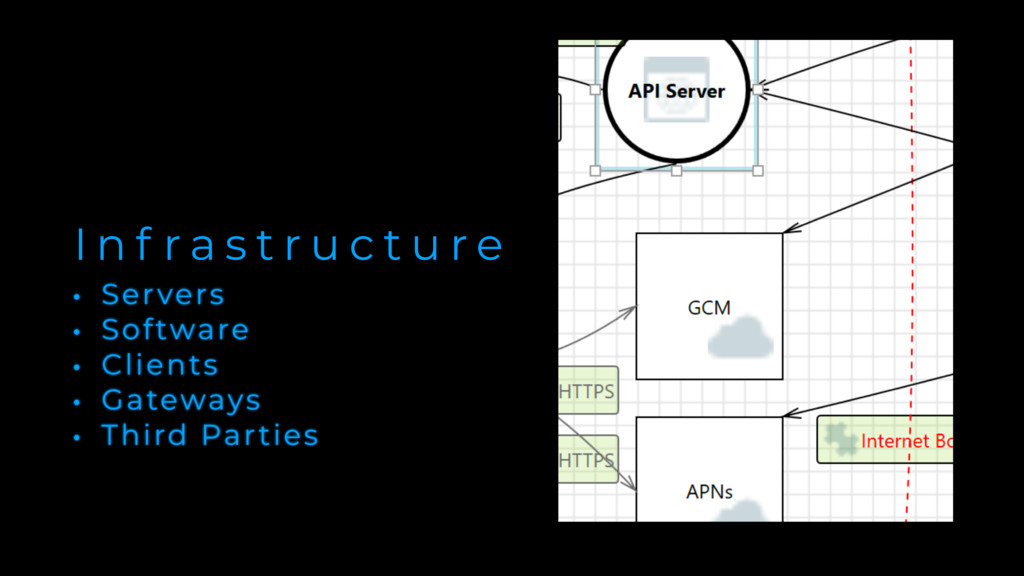
  28. I n f r a s t r u c

    t u r e • Servers • Software • Clients • Gateways • Third Parties
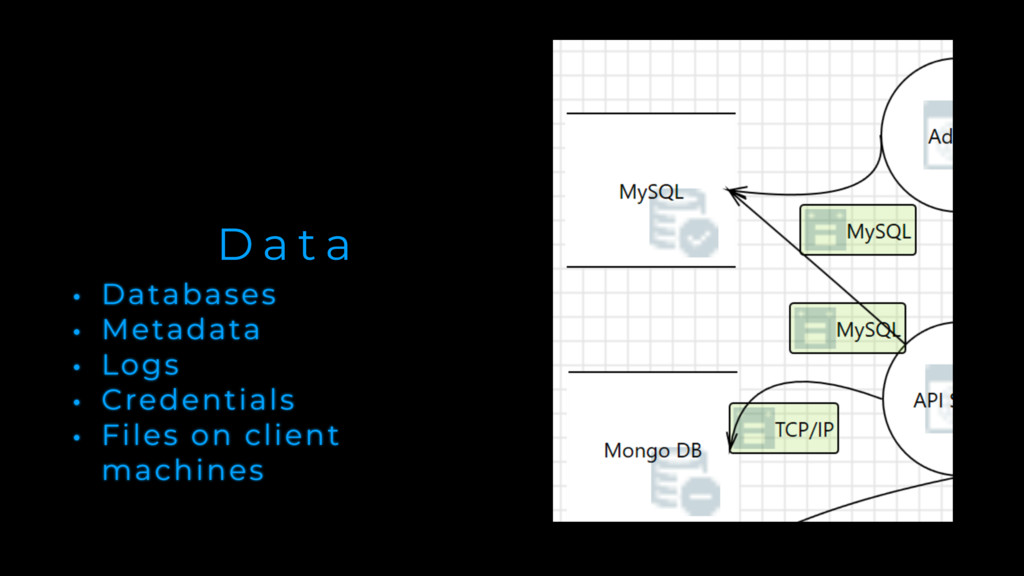
  29. D a t a • Databases • Metadata • Logs

    • Credentials • Files on client machines
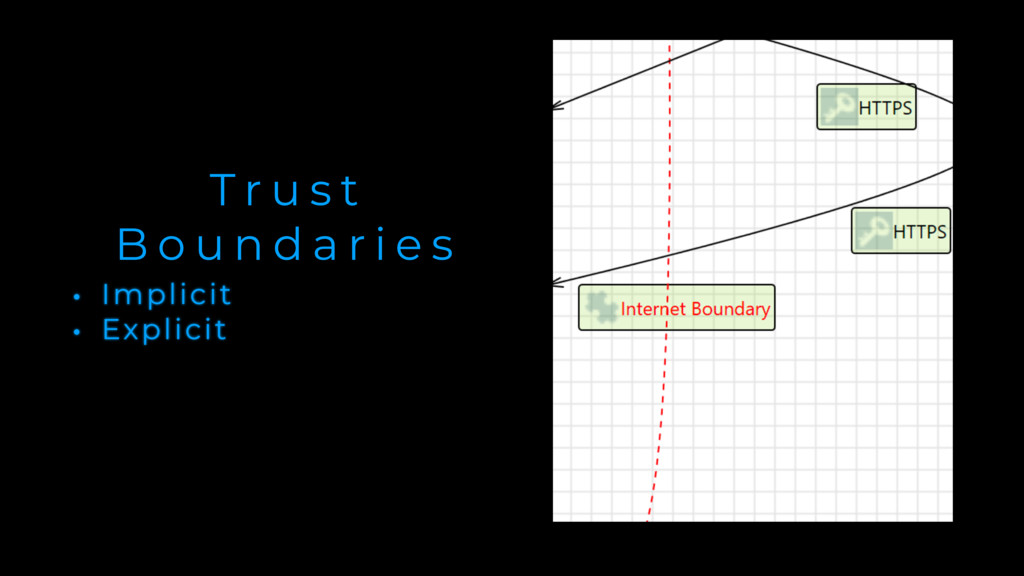
  30. T r u s t B o u n d

    a r i e s • Implicit • Explicit
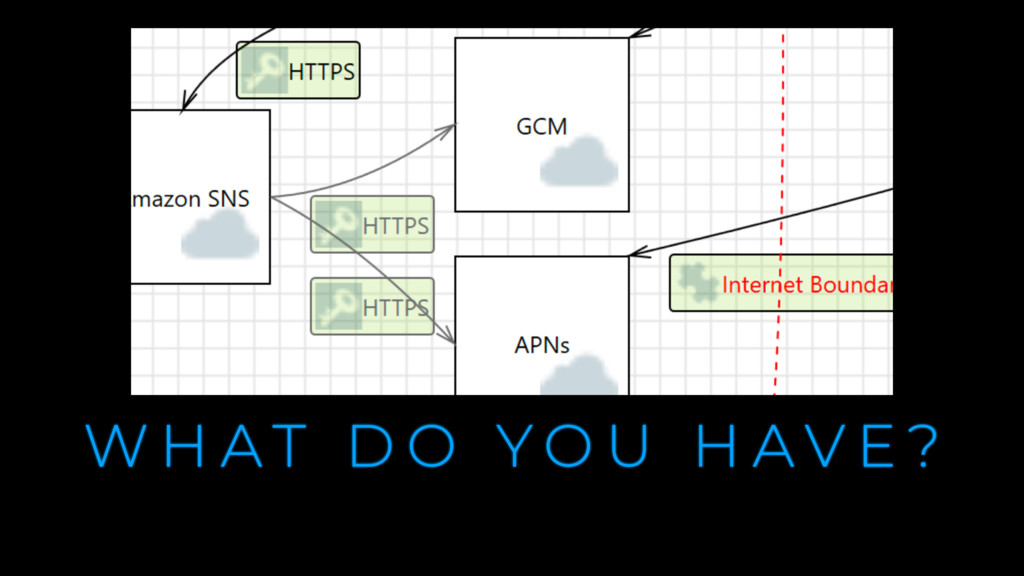
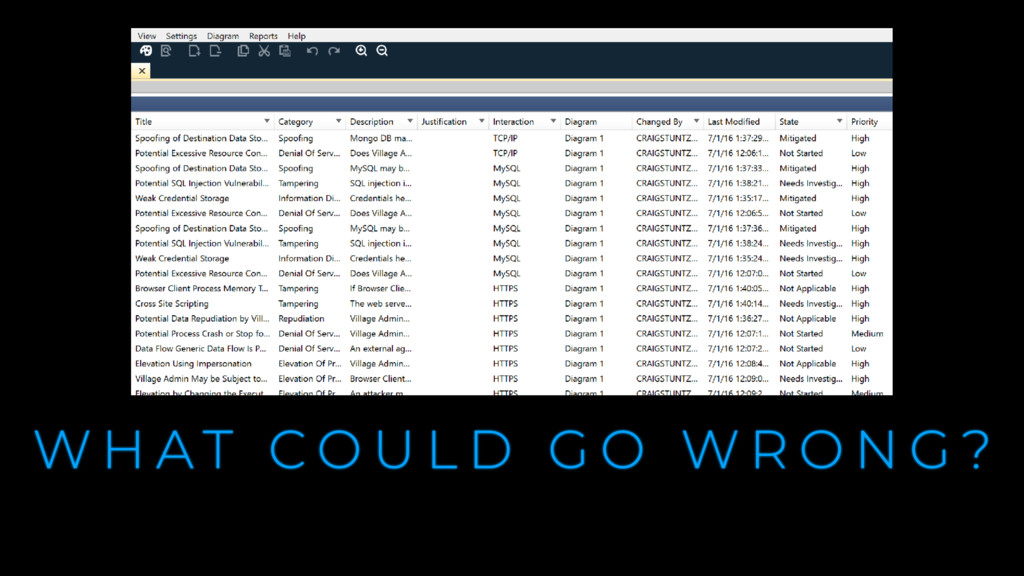
  31. W H A T C O U L D G

    O W R O N G ?
  32. D O M A I N - S P E

    C I F I C R I S K S
  33. T a k e C a r e o f

    P e o p l e F i r s t https://www.flickr.com/photos/wocintechchat/25926827581/
  34. L e a r n f r o m H

    i s t o r y https://commons.wikimedia.org/wiki/File:Maginot_line_1.jpg
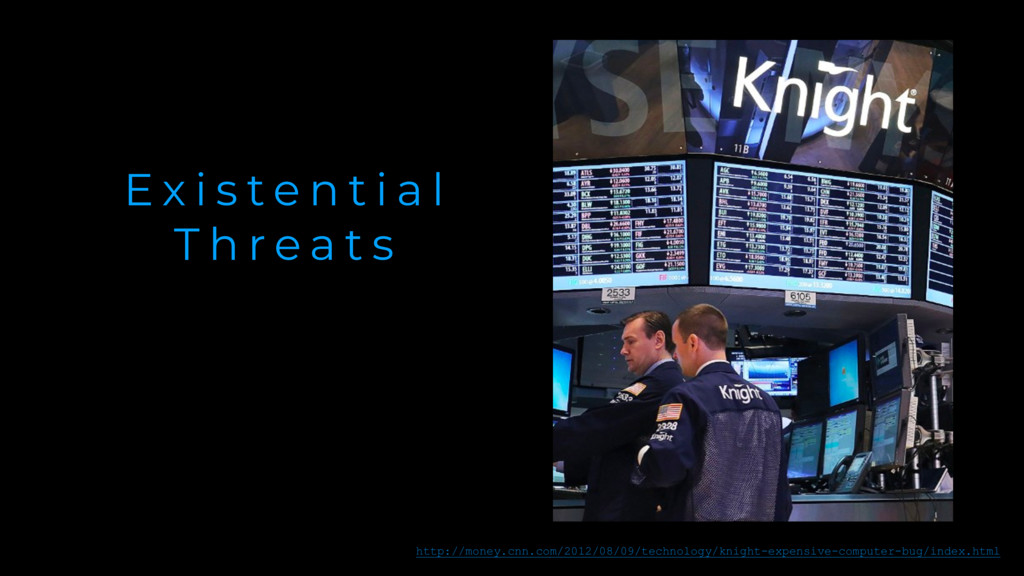
  35. E x i s t e n t i a

    l T h r e a t s http://money.cnn.com/2012/08/09/technology/knight-expensive-computer-bug/index.html
  36. C O M P R E H E N S

    I V I T Y Security f rom First Principles Am I covering all of my bases? Craig Jackson, Scott Russell, and Susan Sons https://upload.wikimedia.org/wikipedia/commons/7/72/Agoncillo_- _W%C3%BCrth_Rioja%2C_Museo_30_-_Christo.JPG
  37. O P P O R T U N I T

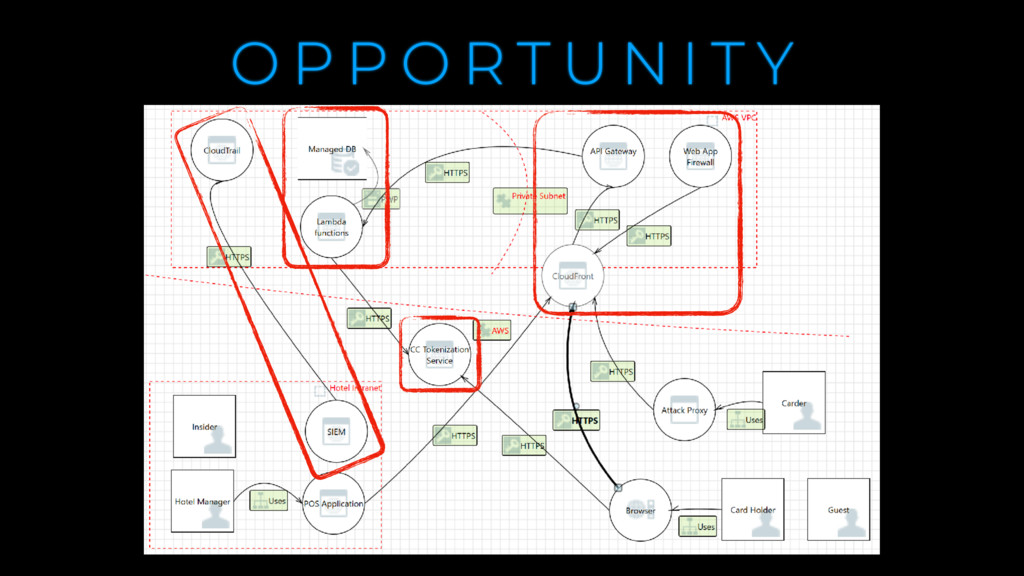
    Y Security f rom First Principles Am I taking advantage of my environment? https://commons.wikimedia.org/wiki/File:Amazing_Bhutan_Monastery.jpg Craig Jackson, Scott Russell, and Susan Sons
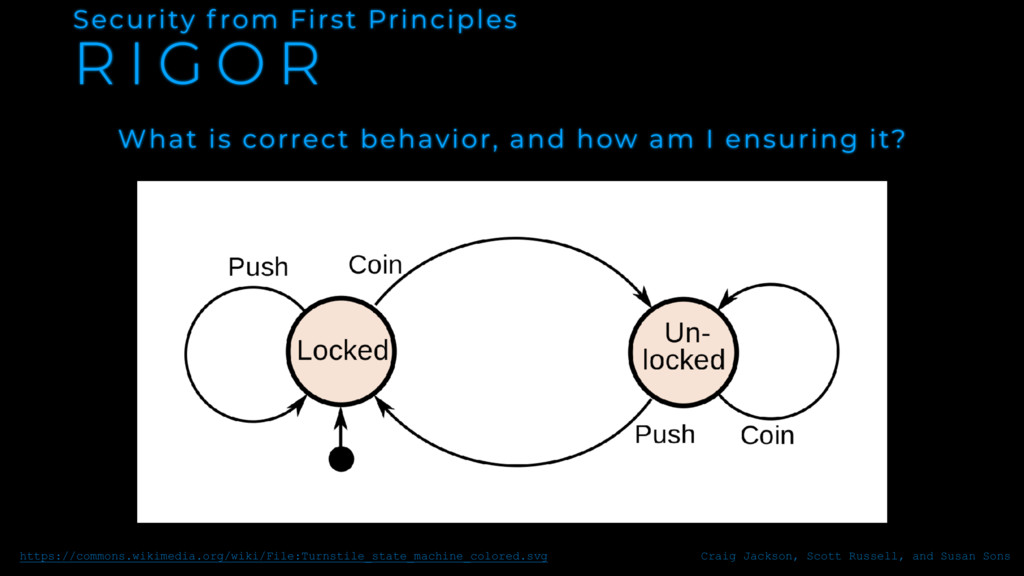
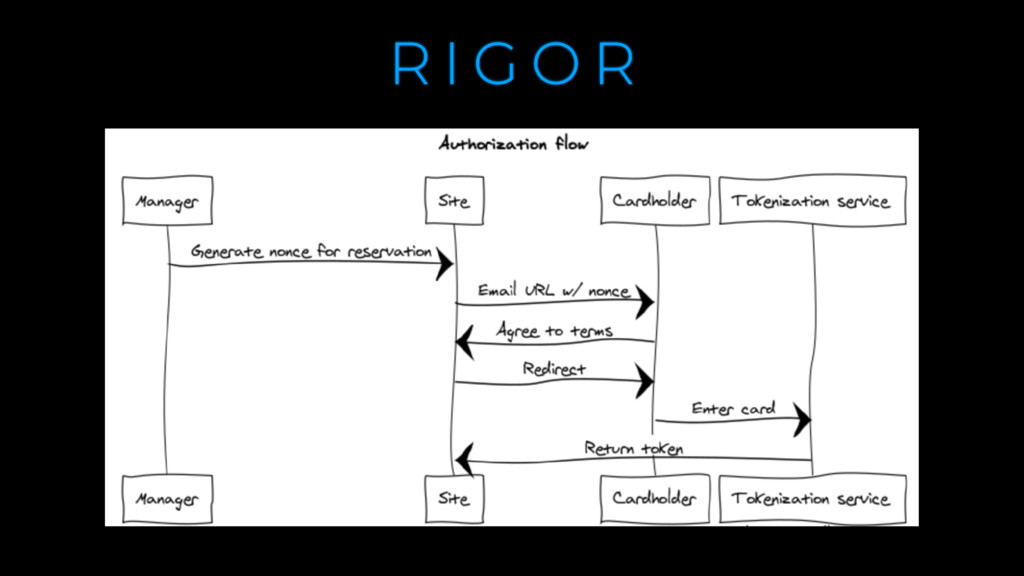
  38. R I G O R Security f rom First Principles

    What is correct behavior, and how am I ensuring it? https://commons.wikimedia.org/wiki/File:Turnstile_state_machine_colored.svg Craig Jackson, Scott Russell, and Susan Sons
  39. M I N I M I Z A T I

    O N Security f rom First Principles Can this be a smaller target? Craig Jackson, Scott Russell, and Susan Sons
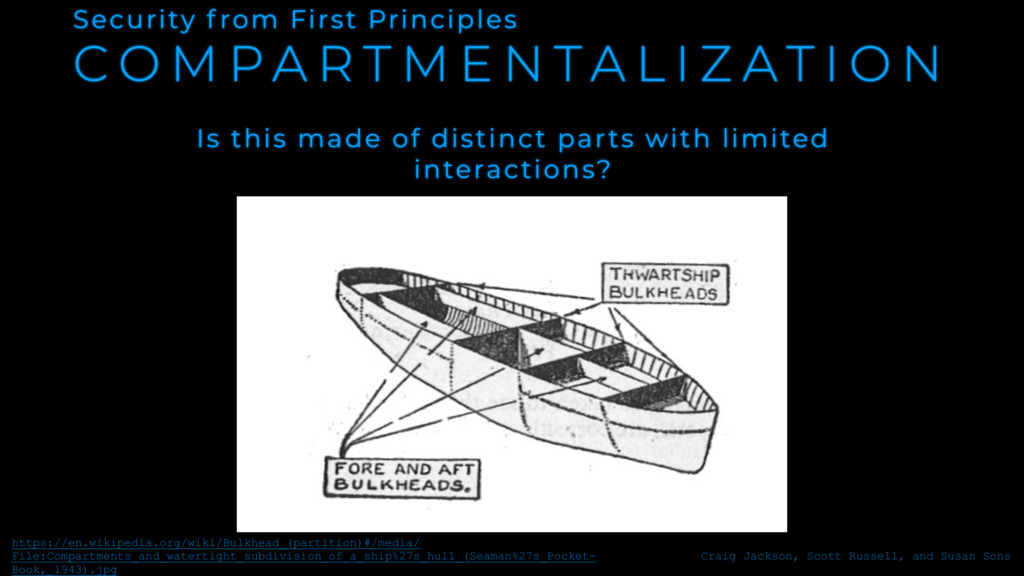
  40. C O M P A R T M E N

    T A L I Z A T I O N Security f rom First Principles Is this made of distinct parts with limited interactions? https://en.wikipedia.org/wiki/Bulkhead_(partition)#/media/ File:Compartments_and_watertight_subdivision_of_a_ship%27s_hull_(Seaman%27s_Pocket- Book,_1943).jpg Craig Jackson, Scott Russell, and Susan Sons
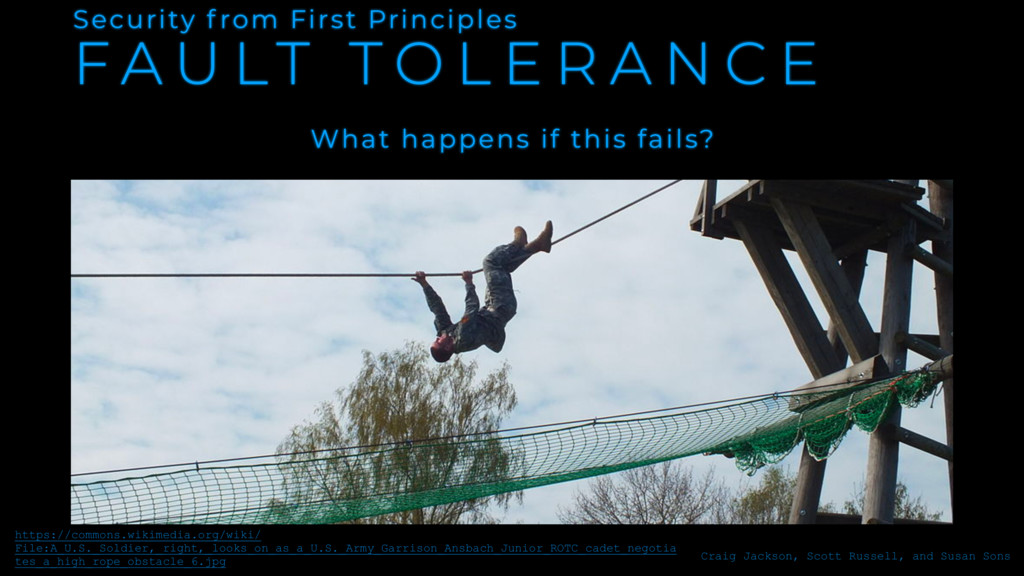
  41. F A U LT T O L E R A

    N C E Security f rom First Principles What happens if this fails? https://commons.wikimedia.org/wiki/ File:A_U.S._Soldier,_right,_looks_on_as_a_U.S._Army_Garrison_Ansbach_Junior_ROTC_cadet_negotia tes_a_high_rope_obstacle_6.jpg Craig Jackson, Scott Russell, and Susan Sons
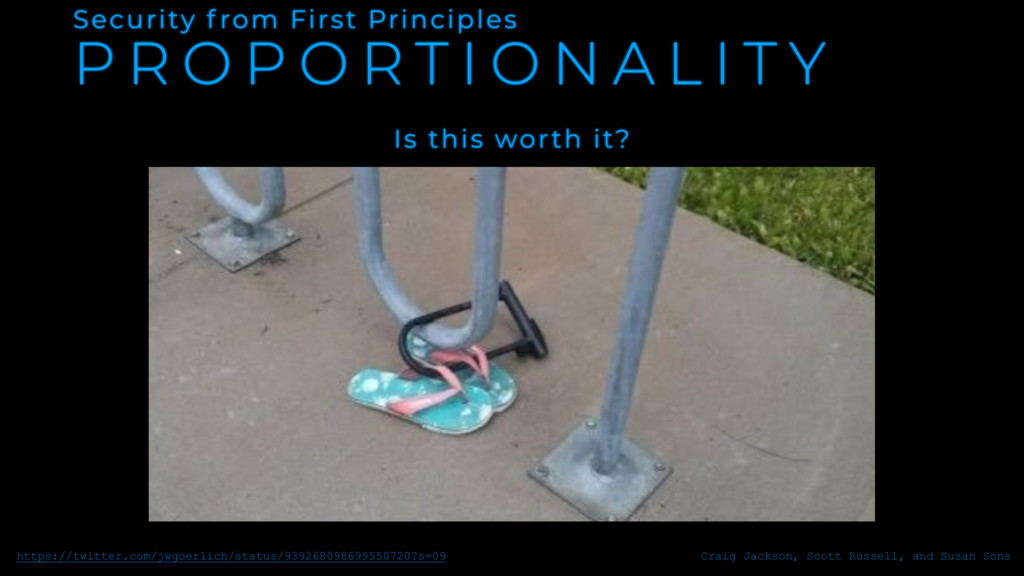
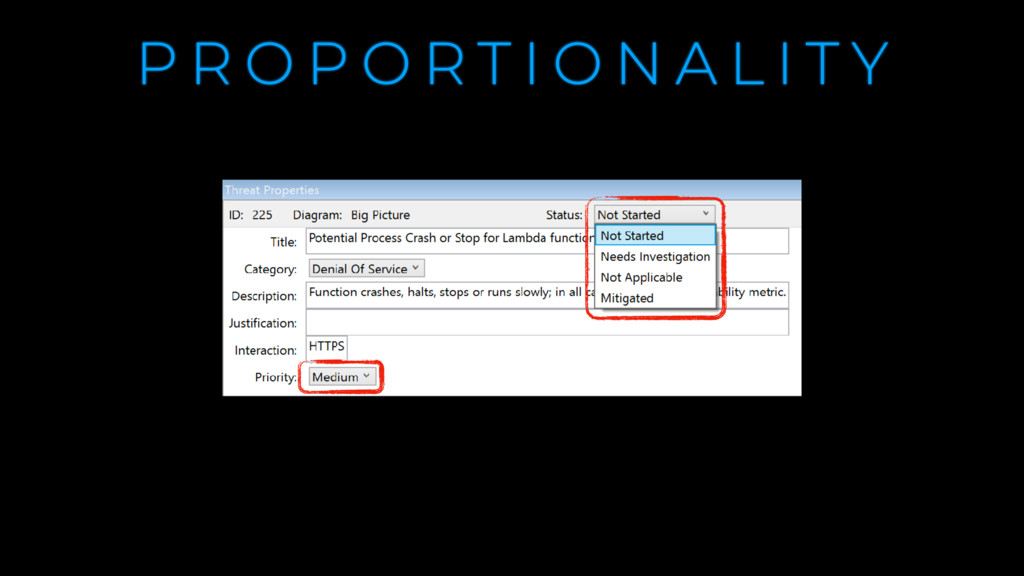
  42. P R O P O R T I O N

    A L I T Y Security f rom First Principles Is this worth it? https://twitter.com/jwgoerlich/status/939268098699550720?s=09 Craig Jackson, Scott Russell, and Susan Sons
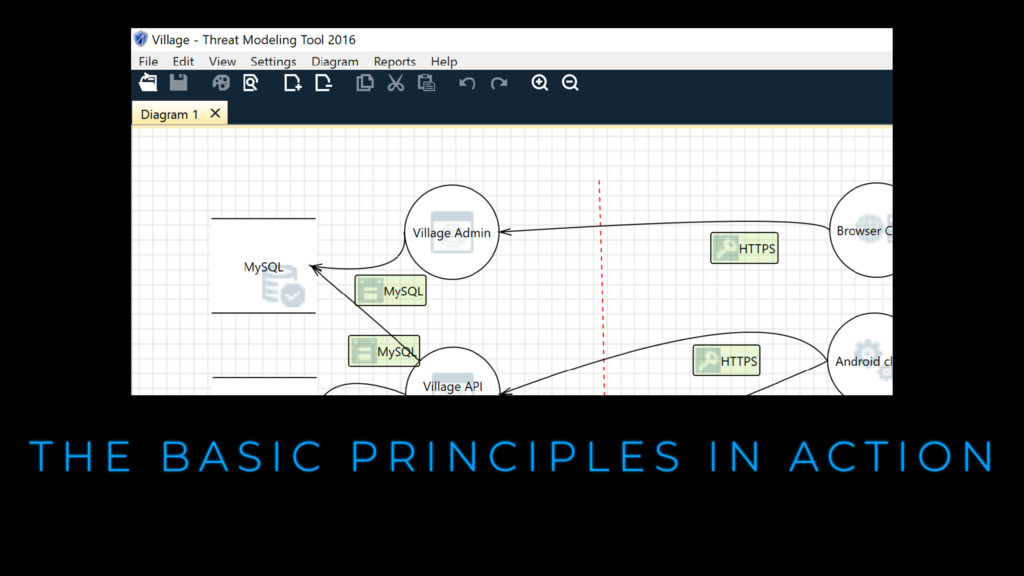
  43. T H E B A S I C P R

    I N C I P L E S I N A C T I O N
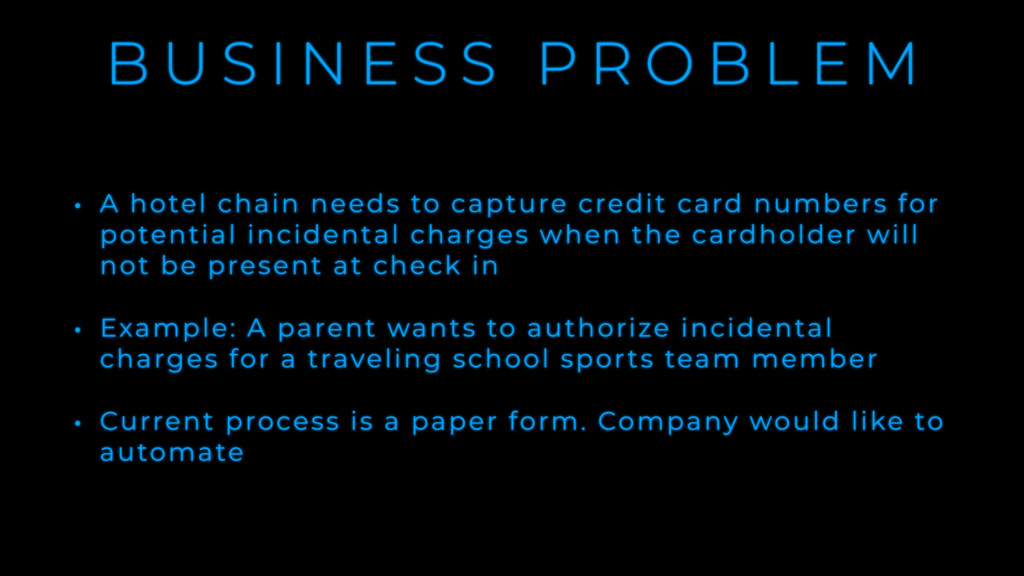
  44. B U S I N E S S P R

    O B L E M • A hotel chain needs to capture credit card numbers for potential incidental charges when the cardholder will not be present at check in • Example: A parent wants to authorize incidental charges for a traveling school sports team member • Current process is a paper form. Company would like to automate
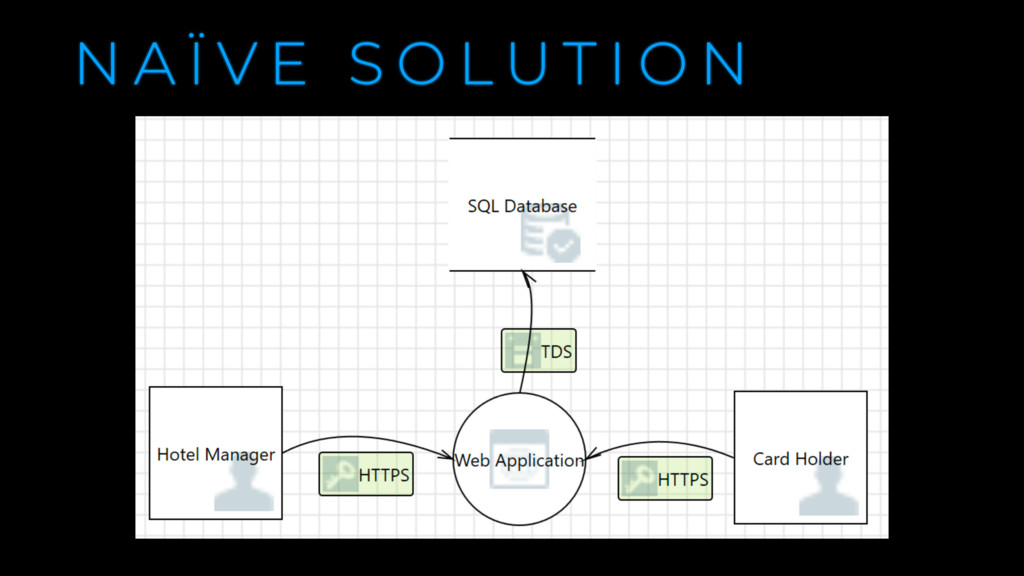
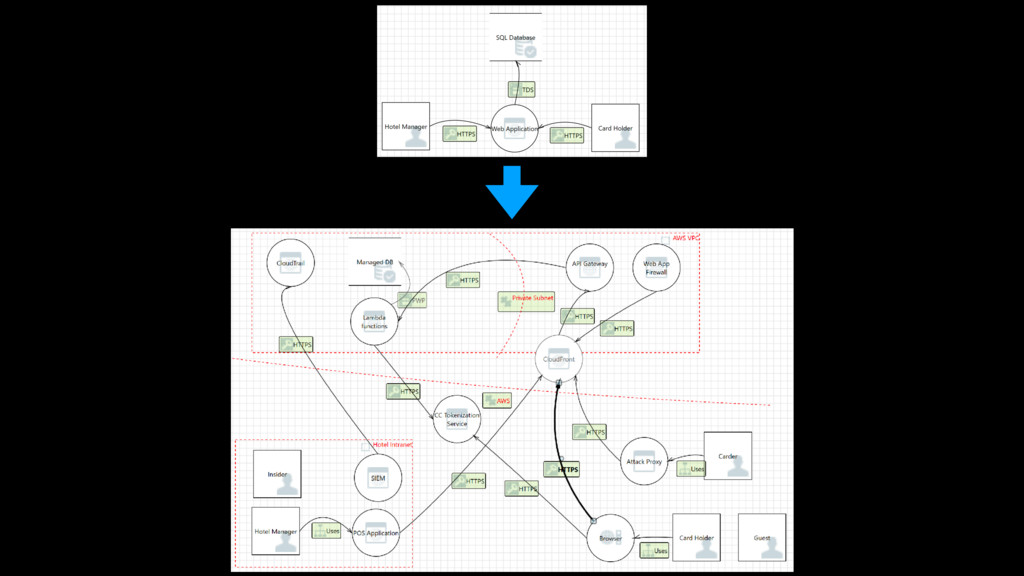
  45. N A Ï V E S O L U T

    I O N “Type a quote here.”
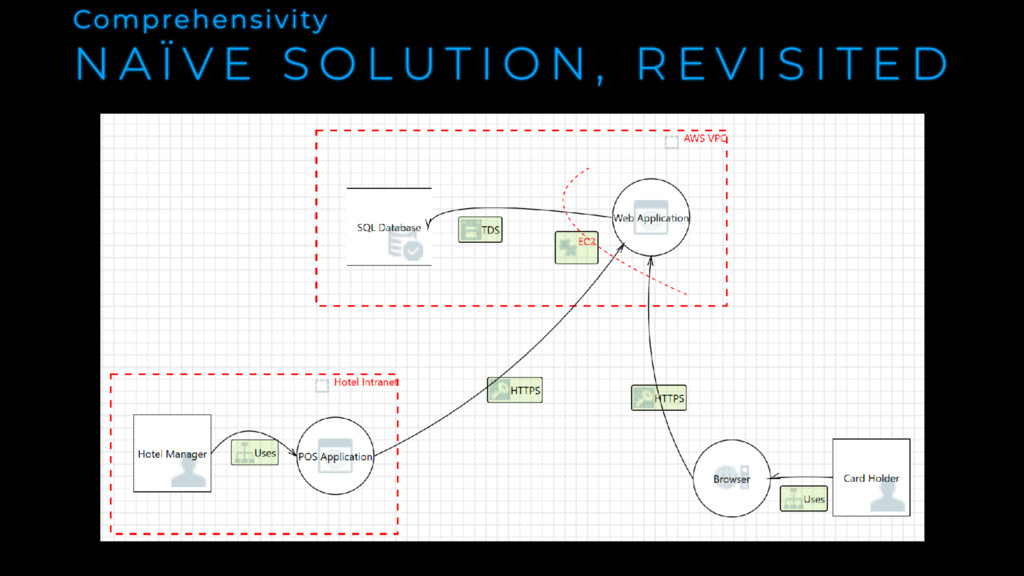
  46. N A Ï V E S O L U T

    I O N , R E V I S I T E D Comprehensivity “Type a quote here.”
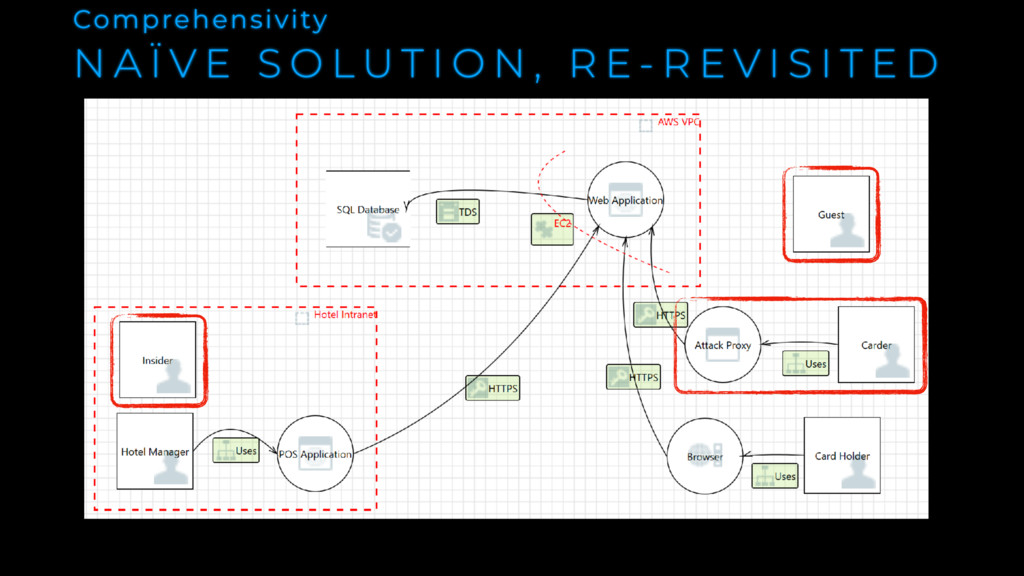
  47. N A Ï V E S O L U T

    I O N , R E - R E V I S I T E D Comprehensivity “Type a quote here.”
  48. N A Ï V E S O L U T

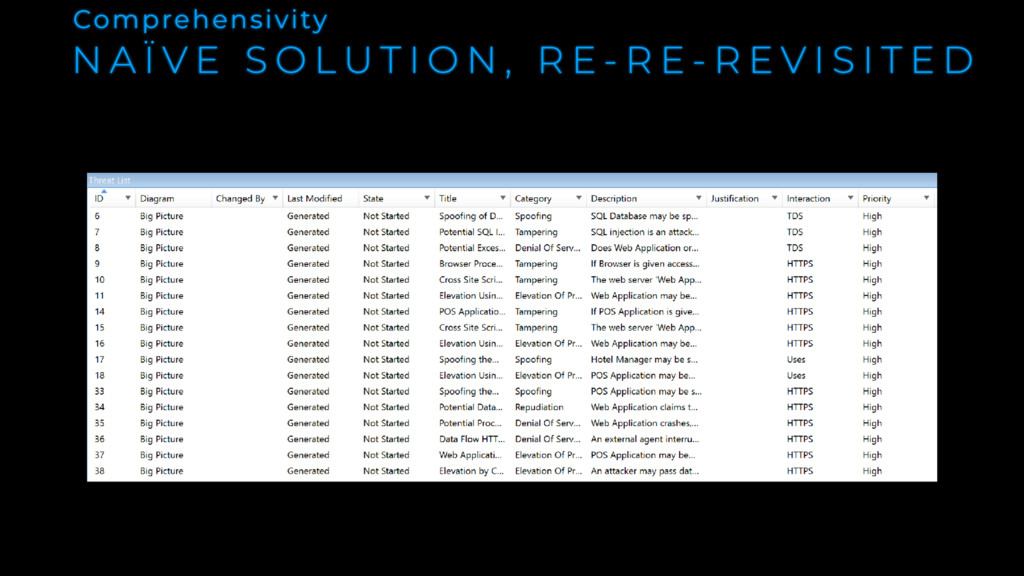
    I O N , R E - R E - R E V I S I T E D Comprehensivity “Type a quote here.”
  49. D E S I G N E D I N

    T O P R O C E S S Comprehensivity https://jeremylong.github.io/DependencyCheck/
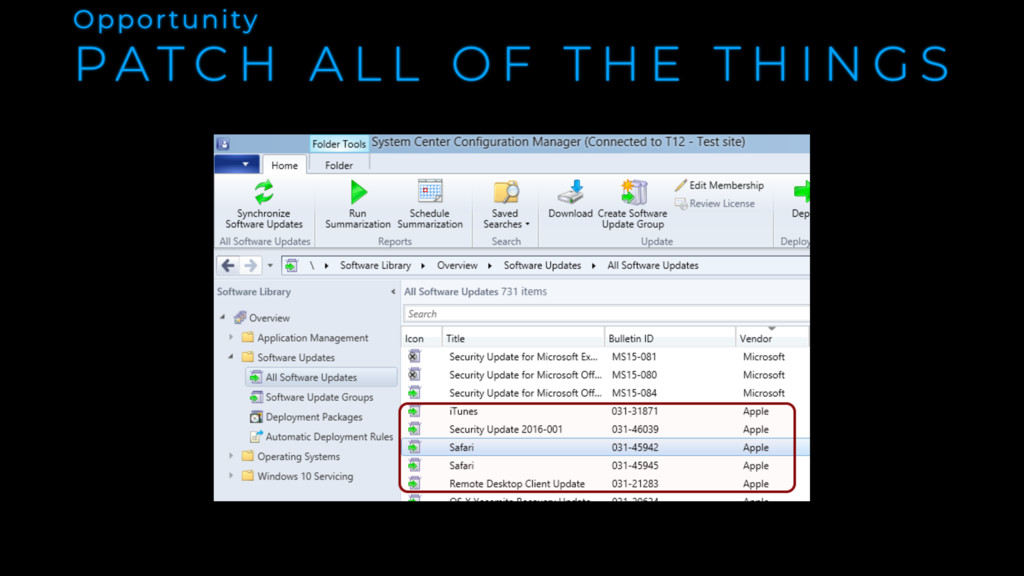
  50. P A T C H A L L O F

    T H E T H I N G S Opportunity “Type a quote here.”
  51. S T A T I C A N A LY

    S I S Rigor “The most important thing I have done as a programmer in recent years is to aggressively pursue static code analysis. Even more valuable than the hundreds of serious bugs I have prevented with it is the change in mindset about the way I view software reliability and code quality.” - J o h n C a r m a c k https://www.gamasutra.com/view/news/128836/InDepth_Static_Code_Analysis.php
  52. M I N I M I Z E A T

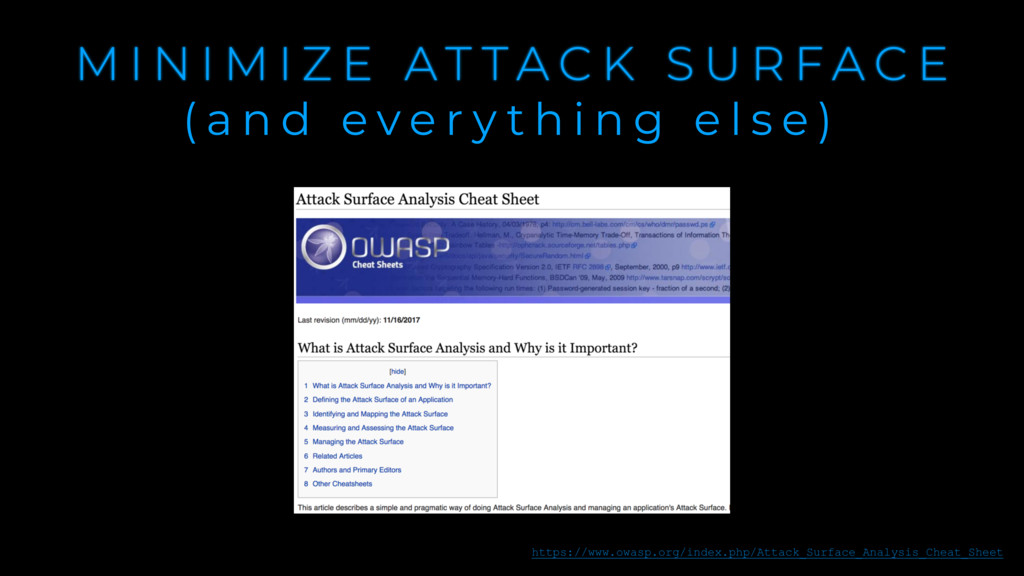
    T A C K S U R F A C E ( a n d e v e r y t h i n g e l s e ) https://www.owasp.org/index.php/Attack_Surface_Analysis_Cheat_Sheet
  53. S T O R E L E S S Minimization

    “Limit cardholder data storage and retention time to that which is required for business, legal, and/ or regulatory purposes, as documented in your data retention policy. Purge unnecessary stored data at least quarterly.” P C I - D S S § 3 . 1 https://www.pcisecuritystandards.org/documents/PCIDSS_QRGv3_1.pdf
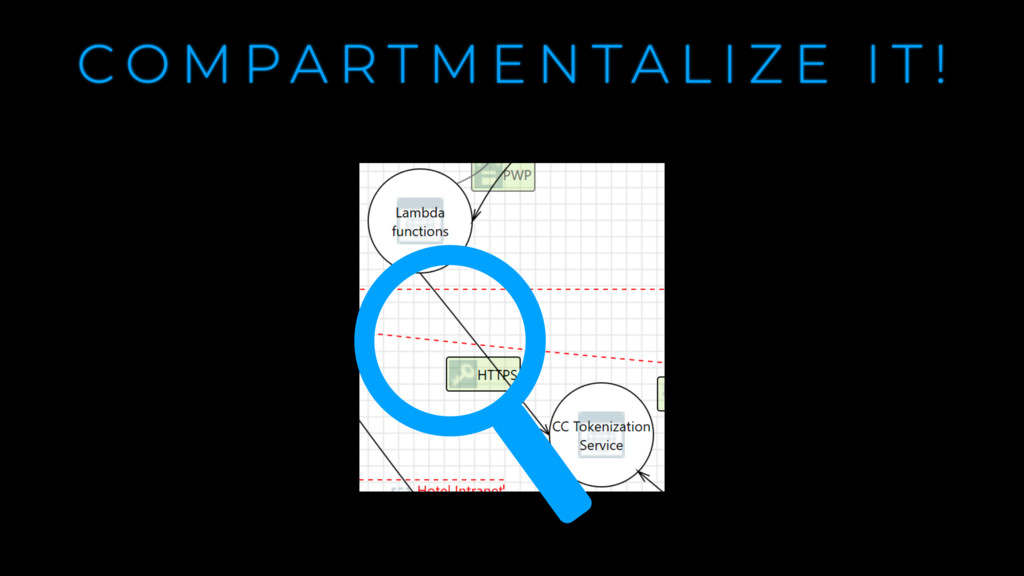
  54. C O M P A R T M E N

    T A L I Z E I T !
  55. D O U B L E E D G E

    D S W O R D Compartmentalization ““Your perimeter is not the boundary of your network it’s the boundary of your telemetry.” http://grugq.github.io/presentations/comae-blackhat-year-of-the-worm.pdf - T h e G r u g q
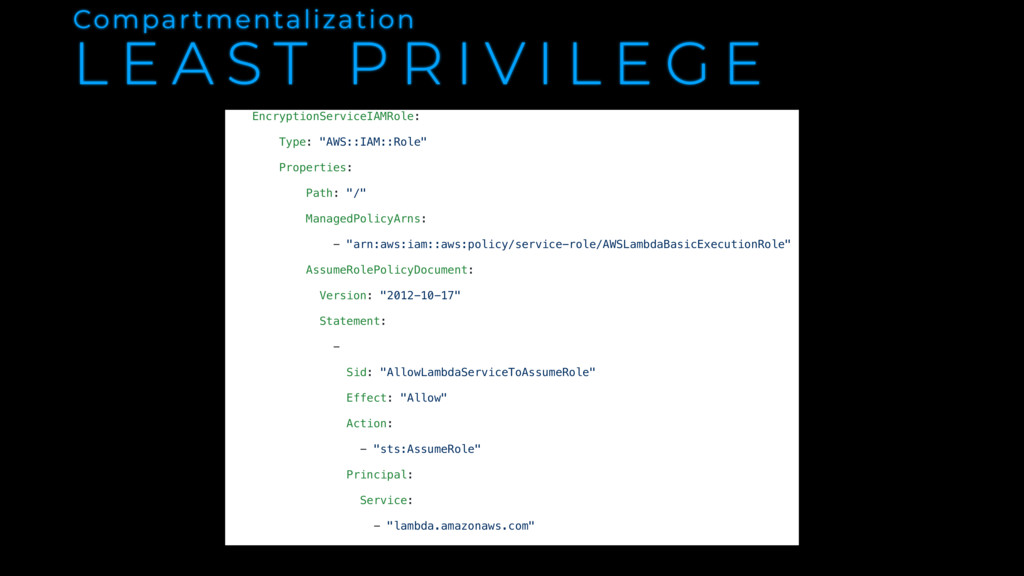
  56. L E A S T P R I V I

    L E G E Compartmentalization EncryptionServiceIAMRole: Type: "AWS::IAM::Role" Properties: Path: "/" ManagedPolicyArns: - "arn:aws:iam::aws:policy/service-role/AWSLambdaBasicExecutionRole" AssumeRolePolicyDocument: Version: "2012-10-17" Statement: - Sid: "AllowLambdaServiceToAssumeRole" Effect: "Allow" Action: - "sts:AssumeRole" Principal: Service: - "lambda.amazonaws.com"
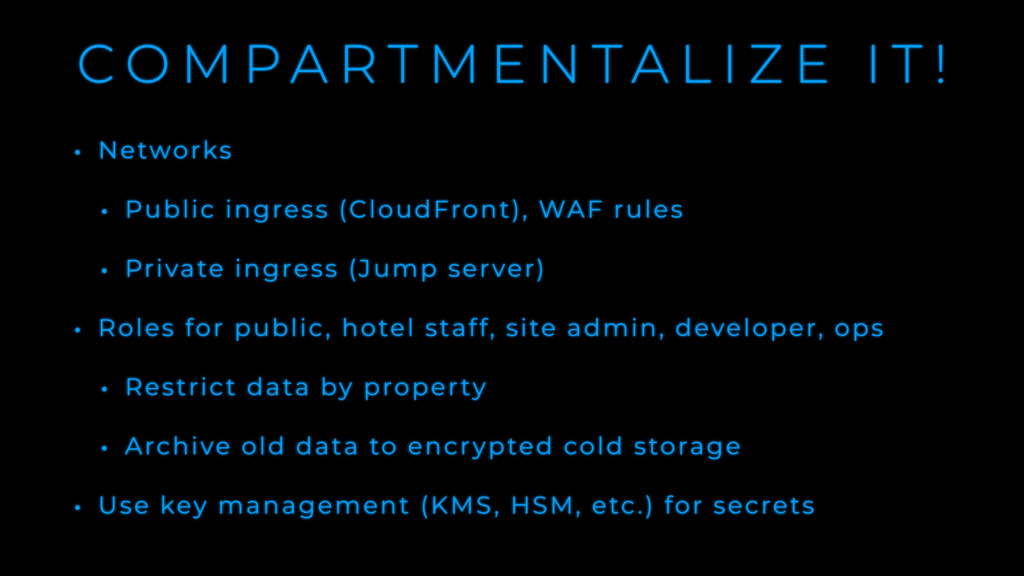
  57. C O M P A R T M E N

    T A L I Z E I T ! • Networks • Public ingress (CloudFront), WAF rules • Private ingress (Jump server) • Roles for public, hotel staff, site admin, developer, ops • Restrict data by property • Archive old data to encrypted cold storage • Use key management (KMS, HSM, etc.) for secrets
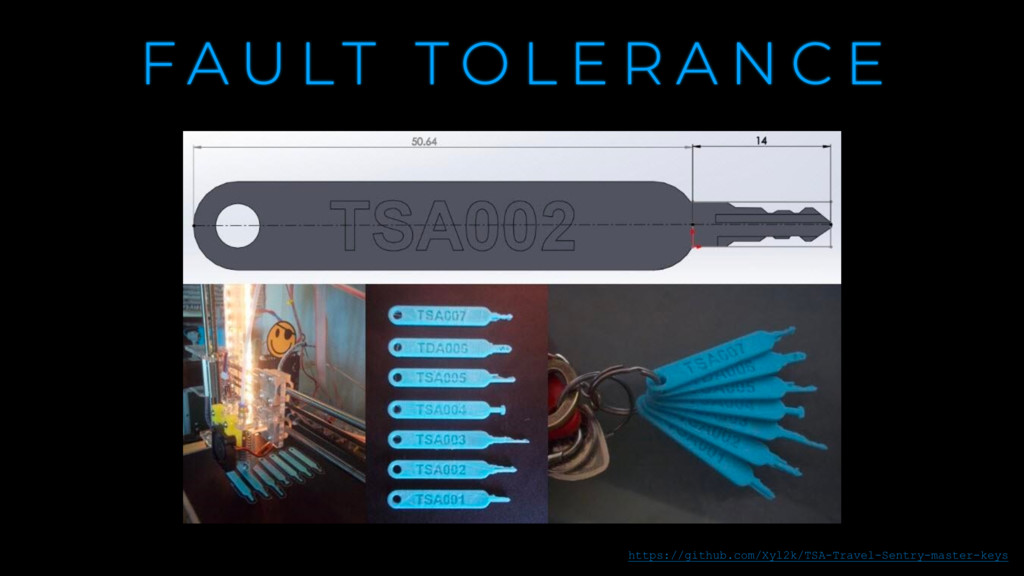
  58. F A U LT T O L E R A

    N C E https://github.com/Xyl2k/TSA-Travel-Sentry-master-keys
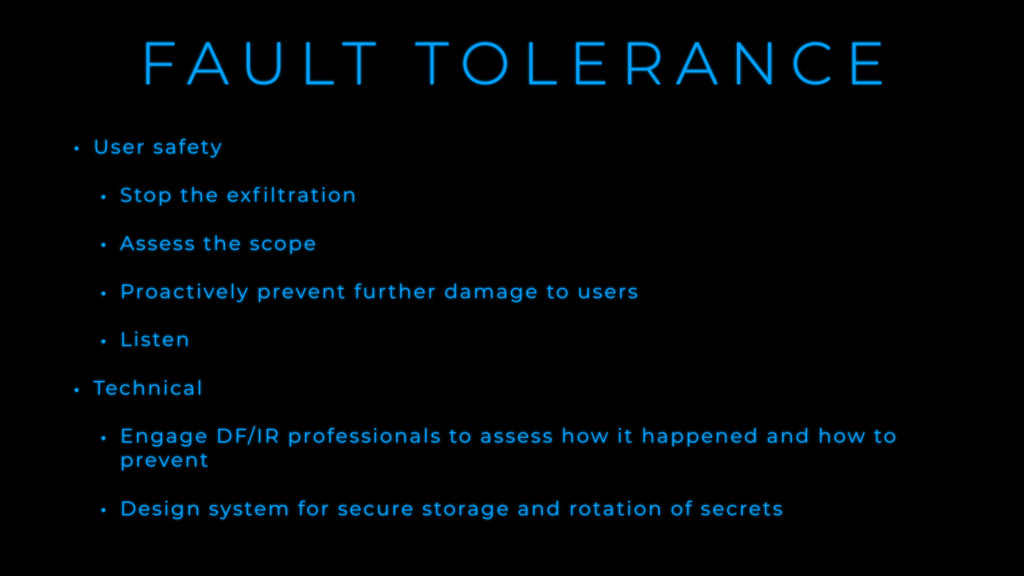
  59. F A U LT T O L E R A

    N C E • User safety • Stop the exf iltration • Assess the scope • Proactively prevent further damage to users • Listen • Technical • Engage DF/IR professionals to assess how it happened and how to prevent • Design system for secure storage and rotation of secrets
  60. L A T H E R , R I N

    S E , R E P E A T • Plan on enumerating the f irst principles at least twice in initial app design • Enumerate again in sprint planning for each sprint • Following f irst principles does not mean “big design upf ront”
  61. F U R T H E R R E A

    D I N G • The Information Security Practice Principles, Center for Applied Cybersecurity Research, Indiana University • Threat Modeling, Designing for Security, by Adam Shostack
  62. C R E D I T S • Some stock

    photography f rom wocintechchat.com, CC- BY 2.0 • Creative Commons photography credited on each slide

More Decks by Craig Stuntz

Other Decks in Programming