Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Mozilla Observatory First Draft
Search
luke crouch
March 15, 2021
Technology
160
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Mozilla Observatory First Draft
luke crouch
March 15, 2021
Transcript
140 slides
Luke Crouch For learning and doing web app security
Me Luke Crouch • Privacy & Security Engineer, Mozilla •
Board member, Techlahoma Foundation • I’ve had 4 cups of coffee already ☕ ☕ ☕ ☕
This talk • 112 slides in ~15m • Mozilla Observatory
• Website • Command-line tool • API • Questions
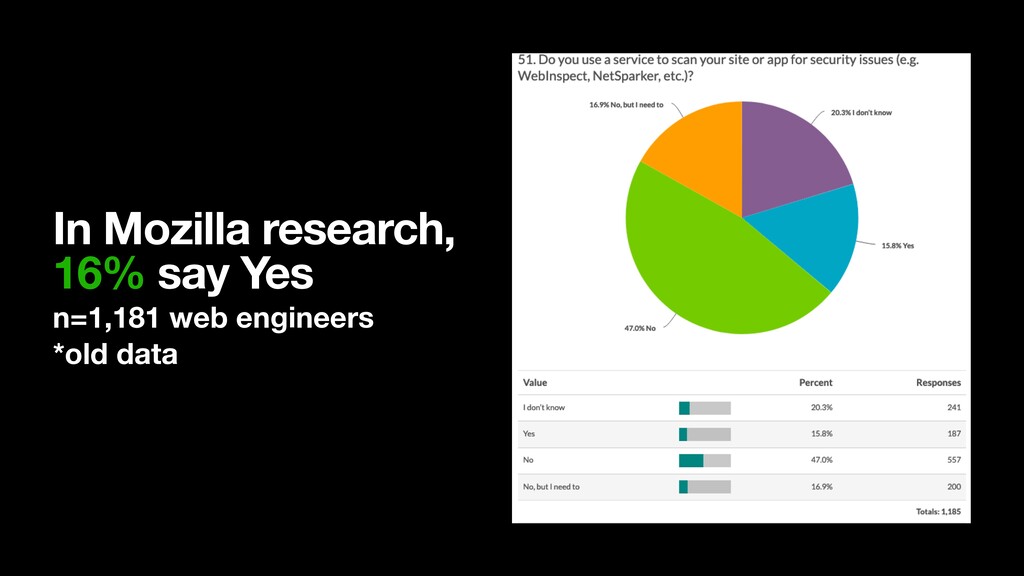
How many of you use a tool to scan your
web site or app for security issues? 🙋
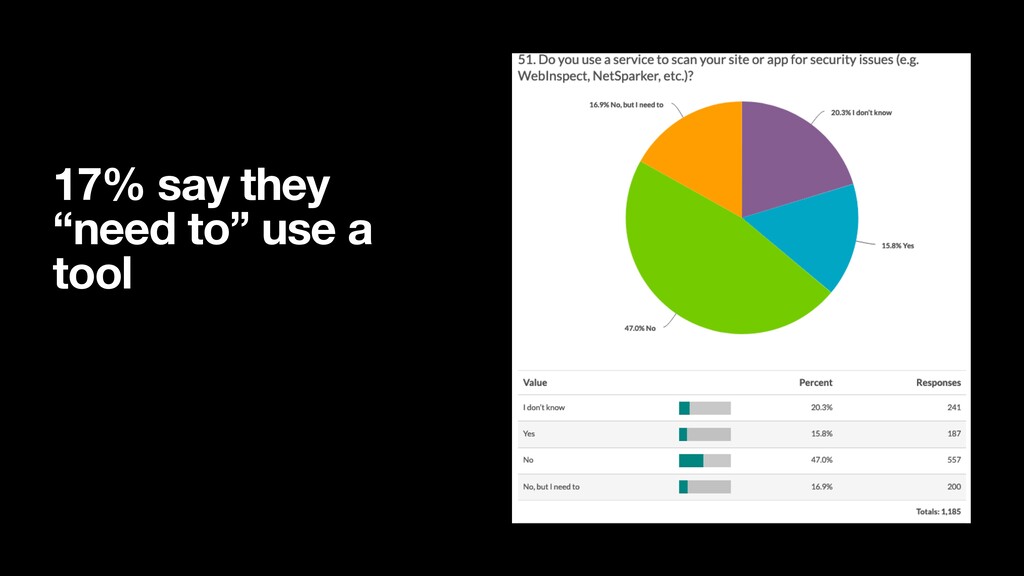
In Mozilla research, 16% say Yes n=1,181 web engineers *old
data
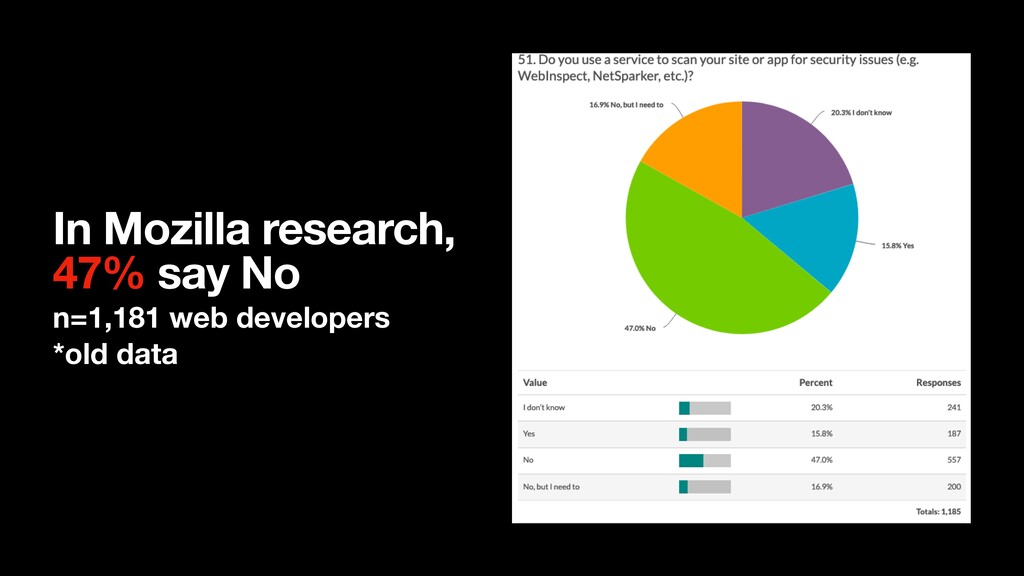
In Mozilla research, 47% say No n=1,181 web developers *old
data
Why don’t you use something to scan your web site
or app?
40% say: I don’t need it
Can’t have security vulnerabilities … … if you don’t know
about your security vulnerabilities.
17% say they “need to” use a tool
THANK YOU!
Because even if your app or site may not seem
like a target …
Your users may be re-using their password …
• their bank • their PayPal • their workplace •
their healthcare provider • their password manager (!) • their computer • etc. • their email • which gives an attacker access to all of those others!
So if your app is hacked, their other accounts could
get hacked too.
Next (rhetorical) question …
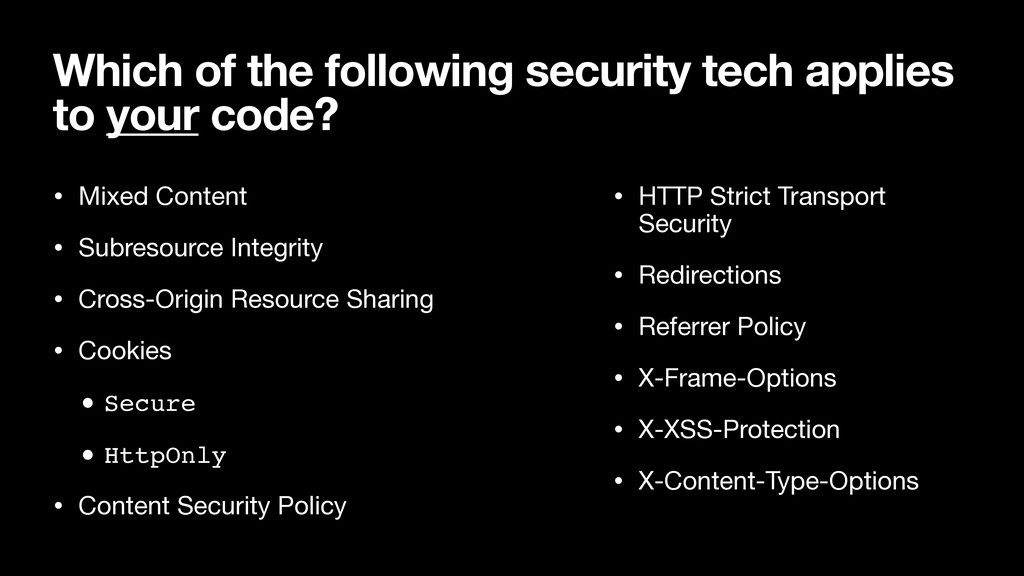
Which of the following security tech applies to your code?
• Mixed Content • Subresource Integrity • Cross-Origin Resource Sharing • Cookies • Secure • HttpOnly • Content Security Policy • HTTP Strict Transport Security • Redirections • Referrer Policy • X-Frame-Options • X-XSS-Protection • X-Content-Type-Options
🤷🤷
Which of the following security tech applies to your code?
• Mixed Content • Subresource Integrity • Cross-Origin Resource Sharing • Cookies • Secure • HttpOnly • Content Security Policy • HTTP Strict Transport Security • Redirections • Referrer Policy • X-Frame-Options • X-XSS-Protection • X-Content-Type-Options
How do you know what you need to know?
Luke Crouch For learning and doing web app security
None
None
None
None
None
None
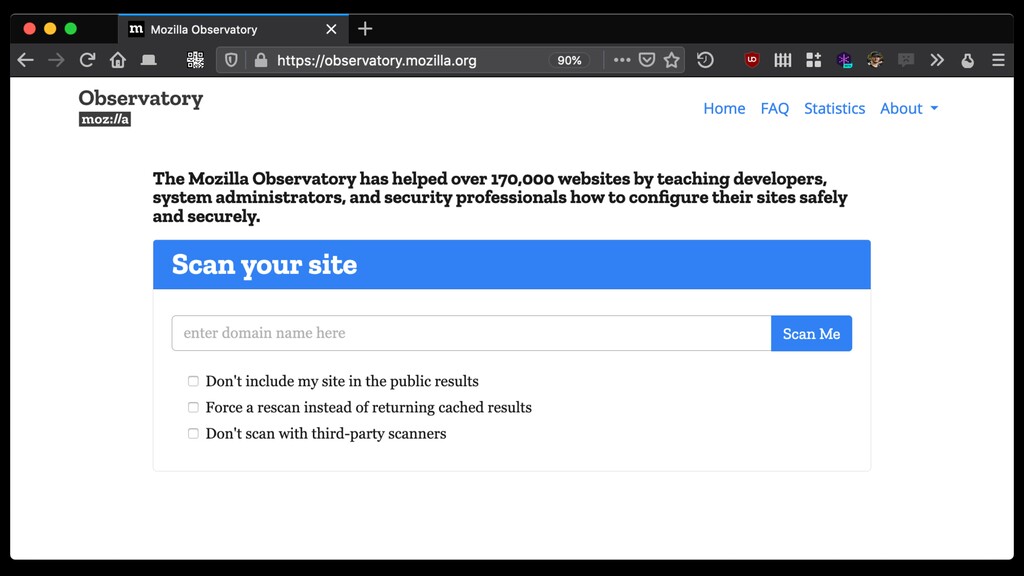
Observatory helps me focus on learning the most important security
for my code right now.
Because the reason most of us don’t do all this
… • Mixed Content • Subresource Integrity • Cross-Origin Resource Sharing • Cookies • Secure • HttpOnly • Content Security Policy • HTTP Strict Transport Security • Redirections • Referrer Policy • X-Frame-Options • X-XSS-Protection • X-Content-Type-Options
we don’t have time to do it all.
But, there’s plenty of “quick wins” you can get with
a little bit of time
So, let’s get started …
⚠ Disclaimer: don’t be evil ⚠
You should only use security scanning and testing tools with
permission
So … don’t go scan a bunch of government websites
Now … let’s go scan a bunch of government websites
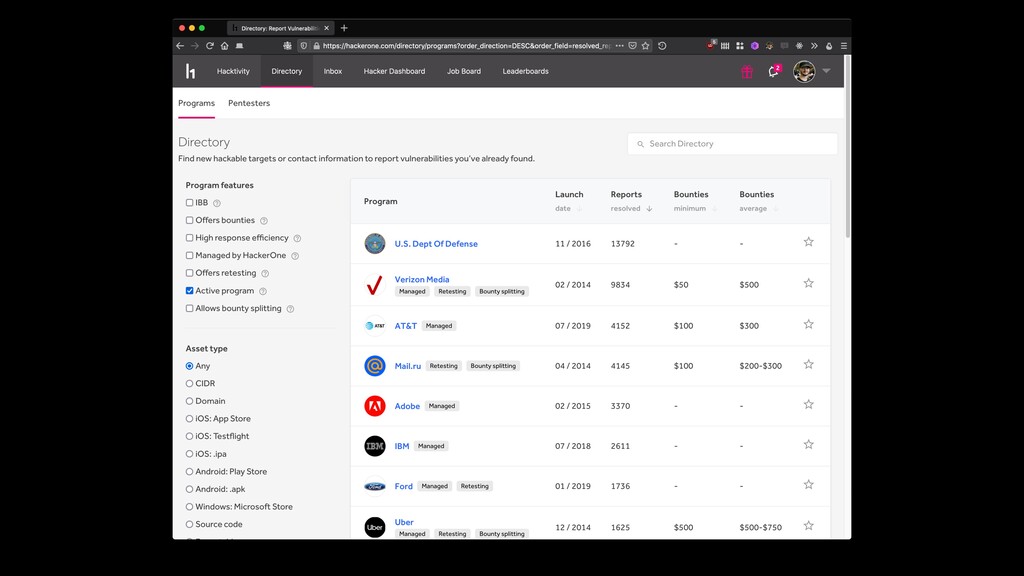
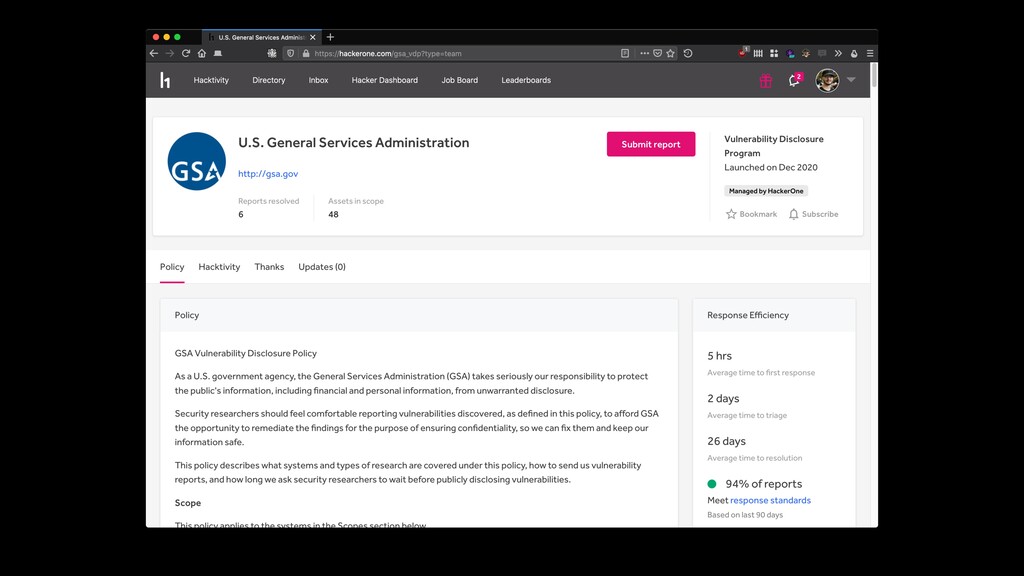
hackerone.com
None
None
None
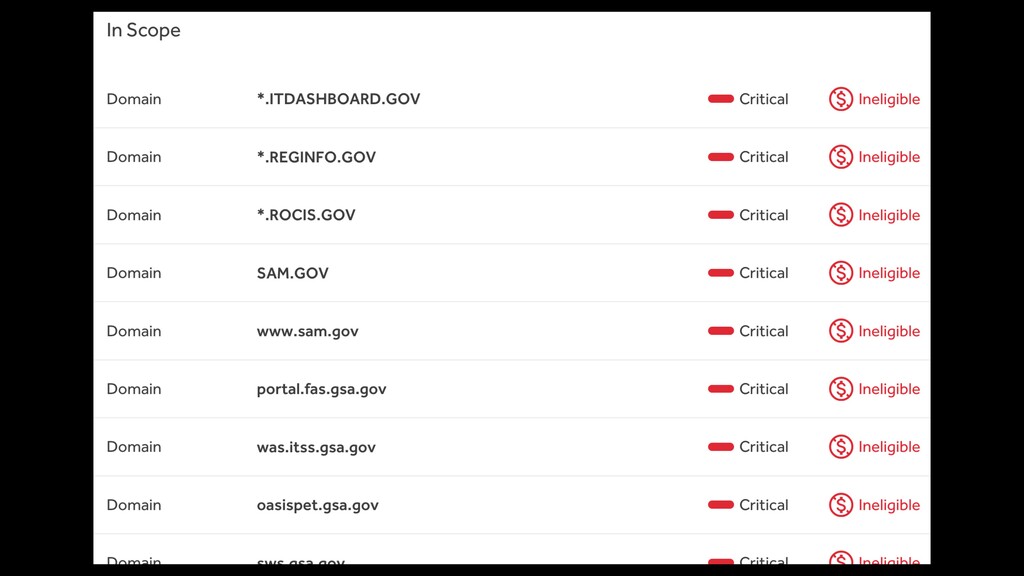
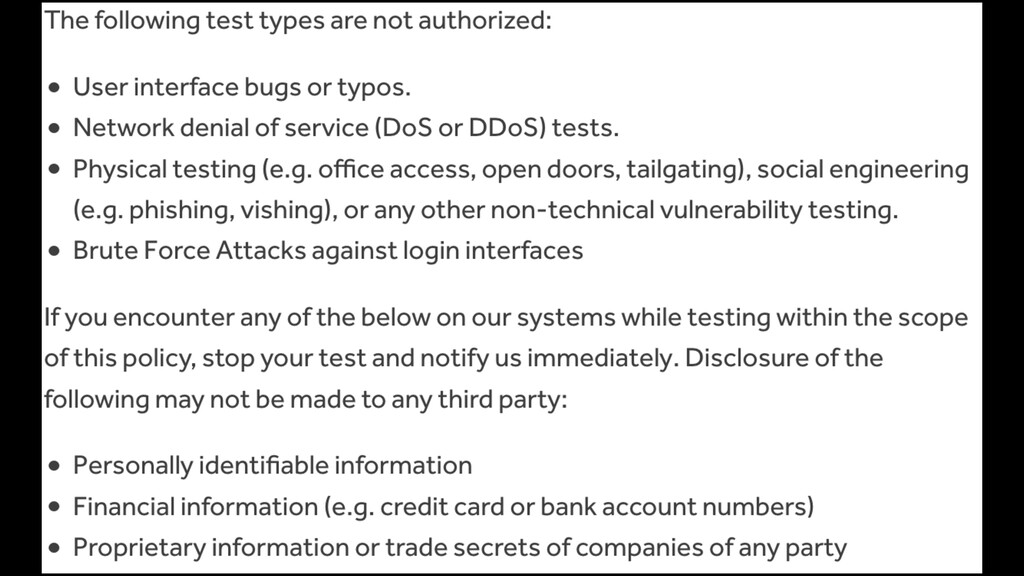
So basically, GSA gives permission to scan some sites, within
certain scope and under certain conditions
None
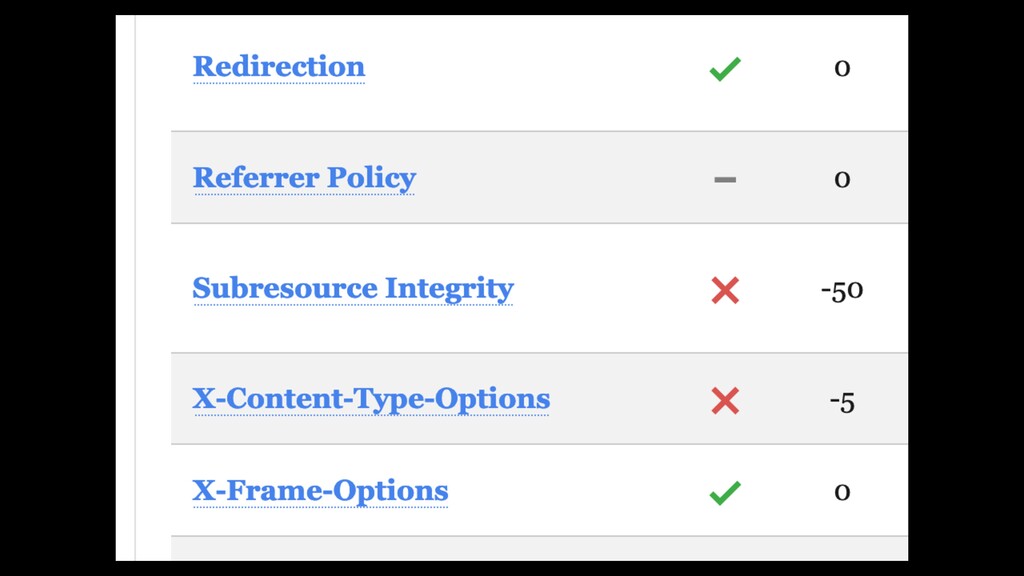
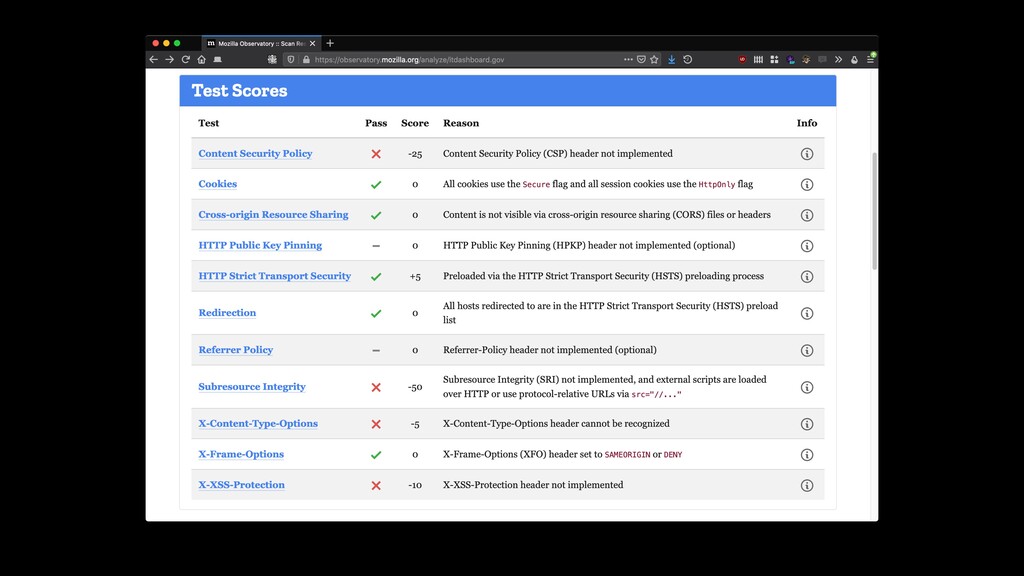
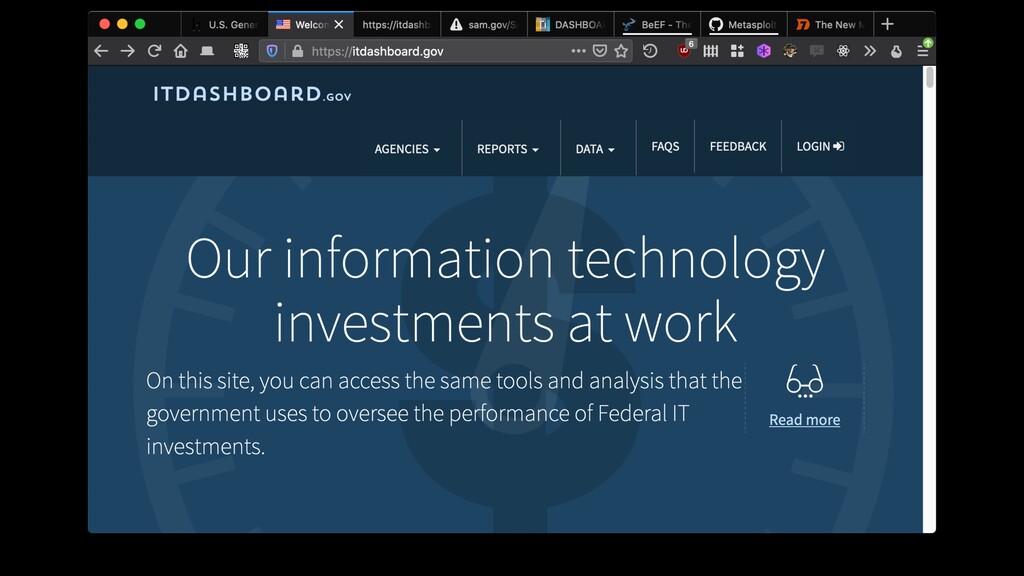
Let’s try the first one on the list: itdashboard.gov
None
None
None
None
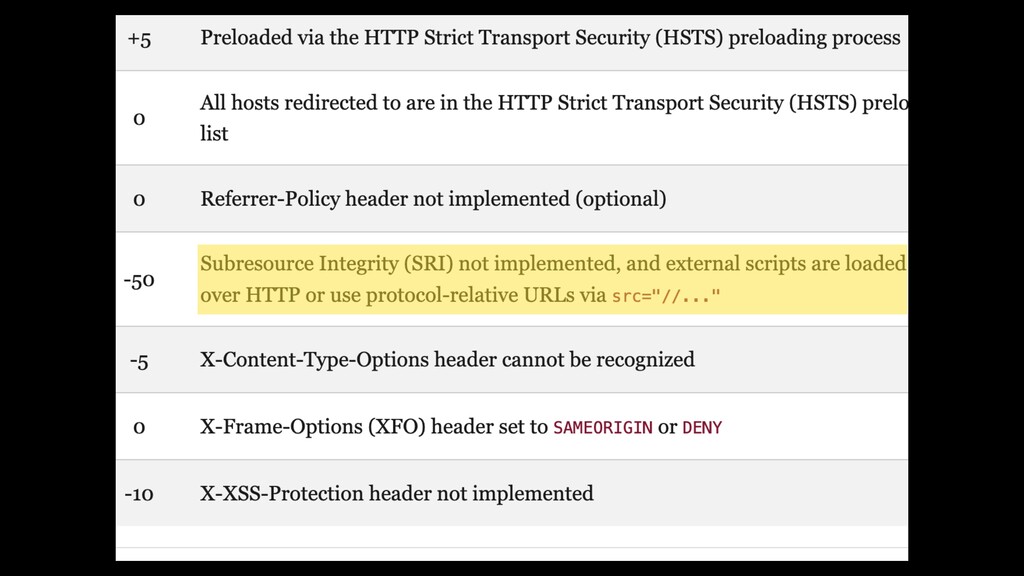
Loading external scripts over (insecure) HTTP - WCGW? 🤷
None
None
https://itdashboard.gov <html> <head> … <script src=“http://ajax.googleapis.com/…”></script> … </head> … </html>
https://itdashboard.gov <script src=“http://ajax.googleapis.com/…”></script> HTTP HTTP
None
None
https://itdashboard.gov <html> <head> … <script src=“http://ajax.googleapis.com/…”></script> … </head> … </html>
None
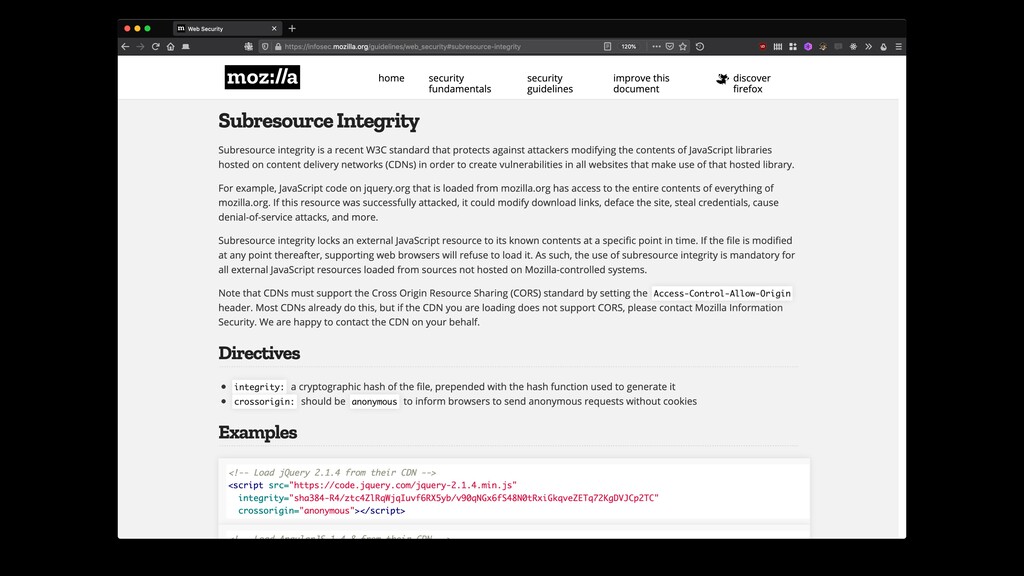
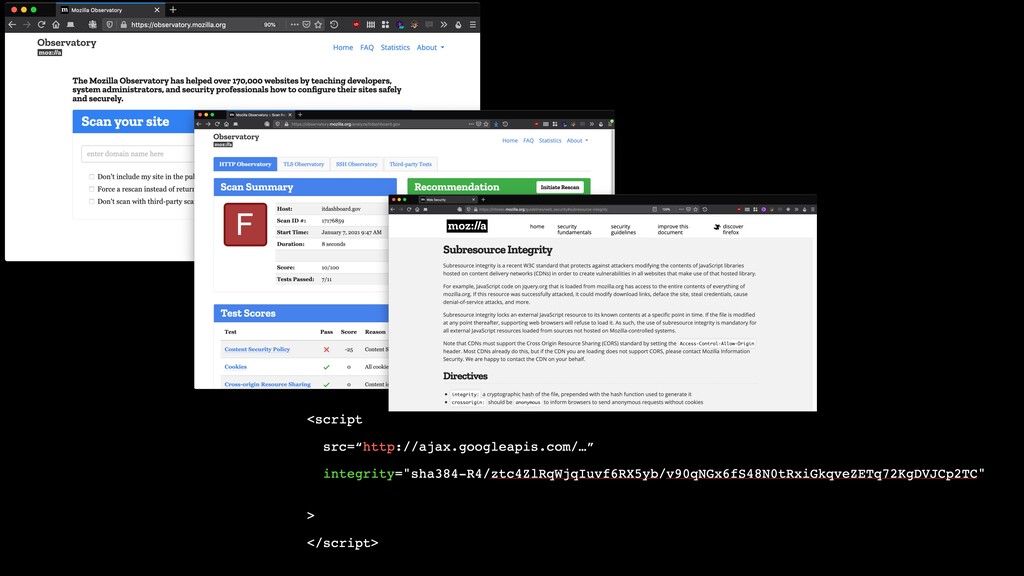
https://itdashboard.gov <html> <head> <script src=“http://ajax.googleapis.com/…” integrity="sha384-R4/ztc4ZlRqWjqIuvf6RX5yb/v90qNGx6fS48N0tRxiGkqveZETq72KgDVJCp2TC" > </script> </head>
</html>
None
None
None
None
None
None
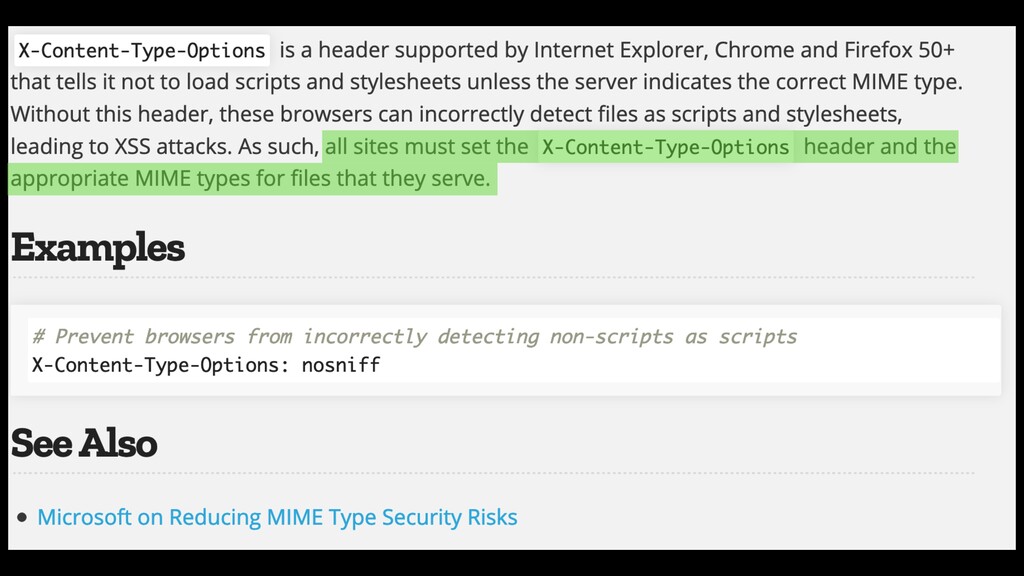
https://www.keycdn.com/support/what-is-mime-sniffing
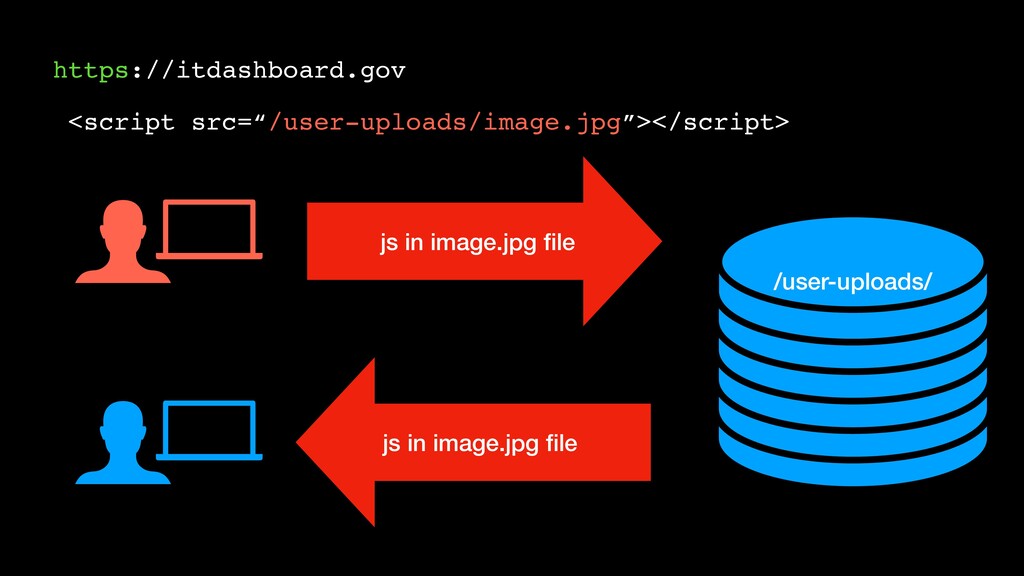
https://itdashboard.gov <script src=“/user-uploads/image.jpg”></script> /user-uploads/ js in image.jpg file js in
image.jpg file
None
Does your server set the right Content-Type for scripts and
styles?
Yes?
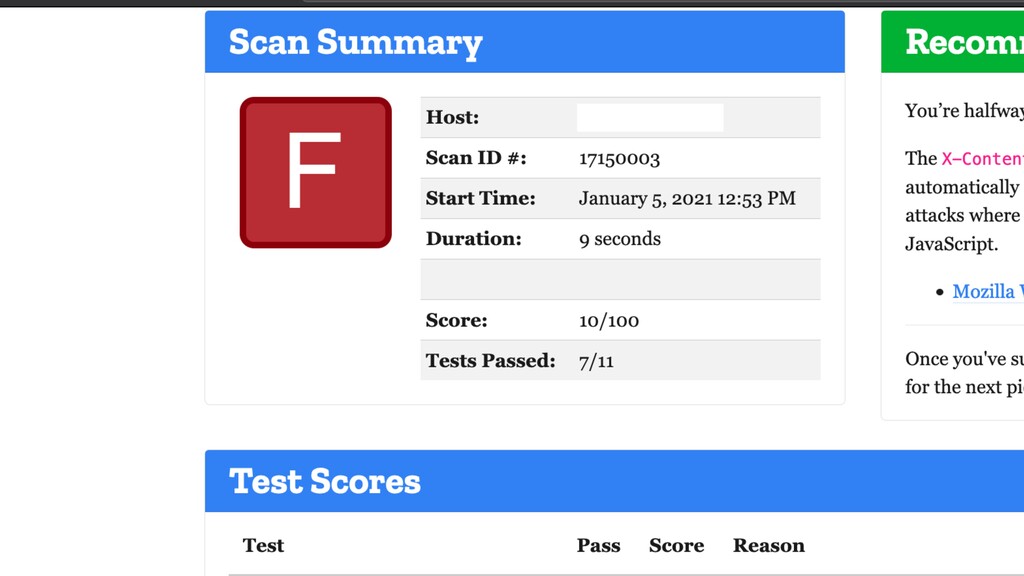
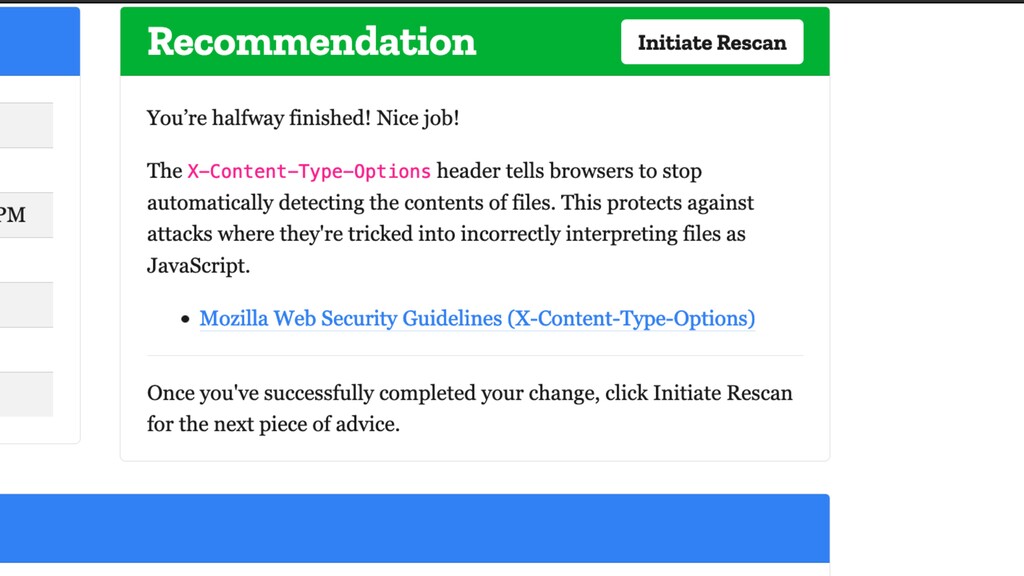
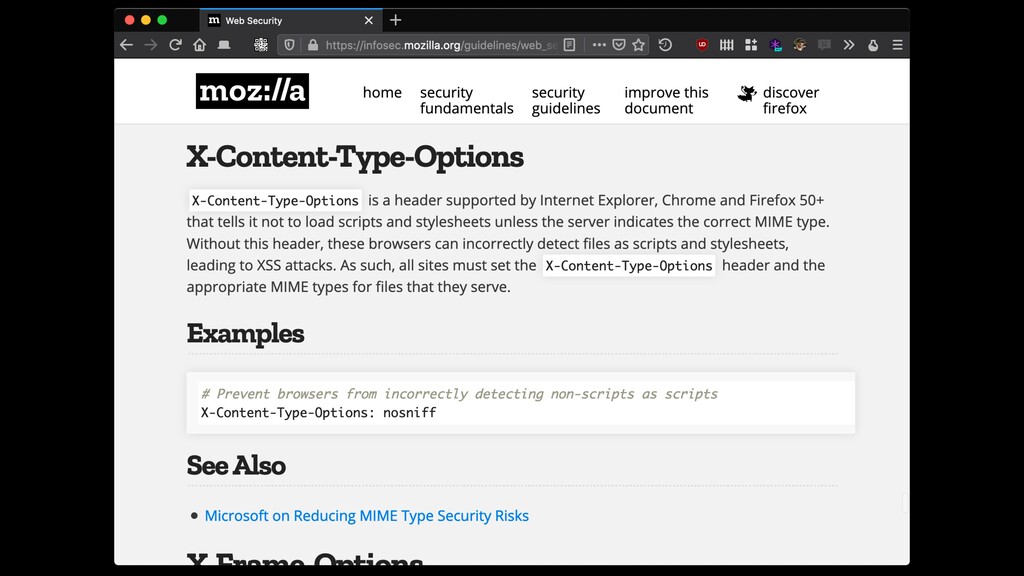
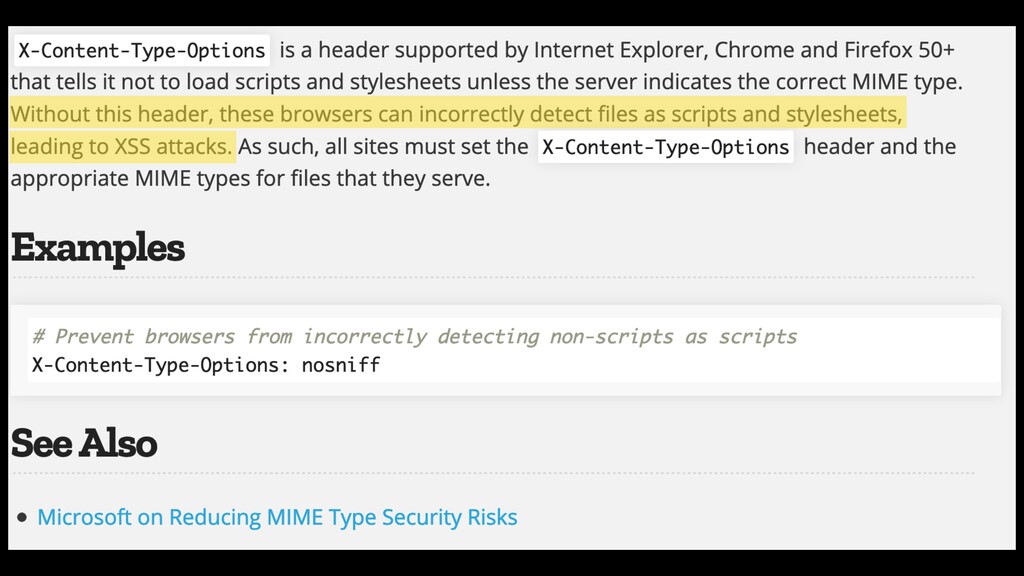
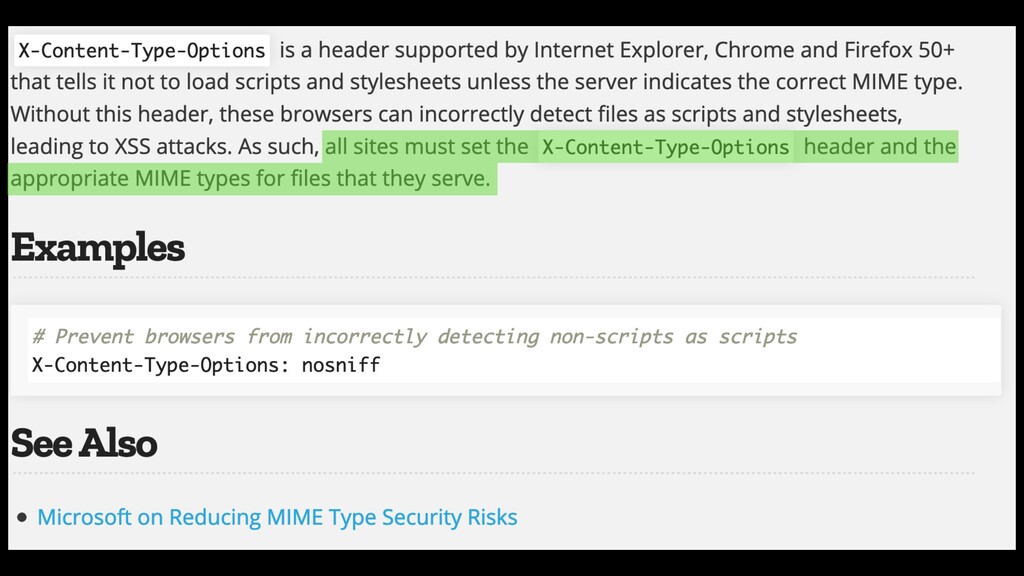
This is “easy” - you can add: X-Content-Type-Options: nosniff across
your entire server.
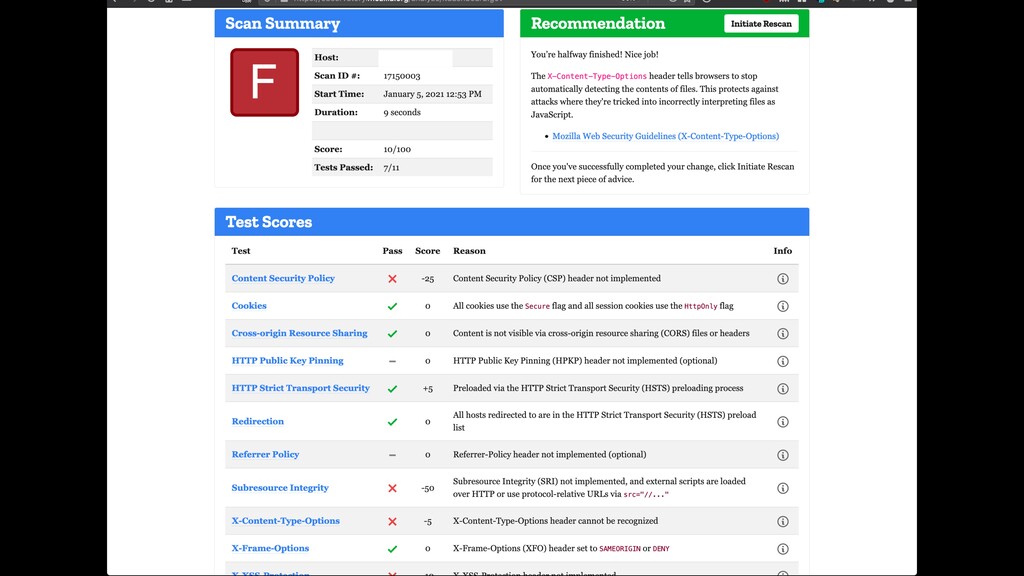
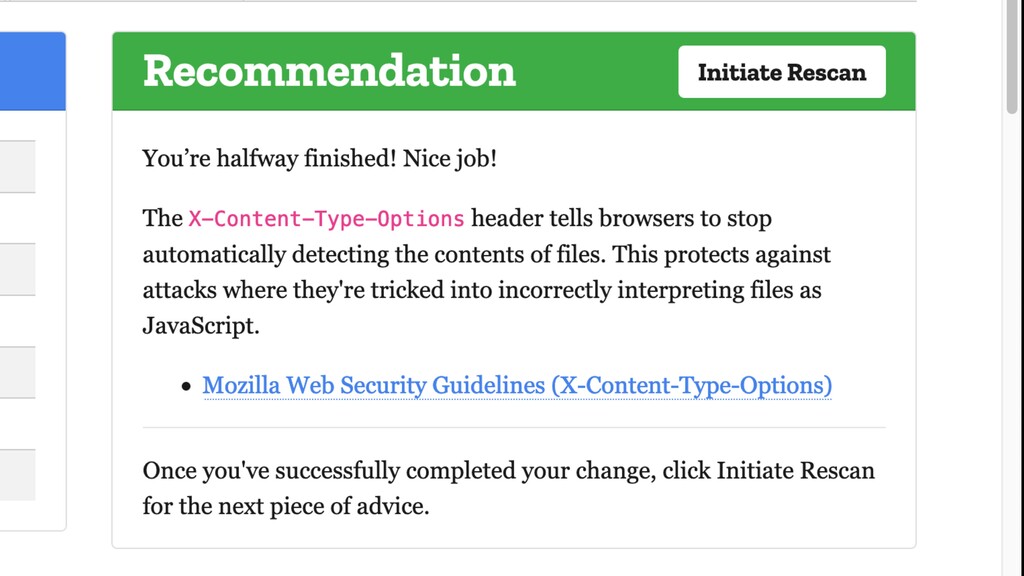
X-Content-Type-Options is the first recommended fix, because it’s easier than
others …
No?
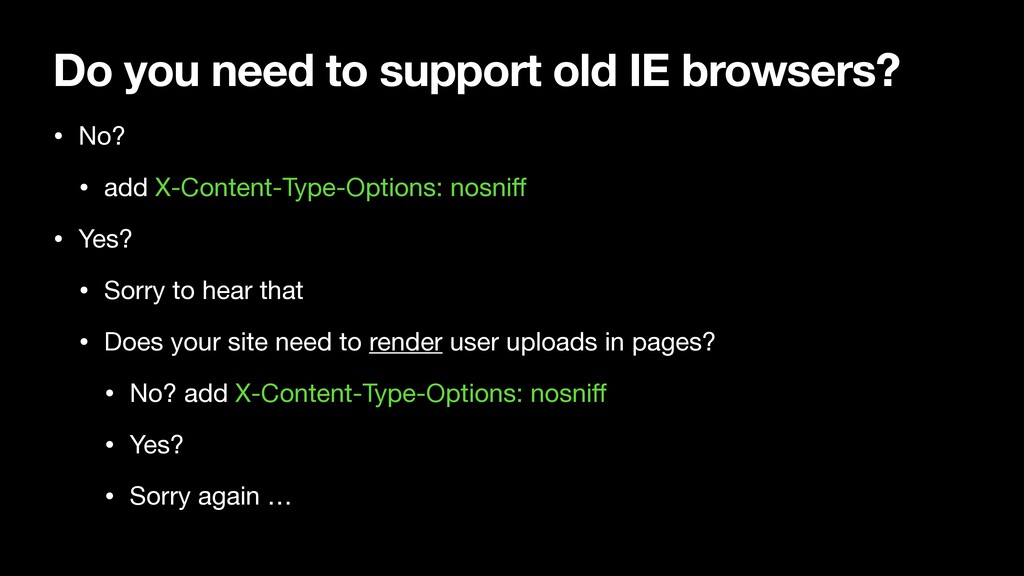
Do you need to support old IE browsers? • No?
• add X-Content-Type-Options: nosniff • Yes? • Sorry to hear that • Does your site need to render user uploads in pages? • No? add X-Content-Type-Options: nosniff • Yes? • Sorry again …
This is how improving your security works
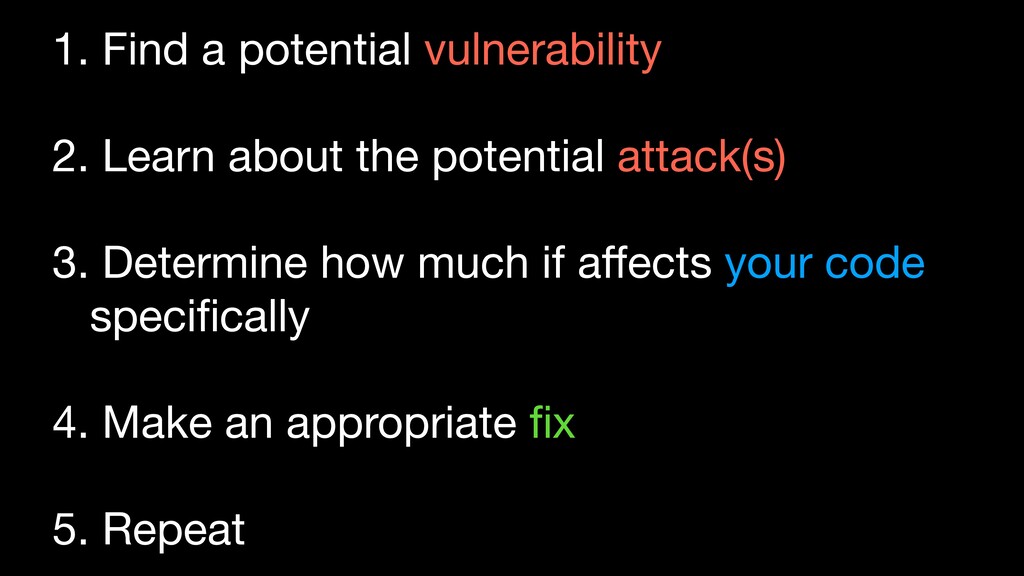
1. Find a potential vulnerability 2. Learn about the potential
attack(s) 3. Determine how much if affects your code specifically 4. Make an appropriate fix 5. Repeat
So, what’s next for itdashboard.gov ?
Normally, you would make the recommended fix …
None
And then
But since GSA won’t give us access to deploy code
on itdashboard.gov …
Let’s just check out the other tests in the report
…
None
None
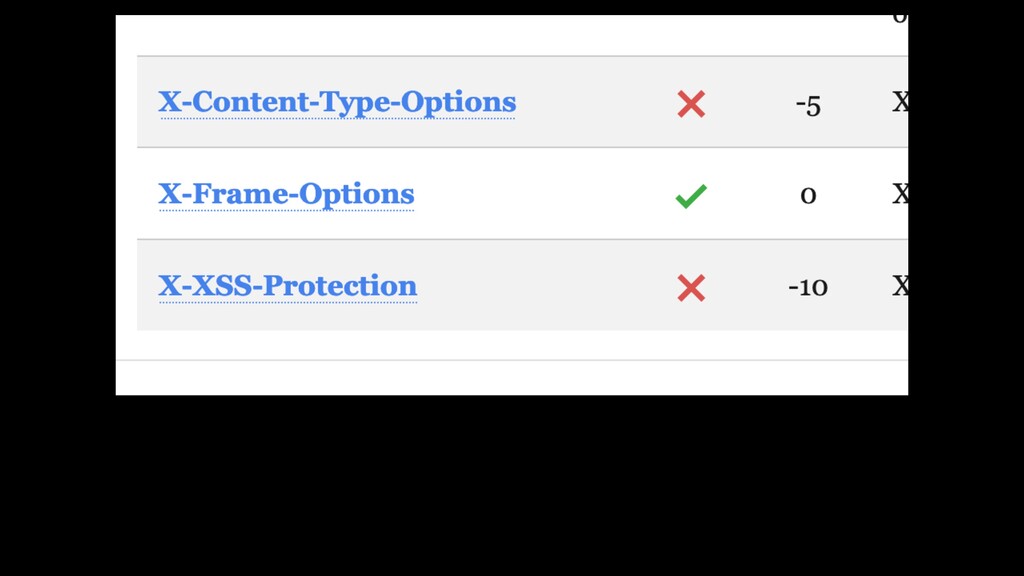
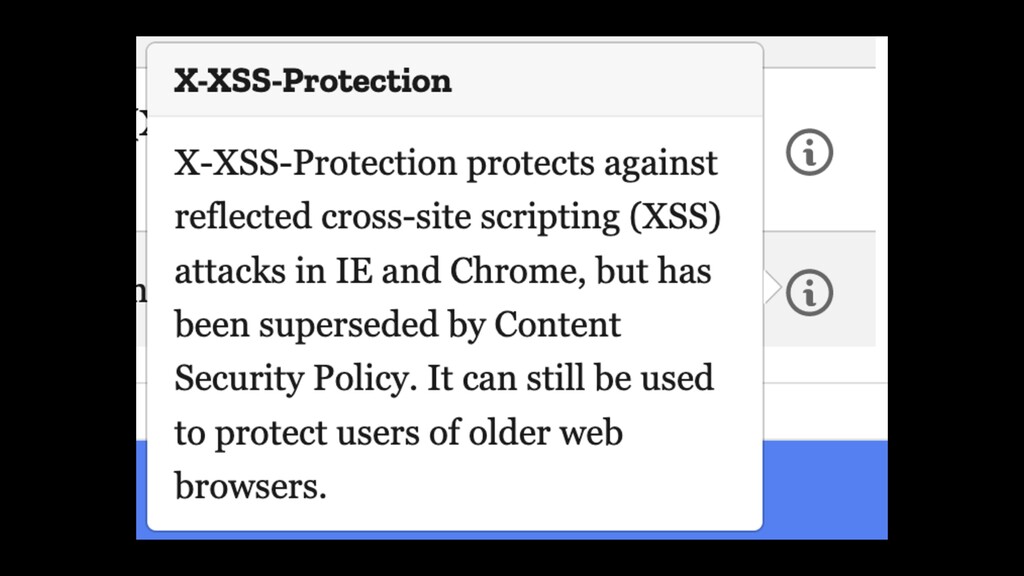
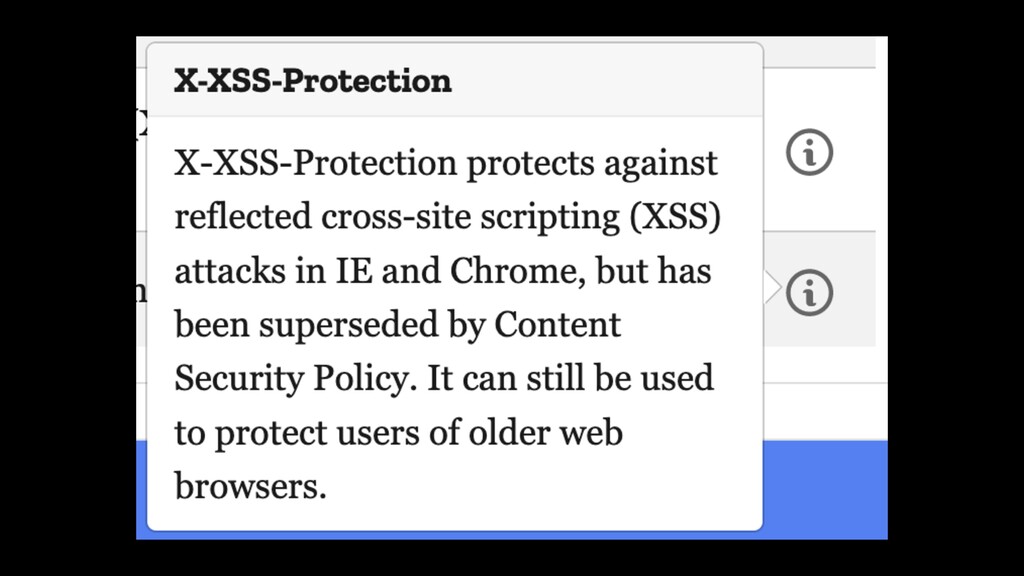
X-XSS-Protection
None
None
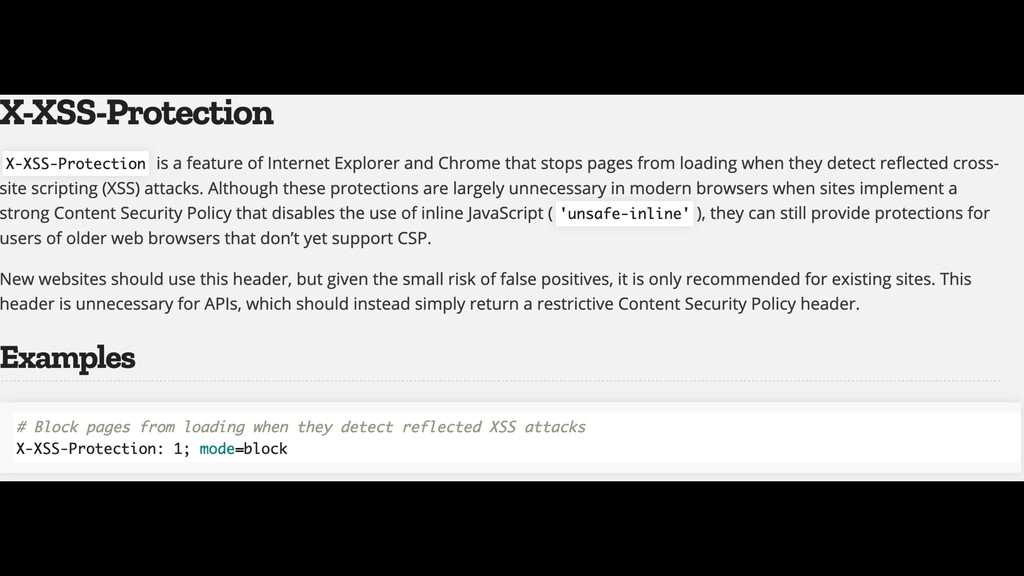
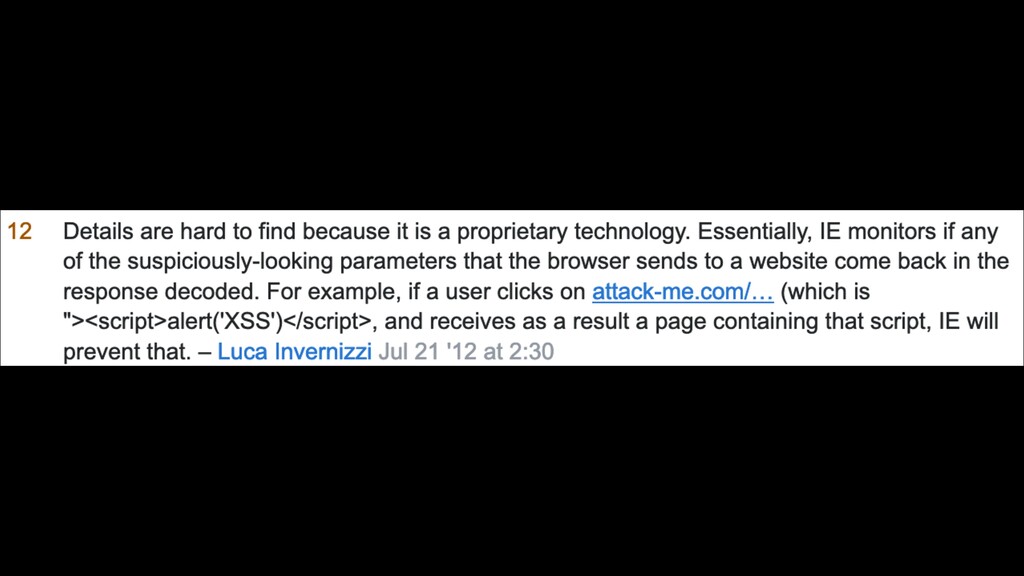
But what does it actually do?
None
https://itdashboard.gov/?param=<script>alert(1)</script> <html> <head><title>…</title></head> <body> <?php echo $_GET[‘param’] ?> </body> </html>
X-XSS-Protection: 1; mode-block
https://itdashboard.gov/?param=<script>alert(1)</script> <html> <head><title>…</title></head> <body> <?php echo $_GET[‘param’] ?> </body> </html>
None
You might as well take care of older browser users
(they need all they help they can get!)
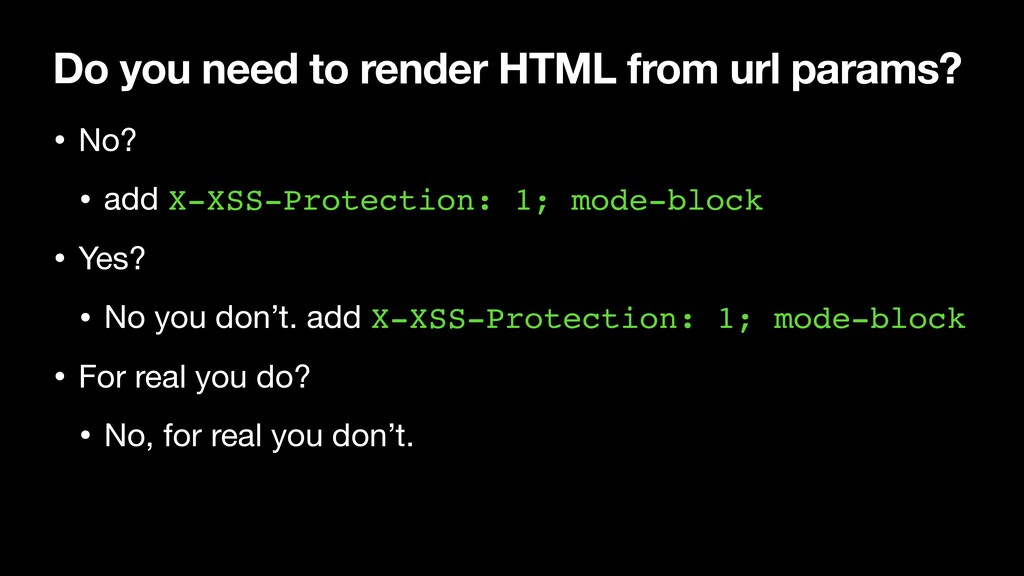
Do you need to render HTML from url params? •
No? • add X-XSS-Protection: 1; mode-block • Yes? • No you don’t. add X-XSS-Protection: 1; mode-block • For real you do? • No, for real you don’t.
None
Observatory Command-Line Interface
npm install observatory-cli
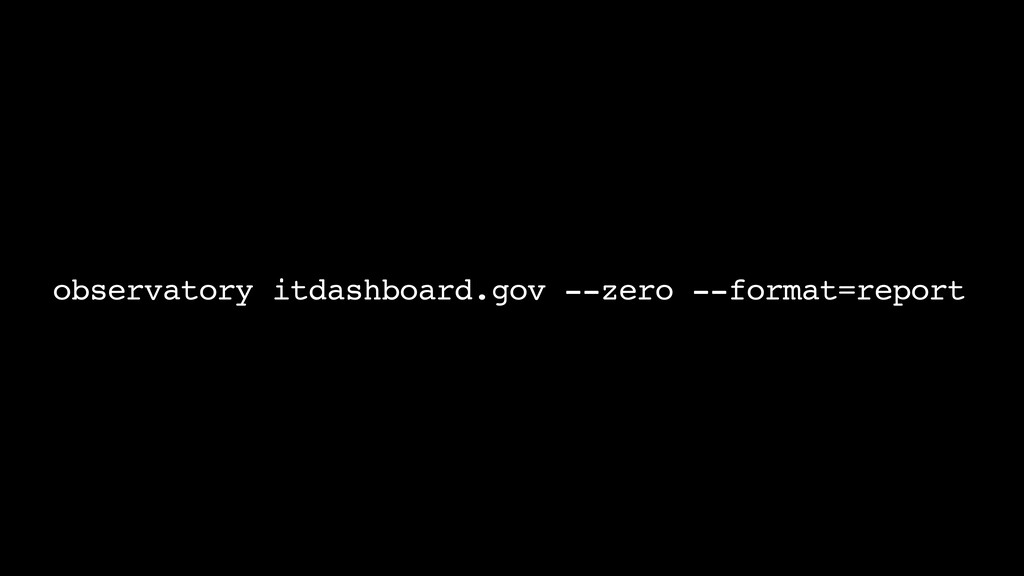
observatory itdashboard.gov --zero --format=report
None
So, same tests and results
Note: no “Recommendation”
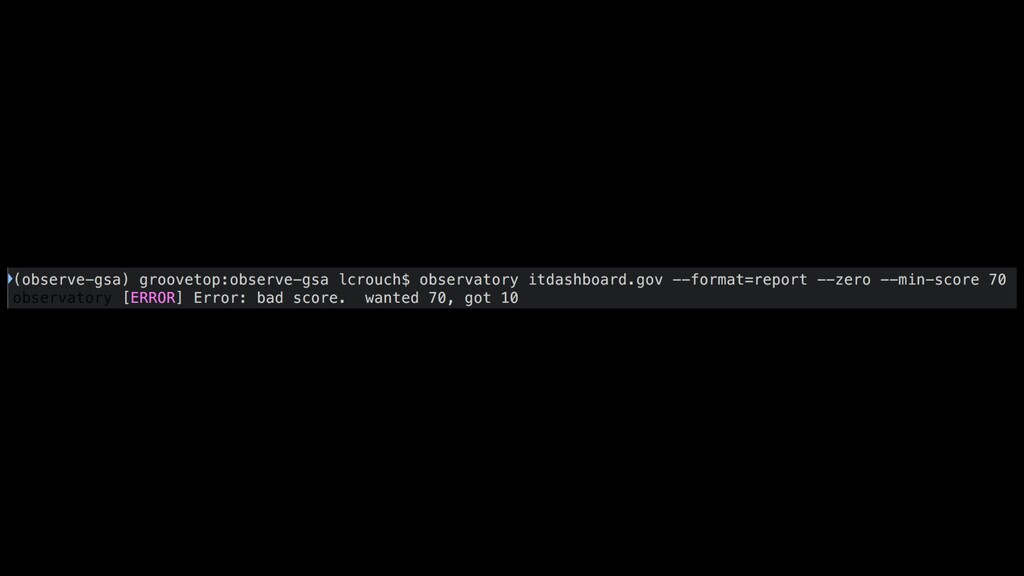
But you could put this in your CI pipeline to
scan a dev or stage site on every code change
And you can make CI fail if the score drops
below a certain level
None
Observatory API
https://github.com/mozilla/http-observatory/blob/master/httpobs/docs/api.md
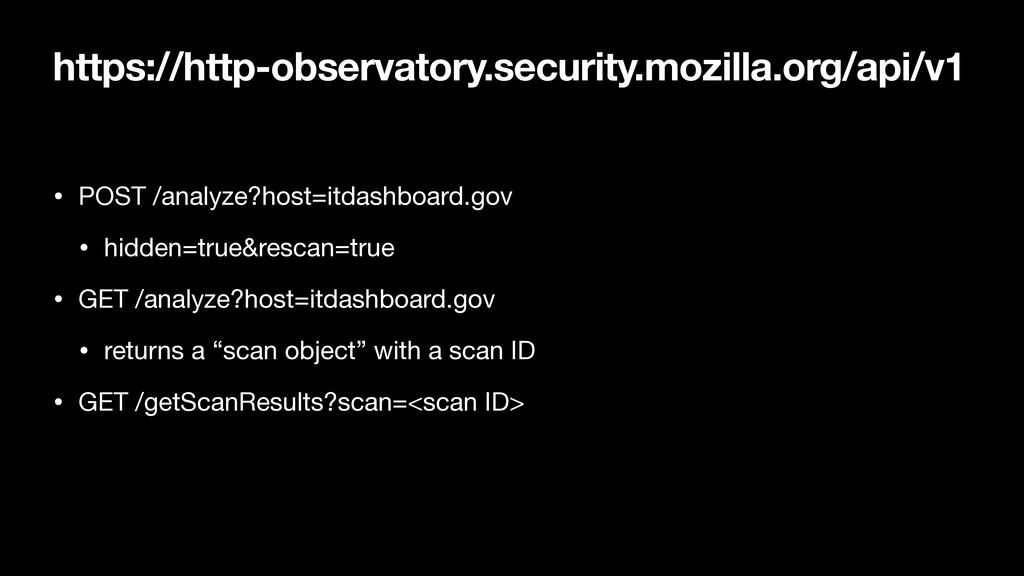
https://http-observatory.security.mozilla.org/api/v1 • POST /analyze?host=itdashboard.gov • hidden=true&rescan=true • GET /analyze?host=itdashboard.gov •
returns a “scan object” with a scan ID • GET /getScanResults?scan=<scan ID>
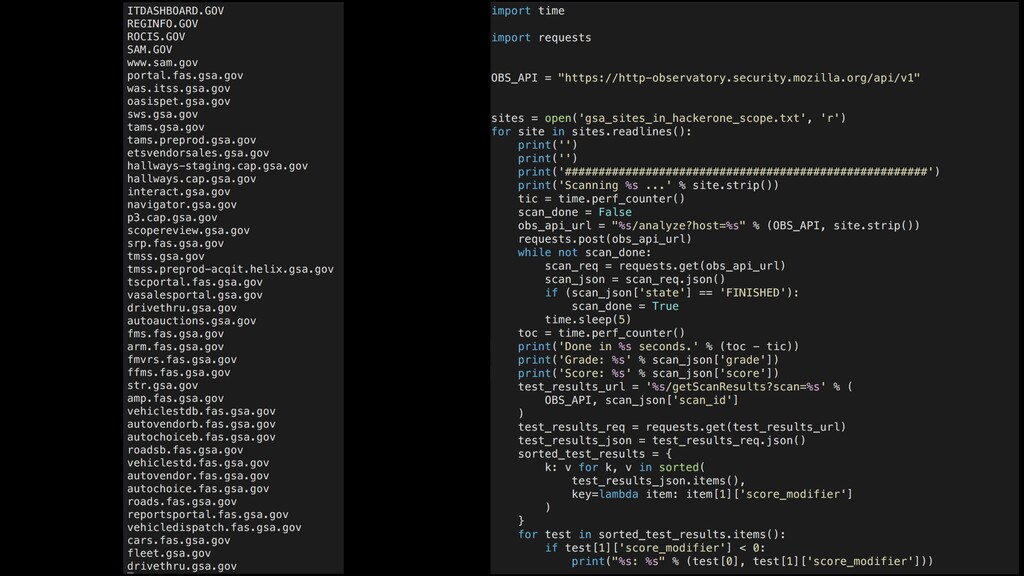
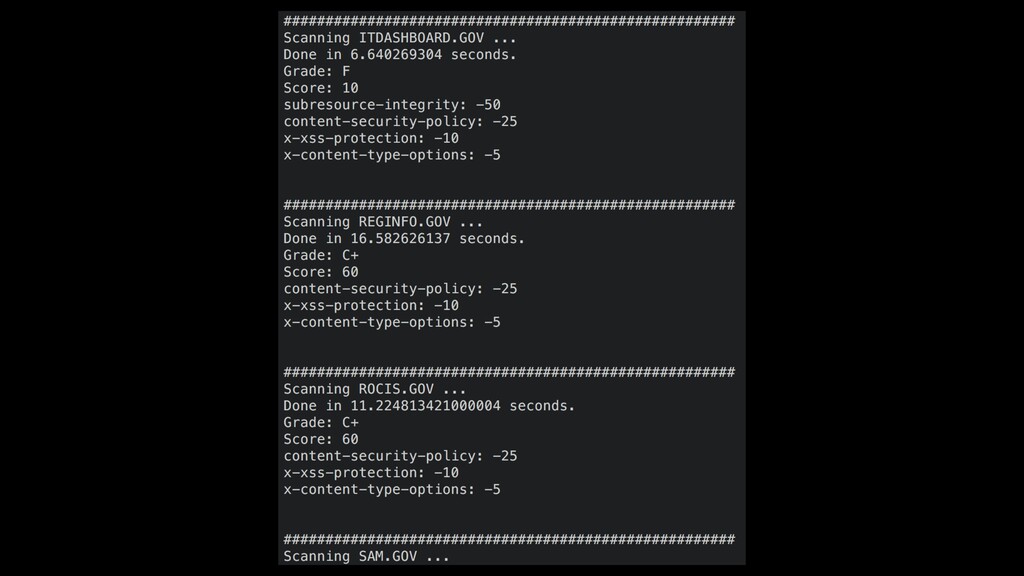
Now, let’s scan ALL the GSA sites in scope …
None
None
⚠ Disclaimer: don’t be evil ⚠
You should only use security scanning and testing tools with
permission
Questions • Mozilla Observatory • Website • Command-line tool •
API • 3rd-party scans • What else?
Appendix
None
None
None
None
None
None
So, let’s go see where itdashboard.gov might be vulnerable?
None
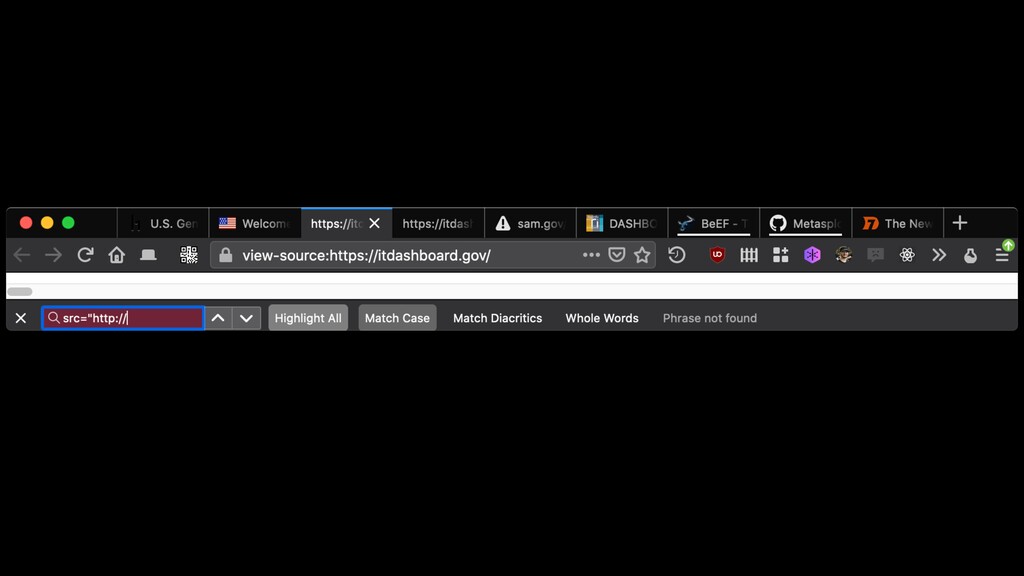
View source …
None
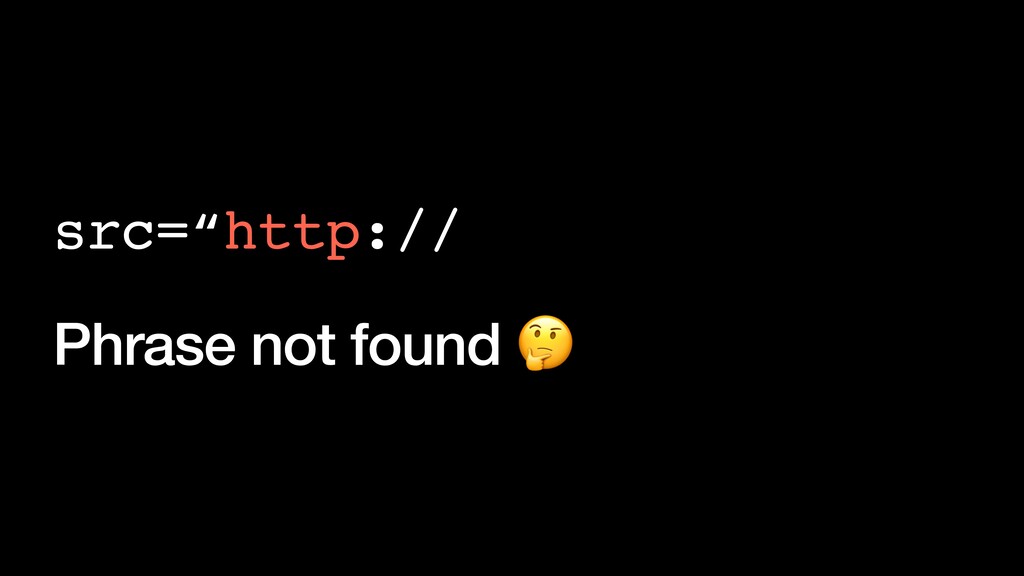
src=“http:// Phrase not found 🤔
None
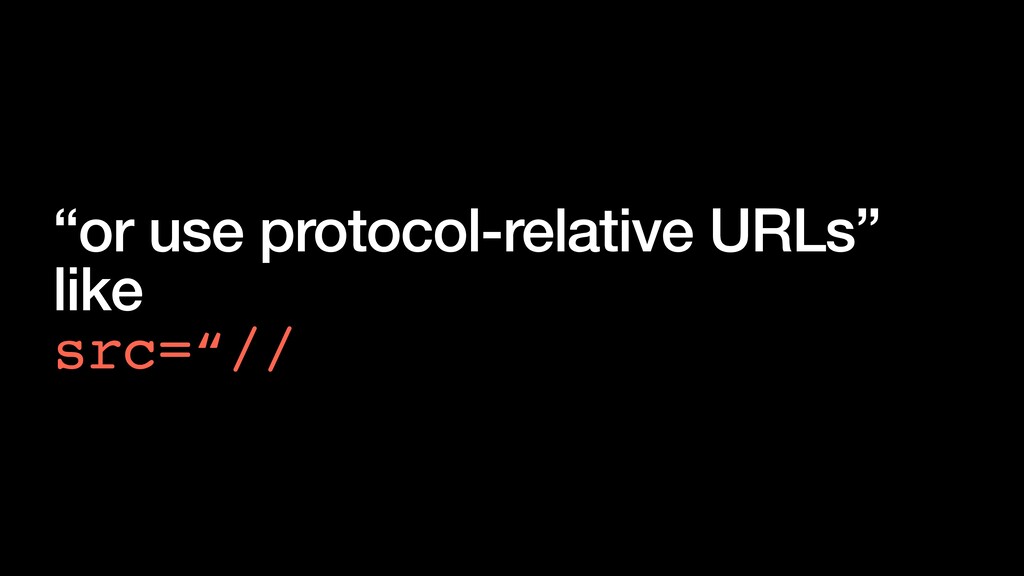
“or use protocol-relative URLs” like src=“//
None
So, if someone accessed this page via insecure http:// ,
we could hack the script
But, if someone accessed this page via insecure http:// ,
we could just hack the page
So when would this ever be a real problem?
When would someone ever access this page over insecure http://
? 🙋
What if someone types “itdashboard.gov” without https?
What if another page links to “itdashboard.gov” without https?
When would someone run this page over insecure http:// ?
When would someone run this page at http://127.0.0.1 ?
None
None
None
Content Security Policy … what’s that?
Insert lots of content about CSP
More Decks by luke crouch
See All by luke crouch
Mr. Brokebot: Lethal language attacks against AI agents
groovecoder
0
240
Pigeons to Padlocks: 5000 years of Network Security
groovecoder
0
130
cryptory-up-to-https-atlas-2024.pdf
groovecoder
0
110
Cryptography: 500 BC to https
groovecoder
0
290
VPNs
groovecoder
0
180
Digital Privacy & Security
groovecoder
0
310
Cryptography: 500 BC to Quantum Computing
groovecoder
0
1.2k
Just enough bitcoing to go cryptojacking with JavaScript
groovecoder
0
150
Can we protect Privacy without breaking the web
groovecoder
0
210
Other Decks in Technology
See All in Technology
AIエージェントのアーキテクチャ設計
nsatoh
0
480
HTTP QUERY時代の型安全な検索APIをKotlinで設計する
sansantech
PRO
1
120
パスワードのない鍵で、 データを手元に置く
ginjihayashi
0
400
認知の質も文化醸成も。数年取り組んで見えてきた技術広報のKPI設計 / Tech PR KPIs: Lessons on Awareness Quality and Culture After Several Years
bitkey
PRO
0
210
E2E Test というハーネス — AI時代の自動テスト民主化
daishukojima
10
6k
MCPでネットワーク障害調査を自動化する前に直すべき3つのこと
yama3133
1
660
From vibe coding to reliable (agentic) development
jcabot
0
200
さようならSSH鍵、こんにちはゼロトラスト ― AIフレンドリーで快適な自宅鯖SSH
atalie2m
14
7.5k
Platform Engineering をベースとした Agentic Software Factory の実践
110y
3
890
Gov-JAWS#9 統合監視機能のマネージドサービス化+AIによる障害時自動調査
fj_yoshimura_kosuke
0
230
OpenTelemetryで変わった 新時代のCloudWatchメトリクス監視
tsukuboshi
0
490
Re:ゼロから始めるシェアハウスのペットな鯖
silmin_
0
270
Featured
See All Featured
Helping Users Find Their Own Way: Creating Modern Search Experiences
danielanewman
31
3.4k
XXLCSS - How to scale CSS and keep your sanity
sugarenia
250
1.3M
Web Performance Is a Journey [PerfNow 2026]
tammyeverts
2
130
Measuring Dark Social's Impact On Conversion and Attribution
stephenakadiri
2
330
A designer walks into a library…
pauljervisheath
211
25k
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
670
Put a Button on it: Removing Barriers to Going Fast.
kastner
60
4.6k
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
780
How to Create Impact in a Changing Tech Landscape [PerfNow 2023]
tammyeverts
56
3.5k
Design in an AI World
tapps
1
390
Exploring the Power of Turbo Streams & Action Cable | RailsConf2023
kevinliebholz
37
6.7k
How to build an LLM SEO readiness audit: a practical framework
nmsamuel
2
990


 groovecoder
 nsatoh
 sansantech
 ginjihayashi
 bitkey
 daishukojima
 yama3133
 jcabot
 atalie2m
 110y
 fj_yoshimura_kosuke
 tsukuboshi
 silmin_
 danielanewman
 sugarenia
 tammyeverts
 stephenakadiri
 pauljervisheath
 konakalab
 kastner
 baasie
 tapps
 kevinliebholz
 nmsamuel