Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
AWSとTerraform初心者が やってみたこと
Search
masa-ita
December 21, 2019
Technology
540
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
AWSとTerraform初心者が やってみたこと
masa-ita
December 21, 2019
More Decks by masa-ita
See All by masa-ita
Ollamaを使ったLocal Language Model活用法
itagakim
1
270
Run Instant NeRF on Docker
itagakim
1
2.4k
3D Clustering and Metric Learning
itagakim
0
440
Cloud TPUの使い方〜BigBirdの日本語学習済みモデルを作る〜
itagakim
0
780
多言語学習済みモデルmT5とは?
itagakim
1
810
AWSのGPUを安く使って TensorFlowモデルを訓練する方法
itagakim
0
440
最近の自然言語処理モデルの動向
itagakim
1
610
ディープラーニングで芸術はできるか? 〜生成系ネットワークの進展〜
itagakim
0
400
IntroductionToTensorFlow2_0.pdf
itagakim
1
400
Other Decks in Technology
See All in Technology
Jev の中身は50行で再現できる。でも本物との差はどこにあるのか
hisuzuya
0
210
渡米前の準備を制す!re:Invent 2026徹底準備術 / The Ultimate Preparation Guide for re:Invent 2026
yuj1osm
1
430
AI時代、つくる力を自分たちの手に。 ──電通×KAG、アジャイルとAI駆動開発で挑む開発の変革
yuukiyo
3
430
なぜ東京にいる私が、新潟の技術コミュニティを運営するのか by 八雲慎之助
yakumo
0
130
【Oracle AI SPOTLIGHT ウェビナー】事例から見る!なぜOCIが選ばれたのか ― AI時代のクラウド戦略を紐解く ―
oracle4engineer
PRO
1
130
推論基盤と Scale-Up Interconnect の現状と制約から俯瞰する技術動向
markunet
2
650
"AWSはちょっと苦手"でも大丈夫。AWS Blocks で手軽に作る Flutter のバックエンド #FlutterKaigi
tacck
PRO
0
110
LLMの知識とAIエージェント
happysamurai294
0
130
日本AIベンチャーレポート2026
kentarofujii
0
260
re:Inventで、人生は変わったのか? / growth-builders-hub-1-reinvent-2026
mhrtech
2
160
Vue で書く 空間コンピューティング、TresJS と WebXR を使ったXR デバイスのフロントエンド開発
hiranuma
0
130
Oracle Database Security 詳細解説
oracle4engineer
PRO
1
150
Featured
See All Featured
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
2
380
The Hidden Cost of Media on the Web [PixelPalooza 2025]
tammyeverts
2
540
How to Ace a Technical Interview
jacobian
280
24k
The agentic SEO stack - context over prompts
schlessera
0
990
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.7k
技術選定の審美眼(2025年版) / Understanding the Spiral of Technologies 2025 edition
twada
PRO
120
120k
[Rails World 2026] Durable orchestration on Rails: from continuation to workflow
palkan
2
960
Avoiding the “Bad Training, Faster” Trap in the Age of AI
tmiket
0
290
The Organizational Zoo: Understanding Human Behavior Agility Through Metaphoric Constructive Conversations (based on the works of Arthur Shelley, Ph.D)
kimpetersen
PRO
0
510
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
70
68k
[SF Ruby Conf 2025] Rails X
palkan
3
1.5k
Templates, Plugins, & Blocks: Oh My! Creating the theme that thinks of everything
marktimemedia
31
2.9k
Transcript
AWSとTerraform初⼼者が やってみたこと 板垣 正敏@JAWS-UG Niigata 2019/12/21
⾃⼰紹介 • 板垣 正敏 • 県内IT企業の技術顧問(2020/3まで) • 中⼩企業診断⼠ • ⽇本Rubyの会
• 新潟オープンソース協会 • Python機械学習勉強会 in 新潟 • TensorFlow Users Group • @itagakim • https://github.com/masa-ita • AWS歴 2017年〜
システムの全体像
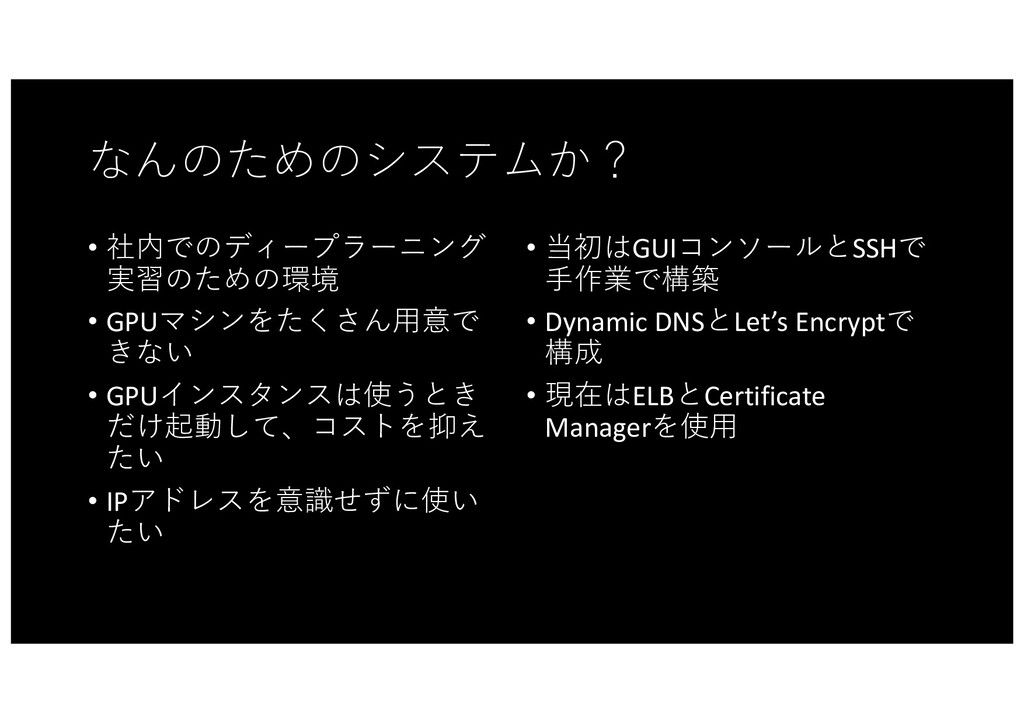
なんのためのシステムか? • 社内でのディープラーニング 実習のための環境 • GPUマシンをたくさん⽤意で きない • GPUインスタンスは使うとき だけ起動して、コストを抑え
たい • IPアドレスを意識せずに使い たい • 当初はGUIコンソールとSSHで ⼿作業で構築 • Dynamic DNSとLet’s Encryptで 構成 • 現在はELBとCertificate Managerを使⽤
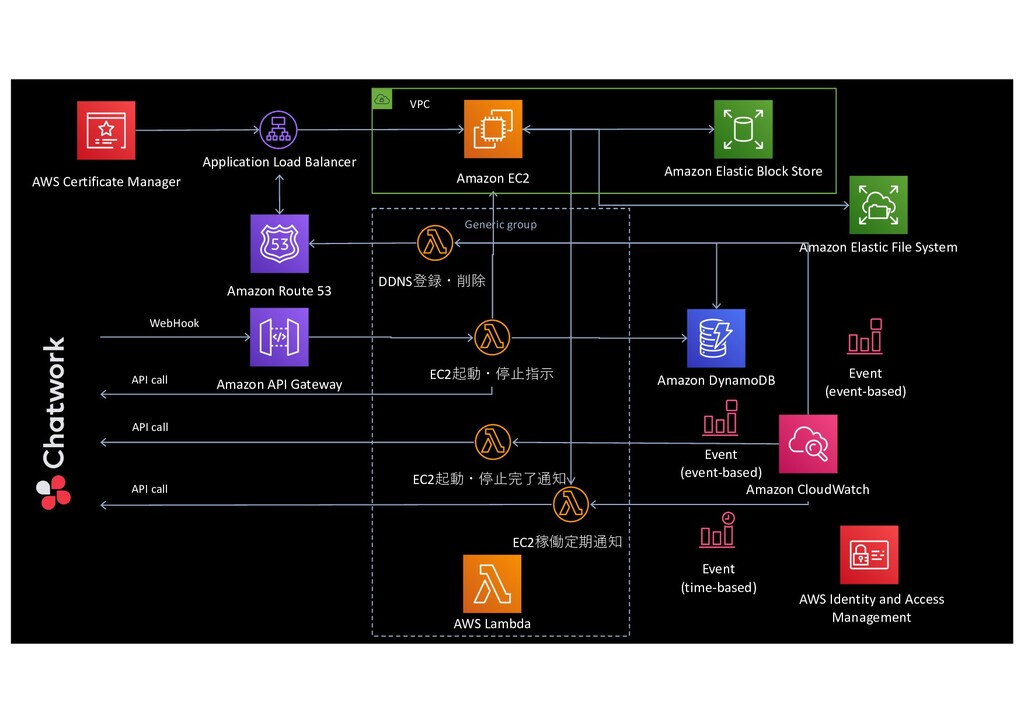
AWS Lambda EC2起動・停⽌指⽰ Amazon API Gateway DDNS登録・削除 Amazon DynamoDB Amazon
EC2 Amazon Route 53 Application Load Balancer Amazon CloudWatch Amazon Elastic Block Store Amazon Elastic File System EC2起動・停⽌完了通知 EC2稼働定期通知 AWS Identity and Access Management Generic group Event (time-based) Event (event-based) Event (event-based) AWS Certificate Manager VPC WebHook API call API call API call
本題:Terraformとは?
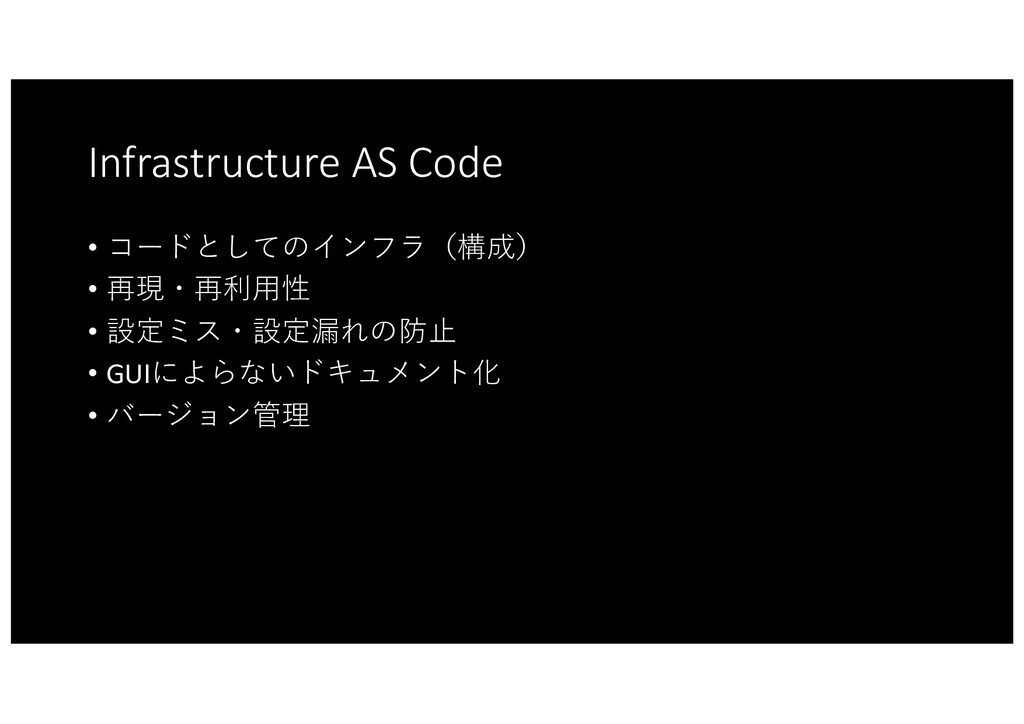
Infrastructure AS Code • コードとしてのインフラ(構成) • 再現・再利⽤性 • 設定ミス・設定漏れの防⽌ •
GUIによらないドキュメント化 • バージョン管理
なぜTERRAFORM? • AWSならCloudFormationがあるが・・・ • Azure, GCP, オンプレ(Vmware, Nutanix, etc.):ワークフ ローの統⼀
• https://www.terraform.io/docs/providers/index.html
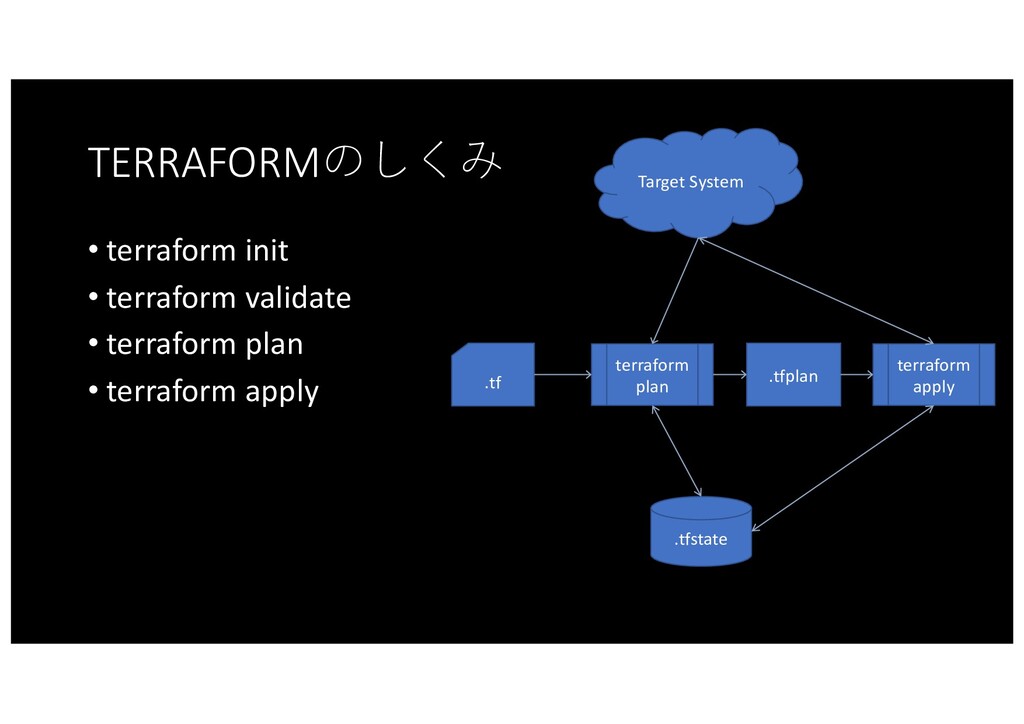
TERRAFORMのしくみ • terraform init • terraform validate • terraform plan
• terraform apply .tf .tfstate .tfplan Target System terraform plan terraform apply
TERRAFORMのインストール • プラットフォームごとにZIPファイルで提供 • シングルバイナリでパスが通っていればOK • MacOSならHomebrewでもインストール可能 • tfenvでバージョン管理も
構成例 Labmdaを⽤いたDynamic DNSの部分のみを紹介
プロバイダ設定 • クレデンシャルは環境変数か awscliの設定ファイルに保存 すべき • バージョンアップでの⾮互換 を防ぐため、Terraformやプロ バイダのバージョン指定が有 効
• 右の例では、.tfstateファイル をS3バケットに保存している (共同作業やリモート参照の ため) terraform { required_version = "0.12.17” backend "s3" { bucket = "tfstate-terraform-demo” key = "network/terraform.tfstate” region = "ap-northeast-1” } } provider "aws" { version = "~> 2.41” region = "ap-northeast-1” }
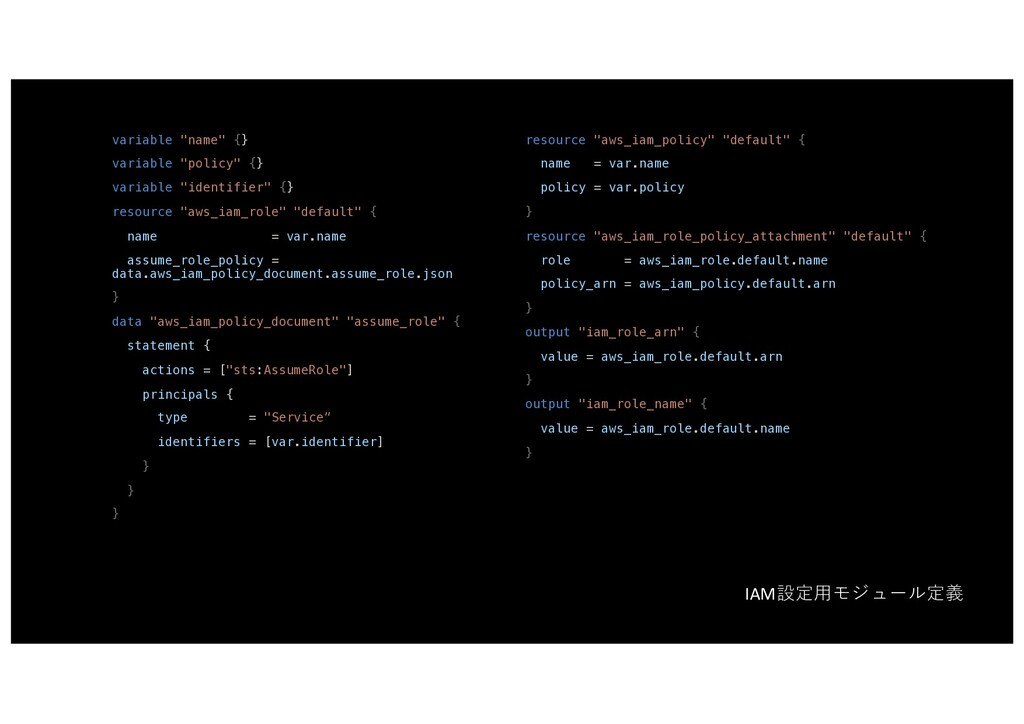
variable "name" {} variable "policy" {} variable "identifier" {} resource
"aws_iam_role" "default" { name = var.name assume_role_policy = data.aws_iam_policy_document.assume_role.json } data "aws_iam_policy_document" "assume_role" { statement { actions = ["sts:AssumeRole"] principals { type = "Service” identifiers = [var.identifier] } } } resource "aws_iam_policy" "default" { name = var.name policy = var.policy } resource "aws_iam_role_policy_attachment" "default" { role = aws_iam_role.default.name policy_arn = aws_iam_policy.default.arn } output "iam_role_arn" { value = aws_iam_role.default.arn } output "iam_role_name" { value = aws_iam_role.default.name } IAM設定⽤モジュール定義
data "aws_iam_policy_document" "for_ddns_lambda" { statement { effect = "Allow” actions
= ["ec2:Describe*"] resources = ["*"] } statement { effect = "Allow” actions = ["dynamodb:*"] resources = ["*"] } statement { effect = "Allow” actions = [ "logs:CreateLogGroup", "logs:CreateLogStream", "logs:PutLogEvents” ] resources = ["*"] } statement { effect = "Allow” actions = ["route53:*"] resources = ["*"] } } module "role_for_ddns_lambda" { source = "./iam_role” name = "role_for_ddns_lambda” identifier = "lambda.amazonaws.com” policy = data.aws_iam_policy_document.for_ddns_lambda.json } Lambda関数⽤IAM定義
data "archive_file" "lambda_function" { type = "zip” source_dir = "lambda/function”
output_path = "lambda/upload/lambda_function.zip” } resource "aws_lambda_function" "ddns_lambda" { filename = data.archive_file.lambda_function.output_path function_name = "ddns_lambda” role = module.role_for_ddns_lambda.iam_role_arn handler = "union.lambda_handler” source_code_hash = data.archive_file.lambda_function.output_base64sha256 runtime = "python2.7” memory_size = 128 timeout = 120 } resource "aws_lambda_permission" "allow_cloudwatch" { statement_id = "AllowExecutionFromCloudWatch” action = "lambda:InvokeFunction” function_name = aws_lambda_function.ddns_lambda.function_name principal = "events.amazonaws.com” source_arn = aws_cloudwatch_event_rule.ec2_lambda_ddns_rule.arn } Lambda関数定義
resource "aws_vpc" "main" { cidr_block = "10.0.0.0/16” enable_dns_support = true
enable_dns_hostnames = true tags = { Name = "main” } } resource "aws_subnet" "main" { vpc_id = aws_vpc.main.id cidr_block = "10.0.1.0/24” map_public_ip_on_launch = true availability_zone = "ap-northeast-1d” tags = { Name = "main” } } resource "aws_internet_gateway" "gw" { vpc_id = aws_vpc.main.id tags = { Name = "main” } } resource "aws_route_table" "public" { vpc_id = aws_vpc.main.id } resource "aws_route" "public" { route_table_id = aws_route_table.public.id gateway_id = aws_internet_gateway.gw.id destination_cidr_block = "0.0.0.0/0” } resource "aws_route_table_association" "public" { subnet_id = aws_subnet.main.id route_table_id = aws_route_table.public.id } resource "aws_vpc_dhcp_options" "aws_subdomain" { domain_name = "aws.rails.to” domain_name_servers = ["AmazonProvidedDNS"] tags = { Name = "aws_subdomain” } } output "vpc_id" { value = aws_vpc.main.id } output "main_subnet_id" { value = aws_subnet.main.id } VPC定義
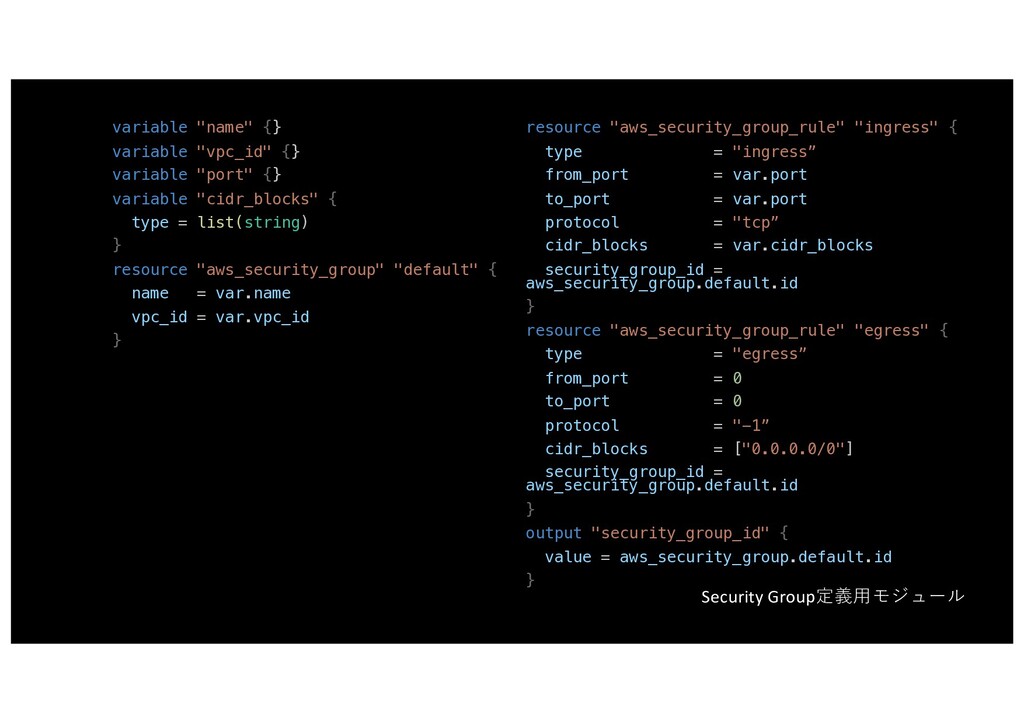
variable "name" {} variable "vpc_id" {} variable "port" {} variable
"cidr_blocks" { type = list(string) } resource "aws_security_group" "default" { name = var.name vpc_id = var.vpc_id } resource "aws_security_group_rule" "ingress" { type = "ingress” from_port = var.port to_port = var.port protocol = "tcp” cidr_blocks = var.cidr_blocks security_group_id = aws_security_group.default.id } resource "aws_security_group_rule" "egress" { type = "egress” from_port = 0 to_port = 0 protocol = "-1” cidr_blocks = ["0.0.0.0/0"] security_group_id = aws_security_group.default.id } output "security_group_id" { value = aws_security_group.default.id } Security Group定義⽤モジュール
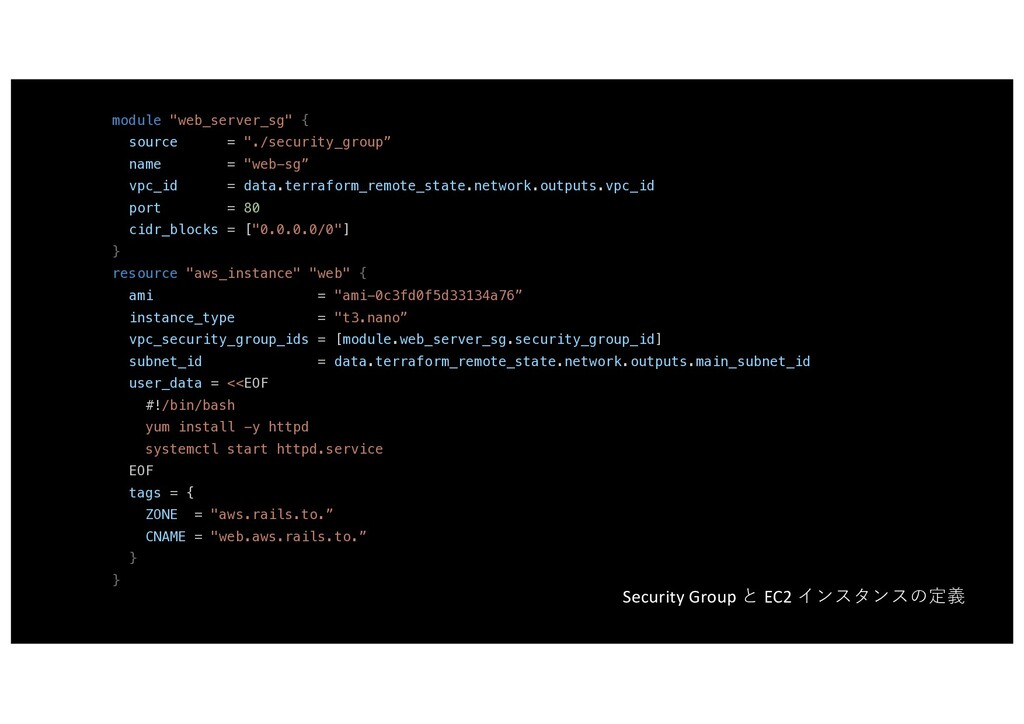
module "web_server_sg" { source = "./security_group” name = "web-sg” vpc_id
= data.terraform_remote_state.network.outputs.vpc_id port = 80 cidr_blocks = ["0.0.0.0/0"] } resource "aws_instance" "web" { ami = "ami-0c3fd0f5d33134a76” instance_type = "t3.nano” vpc_security_group_ids = [module.web_server_sg.security_group_id] subnet_id = data.terraform_remote_state.network.outputs.main_subnet_id user_data = <<EOF #!/bin/bash yum install -y httpd systemctl start httpd.service EOF tags = { ZONE = "aws.rails.to.” CNAME = "web.aws.rails.to.” } } Security Group と EC2 インスタンスの定義
まとめ
Terraform は強⼒なツール • 何よりも構成の再現性がありがたい • GUIが時々変わるクラウドには必須のツールか • プロビジョニングの機能はそれほど便利ではない(ファイル コピーとコマンド実⾏) •
モジュールの使い⽅(使いどころ)がよくわかってません • 最適なリソース分割やディレクトリ配置がまだわかってませ ん
参考図書 • 「実践Terraform」野村友規著 • オンデマンド / Kindle • https://www.amazon.co.jp/dp/4844378139
参照サイト • Terraform Documentation • https://www.terraform.io/docs/index.html • Lamdaを⽤いたDynamic DNSの参考事例 •
https://aws.amazon.com/jp/blogs/compute/building-a-dynamic-dns-for- route-53-using-cloudwatch-events-and-lambda/ • https://github.com/aws-samples/aws-lambda-ddns-function
おまけ: Python機械学習勉強会 in 新潟 Restart #10 やり ます • 2020年1⽉11⽇(⼟)
• 新潟市中央公⺠館(クロスパル) • 「(仮)ディープラーニングで芸術はできるか?〜⽣成系ネッ トワークの進展〜」(itagakim) • 「機械学習による動作認識」(Oh!No!さん) • 「産学連携セミナー報告とインフラWG設⽴の提案」 (haru_fujitaさん) • 「Deep Learningを⽤いた残存⻭の⾃動認識」(historoidさん)


 itagakim
 hisuzuya
 yuj1osm
 yuukiyo
 yakumo
 oracle4engineer
 markunet
 tacck
 happysamurai294
 kentarofujii
 mhrtech
 hiranuma
 helenjbeal
 tammyeverts
 jacobian
 schlessera
 charlesmeaden
 twada
 palkan
 tmiket
 kimpetersen
 madoxten
 marktimemedia