Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
OAuth 101
Search
Nick Jackson
February 20, 2012
Technology
380
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
OAuth 101
A crash course on the basics of OAuth which I gave at Dev8D 2012.
Nick Jackson
February 20, 2012
More Decks by Nick Jackson
See All by Nick Jackson
It's all about the data.
jacksonj04
0
98
Development Tools
jacksonj04
0
120
Eating Your Own Dog Food
jacksonj04
0
360
LNCD and The Cloud
jacksonj04
0
130
MongoDB 101
jacksonj04
1
130
API Driven Development
jacksonj04
0
230
We Can Haz Ur Datas?!
jacksonj04
0
360
Universal Search at Lincoln
jacksonj04
0
58
Jerome Overview
jacksonj04
0
61
Other Decks in Technology
See All in Technology
DBTS2026 盛り上がってますか!?Databricksが実現するAI時代のデータ基盤
akuwano
1
130
cdkd (CDK Direct)
gotok365
3
230
コードレビューをなくして見えたもの
henteko
0
130
2拠点SRE活動始めてみた | sogaoh's LT @ ホンマでっかSRE勉強会 #3
sogaoh
PRO
0
240
増え続けるプロダクトの品質をどう担保するか。ProductSpecとTypeScriptによる取り組み
joere
3
390
Consistency for mere mortals - A gentle guide to consistency
ufried
0
120
AIに任せられるFlutterコードベースを作る 〜仕様をコードで表し、ハーネスで守る〜
myohei
1
630
eBPF 簡介 2026 版
shunghsiyu
0
180
レガシーコードに対する loop engineering的なAI開発プロセス導入について
kubell_hr
0
240
Copilot Coworkで「みのるん式」やってみた
minorun365
PRO
2
1.5k
AIで選択肢が広がった組織設計の理想と現実
konifar
16
7.7k
AIエージェント統制はAPIから——押さえるべき5つの要素
nagix
0
120
Featured
See All Featured
Effective software design: The role of men in debugging patriarchy in IT @ Voxxed Days AMS
baasie
1
600
Ethics towards AI in product and experience design
skipperchong
2
460
Building Better People: How to give real-time feedback that sticks.
wjessup
371
20k
Become a Pro
speakerdeck
PRO
31
6.3k
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
So, you think you're a good person
axbom
PRO
2
2.2k
Breaking role norms: Why Content Design is so much more than writing copy - Taylor Woolridge
uxyall
1
500
Fashionably flexible responsive web design (full day workshop)
malarkey
409
67k
Put a Button on it: Removing Barriers to Going Fast.
kastner
60
4.6k
A Modern Web Designer's Workflow
chriscoyier
699
190k
jQuery: Nuts, Bolts and Bling
dougneiner
66
8.7k
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
Transcript
None
Nick Jackson Web Monkey University of Lincoln @jacksonj04
Story time!
I’m a user of a web service
I own resources on the web service
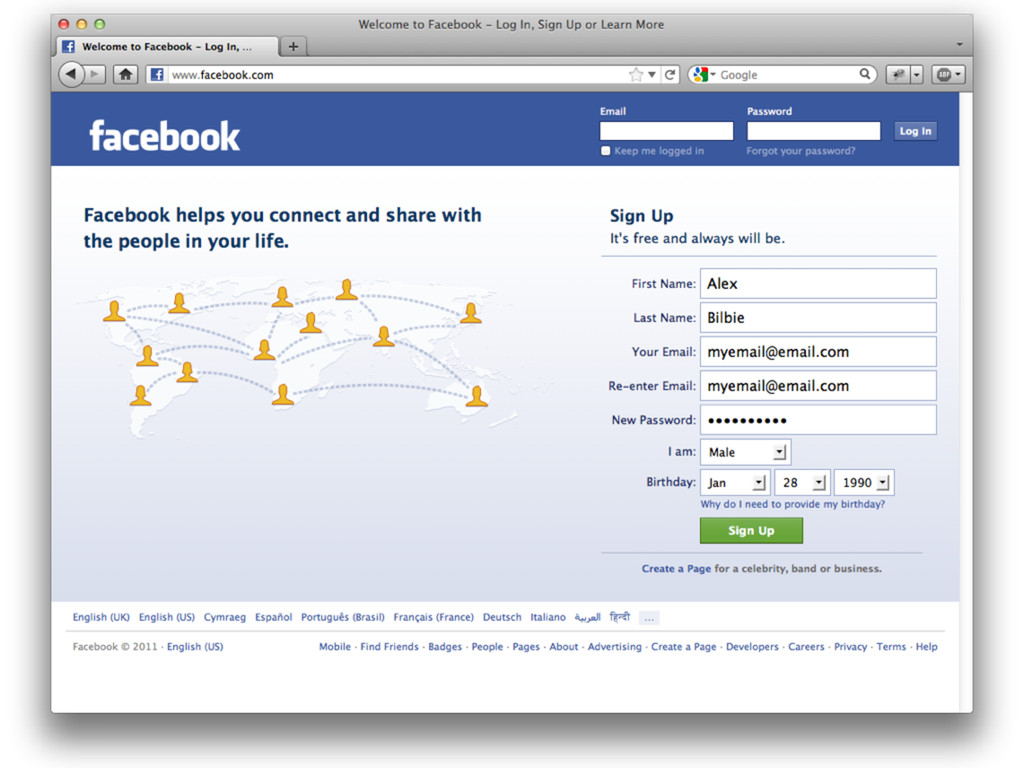
For example, personal details
None
These resources1 are stored on a resource server 2 1.
personal details 2. facebook.com
The resource server exposes user resources over an API
I visit a 3rd party web application
The 3rd party web app is called a client
The client1 wants to use my resources2 1. 3rd party
web app 2. personal details
But the resource server’s API requires user authorisation
How?
Give the client my password
Give the client my password
So what then?
OAuth
“An open protocol to allow secure API authorisation in a
simple and standard method from desktop and web applications.” oauth.net
—˛
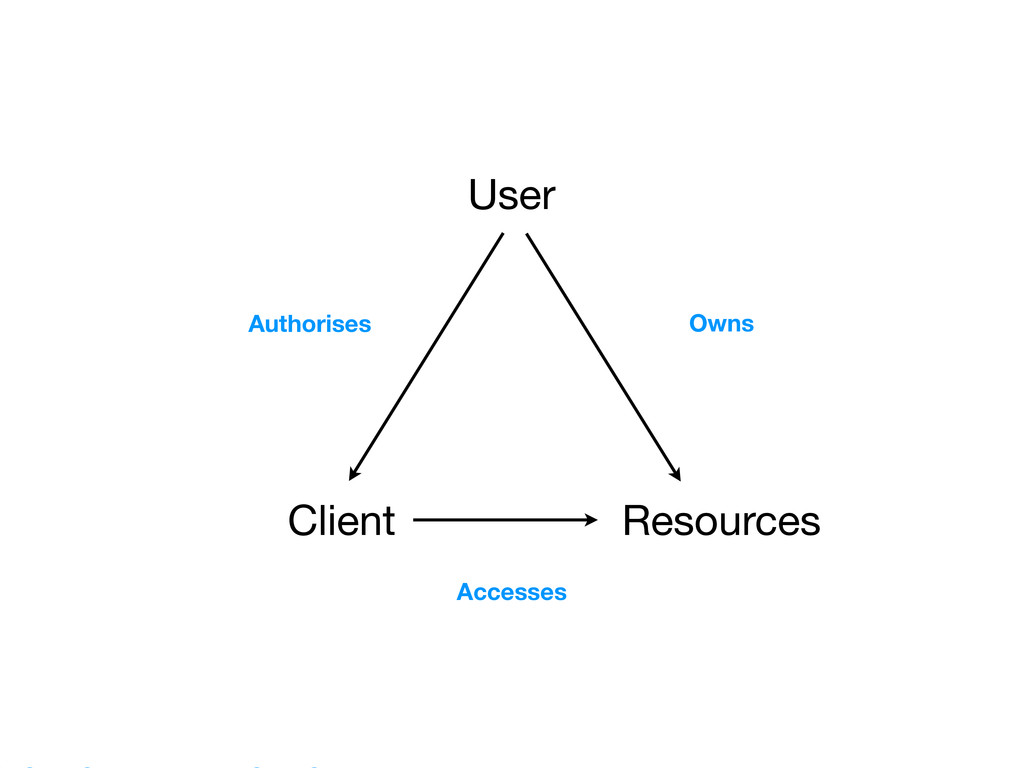
User Client Resources Owns Accesses Authorises
The flow
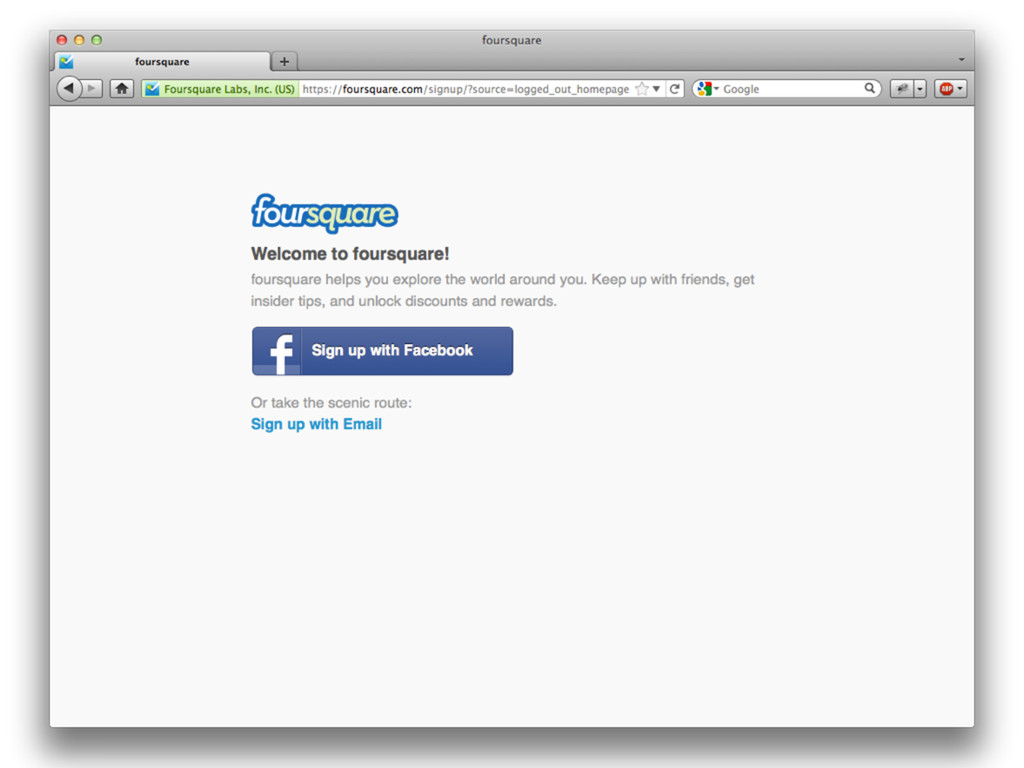
User clicks “sign in” in the client application
None
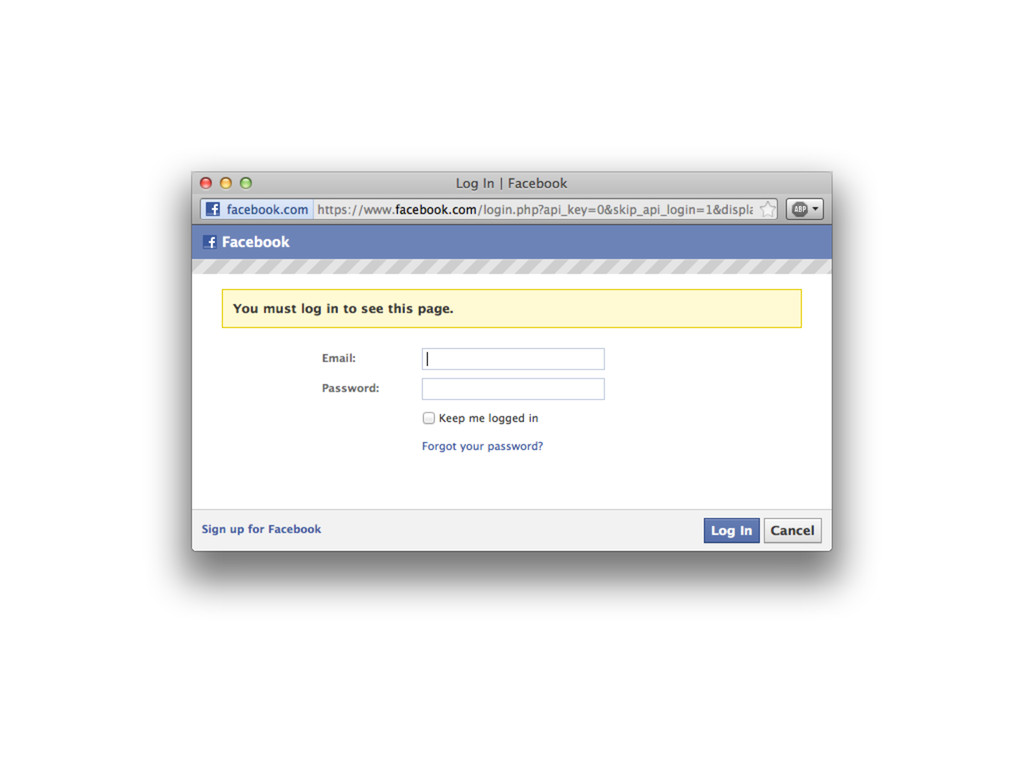
The user is redirected to the resource server and asked
to sign in
None
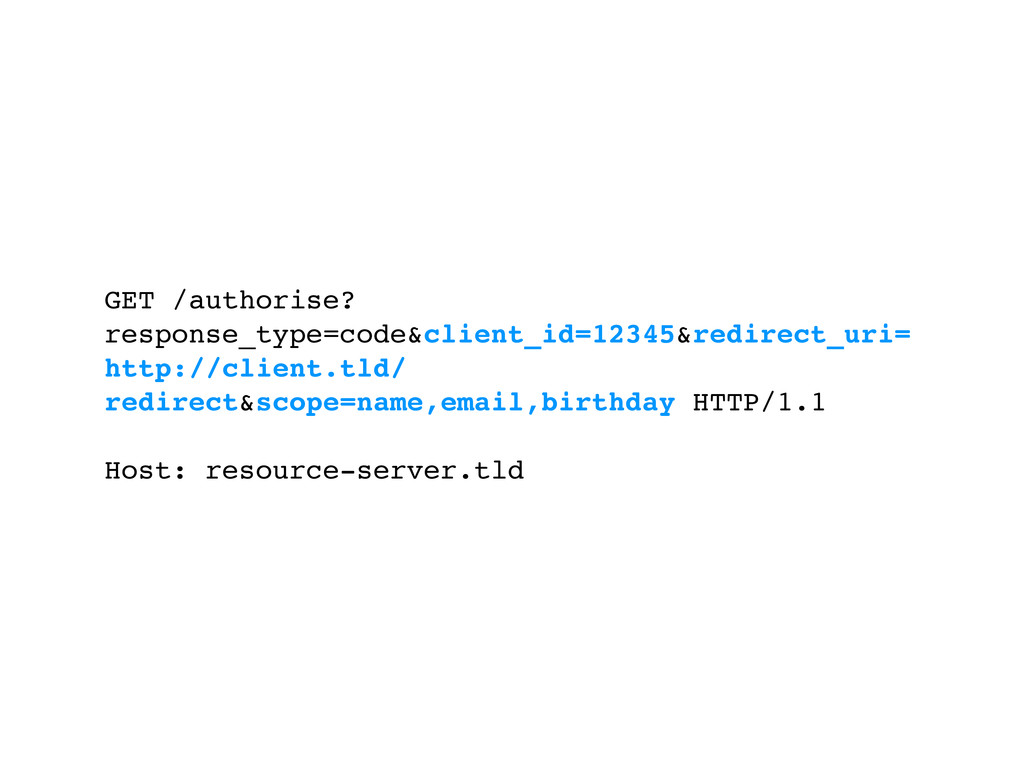
GET /authorise? response_type=code&client_id=12345&redirect_uri= http://client.tld/ redirect&scope=name,email,birthday HTTP/1.1 Host: resource-server.tld
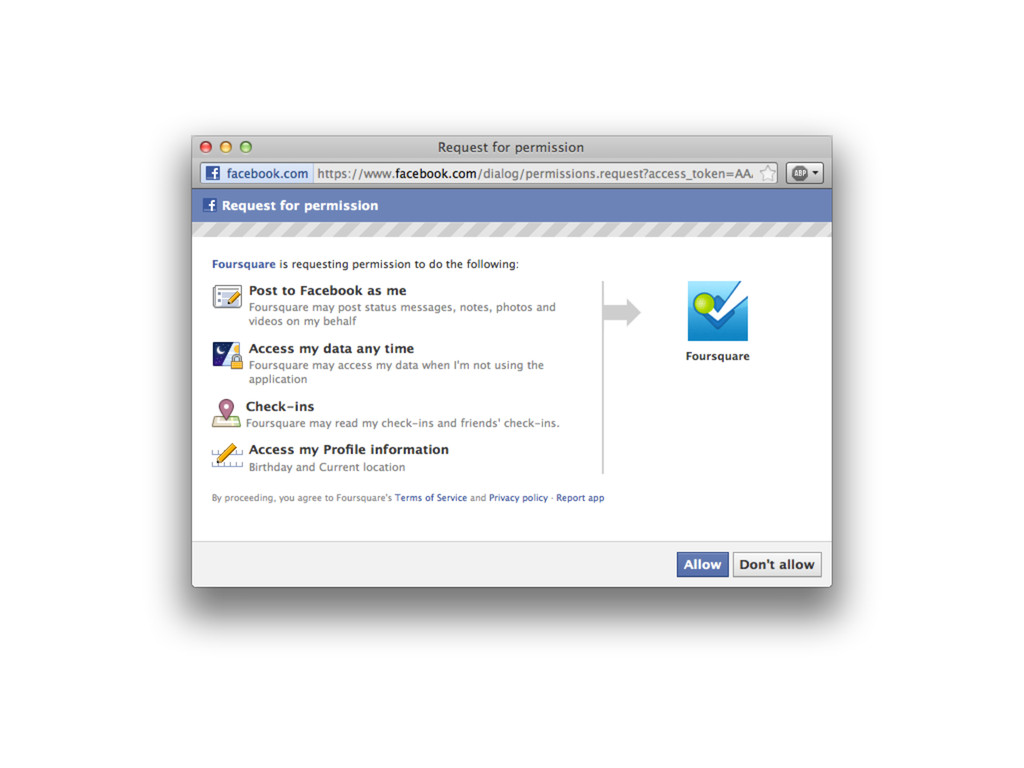
The resource server clearly tells the user the specific data
the client wants to access
None
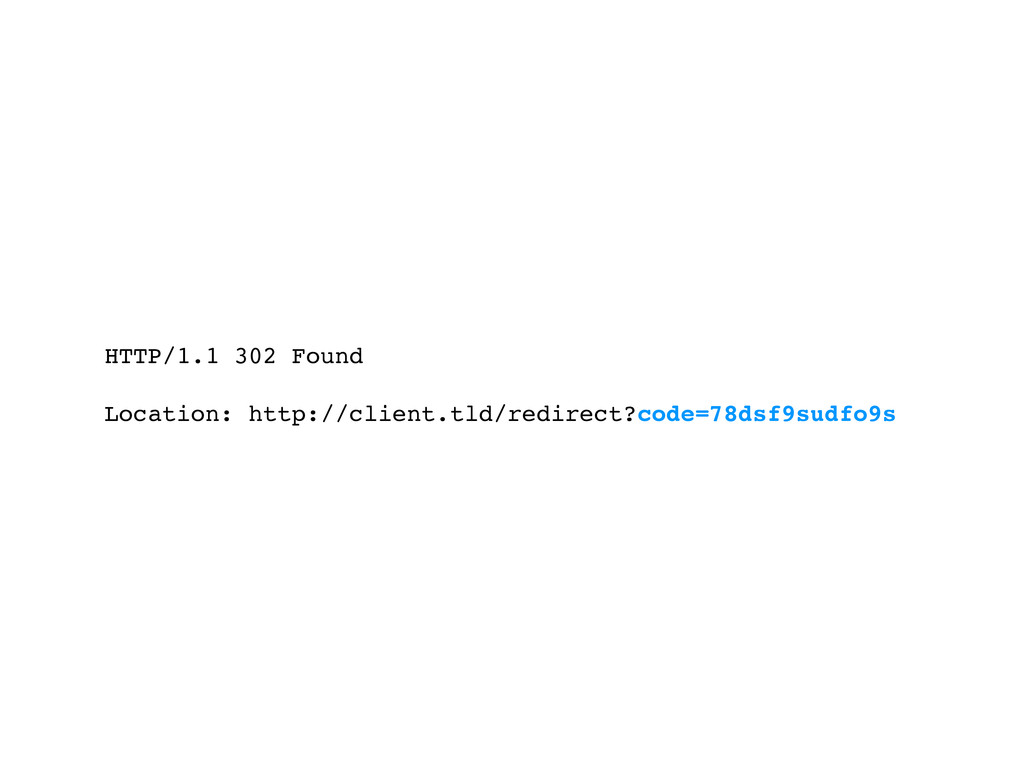
User authorises the application and is redirected back to client
with a authorisation code in the query string
HTTP/1.1 302 Found Location: http://client.tld/redirect?code=78dsf9sudfo9s
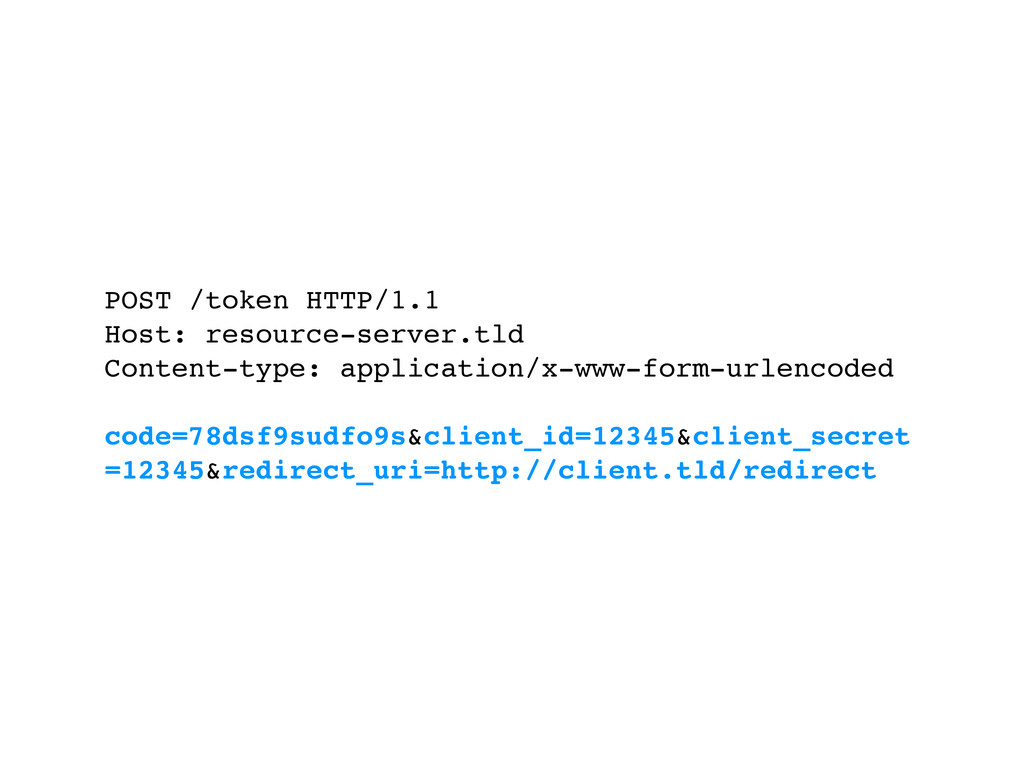
Client exchanges the authorisation code for an access token
POST /token HTTP/1.1 Host: resource-server.tld Content-type: application/x-www-form-urlencoded code=78dsf9sudfo9s&client_id=12345&client_secret =12345&redirect_uri=http://client.tld/redirect
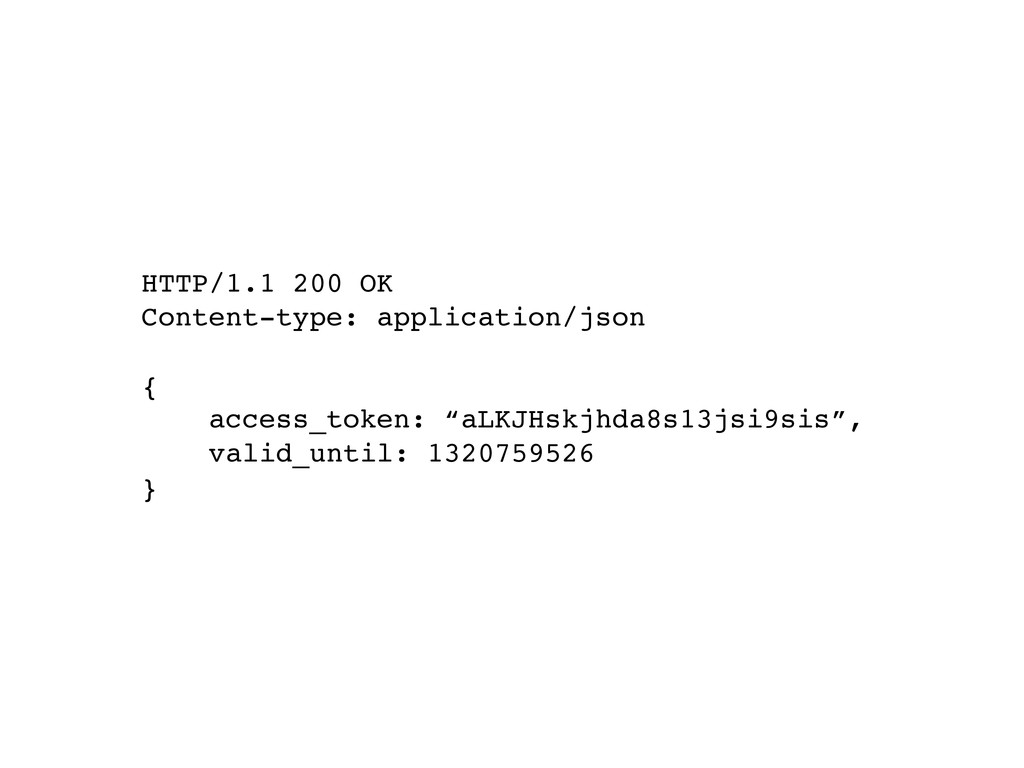
HTTP/1.1 200 OK Content-type: application/json { access_token: “aLKJHskjhda8s13jsi9sis”, valid_until: 1320759526
}
The access token can then be used as authorisation by
the client to access the specified resources for a specific length of time
Advantages
No password sharing <- Happy security conscious user
Developers just need to implement a redirect and a POST
request <- Happy developers
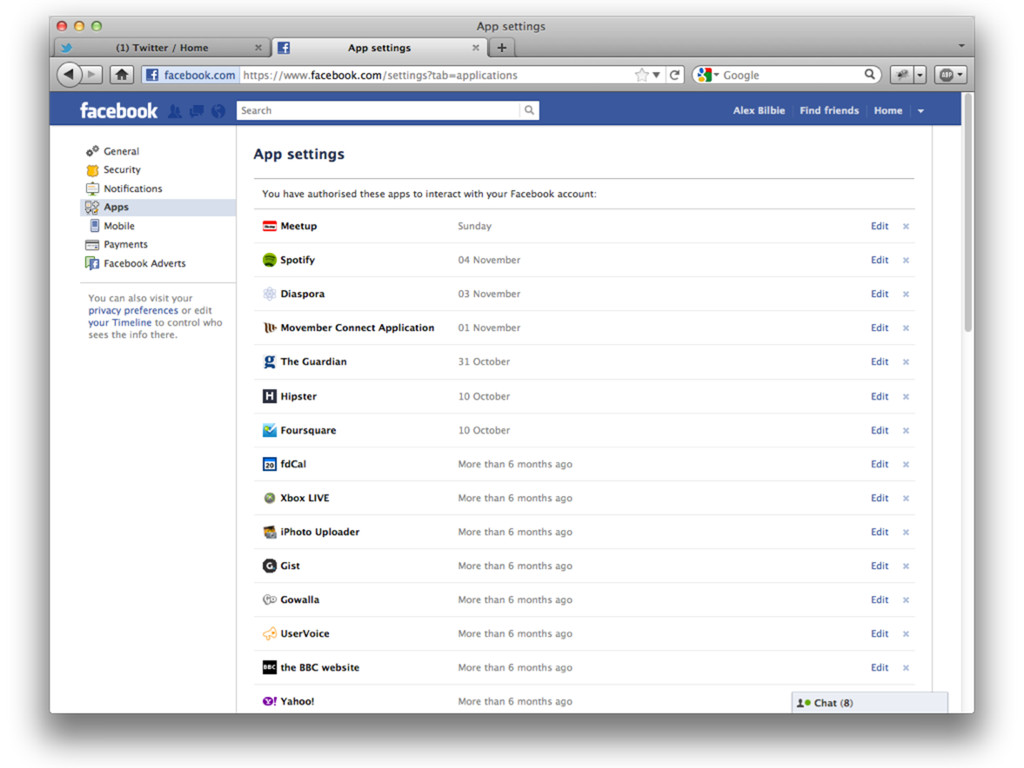
Users can revoke access tokens for specific clients
None
Nefarious clients can have their credentials revoked and all associated
access tokens destroyed immediately
None
None
Currently version 1.0a lncn.eu/giy
Version 2.0 is almost finished lncn.eu/bkw
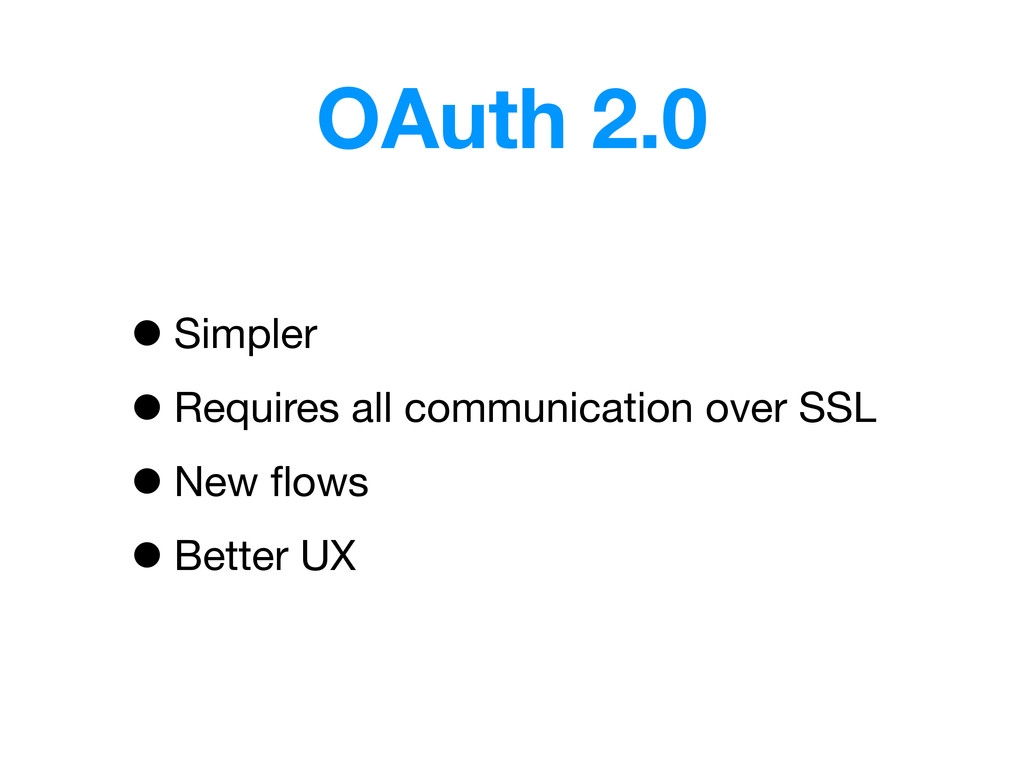
OAuth 2.0 •Simpler •Requires all communication over SSL •New flows
•Better UX
Who’s using OAuth?
None
And in HE?
None
None
None
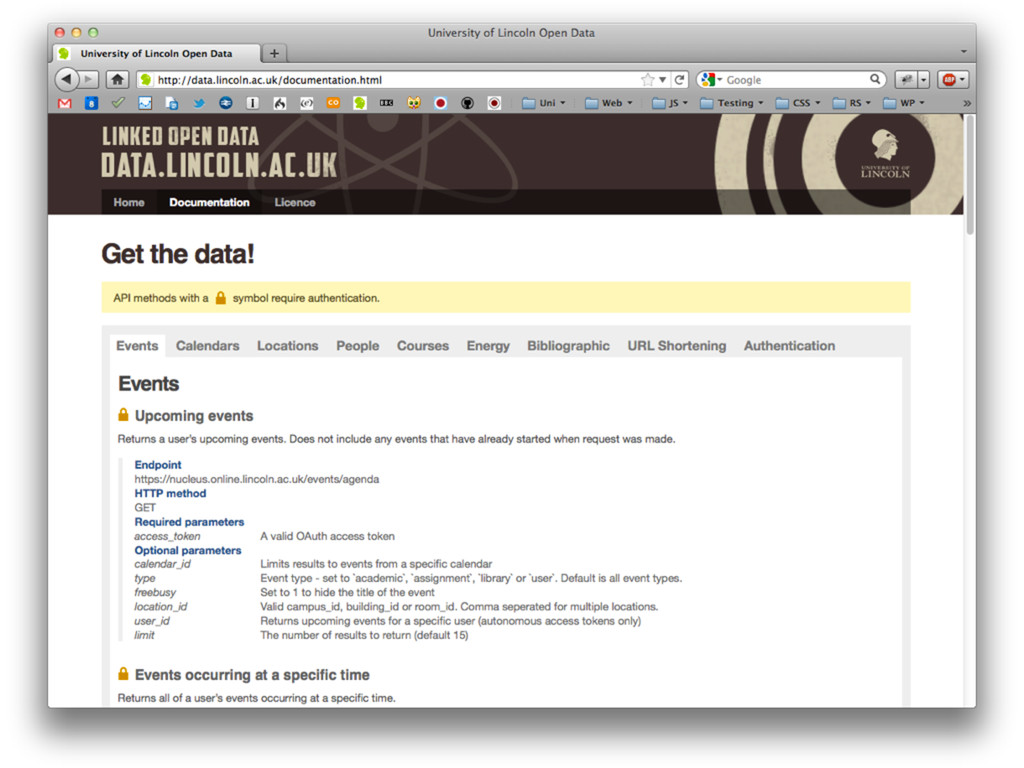
data.lincoln.ac.uk people energy location printing events calendars bibliographic documents
Internal and external authorisation
Open source 2.0 server lncn.eu/ar6
Any questions?
Thank you @jacksonj04


 jacksonj04
 akuwano
 gotok365
 henteko
 sogaoh
 joere
 ufried
 myohei
 shunghsiyu
 kubell_hr
 minorun365
 konifar
 nagix
 baasie
 skipperchong
 wjessup
 speakerdeck
 cassininazir
 axbom
 uxyall
 malarkey
 kastner
 chriscoyier
 dougneiner
 mraible