Share
Embed
Transcript
40 slides
-
Agenda 1. Introduction to threat modeling 2. Apply threat modeling
to identity systems and discover that passwords are the root of many problems. 3. If not passwords, then what? -
Scenario-Based Threat Modeling 1. Scenario: tell a story about an
imagined breach 2. Pre-mortem: trace contributing events 3. Mitigate: figure out where and how best to mitigate Photo by You X Ventures -
Threat Modeling Example Issue Mitigation CI/CD servers have over- scoped
AWS keys Evidence: enable CloudTrail Contain: IAM roles Eliminate: pull-based deploys Code contains OAuth secrets Prevent: move keys to env Eliminate: use Vault/KMS -
Shoulder Surfing Scenario: Jack, a disgruntled employee watches Alberta, the
CFO, log in, and remembers her password. He can now use her password to embezzle funds. Photo by David Rangel -
Shoulder Surfing Issue Mitigation Jack saw Alberta's password Prevent: masked
input Prevent: password complexity Jack can re-use Alberta's password (much) later Contain: password rotation Prevent: password complexity Eliminate: 2FA -
Password File Leak Scenario: a vulnerability in ping allowed Jack
to read /etc/passwd1, which has everyone's passwords in it. 1 Yes, I'm aware of /etc/shadow. I'm using this for simplicity. Photo by Matthew Brodeur -
Password File Leak Issue Mitigation Why didn't we fire Jack
after the last time? ¯\_(ϑ)_/¯ Jack can read anyone's password Prevent: hashed passwords Prevent: password complexity Jack can log in as anyone Contain: password rotation Eliminate: 2FA -
Classic Password Threat Mitigations • Masked input • Password complexity
• Password rotation • Hashed passwords • Two-Factor authentication Are these mitigations effective? -
The idea that a person is at fault when something
goes wrong is deeply entrenched in society. […] More and more often the blame is attributed to “human error.” The person involved can be fined, punished, or fired. But […], human error usually is a result of poor design: it should be called system error. Humans err continually; it is an intrinsic part of our nature. System design should take this into account. Pinning the blame on the person may be a comfortable way to proceed, but why was the system ever designed so that a single act by a single person could cause calamity? — Donald Norman, The Design of Everyday Things -
Verifiers SHOULD NOT impose other composition rules (e.g., requiring mixtures
of different character types or prohibiting consecutively repeated characters) for memorized secrets. Verifiers SHOULD NOT require memorized secrets to be changed arbitrarily (e.g., periodically). — NIST SP 800-63B -
Phishing Scenario: Yesterday your CEO received an email that seemed
to be from her admin, asking her to review some expenses on Dropbox. She followed the link, and entered her Dropbox account. Today, she realized when talking to her admin that he hadn't sent that email. -
Phishing Issue Mitigation The attacker has access to your Dropbox
Prevent: 2FA Your CEO may have used her Dropbox password elsewhere Contain: Password managers Your CEO couldn't tell the difference between the phishing site and the real Dropbox Eliminate: U2F -
Credential Stuffing Scenario: A service you use announces that they've
been breached, and that the attackers have everyone's email and passwords. Several of your staff use the same password for their corporate email.. -
Credential Stuffing Issue Mitigation Password re-use Respond: monitor @haveibeenpwnd Contain:
password managers Elminate: 2FA Elminate: SSO -
Common mitigations against modern attacks on passwords • Password managers
• 2FA (especially U2F) • Single-sign on (SSO) Are these mitigations effective? -
Password managers remain out of reach for most normal computer
users But I never found a way to get people onto 1password in a single training session. The setup process has a lot of moving parts, involving the desktop app, browser plugin, online service, mobile app, and app store. It requires repeatedly typing a long master passphrase. And then, once it is all set up, you have to train people on the unrelated skill of how to use the thing, starting with their most sensitive accounts. And then you leave. — Maciej Cegłowski, What I Learned Trying to Secure Congressional Campaigns -
Mitigation Effectiveness Usability Masked input not effective ! Password complexity
high, when used correctly ! Password rotation not effective " Hashed passwords moderate, when used correctly — Password managers high, if actually used ! 2FA (especially U2F) very effective ! Single-sign on (SSO) very effective # ✨ % -
If U2F is more secure than passwords, why use passwords?
If SSO is more than passwords, why use passwords? -
What would happen if we got rid of passwords? •
Shoulder surfing? • Password leaks? • Phishing? • Credential Stufffing? None of these attacks are effective if users don't have passwords to steal. -
If not passwords... what then? • Federated identity (Facebook, Google,
Github, etc) • Email login • Corporate identity (SAML/OIDC) -
Federated Identity • Great for most consumer-oriented identity systems •
UX is good, though beware of too many identity options. • Unfortunately, forces a tradeoff between privacy and security. • I dream about IndieAuth become widespread, but don't hold your breath. -
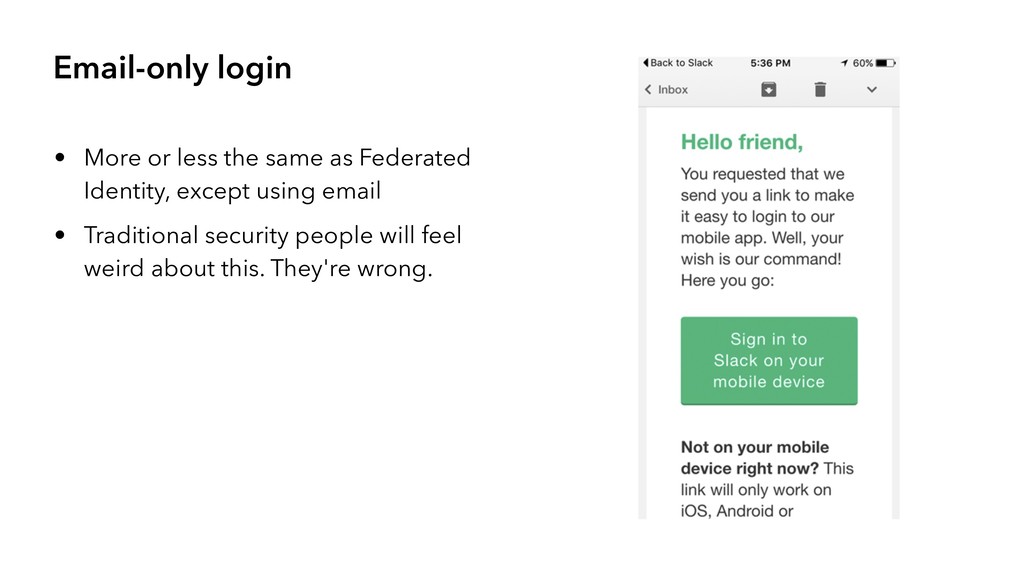
Email-only login • More or less the same as Federated
Identity, except using email • Traditional security people will feel weird about this. They're wrong. -
Corporate Identity • Almost every company with good security practices
uses some sort of corporate identity provider. If you're selling to businesses, you need to support this. • Two standards: SAML and OpenID Connect. Implement SAML first. -
TO •••• WITH PASSWORDS! Stop using passwords. The alternatives are
easier to use and more secure. Only roll your own identity system if you know what you're doing. Thanks! Jacob Kaplan-Moss [email protected] -
Further Reading • Post- and pre-mortem practice: The Infinite Hows
(or, the Dangers Of The Five Whys) • A fun source for scenarios: @badthingsdaily • Data on real-world attacks: • Data Breach Information Report • BusinessInsider ($$$) • Cost of Data Breach Report • On mitigation: The “Five Factors” Used To Secure Systems