Share
Embed
RPで受け入れる認証器を選択する~Idance lesson 2~
#iddance Lesson 2. Digital Identityの秋の資料です。
※ SlideshareからSpeaker Deckに移行しました。
https://www.slideshare.net/KentoGoro/idance-lesson-2

kg0r0
July 01, 2021
Transcript
53 slides
-
⽬次 • はじめに • FIDO2 登録概要 • 認証器のモデル・製品の特定 • MDSの利⽤
• WebAuthnの拡張 • まとめ -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
Registration(Overview) Authenticator Client Relying Party [2] challenge, user info, relying
party info [1] user info [4] relying party id, user info, relying party info, clientDataHash [5] user verification, new keypair, attestation [6] new public key, credential id, attestation [7] clientDataJSON, attestationObject [8] server validation [9] result [3] navigator.credentials.create() -
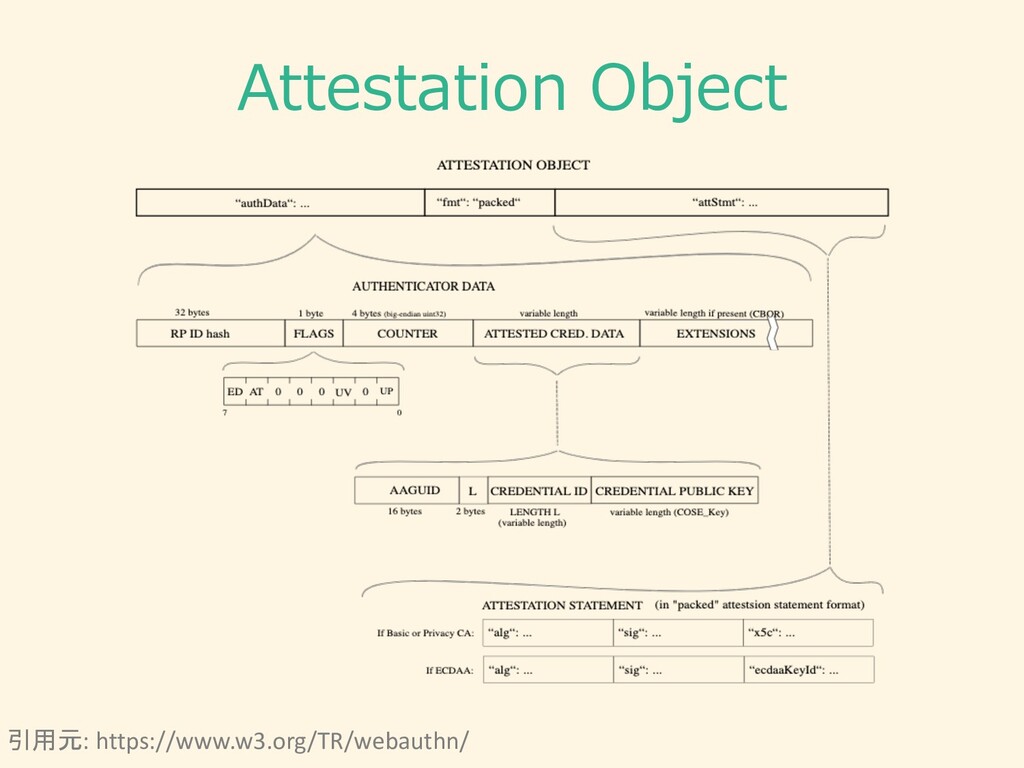
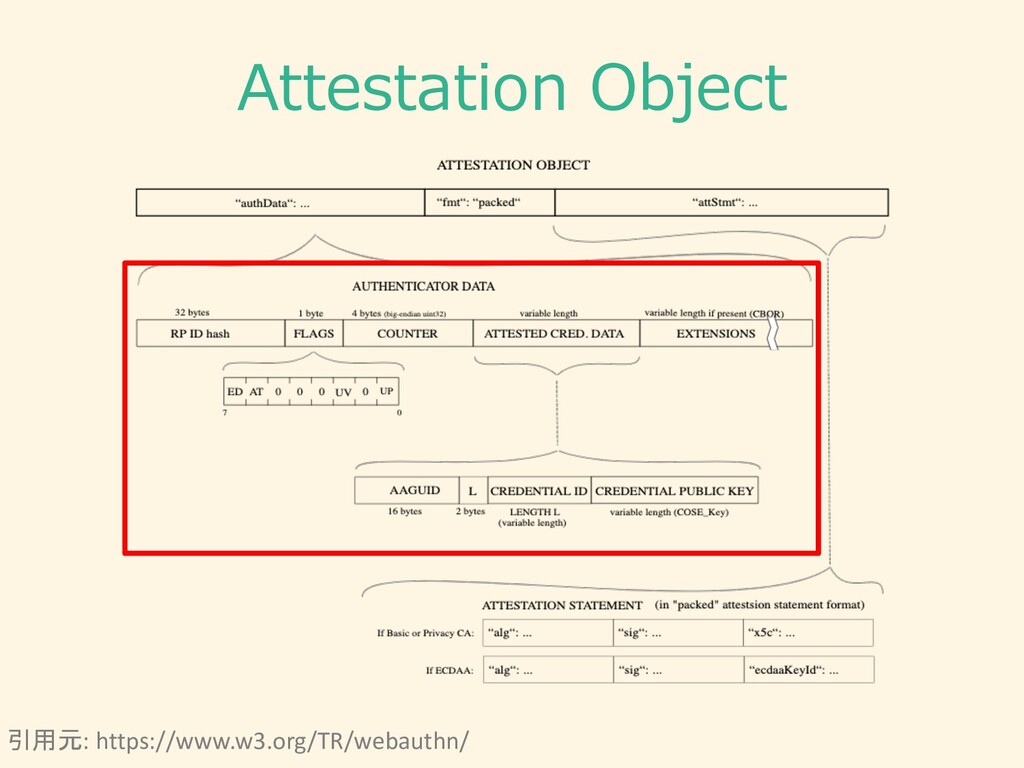
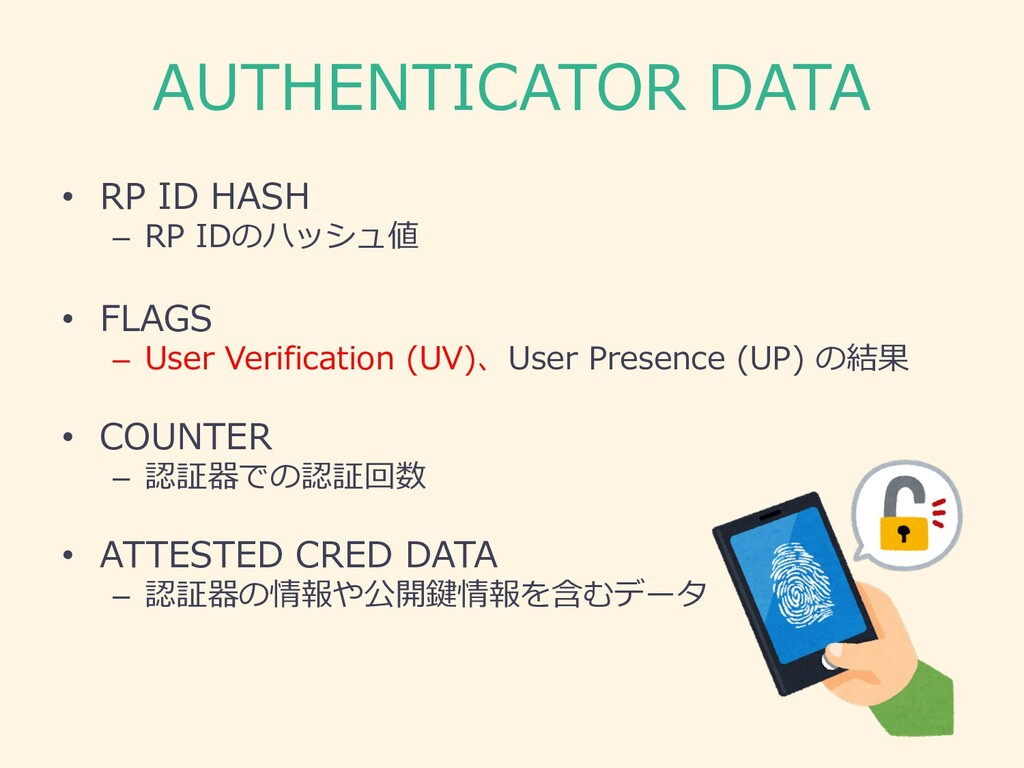
AUTHENTICATOR DATA • RP ID HASH – RP IDのハッシュ値 •
FLAGS – User Verification (UV)、User Presence (UP) の結果 • COUNTER – 認証器での認証回数 • ATTESTED CRED DATA – 認証器の情報や公開鍵情報を含むデータ -
AUTHENTICATOR DATA • RP ID HASH – RP IDのハッシュ値 •
FLAGS – User Verification (UV)、User Presence (UP) の結果 • COUNTER – 認証器での認証回数 • ATTESTED CRED DATA – 認証器の情報や公開鍵情報を含むデータ -
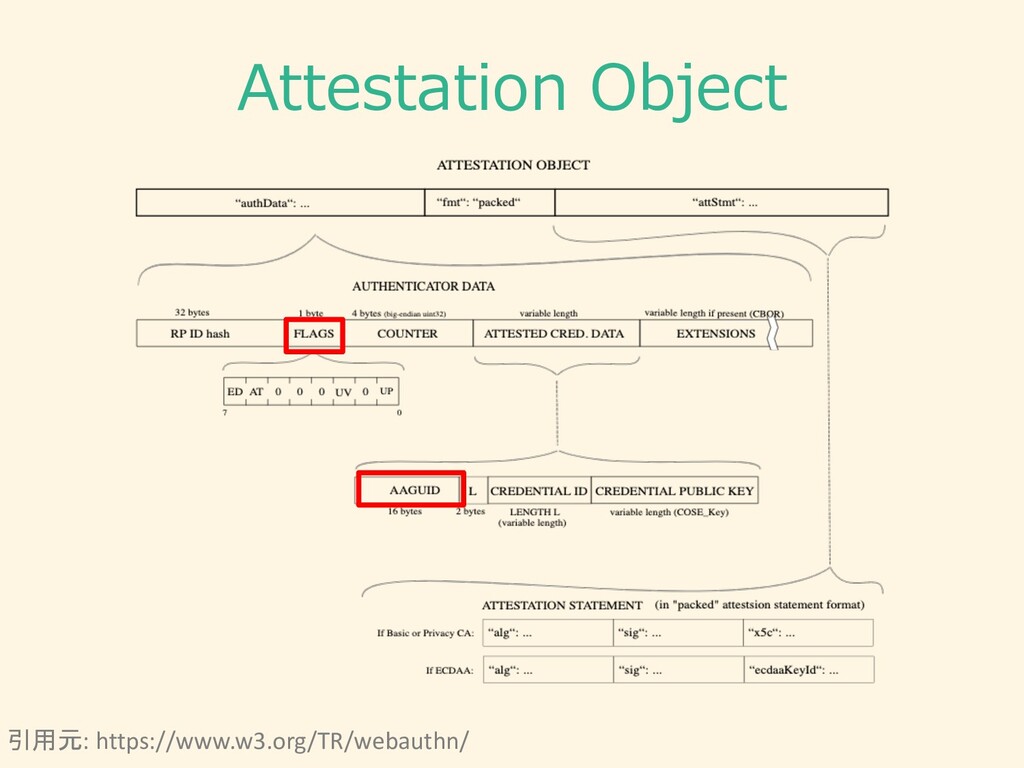
AUTHENTICATOR DATA • RP ID HASH – RP IDのハッシュ値 •
FLAGS – User Verification (UV)、User Presence (UP) の結果 • COUNTER – 認証器での認証回数 • ATTESTED CRED DATA – 認証器の情報や公開鍵情報を含むデータ -
AUTHENTICATOR DATA • RP ID HASH – RP IDのハッシュ値 •
FLAGS – User Verification (UV)、User Presence (UP) の結果 • COUNTER – 認証器での認証回数 • ATTESTED CRED DATA – 認証器の情報や公開鍵情報を含むデータ -
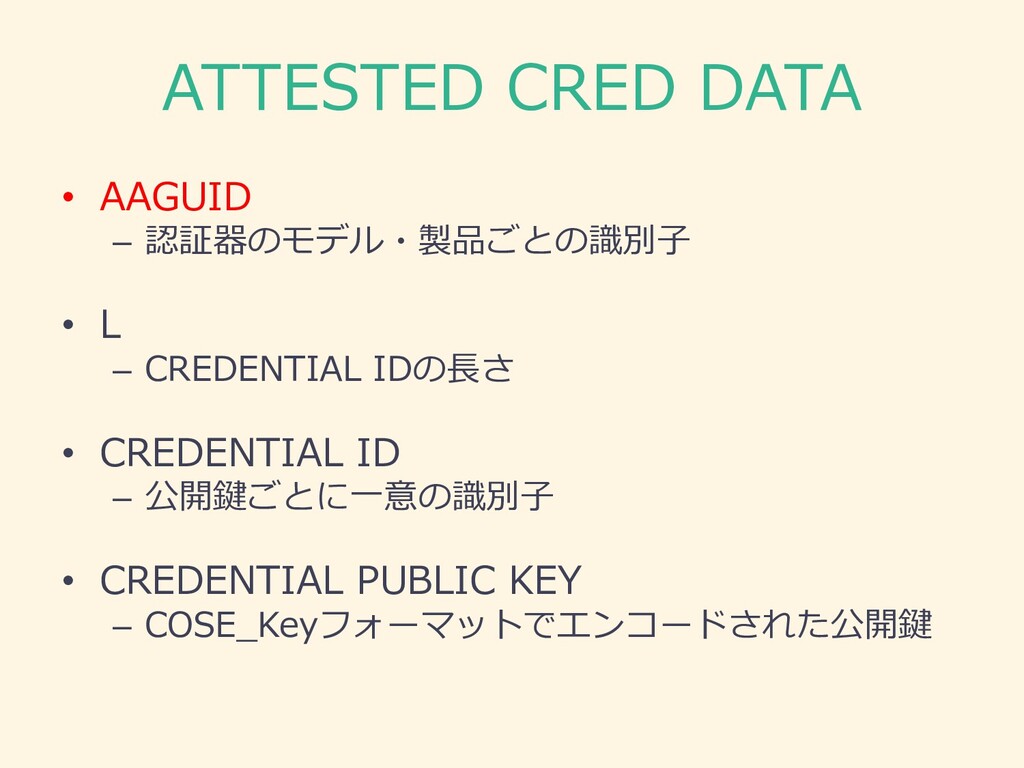
ATTESTED CRED DATA • AAGUID – 認証器のモデル・製品ごとの識別⼦ • L –
CREDENTIAL IDの⻑さ • CREDENTIAL ID – 公開鍵ごとに⼀意の識別⼦ • CREDENTIAL PUBLIC KEY – COSE_Keyフォーマットでエンコードされた公開鍵 -
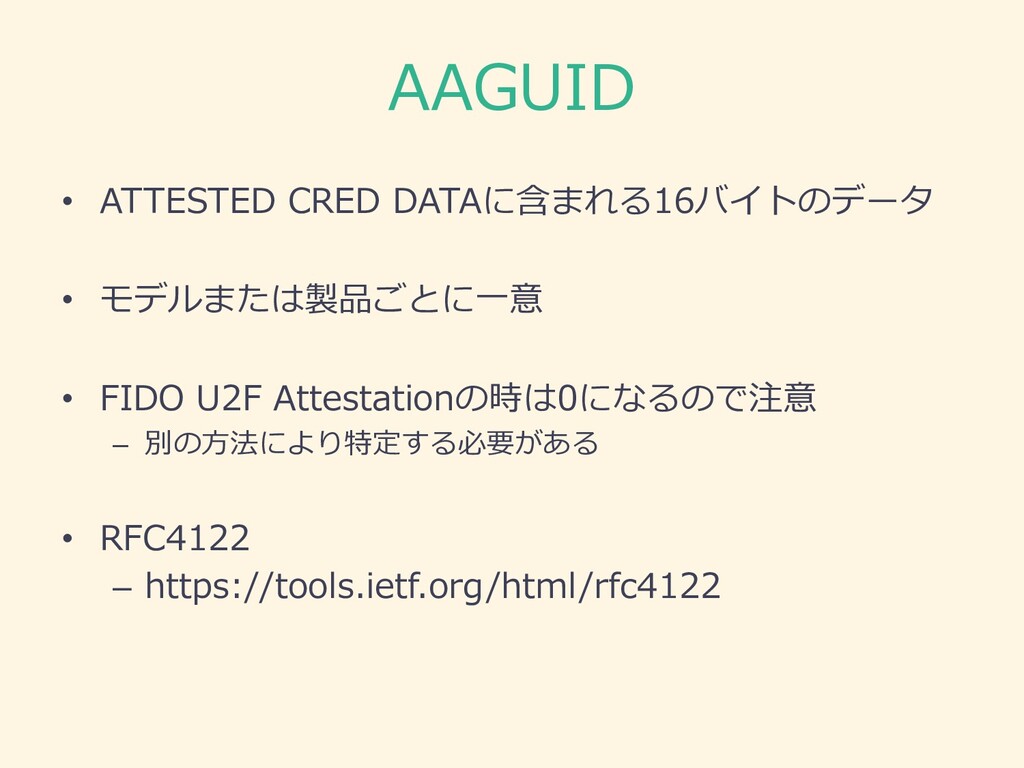
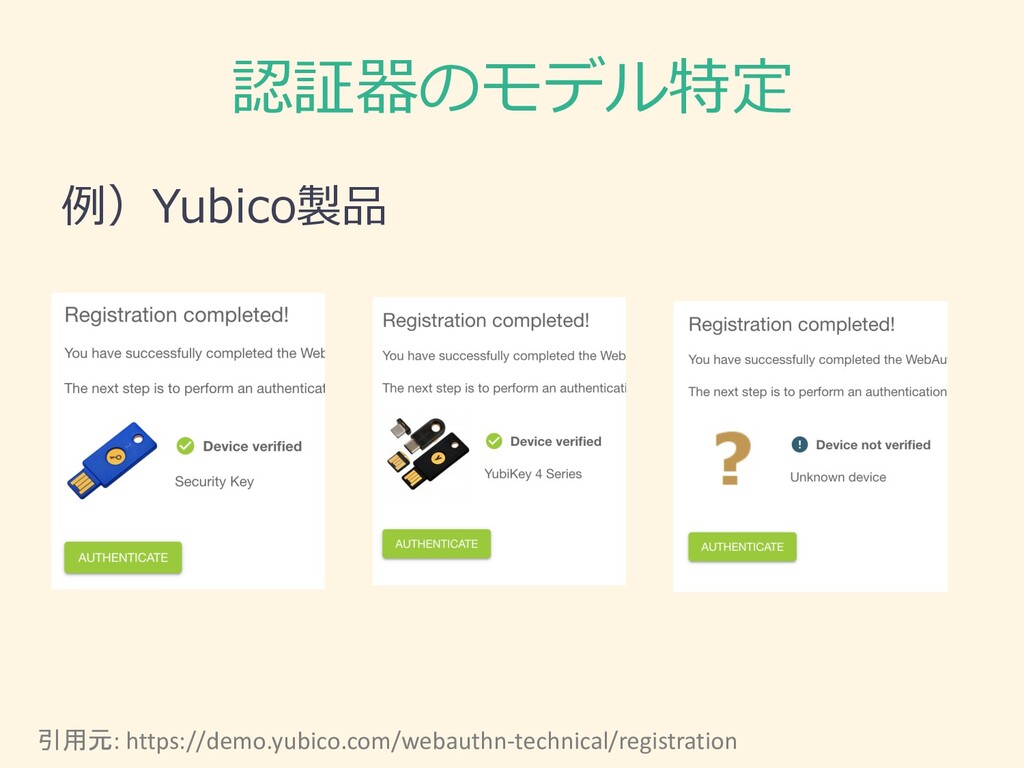
AAGUID • ATTESTED CRED DATAに含まれる16バイトのデータ • モデルまたは製品ごとに⼀意 • FIDO U2F
Attestationの時は0になるので注意 – 別の⽅法により特定する必要がある • RFC4122 – https://tools.ietf.org/html/rfc4122 -
認証器の詳細情報を取得 • さらに認証器に関する情報を取得 • FIDO MDS (Metadata Service) を利⽤ •
AAGUIDからメタデータを検索 -
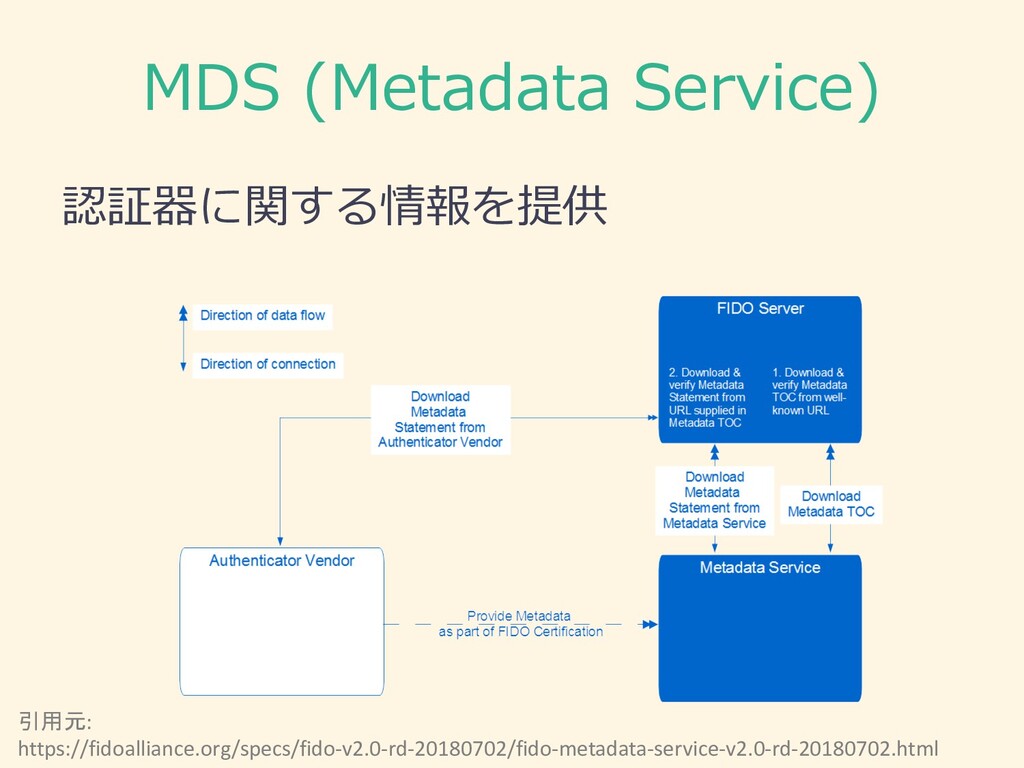
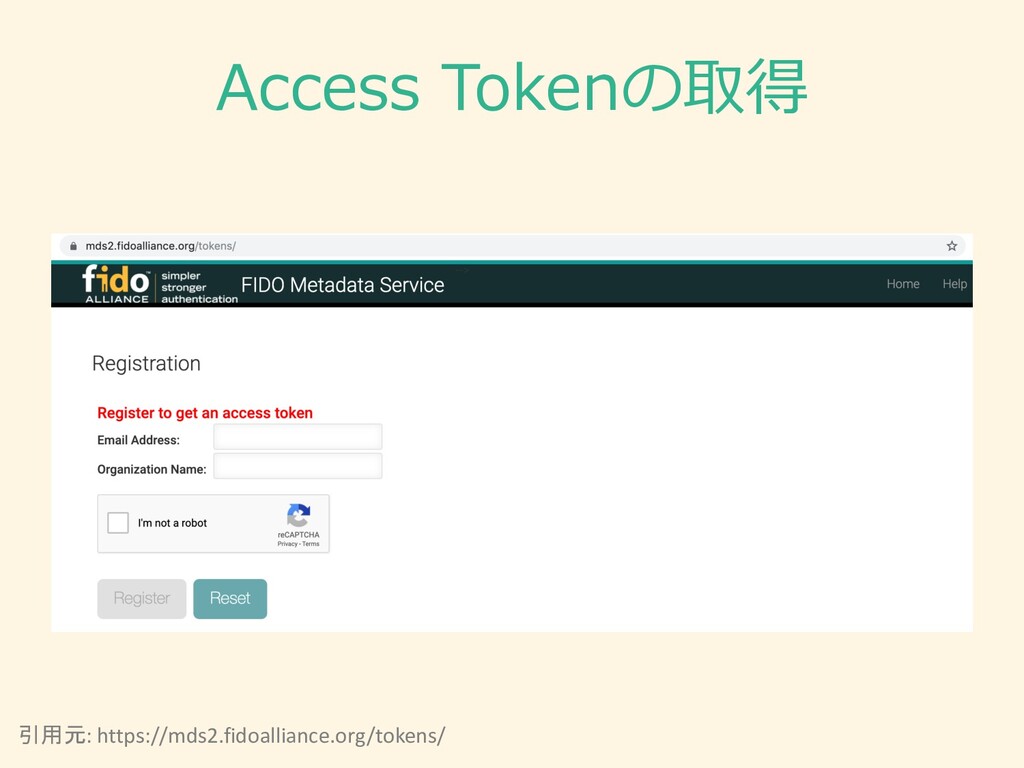
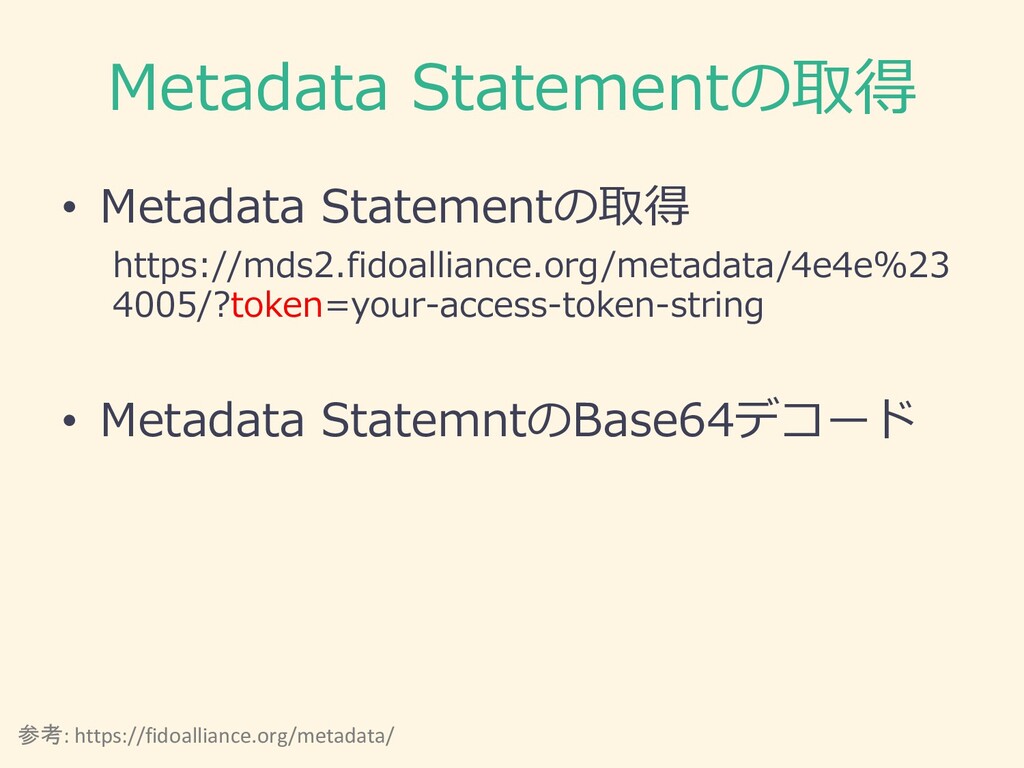
MDS利⽤の流れ • Access Tokenの取得 • Metadata TOC (Table of Contents)
の取得 – metadata statementのURL – metadata statementを検証するためのデータ • Metadata Statementの取得 – 認証器に関する情報 -
Metadata TOCの取得・検証 • Metadata TOC (JWT) の取得 – https://mds2.fidoalliance.org/?token=your- access-token-string
• FIDO AllianceからRoot証明書の取得 • Root証明書の検証 • TOCの検証 参考: https://fidoalliance.org/metadata/ -
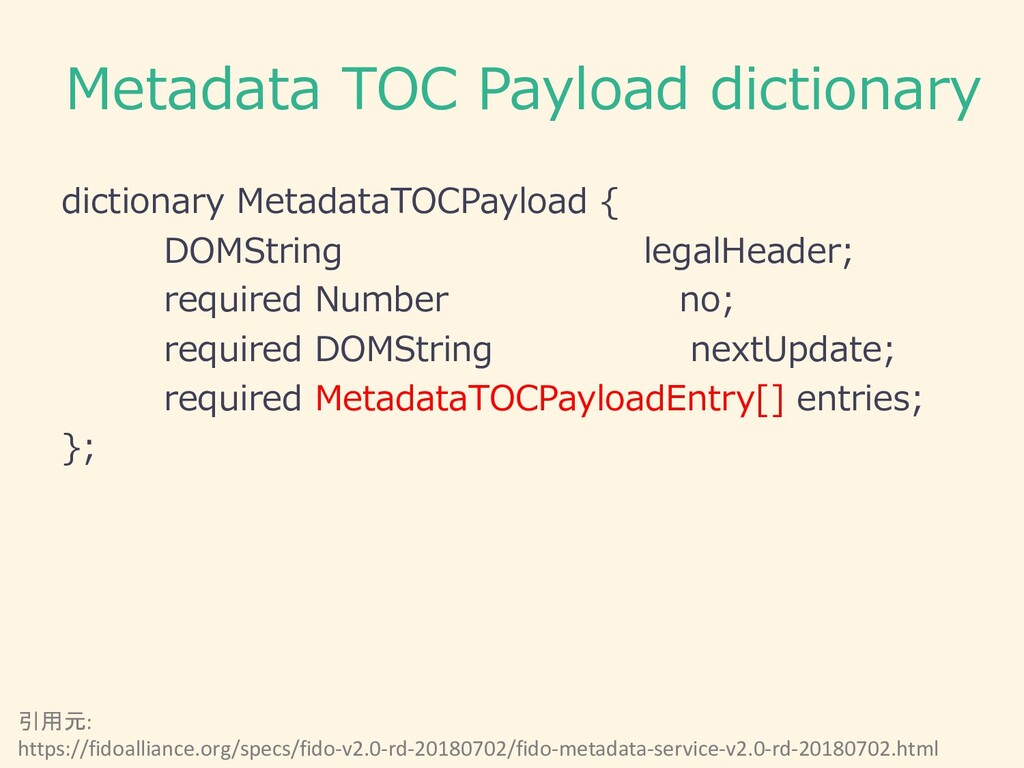
Metadata TOC Payload dictionary dictionary MetadataTOCPayload { DOMString legalHeader; required
Number no; required DOMString nextUpdate; required MetadataTOCPayloadEntry[] entries; }; 引用元: https://fidoalliance.org/specs/fido-v2.0-rd-20180702/fido-metadata-service-v2.0-rd-20180702.html -
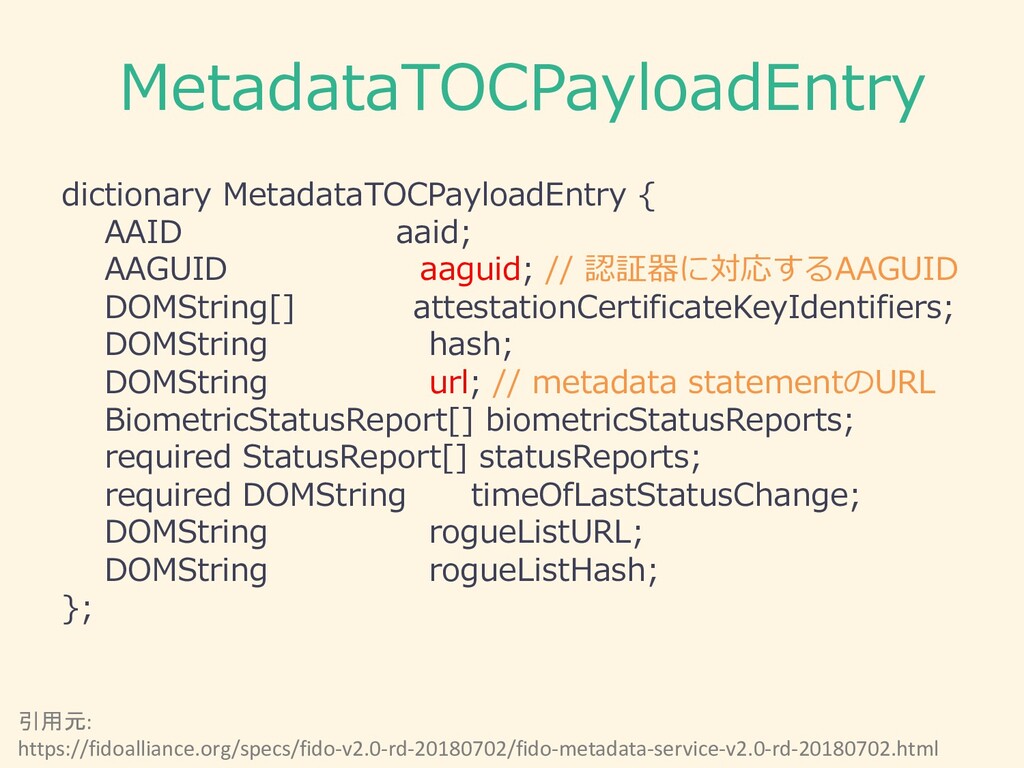
MetadataTOCPayloadEntry dictionary MetadataTOCPayloadEntry { AAID aaid; AAGUID aaguid; // 認証器に対応するAAGUID
DOMString[] attestationCertificateKeyIdentifiers; DOMString hash; DOMString url; // metadata statementのURL BiometricStatusReport[] biometricStatusReports; required StatusReport[] statusReports; required DOMString timeOfLastStatusChange; DOMString rogueListURL; DOMString rogueListHash; }; 引用元: https://fidoalliance.org/specs/fido-v2.0-rd-20180702/fido-metadata-service-v2.0-rd-20180702.html -
MetadataTOCPayloadEntry (⼀部) • biometricStatusReports – 認証器の⽣体認証要素のFIDO Biometric Certificationのステー タス •
statusReports – 認証器のステータス – e.g. NOT_FIDO_CERTIFIED, FIDO_CERTIFIED REVOKED, USER_VERIFICATION_BYPASS • timeOfLastStatusChange – status reposrtの値がセットされた⽇付 • rogueListURL – 信頼できない認証器のリストのURL -
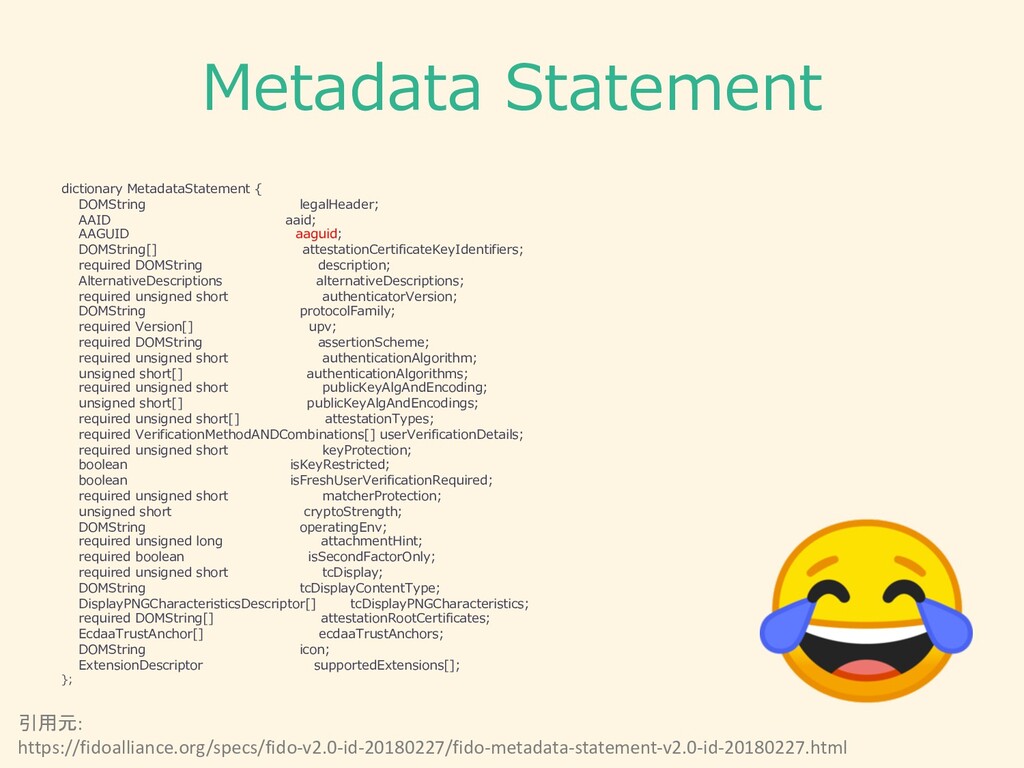
Metadata Statement dictionary MetadataStatement { DOMString legalHeader; AAID aaid; AAGUID
aaguid; DOMString[] attestationCertificateKeyIdentifiers; required DOMString description; AlternativeDescriptions alternativeDescriptions; required unsigned short authenticatorVersion; DOMString protocolFamily; required Version[] upv; required DOMString assertionScheme; required unsigned short authenticationAlgorithm; unsigned short[] authenticationAlgorithms; required unsigned short publicKeyAlgAndEncoding; unsigned short[] publicKeyAlgAndEncodings; required unsigned short[] attestationTypes; required VerificationMethodANDCombinations[] userVerificationDetails; required unsigned short keyProtection; boolean isKeyRestricted; boolean isFreshUserVerificationRequired; required unsigned short matcherProtection; unsigned short cryptoStrength; DOMString operatingEnv; required unsigned long attachmentHint; required boolean isSecondFactorOnly; required unsigned short tcDisplay; DOMString tcDisplayContentType; DisplayPNGCharacteristicsDescriptor[] tcDisplayPNGCharacteristics; required DOMString[] attestationRootCertificates; EcdaaTrustAnchor[] ecdaaTrustAnchors; DOMString icon; ExtensionDescriptor supportedExtensions[]; }; 引用元: https://fidoalliance.org/specs/fido-v2.0-id-20180227/fido-metadata-statement-v2.0-id-20180227.html -
Metadata Statement dictionary MetadataStatement { DOMString legalHeader; AAID aaid; AAGUID
aaguid; DOMString[] attestationCertificateKeyIdentifiers; required DOMString description; AlternativeDescriptions alternativeDescriptions; required unsigned short authenticatorVersion; DOMString protocolFamily; required Version[] upv; required DOMString assertionScheme; required unsigned short authenticationAlgorithm; unsigned short[] authenticationAlgorithms; required unsigned short publicKeyAlgAndEncoding; unsigned short[] publicKeyAlgAndEncodings; required unsigned short[] attestationTypes; required VerificationMethodANDCombinations[] userVerificationDetails; required unsigned short keyProtection; boolean isKeyRestricted; boolean isFreshUserVerificationRequired; required unsigned short matcherProtection; unsigned short cryptoStrength; DOMString operatingEnv; required unsigned long attachmentHint; required boolean isSecondFactorOnly; required unsigned short tcDisplay; DOMString tcDisplayContentType; DisplayPNGCharacteristicsDescriptor[] tcDisplayPNGCharacteristics; required DOMString[] attestationRootCertificates; EcdaaTrustAnchor[] ecdaaTrustAnchors; DOMString icon; ExtensionDescriptor supportedExtensions[]; }; 引用元: https://fidoalliance.org/specs/fido-v2.0-id-20180227/fido-metadata-statement-v2.0-id-20180227.html // 認証器に対応するAAGUID -
Metadata Statement (⼀部) • Key Protection: 秘密鍵の保護⽅法 – KEY_PROTECTION_SOFTWARE 0x0001
– KEY_PROTECTION_HARDWARE 0x0002 – KEY_PROTECTION_TEE 0x0004 – KEY_PROTECTION_SECURE_ELEMENT 0x0008 – KEY_PROTECTION_REMOTE_HANDLE 0x0010 • Matcher Protection Types: ユーザー認証を実⾏するマッチャーの保護⽅法 – MATCHER_PROTECTION_SOFTWARE 0x0001 – MATCHER_PROTECTION_TEE 0x0002 – MATCHER_PROTECTION_ON_CHIP 0x0004 • AttachmentHint: 認証器の接続⽅法 – ATTACHMENT_HINT_INTERNAL 0x0001 – ATTACHMENT_HINT_EXTERNAL 0x0002 – ATTACHMENT_HINT_WIRED 0x0004 – ATTACHMENT_HINT_WIRELESS 0x0008 – ATTACHMENT_HINT_NFC 0x0010 – ATTACHMENT_HINT_BLUETOOTH 0x0020 – ATTACHMENT_HINT_NETWORK 0x0040 – ATTACHMENT_HINT_READY 0x0080 引用元: https://fidoalliance.org/specs/fido-v2.0-id-20180227/fido-registry-v2.0-id-20180227.html -
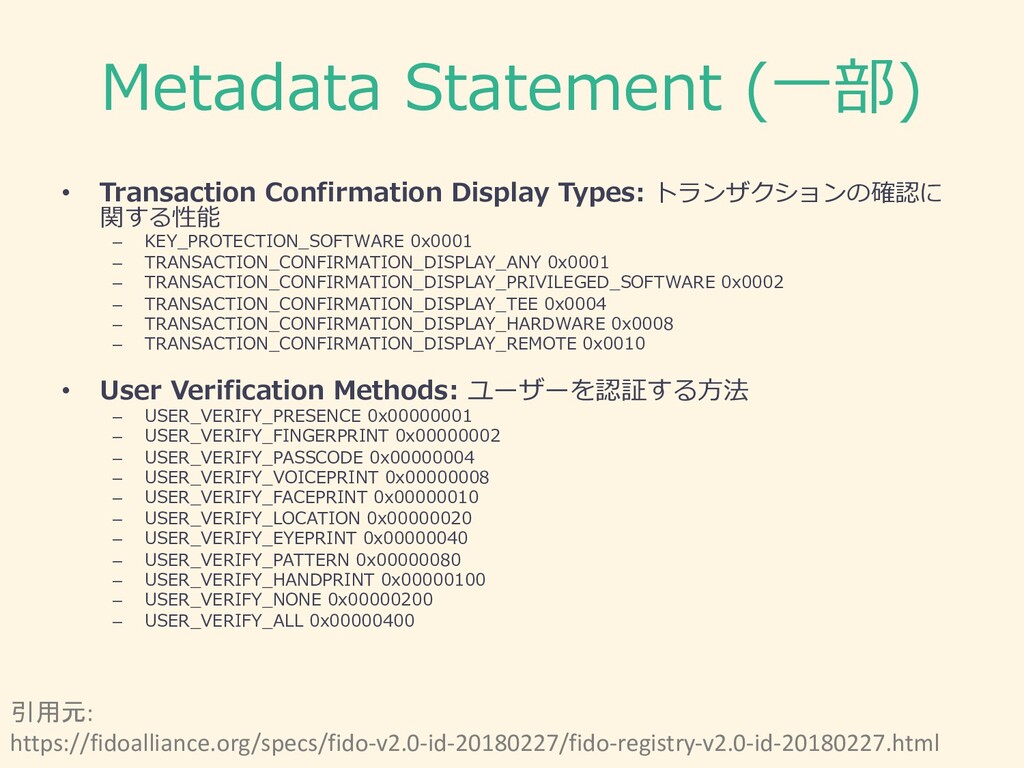
Metadata Statement (⼀部) • Transaction Confirmation Display Types: トランザクションの確認に 関する性能
– KEY_PROTECTION_SOFTWARE 0x0001 – TRANSACTION_CONFIRMATION_DISPLAY_ANY 0x0001 – TRANSACTION_CONFIRMATION_DISPLAY_PRIVILEGED_SOFTWARE 0x0002 – TRANSACTION_CONFIRMATION_DISPLAY_TEE 0x0004 – TRANSACTION_CONFIRMATION_DISPLAY_HARDWARE 0x0008 – TRANSACTION_CONFIRMATION_DISPLAY_REMOTE 0x0010 • User Verification Methods: ユーザーを認証する⽅法 – USER_VERIFY_PRESENCE 0x00000001 – USER_VERIFY_FINGERPRINT 0x00000002 – USER_VERIFY_PASSCODE 0x00000004 – USER_VERIFY_VOICEPRINT 0x00000008 – USER_VERIFY_FACEPRINT 0x00000010 – USER_VERIFY_LOCATION 0x00000020 – USER_VERIFY_EYEPRINT 0x00000040 – USER_VERIFY_PATTERN 0x00000080 – USER_VERIFY_HANDPRINT 0x00000100 – USER_VERIFY_NONE 0x00000200 – USER_VERIFY_ALL 0x00000400 引用元: https://fidoalliance.org/specs/fido-v2.0-id-20180227/fido-registry-v2.0-id-20180227.html -
Registration(Overview) Authenticator Client Relying Party [1] access token MDS [4]
metadata statement [3] access token [2] metadata TOC [5] user info [6] challenge, user info, relying party info [7] relying party id, user info, relying party info, clientDataHash [8] user verification, new keypair, attestation [9] new public key, credential id, attestation [10]clientDataJSON, attestationObject (AAGUID) [11] server validation (check AAGUID) [12] result -
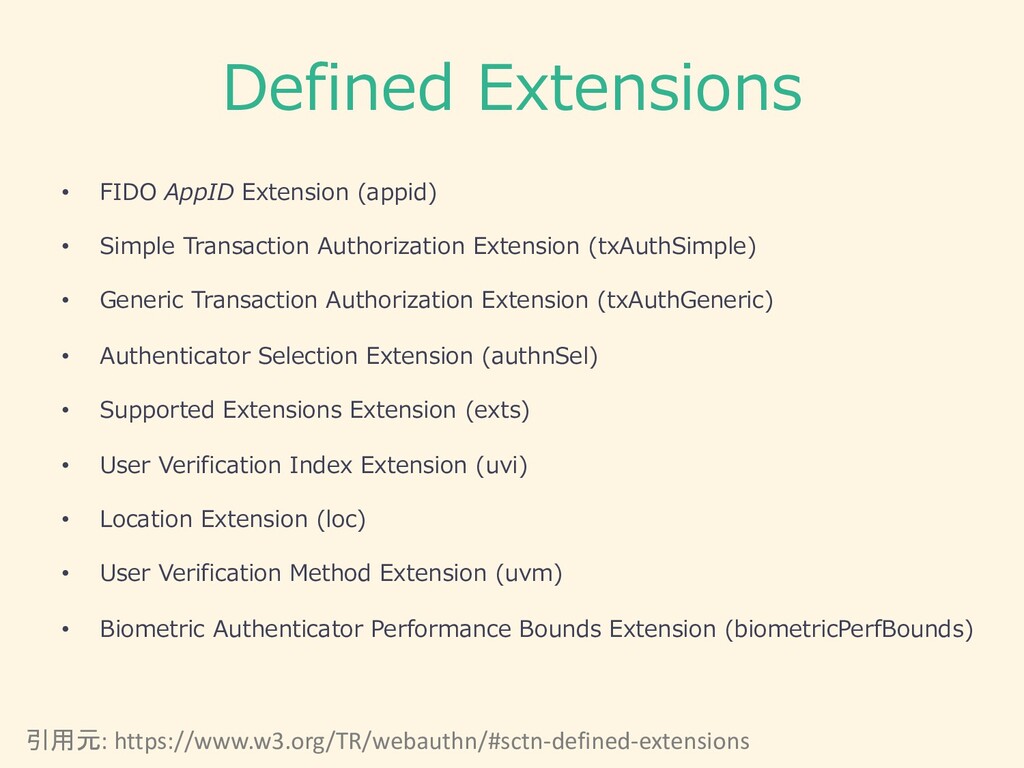
Defined Extensions • FIDO AppID Extension (appid) • Simple Transaction
Authorization Extension (txAuthSimple) • Generic Transaction Authorization Extension (txAuthGeneric) • Authenticator Selection Extension (authnSel) • Supported Extensions Extension (exts) • User Verification Index Extension (uvi) • Location Extension (loc) • User Verification Method Extension (uvm) • Biometric Authenticator Performance Bounds Extension (biometricPerfBounds) 引用元: https://www.w3.org/TR/webauthn/#sctn-defined-extensions -
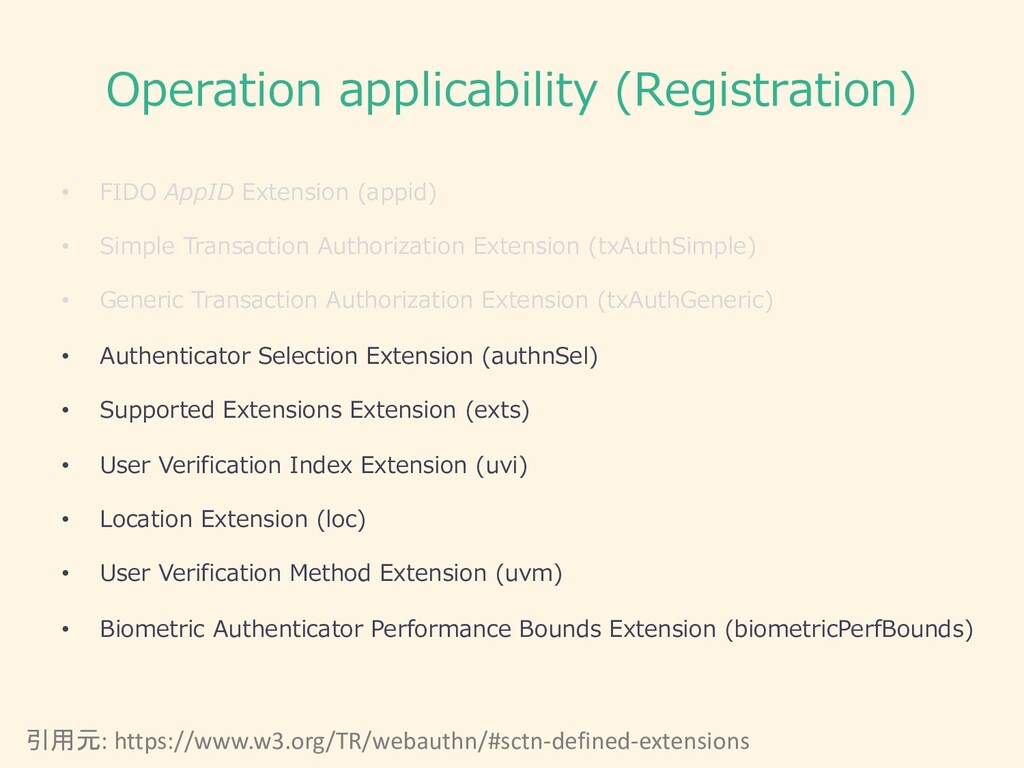
Operation applicability (Registration) • FIDO AppID Extension (appid) • Simple
Transaction Authorization Extension (txAuthSimple) • Generic Transaction Authorization Extension (txAuthGeneric) • Authenticator Selection Extension (authnSel) • Supported Extensions Extension (exts) • User Verification Index Extension (uvi) • Location Extension (loc) • User Verification Method Extension (uvm) • Biometric Authenticator Performance Bounds Extension (biometricPerfBounds) 引用元: https://www.w3.org/TR/webauthn/#sctn-defined-extensions -
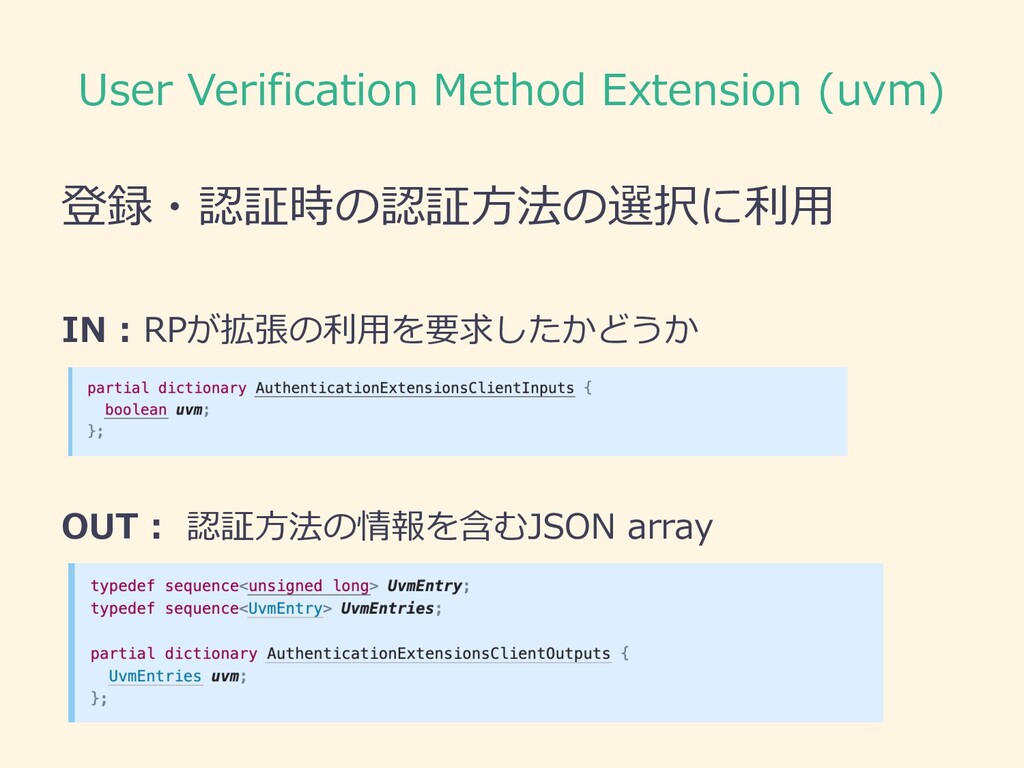
User Verification Method Extension (uvm) 登録・認証時の認証⽅法の選択に利⽤ IN : RPが拡張の利⽤を要求したかどうか OUT
: 認証⽅法の情報を含むJSON array -
Biometric Authenticator Performance Bounds Extension (biometricPerfBounds) 登録時に受け⼊れる⽣体認証器の性能 IN : ⽣体認証の性能限界
• FAR (maximum false acceptance rate) • FRR (maximum false rejection rate) -
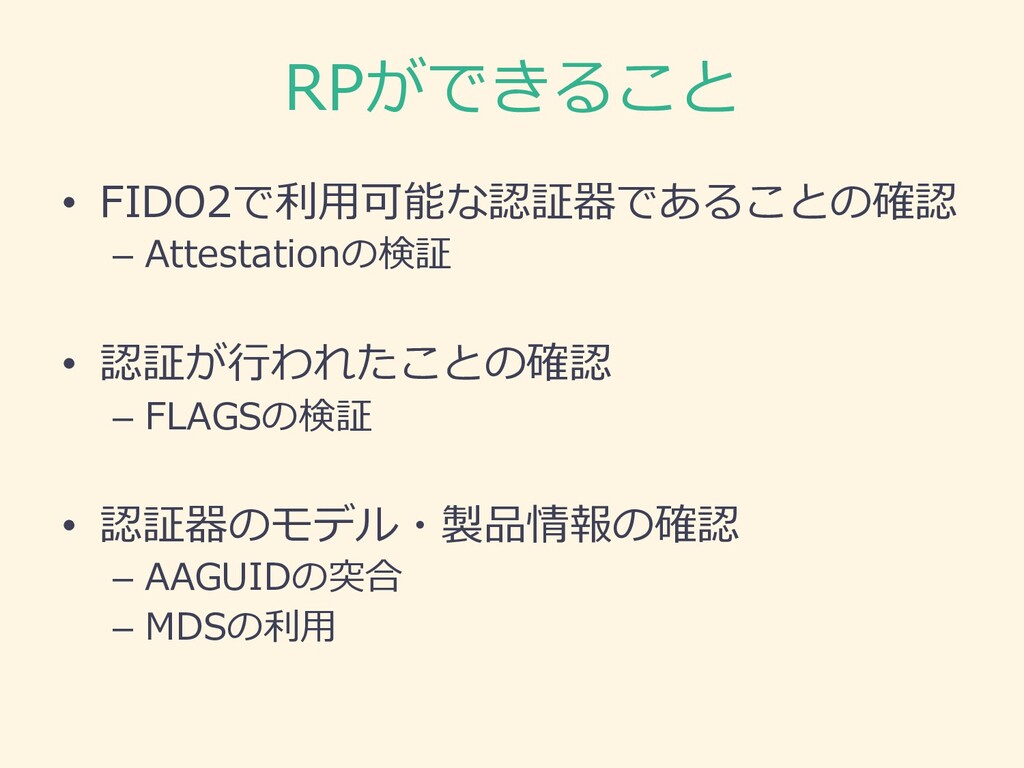
RPができること • FIDO2で利⽤可能な認証器であることの確認 – Attestationの検証 • 認証が⾏われたことの確認 – FLAGSの検証 •
認証器のモデル・製品情報の確認 – AAGUIDの突合 – MDSの利⽤ -
参考 • Web Authentication: An API for accessing Public Key
Credentials Level 1 https://www.w3.org/TR/webauthn/ • FIDO Registry of Predefined Values https://fidoalliance.org/specs/fido-v2.0-id-20180227/fido-registry-v2.0-id- 20180227.html • Test your YubiKey with WebAuthn https://demo.yubico.com/webauthn-technical/registration • FIDO Metadata Service https://fidoalliance.org/specs/fido-v2.0-rd-20180702/fido-metadata-service- v2.0-rd-20180702.html • FIDO Metadata Statements https://fidoalliance.org/specs/fido-v2.0-id-20180227/fido-metadata-statement- v2.0-id-20180227.html
 kg0r0
 takuyay0ne
 littlehands
 akuwano
 orimanabu
 naltatis
 techniczna
 inariku
 wadayusuke
 yoshidashingo
 miu_crescent
 daishukojima
 stephaniewalter
 addyosmani
 popppiees
 morganepeng
 twada
 trallard
 gurzu
 cassininazir
 tammyeverts
 joshbly
 codingconduct