Share
Embed
End-to-End encryption cookbook
MobileOptimized 2016 http://mo.dev.by/english.html
Video: https://www.youtube.com/watch?v=TI3tkdMJe9w
Marcin Krzyzanowski
July 15, 2016
Transcript
44 slides
-
AGENDA • What is E2EE • Naive approach • Real
world solutions • fundamentals • protocols -
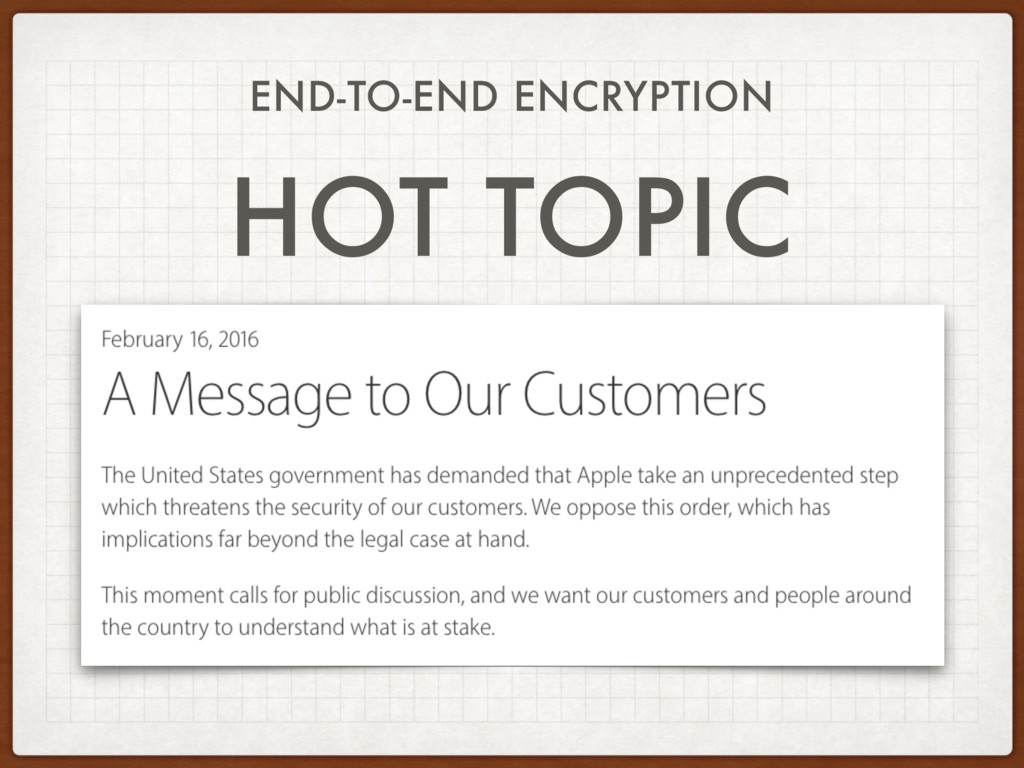
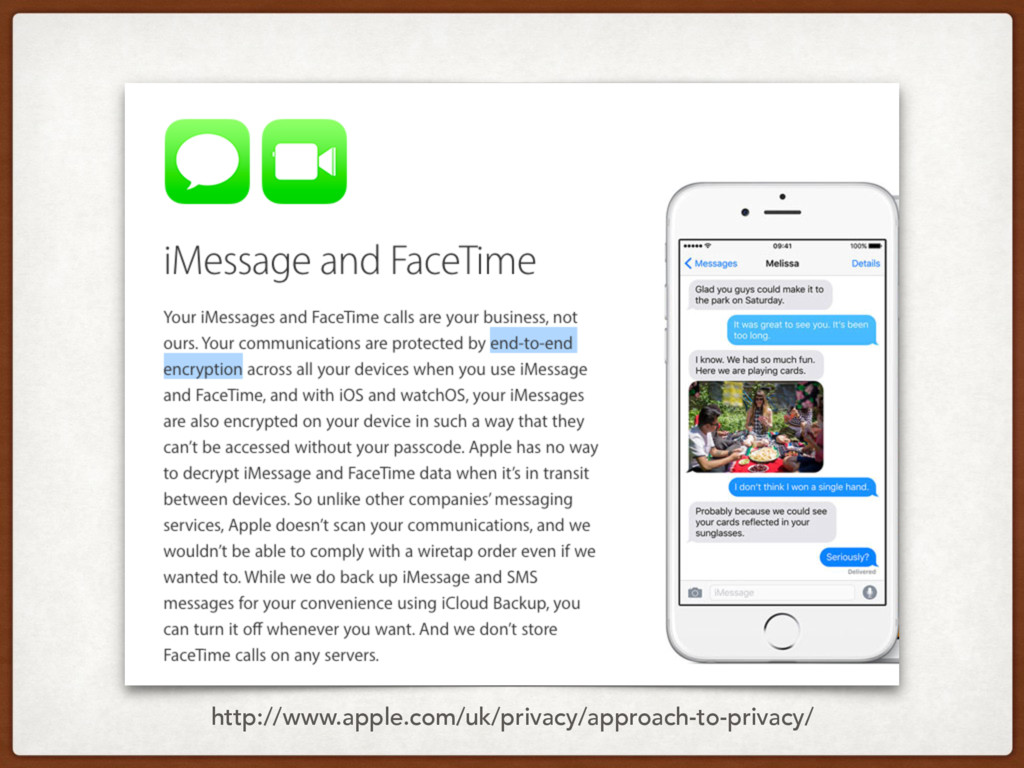
http://www.apple.com/uk/privacy/approach-to-privacy/ - Apple has no way to decrypt iMessage and
FaceTime data when it’s in transit between devices. - We wouldn’t be able to comply with a wiretap order even if we wanted to. - So unlike other companies’ messaging services, Apple doesn’t scan your communications -
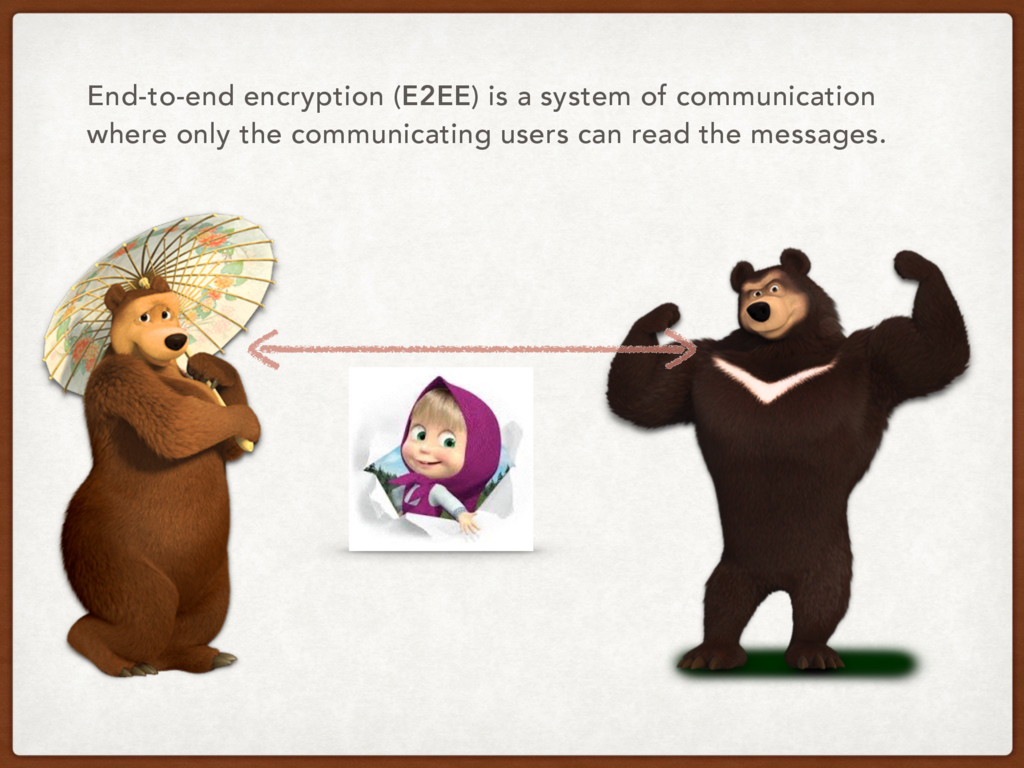
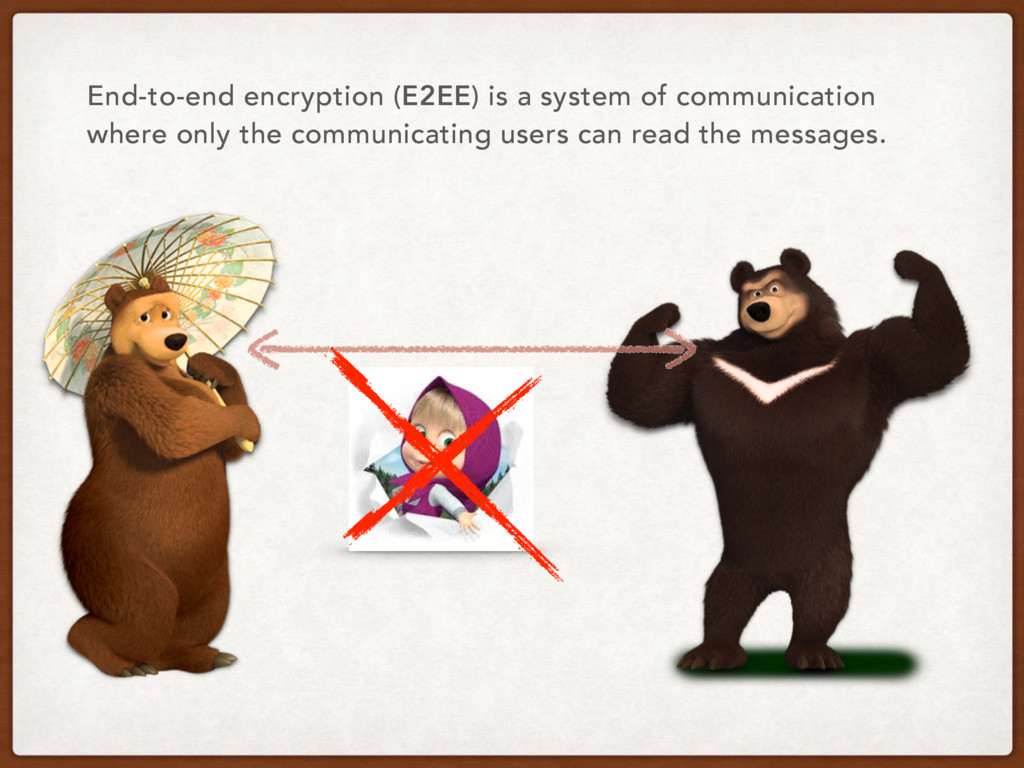
End-to-end encryption (E2EE) is a system of communication where only
the communicating users can read the messages. prevents potential eavesdroppers from being able to access conversation. -
End-to-end encryption (E2EE) is a system of communication where only
the communicating users can read the messages. -
End-to-end encryption (E2EE) is a system of communication where only
the communicating users can read the messages. -
End-to-end encryption (E2EE) is a system of communication where only
the communicating users can read the messages. -
End-to-end encryption (E2EE) is a system of communication where only
the communicating users can read the messages. -
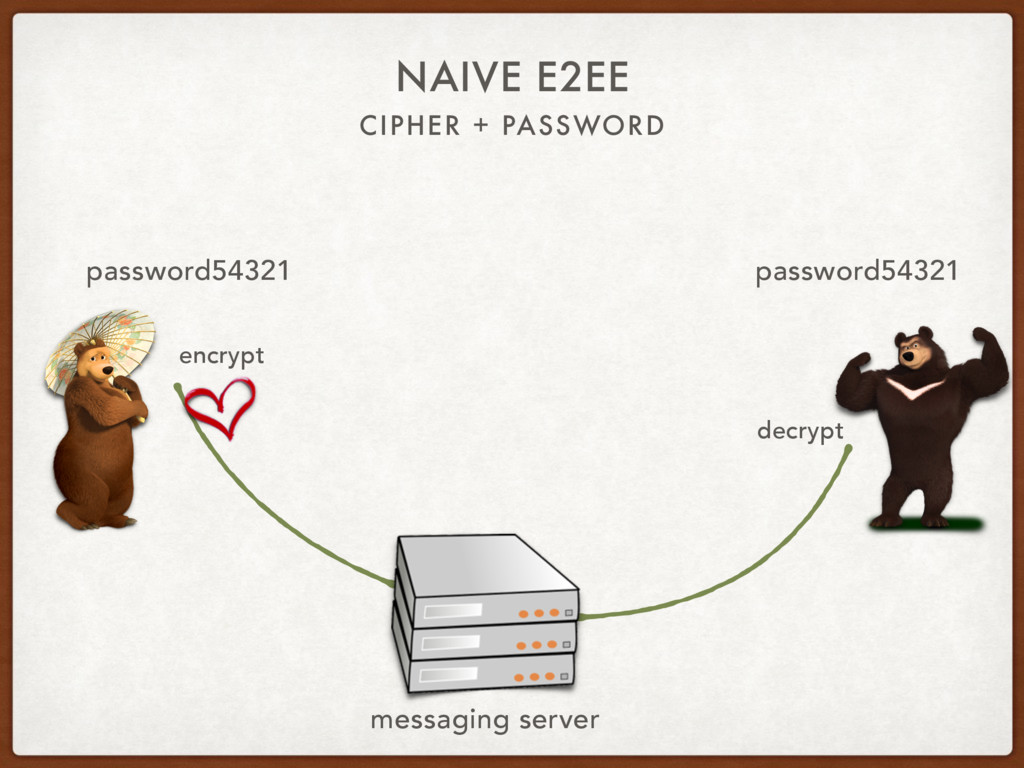
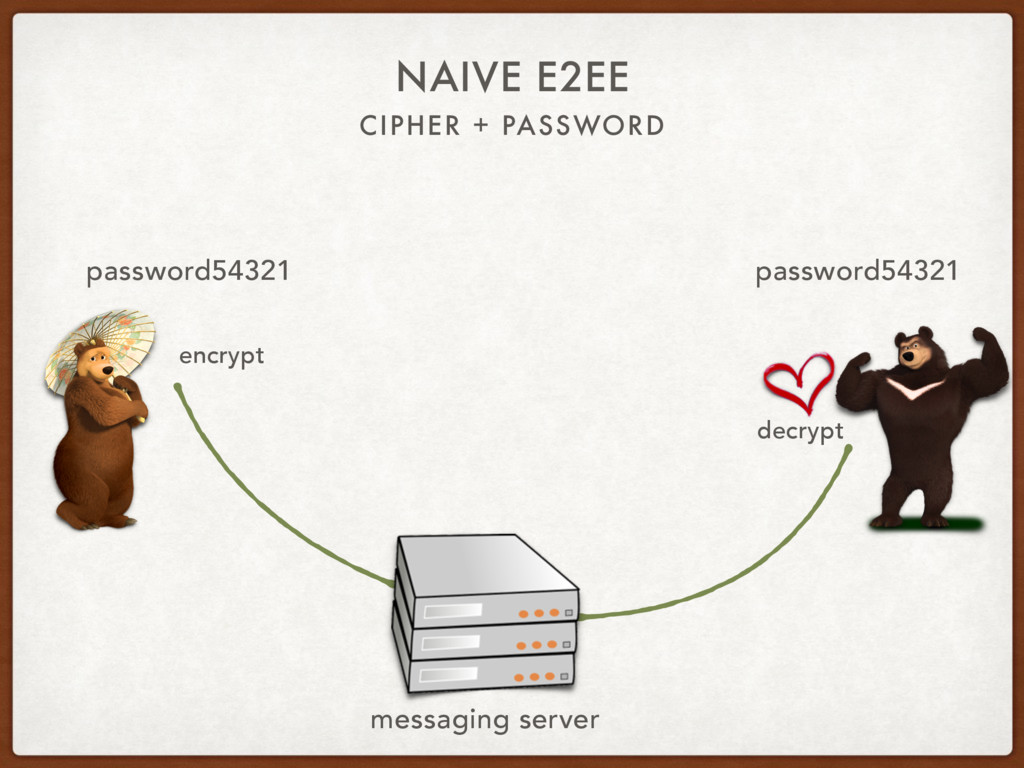
CIPHER + PASSWORD NAIVE E2EE • Two ends • CIPHER
• AES, ChaCha20… • PASSWORD/KEY • password • time based one-time password • Distribute password • printed, mailed, whispered • shared table of passwords, time based password -
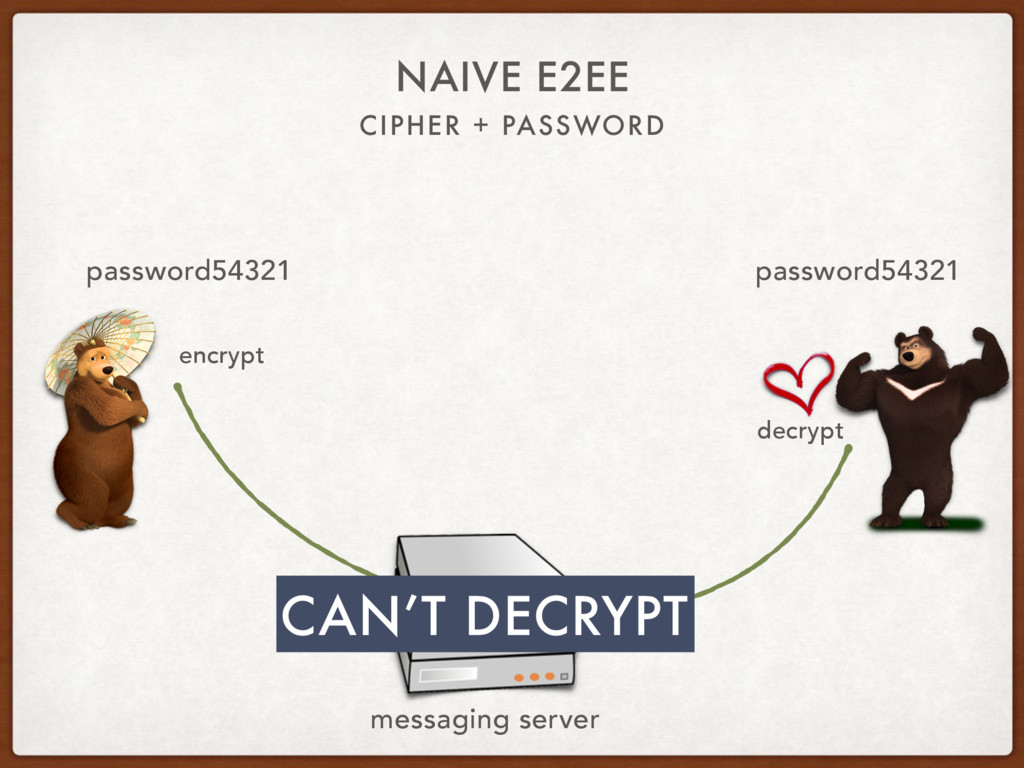
CIPHER + PASSWORD NAIVE E2EE password54321 password54321 decrypt encrypt messaging
server CAN’T DECRYPT -
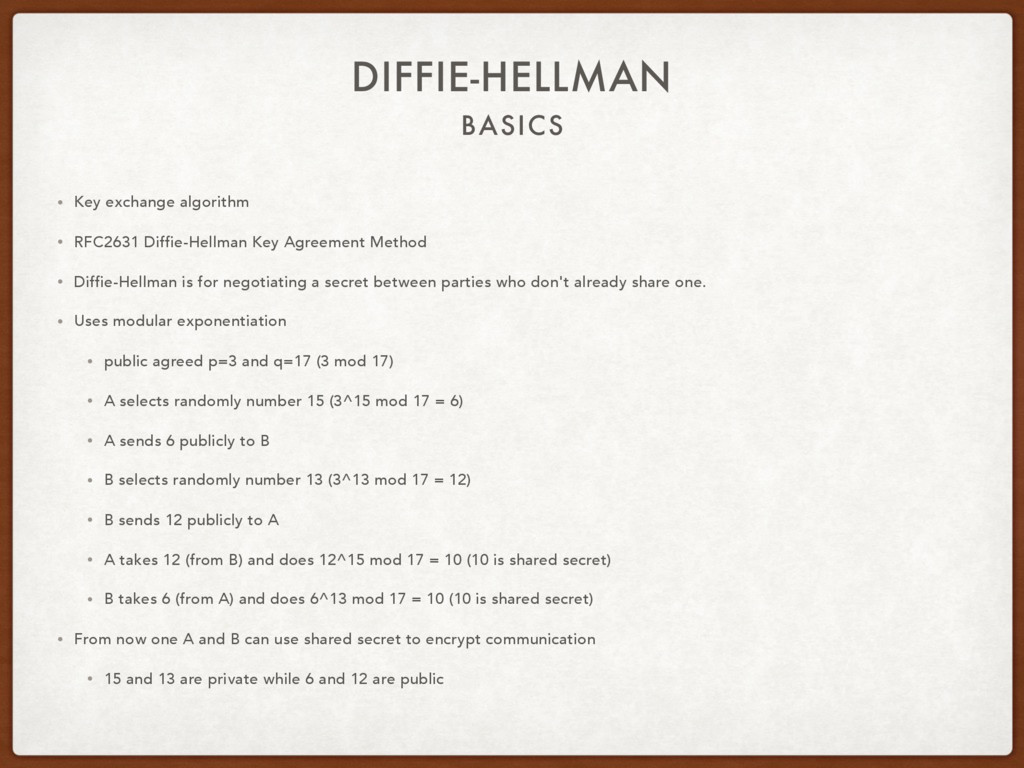
BASICS DIFFIE-HELLMAN • Key exchange algorithm • RFC2631 Diffie-Hellman Key
Agreement Method • Diffie-Hellman is for negotiating a secret between parties who don't already share one. • Uses modular exponentiation • public agreed p=3 and q=17 (3 mod 17) • A selects randomly number 15 (3^15 mod 17 = 6) • A sends 6 publicly to B • B selects randomly number 13 (3^13 mod 17 = 12) • B sends 12 publicly to A • A takes 12 (from B) and does 12^15 mod 17 = 10 (10 is shared secret) • B takes 6 (from A) and does 6^13 mod 17 = 10 (10 is shared secret) • From now one A and B can use shared secret to encrypt communication • 15 and 13 are private while 6 and 12 are public -
BASICS DIFFIE-HELLMAN • Key exchange algorithm • RFC2631 Diffie-Hellman Key
Agreement Method • Diffie-Hellman is for negotiating a secret between parties who don't already share one. • Uses modular exponentiation • public agreed p=3 and q=17 (3 mod 17) • A selects randomly number 15 (3^15 mod 17 = 6) • A sends 6 publicly to B • B selects randomly number 13 (3^13 mod 17 = 12) • B sends 12 publicly to A • A takes 12 (from B) and does 12^15 mod 17 = 10 (10 is shared secret) • B takes 6 (from A) and does 6^13 mod 17 = 10 (10 is shared secret) • From now one A and B can use shared secret to encrypt communication • 15 and 13 are private while 6 and 12 are public -
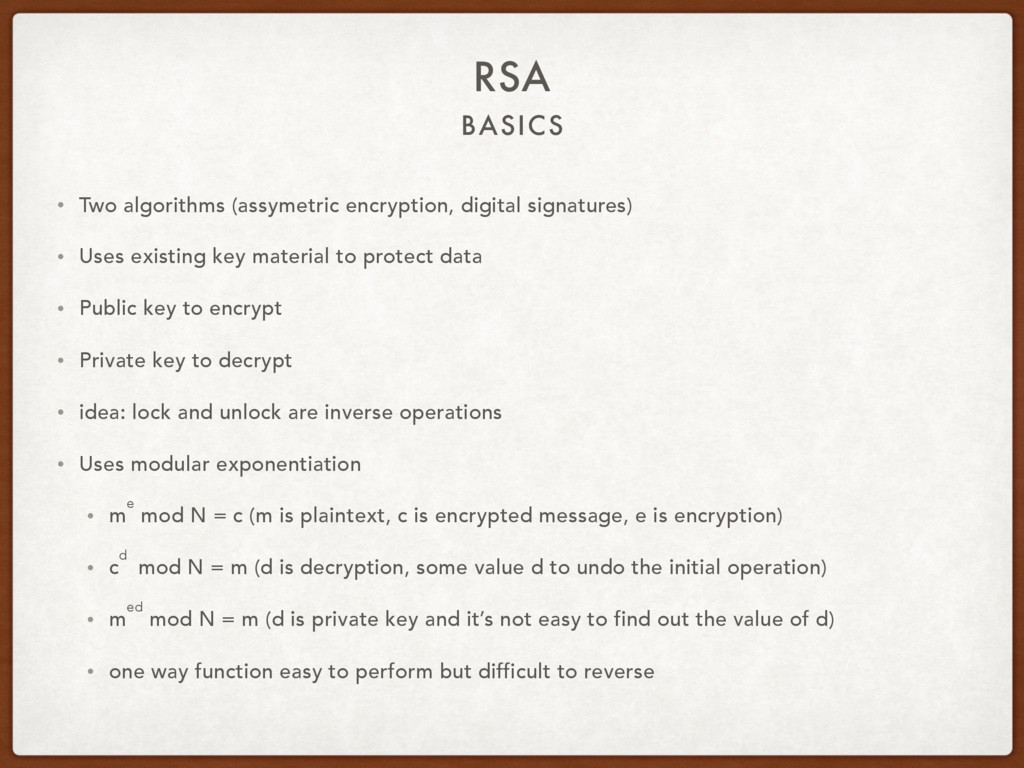
BASICS RSA • Two algorithms (assymetric encryption, digital signatures) •
Uses existing key material to protect data • Public key to encrypt • Private key to decrypt • idea: lock and unlock are inverse operations • Uses modular exponentiation • me mod N = c (m is plaintext, c is encrypted message, e is encryption) • cd mod N = m (d is decryption, some value d to undo the initial operation) • med mod N = m (d is private key and it’s not easy to find out the value of d) • one way function easy to perform but difficult to reverse -
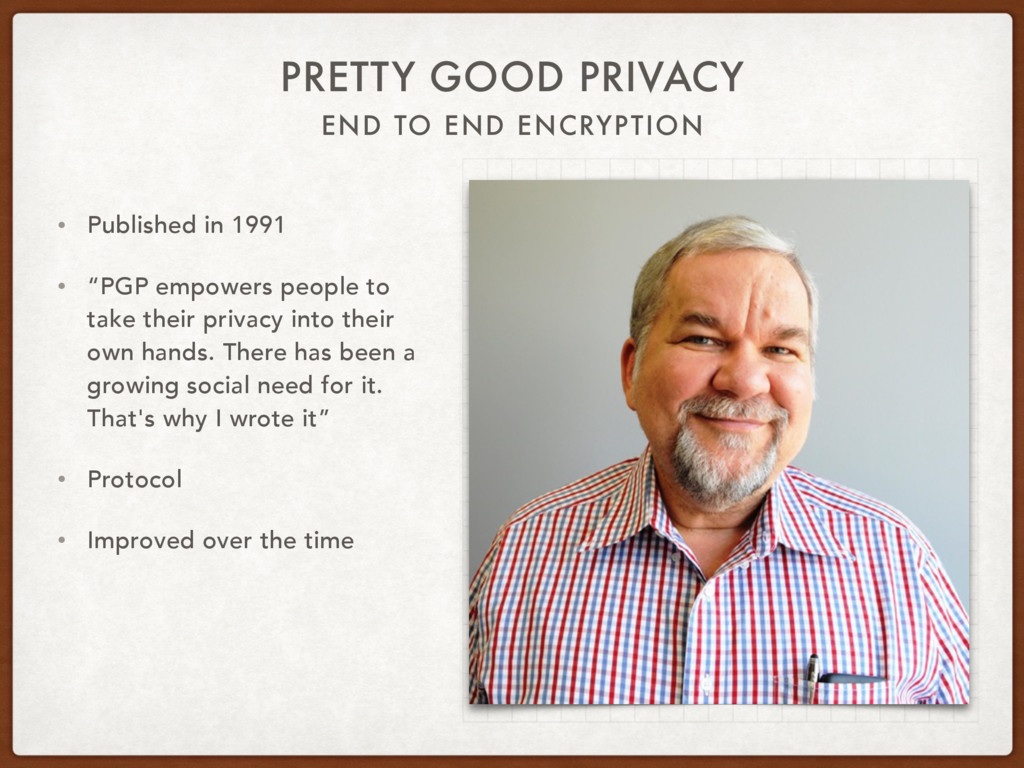
END TO END ENCRYPTION PRETTY GOOD PRIVACY • Published in
1991 • “PGP empowers people to take their privacy into their own hands. There has been a growing social need for it. That's why I wrote it” • Protocol • Improved over the time -
PRETTY GOOD PRIVACY • PGP uses Private and Public keys
along with symmetric ciphers (AES) to build encrypted messages and data signatures. • Encryption • Signature • Defines format of keys • Defines format of message that consist of many packages • Provides authentication mechanism • Web of trust - signing party -
S/MIME • Builds over MIME and Cryptographic Message Syntax •
Relies on X.509 certificates for public key distribution • Depends on the SSL PKI • you have an SSL certificate with your public key, and the fact that it is signed by a certificate authority (CA) "proves" it is really your key. • Certificate enrollment process is complex • Most emailing softwares already implement S/MIME -
OTR PROBLEM “after Alice and Bob have exchanged their message,
it should be impossible for anyone (including Alice and Bob themselves) to subsequently read or verify the authenticity of the encrypted message, even if they kept a copy of it.” -
OTR PROBLEM “after Alice and Bob have exchanged their message,
it should be impossible for anyone (including Alice and Bob themselves) to subsequently read or verify the authenticity of the encrypted message, even if they kept a copy of it.” -
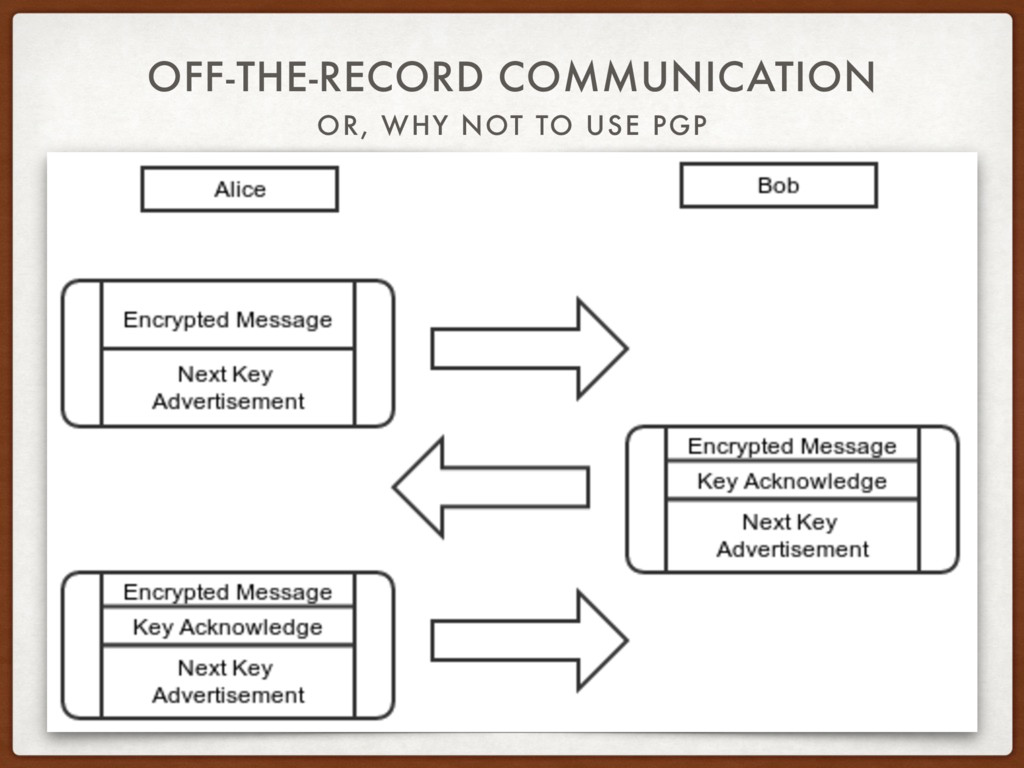
OR, WHY NOT TO USE PGP OFF-THE-RECORD COMMUNICATION • “Quite
often on the Internet, cryptography is used to protect private, personal communications. However, most commonly, systems such as PGP are used, which use long-lived encryption keys (subject to compromise) for confidentiality, and digital signatures (which provide strong, and in some jurisdictions, legal, proof of authorship) for authenticity” • “we argue that most social communications online should have just the opposite of the above two properties; namely, they should have perfect forward secrecy and repudiability” • “In off-the-record messaging, we would like to have an even stronger property than repudiability: forgeability” meal -
OR, WHY NOT TO USE PGP OFF-THE-RECORD COMMUNICATION • “Quite
often on the Internet, cryptography is used to protect private, personal communications. However, most commonly, systems such as PGP are used, which use long-lived encryption keys (subject to compromise) for confidentiality, and digital signatures (which provide strong, and in some jurisdictions, legal, proof of authorship) for authenticity” • “we argue that most social communications online should have just the opposite of the above two properties; namely, they should have perfect forward secrecy and repudiability” • “In off-the-record messaging, we would like to have an even stronger property than repudiability: forgeability” meal -
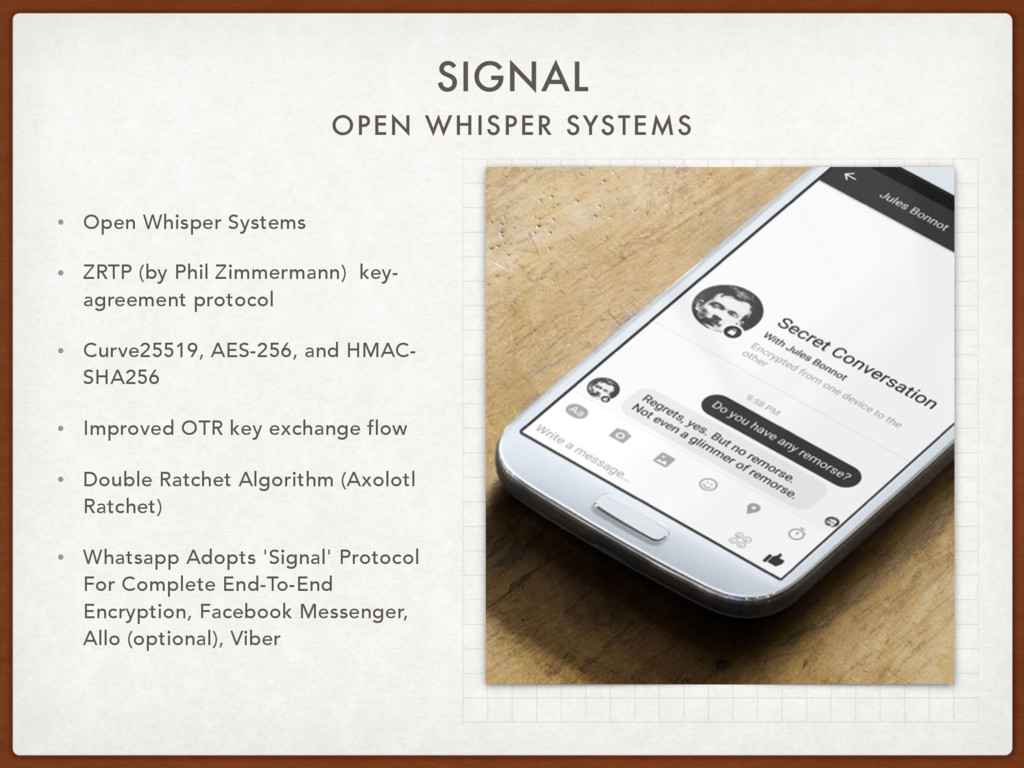
OPEN WHISPER SYSTEMS SIGNAL • Open Whisper Systems • ZRTP
(by Phil Zimmermann) key- agreement protocol • Curve25519, AES-256, and HMAC- SHA256 • Improved OTR key exchange flow • Double Ratchet Algorithm (Axolotl Ratchet) • Whatsapp Adopts 'Signal' Protocol For Complete End-To-End Encryption, Facebook Messenger, Allo (optional), Viber -
SIGNAL PROTOCOL • Poorly documented • Read implementation to understand
protocol • WhatsApp Encryption Overview - Technical white paper -
LIBRARIES • CommonCrypto • OpenSSL • NaCl • ObjectivePGP •
netpgp • gpgme • github.com/WhisperSystems/libsignal-protocol-c • JavaScript libraries bridged to iOS/macOS Cook It Yourself -
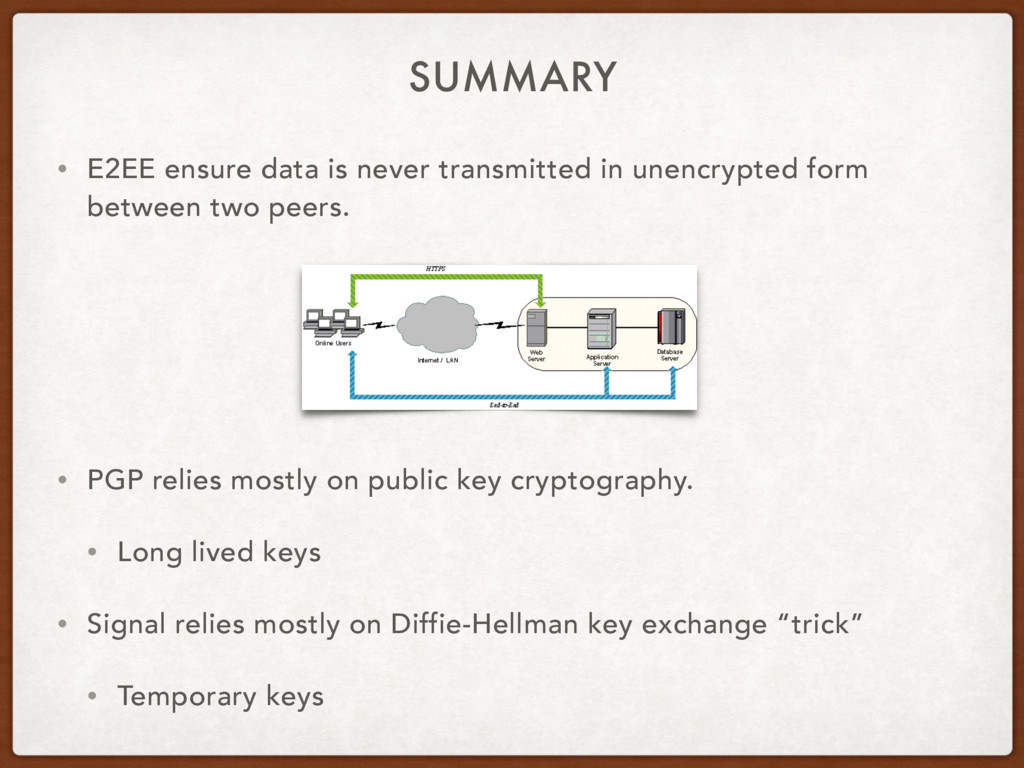
SUMMARY • E2EE ensure data is never transmitted in unencrypted
form between two peers. • PGP relies mostly on public key cryptography. • Long lived keys • Signal relies mostly on Diffie-Hellman key exchange “trick” • Temporary keys